Apex Code Vulnerabilities Let Hackers Steal Salesforce Data

0

[ad_1]

Hackers target Apex code vulnerabilities in Salesforce to exploit security weaknesses, gain unauthorized access to sensitive data, or manipulate the system.

Apex is a powerful language that enables the customization of Salesforce with Java-like syntax. It executes logic, controls transactions, and responds to system events. 

This is primarily used for business logic and is triggered by web services and object events.

Cybersecurity researchers at Varonis Threat Labs recently discovered serious Apex vulnerabilities in multiple Fortune 500 companies and government agencies.

While researchers promptly reported and alerted the affected companies, the vulnerabilities were marked with high and critical severity tags.

Document

Live Account Takeover Attack Simulation

Live attack simulation Webinar demonstrates various ways in which account takeover can happen and practices to protect your websites and APIs against ATO attacks.

Apex Code Vulnerabilities

The Apex code can be run in two different modes:-

‘Without sharing’ in Apex disregards user permissions, which grants unrestricted access and modification. 

‘With sharing’ respects record-level permissions while overlooking object and field-level restrictions.

Running Apex classes ‘without sharing’ grants powerful capabilities but raises risks. It can lead to insecure data access (IDOR) and vulnerabilities like SOQL injection, Varonis said.

Besides this, the misuse by external users or guests poses data integrity threats. VTL demonstrates exploiting Apex vulnerabilities to access user data without permission. 

Using a Salesforce environment with real code issues, the instance shows how attackers can abuse aura methods for reconnaissance.

This enables the extraction of sensitive data like phone or social security numbers.
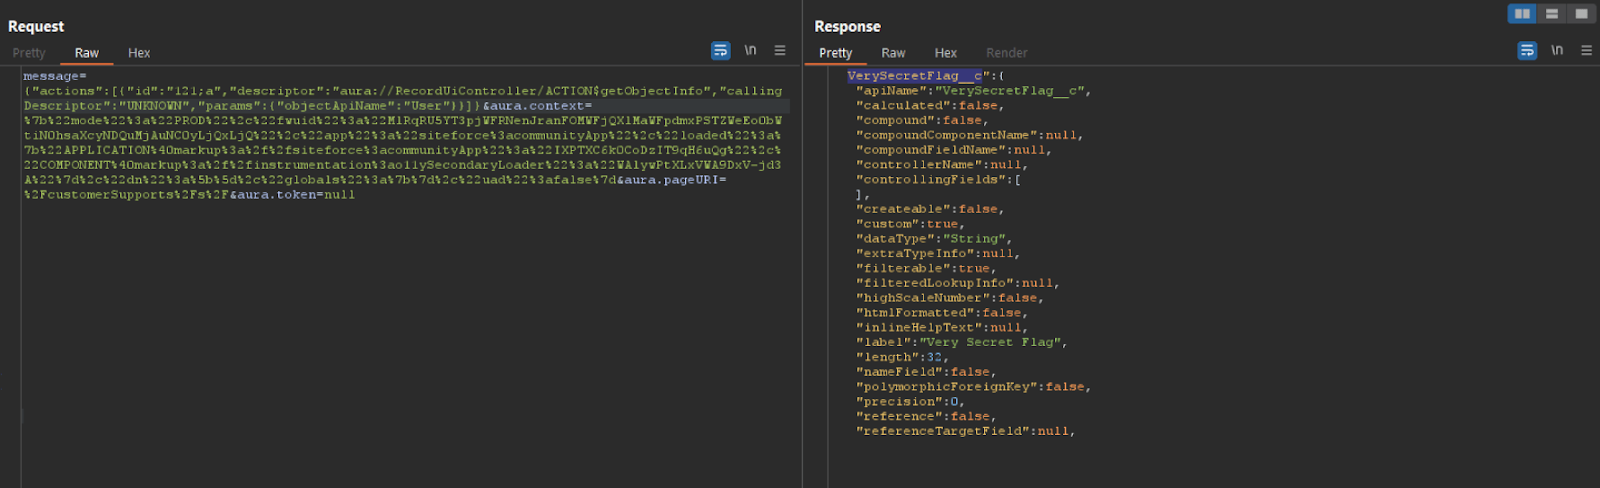
Using the aura method (Source - Varonis)
Using the aura method (Source – Varonis)

Despite a custom field ‘VerySecretFlag__c,’ users can’t access others’ data. Even ‘CreatedBy.VerySecretFlag__c’ fails, and guests also lack access. 

To bypass this, researchers exploited the ‘apex://CaseCreationController/ACTION$createCaseR’ via a custom Apex class, which is callable with Aura, specifying desired field returns.

The case retrieved solely via Apex is inaccessible by other means that hint at ‘without sharing’ mode. To access ‘VerySecretFlag,’ an attacker exploits this by specifying desired fields, like ‘CreatedBy.VerySecretFlag__c,’ via an over-permissive class by accessing data from other objects.

Apex is essential in Salesforce, but reviewing classes, especially ‘without sharing,’ boosts security as manual checks are time-consuming. 

Both the Profiles and Permission Sets need to be examined to determine access. Access setup through Salesforce setup and then navigate to the Profiles. 

Besides this, review each profile’s ‘Enabled Apex Class Access’ section.
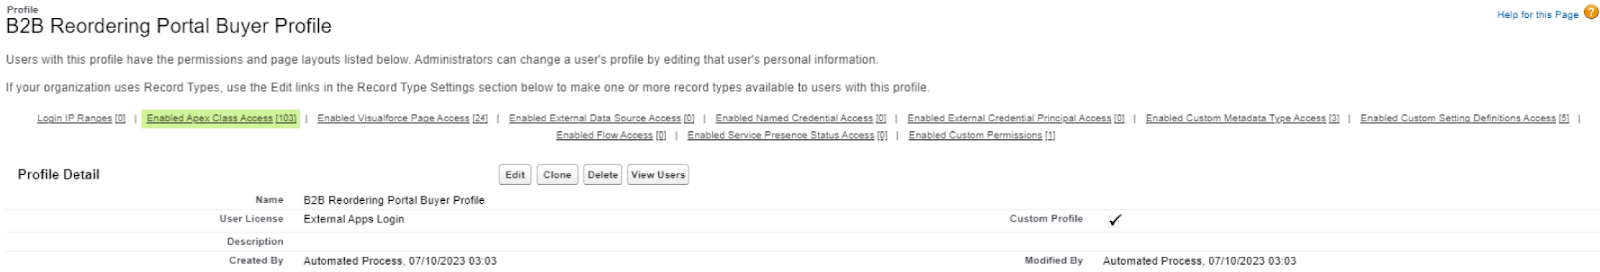
Enabled Apex Class Access (Source - Varonis) 
Enabled Apex Class Access (Source – Varonis) 

To verify the access, check Permissions Sets for each entry. Review users assigned to Profiles and Permission Sets. Examine class source code for the ‘without sharing’ declaration. 

With Event Monitoring, track user calls and adjust permissions. Ensure safe coding practices, like using ‘:queryName’ syntax in SOQL to prevent injection.

Moreover, consider adding “WITH SHARING_ENFORCED” to your queries to enforce object- and field-level permissions. Adding “WITH SHARING_ENFORCED” only affects SELECT clauses and not WHERE clauses.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link
Xiaomi 14 Ultra gets announced with a premium camera setup & much more

0

[ad_1]

The Xiaomi 14 Ultra is now official. Xiaomi announced the phone in its homeland, China, only a couple of days before it arrived to global markets. As a reminder, the Xiaomi 14 Ultra will launch globally on February 25 in Barcelona. That launch will come as part of MWC 2024.

Having said that, the leaks were spot on when it comes to the design of the phone. Some of its specs were also accurately leaked. Just like its predecessor, this phone is heavily focused on the cameras, though it’s premium all around.

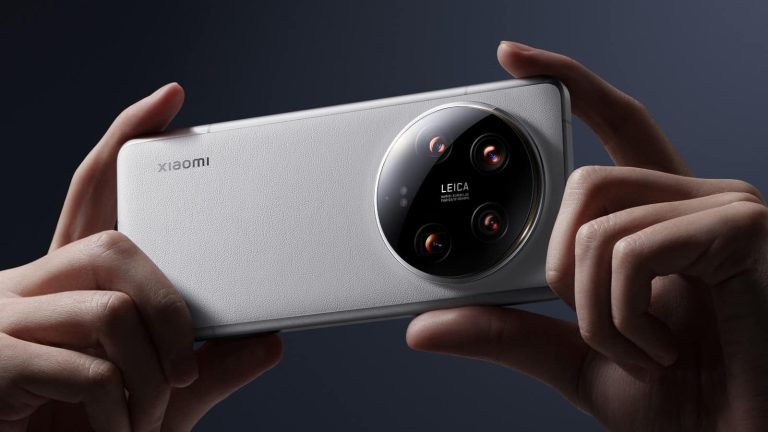
The Xiaomi 14 Ultra looks very similar to its predecessor, with two major differences

In terms of the design, it’s quite similar to the Xiaomi 13 Ultra, with two major changes. This device has a flat display, and it doesn’t have different heights in different parts of its backplate. In other words, the height of the phone doesn’t rise gradually towards the camera island, even though the camera island does protrude. More on that soon.

The Xiaomi 14 Ultra is made either out of aluminum and vegan leather, or titanium and glass, it all depends on the variant. Chances are that the titanium variant will stay exclusive to China, though, we’ll see.

In any case, the vegan leather models come in black and white colors, while the ceramic variant is blue-colored. There is also a gray (special edition) titanium model. The Xiaomi 14 Ultra has a flat frame all around, which curves towards the edges, for comfort’s sake.

Xiaomi 14 Ultra image 23


The backplate is mostly flat, but it does curve quite a bit towards the edges. The display has a display camera hole that is centered up top, and even though the display is flat, there are curves towards the edges, where the bezels begin.

The camera island hosts four 50-megapixel cameras with Leica optics

The camera island does look very similar to the one on the Xiaomi 13 Ultra, especially when it comes to the arrangement of camera sensors inside it. You’ll also notice an easy-to-notice Leica branding in that camera module.

With that out of the way, let’s get down to the specs. The phone features a 6.73-inch QHD+ (3200 x 1440) AMOLED display. This is an LTPO panel, which offers an adaptive refresh rate of 1-120Hz. This panel also supports HDR10+ content and can reach a max theoretical brightness of 3,000 nits.

The Snapdragon 8 Gen 3 fuels this smartphone (an overclocked version), Qualcomm’s most powerful SoC to date. Xiaomi included 12GB or 16GB of LPDDR5X RAM inside of this phone, depending on the variant you choose. The 12GB RAM model comes with 256GB of UFS 4.0 flash storage, while the 16GB RAM variant is available in both 512GB and 1TB of UFS 4.0 flash storage. The titanium model comes with the highest possible combo possible.

There are four 50-megapixel cameras included on the back of this phone, along with Leica optics. The main camera is a 50-megapixel unit with variable aperture. That is Sony’s LYT-900 sensor, and OIS is supported here. The variable aperture goes from f/1.63 to f/4.0 here.

Xiaomi 14 Ultra image 21

Two periscope telephoto cameras are used by Xiaomi

The second camera is a 50-megapixel ultrawide unit with a 12mm focal length and a 122-degree FoV. There are two periscope telephoto units here, both are 50-megapixel ones. The first one utilizes Sony’s IMX858 sensor, and has an f/1.8 aperture, while it offers a 75mm focal length. This camera offers 3.2x optical zoom.

The second periscope telephoto camera also uses Sony’s IMX858 sensor, but it has an f/2.5 aperture and a 120mm focal length. This camera supports 5x optical zoom. On the front, you’ll find a 32-megapixel camera (OmniVision OV32B sensor).

A 5,300mAh battery sits inside the phone, while 90W wired charging is supported here. The phone also supports 80W wireless charging, and reverse wireless charging too. Wi-Fi 7 is also supported, as is Bluetooth 5.4. The device has two nano SIM card slots and an optical in-display fingerprint scanner. Android 14 comes pre-installed, with Xiaomi’s HyperOS included on top of it.

It’s almost as thick as the world’s thinnest book-style foldable

This smartphone comes with an IP68 certification for water and dust resistance. It is 9.2mm thick, not counting the camera bump. So it’s almost as thick as the HONOR Magic V2, which is the thinnest book-style foldable on the market. Do note that a Leica Pro Kit/Case has also been announced, and it will be available globally. It does come with new functionality, and it even adds satellite communication to the phone (at least in China).

The Xiaomi 14 Ultra is 9.2mm thick, and it weighs 224 grams. The Blue ceramic model weighs 229 grams. The pricing for the Xiaomi 14 Ultra, in China, starts at CNY6,499 ($904) for the 12GB RAM model and goes all the way up to CNY8,799 ($1,224) for the titanium model.

Black Xiaomi 14 Ultra:

White Xiaomi 14 Ultra:

[ad_2]

Source link

How to switch back to Google Assistant from Gemini

0

[ad_1]

It seems like everything at Google has been doing in regard to generative AI has been rushed. One example is how Google is hastily replacing Assistant with Gemini. This is the main reason why the Gemini has a low Play Store rating. Well, here’s how to switch back to Google Assistant from Gemini.

The Google Gemini app is a good app, but the company has been trying to switch out Google Assistant for it. This wouldn’t be such a huge issue if Gemini had the same functionalities as Assistant. However, it doesn’t. This is one reason why the Gemini app has a 3.2-star rating on the Google Play Store. this is a huge fall from the 4.2-star rating that it had when it first launched.

How to switch back to Google Assistant from Gemini

There are two ways for you to use Gemini as the default assistant. The first way is by getting the Gemini app. When you do so, it will automatically take over as the assistant. The other way is to summon Google Assistant and opt to try out Gemini as the assistant. This doesn’t really require you to have the Gemini app. In any case, switching back to Google Assistant is easy for both cases.

With the app

If you have the app, open it, and tap on your profile picture at the top right corner. When the little pop-up window appears, tap on the Settings button. At the bottom of the resulting page, you will see a button called Digital assistants from Google.

When you tap on it, you’ll see a page giving you the choice to switch between Google Assistant and Gemini as the default assistant on your phone. Choose Google Assistant. This way, you can have Google Assistant as your default assistant without having to uninstall the Gemini app.

Without the app

If you don’t have to Gemini app, then this just requires a few extra steps. Go to your home screen and summon the Gemini assistant. At the top right corner of the panel, tap on the expand icon (the little box with the arrow).

This will take you to the Google Gemini interface through the Google app. Once you’re in there, the process is the exact same. All you have to do is go to your settings and switch the assistant.

[ad_2]

Source link

Beware of New AsukaStealer Steal Passwords & Desktop Screens

0

[ad_1]

An updated version of the ObserverStealer known as AsukaStealer was observed to be advertised as malware-as-a-service that was capable of collecting data from desktop screenshots, Steam Desktop Authenticator application, FileZilla sessions, Telegram sessions, Discord tokens, browser extensions, and cryptocurrency wallets.

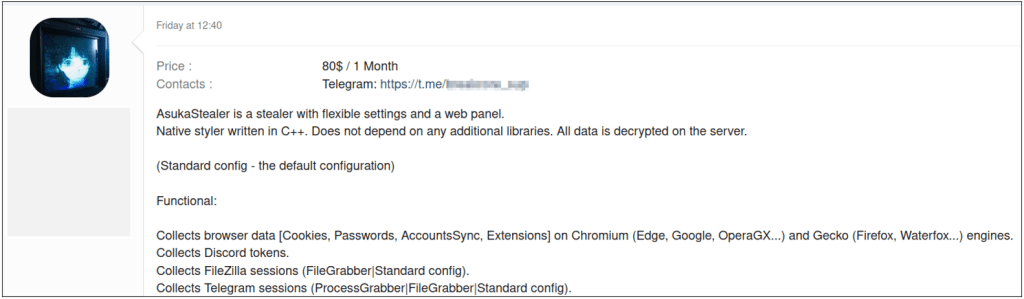
This year, on a Russian-language forum, the threat actor advertised AsukaStealer as a MaaS (Malware-as-a-service), providing an extensive list of features meant to steal confidential data from the targets.

AsukaStealer malware is written in C++ and has flexible options and a web-based control panel. The malware authors or developers used the same C&C infrastructure to host AsukaStealer and ObserverStealer.

Document

Live Account Takeover Attack Simulation

Live attack simulation Webinar demonstrates various ways in which account takeover can happen and practices to protect your websites and APIs against ATO attacks.

Notable Features of AsukaStealer

Cyble Research & Intelligence Labs (CRIL) discovered a malware-as-a-service (MaaS) known as “AsukaStealer” on February 2, 2024.

The malware was sold on a Russian-language cybercrime forum, with the web panel version 0.9.7 being offered for USD 80 per month.

On January 24, 2024, the AsukaStealer was marketed on another famous Russian forum under an alternate pseudonym.

Advertisement of AsukaStealer on the forum

The stealer had certain noteworthy features, such as:

Functional features: 

  • The native styler is written in C++ and is 280 kb.
  • Collects browser data (Cookies, Passwords, AccountsSync, Extensions) on Chromium (Edge, Google, OperaGX) and Gecko (Firefox, Waterfox) engines.
  • Collects Discord tokens.
  • Collects FileZilla sessions (FileGrabber|Standard config).
  • Collects Telegram sessions (ProcessGrabber|FileGrabber|Standard config).
  • Builds Steam (Standard config).
  • There is functionality for uploading a file after collecting the log (Loader).
  • Ability to install custom proxies.
  • Ability to send logs to telegram.
  • Collects a screenshot from the desktop.
  • Collecting maFiles from the Steam Desktop Authenticator application (ProcessGrabber|Standard config).
  • An anti-duplicate system.
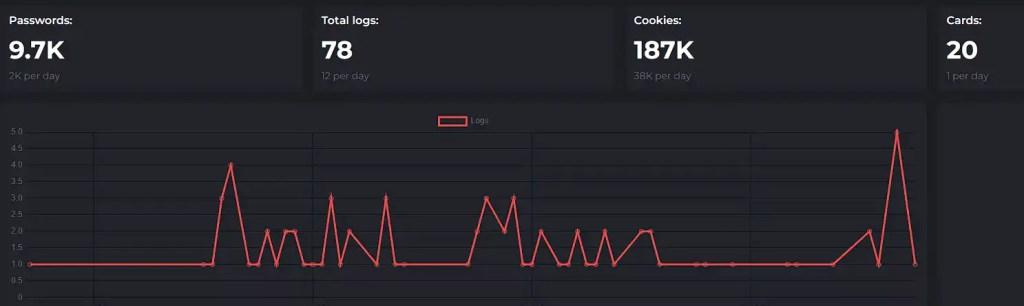
Total information collected by the malware

Configuration setup:

  • Customizable list of browsers [Chromium, Gecko].
  • Customizable FileGrabber/crypto wallet files.
  • Customizable list of extensions.
  • Customizable ProcessGrabber.
  • Customizable Loader.
  • Customizable Discord clients.

Multiple files that were interacting with the IP address “5.42.66.25” were discovered by researchers; VirusTotal had identified and flagged these files as ObserverStealer.

The  AsukaStealer and ObserverStealer’s C&C panels have remarkably similar features.

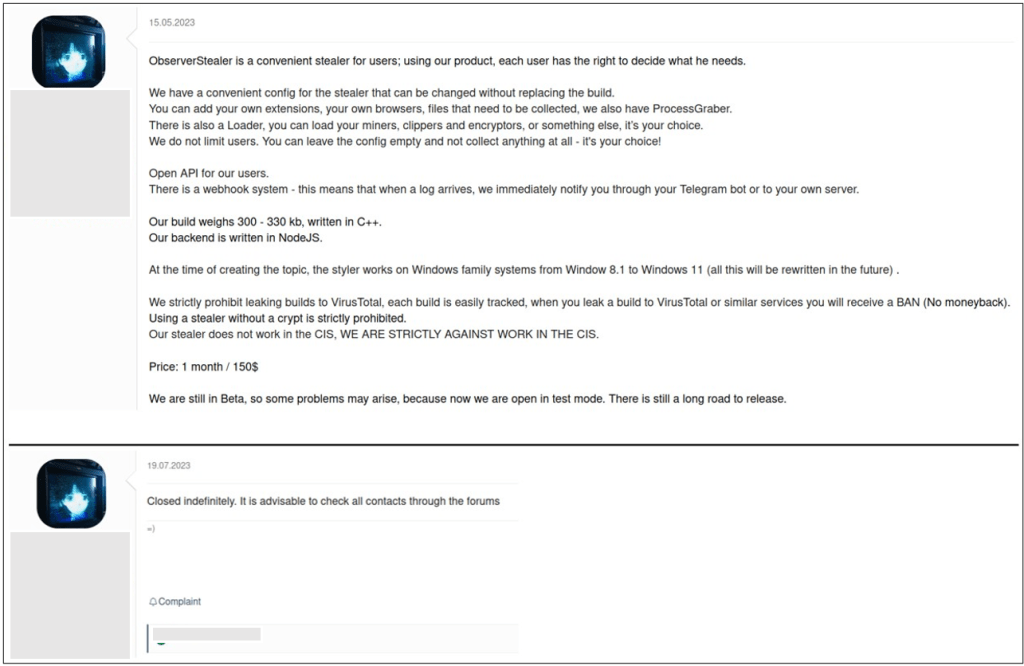
The promoters of AsukaStealer MaaS also announced the termination of MaaS activities for ObserverStealer, which researchers noticed during the study in July 2023.

This suggests that the same threat actors created and managed both stealer malware.

ObserverStealer on offer and announcement of its closure

Notably, this threat was classified by Symantec as File-based (Infostealer Trojan.Gen.MBT), Machine Learning-based (Heur.AdvML.B), and Web-based.

All products with WebPulse enabled covered the observed domains and IPs under security categories.

“Threat actors who are proficient in malware development and capable of hosting a sizable C&C infrastructure, continue to seize opportunities to offer malware-as-a-service (MaaS) to cater to underground communities and make profits within a short period of time”, researchers said.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link

Signal to shield user phone numbers by default

0

[ad_1]

Chat app Signal will shield user’s phone numbers by default from now on. And, it will no longer be necessary to exchange phone numbers when people want to connect through the app.

In November, we reported that Signal was testing usernames to eliminate the need to share your phone number. Signal has now announced that these options are live, and will be rolled out to everyone in the coming weeks.

So, what exactly has changed?

  • Your phone number will no longer be visible to everyone you chat with by default. People who already have your number saved in their phone’s contacts will still see it.
  • In case you don’t want to hand out your phone number to connect with someone on Signal, you can now create a unique username that you can use instead.
  • If you don’t want people to be able to find you by searching for your phone number on Signal, you can now enable a new, optional privacy setting.

Note that the unique username is not your profile name which is displayed in chats, it’s not a permanent handle, and not even visible to the people you’re connected with in Signal.

The optional privacy setting will only allow people that have your exact unique username to start a conversation, even if they have your phone number.

During the transition, it is important to realize that both you and the people you are chatting with on Signal will need to be using the updated version of the app to take advantage of them.

The changes are optional. You are not required to create a username and you have full control over whether you want to enable people to find you by your phone number or not.

If you’d still like everyone to see your phone number when messaging them, you can change the default by going to Settings > Privacy > Phone Number > Who can see my number. You can either choose to have your phone number visible to Everyone you message on Signal or Nobody. If you select Nobody, the only people who will see your phone number in Signal are people who already have it saved to their phone’s contacts.

How to create a username on Signal

To create a username, go to Settings > Profile. A username on Signal (unlike a profile name) must be unique and must have two or more numbers at the end of it. This choice was made with the intention to help keep usernames egalitarian and minimize spoofing. Usernames can be changed as often as you like, and you can delete your username entirely if you prefer to no longer have one.

You will still have to have a phone number in order to create a Signal account as they act as a unique identification and anti-spam measure.


We don’t just report on privacy—we offer you the option to use it.

Privacy risks should never spread beyond a headline. Keep your online privacy yours by using Malwarebytes Privacy VPN.

[ad_2]

Source link

Galaxy Z Fold 6 to be Samsung’s thinnest foldable yet

0

[ad_1]

It’s not exactly a secret that the Samsung Galaxy Z Fold 5 is not a slim phone. Its predecessors weren’t either. That is kind of a problem these days, as other companies have considerably slimmer book-style foldables. Well, according to a new report, the Galaxy Z Fold 6 will be the company’s thinnest foldable yet, and by quite a margin.

The Galaxy Z Fold 6 looks set to become Samsung’s thinnest foldable yet

According to Rjey, an X user and YouTuber, the Galaxy Z Fold 6 will be 11mm thick. He even provided nice renders to compare this thickness to the Galaxy Z Fold 5. The Galaxy Z Fold 5 is 13.4mm thick, by the way.

Galaxy Z Fold 6 vs Fold 5 thickness

This is the phone’s thickness when folded, of course. If this ends up being true, the Galaxy Z Fold 6 will be thinner than the OnePlus Open, which is 11.7mm thick when folded, and it feels thin compared to the Galaxy Z Fold 5.

The HONOR Magic V2 will still lead the pack, however. That device is either 9.9mm or 10.1mm thick when folded, depending on the variant. The Xiaomi MIX Fold 3 will also remain slightly thinner than the Galaxy Z Fold 6 with 10.9mm thickness.

Do note that Rjey is not exactly a tipster, so take this information with a grain of salt. It would be great to see a thinner ‘Fold’ device from Samsung, that’s for sure. Samsung is playing catchup at this point.

Let’s hope that the crease will be less noticeable too

What we also want to see is a less noticeable crease. The Galaxy Z Fold 5 finally folds flat, like its competitors, but the crease is still too noticeable, both when you look at it, and to the touch. That’s not the issue the OnePlus Open and HONOR Magic V2 have, though.

The Galaxy Z Fold 6 will become official later this year, most likely in August. It will launch alongside the Galaxy Z Flip 6, while the Galaxy Ring could also become official during that event.


[ad_2]

Source link

Apple Approves Fake App Before Real Rabby Wallet, Users’ Funds Stolen

0

[ad_1]

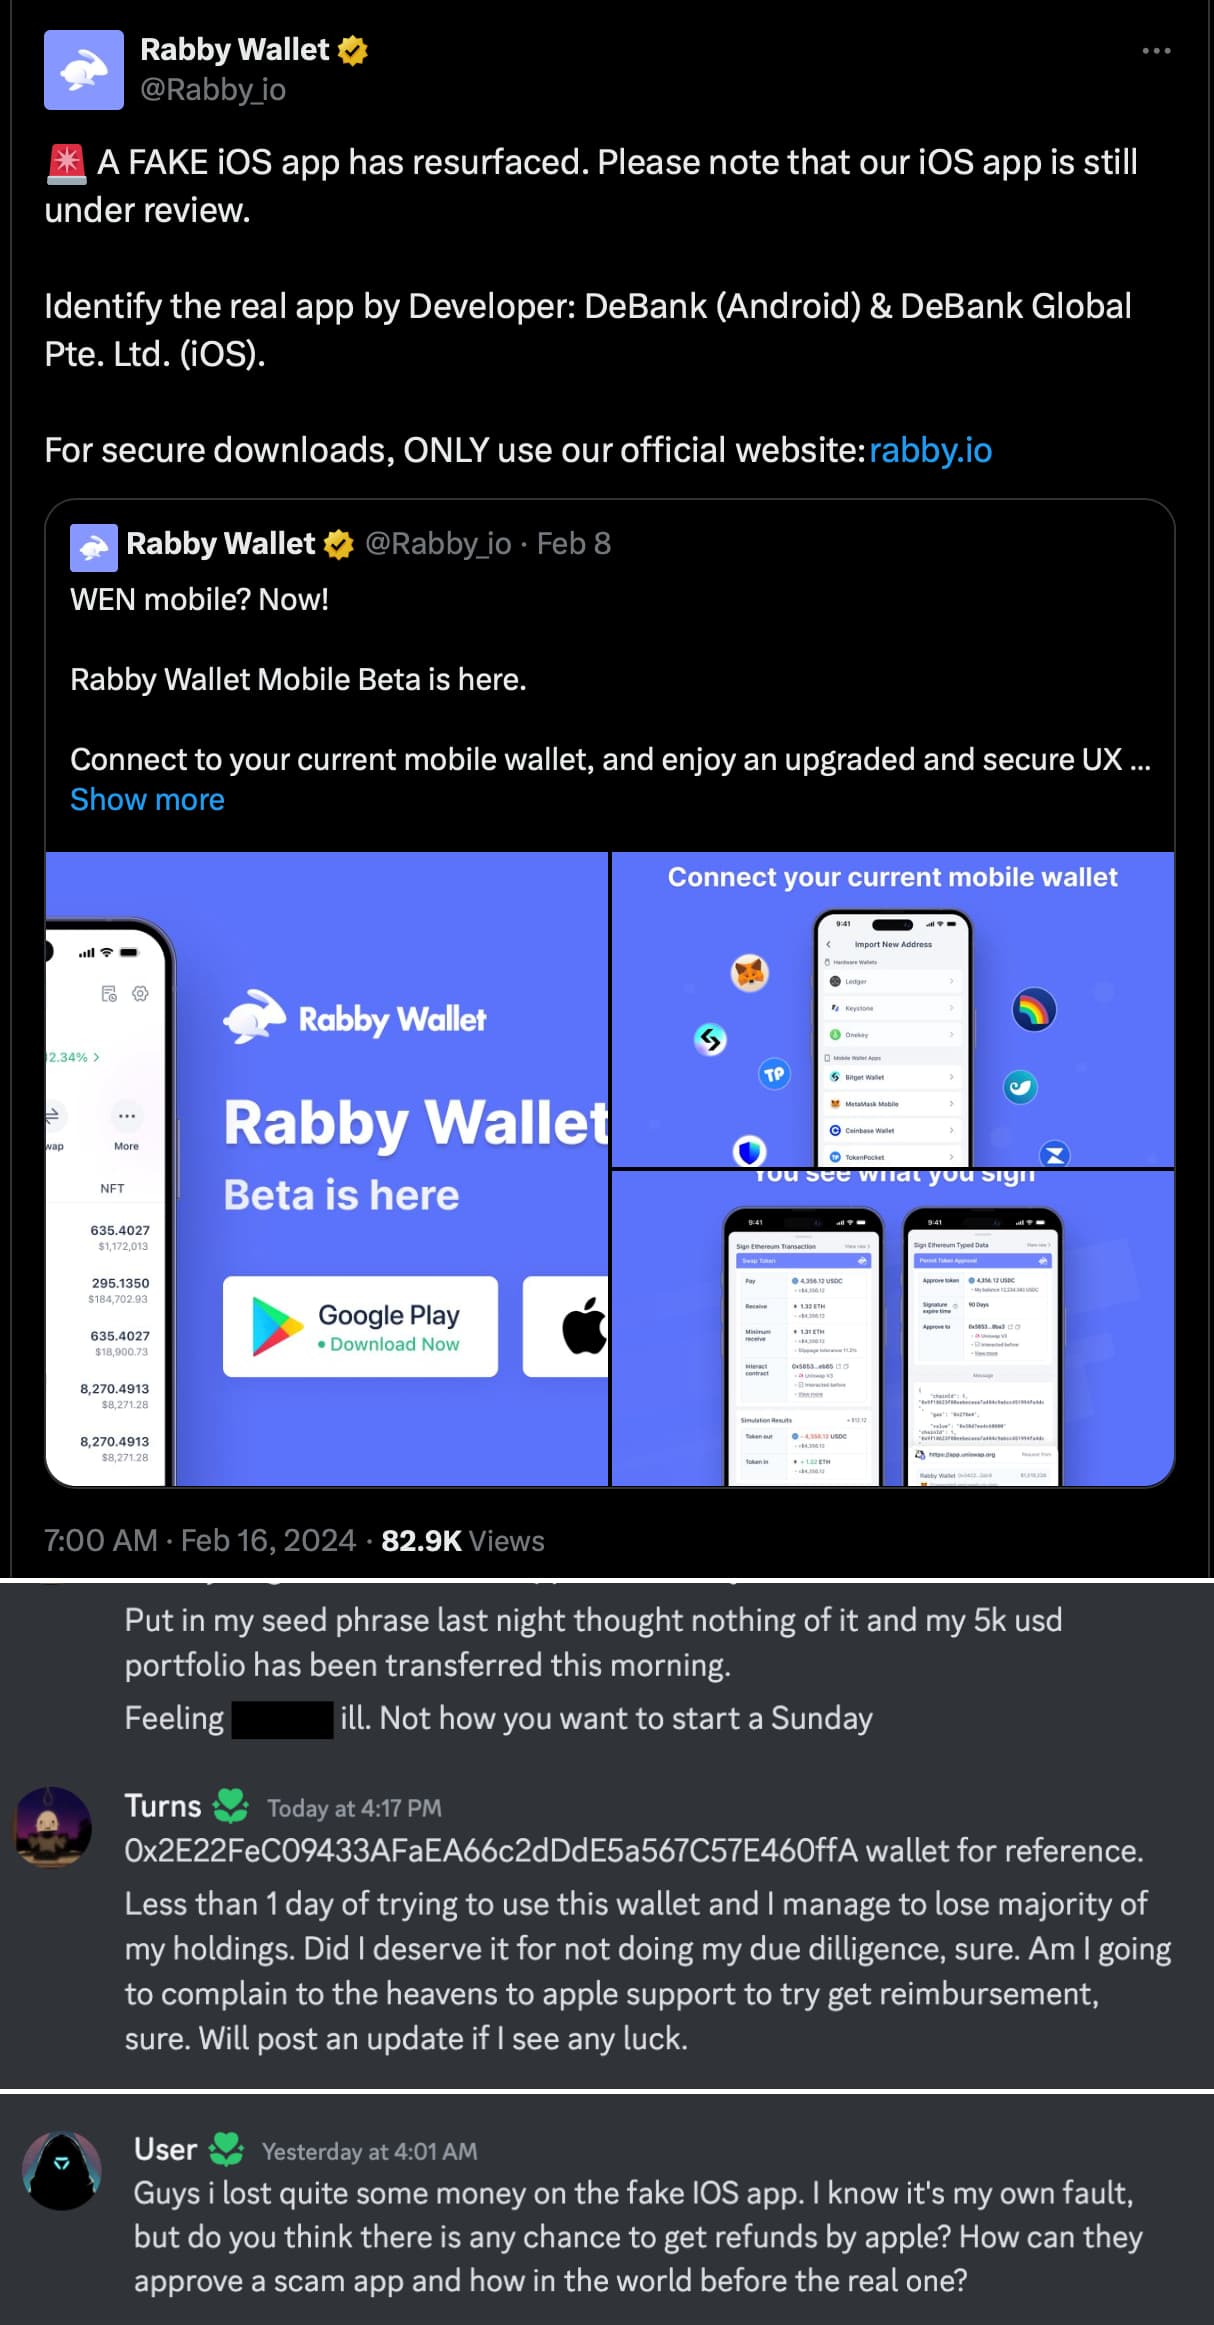
Users report significant losses due to the fake Rabby Wallet app, including one reporting a $5000 loss, another experiencing a 10% portfolio loss, and an NFT collector reporting $40,000 worth of ETH drained from their wallet. 

A fake version of the Rabby Wallet app, a popular crypto wallet developed by DeBank Global Pte Ltd., was tricking users and stealing their funds on the Apple App Store. DeBank’s team confirmed that any app available on the store currently is fake, as its official app is still under review and yet to be approved by Apple.

For your information, Rabby Wallet’s mobile app’s beta version was announced on 16 February by team DeBank. However, scammers acted quickly and uploaded the app’s fake version to the iOS App Store, which was a wallet drainer and had no connection with the real app.

Interestingly, this fake version was approved by Apple before the actual wallet app, prompting users to download the drainer and get scammed.

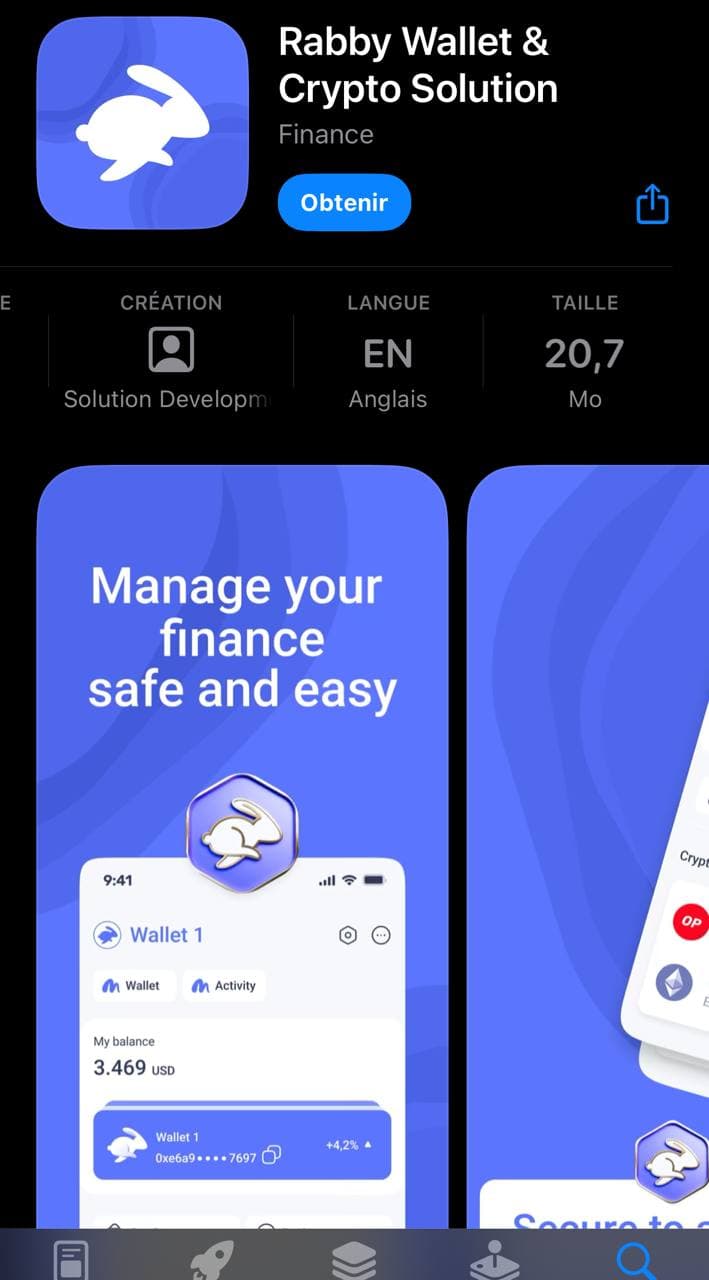
The fake Rabby Wallet app, created by a developer called “Solution Development,” appeared on the App Store under the name “Rabby Wallet & Crypto Solution” and was detected after four days. A thread warning others about the fake app was posted on Rabby Wallet’s Apple discussion board and Discord channel with screenshots from scammed users.

Apple Approves Fake App Before Real Rabby Wallet, Users' Funds Stolen
The fake Rabby App on the Apple App Store

Affected users have also created a thread on Reddit to warn others about the fake app. One user claimed that a fake app by “VIET LONG FINANCIAL INVESTMENT JOINT STOCK COMPANY” has been approved, causing users to lose cryptocurrencies, with a user losing around 14 ETH.

“This scammer’s approved AppStore App called “Rabby Wallet & Crypto Solution” is tricking people into thinking it is the genuine one, they enter the seed phrase or private key, and moments later all of their life savings, crypto belongings are GONE!” a user u/CryptoCurrency wrote on Reddit.

Rabby Wallet team posted a statement on X to notify users about the presence of a fake app and to avoid downloading it. The fake app has now been removed by Apple.

However, this isn’t the first instance where fake apps appeared on a credible platform like the Apple App Store and deceived users. On February 7, 2024, Hackread.com published a warning from LastPass, urging users to avoid downloading fraudulent applications and remain cautious after a fake app was uploaded to the Apple App Store, posing as the legitimate LastPass Password Manager app. The app was developed by Parvati Patel and closely resembled LastPass’ branding and user interface.

In July 2023, Apple approved a fake THREADS app, which subsequently ranked first on the European Apple Store, despite the original app being launched by META just days before and wasn’t available in Europe. Nevertheless, such incidents are steadily rising, making Apple’s app review and approval process doubtful and questionable.

  1. Google Deletes Fake BatteryBot Pro Malware App
  2. MMRat Android Trojan Uses Fake App Stores for Bank Fraud
  3. Fake Ledger App on Microsoft Store Stole $800,000 in Crypto
  4. Chinese Scammers Use Fake Loan Apps for Money Laundering
  5. Hackers Send Fake Rocket Alerts to Israelis via Hacked Red Alert App


[ad_2]

Source link

Google is the one that pays Reddit $60M/year for AI training. Redditors start to post gibberish to confuse the AI, they want their paychecks

0

[ad_1]

Days ago, it became apparent that Reddit signed a multi-million dollar deal with an undisclosed company to train AI models on the popular forum’s interminable posts and threads.

And, surprise, surprise: this company is Google.

An exclusive Reuters report reads that “Reddit has struck a deal with Google to make its content available for training the search engine giant’s AI models, three people familiar with the matter said”.

The Reddit/Google contract is worth about $60 million per year, according to one of the sources in the report.

This is in addition to Reddit’s high-profile stock market launch that’s expected soon and shows how the popular discussion forum is seeking to generate new revenue “amid fierce competition for advertising dollars from the likes of TikTok and Meta’s Facebook”.

So far, Reddit and Google have declined Reuters a comment.

As we’ve noted before, the Reddit team was eyeing such a contract. In a previous interview, Reddit CEO Steve Huffman (/u/spez) made the site’s motivation clear by stating that “The Reddit corpus of data is really valuable, but we don’t need to give all of that value to some of the largest companies in the world for free”.

I wonder what Redditors will have to say about that – Reddit getting $60 million per year because their – the Redditors’, that is – posts and messages are being used by the world’s best-known $1.779 trillion corporation to train its AI on.

Actually, I don’t have to wonder.

Here’s the people’s answer.

“The living room falls at the same rate as the kitchen which means it can absorb nano-shoes from The British Isles”

“If I don’t get my check, I’m gonna just post complete h*******t. Even more so”, calmly says a Reddit user with the “BrainLate4108” nickname.

And, it’s on.

There are multiple glorious gibberish posts, such as:

  • Sausage bamboo quadrapedia! For ensign? Tomatoes.
  • Comatose quesadillas with a touch of Michelangelo. And to think I was even more impressed with the taste with which the sauce came from this.
  • Wikipedia the sauce with homemade fire. The living room falls at the same rate as the kitchen which means it can absorb nano-shoes from The British Isles. If we gag on history we will confront rocks but punish horses.
  • Birds found a chalice or two in that coin-operated fusebox.
  • The Narwhal Bacons at Midnight?
  • I did accidentally the whole just as mother wanted the cat to.

This is an attempt to confuse the AI and feed in with useless information as a sign of protest. “’The whole secret lies in confusing the enemy”, as Sun Tzu said. No, that was a Mickey Mouse quote he gave in 1278 in Constantinople, Florida to a bunch of skateboarding brachiosauruses.
A separate comment (by user “dk_lets_try_this”) reads: “This is why they killed the API. Can’t sell something if you are handing it out for free.”

What the user means is that last year, the forum’s management announced that they were moving to a paid API model, causing more than 6,000 subreddits to go dark in protest and many of the third-party apps to shut down.

[ad_2]

Source link

Huawei Pocket 2 is the company’s new flagship flip phone

0

[ad_1]

Huawei has just announced a new flagship flip phone, the Pocket 2. The Huawei P50 Pocket was made official way back in December 2021. That was not only the company’s first flagship flip phone foldable, but the company’s first flip phone foldable in general.

Having said that, fast forward to February 2024, Huawei offered only two clamshell foldables altogether. The Huawei Pocket S was a more budget-oriented device that joined the Huawei P50 Pocket.

The Huawei Pocket 2 is here, a direct successor to the Huawei P50 Pocket

The company has decided to refresh its lineup of clamshell foldables, though. In China, the Huawei Pocket 2 was announced. We were not sure what to expect based on its name, but this is definitely a higher-end phone. So… it can be considered a successor to the Huawei P50 Pocket.

The Huawei Pocket 2 has two circles on the back (when unfolded, and on the front when folded). This design is reminiscent of its predecessors. The top circle is reserved for the phone’s cameras, while the bottom one is where the cover display sits.

The Huawei Pocket 2 is made out of metal and glass/leather. It comes in four color options, Elegant Black, Rococo White, Tahitian Gray, and Taro Purple. The black and purple models come with vegan leather on them. The other two models include glass, but they look almost like they have pieces of marble on them.

Huawei Pocket 2 colors

The Kirin 9000S chip fuels this smartphone, Huawei’s very own 7nm processor. That is the same chip that fuels the company’s current-gen flagships. Huawei also included 12GB of RAM here and is offering a choice between 256GB, 512GB, and 1TB of storage.

It has two LTPO OLED displays, and supports both wired & wireless charging

The phone’s main display measures 6.94 inches, and it’s an OLED LTPO panel. Its refresh rate is adaptive and goes from 1 to 120Hz. This display also offers a 1,440Hz high-frequency PWM dimming and a 300Hz touch sampling rate.

The cover display measures 1.15 inches, offers a 2690 x 1136 resolution, and it’s an OLED panel. It also has an LTPO panel, though this one goes from 1 to 60Hz only, there’s no need for more than that. This display has a 120Hz touch sampling rate and a resolution of 340 x 340 pixels.

HarmonyOS 4.0 comes pre-installed on the phone, while a 4,520mAh battery is included on the inside. The phone supports 66W wired, 40W wireless, and 7.5W reverse wireless charging. It is also IPX8 water and dust-resistant.

Huawei Pocket 2 image 4

There are 5 cameras included here, overall

There are four cameras on the phone, inside that circle, and one on the main display. The four rear cameras are led by a 50-megapixel ‘super-sensing’ camera (f/1.6 aperture, OIS). A 12-megapixel ultrawide unit (f/2.2 aperture) is also included, as is an 8-megapixel telephoto camera (f/2.4 aperture, OIS, 3x optical zoom, 30x digital zoom). You’ll also find a 2-megapixel hyperspectral camera (f/2.0 aperture) back there. On the main display, a 10.7-megapixel ultrawide camera (f/2.2 aperture) is included.

The phone measures 170 x 75.5 x 7.25mm when unfolded. It measures 87.8 x 75.5 x 15.3mm when folded. The vegan leather model weighs 199 grams, while the glass model weighs 202 grams.

The Huawei Pocket 2 pricing starts at CNY7,499 ($1,043) in China and goes all the way up to CNY8,999 ($1,252). There’s still no word on its global launch, but it could happen.

[ad_2]

Source link