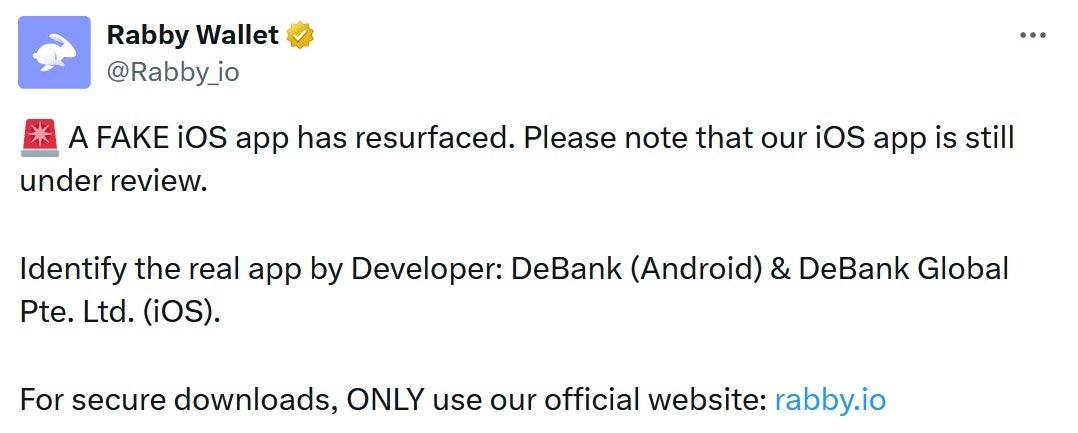
Text from the developer of the real Rabby Wallet app
[ad_2]
Source link

Text from the developer of the real Rabby Wallet app
Israel’s national airline confirmed that “hostile elements” attempted to take over the communication network of an El Al plane from Phuket, Thailand to Ben-Gurion Airport.
In the past week, hackers targeted two El Al flights bound for Israel, attempting to hijack their communication networks and divert the aircraft, as reported by The Jerusalem Post. The flights were en route from Thailand to Israel’s Ben Gurion Airport. It is worth noting that no group has claimed responsibility for this hack.
In the most recent incident, Israel’s national airline confirmed that “hostile elements” attempted to take over the communication network of an El Al plane from Phuket, Thailand to Ben-Gurion Airport, causing it to divert from its destination. Hostile elements contacted pilots twice, once on a flight between Phuket and Ben-Gurion and once on a Bangkok flight.
The aircraft was reportedly flying over an area inhabited by Iranian-backed Houthis. Sources claim the hack may be the work of a Somaliland-based group. For your information, Somaliland is a state in the Horn of Africa.
El Al pilots became suspicious and decided to ignore the sudden change in instructions and switched to another communication channel to double-check their route with air traffic controllers. The airline confirmed that pilots are trained to spot and mitigate threats while in the air. According to the airline, the disruption did not affect the normal course of the flight due to the professionalism of the pilots.
Attempted attack on the communications network of an Israeli flight from Phuket, Thailand
Hostile elements tried “to manipulate the crew, the pilots, into changing the trajectory and diverting the flight to what would have been a hostile area,” @guyaz explains
With @benitalevin pic.twitter.com/kJhedqzwbJ
— i24NEWS English (@i24NEWS_EN) February 18, 2024
“The disruption did not affect the normal course of the flight thanks to the professionalism of the pilots who used the alternative means of communication and allowed the flight to continue on the planned route,” the airline’s statement read.
Aircraft safety should be a point of concern within the cybersecurity fraternity given the growing number of incidents targeting airlines. In September 2022, researchers at Necrum Security Labs discovered two critical vulnerabilities in Contec’s wireless LAN devices, specifically the Flexlan FXA3000 and FXA2000 series, which provide WiFi on airplanes.
The Japan-based Flexlan LAN devices in airplanes contained two critical vulnerabilities, CVE–2022–36158 and CVE–2022–36159, allowing hackers to hack the inflight entertainment system and other high-speed internet access points.
Then in January 2024, Pen Test Partners’ cybersecurity researchers identified a critical issue in Airbus’ Flysmart+ Manager suite, which was remediated 19 months after initial disclosure.
The app, according to Pen Test Partners, developed by Airbus-owned IT services company NAVBLUE, had a disabled security control, allowing insecure communication with servers, potentially allowing an attacker to modify aircraft performance data or adjust airport information.
EASA, the EU’s aviation safety agency, recently released the first Easy Access Rules for Information Security to enforce security best practices across various sectors, including suppliers, airlines, airports, communication infrastructure providers, and air towers.
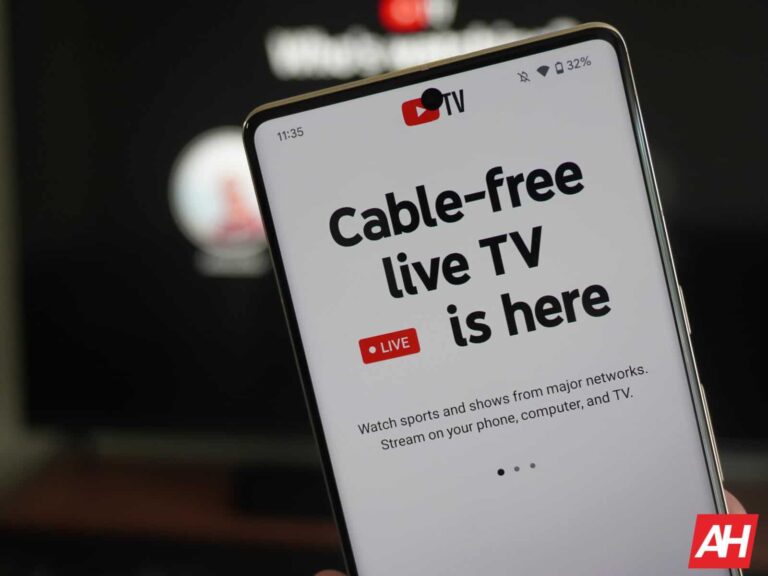
YouTube TV has been testing a feature called Last Channel Shortcut for a few months. This is a feature that allows you to access the last Channel you were watching quickly. Well, Last Channel Shortcut is rolling out to all YouTube TV subscribers.
This is a pretty small feature, but it’s very convenient. If you’re all on one channel, and you navigate to another one, you have to remember what channel you were on in order to navigate back. So, if you happen to forget, then you’ll have to do the work of searching for that channel again. It can get pretty annoying if you’re trying to swiftly navigate back to the channel you were watching before.
This is a simple feature that allows you to quickly go back to the channel you were just watching after switching. So, you won’t have to bother with trying to remember what channel you were watching last.
In order to make sure that you have this, be sure that your app is fully updated. Find YouTube TV on the Google Play Store, and see if you have the green Update button. If you don’t see it, then there’s a chance that you already have the update.
In the YouTube TV app, after you switch to another Channel or video, long press the OK/Select button on the remote. Then, you’ll be taken right back to the last Channel you were just on. It’s as simple as that.
If you don’t see the option, then you’ll probably want to wait a few days for this feature to eventually reach you. It’s currently rolling out, so there’s a chance that it just hasn’t made it to your device yet.
Still on the fence about getting YouTube TV? The service offers hundreds of channels for you to watch. The service costs $72.99/month. If you’re interested, click on the link below.
While technology has changed many aspects of life, the versatile, multi-functional Android device remains one that can serve them all.
Whether you’re a hardcore tech geek or just someone who wants the best phone model they can afford, Androids are for you. Plus, you can dress them up with plenty of accessories fit for every Android enthusiast’s purpose. Keep reading to find out what accessories we recommend for every Android owner!
To anyone who is constantly on the move, a portable charger is a must-have. Whether it is during long travels, a camping expedition, or a normal day you spend away from a power source, an awesome portable power bank will make sure your Android device never gives out on you when you need it most.
In particular, this gadget is a real must-have appliance for those who cannot afford to let their gadgets power off while enjoying their game. If you’re into your online games, particularly casino games, you never know how long a game could last. Some casino and slot games place more demands on a battery than other phone uses like messaging and calls, and you wouldn’t want your phone to run out just as you are about to place a bet in a crypto casino. If this is your story, then a power bank is the right device to get, because you are assured you will not run out of battery, and you can still play on with your game.
Mobile gaming just got more immersive! Get yourself a gaming controller that’s designed for Android devices which will support many of the most popular mobile games from action games to casual favourites.
A dedicated gaming controller offers precise controls and an enhanced gameplay experience. Choose a gaming controller with comfortable ergonomic design and custom buttons to make it easier to play along, and make sure that it fits your phone as many have specific spots for the phone to sit within while you play with your hands, so you don’t have to hold the phone or find somewhere for it to rest.
Cut the cord and enjoy wireless freedom with Bluetooth earbuds. Perfect for commuting, working out, or simply relaxing at home, Bluetooth earbuds offer a seamless audio solution that pairs effortlessly with your Android device. With superior sound quality and extended battery life, modern Bluetooth earbuds rival traditional wired headphones in every aspect.
Use your Android phone safely while driving with a car phone mount.
Your mobile makes a great alternative to a GPS navigator whilst you travel; use it with a hands-free setup while driving for road directions, to take safe phone calls on the move, or to use streaming music apps – with a phone mount that attaches to the dashboard of your vehicle or car air vent.
Boost the storage of your Android device with an external storage drive which is perfect for saving your photos, videos, music, documents, or anything you have on your device and gaining more space overall to keep your digital life well organized.
It is easy to use, simply plug and play files between your Android and external storage drive.
Give your Android smartphone more room to shine by adding another dimension: a smartwatch. Timepiece, fitness tracker, messages and calls, and a voice command to control your phone too. A smartwatch will take your Android experience to a level beyond your expectations! It makes your phone smarter than ever!
Say goodbye to tangled wires and hello to wireless charging with a wireless charging pad for your Android device. Simply place your phone on the pad and enjoy hassle-free charging without the need for cables. With a wireless charging pad, you can keep using your phone while it charges, making it a convenient addition to your tech setup.
Finally, turn your home into a smart home with compatible devices that easily pair with your Android device.
Whether you want to use your Google Smart Home products or smart bulbs to light up your home, these smart products can connect to your phone and can be accessed using voice control.
Be it the thermostat, the lights, or your music of choice, smart home devices make your lifestyle just the more convenient variety.
To sum up, these Android accessories are essential for any tech lover who wants to improve their experience with an Android device in terms of convenience, robotization, productivity, and entertainment at the same time.
We think that all of these items are essential and will make your life that little bit easier. From helping you enjoy your favorite games to creating a smart home full of intelligent products, these accessories will really improve your lifestyle.
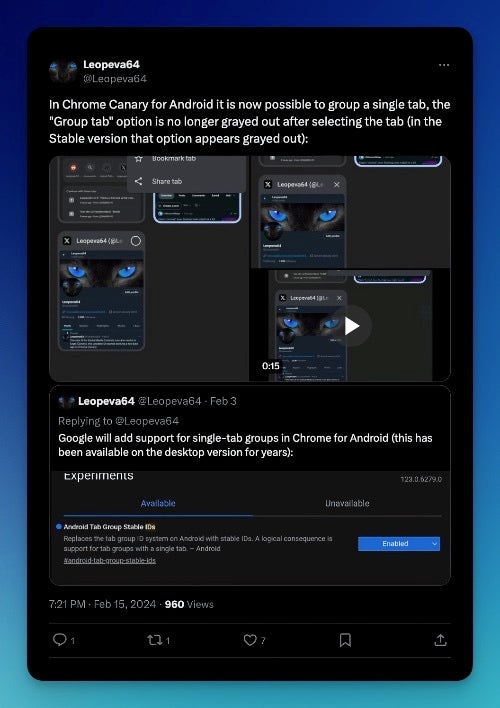
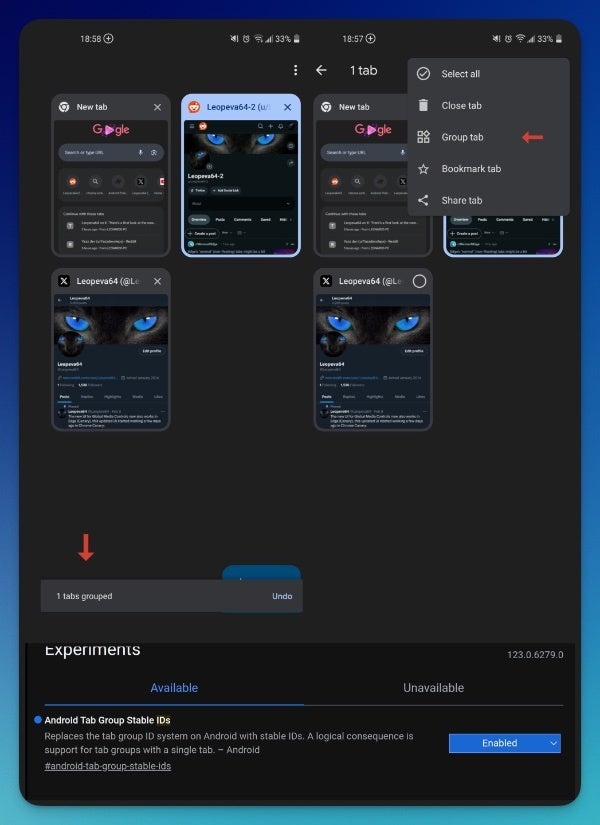
As documented in the above X post, the feature will work by tapping on the three-dot menu, choosing “Select tabs”, picking the tabs you’d like to group, then selecting “Group tabs.” From there, you’ll be able to add more tabs, rename the group, rearrange tabs within it, and use all the typical tab group features.
However, Chrome Canary is a very good way to get a glimpse at what Google is working on for its browser, however unpolished the experience may be. The fact that this setting has been available since earlier this year and it continues to be worked on, is a good sign that this will make it to the stable version in a few months.
Last week, Samsung rolled out its February 2024 update to the Galaxy S22 series and Galaxy A54 in Europe. The update has now reached other parts of the world, including the US. It brings the latest security patch with several dozen vulnerability fixes.
The February SMR (Security Maintenance Release) is currently rolling out to the carrier-locked variants of the Galaxy S22, Galaxy S22+, and Galaxy S22 Ultra in the US. The update comes with the firmware build number S90*USQS4DXB1. A wider rollout covering unlocked units should be on the horizon.
This update is also available in Canada with the build number S90xWVLS4DXB1. Samsung will gradually push it to all eligible Galaxy S22 units globally. The devices are getting 69 security fixes with the new SMR. These include three critical Android OS patches from Google. The update doesn’t bring anything more, so don’t expect new features or improvements.
It is the same pattern for the Galaxy A54 as well. Samsung is initially updating the carrier-locked variants of the 2023 premium mid-range handset in the US. The device is picking up the February update with firmware version A546USQS6BXB1, at least on some networks. It is A546VSQS6BXA8 for Verizon users. Samsung should roll out the update to all users soon.
Regardless of the build number, the changelog for the update remains the same. All Galaxy A54 users in the US are getting nothing more than the latest security fixes here. This is true for all Samsung devices globally this month. The Korean behemoth is preparing to push the One UI 6.1 feature update to eligible models. Its February release is all about security fixes.
One UI 6.1 is the latest version of Samsung’s custom Android skin. Based on Android 14, the new version debuted with the Galaxy S24 series last month. It brought a host of new AI features. The company has baked AI into the system. You find AI features in the camera, gallery, Samsung Notes, Samsung Keyboard, calling app, and more.
Samsung has already announced that One UI 6.1 will roll out to over 100 million Galaxy devices in the next few months. Along with all recent flagships, the company is also expected to update a few mid-range models. The Galaxy S22 series and Galaxy A54 are eligible for this update, though the availability of features may vary depending on compatibility. The rollout should begin in a few weeks.
Meizu seemingly quits the smartphone business, as the company plans to focus on AI. This news does not come as a shock, but it is still a bit surprising. I’ll explain why soon, but let’s first see what happened.
A well-known tipster, Roland Quandt, reported that Meizu said that the company is “All in on AI”. He also said that the meaning behind it is “no more phones from us”. The company is stopping production on “traditional phones”, it’s said.
To quote the company exactly: “Meizu has decided to go All in AI and will stop traditional “smartphone” projects”. The company will focus on the creation of “tomorrow’s devices” driven by AI.
As some of you may know, Meizu was acquired by Geely back in 2022. Geely is a Chinese car maker, for those of you who are out of the loop. Meizu did make some phones since then, but not a lot.
Considering that Meizu barely releases any phones every year, some sort of change was expected. Meizu’s CEO, Shen Ziyu, did note that smartphone consumers are now taking a longer time to upgrade their devices.
It seems like Meizu is canceling the development of its upcoming smartphone models, the Meizu 21 Pro, Meizu 22, and Meizu 23. Shen said that the move away from the smartphone business actually resonates with Meizu’s history.
Some of you may know that Meizu started off as an MP3 manufacturer. It did not start as a smartphone manufacturer. It did switch to the smartphone business at one point, and it did great… for a while. Many expected great things from Meizu, but things took the wrong turn.
Shen added that Meizu is fully ready to embrace AI. The company seems to be planning to launch a new mobile operating system tailored for the AI era. Some sort of an AI hardware product is also coming later this year.
Meizu does reassure its consumers that support existing products will remain live, so no worries there.
A Russian-linked actor, TAG-70, has targeted mail servers in Ukraine, Georgia, and Poland, aiming to collect intelligence on European political and military activities, particularly related to Ukraine’s war efforts.
Recorded Future’s Insikt Group has identified TAG-70, a potential threat actor allegedly working for Belarus and Russia, targeting government, military, and infrastructure entities across Europe and Central Asia since December 2020. The latest round of attacks was observed between October and December 2023.
The group is also known as Winter Vivern, TA-473, and UAC-0114. According to Insikt Group’s report (PDF), Tag-70 was discovered exploiting cross-site scripting (XSS) vulnerabilities in Roundcube webmail servers across Europe.
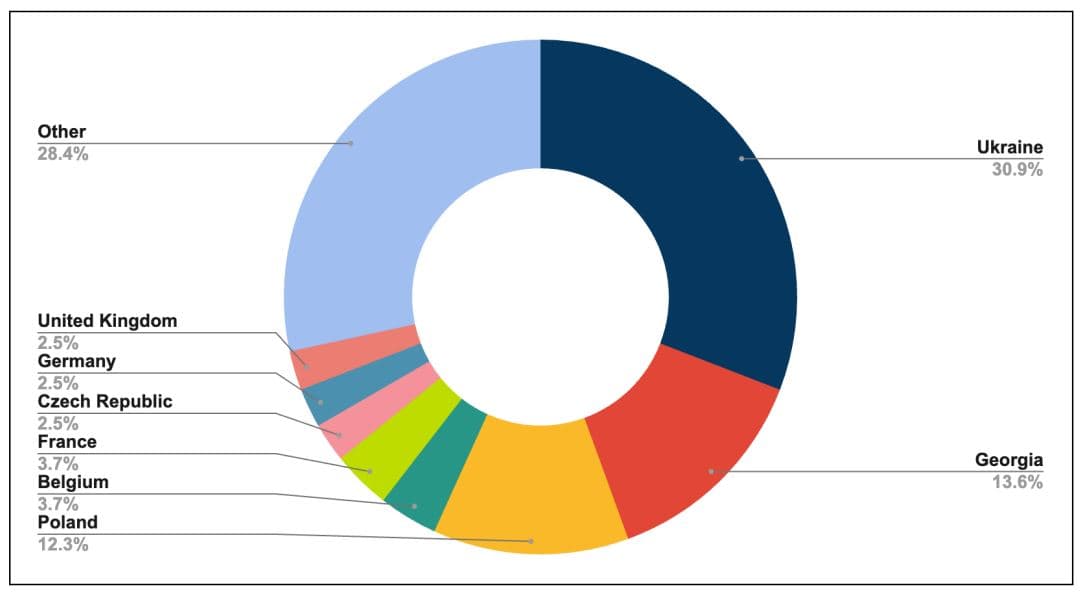
The group mainly targeted government, military, and national infrastructure in Georgia, Poland, and Ukraine whereas targets were also observed in Belgium, France, the Czech Republic, Germany, and the UK.
TAG-70, reportedly, used social engineering techniques to gain unauthorized access to mail servers across 80 organizations, including the Iranian Embassies in Moscow and the Netherlands, and the Georgia Embassy in Sweden.
The campaign aimed to gather intelligence on European political and military affairs, potentially gaining strategic advantages or undermining European security and alliances. Servers were primarily affected in Ukraine (30.9%), Georgia (13.6%), and Poland (12.3%)

This espionage attack uses spearphishing emails to deliver JavaScript payloads, exploiting the Roundcube vulnerability tracked as CVE-2023-563. Malicious code logs users out of Roundcube, presenting a new sign-in window.
The zero-day exploit allowed unauthorized access to mail servers across 80 organizations, including transport, education, chemical, and biological research sectors. The activity is similar to previous campaigns by other Russian-aligned threat groups like BlueDelta and Sandworm, which also targeted email solutions like Roundcube.
The compromised email servers pose a significant risk to Ukraine’s war effort, diplomatic relations, and coalition partners. Researchers warn that cyber-espionage groups targeting webmail software platforms, including Roundcube, may expose sensitive information about Ukraine’s defence efforts, partner countries, and third-party cooperation. They predict that these groups will continue targeting these platforms as Ukraine’s conflict continues and tensions with the EU and NATO rise.
Organizations must patch Roundcube installations, detect indicators of compromise (IoCs), and implement robust cybersecurity measures to mitigate the threat. Other effective security measures include strengthening email security, preferring encryption, secure email gateways, regular audits, employee awareness training, and network segmentation. The sophisticated attack methods and potential national security impact highlight the need for vigilance and awareness.
One part of the WhatsApp experience is being able to see other people’s status updates when you go to the Updates tab. This is pretty convenient, but people have had their gripes for a while. Well, WhatsApp is currently testing a new status update tray in the Android beta, and it’s going to make a lot of people happy.
Currently, this feature is being tested. This means that WhatsApp could very well take this feature away or change it. So, you’ll want to take this news with a grain of salt. There’s no 100% guarantee that that will launch this feature.
This feature was discovered in the WhatsApp beta for Android version 2.24.4.23. You can download this update if you are part of the Android beta version of the app. However, there’s a chance that you still won’t see it even if you get the update. WhatsApp is testing this on a limited number of users.
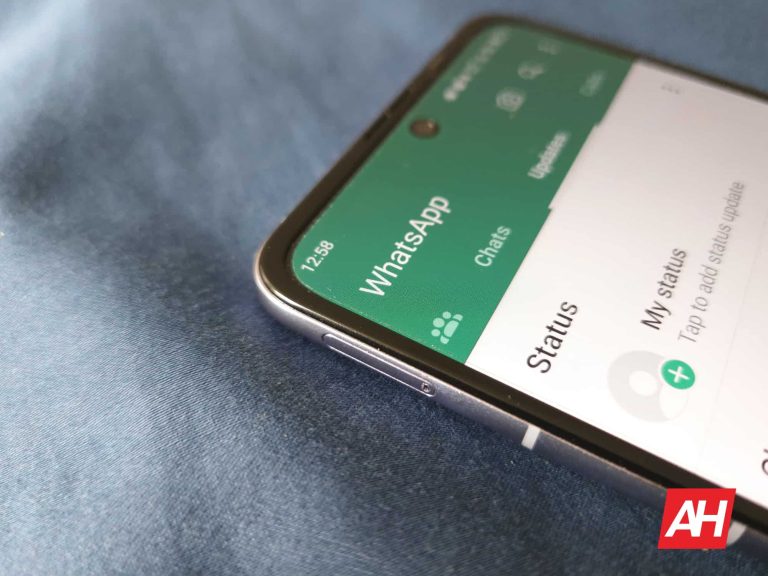
Currently, when you are on the update tab, you’ll see status updates from other users. In order to check the contents of the stories, you’ll have to tap on the user’s profile pictures. That’s not all too inconvenient, but it can be tedious if there are a lot of stories to go through. However, with this update, WhatsApp is testing the ability to get a quick preview of the stories before you tap on the icons.
Looking at this screenshot below, we see a large preview of a story. So, when you are scrolling through the available stories, you will see a preview of the first story posted for each person. This will allow you to see them and get an idea of what the person is posting. It will eliminate the need to tap on every person’s individual profile picture just to see the first story.
At this point, we have no idea when/if WhatsApp plans on releasing this feature to the public. Since it’s still in testing, it could be a while before we see this feature hit the surface. We’ll just have to be patient.
Two major flaws in open-source software could enable bad actors to break into password-protected home and enterprise WiFi networks. The vulnerabilities affecting WiFi networks were published in Top10VPN, with contributions from Mathy Vanhoef, a leading security researcher. The two flaws are separate, but together, open up many home and enterprise WiFi networks to attacks. Specifically, the security vulnerabilities allow for what are known as authentication bypass attacks. These would allow hackers to trick users into connecting to cloned versions of trusted networks, intercept their data, and join the real networks without a password.
The biggest flaw concerns wpa_supplicant v2.10 and lower, which is used by Android devices to connect to password-protected WiFi networks. Additionally, the researchers say that wpa_supplicant is also used to connect to WiFi networks in Linux and ChromeOS devices, so the vulnerabilities are far-reaching. According to the paper, this flaw will only affect devices that aren’t configured properly. However, the researchers add that many Android devices aren’t configured properly. They suspect that 2.3 billion Android users could be affected by this one security flaw.
The wpa_supplicant security issue only concerns enterprise networks (WPA2-E or WPA3-E), so home users need not worry. But considering how many businesses and schools use enterprise networks, it’s still an issue. The education sector seems particularly at risk since ChromeOS devices are extremely common there. Plus, students may be more likely to be duped by cloned WiFi networks, especially at younger ages. It’s also risky due to the fact that sensitive information is often secured by these enterprise networks.
The second vulnerability concerns the IWD software and affects home networks. However, it only puts Linux devices at risk, so not many users will be affected by this flaw.
These security issues have been reported. The wpa_supplicant bug is being tracked as CVE-2023-52160, and the IWD flaw is being tracked as CVE-2023-52161. Presumably, work is being done to patch these flaws immediately.
In fact, there are already some fixes for certain platforms. ChromeOS devices can be updated to version 118, which includes a fix for the wpa_supplicant bug. However, Android devices are still waiting for a fix, which will come in a subsequent Android security update. Until then, the researchers say that a CAT tool can be used to secure their devices. Linux users will need to wait for their preferred distro to release a patch for wpa_supplicant.