iOS Facebook, Instagram apps to charge Apple service fee for boosted posts

0
[ad_1]

Meta is about to implement a 30% fee for those who wish to boost (enhance) the visibility of their posts on the Facebook and Instagram iOS apps, a response to Apple’s 2022 App Store update that mandates a 30% cut from such digital transactions.

This charge targets ads or “boosted posts” designed to expand content reach, necessitating that boosts purchased on iOS be processed through Apple, thereby incurring the 30% service charge before taxes.

“The change, which goes into effect later this month, stems from a 2022 App Store update where Apple extended its typical 30 percent cut of digital purchases to boosted posts, which are essentially ads. The change particularly targeted Meta and other social apps that let people pay in-app to increase the reach of their content”, reads a report by The Verge and adds that Meta notes in a statement that small business owners and influencers who want to purchase a boost on iOS will now be billed through Apple, “which retains a 30% service charge on the total ad payment, before any applicable taxes.”Meta says purchasing boosts via Facebook and Instagram’s desktop or mobile websites is how to get around the Apple fee that is being passed on to iOS users. The alternative imposes significant constraints on iOS app users, who must now preload funds with an additional 30% fee to cover Apple’s transaction costs. This new payment method will debut in the US, with plans to expand to other markets later.

“We are required to either comply with Apple’s guidelines or remove boosted posts from our apps,” Meta says. “We do not want to remove the ability to boost posts, as this would hurt small businesses by making the feature less discoverable and potentially deprive them of a valuable way to promote their business.”

Meanwhile, Apple defends its policy, asserting that digital goods and services within apps must utilize In-App Purchase, including boosted posts.


[ad_2]
Source link
1000+ JetBrains TeamCity Instances Vulnerable to RCE Attacks

0
[ad_1]

A critical security vulnerability was detected in TeamCity On-Premises, tagged as CVE-2024-23917, with a CVSS score of 9.8.

An unauthenticated attacker with HTTP(S) access to a TeamCity server may bypass authentication procedures and take administrative control of that TeamCity server if the vulnerability is exploited.

TeamCity is a building management and continuous integration server developed by JetBrains that can be installed on-premises or used as a cloud service.

Document
Live Account Takeover Attack Simulation

Live attack simulation Webinar demonstrates various ways in which account takeover can happen and practices to protect your websites and APIs against ATO attacks.

This attack, identified as an Authentication Bypass Using an Alternate Path or Channel vulnerability (CWE-288), carries a high risk of damage and exploitability. 

Remote code execution (RCE) attacks that do not require user input can exploit this vulnerability.

All TeamCity On-Premises versions from 2017.1 through 2023.11.2 are vulnerable.

TeamCity Cloud servers have already been patched and verified not to be compromised.

Instances Exposed to the Internet

Shadowserver has observed that 1052 vulnerable JetBrains TeamCity Instances were exposed to the Internet.

Most exposed instances are found in the US 332 instances & Germany 120 instances.

The issue has been patched in version 2023.11.3, and JetBrains has notified its customers.

“We strongly advise all TeamCity On-Premises users to update their servers to 2023.11.3 to eliminate the vulnerability,” JetBrains said.

If you are unable to update your server to version 2023.11.3, JetBrains has released a security patch plugin that allows you to continue patching your environment.

Security patch plugin: TeamCity 2018.2+ | TeamCity 2017.1, 2017.2, and 2018.1

“If your server is publicly accessible over the internet and you are unable to take one of the above mitigation steps immediately, we recommend temporarily making it inaccessible until mitigation actions have been completed,” the company said.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

New Samsung Galaxy Fit 3 leak leaves little to the imagination

0
[ad_1]

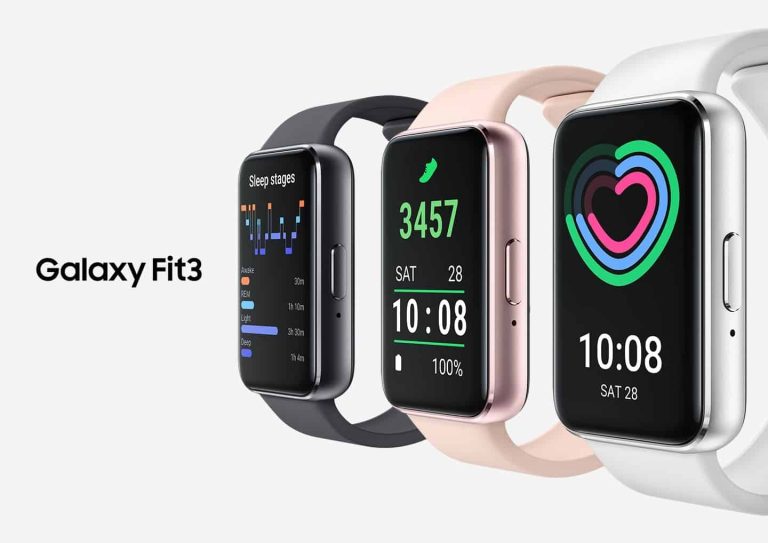
The Samsung Galaxy Fit 3 is one of the worst-kept secret products from the company to date. The wearable has already been the subject of several leaks ahead of the official launch. We already know the key specs and have seen many photos & a video of the fitness tracker. Now, a fresh leak has left nothing to the imagination.

The gadget tipster Roland Quandt has posted complete information and press images of the Fit 3 on the German website WinFuture.

Galaxy Fit 3 will be a basic fitness tracker dressed like a smartwatch

The Galaxy Fit 3 will be arriving as the successor to the Fit 2, which was introduced way back in 2020. While the Fit 2 features a square-shaped display, the Fit 3 will be sporting a bigger smartwatch-like screen. Essentially, the Fit 3 will be a basic fitness tracker that will be dressed like a smartwatch. Despite the low price tag, the new fitness-centric accessory from the brand will flaunt a housing made of aluminum.

Samsung Galaxy Fit 3 design colors

Furthermore, the source suggests that the Fit 3 will be sporting the 5ATM and IP68 certifications for dust and water resistance. Similar to its predecessor, the wearable will be available with a silicone strap in multiple color options.

Of course, the heart rate and SpO2 health sensors will be onboard the new Samsung fitness tracker in years. It will also have other fitness features like sleep monitoring, step counting, stress monitoring, and various workout modes. The Fit 3 will have all the key specs of the expensive Galaxy Watch devices but at an affordable price tag.

A large 1.6-inch AMOLED screen and up to 14 days of battery life

As per the source, the Galaxy Fit 3 will feature a 1.6-inch square-shaped display. The screen will have a resolution of 402×256 pixels and an AMOLED panel, which should be easy to read even outdoors. Software-wise, the device will boot a custom lightweight OS and will come with over 100 preloaded watch faces. The wearable is said to come with 16MB of RAM and 256MB of storage.

Samsung Galaxy Fit 3 white

The Galaxy Fit 3 will pair with the host device via Bluetooth 5.3. Unfortunately, it won’t be featuring support for GPS or NFC connectivity options. Lastly, the latest leak suggests that the fitness tracker will have a 208mAh battery under the helm. It is said to last for up to 14 days under regular use circumstances.

If the reports are to be believed, the Galaxy Fit 3 will be offered for around $75-$100. While the brand is yet to officially confirm, the wearable is expected to be launched by the end of this month. We will know more in the coming days, so stay tuned for regular updates.


[ad_2]
Source link
New Android & iOS malware that wants to steal your face

0
[ad_1]

A new malware has appeared on both Android and iOS, and it wants to steal your face for fraud purposes. The name of this malware is ‘GoldPickaxe’, and it uses a social engineering scheme to trick you into allowing it to scan your face.

New Android & iOS malware wants to steal your face

Once it does that, it uses the scan to generate deepfakes to get access to your bank account. It’s a part of a malware suit developed by the Chinese threat group known as ‘GoldFactory’. That group is behind ‘GoldDigger’, ‘GoldDiggerPlus’, and ‘GoldKefu’ malware.

‘GoldPickaxe’ was spotted by Group-IB, and the company says that the attacks mostly targeted the Asia-Pacific region. They did so on both Android and iOS, though. Thailand and Vietnam were the most targeted, but not the only two countries.

The fear is that this malware could spread like wildfire. The tactics it uses could easily be effective on a global scale. Users do need to allow for such face scans in order to be in danger, but not everyone is tech-savvy and many people would not recognize the threat.

‘GoldPickaxe’ distribution started in October 2023

The distribution of ‘GoldPickaxe’ allegedly started in October 2023. It’s simply a continuation of the three previous malware that we’ve mentioned. It works differently, but it has similar nefarious goals.

GoldPickaxe timeline

How does this malware work exactly? Well, users are approaches to phishing or smishing messages on the LINE app. They’re approached in their own language, and the messages represent themselves as government bodies.

Those messages are trying to get users to install specific apps, such as the ‘Digital Pension’ app. That app is not available via the Google Play Store, but the listing does impersonate the Google Play Store, that’s how users get tricked. That app then scans your face, and the problems begin.

Digital Pension fradulent app

Both Android & iOS users are in danger, but the approach is different

The process is a bit different for iOS users. It was first conducted via the malicious ‘TestFlight’ app, but then Apple removed that app. From that point on, the attackers switched to a malicious Mobile Device Management (MDM) profile, as they are trying to lure people into installing it.

MDM Profile GoldPickaxe

As per usual, please be careful what apps you download, and from where. Don’t let unknown apps scan your face, and be sure you get apps from official stores. Don’t believe fraudulent messages from instant messaging services, and so on. You can never be too careful.


[ad_2]
Source link
Apple readies AI tool to help you code iOS apps, while Google presents turbocharged Gemini 1.5

0
[ad_1]

Welcome to today’s obligatory, inevitable, inescapable Two Minute AI. Just joking – that’s far from the last time you’ll be hearing about AI today (or on any given day in the near future).

Apple, which is way behind the rest of the gang in the AI race, is reportedly set to introduce an artificial intelligence tool designed to assist in software development by auto-completing lines of code, akin to Microsoft’s Copilot (via Reuters).

This feature is expected to be incorporated into Apple’s Xcode development software possibly within the year. Xcode is Apple’s IDE (Integrated Development Environment), designed for creating software on Mac for various Apple platforms, including iOS, iPadOS, macOS, tvOS, and watchOS.

While Xcode is provided free to developers, Apple imposes a $99 annual fee for app submissions to its app stores. Additionally, Apple is exploring further AI integrations, including automated creation of Apple Music playlists and business presentation slide decks, as well as an enhanced “Spotlight” search function capable of deeper app interactions.

What about Google?


Meanwhile, Google is not letting go of the plan to eclipse ChatGPT as the go-to AI solution. The search engine giant has just presented Gemini 1.5 Pro that’s said to be so much more powerful than the Gemini 1.0 Pro. The Gemini Pro is Google’s general-purpose AI model (via The Verge) and the new 1.5 Version bested Gemini 1.0 Pro on “87% of benchmark tests”.

On a side note: Sam Altman’s prodigy platform is not sitting idle. OpenAI seeks ways to pull the plug on Google and occupy its search engine throne, as we reported mere hours ago.

Back to the new Gemini 1.5 Pro: what got Google CEO Sundar Pichai and the rest of the team extremely excited was the updated model’s “enormous context window”. This means that the Gemini 1.5 Pro can handle “much larger queries”, meaning it can check much more information at once.

“That window is a whopping 1 million tokens, compared to 128,000 for OpenAI’s GPT-4 and 32,000 for the current Gemini Pro”, the report reads and continues, stating that 1 million tokens are equal to “about 10 or 11 hours of video, tens of thousands of lines of code”, as Sundar Pichai explained. The context window means you can ask the AI bot about all of that content at once.

Google’s CEO has another idea for the new model (it’s now available to developers and enterprise users ahead of a full consumer rollout coming soon) and imagines movie directors and producers who could upload their entire movie and ask Gemini what reviewers might say; he sees companies using Gemini to look over masses of financial records. “I view it as one of the bigger breakthroughs we have done”, he says.

We might feed the Gemini 1.5 Pro model news from the last 10 years and see if things really started going south after that Harambe gorilla killing in May 2016. It will be an interesting analysis!


[ad_2]
Source link

Ukrainian Pleads Guilty for Leading Zeus & IcedID Malware Attacks

0
[ad_1]

Vyacheslav Igorevich Penchukov, a 37-year-old resident of Donetsk, Ukraine, has pleaded guilty to his key role in developing and deploying the notorious Zeus and IcedID malware attacks. 

In 2022, he was apprehended in Switzerland and extradited to the United States in 2023.

These two malware gangs are notorious for their ability to infect thousands of computers and steal millions of dollars from their victims. 

This group has become infamous for its highly effective cyber attacks on prominent healthcare facilities, government entities, and various private sector enterprises.

Document
Live Account Takeover Attack Simulation

Live attack simulation Webinar demonstrates various ways in which account takeover can happen and practices to protect your websites and APIs against ATO attacks.

Roles in Zeus

In 2009, a member of the Zeus threat actor group named Vyacheslav compromised thousands of business computers. Once the computer was infected, they stole sensitive information such as bank account details, passwords, and personal identification numbers required for online banking.

Penchukov and his associates posed as victims’ employees and tricked banks into making unauthorized transfers from the victims’ accounts.

As a result of his actions, Penchukov was added to the FBI’s Cyber Most Wanted List. Despite this, he continued to collaborate with the IcedID malware operators.

Roles in IcedID

Vyacheslav was involved in working with IcedID between November 2018 and February 2021, a banking malware that surfaced in 2017. The malware is designed to extract sensitive personal information, including banking account credentials, from its victims. 

In addition to this, IcedID malware can install other malware and ransomware on the infected systems. One notable incident involving IcedID was the attack on Vermont Medical Center, which resulted in the crippling of more than 1,300 servers.

“Core to the FBI’s cyber strategy is our willingness to play the long game and take players off the field. Vyacheslav Penchukov was a prolific criminal for over a decade and his criminal activities caused millions in damages,” said Assistant Director Bryan Vorndran of the FBI’s Cyber Division.

Penchukov pleaded guilty to one count of conspiracy to commit a racketeer-influenced and corrupt organization (RICO) act offense for his leadership role in the “Zeus” enterprise. Penchukov (as Andreev) also pleaded guilty to one count of conspiracy to commit wire fraud for his leadership role in the IcedID malware group, reads DOJ press release.

The defendant’s sentencing is set for May 9th, with a potential maximum sentence of 20 years in prison for each charge.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Android Safe Browsing will protect you from malware & phishing

0
[ad_1]

Google is testing a new security feature for Android OS. Called Android Safe Browsing, it helps protect users from malware and phishing attempts. The feature alerts you to harmful links and websites within supported apps. Once rolled out, you will find all supported apps on a dedicated Settings page.

Android Safe Browsing will enhance your online security with malware alerts

Google offers a wide range of security features for Android devices and apps. Its Chrome browser comes with a built-in Safe Browsing tool that checks for potential security threats when loading a page. The firm recently announced efficiency improvements for the feature. It introduced a new mechanism that allows sites to load even while real-time safety checks are in progress, reducing the latency in page load.

It appears Google is simultaneously testing Android Safe Browsing. Noted Android expert Mishaal Rahman was tipped off about the new feature that recently started showing up on some Google Pixel and Samsung Galaxy phones. A screenshot shared by Rahman reveals that the tool will alert users to security threats like harmful links and webpages when browsing within supported apps.

“You might get an alert if you tap a link in your news app that would take you to a known phishing site,” Google explains. The feature has a dedicated Settings page where it lists all the supported apps. There is also a toggle to enable “live threat protection” for “more accurate threat detection.” This page is available under Settings > Security & privacy > More security & privacy on Pixel devices and Settings > Security & Privacy on Galaxy devices.

Android Safe Browsing screenshot

According to Rahman, Android Safe Browsing “likely lists which apps utilize the SafetyNet Safe Browsing API.” Part of Google Play Services, this library “lets apps determine whether a particular URL has been marked as a known threat by Google.” The company might share more details once it is ready to roll out the feature to everyone. Currently, it appears to be testing the tool among a small group of users.

A serve-side update should bring the feature to all Android devices

While Android Safe Browsing may be limited to Pixel and Galaxy devices during the testing phase, it should eventually roll out to all Android devices with GMS (Google Mobile Services). Google may enable the feature through a server-side update via Google Play Services. You can check for it under the Security & Privacy Settings menu on your Android device.


[ad_2]
Source link

Is Google bundling Google One and Nest Aware? Global price hike for Nest Aware on the horizon

0
[ad_1]

Google’s Nest Aware subscription for Nest cameras, offering access to video recording history, smart alerts, and additional features, appears to be integrating into the Google One service.

In version 3.13 of the Google Home app, 9to5Google discovered strings that hint at a potential combined Nest Aware/Google One offering. These findings come after the introduction of Google One AI Premium, providing access to Gemini Advanced (the tech giant’s most capable AI model).

 
“Video history and intelligent alerts” are highlighted as the primary benefits. The interpretation of the discovered strings suggests that Google One subscribers may receive the base Nest Aware plan, priced at $8 per month or $80 annually, offering 30 days of event-based video history.


Nest Aware Plus, providing 60 days of event history and up to 10 days of 24/7 video history, could potentially be offered as an “addon.” The current standalone cost for Nest Aware Plus is $15 per month or $150 annually.


The specific Google One plan that will include this perk is yet to be determined. It seems that AI Premium, priced at $19.99 and above, would be the most suitable option. The integration of Nest Aware could potentially enhance the value of the AI Premium plan. The $9.99 Premium plan with 2 TB might be considered too low in price for the addition of Nest Aware unless a price increase is on the horizon.

 
In Canada, Nest Aware Plus is rising from CA$16 to CA$20 per month and now carries an annual cost of CA$200, while the base plan is set at CA$10 per month or $100 annually. This adjustment will take effect on the next Nest Aware bill occurring on or after March 25, 2024.


[ad_2]
Source link

HONOR Magic6 RSR is the upcoming Porsche Design phone, as expected

0
[ad_1]

HONOR confirmed yesterday that a new Porsche Design smartphone is coming. That phone was said to accompany the Porsche Design HONOR Magic V2 RSR, the company’s premium foldable offering. We assumed that the Porsche Design HONOR Magic6 RSR is the upcoming device, and that was kind of confirmed.

The HONOR Magic6 RSR is the upcoming Porsche Design smartphone

HONOR still didn’t officially confirm it, but the device did get certified, as revealed by Huawei Central. It appeared on the MIIT certification in China. The certification reveals the Magic6 RSR device with a model number BAL-AN20.

HONOR Magic6 RSR MIIT certification

In China, the phone will support satellite connectivity and dual-SIM 5G connectivity as well. That’s what this certification reveals and nothing more, basically. The HONOR Magic6 RSR will basically be the HONOR Magic6 Pro with a different look on the back. That will almost certainly be the case. The same was the case with the Porsche Design HONOR Magic V2 RSR.

The design of the phone did surface in the past, as you can see in the image below. From the front, it looks basically the same as the HONOR Magic6 Pro. From the back, not so much. It has a different-looking camera island, and a different backplate too.

HONOR Magic6 Porsche Design possible design 1

HONOR will likely use vegan leather on the back, and change up the back-facing design

Vegan leather seems to have been used here, as on some other HONOR Magic6 Pro models, but the shape is different. There’s a vertical protrusion in the middle of the phone’s backplate, which makes for an interesting look, and will probably help with grip too.

In regards to the camera island, it has an entirely different shape, not to mention it’s curved on the sides. We’re still not sure this design is the real deal, but it’s possible it is, we’ll have to wait and see.

The HONOR Magic6 Pro has already launched in China, while its global variant will drop at MWC 2024 later this month. It’s expected to be basically the same phone as in China, but without some China-focused features, and with global software.


[ad_2]
Source link

YouTube TV starts rolling out Last Channel Shortcut to all subscribers

0
[ad_1]

YouTube TV has been testing a new feature called “Last Channel Shortcut,” which allows users to switch between channels with ease, for a few months now. The feature was gradually rolled out to various platforms like mobile and Roku devices.

Today, the streaming service announced that Last Channel Shortcut is rolling out to everyone. To take advantage of the new functionality, you’ll need to long-press the Select/OK button on the remote to switch to a channel/video that you were previously watching. Here is a step-by-step guide posted by YouTube TV on reddit:

  • Open the YouTube TV app on your TV
  • Play any video
  • Choose and play another video
  • Long-press (press-and-hold) the OK/Select button on your remote while watching the second video
  • You’ll be taken back to the last channel or video that you were watching

It’s important to mention that the new Last Channel Shortcut feature should work across all content types, including Live, DVR, and VOD. If you’re subscribed to YouTube TV, you should be seeing the new feature already. Hopefully, this won’t be temporarily removed like the “1080p enhanced” feature, which is no longer available after issues have been found.

[ad_2]
Source link