Remote Monitoring & Management software used in phishing attacks

0
[ad_1]

Remote Monitoring & Management (RMM) software, including popular tools like AnyDesk, Atera, and Splashtop, are invaluable for IT administrators today, streamlining tasks and ensuring network integrity from afar. However, these same tools have caught the eye of cybercriminals, who exploit them to infiltrate company networks and pilfer sensitive data.

The modus operandi of these threat actors involves deceiving employees through sophisticated scams and deceptive online advertisements. Unsuspecting employees, misled by these tactics, may inadvertently invite these criminals into their systems. By convincing employees to download and run these seemingly benign RMM applications under the guise of fixing non-existent issues, these fraudsters gain unfettered access to the company’s network.

In this post, we explore a particular phishing scam targeting corporate users via the AnyDesk remote software and how ThreatDown can prevent the misuse of such programs by cybercriminals.

Phishing site hosts remote software

We believe victims are first targeted and then contacted via phishing emails or text messages (smishing) based on their position in the company.

Attackers could trick them by sending them to a typical phishing page or making them download malware, all of which are good options. However, they are instead playing the long game where they can interact with their victims.

Users are directed to newly registered websites that mimic their financial institution. In order to get support, they need to download remote desktop software disguised as a ‘live chat application’.
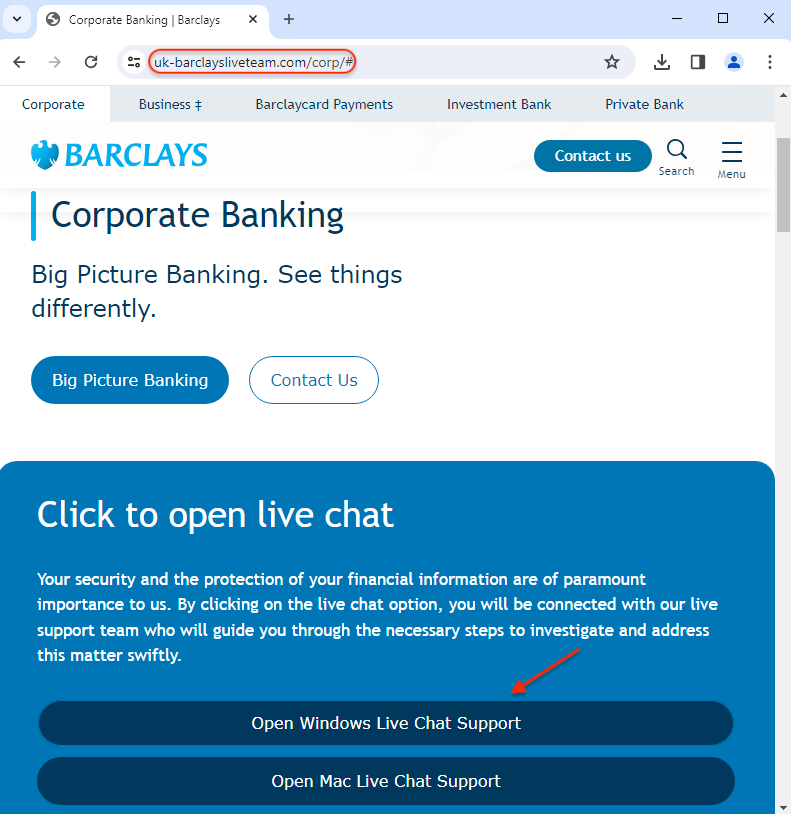
uk-barclaysliveteam[.]com/corp/AnyDesk.exe
uk-barclaysliveteam[.]com/corp/anydesk.dmg

It’s interesting to note that the downloaded software is not malware. For example, in this instance they are using a legitimate (although outdated) AnyDesk executable which would not be detected as malicious by security products.
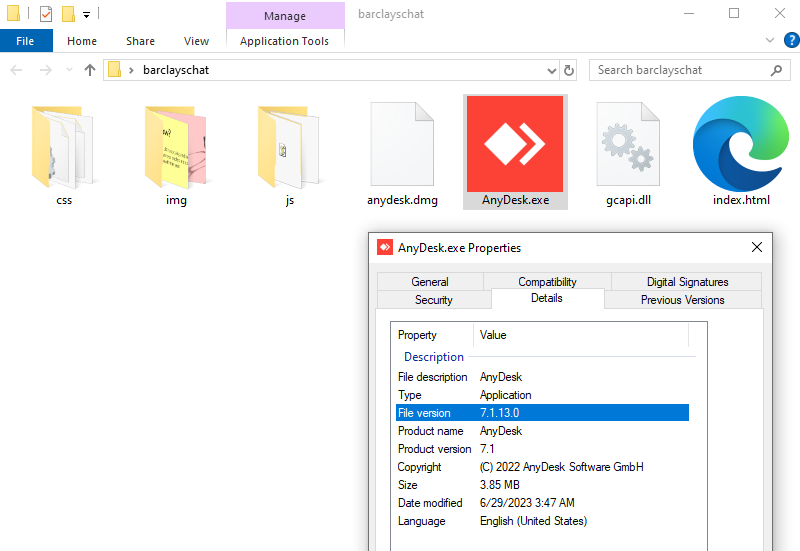
Running the program will show a code that you can give to the person trying to assist you. This can allow an attacker to gain control of the machine and perform actions that look like they came directly from the user.
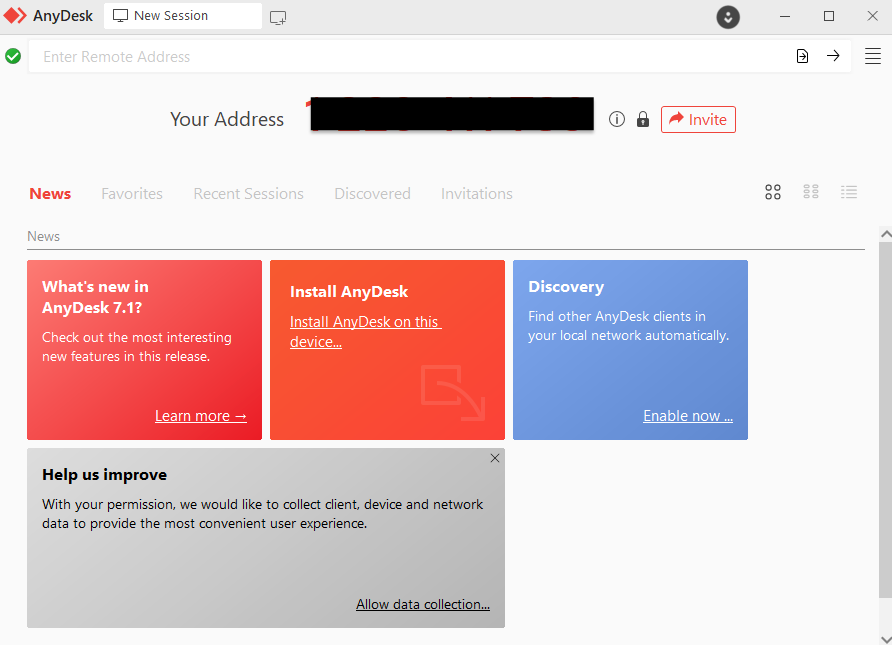
This is one reason why certain banking sites try to can detect if a customer is currently running a remote program, before allowing them to login. However, not all banks have this feature and there are certain cases where threat actors can evade such detection.

There are a number of RMM tools on the market which scammers and criminals will leverage. Ironically, the more popular and simple ones also tend to be the most abused.

AnyDesk recently got in the news for a security breach that allowed the attackers to compromise their production systems. The vendor has since revoked its code signing certificates and is urging customers to update their software.

RMM vendors are aware of the illicit use of their software and regularly remind users about common safety tips. AnyDesk also partnered with fraud fighters such as ScammerPayback to shut down call centers.

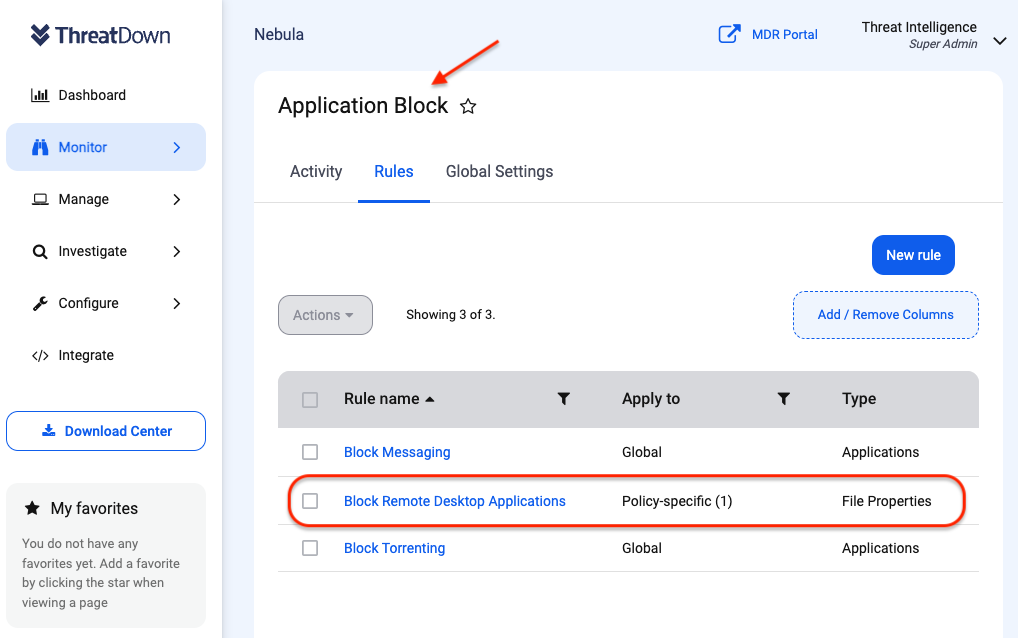
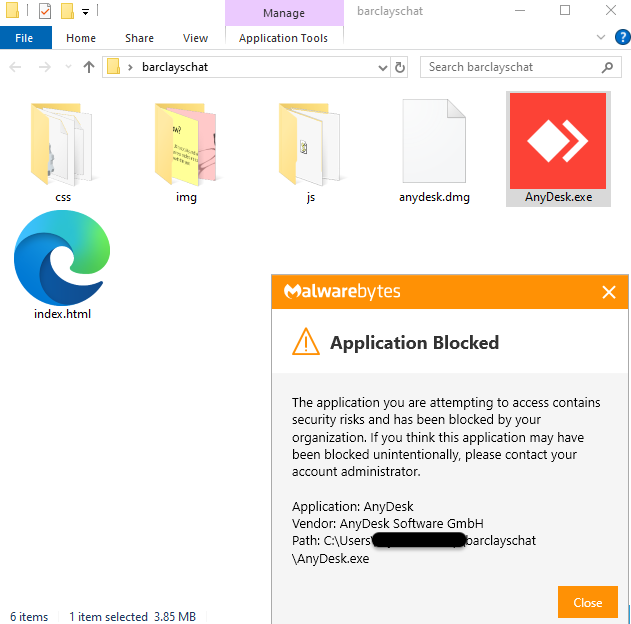
Free with every ThreatDown Bundle, Application Block can easily protect organizations against the rising trend of legitimate RMM tools being exploited. Organizations can block RMM tools via Application Block by:

  • Navigating to the ‘Monitor’ section within their Nebula console.
  • Selecting ‘Application Block’
  • Enabling the ‘Block RMM’ toggle switch provided by ThreatDown or customizing the list to fit their specific needs.

Saving the configuration to immediately block these RMM tools network-wide.

Adopt a robust defense stance by blocking all unnecessary applications, and for those you must use, the EDR/MDR layers of our ThreatDown Bundles will provide an additional safety net in the event of an infection.
Try ThreatDown bundles today

For IT teams plagued by the triad of complex deployment, scattered tooling, and excessive alert noise, ThreatDown bundles emerge as a superior solution that caters to the needs of today’s security teams.

Discover the difference with ThreatDown Bundles and elevate your organization’s defense against cyber threats. Get in touch for a free trial and experience the benefits of a simplified, yet robust, security framework.

Experience ThreatDown Bundles


[ad_2]
Source link

Google just leaked when the Android 15 Developer Preview is coming

0
[ad_1]

It’s February, which means the first developer preview for the new version of Android should be coming any day now. And thanks to a comment posted on the Android Open Source Project, we know precisely when it’s coming.

According to the comment, the first developer preview is scheduled for February 15. That would be this Thursday. Now, typically, Google releases developer previews and betas on the second Wednesday of the month. So, it could actually be coming on February 14, but either way, it looks like this is the week.

The developer on AOSP mentions “Android V,” which is the internal dessert-themed codename for Android 15. That’s Vanilla Ice Cream. It’s unfortunate that Google did away with the dessert names publicly; we really miss those statues for each version of Android.

Android 15 Developer Preview will likely only be available to Pixels

Typically, the first few developer previews are only available on Google Pixel devices. We are expecting the Pixel 5a to lose support for software updates this year. This means that the Pixel 6 and newer will likely get Android 15, and that includes the developer preview, according to Google’s own update schedule. The Pixel 5a is scheduled to stop receiving updates in August 2024, and Android 15 is likely coming in September or possibly October.

The developer preview will be our first authentic look at what Google has been cooking up for Android 15. However, it is essential to note that a lot of the new features will be saved for the first or second beta, which is typically announced at Google I/O in May. In recent years, new versions of Android have been pretty scarce on new user-facing features, with most of those being saved for the feature drops that come about every three months. The recent Android updates have mainly been under-the-hood changes. But we could be in for a surprise this year with Android 15.

It’s hard to believe that Google is already on Android 15; it seems like just yesterday, we were getting updates to Android 4.1 Jelly Bean. Time sure does fly.


[ad_2]
Source link

Eventually, ChatGPT will remember details about you

0
[ad_1]

Don’t you just love reiterating yourself every time you start a conversation with the chatbot? Neither does anyone else. This is the reason why OpenAI is working on a memory feature for a ChatGPT. This will allow the chatbot to remember some information about you so you don’t have to constantly repeat yourself.

The company already has a feature similar to this called Custom Instructions. This basically allows you to train ChatGPT on certain aspects of what you do and what you’re using it for. Then, when you start new conversations, it will already understand the context of what you’re talking about. So, if this is something that you would like, this feature is available already.

OpenAI is working on giving ChatGPT a memory feature

The company’s currently rolling this feature out, so people may start seeing it rather soon. Basically, ChatGPT will gain a memory so that it can remember certain things about you. This is so that people using ChatGPT won’t have to constantly repeat themselves. If you use ChatGPT for health reasons, and you have a specific type of diet, well, you won’t have to constantly remind it of your diet. The chatbot will be able to remember this information about you so that when you want to speak to it again about health, it’ll already know what you can and can’t eat.

However, it’ll actually use memory in two different ways. Firstly, you’ll be able to tell ChatGPT what you want it to remember. This gives you control over what information the chatbot retains about you. So, if you are using ChatGPT for health reasons, and you only want it to remember that you don’t like carrots, then it will only retain that information.

The second way is where ChatGPT will remember certain aspects about you at its own discretion. It will cherry-pick different facts about you to retain. So, if you’re having a conversation with ChatGPT about health, and you mention that you are allergic to shellfish, then it will choose to remember that, as it is a pretty important fact.

Obviously, this raises some red flags

Having ChatGPT remember certain aspects about you seems like a great idea if you use it constantly. You can imagine it being like speaking with a best friend who gets to know you.

However, this definitely raises some flags. Firstly, not many people are comfortable with an AI learning and retaining information about them. No one knows where that information goes. We’ve seen instances where chat conversations were leaked to other users. So, that’s something to keep an eye on.


[ad_2]
Source link

Ivanti VPN Flaws Exploited by DSLog Backdoor and Crypto Miners

0
[ad_1]

Ivanti has released patches for vulnerabilities found in its enterprise VPN appliances, including two flagged as exploited zero-days in early January 2024.

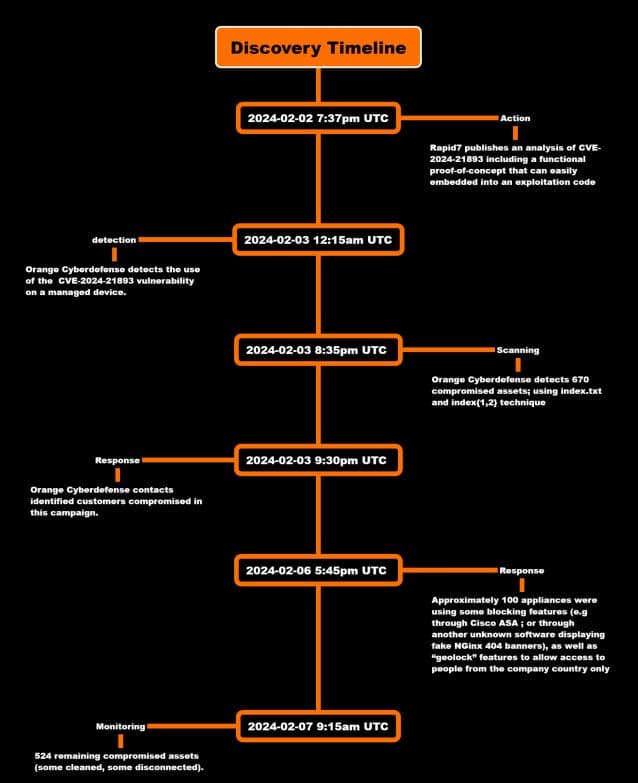
On January 31, 2024, Ivanti released fixes to address four vulnerabilities, including CVE-2023-46805, CVE-2024-21887, CVE-2024-21888, and CVE-2024-21893. The last two vulnerabilities were disclosed the same day when the patch was released, along with a second set of mitigations as substitutes for the fixes. Within hours, Orange Cyberdefense CERT identified attacks targeting this vulnerability, allowing attackers to inject a backdoor into the Ivanti application.

In its report (PDF), Orange Cyberdefense noted discovering attackers exploiting the vulnerability to ensure persistent remote access. They injected a backdoor into a component using the SAML vulnerability, controlling access to the backdoor. Orange identified a compromised appliance on 3 February 2024, with initial mitigations applied but no patch. The attackers conducted reconnaissance to determine root access and deployed a new backdoor, DSLog, indicating they had root access to the device.

A backdoor on a compromised device enables attackers to execute commands and log all web requests, including authenticated ones, and system logs. Orange identified 700 compromised appliances, with over a hundred compromised in attacks targeting CVE-2023-46805 and CVE-2024-21887. The remaining ones had initial XML mitigation applied, preventing direct detection. The backdoor uses a unique hash per appliance.

Ivanti VPN Flaws Exploited by DSLog Backdoor and Crypto Miners
Timeline shared by Orange Cyberdefense

Hackread has been following the exploitation of zero-day vulnerabilities in Ivanti VPN devices. Hackers have exploited them to deploy KrustyLoader malware and cryptocurrency miners. For your information, CVE-2023-46805 and CVE-2024-21887 were found in Ivanti Connect Secure (ICS) and Ivanti Policy Secure Gateway appliances.

CVE-2023-46805, an Authentication Bypass flaw, allows remote attackers to bypass control checks, while CVE-2024-21887 is a Command Injection flaw that lets an authenticated administrator exploit Ivanti appliances by sending crafted requests and executing arbitrary commands. CVE-2024-21888 is a Privilege Escalation vulnerability in Ivanti Connect Secure and Ivanti Policy Secure, allowing a user to gain administrative privileges.

CVE-2024-21893 is a server-side request forgery bug in the SAML component of Ivanti Connect Secure, Policy Secure, and Neurons for ZTA. The issue could be exploited without authentication to leak sensitive information. In its latest advisory, Ivanti noted that a “limited” number of customers were affected by CVE-2024-21893.

The findings were also shared by Shadowserver Foundation, which reported in early February that a zero-day vulnerability, CVE-2024-21893, discovered by Ivanti in January 2024, is being exploited in the wild. Rapid7 reported a surge in attacks since February, with over 170 discrete IP addresses involved.

Organizations are advised to install Ivanti’s patches released on January 31 and February 1, which replace initial mitigations prevent zero-day exploitation, and factory reset their devices. Additionally, they should install security updates released on February 8 to address a vulnerability in the SAML component of VPN appliances, tracked as CVE-2024-22024.

  1. Critical Flaws Found in GNU C Library, Major Linux Distros at Risk
  2. Excessive Expansion Flaws Leave Jenkins Servers Open to Attacks
  3. Critical “PixieFail” Flaws Expose Millions of Devices to Cyberattacks
  4. TeamViewer Exploited to Obtain Remote Access, Deploy Ransomware
  5. Windows Defender SmartScreen Flaw Exploited with Phemedrone Stealer

[ad_2]
Source link

The EU takes it easy on Apple and Microsoft in new Tech Crackdown

0
[ad_1]

Apple’s iMessage and Microsoft’s Bing escaped the scrutiny of the European Union’s new Digital Markets Act by the skin of their teeth. The investigation by the regulator found that both platforms do not hold a dominant enough position to be brought under the DMA’s strict rules for services provided by big tech’s “gatekeepers,” which include Apple, Meta, Google, Amazon, and TikTok.

Of course, Apple and Microsoft both said that they welcomed the decision. Neither one wants to be forced to be interoperable with their competitors, especially Apple.

The Digital Markets Act, or DMA, has already forced big changes for Apple. Including forcing the iPhone to switch to USB-C last year, bringing sideloading to iOS 17.4, and allowing browsers to use different engines for the iPhone. Which is going to allow browsers like Edge, Chrome, and Firefox to be more than just a Safari skin. The interoperability rules would have meant that Meta apps like WhatsApp could request to interoperate with Apple’s iMessage framework.

Does this mean Apple might backtrack on RCS support?

Late last year, Apple announced that it was going to add support for the universal profile of RCS on iMessage starting in late 2024. This decision was made based on the European Union and the new Digital Markets Act, where it was going to be forced to be interoperable. But now that this investigation has finished, and iMessage doesn’t fall under the “gatekeepers,” does that mean Apple might backtrack?

It’s possible that they might. Apple sees iMessage as a big part of the walled garden for keeping its users on the iPhone instead of jumping ship over to Android. But at this point, Apple has already been working on bringing RCS over, so they could stick with the original plan. We do expect to see it launch as part of iOS 18, which should launch in June at WWDC.


[ad_2]
Source link

It looks like Google wants you to access Gemini from your headphones

0
[ad_1]

The writing has been on the wall for Google Assistant for a bit, and Google seems to have added a few more paragraphs to it. Recently, the company unveiled the Gemini app, which has assistant capabilities. Now, it appears that Google is working on a way to have your headphones access the Gemini app.

Right now, you can use Gemini as a voice assistant on your Android phone. When you set the default voice assistant to Gemini, you’ll be able to access it by using the swipe-up gesture on your phone. Then, all you have to do is speak into the phone’s microphone, and you will get an answer. Previously, you would have to press the Send button to deliver your query. However, Google changed that in an update.

So, it appears that Google is working on replacing the Google Assistant with Gemini at some point in the near future. We have no idea when that’s going to happen, but it may happen sooner than later.

Google is working on letting headphones use the Gemini app

You’re definitely going to want to take this news cautiously. This was discovered by an APK deep-dive done by 9To5Google. As such, there’s no telling if Google is going to unveil this feature. Strings of code were discovered in the latest version of the Google app (version 15.6), and the strings allude to this feature. However, since his future was not officially announced, Google could make changes or take it away altogether.

Basically what the strings are appointed to is the ability for headphones to summon Gemini just like they would summon Google Assistant. When they summon the Gemini app, users will be able to speak into the headphones’ microphones and use it just like an assistant. So, if you have a question about a certain topic, you can simply access Gemini through your headphones, and Gemini will give you a spoken response.

However, one thing noted by 9To5Google is the fact that Gemini’s responses can tend to be pretty long depending on what was asked. Via text, you can simply skim through the response and glean whatever information you want. However, if the answer is spoken, then long answers could be a bit annoying. So, hopefully, Google comes up with a way to make the responses more succinct.

There were additional error messages in the code

Along with the code, the folks at 9to5Google also discovered a few error messages within the code. These are messages that will pop up in the case of something happening.

The first message reads “Too many requests in a short time period. Try again later.” The second one reads “Gemini mobile app is getting far more traffic than usual and is temporarily unavailable. Try again later.”

Right now, we’re not entirely sure if Google expects to deliver these error messages often or if the company is just covering its bases. In any case, it’ll be interesting to see if Google actually releases this feature. It seems likely, as the company seems to be looking to replace the Google Assistant at some point. It seems like the logical next step in Google’s overarching AI plan.


[ad_2]
Source link

TheTruthSpy stalkerware, still insecure, still leaking data

0
[ad_1]

In 2022, we published an article about how photographs of children taken by a stalkerware app were found exposed on the internet because of poor cybersecurity practices by the app vendor.

The stalkerware app involved, TheTruthSpy, has shown once again that the way in which it handles captured data shows no respect to its customers. And even less for the victims it’s monitoring.

TheTruthSpy markets itself as a tool that can be placed in the hands of employers who want to keep tabs on employees in the workplace, or in the hands of parents who want to look after their kids. But it can just as easily be placed in the hands of stalkers, abusive partners, or someone who just wants to get a leg up in their divorce proceedings.

Stalkerware like TheTruthSpy typically gets installed secretly, by a person with access to the victim’s phone. For that reason, by design, the apps stay hidden from the device owner, while giving the attacker complete access.

Boasting “more than 15 spying features,” it can track a target’s location; reveal their browser history; record their calls; read their SMS messages; spy on their WhatsApp, Facebook, SnapChat and Viber messages; log what they type; and record what they say.

That alone is bad enough, but the app seems to have a persistent problem with security. In 2022, tech publication TechCrunch discovered that TheTruthSpy and other spyware apps share a common Insecure Direct Object Reference (IDOR) vulnerability, CVE-2022-0732. It describes the bug as “extremely easy to exploit, and grants unfettered remote access to all of the data collected from a victim’s Android device.”

The bug was never fixed, and yesterday Stalkerware researcher maia arson crimew, revealed that it was stumbled upon again by two different hacking groups.

When members of the two hacking groups looked into TruthSpy last december while searching for stalkerware to hack, they independently stumbled upon the same IDOR vulnerability

The good news is that both groups, SiegedSec and ByteMeCrew, said in a Telegram post that they are not publicly releasing the breached data, given its highly sensitive nature. They provided enough data to enable TechCrunch to verify that it is authentic though, by matching IMEI numbers (numbers that uniquely identify phones) and advertising IDs against a list of previous known-to-be compromised devices.

Which means that by installing TheTruthSpy—and a whole fleet of clone apps including Copy9, MxSpy, iSpyoo, SecondClone, TheSpyApp, ExactSpy, FoneTracker and GuestSpy—you are not just spying on someone, you are also potentially exposing their data for anyone to find.

The data reportedly shows that TheTruthSpy continues to actively spy on large clusters of victims across Europe, India, Indonesia, the United States, the United Kingdom and elsewhere.

Sadly, this is no surprise. According to 2023 research from Malwarebytes, 62 percent of people in the United States and Canada admitted to monitoring their romantic partners online in one form or another, from looking through a spouse’s or significant other’s text messages, to tracking their location, to rifling through their search history, to even installing monitoring software onto their devices.

Removing stalkerware

If you want to know if your phone is or was infected with TheTruthSpy’s stalkerware you can use the lookup tool provided by TechCrunch, which has been updated to include information about the most recent leak.

Malwarebytes, as one of the founding members of the Coalition Against Stalkerware makes it a priority to detect and remove stalkerware from your device. It is good to keep in mind however that by removing the stalkerware you will alert the person spying on you that you know the app is there.

Because the apps install under a different name and hide themselves from the user, it can be hard to find and remove them. That is where Malwarebytes for Android can help you.

  1. Open Malwarebytes for Android.
  2. Open the app’s dashboard
  3. Tap Scan now
  4. It may take a few minutes to scan your device.

 If malware is detected you can act on it in the following ways:

  • Uninstall. The threat will be deleted from your device.
  • Ignore Always. The file detection will be added to the Allow List, and excluded from future scans. Legitimate files are sometimes detected as malware. We recommend reviewing scan results and adding files to Ignore Always that you know are safe and want to keep.
  • Ignore Once: A file has been detected as a threat, but you are not sure whether to add it to your Allow List or delete. This option will ignore the detection this time only. It will be detected as malware on your next scan.

We don’t just report on phone security—we provide it

Cybersecurity risks should never spread beyond a headline. Keep threats off your iOS devices by downloading Malwarebytes for iOS today.


[ad_2]
Source link

Galaxy S23, Fold 5 & Flip 5 receive February 2024 update globally

0
[ad_1]

A few days back, Samsung started pushing the February 2024 Android security patch to the Galaxy S23 series and the latest Galaxy foldables, i.e., the Galaxy Z Fold 5 and Galaxy Z Flip 5. The initial rollout only covered the devices in the US. The company has now brought the update to international markets. The latest security patch is also rolling out to the Galaxy M34 and Galaxy F34.

Samsung’s February update is available globally for the Galaxy S23

Samsung’s February SMR (Security Maintenance Release) for the Galaxy S23 series is available globally. The 2023 flagship lineup is receiving the update with the firmware build number S911BXXS3BXAD in Asia, Africa, Europe, and other regions. Users in the remaining few markets should also get the update soon. Don’t expect additional goodies, though. Samsung is only pushing the latest security fixes to the devices.

The story is largely unchanged for the Galaxy Z Fold 5 and Galaxy Z Flip 5. The February 2024 update for the foldable duo doesn’t seem to be available as widely as the Galaxy S23 trio, but it is just a matter of time now. European Fold users, watch out for an OTA (over the air) update with the build number F946BXXS1BXBE in the coming days (it is F946NKSS1BXAD for users in South Korea).

As far as the Flip model is concerned, we can currently only confirm the availability of the February SMR for it in South Korea. The device is getting the update with firmware version F731NKSS1BXAF. Like the Galaxy S23 series and the Fold, the update doesn’t bring anything more than this month’s security patch. Samsung’s latest security update patches 69 vulnerabilities, at least three of which are critical fixes.

While the latest update for these devices may not contain any new features, a more interesting update is on the horizon. Samsung is expected to push One UI 6.1 with new AI features and improvements to the Galaxy S23 series, Galaxy Z Fold 5, Galaxy Z Flip 5, and more eligible models soon. We will let you know when the rollout begins. One UI 6.1 debuted with the Galaxy S24 series.

Galaxy M34 and Galaxy F34 are also getting the latest SMR

Alongside the 2023 flagship Galaxies, Samsung has also updated the Galaxy M34 and Galaxy F34 to the February SMR. These mid-range phones weren’t sold globally, with the latter limited to India and surrounding countries. The devices are picking up the new security update with build numbers M346BXXS3BXB1 and E346BXXS3BXB1, respectively. The Galaxy M34 and Galaxy F34 are unlikely to receive One UI 6.1.


[ad_2]
Source link

Apple Vision Pro must leap four generations to become mainstream

0
[ad_1]

As you may all know, the Cupertino giant has recently announced Apple Vision Pro, a revolutionary mixed-reality headset now sitting at the flagship tier. It has a steep price tag, unaffordable for many. Although the tech behemoth is already working on less expensive versions of Vision Pro, industry analysts think that it may take up to four generations for this device to gain popularity among the masses.

The current state of the Apple Vision Pro

The Apple Vision Pro, introduced earlier this month, has stood out from other VR headsets due to its seamless interface and navigation features. Even its high price tag of $3,499 has not stopped it from becoming widely famed as an ideal consumer commodity for the future. In his recent Power On newsletter, insider Mark Gurman states that Vision Pro needs significant improvements before it can enter people’s lives as a routine gadget. And that the Vision Pro team estimates four years’ worth of hardware, software, and ecosystem upgrades before that happens. 

In their first attempts at venturing into new product lines, generally speaking, Apple products have been marked with flaws, corrected in subsequent releases. The same holds true for Apple’s brand-new offering – Vision Pro. It remains unknown what exactly is going on in Apple’s R&D labs and what specific improvements they are considering. 

Improvements due for future Vision Products

Extending from the newsletter, WCCFTech suggests that Vision Pro’s shortcomings in weight and appearance are undergoing refinement. Among other problems, the heaviness of the Vision Pro is of great importance. It is challenging for extended use and more so during long working hours. Apple may need to address this issue STAT to get the right balance of comfort and practicality. 

Similarly, the battery life has significant room for improvement since the current time averages only 3 hours. The future models might need to host a larger battery and even more efficient hardware, competing with the MacBooks in terms of endurance.

Rumors suggest that the Vision Pro team at Apple is presently working on many of the issues observed by early adopters. Besides the cost-effectiveness of the headset, enhancing battery life and reducing weight could be their main concern. Additionally, MacRumors mused aloud an interesting point about the potential ramifications of this product for iPad sales. The Vision Pro aims to be an iPad-esque offering but with far more potential. Nevertheless, Apple has the final say in directions intended for future Vision products.


[ad_2]
Source link

The Human Factor in Cybersecurity and Financial Decisions

0
[ad_1]

Beneath the surface of those analytical gear lies a crucial element that regularly shapes the future of investments and determines vulnerability to cyber threats – the human component. 

We will explore how deeply rooted feelings, consisting of fear and greed, can cloud judgment, rendering individuals more liable to phishing assaults or falling sufferer to investment scams. 

The Psychology of Investment Decisions

Here is the psychology of investment decisions.

Emotional Influences on Decision-Making

Fear and its Impact

Fear is a powerful pressure that could force people to make impulsive and often irrational choices. 

The worry of missing out (FOMO) or the concern of losing difficult-earned cash can lead buyers down a treacherous path, wherein the warning is frequently thrown to the wind. 

This emotional vulnerability becomes a breeding floor for sophisticated phishing attacks, as cybercriminals exploit this fear to control people into divulging touchy statistics.

Real-lifestyle instances abound wherein traders, gripped by fear at some stage in marketplace downturns, hastily liquidate their investments, simplest to recognize later that it changed into an emotional knee-jerk response with unfavourable outcomes.

Greed and its Pitfalls

Conversely, the insatiable appetite for wealth, fueled via greed, can distort rational wondering and spark people to interact in high-hazard funding strategies. 

This psychological vulnerability exposes them to fraudulent funding schemes and increases their susceptibility to cyber threats. 

Cybercriminals are adept at exploiting the desire for short, vast profits, luring sufferers into complicated funding scams that promise unrealistic returns.

Examining historical instances reveals the devastating results of greed-pushed monetary decisions, wherein people entrust their funds to dubious schemes, only to discover that the promised returns were not anything more than a mirage.

Cognitive Biases in Financial Choices

Confirmation Bias

Confirmation bias, the tendency to prefer information that confirms pre-existing ideals, is a pervasive cognitive bias that substantially affects investment decisions. 

Investors frequently search for facts that align with their views, overlooking contradictory evidence. 

This cognitive blind spot no longer influences investment picks but also makes people extra prone to cyber threats, as they may dismiss caution symptoms that challenge their preconceived notions.

To mitigate affirmation bias, buyers must diversify their facts sources, severely compare opposing viewpoints, and domesticate an open-minded technique to choice-making.

Overconfidence

Overconfidence in one’s ability to expect marketplace tendencies may be a dangerous trap. Investors who overestimate their expertise and skills often engage in risky behaviours, making them vulnerable to investment scams and cyber threats. 

Cybercriminals capitalize on overconfidence by exploiting those who consider they may be proof against phishing attacks or fraudulent schemes.

Triumphant tales of individuals who identified and overcame overconfidence function treasured training, emphasizing the significance of humility and non-stop studying in the ever-converting monetary landscape.

Cybersecurity Vulnerabilities and Emotional Decision-Making

Let’s see some of the vulnerabilities and emotional decision-making.

Phishing Attacks

Exploiting Emotional Weaknesses

Phishing assaults are carefully crafted to exploit human emotions, capitalizing on worry, urgency, and curiosity. Cybercriminals design emails that trigger emotional responses, compelling people to click on malicious links or offer exclusive facts. 

Understanding the emotional triggers in phishing emails (PDF) is vital for people to recognize and face up to those manipulative tactics.

Psychological Tactics Employed with the aid of Cybercriminals

Cybercriminals hire a myriad of mental techniques to execute successful phishing attacks. Creating a fake sense of urgency, being attracted to emotions for credential theft, and imitating dependence on entities are not unusual techniques. 

Analyzing real-life examples of successful phishing assaults illustrates the effectiveness of those strategies and emphasizes the need for heightened vigilance.

Investment Scams and Emotional Manipulation

The Connection Between Investment Scams and Emotions

Investment scams regularly prey on people’s feelings, promising beneficial returns and economic achievement. 

The appeal of quick wealth can blind people to pink flags, putting them at risk of fraudulent schemes. Recognizing the emotional manipulation at play is critical for buyers to protect their belongings.

JustMarkets: A Beacon of Transparency and Education

Transparency in Financial Transactions

According to JustMarkets, a multi-asset online CFD broker, it distinguishes itself by prioritizing transparency in each aspect of monetary transactions. By leveraging blockchain technology, JustMarkets ensures that every transaction is verifiable and traceable. This transparency effectively builds trust and is a formidable deterrent to fraudulent activities.

Prioritizing User Education

Understanding the risks associated with emotional selection-making, JustMarkets strongly emphasizes personal education. 

Through complete educational assets, users have the know-how to make informed decisions. JustMarkets’ commitment to empowering customers with financial literacy is pivotal in creating a safer and more resilient investment environment.

Conclusion

The human thing emerges as a crucial determinant of achievement or vulnerability. Fear and greed, confirmation bias, overconfidence – these mental nuances can form the trajectory of investments and expose people to cyber threats. 

By unravelling the complexities of human psychology in these domain names, buyers can strengthen their selection-making strategies, making sound alternatives in an ever-evolving virtual generation.

  1. The Human Factor in Cybersecurity
  2. Fintech’s Crucial Role in Reducing Cyber Threats
  3. Human Error: Casio ClassPad Data Breach Impacting 148 Countries
  4. New Phishing Scam Hooks META Businesses with Trademark Threats
  5. The Anatomy of Trading Bot Scams: Strategies for Secure Investments

[ad_2]
Source link