What Is Disney Plus Premier Access? Everything You Need To Know

0
[ad_1]

Disney Plus Premier Access can be a bit confusing, but essentially it allows you to watch movies at home, the same day they hit the theater. But not all movies are available on Premier Access. And it’s also not included in the price of Disney+, unfortunately.

Here we’re going to aim to answer all of your questions about Disney Plus Premier Access, to help you get a better picture of what it is, and whether it’s worth it, or not.

What is Disney Plus Premier Access?

When the pandemic started in 2020, Disney decided to delay all of its movie debuts. But eventually decided to launch Mulan in September 2020, on a new service called Disney Plus Premier Access. Essentially, it’s an upgraded version of Disney Plus that will allow you to watch new releases the same day they launch in theaters. Of course, Mulan did not launch in theaters as they were still closed.

Essentially, for a flat fee, you can watch the movie as many times as you want within the initial launch window. That’s generally around 30 days. Mulan, for example, became available for all Disney Plus subscribers on December 4, to watch.

The fee is only to watch it at launch. After the initial launch window, the movie is gone. Which makes this a bit less of a deal. However, if you have a nice home theater and have a group of friends over to watch the movie, you can split the cost and that makes it a bit easier to stomach.

Update: As of September 2021, all future Disney movies will be available in theaters only on day-one. They will later head to Disney+ about 45 days later, for the regular Disney+ price. Meaning that Premier Access is over.

mulan disney plus hotstar

How much does it cost?

Disney Plus Premier Access costs $30 for each movie. And that is on top of the Disney+ subscription that you also need. Which is now $7.99 per month (the price went up on March 26, from $6.99 per month).

At first, Premier Access was announced as a temporary solution for releasing movies during the pandemic. We expect this to end in 2021 however. With Black Widow and Cruella being some of the last movies available on Disney Plus Premier Access. The reason for this is, Disney will make more money on these movies by bringing them to the theater and collecting from the box office. Which is actually important, as Disney needs to make back the money they spent on producing these films. And Marvel (as well as Star Wars) films are not cheap to produce.

We expect that Disney Plus Premier Access will go away in early 2022, if not earlier. Once the world opens up more, after everyone gets their COVID-19 vaccine.

What movies are/were available on Disney Plus Premier Access?

As if Disney Plus Premier Access wasn’t already confusing, the fact that not every movie that came out, launched on Premier Access makes it even more confusing.

The bigger titles like Mulan, Raya and the Last Dragon, as well as Black Widow are or were all on Disney Plus Premier Access. However, Soul, which came out on Christmas Day 2020, was not part of Premier Access. It was available to all Disney Plus subscribers. Disney is only putting in its bigger name movies onto Premier Access, as a way to make back some of that lost revenue from the box office.

How do I purchase a movie on Premier Access?

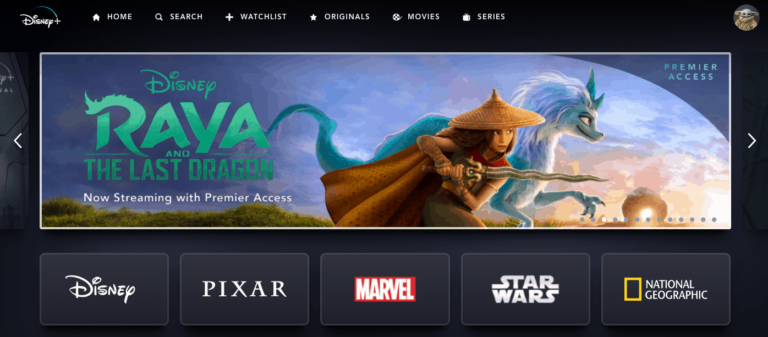
In the top section of the Disney Plus home screen, where you see the scrolling banners, Disney will show movies that are available or coming to Premier Access.

Screen Shot 2021 03 26 at 1 50 29 PM

Just click on the movie you want to purchase, and you’ll be taken to the page that gives you more information on the movie. Including watching the Trailer. Then click on “Get Premier Access” and you’ll go through the purchasing phase.

This page also shows you when the movie will be available for all Disney Plus subscribers. In the case of Raya and the Last Dragon, that’s June 4. That’s almost exactly three months after it launched on Premier Access.

Sign Up For Disney+


[ad_2]
Source link

ExpressVPN Bug Leaked DNS Requests for Windows Users

0
[ad_1]

Security researchers uncover a flaw in ExpressVPN’s Windows client, potentially exposing browsing activity for a small percentage of users.

A recent discovery by security researchers revealed a worrying bug in ExpressVPN‘s Windows client, potentially leaking sensitive DNS requests outside the encrypted VPN tunnel.

This means that, under specific circumstances, websites visited by affected users could be visible to their internet service provider (ISP). While the actual content of online activity remains encrypted, the knowledge of visited websites can still be intrusive and compromise anonymity.

Who Was Affected:

The vulnerability only affected users who had the “split tunneling” feature enabled in their ExpressVPN client. This feature allows users to choose which applications bypass the VPN connection while others remain protected. The issue reportedly impacted roughly 1% of ExpressVPN’s Windows user base.

Impact and Mitigation:

While the leak did not expose the actual content of online activity, it could still reveal browsing habits and potentially be used for targeted advertising or tracking. Thankfully, ExpressVPN swiftly addressed the issue by releasing a patched version (12.73.0) in January 2024. Users with split tunneling enabled are strongly advised to update their clients immediately.

Versions 12.23.1–12.72.0 of our Windows app, published between May 19, 2022, and Feb. 7, 2024, had a bug that allowed some users’ DNS requests to go unprotected when split tunneling was activated. In these instances, the apps that were supposed to use the VPN might, under some circumstances, send DNS requests to third-party DNS servers instead of our servers.

ExpressVPN

ExpressVPN’s Response:

ExpressVPN acknowledged the bug and emphasized its commitment to user privacy. The company also revealed that the bug was discovered and reported by CNET’s Attila Tomaschek.

They released a detailed explanation of the issue and the fix implemented, along with instructions on how to update the client. They also clarified that the vast majority of their users were not affected.

Lessons Learned:

This incident highlights the importance of keeping software, particularly security software, up-to-date. It also reinforces the need for careful consideration when using features like split tunneling, as they can introduce potential vulnerabilities. Users should be aware of the trade-offs involved and prioritize their privacy needs when configuring their VPN settings.

In Summary

  • The bug was discovered and reported by CNET’s Attila Tomaschek.
  • This was not a full-blown data leak, only DNS requests leaked in specific situations.
  • The content of your online activity remained encrypted and protected.
  • The issue only affected certain versions of the ExpressVPN client on Windows.
  • The issue has been fixed and the vast majority of users were not affected.
  1. How to Secure a Website by Monitoring DNS Records
  2. Almost Every Major Free VPN Service is a Glorified Data Farm
  3. New VPN Malvertising Attack Drops OpcJacker Crypto Stealer
  4. Google Incognito Mode: New Disclaimer Reveals Data Tracking
  5. Free VPN Service SuperVPN Exposes 360 Million User Records
  6. Chinese VPN app Quickfox caught exposing 1 million users’ data

[ad_2]
Source link

Google Messages could change how you react to messages

0
[ad_1]

One of the great things about using Google messages (besides the image captioning feature that’s coming) is the fact that you can hold your finger down on the button to add a reaction. This is very quick and convenient, but it seems that Google wants to make a change to it. According to a new report, Google will add a double-tap gesture to use a reaction in Google Messages.

One thing to note is that this was discovered in an APK Deep dive. This means that the information may not be 100% accurate. 9To5Google dug into the code for the most recent version of the Google messages app, and it discovered strings alluding to this feature. However, it’s not a guarantee that Google will unveil this feature in the future. So, you will want to take this news with a grain of salt.

Google Messages could use a double-tap gesture to add a reaction.

Currently, if you want to access additional settings for your messages in Google Messages, you have to hold your finger down on the message. This process isn’t particularly long or labor intensive. When you do so, you will summon the tray holding all of your available reactions. Along with that, you’ll also be able to access additional options for the message. These are the star, copy, and delete options. You’ll also see a three-dot menu that has the forward, view details, and share options.

Having those both being summoned by the same gesture isn’t really a big issue. However, it appears that Google feels differently. According to the APK deep-dive, it appears that the company wants to make adding a reaction a double-tap gesture in Google Messages. So, instead of holding your finger down on a message to add a reaction, all you have to do is tap on it twice.

9To5Google discovered this in version 20240208 _00_RC00 of the Google Messages app. At this point, there’s no telling when/if Google plans on releasing this feature. It doesn’t seem like a future that’s big enough to get much fanfare, so it doesn’t seem likely that the company will release it during another future drop. However, that remains to be seen. This could be another nice feature like the Photomoji feature recently introduced.


[ad_2]
Source link

Gemini is one step closer to replacing the Google Assistant

0
[ad_1]

First, Google Gemini snuffed out Bard, and it appears that it now has Assistant in its sights. At this point, we’re all wondering when Google will replace the Google Assistant with Gemini. Well, it appears that Gemini is taking one step closer to doing so, as you no longer have to press the Send button when you use it as a voice assistant.

Currently, you’re able to use Gemini as a voice assistant of sorts on your phone- this is handled through the Gemini app. You’re able to use the diagonal swipe-up gesture to summon it and speak into your phone as though it were the Google Assistant or Bixby. This basically gives you a more powerful generative AI assistant compared to the more traditional Google Assistant. Undoubtedly, people will migrate toward using Gemini over using Google Assistant.

However, Google did state that Gemini does lack several assistant features that would otherwise make it a more complete alternative.

You no longer have to press the Send button when using Gemini as a voice assistant

There’s one major thing keeping Gemini from feeling like a true-to-form voice assistant. After you speak to Gemini, you have to physically press the Send button in order to send the query. While that’s not the most inconvenient thing, it’s definitely less convenient compared to simply saying what you want to say and having it automatically respond. When speaking to the Google Assistant, that’s what you have to do.

People complained about this, and it appears that Google has responded. Now, when you use Gemini through the swipe-up gesture, you won’t have to press the Send button to send your query. You just have to speak, and then the app will do the rest. This makes this experience a bit more seamless and further cements Gemini as a potential replacement for Google Assistant.

We’re all fairly certain that Google is going to replace the Assistant with Gemini, but the company has not outright stated so. In any case, it’ll definitely be sad to see Assistant go if it does happen. Google officially unveiled it back in 2016 along with the very first Pixel phone. It’s been a staple for the Android operating system ever since, so, it will be sad to see it kill off before its 10th birthday. However, that may be the case.


[ad_2]
Source link

Ransomware review: January 2024

0
[ad_1]

This article is based on research by Marcelo Rivero, Malwarebytes’ ransomware specialist, who monitors information published by ransomware gangs on their Dark Web sites. In this report, “known attacks” are those where the victim did not pay a ransom. This provides the best overall picture of ransomware activity, but the true number of attacks is far higher.

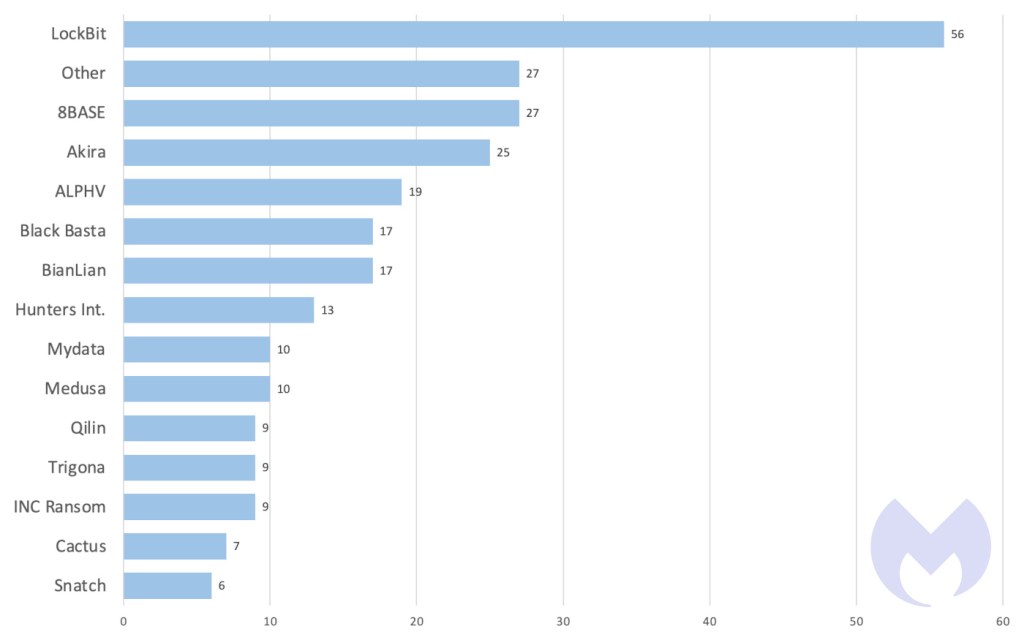
In January, we recorded a total of 261 ransomware victims, the lowest number of attacks since February 2023. This is normal, as past data reveals that historical January months tend to be one of the least active periods for ransomware gangs. But don’t let the relatively low number of attacks fool you: there was plenty of important ransomware news last month. 

In January, researchers observed fake “security researchers” trying to trick ransomware victims into thinking that they can recover their stolen data. Described as “follow-on extortion” attacks, the goal of these scams is to get the victims to pay Bitcoin for supposed assistance.

The two examples we have of follow-on extortion attacks targeted victims of the Royal and Akira ransomware gangs, but it’s unclear if the fake security researchers are a part of either of those gangs. Our guess? It’s more likely that they are a fringe group simply seizing an opportunity to exploit victims already targeted by these gangs. 

Let’s analyze why, using two scenarios, assuming that the follow-up extortioners really are Royal or Akira.  

In scenario one, Royal or Akira steals data, prompting a ransom payment from the victim for data deletion. Then, Royal or Akira sends a splinter group to the same victim claiming Royal didn’t delete the data, offering deletion services for an additional fee. This scenario is pretty unlikely, as it undermines Royal’s credibility from the victim’s perspective, damaging the gang’s reputation.

In scenario two, Royal or Akira steals data, but the victim hasn’t paid for deletion yet. The Royal or Akira splinter group then offers to recover the data for a fee. This predicament forces the victim to choose who to trust, likely deciding that it might be more logical to rely on Royal since they have more incentive to maintain a semblance of reliability. So, it then just becomes a normal double-extortion case but with an unnecessary extra step.

In the first case, the “initial ransomware gang” has no leverage for a second round of extortion without contradicting their own claims and damaging their reputation. In the second case, the initial ransomware gang just does more work to get the same outcome, namely payment for data deletion. 

Neither option presents a guaranteed connection to the original attackers.

Known ransomware attacks by gang, January 2024
Known ransomware attacks by country, January 2024
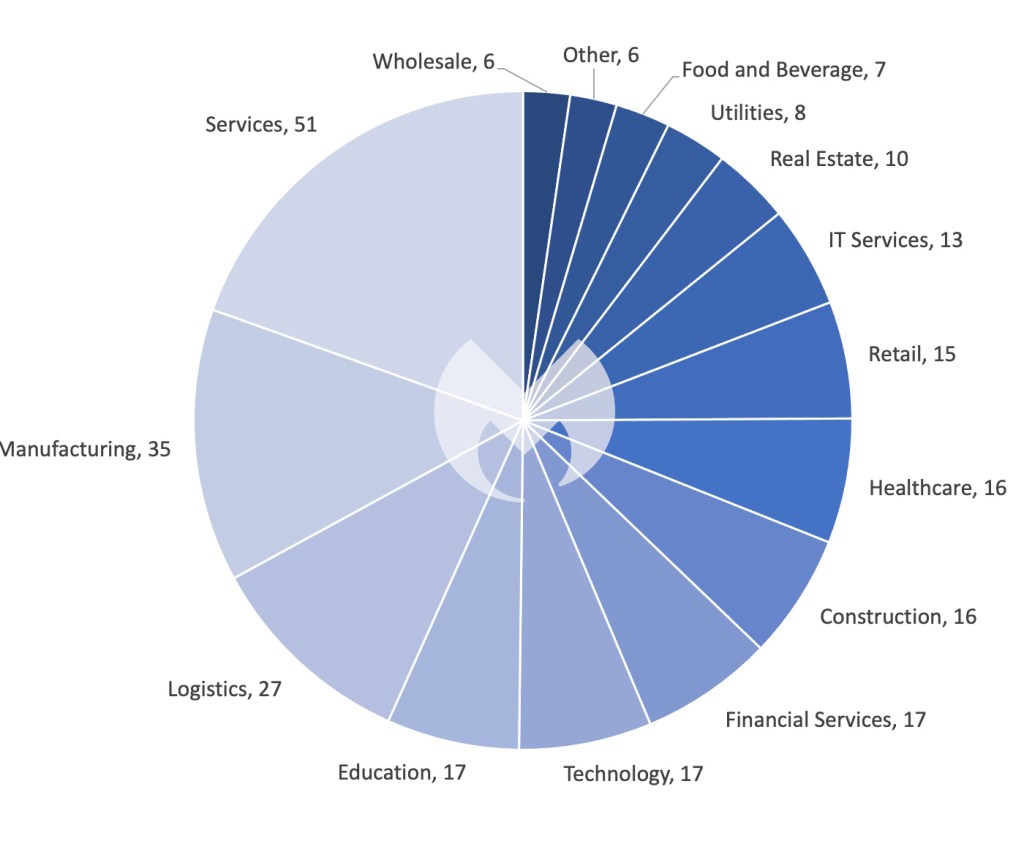
Known ransomware attacks by industry sector, January 2024

In other January news, the UK’s National Cybersecurity Centre (NCSC) released a report suggesting that AI will boost ransomware attack volume and severity in the next two years, particularly through lowering the entry barrier for novice hackers. A simple example is an affiliate using generative AI to create more persuasive phishing emails. This could decrease affiliates’ dependence on Initial Access Brokers for accessing networks, leading to more attacks by individuals enticed by the lower initial investment.

In general, however, we should be cautious about these predictions. Incorporating AI into cybercrime—especially for automated discovery of vulnerabilities or efficient high-value data extraction, as NCSC’s report suggests—is extremely complex and costly. For major gangs like LockBit and CL0P, who manage multimillion-dollar operations, adopting these AI advancements might be more feasible, yet it is still far too early to speculate upon.

In our view, RaaS groups will maintain their current operations in the short term. AI may introduce new methods and techniques for cybercriminals, to be sure, but the core principles of ransomware gangs—based on access, leverage, and profit—will likely continue unchanged for the foreseeable future.

In other news, researchers last month witnessed Black Basta affiliates leveraging a new phishing campaign aimed at delivering a relatively new loader named PikaBot. 

PikaBot, an ostensible replacement for the notorious OakBot malware, is an initial access tool that we first wrote about in mid-December—and it looks like it didn’t take ransomware gangs long to start using it. While our original post about PikaBot focused on its distribution via malicious search ads and not phishing emails, ransomware gangs are known to use both attack vectors to gain initial access. 

A typical distribution chain for PikaBot, writes ThreatDown Intelligence researcher Jérôme Segura, usually starts with an email (within an already-hijacked thread) containing a link to an external website. Users are then tricked to download a zip archive containing malicious JavaScript that downloads Pikabot from an external server. 

As this news marks the first time that PikaBot has been publicly connected with any ransomware operations, it’s safe to assume that the malware is actively being used by other gangs as well—or that if it’s not, it will be soon.

New leak site: MYDATA

Mydata is a new leak site from Alpha ransomware, a distinct group not to be confused with ALPHV ransomware. The site published the data of 10 victims in January.

Preventing Ransomware

Fighting off ransomware gangs like the ones we report on each month requires a layered security strategy. Technology that preemptively keeps gangs out of your systems is great—but it’s not enough. 

Ransomware attackers target the easiest entry points: an example chain might be that they first try phishing emails, then open RDP ports, and if those are secured, they’ll exploit unpatched vulnerabilities. Multi-layered security is about making infiltration progressively harder and detecting those who do get through. 

Technologies like Endpoint Protection (EP) and Vulnerability and Patch Management (VPM) are vital first defenses, reducing breach likelihood. 

The key point, though, is to assume that motivated gangs will eventually breach defenses. Endpoint Detection and Response (EDR) is crucial for finding and removing threats before damage occurs. And if a breach does happen—ransomware rollback tools can undo changes.

How ThreatDown Addresses Ransomware

ThreatDown bundles take a comprehensive approach to these challenges. Our integrated solutions combine EP, VPM, and EDR technologies, tailored to your organization’s specific needs. ThreatDown’s select bundles offer:

ransomware 1

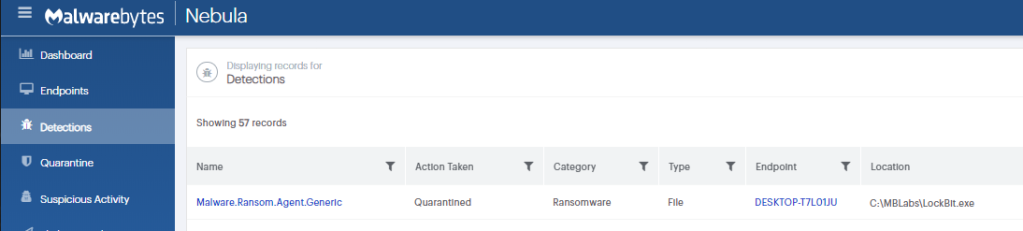
ThreatDown EDR detecting LockBit ransomware

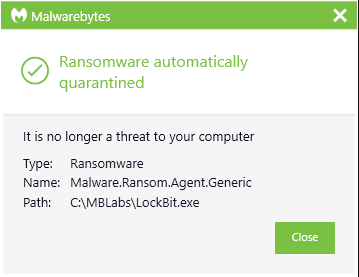
ThreatDown automatically quarantining LockBit ransomware

For resource-constrained organizations, select ThreatDown bundles offer Managed Detection and Response (MDR) services, providing expert monitoring and swift threat response to ransomware threats—without the need for large in-house cybersecurity teams.


Our business solutions remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.


[ad_2]
Source link

Don’t worry, WhatsApp is still testing usernames

0
[ad_1]

When using WhatsApp, giving out your phone number is a must. That’s how people identify you on the application. While the company has been able to remain one of the top messaging apps in the world, this is still something that people have a major issue with. However, WhatsApp is still testing the ability for users to create usernames on the platform.

The company has been working on this feature for several months. In fact, we were seeing hints at this feature ever since May of last year, and it’s leaving people wondering what is taking the app so long. However, completely revamping how users are identified throughout the app definitely seems like a very big ask, so we’re just going to have to be a little bit patient.

WhatsApp is still testing usernames

Not everybody likes giving out their phone number. Sure, if you’re communicating with your friends, family, or trusted work colleagues, it’s not a big issue. However, WhatsApp is also home to many untrustworthy individuals. People try to sell scams, post phishing campaigns, steal data, Etc. You don’t want a sensitive bit of information like your phone number being vulnerable to bad actors such as these.

This is one of the main reasons why people want usernames. Thanks to WABetaInfo, it appears that WhatsApp is getting closer to implementing this change. In the screenshot below, we see the “Choose my username” option under the profile section in the settings. This was spotted in the Android beta version of the app with the build number 2.23.11.15.

WhatsApp username setting

It’s showing up for some beta uses, but it’s not available for everyone. So, be sure to get the update and see if you have the option.

The ability to make a username will make using WhatsApp a much more customizable experience. There are people who may not want to go by their real names or show their phone numbers on the app. Rather, they want to protect their identity while on the platform. Also, you can’t argue with the freedom of expression that comes with being able to make a username.

More WhatsApp news

WhatsApp is also working on letting people designate their favorite contacts on the desktop version. This feature is still in testing.


[ad_2]
Source link

TSMC aims to double its 3nm production in 2024, improve yield

0
[ad_1]

Taiwanese semiconductor behemoth TSMC appears well-prepared to strengthen its lead in the foundry market. The firm reportedly plans to nearly double its 3nm production volume in 2024 compared to 2023. It is also in the process of improving the 3nm yield rate to over 80%.

TSMC is working on improving 3nm yield and production volume

TSMC started 3nm mass production after Samsung but went on to commercially produce the first 3nm smartphone processor ahead of its foundry rival. The company manufactured Apple’s A17 Pro chip used in the iPhone 15 Pro and iPhone 15 Pro Max. Samsung has yet to produce 3nm smartphone chips, with its initial production limited to other use cases such as cryptocurrency mining.

The Korean firm is said to be struggling with yield rates, a measure of the usable chips produced from a wafer. TSMC also has a poor 3nm yield rate compared to previous-gen solutions, but not as poor as Samsung. More importantly, according to X tipster Revegnus, who cited a DigiTimes report, the Taiwanese firm is working towards improving the yield rate to over 80% this year.

If it manages to do that, its production capacity will increase instantly. The publication reports that a higher 3nm yield rate, coupled with other foundry improvements, could enable TSMC to nearly double its production volume this year. Along with Apple, the firm may also manufacture 3nm smartphone chips for MediaTek. It might have landed contracts from companies in other tech sectors too.

This report comes right on the heels of TSMC announcing its second wafer fab in Japan. The company will construct the new factory through Japan Advanced Semiconductor Manufacturing (JASM) as part of a joint venture with its Japanese partners, which include Toyota Motors. TSMC reported a 22.4% month-on-month increase in revenue in January 2024, reaching NT$215.79 billion (approx. $6.9 billion).

Samsung is playing catch-up to its foundry rival

TSMC’s 3nm improvements are bad news for Samsung. The Korean firm has long played second fiddle to TSMC in the foundry market, with many big companies picking the latter’s fab over Samsung. Despite a headstart in the 3nm era, it failed to close the gap to its arch-rival. The Taiwanese behemoth appears to have already gained an advantage in 3nm mass production.

Samsung now aims to compete with TSMC in the 2nm space, the new report states. It has reportedly invited major clients to try its 2nm semiconductor fabrication process. Analysts still don’t appear optimistic about Samsung’s 2nm solution, though. It remains to be seen if the Korean firm can close the gap to TSMC in the 2nm era. Both companies plan to start 2nm mass production in 2025.


[ad_2]
Source link

Ransomware Attack Disrupts Services in 18 Romanian Hospitals

0
[ad_1]

The Romanian Ministry of Health has confirmed that its critical system is down due to the ransomware attack, and authorities are working to restore it.

Romanian authorities have reported a devastating ransomware attack on multiple medical facilities using the Hipocrate Information System (HIS) healthcare management system. The system became non-functional, making hospital staff unable to access files/databases and forcing patients to wait in emergency rooms. For your information, hospitals use this system to manage medical activities and patient data.

The Romanian Ministry of Health confirmed that the system is down at the impacted hospitals and that their file/databases are encrypted. The ministry advises hospitals to focus on restoring IT services and data and urges users to not reach out to IT staff to help them focus on restoration job. Hospitals are working with the National Cybersecurity Center to identify and address the issues, Health Minister Alexandru Rafila stated.

Rafila initially claimed that 15-20 hospitals in Romania and Bucharest could be facing operational difficulties due to the attack, which took place on production servers running HIS IT system. It started on the night of 11-12 February. As per the latest update, at least 18 medical facilities have been affected in this attack. Some hospitals’ websites, including Fundeni Clinical Institute or Military Emergency Hospital “Dr. Alexandru Gafencu” Constanta are unreachable.

Romania’s National Cyber Security Directorate (NCSD) has dispatched specialists to investigate the incident. The identity of the attacker and the theft of patients’ data remain unclear.

“We don’t have the information, but we are working together with the National Cybersecurity Center to elucidate the causes and remedy them,” the minister said.

The list of the eighteen impacted hospitals shared by Romanian-Insider includes the following:

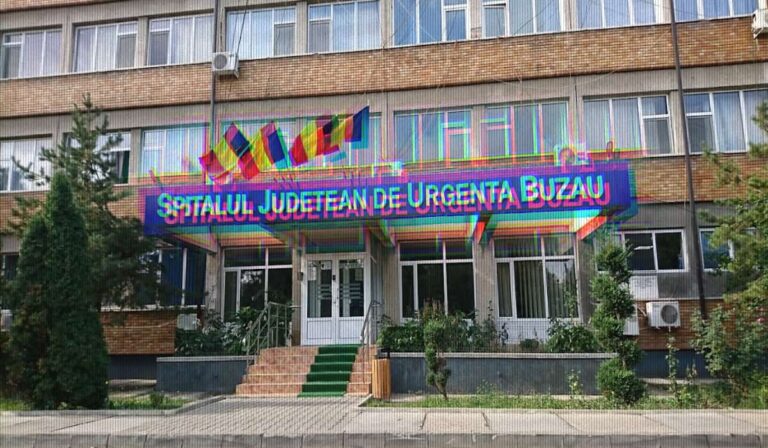
  • Buzău County Emergency Hospital
  • Slobozia County Emergency Hospital
  • Timișoara Institute of Cardiovascular Diseases
  • St. Luca Chronic Diseases Hospital
  • Colțea Clinical Hospital
  • Medgidia Municipal Hospital
  • Targoviste County Emergency Hospital
  • Sighetu Marmației Municipal Hospital
  • Pitești County Emergency Hospital
  • Regional Oncology Institute Iași (IRO Iași)
  • Fundeni Clinical Institute
  • “Sf. Apostol Andrei” County Clinical Emergency Hospital, Constanța
  • Azuga Orthopedics and Traumatology Hospital “Dr. Constantin Opris”
  • “Dr. Alexandru Gafencu” Military Emergency Hospital, Constanța
  • C.F. Clinic Hospital No. 2, Bucharest
  • Prof. Dr. Al. Trestioreanu Oncology Institute, Bucharest (IOB)
  • Baia Mare Emergency Hospital
  • The Emergency Clinical Hospital for Plastic Surgery, Reconstructive Surgery and Burns, Bucharest

Hospitals and medical facilities’ IT infrastructure are vulnerable targets for hackers. Hackread has observed that threat actors generally exploit five pressure points: shutdown of medical appliances, loss of patient medical history, public backlash, and potential federal and criminal investigations.

In September 2020, German hospital named University Hospital Düsseldorf (UKD) suffer a reported ransomware attack which led to the death of a patient. In August 2023, cybersecurity researcher Jeremiah Fowler discovered a massive data leak at Cigna Health, a major health insurance company. The database, containing over 17 billion records, mainly contained healthcare provider information and negotiated medical procedure rates.

Then in November 2023, SafetyDetectives cybersecurity researchers reported a data breach involving over 2 million Turkish citizens’ vaccination data from 2015 to 2023. The data was likely extracted using an information disclosure vulnerability.

In January 2024, Hackread reported the ALPHV ransomware gang’s targeted attack on Transformative Healthcare, occurring in late April 2023. Attackers stole a terabyte of data, including medical and paramedic reports, exposing data of nearly 1 million people, including 20,486 Maine residents. The attacker accessed a server containing patient information, which Transformative claimed was stored to comply with legal obligations.

These incidents indicate how vulnerable hospitals’ data management systems could be. To protect patient data, hospitals should consider implementing better security controls. Hackers can make quick cash from selling Personal Health Information (PHI), which is worth more than PII.

  1. WannaCry responsible for infecting medical devices
  2. CISA warns of disruptive ransomware attacks on US hospitals
  3. POLICE bust hackers planning to hit hospitals with ransomware
  4. Ransomware hackers leak pharmaceutical giant’s data on dark web
  5. Ethical hacker among 3 arrested for blackmail, ransomware attacks
  6. GoodWill Ransomware demands food for poor to decrypt locked files

[ad_2]
Source link

WhatsApp could be bringing favorite contacts to desktop users

0
[ad_1]

If you’re using WhatsApp, you’re bound to have contacts that you communicate with more often than others. Right now, the company is working on bringing a favorite contacts list for the iPhone version of the app. Now, according to a new report, it appears that WhatsApp is working on a favorite contacts list for desktop users as well. This comes after the company rolled out the ability to block numbers from the lock screen.

From the looks of it, if you’re using your favorite contact list of iOS, you’ll be able to quickly access and communicate with contacts from different screens in the app. For example, you’ll be able to quickly call your favorite contacts right from your calls tab. This eliminates the need to actively search for the contact throughout the app. You’ll have quick access to the contacts you interact with the most.

WhatsApp could be working on bringing the favorite contacts list to desktop users

Right now, WhatsApp is testing this feature for iPhones, but it appears that it wants to expand the feature to other platforms. As discovered by WABeta info, the company also wants to bring this feature over to desktop users.

Below, we see a screenshot showing this feature in action. In the Chats tab, we see a new Favorites chip right under the search bar. Below, we see a description of what favorite contacts are, and it also gives you the ability to add contacts via the green button.

WhatsApp favorite contacts web

At this point, we’re not entirely certain how many contacts you can add to your favorites list. We don’t know if it’s going to be unlimited or if WhatsApp is going to cap uses at a specific number. Also, we’re not entirely sure when we’ll see any indication of this feature coming to Android.

However, Android beta testers have enough beta tests going on. For example, WhatsApp is working on the ability for users to reply to announcement channel poses in Communities. In announcement channels, the admins are able to post messages to the members, but members are never able to reply to these messages. However, WhatsApp will soon give users the ability to reply.


[ad_2]
Source link

Microsoft now has an AI sticker generator for your social media posts

0
[ad_1]

At this point, there are a thousand and one AI image generators on the internet. They’re great for making full-fledged images. However, there are people who aren’t interested in making large images. There are some people who just want more possibilities when making social media posts. Well, Microsoft just unveiled its Designer Sticker Creator. This is an AI image generator for social media stickers.

The company has its image creator called Designer Image Creator. This is Microsoft’s full-fledged image generation platform that makes high-quality images. Right now, it’s available through Microsoft Copilot. If you want to quickly access it, you’ll want to go to the Microsoft Edge browser and look for the icon on the side panel.

The side panel will slide out and show you a text field to put your prompt in. Then, you will get AI-generated results right in the panel that you can download and use.

Microsoft brings its new Designer Sticker Creator

We’re at a point where we’re getting tired of The limited selection of stickers that we have to post on social media. Sure, there are a lot, but people want to be able to make their own. Well, Microsoft just came up with a way to do so.

The Microsoft Designer Sticker Creator is a standalone tool that you can access by going to the official site. Once you enter the site, you will see a grid of examples of what you can make. Since it’s an AI image generator, you can be as specific or as vague as you want. You’ll type your prompt into the text field at the top and it will get to work making your new sticker.

These will be high-quality images that you can download in PNG format. Since these are PNG pictures, they will have transparent backgrounds. This gives you the ability to edit them further using image editing software. Say, you want to give your sticker your own unique background. Well, you can paste the sticker into a program like GIMP or Photoshop, and add the background.

How to access this tool

Right now, the Microsoft Designer Sticker Creator is an Early Access platform. So, it’s not available to the public. If you want to use it, you’ll have to sign into your co-pilot account. We’re not quite sure when this feature will make it to the public.


[ad_2]
Source link