Patch now! Fortra GoAnywhere MFT vulnerability exploit available

0

[ad_1]

On January 22, 2024, software company Fortra warned customers about a new authentication bypass vulnerability impacting GoAnywhere MFT (Managed File Transfer) that allows an attacker to create a new admin user.

Fortra GoAnywhere MFT is a file transfer solution that organizations use to exchange their data. Some of the organizations that use GoAnywhere MFT are considered vital infrastructure such as local governments, financial companies, healthcare organizations, energy firms, and technology manufacturers.

The flaw impacts Fortra GoAnywhere MFT 6.x from 6.0.1 and Fortra GoAnywhere MFT 7.4.0 and earlier.

Customers should either install the latest update (now at 7.4.1) to fix the vulnerability, or eliminate the vulnerability in non-container deployments by deleting the InitialAccountSetup.xhtml file in the install directory and restarting the services. For container-deployed instances, replace the file with an empty file and restart. For additional information, see this advisory for customers (registration required).

By handing out these specific instructions it was to be expected that exploit code would come sooner rather than later. And, indeed, researchers were quick to analyze the flawed file and come up with an exploit and Proof-of-Concept (PoC) code.

Fortra told BleepingComputer earlier that there have been no reports of attacks exploiting this vulnerability. This might change quickly now that exploit code is readily available. To find out if your instance was compromised you should look for any new additions to the Admin Users group in the GoAnywhere administrator portal Users -> Admin Users section. Any new and unknown administrative users indicate a compromise and the login date will give you an idea about the time of compromise.

You can also look at the logs for the database which are stored at \GoAnywhere\userdata\database\goanywhere\log\*.log. These files contain a transactional history of the database, adding users will create entries in that log.

The Common Vulnerabilities and Exposures (CVE) database lists publicly disclosed computer security flaws. This vulnerability is listed as:

CVE-2024-0204: Authentication bypass in Fortra’s GoAnywhere MFT prior to 7.4.1 allows an unauthorized user to create an admin user via the administration portal.

Basically it’s a path traversal flaw that allow attackers to read, and write to, restricted files by inputting path traversal sequences like ../ or /..;/ into file or directory paths.

If the mention of the name of Fortra GoAnywhere sent shivers down your security sensors, you may have been reminded of the exploitation by the Clop ransomware gang of a vulnerability in the same software last year.

Despite several warnings about last year’s vulnerability, a great many victims were made even after the patch was available.

Let’s hope we are capable of learning from the mistakes we made in the past.


We don’t just report on vulnerabilities—we identify them, and prioritize action.

Cybersecurity risks should never spread beyond a headline. Keep vulnerabilities in tow by using ThreatDown Vulnerability and Patch Management.

[ad_2]

Source link
Galaxy S24 Ultra scratch test is here, both display & frame tested

0

[ad_1]

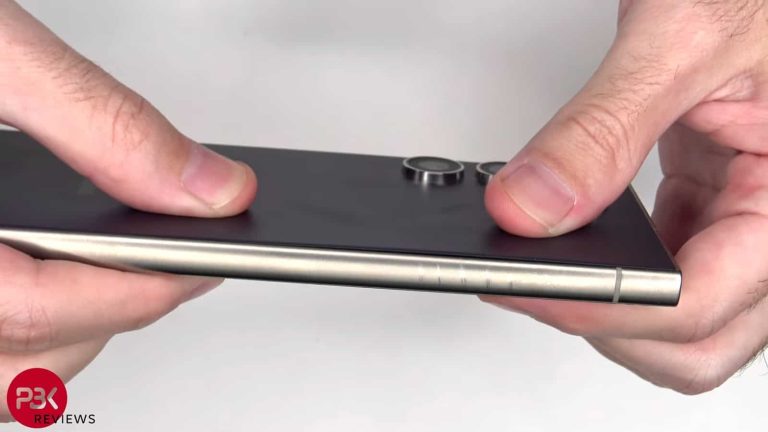
The Samsung Galaxy S24 Ultra durability test appeared on YouTube recently, courtesy of PBKReviews. That very same source just shared yet another test with the public, the Galaxy S24 Ultra scratch test.

The Galaxy S24 Ultra gets submitted to a scratch test, both its display and frame

The phone gets tested in a YouTube video which is embedded below the article. Both its display and frame get tested in the video. As a reminder, the Galaxy S24 Ultra comes with a titanium frame, and all-new Gorilla Armor screen protection.

In the video, the tester used the Mohs hardness test kit, like the one JerryRigEverything is usually using. The display started scratching at level 7, but the tester says that the marks are so faint that he doesn’t even consider them scratches. So you’ll get visible scratches at a level 8, it seems. The phone seems to be doing better than the Galaxy S23 Ultra with the Gorilla Glass Victus 2.

Corning’s Gorilla Armor is making a difference

Just to give you some clarification, Corning did say that the Gorilla Armor protection is more resistant to micro scratches. It also tackles reflections like a champ.

Having said that, the scratch resistance of the titanium frame was also tested in this video. Scratches start showing up at level 5. We don’t see many scratch tests of smartphone frames, so there you go.

As many of you know, this is the first time Samsung is using a titanium frame on one of its phones. It’s also the very first time any phone is using Gorilla Armor screen protection.

It’s safe to say that the phone did well in this test. The display resisted scratches really well, while we don’t really have a lot of comparison frame scratches on offer, but this only proves that titanium can be scratched, so using a case may be your best bet.

[ad_2]

Source link

Microsoft’s market value crossed $3 trillion, just behind Apple

0

[ad_1]

Microsoft’s market value briefly crossed the $3 trillion mark, making it the second most valuable company in the world behind Apple. This marks a huge milestone for the company, and it proves that it continues to massively grow in value each year. In fact, earlier this year Microsoft very briefly overtook Apple as the most valuable company in the world. With these two achievements under its belt, Microsoft seems to be gearing up for a ton of growth this year.

Microsoft’s market value continues to skyrocket

Microsoft is no small company, but its growth has been stagnating in recent years. Some strategic investments and acquisitions later, however, and the company is back on track for unparalleled growth. Microsoft shares hit a record high value of $405.63, allowing the company to breach the $3 trillion mark. This made Microsoft the second of the only two companies to have ever done so.

Shares closed at $402.56, bringing the company back down to $2.99 trillion. However, now that it’s proven that it can, Microsoft is sure to cross that mark again soon. Compared to just five years ago, the company has seen drastic growth. Priced at $107 in early 2019, the current share value of over $400 is impressive, to say the least.

Why Microsoft is growing and what it means for Apple

The most recent trend that is helping Microsoft’s market value grow this quickly is its investments in AI. Microsoft is determined to lead the way in the AI markets popping up across various industries. For example, Microsoft invested $13 billion into OpenAI so far, undoubtedly the most well-known AI company. It’s also made big promises about Copilot, Microsoft’s AI-powered assistant.

Apple, on the other hand, is seeing mixed receptions to its offerings. While it’s true the iPhone has become immensely popular in the States, its smartphones are apparently seeing diminished demand. There are multiple reasons for that, mainly centered around high cost and lack of innovation. These are problems even Samsung has recently begun to face. China seems to be very resistant to Apple’s products, prompting the company to offer its phones at a discount, which is unheard of.

Apple is most likely working on its own AI tools, biding its time. These might be a more refined form of the AI features we’ve recently seen on Google’s and Samsung’s phones. There are also rumors of MacBooks with OLED and even touchscreen displays. But if Apple doesn’t hurry it up, it might lose its coveted spot for good.

[ad_2]

Source link

Meta launches much stricter message setting for teens on Facebook and Instagram

0

[ad_1]

Following its recent changes to the teens experience on its social apps, Meta announced a harsher change meant to help protect teens from unwanted contact.

After limiting teens’ ability to see sensitive content on Instagram and Facebook, Meta introduced today a stricter message setting for teens who are using these two social apps.

Up until now, Meta restricted adults over the age of 19 from messaging teens who don’t follow them. Also, the company limits the type and number of DMs people will be able to send to someone who doesn’t follow them to one text-only message.

The new setting announced today makes it possible to turn off teens’ ability to receive DMs from anyone they don’t follow or aren’t connected to on Instagram, including other teens, by default.

When the new setting is toggled on, teens will only receive messages from people they already follow or are connected to. According to Meta, teens in “supervised accounts” will need to get their parents’ permission to change this setting.

The new default setting will apply to all teens under the age of 16 (or under 18 in certain countries). Those affected will receive a notification informing them about the new changes on Instagram at the top of their Feed.

Apart from Instagram, Meta revealed that it’s also making changes to teens’ default settings on Messenger, so those under 16 (or 18 in certain countries) will only receive messages from Facebook friends, or people they’re connected to through phone contacts.

Finally, Meta plans to launch another feature that will help protect teens from seeing unwanted and potentially inappropriate images in their message from people they’re already connected to.

[ad_2]

Source link

AI likely to boost ransomware, warns government body

0

[ad_1]

The British National Cyber Security Centre (NCSC) says it expects Artificial Intelligence (AI) to heighten the global ransomware threat.

In a report, the NCSC makes the assessment that AI will almost certainly increase the volume and heighten the impact of cyberattacks over the next two years. We’re already seeing that cybercriminals of all trades are using AI in the initial stages of attacks to increase their effectiveness. The NCSC confirmed, saying:

“All types of cyber threat actor – state and non-state, skilled and less skilled – are already using AI, to varying degrees.”

The NCSC expects the volume and the impact of cyberattacks to grow over the next two years.

The volume is expected to grow because AI lowers the barrier for entry-level cybercriminals to carry out effective access and information gathering operations.

The impact is expected to grow for several reasons:

  • AI already helps cybercriminals to compose more effective phishing emails.
  • AI will help to improve existing tactics, techniques, and procedures (TTPs).
  • Reconnaissance and social engineering are specific fields where AI can be deployed.
  • Stolen data can be analyzed by AI-driven tools and used for even more effective attacks.
  • More advanced threat actors, like state sponsored groups will be on the forefront of more sophisticated methods to utilize AI and others will follow.

Generative AI (GenAI) can already be used to create and entertain a convincing interaction with victims, including the creation of lure documents, without the translation, spelling, and grammatical errors that used to reveal phishing.

The NCSC expects that by 2025, GenAI and large language models (LLMs) will make it difficult for everyone, regardless of their cybersecurity posture, to assess whether an email or password reset request is genuine, or to identify phishing, spoofing, or other social engineering attempts.

Currently only state sponsored groups, professional spyware vendors, and the large criminal operations have access to, and know how to use advanced AI tools to increase the effectivity of their attacks. But that availability will undoubtedly grow.

In how far new moves on the front of a United Nations Cybercrime Treaty will have a short-term effect on the behavior of state-sponsored groups is very hard to predict. I’m inclined to say that international legislation has never stopped any hacktivist before, they were just more careful about revealing their location and their principals.

Professional spyware vendors have deep enough pockets to invest in new tools, training, and development. We can expect them to use AI to find new zero-day vulnerabilities and new exploits for largely unpatched vulnerabilities.

As we at Malwarebytes Labs have tested ourselves, ChatGPT can be used to write ransomware. While this may draw new players to the field, they are not expected to have an immediate impact on the threat level. But the NCSC does expect AI to play a larger role in the near future when it comes to the development of malware and exploits.

Since ransomware is the most profitable form of malware at the moment, and this is expected to stay that way, this threat is likely to see the largest increase in volume. Which means that for the visible part of cybercrime, the landscape is not likely to change dramatically. The numbers may increase and the sophistication of the attacks is likely to grow, but the type of malware is probably the same.

To sum up the conclusion of the report, NCSC chief executive Lindy Cameron said:

“The emergent use of AI in cyberattacks is evolutionary not revolutionary, meaning that it enhances existing threats like ransomware but does not transform the risk landscape in the near term.”

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; and disable or harden remote access like RDP and VPNs.
  • Prevent intrusions. Stop threats early before they can even infiltrate or infect your endpoints. Use endpoint security software that can prevent exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like ThreatDown EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Our business solutions remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

[ad_2]

Source link

TikTok planning 30-minute video uploads to compete with YouTube

0

[ad_1]

TikTok will soon offer 30-minute video uploads, it seems, as it’s aiming at YouTube. This information comes from Matt Navarra, a social media consultant. He spotted this option in the iOS beta version of the app.

TikTok seems to be planning to offer 30-minute video uploads

Now, Navarra did mention that some users spotted this option in the Android beta version of TikTok as well. So the change is not exclusive to iOS, not even in the testing phase. Considering that it’s already in beta, we could end up seeing it on offer soon.

TechCrunch reached out to TikTok but did not get a response from the company. It seems to be pretty obvious what TikTok is doing, though. The company completely rules short-form video content and is looking to get more into YouTube’s territory.

TikTok has been slowly, but surely, increasing the duration cap of videos. The original videos were capped out at 15 seconds, then it was bumped up to a minute. Later it was expanded to three minutes, and then 10 minutes.

TikTok actually started testing 15-minute video uploads not that long ago, only a couple of months ago. Well, it seems like the company is aiming even higher than that.

TikTok is aiming at YouTube with this change

While TikTok is trying to up the video limit cap in order to compete with YouTube, YouTube did the opposite. YouTube Shorts are basically competing directly with TikTok’s short-form content and they’ve been around for years.

Needless to say, 30-minute videos are a completely different beast. That move would open TikTok to various new creators who like to go in-depth with their content. That would enable various reviews and all kinds of other content.

At that point, we could even watch full sitcom episodes on TikTok, theoretically. Some studios may even end up using TikTok for that purpose. It would be nice to be able to filter the length of videos you’re getting, though.

If TikTok does make this move, a lot of users could end up with videos that are too long for their liking. The vast majority of TikTok users still expect really short and yet entertaining videos, not long-form content. Who knows, perhaps TikTok is planning some sort of a filter, we’ll see.

TikTok 30 minute video testing

[ad_2]

Source link

Snapdragon 8 Gen 4 could launch sooner than expected

0

[ad_1]

Qualcomm’s Snapdragon 8 Gen 4 processor could launch sooner than expected. That info is based on something a well-known tipster said. The information is coming from Digital Chat Station and was shared via Weibo.

The Snapdragon 8 Gen 4 could launch sooner than expected

The tipster said that internal testing of the chip is progressing well. He did not specifically mention anything related to the launch date of the Snapdragon 8 Gen 4, but he did mention phones that will be fueled by that processor.

He mentioned that those phones will enter mass production in September, which is a bit earlier than usual. GizmoChina seems to think the tipster is talking about the Xiaomi 15 series, amongst others, which is a possibility.

In any case, based on the timing of mass production of these phones, the Snapdragon 8 Gen 4 could indeed launch a bit sooner than expected. The Snapdragon 8 Gen 3 launched on October 24, while the Snapdragon 8 Gen 2 arrived in November.

The Snapdragon 8 Gen 3 arrived on October 24 last year

Qualcomm seems to be moving these launch dates up constantly. Well, that will be the case if the Snapdragon 8 Gen 4 does indeed launch early. Based on what we’ve seen thus far, it will arrive earlier than October 24, perhaps even in September.

Do take all of this with a grain of salt, though, as it’s based on mass production timelines for smartphones expected to be fueled by the Snapdragon 8 Gen 4. Even though those timelines do come from a reliable source.

The Snapdragon 8 Gen 4 will be a 3nm processor, as Qualcomm will stick with TSMC for the production of that chip. That chip is codenamed ‘Sun’, and it allegedly adopts a 2+6 structure. The design and performance of Qualcomm’s Oryon architecture has been “significantly improved”, allegedly. That chip is expected to bring a performance leap to the table.

There’s still a lot of time before the Snapdragon 8 Gen 4 is expected, so let’s wait for more information before making any conclusions.

[ad_2]

Source link

Kasseika Ransomware Exploits Driver Functionality to Kill Antivirus

0

[ad_1]

Ransomware is a tool that hackers use to extort money from their targets like individuals, businesses, and governments. The malware encrypts the target’s data and demands payment to unlock it.

This malicious strategy increases the possibility of payment by giving threat actors financial profits in the form of bitcoin in exchange for vital information.

Cybersecurity researchers at Trend Micro recently discovered that threat actors are actively exploiting the driver functionality to kill Antivirus programs.

Document

Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

Kasseika Ransomware Kill’s Antivirus

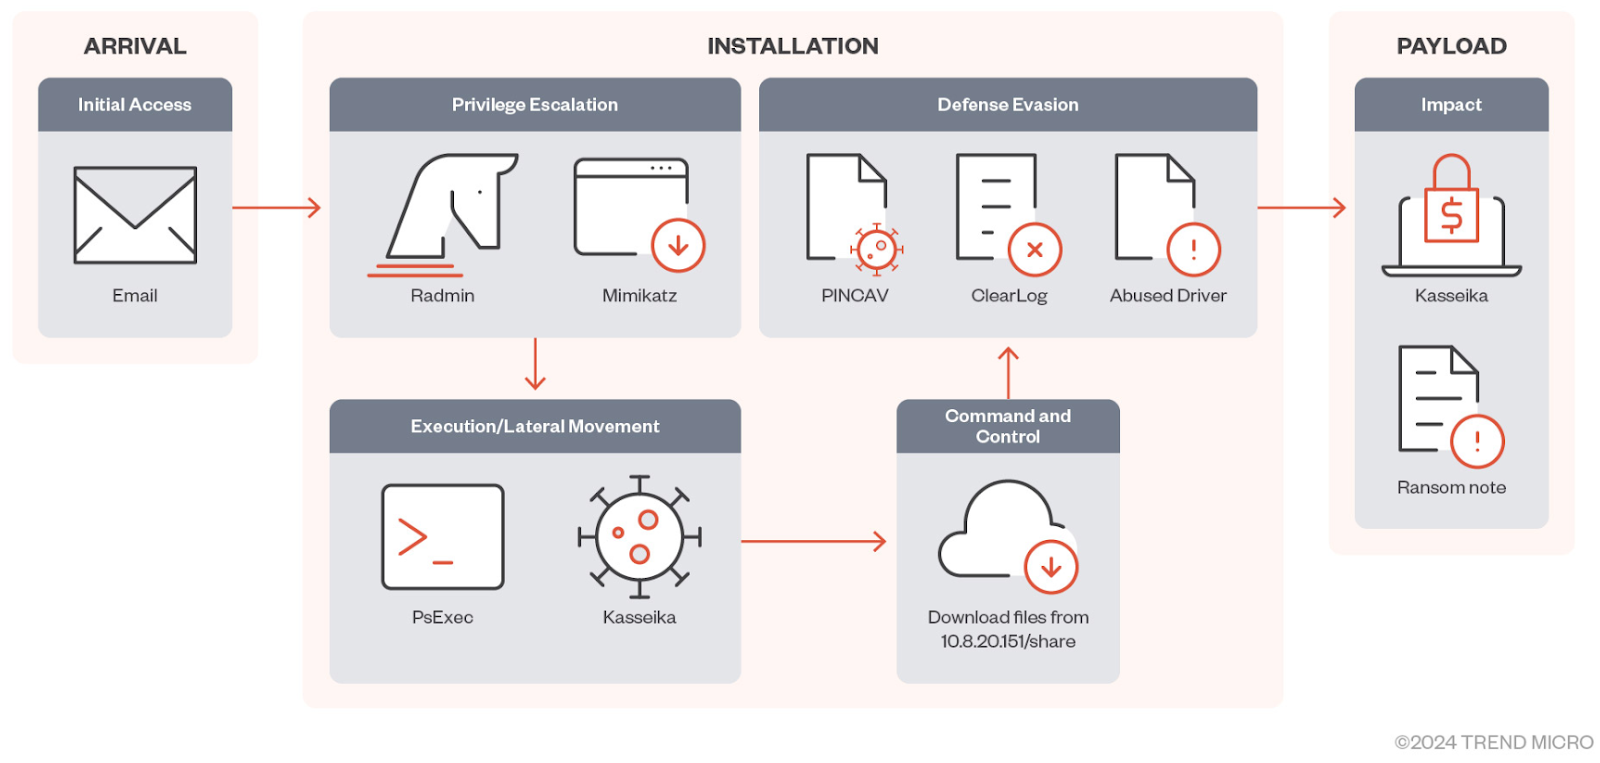
In 2023, Kasseika ransomware joined the BYOVD trend, following Akira, BlackByte, and AvosLocker. They used Martini driver to disable antivirus programs that resemble the BlackMatter with pseudo-ransom extensions. 

This suggests a mature actor with access to BlackMatter’s source code previously linked to DarkSide and ALPHV. Since its 2021 shutdown, exclusive ransomware groups have adapted BlackMatter’s old code for new strains.

Infection chain (Source - Trend Micro)
Infection chain (Source – Trend Micro)

Kasseika ransomware employs targeted phishing for initial access by gathering credentials and using PsExec to move within the network. 

It exploits Martini.sys to disable security tools, which helps terminate processes and leverages FindWindowA API to detect security-related processes. 

The script ensures a clean state by setting up flexible variables for future use. Kasseika transfers files, terminates antivirus processes with Martini.exe, and also executes smartscreen_protected.exe as its ransomware binary. The Clear.bat is then executed to erase traces of the operation.

Kasseika ransomware is a Themida-packed 32-bit Windows PE file that employs robust obfuscation and anti-debugging. 

It terminates processes accessing Windows Restart Manager by modifying the registry keys and enumerating session hashes before encryption. 

It erases shadow copies using WMIC queries and decrypts its extension with Base64 encoding. Kasseika uses ChaCha20 and RSA from CryptoPP by generating a modified matrix for encryption. 

After renaming and dropping CBhwKBgQD.README.txt as a ransom note, Kasseika changes the system wallpaper post-encryption.

Kasseika ransomware employs wevutil.exe to discreetly wipe Application, Security, and System event logs that help in evading easy detection and response by security tools.

Recommendations 

Here below we have mentioned all the recommendations:-

  • Grant admin rights only when necessary.
  • Regularly update security products and perform scans.
  • Secure backups for critical data.
  • Practice safe email and website habits.
  • Encourage reporting of suspicious emails and files.
  • Educate users on social engineering risks regularly.

Organizations can enhance security with a multilayered strategy by covering the endpoints, email, web, and network entry points. 

The detection of malicious components and suspicious behavior by security solutions is crucial for enterprise protection.

[ad_2]

Source link

Tesla, Sony, Alpine Players Breached on Day One

0

[ad_1]

Pwn2Own Automotive 2024 takes place in Tokyo, Japan, from January 24 to 26.

The Pwn2Own Automotive 2024 hacking contest, taking place in Tokyo, Japan from January 24 to January 26, focuses on loopholes in automotive technologies. Tesla is the contest’s sponsor with VicOne and Trend Micro’s Zero Day Initiative as co-hosts.

During the context, they will demonstrate zero-day exploits targeting Model 3/Y or Model S/X systems, including the infotainment, modem, tuner, wireless, and autopilot systems. The top prize for zero-day exploits will be $200,000 and a Tesla car.

On its first day, many vulnerabilities were highlighted, including weaknesses in Tesla’s modem, Sony’s infotainment systems, and Alpine’s car audio players, raising concerns about the security of connected vehicles.

Security researchers hacked multiple fully patched EV charging stations and infotainment systems. The NCC Group EDG team won $70,000 for hacking the Pioneer DMH-WT7600NEX infotainment system and the Phoenix Contact CHARX SEC-3100 EV charger exploiting zero days.  

Sina Kheirkhah successfully attacked ChargePoint Home Flex, earning $60,000 and six Master of Pwn Points. Tobias Scharnowski and Felix Buchmann attacked Sony XAV-AX5500 for $40,000 and four Master of Pwn Points. Gary Li Wang exploited the Sony XAV-AX5500 using a stack-based buffer overflow.

Security researchers successfully hacked a Tesla Modem and earned $722,500 in total in awards for identifying three bug collisions and 24 unique zero-day exploits. Synacktiv Team completed a 3-bug chain against Tesla Modem and JuiceBox 40 Smart EV Charging Station, earning $100,000 and $60,000 along with 10 and 6 Master of Pwn Points, respectively.

This means, the team chained three zero-day bugs to gain root permissions on a Tesla Modem. The Synacktiv Team also successfully attacked the Ubiquiti Connect EV Station, earning six Master of Pwn Points and $60,000.

A third exploit chain targeted the ChargePoint Home Flex EV charger, which earned security researchers $16,000 in cash and $295,000 in prizes.

The PCAutomotive Team successfully targeted the Alpine Halo9 iLX-F509 using a UAF exploit, earning $40,000 and 4 Master of Pwn Points. They discovered a vulnerability in Alpine’s car audio player, allowing arbitrary code execution. This could potentially give attackers control over the audio system, allowing them to play loud noises or inject malicious code into other connected systems.

RET2 Systems also achieved 6 Master of Pwn Points and $60,000 for exploiting a 2-bug chain against the Phoenix Contact CHARX SEC-3100. The PHP Hooligans / Midnight Blue team successfully targeted a Sony XAV-AX5500, earning $20,000.

For additional insights on Pwn2Own Automotive’s day 1 results, check out Zero Day Initiative’s blog.

The Pwn2Own exploits highlight the growing vulnerability of cars to cyberattacks due to the increasing integration of technology in vehicles. While researchers disclose their findings to help manufacturers fix vulnerabilities, car owners must remain vigilant.

  1. 6 of the Best Crypto Bug Bounty Programs
  2. Bug bounty: Hack Tesla Model 3 to win your own Model 3
  3. Pwn2Own 2023: Tesla Model 3, Windows 11, Ubuntu Pwned


[ad_2]

Source link

Android 14 QPR2 Beta 3.1 is now out with bug fixes

0

[ad_1]

Google is now rolling out Android 14 QPR2 Beta 3.1, focusing on resolving numerous bugs and improving system stability. This release comes following the Android 14 QPR2 Beta 3 update released earlier this month, which introduced significant UI changes. Notably, both the Android 14 QPR2 Beta 3 and Android 14 QPR2 Beta 2 released in December have already addressed several bugs.

The latest update, identified as AP11.231215.009, includes the January 2024 security patch. It is available for all Pixel phones starting from the Pixel 6 series to the Google Pixel 8 series. It also includes the Google Pixel 5a, Pixel tablet, and the Google Pixel Fold.

Issues fixed in the Android 14 QPR2 Beta 3.1 update

Among the notable issues addressed in this release are improvements to the Game Dashboard overlay, unlocking failures with always-on display mode and fingerprint, Quick Settings dialog height irregularities, incorrect default search engine settings after a cloud backup restore, display area update issues in accessibility settings, and audio quality degradation during calls or recording using the microphone.

The update also tackles problems related to device keyboard settings, missing translations for various languages, work profile icons not displaying for paused work apps, rendering issues with shaders, incorrect scaling of icons in picture-in-picture mode, launcher glitches for foldable devices, and unresponsiveness of the app divider for foldable devices in split-screen mode. Additionally, various issues impacting system stability, performance, connectivity, camera, and accessibility have been addressed.

Although some known problems still exist

However, Android 14 QPR2 Beta 3.1 is not without its known problems. Some users may experience unexpected reboots due to a native crash issue, and a system connectivity issue may cause call failures. Additionally, foldable or tablet devices may encounter UI navigation handle visibility problems. That is per course when it comes to beta builds, though. This is definitely not ready to be used instead of stable software, but it’s getting there.

[ad_2]

Source link