CISA & FBI released Incident Response Guide for WWS Sector

0

[ad_1]

Malicious cyber incidents, such as ransomware and unauthorized access, have affected the Water and Wastewater Sector (WWS) in the past few years. Particularly, ransomware is a common tactic cybercriminals use to target WWS utilities.

Cyber threat actors target the WWS because it is a vital component of numerous U.S. critical infrastructure sectors, such as energy, healthcare, and public health.

A collaborative Incident Response Guide (IRG) for the WWS Sector was developed by CISA, the Environmental Protection Agency (EPA), and the Federal Bureau of Investigation (FBI) to address cybersecurity challenges in the WWS Sector.

The federal roles, resources, and responsibilities for each phase of the cyber incident response (IR) lifecycle are detailed for the owners and operators of the WWS Sector in this guide.

Document

Free Webinar

Compounding the problem are zero-day vulnerabilities like the MOVEit SQLi, Zimbra XSS, and 300+ such vulnerabilities that get discovered each month. Delays in fixing these vulnerabilities lead to compliance issues, these delay can be minimized with a unique feature on AppTrana that helps you to get “Zero vulnerability report” within 72 hours.

Four Incident Response Lifecycle Phases

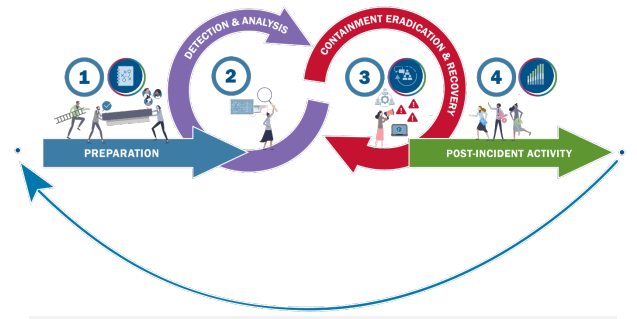
The IR lifecycle comprises four phases:

  • Preparation
  • Detection and analysis
  • Containment, eradication, and recovery
  • Post-incident activities

“The IR lifecycle provides organizations with a step-by-step framework for identifying and responding to a cyber incident. This IRG leverages the IR lifecycle framework, allowing WWS utilities to augment their own IR plans with information on federal roles, responsibilities, and resources”, CISA stated in the guide.
IR lifecycle phases
IR lifecycle phases

An organization can prevent cyber disasters and minimize their damage by being prepared, which also shortens the time it takes to resume regular operations.

The detection and analysis phase includes two key components: Accurate and timely reporting and rapid collective analysis aimed at comprehending the complete extent and implications of a cyber occurrence.

In the IR lifecycle, Containment, Eradication, and Recovery is the next stage. This phase is centered on coordinated messaging and information sharing, remediation, and mitigation assistance.

All pertinent parties must perform an in-depth examination of the occurrence and the response efforts made by responders following any cyber incident. The total of post-incident actions establishes “lessons learned.” 

The guide also mentions special agents and computer scientists with expertise in cyber incident response make up the quick-reaction Cyber Action Team (CAT). The CAT offers assistance with investigations and crucial question resolution that may speed up the progress of a case.

The CAT can deploy across the nation in a matter of hours to respond to significant incidents because of its extensive training in malware analysis, forensic investigations, and computer intrusions.

“This system guides all levels of government, nongovernmental organizations, and the private sector on how to work together to prevent, protect against, mitigate, respond to, and recover from incidents,” CISA said.

Try Kelltron’s cost-effective penetration testing services to evaluate digital systems security. Free demo available.

[ad_2]

Source link
Google changes wording for Incognito browsing in Chrome

0

[ad_1]

Users of Chrome Canary have noticed some slight changes in the wording that Google uses for Incognito mode.

Chrome Canary is mainly intended for use by developers. It’s updated nearly daily with new features, and because it can be used alongside versions of the “normal” Chrome browser (known collectively as Chrome’s “Stable channel”), it can serve for testing and development purposes. So, these developers have access to the latest features and some of them noticed a few updates in the wording about Chrome’s Incognito mode.

Chrome’s Incognito mode aims to protect your privacy from other people who use the same device. It mitigates the risk of a spouse, roommate, or anyone on a public computer spying on your browsing habits. Private browsing mode does so by stopping your browser from saving your browsing information on your computer.

Incognito mode is also sometimes used for troubleshooting, because it ignores the installed browser extensions unless you specifically allow them to run in Incognito mode.

But, although the primary function of private browsing is to locally hide your browsing activity, Incognito mode has an interesting side effect—websites also see you as a new user when you come back in Incognito mode. This can come in handy, but should not be overrated.

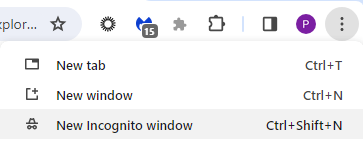
You can open Incognito mode by clicking on the three dots in the right hand upper corner (More) of the browser menu and then on New Incognito window.

Screenshot of Chrome menu to open Íncognito mode
How to open an Incognito window

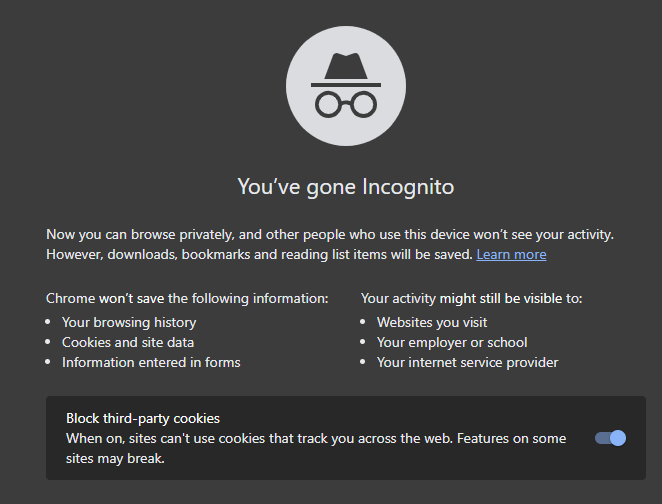
In the Stable channel build this is what you will see when you open an Incognito window.

You’ve gone Incognito

Now you can browse privately, and other people who use this device won’t see your activity. However, downloads, bookmarks and reading list items will be saved.

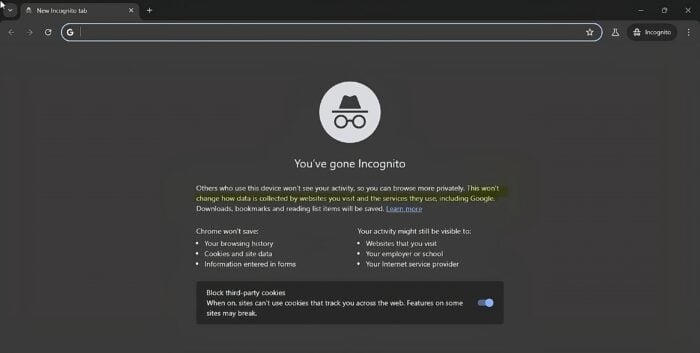
The new warning seen in Chrome Canary when you open an incognito window says:

“You’ve gone Incognito. Others who use this device won’t see your activity, so you can browse more privately. This won’t change how data is collected by websites you visit and the services they use, including Google.“

It’s clear that Google has put more emphasis on users of the same device while moving away from the websites you visit. And it’s true that Incognito mode is primarily designed to keep your information private from other users of the same computer. It isn’t designed to keep your information private from the websites you visit, although that is sometimes a side effect. We have explained this in the past, but it’s noteworthy that Google has now added that it “won’t change how data is collected by websites you visit and the services they use, including Google.”

It’s generally assumed that the changes are tied to the fact that Google has indicated that it is ready to settle a class-action lawsuit filed in 2020 over the Incognito mode. Arising in the Northern District of California, the lawsuit accused Google of continuing to “track, collect, and identify [users’] browsing data in real time” even when they had opened a new Incognito window.

The judge rejected Google’s bid for summary judgement in August of 2023, pointing out that Google never revealed to its users that data collection continued even while surfing in Incognito mode.

Apparently many users, surely not our regular readers, where not aware that Incognito mode is not an anonymous mode. Websites and services, will still be able to track you and collect your data. Enabling the Block third-party cookies setting is more helpful.


We don’t just report on privacy—we offer you the option to use it.

Privacy risks should never spread beyond a headline. Keep your online privacy yours by using Malwarebytes Privacy VPN.

[ad_2]

Source link

Exynos 2400 outperforms Snapdragon 8 Gen 3 in benchmark test

0

[ad_1]

Many people question Samsung‘s decision to use the Exynos 2400 chipset in the Galaxy S24 and Galaxy S24+. This is because of how awful previous-gen Exynos processors have been. However, if a recent benchmark test is anything to go by, the company has turned the tide this year. The new Exynos chip appears to have better performance stability than the Snapdragon 8 Gen 3 that powers the phones in some markets.

Benchmark test shows Exynos 2400 is more stable than Snapdragon 8 Gen 3

After exclusively using a Snapdragon chip in the Galaxy S23 series last year, Samsung is back to its usual dual-chip strategy. The newly launched Galaxy S24 and Galaxy S24+ ship with the Snapdragon 8 Gen 3 (the For Galaxy version with an overclocked CPU) in some markets such as the US and the Exynos 2400 in others, including Europe. The Galaxy S24 Ultra gets the overclocked Snapdragon chip globally.

Thai media outlet Beartai recently ran a 3DMark benchmark test on the Exynos-powered Galaxy S24+ and Snapdragon-powered Galaxy S24 Ultra to compare the performances. More specifically, the devices were subjected to 3DMark’s Solar Bay Stress Test. It is a 20-minute test that evaluates a device’s performance under long periods of heavy gaming workload with ray tracing and advanced graphic experiences.

The test showed that the Exynos 2400 sustained its performance better than the Snapdragon 8 Gen 3. It achieved the highest loop score of 8,905 and the lowest loop score of 5,755. A simple calculation reveals that its performance stability was 64.6%. On the other hand, the Snapdragon chip achieved the highest and lowest loop scores of 8,249 and 3,984, respectively. Its performance stability was only 48.3%.

While benchmark runs don’t always give us the complete picture, things are looking good for the Exynos 2400. The devices used for the test make its win here more impressive. The Galaxy S24 Ultra has a larger cooling system, including a bigger vapor chamber than the Galaxy S24+. This suggests Samsung has improved the thermal management capabilities of the new Exynos chip.

The FOWLP tech may have helped

The Exynos 2400 is the first Exynos processor to feature the Fan-out wafer-level packaging (FOWLP) technology. It helps boost thermal management, keeping the chip cool during prolonged resource-intensive tasks. This might have come into play during this benchmark test. Hopefully, the new Exynos chip will deliver equally brilliant performance during everyday usage and gaming. If it falls behind the Snapdragon again, Samsung might have a tough time convincing people to buy flagship Galaxy phones with Exynos chips.

Galaxy S24 Exynos 2400 Snapdragon 8 Gen 3 benchmark stability


[ad_2]

Source link

New Sophisticated NFT Airdrop Attack Steals Funds

0

[ad_1]

The allure of NFTs, those shimmering digital tokens holding unique artworks and promises of fortune, has captivated the world. 

But amidst the buzz lurks a sinister shadow: the NFT scam. 

Recently, Check Point Research exposed a sophisticated airdrop scam targeting over 100 popular NFT projects, a stark reminder that vigilance is paramount even in the digital realm.

Document

Free Webinar

Compounding the problem are zero-day vulnerabilities like the MOVEit SQLi, Zimbra XSS, and 300+ such vulnerabilities that get discovered each month. Delays in fixing these vulnerabilities lead to compliance issues, these delay can be minimized with a unique feature on AppTrana that helps you to get “Zero vulnerability report” within 72 hours.

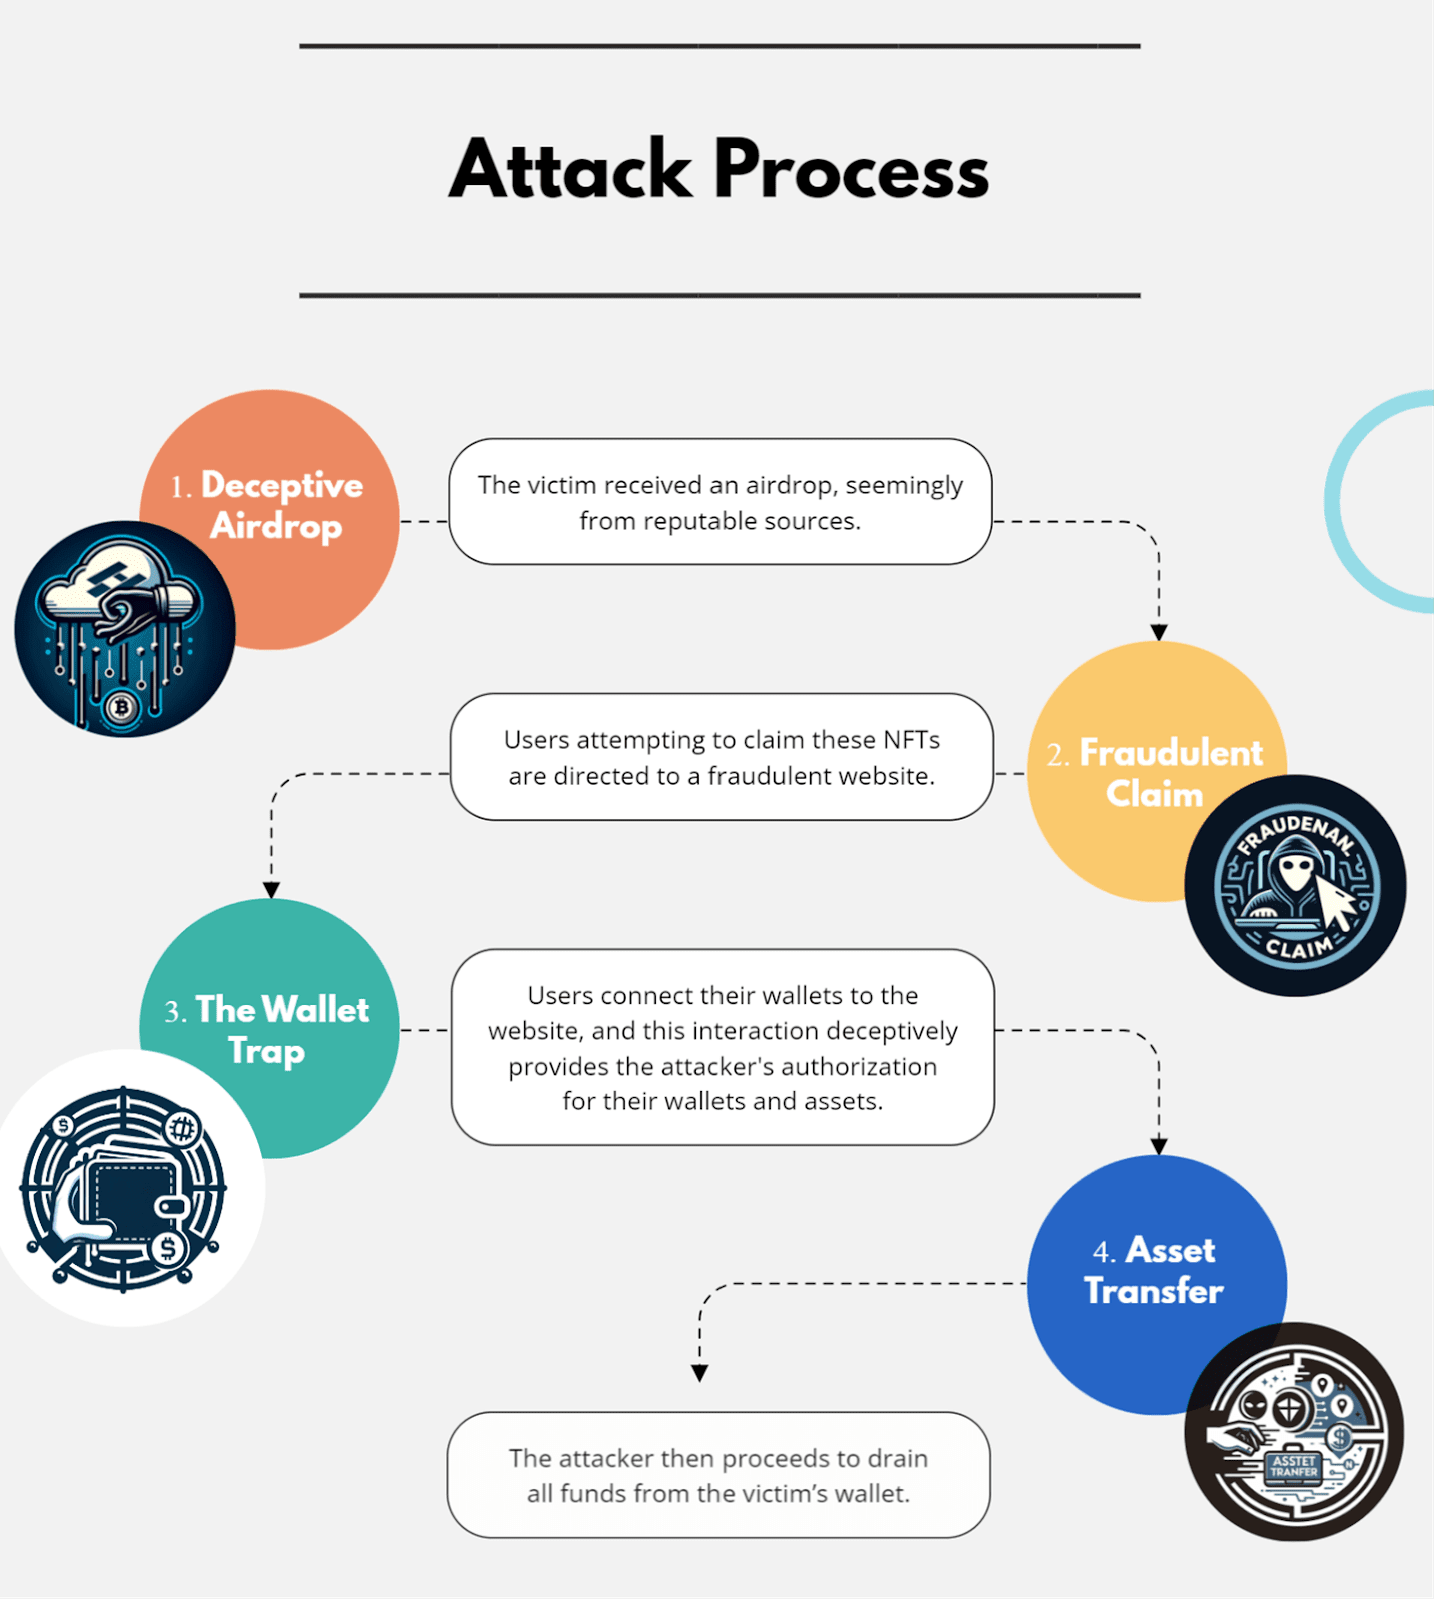
Imagine receiving an airdrop, a seemingly generous gift of NFTs, from a trusted source like Yuga Labs or Immutable X. 

This is the initial stage of the scam, where attackers exploit the trust associated with reputable entities. 

The airdrops, meticulously crafted to resemble genuine offers, entice unsuspecting victims with promises of exclusive rewards.

Sophisticated NFT Airdrop Attack
Attack Process

The Web of Lies Unfurled:

The airdrop leads to a beautifully woven web of deceit: a fraudulent website designed to mimic the aesthetics of the trusted entity. 

The interface, polished and familiar, further lulls victims into a false sense of security. This is where the trap snaps shut.

The website prompts the victim to connect their cryptocurrency wallet, ostensibly to claim the promised NFT. 

This seemingly innocuous action, mirrored in legitimate transactions, masks a sinister truth. 

Victims unknowingly grant the attackers full access by connecting their wallets and surrendering their digital treasure trove.

The scam’s sophistication extends beyond its deceptive appearance. 

The attackers wield sophisticated tools, like source spoofing, to manipulate transaction information. 

This creates the illusion that the airdrop originated from a trusted source, further blurring the lines of legitimacy.

The attackers employ a complex web of proxy contracts and unverified contract codes. 

These act as smoke and mirrors, obfuscating the true nature of the transaction and making it nearly impossible for both users and automated systems to discern the malicious intent.

A Roadmap to Safety

Heed these words:

  • Scrutinize links: Hover over them before clicking to reveal the true destination.
  • Understand smart contract interactions: Seek out resources to educate yourself about the potential risks.
  • Utilize trusted tools: Employ security scanners and transaction verifiers to analyze suspicious activity.
  • Maintain healthy skepticism: Remember, if something seems too good to be true, it probably is.

Try Kelltron’s cost-effective penetration testing services to evaluate digital systems security. Free demo available.

[ad_2]

Source link
CISA urges urgent patching of two actively exploited Citrix NetScaler vulnerabilities

0

[ad_1]

The Cybersecurity and Infrastructure Security Agency (CISA) has added two Citrix NetScaler vulnerabilities to its Known Exploited Vulnerabilities catalog, and it has set the “due date” a week after they were added.

Federal Civilian Executive Branch (FCEB) agencies are handed specific deadlines for when vulnerabilities must be dealt with. Normally, the Directive requires those agencies to remediate internet-facing vulnerabilities on its catalog within 15 days, and all others within 25 days.

The Citrix NetScaler vulnerabilities need to be patched by January 24, 2024. These issues only apply to customer-managed NetScaler ADC and NetScaler Gateway. Customers using Citrix-managed cloud services or Citrix-managed Adaptive Authentication are not impacted.

The Common Vulnerabilities and Exposures (CVE) database lists publicly disclosed computer security flaws. The CVEs that CISA has added to the catalog are:

CVE-2023-6548, an improper control of generation of code (code injection) vulnerability in NetScaler ADC and NetScaler Gateway with a CVSS score of 5.5 out of 10. It allows an attacker with access to NSIP, CLIP or SNIP with management interface to perform Authenticated (low privileged) remote code execution on the interface.

Because this vulnerability only impacts the management interface, network traffic to the appliance’s management interface should be separated, either physically or logically, from normal network traffic, and you should avoid exposing it to the internet.

CVE-2023-6549 is an improper restriction of operations within the bounds of a memory buffer in NetScaler ADC and NetScaler Gateway with a CVSS score of 8.2 out of 10. It allows unauthenticated denial of service. An attacker could exploit this vulnerability when a vulnerable appliance has been configured as a gateway (e.g. VPN, ICA Proxy, CVPN, RDP Proxy) or as a AAA virtual server.

The following supported versions of NetScaler ADC and NetScaler Gateway are affected by the vulnerabilities: 

  • NetScaler ADC and NetScaler Gateway 14.1 before 14.1-12.35
  • NetScaler ADC and NetScaler Gateway 13.1 before 13.1-51.15
  • NetScaler ADC and NetScaler Gateway 13.0 before 13.0-92.21
  • NetScaler ADC 13.1-FIPS before 13.1-37.176
  • NetScaler ADC 12.1-FIPS before 12.1-55.302
  • NetScaler ADC 12.1-NDcPP before 12.1-55.302

Note: NetScaler ADC and NetScaler Gateway version 12.1 is now End Of Life (EOL) and is vulnerable.

Citrix has also observed exploits on unpatched instances and strongly urges affected customers of NetScaler ADC and NetScaler Gateway to install the relevant updated versions as soon as possible.

A few months ago, CISA and the Federal Bureau of Investigation (FBI), along with other international agencies, warned that ransomware gangs are actively exploiting the Citrix Bleed vulnerability which was also found in Citrix NetScaler versions. This goes to show how popular these kind of vulnerabilities are among cybercriminals.


We don’t just report on vulnerabilities—we identify them, and prioritize action.

Cybersecurity risks should never spread beyond a headline. Keep vulnerabilities in tow by using ThreatDown Vulnerability and Patch Management.

[ad_2]

Source link

Titanium didn’t help the Galaxy S24 Ultra lose weight

0

[ad_1]

The Samsung Galaxy S24 Ultra is the very first smartphone from the company to use titanium. The phone comes with a titanium frame, just like the iPhone 15 Pro and iPhone 15 Pro Max. The thing is, unlike the two iPhones, the Galaxy S24 Ultra is not any lighter because of it.

Titanium didn’t help the Galaxy S24 Ultra lose weight, and that’s perfectly normal

The Galaxy S24 Ultra weighs 232 grams, while the Galaxy S23 Ultra weighs 234 grams. The difference here is only 2 grams, which is basically not noticeable. For comparison’s sake, the iPhone 15 Pro and iPhone 15 Pro Max weigh 187 grams and 221 grams, while their predecessors weigh 206 grams and 240 grams. That’s a considerable difference right there.

The battery is also the same in regards to the capacity, so… what’s the gist? Well, you have to keep in mind that the iPhone 14 Pro and iPhone 14 Pro Max used stainless steel instead of aluminum for its frame. The Galaxy S23 Ultra uses aluminum and a lighter version of aluminum at that.

So, the jump from already light aluminum to titanium is apparently not as considerable as some of you thought. A jump from stainless steel to titanium, however, sure is. I hope this clears it up, as some people seemed a bit disappointed by the Galaxy S24 Ultra weight.

The company announced its new flagship smartphone series a couple of days ago

As many of you know, Samsung announced three smartphones a couple of days ago, and one of them was the Galaxy S24 Ultra. The Galaxy S24 and Galaxy S24+ also arrived. Those two phones kept the aluminum build, however. They’re very similar to their predecessors when it comes to weight as well.

All three phones are fueled by the Snapdragon 8 Gen 3 for Galaxy in the US. In Europe, however, the Galaxy S24 and Galaxy S24+ come equipped with the Exynos 2400 instead.

All three phones have a matte glass finish on the back, and all three have seen slight design changes. The frame is completely flat on the Galaxy S24 and Galaxy S24+. The two phones also have slightly thinner bezels and slightly larger displays. The Galaxy S24 Ultra, on the other hand, now has a flat display, and its top and bottom sides are entirely flat.

[ad_2]

Source link

Older Verizon Unlimited plans are getting a $4 price hike starting March

0

[ad_1]

Pricing for some older Verizon Unlimited plans will jump up soon. According to CNET, the operator will be hiking the price of select older Unlimited Plans by $4/month per line. The company is allegedly increasing the pricing to push its customers to opt for the newer unlimited plans. These plans were originally added to the Verizon myPlan lineup in 2023.

Verizon is increasing the pricing of older Unlimited plans to get its users to switch to newer packs

As per the source, the telecom operator is trying to get its customers to switch to the newer Unlimited packs. Soon, the monthly cost of the 5G Get More, 5G Play More, 5G Do More, and 5G Start will be increased. A company spokesperson notes that the price of any of the newer Unlimited packs will “remain the same”.

The effective hike will be $4/month per line, starting from March 1st, 2024. So, the consumers still have more than a month to decide their next Unlimited plan, in case they plan to switch.

Verizon’s new Unlimited packs won’t come with included streaming services

The brand’s unlimited plans include the Unlimited Ultimate, Unlimited Plus, and Unlimited Welcome plans. These packs don’t come with bundles for streaming services or international data roaming days. The consumers have the choice to purchase a $10 add-on for the streaming service they like. These current tariffs are available at the starting cost of $30/month per line.

Verizon Myplan Unlimited

In the statement, the brand spokesperson said that with the new plans, the users “can easily move to myPlan and take advantage of the network option that works best for them, plus exclusive savings on the entertainment, shopping and experiences that matter to them, including Disney Plus, Apple One, Netflix, Max, Walmart and many others.”

Notably, AT&T also recently announced that it is raising the cost of its Unlimited packs by $0.99 per line. These packs include the Unlimited Starter, Unlimited Extra, and Unlimited Premium. It’s worth mentioning that the brand is compensating the users for the hike with extra hotspot data with these packs.

The company has already started notifying its existing consumers that the pricing of these packs will increase from March 5th. After the hike, the AT&T Unlimited packs will be available from $65.99/month for the base pack.

[ad_2]

Source link

Google’s AI chatbot Bard to arrive on Google Messages

0

[ad_1]

In the AI scene, Google plays a leading role with its advancements, like the upcoming AI-boosted Assistant with Bard. This new and improved Assistant is poised to take over from the current one on supported Android devices. And you know what? Google’s chatbot Bard might just be expanding its turf to even more applications.According to info spilled from tipster and code detective Assemble Debug (via Android Authority), it seems Bard is gearing up for action in Google Messages. The scoop is that Bard was spotted in the beta version 20240111_04_RC00 of the Messages app. Looks like users might soon start RCS chats with Bard right in Google Messages and even add Bard to group chats with other users. The shared screenshots show that Bard can help users write messages, translate languages, identify images, and delve into various interests. The chatbot studies your location and past chats to write better answers. Just a heads up, though: Google’s warning that Bard might not always hit the accuracy mark, so it’s wise to give its responses a double-check.Adding to the scoop, lines of code dug up in the beta spill the beans that you gotta be 18 to dive into the Bard experience in Google Messages. And there’s a twist: unlike your regular RCS chats, the chats you have with Bard won’t be wrapped up in end-to-end encryption. Also, Google lays it out straight, mentioning that Bard chats and the related data are set to stick around for 18 months.

What is more, Google emphasizes a crucial point: you should avoid sharing messages with Bard that you wouldn’t want a reviewer or Google to access. The description specifies that while reviewed data is detached from the user’s account, it remains stored for up to three years.

However, Google’s throwing in an option to turn off, manage, and delete your Bard Activity. If you decide to flip the Bard Activity switch off, your chats will only be saved for a short 72 hours.

As of now, the feature still does not work on Google Messages. Traces that Bard is coming to the messaging app were discovered almost a year ago, and now it appears that its integration is finally nearing completion. 

[ad_2]

Source link

Critical “PixieFail” Flaws Expose Millions of Devices to Cyberattacks

0

[ad_1]

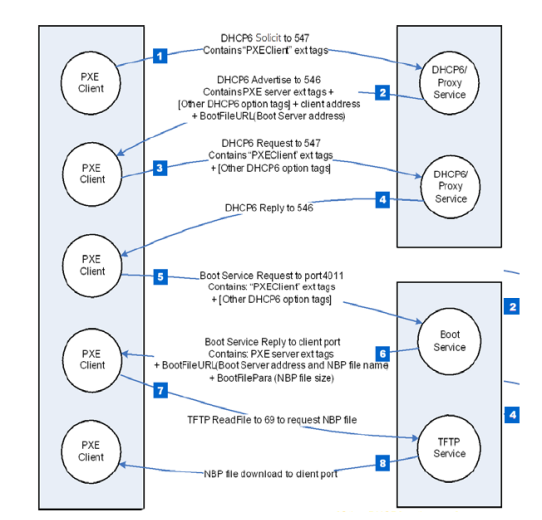
The vulnerabilities, collectively called PixieFAIL, were discovered in the network stack of EDK II, during a cursory inspection of NetworkPkg and could be exploited during the network boot process.

Quarkslab bug hunters discovered nine serious vulnerabilities in EDK II, the de-facto open-source reference implementation of the UEFI specification, which could lead to remote code execution (RCE) attacks before booting the device.

These flaws, discovered in August 2023, led to DNS and DHCP poisoning attacks, information leakage, denial of service, and data insertion attacks at the IPv4 and IPv6 layers.

The vulnerabilities, collectively called PixieFAIL, were discovered in the network stack of EDK II, during a cursory inspection of NetworkPkg and could be exploited during the network boot process.

Network boot is a common feature on enterprise computers/servers, used to load an OS image from the network at boot time. This is popular in data centers and high-performance computing environments. Given that server farms and clusters often have hundreds or thousands of compute nodes, it simplifies management by downloading and running the OS from a central set of servers.

For your information, the Preboot Execution Environment (PXE), netboot, or Pixie boot, specifies a standardized client-server solution for network computers’ booting. It was introduced by Intel in 1998 and later got incorporated into the UEFI specification. With the release of UEFI version 2.2 in 2010, IPv6-based PXE became a part of the specification. The code to PXE is included in the UEFI firmware on the motherboard or within the NIC firmware read-only memory.

EDK II is UEFI’s open-source implementation developed and maintained by Tianocore, a community of developers leveraging the project for their own UEFI implementations. It incorporates NetworkPkg, a TCP/IP stack, to enable network functionalities during the initial PXE stage, allowing remote configuration and booting of networked computers.

According to Quarkslab’s blog post, all nine issues were discovered in the TianoCore EFI Development Kit II (EDK II) and affect UEFI firmware from AMI, Intel, Insyde, and Phoenix Technologies. Threat actors can exploit them for remote code execution, denial-of-service, DNS cache poisoning, and leakage of sensitive information. The vulnerabilities’ details are as follows:

CVE-2023-45229 (CVSS rating 6.5) and CVE-2023-45230 (CVSS rating 8.3) are vulnerabilities in DHCPv6 that cause integer underflow and buffer overflow in the DHCPv6 client.

CVE-2023-45231 (CVSS rating 6.5) and CVE-2023-45232 (CVSS rating 7.5) are vulnerabilities in a DHCPv6 Advertise message, causing out-of-bounds reads and infinite loops when parsing unknown or PadN options.

CVE-2023-45233 (CVSS rating 7.5) and CVE-2023-45234 (CVSS rating 8.3) are vulnerabilities in a DHCPv6 Advertise message causing an infinite loop when parsing a PadN option in the Destination Options header and the other affecting the processing of DNS Servers and Server ID options.

CVE-2023-45235 and CVE-2023-45236 are vulnerabilities affecting DHCPv6 proxy Advertise messages, with CVSS scores of 8.3 and 5.8, respectively, causing buffer overflow and predictable TCP initial sequence numbers. The ninth flaw is CVE-2023-45237 with a CVSS score of 5.3 and is related to a weakness in the pseudorandom number generator.

The list of vulnerabilities in EDK II devices is extensive, with the most severe being buffer overflow vulnerabilities for encouraging arbitrary code execution, potentially allowing attackers initial access and lateral movement.

Quarkslab contacted impacted software vendors to address the issue. Over half a year, they worked together to develop a patch without leaking any information. On January 16, 2024, a patch for fixing PixieFAIL at once was released with a firmware update.

The company has released proof-of-concept code for the first seven vulnerabilities, enabling defenders to detect infection attempts. The CERT Coordination Center has identified Insyde, AMI, Intel, and Phoenix Technologies as affected and published guidelines to deploy the fixes.

  1. Ivanti VPN Zero-Day Flaws Fuel Widespread Cyber Attacks
  2. Hackers can hijack your Bosch Thermostat and Install Malware
  3. Malware Turns Docker Servers into Traffic Boosted Crypto Miners
  4. CISA Warns of Exploited Flaws in Chrome and Excel Parsing Library
  5. Windows Defender SmartScreen Flaw Exploited with Phemedrone Stealer


[ad_2]

Source link

Samsung brings Galaxy A15 5G & Galaxy A25 5G to the US

0

[ad_1]

Samsung has released the Galaxy A15 5G and Galaxy A25 5G in the US. The two affordable 5G smartphones are available for purchase from the company’s official website and Amazon. They are priced at $199.99 and $299.99, respectively.

Galaxy A15 5G and Galaxy A25 5G are now available in the US

Samsung unveiled the Galaxy A15 5G and Galaxy A25 5G last month. The devices first arrived in select Asian and European countries such as Vietnam and France. The Korean firm gradually expanded the availability of the phones to more markets. At the end of December, they went on sale in India. The company has now released both phones in the US.

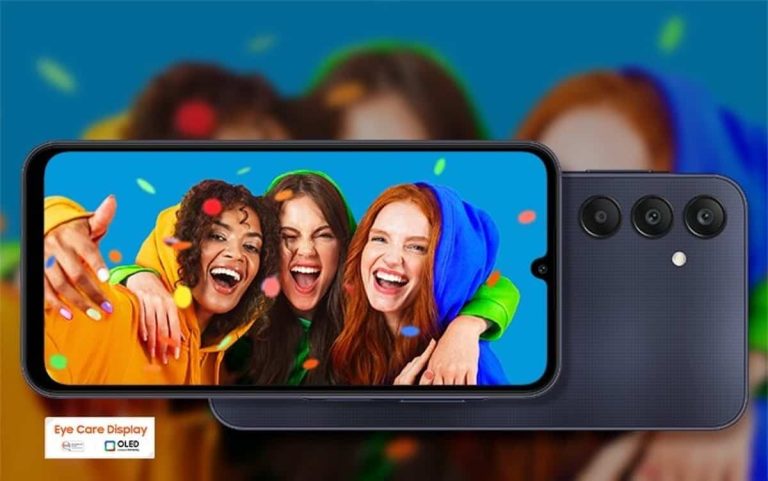
Both phones sport a 6.5-inch Super AMOLED display with an FHD+ (1080×2340 pixels) resolution and a centered U-shaped notch. However, while the Galaxy A15 5G’s display has a 90Hz refresh rate and 800 nits of peak brightness, the Galaxy A25 5G bumps things up to 120Hz and 1,000 nits. You get Vision Booster on both models for an enhanced viewing experience.

Samsung Galaxy A25 5G

These devices also have the same primary rear camera, a 50MP unit with an f/1.8 aperture. However, Samsung offers OIS (Optical Image Stabilization) on the Galaxy A25 5G only. This phone also has an 8MP ultrawide lens instead of the 5MP unit found on the Galaxy A15 5G. The 2MP macro camera and 13MP selfie camera remain unchanged across the two models.

Coming to the chipset, the Galaxy A15 5G features MediaTek’s 6nm Dimensity 6100+ SoC operating at up to 2.2GHz. The other model gets Samsung’s Exynos 1280, a 5nm chip with a peak speed of 2.4GHz—it powered the Galaxy A53 in 2022. While the devices are available in multiple storage and memory configurations in other regions, Samsung is only selling them with 8GB RAM and 128GB storage stateside.

A 5,000mAh battery with 25W charging speed

Samsung has equipped the Galaxy A15 5G and Galaxy A25 5G with a 5,000mAh battery that can be charged at up to 25W speed via a USB Type-C port. Neither model supports wireless charging. The phones boast a side-mounted capacitive fingerprint scanner and Knox security. They run Android 14-based One UI 6.0 out of the box and are eligible for four generations of Android OS upgrades (up to Android 18) and five years of security updates.

If you are looking to buy either of these affordable 5G phones from Samsung, they are available in both unlocked and carrier versions. While the price tags are $199.99 for the Galaxy A15 5G and $299.99 for the Galaxy A25 5G, you might be able to get them cheaper with trade-in bonuses and other promotional offers. Color options for the former include Blue Black and Light Blue, while the latter only comes in a Blue Black color. You can buy the phones from the links below.

Buy the Samsung Galaxy A25 5G (Amazon)

Buy the Samsung Galaxy A15 5G (Amazon)

[ad_2]

Source link