Ivanti Patches Connect Secure Zero-day Flaws Under Attack

0
[ad_1]

Ivanti has warned users of two zero-day vulnerabilities in its Connect Secure and Policy Secure gateways that have already attracted hackers’ attention. The firm confirmed active exploitation of the flaws to target a small number of customers. Since Ivanti has released appropriate mitigation, users must ensure protecting their systems by applying the mitigation until the patches arrive.

Ivanti Connect Secure Zero-Day Flaws

As disclosed through a recent advisory, Ivanti addressed two severe zero-day flaws affecting its Connect Secure and Policy Secure gateways.

Specifically, the two vulnerabilities include the following.

  • CVE-2024-21887 (CVSS 9.1): A command injection vulnerability in the web components of the two Ivanti products. Exploiting the flaw merely required an authenticated adversary o send maliciously crafted requests to execute arbitrary commands on the target appliance.
  • CVE-2023-46805 (CVSS 8.2): An authentication bypass affecting the web components of Ivanti’s ICS and Policy Secure gateways. A remote attacker could exploit the flaw to bypass control checks and access restricted resources.

Mitigation Released – Patches to Arrive Soon!

Ivanti confirmed that both vulnerabilities affect all supported versions – Version 9.x and 22.x. While the firm is yet to release stable patches for the flaws, they have released mitigation to protect vulnerable systems meanwhile.

The vulnerabilities first caught the attention of security researchers from Volexity, who observed the two flaws exploited in a chained manner. The threat actor behind the exploit, as reported, attempted to implant backdoor on the software. Volexity’s blog post shares details about these findings.

Though Ivanti has released the mitigations to prevent the exploit, Volexity explained that applying the mitigation “doesn’t remedy a past or ongoing compromise.” Nonetheless, applying the mitigations is still important to prevent a future exploit, especially for the yet safe but vulnerable devices.

The researchers also advise the users to run thorough security analyses for possible breach signs. Besides, for compromised cases, Volexity recommends rebuilding the ICS VPN appliance, resetting stored credentials and other data, and gathering logs and system snapshots for appropriate analyses. Moreover, organizations should also check for potential lateral movement on the network to detect any other compromised systems.

Let us know your thoughts in the comments.


[ad_2]
Source link
“I’ll miss him so much” Facebook scam uses BBC branding to lure victims

0
[ad_1]

Facebook scams are a constant nuisance and vary from like-farming to scams that can cost you some serious money. The latest one we found is a bit morbid.

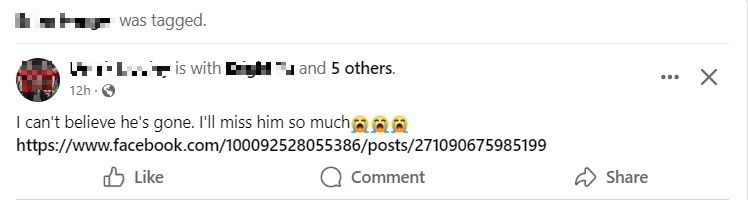
Recently, I’ve seen quite a few posts on my timeline that looked like this:

I can't believe he's gone. I'll miss him so much

Without going into details the post says:

“I can’t believe he’s gone. I’ll miss him so much”

In all the posts I’ve seen, one of my Facebook friends was tagged. When I noticed that happen to two friends that do not know each other, the post did what it was intended to do, trigger my curiosity.

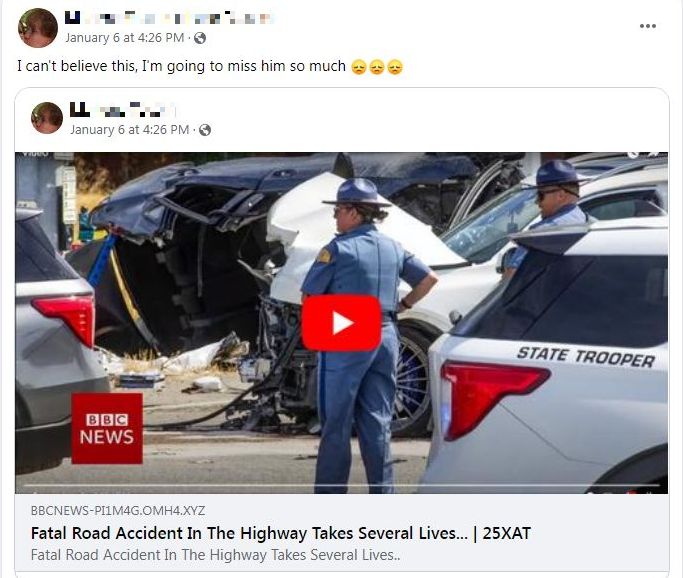
When you follow the posted link, which is a Facebook permalink to a post made by what is probably a compromised account, you’ll see a fake BBC news item about a fatal road accident. The permalink of any post on Facebook is hidden under its time stamp and can be used to share content on or outside of Facebook.

This post features a slightly different text: “I can’t believe this, I’m going to miss him so much”

I can’t believe this, I’m going to miss him so much above a fake BBC news item about a fatal road accident

The BBC news logo in the picture and the BBCNEWS part of the URL are obviously intended to gain your trust, and suggest that it’s safe to play the video.

In reality you will be redirected to the link displayed directly below the movie. We found several variations of that URL. All composed like this “BBCNEWS-{6 characters}.OMH4.XYZ”

Clicking the play button takes you through several redirects, very likely to perform fingerprinting, where sites gather information about your browser, your location, and other sites you’ve visited. The scammers do this to make sure you are redirected to a site that is likely to generate the most profit from people fitting your profile.

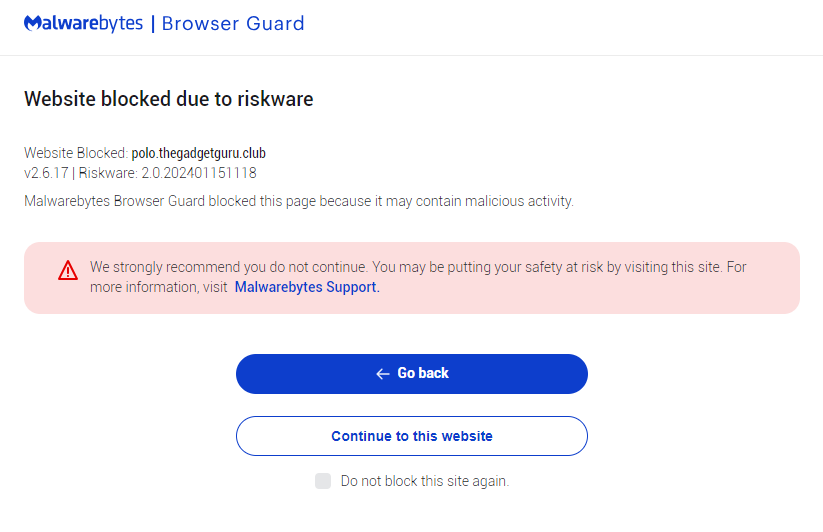
During my testing, I was not logged in on Facebook and surfing from a Dutch IP address, I ended up at polo[.]thegadgetguru[.]club which was unreachable at the time of writing. However, our archives show it’s a known source of pop-ups and has been for at least two years. These pop-ups can lead visitors to potentially unwanted programs, adware, and fraudulent sites.

It’s very likely that changing my IP address to a different location with a VPN and logging in to Facebook will change the outcome of the redirects, but I’m pretty sure none of them will be up to any good.

How to avoid Facebook scams

In this case I was able to spot the scam because it made me suspicious that two unrelated friends might be tagged in a similar post. But there are some other pointers to help you spot Facebook scams.

  • Scrutinize URLs closely. Not every scam campaign is sophisticated or difficult to spot. Start with the URL – if it’s obviously not for the website in question then step away.
  • Reach out to friends and family outside of Facebook or Instagram. If you’re not sure if a message is from the person it says it’s from, give them a call or send them a text message to check they really did send it.
  • Be wary of “free” stuff. Sure, free things are nice—but they shouldn’t cost you anything, and that includes your personal details or a small amount of money that you must pay first. If you see a giveaway doing the rounds on Facebook, go to that company’s official webpage to verify it, or give them a call.
  • Update your browser regularly. This keeps new vulnerabilities at bay, and is another layer of protection you can depend on.
  • Change your login credentials if you think your account may be compromised. And if you’ve used the same password on other sites, change them.
  • Install browser protection, like Malwarebytes Browser Guard, which can alert you to scams and other nasties in the browser.
  • If you’ve decided you’ve had it with Facebook you may like this post on how to deactivate or delete your Facebook account.

Report any posts you may find that are suspicious, scammy, illegal, or downright harmful to other Facebook users’ wellbeing. You can find this feature by clicking in the upper right hand corner of the Facebook post in question and picking either “Report post” or “Report photo”.


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.


[ad_2]
Source link

OnePlus 12 & OnePlus 12R pre-order perks revealed

0
[ad_1]

The global variant of the OnePlus 12 is right at our doorstep. The phone will become official on January 23, after launching in China last month. That being said, the OnePlus 12 pre-order perks have been revealed, at least for the EU.

The OnePlus 12 & OnePlus 12R will come with interesting pre-order perks

This information comes from OnePlus directly, as the information has been shared on a number of OnePlus websites in the EU. It seems like the users in the EU will get a different perk depending on the model of the phone they order.

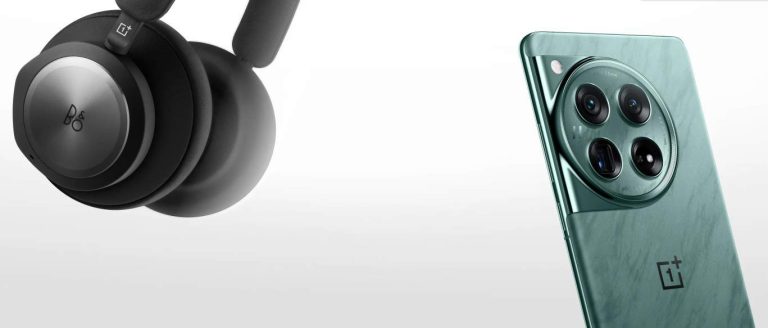
The OnePlus 12 with 16GB of RAM and 512GB of storage, which is the most powerful unit. It will bring you the Bang & Olufsen Beocom Portal headphones free of charge. Those headphones were priced at over $500/€500 when launched in 2022. They are not far from that price tag at the moment.

If you opt to get the more affordable OnePlus 12 model, the one with 12GB of RAM and 256GB of storage, you’ll also get a nice perk. OnePlus will throw in a free pair of the OnePlus Buds Pro 2. Some people prefer truly wireless earbuds either way.

If you’re interested in the OnePlus 12R, don’t fret

Those of you who are planning to get the OnePlus 12R, don’t fret. Any OnePlus 12R device that you pre-order in Europe will get you a free pair of OnePlus Buds Pro 2 too.

Do note that this offer will be limited to 48 hours, it seems. Well… at least when it comes to Bang & Olufsen headphones. We’re not sure about the earbuds, but the same rule could apply.

Another thing worth noting is that the offer may not be available in every market. OnePlus’ Croatia website, for example, doesn’t have the same offer on the table at the moment.

The launch event will kick off on January 23, at 3 PM CET / 2 PM BST / 9 AM EST / 6 AM PST, in case you’re interested.


[ad_2]
Source link

New Galaxy S24 leak details AI features, reveals more info

0
[ad_1]

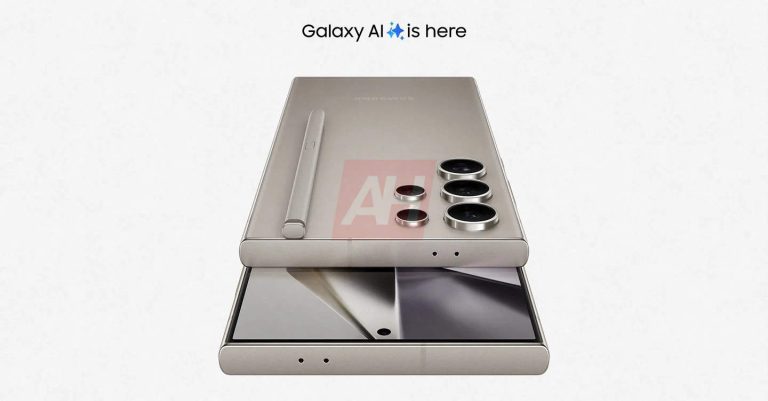
A day before the official unveiling, Samsung’s Galaxy S24 series has been subject to another major leak. Coming courtesy of reliable leakster Evan Blass, we have marketing materials highlighting some of the new features and upgrades the phones will bring to the table. Unsurprisingly, artificial intelligence (AI) is in the thick of everything.

New leak confirms Galaxy S24 AI features

Over the past few months, we have seen hundreds of leaks about the Galaxy S24, Galaxy S24+, and Galaxy S24 Ultra. The leaks suggest that AI will be an integral part of the new Samsung flagships. The company’s official teasers have been focused on the on-device AI capabilities—collectively called Galaxy AI—of the phones.

Circle to search is one of the new AI tools Samsung has developed for the Galaxy S24 series. It lets you make an internet search for anything on the screen by simply drawing a circle around it. Text, photo, or video, the tool works for whatever is displayed on the screen. You can even tap on a specific part of the selected content to pinpoint your search.

Next up, Samsung has integrated AI into its note-taking app, Samsung Notes. Dubbed Note Assist, the tool can summarize notes to highlight key points. It can even format notes for a cleaner presentation. If the note is in a foreign language, the Galaxy S24’s new AI tool can translate it.

Speaking about translation, the upcoming Samsung flagships will introduce a groundbreaking AI feature that breaks language barriers when talking over the phone. The phones can translate audio calls in real-time. If the other party is speaking in a foreign language, Live Translate will translate the audio to your language as they speak. It can even translate your response back to the original language.

The latest Galaxy S24 leak also highlights improved Nightography and other camera features. Leaks suggest the Ultra model can now record 8K videos at 5X zoom. The device gets an Aluminum frame too, while the other two models feature an enhanced Armor Aluminum frame. The entire lineup gets a display brightness boost, going up to 2,600 nits from 1,750 nits.

AI will be all over the new Samsung flagships

These are just a few of the new on-device mobile AI features Samsung will introduce tomorrow. With the room for hardware upgrades shrinking, the company is focusing on improving the Galaxy experience with AI. We will see if it has some more tricks up its sleeves that haven’t hit the Leakland yet. The Galaxy S24 launch event kicks off at 10 AM PT or 6 PM GMT. You can live stream the event on YouTube or Samsung.com.


[ad_2]
Source link

Apple might split its App Store in two to comply with EU regulations

0
[ad_1]

Since the European Union introduced the Digital Market Act (DMA), designed to address concerns regarding the influence of big tech companies, the latter are scrambling to figure out how to play by the rules. Whether they have cracked the code or not, the DMA is kicking in come March, so they have got to shake things up or face some hefty fines.Apple, one of the companies required to comply with the DMA, has not spilled the beans on exactly how it plans to follow the rules. However, according to Bloomberg’s Mark Gurman , a reputable Apple insider, the Cupertino tech giant is looking at splitting its App Store into two versions—one for the EU and another for the US and the rest of the world.

If you are living in the EU, here is the scoop: you will be able to grab apps from places other than the App Store, pay for services using outside payment processors, and enjoy a smoother connection between first-party and third-party apps and features.

The tech giant pulled out all the stops, trying different tricks to convince the EU that its App Store does not need to play by the DMA rules. It even went with the claim that it is running not one but five App Stores. But it seems like the EU is not buying it and is all set to lay down the law on Apple.

Just the other day, Margrethe Vestager, the bigwig at the European Commission for A Europe Fit for the Digital Age, had a sit-down with Apple’s head honcho Tim Cook. Reportedly, they were discussing the ongoing saga of whether Apple should give the green light to third-party alternatives to the App Store.

As mentioned earlier, Apple is keeping its plans under wraps, but stay tuned because we will probably get the lowdown in the weeks leading up to the March deadline. Odds are Apple will drop a new software update to make things tick with the App Store and any sideloading changes. Until then, and even after, if you are not in the EU, the App Store remains your go-to for installing apps on your iPhone.

Down the road, Apple might be feeling a bit lighter in the wallet due to the slowdown in cash flow from the App Store in Europe and the rise of new players who can tap into more of the iPhone’s tech. And guess what? The EU is just the kickoff. Japan is also working on a new law that would make it mandatory for Apple to allow sideloading on iOS.

It would not be surprising if other countries hop on the bandwagon, all aiming to eventually crack open the App Store, no matter where you are.


[ad_2]
Source link

Hackers Abuse GitHub to Host Malicious Infrastructure

0
[ad_1]

GitHub has become a major platform that cybercriminals use for various attack methods such as payload delivery, dead drop resolution (DDR), C2 (Command and Control) and exfiltration. T

This is because GitHub is considered legitimate traffic, which threat actors can leverage to blend in with other legitimate network traffic.

However, cyberattacks are expected to increase, and there are high possibilities of new third-party risk vectors. This requires advanced detection methods and many other things to mitigate them.

In addition, organizations are advised to invest resources in understanding the abuse of Github and code repositories, which might provide more insights into the attacks.

Document
Free Webinar

Compounding the problem are zero-day vulnerabilities like the MOVEit SQLi, Zimbra XSS, and 300+ such vulnerabilities that get discovered each month. Delays in fixing these vulnerabilities lead to compliance issues, these delay can be minimized with a unique feature on AppTrana that helps you to get “Zero vulnerability report” within 72 hours.

Technical Analysis

According to the report shared with Cyber Security News, almost all threat actors use GitHub to evade detection, reduce costs, and reduce operational overhead. However, the primary infrastructure schemes have been changed to payload delivery, DDR, full C2, and exfiltration.

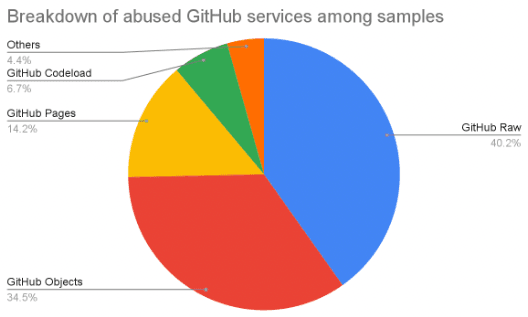
Breakdown of abused GitHub services (Source: RecordedFuture)

Among these, Payload delivery is the most prevalent scheme due to its simple implementation. Though this offers a great deal of benefits, there is a disadvantage to threat actors in using GitHub for payload delivery. The risks include unintended exposure, operational insight leakage, and many others.

Dead Drop Resolving is the second most common technique that uses the GitHub platform. DDR has a minimal risk of data removal from the platform, providing a great place for placing malicious files since GitHub-like platforms have challenges detecting files behind posted addresses or strings without further context.

Command and Control has also been found to be increasing with GitHub platforms but full implementation of C2 in GitHub is uncommon and are performed only by APTs. The reason behind is speculated to be functional constraints in using GitHub’s services.

As for exfiltration, it is also less common when compared to the other methods. This might be due to size and storage limitations, effective alternatives, cost issues, and detectability issues. 

Apart from these major usages, there are several other cases where GitHub is used for hosting phishing operations, fallback channels, infection vector serving, and many others. To date, there have been no effective solutions for mitigating the abuse of the GitHub platform.

This void space must be filled with detection strategies, usage patterns, log availability, and others.

With the increase in abuse of GitHub, network defenders need to allocate more resources to fight against this usage.

A complete report about this abuse has been published, which provides detailed information on infrastructure schemes, specific use cases of Github, and other information.

Looking for cost-effective penetration testing services? Try Kelltron’s to assess and evaluate the security posture of digital systems – Free Demo.


[ad_2]
Source link

Google denies YouTube slowdowns are linked to its ad blocker detection efforts

0
[ad_1]

Google has been in the middle of another controversy this week, as Reddit exploded with reports claiming that YouTube has started slowing video buffer with ad-block enabled.

We assumed that Google has decided to ramp up its efforts to prevent YouTube users from using ad-blockers, which seriously affects the platform monetization model.

YouTube reiterated numerous times in the past that ad-blockers not only go against its terms of service, but they also affect content creators’ earnings. Given YouTube’s stance on the matter, many assumed that the recent video slowdowns were linked with the use of ad blockers.

However, Google recently denied these reports without really offering any reasons for these video slowdowns, most likely because YouTube is not the culprit in this case. 

In a short statement for AndroidCentral, YouTube says that “recent reports users experiencing loading delays on YouTube are unrelated to our ad blocker detection efforts. Our help center offers troubleshooting tips for users experiencing issues.”

Interestingly enough, the latest versions of Adblock and Adblock Plus (5.17) seem to be the only ones that are causing performance problems, at least according to uBlock Origin developer Raymond Hill.


[ad_2]
Source link

Bitcoin casinos optimized for Android devices

0
[ad_1]

In the ever-evolving landscape of digital technology, the convergence of cryptocurrency and mobile platforms has given rise to a new frontier in online gambling. Bitcoin casinos, with their decentralized nature and enhanced privacy features, have found a symbiotic relationship with Android devices. Ergo, this article assesses the dynamic world where these two technologies intersect, exploring the advantages, considerations and future trajectory of Bitcoin casinos optimized for Android.

The rise of Bitcoin casinos: A paradigm shift in online gambling

While traditional online casinos have long been the go-to for those seeking digital entertainment and the thrill of gambling, the emergence of Bitcoin casinos signifies a paradigm shift in this industry. It introduces a new era where blockchain technology enhances security, transparency and anonymity for users, marking a progressive step forward as the world becomes increasingly digital. As the popularity of Bitcoin casinos rises, they stand as pioneers reshaping the very essence of online gambling, offering a transformative experience.

Decentralization: A key element

At the core of Bitcoin casinos lies the decentralized nature of blockchain technology. As NewsBTC says, unlike traditional casinos that rely on central servers, Bitcoin casinos operate on a peer-to-peer network. This establishes a new paradigm where trust and transparency are inherent qualities due to every transaction being recorded on an immutable public ledger. The shift towards decentralization transforms the gaming experience and redefines how we perceive the underlying structure of online casinos, stimulating an era where users have greater control and confidence in their interactions with the platform.

Android devices as catalysts: The dominance of Android in mobile

Android, as a mobile operating system, has dominated the global market, powering a vast array of smartphones and tablets; according to statistical data, Android holds a 69.74% market share in the mobile industry. Its open-source nature and versatility make it a preferred choice for users and developers alike. The synergy between Bitcoin casinos and Android devices opens up a realm of possibilities for users seeking a seamless and secure gambling experience on their mobile devices.

Optimization for mobile: A game-changer

Bitcoin casinos optimized for Android capitalize on the platform’s mobile-friendly architecture; according to Pennsylvania State University, 75.5% of online gamblers prefer mobile platforms for gaming. The optimization ensures that users can access a diverse range of games and functionalities seamlessly on their smartphones; from slot games to live dealer experiences, the integration of Bitcoin transactions into Android casinos is designed for convenience and efficiency.

Advantages of Bitcoin casinos on Android enhanced privacy and anonymity

– Enhanced privacy: One of the primary advantages of Bitcoin casinos on Android is the enhanced privacy they offer. According to industry reports, significantly more online gamblers prioritize privacy when choosing a gambling platform. Traditional payment methods often require users to disclose personal and financial information; Bitcoin transactions, on the other hand, are pseudonymous, providing users with a higher level of privacy and anonymity in their gambling activities.
– Global accessibility and inclusivity: Bitcoin operates on a global scale without being bound by traditional banking systems. According to global usage data, the use of Bitcoin in online gambling jumped twofold in 2021 – a 178% increase – promoting inclusivity in the world of online gambling.
– Reduced transaction costs: The use of Bitcoin in Android casinos often translates to reduced transaction costs; according to financial analysts, Bitcoin transactions typically have lower fees compared to traditional payment methods, allowing users to retain a larger portion of their winnings.
– Considerations for user volatility in Bitcoin price: Although Bitcoin offers advantages in privacy and reduced transaction costs, users must navigate the volatility in Bitcoin prices. According to market trends, the value of Bitcoin can experience significant fluctuations, impacting the value of one’s winnings or losses.

Security measures and responsible gambling

As with any online activity involving financial transactions, security is paramount; according to cybersecurity reports, online gamblers are increasingly prioritizing security features when choosing a gambling platform. Users should choose Bitcoin casinos on Android that implement robust security measures, including encryption protocols and two-factor authentication. Additionally, practicing responsible gambling habits remains crucial to ensure a positive and sustainable gaming experience.

The future trajectory integration of emerging technologies

The future of Bitcoin casinos optimized for Android is likely to witness further integration of emerging technologies. According to tech forecasts, the integration of augmented reality (AR) and virtual reality (VR) may enhance the immersive gaming experience on Android devices, potentially unlocking a market projected to generate USD 454.73 Billion by 2030. Blockchain advancements could also lead to innovations in provably fair gaming, reinforcing trust between players and casinos while contributing to the overall economic impact of this evolving industry.

Regulatory landscape and mainstream acceptance

The regulatory landscape surrounding Bitcoin casinos is evolving, with authorities adapting to the growing popularity of cryptocurrency. Based on the latest regulatory updates, a substantial number of jurisdictions are actively working on establishing regulatory frameworks for cryptocurrency gambling. As the regulatory frameworks become clearer, Bitcoin casinos on Android may witness heightened mainstream acceptance. This could result in a broader adoption and seamless integration within the online gambling industry at large.

Conclusion

The intersection of Bitcoin casinos and Android devices represents a dynamic synergy that unlocks a future of possibilities in online gambling. The decentralized and transparent nature of Bitcoin aligns with the global accessibility and versatility of Android, offering users a unique and secure gaming experience. As the landscape continues to evolve, considerations around security, responsible gambling and the integration of emerging technologies will shape the trajectory of Bitcoin casinos optimized for Android. Users navigating this landscape should approach it with a balance of enthusiasm and informed decision-making, unlocking the potential for an innovative and enjoyable online gambling experience.


[ad_2]
Source link

Microsoft formally introduces Copilot for iOS and Android

0
[ad_1]

Microsoft has been talking about Copilot, its AI companions, for a few months now. Today, the company formally announced that it’s bringing the “full power” of Copilot to more people and businesses.

Although the basic version of the AI companion is free to use, Microsoft introduced today a paid version, Copilot Pro. According to the Redmond-based company, this is a new subscription the offers the most advanced features and capabilities of Copilot to those looking for that kind of experience.

Individuals, as well as businesses, interested in getting Copilot Pro should know that it costs $20 per month.

Those looking for a free experience can explore Microsoft’s Copilot offering, which has been updated with additional improvements and new features. For example, new Copilot GPTs are now available for users looking to customize the behavior of Microsoft Copilot on a topic they’re interested in.

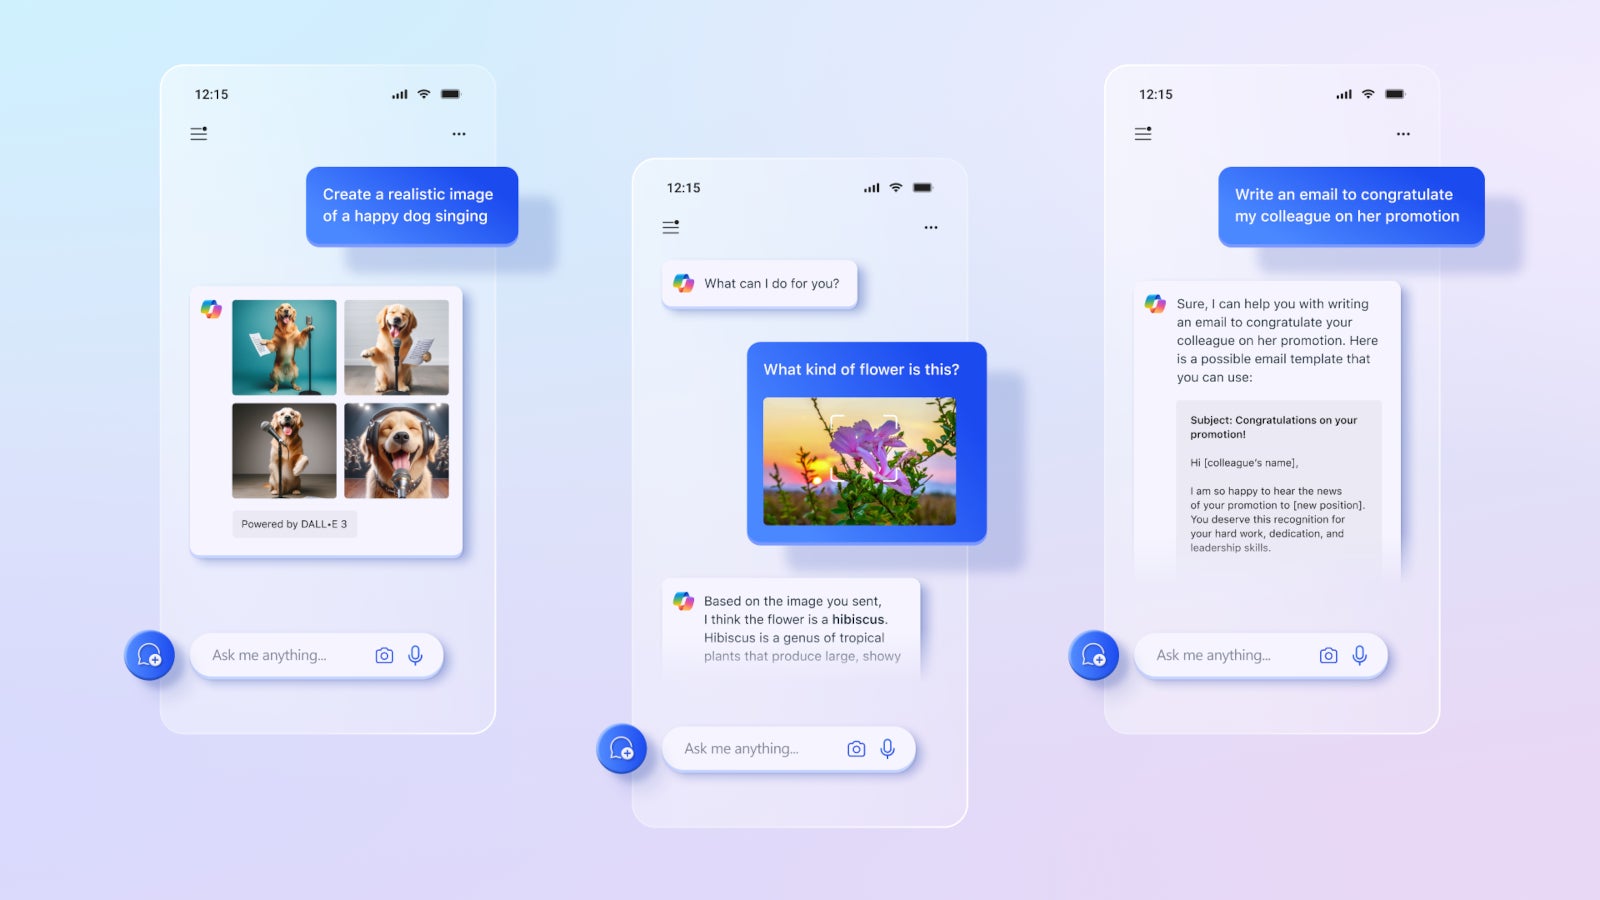
Also, the Copilot mobile app is now available for Android and iOS. This is available for free and can be downloaded from the Google Play Store or the Apple App Store. The mobile app offers the same capabilities of Copilot on PC, including access to GPT-4, Dall-E 3 image creation, and the ability to use images from a phone when chatting with Copilot.

Last but not least, Microsoft revealed that it has decided to add Copilot to the Microsoft 365 mobile app for Android and iOS for individuals with a Microsoft account. While this isn’t available right now, the company confirmed that it will roll out the new feature over the next month.


[ad_2]
Source link

Mastermind Hacker Behind $2 Million Crypto Scam Arrested

0
[ad_1]

The 29-year-old man was arrested in Mykolaiv, Ukraine, for using hacked accounts to create 1 million virtual servers to illegally mine cryptocurrency. It is estimated that the suspect has mined cryptocurrency worth over USD 2 million (or EUR 1.8 million).

The person responsible for the extensive cryptojacking operation was identified and located during several months of intense collaboration between Ukrainian police, Europol, and a cloud provider.

Malicious actors obtain unauthorized access to cloud computing infrastructure and exploit its computational capacity to mine cryptocurrencies in a cloud environment, known as “crypto-jacking.”

Criminals can avoid paying for the required servers and power, which usually exceed the profits, by stealing cloud resources to mine cryptocurrency. The holders of the compromised accounts are faced with enormous cloud costs.

Mastermind Behind Sophisticated Cryptojacking Scheme

According to Europol, the suspect has been identified to be the “mastermind behind a sophisticated cryptojacking scheme”.

The individual compromised the systems of one of the biggest e-commerce organizations globally, according to a report released by the Ukrainian cyber police.

Document
Free Webinar

Compounding the problem are zero-day vulnerabilities like the MOVEit SQLi, Zimbra XSS, and 300+ such vulnerabilities that get discovered each month. Delays in fixing these vulnerabilities lead to compliance issues, these delay can be minimized with a unique feature on AppTrana that helps you to get “Zero vulnerability report” within 72 hours.

The attack began in 2021; initially, 1,500 accounts of the subsidiary company were “hacked” by the hacker. The attacker accomplished this by using self-developed software for automatic password selection – the so-called brute force.

The hacker obtained access to the service’s management by using compromised accounts. Subsequently, the attacker developed a computer virus miner for mining cryptocurrencies, which covertly compromised the company’s server infrastructure.

He built over a million virtual computers to guarantee the malicious software was executed. The individual withdrew about two million US dollars in cryptocurrency to controlled electronic wallets over more than two years of illicit conduct, equivalent to more than 75 million hryvnias.

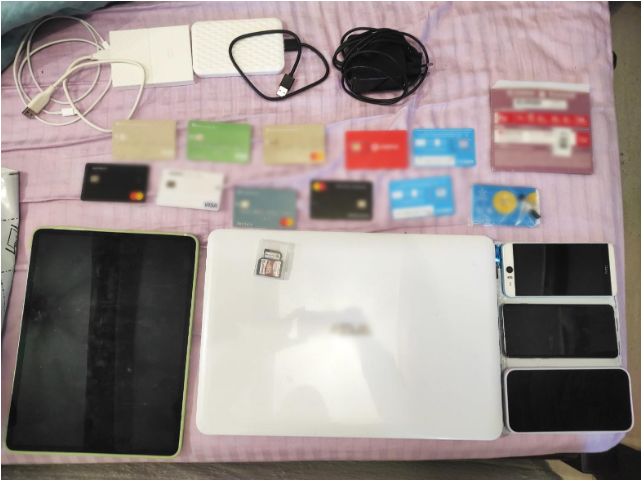
Computer equipment, bank and SIM cards, electronic media, and other evidence seized (Source: cyberpolice.gov.ua)

Protect Oneself from Cloud Cryptojacking

  • Use strong access controls to prevent unauthorized access to cloud resources.
  • Continuously monitor cloud environments for suspicious activities, unauthorized access, and unexpected resource utilization.
  • Keep all cloud resources, including virtual machines and containers, updated 
  • Use security services and tools provided by cloud service providers to enhance security.

Looking for cost-effective penetration testing services? Try Kelltron’s to assess and evaluate the security posture of digital systems – Free Demo.


[ad_2]
Source link