Google Play adopts a new approach to real-money gaming apps

0
[ad_1]

After settling for $700 Million in a Play Store antitrust case back in December, Google moves on to accommodate the growing demand for real-money gaming (RMG) apps. In this regard, Google Play has announced a significant policy shift, signaling a broader acceptance of this genre on its platform. This shift, initiated in 2021, saw the onboarding of a wider range of RMG apps in markets with existing licensing frameworks. Now, based on successful pilot programs and positive feedback, Google Play will support an even wider array of RMG operators and game types, extending opportunities to developers globally.

The initial pilots in India, focusing on Rummy and Daily Fantasy Sports (DFS), yielded insights that have influenced Google Play’s decision to broaden its support for RMG apps. Beginning in June, developers in India, Mexico, and Brazil will have the opportunity to offer a more extensive variety of RMG experiences to users, with plans for further expansion into additional countries in the future.

Google Play to support more RMG apps this year, including game types and operators not covered by an existing licensing framework

Developers participating in the Google Play Pilot Program for RMG apps in India will benefit from an extended grace period until June 30, 2024. Following this period, developers can continue to distribute RMG apps, beyond DFS and Rummy, in compliance with local laws and the updated Google Play policy. Similarly, the pilot program for DFS in Mexico will conclude on June 30, 2024, allowing developers to broaden their offerings to Mexican users within the bounds of legal and policy requirements.

While opening up opportunities for developers, Google Play emphasizes that user safety remains a top priority. Existing developer policies supporting user safety, including age-gating and geo-gating to limit RMG experiences to adults and legal jurisdictions, will remain unchanged. Google Play will also continue its efforts toward user safety and transparency through expanded developer verification mechanisms.

As part of the policy update, Google Play will evolve its service fee model for RMG to reflect the value it provides and sustain the Android and Play ecosystems. Collaborating closely with developers, Google Play aims to ensure that the new approach aligns with the unique economics and various earning models within the RMG industry.

Further details on the updated policy and expansion plans are expected to be shared in the coming months, offering developers a clear roadmap for their involvement in the evolving world of real-money gaming on Google Play.


[ad_2]
Source link
WhatsApp’s text formatting tools finally show up on the Android beta

0
[ad_1]

We all know how it goes with new mobile apps; they land on iOS first, then they hit Android. That’s the case with the text formatting tools in WhatsApp. The feature has been in testing for the iOS beta for a while. However, the WhatsApp text formatting tools have finally made it to the Android beta.

At this point, we pretty much know what these tools look like. Looking at the screenshot below, we see that these tools consist of a quote block, a code block, and two types of bullet points. These will add a different visual flare to your WhatsApp messages. They can come in handy if you are typing out a long and extended message with a list of items.

Whatsapp formatting tools

At this point, we’re not certain when this new update will make it to the public, as it’s still in beta testing. It seems likely that this will make it to the stable release, but since it is still in beta testing, there’s always the chance that there will be some changes before the final release. You’ll have to just stay tuned to see when the company launches the feature.

The WhatsApp formatting tools were finally spotted on Android

WhatsApp beta users on Android have been waiting to get their hands on this feature for a while. We first saw these text formatting tools months ago, but it was only for those using the iOS beta. Now, Android users can try this feature out.

It’s important to note that this feature is not available to all Android beta users. WhatsApp is testing this out on a limited selection of users, so there’s a chance that you won’t see it even if you have the latest version installed.

The version in question is 2.24.2.9. So, if you’re a beta tester, check to see if you have that build number. If you don’t have it installed, see if you have an update available.


[ad_2]
Source link

Apple Vision Pro is anticipated to sell out quickly after February 2 launch

0
[ad_1]

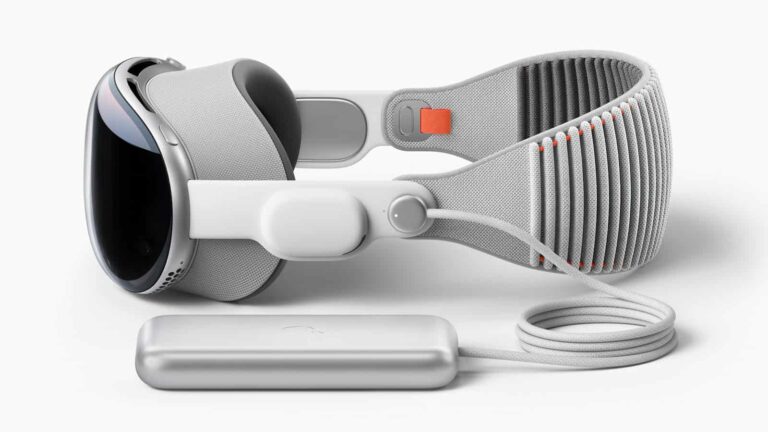
Pre-orders for the Apple Vision Pro will open from January 19. This cutting-edge augmented reality (AR) headset will officially hit the market on February 2. According to TF International Securities analyst Ming-Chi Kuo, the initial shipments of the Apple Vision Pro will be limited, ranging between 60,000 and 80,000 units. Despite this relatively small quantity, industry experts predict a rapid sell-out due to groundbreaking technology innovations and an unparalleled user experience.

Ming-Chi Kuo emphasizes that the hardware specifications and software of the Apple Vision Pro surpass industry standards. The analyst believes that the hefty $3,499 price tag will not deter consumers from acquiring this AR headset. Instead, Kuo suggests that it’s the revolutionary technology and user experience that will drive the rapid depletion of the initial batch. Apple, a company known for its diversified revenue streams, sees the first release of the Apple Vision Pro as a pilot launch, gauging market response to this novel product.

Kuo predicts that Apple will ship around 500,000 units of the Vision Pro in 2024

Although the initial shipment is relatively small, generating an estimated $279.92 million, Apple will likely capitalize on accessory sales. In addition to the AR headset, the company plans to offer prescription lenses priced between $99 and $149. This additional revenue stream underscores Apple’s strategic approach to expanding its market presence in the AR domain.

Looking ahead, Kuo predicts that the company will ship around 500,000 units of the Apple Vision Pro in 2024. Furthermore, he anticipates a prolonged lifespan for this model, with its successor not entering mass production until 2027.

Amidst these projections, rumors circulate about Apple developing a more affordable alternative set for a potential launch in 2025. This lower-cost option may differentiate itself by incorporating an iPhone chipset rather than a Mac one, accompanied by a display that, while inferior, could make AR technology more accessible to a broader consumer base.

In conclusion, the imminent release of the Apple Vision Pro has generated significant excitement in the tech community. With limited initial stock and a high price tag, the success of this AR headset hinges on Apple’s commitment to groundbreaking technology and the overall user experience, as enthusiasts eagerly await the opportunity to explore the possibilities of augmented reality.


[ad_2]
Source link

OpenAI opens its GPT Store, a place to buy customized versions of ChatGPT

0
[ad_1]

Right now, when you use chat CPT, you’re pretty much confined to one version of the chatbot. If you want something specialized, you have to go to other sources. However, OpenAI is looking to change that by introducing the GPT Store. This is a place where you can buy different customized versions of ChatGPT to suit your specific needs.

You’re able to customize ChatGPT to an extent by using Custom Instructions. This lets you tell ChatGPT a bit about yourself and why you’re using the platform. This way, it will have the context needed to generate content based on what you need. So, this is one way you can customize ChatGPT for your preferences.

OpenAI unveils the GPT Store

ChatGPT is smart; it’s a virtual Jack of all trades. However, what if you need a jack of one trade? Well, this is where the OpenAI GPT Store comes in. The company announced this Wednesday. Basically, it’s a digital storefront where you can buy customized versions of ChatGPT.

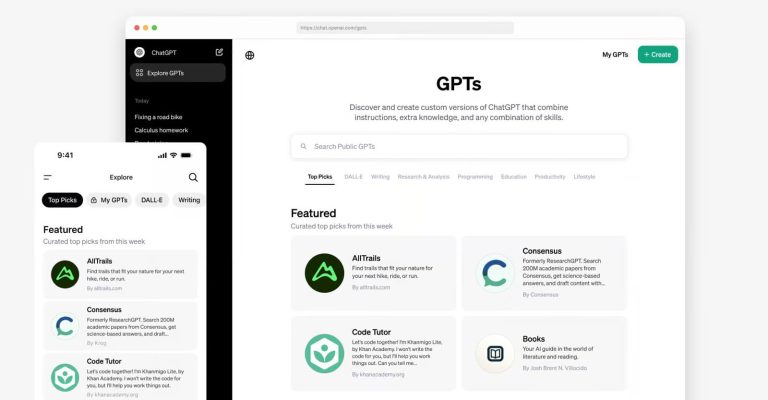
There are different GPTs like ones customized for generating stories, teaching you how to code, analyzing text, scanning PDF files, Etc. Think of it like an app store for different AI chatbots.

Right now, there are dozens of GPTs that you can access, and they’re all separated into different categories. There are bots that center around image generation, writing, productivity, research analysis, programming, education, and lifestyle. There are also a fair amount of GPTs crafted by the ChatGPT team at OpenAI.

These are user-created

This seems to be a pretty open market, as you’re able to post your own GPTs to the store. So, if you’ve built your own GPT, you can easily post it to the store. Eventually, creators will be able to earn from the GPS that they built.  OpenAI is going to open a GPT Builder Revenue program. Initially, it’ll be available for users in the U.S. So, it seems like OpenAI will take a cut of the revenue that you get from purchases, and give the rest to you.

Who can buy GPTs?

It seems weird that you have to spend money in order to spend more money, but that seems to be the way things are at the moment. In order to access the GPT store, you need to have a ChatGPT Plus, Enterprise, or Team subscription. These are all paid accounts, so you won’t be able to access the GPTs if you’re on the free plan.

If you have the proper subscription, you can go to the official GPT Store and explore the GPTs that you want to purchase. Once you purchase it, you’ll be able to access it right from the ChatGPT screen.


[ad_2]
Source link

FCC wants cars to make life harder for stalkers

0
[ad_1]

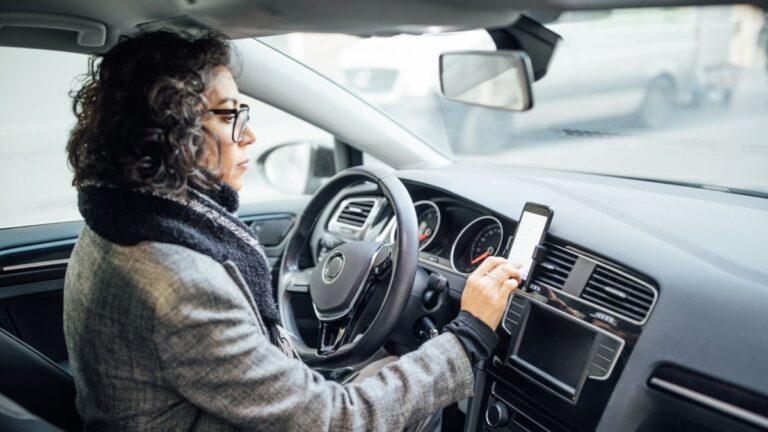
Most new model cars are not just cars anymore. With multiple digital systems, vehicles are increasingly plugged into web applications and digital processes. Some of them are basically smartphones on wheels.

Even if we assume these new features were all created with your convenience in mind, some of them can have some adverse effects on your privacy, and sometimes even your safety.

Addressing the use of connected cars to stalk, intimidate, and harass survivors of domestic violence, the Federal communications Commission (FCC) has issued a press release calling on carmakers and wireless companies to help ensure the independence and safety of domestic violence survivors.

Chairwoman Jessica Rosenworcel of the FCC said:

“No survivor of domestic violence and abuse should have to choose between giving up their car and allowing themselves to be stalked and harmed by those who can access its data and connectivity.”

We have previously talked about cars spying on you, and the poor privacy policies that allow manufacturers to sell the data they gather for targeted advertising. We have also written about a federal judge that ruled it’s fine for car makers to intercept your text messages. But those are privacy concerns. Valid and serious, but on a different level from running the risk of being harassed by a jealous ex.

For readers focused on the privacy issues of connected cars, we can recommend the Mozilla report It’s Official: Cars Are the Worst Product Category We Have Ever Reviewed for Privacy. And when you are parting with a car in the US, you may want to look at the Privacy4Cars app that can provide a Vehicle Privacy Report and claims to be able to delete your data. You will need your Vehicle Identification Number (VIN).

The FCC also asked wireless service providers (AT&T, T-Mobile and Verizon) to describe their partnerships with car manufacturers, seeking information on how the wireless providers work with them and what their policies are for handling geolocation data provided by car manufacturers.

The FCC press release includes statistics showing that more than 12 million people each year are the victims of rape, physical violence, and stalking.

Tips to keep a stalker from tracking your car

Not all cars offer these options, and the tips may not apply to your situation, but here are some general tips for people that are afraid they are the target of a stalker:

  • Use the navigation app on your phone, rather than the one built into your car.
  • Do not store places you visit regularly in the car’s navigation.
  • Consider using a VPN when you connect to your car’s hotspot.
  • Find out which devices can access the car or its location data by using any “remote access” apps for the car and remove the devices that are not under your control.
  • Familiarize yourself with the car manufacturer’s privacy policy so you know where your data might be sent. To give you an idea, data might end up with advertisers, law enforcement, service providers, the car manufacturer and its dealers, tech giants like Apple, Google, and Amazon, connected service providers, and government agencies.
  • Keep the software updated to make sure your car is equipped with the latest protection against potential intrusions.
  • If the suspected stalker has been near your vehicle, inspect it thoroughly for trackers and other unfamiliar hardware.
  • Try not to travel alone and always park in a well-lit, busy area if you are concerned about your physical safety.
  • If you have a dashcam that uses cloud storage, check who has access to the images. They can be used to track your movements.

We don’t just report on privacy—we offer you the option to use it.

Privacy risks should never spread beyond a headline. Keep your online privacy yours by using Malwarebytes Privacy VPN.


[ad_2]
Source link

Texas School Safety Software Data Leak Endangers Student Safety

0
[ad_1]

The data leak occurred due to a misconfigured database at Raptor Technologies, a Texas-based school safety software provider.

A data leak involving Raptor Technologies, a Texas-based school safety software provider, exposed millions of sensitive records about students, parents, and staff.

The leak, discovered by cybersecurity researcher Jeremiah Fowler, exposed personal information, incident response plans, infrastructure challenges, and documents about at-risk students, raising concerns about student privacy and school safety. The leak exposed around 4,024,001 records, exposing students to numerous security risks.

“I reviewed a limited sample of documents and log records that contained what appeared to be sensitive information related to students, teachers, parents, and school safety plans or procedures,” said Fowler.

I immediately sent a responsible disclosure notice and received confirmation that indeed the data belonged to Raptor Technologies,” Fowler wrote in the blog post published by VPNMentor on January 11th, 2024.

Part of the exposed records were school incident response plans, classroom layouts, infrastructure challenges, background check system details, and at-risk student documents, including their “personal and medical conditions, any mental health or legal problems they might be having, and the threats they pose to the school.”

In addition, it contained court-ordered protection orders, divorce decrees, and monthly drills. It also included scanned PDF files and images of legal documents. In summary, Fawler managed to analyse a treasure trove of records including the following:

  1. Testing documents: 1,326 files
  2. Testing logs: 332,409 / 23 GB
  3. Staging documents: 7,900 files
  4. Staging logs: 1,002,394 / 25 GB
  5. Production documents: 81,511 files
  6. Production logs: 2,598,461 blobs / 779 GB

Raptor Technologies secured the database and restricted public access. The duration of the exposure and potentially malicious access remains unknown, as only an internal forensic audit could identify potential threats.

It is worth noting that Raptor Technologies provides a visitor management system for schools to track and screen visitors, volunteers, and contractors, ensuring they are not on sex offender registries or watchlists. The software is used by over 60,000 schools worldwide, including 5,300 U.S. districts. The exposure could potentially impact nearly 40% of American schools.

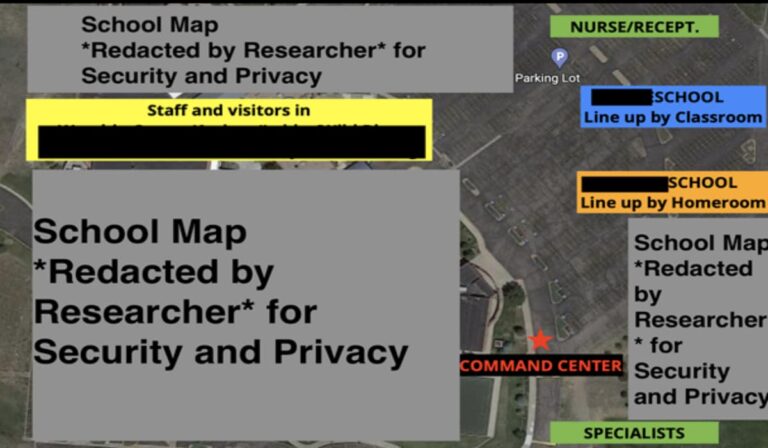
The unprotected database exposed sensitive data such as school maps, camera locations, security vulnerabilities, meeting points, and emergency response plans. These could have real-world consequences if accessed by cybercriminals. Court records contained restraining orders, criminal offences, divorce agreements, and personal information, increasing the risk of identity theft or financial crimes. 

Moreover, health records revealed student health forms, compromising privacy and confidentiality. Incident reports and safety drill summary reports contained students’ names and detailed at-risk behaviour, which can threaten their well-being later in life. School maps identified classroom locations, room numbers, evacuation routes, and camera locations, posing additional privacy risks.

Fowler recommends proactive cybersecurity measures for schools and data management companies, including restricting access, conducting regular assessments, and encrypting sensitive information.

  1. 900 U.S. Schools Hit by MOVEit Hack, Exposing Student Data
  2. Schools Are the Most Targeted Industry by Ransomware Gangs
  3. Conti ransomware gang demanded $40m from US school district
  4. Data Leak Exposes 1.5B Real Estate Records, Including Kylie Jenner
  5. 38 million records exposed in Microsoft Power apps misconfiguration

[ad_2]
Source link

Joomla! vulnerability is being actively exploited

0
[ad_1]

The Cybersecurity and Infrastructure Security Agency (CISA) has added a vulnerability for the Joomla! Content Management System (CMS) to its Known Exploited Vulnerabilities Catalog, based on evidence of active exploitation.

This means that Federal Civilian Executive Branch (FCEB) agencies need to remediate this vulnerability by January 29, 2024 in order to protect their devices against active threats.

Joomla! is an open-source CMS that’s been around since 2005, and has been one of the most popular CMS platforms by market share for much of that time. Many companies, from small outfits to large enterprises, use a CMS in some form to manage their websites. There are lots of advantages to using a popular CMS, but if you do you need to keep an eye out for updates.

Take for example the vulnerability that has been added to the CISA catalog: CVE-2023-23752 was reported, and a fix was created in February 2023. But here we are, active exploitation is upon us.

The vulnerability allows a successful attacker to access an application programming interface (API) through which they can obtain Joomla-related configuration information. The attacker has to construct specially crafted requests, which can eventually lead to the disclosure of sensitive information.

The vulnerability is the result of an improper access check that allows unauthorized access to webservice endpoints that exist in Joomla! versions 4.0.0-4.2.7.

If the database is exposed publicly, the attacker can change the Joomla! Super User’s password. After which the attacker can log in to the administrative web interface and modify a Joomla! template to include a web shell, or install a malicious plugin, giving themselves the ability execute code remotely.

But even if the database is not exposed publicly, exploitation can be used to get the Joomla! user database (usernames, emails, assigned group). This could open up options for credential stuffing. Credential stuffing is a special type of password attack that exploits password reuse by using username and password combinations found on one service to log in to other, unrelated services.

Users are advised to upgrade their CMS to version 4.2.8 or later. The latest version (5.0.1 at the moment of writing) and upgrade packages can be downloaded here.

Secure your CMS

There are a few obvious and easy-to-remember rules to keep in mind if you want to use a CMS without compromising your security. They are as follows:

  • Choose a CMS that actively looks for and fixes security vulnerabilities.
  • If it has a mailing list for informing users about patches, join it.
  • Enable automatic updates if the CMS supports them.
  • Use the fewest number of plugins you can, and do your due diligence on the ones you use.
  • Keep track of the changes made to your site and its source code.
  • Secure accounts with two-factor authentication (2FA).
  • Give users the minimum access rights they need to do their job.
  • Limit file uploads to exclude code and executable files, and monitor them closely.
  • Use a Web Application Firewall (WAF).

If your CMS is hosted on your own servers, be aware of the dangers that this setup brings and keep it separated from other parts of your network.


We don’t just report on vulnerabilities—we identify them, and prioritize action.

Cybersecurity risks should never spread beyond a headline. Keep vulnerabilities in tow by using ThreatDown Vulnerability and Patch Management.


[ad_2]
Source link

Galaxy S24 Ultra leaked in short hands-on video before launch

0
[ad_1]

After countless renders and a few real-life images, we now have a leaked hands-on video of the Galaxy S24 Ultra. A short video posted on X shows the upcoming Samsung flagship’s flat display with AOD (always-on display) enabled. The device launches on January 17 alongside the Galaxy S24 and Galaxy S24+.

Leaked video shows Galaxy S24 Ultra’s flat display

The leaked hands-on video of the Galaxy S24 Ultra was originally posted by noted tipster Ice Universe. The video was later deleted—it was likely a DMCA takedown from Samsung. However, a few other X users re-uploaded it. Unless Samsung strikes again, you can watch it here or a little below in this article.

According to Ice Universe, the video came from a protective film manufacturer. Someone at the firm recorded the video before and after applying the protective film on the Galaxy S24 Ultra and leaked it online. You can see an additional layer of glass on top of the phone’s display toward the end of the video.

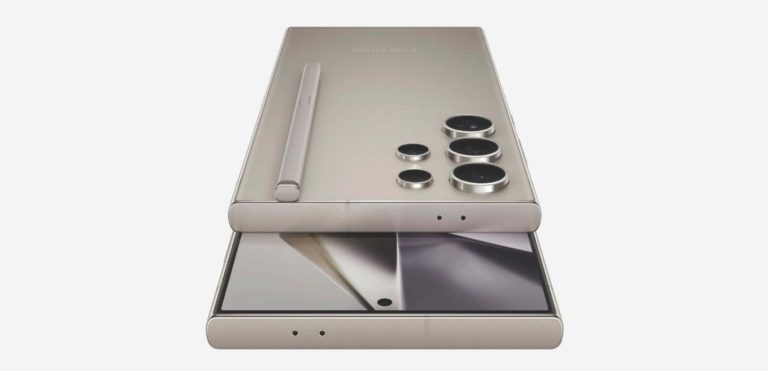
This leak doesn’t reveal anything that we don’t already know about the new Samsung flagship. The device sports a flat display, a major design change over the Galaxy S23 Ultra’s curved display. The new model also switches from an Aluminum frame to a Titanium frame. The unit seen in the video appears to be the violet color variant. The Galaxy S24 Ultra will also come in Gray, Black, and Yellow colors.

The other two models will also be available in the same four colors but with an Aluminum frame. As usual, Samsung will offer a few extra colorways exclusively through its official website. It always does that and is already teasing the same for the upcoming flagship lineup. Green, Blue, and Orange could be the three exclusive color options for the Galaxy S24 Ultra.

The new Samsung flagships debut in less than a week

Samsung has already confirmed that the Galaxy S24 lineup will go official on January 17, i.e. the coming Wednesday. The launch event, aka Galaxy Unpacked, will take place in San Jose and will be streamed live on its official website and YouTube channel. The company will open pre-orders for the phones immediately after launch. It will also open temporary Galaxy Experience Spaces in several cities around the world to let fans try the devices in person before buying them. Just a few more days to go now before the official unveiling.


[ad_2]
Source link

WordPress Plugin Flaw Exposes 300,000+ to Hack Attacks

0
[ad_1]

Hackers target vulnerable WordPress plugins as they provide a potential entry point to exploit website security weaknesses. 

These plugins often have outdated code or known vulnerabilities, which make them attractive targets for malicious actors seeking:-

  • Unauthorized access to the websites
  • To inject malicious code into websites

Recently, on December 14th, 2023, during the Bug Bounty Program of Wordfence, which is dubbed “Holiday Bug Extravaganza,” the following cybersecurity researchers reported an “Authorization Bypass” vulnerability in “POST SMTP Mailer.” 

  • Ulyses Saicha
  • Sean Murphy 

This is a WordPress plugin with more than 300,000 active installations, and successfully exploiting this bug could let the hackers reset the API key.

Document
Free Webinar

Compounding the problem are zero-day vulnerabilities like the MOVEit SQLi, Zimbra XSS, and 300+ such vulnerabilities that get discovered each month. Delays in fixing these vulnerabilities lead to compliance issues, these delay can be minimized with a unique feature on AppTrana that helps you to get “Zero vulnerability report” within 72 hours.

WordPress Plugin SMTP Flaw

Using the vulnerable Mailer plugin on WordPress sites, the vulnerability allows unauthorized threat actors to do the following things:-

  • Reset API keys
  • View logs
  • Access password reset emails
  • Hack sites

A critical vulnerability, identified as CVE-2023-6875 with a VSS Score of 9.8, has been detected. It is highly recommended that users update to the patched version 2.8.8 to address the issue.

Another report unveiled that the POST SMTP Mailer had a Cross-Site Scripting vulnerability that allowed malicious scripts to be injected into websites.

The cybersecurity researchers earned a handsome bounty reward from the Bounty Program Extravaganza, and here below, we have mentioned the reward figures:-

  • Ulyses Saicha earned $4,125
  • Sean Murphy earned $825

On December 8, 2023, the cybersecurity analysts at Wordfence notified WPExperts.io about the vulnerability, and by December 10, 2023, they received the response.

In response, WPExperts[.]io developers acted promptly and issued a patch on January 1, 2024. Not only that, they even urged all the users to immediately update their vulnerable version to the latest patched version, 2.8.8.

Vulnerability in POST SMTP Mailer (up to version 2.8.7) allows unauthorized access and data modification via a type juggling issue in the connect-app REST endpoint.

Stored Cross-Site Scripting risk in POST SMTP Mailer (up to version 2.8.7) arises from inadequate input sanitization in the ‘device’ header, and unauthenticated attackers can inject harmful scripts.

Looking for cost-effective penetration testing services? Try Kelltron’s to assess and evaluate the security posture of digital systems – Free Demo


[ad_2]
Source link

Samsung’s January 2024 update is rolling out to Galaxy S21

0
[ad_1]

Samsung‘s January 2024 update is available for a few more Galaxy devices. It is rolling out to the three Galaxy S21 series flagships. The Galaxy S21 FE, which isn’t a true blue flagship, picked up the new security patch a few days back. Samsung has also rolled out the January SMR (Security Maintenance Release) to several other models, including the Galaxy S23, Galaxy S22, and all recent foldables.

Galaxy S21 series joins Samsung’s January 2024 update party

The latest security update for the Galaxy S21 trio is currently rolling out in Europe. More precisely, it is available for users in Switzerland with the firmware build number G99*BXXS9FWL9. A wider rollout, covering the entire lineup in other European countries as well as the rest of the world, should follow shortly. The build number may vary depending on your region but everyone will get the same update.

As Samsung’s official changelog confirms, the latest firmware release for the Galaxy S21, Galaxy S21+, and Galaxy S21 Ultra is all about this month’s security fixes. There aren’t any new features or functional improvements here, which isn’t surprising. Just two months back, the devices received the Android 14-based One UI 6.0 update with tons of goodies, including some UI changes.

The new update still has a lot to talk about on the security side of things. Rolling out with an OTA (over the air) file size of about 400MB, it brings as many as 80 vulnerability patches. Samsung is pushing 75 Android OS patches and 5 Galaxy-specific patches to Galaxy devices with the January SMR. One of these vulnerabilities is labeled “critical,” potentially allowing attackers to gain remote access to affected devices.

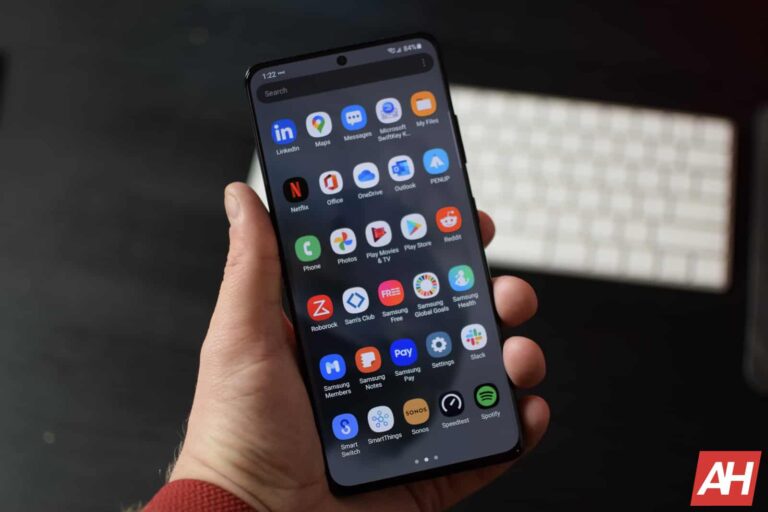
If you are using a Galaxy S21 or any other Samsung phone, you can go to Settings > Software update >Download and install to check for new updates. Note that updates are released in batches and may not be available to everyone at the same time. So, if you don’t see a pending update today, you can always check back later. You may also get a notification once the OTA rollout hits your Galaxy device.

The Galaxy S21 series will get Android 15

The Galaxy S21 phones turn three years old next week but they still have plenty of life left in them. Samsung will push four major Android OS updates to the lineup, meaning that they will get Android 15. The devices should also pick up One UI 6.1, which debuts with the Galaxy S24 series next week. If you plan to upgrade to the new flagship, you can pre-reserve it now with no commitment and get a $50 credit from Samsung when you pre-order.


[ad_2]
Source link