Roborock debuts new, powerful cleaning solutions at CES 2024

0
[ad_1]

Roborock has announced a fleet of new robot vacuums and cleaning solutions at CES 2024, including some new options that actually aren’t robots at all. If you thought Roborock was all about robot vacuums and robot vacuums only, you’d be wrong. While the company’s main bread and butter is robot vacuums, it does make vacuums that you control yourself and manually push around. Like we all used to do 15-20 years ago.

This isn’t Roborock’s first time launching a regular vacuum. It is, however, the company’s first time launching these kinds of vacuums in the US market. During its CES unveiling, Roborock debuted 6 new cleaning solutions. This includes the S8 MaxV Ultra, S8 Max Ultra, Q Revo MaxV, and Q Revo Pro robot vacuums. The remaining two cleaning products are the Flexi Pro and Flexi Lite, which are handheld push vacuums. But just because they aren’t robots that doesn’t mean they don’t provide a high-quality clean.

These two push vacuums include a handful of useful features to ensure your floors don’t stay dirty for long. Not the least of which is an included mop system. There’s also the DirTect feature that uses sensors to detect dirt levels as you clean. this will adjust the cleaning power based on what the sensors detect. And that should allow you to get the clean right the first time so you won’t have to go back over certain areas. They also now feature warm water cleaning during the mop process, and warm air drying so things don’t get musty.

Roborock doesn’t have availability dates or pricing on these just yet. The company does say that information is “coming soon” though.

Roborock has powerful new robot vacuums for 2024

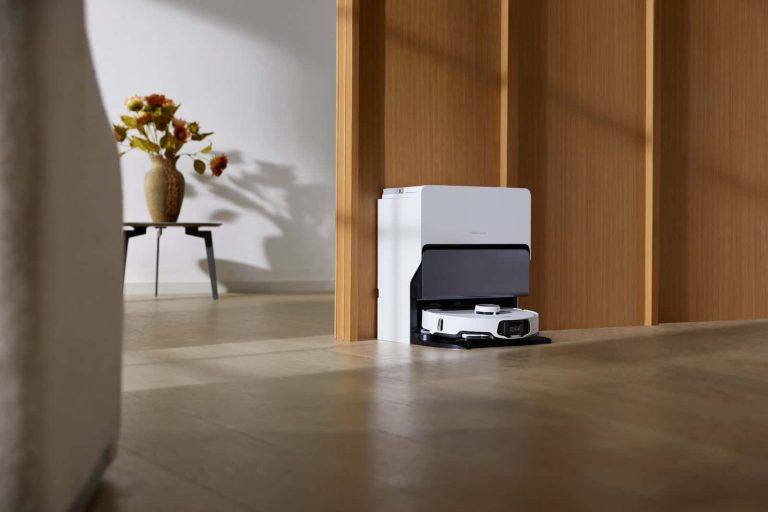
If you don’t care for push vacuums anymore and you’d rather a robot vacuum do all the work, Roborock still has you covered. Its latest cleaning solutions, such as the S8 MaxV Ultra, feature a neat robotic arm called the ‘FlexiArm’ that is designed to get into those pesky hard-to-reach corners. The FlexiArm has the Extra Edge Spinning Mop attached to it that sticks out a little from the edge of the vacuum. This is what allows it to hit those corners and get any dirt and debris that other vacuums might miss.

It comes with the RoboDock Ultra too. A base station for the vacuum that has useful self-dispensing detergent capabilities for the vacuum’s mops. It can also refill the detergent once the vacuum runs out of it. Additionally, it uses water that’s heated to 60 degrees Celcius for better floor cleaning, and then it dries the mop pads with hot air at the same temperature.

You’ll see mops and hot air drying on more robot vacuums these days but not many of them will use hot water for the cleaning process. Roborock says these features are available on the S8 series. So it isn’t just the S8 MaxV Ultra that will offer them. The S8 series will go on sale starting in April via Amazon and Roborock’s online store. The S8 MaxV Ultra will retail for $1,799.99 and the S8 Max Ultra will retail for $1,599.99.

Q Revo vacuums will offer many of the same features for less

A minimum $1,600 price tag is a lot for a robot vacuum, even if it is a high-quality unit. That’s why Roborock also offers the new Q Revo series. These will have a lot of the same features as the S8 series but they’ll be more affordable and cost hundreds less.

You will have to compromise on some features. But the best ones are still there. Like the FlexiArm Edge Mopping system. They also come with a feature-rich Dock 2.0 that will do everything from self-empty the bin to hot-air dry the mops after a cleaning session. Worth noting is that the hot-air drying is 45 degrees Celcius instead of 60 degrees. The hot water dispensing for the mop is still the same at 60 degrees Celcius though.

The Dock 2.0 can also refill the water tank when it runs low. Roborock says the Q Revo MaxV will retail for $1,199.99 and the Q Revo Pro will retail for $999.99. Both will also be available through Amazon starting in April.


[ad_2]
Source link
You may soon be able to send Selfie GIFs in Google Messages

0
[ad_1]
Google appears to be working on an exciting addition to its messaging app, Google Messages. A hidden feature that allows users to send short 4-second videos in the form of GIFs, which would add a fun and dynamic element to their conversations, has been discovered.
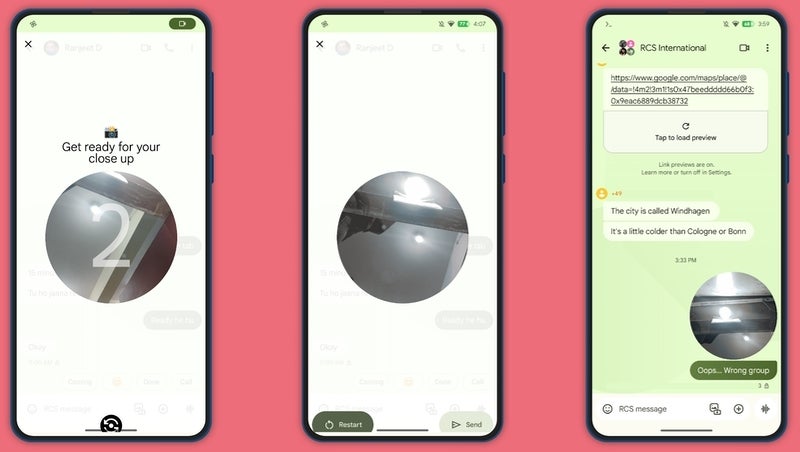
TheSpAndroid recently stumbled upon an interesting feature called Selfie GIFs that can be activated within the Google Messages app by simply long-pressing the camera icon. The feature is reportedly currently in development, and Google has not made an official announcement about it yet.
Once enabled and after long-pressing the camera icon, a new UI pops up with a rounded camera frame in the center. At the bottom, there is a camera switch button that allows users to easily switch between the front and rear cameras. Once the 3-second timer is up, the recording will kick off automatically.

After it’s finished, users will be able to view the recorded video in a GIF format through a preview UI. At that point, users are faced with two choices: Reset or Send. Resetting the recording process can be done by pressing the designated button, while sharing the video as a rounded GIF is as simple as hitting the Send option. This is similar to the functionality currently found in Chromebooks’ camera app.

Image via TheSpAndroid.blogspot.com | @GappsLeaks (Telegram) | @AssembleDebug (X/Twitter)

Google has been actively developing and introducing new features to enhance its widely-used messaging app, Google Messages. In December, the company introduced a range of exciting new features to enhance the texting experience. These additions include screen effects, custom backgrounds, and more.
In addition, the company unveiled a fresh contacts page featuring the Material You carousel plus a range of exciting new features and enhancements for compatible Pixel devices included in the latest Pixel Feature Drop — such as Video Boost, which enhances video playback, and an improved Photo Unblur feature, among others.

Now, it looks like Google is focused on enhancing the messaging experience with the introduction of Selfie GIFs. Although it’s not enabled by default yet, this feature is a fun little addition that will be sure to add a touch of fun to your conversations.


[ad_2]
Source link
Volkswagen Goes AI, Integrates ChatGPT into its Vehicles

0
[ad_1]

Volkswagen claims that ChatGPT will enhance conversations, respond to queries, supply vehicle-specific details, and provide additional features for drivers.

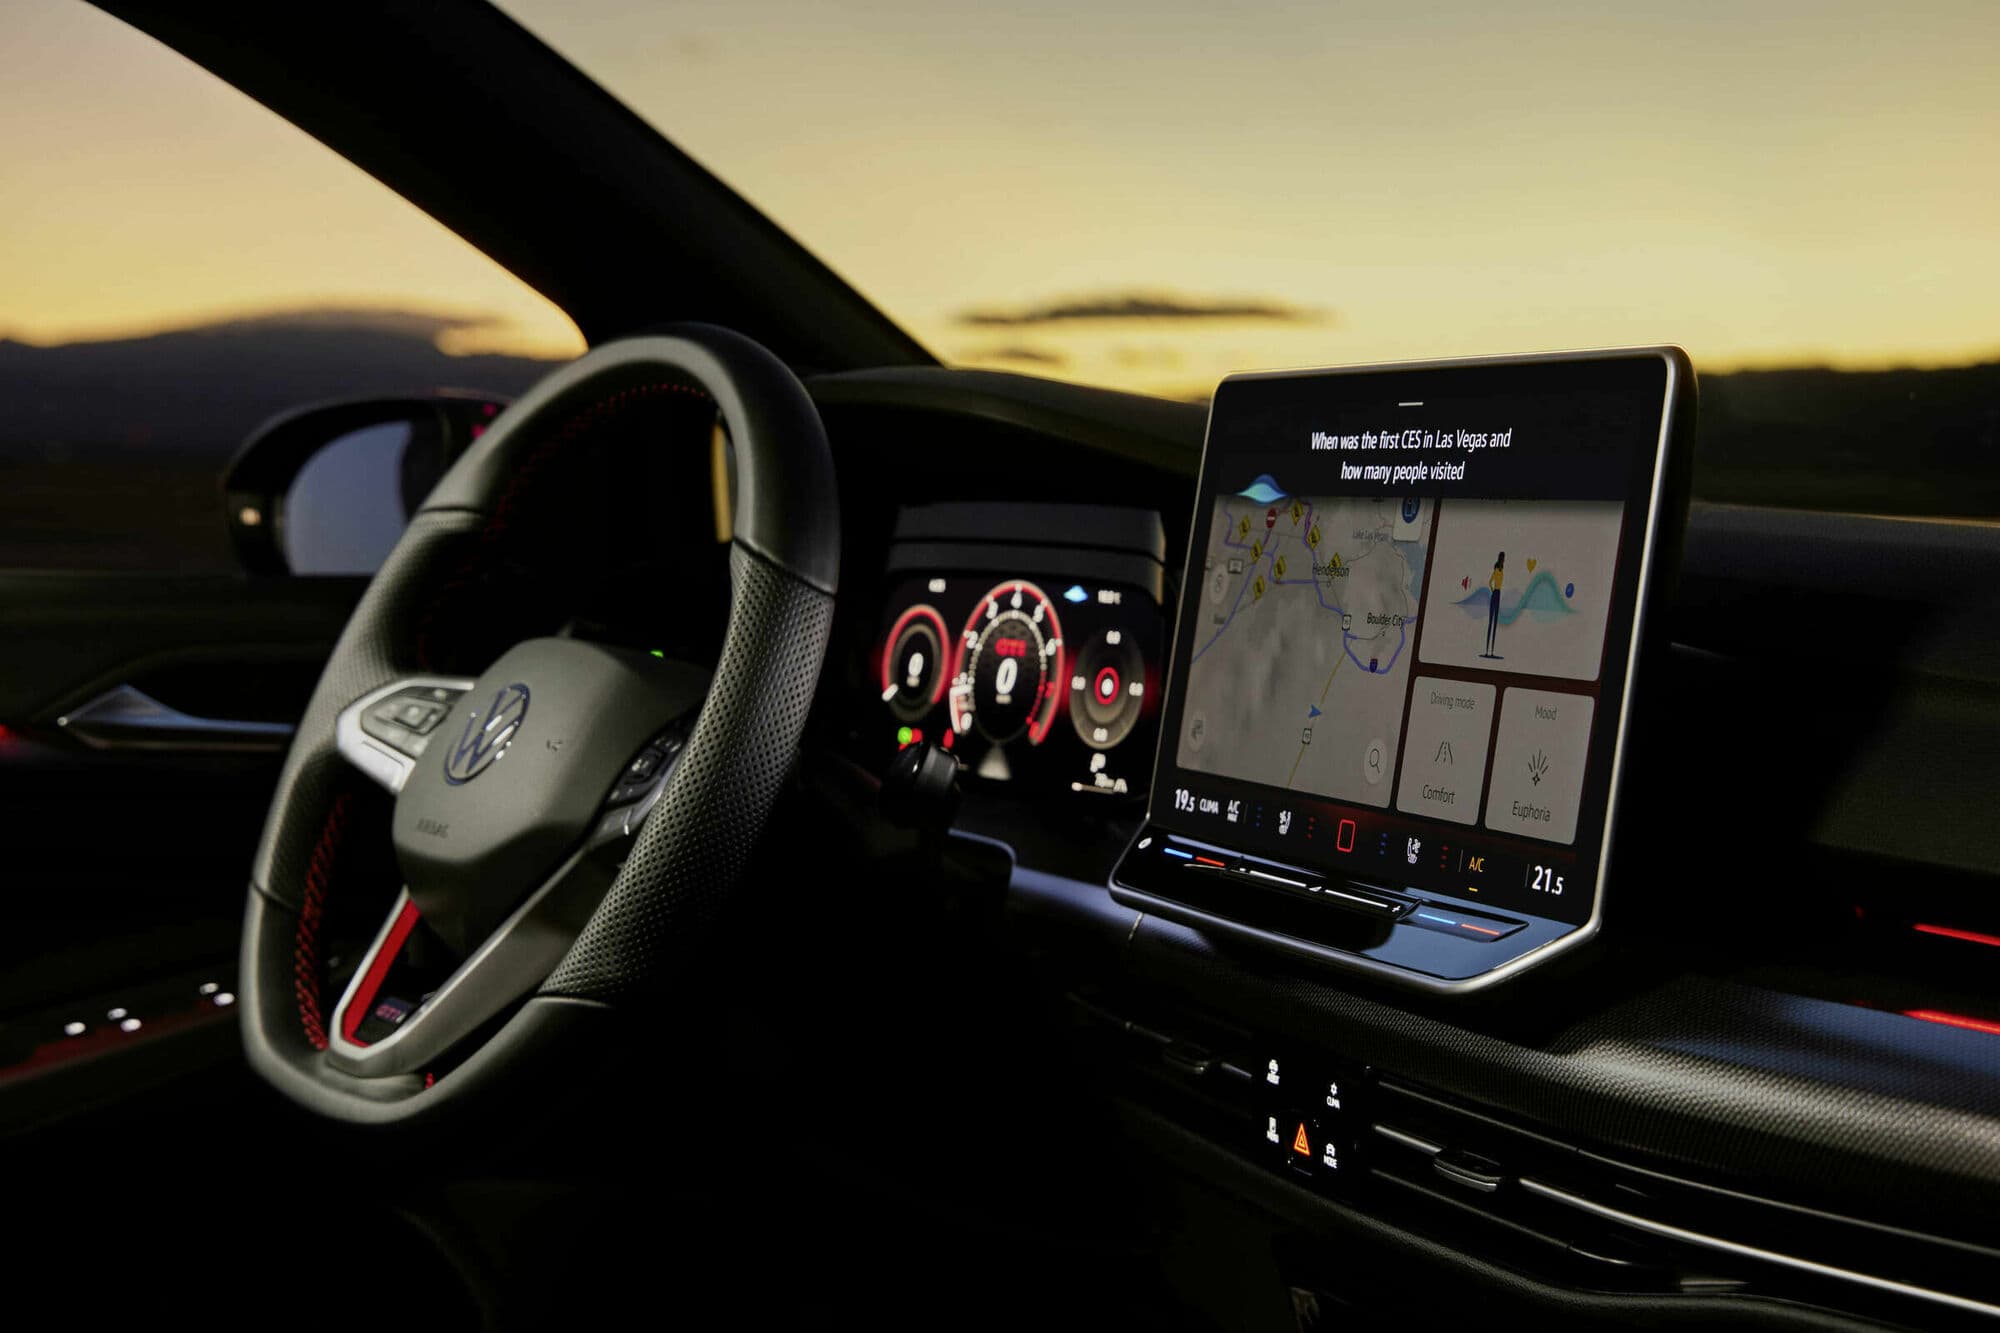
Get ready for car chats that go beyond “turn up the AC.” Volkswagen is making waves by integrating ChatGPT, the powerful language AI, into its vehicles’ voice assistant system, IDA. This groundbreaking move, announced at CES 2024, promises to transform the way we interact with our automobiles, turning them from mere modes of transport into engaging conversational partners.

The OpenAI’s ChatGPT chatbot was already doing wonders in the field of healthcare by diagnosing critical medical conditions when doctors fall short. But now, imagine asking your car to tell you a story while cruising down the highway, or engaging in a philosophical debate about the nature of reality (Just saying).

ChatGPT steps in when IDA reaches its limits, offering richer, more nuanced responses to your queries. Craving a laugh? Ask for a witty joke. Feeling curious? Explore the cosmos through a guided space tour. The possibilities are as limitless as your imagination.

But this isn’t just about entertainment. ChatGPT can also be a helpful companion, answering your burning questions about nearby restaurants, the latest news headlines, or even the meaning of life itself. Say goodbye to frustrating “I don’t know” responses and hello to informed, engaging conversations that keep you company on the road.

Image credit: Volkswagen

Privacy Concerns?

Of course, with any powerful technology, concerns arise. Volkswagen assures drivers that privacy is paramount. All questions will be anonymized and deleted, with ChatGPT kept at arm’s length from your car’s critical systems. Additionally, the potential for bias inherent in any AI system will be closely monitored and mitigated.

Coming to Europe and North America

While the North American launch date remains under wraps, European drivers can buckle up for this conversational revolution starting in Q2 2024, the company said in a press release. This integration marks a significant leap forward in the evolution of in-car technology, blurring the lines between vehicle and companion.

What do Experts Think?

For detailed insights into the new development, we reached out to Dennis Kengo Oka, senior principal automotive security strategist at Synopsys Software Integrity Group. Oka emphasizes the automotive industry’s strides toward enhancing user experience through the integration of powerful AI technologies like ChatGPT into vehicles.

He suggests that automakers can leverage these technologies to develop digital assistants, trained with specific automotive information, thereby simplifying user interactions and improving overall experience.

“The automotive industry is working towards improving the user experience in cars and allowing a more seamless transition from smart homes to smart cars. That is, the same digital assistants you are using in your smart home have also been available in your car for the past few years. However, these systems have been more general and often been limited to only supporting certain commands, e.g., unlock the door or start the engine.“

However, Oka also issues a cautionary note, pointing out potential risks associated with deploying such AI-driven systems in cars. “This would allow a user to easily ask questions about a warning light blinking on the dashboard, plan an efficient route to the airport, open the garage door or connect a user device, find and reserve a charging spot etc., without having to dig through a large user manual or use and manage multiple devices or systems, but what about the risks? It is extremely important to consider what type of training data is used as well as apply policies that define what responses with what type of information are allowed,“ Oka warned.

Nevertheless, whether you’re a tech enthusiast, a seasoned road warrior, or simply someone who enjoys a good chat, Volkswagen’s ChatGPT-powered IDA is sure to have you talking – and not just about the weather.

So, fasten your seatbelts, folks. The future of the open road is looking decidedly more chatty, and Volkswagen is leading the charge. Get ready to engage in some truly intellectual conversations – all from the comfort of your driver’s seat.

  1. How To Use ChatGPT To Trade Cryptocurrency
  2. OpenAI Launches ChatGPT Bug Bounty Program
  3. ARMO integrates ChatGPT to secure Kubernetes
  4. Researchers Leverage ChatGPT to Expose macOS Malware
  5. OpenAI Launches ChatGPT App for iOS, Bolstering Accessibility
  6. ChatGPT Improves Healthcare, But Industry Needs Secure Database First

[ad_2]
Source link
Humane, maker of the AI Pin, just laid off 4 percent of its employees

0
[ad_1]

During late 2023, news started to ramp up about an innovative new product that brings AI to the physical world. It’s called the AI Pin by tech startup Humane. Well, the device is set to start shipping sometime this March, which is good news. However, as for the bad news, Humane just laid off 4% of its staff.

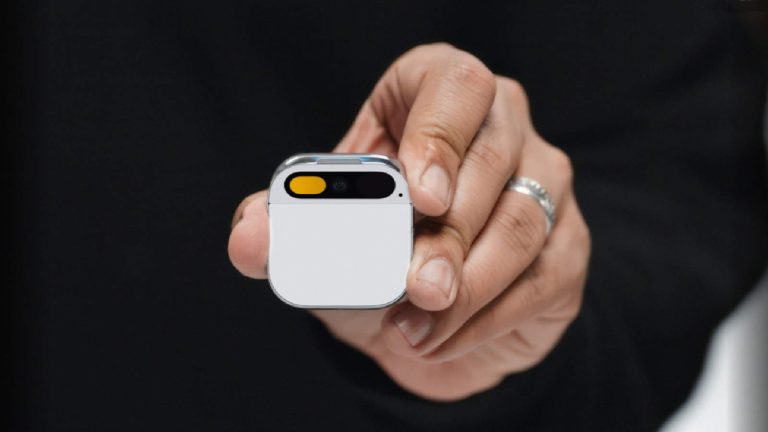
If you’re interested in learning about the AI Pin, you can check out our coverage. In a nutshell, it’s a small pin that you can clip onto your shirt. It uses a camera and microphone to observe the world.

Basically, this is a device to bring ChatGPT with you wherever you go. You use voice commands to communicate with it and summon it. Just like with ChatGPT proper, you can ask it pretty much any question, and it will contact large language models in the cloud to deliver your results. Also, using the camera, you can scan real-world objects and ask questions about them.

The device costs $699, and it comes with a kit including batteries, a charger, a case, and more. Check out the Humane site for more information.

Humane laid off 4% of its staff

The year 2023 was no stranger to massive layoffs. Tens of thousands of workers from several major tech brands have been sent packing due to the economic downturn. We’ve seen rolling layoffs from companies like Meta, Google, Microsoft, Netflix, Verizon, T-Mobile, and more. Each layoff totaled hundreds or thousands of people being laid off.

In the case of Humane, the numbers aren’t quite so substantial. According to a source who chose to remain anonymous, the tech startup had to lay off 4% of its staff, which totals 10 people. The company announced that it was going to bring some cutbacks in order to cut down on costs. A startup company laying off employees before it launches its first product does not really bode well. In any case, we’ll have to see if the AI Pin catches on.

It’s still really early in the game for Humane, so we don’t know if the company will potentially see profits from the Pin. Right now, since the company has not launched a product as of yet, is most likely running off of investors’ money. We will have to wait until the AI Pin gets into people’s hands and starts making rounds with reviewers before we can truly know the company’s fate.


[ad_2]
Source link
Google Wallet now stores airline boarding passes on your wrist

0
[ad_1]
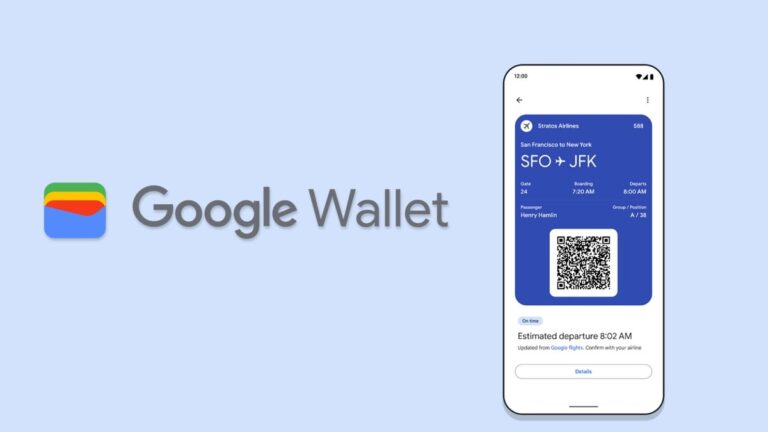
In a recent update, Google Wallet for Wear OS has expanded its capabilities to include support for airline boarding passes. This comes after the addition of loyalty card support back in December.
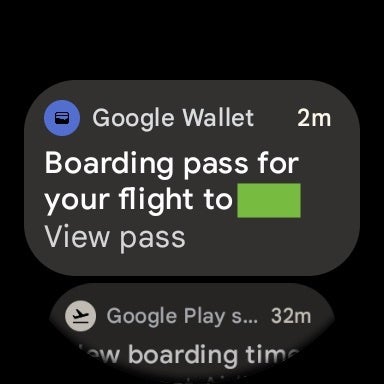
As reported by 9to5Google, your Wear OS 3+ device will now display a new notification from the Google Wallet app on your smartwatch. This notification will inform you about your boarding pass for the flight to any airport with an option to tap on it to “View pass” and thus access the QR code for easy gate scanning.

Image Credit: 9to5Google


This much-needed addition greatly enhances the functionality of Google Wallet for Wear OS, allowing it to seamlessly integrate with a wider range of phone features. When Google introduced loyalty card support in December, it was initially limited to basic membership programs and other types of passes. Unfortunately, excluded from the list were COVID cards, health insurance cards, and private passes.Some users have reported seeing this feature already available on the Pixel Watch 2, while original Pixel Watch users (such as myself) are still waiting for the update, which appears to be server-side. However, as this was not a feature that was announced as a Pixel Watch 2 exclusive, there shouldn’t be any reason why the original Google Pixel Watch wouldn’t receive it.
The support documentation for Google Wallet also includes information on how to find your passes on your smartwatch’s Wallet app, and even includes troubleshooting info should you not be able to find the option to add your boarding pass to your watch. The documentation states that passes are automatically added across all of your synced devices, but your watch must be running Wear OS 3.5 or newer and the Google Wallet app on the watch must be version 23.46.x or above. Additionally, it is stated that Fitbit devices aren’t supported.

[ad_2]
Source link
Atomic Stealer rings in the new year with updated version

0
[ad_1]

Last year, we documented malware distribution campaigns both via malvertising and compromised sites delivering Atomic Stealer (AMOS) onto Mac users. This stealer has proven to be quite popular in the criminal underground and its developers have been adding new features to justify its hefty $3000/month rental fee.

It looks like Atomic Stealer was updated around mid to late December 2023, where its developers introduced payload encryption in an effort to bypass detection rules. Some samples from crack websites made their way to VirusTotal around that time frame, followed by a malvertising campaign we observed in January 2024.

In this blog post, we will review the latest changes with Atomic Stealer and the recent distribution with malicious ads via the Google search engine.

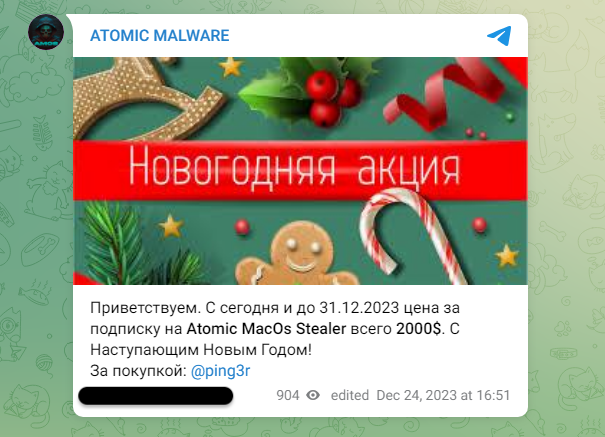
In December, Atomic Stealer ran a promotion via a post on their Telegram channel to offer a special holiday discount to their customers:

Welcome. From today until December 31, 2023, the price for a subscription to Atomic MacOs Stealer is only $2000 . Happy New Year!

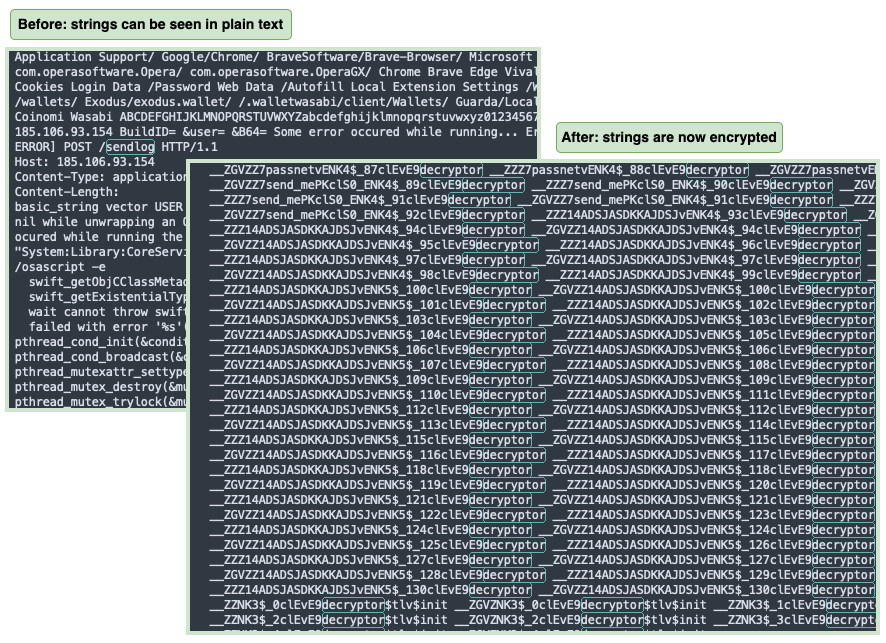
While the developers did not specifically advertise this feature, it appears that around December 17 Atomic Stealer had changed some of its code to hide certain strings that were previously used for detection and identifying its command and control server.

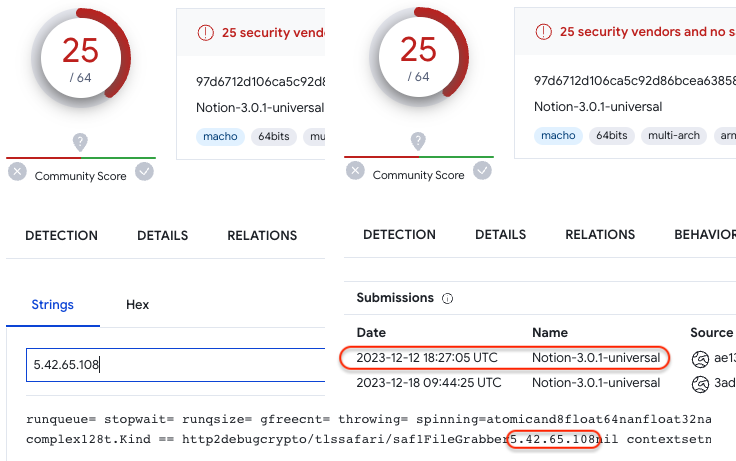
Sample with strings in clear text (Dec 12), showing for example the IP address for the malware’s C2 server:

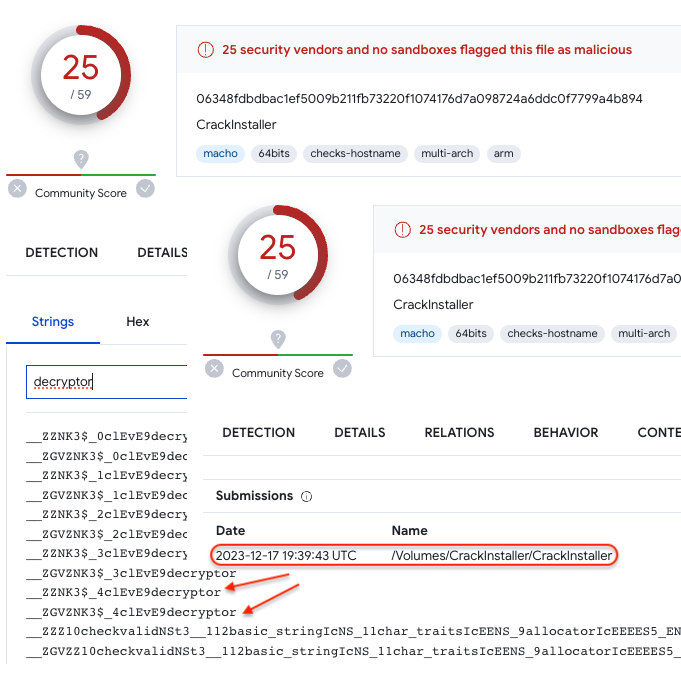
Obfuscated sample (Dec 17), using a new encryption routine that hides strings of interest:

Those two samples above also represent the different distribution channels that Atomic Stealer customers are using to distribute the malware. It’s possible customers using software cracks got access to the update Atomic Stealer before those that leverage malicious ads.

In fact, during the holiday break, we noticed a decrease in malvertising activity, in particular for the campaigns running via Google search ads. This was somewhat expected and typically extends into early January. However, on January 8, we identified a malvertising campaign using similar tactics seen previously by threat actors distributing FakeBat. In this instance, there was also a payload destined for Mac users, Atomic Stealer in its updated version.

Malvertising with FakeBat – Atomic Stealer combo

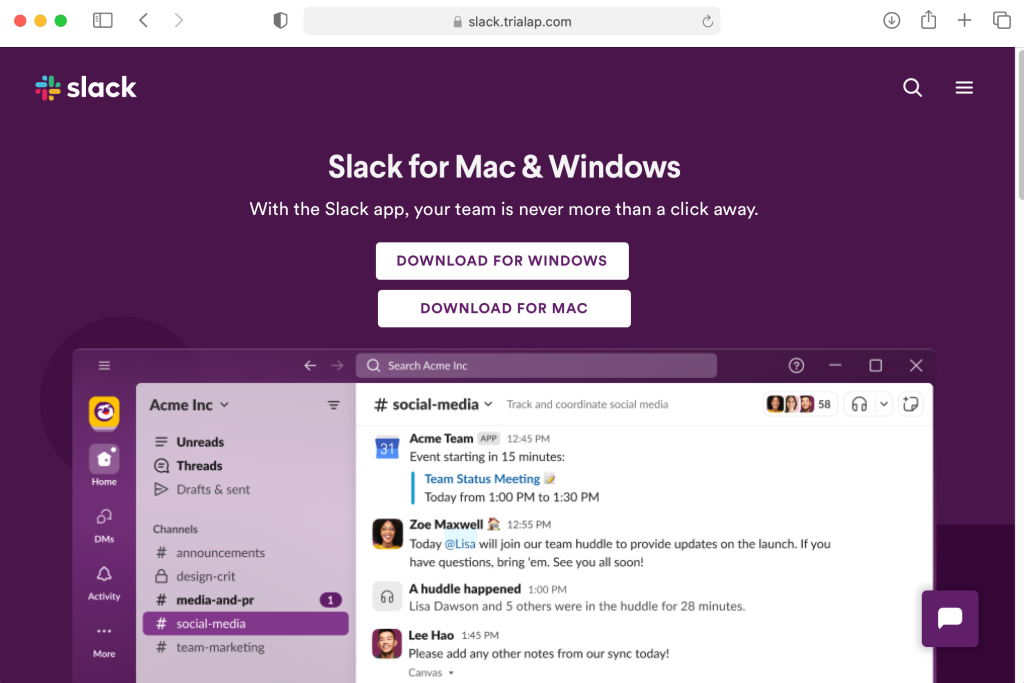
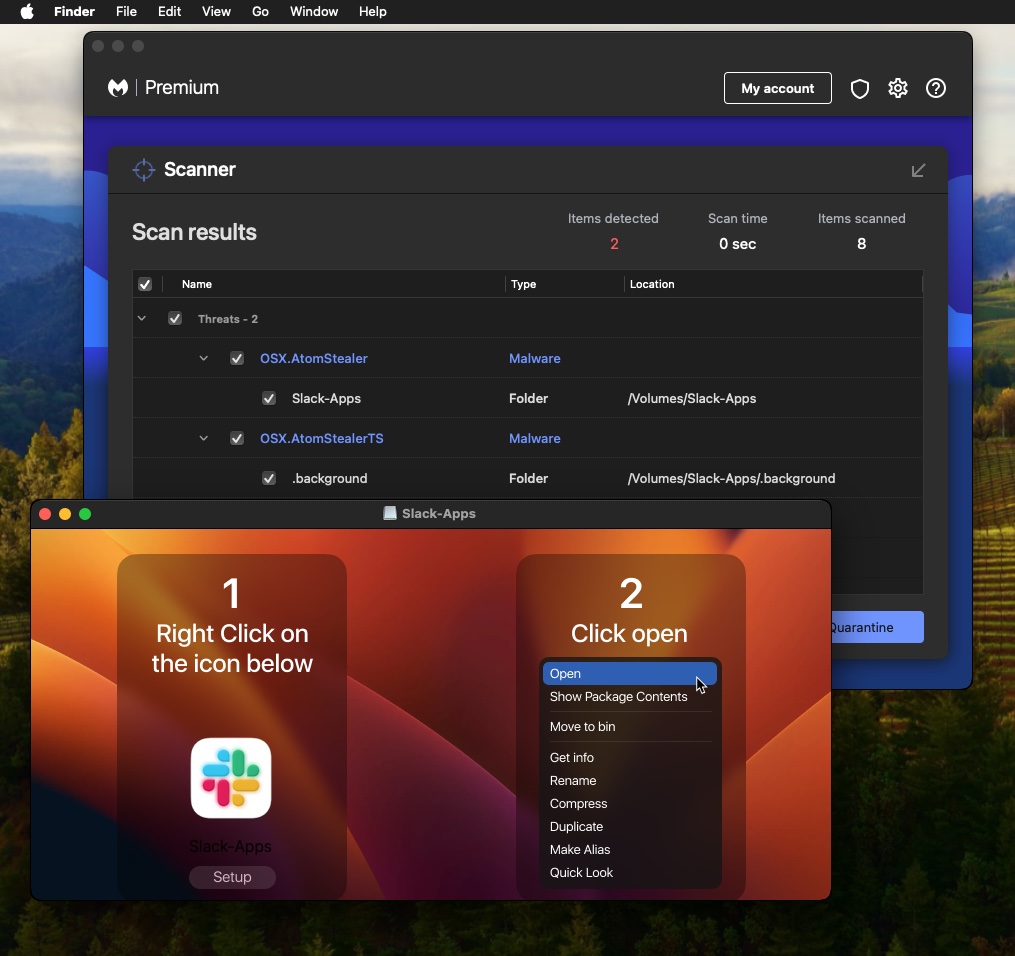
The threat actors are luring victims via a Google search ad impersonating Slack, the popular communication tool, and redirecting them to a decoy website where the app can be downloaded for both Windows and Mac:

The threat actors are leveraging tracking templates to filter traffic and route it through a few redirects before loading the landing page:

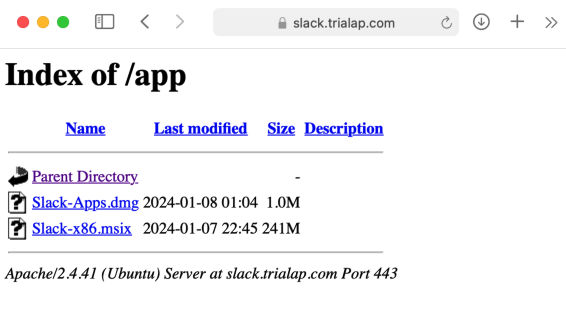
On that same domain, there is an open directory showing the location of the Windows payload which is an MSI installer (FakeBat), and the Mac one, Atomic Stealer (AMOS):

Obfuscated Atomic Stealer

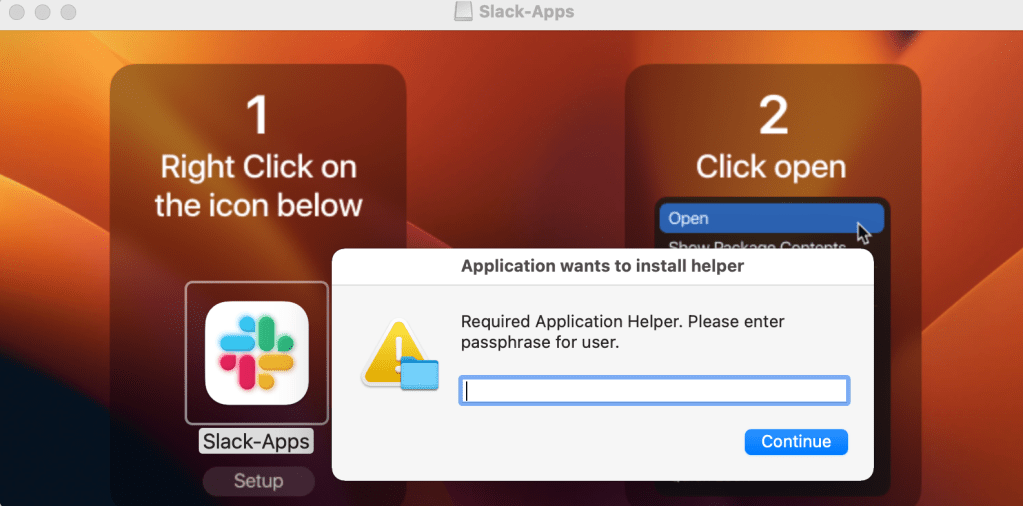
The malicious DMG file contains instructions for users to open the file as well as a dialog window asking them to enter their system password. This will allow Atomic Stealer to collect passwords and other sensitive files that are typically access-restricted.

When comparing the previous Atomic Stealer samples we have, we can see that the application code has changed. Previously, we could see certain strings revealing the nature of the payload (browsers, wallets, etc.) and more importantly the command and control server that receives stolen user data. Now, these strings are no longer visible as the code is well obfuscated:

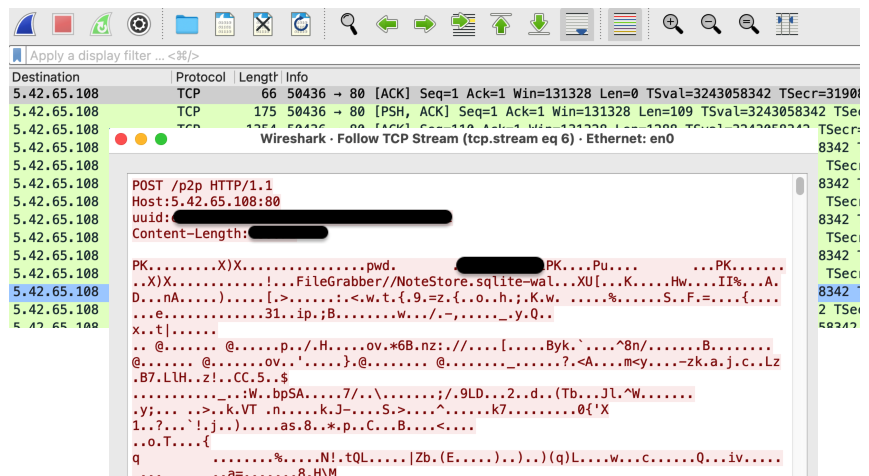
When we analyzed this sample in a sandbox we saw the data exfiltration taking place and the corresponding C2 server:

Stealing victim passwords, crypto wallets and cookies

As detailed in Objective-See’s The Mac Malware of 2023, stealers were the most popular type of malware. It’s not just passwords that are of interest to cyber criminals. Stealing browser cookies can sometimes be even better than having the victim’s password, enabling authentication into accounts via session tokens.

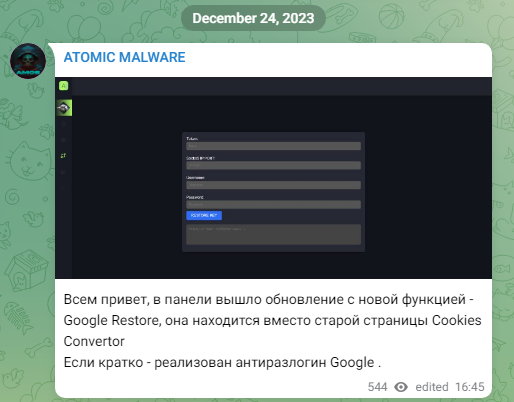
In fact, Atomic Stealer developers were working on a cookie feature they announced on Christmas Eve:

Hi everyone, the panel has released an update with a new feature – Google Restore, it is located instead of the old page Cookies Convertor. In brief – implemented anti-unlogin Google.

As stealers continue to be a top threat for Mac users, it is important to download software from trusted locations. Malicious ads and decoy sites can be very misleading though and it only takes a single mistake (entering your password) for the malware to collect and exfiltrate your data.

We have reported the malicious ad and infrastructure to the respective parties for mitigation.

To stay safe from this and other similar threats, a combination of web protection and antivirus is best suited. Malwarebytes Browser Guard and Antivirus for macOS can prevent and detect Atomic Stealer.

Indicators of Compromise

Malvertising chain

ivchlo[.]gotrackier[.]com
red[.]seecho[.]net

Decoy site

slack[.]trialap[.]com

FakeBat payload URL

slack[.]trialap[.]com/app/Slack-x86.msix

FakeBat hash

49f12d913ad19d4608c1596cf24e7b6fff14975418f09e2c1ad37f231943fda3

FakeBat C2

ads-strong[.]online

Atomic Stealer payload URL

slack[.]trialap[.]com/app/Slack-Apps.dmg

Atomic Stealer hash

18bc97e3f68864845c719754d2d667bb03f754f6e87428e33f9c763a8e6a704a

C2

5.42.65[.]108

[ad_2]
Source link
Exynos 2400 Confirmed for Galaxy S24 and S24+ in Europe

0
[ad_1]

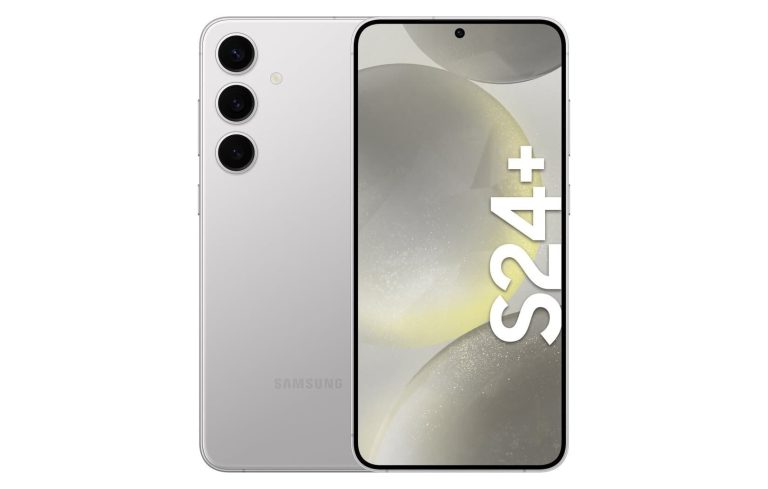
Prospective Galaxy S24 buyers in Europe, here’s the information you were all dreading. According to a Winfuture report, Samsung will ship the Galaxy S24 and Galaxy S24+ with the Exynos 2400 in Europe. The Galaxy S24 Ultra will get an overclocked Snapdragon 8 Gen 3.

Galaxy S24 chipsets confirmed for Europe

It is an open secret that Samsung will use two different processors in the Galaxy S24 series. The Ultra model will feature the Snapdragon 8 Gen 3 globally while the other two models will arrive with the Exynos 2400 in some markets. However, there is confusion about a couple of things.

Firstly, rumors are that the Korean firm will use two variants of the Snapdragon chip—an exclusive “for Galaxy” version with an overclocked CPU and the standard Snapdragon 8 Gen 3. It is unclear whether this differentiation will be based on the model or region or a mix of both.

For example, the Galaxy S24 Ultra could come with the higher-clocked chipset and the others with the standard one (in markets where they feature the Snapdragon SoC). Alternatively, Samsung could use the higher-clocked processor in all three models in some regions and the standard one in others.

Additionally, there is confusion about the regions where Samsung will ship the Galaxy S24 and Galaxy S24+ with the Exynos 2400. Some reports said the Plus model will get the Snapdragon chip in most countries, with the Exynos version coming in very few regions. We now have confirmation that European buyers will get the Exynos version of the phone.

The new report says the Galaxy S24 and Galaxy S24+ versions with “B” at the end of their model numbers (SM-S921B and SM-926B) will feature the Exynos 2400. Interestingly, there is no evidence of a global version of the Galaxy S24+ with a different suffix in its model number. The “N” is for the Korean version and the “U” is for the US version.

If a Snapdragon-powered unit exists for global markets, it may feature the “E” suffix in its model number. But as of now, we haven’t seen anything. Whether that means it will ship with the Exynos chip in most global markets, we will have to wait and see. Thankfully, it won’t be a long wait as the new Samsung flagships go official on January 17.

The Ultra model will get the overclocked Snapdragon chip in Europe

Winfuture’s report also confirms an overclocked Snapdragon 8 Gen 3 for the Gaalxy S24 Ultra in Europe. The chipset has its Cortex-X4 prime CPU core clocked at 3.4GHz, higher than the standard version’s 3.3GHz. There are rumors about other CPU cores being clocked lower than the standard version. However, it could be because of some reports rounding off the values. Stay tuned for the official confirmation from Samsung.


[ad_2]
Source link

OpenAI responded to the New York Times lawsuit, defending fair use

0
[ad_1]

The New York Times has been in a heated battle against OpenAI over the company’s use of copyrighted articles. Just recently, the popular publication site brought OpenAI into court looking to sue it for billions of dollars in damages. OpenAI responded to the New York Times during the lawsuit, alleging that it did not violate copyright law and that its practices are protected under fair use..

To catch you up, ChatGPT uses text-based data scraped from the internet. The data comes from a plethora of sources, and these sources also include big-name publications. Most large publications hide their news articles behind a paywall. The issue is that OpenAI is able to crawl these websites and use the information from their articles. If a person requests information about a news story, it’s possible that ChatGPT could regurgitate sections of copyrighted articles.

This gives users access to copyrighted and paywalled articles for free. This is the crux of the lawsuit.

OpenAI responded to the lawsuit from The New York Times

OpenAI is one of the leading companies in the generative AI field, and it’s come under a lot of fire over AI in general. This is not the company’s first legal tussle. According to the report, OpenAI defended Fair Use and its defense. This means that publicly available material can be used for news reporting, criticism, and commentary. While the New York Times’ articles are behind the paywall, they are still technically available to the public. So, they fall under this umbrella.

One thing that could tip the scale in this case is the concept of regurgitation.  This is when an AI reproduces all or a piece of a work verbatim. This is the thing that The New York Times is slamming OpenAI for. If ChatGPT is indeed regurgitating sections of copyrighted work for non-paying readers to read, that could constitute a violation. It’s the equivalent of a person cutting and pasting parts of a New York Times article onto a free blog for everyone to read.

However, OpenAI states that it’s working on reducing the amount of regurgitation. We’re not quite sure how much of these articles are being regurgitated and how much is being generated from scratch. In any case, if OpenAI can completely phase out regurgitation, then there might not be an issue.

This case is still developing, so you want to stay tuned for more information and updates.


[ad_2]
Source link

Newest version of Fitbit on Android allows you to manually log your body temperature

0
[ad_1]

Fitbit has recently rolled out an update for its Android app, bringing it to version 4.06. This latest update introduces a new feature that enables users to manually record their body temperature readings using their own thermometer.
Users will now be able to tap the FAB (floating action button) and find a new option for “Temperature” alongside Activity, Sleep, Food, Water, and Weight. In the Today feed, the “Body temperature” card under “Health” will take you to a stats page that follows the new design style. This was spotted by 9to5Google following the app update.
Additionally, Fitbit has introduced a new feature that allows users to easily manage their manually logged entries. Now, you can specify a precise time for these entries and even delete them if needed. Users will also have the option to completely disable the card by accessing the “Customize Today” toggles page.

Images Credit: 9to5Google

This feature is a recent addition to the revamped Fitbit app. However, it is possible that it might have already been accessible in the previous version of the app if you owned a Fitbit tracker or smartwatch capable of measuring nightly skin temperature variations.
Google Pixel 8 Pro is equipped with a temperature sensor that will soon be equipped with this functionality to measure body temperature — as soon as the US Food and Drug Administration grants the regulatory approval. Once the feature is available, users will have the convenience of taking a reading from the app and effortlessly saving it to the Fitbit app. This could be extremely helpful to recognize ahead of time the onset of a possible illness or for the purposes of tracking female reproductive health. 

The app can be downloaded or updated on Android from the Google Play Store, while iOS is currently on version 4.08. This latest addition to the Fitbit app is a welcome feature that empowers users to closely track their health and make well-informed decisions regarding their health.


[ad_2]
Source link

Analyzing and Mitigating Cyber Threats

0
[ad_1]

In the world of emerging cybersecurity threats, understanding the significance of threat intelligence is crucial and can not be ignored. Threat intelligence involves the systematic collection, analysis, and application of data to understand potential cybersecurity threats, enabling organizations to proactively defend against malicious activities.

Python, renowned for its readability and ease of use, emerges as a key tool in the domain of threat intelligence. This article digs into the critical role of Python in threat intelligence, explaining how it facilitates the efficient analysis and mitigation of cybersecurity threats.

Understanding Threat Intelligence

Threat intelligence is a strategic initiative containing the comprehensive gathering, analysis, and utilization of information to discern potential cyber threats. This information spans indicators of compromise (IoCs), tactics, techniques, and procedures (TTPs) employed by threat actors, as well as contextual insights into the prevailing threat landscape. Effective threat intelligence empowers organizations to anticipate and counteract cyber threats before they can manifest.

In cybersecurity, the demand for experienced Python developers has become paramount. For those actively seeking highly skilled Python developers to enhance their team and strengthen defences against growing threats, consider exploring potential hires at Lemon.io.

Python’s Role in Threat Intelligence

Python’s dominance in threat intelligence is backed by its readability, user-friendly syntax, and expansive library ecosystem conducive to data manipulation, analysis, and visualization. The following delineates key areas where Python is instrumental in threat intelligence:

  1. Data Collection:

Python’s adeptness in web scraping, API interactions, and data extraction is harnessed by analysts to collect information from diverse sources, including open-source intelligence (OSINT), dark web forums, and social media platforms. Tools like BeautifulSoup and requests streamline the process of retrieving and parsing data.

  1. Data Analysis:

Leveraging libraries such as Pandas and NumPy, Python empowers analysts to process and analyze substantial datasets efficiently. This capability is paramount in threat intelligence, where discerning patterns and anomalies within extensive data sets is imperative.

  1. Machine Learning for Threat Detection:

Python’s rich machine-learning libraries, including Scikit-learn and TensorFlow, empower analysts to develop models for identifying patterns associated with cyber threats. Machine learning algorithms enhance the precision of detecting malicious activities by determining deviations from normal behaviour.

  1. Integration with Security Information and Event Management (SIEM) Systems:

Python scripts seamlessly integrate threat intelligence feeds into SIEM systems, ensuring that analysts are equipped with real-time, up-to-date information for making informed decisions.

  1. Threat Indicators Analysis:

Python plays a crucial role in analyzing Indicators of Compromise (IoCs) like IP addresses, domains, and hashes. Analysts use Python scripts to connect and enhance this data, offering a detailed insight into the threat environment.

  1. Visualization:

Python’s visualization libraries, including Matplotlib and Seaborn, facilitate the creation of meaningful visual representations of data. Visualization is indispensable for presenting intricate threat intelligence data comprehensibly to both technical and non-technical stakeholders.

Python Scripts for Threat Intelligence

Consider a hypothetical scenario to elucidate the utilization of Python scripts in threat intelligence:

Scenario: Detecting Phishing Domains

Phishing remains a persistent threat, prompting threat intelligence analysts to focus on identifying and thwarting phishing domains. Python’s automation capabilities are harnessed for this purpose:

  1. Data Collection:

Python scripts systematically collect data from various sources, including domain registration databases, blacklists, and WHOIS information. This information forms the foundation for constructing a comprehensive list of potential phishing domains.

  1. Data Analysis:

Analysts employ Pandas to filter and analyze the collected data, identifying patterns and characteristics common to phishing domains. This analysis encompasses factors such as the age of the domain, the registrar’s reputation, and the presence of specific keywords.

  1. Machine Learning Model:

A machine learning model, trained on historical data, predicts the likelihood of a domain being utilized for phishing. Scikit-learn facilitates the implementation and deployment of such models.

  1. Integration with SIEM:

Python scripts seamlessly integrate the results into the organization’s SIEM system, ensuring that security teams have real-time insights into potential phishing threats.

  1. Visualization:

Utilizing Matplotlib or Seaborn, analysts craft visual reports highlighting identified phishing domains and associated risk factors. This aids in effectively communicating the threat landscape to decision-makers.

Mitigating Cyber Threats Proactively

Python not only facilitates the analysis of cyber threats but also enables proactive defence measures. The following outlines ways in which Python contributes to the mitigation of cyber threats:

  1. Automated Response:

Python scripts can be tailored to trigger automated responses based on identified threats. For instance, upon detecting a specific IoC, an automated script can promptly update firewall rules to impede communication with the associated IP address.

  1. Threat Hunting:

Analysts leverage Python to develop tools aiding in threat-hunting activities. These tools continuously monitor the network, detect anomalies, and deliver real-time alerts for suspicious activities.

  1. Incident Response Automation:

Python scripts prove invaluable in automating incident response procedures. From isolating compromised systems to collecting forensic data, automation accelerates response times, minimizing the impact of a cyber incident.

  1. Continuous Monitoring:

Python’s proficiency in working with APIs and interfacing with diverse security tools facilitates the development of continuous monitoring solutions. This ensures that threat intelligence is seamlessly integrated into an organization’s security posture.

Challenges and Considerations

While Python is a potent tool in threat intelligence, analysts must navigate challenges and considerations:

  1. Accuracy of Machine Learning Models:

The accuracy of machine learning models is contingent on the quality of the data they are trained on. Analysts must continually update and refine these models to ensure precise threat detection.

  1. Privacy Concerns:

When collecting and analyzing threat intelligence, analysts must navigate privacy concerns and ensure compliance with regulations. Python scripts should be crafted with privacy considerations at the forefront.

  1. Resource Intensiveness:

Certain threat intelligence processes, particularly those involving extensive datasets or complex machine learning models, can be resource-intensive. Analysts must consider computational requirements and optimize scripts accordingly.

  1. Integration Challenges:

Integrating threat intelligence into existing security infrastructure can pose challenges. Python scripts must be compatible with diverse systems and APIs, necessitating ongoing maintenance and updates.

Conclusion

The integration of Python in threat intelligence will persist as a strategic player for organizations seeking to strengthen their cybersecurity and protect sensitive information from malicious actors.

  1. Tools for Testing Your Proxy Servers
  2. What is an OSINT Tool – Best OSINT Tools
  3. What Programming Languages Do Ethical Hackers Use?
  4. CISA Publishes List of Free Cybersecurity Tools and Services
  5. Using GenAI in Your Business? Here Is What You Need To Know

[ad_2]
Source link