WhatsApp is always working on new features, some that we only learn about when the company releases them to the public. However, more often than not we do have information about what’s coming to WhatsApp thanks to the beta program that the app has been running for a very long time.
If you’re not running the beta version of WhatsApp, we have the latest news about what’s expected to come to the app in the not-so-distant future. Thanks to the fine folks at WabetaInfo, we now know that WhatsApp plans to add new text formatting tools.
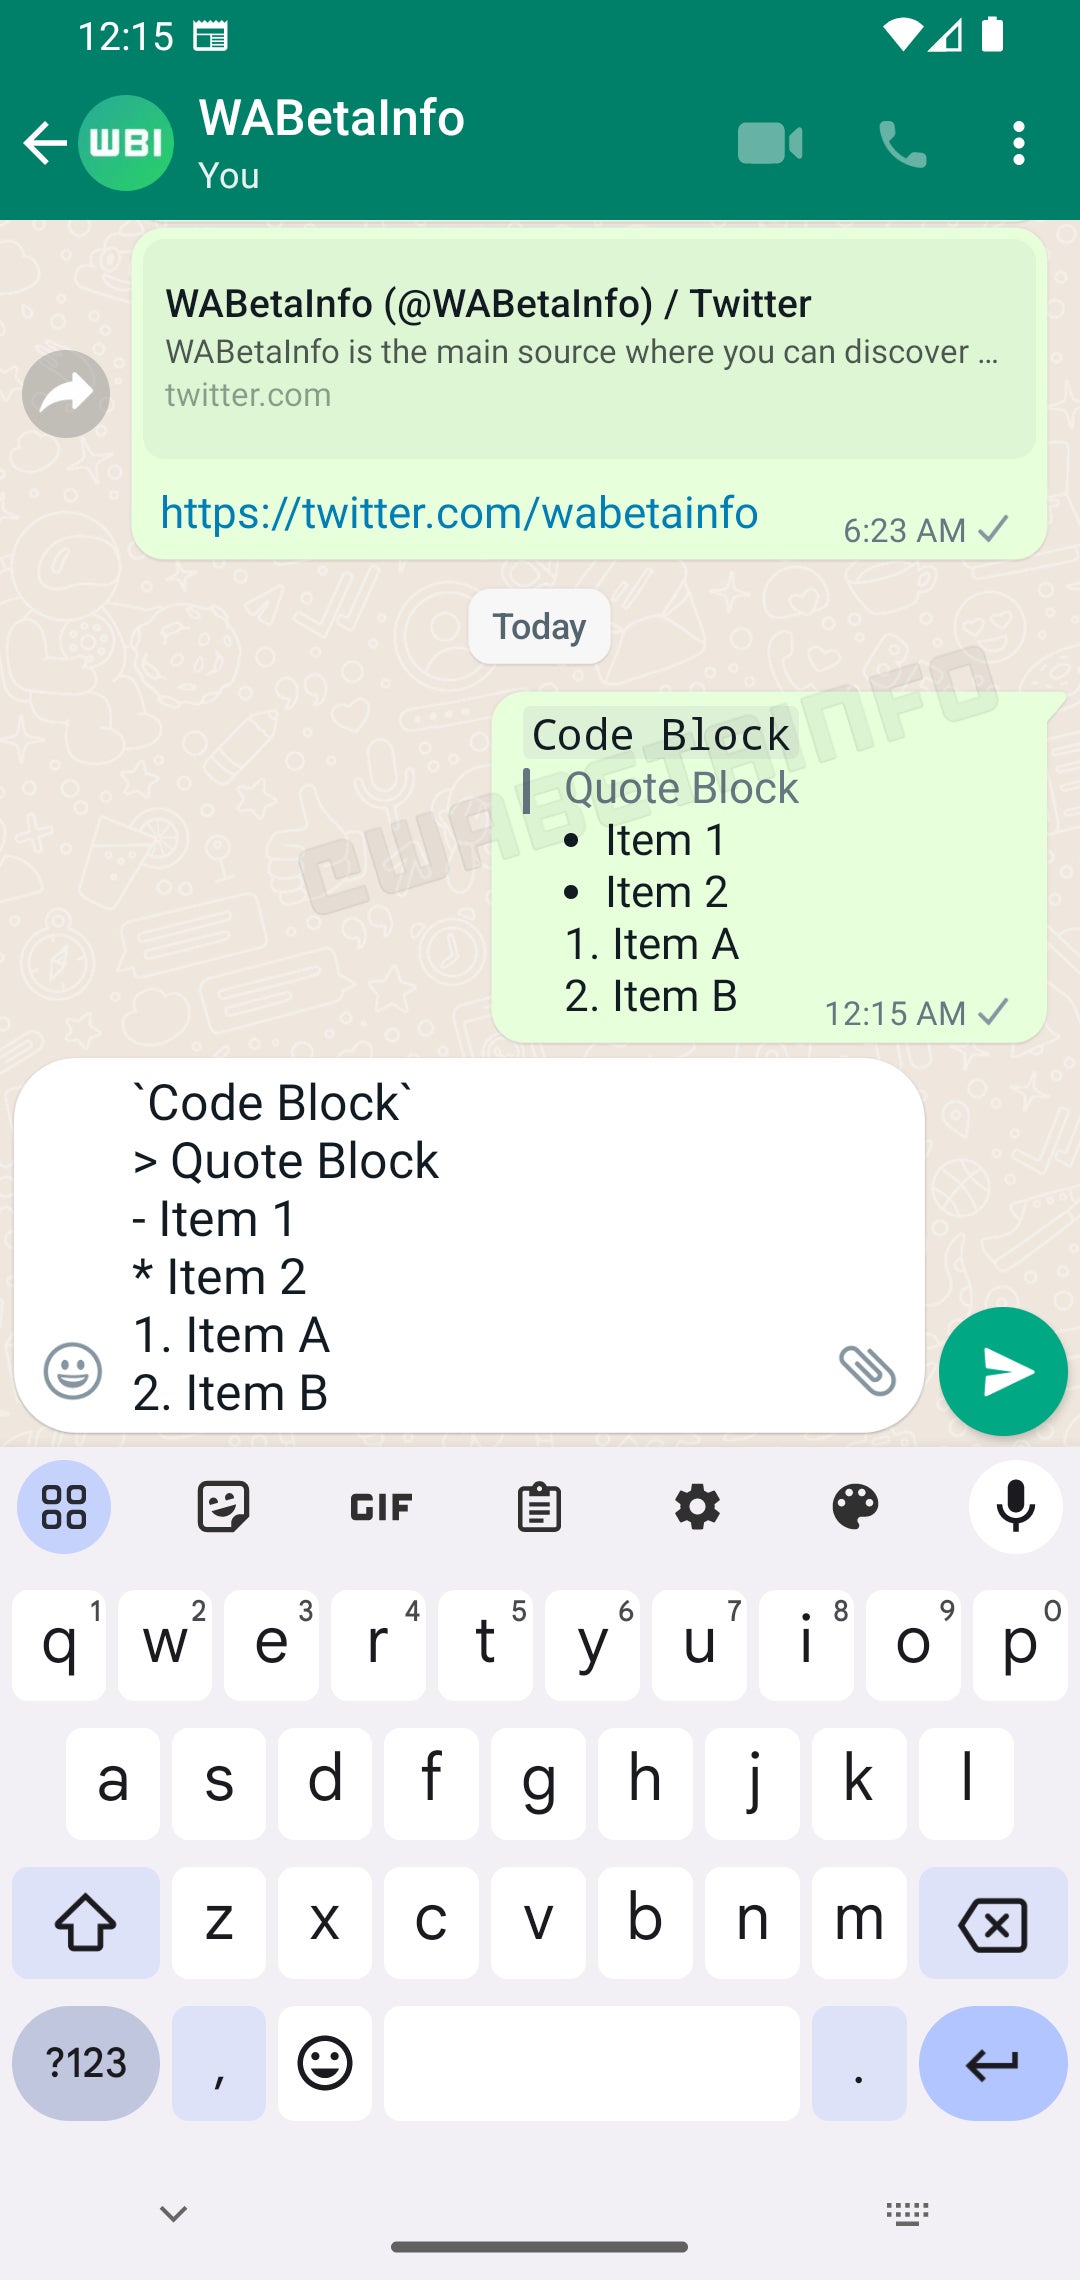
The report mentions additional options such as bullets, code, quote, and lists. As you take advantage of these new options, the text will be formatted as you type in the chat bar.
The new text formatting tools have been rolled out in the beta version of WhatsApp, but only on Android. It’s yet unclear if these will be made available on both iOS and Android platforms at launch, nor when exactly WhatsApp will finish testing them.
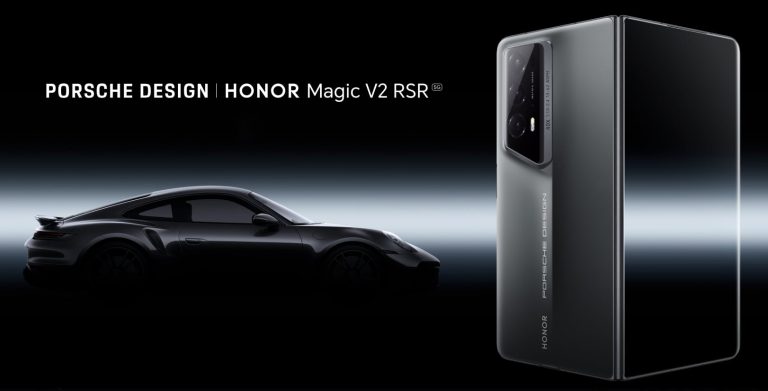
The Porsche Design HONOR Magic V2 RSR is official, and it comes as a surprise
The vast majority of us were expecting a Porsche Design HONOR Magic6 Pro to arrive, mainly due to rumors. HONOR did something else entirely, as almost nobody was expecting the HONOR Magic V2 collab.
The HONOR Magic V2 launched last year in China. Soon after its launch, it was shown off at IFA in Berlin. The phone is expected to launch globally soon, and prior to that, this Porsche Design model arrived.
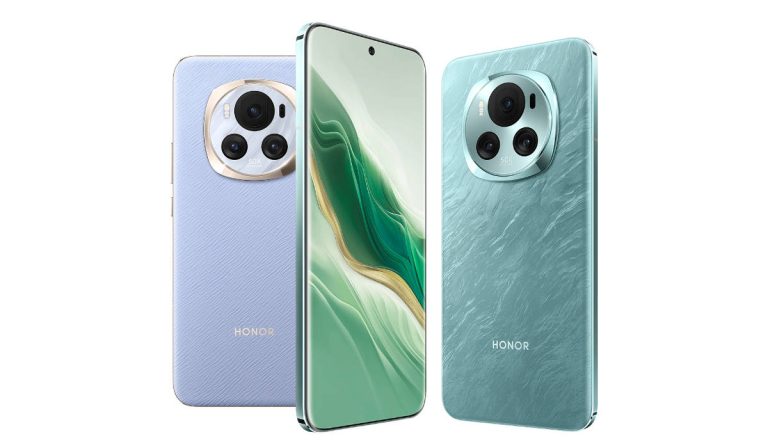
Based on what we can see here, the Porsche Design HONOR Magic V2 RSR is very similar to the regular Magic V2. The difference lies on its back, as it looks different. Not only is the backplate different, but so is the camera island. On top of that, you’ll find the Porsche Design branding back there.
This phone’s backplate is “intricately reminiscent of the hood of a Porsche 911”
This backplate is “intricately reminiscent of the hood of a Porsche 911”, says HONOR. The company also says that it improves the grip of the phone, which is an added improvement, as the glass model is extremely slippery. The phone is available in one color, the Agate Grey, which is the color of a Porsche car.
The two companies also say that they “refined the choice of materials” here. The phone weighs only 234 grams and it’s 9.9mm thick. It comes with the industry’s first Anti-scratch NanoCrystal Shield.
The device has plenty of RAM & storage
The specifications remain unchanged compared to the regular HONOR Magic V2. This variant does top-out RAM and storage, though. It comes with 16GB of LPDDR5X RAM and 1TB of UFS 4.0 flash storage.
The Snapdragon 8 Gen 2 fuels the phone, while a 7.92-inch main display is used. That panel has a resolution of 2156 x 2344, and it’s an OLED display with up to 120Hz refresh rate. The cover display measures 6.43 inches, and it has a resolution of 2376 x 1060. That is also an OLED screen with up to 120Hz when it comes to resolution.
66W wired charging is supported, while three cameras sit on the back
A 5,000mAh battery is included here, while the phone supports 66W wired charging. A charger is included in the box. A 50-megapixel main camera (f/1.9 aperture, OIS, EIS) is backed by a 50-megapixel ultrawide camera (f/2.0 aperture). A 20-megapixel telephoto camera (40x digital zoom) also sits on the back of the phone. A 16-megapixel selfie camera is used here, on both displays.
There are two SIM card slots here, and Android 13 comes pre-installed. HONOR’s MagicOS 7.2 is also a part of the package. IR blaster is included, while the phone supports 5G connectivity and Bluetooth 5.3.
It goes on sale in China today, and it’s quite pricey
The Porsche Design HONOR Magic V2 RSR goes on sale in China today. Its pricing starts at CNY15,999 ($2,252). We’re not sure if the company will release this handset globally, but it’s possible, as the Magic V2 is coming to global markets.
More and more RMG apps will find a new home on Google Play, states the latest piece from the Android Developers Blog. RMG stands for real-money gaming and basically, it embodies any online game where money is staked on the outcome.
As 9to5Google reminds us, Google allowed gambling and betting Android apps to appear in the Play Store in 2021 in markets with pre-existing licensing frameworks. “Since then, this app category has continued to flourish with developers creating new RMG experiences for mobile”, Google says and adds:
Based on the learnings from the pilots and positive feedback from users and developers, Google Play will begin supporting more RMG apps this year, including game types and operators not covered by an existing licensing framework.
Google Play will launch the expanded RMG support in June to developers for users in India, Mexico, and Brazil. Later, the plan is to expand to more countries, if everything goes well.
Google Play’s existing developer policies supporting user safety, such as requiring age-gating to limit RMG experiences to adults and requiring developers to use geo-gating to offer RMG apps only where legal, remain unchanged. “We’ll continue to strengthen them”, the blog reads. In addition, Google Play will continue other key user safety and transparency efforts such as “expanded developer verification mechanisms”.
What’s more, there will be a service fee. Previously, the RMG apps had to be free to install and couldn’t use Google Play Billing, but this will change, as Google states: “We are working closely with developers to ensure our new approach reflects the unique economics and various developer earning models of this industry. We will have more to share in the coming months on our new policy and future expansion plans”.
Hackers use Qbot malware for its advanced capabilities, including keylogging, credential theft, and backdoor functionality.
Previously distributed Qakbot malware campaign was capable of monitoring the browsing activities of the infected computer and logs all information related to finance-related websites.
Qbot also enables the threat actors to create a persistent presence on infected systems, along with facilitating:
Further malicious activities
Potential financial gains
Cybersecurity researchers at Checkpoint recently discovered that threat actors actively use Qbot malware via FakeUpdates, leading to the race for malware attacks.
DocumentFree Webinar
Compounding the problem are zero-day vulnerabilities like the MOVEit SQLi, Zimbra XSS, and 300+ such vulnerabilities that get discovered each month. Delays in fixing these vulnerabilities lead to compliance issues, these delay can be minimized with a unique feature on AppTrana that helps you to get “Zero vulnerability report” within 72 hours.
Technical analysis
Four months after Operation Duck Hunt’s takedown, the Qbot malware was revived in December 2023. FakeUpdates topped the Threat Index and was found to be hitting the education sector hard.
Qbot resurfaces in a phishing attack on the hospitality sector, posing as IRS. Meanwhile, the DLL-triggered Qbot dominated for 10 months before its takedown.
FakeUpdates claims the top spot with a 2% global impact, while Nanocore holds third for six months. However, there are new entries that are from:
Qbot was spotted in the wild in less than 4 months post-infrastructure takedown. This shows that disrupting malware isn’t enough, as threat actors always adapt.
These are the reasons why researchers in the field of cybersecurity highly encourage firms to perform the following:
Implement proactive endpoint security
Perform thorough email scrutiny
Besides this, the following vulnerabilities are the most exploited, as they affect organizations globally:
The HONOR Magic6 arrived alongside its ‘Pro’ sibling today. The two phones are quite similar in terms of the design, but rather different when specs are concerned. They launched in China, while the global launch is expected later on. More on that later. That being said, let’s focus on the design of the Magic6 first, shall we?
The HONOR Magic6 is very similar to its sibling, but there are differences
The HONOR Magic6 is made out of metal and glass just like its sibling. It has a similar-looking camera island on the back, which is easy to differentiate from other phones. The thing is, the HONOR Magic 6’s camera island is a bit smaller than the Magic6 Pro’s.
This handset has a curved display on the front, with minimal bezels. It also has a hole punch which is centered at the top of the display. In that sense, it’s a bit sleeker-looking than the ‘Pro’ model, but it loses the 3D facial scanning functionality.
There is a 6.78-inch display included on the phone. This panel is curved and has a resolution of 2800 x 1264 pixels. It’s an LTPO AMOLED display, and its refresh rate can go from 1 to 120Hz. A 4,320Hz PWM dimming is included here too, to protect your eyes.
The Snapdragon 8 Gen 3 fuels this phone, while fast wired & wireless charging is also included
The Snapdragon 8 Gen 3 SoC fuels the phone, the same chip as on the HONOR Magic6 Pro. Both 12GB and 16GB RAM variants of the phone are available. The 12GB RAM model comes with 256GB of storage, while the 16GB RAM variant is available in both 256GB and 512GB storage flavors.
HONOR included a 5,450mAh battery inside of this phone. The device supports 66W wired charging and 50W wireless charging. A charger is included inside the retail packaging, by the way.
A 50-megapixel main camera (f/1.9 aperture, OIS) is backed by a 50-megapixel ultrawide camera (f/2.0 aperture). The third camera on the back is a 32-megapixel telephoto unit (f/2.4 aperture, OIS, 50x digital zoom). On the front, you’ll find a 50-megapixel wide-angle camera (f/2.0 aperture).
Android 14 comes pre-installed on the phone with HONOR’s brand new MagicOS version
Android 14 comes pre-installed on the device, along with HONOR’s MagicOS 8.0. Two SIM card slots are included, and the phone does support facial scanning, but only via the front-facing camera. A fingerprint scanner sits under the display. 5G is also supported, as is Bluetooth 5.3.
This handset launched in China, but it’s almost certainly coming to global markets. It could launch globally next month, during the MWC 2024. That hasn’t been confirmed yet, though, so take it with a grain of salt.
The HONOR Magic6 comes in Black, Glacier White, Lake Blue, Cloud Purple, and Epi Green colors. Its pricing starts at CNY4,399 ($619) in China.
Invati Connect Secure (ICS) and Ivanti Policy Secure Gateways have been discovered with two new vulnerabilities associated with authentication bypass and command injection.
The CVEs for these vulnerabilities have been assigned as CVE-2023-46805 and CVE-2024-21887. The severity of these vulnerabilities has been given as 8.2 (High) and 9.1 (Critical), respectively.
However, Ivanti has released a security advisory to address these vulnerabilities along with the patched version of the products.
It was also mentioned that Ivanti neurons for ZTA gateways cannot be exploited in production. UTA0178 actively exploited these vulnerabilities.
Exploitation in the Wild
According to the reports shared with Cyber Security News, a threat actor actively exploited these two vulnerabilities to steal configuration data, download remote files, and create a reverse tunnel from the ICS VPN appliance.
Moreover, the threat actor made several changes to the system to evade the ICS integrity checker tool.
In addition, the threat actor backdoored a legitimate CGI file on the ICS VPN appliance to enable command execution over the compromised system.
The attacker also modified the Web SSL VPN JavaScript file to keylog and extract users’ login credentials.
DocumentFree Webinar
Compounding the problem are zero-day vulnerabilities like the MOVEit SQLi, Zimbra XSS, and 300+ such vulnerabilities that get discovered each month. Delays in fixing these vulnerabilities lead to compliance issues, these delay can be minimized with a unique feature on AppTrana that helps you to get “Zero vulnerability report” within 72 hours.
Courses of the Incident
A curl command was for outbound connections to an IP Geolocation service through ip-api[.]com to Cloudflare’s 1.1.1.1 IP address. Additionally, reverse SOCKS proxy and SSH connections were established and downloaded from compromised Cyberoam appliances.
Lateral movements were also noticed through compromised credentials to connect to internal systems through RDP, SMB, and SSH. Furthermore, there was also the transfer of multiple webshell variants, termed as “GLASSTOKEN”, to Internet-accessible web servers and systems that were only internally accessible.
The attacker created and executed several files from the system’s /tmp/ directory, which were no longer on disk at the time of analysis. A list of the following paths was excluded on the list of Integrity Checker Tool,
/tmp/rev
/tmp/s.py
/tmp/s.jar
/tmp/b
/tmp/kill
During the course of the incident, Volexity distributed a few malicious files and tools, the most of which comprised of webshells, proxy utilities, and file alterations that allowed credential harvesting. This was despite the fact that Volexity observed the attacker practically living off the land for the most part.
In numerous instances, the attacker used compromising credentials to enter onto workstations and servers and dump LSASS process memory to disk via Task Manager.
The attacker extracted further credentials offline by exfiltrating this output.
The attacker accessed a system with Virtual Hard Disk backups, including a domain controller backup. After mounting this virtual hard disk, they extracted the Active Directory database ntds.dit file and compressed it using 7-Zip.
The attacker found a running Veeam backup software instance and used a GitHub script to steal passwords.
As said, the attacker updated JavaScript on the ICS VPN Appliance’s Web SSL VPN login page to steal credentials.
A complete report about this incident has been published, providing detailed information about the threat actor’s activities, webshell information, and others.
Value
Entity_type
Description
206.189.208.156
ipaddress
DigitalOcean IP address tied to UTA0178
gpoaccess[.]com
hostname
Suspected UTA0178 domain discovered via domain registration patterns
webb-institute[.]com
hostname
Suspected UTA0178 domain discovered via domain registration patterns
symantke[.]com
hostname
UTA0178 domain used to collect credentials from compromised devices
75.145.243.85
ipaddress
UTA0178 IP address observed interacting with compromised device
47.207.9.89
ipaddress
UTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
98.160.48.170
ipaddress
UTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
173.220.106.166
ipaddress
UTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
73.128.178.221
ipaddress
UTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
50.243.177.161
ipaddress
UTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
50.213.208.89
ipaddress
UTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
64.24.179.210
ipaddress
UTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
75.145.224.109
ipaddress
UTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
50.215.39.49
ipaddress
UTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
71.127.149.194
ipaddress
UTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
173.53.43.7
ipaddress
UTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
Looking for cost-effective penetration testing services? Try Kelltron’s to assess and evaluate the security posture of digital systems – Free Demo
It appears that YouTube might have removed the iMessage mini-app that allows iPhone and iPad users to send videos directly from chat without having to leave the Messages app.
The latest YouTube app update released earlier this week mentions changes like improved performance and bug fixes, but it may have also removed the iMessage mini-app.
The folks at 9to5mac confirm that the iMessage mini-app for iPhone and iPad is no longer available after the latest YouTube update, but at this time it’s impossible to tell whether or not this is something temporary.
It’s been nearly seven years since the iMessage mini-app has been added to YouTube. Unfortunately, it never became popular among iOS users, even though the app allowed them not just to send YouTube videos directly from the chat without leaving the Message app, but they could also watch videos using the native YouTube app.
Let us know in the comments if the feature disappears for you after updating the YouTube app to version 19.01.1. Although it might be hard to guess YouTube’s plans about the iMessage mini-app without an official statement.
AgentTesla is a notorious malware that functions as a keylogger and information stealer.
By logging keystrokes and capturing screenshots on infected systems, this notorious malware targets sensitive data like:-
Login credentials
Financial information
Recently, the cybersecurity researchers at BitSight Security discovered that AgentTesla malware had been actively attacking Windows machines to steal sensitive data.
DocumentFree Webinar
Compounding the problem are zero-day vulnerabilities like the MOVEit SQLi, Zimbra XSS, and 300+ such vulnerabilities that get discovered each month. Delays in fixing these vulnerabilities lead to compliance issues, these delay can be minimized with a unique feature on AppTrana that helps you to get “Zero vulnerability report” within 72 hours.
AgentTesla Malware Attacking Windows
AgentTesla is a .NET-written Windows malware that steals sensitive data and emerged for the first time in 2014. It faced legal issues once it was sold widely, leading to its shutdown in March 2019.
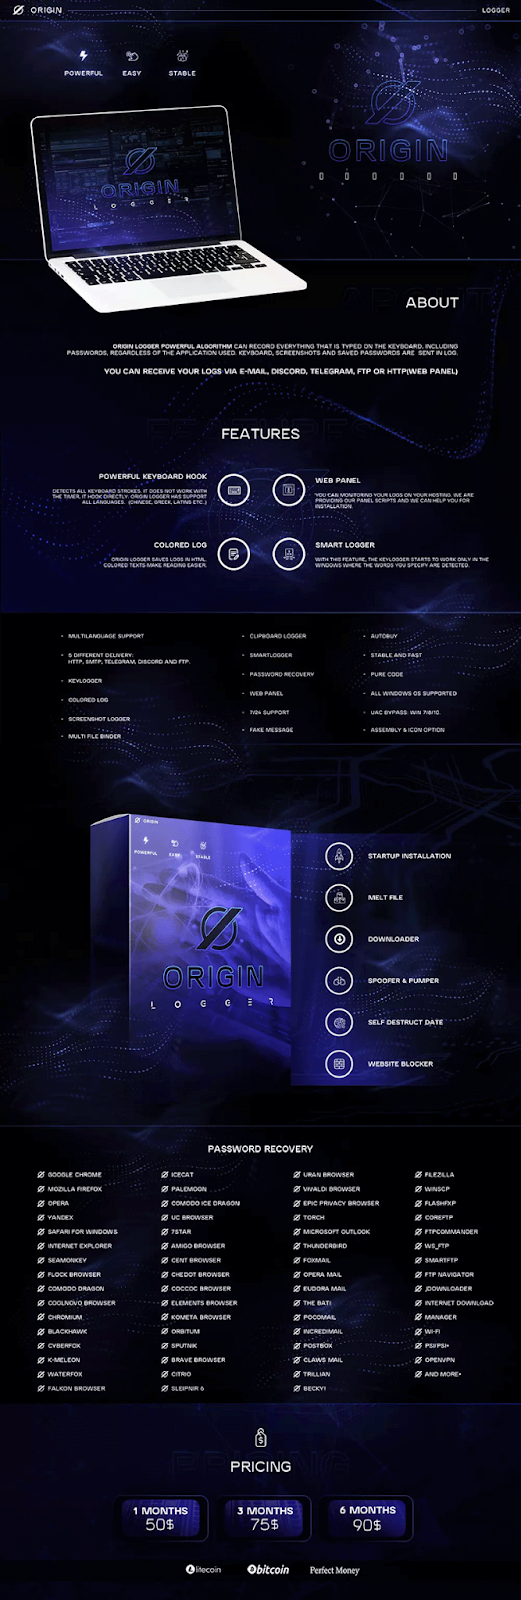
It later reemerged as OriginLogger, which shares the same code base and poses a persistent threat as a licensed-based Malware as a Service (MaaS) on the clear web with websites like-
agenttesla[.]com
originpro[.]me
OriginLogger (Source – Bitsight)
Researchers found that one of the sites sells short-term licenses (up to six months) for AgentTesla’s instance “OriginLogger” with several customizations.
AgentTesla is a prevalent malware that was rebranded and updated in November. It spreads via phishing emails with loaders like:-
After infecting it harvests the following data:-
Credentials
Keystrokes
Clipboard data
Screenshots
Not only that even, it also uses various protocols like:-
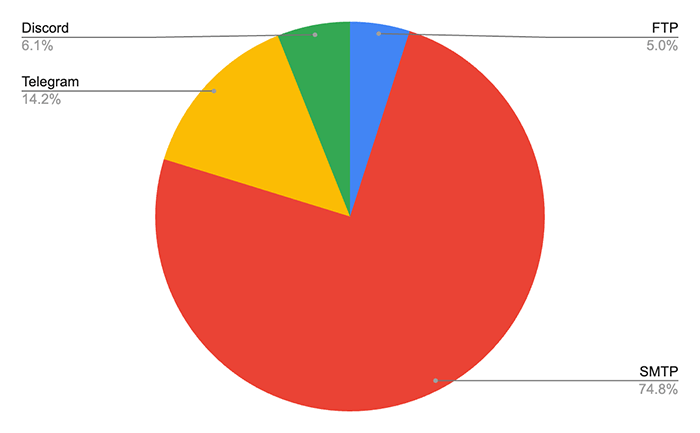
Over 1500 recent AgentTesla configurations were found, and 75% used email for exfiltration. However, since December 2022, no HTTP exfiltration has been observed.
Exfiltration methods by number of configs (Source – Bitsight)
The data gathered by the malware are mainly from:-
Browsers
VPN clients
Mail clients
FTP clients
VNC clients
Microsoft Applications
Social media apps
Pricing plans
In total, there are three plans, and here below, we have mentioned those three plans:-
1-month plan will cost $50
3-month plan will cost $75
4-month plan will cost $90
Researchers accessed 3 months of victim data from 210 malware campaigns, compromising 5300 computers between Oct-Dec 2023.
Around 2000 IP addresses were geographically mapped, which shows that the U.S. was the most targeted country, followed by
Common country top-level domains suggested European ties. Exploited data is used for direct exploitation and profit-driven schemes like ransomware and business email compromise attacks.
To counter the evolving threats, researchers urged to integrate the:-
Multi-layered defense mechanism
Proactive detection
Employee awareness
Robust cybersecurity strategy
Try Kelltron’s cost-effective penetration testing services for free to assess and evaluate the security posture of digital systems
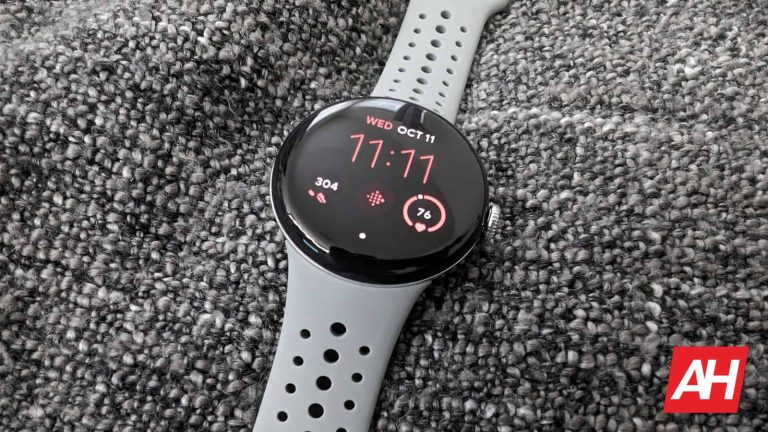
As the second week of January unfolds, Google is gearing up to release a new security patch. It will be the first security update of 2024 for the Pixel Watch and Pixel Watch 2. The tech giant has officially announced the commencement of the rollout for the January 2024 security update. It is specifically tailored for Pixel Watch devices operating on Wear OS 4.
For users eagerly awaiting the update, Google will make it available to the supported watches all over the world gradually over the next week. The phased rollout reportedly depends on the specific device and carrier.
Google recommends installing all available updates to receive the 2024 security patch
The company has primarily focused on addressing security vulnerabilities for the January 2024 security update. The build number of this update is TWD9.240105.004.A1, noted Google. You can explore the detailed changes accompanying the patch in the Android Security Bulletins. However, the emphasis is on enhancing the security posture of Pixel Watch devices. Users should expect fixes and improvements aimed at fortifying the device against potential threats.
To ensure Pixel Watch and Pixel Watch 2 users get the latest security enhancements, Google recommends users install the previously available updates. To do so, you can navigate to the Settings menu, scroll down to System, and select System Updates. Google will likely notify users on their watches when the over-the-air (OTA) update becomes accessible. Google staggers the release across carriers and devices to manage a seamless deployment.
The overarching objective of the January 2024 update is to equip Pixel Watch users with the latest security patches, aligning with Google’s commitment to providing a secure and up-to-date user experience. Users are encouraged to stay vigilant for notifications on their devices and promptly apply the update to fortify their Pixel Watches against potential security threats.
Apple doesn’t want visionOS apps to be called AR or VR
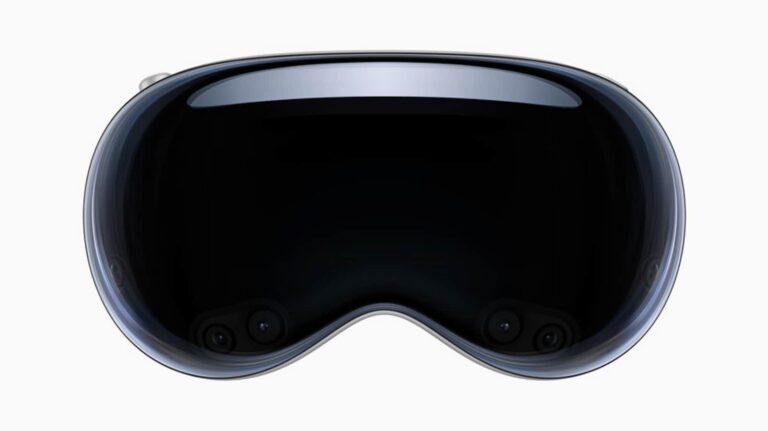
After Apple shared details about the Apple Vision Pro launch, they updated Xcode so that developers can now submit visionOS apps to the App Store. But there’s a rule: Apple doesn’t want developers to use terms like “AR” and “VR” for their new apps. They want to make it clear that visionOS is for spatial computing, not the traditional AR or VR stuff.
There’s more to it. The company has asked developers to avoid using terms such as AR, VR, XR, and MR, according to 9to5Mac. Notably, these terms stand for Augmented Reality, Virtual Reality, Extended Reality, and Mixed Reality, respectively. Notably, folks at TechRadar pointed out that Apple primarily markets the Vision Pro as a “spatial computing” platform. However, at the 2023 WWDC, Apple CEO Tim Cook presented it as an “entirely new AR platform.” You read it right, AR.
Apple’s new laws for developers
A new page on the Apple Developer website outlines all the recommendations and requirements for launching Apple Vision Pro apps on the App Store. The guidelines cover various aspects, including testing procedures, screenshot preparation, icon creation, and more.
Additionally, Apple provides instructions on how developers should name and describe their apps. Apple’s demand from developers to meet requirements such as using the lowercase “v” for the “visionOS” comes as expected. However, the rule against using AR or VR, nevertheless, stands out.
For users eager to experience the Apple Vision Pro, it comes at $3,499 for the 256GB storage variant. It is available exclusively in the US for now.