Multiple QNAP Severity Flaw Let Attackers Execute Remote Code

0
[ad_1]

QNAP has released multiple security advisories for addressing several high, medium, and low-severity vulnerabilities in multiple products, including QTS, QuTS hero, Netatalk, Video Station, QuMagie, and QcalAgent. 

QNAP has also stated all the affected products and their versions and the steps to update each product. The CVEs for these vulnerabilities are as follows:

  • CVE-2023-45039 (Low – QTS and QuTS hero)
  • CVE-2023-45040 (Low – QTS and QuTS hero)
  • CVE-2023-45041 (Low – QTS and QuTS hero)
  • CVE-2023-45042 (Low – QTS and QuTS hero)
  • CVE-2023-45043 (Low – QTS and QuTS hero)
  • CVE-2023-45044 (Low – QTS and QuTS hero)
  • CVE-2022-43634 (High – Netatalk)
  • CVE-2023-41287 (High-Video Station)
  • CVE-2023-41288 (High-Video Station)
  • CVE-2023-47219 (Low – QuMagie)
  • CVE-2023-47559 (High – QuMagie)
  • CVE-2023-47560 (High – QuMagie)
  • CVE-2023-39294 (Medium – QTS and QuTS hero)
  • CVE-2023-39296 (High – QTS and QuTS hero) 
  • CVE-2023-41289 (Medium – QcalAgent)

QTS and QuTS hero Vulnerabilities

CVE-2023-45039, CVE-2023-45040, CVE-2023-45041, CVE-2023-45042, CVE-2023-45043, and CVE-2023-45044 were associated with buffer copy, which was due to the insufficient checking in size of the input.

Exploiting this vulnerability could allow authenticated administrators to execute code through a network.

Document
Free Webinar

Compounding the problem are zero-day vulnerabilities like the MOVEit SQLi, Zimbra XSS, and 300+ such vulnerabilities that get discovered each month. Delays in fixing these vulnerabilities lead to compliance issues, these delay can be minimized with a unique feature on AppTrana that helps you to get “Zero vulnerability report” within 72 hours.

The severity of this set of vulnerabilities has been given as low, according to the QNAP security advisory. However, CVE-2023-39294 and CVE-2023-39296 were given medium and high severity as per the security advisories.

CVE-2023-39294 was associated with OS command injection, which could allow authenticated administrators to execute commands through a network.

At the same time, CVE-2023-39296 was related to prototype pollution that could allow remote users to override existing attributes with incompatible types, resulting in the system’s crashing.

QuMagie Vulnerabilities

CVE-2023-47219 was a low-severity vulnerability associated with SQL injection that could allow an authenticated threat actor to inject malicious code via a network. CVE-2023-47559 and CVE-2023-47560 were a set of high-severity vulnerabilities linked to Cross-site scripting and OS command injection, respectively. 

Both of these vulnerabilities require the threat actor to be an authenticated user. Exploiting these vulnerabilities could result in either the injection of malicious code (CVE-2023-47559) or the execution of commands through a network (CVE-2023-47560).

Video Station Vulnerabilities

CVE-2023-41287 and CVE-2023-41288 were another set of vulnerabilities reported on a QNAP security advisory. CVE-2023-41287 was an SQL injection vulnerability, and CVE-2023-41288 was an OS command injection vulnerability.

These vulnerabilities were marked as high severity by QNAP. However, both vulnerabilities affect Video Station version 5.7.x and have been fixed in Video Station 5.7.2 and later versions.

Netatalk and QcalAgent

The Netatalk vulnerability has been given the CVE-2022-43634, and its severity is high. However, QNAP has not released any other details about this vulnerability or its category. However, according to the security advisory, this vulnerability affects the QTS 5.1.x version and has been fixed in QTS 5.1.3.2578 build 20231110 and later.

CVE-2023-41289 was another OS command injection vulnerability reported to be affecting QcalAgent. This vulnerability was given as a medium severity in the security advisory and mentioned to be affecting QcalAgent 1.1.x

All of the affected products have been fixed, and patches have been released. It is recommended for organizations that use these products to upgrade to the latest versions to prevent becoming prey for threat actors. 


[ad_2]
Source link

Android 14 rolling out to Sony Xperia 1 IV, 5 IV and 10 IV

0
[ad_1]

Sony has released the Android 14 update for its 2022 smartphones. The company is pushing the big Android update to all three models launched in 2022: Xperia 1 IV, Xperia 5 IV, and Xperia 10 IV. It has already updated the 2023 lineup to the new Android version.

Sony rolls out Android 14 to Xperia 1 IV and other 2022 phones

Sony has a negligible, declining share in the global smartphone market but the Japanese firm hasn’t quit. It has religiously released at least three smartphones every year for the past several years. Its Xperia 10 lineup offers mid-range products, while the Xperia 1 and Xperia 5 lineups are premium offerings.

In early November of last year, Sony pushed Android 14 to the Xperia 1 V, the latest flagship model. It followed up with an update for the Xperia 10 V a week or so later. The Xperia 5 V joined the party last week. The company is now ready to move its 2022 Xperia lineup to Android 14. As usual, it took to X, aka Twitter, to announce the update for the Xperia 1 IV, Xperia 5 IV, and Xperia 10 IV.

The rollout has already begun, but it could take a while before Android 14 reaches all eligible units worldwide. Sony will gradually release the update for everyone over the next few days or weeks. You should get a notification once Android 14 is available for your Xperia. You can also manually check for updates from the Settings app on your Sony phone.

As far as new features are concerned, the update brings tons of Android 14 goodies and a few add-ons. Sony’s official announcement says the Xperia 1 IV, Xperia 5 IV, and Xperia 10 IV are getting flash alerts (LED flash or screen) for notifications and alarms. The devices also get enhanced customization of lockscreen shortcuts, compatibility with the Find My Device app, and expanded Nearby Share features.

These Sony phones may not get Android 15

Sony makes some of the most expensive Android phones but doesn’t match the prices with excellent update support. Its current update policy only guarantees two major Android OS updates and up to three years of security updates for Xperia phones. Under this policy, the Xperia 1 IV, Xperia 5 IV, and Xperia 10 IV are done getting Android updates.

Debuted in 2022, all three phones ran Android 12 out of the box. Sony has now updated them to Android 13 and Android 14. Unless the Japanese firm changes its mind in the coming months, the devices will not get Android 15. The Xperia 1 V, Xperia 5 V, and Xperia 10 V should get Android 15, though. They debuted last year running Android 13. We will let you know when we have more information.


[ad_2]
Source link

Xiaomi to show off its first electric car at MWC 2024

0
[ad_1]

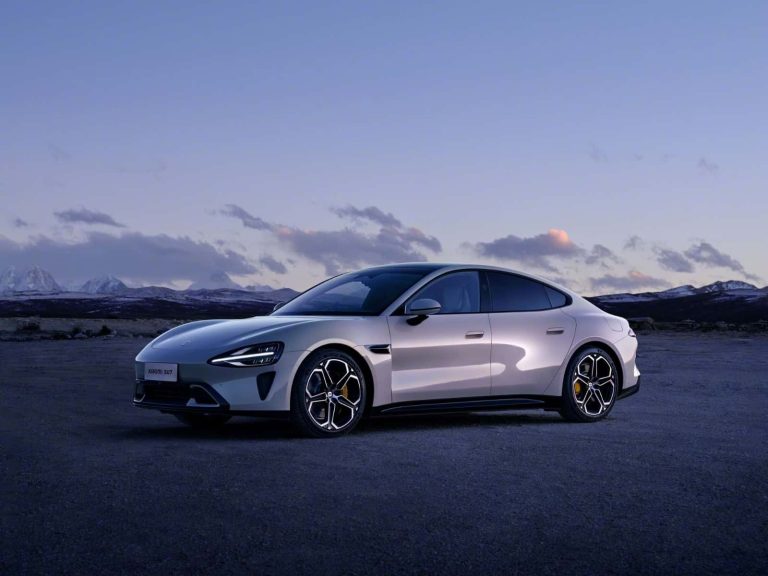
The Xiaomi SU7, Xiaomi’s very first electric car will be shown off at MWC 2024, it seems. The company kind of confirmed that via its latest MWC teaser on social media.

Xiaomi could show off its first electric car at MWC 2024 next month

If you check out the image below, you’ll see what I’m talking about. In it, the company reveals that it will be at MWC 2024. February 26-29 dates are also mentioned here, and those are the official MWC 2024 dates.

Xiaomi MWC 2024

Having said that, you’ll also notice the “Experience Human x Car x Home” part here. This is Xiaomi’s new branding for the unification of its services. HarmonyOS not only comes pre-installed on the company’s phones now, but also its first electric car.

This leads us to believe that the Xiaomi SU7 will be present at MWC 2024. The company cannot really demonstrate this without it. The Xiaomi 14’s global launch will also likely occur in Barcelona, so… there you go.

There will likely be some sort of an event for the Xiaomi 14 series & Xiaomi SU7

Xiaomi will likely host some sort of an event at MWC 2024, or right before it. We still don’t know the details, nor are we 100% it will happen. So stay tuned for that. If you’re in Barcelona between February 26 and February 29, though, you can check out Xiaomi’s booth at Hall 3 I 3M10.

Now, the Xiaomi SU7 was fully presented quite recently, at the very end of last month. Xiaomi showed off two models, the Xiaomi SU7 and Xiaomi SU7 Max. Those two cars look the same, but they’re different under the hood.

Truth be said, based on everything we’ve seen, the Xiaomi SU7 does look quite compelling. Xiaomi still did not share the price tags for the two models, nor did it mention any sort of global availability.

The company did promise that the Xiaomi SU7 series will become available in its homeland at some point this year.


[ad_2]
Source link

Hidizs ST2 Pro Digital IEMs coming soon with USB-C connector

0
[ad_1]

As the smartphone industry continues to ditch the 3.5 mm headphone jack, audiophiles will welcome the Hidizs ST2 Pro Digital IEMs. Hidizs has previously been known for other audio products like DAPs, but has recently taken an interest in IEMs. IEMs, or In-Ear Monitors, are earphones that go inside the ear canal and create a seal, usually with a silicone or foam tip. An example of popular IEMs would be Apple’s AirPods or Samsung’s Galaxy Buds (barring the Buds Live).

The Hidizs ST2 Pro Digital promises excellent sound

Hidizs isn’t really a big name in the IEM market, but their previous products show promise. The Hidizs MS5 are a pair of wired IEMs that deliver excellent sound and give competition to other $300 products. Though slightly tuned more in favor of a consumer-centric, “exciting” sound signature, it still packs a punch. Clarity is great, and imaging and instrument separation is also up to the mark.

Competitors lean more towards a neutral sound signature for more “clinical listening”. The MS5, on the other hand, is geared towards bass heads. It is able to reproduce bass and sub-bass cleanly and accurately without losing the oomph. It also looks great, and is built quite sturdily. They combine metal and resin for a tough pair of earphones resistant to falls. If the MS5 is anything to go by, we can expect the Hidizs ST2 Pro Digital to be about the same in technical capabilities.

Why choose USB-C over wireless?

While most consumers have long since moved on to Bluetooth audio gear, audiophiles cling to wired headphones. This is because of multiple reasons, many of which average users aren’t even aware of. For starters, wired audio gear is able to transmit lossless audio, while even the LDAC codec on Bluetooth isn’t quite there yet. Because of lossless transmission, wired audio gear also sounds much better and at a cheaper cost than wireless alternatives. This is also because wired earphones and headphones do not require batteries and built-in DACs.

Latency is another reason wired is superior to wireless. Though apps like YouTube compensate for Bluetooth audio lag by delaying video playback, games cannot do the same without introducing input lag. So people who play competitive games on their phones prefer wired audio over wireless.

There is currently no release date or info on availability for the ST2. However, TechRadar reports the company is releasing its USB-C to 3.5 mm adapter DAC in February. This DAC promises to deliver high quality sound, and could be a much more convenient replacement for the USB-C dongles you can buy today.


[ad_2]
Source link

How to optimize your cloud spend with FinOps

0
[ad_1]

More organizations are steadily moving to the cloud due to the perceived advantages of shifting their workloads to the cloud. However, some organizations are often stunned when they discover how much they spend on cloud services within a particular period. This is often because of a lack of coordination, collaboration, and cloud optimization in such organizations.

FinOps stands as the ultimate solution to optimizing cloud costs, but businesses and companies do not often recognize it. Nevertheless, FinOps balances the quality of work and the cost of daily operations when implemented in any organization. In this article, we will discuss the meaning of FinOps, some of the FinOps principles, and how to optimize cloud usage using FinOps.

What is Finops?

In FinOps definition, it is generally a set of practices whereby individuals, departments, and organizations as a whole try to reduce how much they spend on cloud services. FinOps is a combination of “Finance” and “DevOps” to form a compound word, simply a collaboration between an organization’s finance and engineering teams. Apparently, this collaboration between these two categories aims to identify methods of reducing cloud costs without negatively impacting the quality of work.

It can also be defined as introducing financial accountability between teams in an organization. This will help them take responsibility for their cloud spending and seek and implement cost-reduction methods. The focus of FinOps isn’t only on reducing costs; it ensures a business entity cuts down costs while operating with as much quality as possible. On the part of the engineering team, FinOps helps them to identify better features, business models, apps, and other things that will improve the quality of work. FinOps also includes tools that help reduce cloud costs and introduce innovation in cloud services, such as Globaldots.

In the discussion of FinOps, there’s what is known as the FinOps Principles, and they are simply some elements that make up an excellent FinOps practice. According to the FinOps Foundation, six principles guide the practice of FinOps, and they include:

– Collaboration

One of the important elements or principles that must be present for the practice of FinOps is collaboration among all the departments in an organization. The finance, engineering, technology, product, and business should work together to ensure they promote cost optimization, innovation, and efficiency in an organization.

– Value-Driven Decision Making

Another principle guiding the practice of FinOps is that decisions made by the organization must align with the value of the cloud. In other words, the decisions each department in the organization makes should have a balance between the cost, innovation, and quality they get from the cloud services.

– Personal Ownership of Cloud Usage

The primary focus of FinOps in organizations is that everyone must take responsibility for the cloud services they use. For instance, those in the engineering department take responsibility for the cost of developing things like apps and web solutions. Hence, each department should have their own cloud budget, and they should tailor their cloud usage according to their assigned budget.

– Accessible and Timely FinOps Data

In implementing FinOps, one of the principles is that data should always be accessible and timely to make informed decisions. To make this possible, each department in an organization should always process and share cloud cost and usage data immediately when it becomes available. Furthermore, there should be real-time visibility, which will help different departments plan and forecast.

– Centralized FinOps Team

A centralized FinOps team is both a necessity and principle of any FinOps practice as they help to oversee what is happening and enforce accountability among departments. Note that the FinOps team only enforces accountability, and each department is still responsible for its cloud costs.

– Variable Cost Model

In the practice of FinOps, organizations should take massive advantage of the variable cost model as it offers proactive system design. Using a variable cost model in FinOps ensures an organization chooses iterative planning rather than less-dynamic long-term plans.

How to Optimize Cloud Spend with FinOps

Below, we will discuss some of the ways an individual or a company can optimize how much they spend on cloud services using FinOps:

– Important to Choose the Right Storage Type

Choosing the right storage type is something that some organizations overlook when discussing FinOps, which often leads to wastage. For instance, Amazon S3 is one of the most commonly used cloud storage options, and there are reasons many people are going for this type of cloud storage. Some of them are that the Amazon S3 is much easier to use and a large chunk of unlimited storage is delivered to users. Another thing to consider is choosing a cloud storage that allows the integration of other AWS and third-party vendor services.

– Right-sizing of Cloud Resources

Right-sizing cloud resources is another crucial step an organization must take to optimize its cloud costs. For instance, if an organization wants to use a cloud resource for around 3 months, they should choose a 1-year plan when paying for it. In other scenarios, an organization shouldn’t pay for a cloud resource meant for 1,000 employees when they only have 100.

– Close Monitoring of Software Licensing Fees

The amount of money spent on software licensing fees is a massive contributor to cloud costs in many organizations. Some organizations sometimes pay software licensing fees for cloud services they don’t use. Hence, there’s a need to deploy tools such as Globaldots, as they often have tracking features to help identify idle software.

– Correction of Cost Anomalies

Some organizations don’t pay attention to some of the cloud services and resources they pay for until they start eating deep into their budget. Hence, correcting cost anomalies early before they heavily impact a department’s cloud budget is very important.

Wrapping Up

As a final note, FinOps is simply those practices that, when implemented in an organization, help introduce innovation and improve the quality of work while reducing the cost of operations. Nevertheless, certain principles guide the implementation of FinOps in any organization.

These principles include collaboration, accessible and timely FinOps data, value-driven decision-making, and many others. Moreover, an organization can optimize its cloud costs by right-sizing its resources, choosing the right storage type, and correcting cost anomalies.


[ad_2]
Source link

Incorporat mobile threat defense device management ecosystem

0
[ad_1]

In recent years, we have seen a significant shift in the global workforce. With the proliferation of high-speed internet and advanced communication tools, remote work has become the new norm for countless professionals. This transition hasn’t just been about convenience; it’s also about embracing the power of mobile devices.

The transition to remote work was well underway before the global pandemic, but COVID-19 dramatically accelerated the adoption of remote work practices. Companies across various industries embraced remote work models to ensure business continuity and employee safety.

However, this shift towards remote work and mobile device dependence has brought new IT challenges to the forefront. The very devices we rely on for work and personal tasks are now the primary targets of cyber threats. Malicious acts are increasingly targeting mobile devices to access sensitive data, compromise corporate networks, and disrupt business operations.

Bridging vulnerability gaps with expanding attack surfaces

The explosive growth in mobile device and app usage has created a vast attack surface, presenting an enticing target for cybercriminals. Despite this, security budgets and staffing levels have not kept pace with the expanding threat landscape. According to the Cyber Security in Focus 2023 report, this year was the first time CISOs considered their budgets to be the biggest barrier to strategy execution. Consequently, security teams are grappling with ever-widening vulnerability gaps. These gaps have far-reaching consequences, as demonstrated by the following statistics.

According to a 2022 Juniper Research report, e-commerce fraud was predicted to increase from $41 billion to a staggering $48 billion in losses in 2023 for online merchants. The emergence of alternative payment methods, such as digital wallets, are contributing to the escalating financial impact of e-commerce fraud.

Zimperium’s 2023 Mobile Threat Report highlights that 70% of digital fraud now occurs on mobile devices, emphasizing the critical importance of mobile security.

Addressing the post-COVID-19 security challenges

As we step into 2024, enterprise security teams are still dealing with the aftermath of the COVID-19 pandemic and the dramatic shifts it accelerated. The adoption of various tools and modalities—telehealth, remote and hybrid work models, cloud storage, SMS-based multi-factor authentication, and QR codes—has surged in recent years, presenting new security challenges.

Security teams have also faced an increase in the number of devices and employees working remotely. The Verizon Mobile Security Index 2022 reported that 79% of organizations surveyed agreed that remote work had adversely affected their cybersecurity and increased the burden on security teams. The 2022 report also pointed out that almost two in three chief information security officers (CISOs) across all regions agree that remote work makes their organization more vulnerable to cyberattacks.

Additionally, the Verizon 2023 Mobile Security Index reported that 62% of companies had experienced a security compromise that was at least partly attributable to remote work in the past three years.

Escalation of cyberattacks

The concerns expressed by security teams are well-founded, as major cyberattacks continue to rise. A survey reported in the Verizon Mobile Security Index 2022 found that 45% of companies surveyed suffered a security compromise in the past 12 months, marking a 22% increase compared to the previous year. This data illustrates the urgency of addressing mobile security in an environment where attacks are becoming increasingly prevalent.

Mobile threat defense: A necessity for protecting sensitive data

To combat the evolving threat and protect sensitive business data, organizations must turn to mobile threat defense (MTD). MTD tools are comprehensive security solutions designed to safeguard mobile devices and apps, and the data they contain from a wide range of threats. MTD’s importance lies in its ability to:

1. Provide continuous monitoring and threat detection, ensuring subtle and evolving threats are identified and mitigated in real-time.

2. Support compliance with stringent regulatory requirements for data protection.

3. Maintain uninterrupted productivity in an era where remote work is integral to many organizations.

Integrating mobile device management with MTD

Mobile device management (MDM) solutions allow you to oversee both device management and automated monitoring of your mobile security posture across your mobile device fleet. Administrators can efficiently monitor the overall device security, view threat alerts, and generate comprehensive reports on security incidents.

MDM allows organizations to remotely manage and secure mobile devices by enforcing policies, restricting access to certain apps or resources, and ensuring device compliance. MDM solutions are often used in conjunction with MTD solutions to enhance security. This adds an additional layer of control, enabling organizations to maintain a secure mobile environment.

  1. Facilitate threat detection with just a few clicks:
  2. An MDM solution simplifies threat detection by providing real-time alerts and advanced analytics, making it easier for IT administrators to monitor and respond to security incidents swiftly.
  3. Evaluate device security constantly:
  4. An MDM solution continually assesses device security, ensuring that smartphones and tablets meet established security standards. Any deviations from these standards trigger immediate notifications and remediation actions.
  5. Configure proactive security measures:
  6. Organizations can proactively set up security policies and controls, ensuring that mobile devices adhere to best practices, including encryption, app allowlisting, and network access policies.
  7. Lockdown vulnerable devices:
  8. In the event of a security breach or non-compliance with security policies, IT administrators can remotely lock down vulnerable devices, preventing unauthorized access and data leakage.

For organizations seeking a comprehensive and robust mobile security solution, the integration of Mobile Device Manager Plus with Check Point Harmony offers a powerful combination. Harmony Mobile, a leading cybersecurity platform, provides advanced threat prevention, zero-day protection, and secure access to network resources. When integrated with Mobile Device Manager Plus, this synergy enhances the security of mobile devices and corporate data, while streamlining the management of these devices.

A passionate technical writer with a motive to demystify complicated tech jargon into simpler ideas!


[ad_2]
Source link

Accenture Buys 6point6 to Expand Cyber Portfolio

0
[ad_1]

Accenture, a global professional services company, has made a strategic move in the U.K. market by acquiring 6point6, a leading technology consultancy specializing in cloud, data, and cybersecurity. 

This acquisition, announced on October 31, 2023, significantly enhances Accenture’s capabilities in these crucial areas, particularly within central government, defense and security, and financial services.

Integrating 6point6’s expertise seamlessly aligns with Accenture’s existing cloud, data, and cybersecurity strengths. 

This synergy will allow Accenture to offer its clients in the U.K. a more comprehensive and integrated suite of services, enabling them to leverage the full potential of these transformative technologies. 

The addition of approximately 400 skilled technologists from 6point6 further bolsters Accenture’s talent pool, providing immediate access to specialized knowledge and experience.

Focus on Key Sectors:

The acquisition strategically targets key sectors in the U.K. market, including central government, defense and security, and financial services. 

These sectors face unique challenges in navigating the complex cloud, data, and cybersecurity landscape. 

6point6’s proven track record in these areas, coupled with Accenture’s global reach and industry expertise, will create a powerful combination to address the specific needs of these demanding clients.

Looking Ahead:

While the deal’s financial terms remain undisclosed, the strategic implications of the acquisition are clear. 

Accenture is positioned to significantly strengthen its position in the U.K. market, particularly in the high-growth cloud, data, and cybersecurity areas. 

This move also aligns with Accenture’s global growth strategy, which focuses on expanding its capabilities in key sectors and markets


[ad_2]
Source link

TCL has a new 115-inch TV that Probably Weighs More Than You!

0
[ad_1]

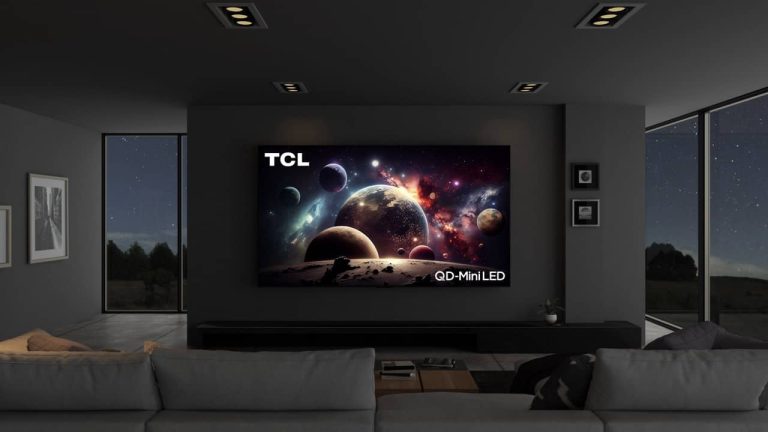
On Monday, at CES 2024, TCL announced a set of new TVs. As one typically does at CES, it is the Consumer Electronics Show after all. But when so many other companies are releasing new TVs at CES today, you really have to grab our attention, and TCL did. It announced the new TCL QM8 TV, which now comes in a 115-inch size. The official model number is 115QM89. We don’t have pricing or availability yet, but TCL has told me that they will be pricing this pretty cheap for what it is. So expect a few thousand and not a few tens of thousands here.

As you might expect, this is a heavy TV, too. It’s technically about four times the size of a 65-inch TV since TVs are measured diagonally. That means this TV is a few hundred pounds, around 250 lbs actually. So it probably weights more than you.

What really catches your eye with the 115QM89 is the sheer size and brightness. This is a 115-inch TV, which is just massive and the largest single display on the market today. There are other larger TVs, like Samsung’s The Wall, but that use multiple smaller display panels that connect together. With this TV, TCL is touting 5,000 nits of peak brightness, which is absolutely incredible. No matter how much ambient lighting you have in a room, you’re going to be able to see this TV.

That’s not the only large TV TCL is announcing today

TCL also has a couple of other large TVs on display at CES this week, which includes a pair of 98-inch TVs in the QM8 and QM7 lineup. The QM7 is essentially a smaller upgrade to last year’s QM7 lineup. This one uses premium High Zone QD Mini LED with precise control of up to 1,500+ Zones. It also has a new High Brightness Ultra LED Backlight that also has incredible brightness with up to 2,400 peak nits of brightness.

The company is also adding a native 120Hz panel refresh rate on all screen sizes, with Game Accelerator 240, HDR Ultra with Dolby Vision IQ, and a 2.1-channel speaker system.

Then there’s the QM8, which is a slightly higher-end model from TCL. The TCL QM8 includes QD Mini LED Ultra for ultra-high zone dimming with up to 5,000+ zones. That is also twice the number of zones of the previous flagship level for truly inky blacks. It includes all of the features of the QM7, along with an Anti-Glare Screen to maintain contrast in ambient room light conditions. There are built-in Dolby Atmos speakers, too.

Finally, coming a bit down to earth, TCL also has the Q6 Pro series. This is a less-expensive model that still offers some really great features, and also comes in smaller sizes. Making it more affordable. The Q6 Pro series will offer TVs from 50 inches up to 85 inches. It also has all of the great features from the Q6 model, along with a Full Array of Local Dimming, which provides for deeper and more inky black levels. As well as about 33% more brightness with 600 peak nits.

Pricing nor availability has been announced for any of TCL’s new TVs. We expect that to happen in the next few months since these TVs aren’t going on sale right away. Last year, TCL’s TVs that were announced at CES did not go on sale until May, so we’d expect the same sort of timeline this year.


[ad_2]
Source link

Unlock Endless Possibilities with the Lenovo ThinkBook Plus Gen 5 Hybrid

0
[ad_1]

Lenovo usually comes to CES in Las Vegas with a number of laptops and a few interesting ones as well. Instead of a foldable laptop this year, Lenovo is debuting the ThinkBook Plus Gen 5 Hybrid. This is a hybrid laptop that can run both Android and Windows seamlessly.

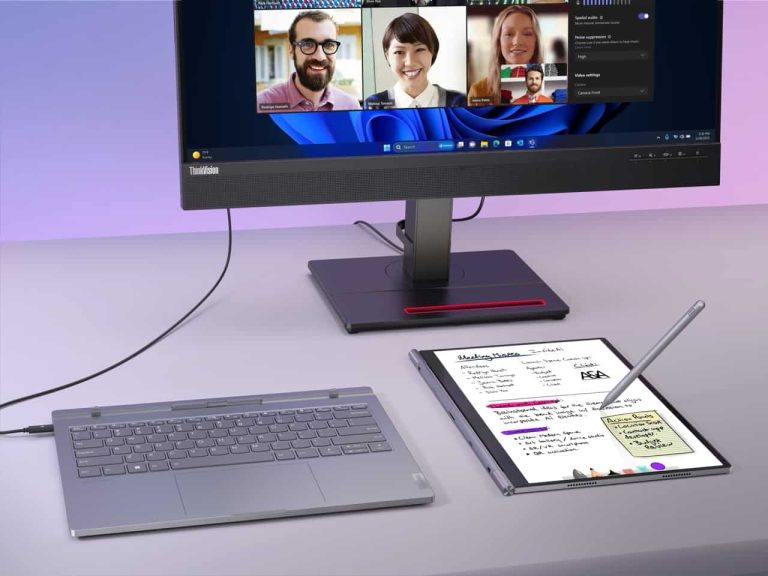
But this still isn’t your usual laptop from Lenovo. The ThinkBook Plus Gen 5 Hybrid is a base system and a tablet that can work independently or together and seamlessly switch from laptop to tablet. Think of the Microsoft Surface; it’s pretty similar to that, except it runs two operating systems.

What’s attractive here is that the base station and the tablet both have individual processors, as well as RAM, storage, and graphics. Making it really interesting.

The Hybrid Station comes with an Intel Core Ultra 7 processor, 32GB of LPDDR5x RAM, 1TB of PCIe Gen 4 SSD storage, and the Intel Arc GPU. It does also include two USB-C ports (Thunderbolt 4), and a combo audio jack.

Meanwhile, the actual tablet houses a Qualcomm Snapdragon 8+ Gen 1 processor, with 12GB of LPDDR5x RAM, 256GB of UFS 3.1 storage, and the Qualcomm Adreno graphics inside. It does have a single USB-C port. There is also a stunning 14-inch 2.8K OLED touchscreen with pen support.

This is a two-product laptop from Lenovo

It’s a little hard to wrap our heads around this, considering it’s using both Intel and Qualcomm processors for each operating system. But it is a way for Lenovo to offer both operating systems without giving one of them the shaft. Android doesn’t really support Intel chipsets, and Windows doesn’t really work well on ARM chipsets like the Snapdragon 8+ Gen 1.

Lenovo says that you can use these separately. So you could plug the base into a monitor for a desktop-like experience while using the tablet as an Android tablet at the same time. It’s not something I’ve really ever thought about needing to do, but it is an interesting thing to do here.

The Lenovo ThinkBook Plus Gen 5 Hybrid will go on sale in the second quarter with a starting price of $1,999.

@androidheadlines

These new Lenovo ThinkBook laptops will blow your mind #lenovo #ces24 #tech

♬ original sound – Android Headlines


[ad_2]
Source link