Why Virtual Board Portals are the Key to Better Collaboration and Decision-Making

0
[ad_1]

Meetings without paper have become a reality thanks to advanced technologies. Digital tools help companies be more efficient while staying focused on their daily routine. Instead of traditional table books and paper documents, all the necessary board materials are stored and accessible via a secure digital platform, known as table management software. 

What are paperless council meetings? 

A digital meeting refers to a business gathering conducted electronically, eliminating the need for traditional paper documents. In such meetings, organizers can instantly access, examine, and annotate meeting materials, agendas, and presentations on their electronic devices.

Embracing paperless council meetings contributes to sustainability by reducing paper waste and diminishing the energy consumption linked to printing, storing, and distributing physical documents. Additionally, the shift to paperless board meetings boosts the overall efficiency of meeting processes and cultivates enhanced communication among directors. 

Why should you enhance Collaboration and Decision-Making with Virtual Board Portals?

Here are the top 7 reasons to switch to paperless meeting software: 

Save time for board members

One of the greatest advantages of smart board software is that directors can use it to exchange relevant updates and documents and study them to prepare for a board meeting.

Then, once the event starts, they can go directly to conversation and decision-making. No endless updates, no boring reports. Only collaboration and fruitful discussions. 

The management of the board of directors is impossible without good budget management. As we’ve mentioned before, traditional meetings can be rather expensive. If you consider board software pricing, you will at least reduce the expenses related to printing all those paper copies that directors need to discuss.

If you decide to organize a virtual event, expenses will decrease considerably because you will not have to cover the travel of directors. Instead of paying for office space, accommodation, and travel, you will only have to support a paperless board meeting solution. 

Improve the efficiency of board meetings

The simple fact that the boards of directors do not need to go through updates at the beginning of the meeting already means that they will not be tired before they start discussing. Therefore, they can think clearly because they are not tired of listening to reports.

In addition, advice portals allow directors to create meeting agendas so that everyone can propose ideas before they take place. The paperless meeting solution provides members with different tools such as votes and polls that can improve the decision-making process. 

Improve collaboration between board members and employees.

Most consulting portal providers allow users to integrate this software with other business tools. According to the knowa board portal overview, this makes it easy to connect the consulting portal to the applications that employees use to synchronize the flow of undocumented documents and thus control the progress of tasks.

According to Nicholas Cooper – CEO of board-rooms.co.uk: “Moving to paperless meetings with this software creates a fluid and centralized workspace for managers, allowing them to stay in touch with employees even without office space”.

Make access to information easy

The paperless meeting management software can be accessed from any device and location, as long as a user has an Internet connection. This means that directors will not encounter delays or problems simply because they cannot receive a printed document. All the information downloaded from the digital board meeting portal is easy to access and members can study it even on the go.

Protect company data

Data leaks are not a joke. They are expensive and can to the company’s reputation once customers have realized that their sensitive data has been exposed. It is therefore crucial for a company to protect its information, and the board portal solution is perfect for this. This software allows you to hold paperless board meetings while keeping company documents reliably protected.

Criminals can’t access a board of directors portal because suppliers secure their servers and their customers’ repositories by encryption. For the benefit of board members and better protection, administrators can use additional security features such as two-factor authentication.

Make your advice flexible

Are the directors of your board located in different countries? Is anyone currently on a business trip? No problem, you can move on to paperless meetings by simply organizing the online event using videoconferencing software and a board portal.

Technology enables us to be flexible and focus less on office space. Take advantage of this opportunity to hold a virtual board meeting, even if some participants cannot physically attend.

Conclusion

Board meetings are electronic meetings of board directors, also known as paperless board meetings. During paperless meetings, directors can access, review, and annotate documents, agendas, and presentations in real-time using an Internet connection and their electronic devices.

Organizing paperless board meetings improves the efficiency of meetings and communication between leaders. It is one of the most efficient methods for Better Collaboration and Decision-Making.

  1. Maximizing Roi With The Best LMS For Elearning
  2. Technology and Software Redefine Business Operations
  3. Using GenAI in Your Business? Here Is What You Need To Know
  4. Learning Management System: What is it and Why do you need it?
  5. Top learning management system (LMS) software for small businesses

[ad_2]
Source link

Galaxy A53 and Galaxy A32 5G get December update in the US

0
[ad_1]

Samsung‘s December security update is available for Galaxy A53 and Galaxy A32 5G users in the US. The latest security patch has been already released for the former in international markets but the rollout for the latter has begun stateside. A few other A-series phones also recently picked up this month’s update.

Galaxy A53 grabs December update in the US

The December SMR (Security Maintenance Release) is available for the carrier-locked version of the Galaxy A53 in the US. The premium mid-range smartphone is getting the update with the firmware build number A536USQS8DWL2. The rollout began a few days back and should soon reach all eligible units, including the unlocked version. Samsung has already updated the device to the December security patch in several other markets.

For the Galaxy A32 5G, the Korean firm is beginning in the US. The aging mid-range phone is picking up the December SMR with the build number A326USQSCDWL1 for carrier-locked units. A wider rollout shouldn’t be too far away for this model either. The international model of the device has yet to receive the update. Samsung might expand its coverage to other regions over the next few days.

The company’s official changelogs confirm that neither phone is getting anything more than this month’s security fixes with the latest update. The December security release for Galaxy devices is a big one. It contains fixes for more than 60 vulnerabilities. Several of those were critical security flaws in Android OS. You can check for new updates through the system Settings app on your Android-powered Samsung phone.

The latest security update is available for more Galaxy devices

Over the past few days, Samsung has also released the December SMR for the Galaxy A73 and Galaxy A52s. Neither model was sold in the US but users in other markets should receive the update soon. The new build numbers for the duo are A736BXXS6DWL2 and A528BXXS5FWL4, respectively. Unsurprisingly, neither phone is picking up additional goodies. They recently received the Android 14-based One UI 6.0 update.

The Galaxy A53 is also coming fresh from the Android 14 update. The Galaxy A32 5G, meanwhile, hasn’t received it and likely won’t. It debuted with Android 11 and picked up updates to Android 12 and Android 13. It is unclear whether Samsung plans to push a third major Android OS upgrade to the three-year-old phone. If the device gets Android 14, we will let you know as soon as the rollout begins.


[ad_2]
Source link

MediaTek unveils collaboration with TSMC for 3nm Dimensity 9400

0
[ad_1]

MediaTek and TSMC have reportedly joined forces to develop the Dimensity 9400, the company’s upcoming 3nm System-on-Chip (SoC). Building on their successful partnership in creating the 3nm SoC, which boasts a remarkable 32 percent improvement in power efficiency compared to its predecessors, both companies are gearing up for the launch of their first joint product.

While the exact name of the chipset has not been officially confirmed, speculation points towards it being named the Dimensity 9400. MediaTek’s CEO, Rick Tsai, recently shed light on this collaboration, emphasizing the strategic alliance’s focus on optimizing efficiency for the upcoming chipset. With the absence of low-power cores similar to the Dimensity 9300, the partnership aims to address potential power draw challenges, possibly leveraging AI and neural cores for specific tasks.

The collaboration for the 3nm Dimensity 9400 reportedly goes beyond just the fabrication

As MediaTek and TSMC extend collaboration on ultra-low power technology, industry insiders anticipate a significant improvement in performance and, especially, power efficiency. The upcoming 3nm SoC from MediaTek will hopefully continue its success trajectory, with the Dimensity 9300 already acclaimed as the most powerful smartphone chipset currently available.

CEO Rick Tsai’s optimistic outlook for 2024 underscores the impact of the artificial intelligence (AI) boom on MediaTek’s fortunes. With MediaTek offering chips tailored for the AI category, next year promises to be a positive turning point for the company.

Rumors surrounding the 3nm Dimensity 9400 suggest a CPU cluster configuration featuring a Cortex-X5 paired with an unnamed CPU design, ensuring unparalleled multi-core performance. Despite the absence of efficiency cores in the Dimensity 9400, a close-knit collaboration between TSMC and MediaTek may mitigate potential power draw challenges. However, Qualcomm will also adopt TSMC’s 3nm fabrication process and may even go for a deeper collaboration like MediaTek as well.

As the race for superior silicon intensifies, both MediaTek and Qualcomm will introduce their cutting-edge SoCs in the coming year, setting the stage for an intriguing showdown in the world of mobile chipsets.


[ad_2]
Source link

Weather in the Google Clock app is much prettier, but there’s a catch

0
[ad_1]

Pixel users have enjoyed a feature where they’d see the weather forecast after dismissing their morning alarms for a few months now. It’s a nice way to start off your day, but the company doesn’t seem to be happy with the presentation. According to a new report, the weather in the Google Clock app is getting a nice revamp.

We’ve also heard about this feature a while before it actually launched. When you dismiss your alarm in the morning, you’ll immediately see a brief forecast of the current day and the next day. This feature is only for Pixel users, so most of the Android smartphone market is left in the dust. We’re not sure if the company is planning on bringing it to more phones in the future.

Weather in the Google Clock app is getting a revamp

As useful as this feature is, Google just doesn’t think that it’s pretty enough. This is why it’s getting a pretty major facelift. This change will look familiar to you if you’re used to setting up Pixel phones all the time. You’ll see large and bubbly animations of shapes in the background. This matches Google’s Pixel aesthetic that stock Android is now known for.

On top of the shapes, you’ll see the forecast for the day. On the top left of the screen, you’ll see the current conditions. A bit lower in the UI and to the right, you’ll see the projected conditions for the day. At the bottom of the screen, you’ll see the Okay thanks button to dismiss it.

So, this is a nice and convenient feature to have for your app. There’s only one little issue. This is a situation where an app loses some function for the sake of fashion. The older version would show you the forecast for the current day and the next day. After the revamp, it only shows you the conditions for the current day.

So, you’ll need to go to the Weather app to see the conditions for future days.


[ad_2]
Source link

Microsoft doubles down on generative AI with standalone Copilot app for Android

0
[ad_1]
Microsoft Copilot, the AI companion chatbot designed to collaborate with people on creative tasks, is now sporting its own dedicated app on Android. Powered by GPT-4 and DALL-E 3, this free app stands ready to unleash its creative and informative powers on your smartphone.
Spotted by eagle-eyed users, the Copilot app quietly landed on December 19th on the Google Play Store, offering a streamlined experience for AI enthusiasts. Currently, there is no listing on iOS for this app, however, Bing for iOS is still an option.
While no logins are required, anonymous users face a daily limit of five prompts and shorter responses, which can be unlocked by signing in with your Microsoft account. Signing in does grant unlimited queries and opens the door to image generation, turning your phone into a mini-art studio powered by DALL-E 3.

Image credit: Microsoft via Google Play Store

While Copilot’s functionality might seem familiar, it’s more than just Bing AI in disguise. This app ditches the web search clutter, focusing solely on AI-powered interaction. Ask complex questions, get simplified explanations, or have Copilot whip up creative text of any kind – it’s all at your fingertips. And the best part? It understands text, image, and even voice prompts, making interaction natural and intuitive.

The Microsoft Copilot app running on a Google Pixel device with GPT-4 toggle turned on

Microsoft’s been on a mission to integrate this AI powerhouse everywhere, from Windows 11 to Bing. This dedicated app could be the next step in its evolution, positioning Copilot as a standalone digital assistant that thrives beyond the confines of web browsers.

Offering this app for free, while bundling GPT-4 and DALL-E 3, is a bold move by Microsoft. Currently, using the free version of OpenAI’s ChatGPT only grants you access to the GPT-3.5 model, and will cost you $20/month to upgrade to the Plus plan that unlocks GPT-4 and DALL-E.

So, if you’re looking for a taste of next-generation AI on your phone, look no further than Microsoft’s Copilot app. It’s free, it’s powerful, and it’s just getting started. The future of AI assistance is here, and it’s fitting right in your pocket.

[ad_2]
Source link

Nim-Based Malware Delivered via Weaponized Word Document

0
[ad_1]

Hackers use weaponized Word documents to deliver malicious payloads through social engineering. 

By embedding malware or exploiting vulnerabilities in these documents, attackers trick users into opening them and leading to the execution of malicious code. 

While leveraging the familiarity and trust associated with such file format, this tactic is effective for several illicit purposes:-

  • Spreading malware
  • Gaining unauthorized access
  • Initiating other cyber attacks

Recently, cybersecurity researchers at Netskope identified a new Nim-based malware, which was delivered via weaponized Word documents by the threat actors.

Nim is a new language that sees a rising malware trend, and experts at Netskope Threat Labs note growing Nim-based threats, anticipating further popularity. 

Among them, the most notable one is “Dark Power” ransomware, which is also a variant of the Nim-based family that surfaced recently.

Nim-Based Malware via Word Document

The malicious Word doc drops the Nim backdoor, which is sent as an email attachment by a fake Nepali official. 

Despite macro security, APT malware, like Menorah, which used a similar tactic months ago, still leverages macros for payload delivery. 

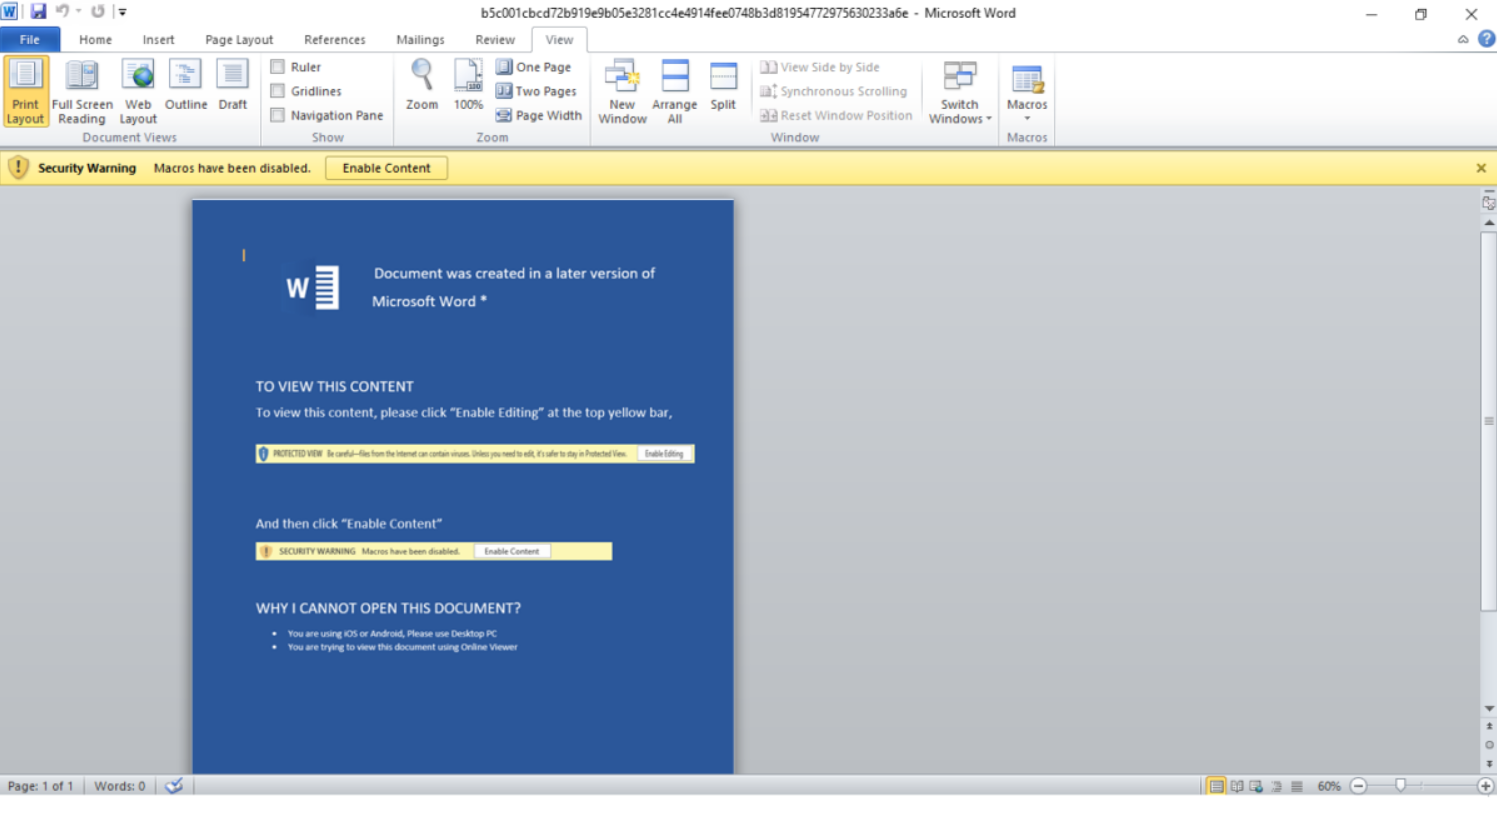
Malicious Word file prior to enabling macro
Malicious Word file prior to enabling macro (Source – Netskope)

Besides this, opening the file shows a blank doc, prompts macro to enable, and then the clicking triggers the:-

  • Auto-routine
  • Code execution

VBA project uses passwords and obfuscation to dodge AV solutions. At the same time, the macros employ Chr( ) and string concatenation. 

Apart from this, the code is divided into four subroutines, and here below we have mentioned them:-

  • sch_task
  • hide_cons
  • read_shell
  • vb_chain

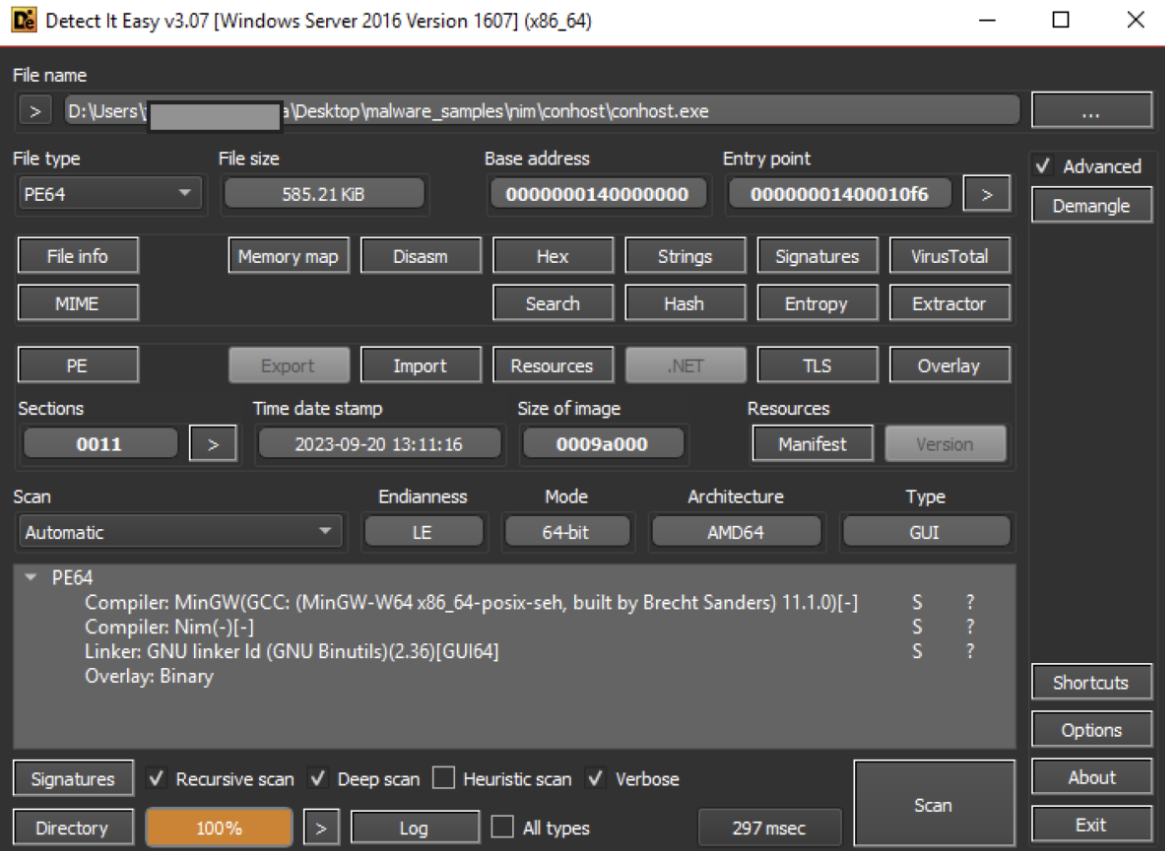
Word doc deploys Nim-based ‘conhost.exe’ backdoor on September 20, 2023. Nim is a versatile language that compiles the following languages together with Pythonic syntax:-

Backdoor operates with user’s privileges, mimicking Nepali authority to deceive users. C&C server imitates government domains ([.]govnp[.]org).

Nim Backdoor
Nim Backdoor (Source – Netskope)

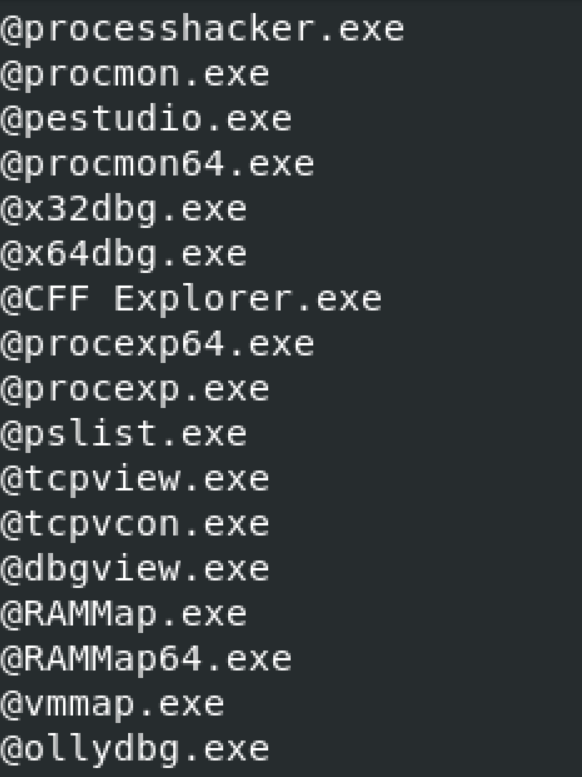
Nim backdoor checks for analysis tools and terminates if found. Then, it fetches the hostname and encrypts it with the ‘bakery’ function.

Processes the backdoor avoids
Processes the backdoor avoids (Source – Netskope)

The encrypted hostname double-base64 encoded, which was:-

  • Spliced with C&C server URL
  • Suffixed with ‘.asp’

The C&C server issues the commands via HTTP GET, the response is decrypted by the ‘confectionary’ function, executed with cmd /c, and then the result is sent back to the server. 

Besides this, for encryption and decryption, “NPA” was used as the key, potentially Nepal Agent.

Here below, we have mentioned all the C2 hosts that were contacted:-

  • mail[.]mofa[.]govnp[.]org
  • nitc[.]govnp[.]org
  • mx1[.]nepal[.]govnp[.]org
  • dns[.]govnp[.]org

The VBscript ‘OCu3HBg7gyI9aUaB.vbs‘ in the startup folder ensures access. Confirms internet connection, pings Google. 

On success, it runs ‘8lGghf8kIPIuu3cM.bat,’ and the batch file drops the files and creates tasks for payload. 

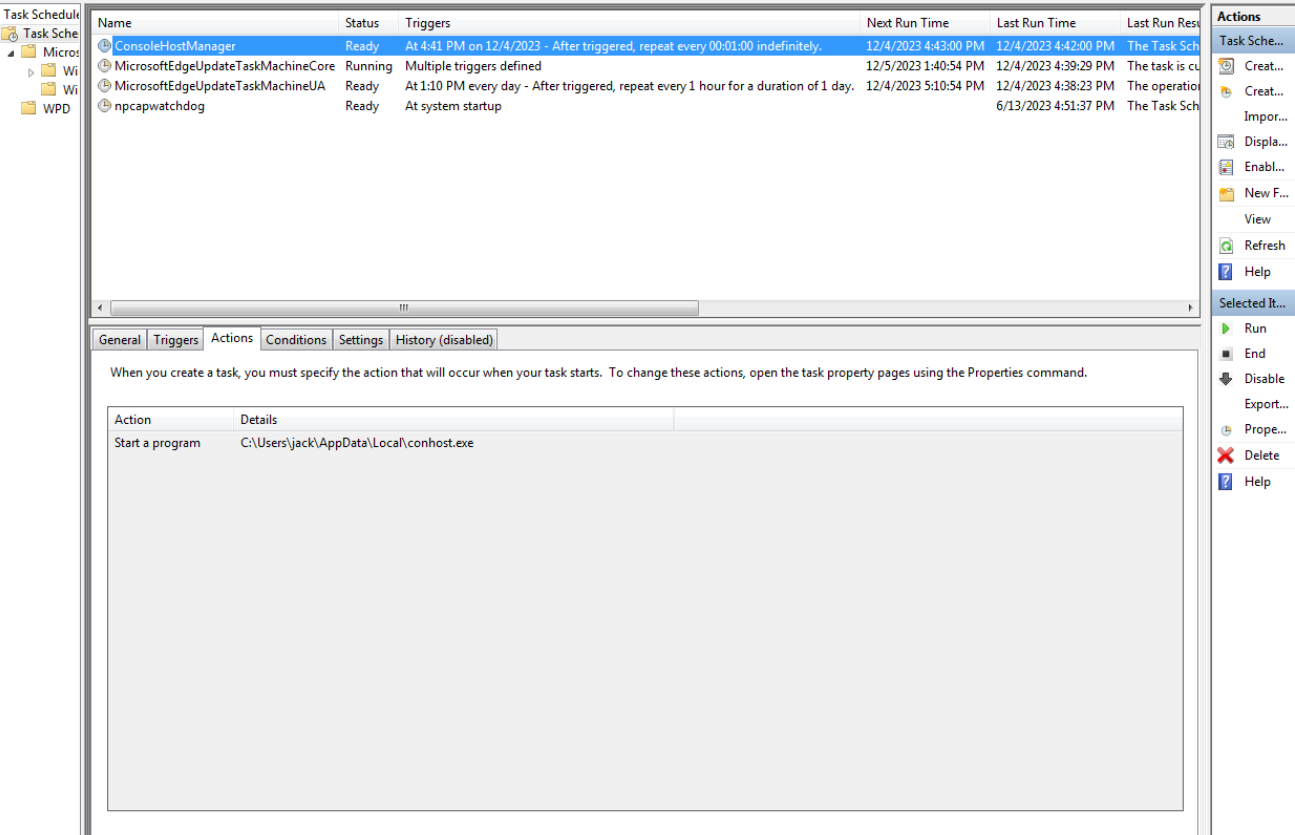
Meanwhile, the ‘d.bat’ establishes the persistent execution with the scheduled task ‘ConsoleHostManager.’

Scheduled Task
Scheduled Task (Source – Netskope)

Malware in rare languages challenges security experts, and the cross-compilation in Nim aids hackers in creating obstacles for security analysts.

IOCs

MD5

  • e2a3edc708016316477228de885f0c39
  • 777fcc34fef4a16b2276e420c5fb3a73
  • EF834A7C726294CE8B0416826E659BAA
  • 32C5141B0704609B9404EFF6C18B47BF

SHA-1

  • 3aa803baf5027c57ec65eb9b47daad595ba80bac
  • 5D2E2336BB8F268606C9C8961BED03270150CF65
  • 4CAE7160386782C02A3B68E7A9BA78CC5FFB0236
  • 0599969CA8B35BB258797AEE45FBD9013E57C133

SHA-256

  • b5c001cbcd72b919e9b05e3281cc4e4914fee0748b3d81954772975630233a6e
  • 696f57d0987b2edefcadecd0eca524cca3be9ce64a54994be13eab7bc71b1a83
  • 88FA16EC5420883A9C9E4F952634494D95F06F426E0A600A8114F69A6127347F
  • 1246356D78D47CE73E22CC253C47F739C4F766FF1E7B473D5E658BA1F0FDD662

Network

  • mail[.]mofa[.]govnp[.]org
  • nitc[.]govnp[.]org
  • mx1[.]nepal[.]govnp[.]org
  • dns[.]govnp[.]org

[ad_2]
Source link

National Amusements Reveals Data Breach Affecting 82,000+

0
[ad_1]

Paramount and CBS’s parent company, National Amusements, took months to reveal the data breach that has impacted more than 82,000 people, including customers and potentially employees as well.

National Amusements, the parent company holding a controlling stake in entertainment giants Paramount, CBS, and numerous theatres across the United States, has come under scrutiny for delaying the disclosure of a major data breach that occurred late last year. The breach impacted 82,128 individuals, comprising both customers and potentially National Amusements employees.

The breach, which went unnoticed for months, was finally reported to the Maine Attorney General. According to the company’s statement, an “unauthorized individual” accessed the company network on December 13, 2022. However, National Amusements only became aware of the intrusion two days later.

Regarding the data affected in the breach, it includes information like name or other personal identifiers combined with financial account number or credit/debit card number (along with the security code, access code, password, or PIN for the account).

National Amusements Reveals Data Breach Affecting 82,000+ Amid Backlash
The data breach notification was submitted to the Maine Attorney General.

The company enlisted the services of a third-party firm to investigate the breach, a process that concluded “recently.” Curiously, the data breach was only officially acknowledged on August 23 of this year, possibly aligning with the completion of the external investigation.

Despite attempts from the media to seek clarification from National Amusements, the company has maintained near-radio silence, leaving questions about the delayed disclosure unanswered.

Currently, the company asserts that there have been no reports of stolen data being exploited by third parties or leaked online. Nevertheless, National Amusements has proactively taken measures to mitigate the aftermath, providing those affected with complimentary credit monitoring services through Experian for varying durations.

If you’re an employee of National Amusements or one of its customers, be cautious about phishing emails. Cybercriminals might impersonate the company to discuss the recent data breach, but their real intention could be to gather additional information, including your financial details. Stay vigilant and verify the legitimacy of any communication you receive related to the incident.

  1. OurMine hackers hack Marvel and Netflix Twitter accounts
  2. Best legal, free online streaming sites for movies, TV shows
  3. Hackers Leak First 8 Episodes of Steve Harvey’s “Funderdome”
  4. Soap2day Shuts Down Permanently – Free Legal, Paid Alternatives
  5. Potential 500GB Nickelodeon Leak: Unreleased Shows, Scripts at Risk

[ad_2]
Source link

200MP camera with 10x optical & 200x digital zoom

0
[ad_1]

The Vivo X100 series launched not long ago. The Vivo X100 Pro is already a true camera powerhouse, but the upcoming Vivo X100 Pro+ is looking to up the ante even more. According to a new rumor, the Vivo X100 Pro+ will not only feature a 200MP periscope telephoto camera, but also some great zoom capabilities as part of it.

The Vivo X100 Pro+ to come with a 200MP camera that enables up to 200x digital zoom

The new rumor says that 10x optical zoom will be enabled on the phone, which is not something you see often. Also, that camera will be able to provide 200x digital zoom. The quality of that digital zoom probably won’t be great, but still, it’s quite impressive to see.

Just to be clear, this information comes from Digital Chat Station, one of the most prominent tipsters out there. That fact alone gives it a lot of credibility, so that’s what we’re expecting now.

That phone will almost certainly be fueled by the Snapdragon 8 Gen 3 chip. Its sibling, the Vivo X100 Pro, comes with the MediaTek Dimensity 9300 chip. In addition to that, a QHD LTPO AMOLED display is also expected.

The Sony LYT-900 camera sensor is expected for the main camera

The Sony LYT-900 camera sensor is said to be used for the main, 50-megapixel camera on the device. The same camera sensor OPPO will use in the OPPO Find X7 Pro flagship. The phone’s ultrawide camera is also expected to be quite compelling. It could be the same as on the Vivo X100 Pro, though.

The Vivo X100 Pro+ could be more appealing to some consumers due to a new chip. The MediaTek Dimensity 9300 has proven to be quite a capable chip, but it also does heat up quite a bit.

The Vivo X100 and Vivo X100 Pro initially launched in November. They landed about a month later, in December, in global markets. The Vivo X100 Pro+ is expected to land in Q1 next year, but nothing has been confirmed yet.


[ad_2]
Source link

The New York Times is suing OpenAI and Microsoft for ‘Billions’ of dollars

0
[ad_1]

Generative AI is just one year into the public, and there have been a ton of lawsuits thrown around regarding this technology. Two of the biggest players in the AI game are now being sued by one of the biggest publication companies. The New York Times is now suing OpenAI and Microsoft over copyrighted material.

This is one of many lawsuits going around nowadays. Several artists, writers, musicians, celebrities, etc. are taking AI companies to court for using their material without their consent. In order to train AI, companies need to scrape a ton of data from thousands of websites. This data could be in the form of pictures, text, music, vocal samples, and so on.

Then, AI companies use the stolen material in their services. Image generators create pictures using image data scraped from artists. That’s just one example. The lawsuits are just going to keep flowing in as AI companies continue to scrape data.

The New York Times is suing OpenAI and Microsoft

When an AI chatbot gives you information on a major legal case that occurred in recent history, you’re likely to see excerpts from news articles. Guess what, you’re probably looking at an excerpt from a copyrighted and paywalled article from the New York Times. The NY Times is one of the major forces in American journalism, and it’s not too happy with OpenAI.

OpenAI’s ChatGPT is the most popular chatbot on the market, and it’s a reservoir of a metric ton of scraped data. Well, The New York Times says that the company scraped millions of articles from the publication. This, according to the company, resulted in billions of dollars in damages. Whether or not that equates to billions of dollars, we don’t really know.

According to the report, The New York Times tried to reach out to the companies in order to come to some sort of accord, but that fell through. So, this seems to be the only course of action left.

When it comes to big cases like these, there’s no telling what could happen. It seems unlikely that the companies will lose billions of dollars in the suit. There’s always the chance that the entities will settle behind closed doors. We’ll need to wait for more information on this matter as it comes out.


[ad_2]
Source link

Possible Data Exfiltration by Hackers

0
[ad_1]

Ubisoft, the renowned video game developer behind iconic franchises like Assassin’s Creed and Far Cry, narrowly escaped a potentially devastating data breach. 

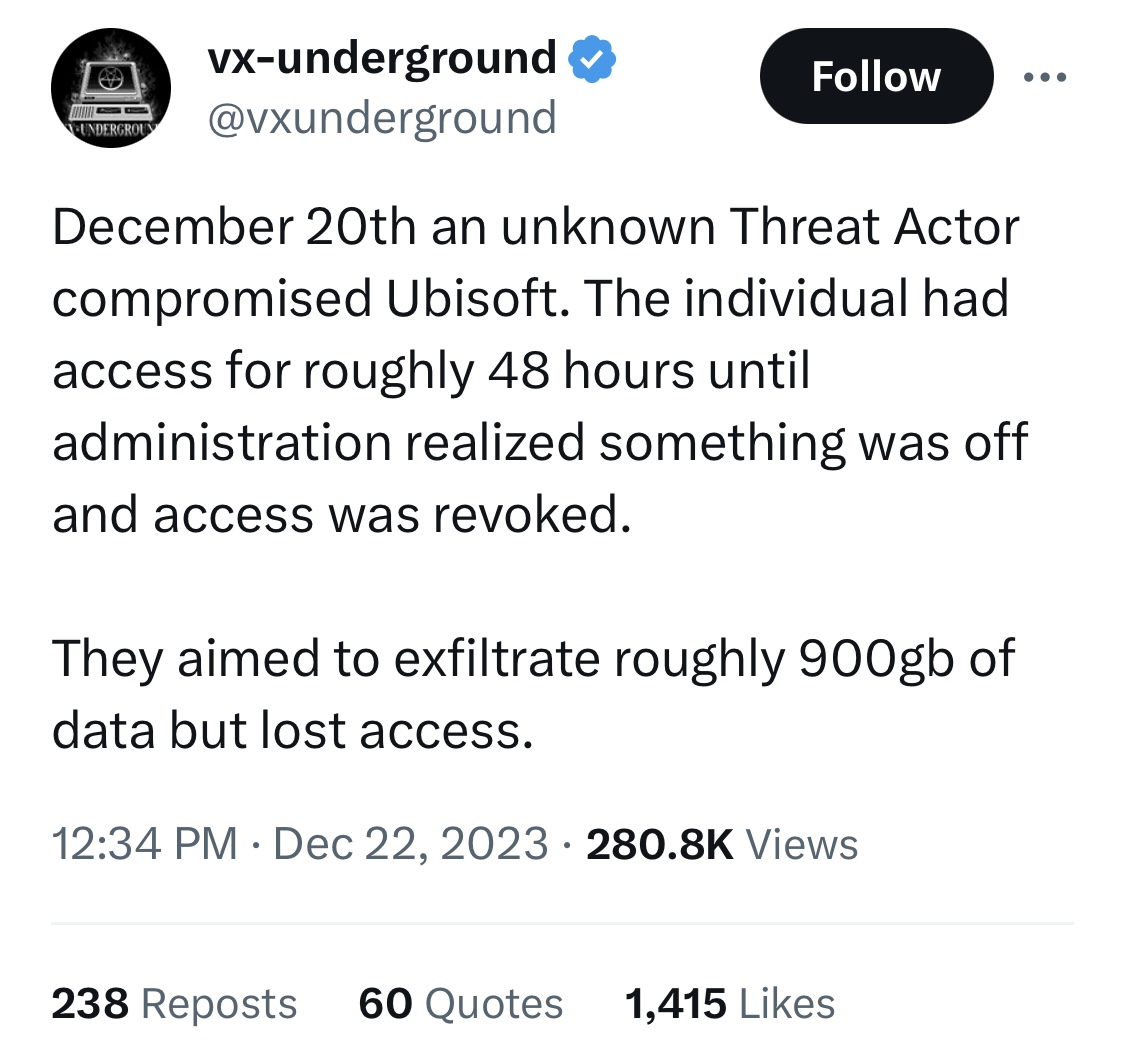
On December 20th, an unidentified threat actor infiltrated their systems, gaining access for approximately 48 hours before Ubisoft’s eagle-eyed security team detected the anomaly and revoked access.

The precise nature of the attack remains shrouded in mystery. 

Details regarding the initial access vector, the attacker’s tools and techniques, and the specific vulnerabilities exploited are still under investigation. 

However, what is known is that the individual gained access to Ubisoft’s internal network and embarked on a brazen attempt to exfiltrate a staggering 900 gigabytes of data.

Malware collective vx-underground shared screenshots provided by hackers of Microsoft Teams accounts and other access points to Ubisoft.

The news was posted on the @vxunderground Twitter page.

Detection and Response

While the exact size and nature of the targeted data remain undisclosed, the sheer volume – roughly equivalent to the storage capacity of 1800 standard DVDs – suggests the attacker sought to acquire a substantial trove of sensitive information. 

This could potentially include source code, game assets, player data, or even internal company documents.

Fortunately, Ubisoft’s security team swiftly identified the suspicious activity, acting commendably and decisively. Within 48 hours of the initial infiltration, they managed to sever the attacker’s access and prevent data exfiltration. 

This swift response undoubtedly saved the company from a potential public relations nightmare and potentially devastating financial losses.

Aftermath and Unanswered Questions

While the immediate threat has been neutralized, the incident leaves a lingering shadow of uncertainty. 

Ubisoft is currently conducting a thorough investigation to uncover the full scope of the attack, identify the vulnerabilities exploited, and implement additional security measures to prevent similar incidents in the future.

The gaming community awaits further details with bated breath. 

Speculation swirls regarding the attacker’s motives, the specific data targeted, and the potential consequences had the exfiltration been successful. 

Ubisoft has assured players that no personal information was compromised.


[ad_2]
Source link