Generative AI may change the world (the gaming world, that is)

0
[ad_1]

Each day, we learn more of generative AI’s endless possibilities and its potential impact on several industries. While it’s set to make some major changes to the human world, there are several frontiers it’s going to explore in the meantime; one of which is gaming. Generative AI is soon set to have some major effects on the gaming world.

Generative AI exists in different forms; thus, it can impact gaming in several key areas. These include production time and NPC interactions. As for when we’ll feel the effects of AI in gaming, we’re not 100% sure. Several industry insiders say that it’s on the scale of years. So, for the time being, the gaming industry is still primarily driven by manpower, and many of us prefer it that way.

Generative AI can affect the gaming world in a few ways

Besides making tools to help users generate absurd images and generate college essays, AI companies are also making tools that help workers speed up productivity. Many businesses use models like GPT-4 and Gemini to assist workers with their tasks, and gaming companies are no exception. According to a study conducted by CNBC, 72% of workers said that AI technology actually helps speed up productivity. That’s not far off from the results of a study that Microsoft conducted.

With faster production speeds, games are expected to be produced more timely. “generative AI is already in use by lots of people. Programmers use Copilot and ChatGPT to help them write code, concept artists experiment with Stable Diffusion and Midjourney, and so on,” says Julian Togelius, New York associate professor of computer science.

Generative AI could also help with NPC interactions

Game companies using AI should come as no surprise, as many major companies are using AI. Google plans to use AI tools in its ad sales department. However, there’s a company looking to bring AI into the actual games. Many games nowadays use scripted interactions between playable characters and NPCs. Well, there are some companies looking to change that sometime in the near future.

Imagine interacting with a villager and having a completely unique conversation that no other player in the world is having. This is something that a company called Inworld is planning on doing, and it’s partnering with Microsoft to make it happen. Basically, the company is looking to work on technology that will let NPCs “evolve beyond predefined roles, adapt to player behavior, learn from interactions, and contribute to a living, breathing game world,” said Kylan Gibbs, co-founder and chief product officer of Inworld AI.

We won’t know how that’s going to be for another couple of years. The companies are still working on this technology, so who knows when we’ll see the first game using generative AI?


[ad_2]
Source link

Cisco to Acquire Multi-Cloud Network & Security Startup Isovalent

0
[ad_1]

In a strategic move destined to fortify its dominance in the ever-evolving realm of cloud security, Cisco has officially declared its intent to acquire Isovalent, a trailblazer in open-source cloud-native networking and security. 

This bold acquisition underscores Cisco’s steadfast commitment to empowering organizations of varying sizes to navigate the intricacies of multi-cloud environments with unparalleled security and efficiency.

The union of Cisco’s industry-leading security prowess with Isovalent’s groundbreaking open-source technologies, including eBPF and Cilium, promises to reshape how organizations approach and manage cyber risks across diverse cloud infrastructures. 

This formidable synergy is set to propel the Cisco Security Cloud vision—an AI-driven, integrated platform designed to provide advanced protection against emerging threats at every layer of the cloud ecosystem.

Envisioning a Secure Multi-Cloud Future

Imagine a future where security seamlessly envelops applications, virtual machines, containers, and cloud assets across distributed environments. 

Jeetu Patel, Executive Vice President and General Manager of Security and Collaboration at Cisco, anticipates this reality through the combined might of Cisco and Isovalent. 

Incorporating Cilium’s power will birth a unique multi-cloud security and networking capability, simplifying and accelerating digital transformation journeys.

Isovalent’s proficiency in eBPF, a revolutionary technology offering unprecedented visibility into operating system internals, has led to the development of Cilium—a preferred solution for cloud-native networking and security. 

Recent innovations, such as Cilium Mesh and Tetragon, enhance the acquisition’s comprehensiveness, providing simplified hybrid cloud connectivity and eBPF-based runtime security enforcement.

A Commitment to Open Source

Cisco’s unwavering commitment to open source is showcased through its promise to nurture, invest in, and contribute to the eBPF and Cilium communities. 

Stephen Augustus, Head of Open Source at Cisco, highlights the collaboration’s potential to accelerate innovation, positioning the Cisco Security Cloud platform as the definitive answer to evolving customer needs.

This acquisition reinforces Cisco’s position within the Cloud Native Computing Foundation and eBPF Foundation, establishing its role as a cornerstone of the open-source ecosystem. 

The collaboration between these industry giants promises to unleash the full potential of eBPF technology, ensuring the safeguarding of workloads irrespective of their cloud residency.

The anticipated closing of the acquisition in the third quarter of fiscal year 2024 will witness the Isovalent team seamlessly integrating into Cisco’s Security Business Group.


[ad_2]
Source link

DOJ saves millions for victims of the Blackcat Ransomware Group

0
[ad_1]

The US Department of Justice (DOJ) has successfully disrupted the notorious Blackcat ransomware group, also known as ALPHV or Noberus. This follows the DOJ’s investigation into Apple’s alleged anti-competitive practices. After hitting Henry Schein with two major ransomware attacks in less than two months, the hacking collective targeted over 1,000 computer networks and extorted millions of dollars from victims. Thankfully, the DOJ’s intervention has halted the operation at least up to some extent, and the DOJ has noted that it’s just the beginning.

“Criminal actors should be aware that the announcement today is just one part of this ongoing effort. Going forward, we will continue our investigation and pursue those behind Blackcat until they are brought to justice.”

The Blackcat ransomware group, known for its members communicating in Russian (as noted by Bloomberg), has been a thorn in the side of businesses and organizations globally. Deputy Attorney General Lisa O. Monaco stated in a DOJ news release, “In disrupting the BlackCat ransomware group, the Justice Department has once again hacked the hackers.”

FBI’s decryption tool rescues over 500 victims of the Blackcat Ransomware Group

The FBI played a crucial role in this operation, developing a decryption tool that aided more than 500 Blackcat victims in recovering their data. This initiative saved victims over $68 million in ransom payments. The FBI not only provided decryption assistance but also gained visibility into the Blackcat ransomware group’s computer network, allowing the seizure of several of its websites.

The modus operandi of Blackcat involves developers creating and updating ransomware software, which “affiliates” deploy in attacks on high-value targets. The developers and attackers then share the illicit profits. Once the hackers infiltrate a network, they steal sensitive data before encrypting the victim’s system. The hackers then demand a ransom, threatening to expose confidential information if the victim denies to pay the ransom.

The group promised decryption and non-disclosure of sensitive information to the victims who paid the ransom, while they left those who resisted locked out. The hackers also exposed their data on the dark web. Blackcat’s targets included major entities like MGM Resorts, Caesars Entertainment, critical infrastructure, and Reddit in the US and Europe, encompassing government facilities, emergency services, defense companies, critical manufacturing, healthcare facilities, and a large UK hospital group.

As the cat-and-mouse game continues, the DOJ’s message is clear: criminal actors involved in cybercrime will be pursued relentlessly until they are held accountable for their actions.


[ad_2]
Source link

Ubisoft Hackers Scrambled for 900GB of Data Before Foiled

0
[ad_1]

Ubisoft Entertainment SA, a French video game publisher, has confirmed an attempt to breach the company’s security to steal personal and sensitive data from its infrastructure.

According to sources, an unknown threat actor accessed Ubisoft’s internal tools on December 20th, allegedly aiming to obtain 900GB of data. After entering the French game publisher’s internal systems, the hacker reviewed users’ access rights and Microsoft Teams, Confluence, and SharePoint. However, Ubisoft managed to revoke access after 48 hours.

Ubisoft, famous games like Assassin’s Creed and Avatar: Frontiers of Pandora, is investigating the breach to determine how the “unknown threat actor” allegedly gained access to the company’s Microsoft Teams, Confluence, Atlas, and SharePoint channels and maintained access for 48 hours before Ubisoft revoked access.

It’s worth noting that the latest cybersecurity incident at Ubisoft occurred just a year after the company was compelled to issue a password reset due to a cyber attack linked to Lapsus$.

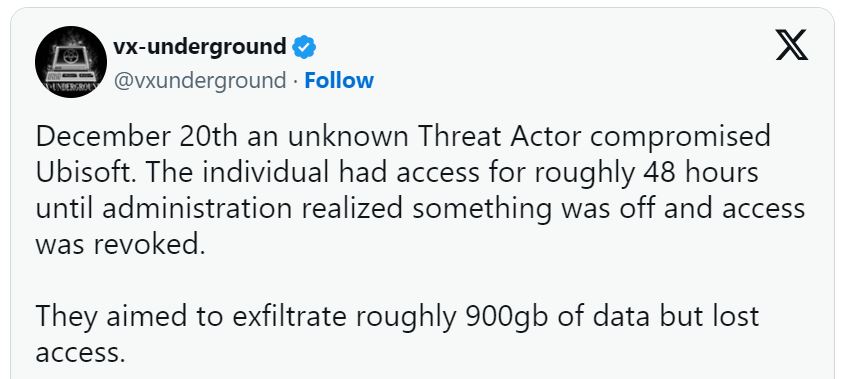
The online malware repository VX-Underground posted about the incident on its X (Twitter) page, explaining that the attackers “aimed” to obtain 900 GB of Ubisoft’s data.

Ubisoft Hackers Scrambled for 900GB of Data Before Foiled

“December 20th an unknown Threat Actor compromised Ubisoft. The individual had access for roughly 48 hours until the administration realized something was off and access was revoked. They aimed to exfiltrate roughly 900 GB of data but lost access.”

The researchers also shared screenshots of Ubisoft’s internal services. Whether the hacker(s) could obtain any data before Ubisoft revoked access or not is still unclear. However, it is suspected that the attackers wanted to obtain Rainbow Six: Siege user data but failed. The company claims to be “aware” of the security incident but hasn’t shared any additional information as yet.

This is the second data breach targeting a major video game company this month. Earlier in December, as reported by Hackread.com, Ratchet & Clank and Spider-Man developer Insomniac Games got sensitive employee data/information regarding unreleased video games stolen in a massive hacking incident.

The hacker published detailed plans of Insomniac for the next decade, including unannounced projects, production details, art assets, and employee information. Ransomware group Rhysida took responsibility for the hack and demanded 50 bitcoins to prevent the data from being published publicly.

In Ubisoft’s case, so far, there’s no indication that anything of the sort was accessed or leaked. Nevertheless, the resurgence of the trend to target gaming giants is not surprising, as hackers are known to ruin Christmas and holidays for gamers.

  1. Online gaming and protection against cyber attacks
  2. Fake Cyberpunk 2077 Android App Delivering Ransomware
  3. Gaming controllers manufacturer exposed 1.1M customer records
  4. ALPHV Ransomware Used Vishing to Scam MGM Resorts Employee
  5. Capcom ransomware attack: Gaming details leaked; no ransom paid

[ad_2]
Source link

How Do You Protect Your APIs from Bot Attacks?

0
[ad_1]
Protect Your APIs from Bot Attacks

Organizations face an escalating threat of bot attacks in the rapidly evolving digital landscape. As revealed in our latest AppSec report, there has been a staggering 56% increase in bot attacks compared to Q2 2023. Previously associated with DDoS attacks, bots are becoming increasingly sophisticated, targeting not only websites and applications but also APIs.

Understanding Bot Attacks on APIs

APIs are crucial components for communication between software applications. As organizations embrace digital transformation, APIs have become integral to their operations. However, this increased reliance also makes them susceptible to malicious bot activities. Understanding the nature of bot attacks on APIs is the first step towards developing effective defense strategies.

  • Credential Stuffing Attacks – Bot operators leverage stolen or leaked credentials to gain unauthorized access to APIs. This is often achieved through automated scripts that systematically input username-password combinations until a successful login.
  • API Abuse – Bots can exploit vulnerabilities in API endpoints to carry out various malicious activities, such as data scraping, inventory hoarding, or launching further attacks within the organization’s network.
  • Brute Force Attacks – Bots employ brute force techniques to crack API authentication mechanisms by systematically attempting different combinations of usernames and passwords until the correct credentials are found.

Why are APIs the Target for Bot Attacks?

Hackers increasingly target APIs due to their widespread use and vulnerability. These attacks are preferred because they are cost-effective and more challenging to detect than traditional browser attacks. As organizations rely more on APIs, securing them becomes crucial for online security.

API attacks are becoming more sophisticated, leveraging cloud computing and distributed networks. Unlike browser attacks, APIs provide a direct path to specific resources, making them attractive to various cyber threats. Detecting malicious API calls is challenging because they lack clues from traditional browser requests.

Attackers find APIs appealing because they are easy to deploy and require fewer resources. Unlike traditional attacks’ costlier “headless” browsers, APIs offer basic and affordable capabilities. Mobile APIs primarily provide a convenient platform for hiding malicious activities.

APIs also grant attackers closer access to the core infrastructure of applications, posing a significant risk. Protecting against API attacks is essential for maintaining the security of digital systems.

Signs of Bot Attacks on APIs

  • A quick and significant increase in traffic can signal a bot attack.
  • Unusual spikes in activity during off-peak times can be a red flag.
  • An uptick in error messages, especially regarding logins or access, could mean a bot attack.
  • Bots follow patterns. Detect repeated or similar requests happening too quickly.
  • A sudden influx from unusual places or concentrated activity in specific regions may indicate bots.

How Do You Protect Against Bot Attacks on Your APIs?

As businesses heavily rely on APIs for instant communication, they face a rising threat from malicious bot attacks. These attacks can lead to significant financial losses, reputation damage, and a loss of customer trust. The legal consequences are also severe, with potential fines and lawsuits for data breaches.

Here are essential techniques to protect from bot attacks on APIs:

Monitor and Manage API Calls

Utilize robust monitoring tools to keep a close eye on all API calls. Implement systems that differentiate between legitimate requests and potential threats from automated scripts. Establish real-time alerts to promptly respond to suspicious activities, minimizing the risk of successful bot attacks.

Prevent Human-Like Bots

Employ advanced authentication mechanisms to distinguish between human and bot interactions, behavioral analysis, and device fingerprinting to challenge and thwart bots attempting to mimic human behavior. Regularly update and enhance these security layers to stay ahead of evolving bot tactics.

Usage and Journey Tracking

Implement comprehensive logging and tracking systems to record the usage and journey of API calls. Analyze historical data to establish standard usage patterns and behavior. Implement anomaly detection algorithms to quickly identify deviations, enabling swift responses to potential bot attacks and minimizing their impact.

Malicious Intent Inspection

Integrate threat intelligence and pattern recognition tools to scan incoming API requests for signs of malicious intent. Employ heuristics and machine learning algorithms to identify patterns commonly associated with bot attacks. Regularly update threat databases and algorithms to ensure the system can effectively recognize emerging threats.

Comprehensive API Visibility

Implement solutions with an automatic API discovery that provides a comprehensive view of all APIs in use within the ecosystem. This includes understanding each API’s dependencies, interactions, and data flows.

Enhanced visibility enables security teams to identify potential weak points and proactively address security concerns, reducing the likelihood of successful bot infiltrations.

Implementing Granular Controls to Counter Bad Bots

Effectively managing bad bots requires a nuanced approach with granular controls. When the system identifies a malicious request with a high confidence level, it should take preventive measures before allowing access to the API and extracting sensitive information.

The suitable response options can be categorized into:

  • Block– Instantly deny access to the API for highly malicious requests, preventing potential harm and safeguarding sensitive information.
  • Feed Fake Data– Confuse bad bots by providing misleading or false data, diminishing the value of their efforts, and deterring future malicious activities.
  • Throttle– Limit the rate of requests from suspicious sources, slow down bots, and reduce the potential impact of their actions.
  • Drop– Reject requests from identified malicious sources without response, minimizing engagement and discouraging further attempts.

Behavior-based Baselines

Conduct thorough behavioral analysis of applications and APIs to establish baseline patterns of normal behavior. For instance, bot protection bundled in AppTrana WAAP involves understanding typical usage patterns, data flows, and access frequencies. 

Any deviations from these established baselines can trigger alerts, allowing security teams to investigate and respond promptly to potential bot attacks. It also regularly updates behavioral baselines to adapt to evolving application usage patterns and emerging threats.
[ad_2]
Source link

Hackers Attacking Linux SSH Servers to Deploy Scanner Malware

0
[ad_1]

Hackers often target Linux SSH servers due to their widespread use in hosting critical services, and the following loopholes make them vulnerable, providing opportunities to hackers for unauthorized access and potential exploitation:-

  • Weak passwords
  • Unpatched vulnerabilities
  • Misconfigurations

Cybersecurity researchers at AhnLab Security Emergency Response Center (ASEC) recently identified that hackers actively attack the Linux SSH servers to deploy scanner malware.

Technical analysis

Threat actors target poorly managed servers, seeking IP and SSH credentials for DDoS and CoinMiner malware. IP scanning identifies active SSH ports, followed by brute force attacks. More CoinMiners mean increased cryptocurrency mining. 

DDoS attacks grow in power with more controlled bots, and to install more malware, actors need target information besides DDoS and CoinMiners, malware scans, and attacks vulnerable systems. 

Meanwhile, SSH scanner malware DDoS bots and CoinMiners may be installed. Besides this, some actors install scanners, selling breached info on the dark web.

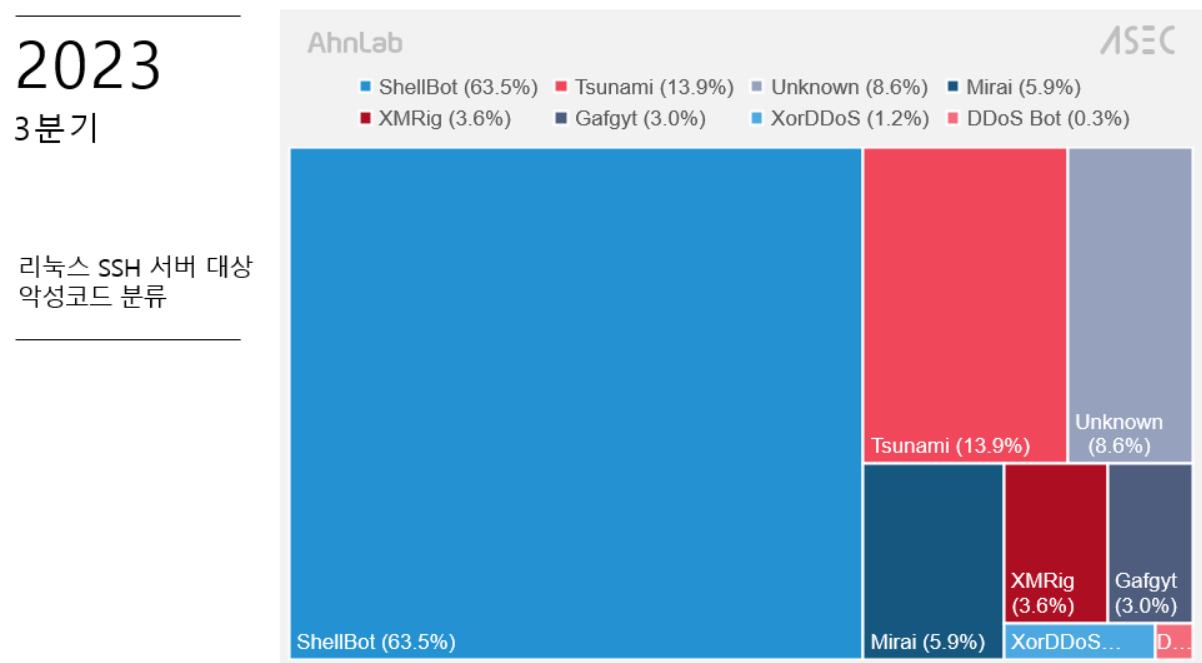
Here below, we have mentioned all the common malware that is installed in attacks against poorly managed Linux SSH servers:-

  • ShellBot
  • Tsunami
  • ChinaZ DDoS Bot
  • XMRig CoinMiner
  • Mirai
  • Gafgyt
  • XorDDoS

Threat actors deploy malware on Linux servers after logging in with stolen SSH credentials.

Classification of malware targeting Linux SSH servers
Classification of malware targeting Linux SSH servers (Source – ASEC)

Threat actor scans for active SSH (port 22) systems using stolen credentials for malware installation. 

The CPU core check command confirms the successful login. The actor downloads a compressed file with a port scanner and SSH attack tool. Notable commands include:-

Threat actor runs “go” script for port scanning, banner grabbing, and SSH dictionary attacks. “gob” and “rand” scripts allow IP class customization. 

The results are saved in “bios.txt” and banners in “banner.log.” The “prg” tool extracts IPs with “SSH-2.0-OpenSSH” from “bios.txt” to use in dictionary attacks, and the successful logins are stored in “ssh_vuln.” 

Besides this, the total CPU cores are checked using “grep -c ^processor /proc/cpuinfo.” After scanning and obtaining credentials, the actor repeats the process and installs the same tools.

Recommendations

To safeguard cybersecurity, researchers recommended the following mitigations:-

  • Always use strong
  • Regularly changed passwords
  • Update patches
  • Employ firewalls
  • Exercise caution with updated security versions like V3

[ad_2]
Source link

How to recognize AI-generated phishing mails

0
[ad_1]

Phishing is the art of sending an email with the aim of getting users to open a malicious file or click on a link to then steal credentials. But most phishers aren’t very good, and the success rate is relatively low: In 2021, the average click rate for a phishing campaign was 17.8%.

However, now cybercriminals have AI to write their emails, which might well improve their phishing success rates. Here’s why.

The old clues for telling if something was a phishing mail were:

  1. It asks you to update/fill in personal information.
  2. The URL on the email and the URL that displays when you hover over the link are different from one another.
  3. The “From” address is an imitation of a legitimate address, especially from a known brand.
  4. The formatting and design are different from what you usually receive from a brand.
  5. The content is badly written and may well include typos.
  6. There is a sense of urgency in the message, encouraging you to quickly perform an action.
  7. The email contains an attachment you weren’t expecting.

While most of these are still valid, there are a few checks you can strike off your list due to the introduction of AI.

When a phisher is using a Large Language Model (LLM) like ChatGPT, a few simple instructions are all it takes to make the email look as if it came from the intended sender. And LLMs do not make grammatical errors or put extra spaces between words (unless you ask them to).

They’re not limited to one language ether. AI can write the same mail in every desired language and make it look as if you are dealing with a native speaker. It’s also easier to create phishing emails tailored to the intended target.

All in all, the amount of work needed to create an effective phishing email has been reduced dramatically, and the number of phishing emails has gone up accordingly. In the last year, there’s been a 1,265% increase in malicious phishing emails, and a 967% rise in credential phishing in particular.

Because of AI, it’s become much harder to recognize phishing emails, which makes things almost impossible for filtering software. According to email security provider Egress 71% of email attacks created through Ai go undetected.

So how do you recognize AI phishing emails?

Here are some ideas:

Number 4 above—The formatting and design are different from what you usually receive from a brand—is helpful. Compare the email with any previous communications you have from the supposed sender. If there are inconsistencies in the tone, style, or vocabulary, this could indicate that the message is a phishing attempt.

Number 5—The content is badly written and may well include typos—AI phishing emails may still use generic greetings, such as “Dear user” or “Dear customer,” instead of addressing the recipient by name. Also, look for generic or mismatched signatures that do not align with the sender’s typical signature.

Number 7—The email contains an attachment you weren’t expecting—If you know the person who sent the email but don’t trust the content, contact the sender through an alternate communication method to verify whether they actually sent it.

For organizations it is important to have a clear reporting procedure and actively follow up on reported suspected phishing emails. If your employees never hear back about a reported phishing email, they are less likely to report the next one. A pat on the shoulder for catching one goes a long way. A lot further than the more common shame-and-blame punishments for clicking a malicious link.

Repetitive phishing training that neither aligns to how users engage with email, nor provides appropriate tools for responding to ambiguous emails are a waste of time, money, and the patience of the employee.

And most of all, make sure that your own communications, internal and external, don’t look like phishing attempts.


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.


[ad_2]
Source link

Google nixed plan to lower Google Play Store Tax in 2021 fearing a huge drop in revenue

0
[ad_1]
It was an epic lawsuit and it was an Epic lawsuit. Two weeks ago a federal jury found that the Google Play Store violated antitrust laws. Google’s in-app payment processing platform and the process of distributing Android apps were both run as monopolies said the jury in Epic v. Google. Epic sued Google after the game developer was sent packing from the Play Store along with its popular Fortnite game after Epic promoted its own in-app payment processing system which violated Play Store rules.
According to a report published by Bloomberg, Google seriously considered changing the in-app payment processing platform from which it was taking 15% to 30% of in-app revenue. In 2021, Google considered an overhaul to the Play Store billing model which was called Project Everest. This was discovered in documents that were released as part of the Epic v. Google antitrust suit.

Google found itself in a tight spot. On one hand, it was worried that if it didn’t make any change to the Play Store’s in-app payment processing platform, it would be done in by regulatory overreach. On the other hand, making changes to the platform could seriously impact the company’s revenue. During an in-house presentation, Google said, “We can defend the status quo for a few months. Making proposed changes sooner may help support reasonable legislation, position Google as a leader, and prevent more draconian legislation.”

Project Everest would have stopped Google from taking its 15% to 30% cut of in-app revenue and instead, developers would be charged for various services related to listing their apps in the Play Store with additional charges tacked on for user downloads and updates. But making this switch would cost Google in the form of a $1 billion to $2 billion decline in annual revenue from apps and $6 billion to $9 billion in revenue from games. 

Google employees floated the idea of having app developers handle in-app payment processing themselves in exchange for paying Google a lower fee. Google calculated that this option would reduce annual Play Store revenue between $250 million and $1.3 billion.
Also two weeks ago, Google announced the terms of a settlement it made back in September with all 50 states, the District of Columbia, and two US territories for $700 million. After giving the states $70 million of the settlement for penalties, restitution, disgorgement, and fees, the remaining $630 million will be shared among Play Store customers who will get a minimum of $2 each.

[ad_2]
Source link

Vietnamese Group Hacks and Sells Bedroom Camera Footage

0
[ad_1]

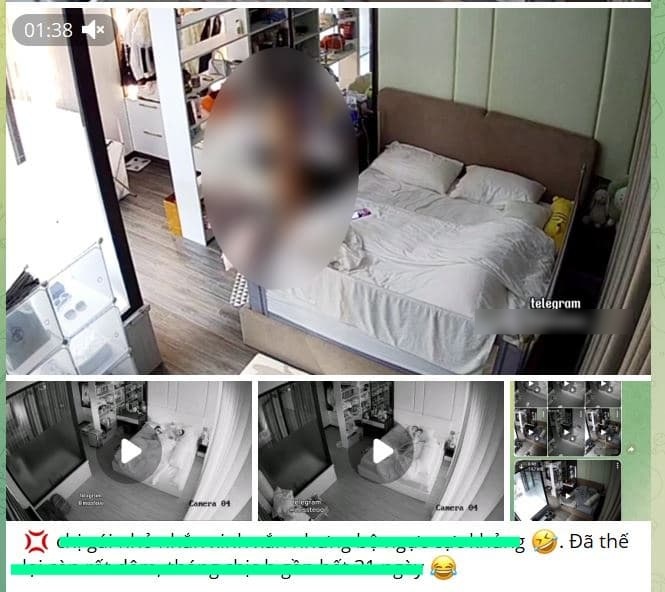
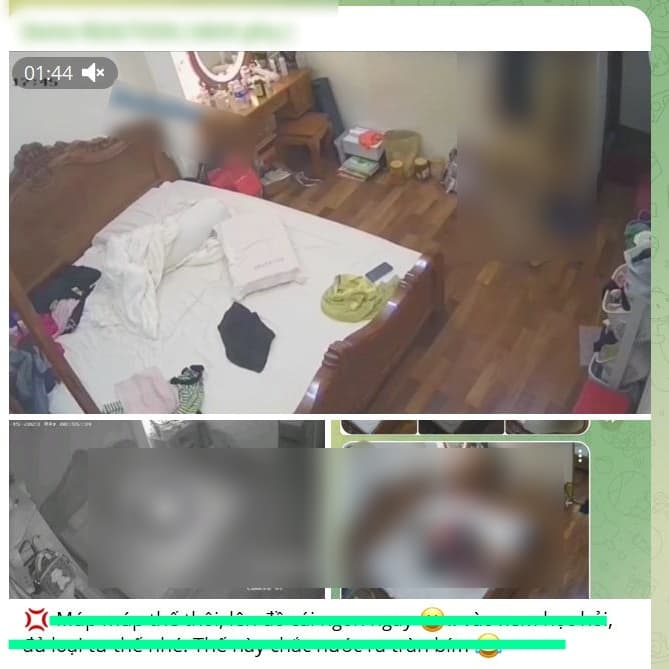
A group of Vietnamese individuals involved in cybercrime is hacking into home security cameras of unsuspecting users and selling private and intimate footage on Telegram for a mere $16.

A Vietnam-based Telegram group has been discovered selling private footage obtained from hacked security cameras, showcasing what they describe as ‘dark corners’ and ‘hot scenes.’ Security experts attribute this privacy breach to poor password hygiene as the primary cause.”

In 2021, cybersecurity researchers at BitDefender debated whether Telegram, an encrypted messaging app, had become the new dark web. As the world approaches 2024, the significance of this argument has never been more evident.

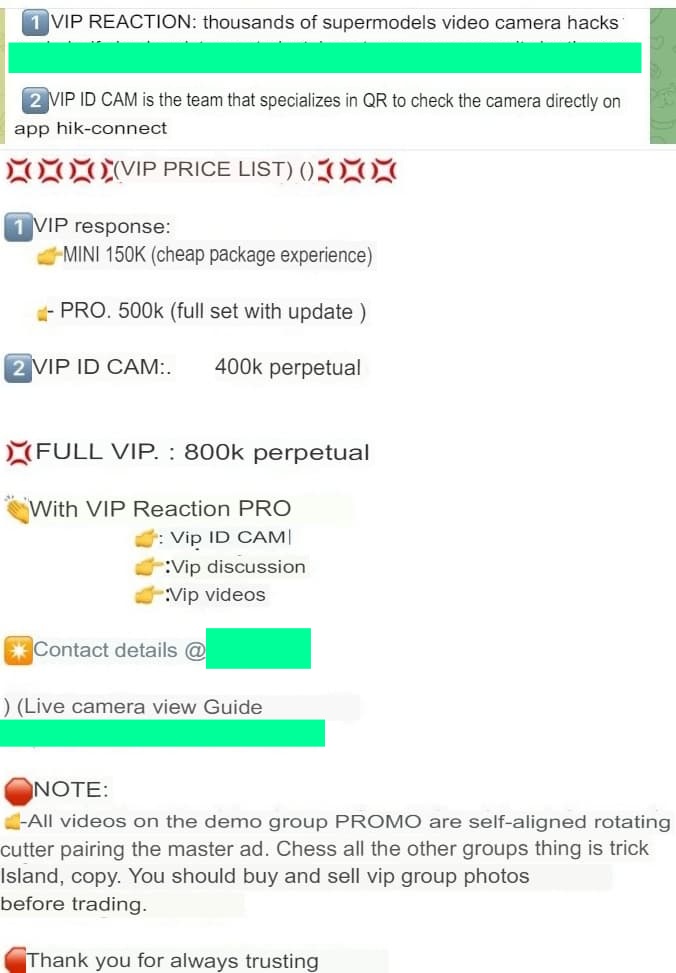
According to details shared by security researcher Minh Hung, who first discovered the notorious Telegram group and published by Vnexpress, the group offers three packages for accessing the hacked footage.

The cheapest package costs 150,000 Vietnamese Dong ($6.16), while the highest package costs VND500,000 ($20.53). The top tier, ‘Super VIP,’ includes 4 years’ worth of hacked footage from hundreds of cameras and live access for VND800,000 ($32.84).

This group claims to specialize in hacking into “private cameras of families and shops in Vietnam” and invited Hung to join them on the channel.

Hackread.com also managed to identify Vietnamese-language Telegram channels offering malicious footage stolen from hacked home security cameras. The screenshots below were taken by Hackread.com:

On the other hand, according to Vnexpress’s report, Hung could watch the videos for the first and second packages, but with the third package, he could download an application from a camera firm and watch live feeds using the provided QR codes. Hung suspected it to be a scam but paid VND800,000 to check it out.

Hung further discovered that the timestamps on security camera feeds matched the current time. Using the application, he could access 15 cameras installed in clothing shops and spas, including bedrooms, living rooms, and dressing rooms.

Should You Install Security Cameras in Your Bedroom?

Installing security cameras in your bedroom raises significant privacy concerns and is generally considered a bad idea. The bedroom is an intimate space where individuals expect the highest level of privacy. Placing cameras in this area not only invades personal boundaries but also raises ethical issues.

The footage captured in bedrooms can include highly sensitive and personal moments, compromising one’s privacy and dignity. Beyond the ethical aspect, it also poses a risk of unauthorized access by hackers, as demonstrated by this article.

Additionally, such surveillance within the confines of a home may lead to legal implications, as it potentially violates laws related to privacy. To maintain a sense of security and privacy, it is advisable to install cameras in public areas of the home while avoiding intrusion into personal spaces like bedrooms.

How to Protect Your Security Camera from Hackers?

whether at home or work, protecting your security cameras from hackers is crucial to protect your privacy and security. Here are some vital tips to help you enhance the security of your security camera system:

  1. Update Firmware Regularly:
    Ensure that your security camera’s firmware is up to date. Manufacturers often release updates that address security vulnerabilities, so regularly check for and install firmware updates.
  2. Use Strong Passwords:
    Create strong, unique passwords for your camera’s login credentials. Avoid default passwords and choose a combination of letters, numbers, and special characters. Change passwords regularly and avoid using easily guessable information.
  3. Network Security:
    Secure your home network by setting up a strong Wi-Fi password and using WPA3 encryption if available. Restrict access to your network by using a strong, unique network password.
  4. ALWAYS Change Default Settings:
    Change default usernames and passwords on your security cameras. Default credentials are often well-known and exploited by hackers.
  5. Enable Two-Factor Authentication (2FA):
    Whenever possible, enable two-factor authentication on your security camera accounts. This adds an extra layer of security by requiring a second form of verification, such as a code sent to your mobile device.
  6. Regularly Check for Suspicious Activity:
    Monitor your camera system for any unusual or unauthorized access. Regularly review footage and set up alerts for suspicious activities, such as multiple failed login attempts.
  7. Keep Cameras Offline When Not in Use:
    Consider disconnecting your security cameras from the internet when you don’t need remote access. This can be done by configuring your router to block camera access during certain hours.
  8. Purchase from Reputable Brands:
    Choose security cameras from reputable manufacturers with a track record of providing regular firmware updates and security patches.
  9. Secure Physical Access:
    Ensure that physical access to your cameras is restricted. Place cameras in locations that are not easily accessible, and consider installing them at a height to prevent tampering.
  10. Regularly Review Camera Logs:
    Some advanced camera systems provide logs of access and activities. Regularly review these logs for any suspicious entries.
  1. ThroughTek Flaw Exposed Millions of IoT Cameras to Spying
  2. Whitehat hacker shows how to detect hidden cameras in hotels
  3. 3TB of clips from exposed home security cameras posted online
  4. This creepy site shows live footage from 73K Private Security Cameras
  5. Israeli Rabbi arrested for hacking CCTV cam at women’ bathing suit shop

[ad_2]
Source link

A week in security (December 18 – December 24)

0
[ad_1]

Last week on Malwarebytes Labs:

Stay safe and happy holidays!


Our business solutions remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.


[ad_2]
Source link