Xiaomi details its first electric cars, and they seem promising

0

[ad_1]

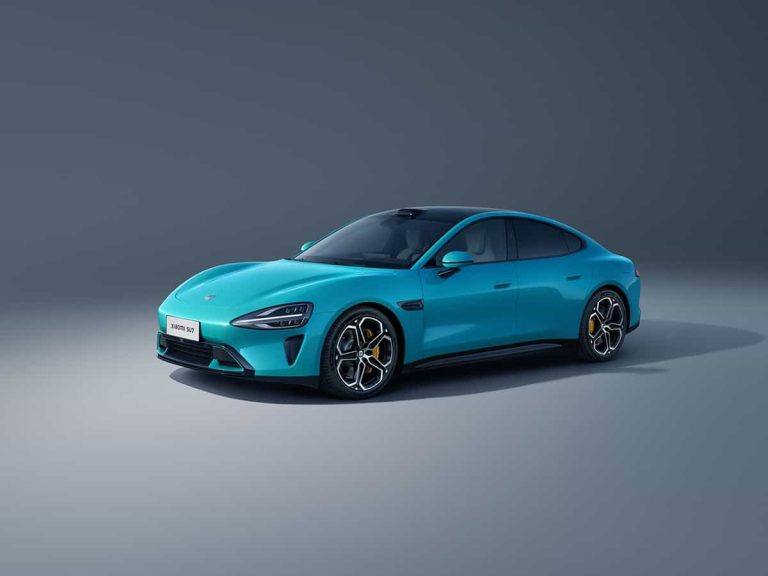
Xiaomi detailed its very first electric cars during a long press conference in China (embedded below the article). The name of the series is the Xiaomi SU7, and it comes in two variants. The Xiaomi SU7 and SU7 Max got detailed.

Xiaomi detailed its very first electric cars, the Xiaomi SU7 & Xiaomi SU7 Max

This is not the first time we’re seeing these cars, or hearing about them. Xiaomi released some info in the past, along with their designs. The company did delve much deeper this time around, giving us some proper information.

First and foremost, do note that this car has been made in partnership with state-owned Beijing Automotive. To our eyes, it looks like a cross between an Aston Martin, a Porsche, and a Tesla, kind of.

The two cards look the same, but they’re different under the hood

The Xiaomi SU7 and SU7 Max look the same, but they’re different under the hood. They’re powered by the Xiaomi HyperEngine V6 and V6s motors with 21,000 rpm. Xiaomi also announced that the HyperEngine V8s is coming in 2025 with 27,200 rpm.

The Xiaomi SU7 cars come with Xiaomi’s new HyperOS pre-installed. They’re compatible with the company’s phones running the same software, of course. That’s Xiaomi’s whole thing now, make everything connected.

Xiaomi SU7 details 6

Here’s what’s different

Let’s talk about the differences between the two models, before we get to anything else. The Xiaomi SU7 can reach 100kmh in 5.28 seconds. It has a 73.6-degree iron lithium battery, and 668km of battery life. We’re looking at a 400V platform here. This car also includes a single Orion chip, and it’s powered by the Qualcomm 8295.

Xiaomi SU7 vs SU7 Max image 1

The Xiaomi SU7 Max, on the other hand, comes with a 101Kwh CATL integrated battery technology. You can pull out 800km of range from this car, and it also supports super-fast charging. It can reach 100kmh in 2.78 seconds, and has a 101-degree ternary lithium Kirin battery. There are two Orion chips included here, a lidar sensor, and the Qualcomm 8295. Air suspension is also included + CDC, not to mention an electric tail wing.

You’ll find a 16.1-inch touch screen on the inside, along with a 56-inch HUD

The Xiaomi SU7 series includes a 16.1-inch touch screen, a 56-inch HUD, and a 7.1-inch flip instrument screen. The central control screen also supports a keyboard expansion. There is a D-shaped steering wheel included in both cars.

You’ll find water drop-shaped headlings on these cards, and 2.48m halo-shaped tail lights. There is a 175-degree ripple curved surface, and G4 continuous curvature on the car outline. The door handles are semi-hidden, and so on. There are three different interior colors, Galaxy Gray, Obsidian Black, and Twilight Red.

There are 8 sets of air ducts included, and 17 air outlets

You will find 8 sets of air ducts, and 17 air outlets inside. The rear wing can provide 130 kilograms of downforce when traveling at the highest speed. The Xiaomi SU7 and SU7 Max include 25 speakers, and Dolby Atmos support.

When it comes to space, the vertical space in the front row reaches 1,012mm, and people up to 1.88 meters have plenty of headroom. The rear section exceeds that of the Tesla Model S and BMW 5 series, said Xiaomi. The front luggage space is 105 liters, and the trunk offers 517 liters of space.

Xiaomi also included 7 airbags, but the company did not provide us with price tags

The Xiaomi SU7 series utilizes an armored steel-aluminum hybrid body. It has a strength of 2,000MPa, and the highest vehicle torsional stiffness of 51,000 Nm/deg. You’ll find 7 airbags on the inside.

The Xiaomi SU7 cards come in Aqua Blue, Mineral Gray, and Verdant Green colors, as you can see below. We still don’t know the pricing of these cards, but Xiaomi did say they’re coming to the Chinese market in 2024.


[ad_2]

Source link

Galaxy S24+ could ship with Snapdragon 8 Gen 3 globally; more specs leak

0

[ad_1]

Samsung is less than three weeks away from unveiling its next-gen flagship smartphones. While it hasn’t officially announced the launch date, leaks have revealed that the Galaxy S24 series will break cover on January 17, 2024. Thanks to those leaks, we also already know pretty much everything about the new devices, or do we? A fresh leak says the Galaxy S24+ won’t have an Exynos 2400 version and will ship with the Snapdragon 8 Gen 3 globally.

Galaxy S24+ might come with the latest Snapdragon chip globally

After exclusively using a Snapdragon processor on the Galaxy S23 series this year, Samsung is returning to its in-house Exynos chips with the Galaxy S24. Leaks so far have hinted at a dual-chip strategy for the new flagships. The Ultra model is said to get an overclocked Snapdragon 8 Gen 3 in all markets. The other two models would ship with the Snapdragon chip in the US and Canada and the Exynos 2400 in the rest of the world.

However, an alleged spec sheet for the Galaxy S24 lineup posted on X by @WigettaGaming says something else. It hints at the Snapdragon chip for both Plus and Ultra models globally. Only the vanilla Galaxy S24 will have a dual-ship strategy—Snapdragon in the US and Canada and Exynos everywhere else. If true, Samsung might have decided this at the last minute. There is no evidence of a Snapdragon-powered global version of the Galaxy S24+.

All benchmark listings so far have shown it with the Exynos chip. The same goes for the Galaxy S24 too. The Ultra models’ global version, meanwhile, has been spotted only with the Snapdragon 8 Gen 3. There have been a few rumors about the Plus model getting the Snapdragon globally but without any evidence. Considering this, we won’t vouch for the accuracy of the latest leak. Thankfully, the official launch isn’t far away now.

Galaxy S24 fresh spec sheet leak

Other known Galaxy S24 specs

Leaks have already revealed detailed specs of the Galaxy S24 lineup. The vanilla model sports a 6.2-inch display with an FHD+ resolution. The Plus and Ultra models have 6.7-inch and 6.8-inch displays with a QHD+ resolution. It’s an LTPO AMOLED panel for all three models with a 1-120Hz variable refresh rate and 2,600 nits brightness.

The Galaxy S24 Ultra has a 200MP primary camera paired with a 50MP 5x zoom camera, a 10MP 3x zoom camera, a 12MP ultrawide lens, and a 12MP selfie camera. The other two models lack the 5x zoom camera and feature a 50MP primary shooter instead of a 200MP unit. The remaining three cameras—3x zoom, ultrawide, and selfie—are unchanged. All three models support 8K video recording.

Coming to the batteries, Samsung has equipped the smallest Galaxy S24 with a 4,000mAh battery, Plus with a 4,900mAh battery, and Ultra with a 5,000mAh battery. The former supports 25W wired charging while the latter two go up to 45W charging. The wireless charging speed is capped at 15W for all models, while the reverse wireless charging speed is capped at 4.5W.

The entire lineup boasts LPDDR5X RAM technology but only the bigger two models get 12GB of memory. The vanilla Galaxy S24 has 8GB RAM. It also starts at 128GB of internal storage with UFS 3.1 tech. Its 256GB version has a UFS 4.0 solution, though. UFS 4.0 storage is the standard on the other two models, which start at 256GB storage. Samsung will offer several new AI features on the Galaxy S24 series. Stay tuned for the official launch.


[ad_2]

Source link

Redefining convenience, security and certainty

0

[ad_1]

Blockchain, though seeing headlines in recent years for its use in cryptocurrencies, is not that young in today’s tech world’s perspective. For most of us, it’s only limited to its use in cryptocurrencies. But blockchain can go way beyond just cryptocurrencies in making life easier.
Blockchain is special and holds the key to redefining the way we live and do things. Things that are important and require too much of our attention and effort. In today’s article, we’ll take a look at why blockchain is something close to revolutionary, and how versatile it is in its potential use cases.

Blockchain Can Be Used in Endless Ways for Endless Purposes

So, now that we know blockchain technology to be the new and improved way of storing and transferring data, it’s time we understand how the secure, transparent, and decentralized nature of blockchain means that there is endless potential in the ways we can utilize it. Let’s look at some of the most promising use cases for blockchain.

Financial Transactions

This is the use case that brought blockchain to reality, and its potential to be a medium for fast, secure, and transparent transactions has already been proven through the boom of cryptocurrencies over the last several years.

Nowadays, cryptocurrencies are being used for various purposes. Business transactions, marketplace transactions, and other forms of transactions related to various services are using blockchain technology, for example in the online casino industry. Blockchain makes casino gaming safer, cheaper, faster, and more transparent, making crypto casinos more reliable and attractive to consumers. It’s no surprise that new crypto casino sites are springing up like mushrooms everywhere.

Identification and Data Management

We’ve entered a huge domain here. It’s possible to create personal identification systems that are reliable and confidential through blockchain. In many industries, it can be used to store the data of individuals over time.

For example, blockchain can be used to store medical records digitally and securely, making it easier to update and keep track of. This can help doctors ensure faster, more accurate, and more efficient care. For the education sector, it can be used to store records, performance analytics, and grades of individual students over time. This’ll make it easier for teachers to identify the strengths and weaknesses of every student, and ensure proper education. The potential is endless.

Digital Identity and Certification

Blockchain can create a digital identity for you that’s hard to fake or steal. Also, the fact that it can store data over time, means that you can use it to create certifications for certain facts. For example, if you connect your car’s odometer to the blockchain, you can prove to a potential buyer that the odometer reading hasn’t been tampered with. Pretty neat, right?

Supply Chain Management

By implementing blockchain into their supply chain, companies can keep track of individual product sales, inventories, as well as individual units of product. This can be quite handy for certain industries. For example, if a certain batch of food causes food poisoning in many people, the manufacturer can quickly track it down and remove that specific batch from the market.

The thing is, we can only talk about so many use cases in such a short article, when the potential is virtually endless. To sum it up in short, any process that requires a third party to be initiated and audited, from data management, credentials, finances, ownership certification, voting, etc can be decentralized by blockchain to ensure maximum security and transparency.

So, What Makes Blockchain So Secure?

The name of the tech is pretty self-explanatory. It consists of blocks that hold data in them, and they are linked like chains. More on this in a bit. Every block represents a certain value in a certain context. For example, in cryptocurrencies, when you make a transaction, a block holds the data of the sender, receiver, amount sent, etc.

Every block also consists of a unique hash and the hash of the block before it, and this is exactly what makes it so secure and transparent. Changing anything in a block changes its hash. So, even if you do tamper with the data in a block, the changes won’t fit. The previous hash written in the block won’t match anymore.

As the data of the whole chain is stored on countless computers around the world, it’s virtually impossible to tamper with the overwhelming number of blocks. And whatever change you try to make can be identified and pinpointed.

What Does the Future Hold?

Blockchain is a powerful tool that can transform various aspects of our lives, making them easier and safer by improving how we store and transfer data. And it’s already in its worst phase, meaning, it’s only going to get better from now on.

In the coming years, we may see a drastic shift in the sectors we talked about as the technology gets better and the world starts to adapt. Blockchain is here to stay.

[ad_2]

Source link

Apache OfBiz Zero-Day Let Attackers Bypass Authentication

0

[ad_1]

A new vulnerability has been discovered in Apache OfBiz, an open-source Enterprise Resource Planning (ERP) system.

Apache OfBiz is used as a part of the software supply chain in Atlassian’s JIRA, which is predominantly used in several organizations. This vulnerability was a bypass to a previously discovered vulnerability, CVE-2023-49070.

Since the root issue of CVE-2023-49070 was left open, a bypass has been discovered as a workaround for the patch. This new vulnerability has been assigned with CVE-2023-51467, and the severity has been given as 9.8 (Critical).

Apache OfBiz Zero-Day

CVE-2023-49070 was a pre-auth RCE vulnerability due to the presence of XML-RPC, which is no longer maintained. However, the released patch was only with removing XML RPC code from the application, which was open for an authentication bypass.

Test Cases

There were two test cases for exploiting this vulnerability—the first one involved including the requirePasswordChange=Y in the URI with empty USERNAME and PASSWORD parameters. 

Due to the misconfiguration of the login condition block, the application resulted in the checkLogin function returning with a “success,” leading to the authentication bypass.

The second test case was similar to the first one, with slightly changing parameters. The USERNAME and PASSWORD parameters are submitted with invalid values.

However, the checkLogin function flow did not enter into the conditional block, which resulted in the authentication being bypassed.

This vulnerability has a publicly available exploit, which penetration testers and security engineers can use to test if the vulnerability exists on their application.

Furthermore, a complete report about this vulnerability has been published by SonicWall, providing detailed information about the code analysis, exploitation, and other information.

Apache OfBiz has fixed this vulnerability in version 18.12.11 and newer. Users of Apache OfBiz are recommended to upgrade to the latest version of this software to prevent this vulnerability from getting exploited by threat actors.

[ad_2]

Source link

25 malware apps spotted, they can take control of your Android device

0

[ad_1]

25 dangerous apps have been spotted on the Android platform, they’re plagued with malware, and can take control of your device. This information comes from the McAfee Mobile Research Team.

25 malware Android apps have been spotted and they can gain control of your device

Do note that all of those apps that were available via the Google Play Store have been removed. They’ve been removed even before McAfee published its report. If you still have them installed, however, that’s a problem.

These apps are infected by ‘Xamalicious’ malware. They’re mostly placed in games, health, horoscope, and productivity categories. McAfee also highlights that most of the apps mentioned are still available via third-party Android stores.

How do these apps operate? Well, they use ‘social engineering’ to get accessibility privileges, so that your phone can communicate with a command-and-control server. That communication goes unnoticed by the user.

At that point, a second payload is downloaded to your device, and can take full control of it. It can then perform various fraudulent actions, ranging from clicking on ads, to doing various other things.

13 of these apps have been available via the Google Play Store

13 of those 25 apps have been available via the Google Play Store. All of them have been removed, as mentioned earlier, but if you still have them installed, uninstall them. The list is available below.

– Essential Horoscope for Android
– 3D Skin Editor for PE Minecraft
– Logo Maker Pro
– Auto Click Repeater
– Count Easy Calorie Calculator
– Sound Volume Extender
– LetterLink
– NUMEROLOGY: PERSONAL HOROSCOPE &NUMBER PREDICTIONS
– Step Keeper: Easy Pedometer
– Track Your Sleep
– Sound Volume Booster
– Astrological Navigator: Daily Horoscope & Tarot
– Universal Calculator

These apps have been installed over 100,000, together. Two of them have over 10,000 installs on their own. So, plenty of users actually reached for the install button. If you’re one of them, remove these apps as soon as possible.

Full details on all 25 applications can be found in McAfee’s original report. The remaining 12 apps were not listed on the Google Play Store at any point.

[ad_2]

Source link

Instagram is working on a profile-sharing feature for Stories

0

[ad_1]

Instagram stands as one of the foremost social media platforms, boasting a massive user base exceeding 2.5 billion worldwide. Its parent company, Meta, consistently introduces fresh features and updates, such as the recent AI-driven Backdrop, designed to dynamically alter story backgrounds for an enhanced user experience. Now, rumors hint at the imminent arrival of another addition to Instagram’s ever-evolving toolkit.Leaker and app developer Alessandro Paluzzi (via Android Headlines) recently discovered that the Meta-owned app is in the process of developing a new feature. This upcoming addition will allow users to share someone else’s profile directly in a Story.

The feature will work similarly to the existing “Add to Story” function but with a focus on promoting another user’s profile. It will offer a straightforward way for Instagram users to direct their followers’ attention to other profiles, potentially increasing the shared profile’s visibility and follower count.

As you can see from the image in the post, a new “View Profile” button invites viewers to visit the mentioned profile. Instagram already lets you share all sorts of stuff on Stories, like, for example, other people’s posts. But with this new feature, boosting a profile’s visibility will get way easier.

Enabling profile sharing on Instagram Stories opens up new avenues for discovery, engagement, and brand exposure, particularly beneficial for creators and businesses. Think about it—creators can collaborate with each other, and businesses can share profiles in Stories, drawing in potential customers and giving their brand a little extra spotlight.

It is still unknown when exactly this work-in-progress feature will be available to all Instagram users, but it is likely to be early in 2024, so stay tuned for updates.

[ad_2]

Source link

4 sneaky scams from 2023

0

[ad_1]

In 2023, the public primarily confronted two varieties of online scams: the technical and the topical.

Technical scams abuse legitimate aspects of modern internet infrastructure to lead users to illegitimate or compromised sites. A team of hackers can, say, boost their own info-stealing websites through Google search results, providing a veneer of authenticity to their malicious intent. These scams can involve vast criminal segmentation and coordination between malware developers, code writers, and hackers who sometimes also infect legitimate websites with dangerous tools.

Topical scams, on the other hand, are simpler. By leveraging major news events or luring users with too-good-to-be-true deals, cybercriminals trick victims into giving away their vital credit card information through cyberspace.

Both are dangerous, both are effective, and both had their fair share of sneaky examples this year.

With your holiday shopping over (or, we hope it’s over, as it’s a bit late now for gifts), we at Malwarebytes Labs wanted to look back on four of the sneakiest online scams we saw last year.

Forged in fire, fraud on Facebook

In November, an insulated tumbler made by the drinkware company Stanley allegedly survived a roaring fire that sadly destroyed a woman’s car. The car owner, Danielle Marie Lettering, posted a video on TikTok that showed a Stanley tumbler—merely singed—inside a wrecked Kia.

“Everybody is so concerned if the Stanley spills but what else,” Lettering said in the video she posted. “It was in a fire yesterday and it still has ice in it.”

Lettering’s TikTok video has more than 90 million views and a wealth of comments about first-time interest in Stanley’s products.

And right on time, just weeks later, Malwarebytes Labs spotted a fraudulent Facebook ad—posing as a legitimate sale from Dick’s Sporting Goods—selling the now-storied Stanley Quencher cup for just $19, a steal compared to Amazon listings near $45.

Users who clicked on the ad were not taken to the legitimate website for Dick’s Sporting Goods, but instead routed to a website where the payment processor was registered in Hong Kong.

Sprung just before Black Friday, this scam had it all—the urgency of an annual mega-shopping event, the name of a recognized and trusted online retailer, and the allure of a once-benign product now launched into viral celebrity.

WoofLocker sends victims into a redirection labyrinth

Tech support scams often follow a similar plot: Cybercriminals will place malicious ads online that label a bogus phone number for everyday users who are experiencing common tech problems. When those users look up their tech troubles online, they’ll see results that display the scammers’ phone number, fooling them into calling what they think is a legitimate helpline, only to be led through a series of social engineering tricks to eventually hand over their money.

But the tech support scam held up by “Wooflocker” is different.

Wooflocker does not rely on malicious advertising (also known as malvertising). Wooflocker only ensnares victims who, of their own accord, visit any of several compromised websites.

With every visit to a compromised website, a user is surreptitiously “fingerprinted”—if their IP address, computer environment, and cyber-defenses (or lack thereof) are all preferable to the hackers behind Wooflocker, then those website visitors are redirected to another domain with a URL that is created then and there by Wooflocker’s hacking scripts.

Malwarebytes Labs first spotted Wooflocker in 2020, and even then, we learned that the cybercriminals behind it had likely been building out their web traffic redirection machine since 2017. But in the years since we last checked in, Wooflocker has become more sophisticated. The current iteration of Wooflocker now relies on web hosting services in Bulgaria and Ukraine, which could potentially provide added protection against any takedown efforts.

The “logout king” gets pinned

In March, the reporting outlet ProPublica revealed that, after months of investigation, it had likely tracked down one of the most notorious online scammers—the self-proclaimed “log-out king,” also known as OBN Brandon.

OBN Brandon’s trick is almost always the same. He reports accounts of growing Instagram influencers to the customer service department of Meta, the company formerly known as Facebook, which also owns Instagram. Once he wrongfully enacts a ban on the account, OBN Brandon reaches out to the person behind the account and says he can bring it back—for a price.

As to how OBN Brandon convinces Meta’s customer support to take down an account, there are multiple tactics. According to ProPublica:

“In some cases OBN hacks into accounts to post offensive content. In others, he creates duplicate accounts in his targets’ names, then reports the original accounts as imposters so they’ll be barred for violating Meta’s ban on account impersonation. In addition, OBN has posed as a Meta employee to persuade at least one target to pay him to restore her account.”

Once a simple image-sharing tool, Instagram has now ballooned into a business platform for countless influencers who take promotional offers from larger companies to be featured in posts and Reels—which are short-form videos on the app. Similarly, many small businesses and entrepreneurs use the platform to self-promote and connect users to their products and services.

One OBN victim that ProPublica spoke to claimed that, before his account was targeted, he had been making between $15,000 and $20,000 a month simply from his Instagram account.

“People pay me all the time to post promos for music, crypto,” the individual told ProPublica. “I can make five, 10 grand by accident if I needed to. … The money’s crazy.”

In its investigation, ProPublica identified a 20-year-old Nevada man as a likely operator or affiliate behind OBN Brandon. Once the outlet gave more details to Meta, Meta sent a cease-and-desist order to the man, also banning him from the platform.

In their villain era

For years, Taylor Swift fans were starving.

Not since 2018 had the most recent TIME Person of the Year produced a full-fledged world circuit tour. But in 2023, that changed, when Swift began her “Eras” tour, a globe-spanning celebration of her past albums that, on stage, delighted audiences for three-and-a-half hours every night, no matter the weather.

Still in production, Swift’s “Eras” tour has already brought in literal billions for the pop star goddess, according to one Washington Post estimate.

But the tour has also brought in a significant payday for ticket scammers.

In June, just a few months into the start of the “Eras” tour, Attorney General Dana Nessel for the state of Michigan issued a warning to Swift fans in her state.

“Michigan residents who are defrauded by online ticket scammers should not just shake it off,” said Nessel. “We know these scams all too well. If you believe you were taken advantage of, filing a complaint with my office is better than revenge.”

According to Malwarebytes Labs’ own reporting at the time, scams that preyed on the Eras tour were popping up all across the United States:

“Other locations for the tour are trying to get ahead of the scam curve, issuing their own warnings ahead of events where possible. For example, Cincinnati has highlighted tales of woe related to fake ticket sales on Facebook. Detroit flagged fake ticket sales on Instagram. CBC covered multiple fake sale attempts cheating folks in Canada out of significant chunks of money. Elsewhere, teens have lost out on $1,200 thanks to Craigslist scammers.”

With many, many, many more shows scheduled (the latest of which is in December 2024), stay alert.


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.
[ad_2]

Source link

iPhone users on TikTok are freaking out as the app is requesting sensitive personal data

0

[ad_1]

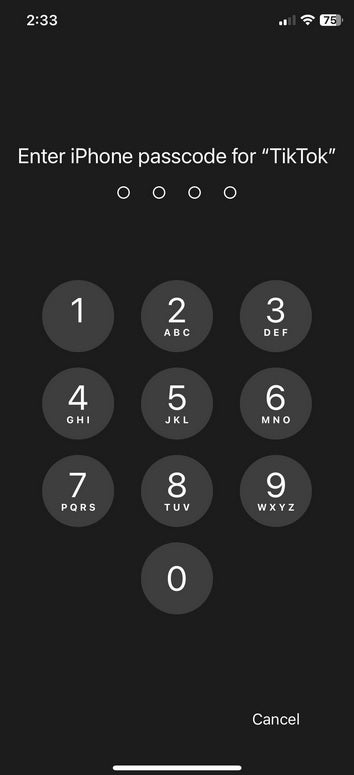
There is something that is making TikTok users with an iPhone a bit nervous. According to Reddit, the short-form video app is asking users for their iPhone passcode before allowing them to continue to use the app. We recently showed you an interview with a cybercriminal who ripped off people for an amount estimated to be anywhere between $300,000 and $2 million. His MO was to watch iPhone users punch in their passcode, steal the iPhone; and take control of that device inside of 10 minutes.
Yes, it is true that when it comes to TikTok, you still have your iPhone in your possession, but it still is not a good idea to reveal your iPhone passcode to a company that has been accused of stealing users’ personal data. TikTok doesn’t explain why it needs your iPhone passcode, and we don’t want to give them an alibi, but it seems possible that some kind of software bug is behind the requests. On Reddit, one TikTok user with an iPhone swears that the constant request for his passcodes went away once he installed version 32.5.0 of the iOS TikTok app.

On the other hand, there are several TikTok users who say that installing the update did not stop the app from requesting their iPhone passcode and many have been so unnerved by the whole thing that they changed passwords on important apps including their banking and other financial apps. While deleting the TikTok app might be the easiest thing to do, many won’t do this for fear that they will lose all of their favorite videos that they saved on the app.

If you don’t mind risking losing everything you’ve saved and starting over, you could try deleting the TikTok app from your iPhone and reinstalling it. Some Redditors swear by that solution. But what happens if you simply choose not to type in your iPhone passcode? Those who tapped the cancel button instead of their passcode were able to continue with their TikTok session. That certainly makes the whole issue sound like some sort of software bug rather than a devious plan to steal iPhone passcodes.

So for now, we urge you to calm down. Try the cancel button when prompted for your iPhone passcode. If that doesn’t work, try updating to version 32.5.0 of TikTok. If that doesn’t work, delete the app and reinstall it from the App Store. If that doesn’t work, try to contact ByteDance in California at (844) 523-3993.

[ad_2]

Source link

10 Prominent Cybersecurity Acquisitions of 2023

0

[ad_1]

The cybersecurity domain is undergoing rapid changes owing to the rise in frequency and complexity of cyber threats.

As the digital world expands, the risk of cyberattacks is increasing, and security experts must stay vigilant to safeguard against potential breaches.

As digital risks grow, big companies are acquiring others in the cybersecurity field to enhance their capabilities and stay ahead of evolving threats. 

Acquisitions provide access to the following key things:-

  • Advanced technologies
  • New talent
  • Threat intelligence

These key things allow these companies to strengthen their overall security posture and offer more comprehensive solutions to clients in an ever-changing threat landscape.

Impact of mergers & acquisitions (M&A)

Cybersecurity market is set to grow from $153.6bn (2022) to $424.9bn (2030). While the mergers & acquisitions (M&A) are significantly impacted by the following key factors:-

  • Risk aversion
  • High asset values
  • Capital costs

However, the limited international support prompts cybersecurity firms to merge for the required market demands that must be fulfilled.

Here below, we have mentioned all the key impacts of mergers & acquisitions (M&A) of cybersecurity companies:-

  • Enhanced Capabilities
  • Expanded Product Portfolio
  • Increased Market Share
  • Improved R&D (Research and Development)
  • Access to Talent
  • Streamlined Operations
  • Global Expansion
  • Improved Threat Intelligence
  • Compliance and Regulation Adherence
  • Economies of Scale

Prominent Cybersecurity Acquisitions 2023

Here below, we have mentioned all the top 10 prominent cybersecurity acquisitions of 2023:-

Now let’s discuss the above-mentioned prominent Cybersecurity Acquisitions of 2023:-

Cisco Acquired Splunk

Cisco Acquired Splunk

Cisco acquires Splunk for $28 billion in cash, aiming to bolster AI-enabled security. The deal, at $157 per share, enhances strength and shareholder value.

The merger accelerates Splunk’s growth, encouraging innovation and global expansion. Approval from both boards anticipates finalization by Q3 2024.

Besides this, the transaction won’t affect Cisco’s share buyback or dividend program.

Broadcom Acquired VMware

Broadcom acquired VMware, and this merger blends Broadcom’s engineering with VMware’s cloud expertise, promising agility in the digital era.

Broadcom’s innovation commitment shines in industry-leading products, and this merger will provide the ability to explore the power of VMware Cloud Foundation by reshaping private and hybrid clouds.

The union promises enhanced solutions and accelerated innovation in this transformative generation.

Accenture Acquired Innotec Security

Accenture Acquired Innotec Security

Accenture acquired Innotec Security, a top Spanish cybersecurity-as-a-service provider, on November 2, 2023, strengthening Accenture’s cybersecurity capabilities and market presence in Spain.

Innotec Security, founded in 2002, boasts 500 cybersecurity experts and a wide range of services. The acquisition from Entelgy Group expands Accenture’s workforce and expertise in cybersecurity-as-a-service.

With 19 previous acquisitions, Accenture is a global leader in managed security services, securing the top spot in Gartner’s 2022 report. Besides this, the deal marks a strategic step in cybersecurity advancement.

Thales Acquired Imperva

Thales Acquired Imperva

Thales acquires a top-notch US cybersecurity firm known for data and app security at $3.6B. A global tech leader, Thales spans Defense, Aeronautics, Space, and Digital Identity.

A cyber leader, Imperva secures apps, APIs, and data with integrated edge, app, and data security. Partnership boosts both data and app security, propelling Thales into the app security market. Combined revenue exceeds €2.4B.

Deal impacts three key areas, finalizing in 2024 pending approvals.

SentinelOne Acquired Krebs Stamos Group

SentinelOne Acquired Krebs Stamos Group

SentinelOne tackles cyber threats with PinnacleOne, a strategic advisory group led by Krebs and Stamos. Launched at OneCon, it offers holistic risk management for businesses amid tech, cybersecurity, and geopolitics complexities.

PinnacleOne, a think tank and advisory, aids executives in navigating modern risks. Krebs, ex-CISA director, is the Chief Intelligence Officer, while Stamos, ex-Facebook CSO, is the Chief Trust Officer. Acquisition of KSG enhances SentinelOne’s security capabilities.

IBM Acquired Polar Security

IBM Acquired Polar Security

Under CEO Arvind Krishna, IBM acquired 5th company, Polar Security, focusing on cloud and AI capabilities. With 30+ acquisitions since April 2020, IBM addresses the “Shadow Data” surge amid COVID-19.

Polar Security offers Data Security Posture Management (DSPM) to locate and secure sensitive data across storage locations.

Automation detects structured or unstructured data, provides remediation, and generates security reports.

IBM plans to integrate Polar Security’s DSPM tech with Guardium for comprehensive data security, and for now, the acquisition price is undisclosed.

Proofpoint Acquired Tessian

Proofpoint Acquired Tessian

Proofpoint offers cloud-based solutions to prevent threats and protect sensitive data; with Tessian acquisition, it targeted misdirected emails and data exfiltration.

However, Tessian’s AI platform enhances Proofpoint’s email data loss prevention service.

This helps in mitigating accidental and malicious data loss. The integration of Microsoft 365 and Google Workspace ensures seamless email security implementation.

Okta Acquired Spera Security

Okta Acquired Spera Security

Okta acquired Spera Security, a rising star in Identity security, and it focuses on uncovering threats within SaaS and infrastructure applications.

The strategic union aims for a robust “Zero Trust” security posture. With 86% of breaches from Identity-related attacks, the alliance addresses phishing and social engineering challenges.

Okta and Spera offer a beacon of hope, providing comprehensive visibility and threat monitoring in the expanding SaaS and cloud landscape. The alliance is a commitment to empower users for a more secure digital future.

Cisco Acquired Isovalent

Cisco Acquired Isovalent

Cisco boosts cloud security dominance with Isovalent acquisition, a pioneer in open-source cloud-native networking.

The union uses Cisco’s Security Cloud vision to reshape cyber risk management across diverse cloud infrastructures.

The acquisition reinforces Cisco’s role in open-source foundations, positioning it as a cornerstone. Isovalent’s integration into Cisco’s Security Business Group is set for Q3 FY 2024.

Check Point Acquired Perimeter 81

Check Point Acquired Perimeter 81

Check Point acquires Perimeter 81 for $490M, accelerating secure access adoption globally. Perimeter 81, a Forrester Zero Trust Wave leader, brings cloud and on-device protection to over 3,000 customers.

Integration into Check Point Infinity architecture enhances threat prevention, creating a unified solution for network, cloud, and remote users.

The acquisition supports Check Point’s vision for the fastest, most secure SASE solution.

[ad_2]

Source link

Why is banking software development so important for the financial sector?

0

[ad_1]

Is it so important for banks to go digital?

Global digitalization is a process which started years ago, but the recent COVID-19 pandemic has shown that online solutions are more than welcome. Traditional banking services are not so popular and effective anymore. Most clients – especially generation Y – readily reach for modern tools. After years of testing they are mostly stable, run smoothly and grant a high level of security. That makes even elderly people feel comfortable while using online banking.

Such rapid growth of expectations towards financial software creates literally a gold rush. Banks that can keep up that pace win trust and a large number of new clients. Entities that are strictly devoted to the previous service model incur losses.

Traditional banking has a really long story, reaching far into the medieval ages. However, an inflexible approach to the market may turn out to be their doom. According to the Statista website, so-called neobanks (entities that operate solely on the internet) are growing stronger and in a few years may pose a serious threat.

What are the main challenges that arise while making banking software?

Financial sector is heavily regulated by law. At the same time, an entity must ensure that provided services are secure and must run simultaneously for thousands of clients. There’s no point in arguing that manual labor of clerks cannot be efficient enough to satiate market hunger. Thus, banking software development is a crucial step to implement automation. However, it’s not as easy as it may seem, while banking entities have to cope with requirements connected with:

– biometric authentication;
– outdated technology stack ang legacy systems;
– legal regulations such as GDPR, PSD2 (and upcoming PSD3) and PCSDSS concerning payment cards;
– evolving ways of communication – simple customer service is not enough while people expect video calls, AI assistants and selfie/OCR bank account setup.

It’s worth noting that different kinds of financial services require a slightly different approach. Retail, corporate and investment banking need tools designed for a particular niche of client.

Discover top trends in software development for financial sector

Dynamic technology evolution touches each and every sector in our lives. From smartphones and cars to banking software, we demand more fluent and more convenient use. How does it impact banking software? What are the new directions for developers?

One of the hottest topics is machine learning (ML) which is a part of a wider AI topic. ML algorithms are used to gather data about clients to help in the decision-making process. It may be used for credit underwriting, fraud detection, task automation and security management.

Another “holy grail” is biometrics. Perceived as an ultimate security measure, biometric data help to authorize logging, payments, withdrawing money from ATMs and most of all – onboarding new clients. There are a few biometric methods – from face recognition, through fingerprint and iris scans to voice recognition and behavioral biometrics.

Banking software development is an expensive and time-consuming investment. Correctly done, however, it can greatly reinforce brand, automatize a lot of business processes and attract new clients.

[ad_2]

Source link