Phishing is the art of sending an email with the aim of getting users to open a malicious file or click on a link to then steal credentials. But most phishers aren’t very good, and the success rate is relatively low: In 2021, the average click rate for a phishing campaign was 17.8%.
However, now cybercriminals have AI to write their emails, which might well improve their phishing success rates. Here’s why.
It asks you to update/fill in personal information.
The URL on the email and the URL that displays when you hover over the link are different from one another.
The “From” address is an imitation of a legitimate address, especially from a known brand.
The formatting and design are different from what you usually receive from a brand.
The content is badly written and may well include typos.
There is a sense of urgency in the message, encouraging you to quickly perform an action.
The email contains an attachment you weren’t expecting.
While most of these are still valid, there are a few checks you can strike off your list due to the introduction of AI.
When a phisher is using a Large Language Model (LLM) like ChatGPT, a few simple instructions are all it takes to make the email look as if it came from the intended sender. And LLMs do not make grammatical errors or put extra spaces between words (unless you ask them to).
They’re not limited to one language ether. AI can write the same mail in every desired language and make it look as if you are dealing with a native speaker. It’s also easier to create phishing emails tailored to the intended target.
All in all, the amount of work needed to create an effective phishing email has been reduced dramatically, and the number of phishing emails has gone up accordingly. In the last year, there’s been a 1,265% increase in malicious phishing emails, and a 967% rise in credential phishing in particular.
Because of AI, it’s become much harder to recognize phishing emails, which makes things almost impossible for filtering software. According to email security provider Egress 71% of email attacks created through Ai go undetected.
So how do you recognize AI phishing emails?
Here are some ideas:
Number 4 above—The formatting and design are different from what you usually receive from a brand—is helpful. Compare the email with any previous communications you have from the supposed sender. If there are inconsistencies in the tone, style, or vocabulary, this could indicate that the message is a phishing attempt.
Number 5—The content is badly written and may well include typos—AI phishing emails may still use generic greetings, such as “Dear user” or “Dear customer,” instead of addressing the recipient by name. Also, look for generic or mismatched signatures that do not align with the sender’s typical signature.
Number 7—The email contains an attachment you weren’t expecting—If you know the person who sent the email but don’t trust the content, contact the sender through an alternate communication method to verify whether they actually sent it.
For organizations it is important to have a clear reporting procedure and actively follow up on reported suspected phishing emails. If your employees never hear back about a reported phishing email, they are less likely to report the next one. A pat on the shoulder for catching one goes a long way. A lot further than the more common shame-and-blame punishments for clicking a malicious link.
Repetitive phishing training that neither aligns to how users engage with email, nor provides appropriate tools for responding to ambiguous emails are a waste of time, money, and the patience of the employee.
And most of all, make sure that your own communications, internal and external, don’t look like phishing attempts.
We don’t just report on threats—we remove them
Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.
It was an epic lawsuit and it was an Epic lawsuit. Two weeks ago a federal jury found that the Google Play Store violated antitrust laws. Google’s in-app payment processing platform and the process of distributing Android apps were both run as monopolies said the jury in Epic v. Google. Epic sued Google after the game developer was sent packing from the Play Store along with its popular Fortnite game after Epic promoted its own in-app payment processing system which violated Play Store rules.
According to a report published by Bloomberg, Google seriously considered changing the in-app payment processing platform from which it was taking 15% to 30% of in-app revenue. In 2021, Google considered an overhaul to the Play Store billing model which was called Project Everest. This was discovered in documents that were released as part of the Epic v. Google antitrust suit.
Google found itself in a tight spot. On one hand, it was worried that if it didn’t make any change to the Play Store’s in-app payment processing platform, it would be done in by regulatory overreach. On the other hand, making changes to the platform could seriously impact the company’s revenue. During an in-house presentation, Google said, “We can defend the status quo for a few months. Making proposed changes sooner may help support reasonable legislation, position Google as a leader, and prevent more draconian legislation.”
Google decided that Project Everest would cost Google too much money
Project Everest would have stopped Google from taking its 15% to 30% cut of in-app revenue and instead, developers would be charged for various services related to listing their apps in the Play Store with additional charges tacked on for user downloads and updates. But making this switch would cost Google in the form of a $1 billion to $2 billion decline in annual revenue from apps and $6 billion to $9 billion in revenue from games.
Google employees floated the idea of having app developers handle in-app payment processing themselves in exchange for paying Google a lower fee. Google calculated that this option would reduce annual Play Store revenue between $250 million and $1.3 billion.
Also two weeks ago, Google announced the terms of a settlement it made back in September with all 50 states, the District of Columbia, and two US territories for $700 million. After giving the states $70 million of the settlement for penalties, restitution, disgorgement, and fees, the remaining $630 million will be shared among Play Store customers who will get a minimum of $2 each.
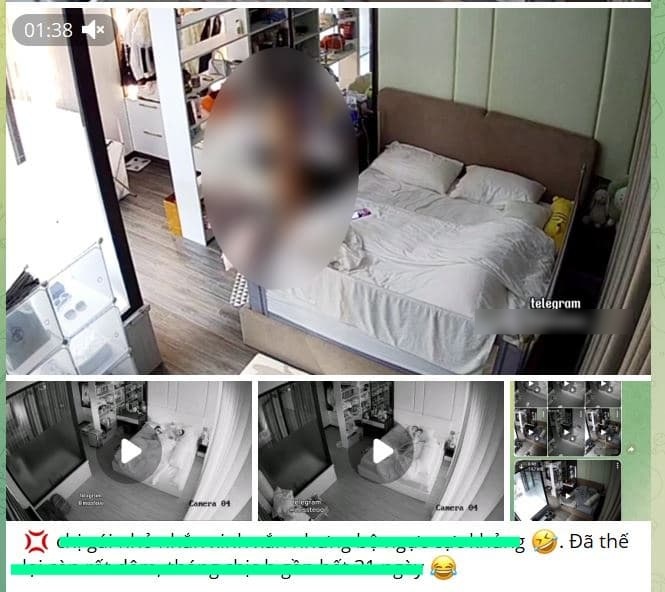
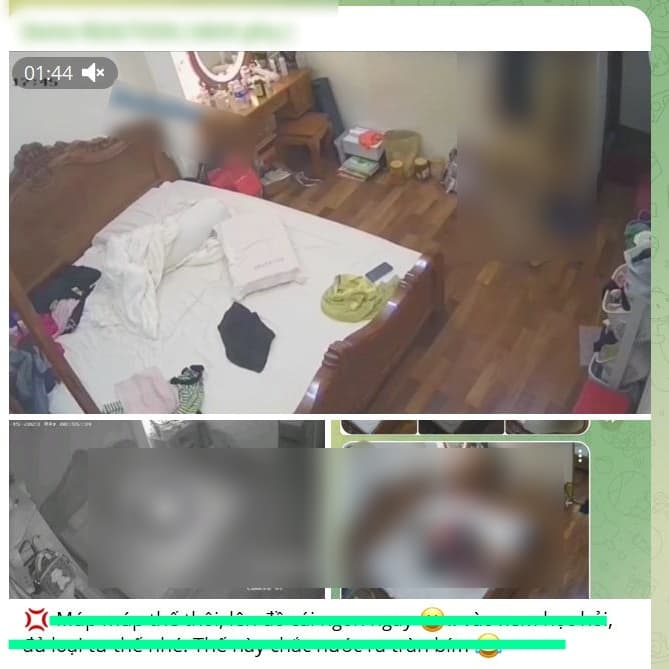
A group of Vietnamese individuals involved in cybercrime is hacking into home security cameras of unsuspecting users and selling private and intimate footage on Telegram for a mere $16.
A Vietnam-based Telegram group has been discovered selling private footage obtained from hacked security cameras, showcasing what they describe as ‘dark corners’ and ‘hot scenes.’ Security experts attribute this privacy breach to poor password hygiene as the primary cause.”
In 2021, cybersecurity researchers at BitDefender debated whether Telegram, an encrypted messaging app, had become the new dark web. As the world approaches 2024, the significance of this argument has never been more evident.
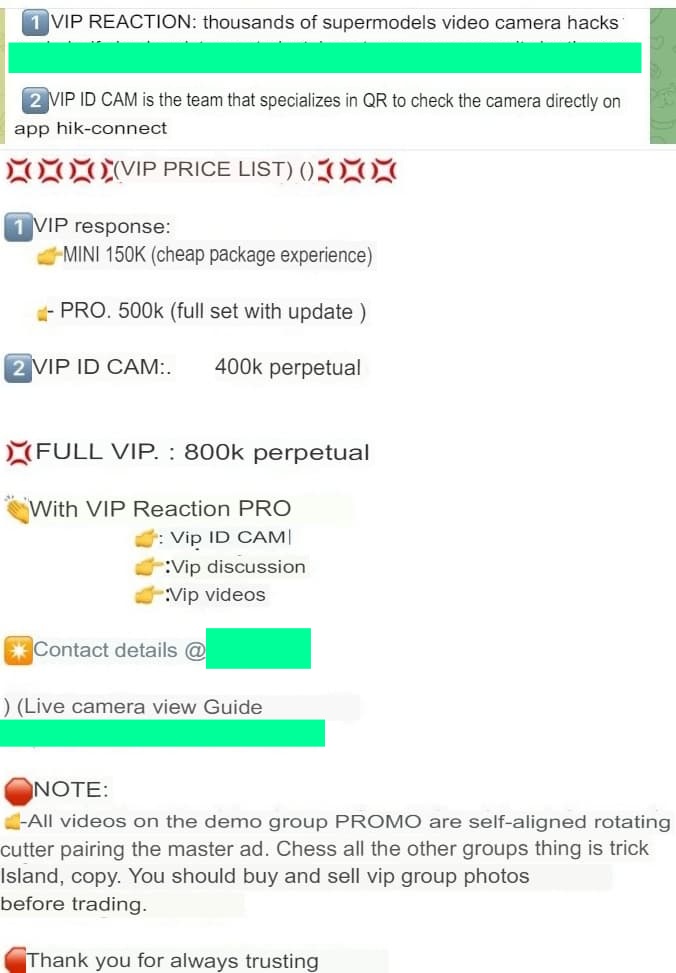
According to details shared by security researcher Minh Hung, who first discovered the notorious Telegram group and published by Vnexpress, the group offers three packages for accessing the hacked footage.
The cheapest package costs 150,000 Vietnamese Dong ($6.16), while the highest package costs VND500,000 ($20.53). The top tier, ‘Super VIP,’ includes 4 years’ worth of hacked footage from hundreds of cameras and live access for VND800,000 ($32.84).
This group claims to specialize in hacking into “private cameras of families and shops in Vietnam” and invited Hung to join them on the channel.
Hackread.com also managed to identify Vietnamese-language Telegram channels offering malicious footage stolen from hacked home security cameras. The screenshots below were taken by Hackread.com:
One of the sold footage recorded from a hacked home security camera (Credit: Hackread.com).
One of the sold footage recorded from a hacked home security camera (Credit: Hackread.com).
Screenshot shows “price package offered to “buyers” – Some disturbing details have been redacted (Credit: Hackread.com
On the other hand, according to Vnexpress’s report, Hung could watch the videos for the first and second packages, but with the third package, he could download an application from a camera firm and watch live feeds using the provided QR codes. Hung suspected it to be a scam but paid VND800,000 to check it out.
Hung further discovered that the timestamps on security camera feeds matched the current time. Using the application, he could access 15 cameras installed in clothing shops and spas, including bedrooms, living rooms, and dressing rooms.
Should You Install Security Cameras in Your Bedroom?
Installing security cameras in your bedroom raises significant privacy concerns and is generally considered a bad idea. The bedroom is an intimate space where individuals expect the highest level of privacy. Placing cameras in this area not only invades personal boundaries but also raises ethical issues.
The footage captured in bedrooms can include highly sensitive and personal moments, compromising one’s privacy and dignity. Beyond the ethical aspect, it also poses a risk of unauthorized access by hackers, as demonstrated by this article.
Additionally, such surveillance within the confines of a home may lead to legal implications, as it potentially violates laws related to privacy. To maintain a sense of security and privacy, it is advisable to install cameras in public areas of the home while avoiding intrusion into personal spaces like bedrooms.
How to Protect Your Security Camera from Hackers?
whether at home or work, protecting your security cameras from hackers is crucial to protect your privacy and security. Here are some vital tips to help you enhance the security of your security camera system:
Update Firmware Regularly: Ensure that your security camera’s firmware is up to date. Manufacturers often release updates that address security vulnerabilities, so regularly check for and install firmware updates.
Use Strong Passwords: Create strong, unique passwords for your camera’s login credentials. Avoid default passwords and choose a combination of letters, numbers, and special characters. Change passwords regularly and avoid using easily guessable information.
Network Security: Secure your home network by setting up a strong Wi-Fi password and using WPA3 encryption if available. Restrict access to your network by using a strong, unique network password.
ALWAYSChange Default Settings: Change default usernames and passwords on your security cameras. Default credentials are often well-known and exploited by hackers.
Enable Two-Factor Authentication (2FA): Whenever possible, enable two-factor authentication on your security camera accounts. This adds an extra layer of security by requiring a second form of verification, such as a code sent to your mobile device.
Regularly Check for Suspicious Activity: Monitor your camera system for any unusual or unauthorized access. Regularly review footage and set up alerts for suspicious activities, such as multiple failed login attempts.
Keep Cameras Offline When Not in Use: Consider disconnecting your security cameras from the internet when you don’t need remote access. This can be done by configuring your router to block camera access during certain hours.
Purchase from Reputable Brands: Choose security cameras from reputable manufacturers with a track record of providing regular firmware updates and security patches.
Secure Physical Access: Ensure that physical access to your cameras is restricted. Place cameras in locations that are not easily accessible, and consider installing them at a height to prevent tampering.
Regularly Review Camera Logs: Some advanced camera systems provide logs of access and activities. Regularly review these logs for any suspicious entries.
Our business solutions remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.
Just in time for the holiday vibe, a federal judge ruled that X/Twitter violated contracts by failing to pay millions of dollars in bonuses that the social media company had promised its employees.
Reuters is reporting on the story of Mark Schobinger, Twitter’s senior director of compensation before leaving Elon Musk’s company in May. Mark sued X/Twitter the very next month, claiming breach of contract. His problem is that before and after billionaire Musk bought Twitter last year, the company promised employees 50% of their 2022 target bonuses – and never made those payments.
Now, US District Judge Vince Chhabria denied Twitter’s motion to dismiss the case, ruling that Schobinger plausibly stated a breach of contract claim under California law and he was covered by a bonus plan. “Once Schobinger did what Twitter asked, Twitter’s offer to pay him a bonus in return became a binding contract under California law. And by allegedly refusing to pay Schobinger his promised bonus, Twitter violated that contract”, the judge wrote.The counterpart – that’s X/Twitter – and their lawyers argued that the company made only an oral promise that was not a contract and that Texas law should govern the case.
Meanwhile, Meta gets fined in Italy
Meanwhile, Meta is not too far back, bringing its fair share of holiday scandals as well. The Facebook, Instagram parent company was just fined in Italy for breaches of a ban on the advertising of gambling.
Meta has been fined €5.85 million ($6.45 million) in connection with profiles and accounts on Facebook and Instagram, as well as sponsored content that promoted either betting or games with cash prizes, communications watchdog AGCOM said in a statement on Friday.
Similar fines were set aside for YouTube (€2.25 million) and Twitch (€900,000) recently.
It’s been more than a month since the last time we talked about one much-needed feature for the Gmail app: an Unsubscribe button that’s convenient and spares you the need to scroll and poke around in menus.
Back in November, it became known that the Gmail team was testing a tweak for Android users to let them unsubscribe from unwanted mail quickly and easily – now, it’s not Android phones that get it.
Instead, the iOS users get it first (via Android Authority) and the solution is quietly rolling out.
There’s a prominent “Unsubscribe” button in Gmail for iOS and users are seeing it right below the email’s subject line and above the email content. The report has some screenshots to get a better idea of the updated user interface, here they are:
Instead of tapping the 3-dot menu icon at the top of the message window and then searching for “Unsubscribe” (or scrolling to the bottom of the email and looking for the sender’s “Unsubscribe” button), this new solution is far more convenient and time-saving. No scrolling, no searching, just a single tap on the button and you’re ready to go. This iOS Gmail app addition is similar to the web version’s unsubscribe button, which is placed below the subject line and next to the sender’s details.
So far, the new unsubscribe button is not yet to be found on Android devices. Quite the irony in the light of the fact that Android is Google’s own platform, but that’s not the first time Google has brought features to iOS before Android – like the option to delete the last 15 minutes of the browsing history in the Google app, and the ability to crop videos in Google Photos.
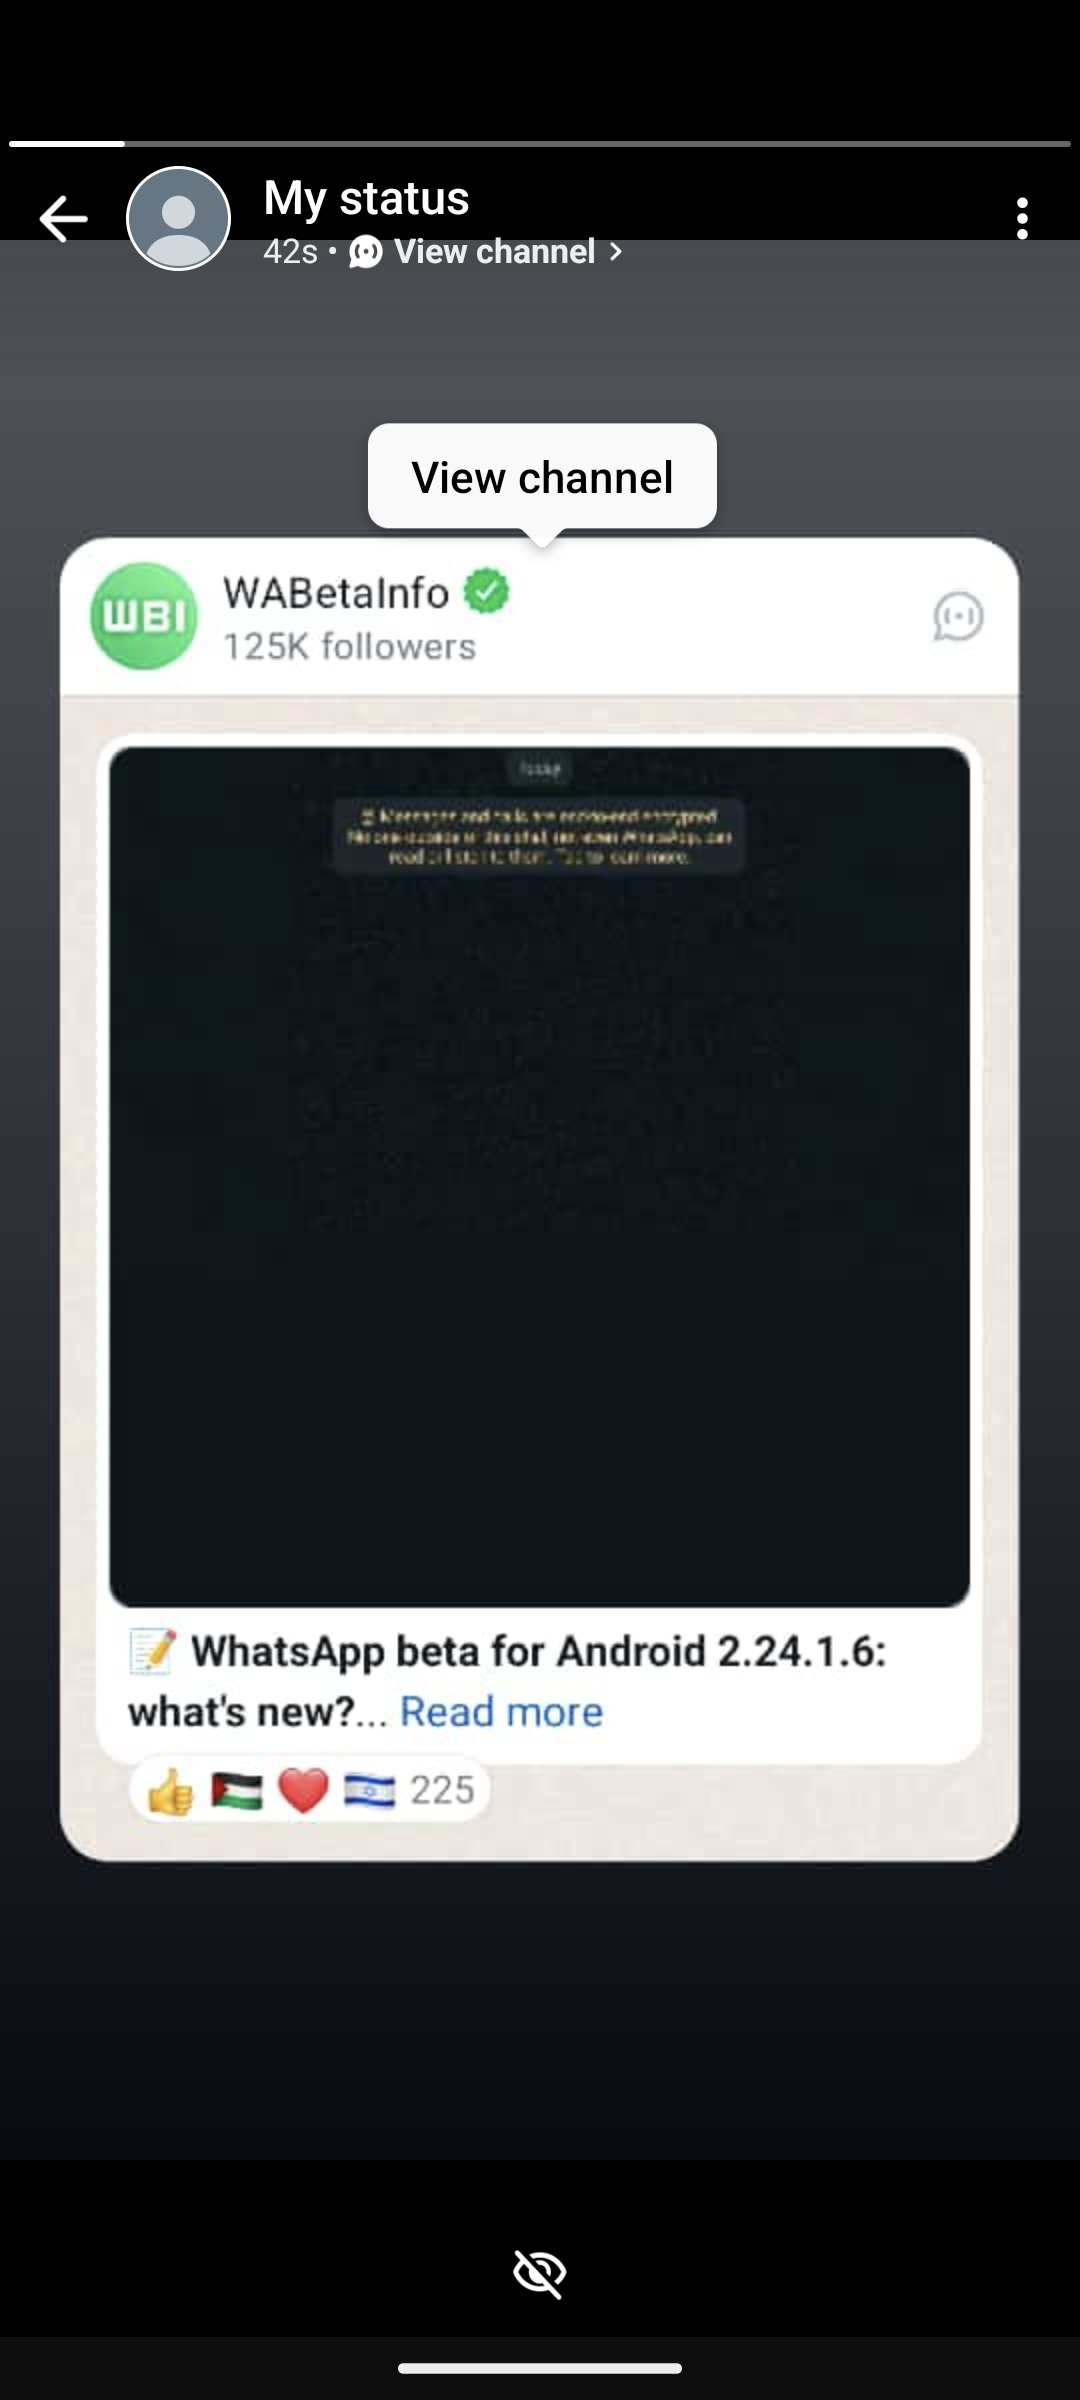
The WhatsApp beta for Android (v.2.24.1.6) update brings a new interface when sharing channel updates to Status.
For now, the feature is available to some beta testers, but it’ll be rolled out to more people in the coming weeks (via WABetaInfo).
As seen above, those who have received the v.2.24.1.6 update may explore a new interface that enhances the way users view a channel update from a status update. Specifically, WhatsApp will create a dedicated layout for the channel update, with the aim of providing clarity that the content posted on Status originates from a channel.
Those who want to check it out and see if this feature is already available to their accounts, can simply share a channel update to their status (the quickest method to do this is by forwarding a channel update). It’s also important to note that WhatsApp has recently introduced another entry point within the status subtitle, allowing users to promptly access and view the content from the associated channel.The WhatsApp experts at WABetaInfo say that the refreshed interface offers an intuitive layout, “making it easier for users to interact and access shared channel updates”. They also note that this interface aligns with contemporary design trends – “it’s very similar to the layout offered by Instagram when sharing posts as Instagram Stories”.
The ransomware extortion landscape is evolving with threat actors adopting new methods to blackmail and threaten their victims. Single-extortion, where cyber criminals demand payment to decrypt locked data or systems is quickly becoming less frequent with ransomware groups increasingly adopting double-extortion – where threat actors demand a ransom payment to decrypt victim data/systems and then threaten to publish stolen data unless the ransom is paid. Triple-extortion is also on the rise, such as distributed denial-of-service (DDoS) attacks or further intimidation of the victim/their customers, employees and stakeholders into paying a ransom.
This played out recently when notorious ransomware group BlackCat/APLHV filed a US Securities and Exchange Commission (SEC) complaint against one of its alleged victims for failing to comply with a four-day cyber attack disclosure rule. The unprecedented move took the threat group’s extortion efforts to a new level after it claimed to have recently breached and stolen data from the software company MeridianLink.
Cyber Security Hub spoke with Dr Jason Nurse, Institute of Cyber Security for Society at the University of Kent, and a co-lead of the Royal United Services Institute’s (RUSI) Ransomware Harms and the Victim Experience project, about the changing ransomware extortion landscape and the threats it poses to businesses.
Cyber Security Hub: In what ways are ransomware extortion methods evolving?
Dr Jason Nurse: Ransomware attacks have evolved significantly, displaying increased sophistication and harm-potential. In the past, cyber criminals sought to paralyze an organization’s systems and extort a ransom for access to be restored. In response to businesses enhancing their recovery capabilities and resisting payment, our research has discovered that attackers have adapted their methods to inflict a wider variety of harms.
CSH: What impact are evolving extortion methods having on the ransomware threats faced by organizations?
JN: The evolution of extortion methods means that the ransomware threat is pervasive and a persistent challenge for organizations. We found an extensive range of harms in our recent analysis of impacts from ransomware attacks. As businesses respond to the threat by bolstering their defenses – through measures like improving intrusion prevention systems, employee training and reinforcing backup strategies – cyber criminals promptly adjust their strategies to up the ante.
The significance of this threat has prompted increased government involvement. The Counter Ransomware Initiative (CRI) is an excellent example of such an effort and the recent agreement by CRI member states not to pay ransoms using government funds is certainly a powerful step forward in addressing this complex issue.
CSH: What do evolving extortion trends signify about today’s ransomware threat actors?
JN: The evolving trends in ransomware extortion mechanisms highlight a significant characteristic of today’s threat actors – their unwavering determination. These actors exhibit a remarkable readiness to adapt in any manner necessary to heighten the prospects of securing a ransom payment. Naming and shaming victim organizations on dark web notice boards, contacting individuals who do business with those organizations and disclosing sensitive corporate data all highlight a surprising level of resolve.
What has undoubtedly shocked most of the security community, however, has been the engagement of one cyber criminal group with the SEC. In this instance, the group filed a complaint alleging a business’s failure to disclose a purported data breach instigated by the hackers. This places an organization in a challenging position, considering reporting obligations, notification procedures and the broader implications of negative publicity.
CSH: What’s your advice to any organization being extorted following a ransomware attack?
JN: Payment is not the only option – and should certainly not be the first option. The organization must recognize that ransomware groups will employ various tactics to push for a payment. If an organization is being extorted, the initial step should involve isolating all infected systems from the central network or shutting them down altogether. The organization can then engage with law enforcement, regulatory bodies, cyber insurance providers and, depending on the expertise internally, incident response firms for support in their response.
Some of these services may have access to decryption keys (e.g. No More Ransom), offer threat intelligence about the attacker, provide insights into the repercussions of payment and furnish information about the attacker’s affiliations with other entities. Such resources prove invaluable as the organization deliberates on the most effective response to the extortion attempt.
CSH: How can security stay ahead of ransomware extortion?
JN: This is very much an arms race. Cyber attackers are constantly exploring ways to increase the effectiveness of their ransomware extortion tactics. Conversely, defenders are continually preparing and responding to the best of their ability. A proactive strategy for cyber security to get ahead of the threat of ransomware involves developing a better understanding of all its facets – the attackers, the attack vectors, the harms, the payment mechanism, etc. – and tackling each of them directly.
For instance, there have been cases where law enforcement has tracked down attackers and regained extorted funds and apprehended those responsible for attacks. Our research is driven by the conviction that only through a nuanced understanding of the diverse harms stemming from ransomware extortion can we formulate improved policies and mechanisms to address this pervasive threat.
RomCom ransomware is being spread via poisoned Google adverts for legitimate software companies including Chat-GPT, PDF Reader Pro and Devolutions’ Remote Desktop Manager.
According to researchers at IT security company Trend Micro, malicious actors are using Google advertisements for trusted companies to entice people into clicking on the advert and downloading RomCom ransomware onto their devices. The malicious actors are doing this through the use of fake sites set up to look like legitimate ones with poisoned uploads that execute the malware on victims’ devices once it is downloaded.
By using paid advertisements slots and SEO tactics, malicious actors can ensure that the poisoned uploads remain at the top of Google’s search results, meaning that more people are likely to fall victim to these trojanized adverts.
RomCom ransomware has been linked to a Cuban ransomware affiliate dubbed ‘Tropical Scorpius’ by Trend Micro. The malware is responsible for a number of attacks across the globe, including those against Ukrainian government agencies in October 2022.
Once it is downloaded onto a device, the backdoor malware can cause damage to victims in a number of ways, including executing more malicious files on the infected device, running malicious programs and exfiltrating data from the compromised devices. It can also run spyware in hidden windows, set up proxy servers for malicious activities and even compress and send files on the infected device to servers owned by the malicious actors.
RomCom ransomware also has the ability to take screenshots on the device, meaning that any confidential, personal or compromising information entered into the device can be used by the hackers for their own means. This includes gaining access to financial services like banks, cryptocurrency wallets and other payment services, access chat messages stored on the device and steal all login credentials entered into the device.
Bumblebee ransomware spread via poisoned Google ads
In April of this year, it was found that malicious actors were employing SEO tactics and paying for targeted advertisements to entice victims into clicking on malware.
Cyber security company Secureworks found malicious actors had been using poisoned ad installers as trojans to spread Bumblebee malware. These ad installers were associated with a number of well-known companies including Zoom, Citrix Workspace, Cisco AnyConnect and OpenAI’s ChatGPT. For example, Secureworks researchers found that a malicious actor had not only created a poisoned ad installer for Cisco AnyConnect, but a fake download page for the malware as well. They were able to do this by exploiting a compromised WordPress site.
Once Bumblebee malware is downloaded, malicious actors most often use it to launch ransomware within the infected device. In one case, Secureworks researchers found that the malicious actor moved laterally across the device, downloading and launching a number of applications and software programs including legitimate remote access tools AnyDesk and Dameware as well as penetration testing malware Colbalt Strike.
In the current high-tech age, consumer data is a business’s most important asset as they progressively shifts towards digital transformation. Consumers want tailored experiences from brands and businesses that meet their specific needs. In these conditions, companies need to gather, examine, and utilize consumer data much more efficiently than they did in the past. In addition, Adobe Experience Cloud Products like Adobe Real-Time CDP are available to assist.
A revolutionary solution called Adobe Real-Time Customer Data Platform was created to assist companies in realizing the whole value of their customer data. It offers a single, accessible place for real-time information management, organization, and activation. This post delves deeply into Adobe Real-Time CDP, showing you how to use it to enhance marketing ROI, provide individualized customer experiences, and propel company expansion.
Describe CDP
A customer data platform (CDP) is a solution that compiles client information into a single database, giving marketing teams the vital information they need to start a campaign. The primary objective of a CDP is to gather information from offline and online sources to provide a complete picture of a customer. With this data, a CDP system might help businesses anticipate the best course of action with a certain customer.
Furthermore, customer support teams may use CDPs to provide more individualized customer support. Data warehousing solutions and marketing automation are two more application areas.
CDPs are often separated into many categories. The most popular method for combining customer data to create a single consumer profile is data CDP. Conversely, campaign CDPs provide cross-channel and multichannel marketing centres in addition to campaign management. Additionally, analytics CDPs are proficient in data analysis.
But it’s critical to understand the differences between CDPs and data management platforms, data warehouses, and CRM systems. Unlike CRMs, CDPs collect a wide variety of data from many sources without requiring any human upkeep. While CRMs, which collect customer transaction data and are usually maintained by salespeople, also concentrate on finding segmented audience profiles.
So what exactly is Adobe Real-Time CDP?
Adobe Real-Time CDP: What is it?
Adobe Real-Time CDP allows you to deal with customer data, much like the majority of conventional customer data solutions. One significant benefit, however, is that you get information as soon as it becomes available. Adobe Real-Time CDP depends on the following four pillars to do this:
Gathering of Data: The platform gathers information from a variety of sources, such as physical channels, smartphone applications, and e-commerce websites.
Unification of Data: Adobe Real-Time CDP creates a single customer view by combining consumer data gathered from several contact points.
Instantaneous Activation: As soon as new data enters the system, the platform uses it to activate client data in real-time to create tailored experiences and adjust them across channels.
Division: To provide more individualized customer experiences, Adobe Real-Time CDP divides your clientele into groups according to their demographics, actions, and other factors.
Adobe Real-Time CDP can generate a single, cohesive picture of each client with the use of these capabilities. Real-time data allows you to create relevant and tailored customer experiences that increase engagement and win over new clients as devoted ones. Adobe’s capacity to activate data across several channels also leads to increased customer satisfaction and marketing return on investment.
How Does Real-Time CDP from Adobe Work?
To put it simply, managing client data in Adobe Real-Time CDP is rather easy. Ingestion, unification, and activation make up its components:
swallowing. To begin with, Adobe Real-Time CDP pulls data from several sources, including mobile applications, e-commerce websites, POS systems, CRM systems, and outside sources. The platform supports many formats and manages massive data volumes.
fusion. Next, a variety of identity resolution methods are used by Adobe Real-Time CDP to unify the imported customer data. The platform creates a single, cohesive picture of each prospect by connecting consumer profiles from many data sources.
Turning on. In the last phase, customer data activation across email, online, mobile, and advertising channels is carried out via Adobe Real-Time CDP. As a result, it enables you to provide tailored experiences across the whole consumer journey and bridge any gaps between various marketing initiatives.
Adobe Real-Time CDP gathers and combines client data from several sources using a real-time data processing engine. It is noteworthy to add that machine learning techniques are used for these and other operations by the platform. For example, it utilizes the most recent technological advancements to evaluate client data and provide cohesive consumer profiles.
After client data has been gathered and consolidated, you can use Adobe Real-Time CDP to make the information that has been ingested available via a variety of channels. Measuring the effectiveness of your customized marketing initiatives is simple with the platform’s real-time analytics and reporting features.
Let’s now examine how obtaining a comprehensive customer perspective using Adobe Real-Time CDP enables you to completely reconstruct a customer journey. The platform can standardize and integrate cross-channel data, as we have previously said, giving you a single source of truth that incorporates all contact points (both online and offline). Next, Adobe Real-Time CDP builds customer categories that may be customized as additional data is gathered, based on specific journey stages, purchase behaviour, timing, and user status.
Through easy procedures and a straightforward admin experience, everyone can access all of the data and insights. You get several tools that provide a steady stream of data that your team may access. Another noteworthy enhancement that elevates Adobe Real-Time CDP to a significant tool that offers privacy-centric identity resolution is first-party monitoring across all touchpoints. Without creating a single line of code, the platform guarantees that everyone who requires it can manage omnichannel data.
In terms of AI and machine learning, Adobe Real-Time CDP makes use of cutting-edge technology to calculate the effectiveness of your marketing across various client journeys. Predictive qualities, audiences, and actions may all be streamlined to provide you with more information and help you decide on your plans.
Right now, things can seem confusing, but there’s nothing to be concerned about. Everything becomes obvious the first time you work with the real interface. The five easily navigable areas of Adobe Real-Time CDP are Sources, Destinations, Identities, Segments, and Profiles.
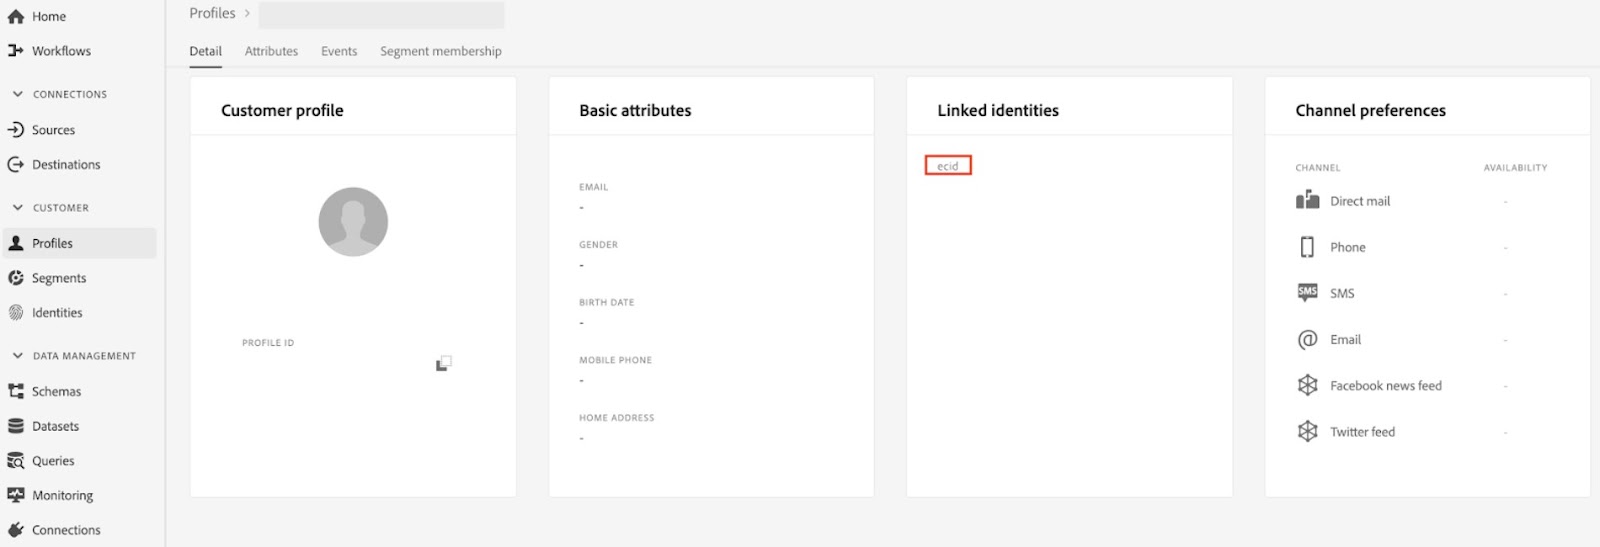
Tab for Real-Time CDP profiles
Profiles: A profile is an assortment of data that may be used to uniquely identify a person or other entity. Although the profile in this example is associated with the ECID identity, this profile can have other identities as well, such as an email address or phone number.
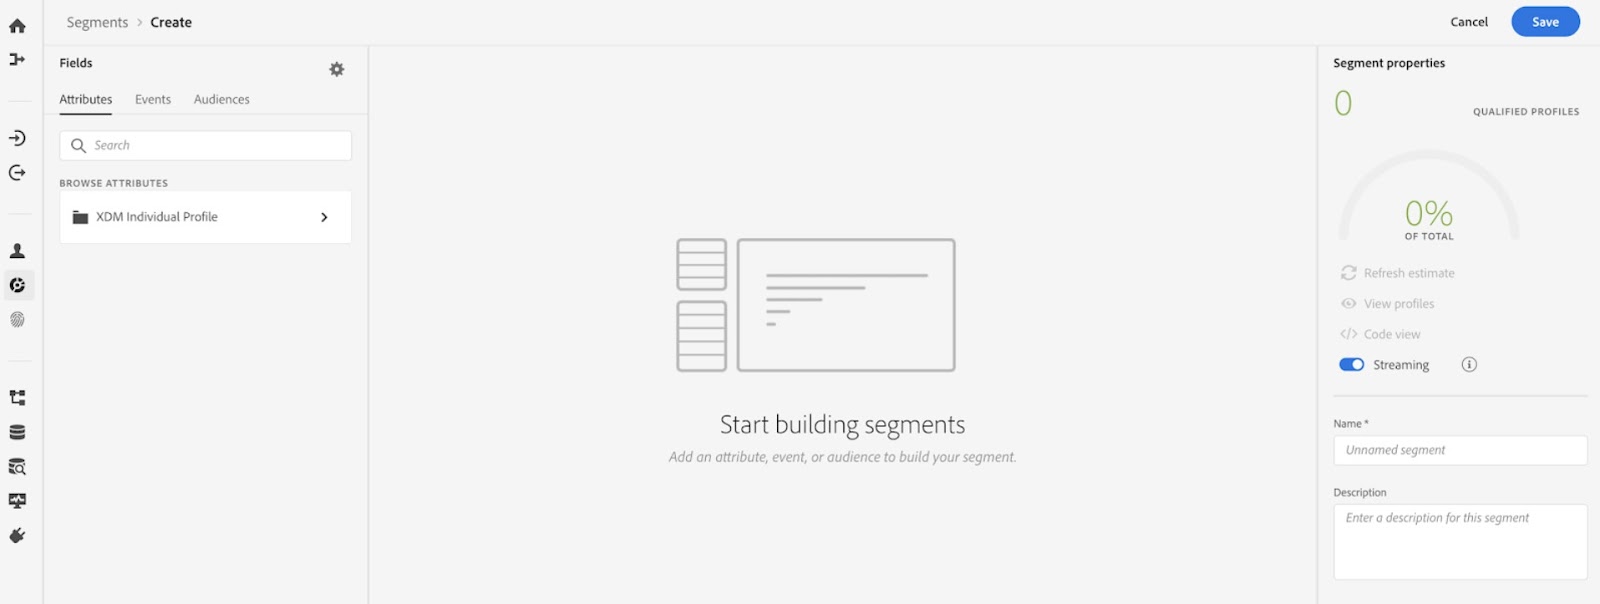
Sections: You may divide profiles into groups based on a variety of criteria by using segments. Real-Time CDP segments like those in other Adobe products.
Tab for Real-Time CDP Segments
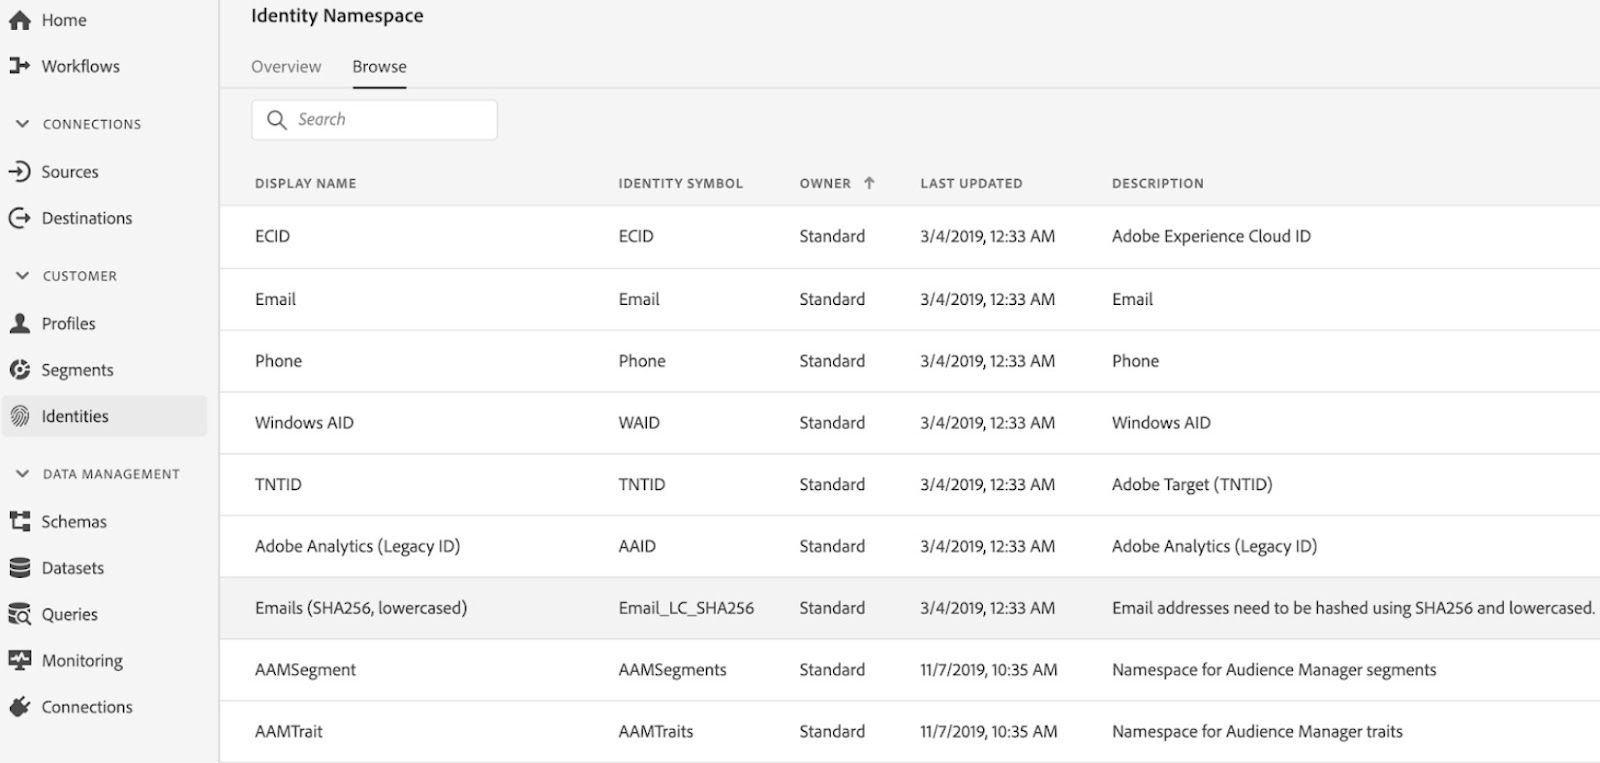
Personas. Identity namespaces containing distinctive personal data, such as address, phone number, email address, etc., are stored on the identity page.
Real-time identification of CDPs tab
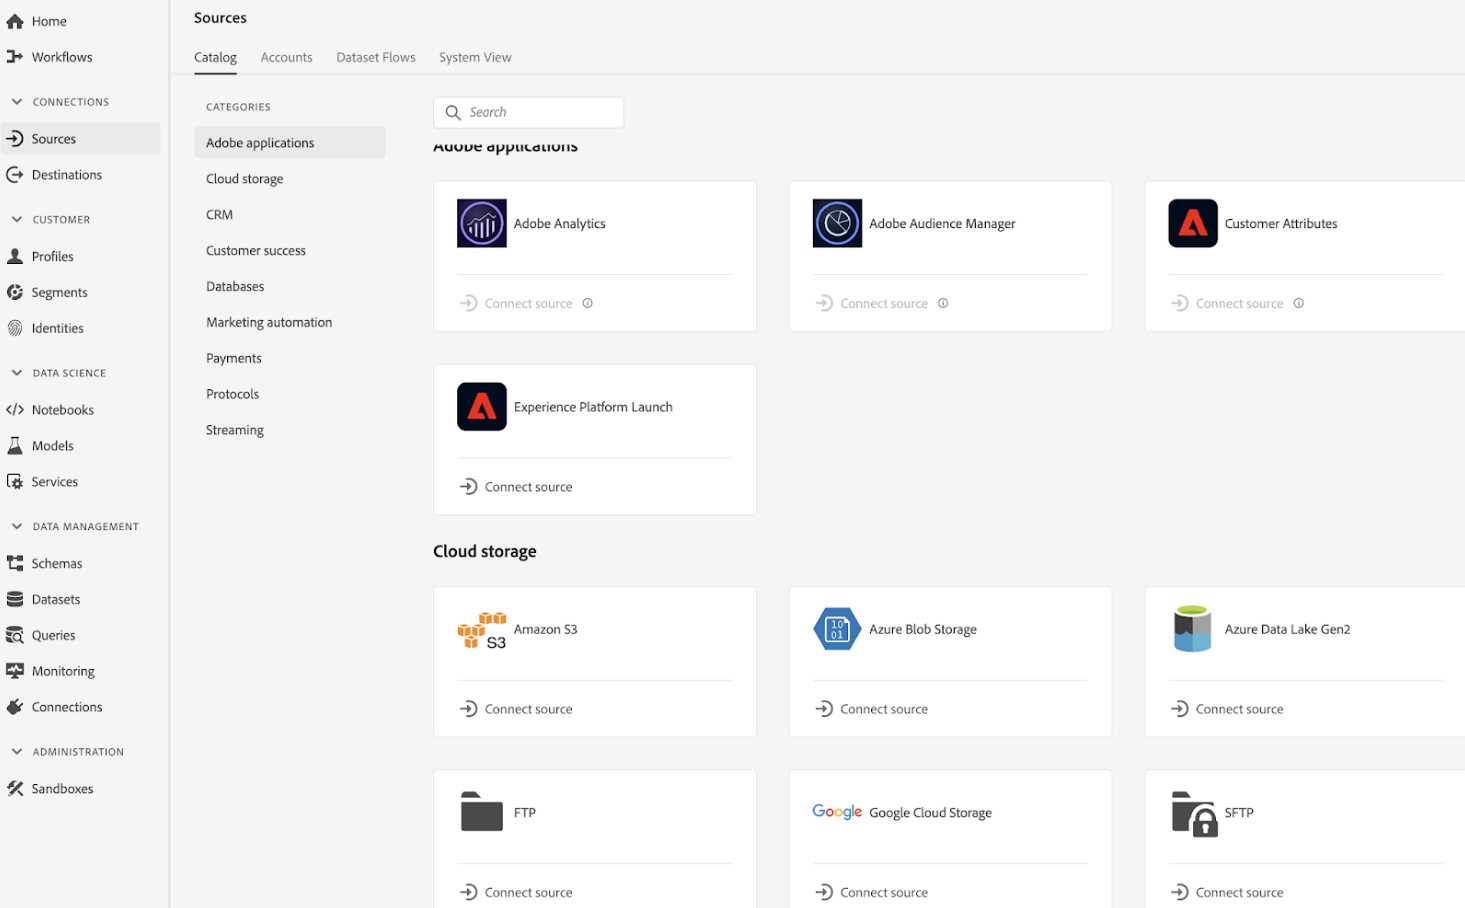
References: You may find several sources for data in this area. You may find them under the Sources -> Catalog section. Here is where you may link your Real-Time CDP to other sources, CRM programs, and Adobe apps.
Tab for Real-Time CDP sources
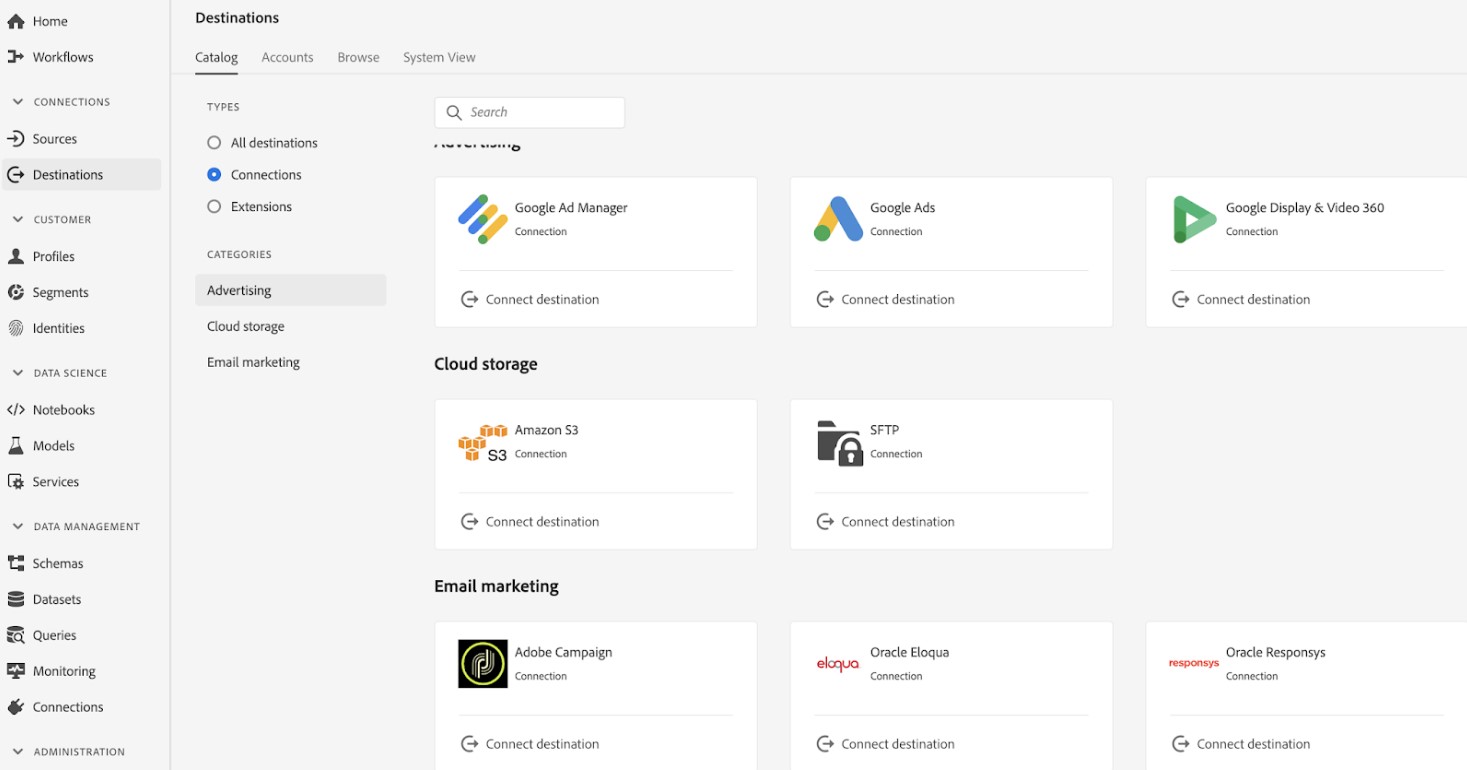
Locations: The Sources and Destinations sections are comparable. Here is where you may turn on the audiences and share them with other systems that need specific consumer information. You may export segments or profiles using Real-Time CDP.
Tab for Real-Time CDP Destinations
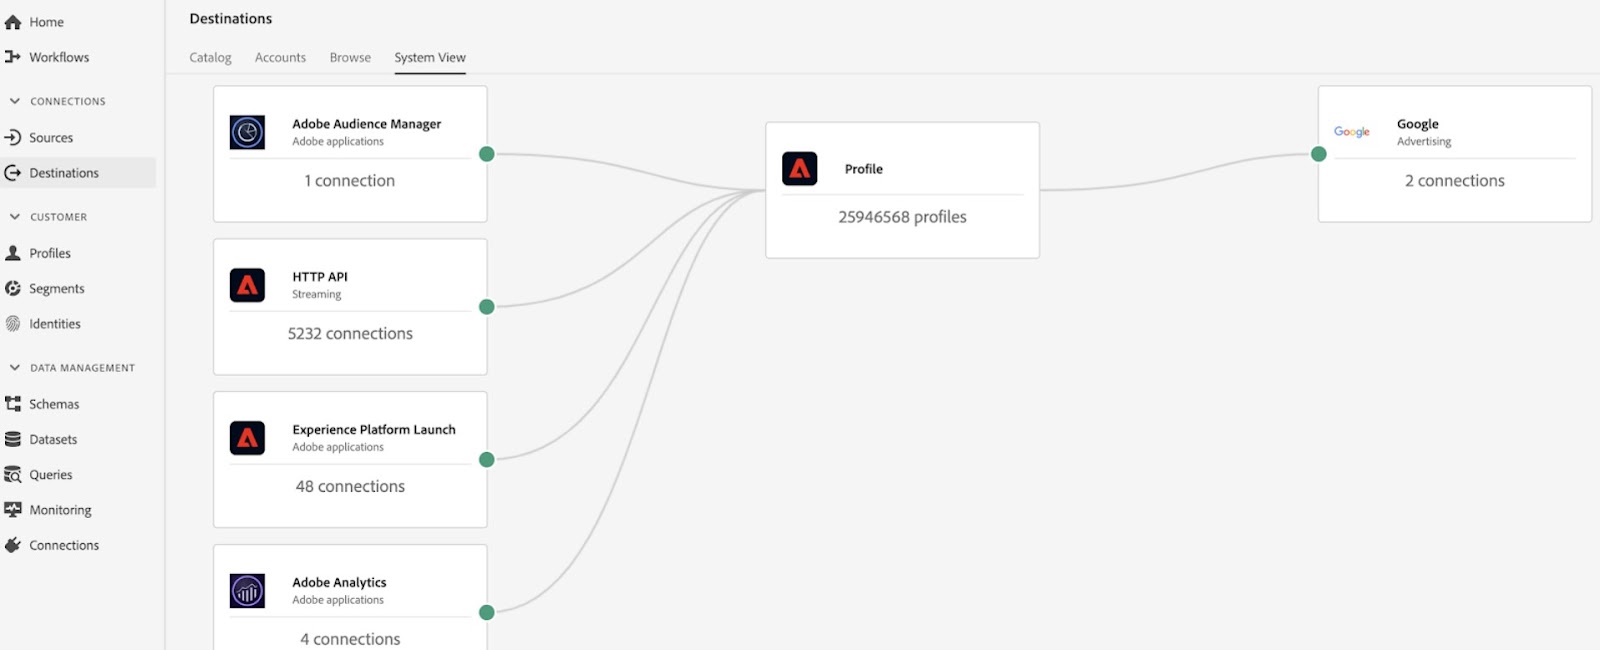
In Adobe Real-Time CDP, the process of connecting profiles to sources and sending them to a destination is shown in the following graphic representation:
CDP connectivity in real-time tab
All pictures were obtained from this article: Overview of Real-Time CDP. To understand more about the platform, check the video below to see how connections are made in Adobe RT CDP.
Adobe Real-Time CDP: Advantages
You may wonder what advantages Adobe Real-Time CDP offers. In addition to the functionality seen on rival platforms, the platform provides several significant competitive advantages. The advantages of Adobe Real-Time CDP are as follows:
Instantaneous Understanding: With Adobe Real-Time CDP, you can enhance your marketing strategy and make data-driven choices by getting real-time insights into customer behaviour.
Multichannel Advertising. By gathering information via a variety of channels, the platform makes sure that every touchpoint offers a consistent and tailored experience. To create a cohesive picture of every consumer, it connects customer profiles from various data sources using identity resolution algorithms.
Individualization: As we’ve previously shown, Adobe Real-Time CDP may be used to provide unprecedented levels of customisation. Businesses may design tailored customer experiences using the platform that meets customers’ expectations. Delivering tailored communications that connect with your customers may be made easier with the flow of real-time consumer data integrated across all channels.
You can increase customer engagement and happiness by using Adobe Real-Time CDP. When your customers participate in experiences that align with their wants and preferences, they are more inclined to interact with your brand.
Increased ROI: With all these benefits of Adobe Real-Time CDP, you may raise the return on investment (ROI) of your marketing initiatives, resulting in increased sales and profitability.
Flexibility: Large data quantities may be handled with Adobe Real-Time CDP, which is a highly scalable solution. You may use the platform as a market giant with thousands of clients across several channels, or you can start small and expand.
The rivals of Adobe Real-Time CDP include, among others, Insider, Klaviyo, Insightly, Bloomreach, and Planhat.
How Can Adobe Real-Time CDP Be Implemented?
To put Adobe Real-Time CDP into practice, follow these easy steps:
Establish Business goals: Before identifying the primary use cases for Adobe Real-Time CDP, you must establish your business goals.
Determine Data Sources: The next step is to decide which data sources to include in Adobe Real-Time CDP.
Define Data Model: Next, you may specify the properties, events, and interactions of each customer in Adobe Real-Time CDP to build a unified view of them all.
Set Up Data Ingestion: This time, data ingestion is in turn. To import data from several sources into Adobe Real-Time CDP, you may use APIs, batch processing, or real-time streaming.
Configure Data Unification: Data unification is the subject of the next step. To connect client profiles across many data sources, you must set up this procedure.
Set Up Data Activation: Lastly, data activation configuration is possible. Customer data will be activated across many channels as a result.
Adobe CDP Industries in Real-Time
Adobe Real-Time CDP applies to a variety of sectors. The most often-used business features for the platform are listed below:
E-commerce: You may utilize Adobe Real-Time CDP as an e-commerce retailer to give targeted discounts, abandoned cart reminders, and tailored product suggestions. When used with Adobe Commerce, it gains much more potency.
Financial Services: Adobe Real-Time CDP may assist you in providing individualized loan offers, investment advice, and financial planning suggestions if you own a financial services business.
Healthcare: Adobe Real-Time CDP may help by sending out customized appointment reminders and instructions for follow-up treatment.
Travel: Businesses in the travel sector may give individualized trip suggestions, loyalty programs, and real-time flight information by using Adobe Real-Time CDP.
Retail: Use Adobe Real-Time CDP to tailor in-store experiences, product suggestions, and promotions if you are a retailer.
Marketing: By providing real-time insights on customer behaviour, Adobe Real-Time CDP may assist marketing teams. They may thus improve ads with more individualized experiences thanks to it.
Customer service: By providing individualized help and suggestions with Adobe Real-Time CDP, customer service teams may increase customer happiness and retention.
Keep in mind that these are just a few sectors in which Adobe Real-Time CDP may be used.
Use Cases for Adobe Real-Time CDP
Let’s now examine a couple of the previously listed Adobe Real-Time CDP use cases:
Personalized Product Suggestions: Let’s say that you are employed in the retail apparel industry. With Adobe Real-Time CDP, you can gather client information and provide tailored product suggestions according to their browsing habits, prior purchases, and preferences.
Abandoned Cart Reminders: Use Adobe Real-Time CDP to deliver customized abandoned cart reminders if your company has an e-commerce website.
In the meantime, you may use Adobe Real-Time CDP to send loyalty incentives to clients who regularly make purchases from your company. It applies to several sectors.
Real-Time Marketing Campaigns: As a marketer, you may make real-time adjustments to your campaigns by using Adobe Real-Time CDP. Personalized offers and communications may be sent to customers based on their ever-changing interests and behaviour.
Personalized Health Care Reminders: If you work in the medical field, you can use Adobe Real-Time CDP to send patients customized reminders that are tailored to their preferences and medical history. You may even use this information to provide individualized health advice.
Examples of Adobe Real-Time CDP
Real-Time CDP seamlessly integrates with other Adobe Experience Cloud products, such as Customer Journey Analytics, as we’ve previously shown. Let’s examine re-engaging customers via the use of both technologies.
Without a complete understanding of the client experience, it is difficult to predict when a client will go. The issue is that it’s unclear what steps your prospects take to leave the party. To get more clarity, you may utilize Adobe’s Customer Journey Analytics. Applying filters to flow and fallout graphs on the platform enables you to delve further into various customer-associated paths.
Then, by contrasting the actions of a disengaged audience with those of a committed audience, you may ascertain the experiences that were overlooked. Send an audience to Real-Time CDP to activate in the relevant channels where they encounter win-back experiences once they have been identified as a high-potential re-engagement candidate.
The length of a customer’s trip may vary depending on the kind of transaction they are seeking. Longer purchase cycles may make it challenging to understand where customers get stuck and all of the cross-channel touchpoints that play a role in the decision-making process. Nonetheless, integrating your offline and internet data offers a comprehensive viewpoint.
This implies that you may begin dissecting trips to identify the trouble spots that want improvement. You may find these spots and reorganize customer journeys with tested experiences utilizing AI, machine learning, a simple drag-and-drop interface, and rich visualizations with Real-Time CDP and Customer Journey Analytics.
These tools provide you with many methods to analyze conversion rates. As a result, you may discover more about your strong and weak places, which would improve the experience at every touchpoint.
Assume you manage a plant-selling e-commerce website. You want to increase profitability and customer engagement by giving your customers individualized experiences.
To start, you may gather customer activity data from your online business by integrating Adobe Real-Time CDP. This data includes browsing and purchase histories as well as preferences. Following the unification and processing of this data, Adobe Real-Time CDP creates a comprehensive customer profile for every single purchase.
Afterwards, you might use this information to deliver customers personalized product recommendations based on their browsing and past purchases. For instance, if a customer has already bought a succulent, you may recommend other plants that go well with it, such as cactus or another succulent.
Additionally, customers who add items to their shopping cart but abandon them may get abandoned cart alerts from Adobe Real-Time CDP. You may encourage customers to finish their purchases and increase your conversion rate by giving them a personalized message that includes the specific items they still have in their cart.
Furthermore, you may create loyalty programs for customers who make frequent purchases from your business, which could provide exclusive access to new products or discounts. You may use Adobe Real-Time CDP to help you find these customers and provide customized offers that will entice them to make more purchases from your business.
To be more precise, let’s examine The Home Depot as an example. To provide a consistent online and in-store customer experience, the business used Real-Time CDP and Customer Journey Analytics. Their goal was to rethink the whole customer experience, so they put in place a customer-based approach that was journey-focused.
By combining information from many sources, such as internet use, in-store sales, contact centre data, etc., the business was able to construct cohesive client profiles. With this data, it was possible to segregate high-value clients into hundreds of distinct groups according to certain travel routes.
Additionally, understanding how consumers interacted before making a purchase was aided by the integration of Customer Journey Analytics and Real-Time CDP. The most significant touchpoints across the whole client journey were found by this observation.
Home Depot was able to propose suitable items and in-store locations by optimizing its marketing and customization efforts. It caused tailored experiences to be delivered up to ten times quicker, a notable rise in personalized marketing (62%), and a notable increase in online purchases that were picked up in-store (55%).
In summary
As you can see, Adobe Real-Time CDP might help you provide your customers with customized experiences. This platform is unquestionably the best option if you’re seeking a way to increase revenue and engagement. It can assist you in creating a comprehensive customer profile that incorporates data from many sources. Afterwards, you may use this information to create customized offers, reminders, and recommendations that entice customers to return.
The platform’s suitability for a range of industries, such as e-commerce, healthcare, banking, etc., is another fantastic feature. Adobe Real-Time CDP may assist you in obtaining the most comprehensive information, regardless of where your company is located.
As a result, in the current digital age, it is an essential tool for companies looking to remain competitive. With the help of its powerful data processing engine, machine learning algorithms, and real-time analytics capabilities, businesses can outperform their rivals and not just survive.
FAQ for Adobe Real-Time CDP
Adobe Real-Time CDP: What is it?
A customer data platform called Adobe Real-Time CDP is made to combine data from several sources into a single, cohesive customer picture. As a user, you can make use of Real-Time CDP to provide individualized experiences by getting to know each customer’s preferences, actions, and past.
What are the main characteristics of Adobe Real-Time CDP?
Activation across multiple channels, scalability, unified customer profiles, and real-time data access are some of the primary benefits of Adobe Real-Time CDP.
In comparison to other CDPs, how does Adobe Real-Time CDP fare?
Adobe Real-Time CDP has several benefits over other CDPs, such as scalability, support for various channels, and real-time data access.
How is Adobe Real-Time CDP implemented?
To put Adobe Real-Time CDP into practice, follow these steps:
Specify company goals.
Establish the data model.
Determine the sources of the data.
Set up data activation, data unification, and data intake.
Is Adobe Real-Time CDP appropriate for small companies to use?
It is, indeed. All sizes of organizations may benefit from using Adobe Real-Time CDP. Because of its exceptional scalability, you may start small and expand to manage massive amounts of data.
What advantages can Adobe Real-Time CDP offer?
Benefits of using Adobe Real-Time CDP include more customer interaction, higher marketing return on investment, company expansion, and more customized experiences.
Does Adobe Real-Time CDP adhere to laws governing data privacy?
There’s no need to fret if you’re worried about problems related to data privacy requirements since Adobe Real-Time CDP complies with laws like the CCPA and GDPR. To guarantee adherence to important criteria, the platform offers functions including access requests, deletion, and management of data consent.
What type of Adobe Real-Time CDP support is available?
For Adobe Real-Time CDP, Adobe provides a range of support options, including as technical assistance, instruction, and consulting services. To help you start, there are also community forums, documentation, and a knowledge base available.
What is the price of Adobe Real-Time CDP?
The quantity of data, the number of data sources, and the degree of support needed all affect how much Adobe Real-Time CDP costs. For information about prices, get in touch with Adobe.
Is it simple to utilize Adobe Real-Time CDP?
Adobe Real-Time CDP is simple to use because of its intuitive UI. Additionally, the platform offers several pre-built connectors and templates to aid in a business’s rapid startup.