Comcast Cable Communications, doing business as Xfinity, has disclosed a data breach affecting more than 35 million people. The firm said that, during a routine cyber security exercise in October, it discovered suspicious activity on its internal systems. It subsequently determined that, between October 16 and October 19, 2023, there was unauthorized access to systems via a Citrix software vulnerability known as Citrix Bleed.
Xfinity determined that information was likely acquired, with the customer data in scope including usernames and hashed passwords, contact information, last four digits of social security numbers, dates of birth and/or secret questions and answers. The data analysis is continuing, the firm said. Xfinity has notified federal law enforcement and initiated an investigation into the nature and scope of the incident.
In a statement shared with Bleeping Computer, a Comcast spokesperson said the company’s operations were not impacted and that it received no ransom demand after the incident.
Xfinity customers advised to reset passwords and use MFA
Xfinity has required customers to reset their passwords to protect affected accounts. The company has strongly recommended that customers enable two-factor or multi-factor authentication (MFA) to secure their Xfinity account and also advised them to change passwords for other accounts for which they use the same username and password or security question.
“This breach is particularly alarming as the type of data that has been declared stolen indicates that passwords and answers to identifying secret questions and answers have been lost,” commented Darren James, senior manager at Specops Software, an Outpost24 company. Many people re-use the same password and security questions across many platforms, so if this data has been exposed, then it’s not just the Xfinity account that is vulnerable. It’s potentially many other services as well, he added.
“Even though the passwords may have been hashed, depending on the hashing algorithm used and the length of the password, it is still relatively easy to brute force these hashes back to clear text very quickly using relatively inexpensive hardware. It does not appear that the secret questions and answers were hashed at all.”
Citrix Bleed vulnerability actively exploited
The Citrix Bleed vulnerability (CVE-2023-4966) affects Netscaler Gateway and Netscaler ADC products. It allows threat actors to exploit and bypass password requirements and MFA to hijack legitimate user sessions and acquire elevated permissions to harvest credentials, move laterally and access data and resources.
Citrix released a patch for the flaw on October 10, 2023, but attackers have been abusing it as a zero-day vulnerability since late August 2023.
“The Citrix Bleed vulnerability is particularly concerning because it allows unauthenticated remote attackers to gain sensitive information from the servers, such as session authentication tokens,” said Thomas Richards, principal security consultant at Synopsys Software Integrity Group. Once an attacker gains access to the session tokens, they can impersonate the authenticated user and perform actions as that user.
In the instance of Comcast, the attackers were able to hijack a session of an employee and gain access to the same systems that employee has access to, he added. “Buffer overflow vulnerabilities such as this are less common nowadays due to better secure design practices, however, when they occur they are always damaging. Organizations can protect themselves from these threats by installing critical patches by vendors as soon as they are released and monitoring critical systems for malicious traffic.”
The Asia-Pacific (APAC) region has long been at the forefront of technological advancement and digital transformation. However, the relentless threat of malware looms larger than ever, necessitating robust strategies and measures for organizations to protect their systems and networks.
Malware – encompassing malicious software such as viruses, ransomware, spyware and other threats – poses a significant threat to the integrity and safety of sensitive data across the APAC region. The consequences of a successful malware attack can be severe, leading to financial losses, reputational damage and compromised customer trust.
Malware attacks – the threat to APAC
The evolving nature of malware and the sophisticated tactics employed by cybercriminals mean it is imperative for APAC organizations to implement comprehensive strategies that encompass preventive, detective and responsive measures.
According to IBM Security’s X-Force Threat Intelligence Index 2023, Asia-Pacific was the most attacked area in 2022 – the second year in a row the region topped the charts – accounting for 31 percent of global incidents (a five percent increase on 2021).
IBM Security found Japan was by far the worst hit country in APAC, accounting for 91 percent of cases. The Philippines suffered five percent of the region’s attacks, with Australia, India and Vietnam each accounting for 1.5 percent.
Backdoor attacks emerged as the most common modus operandi of cybercriminals targeting APAC, occurring in 31 percent of cases across the region. Ransomware ranks were second at 13 percent, while malicious documents (maldocs) claimed the third spot with 10 percent.
Among the observed impacts of malware attacks, extortion topped the list with 28 percent, followed by significant implications for brand reputation at 22 percent, while data theft held the third position at 19 percent.
APAC malware attacks
The malware threat to organizations in the APAC region was underlined in February 2023 when cyber security firm Symantec uncovered a campaign targeting entities in Asia’s medical and shipping industries.
The attackers – named ‘Hydrochasma’ by Symantec – used a range of phishing lure documents tailored to the victim organizations, with email subject lines carefully designed to be relevant to the target.
With the campaign dating back to October 2022, malware used by the Hydrochasma attackers includes commonly used tools such as Meterpreter, Procdump Sysinternals, BrowserGhost and Cobalt Strike.
According to Symantec, the lack of custom malware used in the campaign is notable as “publicly available tools can help make an attack stealthier, while also making attribution more difficult”.
APAC organizations fight back against malware
In the face of such malware threats and attacks, there are some notable examples of APAC organizations taking decisive action.
For example, in autumn 2022, Singapore Telecommunications (Singtel) suffered a double whammy when its Australian unit Optus was hit by two cyber attacks within weeks, compromising data of former and current employees, clients and millions of customers.
In response, Singtel CEO Yuen Kuan Moon immediately set aside A$140m to deal with the problem.
“We want to make sure we focus on this at a group level,” he told CNBC, revealing that the funds would be used to set up an external independent review, provide a credit monitoring service for affected customers and replace identification documents where needed.
“We are working with federal and state government agencies to address concerns, to learn from this and to share the learnings with the business community and public to improve cyber awareness,” the CEO added.
Cyber security recruitment and training in APAC
Other APAC organizations are focusing on training and recruitment to address cyber security. For example, Japan-based tech giant Rakuten is focusing on developing cyber security professionals for the future.
Under the guidance of Yoshinari Fukumoto, CISO Advisor and general manager of the cyber security defense department at Rakuten Group, the company has forged a partnership with the Tokyo Institute of Technology, resulting in an annual cyber security attack and defense intensive program based on practical cyber security knowledge from a real-world security team.
The Rakuten cyber security defense department’s internship program also offers students the opportunity to explore cyber security as a career path. The focus on developing talent is timely, as demand for cyber security professionals in APAC is surging, according to the 2022 (ISC)2 cyber security Workforce Study. The report found that 71 percent of APAC respondents expected their cyber security staff to increase somewhat or significantly within the next 12 months.
Organizations in APAC territories are also readying their existing staff for action against the threat of malware, as well as covering themselves for future breaches. A Statista survey on cyber security conducted among companies in the Asia-Pacific region in 2022 found that 68 percent of respondents favored regular training exercises as their primary measure to combat cyber incidents, while 52 percent of participants opted to purchase cyber insurance as a response measure.
Protection against malware in APAC
Meanwhile, a number of tech giants are taking significant steps to help APAC companies address the need for greater cyber security.
In 2022, IBM opened a new security command center in India to help Asia-Pacific organizations increase their cyber resilience.
In the previous year, Microsoft announced a raft of new products and guidance to enhance security in hybrid work environments across APAC.
Malware protection guidance in APAC
The need for APAC organizations to be vigilant against malware is clear. A recent report by the Cyber Security Agency of Singapore (CSA) noted an increase in phishing scam campaigns and ransomware.
The organisation’s guidance for guarding against such attacks includes:
Ensuring appropriate security controls are implemented.
Implementing network segmentation within the environment and limiting communications between different network zones.
Enhancing monitoring and detection capabilities to identify anomalous activities.
Mapping out dependencies between operations and business flows and developing appropriate contingency plans.
Similarly, the Australian Cyber Security Center offers organizations – including small businesses – comprehensive guidance on malware threats, as well as resources to report incidents and recover from them.
Staying one step ahead of malware in APAC
By understanding the evolving malware threat, staying abreast of emerging technologies, and implementing proactive security measures, APAC organizations can fortify their cyber security and ensure a safer and more resilient digital future for the entire region.
Have you ever found yourself in a situation where you wanted to cancel a subscription before the deadline so that you wouldn’t have to pay for the next month’s service? What often happens is that the directions explaining how to cancel a current subscription can’t be found and there is no way to get in touch with the company. And you end up paying monthly for something you don’t want and/or don’t use.
SiriusXM is accused of “trapping subscribers” who want to cancel their subscriptions
According to Variety, New York Attorney General Letitia James has filed a lawsuit against radio and audio streamer SiriusXM. Check out this phrase that James uses to describe what SiriusXM allegedly did. She accused the company of “trapping consumers” in paid subscriptions by “maintaining deliberately long and burdensome cancellation processes.” If you’ve ever been in this situation, you’ll understand how apt those words are.
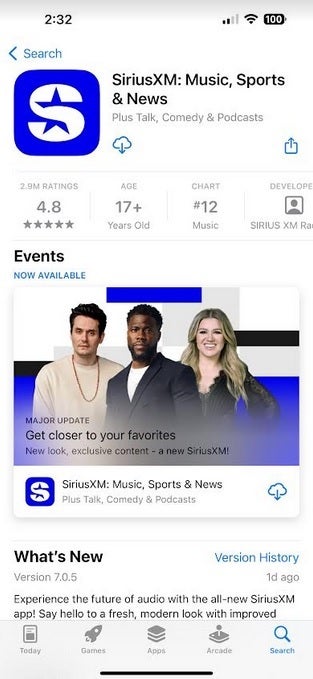
SiriusXM listing in the App Store
Canceling a free trial or a paid subscription shouldn’t require the consumer to get on his knees to plead his case with the company. Yet, James wrote in the complaint that SiriusXM “forces its subscribers to call or chat online with an agent to cancel a subscription, then deliberately draws out those interactions as part of its strategy to prevent subscribers from canceling.”
The court filing states that SiriusXM violated both state and federal laws by not offering subscribers a “simple, timely and easy to use” process to cancel a subscription. Additionally, James’ office said that SiriusXM used fraudulent and deceptive actions to mislead subscribers who wanted to cancel their subscriptions.
The lawsuit says that “When customers decline the offers, agents are trained not to take ‘no’ for an answer and to keep bombarding customers with questions or offers until they either relent or become frustrated.” SiriusXM data cited by the court filing shows that it takes 11.5 minutes for a customer to cancel a subscription over the phone and 30 minutes to cancel online. In one situation mentioned in the complaint, a SiriusXM agent kept a subscriber in a chat for 40 minutes ” even though the subscriber made repeated requests clearly asking to cancel his subscription.
The court documents go into further detail. “Sirius’s strategy for frustrating cancellations includes forcing most subscribers to interact with a live customer service agent, even though Sirius has the ability to process cancellations without the involvement of live agents. Sirius trains its agents to put subscribers through a lengthy, six-part script, and to refuse cancellation until either the agent reaches the end of the script, or the subscriber’s frustration reaches a point that they become openly agitated by the process—or give up altogether.”
“As part of its cancellation process, Sirius requires its live agents to present a series of renewal offers to retain the consumer as a subscriber. But when a consumer declines an offer, or refuses to hear further offers, Sirius instructs its agents not to take ‘no’ for an answer. Instead, agents are instructed to think of every ‘no’ simply as a request for more information!—and to press forward until the consumer accepts an offer or abandons the cancellation effort, hounding them with additional questions and information.”
The lawsuit demands that SiriusXM make “full monetary restitution”
In a statement, James said, “Having to endure a lengthy and frustrating process to cancel a subscription is a stressful burden no one looks forward to, and when companies make it hard to cancel subscriptions, it’s illegal. SiriusXM responded by saying, “Like a number of consumer businesses, we offer a variety of options for customers to sign up for or cancel their SiriusXM subscription and, upon receiving and reviewing the complaint, we intend to vigorously defend against these baseless allegations that grossly mischaracterize SiriusXM’s practices.”
The lawsuit seeks to force SiriusXM “to make full monetary restitution and pay damages to all aggrieved consumers, known and unknown” and to disgorge all profits generated by the fraudulent, illegal, and deceptive actions. The suit seeks to impose a $5,000 fine for each violation of New York State law prohibiting deceptive acts and practices.
SiriusXM has approximately 34 million subscribers with nearly 2 million of them living in the state of New York.
From phishing links to malware attacks, these crypto drainers or cryptocurrency stealers have been exploiting Google Ads and Twitter Advertising features (formerly known as X).
Wallet or cryptocurrency drainers have been a significant threat to users. These malicious programs illegally transfer cryptocurrency from victims’ wallets using various techniques, including campaign launches, deceptive websites, wallet connections, smart contract interaction, asset transfer, and obscuration.
For your information, a crypto drainer or cryptocurrency stealer is a type of malicious program designed to steal cryptocurrency from your wallet. They work by tricking you into approving transactions that allow the attacker to transfer your funds away, often without your knowledge or consent.
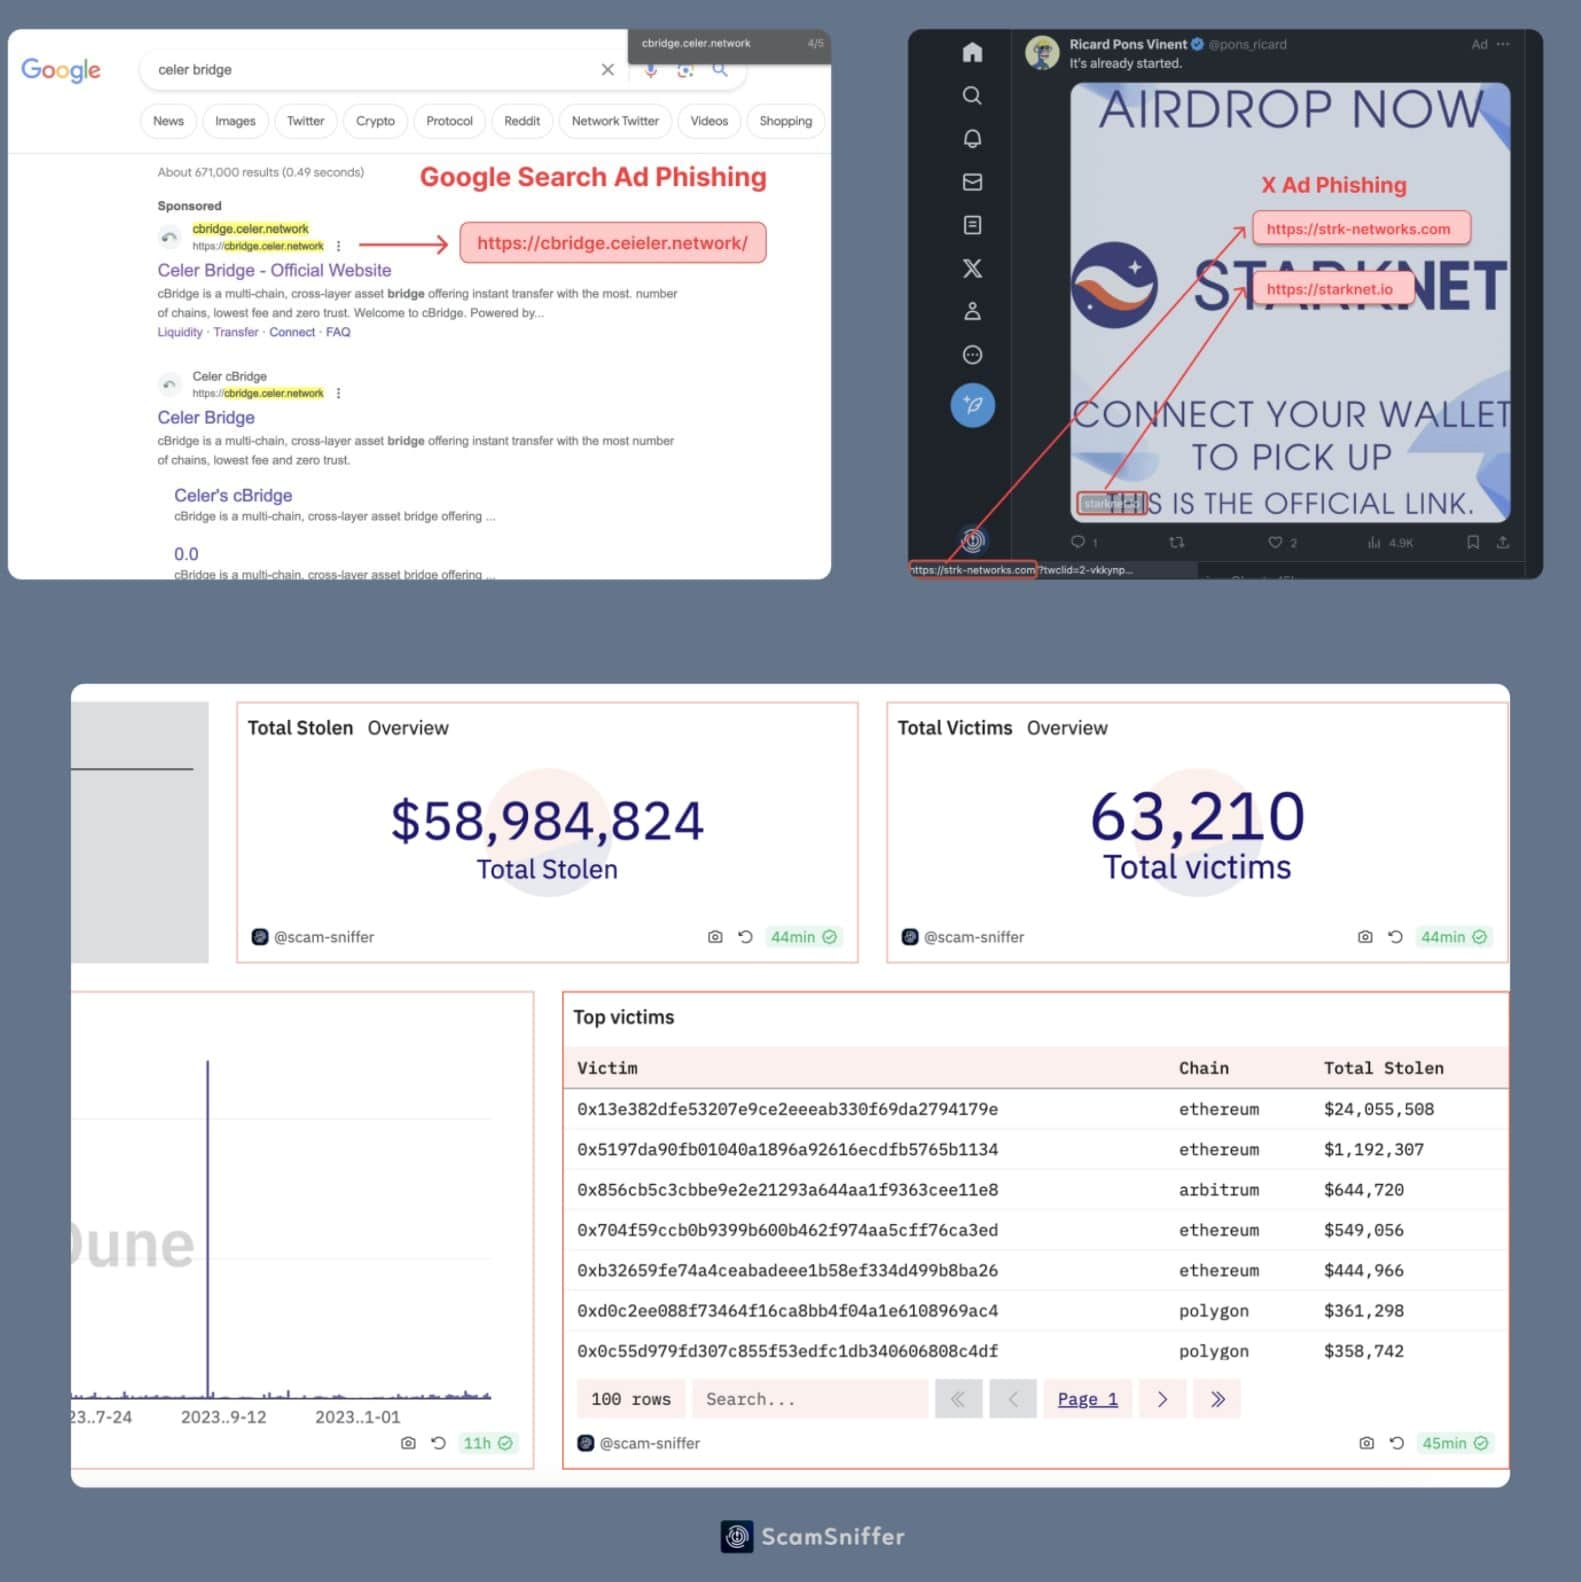
Anti-scam solutions provider Scam Sniffer has discovered a series of crypto drainer malware attacks stealing approximately $59 million from 63,210 victims by embedding a wallet drainer dubbed MS Drainer in Google search and X (formally Twitter) ads. The attack campaign leverages malicious ads on Google and X to redirect users to phishing pages.
Screenshot: Scam Sniffer
Unsuspecting users click on the ads linked to common keywords from the DeFi world. These ads can bypass ad audits and use redirect deception, targeting specific regions. Thousands of phishing sites were found using drainers between March 2023 and today, with spikes in activity in May, June, and November.
These sites were promoted in Google Search by exploiting Google’s tracking template. Ads on X were more prevalent, promoting NFT airdrops and new token launches on sites with drainers that steal funds from users’ wallets.
Researchers monitored 10,072 phishing websites and found that 60% of ads on X directed users to malware designed to steal cryptocurrency. MS Drainer is available on a Dark Web forum, and unlike other malware where developers charge a 20% fee, its source code is sold directly to customers.
On December 22, Check Point Research (CPR) published research highlighting an alarming increase in sophisticated phishing attacks targeting various blockchain networks using crypto wallet-draining techniques, targeting Ethereum, Binance Smart Chain, Polygon, Avalanche, and almost 20 other networks.
CPR linked the attacks to Angel Drainer, a group known for its involvement in cyberattacks in the cryptocurrency space. Despite the shutdown of similar groups like Inferno Drainer, which helped steal over $80 million in cryptocurrency, Angel Drainer continues to operate. Attackers create fake airdrops or phishing campaigns, offering free tokens to lure users. They redirect users to a fraudulent website, requiring wallet connections.
Users are lured into interacting with smart contracts designed to steal tokens. Unknowingly, users grant attackers access to their funds, enabling token theft. Attackers use methods like mixers or multiple transfers to liquidate stolen assets. Permit in ERC-20 tokens allows token holders to approve spenders to transfer tokens without conducting on-chain transactions. However, if a user is tricked, the attacker can transfer funds without logging a trace to the blockchain.
CPR and Scam Sniffer recommend that the advertising industry prevent malicious ads from reaching innocent users and urge consumers and users to exercise caution when opening links in online ads.
“Ad platforms need to enhance their verification processes to prevent malicious actors from exploiting their services,” Scam Sniffer noted.
In the shadowy realm of commercial spyware, the spotlight turns to the notorious Intellexa spyware and its Predator/Alien solution, as dissected by Cisco Talos in their comprehensive May 2023 report.
This expose navigates the labyrinthine intricacies and disconcerting features of Intellexa’s offering, highlighting profound concerns surrounding accountability and ethical boundaries.
Intellexa’s Predator stands as a persistent specter, transcending the conventional escape route of device reboots.
The optional persistence add-on ensures the spyware’s survival, presenting a formidable challenge even after a device restart, contingent on the selected license.
With a chilling awareness of its clientele’s cross-border targets, Intellexa raises unsettling questions about potential misuse for political repression and human rights violations.
The global scope of their operations calls for heightened scrutiny of the geopolitical implications of commercial spyware.
Public scrutiny and reports seem to barely ruffle Intellexa’s feathers.
Adaptable and quick to assimilate new exploit chains, the spyware vendor renders domain exposure a futile attempt at containment, echoing the resilience of this clandestine industry.
Intellexa Spyware Adds Persistence
Talos’ technical deep dive into Predator unveils the labyrinthine architecture of the spyware, illuminating the challenges in detection and mitigation.
The report serves as a crucial resource for understanding the evolving landscape of sophisticated cyber threats.
Using Intellexa as a case study, Cisco Talos underscores the inherent risks embedded in the commercial spyware landscape.
Cautionary notes echo the necessity for stringent regulations to navigate the precarious intersection of technology and ethics.
Evolutionary Trajectory:
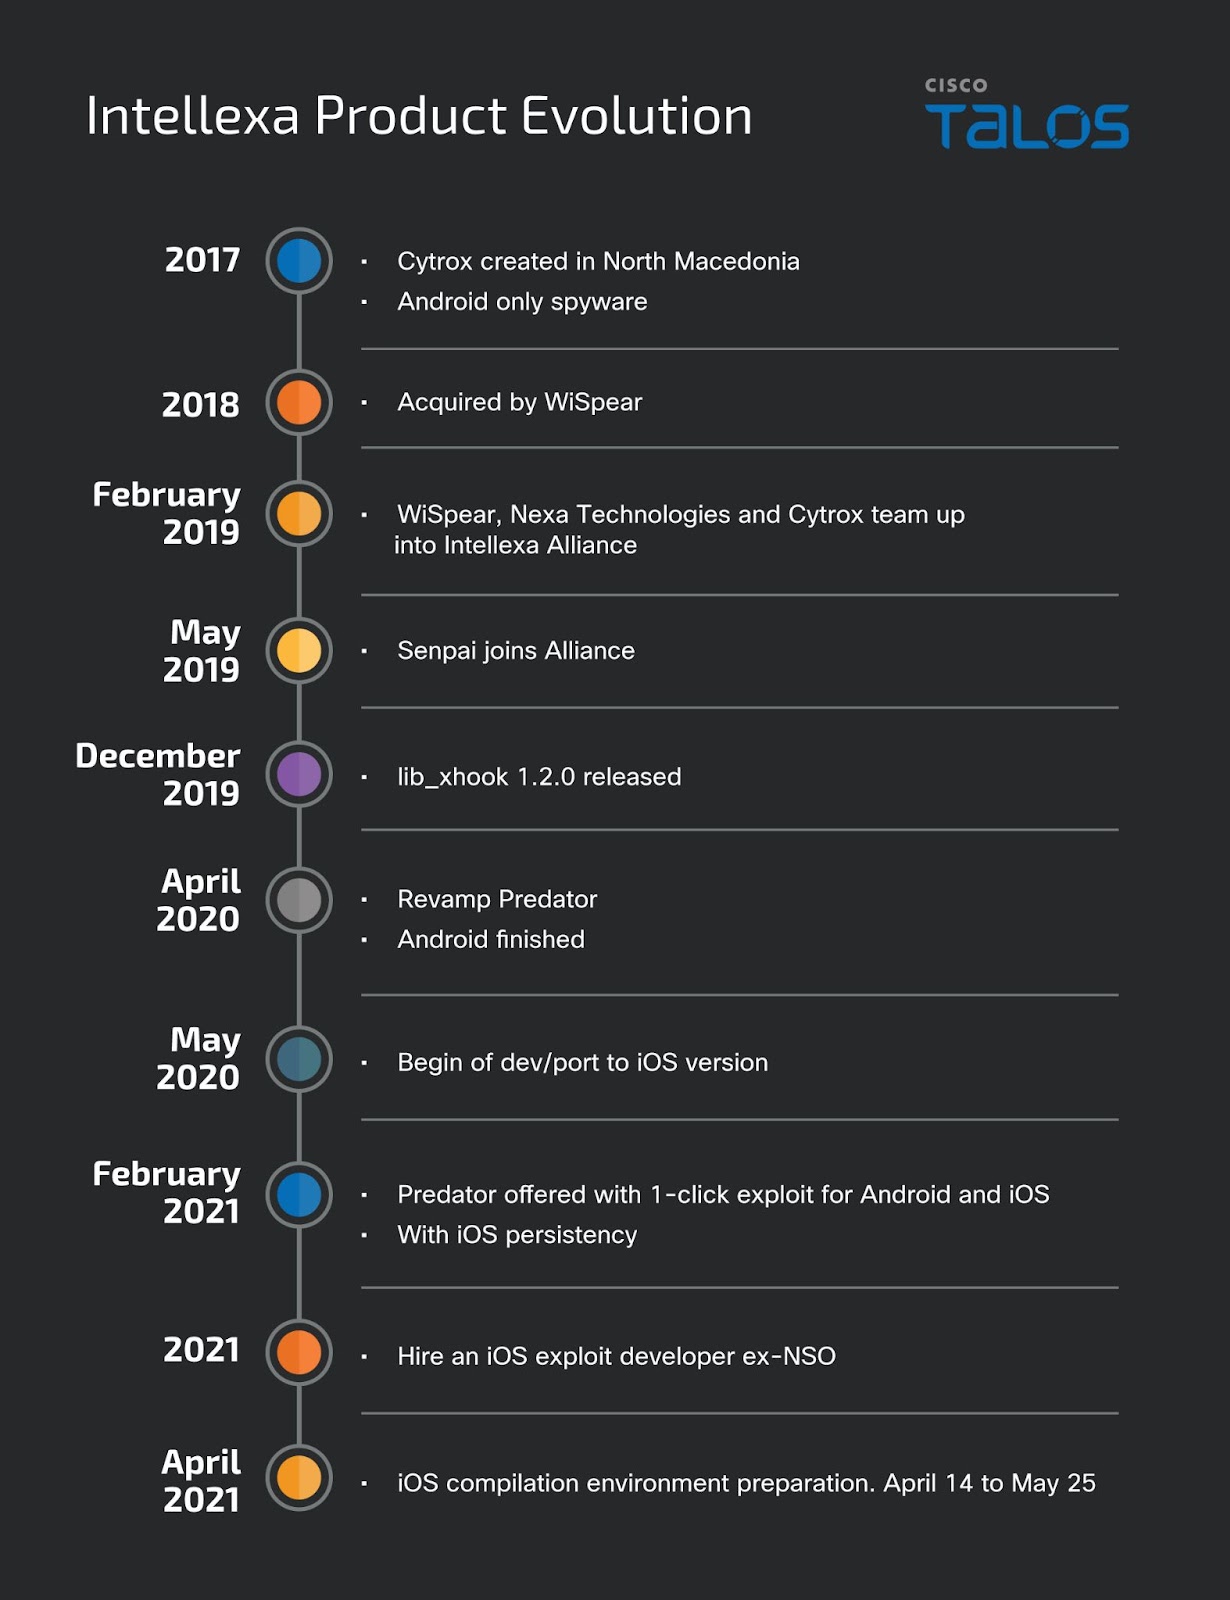
Tracing Intellexa’s journey from a struggling Cytrox to a formidable spyware provider exposes the alarming trend of knowledge and expertise converging in this domain.
The metamorphosis raises pertinent questions about the trajectory of surveillance technologies.
Leaked proposals unravel the substantial financial investments associated with Intellexa’s offerings, highlighting the exclusivity of such spyware and its likely patrons—state-sponsored agencies.
The hefty price tags underscore the commodification of espionage.
Plausible Deniability:
Craftily constructed proposals from Intellexa allocate responsibility for infrastructure and delivery methods to customers, creating a veil of plausible deniability.
This strategic move shields the spyware vendor from potential repercussions.
Recruitment strategies and LinkedIn profiles unveil a concerning talent pool fueling the commercial spyware industry.
The ease with which these companies attract highly skilled engineers raises ethical concerns about the workforce behind the clandestine operations.
Intellexa’s ability to seamlessly adapt to new operating systems underscores the modular design of Predator.
The reliance on Python modules facilitates swift adjustments, solidifying the spyware’s resilience in the face of evolving technological landscapes.
The vulnerability of exploit chains becomes a fleeting concern for Intellexa, swiftly replaced by commercial exploit vendors to minimize disruptions.
This adaptive strategy serves as a testament to the symbiotic relationship between spyware vendors and exploit providers.
Talos advocates for detailed technical analyses and public disclosure of malware samples as a powerful tool against spyware vendors.
This transparency imposes development costs on the industry and empowers researchers to fortify cybersecurity defenses.
Hackers use PowerShell commands because they provide a powerful scripting environment on Windows systems, allowing them to stealthily execute malicious scripts and commands called Operation RusticWeb.
While besides this, the PowerShell’s capabilities make it an attractive tool for gaining:-
Unauthorized access
Performing reconnaissance
Executing various cyber attacks
Cybersecurity researchers at SEQRITE Labs recently identified operation RusticWeb, in which they found threat actors using PowerShell commands to exfiltrate confidential documents.
RusticWeb Using PowerShell
The operation RusticWeb tracks overlapping tactics with Pakistan-linked APT groups like-
While threat actors shift from compiled languages to the following languages for cross-compatibility and evasive tactics:-
Golang malware examples include Windows-based Warp with Telegram bot C2 and Linux-based Ares RAT stager payload. Rust-based payloads in Operation RusticWeb use malicious shortcuts and a fake AWES domain for data exfiltration.
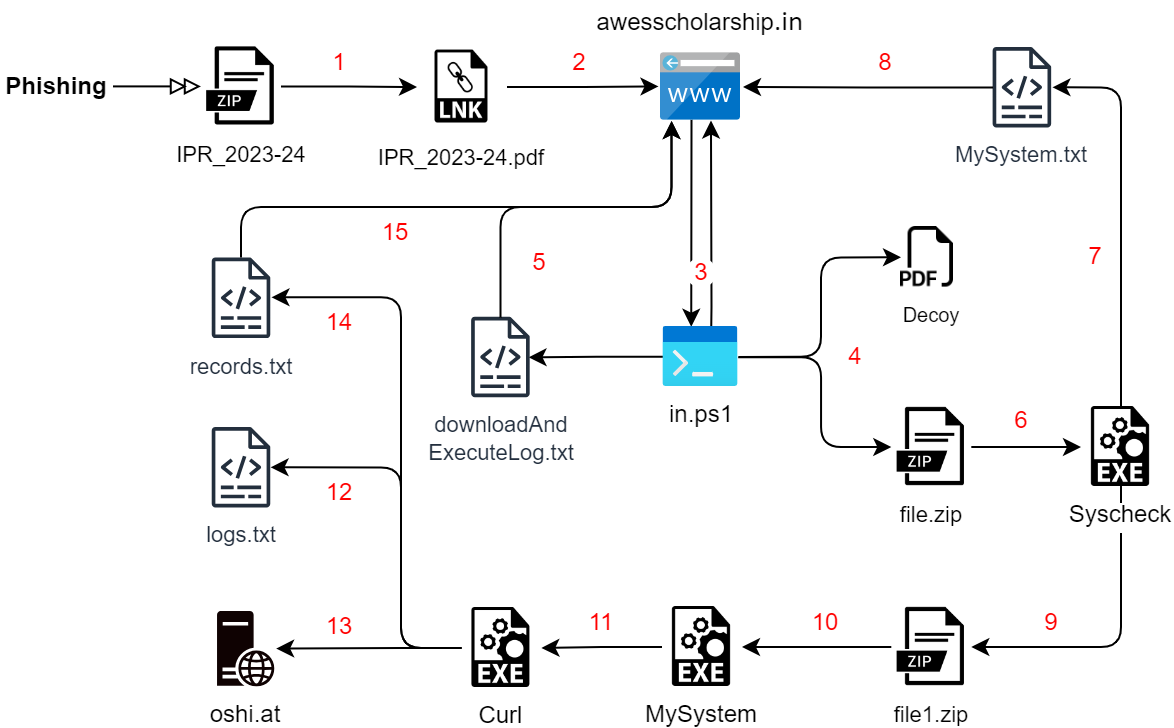
Spear-phishing targets victims with an archive file named ‘IPR_2023-24,’ triggering PowerShell to download scripts from rb[.]gy domain.
Infection Chain 1 (Source – SEQRITE Labs)
The campaign started in September, with 26.53% activity from India. Fake domain ‘awesscholarship[.]in’ mimics AWES, redirecting to the official page.
PowerShell script sets up paths for payload downloads and uploads. Besides this, the decoy PDF file extraction triggers Rust-compiled EXE payload execution.
Another Rust-based malware does the following things:-
Steals files
Collects system info
Uploads via OshiUpload
New December payloads target Kailash Satyarthi Children’s Foundation, indicating a focus on Indian government officials associated with children’s foundations or societies.
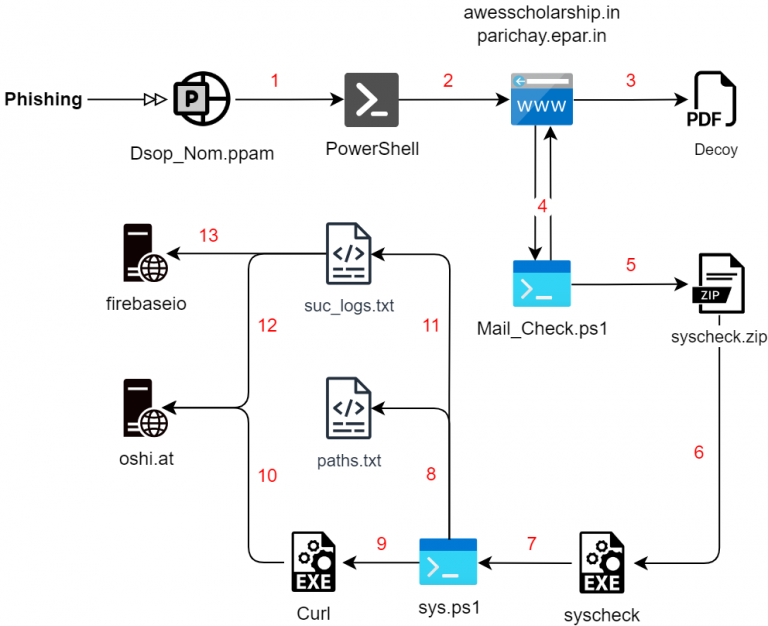
In a December infection chain, maldocs were used with PowerShell scripts for enumeration and exfiltration, omitting Rust-based payloads. Two fake domains and encrypted PowerShell scripts were involved.
Phishing maldoc initiates infection with a VBA macro containing obfuscated encrypted PowerShell commands. Similar maldocs use modified PS commands, converting numbers to ‘PoWeRSHEll’ upon document opening.
PowerShell command decryption employs techniques akin to Emotet, with slight variations. Obfuscation uses Invoke-Obfuscation techniques to mask the IEX command trigger.
Decrypted PowerShell commands download decoy files and next-stage script from domains, executing them in Downloads and Documents directories.
Infection Chain 2 (Source – SEQRITE Labs)
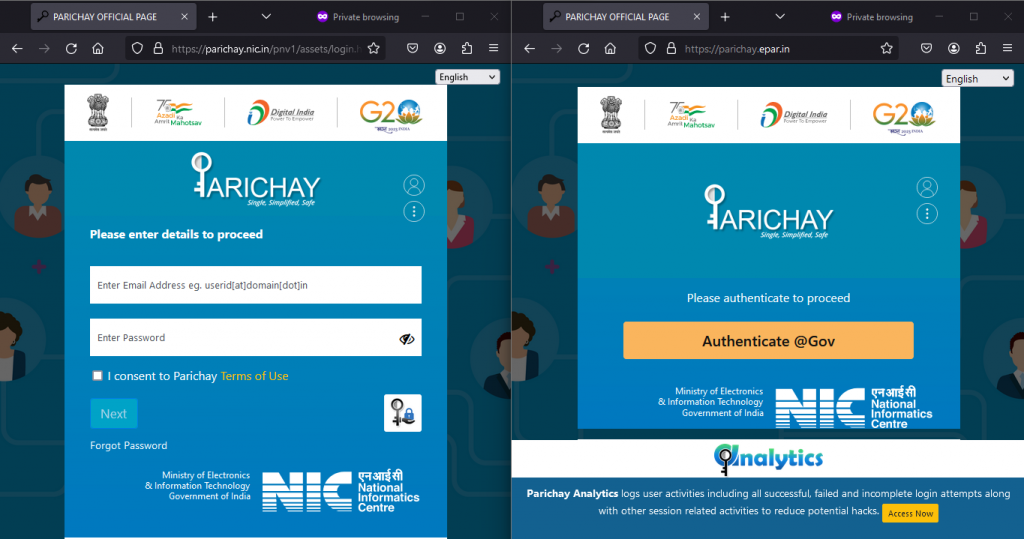
In the first scenario, the downloads occur from ‘parichay.epar[.]in,’ and in the second scenario, the fake domain mimics ‘parichay.nic[.]in,’ an Indian Government SSO platform.
Legitimate and fake Parichay domains (Source -SEQRITE Labs)
The initial decoys pertain to the DSOP Fund form, and the Ministry of Defence presentation was the second. PowerShell script ‘Mail_check.ps1’ drops encrypted ‘syscheck.exe’ to Startup for persistence.
Rust-based payload with PDB name ‘Aplet.pdb’ (Dec 14 timestamp). Here below, we have mentioned all 13 file types that are shortlisted:-
.pp
.pptx
.pdf
.xlsx
.xlsm
.xls
.xlam
.doc
.docx
.docm
.txt
.dot
.ppam
New phishing hits the Indian government, stealing secrets via Rust payloads, encrypted PowerShell, and OshiUpload.
Fake domains mimic government entities in the RusticWeb attack, possibly tied to the APT threat linked to Pakistan. As threat actors adopt Golang, Rust, and Nim, researchers urged users to stay vigilant and take all the necessary security precautions.
In this article, we’ll compare the Google Pixel 8 vs Apple iPhone 15. These two phones are a part of Google and Apple flagship lineups, even though they’re not the most powerful offerings. Their price tags are somewhat similar, however, and chances are that quite a few of you are considering getting one or the other. So, we’ll do our best to help out with that decision. We’ve already compared the Google Pixel 8 and Apple iPhone 15 Pro, so it’s now turn for the vanilla iPhone 15.
As per usual, we’ll first list the specs of both phones, and will then move to a number of other categories. Those categories are design, display, performance, battery, cameras, and audio. There’s plenty to talk about here, as these two smartphones are quite different. Having said that, let’s begin, shall we?
From the design standpoint, these two devices are quite different. The Google Pixel 8 is quite curvy. Its backplate is curved towards the sides, while the sides themselves are also quite curved. The iPhone 15 is the opposite of that. Its front and back sides are flat, and so is the phone’s frame, all around. The frame is slightly curved towards the edges, though, for comfort’s sake.
The two devices also look different. The Pixel 8 has a flat display and a centered display camera hole, along with very thin bezels. Those bezels are not uniform, but almost. All of its physical buttons sit on the right-hand side. The iPhone 15, on the other hand, has a flat display too, with a pill-shaped cutout at the top. Its bezels are also quite thin, and they’re also uniform. The physical buttons are split between the left and right sides of the phone.
If we flip them over, you can see even more differences. The Pixel 8 includes a camera visor on the back, which connects to the frame on the left and right sides. It is covered by metal, and does protrude on the back. The iPhone 15, on the flip side, has a regular camera island in the top-left corner. The two devices are similar in size, but the Pixel 8 is slightly taller, slightly narrower, and a bit thicker. It is also 16 grams heavier than the iPhone 15, at 187 grams. Both smartphones are IP68 certified for water and dust resistance, and both are quite comfortable to use, albeit quite slippery.
Google Pixel 8 vs Apple iPhone 15: Display
The Google Pixel 8 features a 6.2-inch fullHD+ (2400 x 1080) OLED display. That panel is flat, and it supports a 120Hz refresh rate. The display also offers support for HDR10+ content. It gets up to 2,000 nits of brightness at its peak. The screen-to-body ratio here is 85.5 percent, and the display aspect ratio is 20:9. This panel is protected by the Gorilla Glass Victus from Corning.
On the iPhone 15, you’ll find a 6.1-inch 2556 x 1179 Super Retina XDR OLED display. That panel is also flat, and it supports HDR10 content. Dolby Vision is also supported, and the panel goes up to 2,000 nits of brightness at its peak. This is only a 60Hz panel, unfortunately, you’re not getting a high refresh rate here. The screen-to-body ratio is 86.4 percent, and the display aspect ratio is 19.5:9. The iPhone 15 panel is protected by the Ceramic Shield Glass.
The Google Pixel 8 does have one major advantage here, its refresh rate. You will notice the difference between them. Some people simply don’t care, though, so if a high refresh rate doesn’t matter to you, both displays are great. They are very vivid, have great viewing angles, and the blacks are deep. The touch response is also very good, and both displays have good protection too. They’re both also plenty bright, no complaints there.
Google Pixel 8 vs Apple iPhone 15: Performance
Google’s handset is equipped with the Google Tensor G3 processor. It also includes 8GB of LPDDR5X RAM, and UFS 3.1 flash storage. The Apple iPhone 15, on the other hand, comes with the Apple A16 Bionic processor, 6GB of RAM, and NVMe flash storage. The iPhone 15 does have a more powerful SoC, despite the fact it’s not the latest one, though the Tensor G3 is great for AI, and it’s well-optimized for the Pixel.
The point is, both of these smartphones offer great performance. When it comes to regular actions, such as browsing, taking pictures, consuming multimedia, and various other everyday tasks… they’re both very smooth. Even multitasking goes without a hitch, no complaints there. The gaming department is where you may notice a difference, however, especially if you’re into high-end titles.
Let’s take Genshin Impact for example, as that’s always a good benchmark. It runs better on the iPhone 15, even though the Pixel 8 is not far behind. The Tensor G3 is not made for gaming, but it proved it can handle games without a problem. It does get warmer than the iPhone 15 while gaming, though.
Google Pixel 8 vs Apple iPhone 15: Battery
The Google Pixel 8 packs in a 4,575mAh battery. The iPhone 15 has a 3,349mAh battery. Apple’s iPhones usually have smaller battery packs due to the nature of iOS, but that doesn’t necessarily mean that they have inferior battery life. Is that the case here? Well, from what we’ve seen, the two phones are on par in terms of battery life. Neither is outstanding, but both are good.
Getting around 6.5-7 hours of screen-on-time should be possible on both. Do note that we’re talking about battery life without the gaming component. Your mileage may vary, though, of course, as you’ll be using your phone differently, with different apps installed, and with different signal strengths. The point is, both smartphones do offer good battery life, it’s just not outstanding or anything of the sort. For most people, however, this will be plenty.
Neither phone offers particularly fast charging, unfortunately. The Pixel 8 supports 27W wired, 18W wireless, and 5W reverse wireless charging. The iPhone 15, on the flip side, supports 20W wired, 15W wireless MagSafe and Qi2 charging, and 7.5W wireless Qi charging. Reverse wired charging is also on offer at 4.5W. Neither of these two smartphones comes with a charger in the box, though, so keep that in mind.
Google Pixel 8 vs Apple iPhone 15: Cameras
On the Pixel 8, you’ll find a 50-megapixel main camera, along with a 12-megapixel ultrawide unit (126-degree FoV). The Apple iPhone 15, however, has a 48-megapixel main camera, and a 12-megapixel ultrawide unit (120-degree FoV). The good news is, both smartphones do a great job in the camera department. The pictures coming from these two phones are considerably different, though.
The images from the Pixel 8 look contrasty and processed, which is a look many people truly appreciate. The iPhone 15 is trying to keep things closer to real life, but also enhance pictures a bit, so that they pop. Both smartphones do succeed, as the images end up looking sharp, detailed, and vivid. Both handle HDR situations really well, but that’s where the Pixel 8 truly shines.
In low light, the Pixel 8 has a tendency to brighten up shots more, which is not a bad thing. Low-light shots from the iPhone 15 do look more realistic, and they’re darker. Both devices manage to retain quite a few details in low light. Their ultrawide camera do keep a good balance too, and can be used in low light as well. They also manage to keep the color science of the main camera, which is great.
Video recording is still something that the iPhone excels at, and that’s the case here too. The Pixel 8 is only a step behind, however, as the videos do end up looking great.
Audio
You will find stereo speakers on both the Google Pixel 8 and Apple iPhone 15. Speakers on both of them are good. They’re loud enough, and well-balanced. We’ve heard better speakers, though, many of them. Still, not many people will find things to complain about.
What you’re not getting on either phone is a 3.5mm headphone jack. You can always use their Type-C ports for wired audio connections, but there’s no dedicated audio jack. Both smartphones do ship with Bluetooth 5.3 support, however, so you can connect your headphones wirelessly.
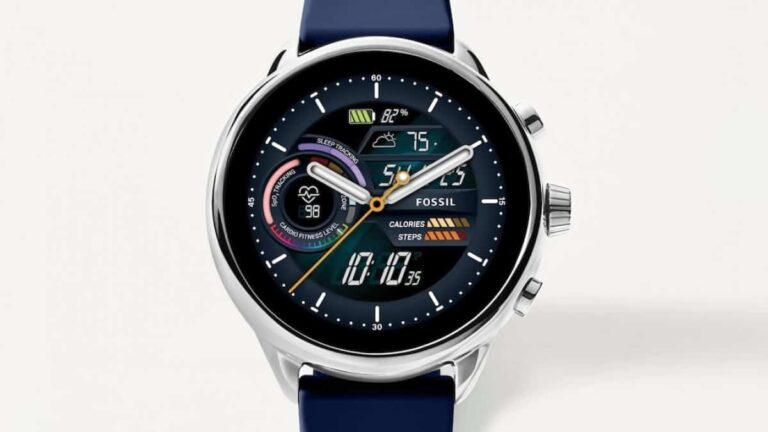
Fossil might have given up on Google’s Wear OS-powered smartwatches. Multiple Reddit users have claimed that Fossil won’t be releasing another Wear OS-based watch in the future. The Reddit posts seem to be in line with the rumors around the future of Fossil’s Wear OS-powered smartwatches.
Fossil Gen 7 Wear OS watch allegedly won’t see the light of the day
Several Reddit users have allegedly spoken to retail employees. They have purportedly shed some light regarding the future of Fossil’s Wear OS-based products. The employees claim that the Fossil Gen 7 Wear OS watch will not see the light of the day. The reports could be true because the Gen 7 watch hasn’t been the subject of major headlines.
The company’s usual late-summer product launch timeframe has also come and gone without any new devices. Also, CES 2024 is just around the corner when Fossil usually introduces its latest wearables. However, there aren’t many leaks or any signs regarding the Fossil Gen 7 Wear OS smartwatch.
Notably, more than two years have passed since the launch of Fossil Gen 6, the brand’s latest Wear OS watch. The most recent development for the lineup was the rollout of Wear OS 3.5 update in November this year.
Furthermore, one Reddit user claims a “friend who works at Fossil” suggests that the brand is waiting for new chipsets. The company is purportedly waiting for the chipset giant Qualcomm to release a new Wear OS platform. However, there haven’t been any reports of Qualcomm developing a new chipset for Wear OS devices. So, there’s not much to back the information posted by the Reddit user.
Fossil is running a fire sale on the Gen 6 watch, possibly to clear inventory
Fossil is currently running a fire sale of its last Wear OS smartwatch, the Fossil Gen 6 Wellness Edition. It is available to buy on the company’s website for $129, which is 50 percent off the usual retail price. Fossil may be running this sale around Christmas to clear the remaining stocks of the Gen 6 Wellness Edition.
Notably, most of the original Fossil Gen 6 watches have also disappeared from sale on the company’s online store. Only some of the Gen 6 hardware is available to purchase at the moment.
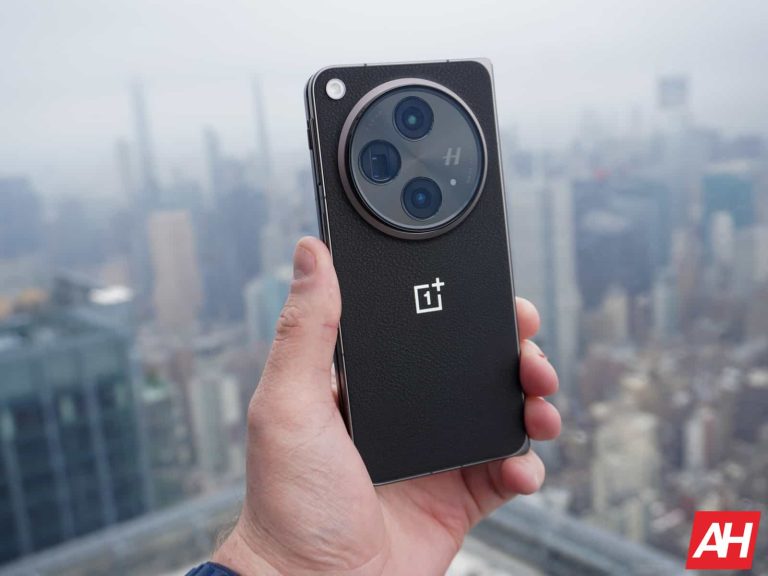
OnePlus entered the foldable market with the OnePlus Open this year. It turned out to be a massive success and also made it to our list of best smartphones of 2023. Well, the OnePlus’ foldable is getting an update, but hold your horses because it’s not Android 14. Nevertheless, it is still a noteworthy update. The latest update is OxygenOS 13.2 and as the name suggests it builds upon the Android 13.
OnePlus Open receives a new update but it’s still Android 13
As spotted by the Telegram channel OnePlus Open: The Chatroom (via Android Authority), the latest Oxygen OS 13.2 weighs about 190.66 MB in size and comes with firmware version CPH2551_13.2.0.203(EX01), including the latest December 2023 security patch. It is comparatively lighter than the last November 2023 security patch which weighed around 508.98 MB.
What’s new with the OxygenOS 13.2 update on the OnePlus Open?
The new update brings several performance upgrades to enhance the overall experience. It tackles both system and camera performance, offering a smooth and stable browsing experience. Specifically, it improves touch controls and reduces the device’s power consumption. Additionally, network stability receives a boost, promising seamless connectivity.
Photography enthusiasts will be happy to know that OxygenOS 13.2 addresses several camera concerns. It finally fixes the shutter lag issue when switching out of Nightscape, tackling those unresponsive UI elements like Retouch and Flash. It also resolves the main screen freezing when using Dual Preview with the rear camera. With these improvements, capturing stunning photos and videos is now smoother than ever on OnePlus Open.
The latest OxygenOS 13.2 update will be rolling out to all devices throughout the week. Ideally, your phone will automatically download. But if you’re eager to jump in, you can check for it yourself by heading to Settings > About device > OxygenOS > Check for update. There’s no official word on OnePlus Open’s Android 14 update yet. However, with other OnePlus models like the mid-range Nord CE 3 Lite already receiving the update, it’s anticipated to be available for the OnePlus Open soon.
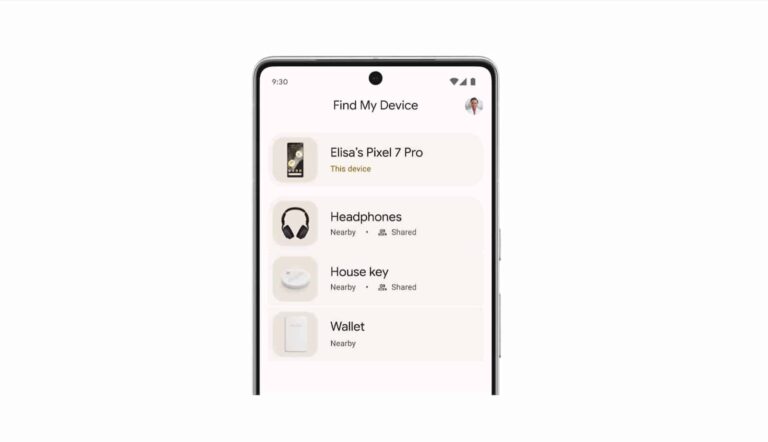
Google and Apple have jointly submitted a proposed industry specification to implement Android’s ‘Find My Device‘ network. It aims to ensure compatibility with unauthorized tracking detection and alerts across Android and iOS platforms. Notably, the implementation of the ‘Find My Device’ network is currently waiting for Apple to adopt the required specifications.
Bluetooth location-tracking devices, often used for finding personal items, have raised concerns about potential unwanted tracking of individuals. The proposed specification outlines best practices and instructions for manufacturers. It provides guidance on incorporating unauthorized tracking detection capabilities into their products.
Dave Burke, Google’s Vice President of Engineering for Android, emphasized Android’s commitment to user protection, stating, “Android has an unwavering commitment to protecting users and will continue to develop strong safeguards and collaborate with the industry to help combat the misuse of Bluetooth tracking devices.”
Google and Apple lead initiative to combat unwanted tracking with Android’s ‘Find My Device’ network
Apple, which introduced AirTag with proactive features to discourage unwanted tracking, sees the industry specification as a critical step forward. The collaboration of both Apple and Google builds upon AirTag protections, representing progress in combating unwanted tracking across iOS and Android, notes Ron Huang, Apple’s Vice President of Sensing and Connectivity.
Importantly, the proposed specification not only incorporates feedback from device manufacturers but also integrates input from safety and advocacy groups. The Internet Engineering Task Force (IETF) has proposed the specification required to implement Android’s ‘Find My Device’ network. Interested parties are invited to review and provide comments over the next three months. Google and Apple plan to address feedback and release a production implementation of the specification for unwanted tracking alerts by the end of 2023, supported in future versions of Android and iOS. This week Google has up
All in all, the collaboration between Google and Apple represents a significant step towards establishing industry-wide standards to enhance user privacy and safety. It’ll particularly address the potential misuse of Bluetooth location-tracking devices for unwanted tracking.