If you want to use 32-bit apps on the OnePlus 12, there’s a way

0
[ad_1]

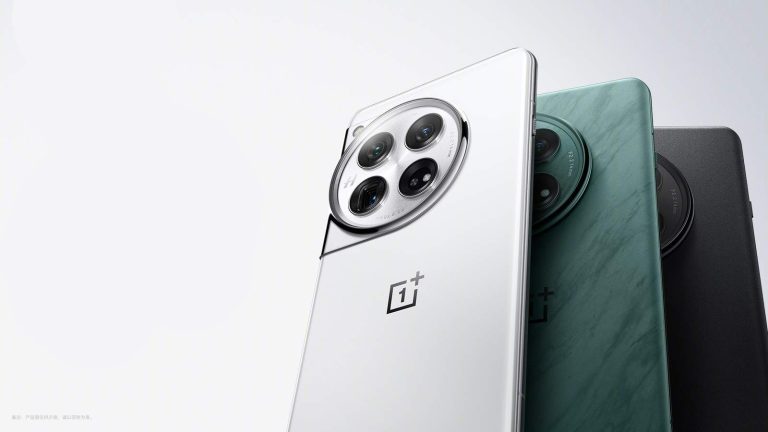
The march of progress is great, but sometimes, it’s a little too fast. A lot of the apps that we used to use back in the day can’t be used now because they are 32-bit apps. The tech world has moved onto 64-bit apps. That’s the case with the OnePlus 12, but there’s a way to still use 32-bit apps on this phone.

Android is in the process of phasing out 32-bit apps. Google has already washed its hands of the technology several years ago, so you can’t download 32-bit apps from the Play Store. However, other app stores were slower to make the switch. This means that it’s pretty hard to play older games like Flappy Bird.

But, you will be able to use 32-bit apps on the OnePlus 12

The OnePlus 12 uses the Snapdragon 8 Gen 3, and that chip only uses 64-bit cores. This means that using 32-bit apps is out of the question. This is unfortunate, as there are timeless apps that are still fun today on newer devices. However, according to a new report, OnePlus has a way to bridge the gap between 32-bit and 64-bit.

This is a method that’s being used by other Chinese companies. That makes sense, as many Chinese app stores still held onto 32-bit apps as recently as a few years ago. You’re also likely to find older apps on other sites across the internet. So, the 32-bit app era isn’t completely over.

The method is called 32-bit to 64-bit Arm Binary translation. It’s through a product called “Tango” from Amanieu Systems, and it’s a way to get 32-bit apps to play on newer hardware. It’s a software answer to a hardware question, and it’s extremely useful. Xiaomi is another company that’s using this method.

Before the OnePlus 12 shipped, it’s possible that this method was going to be much more restricted. Mishaal Rahman stated that the phone could have possibly shipped with a list of select apps compatible with Tango. However, it looks like the list was abolished, so any 32-bit app can run on the OnePlus 12.


[ad_2]
Source link

Global malspam targets hotels, spreading Redline and Vidar stealers

0
[ad_1]

The latest global malspam campaign targets the hotel industry, emphasizing the need to stay alert against such attacks at all times.

Cybersecurity researchers at Sophos X-Ops have issued a warning to the hospitality industry about a sophisticated malspam campaign targeting hotels worldwide. The campaign leverages social engineering tactics to lure hotel representatives into opening password-protected archives containing malware designed to steal sensitive data.

A malspam attack is a cybersecurity threat where malicious actors send emails containing malware to infect your device and steal your data or disrupt your system. Imagine a spam email filled with not just junk, but hidden traps waiting to ensnare you. That’s essentially what a malspam attack is.

According to researchers, attackers are targeting hotels worldwide with email complaints about service problems (e.g. allege violent attacks, bigoted behaviour, and theft of items) or requests for information (e.g. asking for accommodation for someone with allergies, business support, or accessibility for disabled or elderly guests) to create an aura of legitimacy before sending links to malicious payloads.

The malspam campaign was reported just days after FortiGuard Labs researchers identified a similar campaign targeting unsuspecting users with a fake hotel reservation/booking scam. In this campaign, scammers compromised devices using the MrAnon Stealer.

These emails contain links to password-protected archives hosted on public cloud storage platforms like Google Drive. The password, often simple (e.g., “123456”), grants access to the malware, primarily of the Redline Stealer or Vidar Stealer families. It utilizes obfuscation techniques like password protection and jump commands to evade detection. Additionally, large file sizes (larger than executables) often containing zeroes as spacefill are used to prevent analysis.

Sophos researchers identified that the attackers are using the same methodology that they discovered in April 2023. The emails typically span a wide range of subjects that can be broadly categorized into complaints about serious issues faced during a recent stay at the hotel and requests for information for future bookings.

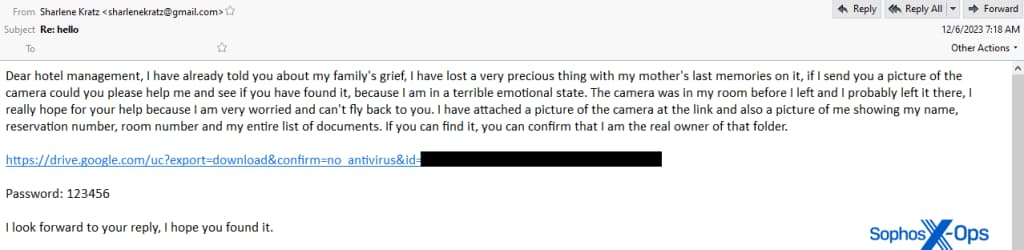
Either way, the attackers send links to malware payloads wrapped in password-protected archive files, posing a threat to hotel representatives. In every case, the threat actor provided documentation as proof of their complaints, which contained malware. These messages are engineered to play on emotions. For instance, in one of the messages, the sender asks for help locating a camera with photos of a deceased relative.

Global malspam targets hotels, spreading Redline and Vidar stealers
One such example (credit: Sophos X-Ops)

In another sample, the threat actor claims to have already booked rooms through the website but needs accommodation for a family member with a disability with a link to a ZIP file containing medical records. The threat actor adds that the link may only be compatible with Windows computers.

Most samples have a code-validation certificate, with some being new or fake. Endpoint protection tools may exclude valid certificates from scanning, or only check for the presence of a certificate. The malware connects to a Telegram encrypted messaging service URL.

The bot then downloads a payload from the URL and uses HTTP POST requests to submit telemetry about the infected machine. The malware does not establish persistence on the host machine, only runs once, extracts and exfiltrates data, and quits. The bot profiles the machine and sends information about it to the bot controller.

Sophos X-Ops has retrieved over 50 unique samples from cloud storage hosted by threat actors conducting the campaign. Most samples displayed few detections in Virustotal. Sophos has published IoCs (indicators of compromise) to their GitHub repository.

Sophos’ principal threat researcher Andrew Brandt shared the following comment with Hackread.com on the malspam campaign, explaining the risks it entails for the hospitality industry.

“An attack like this, that takes advantage of well-meaning hospitality managers, could not only cause problems for the hotel but also the guests staying there. Hotel managers hold (in some cases, literally) the keys to everything that happens on the premises, and their passwords give them access to a lot of non-public information about staff, guests and visitors. 

“The malware used in these attacks isn’t particularly sophisticated. Once the criminals behind these attacks have stolen passwords, they can use these credentials to gain access to additional hotel assets or sell the credentials to other criminals. While this attack is aimed squarely at hotel managers, the compromised privacy of hotel guests – general consumers – is collateral damage.”

“Guests rely on the discretion of hotel staff for a variety of reasons, but an attack like this takes away the hotel staff’s ability to protect customers from cybercriminals who could misuse the stolen credentials. Hotel staff and front-line managers should be on alert for the unique and unusual characteristics of this attack. In addition, they should note that the spammers in this campaign do not have, and (when asked) will refuse to provide reservation details in the body of the message but may attempt to convince hotel employees that such information is embedded in the linked, malicious archive file.

“In situations where the person contacting the hotel refuses to provide basic information in the message itself, such as the name of the registered guest, their dates of stay, or reservation number, be wary. The use of password-protected archive files as a delivery method is another giveaway that something is seriously amiss.

“Hotel IT managers should deploy multi-factor authentication everywhere it is practical and push policies to Windows computers that change the default setting in Windows that conceal the file suffix for known file types. That way security teams can deliver training and messaging about file extensions (.exe or .scr, among others) that are dangerous for staff to open. And finally, all computers used to communicate with guests should have adequate endpoint protection software.”

  1. Booking.com Scam Targeting Guests with Vidar Infostealer
  2. Silent Ransom Group Utilizes Callback Phishing for Network Hacks
  3. USPS Delivery Phishing Scam Exploits SaaS Providers to Steal Data
  4. Iran’s MuddyWater Group Hits Israelis with Fake Memo Spear-Phishing
  5. LinkedIn Phishing Scam Exploits Smart Links to Steal Microsoft Accounts

[ad_2]
Source link

US Galaxy S22 phones receive Samsung’s December 2023 update

0
[ad_1]

Samsung Galaxy S22 users in the US have a new software update coming their way. The company is pushing the December 2023 Android security patch to the 2022 flagship lineup. International versions of the phones have already picked up this month’s security update.

December update released for Galaxy S22 series in the US

It hasn’t been long since Samsung released the Android 14 and One UI 6.0 update for the Galaxy S22, Galaxy S22+, and Galaxy S22 Ultra. The big update brought tons of new features, improvements, and other changes to the phones. It came with the November security patch in tow.

Samsung recently rolled out the December SMR (Security Maintenance Release) for the trio in Europe and other regions. The US versions of the phone are now picking up the latest security patch. It is available for carrier-locked and unlocked units on a few carrier networks. A wider rollout should be just around the corner.

The latest update for the Galaxy S22 series in the US comes with the firmware build numbers S90*USQS3DWKA (carrier-locked) and S90*U1UES3DWL1 (unlocked). As reported by SamMobile, the update doesn’t bring anything more than this month’s security fixes. After all, the devices recently picked up a major feature update in the form of Android 14-based One UI 6.0.

As far as the December SMR is concerned, Samsung is pushing fixes for more than 60 security issues. Like before, this is a combined total of Android OS patches from Google and Galaxy patches from the Korean firm. Google fixed seven critical and over 40 high-severity vulnerabilities this month. Galaxy patches include flaws in Knox, AR Emoji, Smart Manager, and other system components.

Along with the Galaxy S22 series, Samsung has released the latest SMR for several other Galaxy phones. You will get a notification when a new update reaches your device. You can also check for updates from the Settings app. Note that updates aren’t released for all eligible devices simultaneously, so you might have to wait a few days.

Samsung will update its 2022 flagships to One UI 6.1

One UI 6.1 will be the next major feature update for the Galaxy S22 series. Samsung will debut the new One UI version with the Galaxy S24 series early next year. Based on Android 14, it brings several new AI features. The Galaxy S22 trio will also receive Android 15 and Android 16 updates. Security updates will come at least till the first half of 2027, so there is plenty of life left in these phones.


[ad_2]
Source link

Samsung pushes Android 14 to older foldables & Galaxy F54

0
[ad_1]

Yesterday, Samsung released the Android 14-based One UI 6.0 update for the Galaxy Z Fold 4, Galaxy Z Flip 4, Galaxy Z Fold 3, and Galaxy Z Flip 3 in the US. The big Android update for the 2022 and 2021 Galaxy foldables is now available in more markets. We have confirmation that One UI 6.0 for these devices is rolling out at least in Asia. Additionally, the Galaxy F54 has picked up the update.

Samsung updates its older foldables to Android 14

Samsung took longer than expected to release Android 14 for its older foldables. The Galaxy Z Fold 5 and Galaxy Z Flip 5 picked it up almost a month back but the 2022 and 2021 lineups had to wait until this week. The US versions of the Galaxy Z Fold 4, Galaxy Z Flip 4, Galaxy Z Fold 3, and Galaxy Z Flip 3 received it yesterday. The update is available for both carrier-locked and unlocked units stateside.

Now, One UI 6.0 is rolling out to the four foldables in Asian markets, including India and South Korea. In India, the update for the Galaxy Z Fold 4 bears the firmware build number F936BXXU4EWL1. It is F936NKSU2EWL1 in Samsung’s homeland. Those for the Galaxy Z Flip 4 are F721BXXU4EWL1 and F721NKSU2EWL1, respectively. The phones are receiving the December security patch in both regions.

As of this writing, the Galaxy Z Fold 3 and Galaxy Z Flip 3 appear to be receiving this update in Korea only. The new build numbers for the two devices are F926NKSU3HWL1 and F711NKSU3HWL1, respectively. The December SMR (Security Maintenance Release) is part of the package for these foldables too. It shouldn’t be long before Samsung updates the phones to Android 14 and One UI 6.0 globally.

This update brings UI changes, smoother system animations, new features, and functional improvements to your Samsung foldable. Additionally, it introduces the December security release that patches more than 60 vulnerabilities, including at least seven critical ones. Like before, you can check for updates from the Settings app. You may also get a notification when the update is available for your phone.

Galaxy F54 is also receiving this update

Along with its older foldables, Samsung has released Android 14 for the Galaxy F54. The F-series phone is only sold in India and a few neighboring countries such as Nepal. The update comes with firmware version E546BXXU3BWL1 and bundles the November security patch. The Korean firm will soon release One UI 6.0 for the remaining eligible budget and mid-range phones. It has pushed the update to all flagship models.


[ad_2]
Source link

Instagram is testing a way to let you preview your photo grid without using a third party app

0
[ad_1]
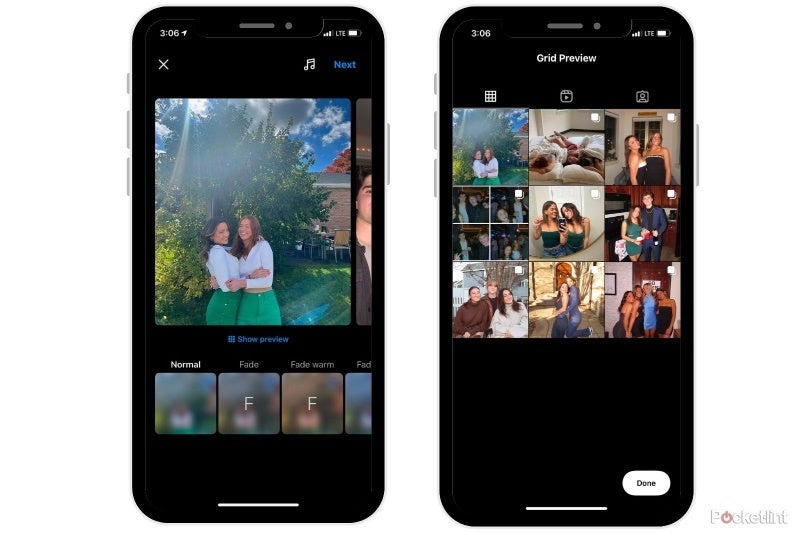
Instagram is testing the ability for users to preview how a post will look prior to publishing, effectively putting behind the days of posting a pic and praying it didn’t clash with your perfectly curated photo grid. This new grid feature is currently only available to a small number of Instagram users using the latest version of the app.
Once achievable only by using third party apps, Instagram enthusiasts who meticulously craft their online persona will now be able to ensure each post seamlessly blends into the bigger picture. The feature has already been spotted by several users, seemingly randomly chosen via an A/B test, and reported on by Pocket-lint.

In this test, users are presented with an option to “Show Preview” when posting, right before tapping on “Next” to make the post official. This intuitive tool grants users the power to visualize their post’s placement within the grid before hitting publish.

This feature is perfect for brands, influencers, and everyday users alike. Businesses can ensure their branded content aligns with their visual identity, influencers can craft cohesive feeds that resonate with their audience, and individual users can finally achieve that coveted “Instagram-worthy” grid without the trial-and-error frustration.
However, not everyone may have immediate access to this powerful tool. Instagram often implements new features in a phased rollout, so patience may be required. In the meantime, alternative solutions like third-party grid planning apps can help users achieve the same results.

An official announcement has yet to be made for this feature’s rollout and there is no official timeline for widespread availability. However, based on past update patterns, we can speculate that a full rollout could take place within the next few app updates while the A/B test progresses. Until then, Instagram users can anticipate the grid preview feature with justified excitement.


[ad_2]
Source link

5 Fraud Prevention Strategies That Help Companies Ward Off Cyber Attacks

0
[ad_1]

Building a successful business is no small feat. You pour your heart and soul into it – serving customers, innovating, and slowly seeing those sales and profits rise. But in the back of your mind, you can’t help but wonder – what if someone tries to take advantage of all my hard work?

The unfortunate reality is that fraudsters are everywhere these days, looking for any weakness to exploit – and both large and small businesses are in the crossfires. In fact, according to PwC’s 2022 survey, over half of companies experienced fraud in the past two years, the highest in 20 years of research.

From cyber-attacks to wire fraud to dishonest employees, there’s no shortage of threats that aim to profit off your hard work. And catching these schemers is tough. It often requires teams of fraud experts and the latest technology just to have a chance. But to survive and thrive, it’s more crucial than ever to put up your guard.

So, in this guide, we’ll explore five key fraud prevention solutions that businesses are using to ward off attacks and reinforce their defences against the relentless creativity of fraudsters lurking in wait.

Anomaly Detection Using AI and Machine Learning

Trying to manually catch fraud is like searching for a needle in a haystack – almost impossible for overworked human teams. Thankfully, we can augment our fraud fighters with artificial intelligence guard dogs that never sleep on the job.

These AI systems tap into huge volumes of payment, login, and activity data to learn what “normal” looks like across customers. Their adaptive algorithms account for new trends and changes over time to avoid getting tricked.

Armed with the baseline, AI sentries constantly patrol networks and account for anything fishy – weird transfers, suspicious logins, and activity spikes. They use advanced pattern spotting and predictive powers humans can only dream of to surface risky anomalies fraud agents should investigate.

So even if scammers dream up some elaborate new scheme, AI fraud patrol stays vigilant, ready to sniff it out and chase the crooks down. The artificial guards alert human counterparts to emerging dangers so we can outsmart the tricksters targeting our data and dollars. With an unfatiguing, adaptable digital watchdog keeping a close watch, fraudsters don’t stand a chance no matter what new tricks they try.

Continuous Authentication Through Biometrics

Where AI provides the behavioural analysis to sniff out fraud, biometrics technology delivers the identification confirmation required to stop it. Fingerprint and facial recognition, retinal scanning, voice verification – these biological analyses are very difficult for perpetrators to circumvent with false identities or impersonation. 

By tying access rights and account privileges directly to individually unique human attributes, biometrics makes stealing credentials or performing illicit transactions under pretences extremely arduous. Would-be fraudsters can create fake IPs and phishing sites, but their voices, faces, eyes, and fingertips will never copy genuine users’ biological blueprints. 

Advanced solutions even monitor for suspicious variations in authentication patterns, adding layers of continuous user verification needed to shut down modern fraud ploys in their tracks.

Ethical Hacking: Unleashing the White Hat Hackers

If the business leader truly wants to future-proof their defences, they may need to bring in some extra firepower in the form of ethical hackers. Acting as allies in the fight, these cybersecurity experts test systems and networks for vulnerabilities that fraudsters could exploit, before the criminals get a chance.

Armed with extensive knowledge of common exploits and attack vectors, ethical hackers play offence to reveal security holes and weaknesses. Through controlled penetration testing, social engineering evaluations, and red team exercises, they exploit flaws with permission to show where fraud prevention measures are lacking. These white hat hackers think like the enemy, revealing openings so they can be reinforced.

By incorporating ethical hacking assessments into standard risk management practices, companies stay continually up-to-date on where fraud prevention blindspots (PDF) exist. When new threats arise or cyber defences become outdated, ethical hackers make sure protection strategies don’t lag behind the endless schemes of swindlers. They provide both sword and shield for our heroes in their never-ending quest to banish fraud.

AI-Powered Threat Intelligence

On the frontlines, fraud analysts struggle to detect real dangers amidst floods of data. The key is transforming raw information into threat intelligence – insights that reveal imminent attacks.

Through aggregating external cyber crime sources with internal transaction and network statistics, next-gen systems digest reams of data into intelligence reports. Curated dashboards showcase emerging fraud trends, compromised credentials circulating dark web markets, and technical tactics gaining popularity amongst hackers.

Advanced machine learning models process the aggregated intelligence to uncover anomalies indicative of budding schemes. They spotlight unseen connections that reveal frauds hiding within massive volumes. All while keeping findings tailored to the company’s vertical, technologies, and business flows most vulnerable.

This enriched intelligence allows analysts to operate proactively, armed with the trends and tendencies of fraudsters targeting their sectors. No more sifting blindly through haystacks. Defenders gain targeted insights revealing where to best focus protections against schemes being actively assembled. And key warnings ensure new attack developments don’t catch teams off guard.

Deception Technology

You know that feeling when you just sense someone’s up to no good, but you can’t quite catch them red-handed? Well, that’s why more businesses are fighting fire with fire by planting boobytraps for lurking fraudsters.

The idea is to hide fake customer records, wallet addresses, and other tempting targets around your systems – like undercover bait cars. When scammers take the bait and try accessing the fakes thinking they’ve hit the jackpot, alarms blaze to reveal the unfolding attack attempt.

Now you’ve flushed the predators out into the open and gained a huge edge. Your team can deeply analyze their schemes using rich forensic trails – trails that traditional tools would’ve missed. You further bolster defences based on the uncovered intel before real damage occurs. This can also uncover undiscovered attackers who may already be roaming within corporate walls. 

With enough well-designed decoys mimicking your real assets, you can outfox threats hiding in the shadows that even skilled analysts rarely anticipate. Deception technology transforms fraud prevention from chasing crimes to proactively catching scammers with their hands in the cookie jar. 

Final Word

While fraudsters will probably always come up with new tricks, taking a proactive stance through the smart use of these advanced defences can help businesses stay ahead of the curve. Having AI lookouts constantly on patrol, biometrics verification keeping identities verified, ethically-minded hackers pointing out weak spots before the bad guys find them, and threat reports highlighting what mischief makers are scheming in your neck of the woods – it all adds up to better visibility and protection. 

And sprinkling some digital boobytraps with deception gives you a chance to catch sneaky bandits red-handed before they cause trouble. Seems keeping sharp yet staying one step ahead is key to surviving the never-ending game of cat and mouse against slippery scam artists. None of these solutions are perfect alone, but together they just might let you get the upper hand.

  1. How to Identify and Avoid Online Trading Scams
  2. How To Safeguard Your Data With Cloud MRP System
  3. PDF Security – How To Keep Sensitive Data Secure in a PDF File
  4. Deepfakes Are Being Used to Circumvent Facial Recognition Systems
  5. The Imperative of Automating Fraud Detection in Financial Institutions
[ad_2]
Source link

Google will delay December 2023 Google Play System Update

0
[ad_1]

Google has decided to skip the December 2023 Google Play System update. These updates might not be something you’re familiar with, but they play an important role in keeping your phone running smoothly and fixing bugs, even if your device isn’t getting a major Android update. While these updates typically roll out every month, Google is taking a break this December. Don’t worry, though! The next update is right around the corner, arriving in January 2024.

Google Play System’s next update will fix app crashing issue

Android expert Mishaal Rahman shared some news. He pointed out that Google employees have mentioned that there won’t be a December 2023 Google Play System update. But the January update will bring a fix for a pesky issue that causes certain apps to crash. So, if you’ve already received the November 2023 update, you’re good to go until then!

Why these updates are a big deal?

Remember the early days of Android? Those updates were frequent, but they weren’t always delivered quickly or consistently. In some cases, some devices never received updates at all. To fix this, Google introduced Project Treble. This helped phone makers deliver updates to their devices without having to wait for everyone else.

Then came Project Mainline with Android 10, built on the foundation laid by Treble. Mainline took things a step further by making it easier to update critical parts of the Android system. This means Google could, then, fix bugs and improve performance without relying on phone manufacturers to push out updates.

Project Mainline works through special components called Mainline modules. These modules are delivered to your phone through Google Play Services, not the traditional Play Store app. There are 25 modules in total, and ART is one of them. It stands for Android Runtime and is a crucial tool in Android that helps apps run smoothly. With Android 12, ART received a significant upgrade, making it even easier for Google to send updates and improvements.


[ad_2]
Source link

Navigating eSIM Policies and Regulations

0
[ad_1]

As eSIM technology becomes more widely adopted, we can expect to see even more devices and carriers offering support for this new generation of SIM cards.

eSIM, which stands for embedded SIM, is a new generation of SIM card technology that’s soldered directly onto the motherboard of your device, like a smartphone or smartwatch. Unlike traditional SIM cards, which are removable plastic cards with a gold chip, eSIMs are permanent fixtures within your device.

As the adoption of eSIM technology, such as the Global YO eSIM App, continues to grow, it’s essential to understand the policies and regulations that govern its use. Navigating the legal landscape ensures that businesses and consumers can fully leverage the benefits of eSIM while staying compliant.

The Evolution of eSIM Policies

eSIM technology has evolved rapidly in recent years, and so have the regulations surrounding its deployment and usage. Governments and regulatory bodies are keen on ensuring that eSIM adoption (PDF) aligns with legal and security standards.

Benefits of eSIM technology:

  • Convenience: eSIMs eliminate the need to physically swap SIM cards when switching carriers or plans. You can simply download a new carrier profile onto your device through software updates.
  • Security: eSIMs are more secure than traditional SIM cards as they’re soldered onto the device and cannot be easily removed. This makes them less vulnerable to loss or theft.
  • Flexibility: eSIMs allow you to have multiple carrier profiles stored on your device at the same time. This is useful for travellers who want to use a local SIM card when abroad, or for businesses that want to manage multiple lines on one device.
  • Environmental impact: eSIMs eliminate the need for plastic SIM cards, which reduces e-waste.

Key Aspects of eSIM Regulations

1. SIM Card Registration

Some countries require mandatory registration of eSIMs to track ownership and prevent fraudulent activities. Compliance with these regulations is essential to avoid legal complications.

2. Data Privacy

eSIMs often store sensitive data, including user credentials. Regulations like GDPR in Europe emphasize data protection and privacy, making it crucial for eSIM providers to comply with these standards.

3. Mobile Network Regulations

Regulations governing mobile network operators also impact eSIM usage. Ensuring that eSIM technology complies with these regulations is vital for seamless connectivity.

Staying Compliant with eSIM Regulations

To navigate eSIM policies and regulations effectively, consider the following:

1. Choose a Reputable eSIM Provider

Opt for eSIM providers like Global Yo, which prioritize compliance with regional regulations, ensuring a smooth and lawful user experience.

2. Understand Local Laws

Before deploying eSIM technology in a specific region, thoroughly research and understand the local eSIM regulations to ensure compliance.

3. Data Protection Measures

Implement robust data protection measures to safeguard user information, aligning with privacy regulations.

4. Regular Updates

Stay informed about changes in eSIM policies and regulations, as they can evolve. Keep your eSIM technology up to date to remain compliant.

Conclusion

Navigating eSIM policies and regulations is crucial for the successful adoption and use of this technology. As governments and regulatory bodies continue to address the challenges posed by eSIM, businesses and consumers need to stay informed and compliant.

With a reliable eSIM provider like Global Yo and a commitment to understanding and adhering to local regulations, you can harness the benefits of eSIM technology while ensuring that your usage remains lawful and secure.

For more information and to explore eSIM solutions that align with regulations, visit the Global Yo eSIM App (iOS) and Global Yo eSIM App (Android).

If you have any questions or concerns about eSIM policies and regulations, feel free to reach out. Compliance is key to enjoying the advantages of eSIM while staying on the right side of the law.

  1. How to Obtain a Virtual Phone Number and Why You Need One
  2. The Top Mobile Security Considerations for Business Travelers
  3. Use Internet anonymously through Tor-enabled SIM card Onion3G

[ad_2]
Source link

OnePlus 12R will launch in both Europe & North America

0
[ad_1]

OnePlus has confirmed that the upcoming OnePlus 12R handset will launch in both Europe and North America. The company confirmed as much during the ‘fireside chat’ on YouTube.

Before we continue, do note that the OnePlus R series was exclusive to India thus far. That same series launched in China under the ‘Ace’ brand, though. Those are the only two markets the devices were made available.

The OnePlus 12R will launch in Europe and North America, it’s official

That will be changing, however, on January 23. That is the global launch date for the OnePlus 12 series, as confirmed recently. OnePlus’ President, Kinder Liu, flat-out said: “Yes, in addition to India, this time we will launch the OnePlus 12R in North America, Europe, and other parts of the world as well”.

The OnePlus 12R will be quite powerful in its own right, at least based on the rumored specs. Previous OnePlus R phones were rather powerful as well, so this is not surprising. It will, however, be inferior to the OnePlus 12, of course.

The phone is expected to include a 6.7-inch OLED display with a 120Hz refresh rate. The Snapdragon 8 Gen 2 will likely fuel the device, while a 5,500mAh battery is also rumored. 100W wired charging is also expected, and the charger will be included in the package.

The OnePlus 12R will include three cameras on the back, and Android 14 out of the box

A 50-megapixel main camera will be backed by a 32-megapixel telephoto camera, and an 8-megapixel ultrawide camera. Android 14 will come pre-installed on the phone, along with OxygenOS 14.

The OnePlus 12 will include a more powerful processor, a slightly larger display, a more powerful camera setup, and so on. It will still clearly be the flagship smartphone, but the OnePlus 12R could attract some people.

If OnePlus manages to get the price tag right for the OnePlus 12R, that phone could prove to be quite popular. The price tag will be extremely important.


[ad_2]
Source link

AI-enhanced low-light photography coming to Galaxy S24 Ultra

0
[ad_1]

Samsung‘s Galaxy S24 series may use artificial intelligence (AI) to improve low-light photography, at least the Ultra model. The phone can reportedly identify a dozen different kinds of objects in Night Mode images captured with the 200MP primary camera and optimize them for better quality. It is unclear whether the company will offer the same AI optimization capabilities on the other two Galaxy S24 models.

Galaxy S24 Ultra uses AI to improve low-light images

The Galaxy S23 Ultra is one of the best camera phones you can buy today. It delivers excellent overall camera performance, including low-light photography. Samsung is keeping the 200MP camera unchanged on the 2024 model. Coupled with improved software processing, the new Ultra flagship is already expected to go up a notch over its predecessor with its image quality.

It appears the Korean firm will add AI to the mix. Noted Samsung insider Ice Universe says the Galaxy S24 Ultra will use AI to detect 12 kinds of objects in a scene when capturing photos in low-light environments. It will then optimize the scene to add more details and make the image look better. The phone will likely enhance colors, tone, and dynamic range to improve the overall quality of the photo.

The source didn’t specify what objects the Galaxy S24 Ultra’s camera AI can identify. However, we should be talking about stuff like humans, animals, vehicles, buildings, nature, food, etc. If the phone also reduces the noise in dark areas, it will address one of the few complaints about the current Ultra model’s low-light images. Hopefully, Samsung will lend some of these improvements to the Galaxy S24 and Galaxy S24+ too.

The new Ultra may capture 24MP images by default

Samsung’s 200MP cameras capture 12MP photos by default. They use pixel binning to merge neighboring pixels and capture more light. If the conditions are bright enough, you can manually switch to 50MP or 200MP modes for that extra bit of detail in photos. This has worked perfectly on the Galaxy S23 Ultra but the company will seemingly improve the implementation of pixel binning next year.

The Galaxy S24 Ultra is said to capture photos in a 24MP resolution by default. The information comes from X tipster Ahmed Qwaider. If true, the new Ultra will give you more details in images. Rumors say Samsung will unveil its 2024 flagship lineup on January 17. The launch event, which the company calls Galaxy Unpacked, will take place in San Jose, USA. The phones may arrive in stores at the end of January 2024.


[ad_2]
Source link