Sidewinder Hackers Using Weaponized Docs to Install Malware

0
[ad_1]

Sidewinder APT group’s sophisticated threat landscape reveals a skilled and persistent threat targeting the Nepalese Government entities. 

Their focus extends to South Asian governments, with researchers also identifying a recent complex attack on Bhutan.

Cybersecurity researchers at Cyfirma recently identified that the operators of the Sidewinder hacker group are actively using weaponized documents to deliver backdoors.

Here below we have mentioned all the other names of the Sidewinder APT group:-

  • Rattlesnake
  • Hardcore Nationalist
  • HN2
  • APT Q4
  • RAZOR Tiger
  • APT Q39
  • BabyElephant
  • GroupA21

Sidewinder Hacker Group

Using decoy documents resembling Nepalese Prime Minister’s Office communications, the group employs advanced tactics like email spear-phishing and malicious macros. 

That’s why urgent attention and coordinated action from the stakeholders are crucial.

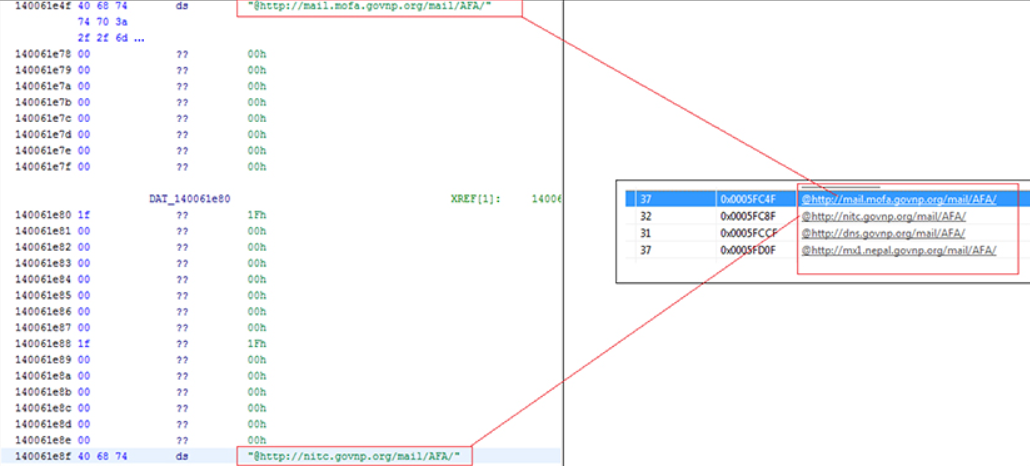
In the main payload “conhost.exe” (Nim Backdoor), all the URLs are hardcoded, and they are settled to the following IP address:-

Here below, we have mentioned all the URLs:-

  • http[:]//mail[.]mofa[.]govnp[.]org/mail/AFA/
  • http[:]//nitc[.]govnp[.]org/mail/AFA/
  • http[:]//dns[.]govnp[.]org/mail/AFA/
  • http[:]//mx1[.]Nepal[.]govnp[.]org/mail/AFA/

Spear-phished email delivers a malicious document, triggering an embedded macro upon opening. The victim is manipulated as the document prompts them to enable editing.
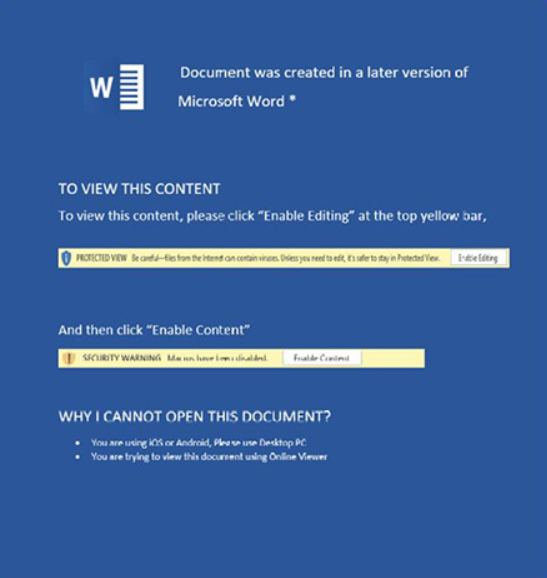
Malicious document
Malicious document (Source – Cyfirma)

The deceptive content hints at targeting Nepalese government officials. The document’s embedded macro, part of a multi-stage attack, establishes persistence and executes payloads. 

The opening of the document triggers the macro and creates a VBScript file for persistence. It introduces delays and checks internet connectivity before executing encoded batch files. 

The batch script directs the execution of VBScript and other batch files, creating scheduled tasks and self-deleting files. Functions like read_shell write binary data to a file, while hide_cons hide the console window. 

The vb_chain function coordinates various actions, including creating and executing scripts and scheduling tasks to establish a chain of events on the infected system.

The VBScript file unzFile.vbs extracts contents from conhost.zip. The following batch file executes scripts, creates tasks, and handles cleanup:-

  • 2L7uuZQboJBhTERK.bat
  • 2BYretPBD4iSQKYS.bat
  • d.bat
  • e.bat 

The macro exhibits advanced evasion with obfuscation by leveraging the following elements:-

  • VBScript
  • Batch files
  • Scheduled tasks

Besides this, its multi-stage execution makes the complete analysis more challenging and complex. 

Enabling macros triggers the deployment of scripts and the Nim backdoor-like conhost.exe. This executable aims to connect to the threat actors’ C2 server for unauthorized access, indicating an ongoing campaign since September.

The reverse shell sample enables threat actor access through a reverse shell, providing control over the compromised system. Trojan.khalesi obstructs dynamic analysis, detecting and exiting if tools are found. 

The binary targets various monitoring and analysis tools. The process tree reveals the periodic use of cmd.exe to execute tasklist.exe, which is likely for information gathering or system monitoring.
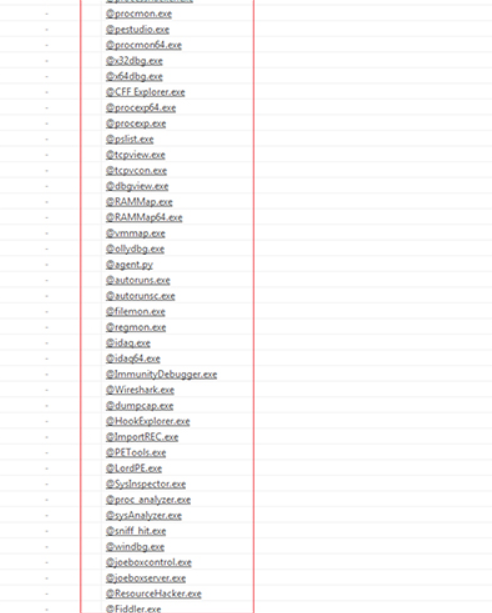
.exe files
.exe files (Source – Cyfirma)

Recommendations

Here below, we have mentioned all the recommendations provided by the security analysts:-

  • Use robust endpoint security.
  • Employ reputable antivirus and anti-malware.
  • Regularly update OS, applications, and security software.
  • Segregate the network into segments.
  • Educate and train employees on phishing and social engineering dangers.
  • Configure firewalls to block outbound communication.
  • Deploy behavior-based monitoring.
  • Establish application whitelisting policies.
  • Monitor network traffic closely.
  • Create a comprehensive incident response plan.
  • Stay updated on threat intelligence and IOCs.
  • Maintain regular backups of critical data.
  • Implement safeguarding measures.
  • Restrict user permissions.

IOCs

IOCs
IOCs (Source – Cyfirma)

[ad_2]
Source link

FBI Seizes Dark Web Domain of Blackcat

0
[ad_1]

Although the main dark web domain of the ALPHV Ransomware has been seized, the blog remains online.

The official website of the notorious ALPHV (aka Blackcat) has been seized by law enforcement authorities, including the FBI, the US DoJ, and several European security agencies under Europol.

The latest development should not come as a surprise, as a few days ago, the ALPHV gang went offline amid rumours that it had been taken down by law enforcement. These claims were categorically denied by the gang; however, today’s seizure confirms the previous rumours.

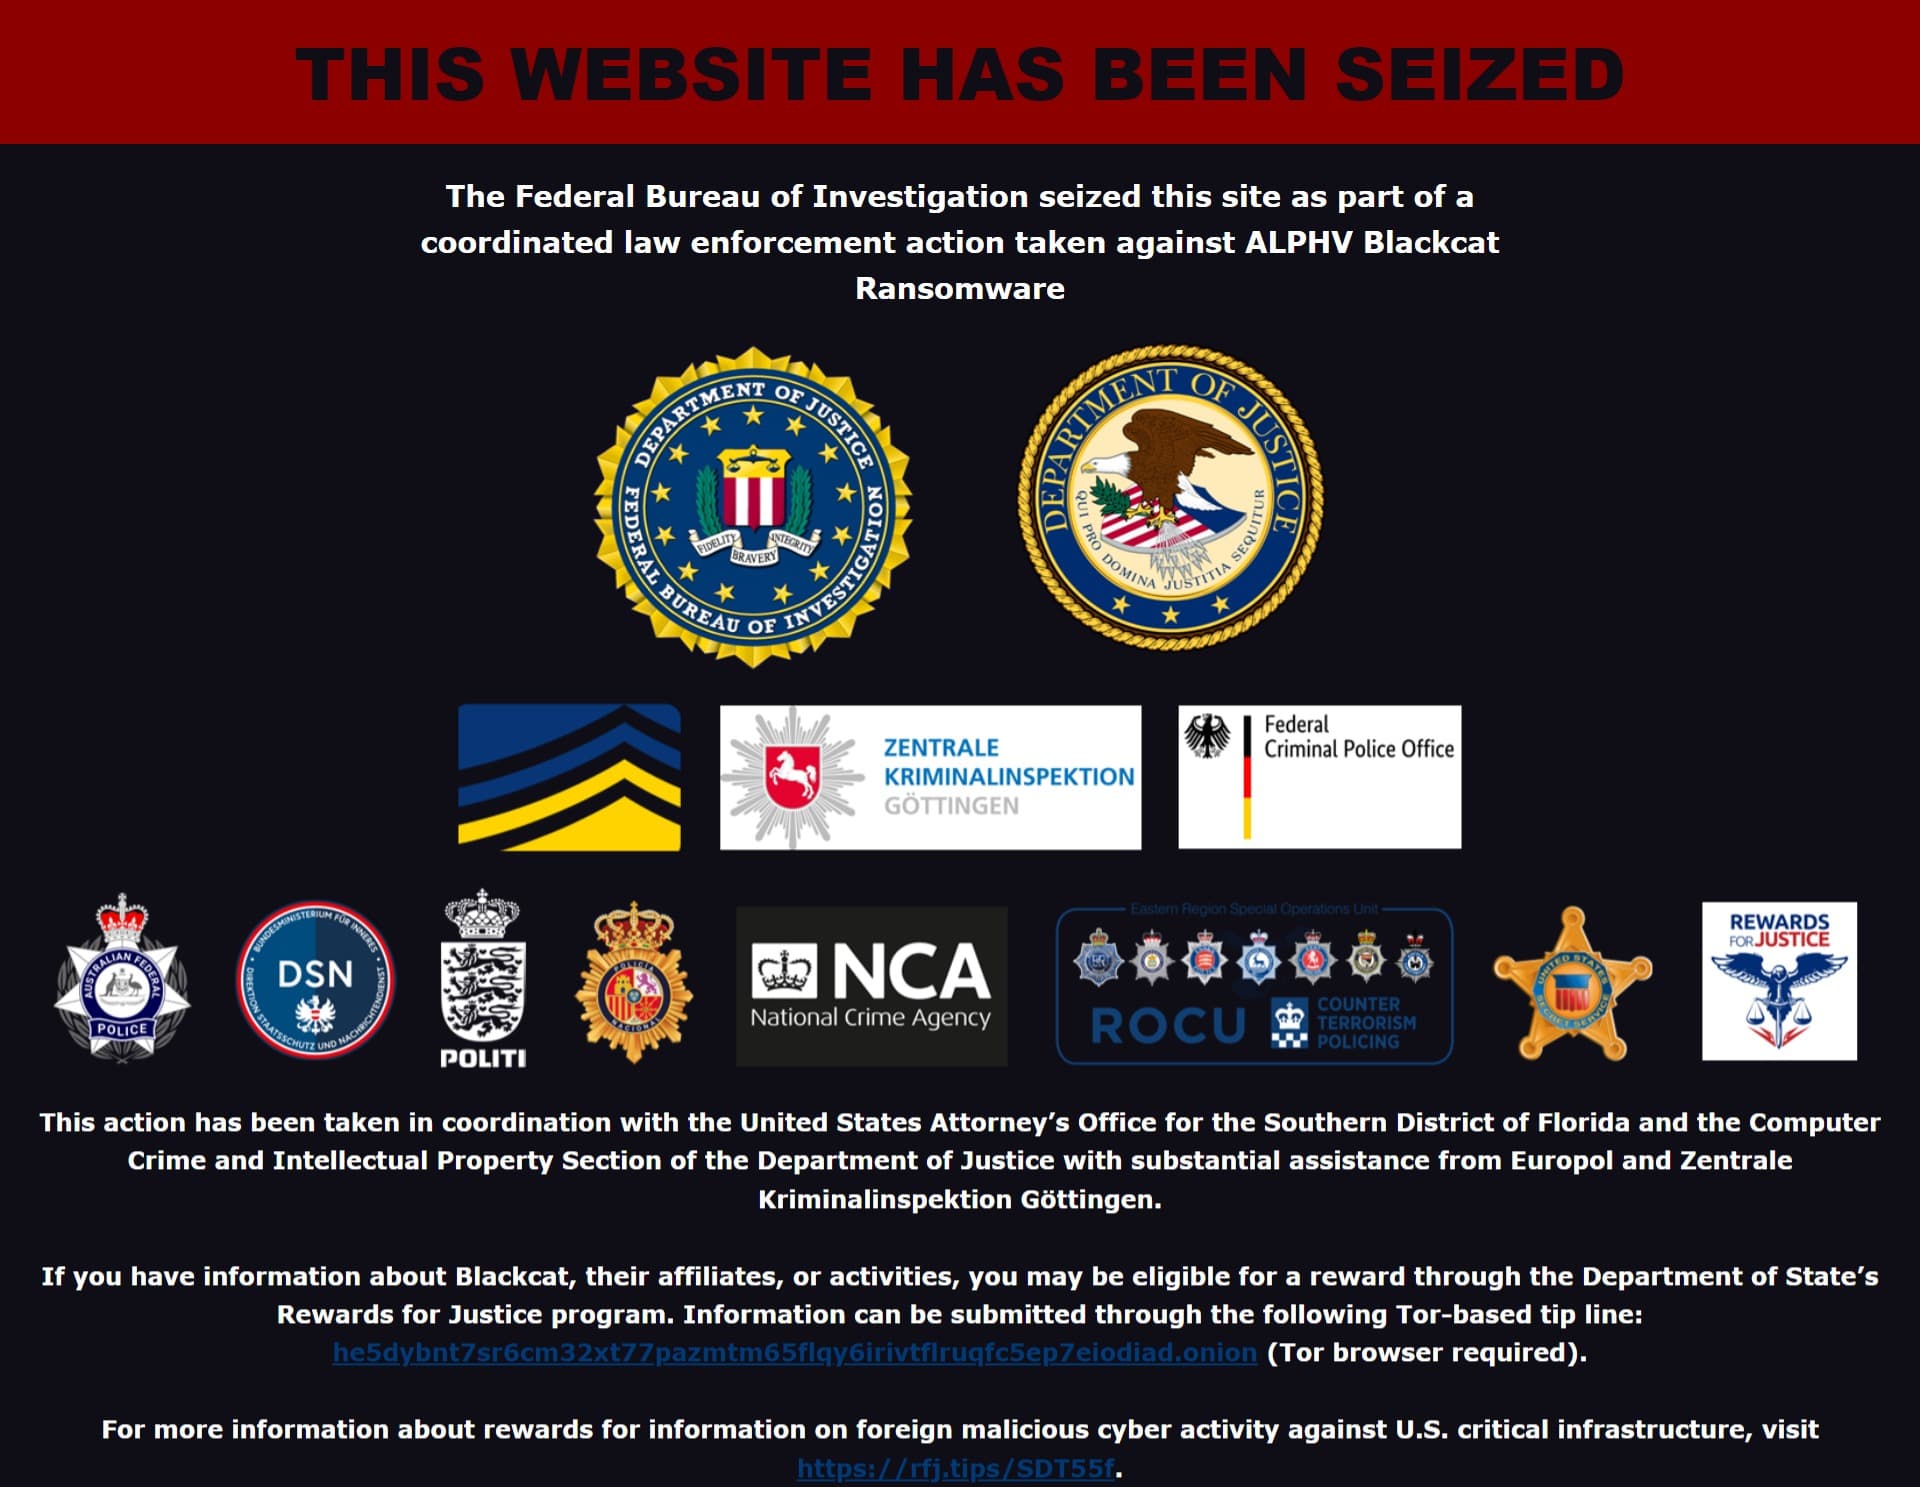
As seen by Hackread.com, the homepage of the ALPHV ransomware website was defaced with a banner announcing the seizure. However, the blog on which the ransomware gang advertised their hacks is still online and no seizure notice is seen at the time of writing.

FBI Seizes Dark Web Domain of Blackcat - ALPHV Ransomware
The banner that the ALPHV Ransomware gang’s domain currently shows (Screenshot credit: Hackread.com)

“This website has been seized – The Federal Bureau of Investigation seized this site as part of a coordinated law enforcement action taken against ALPHV Blackcat Ransomware.

This action has been taken in coordination with the United States Attorney’s Office for the Southern District of Florida and the Computer Crime and Intellectual Property Section of the Department of Justice with substantial assistance from Europol and Zentrale Kriminalinspektion Göttingen.

If you have information about Blackcat, their affiliates, or activities, you may be eligible for a reward through the Department of State’s Rewards for Justice program.”

It’s safe to say that ALPHV ransomware has targeted a wide range of organizations across various industries, including critical infrastructure, finance, education, and manufacturing. However, the exact number of victims and the full extent of the damage remains unknown. The ALPHV gang’s known victims include MGM Resorts, NCR Data Center, Amazon’s Ring, and several others, among which are the following:

  • Seiko
  • Motel One
  • Swissport
  • Western Digital
  • NCAT State University
  • NJVC (US defence contractor)
  • Bet9ja (Nigerian betting platform)
  • SOLAR INDUSTRIES INDIA (industrial explosives manufacturer)
  • Creos Luxembourg S.A. (gas pipeline and electricity network operator).

So What Not?

Although the FBI has not officially announced the seizure, it appears that no arrests were made, and only the domain was taken offline. In a tweet, the online malware repository Vx-Underground claimed that they were contacted by the gang’s team, revealing that they have already moved their server to a new domain.

Random Facts About ALPHV ransomware

  • Emerged in December 2021: This relatively new ransomware group quickly gained notoriety for its sophisticated tactics and aggressive targeting.
  • BlackCat alias: ALPHV is also known as BlackCat, often used interchangeably.
  • Targets: Primarily attacks high-profile organizations across various sectors like finance, healthcare, critical infrastructure, and manufacturing.
  • Tactics: Employs double extortion tactics, stealing victim data before encrypting it, and threatening to leak it if ransom demands are not met.
  • Technical sophistication: Known for using advanced encryption algorithms and evasion techniques to avoid detection.

As of now, attributing ALPHV to a specific group or country with certainty is difficult due to the nature of cybercrime and the group’s efforts to remain anonymous. Nevertheless, this article will be updated with additional information. So keep visiting Hackread.com!

  1. Finnish Dark Web Marketplace PIILOPUOTI Seized
  2. NetWire Malware Site and Server Seized, Admin Arrested
  3. Genesis Market’s Clearnet domain seized; Dark Web site still online
  4. Ragnar Locker Ransomware Gang Dismantled, Key Suspect Arrested
  5. Hive Ransomware Gang Disrupted; Servers and Dark Web Site Seized

[ad_2]
Source link

Google to bring remote uninstallation to the Play Store

0
[ad_1]

Most Android users rely on the Play Store to install their apps and games. The venue currently lets users remotely install apps on all of their connected devices. However, remote uninstallation is a feature that Google hasn’t yet brought to the Play Store. But soon, this might change.

According to Assemble Debug (via AndroidPolice), Google was spotted working on remote app uninstallation in the Play Store v38.3 update. While this version was rolled out in November, the remote uninstallation was first seen in September. Back then, Google said the feature would land on Android devices with Play Store v38.3. After postponing the launch for unknown reasons, the company has now revealed the feature with Play Store version 38.8.

As the official changelog states, users on Google Play Store v38.8 can remotely uninstall apps on connected devices. The feature supports Android Auto, PCs, Smartphones, TVs, and wearables. This update isn’t yet widely available, and Google is busy fine-tuning it. But you can expect to have remote app uninstallation on your device soon.

How remote app uninstallation will work on Play Store

Once the update is available, you can find the app uninstallation feature in the “Manage” tab on the “Manage apps & devices” page. By tapping “✓ This device,” a sheet containing all your connected devices appears at the bottom of the page. After choosing the device, you can access the apps that are already installed on it. Then, you just need to select the apps you want to uninstall and tap the delete icon on the top right. In the final step, a popup appears that wants you to confirm or cancel the process on the selected device.

You can also sort your apps based on name and size on the related page. Additionally, it is worth noting that the Play Store app list might not be complete, and some apps might be missing. This could be due to a glitch in the update, and Google might fix it prior to the official launch.

Remote app uninstallation is a welcome addition to the Play Store and makes it much easier to handle multiple devices through only one device. Before this, users had to go through a complicated process to uninstall an app remotely. With the Play Store’s latest update, it just takes a few taps.


[ad_2]
Source link

Apple Rushes for Software Solution to Prevent U.S Apple Watch Import Ban

0
[ad_1]

On Monday, it was announced that Apple would halt sales of its Watch Series 9 and Watch Ultra 2 products later this week. This is due to an imminent import ban coming from the patent dispute with medical device company Masimo over the blood oxygen sensor on the Apple Watch.

Now according to Bloomberg, engineers are “racing” to adjust how the oxygen saturation is determined and how the data is provided to consumers. This is an update that would presumably remove the technology that is allegedly violating Masimo’s patents. This is in line with what Apple stated, that it is “pursuing a range of legal and technical options” to make sure that the Apple Watch sales are able to resume as soon as possible.

Masimo told the publication that “the hardware needs to change.” This is because the patent is related to the hardware that powers the Apple Watch blood oxygen sensor, and Masimo believes that a software change would not be enough to address the allegations.

Apple is preemptively complying with the sales ban

In October, the ITC ordered a ban on some Apple Watch exports – mainly those that Apple currently sells that have the blood oxygen sensor. The US President could review the court’s order and veto the ban ahead of when Apple would need to stop selling the watch, which would be 60 days after the ban was ordered. Meaning that The White House has until December 25 to make a decision.

However, Apple has decided to comply with the ban preemptively. This is likely because a President very rarely vetoes an ITC sales ban. Apple has announced that they will stop selling the Apple Watch Series 9 and Watch Ultra 2 in the US at retail stores on December 21 at 12 PM PT/3 PM ET. And online sales will stop after December 24.

Keep in mind however, that the ITC sales ban only affects banning Apple from selling these products, and not other retailers like Best Buy, Amazon, and even the carriers. So there will be other places to get a new Apple Watch. Additionally, the Apple Watch SE will remain on sale since it is not affected, as it does not have a blood oxygen sensor.


[ad_2]
Source link

Tech Device Manufacturers Urged by CISA to Remove Passwords

0
[ad_1]

Recently, the Cybersecurity and Infrastructure Security Agency (CISA) has requested technology device manufacturers to take measures to eliminate default passwords due to the threats posed by IRGC actors.

This step has been taken to ensure the security of tech devices and prevent unauthorized access by malicious actors.

The use of default passwords makes it easier for hackers to gain access to devices and exploit them for nefarious purposes.

It’s important to be aware that malicious cyber actors often use default passwords (such as “1234”, “default,” or “password”) to gain initial access and move laterally within businesses. This is especially true for systems that are exposed to the internet.

It’s crucial to implement strong and unique passwords to protect your systems and sensitive data from unauthorized access.

It has been reported that the critical infrastructure of the United States was recently targeted by threat actors who were successful in their attempts to exploit it.

The attackers were able to gain access to the infrastructure by exploiting static default passwords, which were found to be malfunctioning.

This incident highlights the importance of maintaining strong security measures and regularly updating passwords to prevent unauthorized access to critical infrastructure systems.

Based on recent and continuing threat activity, CISA is issuing this alert to require all technology manufacturers to remove default passwords from all product designs, releases, and updates.

Evidence has been mounting for years, showing that it is insufficient to rely on thousands of consumers to change their passwords.

Instead, serious action by technology manufacturers is the only way to effectively address the serious threats that critical infrastructure organizations confront. 

Notably, It is unacceptable to utilize default passwords that are generally known in the present threat environment.

Additionally, the hackers targeting programmable logic controllers (PLCs) hardcoded with a four-digit password demonstrate the significant potential for real-world harm caused by manufacturers distributing products with static default passwords.

The default password was easily accessed by actors with IRGC (Iranian Government’s Islamic Revolutionary Guard Corp) ties, giving them access to vital services that are provided to communities all around the nation.

The recent security breach has highlighted some important lessons for the Cybersecurity and Infrastructure Security Agency (CISA).

Despite the attack, the agency is determined to learn from these compromises and implement more robust security measures to prevent future incidents.

 Take Ownership of Customer Security Outcomes

In this principle, attention is given to the key security areas that manufacturers should protect, such as public safety and health. It includes:

  • Provide instance-unique setup passwords with the product.
  • Establish time-limited setup passwords that require activation of more secure authentication methods, including phishing-resistant MFA, and disable themselves after the setup process.
  • The purpose of the initial setup and the specification of instance-unique credentials require physical access.

Build Organizational Structure and Leadership

Product and public safety concerns are fundamentally at the core of cybersecurity issues; thus, manufacturers should make sure that business units in charge of product and service design, development, and delivery understand this.

Manufacturers should ensure that design and development teams engineer products with built-in security and safety by default.


[ad_2]
Source link

Third OnePlus 12R camera won’t be as useful as it should be

0
[ad_1]

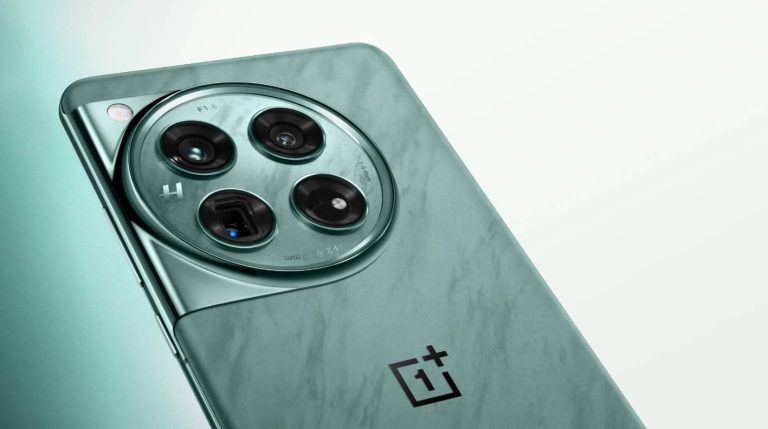
The OnePlus 12R is coming next month, as it was confirmed recently. The company confirmed that it will launch alongside the OnePlus 12 on January 23. That will be their global launch, as the OnePlus 12 already launched in China. Having said that, more OnePlus 12R info just surfaced, as it seems like its third camera on the back won’t be as useful as we’ve hoped it will.

The third OnePlus 12R camera on the back won’t be what we hoped for

A lot of OnePlus 12R information already surfaced. We have almost all of its specifications at this point. Some details are missing, and Max Jambor, a well-known tipster, has just decided to fill in one of those gaps.

The third camera on the back of the OnePlus 12R will be a 2-megapixel unit, as rumored, unfortunately. It will be a 2-megapixel macro camera, the tipster has confirmed. Initially, it was rumored to be a 32-megapixel telephoto camera with 2x optical zoom.

Needless to say, that telephoto camera would be far more useful. A 2-megapixel camera is generally not great, especially when it comes to a macro camera. Chances are you’ll stay away from it in general, and use the main or ultrawide shooters for macros.

2-megapixel macro cameras usually end up being underwhelming

Not a single phone I’ve tested, that contained a 2-megapixel macro camera, was supposed to have it. The images taken with it don’t look great in basically any condition. You can get somewhat usable shots in great lighting, but only barely.

It is understandable that OnePlus had to cut costs, however. The OnePlus 12R will have a great set of specs in general, and presumably a great price tag, so something had to go. It would maybe be a better idea to omit the third camera altogether than to use this one.

Either way, we’ll see what exactly we’ll get. The other two cameras do look good on paper. A 50-megapixel main camera (Sony’s IMX890 sensor), and an 8-megapixel ultrawide camera. Those are not the very best camera specs out there, but… you can’t expect that considering this will technically be a mid-range device. The OnePlus 12 will be an entirely different story.

The Snapdragon 8 Gen 2 will fuel the OnePlus 12R, allegedly. The phone is said to include a 5,500mAh battery, and support 100W charging. A large 120Hz display will also be in use, by the way.


[ad_2]
Source link

Galaxy S24 could utilize AI to erase objects from videos

0
[ad_1]

Samsung‘s Galaxy S24 flagships will ship with Android 14-based One UI 6.1 out of the box. The new One UI version brings a plethora of AI features. Leaks have revealed AI-powered battery health protection tools, wallpapers, lockscreen effects, image expansion, object relocation in images, notes arrangement and summary, circle search, voice detection in recordings, and more. It appears the Galaxy S24 lineup also uses AI to erase objects from videos.

Galaxy S24 may let you erase objects from videos using AI

A recent post on X by @BennettBuhner detailed a bunch of AI features Samsung will introduce with One UI 6.1 on the Galaxy S24 series. The tipster says the new flagships will use AI processing to optimize videos. AI can help enhance the quality of videos in low-light scenes by reducing graininess and improving stability and exposure. The phones also improve low-light photos with the help of AI.

Additionally, the Galaxy S24 lineup can remove objects from photos and videos. You have to simply select an object in a photo or video clip and AI will remove it from all scenes. It will automatically fill in the space with relevant details depending on surrounding objects. This may be easier to pull off in photos than videos but Samsung seems confident that its self-developed AI solution will give satisfactory results to users.

The upcoming flagship lineup is also said to boast an on-device AI chatbot, similar to ChatGPT. The tool can give you answers to your questions and solve basic equations. Based on Samsung’s official announcements and leaks, it will be available offline. The source says the AI chatbot may not be available at launch. The Korean firm may still be working on it. The feature may arrive later via a software update.

The Galaxy S24 series may also monitor your phone calls and detect the topic you discussed. Since this can be a privacy concern, the feature will likely be optional. When enabled, AI will offer you suggestions based on what you spoke during the call. For example, if you planned a meeting, it may ask you to set up a reminder or add the event to your calendar. This feature may also work when you use Bixby Text Call which can translate and transcribe voice calls.

These AI features may reach other Galaxy flagships later

All of these AI features are part of Samsung’s One UI 6.1. The company will update the likes of the Galaxy S23 and recent foldables to the new One UI version following the Galaxy S24 launch. The update should bring some of these features if not all. The new flagships are expected to go official on January 17, 2024. So it is just about a month of waiting now before the Korean firm presents its AI-powered phones.


[ad_2]
Source link

“Get Paid to Like Videos”? This YouTube Scam Leads to Empty Wallets

0
[ad_1]

Beware! YouTube “Social Media Marketing” Scam Snatches Cash After Luring Users with Likes & Subscriptions.

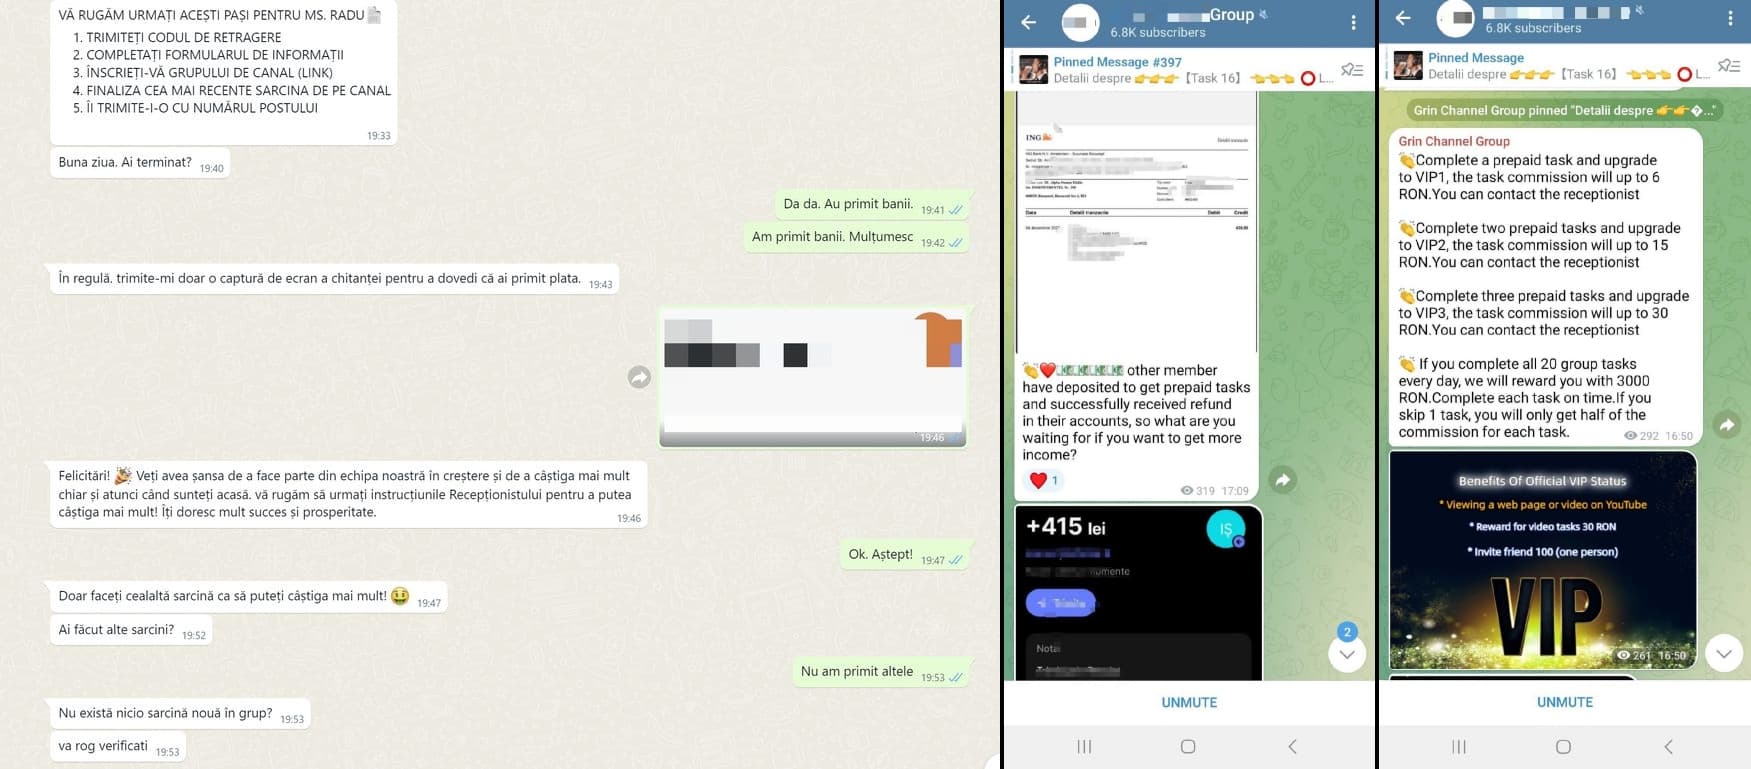
Cybersecurity researchers at Bitdefender Labs have uncovered a new scam wherein users earn money by liking random YouTube videos. In this scam, threat actors send a message from an unknown number, usually beginning with an African country code, promising payment for liking videos on YouTube. 

Bitdefender researchers participated in one such scam for investigative purposes and found that scammers ask for personal information, including WhatsApp phone number, age, occupation, full name, and bank account number before asking the victim for likes and subscriptions.

Further, researchers were instructed to like three YouTube videos and send screenshots as proof. The researchers were then instructed to download Telegram, join a channel, and discuss payment with a receptionist. After providing the required data, researchers received a payment of 30 RON ($6.50). The scammer then promised additional daily tasks.

However, the scam’s second phase starts after the victim joins the Telegram channel. They are invited to join a VIP group for higher-earning tasks, which can only be unlocked for a fee, ranging from $21.66 to $1,083. Once the victim makes the payment, scammers block their number and stop communicating. Their Telegram channel features screenshots of payments made to victims to gain trust, highlighting the scammers’ intent.

According to Bitdefender Labs’ blog post, researchers found similar job listings on Facebook groups promoting remote work or lucrative pay for liking/subscribing to YouTube channels. One of the posts read, “Hello. I’m Lopez Digital Marketing at , do you want some extra income?

Scammers claim that users can make 30 RON by liking 3 videos and earn around 200-2,000 RON or more per day. One of the intros scammers posted with the offers read (translated in English from Romanian):

“We are a global multinational company and we are currently working as a social media team to increase the visibility of social media celebrities on YouTube and get paid by following and liking our celebrity YouTube accounts. We have to fill out the form to pay you a salary of 30 RON.”

"Get Paid to Like Videos"? This YouTube Scam Leads to Empty Wallets
Screenshots from the Telegram channel run by scammers reveal their efforts to prompt people to like a YouTube video about Romania, share payment invoices, and invite unsuspecting victims to join a VIP Telegram group. (Credit: BitDefender)

Although this isn’t the first time a scam is pitched to make money, this time, “victims actually get paid something,” which is “a highly successful tactic”, explained Bitdefender’s Cyber Threat Intelligence Lab’s Manager, Nicolae Postolachi.

That’s because it generates a sense of trust and convinces users to “invest” in becoming VIP members to earn easy money on effortless tasks such as liking YouTube videos.

Remember, there are no secret tools, apps, or platforms that enable easy money. To steer clear of scams on WhatsApp, exercise caution with recruiters who demand high payments for tasks like watching or liking YouTube videos, encourage users to download Telegram, or request upfront payments to unlock higher-paying opportunities.

If you fall victim, take screenshots, cease communication, block the user, and leave the Telegram group. Secure your accounts with strong passwords and enable two-factor authentication. Report the scam account to the social media platform, file a police report, and alert friends and family.

  1. Hackers used fake job website to scam jobless US veterans
  2. Fake Resumes, Real Malware: Hackers Target Job Recruiters
  3. Fake LinkedIn job offers scam spreading More_eggs backdoor
  4. Interpol Busts Human Traffickers Luring Victims with Fake Job Ads
  5. Hackers Used Fake LinkedIn Job to Hack Off $625M from Axie Infinity

[ad_2]
Source link

Government offices in China ban Samsung and Apple phones

0
[ad_1]

China is intensifying its ban on foreign smartphones in government offices. Several Chinese agencies and state-backed firms have ordered employees to stop bringing Apple iPhones, Samsung Galaxy phones, and other non-Chinese devices to the workplace. These “verbal directives” were issued in at least eight provinces over the past month or so, people familiar with the matter told Bloomberg.

China bans Samsung and Apple phones from government offices

The ties between the US and China, the world’s two largest economies, have worsened in recent years. The two countries are fighting a trade war that escalated in 2019 after the Donald Trump-led US government placed the Chinese electronics giant Huawei in its Entity List. The sanctions cut off the firm’s access to the latest foreign technologies, limiting its business scope and competitiveness.

The US has continued to tighten its sanctions on Huawei and is also exploring a ban on TikTok. The Chinese-origin video app is already banned from government devices in most states. China, meanwhile, is increasingly becoming self-sufficient in the field of technology. A robust domestic supply chain has enabled Huawei to stand up and fight its way back into the global smartphone scene.

While it is still far from where it was before the 2019 US sanctions, the Chinese government is helping its cause. Xi Jinping’s administration has long banned foreign devices from sensitive government departments. Other official agencies and firms are now following suit. Bloomberg’s sources have confirmed such directives in provinces along the prosperous coastal region and other parts of the country.

The scale of this ban is unknown, i.e., how many agencies have ordered their employees against bringing Apple and Samsung phones to the office is unclear. However, China hasn’t passed any written law to ban foreign devices from government offices. “China has not issued laws and regulations to ban the purchase of Apple or foreign brands’ phones,” a Chinese Foreign Ministry spokeswoman said in September.

iPhone sales are already declining in China

This ban will affect Apple more than Samsung. Despite being the world’s biggest smartphone company, the latter has a negligible presence in the world’s largest smartphone market (less than a two percent market share). On the other hand, Apple generates about a fifth of its smartphone revenue from China. It produces the majority of iPhones in the world’s largest country, though it is gradually shifting away.

As the US-China trade war intensifies, Apple is becoming collateral damage. Studies have shown that iPhone sales in China are dropping. The iPhone 15 series is selling worse than the previous generation. The more China pushes for self-sufficiency, the bigger will be the impact on Apple. The company’s CEO Tim Cook is trying to maintain a healthy relationship with Beijing but those efforts may not help.


[ad_2]
Source link

New SMTP Smuggling Attack Lets Hackers Send Spoofed Emails

0
[ad_1]

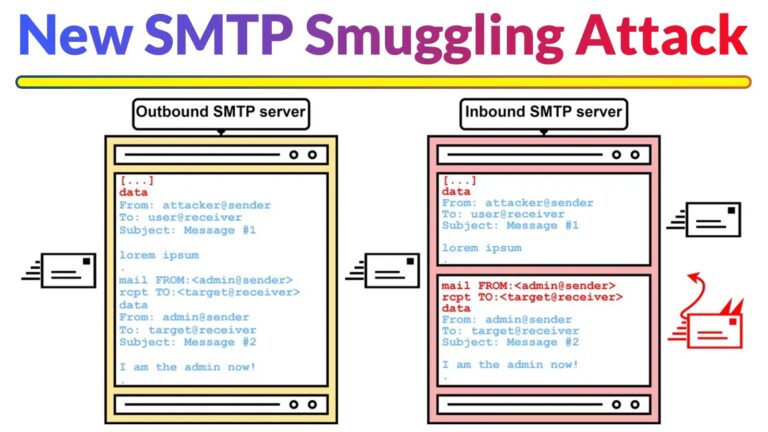
SMTP (Simple Mail Transfer Protocol) smuggling is a technique where attackers exploit the inconsistencies in how proxy servers or firewalls analyze and handle the SMTP traffic. 

Threat actors can smuggle malicious payloads or evade detection by exploiting these inconsistencies.

This complete process makes it difficult for security systems to accurately diagnose the email transfer process, leading to potential security vulnerabilities.

In collaboration with SEC Consult, Timo Longin unveiled a new SMTP exploitation technique named SMTP smuggling.

Vulnerable servers globally can be exploited for phishing attacks by sending malicious emails from any address.

Besides this, multiple 0-day flaws were found, and vendors were already notified in a 2023 responsible disclosure.

New SMTP Smuggling Attack

SMTP protocol interpretation differences enable SMTP smuggling, sending spoofed emails while passing SPF checks. 

There are two types of SMTP smuggling were discovered, and we have mentioned them:- 

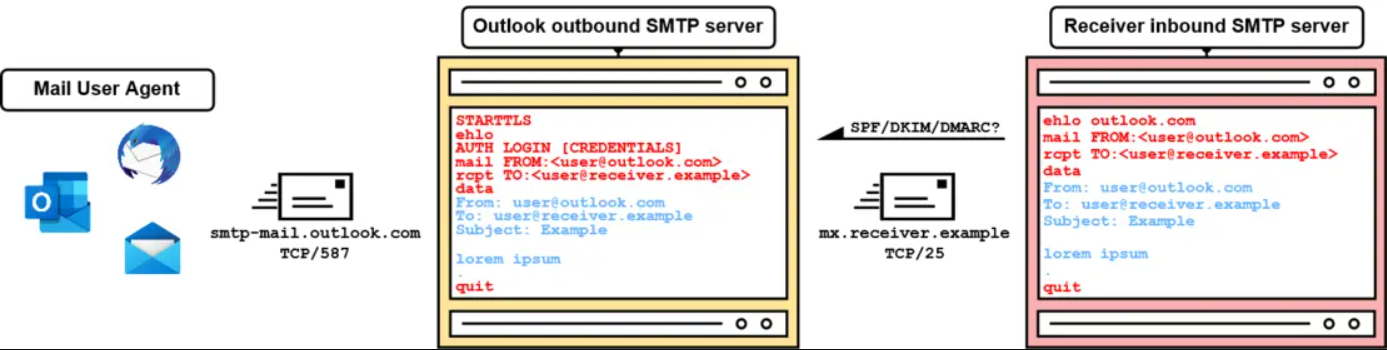
Overview of a simplified e-mailing process via SMTP from left to right
Overview of a simplified e-mailing process via SMTP from left to right (Source – SEC Consult Vulnerability Lab)

This allows spoofing from various domains to major SMTP servers. Microsoft and GMX fixed vulnerabilities, but SEC Consult urges manual updates for Cisco Secure Email users.

MUA (Mail user agent) connects to Outlook’s MTA (Mail transfer agent) via TCP/587. After that, a series of SMTP commands are sent; Outlook SMTP evaluates permission, then sends an inbound email to the receiver’s SMTP server via TCP/25, bypassing:-

Inbound SMTP servers verify sender authenticity using SPF, DKIM, and DMARC to prevent arbitrary domain emails. SPF relies on DNS records for sender IP permission, and the failure results in non-forwarding or spam marking. 

However, SPF checks only the MAIL FROM domain, not the arbitrary value in the From header, which poses a limitation.

DKIM signs message data, including the From header, verified by the receiver with a public key in DNS. 

But it doesn’t enforce the key’s domain. DMARC introduces identifier alignment by checking if the “From” domain aligns with SPF and/or DKIM. 

The policy (p=) specifies the rejection of messages failing DMARC, ensuring acceptance only with valid SPF or DKIM.

Email providers used

Here below, we have mentioned all the email providers that are used:-

  • outlook.com 
  • gmail.com 
  • gmx.net 
  • icloud.com 
  • zoho.com 
  • fastmail.com 
  • runbox.com 
  • startmail.com 
  • mailbox.org 
  • aol.com 
  • yahoo.com 
  • web.de 

Analyzing outbound SMTP servers revealed an anomaly in Microsoft Outlook’s (outlook.com) server. Sending <LF>.<LF> sequence results in non-transmission, triggering an error message:-

  • “550 5.6.11 SMTPSEND.BareLinefeedsAreIllegal; message contains bare linefeeds, which cannot be sent via DATA and receiving system does not support BDAT”

Unlike GMX, Outlook doesn’t filter <LF>.<CR><LF> sequences. Smuggling to certain receivers is blocked due to Outlook’s use of the optional BDAT SMTP command, an alternative to DATA, specifying message length without relying on an end-of-data sequence.

Due to negligent outbound server sanitization, SMTP smuggling is possible in GMX and Exchange Online. 

Investigating insecure inbound SMTP servers, a scanner tests for permissiveness with exotic end-of-data sequences. While here, a timeout indicates the server ignored the unconventional sequence.

Research uncovered exotic inbound SMTP servers interpreting end-of-data sequences like <CR><LF>\x00.<CR><LF> (null byte represented by “\x00”). 

Despite prompt patches by Microsoft and GMX, inbound SMTP smuggling to default-configured Cisco Secure Email instances remains possible. Changing these configurations is strongly advised.

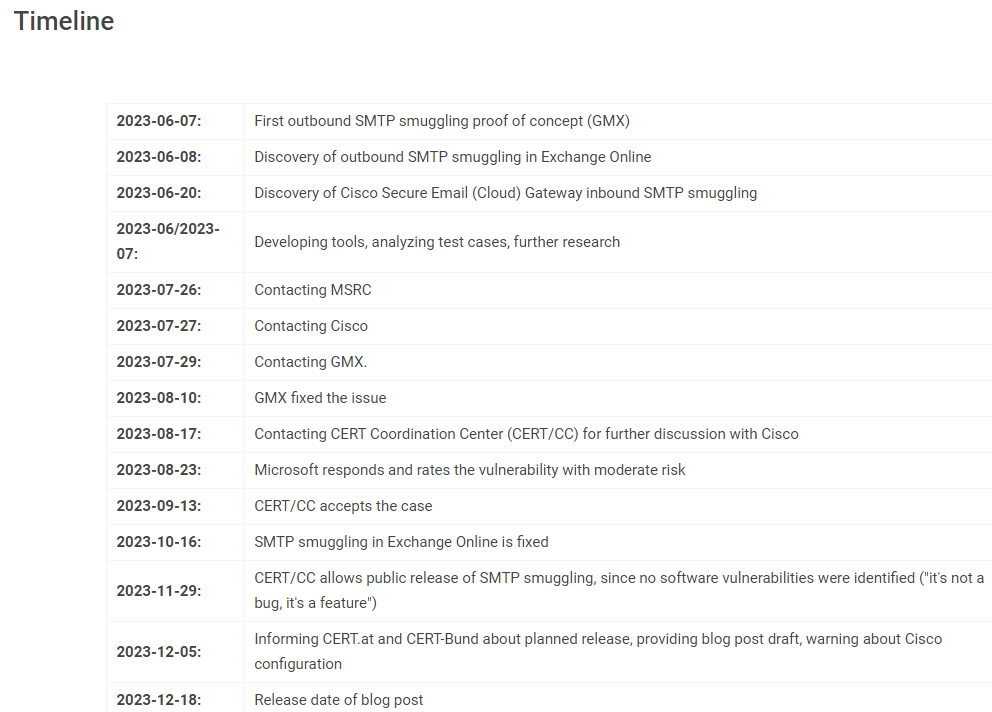
Timeline

Timeline
Timeline (Source – SEC Consult Vulnerability Lab)

[ad_2]
Source link