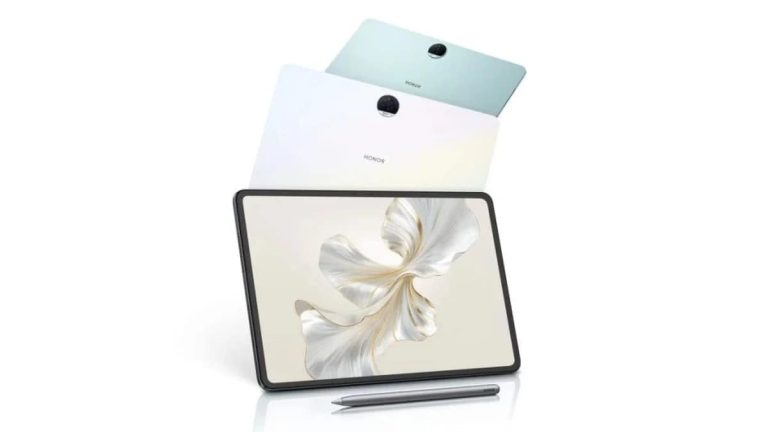
The HONOR Pad 9 is a budget tablet which comes in a ‘Soft Light Edition’ too
Before we begin, do note that the HONOR Pad 9 is a budget device. Despite that, however, the bezels around its display are rather thin (for a tablet), and the device looks very nice overall. It has a flat frame all around, and an easily noticeable circular camera island on the back.
This tablet also launched in two versions, a standard version, and a ‘Soft Light Edition’. That version comes with paper-like eye-protection, it basically has a matte display. That reduces the impact of light, and makes it easy to use the device outdoors. This made us think of the Huawei MatePad 11.5-inch PaperMatte Edition straight away.
It has a large 12.1-inch display
That being said, the device has a 12.1-inch 2560 x 1600 TFT LCD display. That display can project 1 billion colors, and has a peak brightness of 500 nits.
The Qualcomm Snapdragon 6 Gen 1 SoC fuels this tablet, it’s a 4nm processor. 8GB and 12GB RAM variants have been announced, along with 128GB, 256GB, and 512GB storage flavors.
There are 8 speakers included here
Android 13 comes pre-installed on the tablet with MagicOS 7.2 skin on top of it. There are 8 speakers included on the device, with two microphones. An 8,300mAh battery is also included, and 35W wired charging support. Yes, a charger is included in the retail box.
There is one camera included on the back, a 13-megapixel unit (f/2.0 aperture, 4K video recording). On the front, you’ll find an 8-megapixel camera (f/2.2 aperture). Bluetooth 5.1 is also supported here.
Three color options have been introduced
The HONOR Pad 9 measures 278.27 x 180.11 x 6.96mm, while it weighs 555 grams (standard version). The soft light model weighs 559 grams. The HONOR Pad 9 comes in Blue, Gray, and White colors.
The pricing of this tablet goes from CNY1,599 ($223) for the 8GB RAM + 128GB storage model, to CNY2,199 ($307) for the 12GB RAM + 512GB storage variant.
Due to the widespread use and popularity of Windows and macOS, threat actors often target these platforms.
Windows is a common target because it dominates the global operating system market, while macOS is targeted because of its majority among:-
Professionals
Creative industries
Recently, cybersecurity researchers at ATT discovered JaskaGO malware, which was found to be attacking Windows and macOS operating systems.
JaskaGO Malware Attacking Windows
JaskaGO, using the Go programming language, signifies a rise in malware trends. Go’s simplicity attracts authors, creating versatile threats.
Despite macOS’s perceived security, JaskaGO eliminates the myth, targeting both macOS and Windows users. It disguises itself as legit software on pirated pages, evolving and spreading since its first Mac-focused appearance in July 2023.
Moreover, the low detection rate of this malware creates complex challenges for antivirus engines.
The malware tricks users with a fake error box on startup, pretending to fail. It checks for virtual machines by examining system details like:-
Processors
Memory
MAC addresses
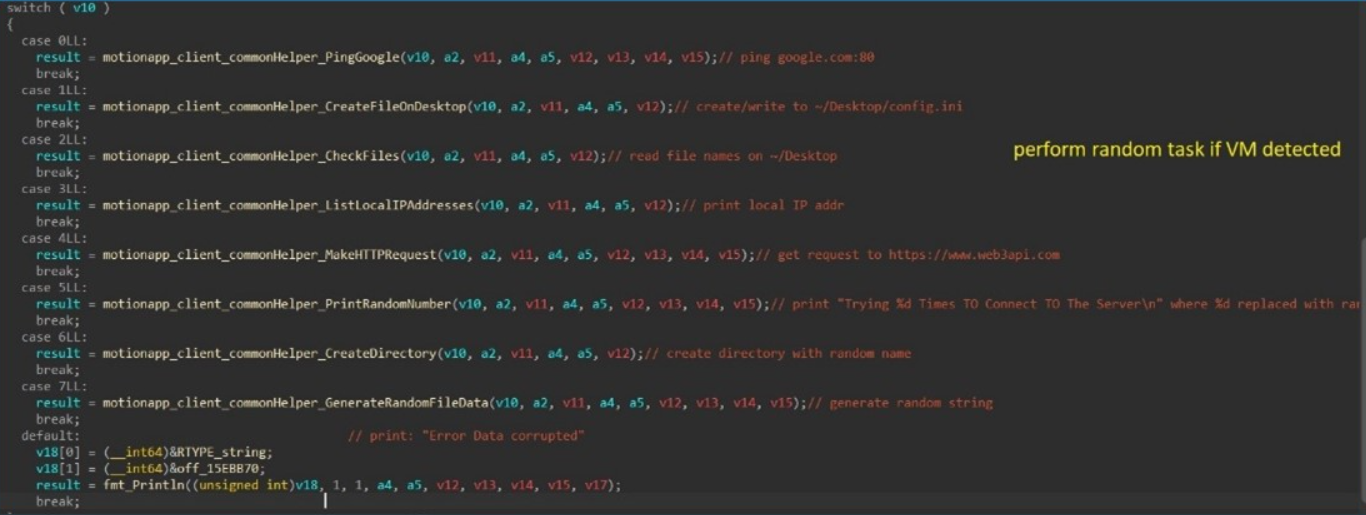
Besides this, the detection of VM-related traces triggers random command execution. Here below, we have mentioned the commands:-
Ping Google.
Create a File on the Desktop (e.g., config.ini).
List files on the user’s desktop.
List local IP addresses.
Make a simple HTTP GET request to https://www.web3api.com.
Print a random number.
Create a directory with a random name in the user’s home directory.
Print a random string.
Perform random task (Source – ATT)
Once VM detection is evaded, JaskaGO gathers victim info and connects to its command center, staying alert for further commands.
JaskaGO skillfully exfiltrates data, storing and zipping it in a dedicated folder before sending it to the threat actor.
Here below, we have mentioned all the stealers used:-
JaskaGO is a cross-platform threat challenging macOS invulnerability, using anti-VM tactics for stealth, persistently embedding in systems, and transforming into a dangerous threat with stealer capabilities.
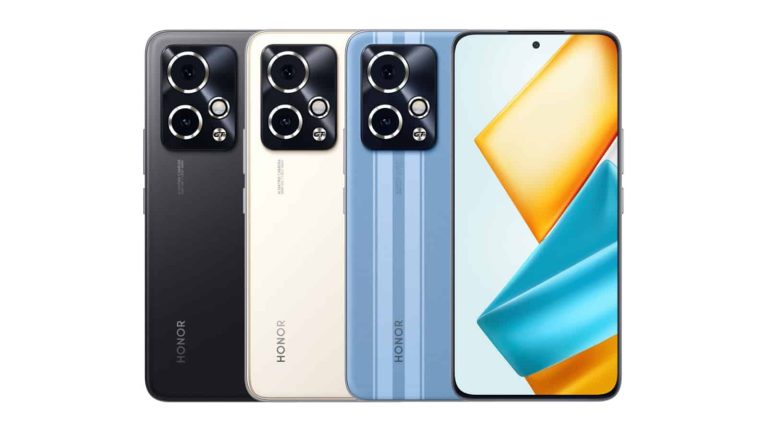
A new HONOR smartphone has just launched. The device in question is called the HONOR 90 GT, and it was announced in China. Despite the fact it has the HONOR 90 brand, it looks both different than its sibling, and it sports different internals.
The HONOR 90 GT got announced with up to 24GB of RAM
The HONOR 90 GT got announced in China, and it actually has a really nice spec sheet. The phone features a display camera hole the display, while its bezels are quite thin. The bottom bezel is thicker than the rest, though.
You’ll notice that all of its physical buttons sit on the right-hand side. There are two cameras placed on the back of the device, while the frame around the phone is flat.
On the front, you’re getting a 6.7-inch 2664 x 1200 OLED display. That is a 120Hz panel, and it can project 1 billion colors. It also comes with a 3,840Hz high-frequency PWM dimming, and multi-finger touch enhancement algorithm.
The Snapdragon 8 Gen 2 SoC fuels this phone, while advanced cooling is also a part of the package
The Snapdragon 8 Gen 2 fuels this smartphone, and it was launched in several variants. 12GB, 16GB, and 24GB RAM models are available. The 12GB RAM variant comes with either 256GB or 512GB of storage. The 16GB RAM model includes 256GB of storage. The top-end 24GB RAM variant comes with 1TB of storage.
The HONOR 90 GT also includes a 3D dual-power iced VC, which includes an innovative 3D structure design. It has a 2,164mm³ cavity volume, and 5,268mm² soaking area for ultra-high thermal conductivity.
Android 13 comes pre-installed here, with HONOR’s Magic UI 7.2. There are two SIM card slots included (2x nano SIM), and an in-display fingerprint scanner. You’ll also find stereo speakers here, along with Bluetooth 5.3.
The device supports 100W charging, and comes in three colors
A 5,000mAh battery sits on the inside, and it supports 100W wired charging. Yes, the charger is included in the box as well.
A 50-megapixel main camera (Sony’s IMX800 sensor, f/1.95 aperture) is backed by a 12-megapixel ultrawide camera (f/2.2 aperture). On the front, you’ll find a 16-megapixel shooter (f/2.4 aperture).
The HONOR 90 GT measures 162.5 x 75.3 x 7.9mm, while it weighs 187 grams. The device comes in Blazing Gold, GT Blue, and Starlight Black colors. Its pricing starts at CNY2,599 ($364), and goes up to CNY3,699 ($518).
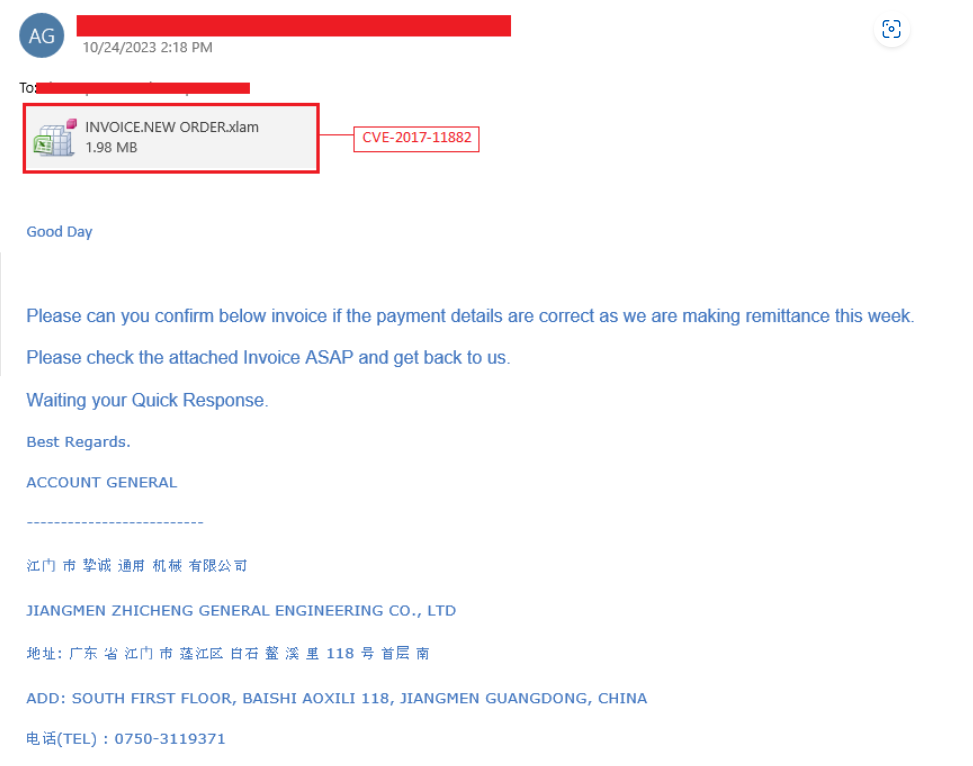
It has been reported that malicious individuals are utilizing a malware called Agent Tesla to target Microsoft Office users using versions affected by CVE-2017-11882 XLAM.
This malware is taking advantage of a remote code execution vulnerability in Equation Editor, which is present in Microsoft Office and known as CVE-2017-11882.
Remote code execution (RCE) is a type of cyberattack where an attacker uses a remote computer or network to execute malicious code without requiring user data.
Sensitive information can be accessed remotely through a code execution vulnerability, without requiring physical network access by hackers.
It is important to be aware of spam emails that contain malicious attachments. Hackers often use this technique to inject harmful programs onto a user’s device.
Once the user downloads and opens the attachment, the malicious program is activated, potentially causing harm to the device and compromising sensitive information.
Spam with a malicious attachment
According to the Zscaler report, if a user downloads and views a malicious attachment on a vulnerable version of Microsoft Excel, the Excel file will connect to a negative location and start downloading other files without requiring any further action from the user.
Variable names in the VBS file are 100 characters long, which complicates the deobfuscation and analysis process. The JPG file contains a malicious Base64-encoded DLL.
After the JPG file is downloaded, the VBS file initiates the execution of a PowerShell executable. This executable then retrieves a DLL in Base64-encoded form from the image file. The DLL is subsequently decoded, and its malicious procedures are loaded.
PowerShell performs the main operation for reading and writing the registry. After this, the DLL injects a thread into the main function, which retrieves the Agent Tesla payload.
Agent Tesla attempts to install hooks for both the clipboard and keyboard to monitor and record every keystroke that the user types and collect data from the user’s copied information.
Agent Tesla employs a technique known as window hooking to monitor users’ keystrokes, mouse movements, and event messages. The function of the malicious actor ceases before the user can react.
A Telegram bot controls the threat actor who receives the data exfiltrated from the virus. To protect our information, we must keep ourselves informed about cyber threats and stay updated.
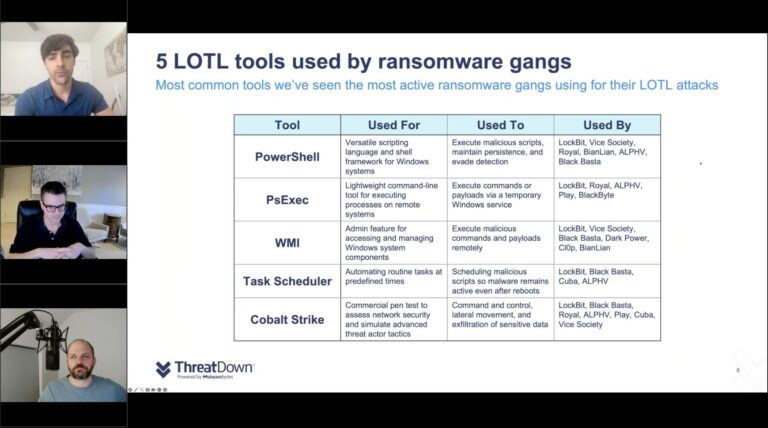
Discover the intersection of Ransomware-as-a-Service (RaaS) gangs and Living Off The Land (LOTL)attacks in our latest webinar, now available on-demand, led by cybersecurity experts Ian Thomas, Mark Stockley, and Bill Cozens.
The webinar revealed how RaaS gangs use LOTL tactics, leveraging legitimate IT tools like Powershell and WMI to blend malicious activities within normal network operations, significantly challenging detection efforts.
Attendees gained an in-depth understanding of LOTL attacks, tools exploited by RaaS gangs, and strategies for IT teams to identify and block these advanced threats.
Some highlights from the webinar include:
Expert analysis: Insights from seasoned cybersecurity professionals on the critical need for multi-layered defense strategies.
Practical advice: Real-world, actionable tips for IT teams to detect and counter covert LOTL operations.
Case studies: Detailed scenarios demonstrating the impact and complexity of LOTL attacks.
Understanding the relationship between LOTL and RaaS is vital for evolving cybersecurity strategies. The webinar emphasizes the importance of blending technology and human expertise to detect and combat these sophisticated threats effectively.
Enhance your ransomware knowledge and preparedness by watching this essential webinar on-demand. Alternatively, download the report that the webinar is based on here.
Pharmacy chain Rite Aid has been denied the right to run facial recognition systems in its stores for five years, by a Federal Trade Commission (FTC) ruling. The regulator found so many flaws in the retailer’s surveillance program that it concluded Rite Aid had failed to implement reasonable procedures and prevent harm to consumers in its use of facial recognition technology in hundreds of stores.
In May 2023, the FTC issued a warning that the increasing use of consumers’ biometric information and related technologies, including those powered by machine learning, raises significant consumer privacy and data security concerns, and the potential for bias and discrimination.
“The agency is committed to combatting unfair or deceptive acts and practices related to the collection and use of consumers’ biometric information and the marketing and use of biometric information technologies.”
According to the FTC, Rite Aid deployed artificial intelligence-based facial recognition technology from 2012 to 2020, in order to identify customers who may have engaged in shoplifting or other problematic behavior.
The FTC found that Rite Aid deployed a massive, error-riddled surveillance program, provided by vendors that could not properly safeguard the personal data the chain hoarded. The company also failed to inform consumers that it was using the technology in its stores.
According to the complaint, Rite Aid contracted with two companies to help create a database of images of individuals considered persons of interest for engaging in or attempting to engage in criminal activity at one of its retail locations. The images were derived from CCTV camera’s in the stores and smartphone pictures taken by employees. These were stored in a database along with their names and other information, such as any criminal background data.
Despite the fact that the system relied on low-quality images to identify these so-called persons of interest, the chain instructed staff to ask these customers to leave its stores. The employees, acting on false positive alerts caused by the flawed system, followed consumers around the stores, searched them, ordered them to leave, called the police to confront or remove consumers, and publicly accused them of shoplifting or other wrongdoing.
According to the complaint, Rite Aid’s system falsely flagged numerous customers, including an 11 year-old girl whom employees searched based on a false-positive result. The FTC says that Rite Aid did nothing to prevent their customers from being falsely accused. In addition, the FTC says Rite Aid’s actions disproportionately impacted people of color.
But even if the system had been completely accurate, there were enough problems in the way the system was deployed:
Without consent or warning, the system scanned everyone who came into certain stores and matched them against an internal list. Store patrons located in plurality-Black, plurality-Asian, and plurality-Latino areas were more likely to be subjected to and surveilled by Rite Aid’s facial recognition technology.
Rite Aid failed to test, assess, measure, document, or inquire about the accuracy of its facial recognition technology before deploying it.
The use of low-quality images in connection with its facial recognition technology increased the likelihood of false-positive match alerts.
It failed to monitor or test the accuracy of the technology after deployment.
Employees were not trained to understand the possibility of false positives nor did they take action so employees would report false positives.
This is not the first time Rite Aid and the FTC have clashed. In 2010, Rite Aid agreed to FTC charges that it failed to protect the sensitive financial and medical information of its customers and employees, in violation of federal law.
Rite Aid violated the 2010 data security order, and in addition to the ban and required safeguards for automated biometric security or surveillance systems the FTC requires the company to:
Delete, and direct third parties to delete, any images or photos they collected.
Notify consumers when their biometric information is used.
Investigate and respond in writing to consumer complaints about actions taken against consumers related to an automated biometric security or surveillance system.
Provide clear and conspicuous notice to consumers about the use of facial recognition or other biometric surveillance technology in its stores.
Delete any biometric information it collects within five years.
Implement a data security program to protect and secure personal information.
Obtain independent third-party assessments of its information security program.
Provide the Commission with an annual certification from its CEO documenting Rite Aid’s adherence to the order’s provisions.
While the FTC ruling highlights Rite Aid’s wrongdoings, it also acknowledges the fact that there are many problems with facial recognition. Because of the privacy implications some tech giants have backed away from the technology, or halted development.
People should at least be informed about when and why facial recognition technology is used, so they can decide for themselves whether they want to participate.
We don’t just report on threats—we remove them
Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.
Google has released an emergency security update for Chrome that brings the browser’s Stable channel to version 120.0.6099.129 for Mac, Linux and to 120.0.6099.129/130 for Windows. This update includes one security fix for a vulnerability that was subject to an existing exploit.
The easiest way to update Chrome is to allow it to update automatically, which basically uses the same method as outlined below but does not require your attention. But you can end up lagging behind if you never close the browser or if something goes wrong—such as an extension stopping you from updating the browser.
So, it doesn’t hurt to check now and then. And now would be a good time, given the severity of the vulnerability in this patch. My preferred method is to have Chrome open the page chrome://settings/help which you can also find by clicking Settings > About Chrome.
If there is an update available, Chrome will notify you and start downloading it. Then all you have to do is relaunch the browser in order for the update to complete.
After the update, the version should be 120.0.6099.129, or later.
Google never gives out a lot of information about vulnerabilities, for obvious reasons. Access to bug details and links may be kept restricted until a majority of users are updated with a fix. However, from the update page we can learn a few things.
The Common Vulnerabilities and Exposures (CVE) database lists publicly disclosed computer security flaws. The zero-day patched in this update is listed as CVE-2023-7024, a heap buffer overflow in Web Real-Time Communications (WebRTC).
WebRTC on Chrome is the first true in-browser solution to real-time communications (RTC). It supports video, voice, and generic data to be sent between peers, allowing developers to build powerful voice- and video-communication solutions. The technology is available on all modern browsers as well as on native clients for all major platforms.
A WebRTC application will usually go through a common application flow. Access the media devices, open peer connections, discover peers, and start streaming.
A buffer overflow is a type of software vulnerability that exists when an area of memory within a software application reaches its address boundary and writes into an adjacent memory region. In software exploit code, two common areas that are targeted for overflows are the stack and the heap.
The heap is an area of memory made available for use by the program. The program can request blocks of memory for its use within the heap. When it uses memory blocks outside of the reserved area, this can influence other programs. This fact can be abused by an attacker.
The vulnerability was reported by members of Google’s Threat Analysis Group. This group frequently finds vulnerabilities that are used by state-sponsored groups in targeted attacks. This could indicate that Google found this vulnerability while researching an active attack, which matches the fact that an exploit for the vulnerability exists in the wild.
Since WebRTC is a Chromium component, users of other Chromium based browsers like Microsoft Edge will probably see a similar update.
We don’t just report on threats—we remove them
Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.
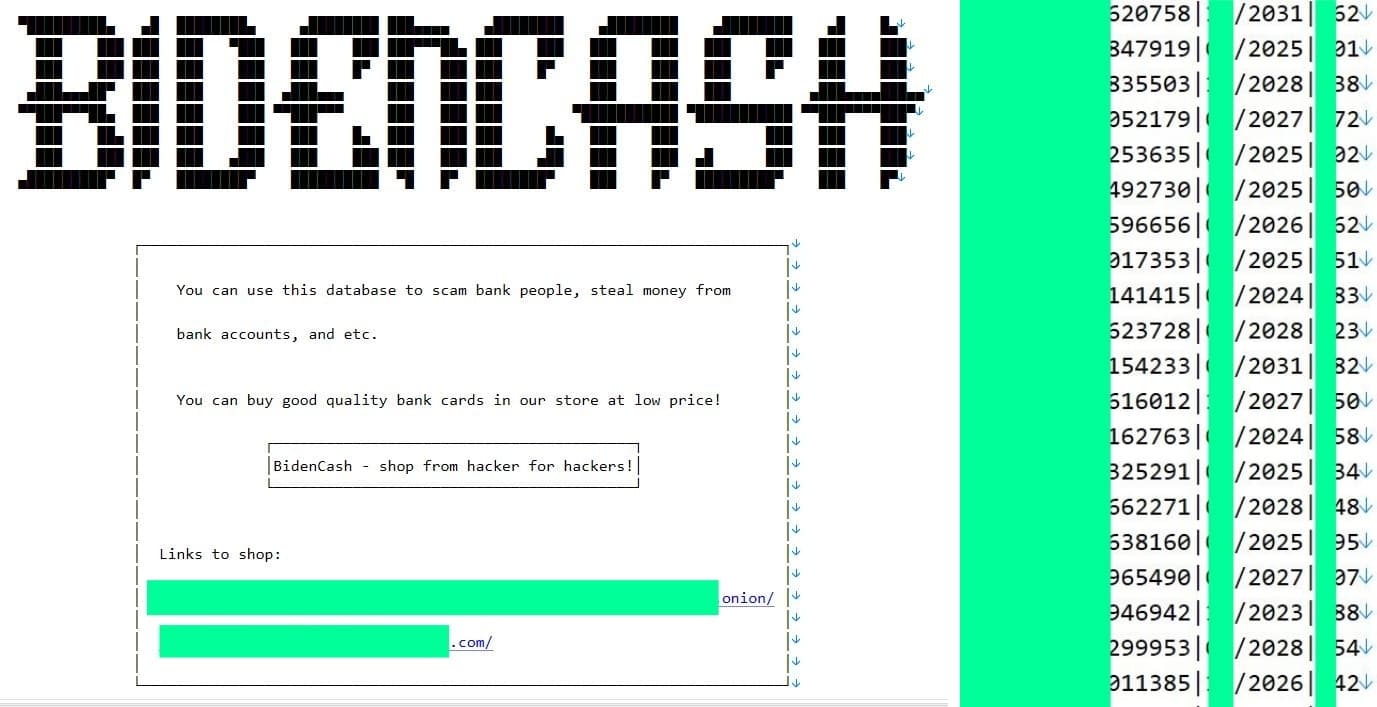
The latest leak from BidenCash includes payment card credentials in plain text, but unlike the site’s previous leaks, it does not include names or emails of cardholders.
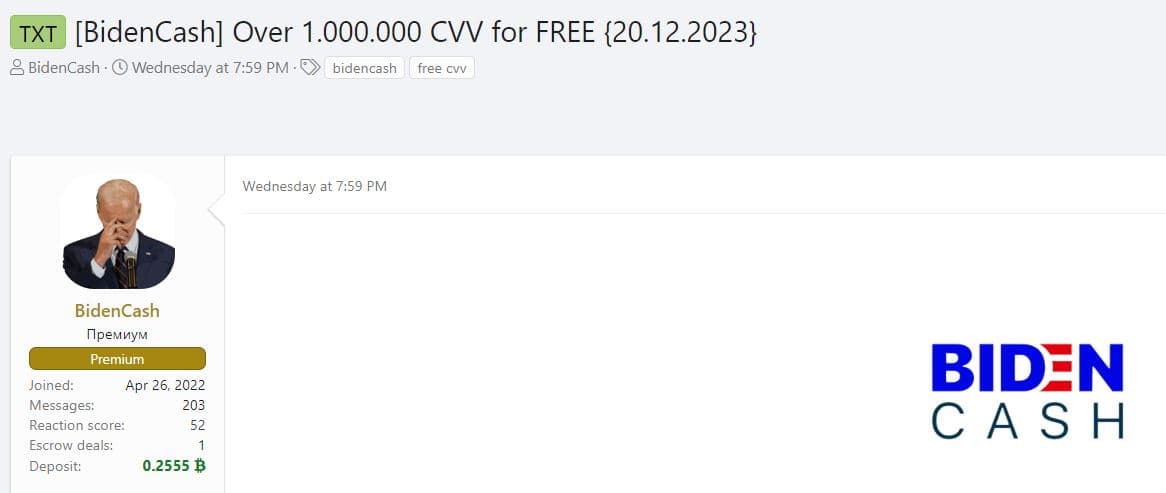
BidenCash, a notorious dark web carding marketplace, has leaked over 1.6 million valid payment card data including debit and credit card details on a notorious Russian language cybercrime and hacking forum- The same forum offered the sale of military satellite access for $15,000 in June 2023.
The overall count of leaked card details stands at 1.9 million (1,912,969). Upon deduplication, the precise figure is reduced to 1.6 million cards (1,169,843), Hackread.com can confirm.
Screenshot from the Russian forum (Credit: Hackread.com)
It is worth noting that on March 23, 2023, BidenCash leaked 2 million card data as part of its birthday celebration. The leak included cardholders’ full names, bank details, card numbers, expiration dates, card verification value (CVV) numbers, home addresses, and more than 500,000 email addresses.
This time around, there are no names or email addresses of the card owners involved. Instead, the leaked information consists of the full card number, expiry date, and CVV numbers – All in plain text format.
Screenshot from the leaked dataset (Credit: Hackread.com)
No Names is Good News
The absence of names in the leaked credit card data is good news for cardholders as it adds a layer of ambiguity and potentially mitigates the severity of the incident. While the compromised information includes sensitive details, the lack of associated names limits the extent to which the leaked data can be directly linked to specific individuals.
Without the inclusion of personal names, the potential for identity theft or targeted fraudulent activities may be reduced. However, it is crucial to note that the leaked financial details alone still pose a significant risk, as cybercriminals can exploit this information for unauthorized transactions and financial harm.
The overall impact of the breach, therefore, depends on the extent to which the compromised credit card details can be effectively exploited without the corresponding personal identifiers.
While the countries to which these cards belong remain unclear, BidenCash is notorious for engaging in large-scale selling and leaking of financial details. This includes a substantial amount of payment card data issued in countries such as the following:
India
China
Mexico
Canada
United States
United Kingdom
The specific operational details of BidenCash remain uncertain however, carding sites primarily acquire credit card information through diverse means. These methods include the utilization of information-stealing malware, phishing attacks, skimming, and exploiting vulnerabilities in point-of-sale (PoS) systems.
“Our system automatically and in real-time tracks publicly available cards on Telegram channels, Discord chats, and forums to prevent unscrupulous suppliers from using outdated material. If a card sold by us is found publicly available, we impose a fine on the supplier. If a supplier’s materials regularly appear in public, they are blocked. Our unique system, applied only on our platform, reflects our commitment to our reputation. Over the past month, the system has detected over 1,900,000 cards.”
BidanCash Website
If you own a debit or credit card, it is crucial to take extra precautions to ensure that your card is not being misused and that its credentials are protected from third parties. Caution is essential, particularly in watching out for phishing scams and malware attacks that target your financial information.
If your card issuer experiences a security breach, the responsibility rests on them to address the situation. However, it is vital to regularly monitor your bank statements and notify your bank of any suspicious transactions. Proactive communication with your financial institution is key to addressing potential issues and enhancing the security of your card information.
Maintaining updated systems and applications is a challenge for any IT team—especially considering the sheer volume of vulnerabilities organizations must find and prioritize on a rolling basis.
ThreatDown Vulnerability Assessment (VA), now included for free in every ThreatDown bundle, simplifies the vulnerability-finding process by automatically identifying gaps in your environment and prioritizing the results.
Based on the scans shared by the VA, ThreatDown Patch Management (PM), patches both the operating system and third-party applications installed on endpoints. But how exactly do both solutions work together?
Our journey with how Threat Down Vulnerability Assessment and Patch Management works begins as all great cybersecurity journeys begin: A clunky, on-prem server directly wired up to all your endpoints.
Just kidding. This isn’t the 1970s anymore. Thankfully.
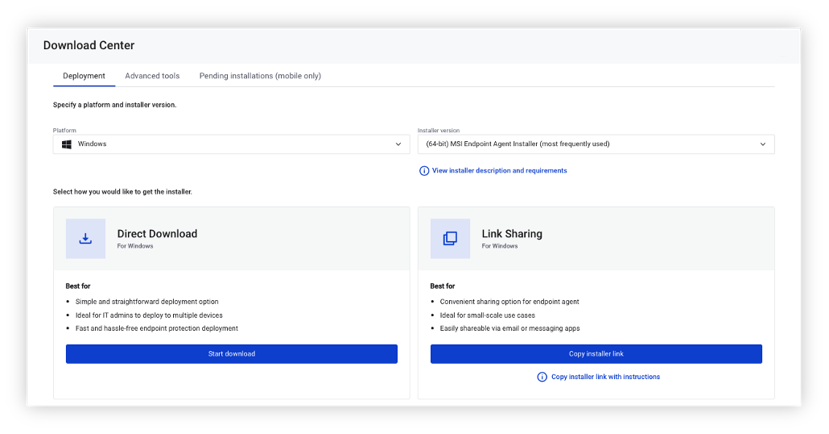
The cornerstone of all ThreatDown security solutions—not just Vulnerability Assessment, but Endpoint Detection and Response (EDR) in general—is a lightweight endpoint agent (EA). The EA is a software tool which collects and sends endpoint security data to a central system for analysis and threat response
You can distribute the ThreatDown EA to endpoints either manually to each user or automatically via network-wide remote deployment tools.
2. Vulnerability Assessment scans endpoints
When you download the ThreatDown Endpoint Agent on your devices, it can then scan for installed third-party software and find out if there are any known vulnerabilities in them.
To enable a Vulnerability Assessment policy in Nebula, check out this simple step-by-step guide. There are two ways to scan for vulnerabilities: on-demand or scheduled.
3. VA finds vulnerabilities across third-party applications
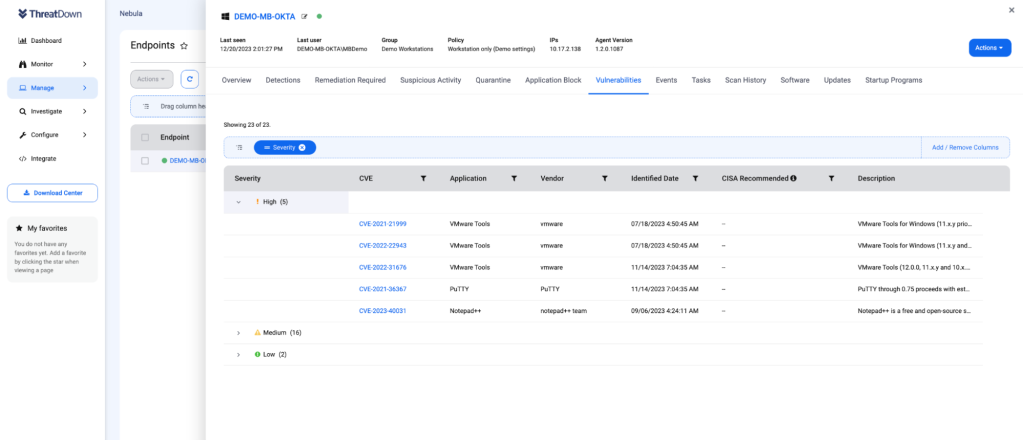
The ThreatDown EA sends the results of the vulnerability scan to Nebula, our cloud-hosted security platform. Vulnerability data is stored and displayed for up to 90 days across all endpoints.
All vulnerabilities found are automatically assigned a severity rating based on the Common Vulnerability Scoring System (CVSS) standard. As well, vulnerabilities are tagged as “CISA recommended” if they are found in the Cybersecurity and Infrastructure Security Agency (CISA) managed catalog of known exploited vulnerabilities.
In Nebula, you have a few options for how you want to view found vulnerabilities:
Vulnerabilities page
On the left navigation menu, go to Monitor > Vulnerabilities to view vulnerabilities across your environment.
Endpoint page
On the Endpoints page, add a new column for a quick glance of the severity of CVEs for each endpoint. Hover over the diagram for a breakdown of vulnerabilities by severity.
Vulnerabilities tab
Navigate to the Vulnerabilities tab from Manage > Endpoints to view the vulnerabilities of a specific endpoint.
4. VA shares these findings with the Patch Management integration
Finding vulnerabilities, of course, is just one half of the battle.
After our free Vulnerability Assessment tool does its discovery work, our Patch Management module automatically imports the scan data and uses it to determine which patches and application updates need to be deployed.
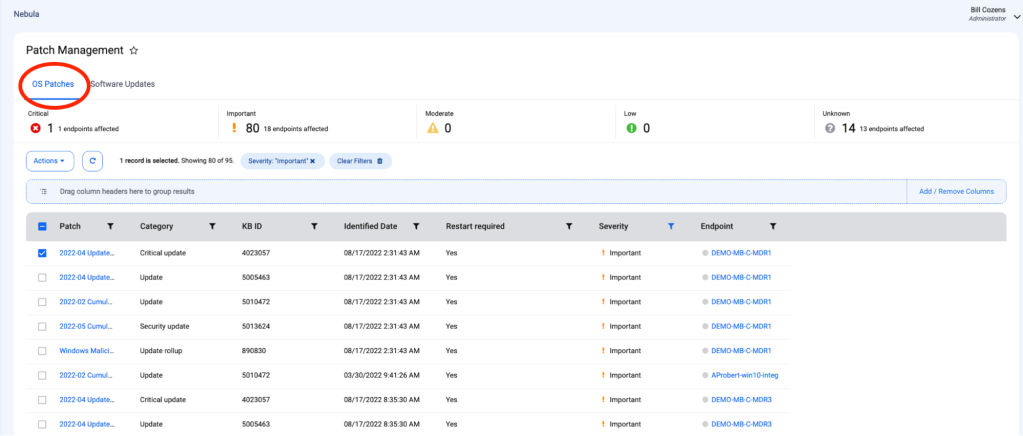
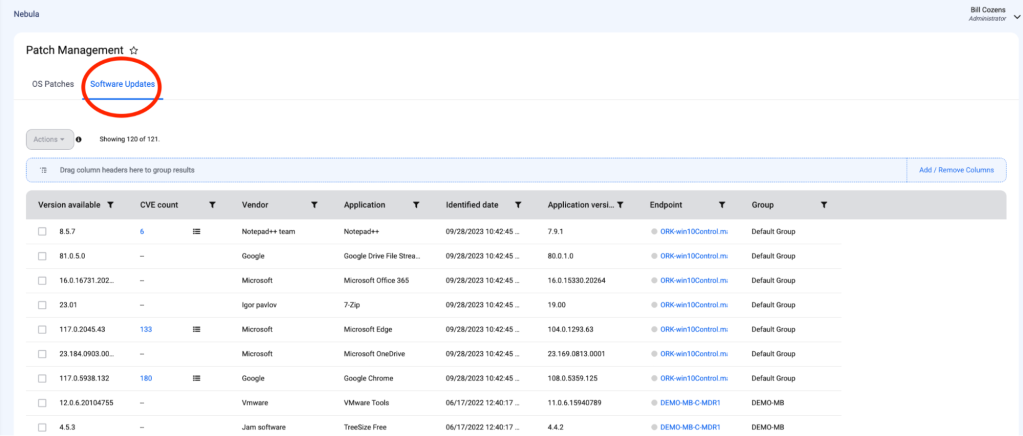
With Patch Management, you can apply two different types of patches: operating system patches and software patches. To view and install both OS and software patches across your environment, navigate to Monitor > Patch Management on the left navigation menu.
5. Patch Management automatically updates OS and third-party applications to the latest versions
To apply patches en masse, check the boxes for the systems or applications on endpoints you wish to update and click Actions > Update Software.
Bam, you’re done.
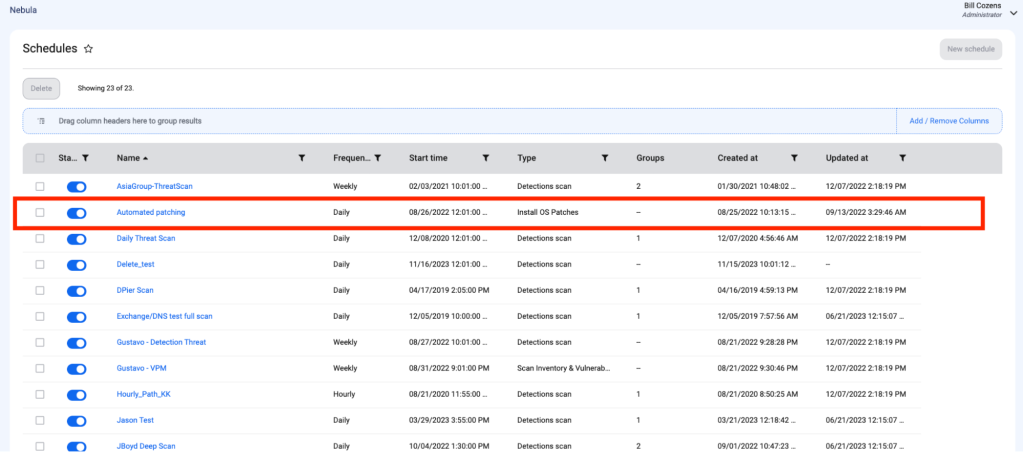
To help automate the patching process, you can create a schedule to install third-party software updates regularly. This schedule installs all system and third-party software updates found when the schedule is run.
Streamlining Vulnerability Response with ThreatDown
Managing vulnerabilities and patches yourself can be a pain. But, as we’ve broken down in this article, ThreatDown takes care of vulnerability management all from one console.
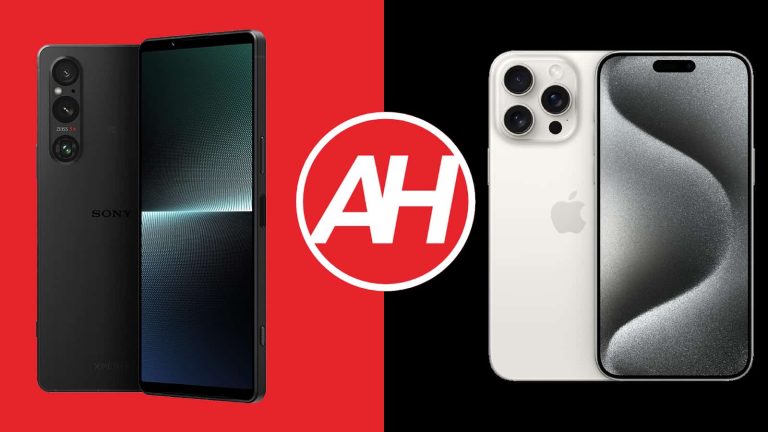
Both Sony and Apple released immensely compelling flagship smartphones this year. Sony’s launched in May and became available in July. Apple’s both launched and went on sale in September. Having said that, we’re here to compare the Sony Xperia 1 V vs Apple iPhone 15 Pro Max. If you’re in the market for a large flagship smartphone, with all the bells and whistles, these two phones are definitely worth checking out.
We’ll first list their specifications, as we usually do in comparisons. Following that, we’ll compare the two phones across several other categories. We’ll compare their designs, displays, performance, battery life and charging, cameras, and audio output as well. With that in mind, let’s get this going.
Specs
Sony Xperia 1 V vs Apple iPhone 15 Pro Max, respectively
Sony Xperia 1 V vs Apple iPhone 15 Pro Max: Design
The Sony Xperia 1 V and Apple iPhone 15 Pro Max are visibly different devices. They both do have a flat frame all around, but that’s basically where the similarities end. The Xperia 1 V has a flat display without a display camera hole or notch. It has slightly thicker bezels at the top and bottom, though. The iPhone 15 Pro Max, on the other hand, includes a flat display too, with thin, uniform bezels. However, it does also have a pill-shaped cutout in that display for the front-facing camera and facial scanning tech.
Both smartphones have three cameras on the back. The Xperia 1 V has three vertically aligned units, which are placed in the top-left corner. The iPhone 15 Pro Max has a recognizable camera setup on the back; the one Apple has been using for several generations. Those cameras also sit in the top-left corner. In addition to the power/lock and volume rocker keys, both smartphones do have an additional button. The Xperia 1 V has a shutter button on the right, while the iPhone 15 Pro Max has an Action Button on the left.
Despite the fact the Xperia 1 V has a smaller display, it is taller due to its aspect ratio. It is also considerably narrower than the iPhone 15 Pro Max, while being the same thickness as Apple’s device. The Xperia 1 V is also considerably lighter at 187 grams. The iPhone 15 Pro Max weighs 221 grams. Both smartphones offer an IP68 certification for water and dust resistance, which is always nice to see. They do feel different in the hand, though, but the premium aspect is easily noticeable on both.
Sony Xperia 1 V vs Apple iPhone 15 Pro Max: Display
There is a 6.5-inch 4K (3840 x 1644) OLED display included on the Sony Xperia 1 V. That display is flat, and it supports a 120Hz refresh rate. In addition to that, HDR content is also supported here. That panel has a 21:9 aspect ratio, and around 84.2-percent screen-to-body ratio. The display is protected by the Gorilla Glass Victus 2 from Corning.
The Apple iPhone 15 Pro Max, on the flip side, has a 6.7-inch 2796 x 1290 panel. That is a flat LTPO Super Retina XDR OLED display. That panel also has a 120Hz refresh rate, while it supports HDR10 content. Dolby Vision support is also a part of the package. This panel has a 19.5:9 aspect ratio, and an almost 90 percent screen-to-body ratio. This display gets up to 2,000 nits when it comes to brightness. It is protected by the Ceramic Shield Glass.
In all honesty, there’s not much to complain about when it comes to either of these two displays. They both offer vivid colors, deep blacks, and great viewing angles. The touch response is also quite good. The iPhone 15 Pro Max’s display does have the advantage of being a bit brighter, but the difference is not that big. The Xperia 1 V has a sharper panel, though you’ll be able to utilize 4K resolution only with 4K content. Not many people will notice the difference on a display of this size.
Sony Xperia 1 V vs Apple iPhone 15 Pro Max: Performance
Sony’s flagship is fueled by the Snapdragon 8 Gen 2 processor. That is Qualcomm’s second most powerful chip at the moment, it was the most powerful one until recently. The phone is also equipped with 12GB of LPDDR5X RAM, and UFS 4.0 flash storage. The iPhone 15 Pro Max, on the flip side, is fueled by the Apple A17 Pro chip. It includes 8GB of RAM, and NVMe flash storage.
Both of these chips are truly powerful, even though the Apple A17 Bionic does have the edge in terms of sheer performance power. The Xperia 1 V does have the edge in the RAM and storage departments, when it comes to sheer performance, that is. How does that reflect on a day-to-day performance, however? Well, both smartphones do a great job in that regard, to say the least.
They’re both perfectly smooth. They can handle anything you throw at them with ease. That goes for regular tasks, and even more complicated ones, such as gaming. No matter what game you dig up or how demanding it is, these two handsets can handle it. That’s not surprising, but it’s worth noting. They both do get quite warm during gaming sessions, but never too warm to handle.
Sony Xperia 1 V vs Apple iPhone 15 Pro Max: Battery
A 5,000mAh battery sits inside the Sony Xperia 1 V, while a 4,441mAh unit can be found inside the iPhone 15 Pro Max. Apple’s iPhones usually have smaller battery packs than their Android counterparts. That’s because they do work differently, and usually require less battery power to provide similar battery life. That being said, is the battery life any good on these two phones? Well, yes, it is, definitely.
From what we’ve seen, the iPhone 15 Pro Max does offer a bit more in that regard, but the difference is not that big. Getting over 8 hours of screen-on-time with the iPhone 15 Pro Max was perfectly doable for us. The phone lasted quite a bit once the initial struggles were over. The Xperia 1 V, on the other hand, can provide up to 7-7.5 hours of screen-on-time, presuming you’re not pushing it hard with gaming and so on. Your mileage could and will vary, of course. Each of us uses our phones differently, so we do get different results. What we can say, however, is that both of these phones offer great battery life, and not many people will have complaints.
When it comes to charging, Sony’s flagship supports 30W wired, 15W wireless, and 5W reverse wireless charging. The iPhone 15 Pro Max, on the other hand, supports 20W wired, 15W wireless (MagSafe and Qi2), and 7.5W Qi charging. 4.5W reverse wired charging is also supported here. Do note that neither phone comes with a charger in the box, though.
Sony Xperia 1 V vs Apple iPhone 15 Pro Max: Cameras
There are three cameras on the back of each of these two phones. The Sony Xperia 1 V includes a 48-megapixel main camera, a 12-megapixel ultrawide unit, and a 12-megapixel telephoto camera (3.5x-5.2x continuous optical zoom). The iPhone 15 Pro Max has a 48-megapixel main camera, a 12-megapixel ultrawide unit (120-degree FoV), and a 12-megapixel periscope telephoto camera (5x optical zoom).
Quite a few flagship smartphones this year were really compelling in the camera department, and these two are definitely close to the top. They both offer great camera performance in both still images and video. The iPhone 15 Pro Max does have the edge in the video department, while the situation with stills is a close battle and more a thing of preference than anything else. We’d say that the iPhone 15 Pro Max is still more consistent, even when it comes to stills, though.
Images from the iPhone 15 Pro Max are almost always spot on, and it’s one of the best point-and-shoot cameras out there (when it comes to phones). The Xperia 1 V is also a very good point-and-shoot camera, but its magic lies in its very capable camera apps. You can really dial in your shot to make it look perfect, if you’re so inclined. The two phones capture plenty of details during the day, while they also do an outstanding job in nighttime conditions too. Their secondary and tertiary cameras do a good job of following the main camera’s color science too.
Audio
Both phones are equipped with a set of stereo speakers, and both of them do a great job. The sound is plenty loud, and also very well-balanced. The iPhone 15 Pro Max technically provides a slightly louder output, but the difference is so minuscule that many of you wouldn’t even notice the difference.
The Xperia 1 V does have one advantage when it comes to wired audio, it includes a 3.5mm headphone jack. You’ll need to utilize the iPhone 15 Pro Max’s USB-C port in order to connect your headphones via a wired. Both smartphones are equipped with Bluetooth 5.3, however.