Samsung Galaxy S24+ 8GB variant might not exist

0
[ad_1]

It seems when the new Galaxy phones launch next year, there might not be a Samsung Galaxy S24+ 8GB variant for you to purchase. Consumers looking to upgrade to the newest Galaxy phones have been waiting for news about the latest offerings from Samsung. As such, many leaks and rumors have occurred as the hype builds up to Samsung’s official announcement. And it looks like Samsung is making a crucial change when it comes to RAM on its phones.

Leaked Galaxy S24 specs on X

X seems to be the place to find the latest rumors about Samsung’s upcoming devices. User Tech_Reve has made a name for themselves over the years; providing many leaks that turned out to be accurate. Tech_Reve has now leaked a chart on X detailing the different upcoming Galaxy S24 phone variants. This chart includes the Galaxy S24, the Galaxy S24+, and the Galaxy S24 Ultra.

If the chart is accurate, then only the base Galaxy S24 will have 8 GBs of RAM. Both the S24+ and the S24 Ultra will only feature 12 Gigs of RAM. This indicates a very welcome, if slightly unexpected, shift to higher RAM being standardized by Samsung. If the industry follows suit, and they often do, this could mean pretty soon it would only be budget phones that have 8 GBs of RAM.

Memory configurations and color options

On the chart Tech_Reve leaked we could see what configurations and colors the new phones will be launching with. The base Samsung Galaxy S24 will have 8 GBs of RAM and a choice between 128 GBs or 256 GBs of storage. There might not be a Samsung Galaxy S24+ 8GB phone, but the S24+ does offer 256 GB and 512 GB storage options alongside its 12 Gigs of RAM. Lastly, the S24 Ultra is the best of the best and has 256 GBs, 512 GBs, and a terabyte of storage along with 12 GBs of RAM.

We also got a look at the colors these phones will be launching with. Naturally, we’ve got the standard black and gray options. Those will probably sell quite well. But we also have some less popular colors; violet and yellow. It is unknown at the moment if these four are the only colors Samsung will offer. There might be more not shown in the leak. Violet might turn out to be a fan favorite if implemented properly, and some people will definitely be wanting a bright yellow phone.

Samsung is expected to announce its new phones in January of next year, maybe as soon as less than a month from now. We’ll get a more in-depth look then, and cover the new exciting details that emerge.


[ad_2]
Source link

Mortgage Giant Mr. Cooper Data Breach; 14 Million Users Impacted

0
[ad_1]

Initially, the data breach was thought to affect only 4.3 million current customers, but now the impact has extended to an additional 10 million.

In a new cybersecurity incident, Coppell, Texas-based mortgage and loan giant Mr. Cooper has become the latest victim of a cyberattack that may have compromised the sensitive personal information of more than 14 million individuals, impacting both current and former customers.

The company, in its data breach notifications to state and federal regulators, disclosed that the incident initially thought to affect 4.3 million current customers now extends its reach to an additional 10 million past customers.

The severity of the situation prompted the company to file a data breach notification with the Maine Attorney General, revealing that a staggering total of 14,690,284 individuals could be affected, with 59,917 of them being residents of Maine.

The data breach came to light in early November 2023, when Mr. Cooper announced that it had fallen victim to a cyberattack on October 30, 2023. The breach, discovered the following day, prompted the company to take swift and decisive action by shutting down all IT systems. This included the temporary closure of the online payment portal, a vital platform used by customers to manage their loan and mortgage payments.

The company is now actively engaged in investigating the extent of the breach and has begun the process of notifying affected individuals. The compromised data is said to include sensitive personal information such as names, email addresses and personal identifiers in combination with Social Security Numbers (SSN), raising concerns about the potential misuse and identity theft implications for the affected customers.

Mortgage Giant Mr. Cooper Data Breach; 14 Million Users Impacted
Mr. Cooper has launched a dedicated website to keep impacted customers updated on the data breach. (Screenshot: Hackread.com)

However, Mr. Cooper assures its customers that it is working to enhance its cybersecurity measures to prevent any future breaches. In the meantime, affected individuals are encouraged to remain alert, monitor their financial accounts, and take necessary precautions to safeguard their personal information.

In a comment to Hackread.com, Claude Mandy, Chief Evangelist of Data Security at Symmetry Systems highlighted the challenge organizations face with data retention due to legal requirements and business aspirations. Despite the desire to use data for analytics and customer re-engagement, data often remains untouched, leading to breaches that impact both current and past customers.

“Unfortunately, a lot of organizations are stuck between a rock and a hard place, when it comes to the retention of data. Various laws and legislature require organizations to keep records for over 7 years, but they also hope to attract their past customers back into the fold and plan to leverage it to develop future analytics insights. In reality, this data just lies untouched where it lies, often long past their actual retention policies. Regardless of the reason, it is not unusual to see breaches impacting not only current customers but previous customers too.“

Mandy emphasizes the importance of proactive data management, citing an example where Symmetry Systems enabled a Fortune 100 organization to delete 25% of their cloud assets without business impact. Additionally, he notes that the absence of credit card numbers in Mr. Cooper’s breach may suggest the use of outsourced payment providers that tokenize credit card information for enhanced security.

“Increasingly our customers with the help of our data-centric monitoring, identify and proactively delete data beyond its retention lifecycle, and further reduce access to sensitive data in a manner commensurate with its actual usage and sensitivity. In one example, we enabled a Fortune 100 organization on Google Cloud to delete over 25% of their cloud assets such as Projects, Identities, and production data without any business impact.“

“The lack of credit card numbers in the breach notification isn’t exceptionally notable given that Mr Cooper doesn’t offer credit card facilities to its customers, and mortgage companies generally restrict credit card payments for mortgages. For other organizations that do, this may be a sign that they are leveraging an outsourced payment provider that tokenizes (i.e. replaces with a token) credit card numbers to secure them.“

The announcement of the data breach at Mr. Cooper came just days after Delta Dental, a dental insurance provider based in Oak Brook, Illinois, United States, revealed that it had experienced a data breach affecting 7 million customers.

Nevertheless, impacted individuals are urged to be watchful for phishing emails that may falsely claim to originate from the company, claiming to provide new updates. However, the actual motive could be to exploit the situation and attempt to steal user data.

  1. Sensitive Data of 123 Million American Households Exposed​
  2. Hackers Claim Major Data Breach at Smart WiFi Provider Plume
  3. Mortgage Broker 8Twelve Exposes Data of Canadian Residents
  4. Sony Data Breach via MOVEit Vulnerability Affects Thousands in US
  5. Cybercriminals Selling Social Security Numbers of Infants on Dark Web

[ad_2]
Source link

Google Photos media could soon be accessible via Android’s new Photo Picker

0
[ad_1]
Android 13‘s Photo Picker was a breath of fresh air for privacy-conscious users. Unlike the all-or-nothing access of app-specific pickers, it granted granular control over what photos and videos you share. But its usefulness was limited – your local library was all it knew. However, good news is on the horizon, with cloud media providers like Google Photos finally preparing to join the party.
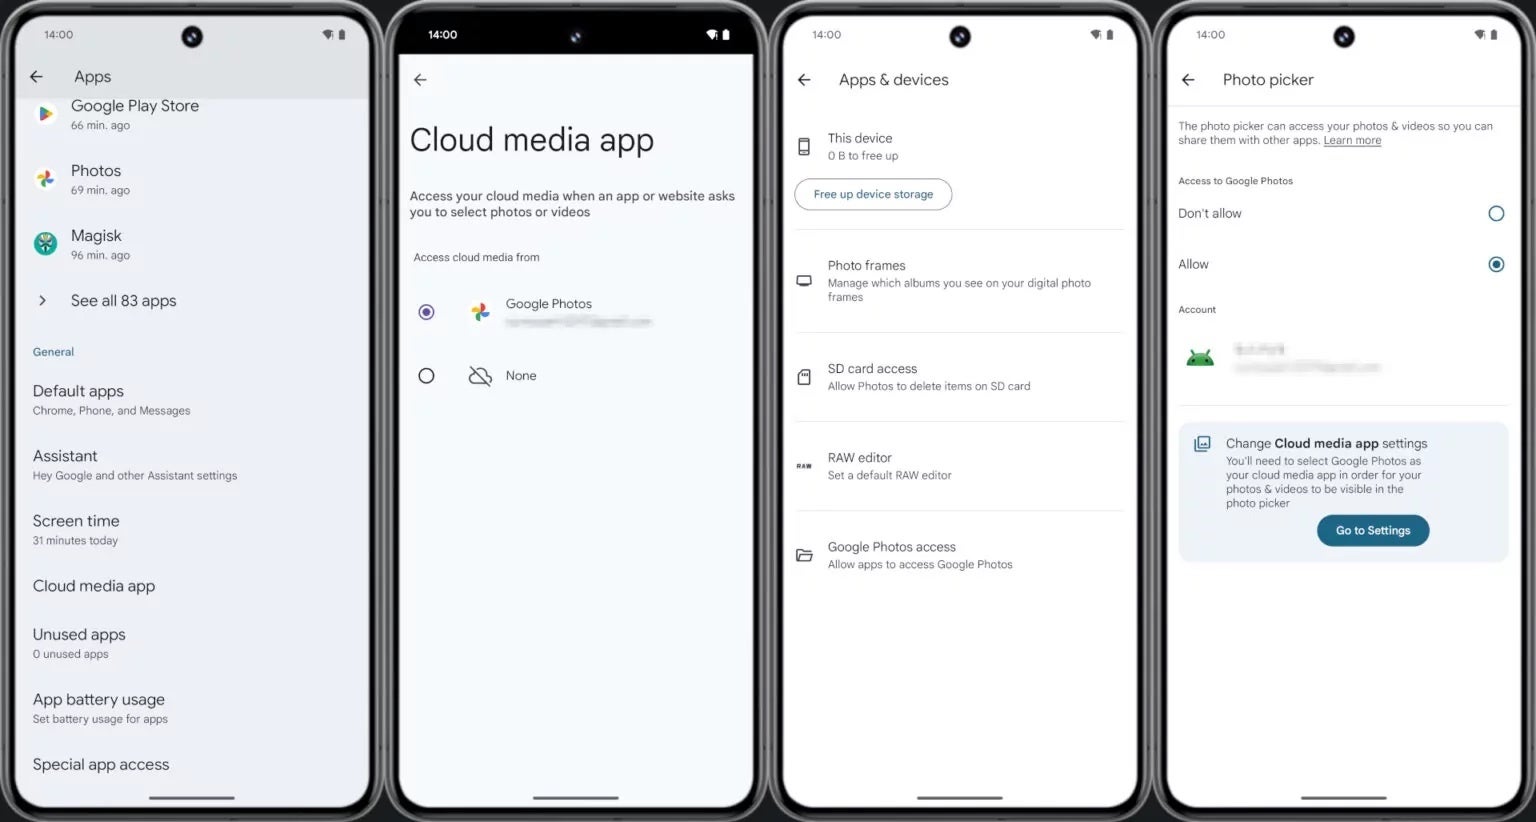
As spotted by Android Authority, recent Google Photos updates reveal full support for the Photo Picker for cloud support. Activating this feature via a hidden flag opens a new “Cloud media app” page in settings, where you can enable Google Photos. This, in turn, unlocks a “Google Photos access” option within the Photos app, letting you grant the Photo Picker permission to your cloud library.

This functionality was announced during Google I/O 2022 and has since then been recently added to apps like Google Keep, Google Chat, and Google Messages on devices running Android 11 with the November 2023 Google Play system update. However, adoption outside of Google’s own apps requires app developers to implement the API, and adoption has been slow.


Now, with the addition of Google Photos, and hopefully the wider rollout of this feature, developers might now be encouraged to adopt the Photo Picker, giving users unparalleled control over their shared memories. Hopefully, with Google Photos paving the way, other cloud providers like Microsoft OneDrive will follow suit, creating a truly universal and privacy-respecting sharing experience on Android.

As great as this all sounds, there are still some issues that need to be worked out with the Photo Picker. For example, as noted by Android expert, Mishaal Rahman, app-created albums like Snapseed’s remain hidden in the “Photos” tab, absent from “Albums.” Additionally, he’s found that cloud media doesn’t appear in the new Android 14 permission dialog for partial access.

Yet, these are minor hiccups in a major step forward. The hope is that other cloud providers will see the benefit of using the Photo Picker and begin to have their app developers implement the changes necessary to turn this feature on for them. Google has already taken the first step to make this happen.


[ad_2]
Source link

Google Calendar may soon add scrollable Month Navigation Chips

0
[ad_1]

Google Calendar is likely to receive a notable improvement in user navigation with the introduction of scrollable Month Navigation Chips. This feature aims to simplify the process of moving between months, providing users with a more efficient and user-friendly experience.

When users click on a month displayed in the top bar, a table of calendar days unfolds, allowing for left and right scrolling to switch between months. The new addition of scrollable Month Navigation Chips directly below this table brings an extra layer of convenience. This feature enables users to easily locate a specific month and swiftly transition to it.

The implementation of scrollable chips in the calendar app is part of Google’s ongoing effort to refine the user interface of its Android apps. Over the past couple of years, the company has introduced similar chip-focused design changes in applications like Google Contacts and Chat. Now, Google is extending this approach to the Calendar app, enhancing the overall usability of the platform.

Month Navigation Chips in Google Calendar appear to take only a little space while letting you quickly switch months

The (unofficial) Google News Telegram channel shared insights into this development, describing the new feature as a row of scrollable month navigation chips underneath the calendar table. While the current version of Google Calendar allows users to scroll through months horizontally, the addition of these chips further streamlines the process, making it more intuitive and time-saving.

Although this insight from Google News doesn’t include the exact version of Google Calendar that incorporates this change, it mentioned that the feature is currently concealed behind a flag. The provided screenshot of the updated UI suggests that the addition of horizontal chips does not significantly impact the Schedule view on the Calendar app.

While there is no precise information on when this refined design will be widely available to Calendar users, the existence of the feature behind a hidden flag indicates ongoing development. Users may need to wait for an official rollout, but the prospect of an improved navigation experience makes it a feature worth anticipating.

Month Navigation Chips in Google Calendar


[ad_2]
Source link

Apple quietly patches Flipper Zero exploit crashing iPhones

0
[ad_1]

iPhones can no longer be forced to crash with Flipper Zero tools, after an iOS 17.2 software update appears to have quashed the vulnerability. The patch was first reported by ZDNet, and later confirmed by 9to5Mac in further tests. For those unfamiliar, the Flipper Zero device is a pen-testing tool that can be as harmless or harmful as you make it. The tool won’t do any damage out of the box, but it can be used for nefarious purposes, which is why Amazon banned it earlier this year. After loading it up with third-party software, you can do a lot with the Flipper Zero, including disrupt iPhone users until a few days ago.

The Flipper Zero exploit was more of a prank than an actual security vulnerability, but it’s easy to see why Apple wanted the issue fixed for good. With the testing device, someone could use Bluetooth to send seemingly-endless connection notifications to a nearby iPhone. This extreme amount of connection requests would lock up an iPhone, causing it to crash. Essentially, it’s a simple denial-of-service (DoS) attack that overwhelms iOS will so many notifications that it forces a reboot. Though it’s basically harmless, it can be extremely frustrating to be on the wrong end of. And provided you needed your smartphone in an emergency, this DoS attack would have higher stakes.

Now, iPhone users won’t have to worry, as long as they’ve updated to iOS 17.2. Apple seeded the update on Dec. 12, so most users should already have the update by now. However, you can check to make sure your iPhone is up-to-date by heading to Settings > General > Software Update. The fix did take a while, since the Flipper Zero attack was first discovered in September.

Can the Flipper Zero still bother iPhone users?

Although the crashes and forced reboots are no longer an issue, the underlying vulnerability is still somewhat present. The Flipper Zero testing tool can send a few Bluetooth connection notifications to nearby iPhones, but not enough to send them into a loop. So, the Flipper Zero can be used to annoy people, but it won’t perform a DoS attack anymore. To be fair, there’s nothing more Apple can do to prevent Flipper Zero from connecting without also blocking valid Bluetooth devices as well.

Part of the reason the Flipper Zero is so effective is that it can be used at range. The pen testing tool can interact with devices from between 30 and 50 feet away, which is quite a bit of distance. If you’re in a big crowd, it would be hard to figure out who is messing with your devices. Luckily, that isn’t a worry for iOS 17.2 users anymore.


[ad_2]
Source link

YouTube changes TV ad experience with longer, but fewer breaks

0
[ad_1]

In the highly competitive landscape of streaming services, YouTube has maintained its position as the most-watched platform in the United States for almost a year, according to Nielsen. Recognizing the evolving preferences of viewers and the need for a seamless experience, YouTube is rolling out a significant update for connected TVs to enhance the streaming experience for its users and advertisers.

Users will see fewer, but longer ad breaks during long-form content on TV screens. Catering to the preference of 79% of viewers who favor grouped video ads, YouTube aims to create a more cohesive viewing experience. In early tests on connected TVs, over half of YouTube CTV streamers experienced a remarkable 29% longer viewing session before encountering the next ad break. This change is set to be implemented globally, ensuring users worldwide can enjoy extended content without frequent interruptions.

YouTube also focuses on users’ ad experience alongside the revenue from it

Moreover, YouTube is addressing viewer preferences regarding ad break information. Research indicates that a majority of viewers prefer knowing the total time remaining in an ad break rather than the number of ads remaining. In response, YouTube will now display the time left until the ad break ends, providing users with more transparency and control over their viewing experience.

In addition to optimizing ad breaks, YouTube has expanded its Shorts experience to connected TVs. Following a surge in viewership, with global views of YouTube Shorts on connected TVs growing by over 100% from January to September 2023, Shorts ads will now be available globally on CTVs. Advertisers can seamlessly incorporate Shorts ads into their campaigns, ensuring a consistent viewer experience across both mobile and TV screens.

This move from YouTube comes after its efforts to convince users to disable their ad blockers. It explains the platform’s focus on the user experience besides their revenue from ads. Users can expect longer but fewer interruptions in long-form content on their TVs soon.


[ad_2]
Source link

TikTok now looks so much better on your foldable phone

0
[ad_1]

If you’re one of the maniacs who watch TikToks on a tablet, your life is about to get better. Obviously, TikTok is an app that’s meant to be viewed on phone-sized screens, but your phone isn’t always around. TikTok just announced that it’s making the app work much better on larger screens.

Larger screens are getting more attention nowadays because of the rise in the foldable phone market. Thanks to companies like Samsung, Motorola, Vivo, Oppo, Google, etc. foldable phones are all the rage in the tech industry despite a diminishing economy. This is why we’re seeing more apps change their DNA to work on larger screens.

TikTok now works better on larger screens

Making vertical videos look good on a large screen requires some compromises, but ByteDance, the company that owns TikTok, did a good job with its implementation. When you view your videos on larger devices, the company says that you’ll see the videos in higher quality. That’s important if the videos are going to be stretched over a larger canvas.

Your video will sit in the middle of the screen with UI elements on either side of it. The right side will have the “Like”, comment, bookmark, share, and video audio buttons. This is what you see on smaller screens as well However, unlike with smaller screens, these elements don’t overlap the video. They sit in their own letterbox on the right of the video.

TikTok on larger screens

This goes for information on the left of the screen to an extent. On the left side, you’ll see the video’s description. If your device is in landscape orientation, then the description most likely won’t overlap the video. However, in portrait orientation, it looks like the description will overlap the video just a bit.

You’ll also see the navigation bars on the top and bottom of the screen just like with smaller screens. So, in essence, the app didn’t really make too big of a change. However, it was effective, and it enhances the overall experience.


[ad_2]
Source link

How Google Bard and Gemini are different

0
[ad_1]

AI AI AI, that’s all we hear about nowadays. There are several different flavors of artificial intelligence on the market with Google, OpenAI, Microsoft, Anthropic, and other chefs dishing them out. To the common user, it can be tough to differentiate between the products that are sprouting. Thus, many people don’t know fundamental information like how Google’s Bard and Gemini are different.

It might not mean much to the average user looking to AI for casual tasks. However, if you’re looking to have a deeper understanding of the fundamentals of AI, then this is information that you’ll want to learn. Knowing how Bard and Gemini are different will also help you know more about other AI products like OpenAI’s ChatGPE and GPT-4. So, here’s a handy rundown of how these are all different.

What is Bard?

Google launched Bard back in March of 2021. It’s a chatbot that’s meant to take on the likes of ChatGPT. So, that’s the interface that you interact with. You’re able to enter text-based prompts and get results based on them. You’re also able to input images to get text-based responses from the bot. Imagine it as the face of a person. You directly interact with a person to their face, and that’s where you get your responses. 

What is Gemini?

If you’re still unfamiliar with what Google’s Gemini is, here’s a quick rundown (we also have more information if you want to know everything you need to know about Gemini). Google launched Gemini on December 6th, 2023. It’s a multimodal model, which means that it can accept more than one form of media. So, if you want to feed it images, it’s able to understand what’s present in that image. Google says that Gemini can understand text, images, video, and audio.

Versions of Gemini

The company launched Gemini in three different sizes. The smallest version is called Gemini Nano, and this is designed to live on devices. It’s actually powering some AI tools on the Pixel 8 Pro. As you can imagine, this isn’t as powerful as the other versions, but it makes the Pixel 8 Pro one of the smartest phones on the market.

The next size up is Gemini Pro. This is what’s powering Bard. Gemini pro provides more power over the model that previously powered Bard, and it could be very useful for individual developers and smaller companies. In fact, Gemini Pro is currently available for developers to use. At the time of writing this article, it’s free to use, but this is only a limited-time trial.

Lastly, the largest size is called Gemini Ultra. This version, as of the time of writing this article, is not available. When it launches, it will be for large enterprise applications. The two smaller versions are only able to output text as their responses like ChatGPT. However, Gemini Ultra is expected to be able to output different forms of media like text, music, and images. At the moment, we’re not sure how Google is going to implement this, but we’re certain that it will come with a price tag. Gemini Ultra is slated to come out sometime in early 2024. We expect it to come out before the end of January.

How Bard and Gemini are different

It must have been confusing hearing that Gemini was coming out. This put into question what the company was planning on doing with Bard. Was it going to have both of them coexist? Is Bard on its way out? This got more confusing when we found out that Bard was being powered by Gemini. However, this is why it’s important to know what Bard and Gemini are because they’re not the same thing.

As stated, Bard is the chatbot. Gemini, on the other hand, is not a chatbot; it’s what’s called the “Model”. If Bard is the face of a person, then Gemini is the brain. You, undoubtedly, heard about companies scraping data from around the internet to train models. Well, all of the data from the internet goes right into the model; that’s what’s being trained.

When Google is scraping data from the internet, it feeds it into Gemini so that it gets smarter. When you use Bard, it taps into the Gemini model to receive its information.

Pixel 8 Pro and Gemini

A model doesn’t need to be tied to a model to be functional. Let’s use the Pixel 8 Pro as an example. The chip powering this phone, the Tensor G3, has Gemini Nano implemented on it. This powers some powerful AI tools on the phone, but the tools aren’t necessarily associated with a chatbot.

The Pixel Recorder app uses AI to transcribe audio recordings. When it uses that feature, the app taps the Gemini model present on the chip to decipher the text in the audio recordings. So, in this case, the Pixel Recorder app plays the role of the chatbot. The Pixel Recorder is the interface that you interact with directly.

Another example is OpenAI’s products

If you’ve been in the loop with AI products, you’ve been hearing about ChatGPT, GPT-3.5, and GPT-4. Again, many people might be confused about what all of these are. Well, ChatGPT is the equivalent of Bard. It’s the chatbot that you interact with.

GPT-3.5 is the model that powers the chatbot. What’s the difference between GPT-3.5 and GPT-4? Well, if you’re a free ChatGPT user, then the chatbot you’re using is powered by GPT-3.5. This is a powerful model, but it’s not as powerful as GPT-4. That’s the larger and more advanced model.

Think of it as a bigger brain. and it powers ChatGPT if you’re subscribed to ChatGPT Plus. This is the company’s $20/month subscription plan that offers more perks than the free plan. Using GPT-4, you’re also able to use images as input, which is not present with ChatGPT.
[ad_2]
Source link

Lawmakers demand Apple be investigated for Antitrust violations after shutting Beeper Mini

0
[ad_1]

Apple’s decided a little over a week ago to put the kibosh on the Beeper Mini app that was allowing Android users to use iMessage and become a “blue bubble” on iOS. Let’s be real though, it isn’t just the color of the bubble that’s at stake here. With access to iMessage, Android users don’t have to chat with their iPhone totin’ pals, family, and fellow workers over the antiquated SMS platform.
When an Android user messages an iPhone user, the images and video shared are of poor quality, there is no end-to-end encryption, no read receipts, no typing indicators, and of course, the text bubbles are green. Apple already announced that sometime next year, it will support RCS and most of these great features will work on cross-platform chats between iOS and Android users. The latter group will have to have an RCS-enabled app like Google Messages installed.
For now, though, Apple is willing to protect iMessage, a feature it cites as a selling point for the iPhone. That alone explains why Apple had been so unwilling to add RCS support. And while it might be part of the reason why Apple shut down Beeper Mini, some lawmakers are not happy with Apple for taking this action. In addition to Senator Elizabeth Warren, who quickly knocked Apple and called the company anticompetitive, a group of bipartisan lawmakers sent a letter to Assistant Attorney General Jonathan Kanter complaining about Apple’s actions.

After explaining that to keep markets in the U.S. free and open, the Antitrust Division must be able to “police abuses of market power.” The letter then explains what happened and notes that “Apple executives have previously admitted the company leverages iMessage to lock users into Apple’s ecosystem of devices and services. Beeper Mini threatened to reduce this leverage creating [a] more competitive mobile applications market, which in turn a more competitive mobile device market.”

The letter also cites a report from the Department of Commerce called “Competition in the Mobile Application Ecosystem.” The report calls Apple a “gatekeeper” with a “mobile app ecosystem” The end of the letter mentions that the four lawmakers who affixed their signatures to the latter are concerned that Apple’s recent actions to disable Beeper Mini harm competition while hurting consumers “and will discourage future innovation and invention in interoperable messaging services.”

The lawmakers are referring the matter to the Antitrust Division to investigate whether Apple violated antitrust law.


[ad_2]
Source link

Disruptions at 70% of Iran’s Gas Stations Blamed on Cyberattack

0
[ad_1]

The responsibility for the attack has been claimed by Gonjeshke Darande,” (which means Predatory Sparrow in Persian), a hacker group with pro-Israeli sentiments.

A hacking group linked to Israel has claimed responsibility for a cyberattack that reportedly disrupted most gas stations in Iran, leading to long lines and angry crowds. The group, known as “Gonjeshke Darande,” (which means Predatory Sparrow in Persian) cited that the attack was in response to the Islamic Republic’s aggression.

In a series of Tweets on X (formerly Twitter) in both English and Persian languages, the group explained the reason behind the attack:

“We, Gonjeshke Darande, carried out another cyberattack today, taking out a majority of the gas pumps throughout Iran. This cyberattack comes in response to the aggression of the Islamic Republic and its proxies in the region.”

Addressing Iran’s leader Ayatollah Ali Khamenei, the group said he is playing with fire and will pay the price.

“Khamenei, playing with fire has a price.”

In a statement given to Iran’s state TV, the country’s Oil Minister Javed Owji, said that the attack was caused by external interference and led to service disruption on 70% of Iran’s gas stations. At least 30% of Iran’s gas stations are operational, with the rest gradually resolving service disruptions.

Some petrol stations, particularly in the capital, have experienced software issues with their fuel systems, and experts are working to fix the issue. The possibility of a cyberattack is also being considered.

Gonjeshke Darande revealed that the attack was conducted in a controlled manner, limiting potential damage to emergency services and ensuring a portion of gas stations were left unharmed. The group also emphasized the precautions taken to avoid harm to civilians, claiming that these companies are subject to international sanctions and continue their operations despite restrictions.

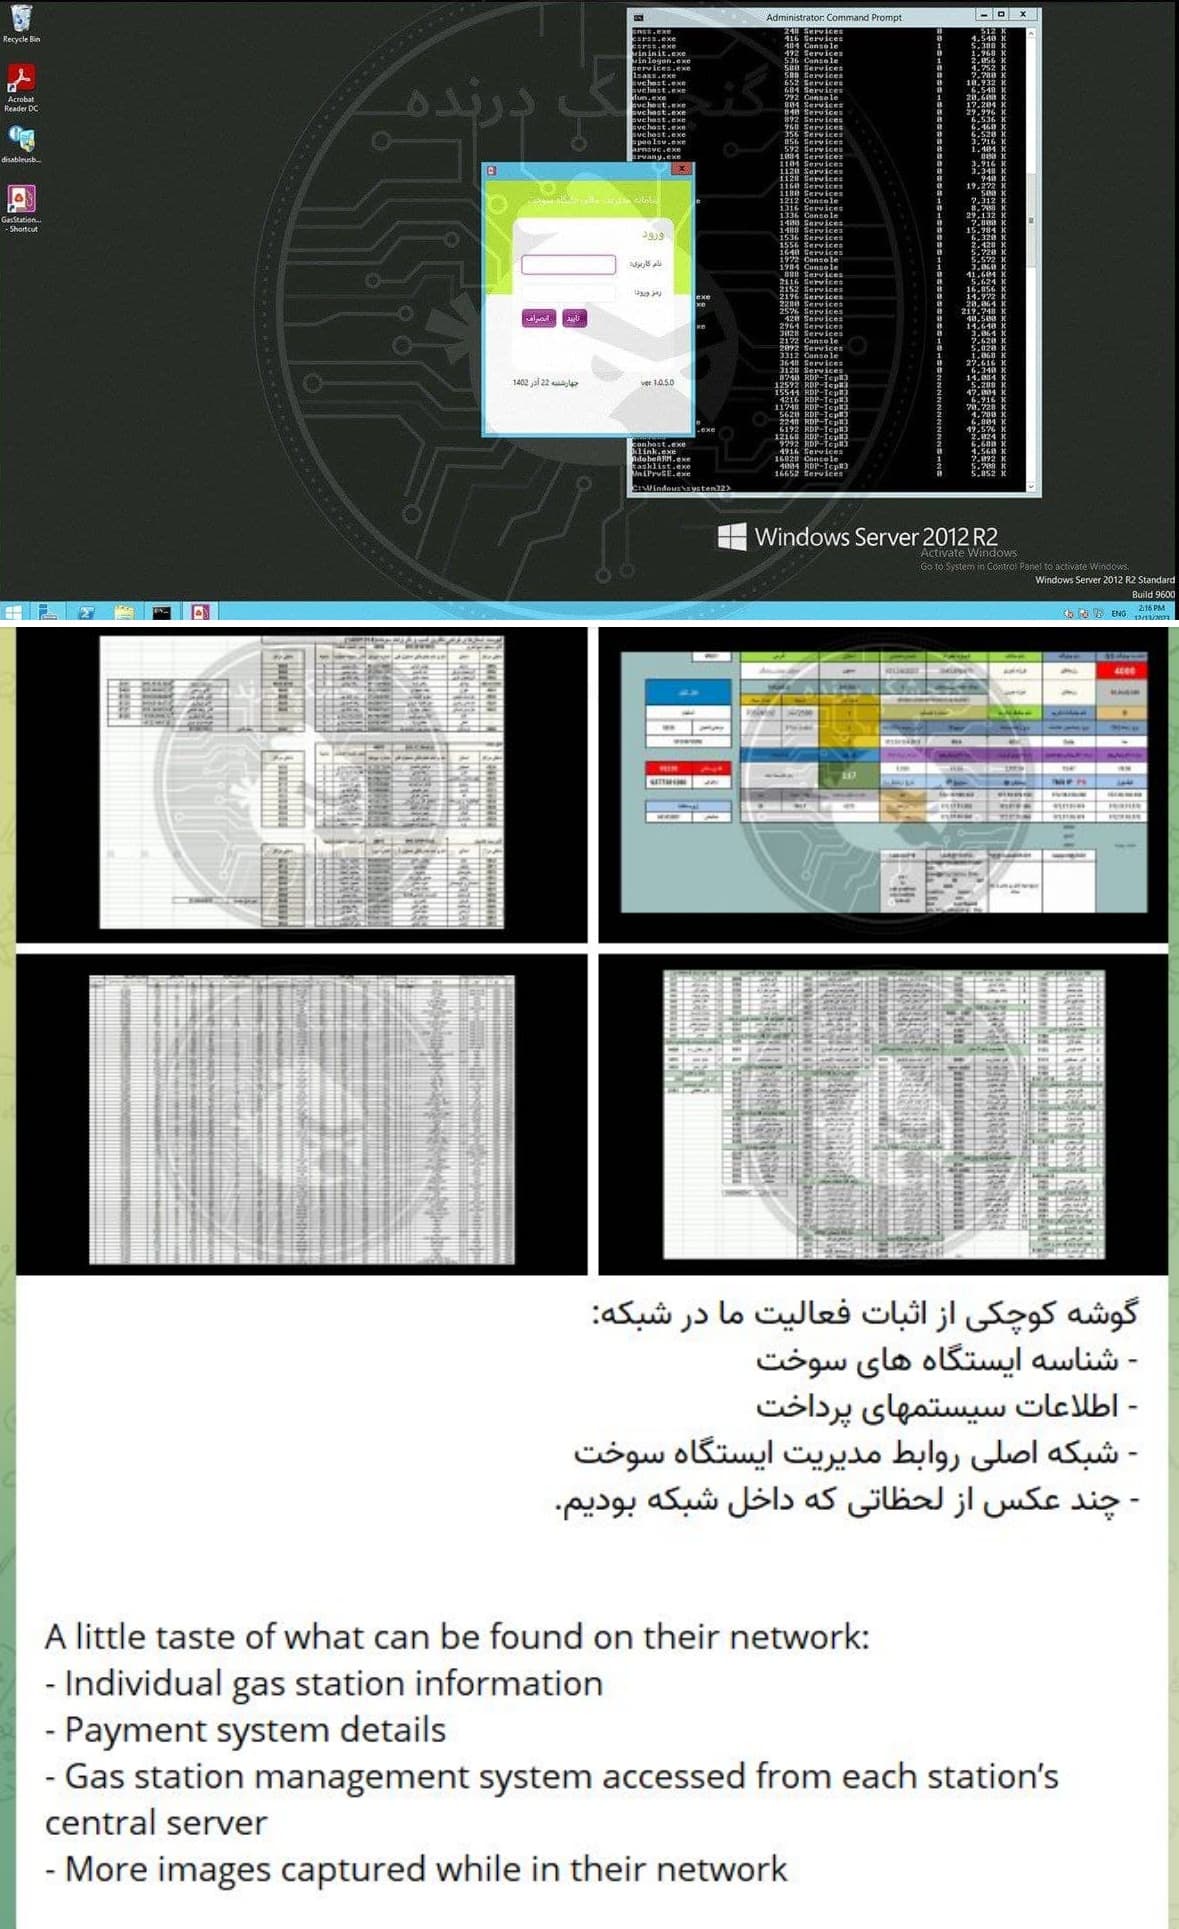
Screenshot from the Telegram channel of the Gonjeshke Darande group (Credit: Hackread.com)

“We delivered warnings to emergency services across the country before the operation began, and ensured a portion of the gas stations across the country were left unharmed for the same reason, despite our access and capability to completely disrupt their operation,” the attackers noted.

This isn’t the first time Gonjeshke Darande has targeted Iranian infrastructure. It claimed responsibility for a cyberattack on Iran’s major steel companies in June 2022. The attack started a fire in a steel factory, releasing top secret documents proving the companies’ affiliation with Iran’s Revolutionary Guard Corps. The plant’s CEO confirmed no harm

The country’s civil defence agency is currently investigating the Monday attack on Iran’s gas stations, and Israeli media has covered the alleged attack. It is worth noting that there has been no statement from the Israeli government about the cyberattack.

  1. Iranian Gas Stations Crippled After Suffering Cyberattack
  2. Watch as hackers disrupt Iran’s prison computers; leak live footage
  3. Anonymous Hits Iranian State Sites, Hacks Over 300 CCTV Cameras
  4. Iran State-Run TV’s Live Transmission Hacked by Edalate Ali Hackers
  5. Iranian State TV Hacked During President’s Speech on Revolution Day
  6. Iran’s Fars News Agency website hacked as part of anti-govt protests
  7. Black Reward Hackers Steal Emails from Iran’s Atomic Energy Agency

[ad_2]
Source link