Spanish Police Nab Venezuelan Leader of Kelvin Security Hacker Group

0
[ad_1]

The Kelvin Security Hacker Group stands accused of conducting 300 high-profile cyber attacks over the last three years, targeting strategic sectors in 90+ countries.

In an announcement on December 10, 2023, the Spanish National Police in Alicante city revealed the arrest of the alleged leader of the financial arm of ‘Kelvin Security,’ a notorious hacking group.

Identified as a Venezuelan citizen, apparently, under the suspect’s leadership, the Kelvin Security group was involved in over 300 high-profile cyber attacks spanning the last three years, targeting strategic sectors in more than 90 countries.
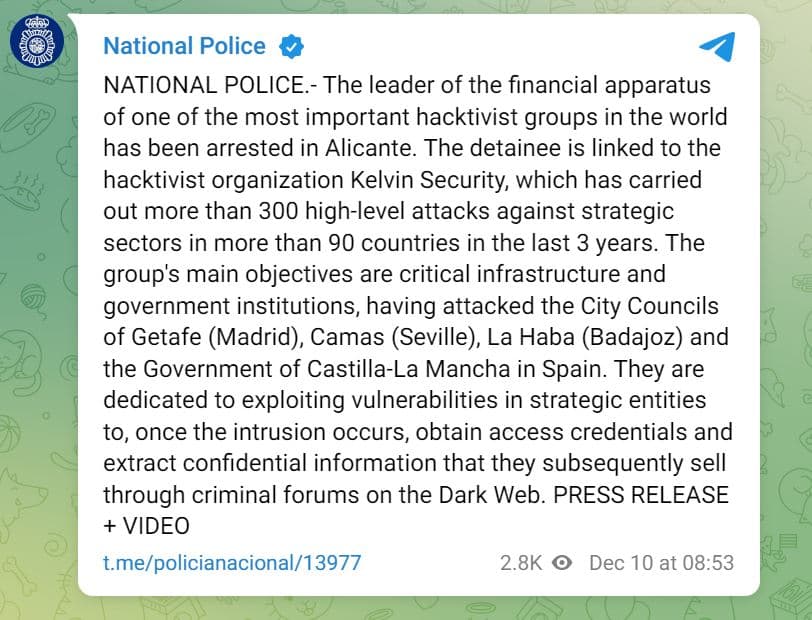
Leader of Kelvin Security Hacker Group Arrested in Spain
Spanish Police on Telegram (Translation by Hackread.com)

The group’s modus operandi involved exploiting vulnerabilities in strategic entities to gain access credentials and extract confidential information. Subsequently, they traded this sensitive data on various cybercrime, hacking and dark web forums.

The arrested Venezuelan individual now faces charges including membership in a criminal organization, disclosure of secrets, computer damage, and money laundering. He is believed to be the central figure responsible for laundering funds obtained through the group’s illicit activities, primarily utilizing cryptocurrency exchanges.

The investigation initiated two years ago, originated from sophisticated cyber attacks on the computer systems of Spanish municipalities Getafe and Camas. Cyber investigation experts traced these attacks back to the cybercrime forums operated by the ‘Kelvin Security group on the dark web.

Exploiting vulnerabilities in websites, software, and information storage services, the group systematically extracted sensitive data from institutions and entities in strategic sectors globally. Their latest known attack occurred in November 2023, when they exfiltrated a database containing confidential information of over 85,000 customers from an energy company.

The apprehension of the suspected leader of the Kelvin Security hacker group underscores the determination of cybercriminals to conceal their tracks, yet authorities consistently stay one step ahead.

  1. Owner of Breach Forums Pompompurin Arrested in New York
  2. Alcasec Hacker, aka “Robin Hood of Spanish Hackers,” Arrested
  3. Ragnar Locker Ransomware Gang Dismantled, Key Suspect Arrested
  4. Operator of Major Proxy Botnet ‘IPStorm’ Arrested, Pleads Guilty in US
  5. Multimillion-Dollar Vishing Scam Busted: Czech-Ukrainian Gang Arrested
  6. Senior OPERA1ER Cybercrime Gang Member Arrested in Global Operation

[ad_2]
Source link
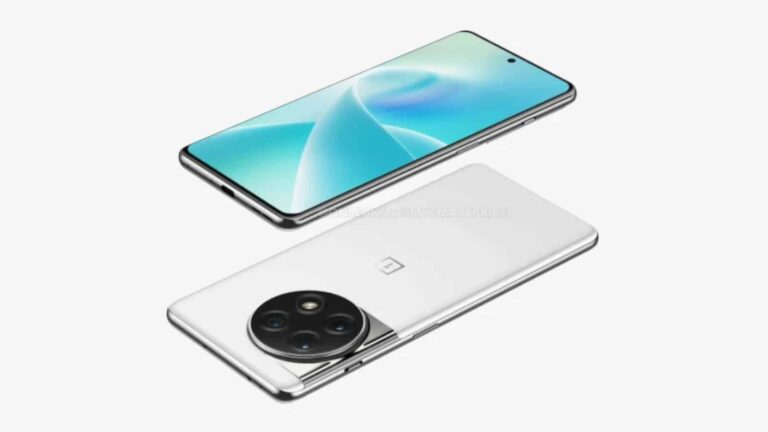
OnePlus 12R camera specifications leaked ahead of launch

0
[ad_1]

OnePlus launched its latest flagship smartphone, the OnePlus 12, in China earlier this month. It is set to debut in the global markets next month alongside other products. These are expected to include the OnePlus 12R, OnePlus Buds 3, and OnePlus Watch. Now, the OnePlus 12R’s camera specifications have been leaked ahead of launch. The upcoming budget flagship will arrive as a rebadged version of the China-limited OnePlus Ace 3.

OnePlus 12R camera specifications leaked

As per tipster Yogesh Brar, the OnePlus 12R will have a triple rear camera package. The setup will comprise of a 50MP 1/1.56-inch Sony IMX890 primary sensor with f/1.8 and 24mm focal length. It will also support OIS.

There will be an 8MP Sony IMX355 ultra-wide-angle with 16mm focal length and 112-degree field of view. The telephoto lens will utilize a 32MP Sony IMX709 sensor with f/2.0 aperture and a 2x optical zoom. The smartphone is said to be capable of recording up to 4K videos at 60fps.

Going by the new leak, it looks like the OnePlus 12R will retain the same primary and ultra-wide cameras as its predecessor. The third unit will be a telephoto lens compared to a 2MP macro on the OnePlus 11R.

OnePlus 12R camera specs

The OnePlus 12R has already been spotted in leaked renders previously revealing a slightly curved display with a center-aligned punch-hole cutout and a half-pill-shaped island housing a circular module that stretches from the side frame. Additionally, a recent leak revealed that the upcoming offering will feature a 6.78-inch 1.5K BOE X1 display panel.

It will be powered by a Snapdragon 8 Gen 2 processor and be powered by a 5,500mAh battery unit (which is 500mAh larger than its predecessor) with support for 100W fast charging. The leaked specifications put it almost on par with the OnePlus 11 (review) apart from a few differences.

The OnePlus 12 is very much expected to launch in the global markets on January 23 if the recent confirmation from the company’s executive and the previously leaked marketing material is anything to go by.


[ad_2]
Source link

A Must-Have for Foodies This Christmas

0
[ad_1]

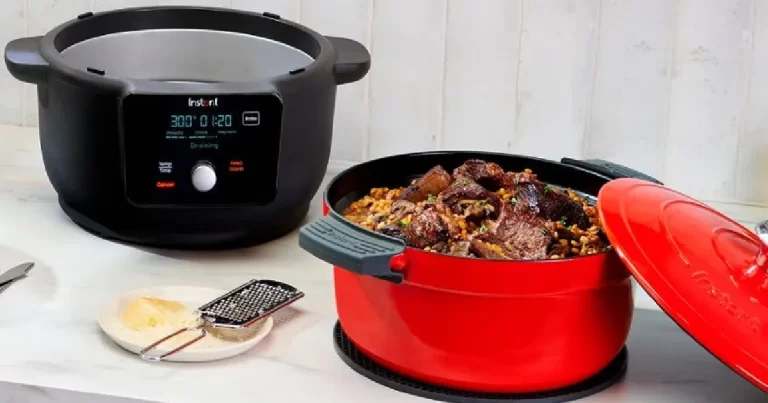
Instant Brands has really made a name for itself with the Instant Pot. But that is not the only product that the company makes. It has ventured into a bunch of other small appliances for your kitchen, including an Electric Dutch Oven, which is a must-buy for any foodie on your Christmas shopping list this year.

The Instant Electric Dutch Oven starts at around $130 for a six-quart-sized model. At six quarts, that’s going to be large enough to cook about six servings of food at a time. So it’s perfect for a small to medium-sized family.

Much like the Instant Pot, the Instant Electric Dutch Oven does much more than just one thing. It’s a 5-in-1 Dutch Oven, which has the ability to braise, slow cook, sear, or saute, manual and keep warm. What makes this Dutch Oven even more impressive is that it has a cast iron cooking pot, which can be removed and used on the stovetop or in the oven. That makes this Dutch Oven so much more versatile. Instant also sells this in a variety of colors, making it look great on a tabletop.

Be aware that the slow-cooking settings are pretty lacking on the Instant Electric Dutch Oven. This one really only has one slow-cook setting. So you’re stuck with it cooking at around 203 degrees. But there is a fix for this, or really a workaround. You can use the Manual mode to set the slow cooker at a “high” setting.

What exactly is a Dutch Oven?

If you’re like me and didn’t know what a Dutch Oven really was before, well, let’s do a quick explainer. A Dutch Oven is a heavy, wide, and fairly shallow pot that has a tight-fitting lid. Most people will think of this as an enameled cast iron casserole pot with two handles and a lid. Or was that just me?

A Dutch Oven needs to be heavy so that it can maintain a constant temperature either in the oven or on the stove for a long time. The tight-fitting lid helps to keep the heat inside the pot so your food cooks as it should.

Once you’ve used a Dutch Oven, you won’t want to go back. I picked up a different Electric Dutch Oven back on Black Friday, and I absolutely love it. It was slightly cheaper than Instant’s version here. However, it is already sold out.

You can use a Dutch Oven for a number of things. Typically meals that you need to cook for a long time. These are also great for searing all types of food since they are typically made out of cast iron and can remain scorching hot for quite some time.

It is called a Dutch Oven because of an old story that talks about an English man visiting the Netherlands and seeing a round, fairly shallow pot being made by casting molten iron in molds made from sand. So that’s why the material is called cast iron, and the Dutch part of it came from where the man first saw these pots.

Why you should buy a Dutch Oven and an Instant Pot

Having an Instant Pot and a Dutch Oven in your kitchen is a really good idea. Both of these appliances can do all sorts of things differently. An Instant Pot is great for making rice, yogurt, and so much more.

But it really falls short as a slow cooker. The reason for this is that the Instant Pot only heats up the bottom and not the sides. A slow cooker or Crock Pot will instead heat up the sides and the bottom to slow cook your food. This means that the food will be cooked more evenly without the food sticking to the bottom of the pan.

Of course, getting both will really depend on your kitchen and what you cook. But having both is a really good idea. I used both quite often, and wouldn’t trade them for anything else in the world.

Buy at Amazon


[ad_2]
Source link

Galaxy Note 20 & A52 grab Samsung’s December update in the US

0
[ad_1]

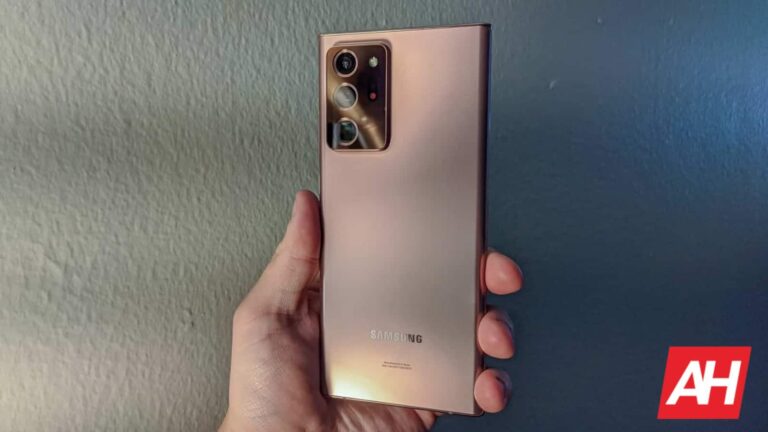
Samsung‘s December security update is available for more Galaxy devices in the US. The company is pushing the latest security patch to the Galaxy Note 20 series and Galaxy A52 stateside. The Galaxy S23 series, which started picking up the new SMR (Security Maintenance Release) last week, is now getting the update widely across the nation.

The Galaxy Note 20 series receives the December update in the US

A few days back, Samsung released the December security update for the Galaxy Note 20 and Galaxy Note 20 Ultra in Latin America. Both 4G and 5G versions of the last Note-branded phones received the update. The company is now pushing the latest SMR to the 5G versions of the duo in the US (4G versions weren’t sold stateside). The new firmware build number for unlocked units is N98*U1UES6HWK1.

Samsung will soon release the December SMR for the carrier-locked variants of the 2020 S Pen-wielding flagships. The build number may vary but the changelog should remain the same. After all, the update doesn’t bring anything more than this month’s security fixes. “The security of your device has been improved,” Samsung’s official changelog states. The Galaxy Note 20 isn’t eligible for Android 14.

While there may be no new features or improvements to look forward to, the latest security patch for Galaxy devices is fairly large. Samsung is pushing fixes for more than 60 vulnerabilities, including seven critical and 40-odd high-severity security flaws in the Android OS, two Samsung Semiconductor issues, and over a dozen Galaxy-specific vulnerabilities.

All of these security fixes are also rolling out to the Galaxy A52 in the US. The carrier-locked units are receiving the update with the build number A526USQSCEWK3. Samsung should soon push it to unlocked units too. The mid-range phone started picking up the December SMR in global markets last week. The device is eligible for Android 14 and may receive the big update later this month or in early 2024.

The latest security patch is widely available for the Galaxy S23 series

The Galaxy S23 series was the first to receive Samsung’s December security update. The rollout began last week for the carrier-locked variants in the US. While international versions are yet to receive the new SMR, the company is now pushing it to the unlocked units stateside. The update comes with the build number S911U1UES2BWKA and doesn’t bring anything more than the latest security fixes. The flagship lineup recently picked up Android 14 and One UI 6.0 with tons of new features.


[ad_2]
Source link

Want to learn more about Generative AI? Google has free courses for you

0
[ad_1]

Generative AI is a norm in our society nowadays, and it can be a pretty complex subject for most people. If you’re curious about what generative AI is, and you want to know more about it, then Google has something for you. Google has launched some helpful courses to help people learn more about AI and what it can do. 

This comes right on the heels of Google launching Gemini. This is the company’s latest multimodal AI model that looks to take on the likes of GPT-4 on the battlefield. It’s much more powerful than Bard… well, that’s half true. Google actually augmented Bard with Gemini Pro. Either way, you can access it that way. There are several ways to access Gemini, actually. 

Google has courses to help teach you about generative AI

Google is no stranger to offering free courses to help people learn. If you want to learn Android development, there’s a full course to teach you how to use Android Studio and code in Kotlin. This is among several others.

Today, a post from X user Shruti Mishra outlines these courses. The post says that you’ll be able to master these courses in only 12 days. There are 11 short courses in all, and they’re all pretty short; the first one is only 22 minutes long. You can take them at any point and even finish all of them in one day.

The courses will go through the fundamentals of generative AI and teach you about many of the finer bits of the technology. You never know if you’ll discover your passion for AI.

Since generative AI is an extremely intricate and complicated subject, you shouldn’t expect to become an expert in just under two weeks. This is a microlearning experience only to give you the fundamentals on AI. Basically, don’t start filling out a job application to Google DeepMind after taking the courses. However, if you just want to know more about AI and what makes it tick, these courses are for you.


[ad_2]
Source link

The Fairphone 5 achieves a perfect 10 for repairability from iFixit

0
[ad_1]

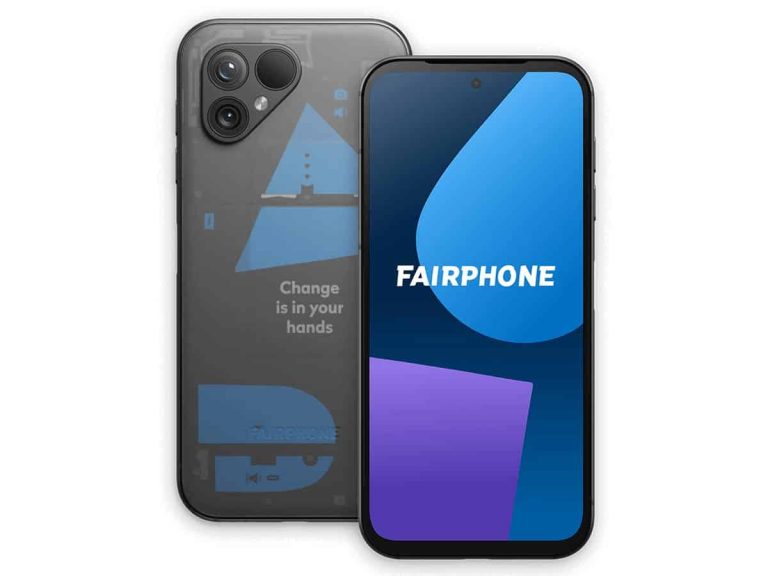
Fairphone’s Android handsets are known for their sustainability and repairability, and it’s no different with the latest model. The Fairphone 5, which debuted in August this year, achieved a perfect ten in the iFixit repairability score. It is the fourth straight model to receive a 10/10 in the firm’s repairability evaluation.

The Fairphone 5 achieved a 10/10 repairability score

The Fairphone 2 was the first-ever phone to achieve a perfect ten for repairability from iFixit. The company has since reiterated this winning formula of “modularity paired with easy access to all major components” for each new generation. The latest model keeps the same core design with some minor “quality of life improvements” that fixers would love.

The plastic back cover still comes off fairly easily as Fairphone doesn’t glue it in place. You just have to unclip it and you are already in. However, the company has redesigned the cover and increased the thickness of the nano coating for an IP55 rating for dust and water resistance. The Fairphone 4 has an IP54 rating, so the new model has better protection against water.

On the inside, we have a larger battery (4200mAh instead of 3905mAh) that takes up more space than before but is still easily removable. The first quality-of-life improvement is seen on the connector cover of the top module. Fairphone has attached it to the module itself rather than keeping it separate. This ensures that the small plastic piece doesn’t get lost or misplaced during the repair.

Elsewhere, replacing the USB Type-C charging port of the Fairphone 5 is easier thanks to the company using a small metal lid. “No more prodding using a small cutout,” iFixit noted. The new phone also switches to a motherboard and daughterboard design instead of a single board that snakes around the casing. Fairphone made this change to make room for the bigger battery.

The company has color-coded the cables connecting the two boards and added stickers to denote the correct place for each cable. “That’s what intuitive repair design is all about,” iFixit says. “It should be easy to do the right thing and complicated to do the wrong thing.” Replacing other components such as the cameras is fairly straightforward too. Like before, you can replace each camera individually.

The longevity of Fairphone devices complements their repairability

Fairphone phones aren’t all about repairability. The aim is to make sustainable devices that can run for years with an easily repairable design. The Fairphone 2 received updates for seven years after launch, something no other Android maker has done yet. For the Fairphone 5, the company has promised 8-10 years of support, including five major Android OS upgrades.

Hopefully, its Qualcomm QCM6490 processor can handle Android and its apps five years from now. The chip is purpose-built for industrial and commercial IoT applications and comes with longer support than Qualcomm’s standard smartphone SoCs. The Fairphone 5 is available in Europe but there is no word yet from the company for a US release. The previous-gen model arrived in the US nearly two years after its European debut.


[ad_2]
Source link

Google’s Gemini video was staged, which is kind of a relief

0
[ad_1]

So, Google just launched its multimodal juggernaut named Gemini. It’s the new extremely powerful AI model from the company, and it’s meant to go up against models like GPT-4. As part of all of the launch festivities, we saw a hands-on video showcasing Gemini’s capabilities. Well, Google admitted that its Gemini hands-on video was staged.

So, to catch you up, when Google launched Gemini, it showed a hands-on video where the person was showing off some of Gemini’s abilities. It gave the appearance that Gemini was processing real-time audio and video data. When the person would put an object into the camera, it would ask Gemini questions about what it “sees” and provide answers. We’d hear an AI-generated voice respond.

It’s a great showcase of Gemini’s capabilities… or it would be if it were REAL.

Google admits that its Gemini hands-on video was staged

A Bloomberg opinion piece spilled this bit of tea. It states that Google revealed that the video wasn’t 100% real. The real-time vocal interactions between the presenter and Gemini weren’t there. That was all through the magic of video editing. Also, the interactions were sped up in post, which made it seem faster than it actually is.

But, while the video wasn’t 100% real, we can’t say that it was 100% fake. It’s a showcase of Gemini’s abilities, and we’re still seeing its abilities. Google used “still image frames from the footage, and prompting via text.” So, rather than having a casual conversation with Gemini, the company fed still images into the model and typed what it wanted Gemini to produce. 

In essence, we’re still seeing Gemini’s capabilities; we’re still seeing what it can produce given the input. Google used Hollywood magic to make it seem more powerful than it is. As for the speed of the responses, Google stated in the description that the responses were sped up for brevity.

Is the company wrong for doing this? Who knows? That’s a debate for the YouTube comment section.

The video was staged, and that’s a bit of a relief

Regardless of whether the video was faked, it’s still much more powerful than Bard. The model is smarter with more tokens and parameters, blah blah blah. No matter what happens, businesses will still have tools to speed up production and efficiency. There are also several ways to access Gemini.

However, the video got pretty scary for any creators watching. We literally saw Gemini create a cool tropical song in seconds, something that would take a composer much longer. We also saw it create images in seconds from yarn. Ever since DALL-E finally got good and since ChatGPT hit the market, human creators have been on the verge of being obsolete. The situation isn’t getting any better, and the hands-on video truly made it look like Google finally put the final nail in the coffin for creators.

However, the fact that it was staged, shows that the technology isn’t quite there just yet. Creators have just a bit more time. That’s all we can ask for at this point.


[ad_2]
Source link

Hackers Trick Users With Data Leak Message to Deploy Malware

0
[ad_1]

Researchers discovered the spread of a malicious exe file that targets specific individuals and is disguised as information related to a personal data leak.

The malware functions as a backdoor, executing obfuscated commands in XML format after receiving them from the threat actor.

Because this malware is focused on specific targets, users should avoid opening attachments in emails from unknown senders.

Malicious exe File Disguised as a Word File

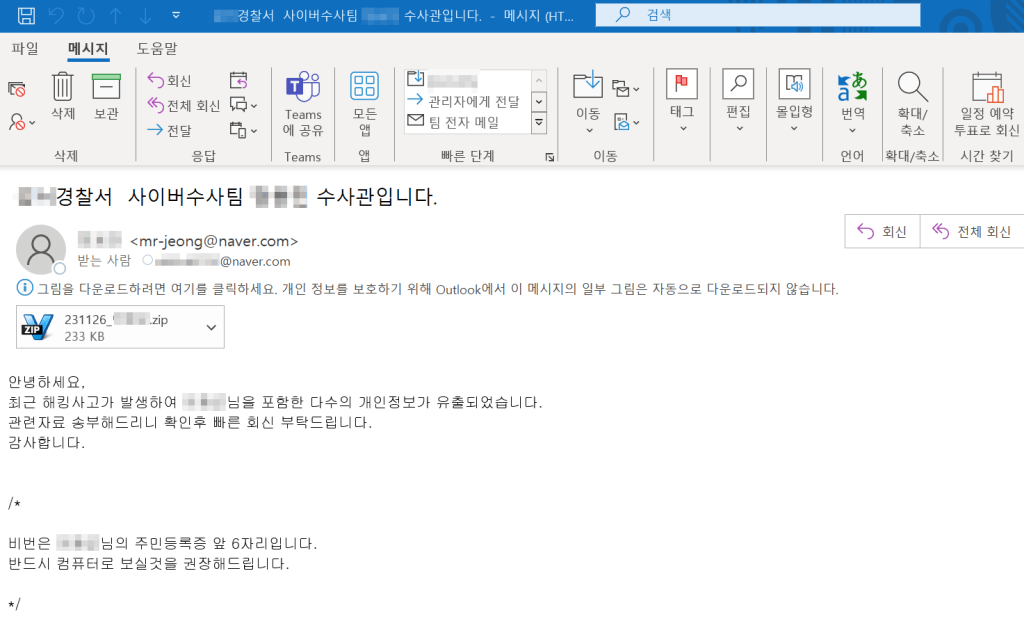
According to the AhnLab Security Emergency Response Center (ASEC), an email purporting to be from a cyber investigation team was sent. Furthermore, the infected exe file was pretended to be a Word document.

https://i0.wp.com/asec.ahnlab.com/wp-content/uploads/2023/12/image-31.png?resize=1024%2C619&ssl=1
An email impersonating a cyber investigation team

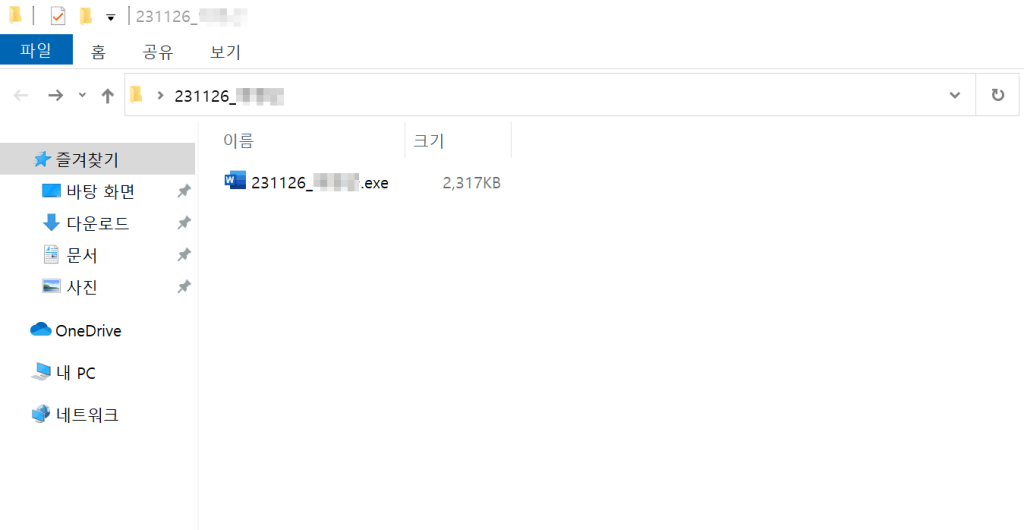
“When the malicious exe file is executed, the files in the .data section are created into the %Programdata% folder. Out of the created files, all files are obfuscated except for the legitimate doc file”, ASEC said in a report shared with Cyber Security News.

https://i0.wp.com/asec.ahnlab.com/wp-content/uploads/2023/12/image-16.png?resize=1024%2C530&ssl=1
The malicious exe file disguised as a Word file

Except for the legitimate doc file, every file that was generated is obfuscated as given below:

  • Lomd02.png (Malicious jse script)
  • Operator.jse (Malicious jse script)
  • WindowsHotfixUpdate.jse (Malicious jse script)
  • 20231126_9680259278.doc (Legitimate doc file)
  • WindowsHotfixUpdate.ps1 (Malicious PowerShell script)

Researchers said among the newly generated files is a valid document file called ‘20231126_9680259278.doc’. This was most likely included by the threat actor to trick the user into thinking they had opened a legitimate file.

Because the C2 was closed in this case, the malware’s ultimate action was not visible; however, researchers say it functions as a backdoor by receiving obfuscated commands from the threat actor and executing them in XML format.

In this scenario, normal users are unable to detect that their PCs are infected with malware because the bait file is executed concurrently.

Hence, individuals should avoid opening attachments from emails they receive from unidentified sources since these malicious files are meant to target individual people.


[ad_2]
Source link

“Amazon got hacked” messages are a false alarm

0
[ad_1]

Amazon customers have been seeing a message on social media that has caused some alarm.

Most of the posts look like one of these (depending on the social media platform):

“PSA!! Amazon got hacked. For USA based people, check your Amazon account. Hackers added HUB lockers as your default delivery addresses. Remove it! I had 2 added to mine.”

Hub lockers are local secure places for people to pick up their Amazon order rather than risk them being left on a doorstep, so the concern was that someone could buy something on your account and then send it to the Hub locker to be picked up.

Here’s another similar post, this time saying the lockers were actually fake:

“PSA: check your saved addresses on Amazon. Amazon got hacked and a lot of people (including me) have random “Amazon lockers” saved in their addresses – which are not actual lockers. If you do use Amazon lockers, be sure to verify that the locker you’re sending it to is an actual locker.

Double check your order history and make sure there aren’t any orders you don’t recognize. And check your bank accounts to make sure your credit card on file is also not being used for unauthorized purchases. “

It’s not surprising that those messages would raise the alarm amongst Amazon’s customers, but thankfully the security alert is nothing to worry about.

The additional addresses are genuine Hub locations or other pick-up locations and they weren’t put there by hackers. Amazon added them in error.

As an Amazon spokesperson told Snopes:

This isn’t a data security matter and our systems are secure. Amazon pickup locations were added to a small number of customer accounts in error, and we are working to fix the issue. We apologize for any inconvenience this may have caused, and customers with questions about their account are welcome to contact customer service.

Things like this are tricky – on the one hand we are always pleased for people to share security issues and alert others to potential problems. However in this case it appears as though people were forwarding the message without first checking if it was, in fact, a real issue.

And nowadays with social media and instant messaging, rumours like these can spread fast. All it takes is some panic, little research, and a lot of contacts.

If you see a message like this, always do a bit of research before forwarding it on. Sites like Snopes allow you to search for keywords and you’ll find a lot of hoaxes including this one.


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.


[ad_2]
Source link

X app for large displays starts rolling out to Pixel Fold & tablet

0
[ad_1]

A tweaked X app for large displays is now rolling out to the Google Pixel Fold and Pixel Tablet. The app has not been completely revamped to fit large displays, but this is definitely better than having no change at all.

The Google Pixel Fold & Pixel Tablet are getting new X app optimized for large displays

Instead of having a really ugly, stretched-out interface with black boxes on the sides, the app now makes use of the full width of the display, without stretching the content. You can see how it looks below.

X app large displays 1

So, you’ll basically be getting the same layout as on smartphones, as far as the main feed is concerned, at least. The bottom bar is now spread out from one side of the screen to the other. The same goes for the top bar too.

Now, the change is rolling out to Google’s devices, but they should technically become available on other, similar devices. So, the OPPO Find N and Find N2 also have more of a horizontal layout when unfolded, so this change is expected to become available for those devices too. That’s just an example.

This change should also be visible on other, similar devices… soon, if not already

That also goes for Android tablets in general, the moment you flip them to landscape mode. We’re not sure when will it be visible on those devices, though. If you do have a non-Pixel Android tablet, do try it when you get the X v10.18.0 app.

That being said, let’s hope X will improve upon this offering moving forward. It would be nice to see a proper tablet app on both foldables and tablets. An app that would adapt nicely to all foldables, not just landscape-oriented ones.

The X app doesn’t exactly look great on the Galaxy Z Fold series, and other foldable devices that have a square-ish screen when unfolded. They simply get a stretched-out version of the regular app.

It would be nice to see a complete revamp of X for large-screen devices. So, let’s hope that is coming at some point down the road.


[ad_2]
Source link