Huawei vows to deliver ‘disruptive’ products in 2024

0
[ad_1]

Huawei has promised to deliver “disruptive” products in 2024. That information comes from the head of Huawei Technologies’ consumer business, Richard Yu Chengdong. He also added that next year could “rewrite the history of the industry”.

Huawei promised to deliver “disruptive” and “innovative” products in 2024

In addition to using the word “disruptive”, Richard Yu also reached for “leading” and “innovative” descriptions. He shared these opinions at the company’s annual fan club event, which took place on Saturday.

Richard Yu did not elaborate on what he said, though. He obviously wants to keep the products a secret, but based on his words, Huawei has a major year planned for 2024. The company did manage to surprise us a number of times this year, so it will be interesting to see what happens in 2024.

Richard Yu also added that Huawei will release native apps and products based on its self-developed mobile platform next year. He was talking about HarmonyOS, of course.

A 100% shipment growth is expected for the Huawei P70 series

Now, a 100% shipment growth is expected for the Huawei P70 series of devices. Huawei announced the Mate 60 series with its brand new SoC, the Kirin 9000s, which enables 5G. This processor is manufactured by SMIC, and it’s a 7nm chip. It’s also the first Huawei chip in a long, long time.

The US sanctions managed to mess up Huawei’s plans considerably. Huawei seems to be getting things back on track, even though it’s prevented from using Google services on its devices.

More Kirin-branded chips are expected moving forward, and it remains to be seen if a new one will be used in the Huawei P70 series. Huawei could reach for the Kirin 9000s again, we’ll see.

Huawei actually had problems keeping up with the Mate 60 demand, and it still does. So things are looking up for Huawei, as 5G returned to the company’s smartphones.


[ad_2]
Source link

Threads is coming to the EU on December 14: Official

0
[ad_1]

It was recently confirmed that Threads will launch in the EU in December, and now we know when. Threads is coming to the EU on December 14, it has been officially confirmed by the company.

Threads will launch in the EU on December 14, it’s ready to go

As many of you know, Threads officially launched earlier this year. It became available in early July, excluding the EU, though. Meta had to adapt Threads to comply with the EU regulations, and it seems like everything is ready to go now.

Meta actually included a countdown timer on the Threads website, so you can see when exactly will it launch. Do note that this timer is not available to users outside of the EU, though, of course.

Furthermore, Instagram users from the EU can also look up the term ‘ticket’ within the app. You’ll discover a digital invitation to Threads, in addition to a scannable QR code and a launch time.

Threads managed to attract a lot of users in a very short time span

Having said that, Threads managed to acquire a lot of users in a very short time span. This social media network launched at the perfect time. Twitter aka X was in the midst of a transition prompted by its new owner, Elon Musk.

It took Threads only 7 hours to boast 10 million users. That number doubled after 12 hours, and quickly grew to 30 million users. Not long after that, Threads hit 55 million users, and in October, it was announced that almost 100 million users were actively using the app/service.

Threads is a new social media network by Meta, and the company did a smart thing here by allowing people to log in via Instagram. That was the integration is much stronger, and that’s probably partially the reason why it managed to become so successful so fast.

Threads is a direct competitor to Twitter, and that’s quite obvious. It will be interesting to see if the EU launch will significantly boost the number of users using Threads. It would certainly have more effect if the social media network ended up being available in the EU from the get-go.

Threads EU countdown timer


[ad_2]
Source link

Over 50% Insider Attacks Uses Privilege Escalation Vulnerability

0
[ad_1]

In the labyrinth of cybersecurity, the specter of insider threats emerges as a formidable adversary, wielding both malicious intent and unintentional foibles. 

This expose delves into the intricacies of how insiders exploit vulnerabilities, introducing an air of risk through actions both deliberate and unwitting. 

Embark on a journey through the key findings from CrowdStrike’s insightful analysis and discover recommendations to fortify the bastions against this multifaceted menace.

Insider Threat Exploiting Vulnerabilities

High Prevalence:

Within the clandestine world of insider threats, a staggering 55% of incidents unfold with audacious attempts to exploit vulnerabilities. 

These endeavors aim for Privilege Escalation Vulnerability, unlocking a gateway to further clandestine objectives that imperil organizational sanctity.

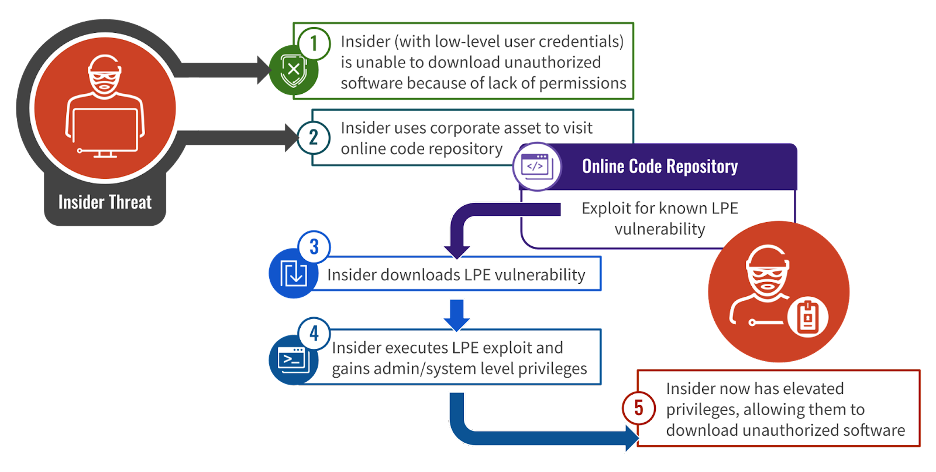
Figure 1. Hypothetical example of an insider threat leveraging a local privilege escalation (LPE)
A hypothetical example of an insider threat leveraging a local privilege escalation (LPE)

Diverse Techniques:

The arsenal of insiders encompasses a diverse array of publicly known vulnerabilities, with exploits such as CVE-2017-0213, CVE-2021-4034, and CVE-2015-1701 acting as the proverbial keys to unauthorized realms. 

These vulnerabilities serve as conduits for downloading forbidden software, tampering with evidence, and manipulating systems of utmost sensitivity.

CVE NumberCVE NameTargeted OSIn CISA KEV
CVE-2021-42013Apache HTTP Server 2.4.49 and 2.4.50 Path TraversalMacYes
CVE-2021-4034Polkit Out-of-Bounds Read and Write Vulnerability (aka PwnKit)LinuxYes
CVE-2020-0601Windows CryptoAPI Spoofing VulnerabilityWindowsYes
CVE-2016-3309Windows Kernel Privilege Escalation VulnerabilityWindowsYes
CVE-2022-21999Windows Print Spooler Elevation of Privilege VulnerabilityWindowsYes
N/AMetasploit FrameworkN/AN/A
N/AElevateKitN/AN/A

Target Objectives:

The exploitation of vulnerabilities opens a Pandora’s box of unauthorized activities, enabling insiders to download forbidden software, tamper with evidence, and manipulate systems of utmost sensitivity. 

The stakes are high as privileged access becomes the linchpin for these insidious maneuvers.

Unwitting Insider Threats

In a delicate dance between authorized testing and training activities, insiders unwittingly introduce risk through unauthorized downloads of exploits and offensive tools. 

This inadvertent yet perilous ballet constitutes 45% of insider threat incidents, threatening to disrupt operations and provide assailants with covert footholds.

The inadvertent foray into risk often finds its roots in authorized testing and training activities. 

However, these actions, while seemingly innocuous, violate safe handling procedures, unleashing potential damage that could reverberate through operations and expose vulnerabilities.

The ramifications of unwitting actions are profound, with the potential to disrupt operations, furnish assailants with strategic footholds, and introduce insidious malware that festers within the organizational fabric.

A revelation surfaces as the report uncovers an unsettling correlation—many vulnerabilities exploited by insiders mirror the tactics employed by external attackers. 

This nexus emphasizes the indispensability of comprehensive defense mechanisms.

In the eternal chess game of cybersecurity, timely patching and vulnerability management stand as unwavering sentinels, thwarting known attack vectors and narrowing the avenues for exploitation.

A clarion call resonates across organizational corridors, advocating for bespoke training programs that equip employees—new and existing—with the acumen to navigate the treacherous waters of exploits and offensive tools. Knowledge becomes the frontline defense.

Recommendations 

Implement EDR and MDR:

Comprehensive protection unfolds through the synergy of advanced technologies.

The establishment of unequivocal guidelines for downloading, storing, and executing exploits and offensive tools becomes the linchpin of organizational resilience. 

Clear protocols carve a path toward secure digital operations.

User Awareness Training:

In the age-old adage that knowledge is power, the regular dissemination of cybersecurity best practices and insider threat awareness among all employees becomes a non-negotiable mandate. 

Awareness becomes the fulcrum upon which organizational defenses pivot.

Patch Management:

The orchestration of timely patching becomes a symphony of resilience, addressing known attack vectors and solidifying the organizational ramparts against evolving threats. 

A proactive stance prevails in the perpetual cat-and-mouse game of cybersecurity.


[ad_2]
Source link

Insights into your unpatched vulnerabilities

0
[ad_1]

Every day, nearly 70 brand-new vulnerabilities are discovered in software products around the world. That’s almost 25,550 new problems each year, of which roughly 4,250 (or every one-in-six) will be classified as “critical.”

But with little guidance beyond “critical” classifications—and with the potential for non-critical vulnerabilities to still be exploited for devastating malware attacks—resource-constrained IT organizations need help. How can IT teams prioritize amongst potentially thousands of vulnerabilities if they don’t know which to fix first?

Malwarebytes analyzed the vulnerabilities identified by its ThreatDown Vulnerability Assessment module, now included at no additional cost in all ThreaDown bundles, to reveal the most common “critical” and “important” unpatched vulnerabilities on known endpoints.

The vulnerabilities compiled show up across four major software products:

  • Adobe Flash Player
  • Adobe Acrobat Reader
  • VideoLan VLC Media Player
  • Zoom

The most prevalent vulnerabilities:

In the 100 most prevalent unpatched vulnerabilities, the majority (93 out of the 100) are found in software by Adobe, Zoom, and Mozilla. [MOU3] 

No vulnerability listed as critical made it into the top 100 most prevalent vulnerabilities. But one critical vulnerability was close: CVE-2020-9633 in Adobe Flash Player. The vulnerable version of Flash is still in use because Adobe silently introduced a time bomb in later Flash Player versions that would prevent Flash Player from working and playing any Flash content after January 12, 2021. So organizations that have certain Flash content they need to play often to go back to that vulnerable version.

Relatedly, the most prevalent vulnerabilities labeled “Critical” come from a more diverse group of software vendors, with four distinct top contributors:

  • 30 % UltraVNC (Server and Viewer)
  • 20 % Python (versions 3.6 to 3.10)
  • 18% Microsoft (Edge and Visual Studio)
  • 14 % Adobe (Flash Player, Acrobat, and Reader)

Read on to see details of the top 5 unpatched critical vulnerabilities and the top 5 unpatched important vulnerabilities, as uncovered by ThreatDown, powered by Malwarebytes.

The top 5 unpatched CRITICAL vulnerabilities:

Adobe Flash Player

CVE-2020-9633: Adobe Flash Player Desktop Runtime 32.0.0.371 and earlier, Adobe Flash Player for Google Chrome 32.0.0.371 and earlier, and Adobe Flash Player for Microsoft Edge and Internet Explorer 32.0.0.330 and earlier have a use after free vulnerability. Successful exploitation could lead to arbitrary code execution. Adobe has released security updates for Adobe Flash Player for Windows, macOS, Linux and Chrome OS.

Zoom:

CVE-2022-22785: The Zoom Client for Meetings (for Android, iOS, Linux, MacOS, and Windows) before version 5.10.0 failed to properly constrain client session cookies to Zoom domains. This issue could be used in a more sophisticated attack to send an unsuspecting users Zoom-scoped session cookies to a non-Zoom domain. This could potentially allow for spoofing of a Zoom user.

CVE-2022-22786: The Zoom Client for Meetings for Windows before version 5.10.0 and Zoom Rooms for Conference Room for Windows before version 5.10.0, fails to properly check the installation version during the update process. This issue could be used in a more sophisticated attack to trick a user into downgrading their Zoom client to a less secure version.

Adobe Acrobat Reader

CVE-2016-1038: Adobe Reader and Acrobat before 11.0.16, Acrobat and Acrobat Reader DC Classic before 15.006.30172, and Acrobat and Acrobat Reader DC Continuous before 15.016.20039 on Windows and OS X allow attackers to bypass JavaScript API execution restrictions via unspecified vectors. Installing a more recent version eliminates this vulnerability.

CVE-2016-1044: Adobe Reader and Acrobat before 11.0.16, Acrobat and Acrobat Reader DC Classic before 15.006.30172, and Acrobat and Acrobat Reader DC Continuous before 15.016.20039 on Windows and OS X allow attackers to bypass JavaScript API execution restrictions via unspecified vectors. Installing a more recent version eliminates this vulnerability.

The top 5 unpatched IMPORTANT vulnerabilities:

Zoom:

CVE-2023-39211: Improper privilege management in Zoom Desktop Client for Windows and Zoom Rooms for Windows may allow an authenticated user to enable an information disclosure via local access. Upgrading to 5.15.5 or later eliminates this vulnerability.

CVE-2023-34116: Improper input validation in the Zoom Desktop Client for Windows may allow an unauthorized user to enable an escalation of privilege via network access. Upgrading to version 5.15.0 or later eliminates this vulnerability.

CVE-2023-39213: Improper neutralization of special elements in Zoom Desktop Client for Windows and Zoom VDI Client may allow an unauthenticated user to enable an escalation of privilege via network access. Upgrading to version 5.15.2 or later eliminates this vulnerability.

Adobe:

CVE-2023-29320: Adobe Acrobat Reader versions 23.003.20244 (and earlier) and 20.005.30467 (and earlier) are affected by an Violation of Secure Design Principles vulnerability that could result in arbitrary code execution in the context of the current user by bypassing the API blacklisting feature. Exploitation of this issue requires user interaction in that a victim must open a malicious file. Updating to the latest version eliminates the vulnerability.

VLC media player

CVE-2020-26664: A vulnerability in VideoLAN VLC media player 3.0.11 allows attackers to trigger a heap-based buffer overflow via a specially crafted file. A buffer overflow is a type of software vulnerability that exists when an area of memory within a software application reaches its address boundary and writes into an adjacent memory region. In software exploit code, two common areas that are targeted for overflows are the stack and the heap. A buffer overflow may result in arbitrary code execution. Installing the 3.0.20 release of VLC eliminates the vulnerability.

You Can’t Fix What You Can’t See

While only on very rare occasions do vulnerabilities make mainstream news headlines, but when they do, the impact can be enormous. The exploitation of the MOVEit vulnerability by Cl0p ransomware operators impacted over 60 million individual victims (between May and September of 2023. And remember that not every “critical” vulnerability is synonymous with an exploited vulnerability. With an additional 1,000 entries added to CISA’s known, exploited vulnerabilities catalog in just the past two years, few organizations have the IT staff to keep track of everything.

Many organizations only have limited visibility into which vulnerabilities might impact them, and nearly every organization relies on the Common Vulnerabilities and Exposures (CVE) database, which lists publicly disclosed computer security flaws. But this isn’t a perfect resource.

In 2023, CVE-2023-4863 was discovered, originally described as a heap buffer overflow in WebP  within Google Chrome. The average person, upon learning about this vulnerability, may have thought that the problem was limited to Chrome, or maybe even realize that other Chromium based browsers could be affected. Yet the reality was quite different. It turned out that the bug was deeply rooted in the libwebp library, which is not only used by Chrome but by virtually every application that handles WebP images. So anyone that patched their Chrome browser might think they thwarted that vulnerability, when in reality they might still be vulnerable, just in different software.

This type of library oversight happens quite often. Most people, including thoroughly trained and experienced IT staff, have no idea about all the building blocks that were used to create the environment and software that they use.

This is where dedicated software to alert staff about existing vulnerabilities in their environment integrated with patch management capabilities can help save the day.

Free Vulnerability Assessment

Today Malwarebytes announced its offering customers its ThreatDown Vulnerability Assessment solution without extra costs to help reduce attack surfaces and improve their security posture. The full featured comprehensive vulnerability scanning is now included in every ThreatDown Bundle at no additional cost via its integrated console.

Learn more about how ThreatDown bundles can help you to improve your security by quickly finding and fixing vulnerabilities here.


We don’t just report on vulnerabilities—we identify them, and prioritize action.

Cybersecurity risks should never spread beyond a headline. Keep vulnerabilities in tow by using ThreatDown Vulnerability and Patch Management.

[ad_2]
Source link

Microsoft is preparing to pump more AI into Windows

0
[ad_1]

A recent report from a well-known insider, Zac Bowden, has sparked a fresh wave of speculation about the addition of cutting-edge AI in Microsoft’s upcoming Windows release. Codenamed Hudson Valley and scheduled for a September or October 2024 launch, the new Windows version is expected to be heavily focused on artificial intelligence, introducing groundbreaking features. However, the big question remains: Will it be Windows 12 or another iteration of Windows 11?

Windows 12 is likely to fragment the user base even more, with users still sticking to the older versions for obvious reasons

According to Bowden’s sources within Microsoft, there is internal skepticism about labeling Hudson Valley as Windows 12. The primary concern cited is Microsoft’s wariness of further fragmenting the user base. According to reports, Windows 10 is still more popular than Windows 11. The company currently oversees approximately 1.4 billion Windows users, with only half a billion on the latest version of Windows. Meanwhile, 1 billion users are still relying on Windows 10 or older versions.

It’s not like Windows users aren’t interested in new features and revamped look, but the compatibility of older systems has prevented many from getting to the newest version. The speculated next-generation AI features of Windows 12 will likely require up-to-date NPU hardware to function. So, Windows 12 will also prevent some Windows 11 users from upgrading to it. So, introducing a new version will likely increase the fragmentation even further. If anything, it will only complicate the support and management of these diverse systems.

However, the potential move away from Windows 12 doesn’t mean the end of significant changes. Microsoft is reportedly considering adjustments to its approach to Windows updates. While the current model includes frequent ‘Moment’ (smaller) updates throughout the year, Microsoft is planning a return to a more traditional annual feature update cycle, with fewer ‘Moment’ updates.

Microsoft might continue the AI addition with Windows 11

The speculation surrounding the naming decision gains weight when considering the recently leaked information about Windows 11 24H2. This lends credibility to the notion that Microsoft may prioritize maintaining a more unified Windows user base under the Windows 11 umbrella.

In conclusion, Microsoft’s decision on whether to brand the Hudson Valley release as Windows 12 or another iteration of Windows 11 is still up in the air.


[ad_2]
Source link

Crypto Exchange Founder Pleads Guilty for Dark Web Transfers

0
[ad_1]

Bitzlato Ltd., a cryptocurrency exchange, was founded and is primarily owned by an individual who facilitated transactions between buyers and sellers in dark markets.

The exchange acted as a conduit for such transactions to take place, making it an important player in the underground world of illicit activities involving digital currencies.

A cryptocurrency exchange works similarly to stock exchanges, which helps investors buy and sell in digital currencies such as Bitcoin, Ethereum, or Tether.

According to reports, Bitzlato Ltd. was identified as the primary entity involved in facilitating illegal transactions for the infamous online drug market, Hydra.

Exchange Founder Pleads Guilty

Hydra Market, the biggest and longest-running darknet market in the world, was Bitzlato’s biggest counterparty in cryptocurrency transactions.

Hydra Market was an online marketplace for drugs, financial information that had been stolen, false identification documents, and money laundering services.

Users exchanged more than $700 million worth of bitcoin with Bitzlato, either directly or through middlemen, before Hydra Market’s closure in April 2022 as a result of seizures made by German and American law enforcement.

“As alleged, Bitzlato advertised a haven for fraudsters, thieves, and other criminals to launder illicit proceeds — but their business model didn’t account for federal law enforcement,” said Deputy Attorney General Lisa O. Monaco. 

Anatoly Legkodymov, a Russian national who resided in Shenzen, agreed to dissolve Bitzlato and to release any claim over approximately $23 million in Bitzlato’s seized assets.

Legkdoymov’s plea shows the impact on anyone who provides a haven for criminals and their illicit wealth.

According to the report, Bitzlato, a cryptocurrency exchange with global operations and a Hong Kong registration, advertised that it only needed minimal identification from its users; either selfies or passports are required.

The users of Bitzlato can directly submit identifying information, allowing them to provide information. It’s claimed that Bitzlato turned into a haven for money meant for use in illegal activities as a result of these inadequate know-your-customer (KYC) processes.

On multiple occasions, Legkodymov was informed that the cryptocurrency sent through Bitzlato was either meant for use in illegal transactions or was the proceeds of crime.

As a result of this illegal exchange, Legkodymov faces a maximum of 5 years in prison, but the government has not yet confirmed the date.


[ad_2]
Source link

OnePlus 12 global launch date confirmed by OnePlus exec

0
[ad_1]

One of the company’s executives has just confirmed the OnePlus 12 global launch date. According to the Economic Times India, Alexander Vanderhaeghe, confirmed the news. He is a Country Manager of OnePlus Benelux, and he confirmed January 23, 2024, as the launch date.

That is the date was first shared by Max Jambor, a well-known tipster, and now seemingly confirmed by a OnePlus employee. OnePlus still has to officially confirm the date, though, of course.

The OnePlus 12 global launch date seemingly confirmed by a OnePlus exec

Alex Vanderhaeghe allegedly confirmed the date during a special event held in Antwerp, Belgium. That event was held to celebrate the company’s 10th anniversary. He said: “The OnePlus 12 will be presented globally on January 23, 2024”, which is a rather clear confirmation.

OnePlus is also set to introduce the OnePlus 12R, alongside the OnePlus 12. The company’s R series of devices was exclusive to India thus far. This smartphone is rumored to be available in a number of additional markets, possibly even Europe and the US. It will be inferior to the OnePlus 12, of course.

The OnePlus 12 was already announced in China, so there’s not much mystery surrounding its design or specs. The all-new OnePlus 12 does resemble its predecessor, though it is more powerful, of course.

The OnePlus 12 brings back fast wireless charging, after its predecessor ditched the feature entirely

This handset actually brings back some much-requested features. It includes 50W wireless charging, while the OnePlus 11 didn’t include wireless charging at all. It also improved water and dust resistance compared to its flagships.

The OnePlus 12 has a very compelling camera setup, and it’s also very powerful in general. The Snapdragon 8 Gen 3 fuels the device, while OnePlus included plenty of high-end RAM and storage too.

A 5,400mAh battery is included too, and in addition to 50W wireless charging, 100W wired charging is included. The same goes for a charger, by the way.


[ad_2]
Source link

A week in security (December 4 – December 10)

0
[ad_1]

December 8, 2023 – Meta’s Project Llama aims to help developers filter out specific items that might cause their AI model to produce inappropriate content.

December 5, 2023 – Accounting software provider Tivalti is investigating ALPHV/BlackCat claims it was breached. In a typical supply-chain attack ALPHV is threatening some of their customers like Roblox and Twitch

December 4, 2023 – 23andMe has released new details about the credential stuffing attack that took place in October.

December 4, 2023 – US senators issued subpoenas for the CEOs of five social media giants to testify over their “failure to protect children online”.

December 4, 2023 – A list of topics we covered in the week of November 27 to December 3 of 2023


[ad_2]
Source link

Google Play Movies & TV for Android TV is going away in January 2024

0
[ad_1]

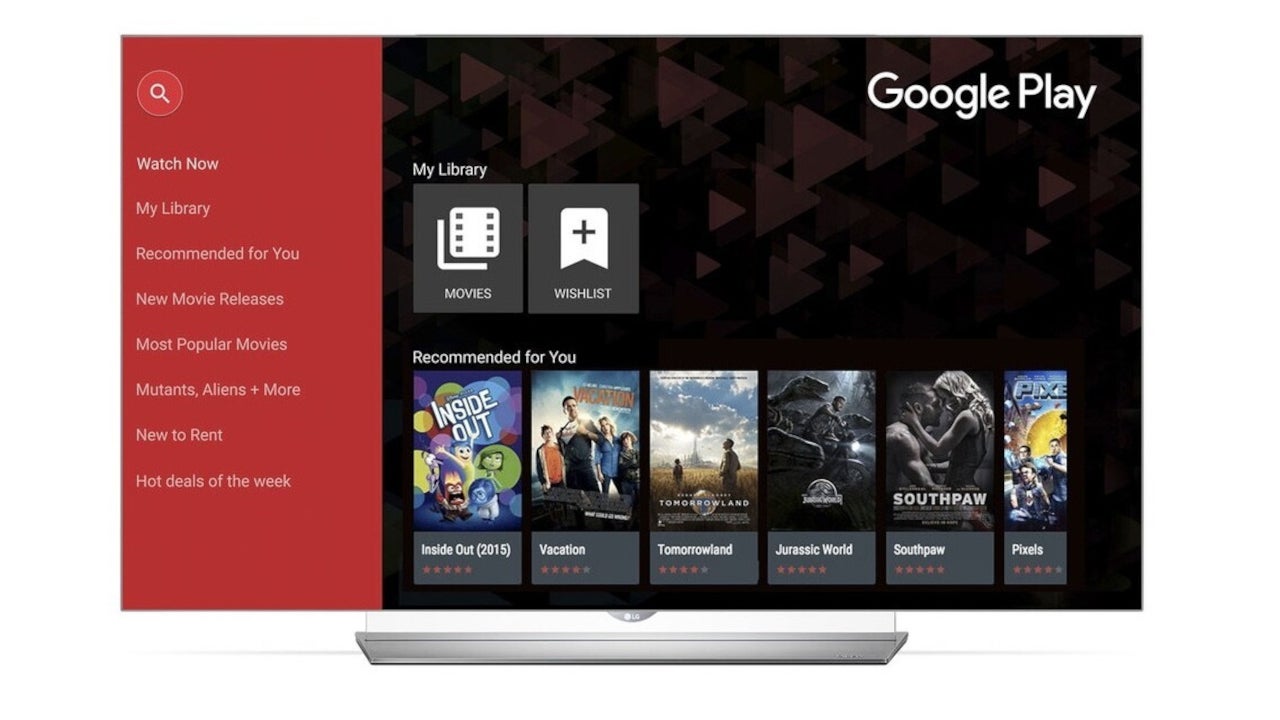
Google has been making a lot of changes to many of its apps, phasing out some, replacing others, or completely removing them. Google Play Movies & TV is one of the apps that the search giant decided to discontinue earlier this year.

The last piece of information regarding the app confirmed Google Play Movies & TV app for Android TV will get the ax on October 5. Over the weekend, Google detailed how users will be able to access purchased content after the app is completely gone on January 17, 2024.

First off, Google Play Movies & TV will no longer be available on Android TV devices or the Google Play website. However, this change will be rolled out over the next few weeks depending on location and country.

Secondly, users will be able to access all of their previously purchased titles on Android TV devices, Google TV devices, the Google TV mobile app (Android and iOS), and YouTube. Here is how you’ll be able to do that starting January 17, 2024:

  • On TVs and streaming devices powered by Android TV – The Shop tab will be your new home for watching previously purchased titles or buying and renting new movies on Android TV. All purchased content will be available in the Your Library row on the Shop tab.
  • On cable boxes or set-top boxes powered by Android TV – The YouTube app will be your new home for watching previously purchased titles or buying and renting new movies from Google.
  • On a web browser – YouTube will be your new home for watching previously purchased titles or buying and renting new movies on a web browser. All content purchased from Google, including active rentals, will be available on the YouTube website.

That being said, you have until January 17, 2024 to pay your respects to the Google Play Movies & TV app for Android TV.

[ad_2]
Source link

Researchers Uncovered an Active Directory DNS spoofing exploit

0
[ad_1]

In the intricate web of our interconnected world, the Domain Name System (DNS) stands as a linchpin, directing users to their online destinations. 

Yet, even this vital system is not impervious to the dark art of malicious manipulation.

In a recent revelation by Akamai security researchers, a chink in the armor of DNS security has been exposed. 

This vulnerability, resulting from exploiting DHCP DNS Dynamic Updates, opens the door for attackers to engage in the deceptive art of DNS record spoofing.

Navigating the Vulnerability’s Landscape

Dynamic Host Configuration Protocol (DHCP), the silent orchestrator of IP addresses and configurations in network devices, harbors a vulnerability in its feature set. 

DHCP DNS Dynamic Updates, designed for automatic DNS record updates, becomes a double-edged sword when left unguarded. 

The absence of authentication in this process allows any device on the network to masquerade as others, initiating a dangerous game of impersonation.

DNS records act as the internet’s address book, translating human-readable domain names into numerical IP addresses. 

Spoofing these records allows attackers to redirect unsuspecting users to malicious websites, mimicking legitimate platforms like banks, social media sites, and even internal company resources. 

This enables them to steal login credentials, access sensitive information, and even launch further attacks within the network.

Abused DHCP Feature

The vulnerability lies within a feature called DHCP DNS Dynamic Updates. 

This feature allows DHCP servers to automatically register and update DNS records for connected devices, ensuring smooth network access. 

However, its inherent lack of authentication makes it susceptible to exploitation. 

Malicious actors can exploit this vulnerability by sending forged requests to the DHCP server, effectively tricking it into creating or modifying DNS records and ultimately redirecting users to their crafted phishing sites.

The potential impact of this vulnerability is significant. Microsoft DHCP servers are widely used, with Akamai observing them on 40% of the networks it monitors.

This translates to millions of organizations and individuals potentially exposed to DNS spoofing attacks, making this a critical threat requiring immediate attention.

Akamai recommends implementing mitigation strategies until a patch is available from Microsoft.

This article has only scratched the surface of the issue. To delve deeper into the technical details of the vulnerability, how to exploit it, and advanced mitigation strategies, please refer to the original research paper by Akamai.


[ad_2]
Source link