AI-generated FAQs might come to the Google Play Store

0
[ad_1]

The Play Store is the most trusted venue for Android users to get their apps and games. While Google has added a taste of AI to almost every service and app it has, the Play Store is at the back of a long queue to get more AI-driven features. At the previous Google I/O event, the tech firm announced some generative AI tools that help developers craft new Play Store listings through Google’s PaLM 2 model.

The feature helps developers write more compelling descriptions for their apps to entice more users to download them. But Google’s upcoming AI additions to the Play Store will be focused on frequently asked questions, according to AndroidPolice (via SpAndroid).

AI-generated FAQs will soon come to the Google Play Store

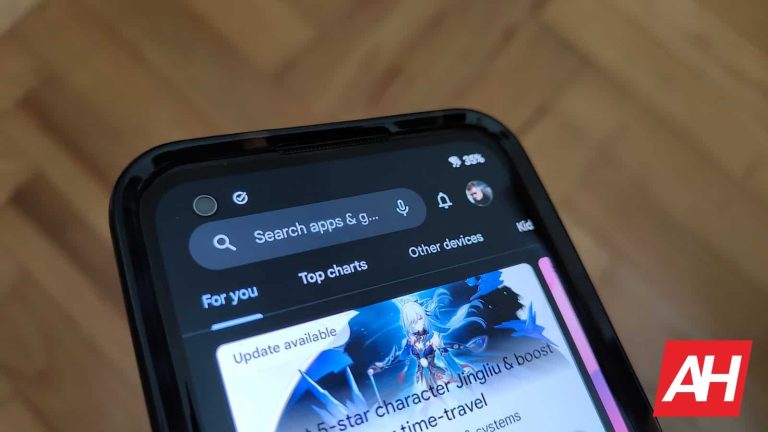
The teardown of Google Play Store v38.4.12 reveals that Google is working on a new feature that brings AI-generated FAQs to its app store, letting developers craft the frequently asked questions in the listings by generative AI. Yet, there’s no screenshot of how the feature works, but the strings on the Play Store code confirm it’s in the works.

The AI-generated FAQs will supposedly appear below each app and game listing. As the name implies, they answer users’ most important questions about an app or game. We might hear more about the feature in the Play Store’s upcoming updates.

The app researcher who found the feature claims AI-generated FAQs will “eventually make its way to the Play Store,” and it’s not an experimental feature. The Play Store Download Buddy underwent the same procedure, and after a year of testing, it made its first debut in September. In case you didn’t know, Download Buddy displays an app installation progress on the screen through a movable floating arrow.

Given that AI is expanding its role in Google apps and services, the Play Store could get more AI-driven features in future updates. As the platform evolves, Google also wants to ensure more quality apps are available to users. The firm has recently obligated app developers to test their apps with a group of at least 20 people for a minimum of two weeks before releasing them to the Play Store.


[ad_2]
Source link
The 2027 MacBook OLED models will have touchscreen displays

0
[ad_1]

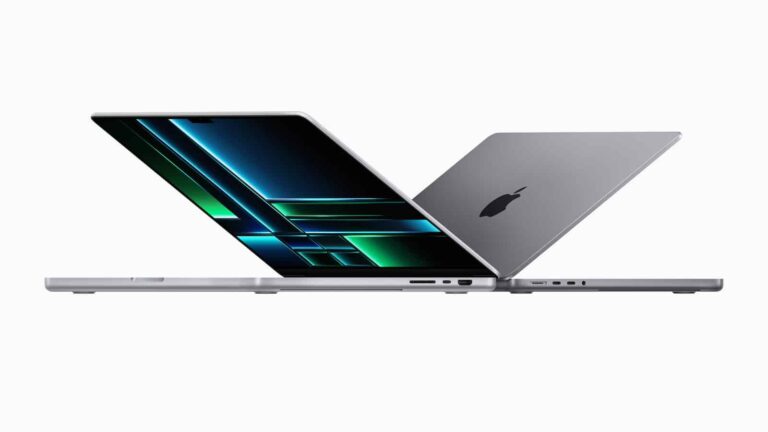
Recent reports now claim that the 2027 MacBook OLED models will launch with touchscreen displays. A few days ago, netizens learnt that Apple is preparing to launch OLED iPad models next year. A few years after these hit the market, the tech giant will follow up with the addition of touchscreen OLED displays to all the MacBook models they offer.

By 2027 all MacBook models will start using impressive OLED display technology. This means that both the Pro and Air models will join the OLED party, but the Pros might step up the quality of their OLED screens. If all reports on this matter are accurate, then netizens should expect all MacBook models to feature OLED display panels by the year 2027.

New reports also claim that at this time Apple will be bringing touchscreen displays to their OLED MacBook models. This is a welcomed improvement as the company will be dropping the Liquid Retina XDR display. Information on the touchscreen display that might arrive on these MacBooks has already hit the internet.

Details on the touchscreen display that’ll be available on 2027 MacBook OLED models

The news that Apple is preparing to launch the OLED iPads is a bit older than that of the coming touchscreen MacBook displays. However, both work hand in hand and will hit the launch stage around the same time on all iPad and MacBook models. Already the details on the screen and the models they’ll come on are available on the Internet.

According to the reports from Tech Reve the MacBook Pro and Air models will all get touchscreen displays by 2027. There will be two major suppliers for this touchscreen display that will be in use on Apple 2027 MacBook models. One supplier will be Samsung and the other supplier will be LG, these two are constant display suppliers from Apple devices.

The display-integrated touch technology that’ll come from Samsung is the “Y-OCTA.” That to come from LG is the “Touch On Encapsulation (TOE).” There is a chance that the display from Samsung will be in use on the MacBook Air models and that from LG will be on the Pro models.

The reason behind this is that Samsung might not supply the OLED panel for use on the iPad Pro models by 2027. This might also carry along to the MacBook Pro models as well. LG Display might be tasked with the responsibility of supplying the OLED touchscreen panels for the 2027 MacBook Pro models.

Both panels from Samsung and LG will feature new technology that’ll help to keep costs down. In a few years, netizens will see the first MacBooks to launch using OLED touchscreen technology. However, the introduction of OLED screens on Apple larger screen products will start next year with the iPad Pro models.


[ad_2]
Source link

You will soon get an easy-to-access “unsubscribe” button in Gmail for Android

0
[ad_1]
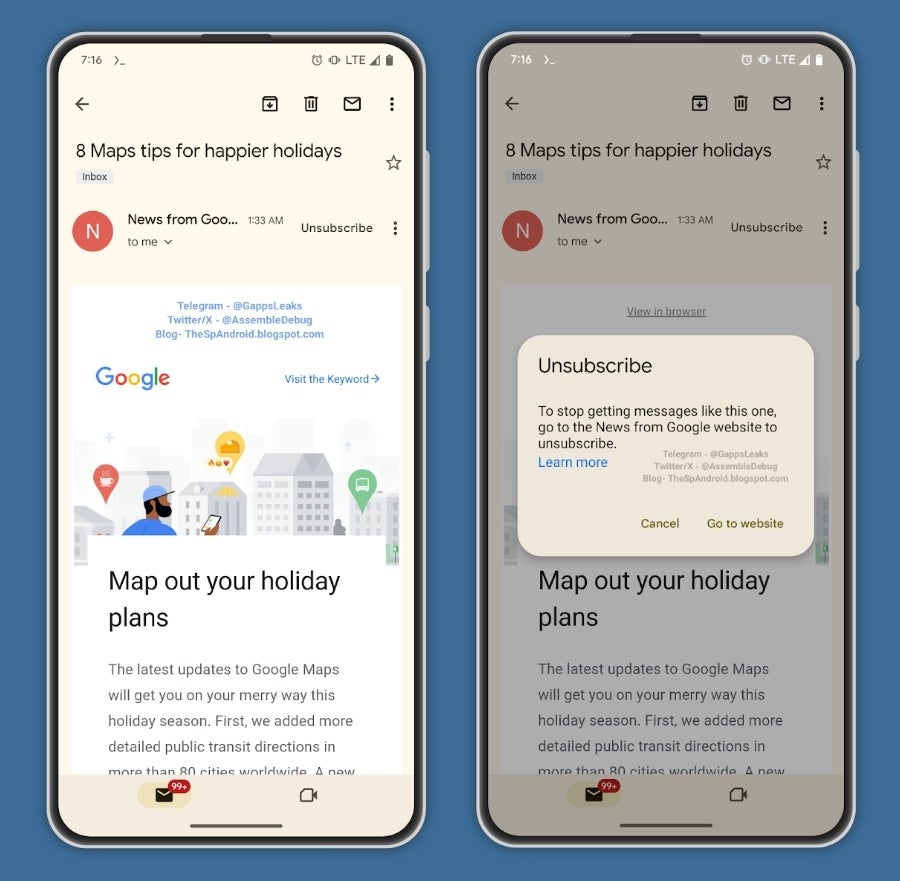
Google is testing a feature on the latest version of the Android Gmail app which has been available via the web for some time now: the ability to easily unsubscribe from promotional bulk email senders via a quick button. Once live, this will allow you to easily remove yourself from these lists without having to hunt for the “unsubscribe” link that is usually placed at the bottom of such emails.
The unsubscribe button has been part of the Gmail web experience for a while, appearing on top of emails and making it easier for users to find and unsubscribe from unwanted emails. There are times when this button will take you straight to the sender’s website where you can then unsubscribe, but oftentimes, it works automatically and provides a confirmation.

However, this had not been the case on the Gmail mobile app, where options for blocking and reporting spam are currently available but hidden inside the 3-dot menu. The lack of this easy-to-access button forces users of the Android mobile app to scroll down through the email itself to find the unsubscribe link to click on. This, of course, requires a little more time and effort from the user, as these links are usually inconveniently placed in a very small font.

The new button was spotted by AssembleDebug from TheSpAndroid in version 2023.11.12 of the Gmail app, which is currently not live for all users. Furthermore, even on this newer version of Gmail, a hidden flag had to be enabled in order to make the feature work. This usually means that the feature is not yet ready for prime time.
The introduction of this feature on the Gmail Android app — whenever it does get widely rolled out — is likely the product of the work Google has been doing to force bulk email senders to give you an easy way out. According to new guidelines that Google set earlier this year, commercial emails will have to have a one-click unsubscribe button that’s clearly visible in the message, and the process to unsubscribe will have to be completed within two days.

Based on this, it appears that Google is taking this one step further by implementing its own solution to making the unsub option a bit clearer for users. I can see this being a huge time-saver for those that like to triage their email feed before starting their workday and would appreciate having a fast and easy way to unsubscribe to those pesky email lists.


[ad_2]
Source link

Scattered Spider ransomware gang falls under government agency scrutiny

0
[ad_1]

As you may have read in our November Ransomware Review, Scattered Spider is a relatively new, albeit dangerous, ransomware gang who made headlines in September for attacking MGM Resorts and Caesar Entertainment. For small security teams, one of the most important findings about the group is their use of Living Of The Land (LOTL) techniques to avoid detection: Scattered Spider aka Octo Tempest employs everyday tools like PowerShell for reconnaissance and stealthily alters network settings to bypass security measures. They also exploit identity providers and modify security systems, blending their malicious activities with normal network operations.

In a joint cybersecurity advisory (CSA) on Tuesday, the Cybersecurity and Infrastructure Security Agency (CISA) and the Federal Bureau of Investigation (FBI) provided detailed information about the techniques leveraged by Scattered Spider. The advisory was issued in response to the recent activity by Scattered Spider against the commercial facilities sector and subsectors.

CISA and the FBI consider Scattered Spider to be experts that use multiple social engineering techniques, especially phishing, push bombing, and SIM swap attacks, to obtain credentials, install remote access tools, and bypass multi-factor authentication (MFA).

Push bombing is a targeted MFA attack in which an attacker triggers multiple login attempts against the target’s single-sign-on (SSO) portal or publicly exposed corporate apps and services. The objective is that the target will grow tired of the notifications or make a mistake and allow the access.

SIM swapping, also known as SIM jacking, is the act of illegally taking over a target’s cell phone number. This can be done in a number of ways, but one of the most common methods involves tricking the target’s phone carrier into porting the phone number to a new SIM under the control of the attacker.

Scattered Spider is a group that typically targets large companies and their contracted information technology (IT) help desks. To lend credibility to their phishing mails they often register domains like victimname-sso[.]com, victimname-servicedesk[.]com or victimname-okta[.]com.

Once the groups establish access, Scattered Spider often searches the victim’s Slack, Microsoft Teams, and Microsoft Exchange online for emails or conversations regarding the intrusion, along with any security response to see if their attack has been discovered.

The advisory describes how elaborate these efforts can be:

“The threat actors frequently join incident remediation and response calls and teleconferences, likely to identify how security teams are hunting them and proactively develop new avenues of intrusion in response to victim defenses.”

According to several sources, Scattered Spider has a relationship to ALPHV/BlackCat and has recently started using their ransomware for data exfiltration and file encryption.

The FBI seemingly struggles to arrest group members, even though they’re believed to be based in the US and other Western countries, because victims don’t come forward and share details about their incidents. For that reason, the FBI and CISA have urged victim organizations to share information about attacks with the agencies.

Another initiative that may hinder Scattered Spider’s tactics is the fact that the US Federal Communications Commission (FCC) has adopted new rules to protect US consumers from SIM-swapping attacks and port-out scams. These new rules require US wireless providers to use secure methods of authenticating a customer when they request porting a SIM card to a new device or their phone number to a new carrier.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; and disable or harden remote access like RDP and VPNs.
  • Prevent intrusions. Stop threats early before they can even infiltrate or infect your endpoints. Use endpoint security software that can prevent exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Our business solutions remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.


[ad_2]
Source link

Octo is a banking trojan terrorizing Australian Android users

0
[ad_1]

In Australia, a sophisticated Android banking trojan called Octo poses a severe cyber threat. Using various distribution methods, Octo has successfully targeted hundreds of Australians across more than 15 major banks. This trojan mimics legitimate bank login fields, luring users into entering their credentials on fake pages. By submitting their information, users are inadvertently granting access to their sensitive banking information to the threat actor.

Octo made its debut in January 2022, with its origins attributed to a threat actor known as “Architect,” presumed to be of Russian descent. The trojan shares striking similarities with another malware, ExobotCompact, raising suspicions that Architect either rebranded or is the mastermind behind both.

The trojan has historically gained initial access through the Google Play Store or via smishing campaigns. Smishing refers to the practice of sending SMS phishing messages that impersonate legitimate entities. Moreover, it is a cyber-attack that aims to steal sensitive information, such as login credentials or financial details. Octo’s primary targets are Android phones, including popular brands like Samsung and Google. Threat Fabric’s senior analyst, Dario Durando, uncovered a malicious campaign of Octo posing as a Google Chrome mobile browser update. This specific campaign resulted in at least 900 individuals downloading Octo. He claims that Octo is being rented out as malware-as-a-service, with individual threat actors using it to distribute malware.

Octo, a stealthy Android trojan, threatens users with sophisticated banking attacks

Octo proves to be a highly complex and dangerous malware strain, using various attack methods such as intercepting text messages, harvesting contacts, and even recording calls. The trojan’s capabilities extend to keylogging, overlay attacks, and resilience against uninstallation attempts. The threat actor behind Octo’s distribution in Australia operates a sophisticated overlay attack.

Dario Durando’s findings revealed the alarming ease with which users unknowingly downloaded Octo through a fake Google Chrome mobile browser update. After gaining access to the victim’s device, the Trojan executed a banking login overlay attack, a form of phishing. Once submitted, this attack successfully stole the user’s login credentials. Operating discreetly in the background, Octo proceeded to steal cookies, log keystrokes, uninstall apps, and intercept notifications, underscoring Octo’s comprehensive and intrusive capabilities.

Australia’s vulnerability to such cyber threats is exacerbated by a significant surge in scams. Reports show an 80% increase in 2022 compared to the previous year. Phishing alone accounted for approximately 25 million incidents. Stephanie Tonkin from the Consumer Action Law Centre highlighted the nation’s susceptibility to cyber threats, citing a lack of robust laws and systems to counteract scams.


[ad_2]
Source link

Apple’s Head of Security Engineering opposes sideloaded apps

0
[ad_1]

In the ongoing debate over sideloading apps, Apple’s Head of Security Engineering and Architecture, Ivan Krstic, has shared his perspective. The European Union has taken a significant step by signing the Digital Markets Act (DMA), a move that, if approved, would force Apple to allow sideloaded apps. While some argue that sideloading apps could break Apple’s monopoly, providing users with more freedom and promoting a diverse app ecosystem, Krstic presents a contrary viewpoint.

The Digital Markets Act, introduced in the European Union, identifies major online “gatekeepers.” Gatekeepers meeting specific criteria must comply with rules that promote a fair business environment, encourage innovation, and benefit consumers. Compliance involves allowing third-party access and avoiding unfair practices, with penalties for non-compliance. In this context, Apple needs to adjust its app store practices to align with these rules, should the DMA be approved.

If Apple allowed sideloading, users could download third-party apps directly to their iPhones from any website. The European Commission argues that this step is necessary for fair competition, providing users with greater options in choosing and obtaining their preferred apps.

Apple faces debate over sideloaded apps, impacting user choice and security

However, Krstic challenges this notion by saying:

“That’s a great misunderstanding – and one we have tried to explain over and over. The reality of what the alternative distribution requirements enable is that software that users in Europe need to use – sometimes business software, other times personal software, social software, things that they want to use – may only be available outside of the store, alternatively distributed.”

“In that case, those users don’t have a choice to get that software from a distribution mechanism that they trust. And so, in fact, it is simply not the case that users will retain the choice they have today to get all of their software from the App Store.”

Krstić argues that Apple allowing sideloaded apps would compel European users to seek essential software from sources other than the App Store for business, personal, or social use. This would deprive users of the convenience of accessing trusted distribution channels and could potentially damage their confidence in the safety of the apps they download.

The controversy surrounding sideloading apps revolves around a dual concern. On one side, there are privacy issues, as users could face potential security risks when downloading third-party apps. Conversely, there are worries about monopolistic practices and the decline of user freedom.


[ad_2]
Source link

A Gmail Unsubscribe button is coming for Android users soon

0
[ad_1]

Android users are now noticing a Gmail Unsubscribe button that might be arriving for their usage. This new button will help users to unsubscribe from emails or newsletters that they have no business with. Currently, if Gmail users want to unsubscribe from an email channel, they need to scroll to the bottom of the interface and find the unsubscribe button.

By making the button more obvious and in reach, Google is helping users unclutter their space faster than ever before. Previously, Google brought this unsubscribe option to users who weren’t opening emails for specific senders. Now the tech giant seems to be working on this tool to make it always available for users to access and get rid of bugging emails.

This button is already undergoing development and has been spotted by some who are familiar with this matter. From the available details, it is clear the position where this button will sit and how it’ll function. If you’re tired of getting emails from various businesses because you unknowingly signed up for their newsletter or emails, this feature will be handy for you.

You’ll soon be able to unsubscribe from annoying emails with the coming Gmail Unsubscribe button

You will probably agree that you have a ton of emails in your Gmail inbox that you have no business with. These emails come as a result of signing up to websites in a bid to access the services they offer. After making use of these services, you are often stuck with the annoying emails that they send out to their subscribers.

This is very annoying and most people resort to unsubscribing from these emails when they’ve had enough. However, to unsubscribe from these services one needs to scroll to the bottom of the email page. Here the tiny unsubscribe button sits, and most users might have a hard time locating it.

All of this is coming to an end as Google is now working on a large unsubscribe button. This new button will sit on the top right-hand side of the email interface, just next to the sender’s name. By tapping on this button, users will be able to head over to the sender’s website and unsubscribe from their emails.

At the moment, this feature is in development, with just a few Gmail users having access to it. However, Google is working to make it readily available to more users in the coming weeks. Users will be able to get access to this coming feature via an update to the Gmail app that’ll soon roll out globally.


[ad_2]
Source link

Sundar Pichai advises not to sideload apps, stick to Play Store

0
[ad_1]

Sideloading has been a trending topic lately. While Android had it since its inception, Apple is being forced to allow third-party apps and app stores. However, Google CEO Sundar Pichai’s remark hints that he doesn’t like sideloading apps from third-party stores either.

Sundar Pichai advises against sideloading apps

Google is currently embroiled in a legal battle with Epic Games over its app store practices. During a recent court hearing, Google boss Sundar Pichai expressed his concerns about sideloading apps.

Sundar Pichai has warned against sideloading, citing the potential security risks involved. He stated that sideloading could expose users to malware. “We don’t want to allow you to completely compromise your phone. It can install malware on your phone. It can compromise your safety, very significantly.” These comments appear to clash with Android’s open-source philosophy.

Google’s recent move to scan sideloaded apps for malware raises concerns. The Play Store’s new update scans third-party apps installed on your devices. It increases the company’s control over app distribution on Android.

While Google claims its Play Store offers the best security for users, a recent Kaspersky report found that over 600 million malicious apps were downloaded from the Play Store in 2023 alone. It is worth mentioning that Play Store has quite a history of delisting apps several times every once in a span.

All of this suggests that Google is tightening its grip on the Android app ecosystem. The ongoing legal battle with Epic Games is likely to further shape the future of app distribution on Android.

Google rival Apple to allow sideloading apps on iPhone

The EU’s Digital Markets Act will likely force Apple to allow sideloading apps into the iPhone. Folks at Phone Arena have drawn a parallel between sideloading and the introduction of RCS in iPhone. Apple may allow sideloading apps on iPhone, maybe by 2024. However, it will be limited to EU users.

Apple has never allowed sideloading because it poses a risk to users and the data on their devices. This was also the late Steve Jobs’ vision to keep users safe. However, how Apple or its users will address this issue will likely become clear in the coming days.

Android users, on the other hand, have always had the flexibility to install apps from either the Play Store or third-party sources. Pichai’s statements will likely draw attention and elicit mixed reactions from users and developers.


[ad_2]
Source link

Amazon fires several hundred workers as Alexa shifts focus to Gen AI

0
[ad_1]

Amazon is firing “several hundred” employees in its Alexa division. Notably, Amazon has decided to power-equip Alexa to be as smart and modern as AI chatbots like Bard and ChatGPT.

Amazon is firing several hundred employees

Amazon will be bidding goodbyes to several employees, read an internal memo obtained by Geekwire. “As we continue to invent, we’re shifting some of our efforts to better align with our business priorities, and what we know matters most to customers—which includes maximizing our resources and efforts focused on generative AI,” read an email from Daniel Rausch, Alexa and Fire TV vice president.

Raush added that the shift could be the reason why the company is letting go of several hundred “roles” employees. Engadget reached out to the company, and a spokesperson confirmed that this is indeed happening.

What’s next for Alexa with Gen AI?

Amazon recently announced that it will revamp Alexa with capabilities that mirror those of ChatGPT. Therefore, the Large Language Model will power up the update. Notably, ChatGPT also uses LLM technology.

Amazon’s SVP of Devices & Services, David Limp, emphasized that this latest model is specifically tailored for voice interactions. It caters to the preferences of Amazon’s customers, including real-time information access, efficient smart home control, and enhanced home entertainment experiences.

Alexa is getting a major update

Alexa is receiving a major update. So, it will kill the need to say the wake word “Alexa” for every request. Users will be able to issue complex commands. This includes instructing Alexa to prepare the house for bedtime every weekday at 9 PM, dim the lights, lock the doors, and adjust the temperature. All that with a single utterance. Moreover, Alexa will also focus on enhanced conversational capabilities.

Amazon’s workforce has been steadily shrinking over the past year. Because the company has implemented large-scale cutbacks for the first time in its history. The latest round of layoffs affected 180 employees in the gaming division, including the entire staff of Crown, a company-backed Twitch channel. This follows similar job cuts in the music streaming unit and gaming divisions. The cutbacks began a year ago and a total of 27,000 employees have been laid off since then.


[ad_2]
Source link

READYgg Onboards 15 Million Web2 Players into Web3 in Partnership with Aptos Labs

0
[ad_1]

Millions of players will enter web3 gaming thanks to a new partnership between READYgg and Aptos Labs realized through READYgg’s robust and talented network, all on Aptos, the blockchain with the fastest time-to-finality necessary for seamless gameplay. 

As a result of the new partnership, up to 15 million web2 gamers will migrate to web3 and Aptos. Starting November 20, players can be whitelisted for early access to the new releases launching on December 6. 

READYgg has already signed over 20 major web2 publishers, representing a library of 2,000 games played by over 200m monthly active users. Four of these web2 publishers will now operate on the Aptos blockchain by the end of 2023, with a minimum of a dozen more to follow next year.

Titles will include Runestone Keeper, a roguelike dungeon crawler game (PC/Android/iOS), Rescue Robots Sniper Survival (Android), a first-person action game, Minijuegos, a hypercasual platform, and ToroFun, a browser-based social gaming portal. All these titles will feature web3 elements, such as non-fungible tokens (NFTs), while Minijuegos and ToroFun will also boast an innovative NFT-based loyalty system. 

In addition to benefiting from a performant blockchain with speed and asset portability built-in, publishers joining the READYgg / Aptos ecosystem will enjoy potential funding or grants through the READYgg $RDYX token – known as “The Gamer’s Token” – and predictable Aptos usage fees empowering publishers to run web3 components with less exposure to price volatility.

“It is difficult to overstate just how overjoyed we are about this commitment from Aptos Labs,” said David S. Bennahum, CEO and co-founder of READYgg. “Bridging web2 games to web3 has always been our goal, which is why we’ve built a range of tools traditional publishers can use to seamlessly reach a web3 audience and bring their typical users into the world of on-chain gaming.” 

“Aptos Lab’s expertise will ensure that millions of web2 gamers can get to grips with web3 very quickly, without having to contend with any kind of imposing learning curve,” said Christina Macedo, COO & Co-Founder of READYgg. “They can just have fun, and that’s all that matters”

“This partnership with READYgg will accelerate the delivery of studio-quality web3 games, user experiences, and compelling ownable assets,” said Mo Shaikh, co-founder & CEO of Aptos Labs. 

From the start, READYgg’s vision has been to enable billions of people—developers, players and content creators, in particular in emerging markets—to have the opportunity to access and appreciate web3 easily through games and game economies.

READYgg’s tools and ecosystem democratize access to web3 game creation and open a path to true mass adoption and scale into web3. The partnership with Aptos Labs will expand what’s possible in web3 gaming and deliver unparalleled UX on par or better than anything worth playing on web2.

About Aptos Labs

Aptos Labs, co-founded by Mo Shaikh and Avery Ching, is dedicated to creating better network tooling and seamless usability to bring the benefits of decentralization to the masses. Having now raised over $400M, Aptos Labs is backed by top-flight investors, including a16z, Jump Crypto, Binance Labs, Dragonfly, PayPal Ventures, Andreessen Horowitz and Franklin Templeton Investments

About Aptos Network

Aptos is a next-generation Layer 1 blockchain. Aptos’ breakthrough technology and programming language, Move, are designed to evolve, improve performance and strengthen user safeguards. Please visit the Apotos Foundation for more information on the Aptos blockchain.

About READYgg

READYgg uses blockchain and game development technology to connect and empower games. The company specializes in supporting publishers and studios as they evolve to web3 while providing the best possible experience to their game communities.

  1. 6 of the Best Crypto Bug Bounty Programs
  2. The Benefits Of Blockchain In The Travel Industry
  3. What is Blockchain Gaming and its Play-to-Earn Model?
  4. The Advantages of a More Secure and Safer Blockchain
  5. The Rise of Blockchain Gaming and Secure Marketplaces

[ad_2]
Source link