6 FinOps Principles and Best Practices

0
[ad_1]

FinOps holds the idea that businesses can reach their desired peak performances without cloud wastages. Read here to see the principles guiding these ideas. 

FinOps is becoming the backbone controlling the usage and the amount of money an organization spends on cloud resources. This is because it preaches the concept of an organization taking performance and achievements to new peaks while keeping costs low. 

In other words, FinOps is a concept or culture that is aware of all the unnecessary expenses a business covers while operating in the cloud. Below, we will discuss some of the principles and practices that help implement FinOps. 

What is Finops, And How Does it Work? 

Understanding what is FinOps in the cloud can be the gateway that will help a company or an organization to make headway in reducing their cost of operations. FinOps is simply a merge of tech and finance — basically, teams from the tech, IT, and financial sectors coming together to help reduce the cost of operations. In other words, FinOps is also the process of using quality services or operating at the highest level without having to spend a large amount of money. 

This means that every team within an organization comes together to analyze the amount they spend on their work resources. This analysis aims to know where to cut costs without putting the quality of work at risk. 

The fact remains that many organizations pay for many work resources, especially cloud resources, without using them. In other scenarios, they sometimes overpay for a resource they are only going to use for a short period or buy more than they actually need. This leads to wastages that can amount to thousands and, for large organizations, millions of dollars. This is precisely what the idea of FinOps wants to clear up — helping teams in an organization understand they can still operate effectively and efficiently without wasting too many resources. 

The idea of FinOps isn’t a passive one. It needs everyone on board: the engineering team, finance, the executives, associates, etc. It’s not merely cutting costs — for instance, using a FinOps solution like Globaldot helps an organization make more informed and insight-rich decisions. 

6 FinOps Principles and Best Practices 

Below are some of the best principles and practices an organization can apply to reduce costs and improve quality. 

One of the things that characterizes the traditional methods of optimizing costs is that it is too department-centric. In other words, each department was concerned about reducing their costs in the cloud, often leaving other departments out. One of the basic FinOps principles is collaboration from all the departments or teams in an organization. 

The emphasis of FinOps has always been on all the different teams in an organization coming together to optimize cost and performance. The finance team of an organization is presumed to be more knowledgeable about FinOps. Collaboration among different departments enables more knowledgeable ones to educate the less knowledgeable, such as the engineering or IT department, on reducing cloud costs. 

  • Transparency and Cost Visibility 

One of the principles of cloud FinOps is that all teams in an organization should be open about the amount they spend and their performance data. One way to uphold organizational transparency is by providing a comprehensive overview of cloud spending. 

Cost visibility digs deep into the spending landscape of an organization for as far back as many years. The primary purpose of cost visibility is to know the spending mistakes of an organization and determine how this can be corrected. 

  • Centralization and Unified Goal Setting 

Having a centralized, unified goal setting can only come from collaboration between all the teams in the organization. When there’s collaboration between all the teams in the organization, it leads to a unified goal setting. 

This means all the teams in the finance, IT, marketing, and technology departments work together to make goals that will move the organization forward. Having all teams in all departments come together helps everyone to be on the same page. Each goal a team is making compliments that of the other team. 

  • Governance and Creation of Policies 

One of the principles guiding the FinOps culture in an organization is the set of rules that every team member must abide by. This can only happen through governance. Governance as regards FinOps is the creation of policies that control members’ cloud usage and, subsequently, the organization’s cost savings. 

Labelling and tagging cloud resources and services is one of the best FinOps practices that help to ensure visibility and transparency consistently. Tagging is the process of labelling or annotating all the resources in a cloud infrastructure so that each can be read and traced back at any time. 

The tagging of each cloud resource can be according to their costs, the department using them, the specific project they featured in, or even a combination of these three. Ultimately, it provides a holistic form of visibility that allows an organization to know how much they are spending at any moment, trace, and put an end to overspending. 

  • Budgeting and Forecasting 

Budgeting and forecasting are two principles that are very crucial in FinOps as they are what help guide an organization in the right direction. These two components are primarily concerned with making sure a company’s budget concerning cloud resources is precise and not wasteful. 

Hence, they determine how much an organization can spend on specific cloud resources and services while considering that the organization can scale up at any time. Budgeting is as simple as allocating funds, while forecasting, in this case, makes accurate predictions of how much expandable a business might be or grow within a specific time. 

Wrapping Up 

Above was a discussion of the meaning of FinOps and how it helps an organization balance its performance and cloud costs. However, for FinOps to be fully implemented in any organization, some principles and practices must be in place. 

These principles and practices include collaboration among teams, transparency, and cost visibility. Furthermore, it also includes other things like governance, unified goal setting, tagging & labelling, budgeting & forecasting, etc. Apparently, introducing all these practices and principles will help optimize cloud costs and performance by a wide margin. 

  1. Advantages of a Cloud VPS Server
  2. How To Safeguard Your Data With Cloud MRP System
  3. The Role of DevOps in Streamlining Cloud Migration Processes
  4. Insights on Google Cloud Backup and Disaster Recovery Service
  5. The Evolution of Captive Portal to Cloud Authentication Solutions 

[ad_2]
Source link

Nothing Chat pulled from Play Store due to security concerns

0
[ad_1]

It turns out that the new Nothing Chat has some security concerns, as new reports have revealed. This service is prone to security compromises that can result in the reveal of users’ personal information. Despite being impressive and all, this new feature from Nothing doesn’t provide users with end-to-end encryption for their chats, and this isn’t the way to go.

A few days ago, Nothing took to their various platforms to announce the launch of their new Chat feature. This brought iMessage support to Nothing devices using a third-party service known as Sunbird. With the help of this service, nothing was able to eradicate the green bubble blue bubble identification while texting an iPhone.

This feature’s launch shook the Android tech community from various angles, with some wanting to know how exactly Nothing pulled this stunt off. The curiosity of netizens and fans led to them digging into this new feature to find out more about it, and their findings are quite surprising. Users of Nothing devices should not use this feature for the following reasons that this article points out.

Security flaws & shortcomings of the new Nothing Chat feature exposed

Over the past months, Google has been pushing Apple to adopt RCS messaging services. The aim of this is to make texting between an Android device and an iPhone more secure and feature-packed. Apple on their part have locked Android texts under the green bubble for quite a while, limiting them to only SMS texting capabilities.

In a bid to break the texting barrier that Apple creates between iPhone and Android devices, a ton of developers stepped into the scene. One such developer is the Sunbird app, and this is Nothing’s partner on this iMessage-supported Chat feature.

While their iMessage-supported product gets the job done, it also brings security threats to the end users. From recent findings, it becomes obvious that this service runs on HTTP and not HTTPS, hence the lack of a security defence. So users who upload their personal information on this service are at risk of bad actors stealing them.

In addition to this security flaw is the fact that messages exchanged using this feature are not end-to-end encrypted. So, after getting their personal information accessed, users of this service can also have their chats spied on. There is also the accusation that Sunbird uses the BlueBubble App service to remove the green bubbles on iMessage.

Due to these security concerns, Nothing has pulled the Chat app off the Google Play Store. The green bubble, blue bubble era is coming to an end with Apple preparing to launch a more secure messaging channel. Until then, users can avoid other features or services that claim to eradicate the messaging barrier between Android and iPhones.


[ad_2]
Source link

OpenAI has a new CEO, and he used to run Twitch

0
[ad_1]

Over the course of a single weekend, OpenAI has been completely turned upside down. On Friday, the company fired CEO Sam Altman. After a bit of a back-and-forth, the company was able to track down a new Lord and Master. According to reports, OpenAI brought on Emmet Shear as the new CEO.

The situation with OpenAI seems to change and shift by the hour. Just an hour after Microsoft confirmed that it had hired Sam Altman, we got the news that Emmet Shear will be taking the helm. Sheer is the co-founder of Twitch. He resigned from his post as CEO of the streaming company earlier this year.

OpenAI hired Emmet Shear, as the company keeps from sinking

The company’s chief technology officer, Mira Murati, was appointed the interim CEO over the weekend while the company was negotiating Altman’s return. Now, there’s a new sheriff in town, but this might be temporary as well, Sheer made a post on X saying, “Today I got a call inviting me to consider a once-in-a-lifetime opportunity: to become the interim CEO of @OpenAI.” In the post, he said that he mulled it over for a couple of hours before accepting the offer.

In his post, he noted that the position is an interim CEO, which means a temporary position. It seems that the company still has its options open. In any case, Sheer outlined some plans he has for the next 30 days.

He’s going to hire an independent investigator to “dig into the entire process leading up to this point and generate a full report.” Next, he’s going to speak to as many OpenAI personnel to learn as much about the company. Lastly, he’s going to reform the management and leadership team in the company.

These are pretty vague plans for the moment, but this news is still hours old; it’s still fresh from the oven. Right now, we don’t know what’s going to happen with OpenAI, as the company is dealing with fluctuating leadership, pressure from upset investors, and a mass exodus of its staff. We’ll keep you up to date on what happens next.


[ad_2]
Source link

Threat Intelligence with Sandbox Analysis: Security Analyst Guide

0
[ad_1]
Threat Intelligence with Sandbox Analysis

Threat intelligence (TI) is critical to organizations’ cybersecurity infrastructure, allowing them to keep track of the evolving threat landscape and ensure timely detection. However, TI Solutions’ information frequently lacks the specifics required for thorough security measures. One way to address this problem is by using malware analysis sandboxes.

What is Threat Intelligence?

Threat intelligence refers to the information about well-studied and emerging threats extracted from large data arrays. It has actionable indicators of compromise (IOCs). It works with security information and event management (SIEM) systems to find problems on the network and application levels and help with security decisions.

There are two types of TI sources: internal and external. For a proper security posture, a combination of both is required.

Internal sources of TI include data collected from the organization’s own networks and systems, such as:

External sources of TI include information collected from outside the organization, such as:

  • Open-source intelligence (OSINT), such as news articles, social media posts, and security research blogs
  • Commercial threat intelligence feeds
  • Government and industry reports
  • Information sharing and analysis centers (ISACs)

One example of external threat intelligence is ANY.RUN’s Threat Intelligence Feeds, a service that offers near-real-time visibility of the global threat landscape and is compatible with various SIEM solutions.

What is Sandbox Analysis?

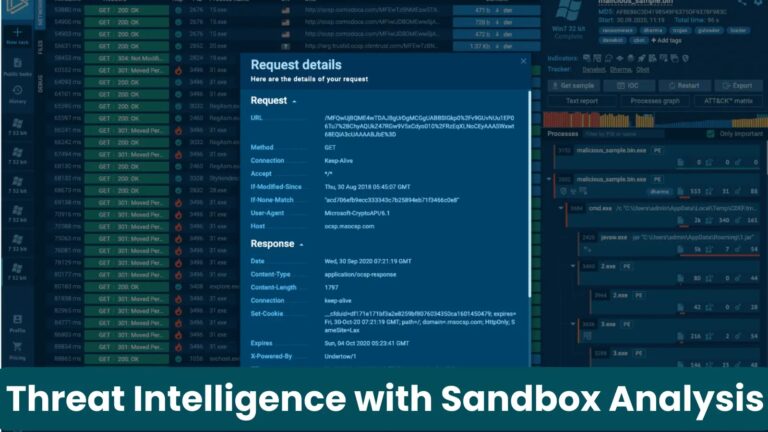
Sandboxing is a method of examining malicious files and links by isolating them in a safe environment of a virtual machine. This allows security teams to analyze potential threats without putting their systems at risk.

For instance, ANY.RUN’s cloud-based malware analysis sandbox lets users upload any file or URL to it and see how it behaves. It also allows them to directly interact with the infected system and files like on an ordinary computer. The sandbox collects data, processes it, and presents crucial information, such as IOCs and malware configs, to users, which then can be used to make better security decisions.

Document
14 Days FREE Trial

It Includes Private space for your team with a productivity trackerUp to 20 minutes of analysis per tastefully interactive Windows 7, 8, 10, 11 VMs.

How Sandboxing Enriches Threat Intelligence

Understand the behavior of malware

Threat intelligence feeds provide valuable information about emerging threats and vulnerabilities, but they often lack granular details about the specific actions of malware. With sandbox analysis, it is possible to closely observe the behavior of threats, such as how they communicate, how they spread, and what vulnerabilities they exploit. 

The insights gained from sandbox analysis can be used to enrich threat intelligence feeds with more actionable details. Such findings can be used to identify additional information on the malware, update signatures or detection rules, and develop targeted mitigation strategies.

Validate threat intelligence feeds 

The accuracy of TI feeds may not always be guaranteed, requiring additional validation on the part of security teams. Sandboxing allows analysts to run the suspected file or URL in a safe environment after evaluating alerts raised by feed information.

By observing the behavior of the malware in the sandbox, analysts can confirm whether it exhibits malicious actions. This validation process helps ensure that security teams respond to genuine threats and not waste time on false positives.

Identify relationships between threats 

Threat intelligence feed databases often contain disconnected data points about individual threats, making it challenging to identify patterns and relationships between them. This fragmented view of a single threat campaign can hinder effective response. 

By submitting the samples identified by feeds as malicious to a sandbox, analysts can observe the behavior of the malware and extract more IOCs, such as IP addresses, that can be cross-referenced with the feed database, revealing other files associated with the same malicious campaign and the broader scope of the threat’s potential impact.

How to integrate threat intelligence feeds with a sandbox

Security teams looking to integrate threat intelligence feeds and sandboxing platforms require tools that work seamlessly together. ANY.RUN offers a unified solution that simplifies this integration process.

ANY.RUN has an extensive database of over 50 million samples of malicious files and links. This vast repository, constantly updated with 14,000 new samples each day, is fueled by the contributions of over 400,000 analysts worldwide.

By leveraging ANY.RUN’s Threat Intelligence Feeds, organizations gain real-time access to a continuous stream of up-to-date information on both known and emerging threats. Updated every two hours, the service provides not only a database of IOCs but also contextual information, including samples that users can further analyze in ANY.RUN’s interactive sandbox to gain deeper insights into threats.

Conclusion

Using a combination of threat intelligence feeds and malware analysis sandboxes leads to effective threat detection and examination. Feeds provide real-time identification of suspicious files and links, enabling sandboxes to conduct a thorough analysis, enhancing security decision-making and safeguarding organizations from cyberattacks.

Discover how the ANY.RUN sandbox can enhance your organization’s security posture with a 14-day free trial that offers Windows 10 and 11 VMs, a private space for your team, extensive set of analysis tools, and comprehensive reports with IOCs and configs. 


[ad_2]
Source link

Student discount: Get 50% off Malwarebytes

0
[ad_1]

Technology is now an indispensable part of student life, used for everything from socialising and calling home, to writing and researching essays. Unfortunately, that makes students taking their first steps into adult life a prime target for cybercrime.

But how can you be sure the Wi-Fi network you’re connecting to at your library or local coffee shop is safe? What about when you’re inside college walls? More than that, your social media accounts likely hold a lot of information about you, information you don’t want to get into the wrong hands.

It’s hard to know who to trust online, and one click on a dodgy link could lead to compromised accounts, identity theft or even malware.

And, as one student we spoke to said “Nothing is worse than losing a school essay”.

We know you need to protect yourself and your important files online, but we also know that you’re probably feeling strapped for cash at the moment.

We’ve got good news. Malwarebytes is now offering 50% off our products to students, wherever you are in the world.

Here’s what we can help with:

  • Protect your important essays from ransomware and other nasties with Premium Security
  • Help you shop online safer, with protection against infected ad and credit card skimmers in Browser Guard
  • Keep your identity safe and protect your social media accounts with Identity Theft Protection
  • Block trackers and ads with Browser Guard
  • Work safely in coffee shops, libraries and other public places with Privacy VPN
  • Game faster and in peace while staying protected by using Play mode to suspend notifications

Find out more and see pricing on our student discount page.


[ad_2]
Source link

Galaxy A15 5G renders leaked as Samsung prepares for launch

0
[ad_1]

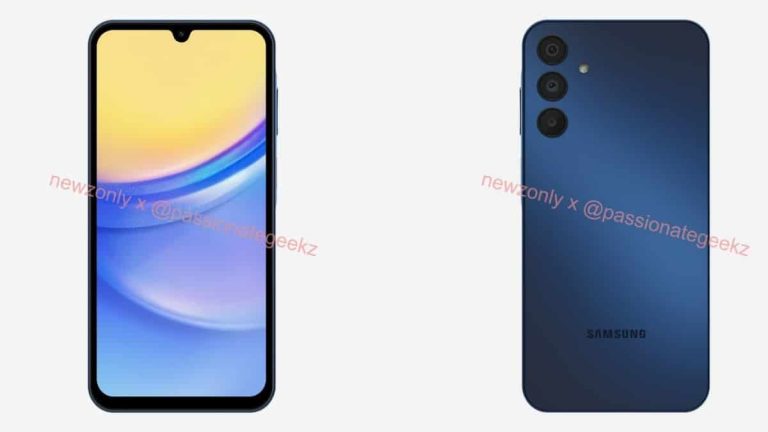
Alongside the Galaxy S24 series, Samsung is working on a bunch of budget and mid-range smartphones for 2024. The Galaxy A25 5G, Galaxy A15 LTE, and Galaxy A15 5G are among the devices expected to go official within the next few months. We have already seen the former two in leaked renders, including an exclusive leak of the Galaxy A25 5G from us. The Galaxy A15 5G has now shown up in renders ahead of launch.

Leaked Galaxy A15 5G renders show a familiar design

Renders of a dark blue-colored Galaxy A15 5G were recently published by Newzonly in collaboration with @passionategeekz. As expected, the phone shares its design with its 4G sibling. We have a flat display with a U-shaped notch and notable bezels, particularly the chin. Samsung has slightly raised the frame around the power and volume buttons on the right side, something we have seen on the Galaxy A25 5G and Galaxy A15 too.

The power button appears to incorporate a capacitive fingerprint scanner, which is a norm for low-cost smartphones. The edges are otherwise flat and so is the back panel. On the back, the Galaxy A15 5G has the same camera array that we have seen on all Samsung phones this year and leaked renders of upcoming models. The company has fitted the phone with three cameras all of which protrude out of the back panel individually.

Samsung is seemingly creating a brand identity for Galaxy devices, and that identity is a bump-less vertical rear camera layout. The new budget handset has an LED flash unit next to the camera column. The renders don’t show the Galaxy A15 5G from other angles, so we can’t tell you whether the phone features a 3.5mm headphone jack. We hope it does. The publication says the handset may also come in black, yellow, and other colors.

The 4G and 5G models of this phone feature the same chipset

Samsung will reportedly equip the Galaxy A15 5G with a 6.5-inch FHD+ (2,400 x 1,080 pixels) display with a 90Hz refresh rate. It features MediaTek’s Dimensity 6100+ 6nm processor. It’s the same chipset as the Galaxy A15 LTE’s Helio G99, with the difference being 5G support for the former. The octa-core SoC has a peak CPU speed of 2.2GHz and features the Mali G57 GPU.

The Galaxy A15 5G may feature a 50MP primary rear camera, 5MP ultrawide lens, 2MP macro camera, and 13MP selfie shooter. It should come with up to 128GB of storage and possibly 6GB of RAM. The device will support expandable storage via a microSD card. A 5,000mAh battery will fuel the phone with 25W fast charging. Samsung may launch the phone in early 2024 if not before the end of 2023.


[ad_2]
Source link

Sam Altman says goodbye to OpenAI and hello to Microsoft

0
[ad_1]

There’s been a whirlwind of drama circling OpenAI over the weekend, and the winds kee blowing. After Sam Altman butted heads with the company’s board, the former is now out of a job… well he was. According to a new report, Microsoft just hired Sam Altman.

Let’s catch you up

So, in case you don’t know, Sam Altman was fired from OpenAI on Friday. This news came as a shock to everyone, Altman involved. The board stated the reason as being that he wasn’t “consistently candid in his communications” with the board. We’re still not sure what he wasn’t quite honest about, but it led them to jettison him. The company’s chief technology officer, Mira Murati was appointed the temporary CEO until the company could find a permanent CEO.

Then, OpenAI sings “Baby Come Back”

After just a day, OpenAI entered talks with Altman to return to the company. The quick decision to fire him did not sit well with investors and many of the workers at the company threatened to leave. So, losing investors and employees threw the company into a spin. If Altman agreed to come back by a 5PM EST deadline, the employees wouldn’t walk.

However, a truce wasn’t reached by that deadline or the second deadline set. This means that OpenAI is in a massive pickle at the moment.

Microsoft just hired Sam Altman

This situation, which happened over a single weekend, mind you, has just gotten a bit weirder. OpenAI didn’t only lose Sam Altman, but it also lost the company’s president and former board member Greg Brockman. Well, the two were already contacting investors and looking to start a new company before OpenAI asked for their return.

However, after no agreement was reached, Microsoft stepped in and snatched up Altman. In a statement on Sunday, Microsoft CEO Satya Nadella said “we remain committed to our partnership with OpenAI and have confidence in our product roadmap.” So, it seems that the company is still investing in OpenAI, but we don’t know for how much longer.

In any case, it hired Altman, Brockman, and several colleagues to lead a new advanced AI research team at the company. Since this is still new, we’re all unsure how the company is going to handle everything. Its AI is built on OpenAI’s LLMs. If OpenAI’s fortunes don’t improve, then it, along with all of the AI tools it’s powering, could go down.

Will Microsoft ditch OpenAI for its own AI? Will the company pull its funding for OpenAI and let that ship sink? Who knows?

Civil war at OpenAI

Right now, OpenAI is going through a rough transition. With Altman gone, many of the staff are not happy. They’ve set their demands; either the board goes or they go. They want the board to be kicked out of the company or they walk out. Those are similar to Sam Altman’s conditions to return. He wanted “governance changes”.

Now, these changes could happen one way or another. And, speaking of changes, the company has appointed a new CEO. Twitch co-founder and ex-CEO Emmit Shear has taken the helm. With this new face, there’s a new hope that things will start looking up for the company. This story is still developing, so we’ll keep you up to date on what’s going on.


[ad_2]
Source link

Tinder goes beyond photo swiping with redesigned profile pages with prompts, quizzes, and tags

0
[ad_1]

One of the world’s most popular dating apps is gearing up for a makeover with a fresh set of profile and discovery features designed to align with the evolving connections of the new generation of daters.

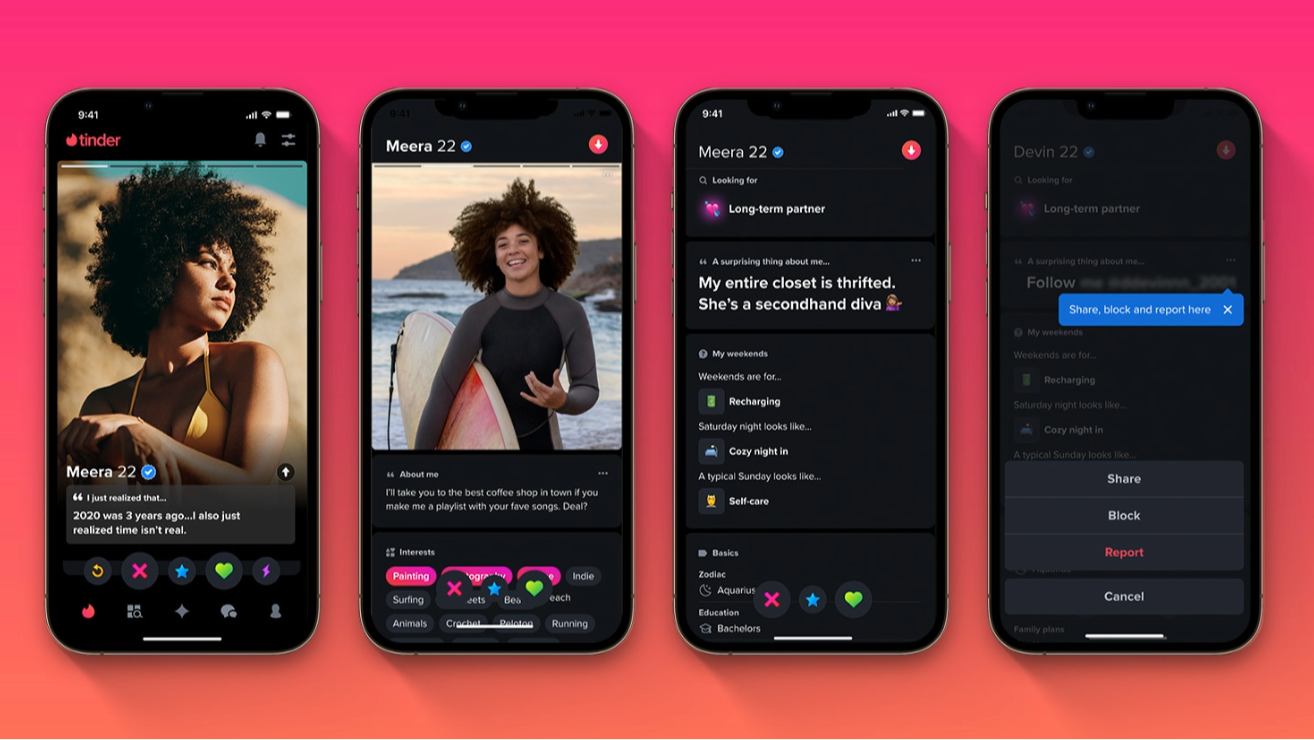
Tinder is shaking things up by giving profile pages a facelift, aiming for a more informative layout to kickstart smoother conversations. According to an official blog post, the app is rolling out features like profile prompts as conversation kick-starters, profile quizzes, basic info tags, and a dark mode.


Mark Van Ryswyk, Tinder’s Chief Product Officer, noted that the company recognizes the shift in priorities for the new generation of daters, that “prioritizes value-based qualities such as respect (78%) and open-mindedness (61%) over looks (56%).” This shift is the driving force behind the introduction of these new features.In the latest update, Tinder users can now leverage profile prompts, allowing them to share responses to prompts like “The key to my heart is,” “The first item on my bucket list is,” and “Two truths and a lie.” Additionally, users can craft quizzes about themselves, providing potential matches with insights.

Another addition is the option to share basic information through profile tags, covering interests, pets, drinking habits, and zodiac signs. Tinder has also enhanced user safety by introducing the ability to report specific content within these sections.

Beyond these features, Tinder is giving its interface a makeover, incorporating new animations, including a revamped “It’s a Match!” screen, and introducing a dark mode setting “for late-night activity or discreet public matching.”

Staying ahead of the tech curve, Tinder had previously delved into AI with a feature helping users select their best photo. Additionally, the app introduced a feature that lets friends play matchmakers by viewing and suggesting potential matches.


[ad_2]
Source link

Intel Released Urgent Patch For Reptar Vulnerability In Its CPUs

0
[ad_1]

Intel recently released a critical security fix for a newly discovered vulnerability affecting its CPUs. Dubbed “Reptar,” the vulnerability affects most modern Intel chips, attracting attention from numerous security researchers. Considering its severity, patching the vulnerable systems immediately is inevitable.

New Reptar Vulnerability Risks Intel CPUs

According to a recent Intel advisory, the tech giant patched a high-severity vulnerability affecting its CPUs, urging users to update their systems at the earliest.

As explained, the tech giant found a privilege escalation vulnerability in its CPUs that could allow an authenticated adversary to access sensitive information or trigger a system crash. Stating the issue in the advisory, Intel described,

Sequence of processor instructions leads to unexpected behavior for some Intel(R) Processors may allow an authenticated user to potentially enable escalation of privilege and/or information disclosure and/or denial of service via local access.

This vulnerability (CVE-2023-23583), identified as “Reptar,” received a high-severity rating with a CVSS score 8.8.

While this discovery seems like a usual vulnerability detection, its severity appears from the fact that this vulnerability also caught the attention of Google researchers.

According to a recent post, Google researcher Travis Ormandy and other researchers from the Google Project Zero Team also discovered this vulnerability independently. And what caught their attention was the peculiarity of this flaw’s behavior.

We observed some very strange behavior while testing. For example, branches to unexpected locations, unconditional branches being ignored and the processor no longer accurately recording the instruction pointer in xsave or call instructions.
Oddly, when trying to understand what was happening we would see a debugger reporting impossible states!

Ormandy’s post presents a detailed analysis of the vulnerability. Following this discovery, Google researchers also contacted Intel to report the matter. Intel also acknowledged their bug report in its advisory.

Patches Being Released For The Users

To patch this flaw, Intel released a microcode update that the respective vendors have started rolling out to the consumers. For instance, NetApp and Citrix have recently released updates for their users to address this vulnerability. All users must ensure to update their computers, mobile devices, and servers with the latest system and BIOS updates to receive the patch.

Besides, for systems where an immediate patch isn’t possible, Ormandy recommended disabling the “fast strings via the IA32_MISC_ENABLE model specific register.” However, the researcher warned that this mitigation strategy may cause “significant performance penalty” and so shouldn’t be applied unless inevitable.

Let us know your thoughts in the comments.


[ad_2]
Source link

Fortify Your Online Business – Security Tips for Starting an e-Commerce Website

0
[ad_1]

From installing firewalls to choosing secure hosting, every aspect is crucial in online business.

Are you in the process of creating an e-commerce website? Many entrepreneurs choose to open online businesses because they can save a lot of money on overhead costs. But if you don’t have the proper security in place, it may cost you thousands of dollars to recover after a website breach. 

Every day, cybercriminals are finding new ways to hack into people’s business accounts to steal information and money. To help safeguard your online store, we’ve provided a guide on how to build a secure e-commerce website to protect your business from potential threats. 

Choose a Trustworthy Platform to Build Your Website

For people to buy your products and services, you must create a website where customers can order and pay for what they need. The top website builders will have a plethora of features to help you build a secure website for your customers, such as drag-and-drop tools and customizable templates. 

On the other hand, web builders must guarantee the safety of your customer’s information. The builder you choose must not steal information and sell it to third-party organizations. You should also choose a website builder with hosting services so your site loads faster. 

Choose a dedicated web hosting service that is more secure compared to sharing a server with other websites on the internet. 

Utilize HTTPS for Your Site 

Hypertext Transfer Protocol Secure (HTTPS) provides a secure and encrypted connection between a user’s browser and the website server. The encryption ensures that sensitive data like bank account details, credit card information, and addresses are protected from cybercriminals.  

What’s more, websites that have HTTPS addresses are recognized as being more trustworthy. It provides a padlock icon on your website’s URL that shows the user the site is secure and protected from threats. 

Using HTTPS can also boost your page ranking on search engines like Google because they prioritize sites with these credentials. 

Lastly, HTTPS requires a Secure Socket Layer Certificate (SSL) to transfer data securely. If your online business accepts card payments, then you must have an SSL certificate to remain compliant with Payment Card Industry Data Security Standards. 

Utilize Web Application Firewalls

E-commerce websites rely heavily on complex web applications such as SQL injections and cross-site scripting. However, these applications can have vulnerabilities. A Web Application Firewall (WAF) can give your website an extra layer of protection by detecting and blocking these threats to prevent breaches.  

When there are potential threats, you may have to temporarily shut down the website to protect your customers. This can be a costly exercise. But a Web Application Firewall can prevent website downtimes by filtering out malicious traffic that can cause your website to shut down.  

Strong Password Policies 

When you create your e-commerce website, you must administrate strong password policies for both your staff and customers. Encourage customers to create strong passwords that are at least 8 to 10 characters long using numbers, special characters, and capital letters. 

Furthermore, you should allow your customers to set up two-factor authentication so they can be notified if someone is trying to gain access to their accounts. Advise your customers not to use their names, ID numbers, or cell phone numbers to sign into the website. 

You can prevent users from creating weak passwords by not allowing them to go to the next stage of the sign-up process unless they meet the password policies. Or you can have a password generator on the site so users can automatically create secure passwords.  

Update Your Website Regularly 

Another way you can prevent cyber threats when creating an e-commerce website is to update your site and plugins regularly. There will be regular security patches that can address new vulnerabilities. These updates can include enhanced security measures to strengthen your website’s defences. 

Updating your website and plugins will ensure that your e-commerce business stays compliant with industry standards. It can also improve your website’s overall performance by fixing bugs and enhancing certain functionalities. This will improve the user’s experience whenever they visit your website. 

With a fast and secure website, your customers and visitors will feel more at ease, and it will provide a level of credibility to your online business. 

Final Thoughts 

Creating a professional e-commerce website is a long and complex process. If you’re not careful, you’ll create a site that’s easy for hackers to gain access to. 

But with the right tools, strategies, and knowledge, you can create a secure site that customers feel comfortable signing in to. Use the tips in this article to build a successful website that’s secure and trustworthy. 

  1. The Advantages of a More Secure and Safer Blockchain
  2. How To Make Drupal Migration Successful: 6 Useful Tips 
  3. How to Install Microsoft Exchange Updates with Reliability
  4. Casio’s Data Breach: Database Security a Major Challenge!
  5. PDF Security – How To Keep Sensitive Data Secure in a PDF File

[ad_2]
Source link