A week in security (November 13 – November 19)

0
[ad_1]

November 17, 2023 – The ALPHV/BlackCat ransomware group has filed a non compliance complant with the SEC against one of its victims.

November 17, 2023 – Learn how ThreatDown bundles help IT teams save time, money, and stop more threats.

November 16, 2023 – An alarm system company that allows people to call for help at the touch of a button has suffered a cyberattack, causing serious disruption.

November 15, 2023 – In October, we witnessed the takedown of several high-profile groups, including alleged Sony attacker RansomedVC.

November 15, 2023 – Microsoft has patched a total of 63 vulnerabilities this Patch Tuesday. Make sure you update as soon as you can.


[ad_2]
Source link

Gang of 5 Employees Stole The Customer Data

0
[ad_1]

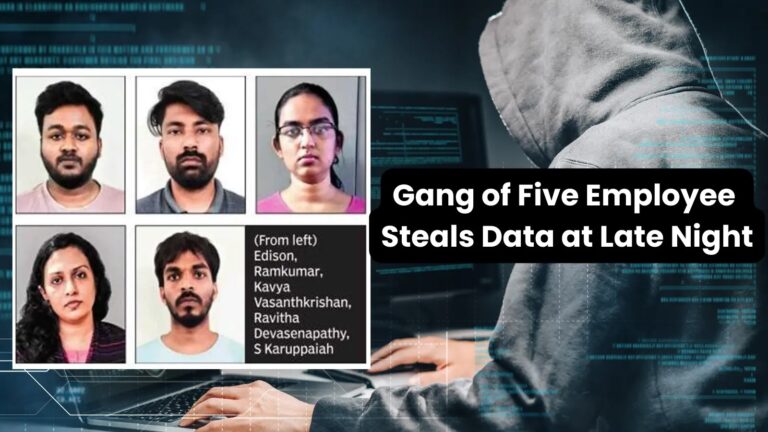
The sequence of events sounds like it was taken straight from a movie script. Five software programmers were working late into the night, chatting on their phones while they worked.

During the wee hours of October 9, between 1:00 am and 4:00 am, they managed to hack the company’s primary server and successfully gained access to sensitive customer data, which they then proceeded to steal.

The following day, all five software company employees in Chennai showed up to work in Bengaluru or Chennai, where they joined their coworkers in expressing their shock and horror at the loss of sensitive information belonging to five of the company’s most valuable clients.

The business owner had no idea what was happening as he saw his six years of hard work go down the drain. His workforce mostly defected. 

Then he discovered that his US-based clients had been cut off because the operating system he used, Amazon Web Services (AWS), had changed their credentials. He tried to contact them but was met with silence.

Document
Protect Your Storage With SafeGuard

StorageGuard scans, detects, and fixes security misconfigurations and vulnerabilities across hundreds of storage and backup devices.

He eventually went to the police in Chennai, India, about the cybercrime. The investigators followed the internet protocol address and other technical facts from where the server was accessed and gained a breakthrough within a few hours. 

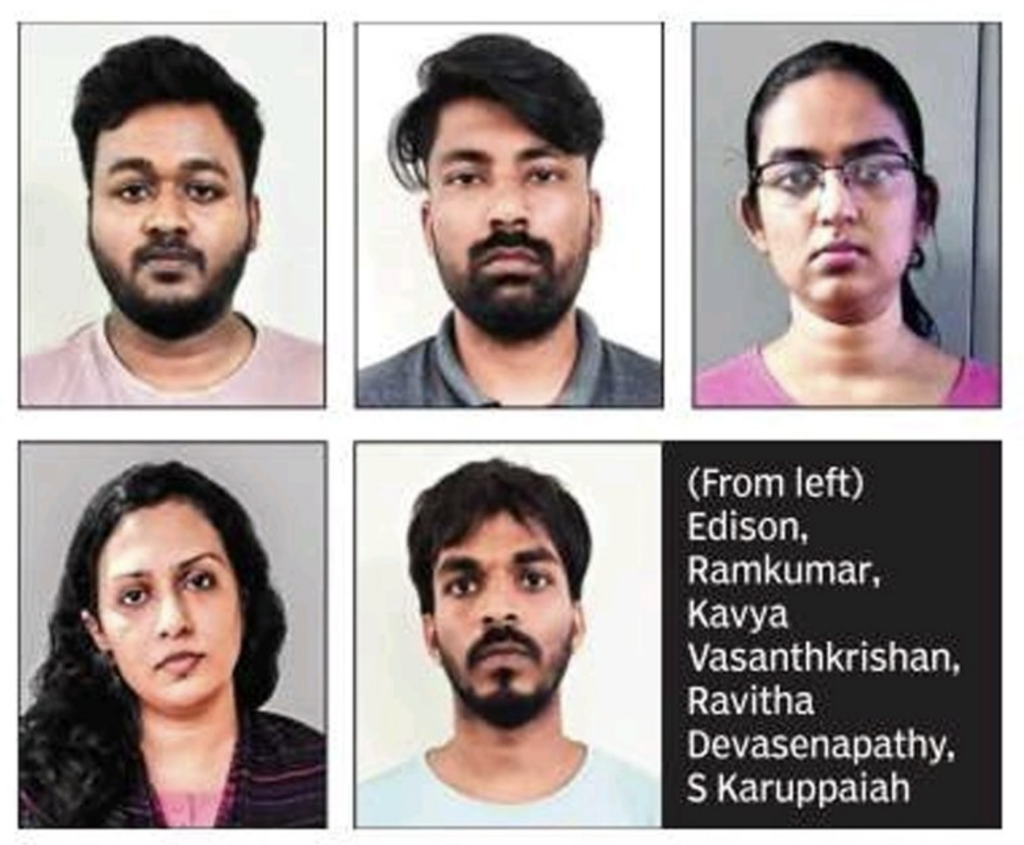
Cyber Security News learned from the local authorities that they narrowed it down to five people: two in Chennai and three in Bengaluru, all firm employees. Edison, 29, who was responsible for the company’s operations in Chennai, was the one who logged onto the server and began the theft. According to their findings, he participated in a conference call with four other people.

Using this information, they were able to track down his coworker in Chennai, Ramkumar, as well as three employees at the Bengaluru office: Kavya Vasanthkrishan, Ravitha Devasenapathy, and S Karuppaiah.

Police discovered that the five had formed a new software firm called “Blue Dawn” the day following the theft and had contacted the five victims, whose information had been taken, offering their services at a steep discount.

Australian cybercrime investigators are looking for a second software programmer who helped steal the data. They want to ask Interpol for assistance tracking him down and will issue a lookout circular.

Patch Manager Plus, the one-stop solution for automated updates of over 850 third-party applications: Try Free Trial.


[ad_2]
Source link

Revolutionizing self-storage with smart technology

0
[ad_1]

The evolution of technology has significantly impacted various industries, and the self-storage sector is no exception. Today, smart technology is reshaping the way we approach the storage and protection of our belongings. This article explores the integration of smart tech features into self-storage units, highlighting how these advancements are enhancing user experience and security. From digital locks to climate control systems managed via smartphones, technology is adding an unprecedented level of convenience and efficiency. These technological solutions offer more than just a way to store items; they provide peace of mind through enhanced security, easy accessibility, and improved management of storage conditions. The implementation of Internet of Things (IoT) devices, remote monitoring capabilities, and automated systems represents a new era in self-storage, where convenience and security go hand in hand. As we delve deeper into this topic, we’ll uncover the various facets of smart storage technology and its benefits to users, illustrating how these innovations are setting new standards in the storage industry.

Digital Locks and Security Features

The advent of digital locks and advanced security features has revolutionized the safety protocols of self-storage units. In an era where security is paramount, these digital solutions offer users a higher degree of protection for their stored items. Digital locks, in particular, provide a keyless entry system that enhances security and convenience. These locks can be controlled remotely, allowing for easy access management without the need for physical keys, which can be lost or copied.

Incorporating these advanced security features into climate controlled storage units adds another layer of assurance for users. Not only are their belongings protected against environmental factors, but the integration of digital locks ensures that access to these units is tightly controlled and monitored. This combination of climate control with robust security systems represents a significant advancement in the storage industry, offering users a secure environment for their valuable or sensitive items.

As we continue to see technological innovations in security, these features are becoming increasingly sophisticated, offering real-time alerts, personalized access codes, and integration with mobile apps, all contributing to a more secure and user-friendly storage experience.

Climate Control via Smartphone Apps

Smartphone applications have brought a new level of control and convenience to managing the climate within storage units. These apps allow users to monitor and adjust settings remotely, ensuring that their stored items remain in optimal conditions. This technological advancement is particularly beneficial for storing sensitive items that require specific environmental conditions.

Here are several key features that these apps offer:

– Remote Temperature Adjustment: Change the temperature settings from anywhere.
– Humidity Level Monitoring: Keep an eye on humidity levels to protect sensitive items.
– Customizable Alerts: Receive notifications for any significant changes in climate.
– Energy Consumption Tracking: Monitor how much energy your storage unit is using.
– Access History Logs: Review when and how often the climate settings were adjusted.

For insights into the latest advancements in climate control technology, visiting resources like the U.S. Department of Energy can provide valuable information. Utilizing smartphone apps for climate control not only adds a layer of convenience but also enhances the safety of stored items.

It allows users to react quickly to any environmental changes, thereby reducing the risk of damage to their belongings. This integration of smartphone technology in self-storage illustrates how digital innovation is transforming the industry, making storage solutions more adaptable and user-friendly.

IoT Integration in Storage Units

The integration of the Internet of Things (IoT) in self-storage units is a leap forward in enhancing functionality and user experience. IoT technology connects various components of a storage unit to the internet, allowing for seamless control and monitoring. This integration brings a multitude of benefits. For instance, IoT sensors can track environmental changes within the unit, providing real-time data on temperature and humidity levels. This is particularly crucial for storing items that are sensitive to environmental fluctuations.

Moreover, IoT devices can enhance security features. They can be linked to motion detectors, surveillance cameras, and access control systems, providing comprehensive security monitoring. In case of any unusual activity, these systems can send instant alerts to the user’s smartphone, enabling prompt response. Additionally, IoT technology can optimize energy usage in the unit, adjusting climate control systems to operate more efficiently based on the internal conditions and external weather patterns.

The use of IoT in storage units exemplifies how smart technology is revolutionizing traditional practices. It’s not just about storing items; it’s about creating an intelligent environment that adapts to the needs of the contents and provides users with detailed insights and control over their storage space. This technological advancement is setting new standards in the self-storage industry, offering users a blend of convenience, security, and efficiency.

Remote Monitoring and Alerts

Remote monitoring and alerts stand as a cornerstone in the realm of smart storage technology, providing users with real-time oversight of their stored belongings. This advanced feature has transformed how individuals interact with their storage units, offering a new level of engagement and peace of mind.

Key aspects of this technology include:

1. Real-Time Surveillance: Access live feeds from storage unit cameras directly on your smartphone.
2. Instant Alert System: Receive immediate notifications for any unusual activity or environmental changes.
3. Access Logs: Review detailed logs of who accessed the unit and when.

For those interested in the technological intricacies of these systems, visiting websites like the National Institute of Standards and Technology can provide deeper insights. This level of surveillance and information access ensures that users are always connected to their storage units, regardless of their physical location.

Whether it’s checking on the unit while on vacation or receiving an alert about a potential security breach, these features empower users with information and control. This advancement in storage technology not only enhances the security of the stored items but also provides a convenient and intuitive way for users to manage their storage needs remotely.

Automation in Storage Management

The incorporation of automation in the management of self-storage units marks a significant evolution in the industry. This automation streamlines various processes, making storage management more efficient and user-friendly. One of the key areas where automation plays a crucial role is in customer service and communication. Automated systems can handle routine inquiries and provide quick responses, thereby enhancing customer experience. This is akin to the importance of reliable telephone services in businesses, where efficient communication is integral to customer satisfaction and operational efficiency.

Automated billing and payment systems are another aspect where technology shines. These systems reduce the likelihood of human error and ensure transactions are processed smoothly and securely. Additionally, automation in maintenance and climate control ensures that the storage environment remains consistent without the need for manual intervention, thereby preserving the condition of stored items.

The integration of automation in self-storage is not just about introducing new technology; it’s about redefining the way storage facilities operate, making them more responsive, efficient, and customer-centric. This shift towards automation is setting new standards in the storage industry, aligning it with the broader trend of digital transformation in various sectors.

Embracing Future Storage Solutions

Embracing the future of self-storage means integrating smart technology to enhance efficiency, security, and user experience. The advancements in digital locks, climate control apps, IoT integration, remote monitoring, and automation are redefining the standards of storage units, making them more than just a space to store items. These innovations offer users unprecedented control and peace of mind, marking a new era in the self-storage industry.
[ad_2]
Source link

Crypto Scammers Exploit Gaza Crisis, Deceiving Users in Donation Scams

0
[ad_1]

Cybersecurity researchers reveal a new crypto donation scam manipulating the humanitarian crisis in Gaza, with scammers preying on sympathy for Palestinian children to solicit funds – Over 200 individuals and numerous organizations have fallen victim to the elaborate scheme.

Cybersecurity researchers at Abnormal Security have uncovered a deceptive new crypto donation scam exploiting the humanitarian crisis in Gaza where scammers trick users by generating sympathy for Palestinian children to request donations. Around 212 individuals across 88 organizations have become targets of this charity attack.

Threat actors like to capitalize on geopolitical events as trapping people and gaining sympathy becomes easier. We witnessed the same in the case of the missing Malaysian flight MH370, how scammers propagated fake videos and images, falsely claiming that the missing jet was found in the Bermuda Triangle. In reality, they exploited the incident to spread malicious links.

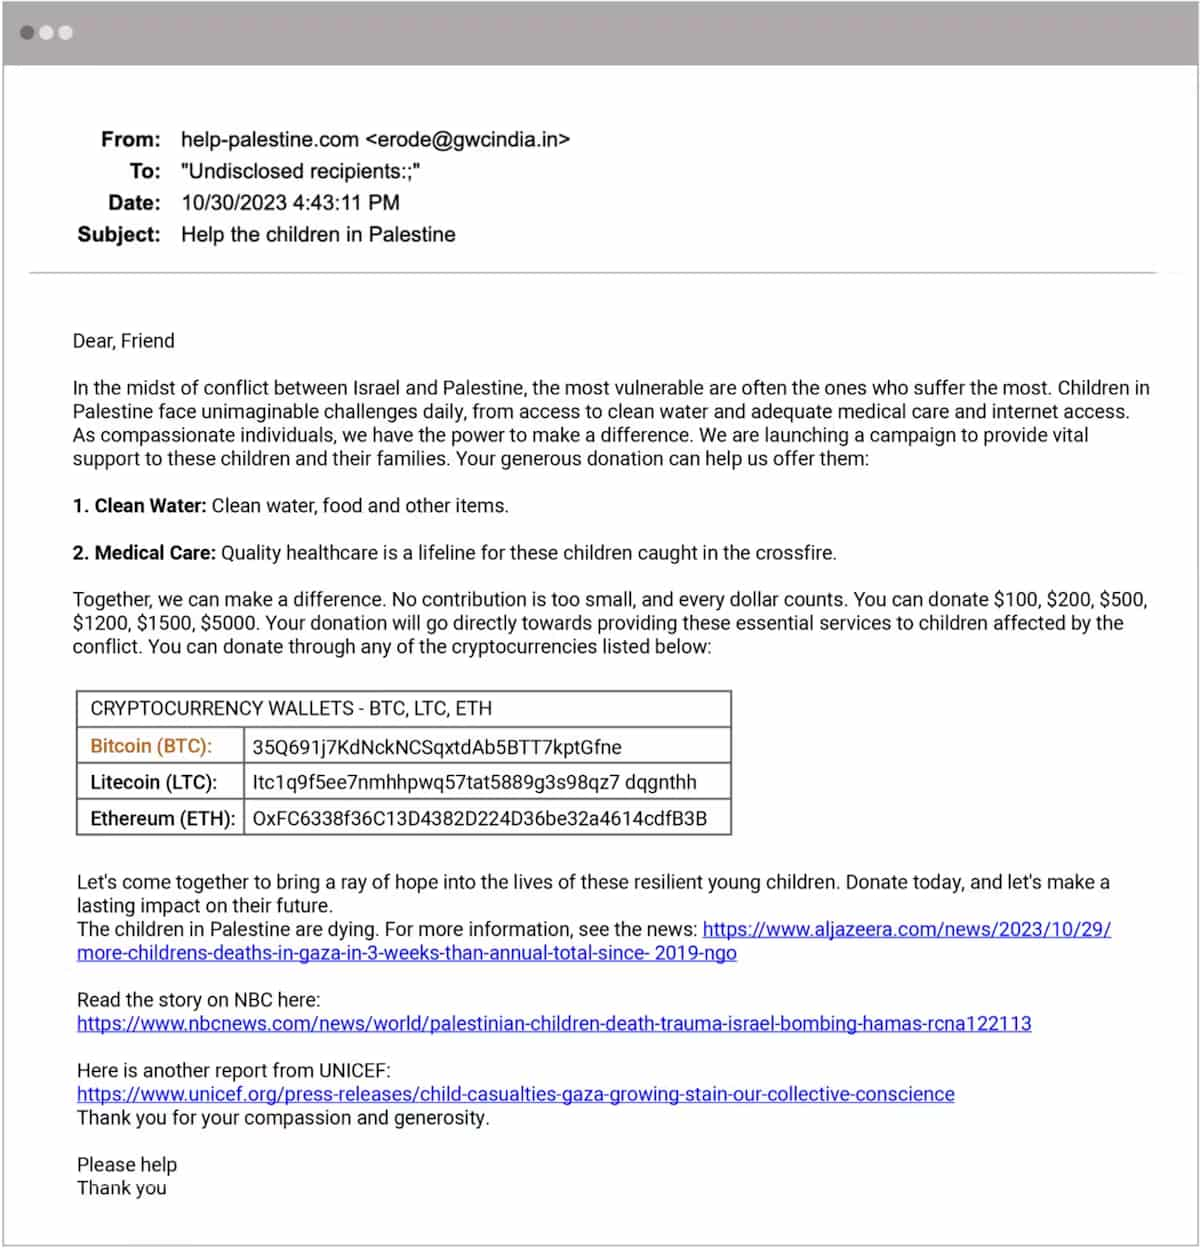
In the latest fraud campaign, scammers send emails that are apparently sent by a group called “help-palestinecom.” The sender urges the recipients to contribute to their campaign to support Palestinian families.

It is worth noting that scammers ask for donations in cryptocurrency ranging from $100 to $5000 and include cryptocurrency wallet addresses for Bitcoin, Ethereum, and Litecoin to avoid being tracked.

Unsuspecting users fall for the lure and donate, thinking that this money would help provide Palestinian children with basic needs such as medical care, clean water, and internet access. 

To enhance the email’s legitimacy, the scammers have included links to three of the latest news articles on the impact of the conflict on children. Moreover, they have strategically used emotionally stirring language to emphasize the challenges of children in Palestine.

For instance, they used “children in Palestine face unimaginable challenges daily,” “a lifeline for these children caught in the crossfire,” and “the children in Palestine are dying.” To avoid detection, scammers have used multiple tactics, including spoofing the email address of an Indian stock brokerage firm Goodwill Wealth Management and creating a fake domain.

According to Abnormal Security’s CISO and advisory author, Mike Britton, legacy secure email gateways (SEGs) fail to detect this scam because of social engineering techniques used by scammers and the absence of apparent indicators such as grammatical errors or payloads. Britton emphasized the need for AI-based email security solutions that could distinguish between malicious and genuine content.

“AI-powered email security platform is trained to identify social engineering tactics, it recognizes that this email is attempting to leverage emotional manipulation to convince the target to bypass rational thinking and quickly transfer funds. It can also detect and flag the mismatch between the sender’s email and the reply-to address, as this is a common attack tactic,” Britton explained.

Crypto Scammers Exploit Gaza Crisis, Deceiving Users in Donation Scam
The scam email sent by scammers for a crypto donation scam (Credit: Abnormal Security)

The scam is the latest to join the manipulative attacks exploiting ongoing geopolitical crises. The FBI issued warnings on 6 and 14 November 2023 to alert users about fraudsters attempting to exploit the war in Gaza.

The bureau highlighted that fraudsters can use emails, social media, cold calls, crowdfunding sites, and charities/fundraisers to solicit payments. FBI warnings noted that apart from opportunistic cybercriminals, terrorist organizations can also establish fake charities to “subsidize their operations.”

Users are, therefore, advised to exercise caution and verify the legitimacy of the sender and their claims before donating.

  1. Scammers using fake WHO Bitcoin wallet to steal donation
  2. Ransomware group donates $20,000 in BTC to two charities
  3. US disrupts 3 cryptocurrency campaigns run by terror groups
  4. Black Lives Matter movement exploited to spread Trickbot malware
  5. Indian PM Modi’s Twitter handle hacked to ask for Bitcoin donations

[ad_2]
Source link

Samsung’s already secured the names of its future foldable phones

0
[ad_1]

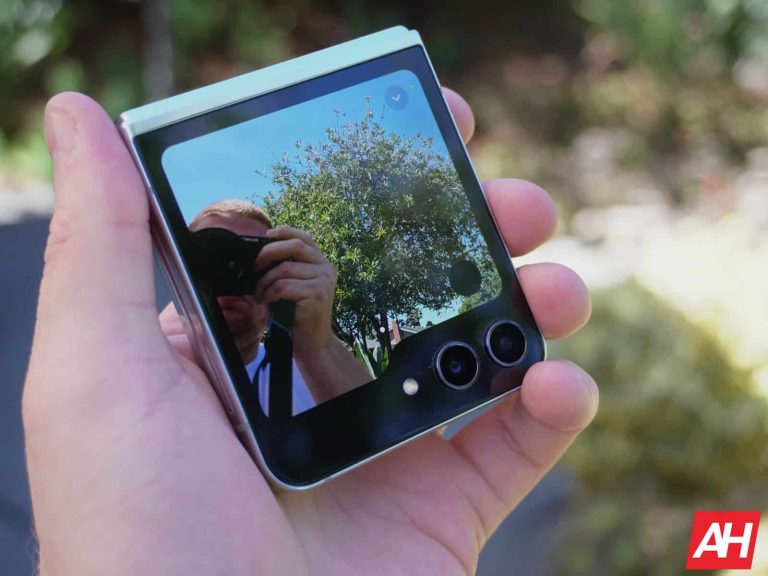
Samsung has remained consistent with the naming convention for its Foldable phones. We are currently on the 5th generation of foldables from the company, and we’re not expecting to hear any notable leaks about the next generation for several months. While that’s the case, we all have a pretty solid idea of what the future foldables are going to be called. According to a report, Samsung has already secured the names for its future foldable phones.

The Galaxy Z Fold and Z Flip 5 or some are the best foldables that you can get your hands on this year. While the Fold 5 was a very iterative upgrade, the Flip 5 brought a much larger screen compared to last year’s phone. This made it very popular with the users.

At Android Headlines, we reviewed both of the devices, so you can have a first-hand account of them. You can read the Galaxy Z Flip 5 Review to learn about the clamshell-style device. Also, you can read the Galaxy Z Fold 5 Review to learn about the more premium productivity-focus device.

Samsung has already secured the names for its future Foldables

It should really surprise no one that Samsung is planning on sticking with this naming convention. It’s not like the line is in need of a huge rebranding. Samsung’s phones are still the most popular Android handsets, and people buy more year after year. So, the company doesn’t need to switch directions.

The names of Samsung’s future foldables were spotted online through several certification organizations including the World Intellectual Property Organization (WIPO). Surprising no one, the upcoming phones are the Galaxy Z Fold 6, Galaxy Z Flip 6, Galaxy Z Fold 7, and Galaxy Z Flip 7. These are going to be the next two iterations in both series.

So, it’s obvious that Samsung is not going to change anything with the names. However, we do hope that Samsung will bring notable changes to the actual hardware with future iterations. Innovation has pretty much slowed with Samsung’s Foldables, and that’s allowing other companies like OnePlus, Vivo, Oppo, and Tecno to rise up and challenge the Galaxy Foldable experience


[ad_2]
Source link

Sam Altman could return to OpenAI… but he has demands

0
[ad_1]

In case you didn’t know, OpenAI’s CEO, Sam Altman, was fired from the company on Friday. This news took the tech world and even Altman by surprise. Well, it seems that the board has had a change of heart, as they are all in talks with Altman to return to the company just one day after the ousting.

On Friday, Altman was ejected from his role, and OpenAI said that it was because he “was not consistently candid in his communications with the board, hindering its ability to exercise its responsibilities.” That’s not the clearest answer, and we can’t take public-facing company statements at face value.

In any case, since he’s been fired, OpenAI’s President and former board member Greg Brockman quit his position. According to the report, he and Altman were talking to investors about starting another company. This was all over the course of a weekend.

Sam Altman might return to OpenAI… but he has demands

Since his firing, the company has since reached out to him to return to the company, several sources told The Verge. The plan was originally to have the company’s chief technology officer, Mira Murati, take over as the CEO temporarily until the company can find a replacement. However, just a day after Altman was fired, the company has been looking to bring him back.

We’re not sure if he’s going to be returning or not; however, he has demands. Reports say that Altman wants “governance changes” if he returns. We’re not sure what those changes are, but we might have an idea. A source close to Altman says that the board agreed to resign by a 5PM PST deadline to make way for Altman and Brockman to return. This makes it sound like his condition for returning was clearing out the board. However, the board missed that deadline. So, we’re not sure what’s going to happen at this point.

This drama is going to continue

We don’t know what’s going on with the company now, but the last we heard of it, it was heading toward bankruptcy. That was not too long ago, so the company’s fortunes might not have changed all that much. With the financial drama, no CEO, and no president, OpenAI’s future looked grim. The company was most likely falling to pieces in the hours after Altman was fired. This could be the reason why the company was quick to ask for him back.

Microsoft told The Verge that it’s still committed to supporting OpenAI, Altman or no Altman. However, being an investor in the company, an executive change like this with no warning will make Microsoft keep its eyes on the company. This should go for all investors, as the company seems to be stumbling.

We’ll keep you up to date on what’s going on with the company as this story develops.


[ad_2]
Source link

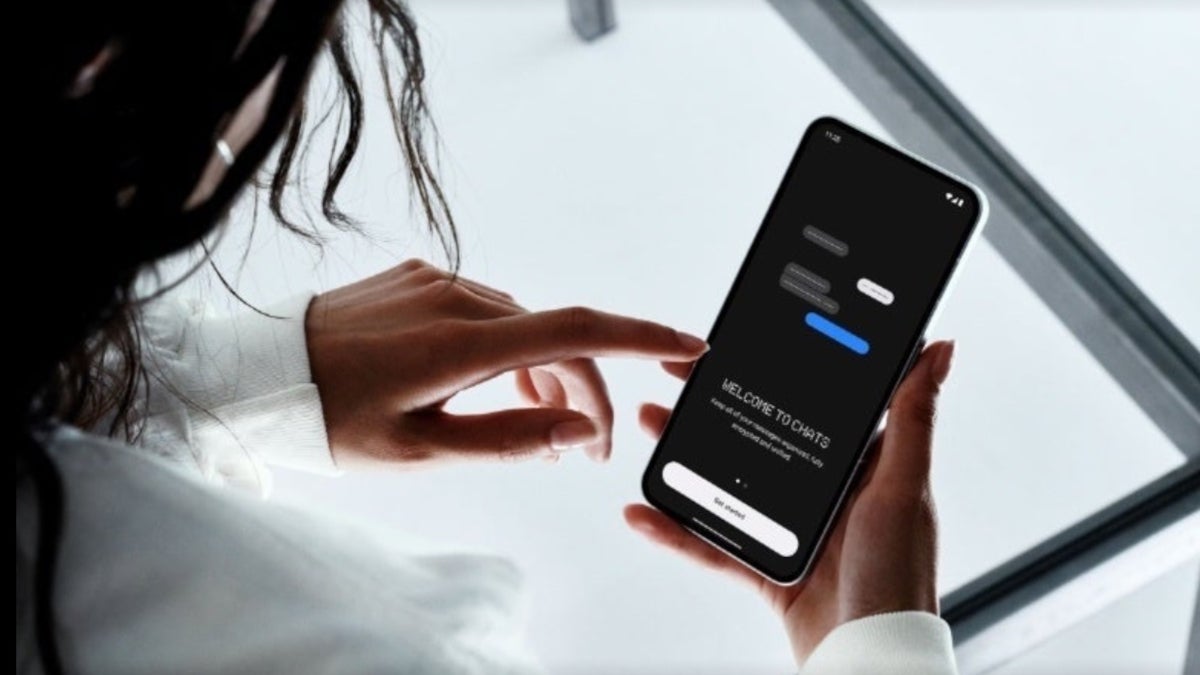
Nothing Chats beta gets pulled from the Play Store due to major privacy contradiction

0
[ad_1]

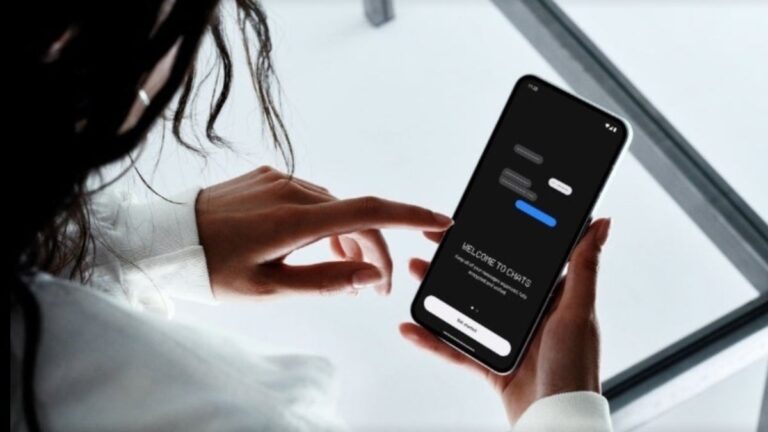
Last week, just before Apple stunned the tech world by announcing that it would allow iPhone to support RCS starting next year, Nothing CEO Carl Pei had announced the Nothing Chats app. Created in partnership with the Sunbird universal messaging platform that was planning to bring iMessage to Android users, the Nothing Chats app would allow Nothing Phone (2) users to use iMessage on their Android powered Nothing (2) phone.
The Verge reports that Nothing pulled the Nothing Chats beta app from the Google Play Store and is “delaying the launch until further notice” while seeking to exterminate several bugs. The app would  have allowed Nothing Phone (2) users to text with iMessage but only if Sunbird could log into users’ iCloud accounts. Texts.blog, the blog of messaging client Texts.com, referred to the Nothing Chats app as a reskinned version of the Sunbird app and said that the app was not secure.
Texts.blog wrote, that both “Sunbird” and the “Nothing Chats” app require that users send their Apple ID info to their servers, where they are authenticated using a virtual machine running MacOS.

The Texts.com team discovered that messages sent using Sunbird’s platform are not encrypted (Sunbird has access to every message sent and received through the app). A tweet from Android app developer Dylan Roussel says that Sunbird does this by “abusing @getsentry, which is used to monitor errors. But Sunbird logs messages, pretending they are errors.” This contradicts an FAQ directly taken from the Nothing website on 11/17/2023 and later.

The question in the FAQ asked, “Are my messages secure?” The answer stated, “Yes, Nothing Chats is built on Sunbird’s platform and all Chats messages are end-to-end encrypted, meaning neither we nor Sunbird can access the messages you’re sending and receiving.” But that does not match what Texts.com discovered. And if there is no encryption and your texts are compromised, you have sent your Apple ID to a third-party service and could allow attackers to view your photos, videos, contacts, notes, and more.

None of this will have any impact on Apple’s decision to support RCS which was most likely an attempt by Apple to get ahead of the EU’s Digital Markets Act (DMA) which could have forced Apple to add RCS support to the iPhone in the 27 EU member countries if the EU decided to call iMessage a “gatekeeper.”

[ad_2]
Source link

Dark Effects of Bot Attacks that Drive 73% of Internet Traffic

0
[ad_1]

In a chilling revelation, the cybercrime economy is projected to soar to $10.5 trillion by 2025, driven by financially motivated bad actors orchestrating dark enterprises. 

Uncover the intricate web of these malicious activities and the alarming surge in cyber threats.

The Breaking Bad Bots: Bot Abuse Analysis and Other Fraud Benchmarks3 report by Arkose Labs provides a comprehensive analysis of bot abuse trends and fraud benchmarks. 

The report illuminates that bot attacks have become more sophisticated and are now capable of emulating human behavior. 

Insights on the prevalent types of bot attacks are also outlined in the report. These include fake account creation, payment fraud, and account takeover attempts.

Explore the rise of sophisticated bots that not only target coveted items like Taylor Swift tickets and Nike shoes but also contribute to far more sinister crimes. 

Delve into the staggering statistics, revealing a 121% increase in total attacks in Q2 of 2023 and the ominous shift toward human-based attacks in Q3.

The Chilling Impact on Financial Institutions

Witness the battleground in the financial sector, where bad actors are strategically targeting online bank accounts. 

With a 202% surge in attempts to seize consumer financial accounts and a 164% increase in fake new bank accounts, the financial industry has become a prime target for cybercriminals.

Unravel the disturbing connection between cybercrime and dating sites, where bad actors exploit vulnerabilities to initiate money-making romance scams. 

Discover the shocking statistics, including a 36,000% increase in fake account creations in Q3, leading to potential profits from human trafficking and other illicit activities.

Enter the era of Generative AI (GenAI) and its transformative impact on cybersecurity. 

Explore how cybercriminals employ GenAI for content generation, crafting perfectly worded phishing emails and responses on dating apps. 

Brace for a surge in romance scams as GenAI becomes a powerful tool in the cybercriminal arsenal.

DIY Fraud and the Escalation of Cyber Attacks

Unveil the democratization of cybercrime through DIY Fraud, also known as cybercrime-as-a-service (CaaS). 

Witness the deployment of automated bots at an unprecedented scale, causing trillions in damages and posing a formidable challenge to security teams worldwide.

Navigate the technological advancements driving the proliferation of complex bots. 

From intelligent bots leveraging machine learning to the staggering 167% increase in total bot attacks, understand the evolving landscape and the need for adaptive defenses.

Patch Manager Plus, the one-stop solution for automated updates of over 850 third-party applications: Try Free Trial.


[ad_2]
Source link

Google works on improving Play Store security to keep malware-laden apps off Android phones

0
[ad_1]

Google and its Android mobile platform have a problem. Even though Google Play Protect scans apps before you install them on your phone, a recent report from cybersecurity firm Kaspersky revealed that apps stuffed with malware were installed 600 million times on Android phones this year. If Google is doing all of this scanning, how is this possible? Let’s take a look at a typical Android user. Let’s call him Andy.
Andy is impressed by an ad he saw for an app in the Google Play Store that will allow him to edit his videos on-device, so he installs the app on his phone. A few weeks later, the developer (a totally made-up firm called Dewey, Cheetum, and Howe) pushes out an update to the previously benign app that adds the necessary permissions and code to steal the passwords used by Andy to open his financial apps; days later, Andy notices a few unauthorized withdrawals from his bank account.
First seen by AssembleDebug in the GApps Flags & Leaks Telegram channel (via AndroidPolice), Google has created a new onboarding UI for the Play Store. Leaked screenshots show that Android users like Andy may be asked to verify their identity and the method of payment used for in-app purchases. The verified information can be used to make sure that Andy doesn’t accidentally install an app in the future with a hefty price tag, or mistakenly install an app loaded with malware.

For example, Android users can choose to require verification for all purchases made through the Google Play Store using a fingerprint or facial recognition. Users will have the option to add authentication preferences by using built-in Android security features, checking apps and the user’s device using Play Protect, and securing purchases made via the Play Store by adding payment preferences.

If your Android phone is set up with the appropriate settings enabled, a download from the Play Store can be stopped immediately during the installation process if malware is detected. Last month, settings surfaced for a feature called Android Safe Browsing that would notify users of a threat in real time as they surfed the internet. This could end up being part of Google Play Protect.

While waiting for Google to make its Play Store security improvements official, users can require that all purchases made on the Play Store be authenticated. And Google Play Protect can, as noted earlier, scan the apps on your phone for malware.


[ad_2]
Source link

Multimillion-Dollar Vishing Scam Busted: Czech-Ukrainian Gang Arrested

0
[ad_1]

Europol Warns of Growing Vishing Trend as Criminals Exploit Phone Calls for Massive Financial Gains

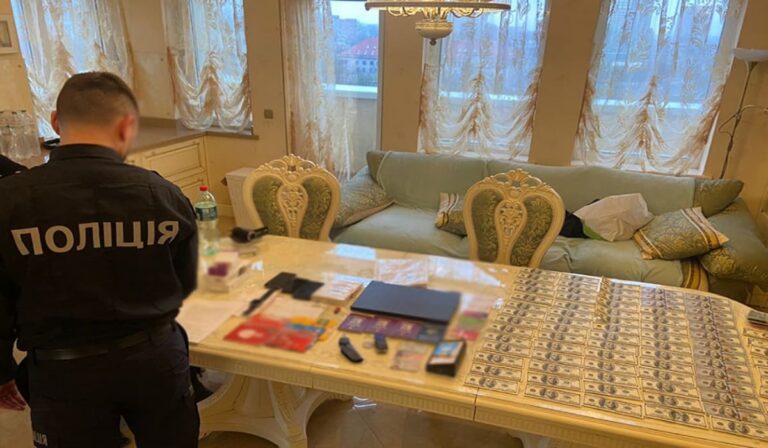
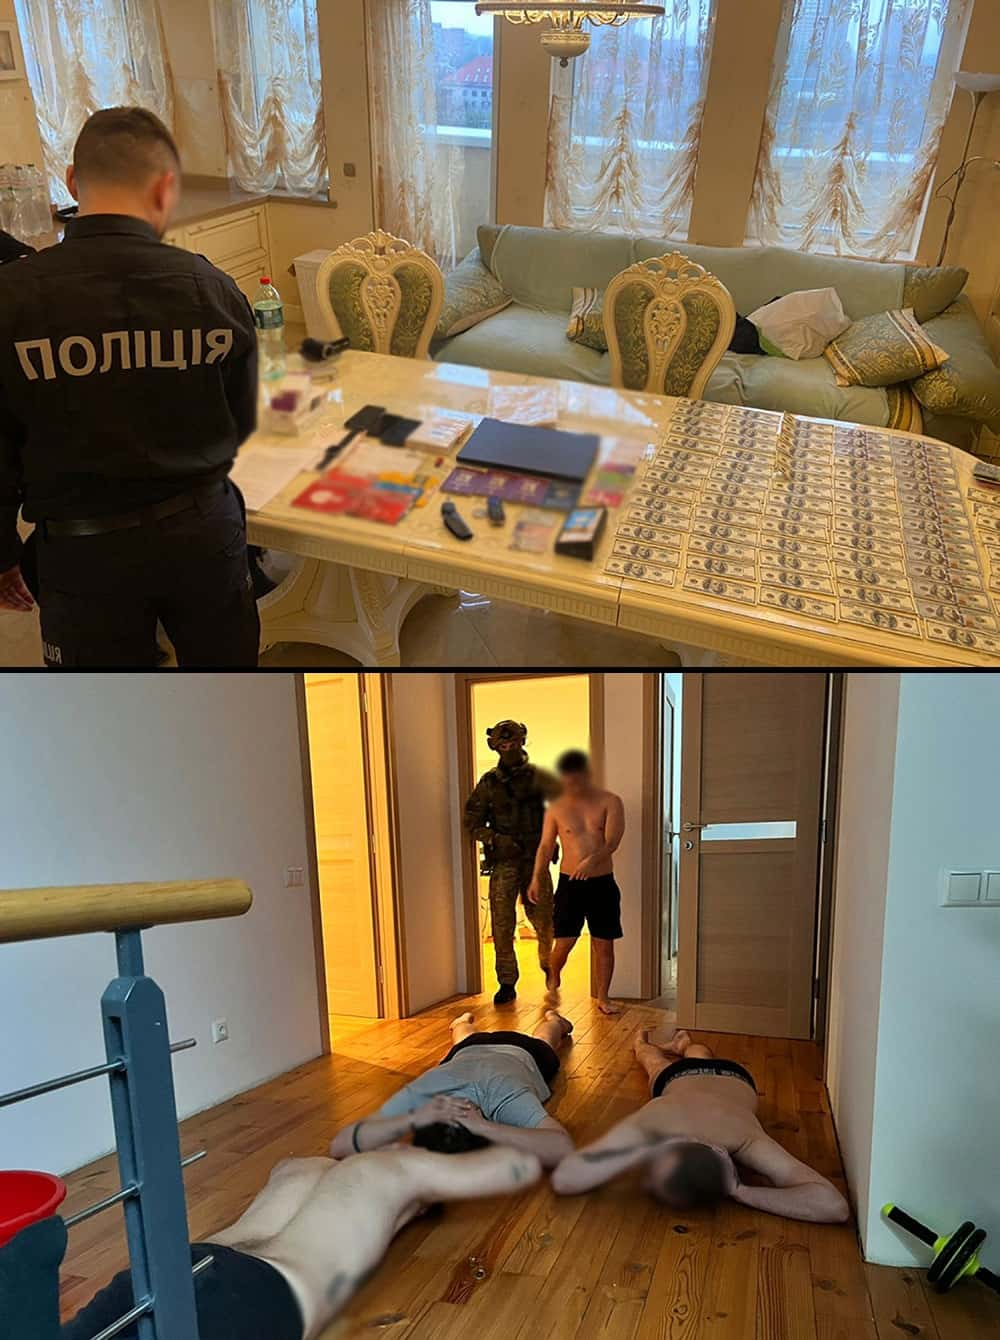
Ukrainian and Czech police under the supervision of Europol have dismantled a criminal gang that stole millions of dollars from bank customers in Czechia through vishing scams. According to Europol’s press release, the police also arrested ten suspects (aged 18-29) in connection with the multimillion-dollar fraud ring.

A joint investigation was initiated by Europol that led to the arrest of four individuals in Czechia and six in Ukraine in April 2023. Those arrested from Ukraine were later extradited to Czechia.

During the crackdown, investigators seized SIM cards, mobile phones, and computer equipment from the suspects’ vehicles, call centers, residences, and offices located in Czechia (Domazlice, Rokycany, and Plzen) and Ukraine (Dnipropetrovsk). Some of the suspects had a history of drug offences, violent crimes, and document forgery.

The criminal organization, based in Ukraine, conducted vishing attacks against Czech victims. They operated from call centers in Ukraine and called bank customers using spoofed phone numbers, posing as bank security officers. This scamming method is called vishing (created by combining voice and phishing).

The targets were told that their bank account was hacked and lured into revealing their banking data, such as credit card numbers, login credentials, and other details. Scammers also made phone calls pretending to be a police official to confirm the hacking.

After gaining trust, the scammers persuaded their victims to transfer funds from their “compromised” bank accounts to “safe” bank accounts, which the scammers owned. Through these scams, the fraudsters made approximately $8.7 million (€8 million) from victims in Czechia alone.

The Czech Republic police uncovered this scam. In November 2021, they contacted Eurojust to launch an investigation. Europol then formed a joint investigation team in June 2022, comprising Europol’s European Cybercrime Centre (EC3) officials and the Czech and Ukrainian investigators. The agency organized five meetings to facilitate judicial cooperation between the authorities.

The police called the gang’s activities one of the “most extensive series of frauds committed through fake bankers.” Currently, Europol is conducting analytical work and providing digital forensic support for the confiscated equipment.

Multimillion-Dollar Vishing Scam Busted: Czech-Ukrainian Gang Arrested
Image via Czech Republic police

Vishing fraud has become more widespread and popular lately. It usually involves someone pretending to be from a reputable organization, institution, or government agency and deceiving people into disclosing confidential, personal data.

The severity of vishing scams is highlighted by the September 2023 incident when the notorious ALPHV (BlackCat) ransomware gang exploited vishing to deceive an MGM Resorts employee, enabling them to breach the company’s security and compromise its network.

To protect yourself from such scams, always be cautious of unsolicited phone calls, note the caller’s phone number, and tell them you will call back and quickly verify their identity by calling the organization.

Don’t believe any caller if they have basic information about you because it could be taken from social media. Lastly, keep your credit/ debit card PIN or online banking password private because bank representatives would never ask for this information.

  1. Police Dismantle SIM Swapping Gang in Spain
  2. 48 DDoS-hiring Services Busted by FBI in Major Sweep
  3. Cisco Breach – Employee’s Google Account was Hacked
  4. The Types of Phishing Attacks and How to Dodge All of Them
  5. SpyNote Spyware Using SMS Phishing Against Banking Customers

[ad_2]
Source link