TikTok seeks to curb misinformation during the Israel-Hamas war

0
[ad_1]

Following other social media platforms in recent times, TikTok is announcing its plans to curb misinformation during the ongoing Israel-Hamas war. This will help give users the correct information from reliable sources on the events unfolding during the conflict. With their new eight-point agenda, the social media service provider aims to protect their users from misinformation during these times.

In an aim to tackle misinformation and uphold TikTok’s community guidelines, the company is launching a new command center. With this new command center, the platform will be able to monitor and curb any post spreading misinformation during this period. They are also improving their proactive automated detection systems to help identify new threats such as graphic and violent content.

To better monitor events surrounding the Israel-Hamas conflict, TikTok is hiring “moderators who speak Arabic and Hebrew to review content related to these events.” Other majors include the new opt-screens, and corporations with government agencies and experts, to mention a few. With these guidelines in place, TikTok is confident that it’ll be able to curb misinformation during the Israel-Hamas conflict.

You should start seeing the new improvements to TikTok on your app and they’ll help curb misinformation, hence keeping you safe.

A few days ago, Elon Musk was called out by the EU for the way his social media platform handles the Israel-Hamas conflict. Following this, X gave a comprehensive rundown of how it is fighting misinformation during this period. After the EU’s encounter with X, other social media platforms have had to increase their efforts to keep users safe from misinformation.

TikTok is now the next in line to make its plans to curb misinformation public. Its fight against misinformation on the Israel-Hamas conflict will lead to removing violent content and accounts. This is one of the areas TikTok is stepping up in this fight against misinformation.

Another area where users will be able to spot TikTok’s efforts to curb misinformation will reflect while they scroll through videos. TikTok is now adding an opt-in screen that’ll display graphically shocking content. Users can opt in and view such content or continue their scrolling in search of more uplifting videos.

The ByteDance-owned platform claims to have taken down over 500,000 videos displaying violent content from this conflict. They go on to claim that over 8,000 live streams were closed over misinformation concerns. Aside from these features and achievements, TikTok is also reminding users of other ways they can protect themselves from misinformation.

Users can rely on the report content feature to help the platform track down misleading posts. With this feature, TikTok says that it can help keep misinformation away from users on the platform. In your everyday usage of your TikTok app, you might come across some of these protective features.


[ad_2]
Source link
WhatsApp announces passkeys support for Android users

0
[ad_1]

Last week, Google announced that passkeys would become the default authentication method for its users on personal accounts. Within that announcement Google also stated that passkeys support is growing, listing a few of the companies that had already enabled them on their apps and websites, with a mention of WhatsApp as one of the ones that would be adding compatibility soon.
This confirmed earlier reports that WhatsApp had already been testing this functionality with its beta users and that it would be tied to Google’s Password Manager. Today, WhatsApp finally announced that passkeys support is now official for its Android users who can now use their device’s screen lock method to unlock their accounts, such as their face, fingerprint, or device pin.

Previously, WhatsApp had implemented an optional two-step verification pin and a fingerprint lock feature that users could set to trigger automatically after a set length of time. This type of authentication is not being removed from the app, but rather joined now by passkeys, offering an additional layer of security.

Although passkeys support has now been made public by the company, it appears that the feature is not yet live on the latest stable version of the app (v2.23.20.76). However, it is definitely working in the latest beta (v2.23.21.12) for those enrolled in the WhatsApp beta program.

The signup process is quick and straightforward as it is using the screen lock method that you already use on your phone. Additionally, through this signup process you learn that your newly created passkey is indeed being stored in Google’s Password Manager, which makes it possible to use on other devices where you are signed in to your Google account. It is unclear at this time if an app update is forthcoming for the stable version of the app, or if the feature will be rolled out in stages via a server push.


[ad_2]
Source link

Stealthier Version of ROMCOM Backdoor Targets Female Politicians

0
[ad_1]
  • Japanese cybersecurity firm Trend Micro has detected a new malware attack campaign dubbed ROMCOMLITE.
  • Cyberespionage gang Void Rabisu is targeting female Politicians and government officials. with the new ROMCOM backdoor variant.
  • This new variant is compact and stealthier than its predecessor.
  • Attackers are using spear-phishing to distribute the backdoor through fake meeting invites.
  • If the malware invades a system successfully, it can harvest data, execute remote commands, or capture screenshots.

A notorious cyberespionage group Void Rabisu, aka Storm-0978, Tropical Scorpius, and UNC2596, has launched a brand-new campaign targeting female political leaders and government officials using a revamped version of a previously detected ROMCOM backdoor.

Hackread.com had reported in July 2023 that Void Rabisu is intensifying its efforts to target politicians, citing a report from the BlackBerry Threat Research and Intelligence team about discovering a campaign where the group targeted Ukraine and NATO supporters with the ROMCOM backdoor RAT delivered via malicious documents.

The ROMCOMLITE campaign was discovered by Japanese cybersecurity firm Trend Micro. This new variant, dubbed ROMCOM 4.0 by Trend Micro and Peapod by Microsoft, allows attackers to gain unauthorized access to the target’s computers and steal sensitive data.

The backdoor was detected in early August, and the malware analysis was published on 31 October. In the report, Feike Hacquebord and Fernando Merces explained that Void Rabisu’s targets were attendees of the Women Political Leaders (WPL) Summit held in Brussels in June 2023.

For your information, Void Rabisu is a sophisticated, hybrid group that conducts espionage and financially motivated attacks and prefers using the Cuba ransomware. It also serves as an APT actor targeting government and military entities/officials.

The gang was discovered first in 2022, but researchers agree that it has been active for a long time. They also suspect this group harbours a geopolitical agenda, as most of its previous campaigns targeted the Ukrainian government/military and EU political/government governments.

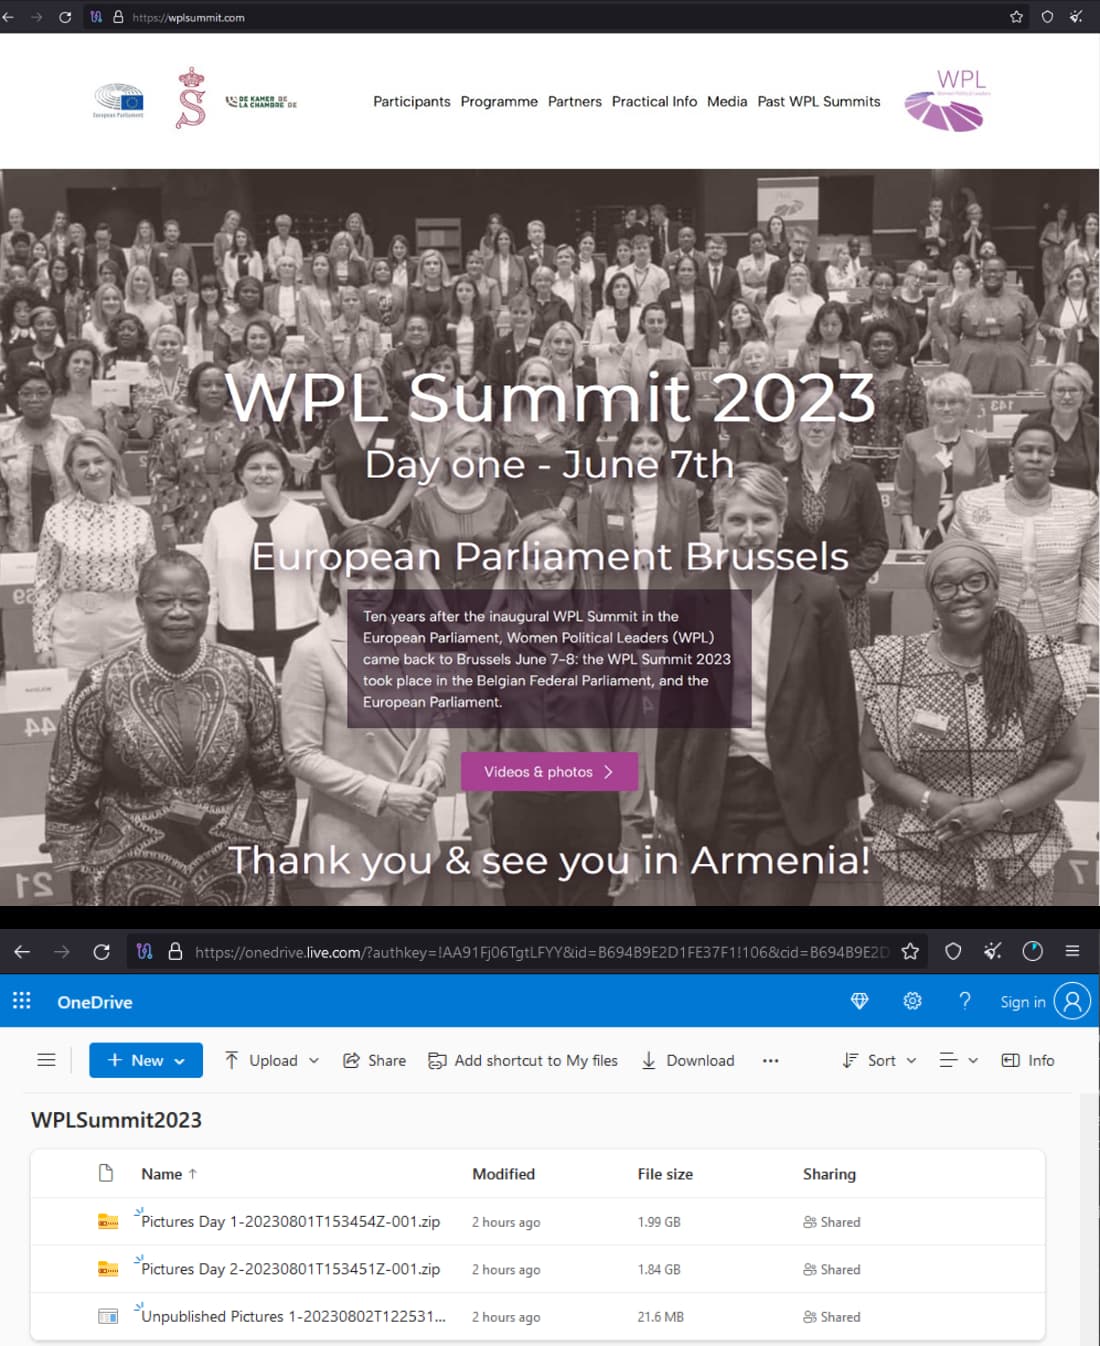
In the recent campaign, Trend Micro noted that the backdoor payload was embedded in a malicious copy of the WPL Summit’s official website to improve gender equality in politics. The malicious new backdoor ROMCOM 4.0 is designed to evade detection and remain hidden on the infected system to avoid raising suspicion.

As per the report, the Videos &photos link of the original domain redirects the visitor to a Google Drive folder containing the event’s photographs. Then the fake website (wplsummitcom) directs the visitor to a OneDrive folder containing two compressed files and an executable file (titled: Unpublished Pictures 1-20230802T122531-002-sfx.exe), which is malware.

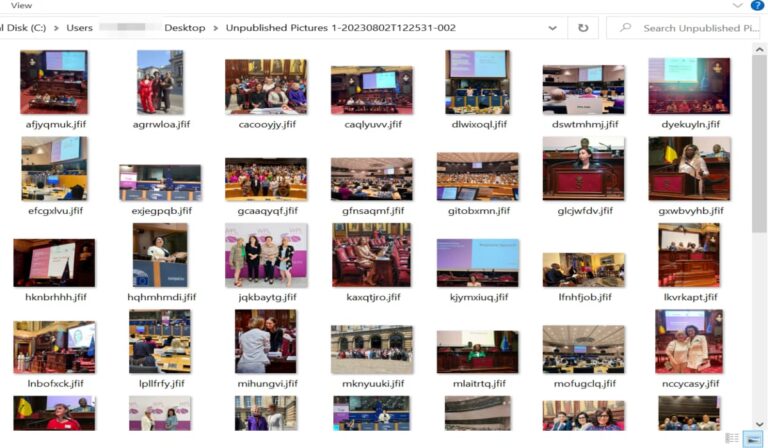
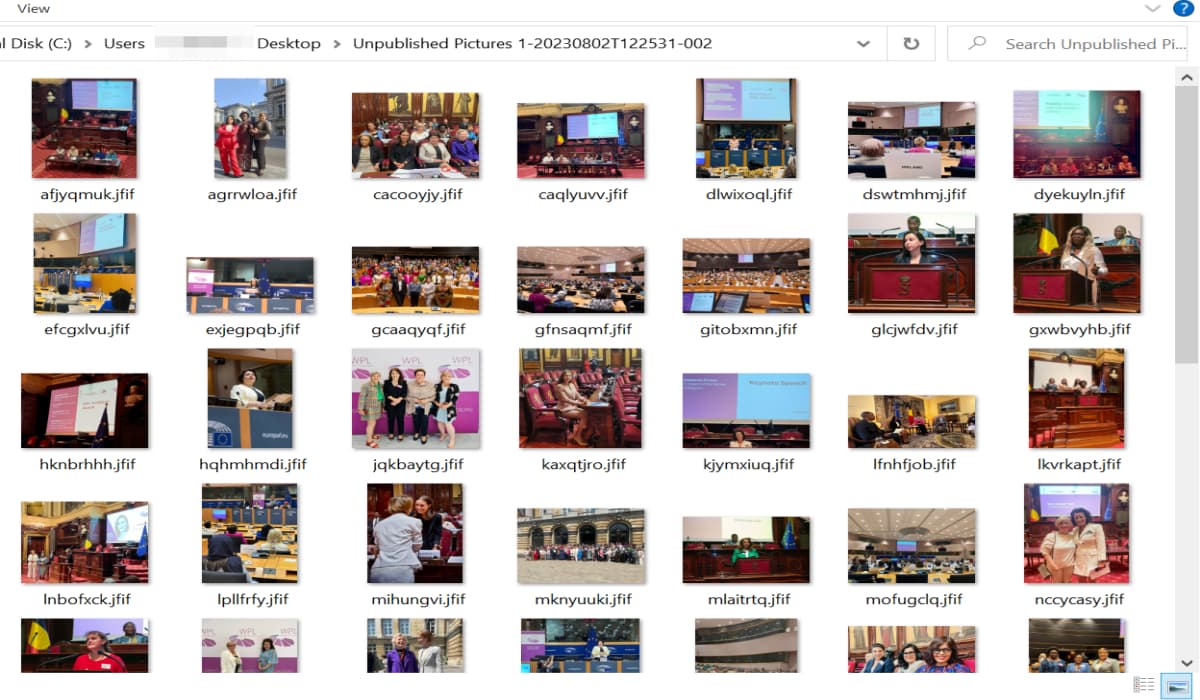
The gang created this fake website on 8 August, primarily to attract visitors from the original WPL summit domain. The executable file is signed with a valid certificate by a firm called Elbor LLC and extracts 56 photos from its resource section after the user clicks on Extract.

ROMCOMLITE: Stealthier Version of ROMCOM Backdoor Targets Female Politicians
Fake Malicious Website for the WPL Summit 2023 and the folder downloaded by clicking on the ‘Videos & Photos’ contains images and malware downloader (Screenshot Credit: Trend Micro)
ROMCOMLITE: Stealthier Version of ROMCOM Backdoor Targets Female Politicians
Pictures dropped by the malware downloader from the event – According to Trend Micro, these images have been gathered by hackers from different social media posts.

Attackers use spear-phishing tactics to lure their targets. They send fake meeting invitations and other lures so that the targets open malicious attachments or click on links containing the malware.

This is a similar tactic Void Rabisu has used in its campaign discovered in June 2023, where the gang used lures related to the Ukrainian World Congress and the July NATO summit to deliver a zero-day exploit based on an RCE vulnerability in MS Office and Windows HTML, tracked as CVE-2023-36884. Microsoft disclosed this campaign in July.

However, Trend Micro report reveals that the group has used a new tactic in this campaign involving TLS-enforcing by the RomCom C2 servers to make discovering ROMCOM’s infrastructure hard to detect.

“We observed Void Rabisu using this technique in a May 2023 RomCom campaign that spread a malicious copy of the legitimate PaperCut software, in which the C2 server ignored requests that were not conformant,” the report read.

Trend Micro claims there’s no evidence to believe Void Rabisu is a state-sponsored actor. Still, it is clear that the group is trying to benefit from the “extraordinary geopolitical circumstances caused by the war in Ukraine.”

  1. Hackers Target Israeli Rocket Alert App Users with Spyware
  2. Gender Diversity in Cybercrime Forums: Women Users on the Rise
  3. Israeli Rabbi arrested for hacking CCTV cameras at women’ bathing suit shop

[ad_2]
Source link

Google promises lossless USB audio for the Pixel 8 series in future releases

0
[ad_1]

Google’s VP of Engineering has confirmed the company will bring lossless USB audio to the Pixel 8 series in a later release. The feature could significantly upgrade audio quality on Pixel 8 and Android devices.

Lossless audio is a digital format that came to Android with the Android 14 Beta 2 update. As Google’s VP of Engineering, Dave Burke, explains, lossless USB audio preserves the original audio quality and ensures “bit perfect audio” as it bypasses the audio mixer, processing effects, etc. The format is added on the OS level, and manufacturers and app developers must take the next step.

Burke added that the Pixel 8 series and other Android devices could get lossless audio in their hardware abstraction layer (HAL) in later releases. App developers should also adopt the new API to add lossless audio to their apps.

Lossless audio is coming to Pixel 8 series in later releases

It remains to be seen when Pixel 8 devices and other Android OEMs officially add support for lossless audio. But it shouldn’t take too long before you can listen to your favorite audio without quality loss. The exact schedule could be announced later.

The most significant advantage of lossless audio is it lets music move through your device to USB headphones uncompressed and unchanged. This means the music you hear is in its purest form and sounds very clear. Google says the lossless audio feature is designed for “audiophile-level experiences over USB wired headsets.”

Apple has already developed its lossless audio technology, dubbed Apple Lossless Audio Codec (ALAC), now available to Apple Music users. Android users currently need to rely on DAC (digital-to-analog converter) to use this former. However, with the later releases, the feature comes to your device by default.

The music streaming apps are expected to be at the forefront of adopting lossless audio API. Spotify is already spotted working on lossless audio. However, the feature could be part of the “Supremium” tier, which costs $19.99 monthly. The new tier also offers up to 20 hours of audiobook listening.


[ad_2]
Source link

Montana’s ban on TikTok goes before a federal district judge

0
[ad_1]

A few months ago, Montana’s ban on TikTok came into the spotlight, and it aims to impact access to the app for users. This ban came during the period TikTok was under investigation by the US government for its association with parent company ByteDance. The state of Montana was the first state to effect a ban on the social media app in its region, and now a federal district judge questions that move.

Following the ban, TikTok as well as creators in its region took the Montana government to court. The plaintiffs argue that this ban is unconstitutional and an infringement on the freedom of speech for TikTok and its users. This ban will not only take a toll on TikTok but also cut its users away from the services that the app offers them.

In its defence, the Montana state government claims that the ban is in place to protect the online privacy of citizens. This was also the same ground on which the previous threats of banning TikTok in the US stood. However, this claim didn’t lead to the ban of TikTok in the US, but the government of Montana might have taken things into their hands.

A federal district judge questions Montana’s ban on TikTok ahead of it going into effect next year

At the moment, Montana’s ban on TikTok is not yet fully effective, but the state is pushing to block citizens from the app. They aim to do this by barring residents of the area from downloading the app via their mobile app stores. However, US District Judge Donald W. Molloy isn’t standing with the state’s decision, and he calls it confusing.

During the hearing on Thursday, Donald W. Molloy put Montana’s decision through scrutiny. The state’s evidence that TikTok engages in affairs that are a risk to national security came under consideration. After consideration, this evidence didn’t hold much water, as the social media platform’s demands from users aren’t conscientious.

In Molly’s words, “TikTok is asking for information that the users consent to, and they give that voluntarily to TikTok.” So the claims that the platform illegally accesses personal data from users for other uses don’t add up. US District Judge Donald W. Molloy points to Montana’s arguments as being confusing.

The state was also questioned as to their right to make decisions for users whether they should share their data with TikTok. Surprisingly, the Montana state government didn’t find any documents proving that TikTok is a threat to national security. So the state’s plans to ban TikTok from their residents’ devices by next year lack good judgment.

However, the US government has a ban on TikTok for government devices. This should have been the path that the Montana state government should have taken instead of imposing the ban on citizens. Montana’s ban on TikTok will soon see a preliminary injunction ahead of the court’s final decision on this matter.


[ad_2]
Source link

How Google Maps helps save you from getting a speeding ticket

0
[ad_1]
Google Maps users know that the app will show them the speed limit along the routes they are traveling on. This comes in handy on low-visibility days when a speed limit sign can’t be properly viewed. And if you are driving in an area that you’re not familiar with, a quick glance at Google Maps will show you how fast you should be driving. Google obtains speed limit data from various sources.
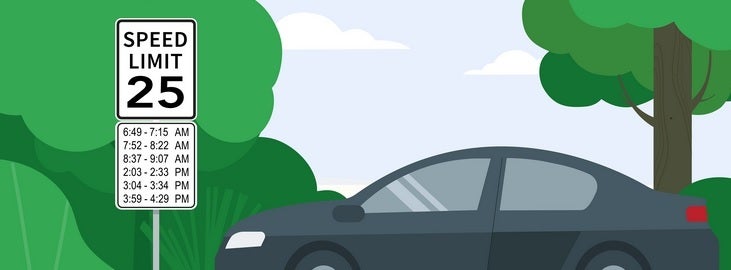
In a post published today, Google says that one source is “authoritative data from local governments that helps us know what the default speed limits are for different types of roads when there is no signage. For example, in California, 25 miles per hour is the default speed limit in residential areas.” And some speed limits fluctuate due to the time of day, weather, and other factors. To keep track of those varying speed limits, Google relies on AI and imagery.

Google uses imagery from Street View, third-party sources, and AI to determine which signs give speed limit information

Google uses imagery from Street View and third-party sources along with its AI capabilities to figure out which signs are speed limit signs. Even if a specific sign looks different than the speed limit signs in other countries, Google can determine whether it is showing drivers what the speed limit is in a certain country. As an example, Google points out that in the U.S. a speed limit sign is marked as such while in Germany a speed limit sign might show just numbers indicating the maximum speed allowed.

GPS is used to match the geographical location of such a sign with its location in the world helping Google determine exactly where the sign is located. This helps it to know exactly where to change the speed limit along your route.

When a speed limit is changed due to requests from a community or traffic conditions are temporarily or permanently changed, Google can check it out by taking a look at traffic patterns. If it notes that drivers are constantly driving in a certain area at a rate below the speed limit, it could be a sign that the speed limit has been reduced. This might happen if a new school has been built in the area, or the government considers the road a high-risk area and wants drivers to slow down.

Google will look for confirmation of a change by turning to official data from local governments and by looking at refreshed Street View imagery. If the latter does not exist, it requests the imagery from third-party partners. Google says, “If the partner has photos available, we use a combination of AI and help from our operations team to identify the sign in the images, extract the new speed limit information, and update Google Maps.”

Google’s speed limit data helped the Volvo EX30 pass the EU’s General Safety Regulations

Automakers need to know speed limit data to help them add certain features to their cars. For assisted driving or fully automated driving features to work, cars need to have accurate speed limit information just as human drivers do. The EU’s General Safety Regulations (GSR) require that new vehicles registered after July 2024 must have an intelligent speed assistance (ISA) feature displaying the legal speed limit at all times. This feature must warn drivers if they are speeding. 

Google says that in order to meet the requirements, vehicles must deliver accurate speed limits for at least 90% of any drive. While cars will be equipped with cameras and sensors to help them make sense of speed limit signs, the same issues that prevent human drivers from reading them (the weather, poor placement of a sign, and physical obstacles covering the sign) can affect cameras and sensors from obtaining the correct speed limit information.

According to the report, Google notes that the ISA feature in Volvo’s EX30 passed the EU’s GSR certification by using Google Maps’ speed limit data. As the company so proudly states, “This means that the EX30 can reliably display the legal speed limit, even when there aren’t clear signs on the road.” If Google Map’s speed limit data can be accurate enough to help a car pass the EU’s GSR certification, imagine how it can help you arrive at a destination quickly and safely.


[ad_2]
Source link

Microsoft Launches Bug Bounty Program For AI Bing

0
[ad_1]

Following the roll-out of new AI-powered Bing across different products, Microsoft has launched a dedicated bug bounty program for this technology. Under this program, security researchers and bug hunters can earn up to $15,000 for reporting relevant vulnerabilities.

Microsoft Announces Bug Bounty For AI-Powered Bing

According to a recent post, Microsoft has announced launching a dedicated bug bounty program for its new Bing. Under this program, the tech giant welcomes bug reports for all its products, flaunting the new AI-Bing experience. And for this effort, the firm has pledged lucrative rewards for the researchers.

Specifically, the products eligible for this Microsoft AI bug bounty program include the Edge browser’s Bing integration, Bing Chat for Enterprise, AI integration on the Bing search website (bing.com), and AI-powered Bing experience with Skype and Microsoft Start applications (for iOS and Android systems).

The researchers submitting their bug reports may receive from $2,000 to $15,000 (USD) bounties, as mentioned on Microsoft’s bounty program website.

This program particularly deals with AI-related Bing vulnerabilities. For vulnerabilities in other Bing-related products, Microsoft will handle the reports under the M365 Bounty Program. Recognizing that correctly submitting the bug reports for the relevant platform can be difficult, Microsoft assured rerouting the reports to the relevant program after reviewing the submission.

The Redmond giant rolled out the new AI-powered Bing Search as the innovative smart assistant for users. By integrating OpenAI’s ChatGPT with its search engine, Bing, Microsoft developed a one-stop solution for Bing.com and Microsoft Edge users to solve their queries intelligently.

Following its rise in popularity, the technology also garnered negative attention, eventually becoming an inadvertent vector for malware distribution. Hence, the recent move to invite the security community to assess Bing AI’s defense against existing threats made perfect sense.

With the dedicated bug bounty program, Microsoft not only gives bug hunters another opportunity to make money but also steps ahead to ensure a safe AI experience for Bing users.

Let us know your thoughts in the comments.


[ad_2]
Source link

New Cisco Web UI Vulnerability Exploited by Attackers

0
[ad_1]

Cisco is aware of the active exploitation of this vulnerability, but there are no workarounds available.

Cisco has warned customers of a previously unknown vulnerability in the web UI feature of Cisco IOS XE Software that is being actively exploited by attackers. The vulnerability allows a remote, unauthenticated attacker to create an account on an affected system with privilege level 15 access, which could further allow them to gain full control of the device.

The vulnerability (CVE-2023-20198) affects Cisco IOS XE Software if the web UI feature is enabled, which is done by default. Cisco recommends that customers disable the HTTP Server feature on all internet-facing systems to mitigate the risk of exploitation.

In its security advisory, Cisco said that the company is aware of the active exploitation of this vulnerability, and there are no workarounds available. Cisco is working on a software patch to address the vulnerability, but a release date has not yet been announced.

John Bambenek, Principal Threat Hunter at Netenrich, a San Jose, Calif.-based security and operations analytics SaaS company commented on the advisory and warned that “The fact there isn’t a patch yet makes this issue all the more urgent and admins should take this opportunity to ensure their Cisco IOS devices either disable the Web UI or only have it accessible from private administrative LANs that are restricted to authorized users.”

Mayuresh Dani, Manager, Threat Research at Qualys, a Foster City, Calif.-based provider of disruptive cloud-based IT, security and compliance solutions stressed that Cisco has not provided the list of devices affected, which means that any switch, router or WLC running IOS XE and has the web UI exposed to the internet is vulnerable.”

Dani disclosed concerning statistics regarding Cisco devices with their web UI exposed to the internet. These findings indicate that more than 40,000 Cisco devices fall into this category, with the majority of them actively listening on port 80.

“Devices that have web UI and management services publicly exposed to the internet or to untrusted networks should be modified so that they are not exposed to untrusted networks by means of ACLs or other solutions. 2. Disable the web UI component on these devices,” Dani advised.

Indicators of Compromise

To determine whether a system may have been compromised, customers can check the system logs for the presence of the following log messages:

  • %SYS-5-CONFIG_P: Configured programmatically by process SEP_webui_wsma_http from console as user on line
  • %SEC_LOGIN-5-WEBLOGIN_SUCCESS: Login Success at 03:42:13 UTC Wed Oct 11 2023

Customers can also use the following command to check for the presence of the implant:

curl -k -X POST "https://systemip/webui/logoutconfirm.html?logon_hash=1"

If the request returns a hexadecimal string, the implant is present.

Recommendations

Cisco strongly recommends that customers disable the HTTP Server feature on all internet-facing systems. To disable the HTTP Server feature, use the no ip http server or no ip http secure-server command in global configuration mode.

Customers who cannot disable the HTTP Server feature should restrict access to those services to trusted networks.

Cisco is also working on a software patch to address the vulnerability, and customers are advised to apply the patch as soon as it is available.

  1. Cisco’s new tool will detect malware in encrypted traffic
  2. New 19 CISA Advisories Highlight Vulnerabilities in Top ICS Products
  3. New Akira Ransomware Targets Businesses via Exploited CISCO VPNs
  4. Ex-employee hacked Cisco’s AWS Infrastructure; erased virtual machines
  5. Unpatched Cisco Catalyst SD-WAN Manager Systems Exposed to DoS Attacks

[ad_2]
Source link

Samsung pushes October update to the US Galaxy S23

0
[ad_1]

It’s turning out to be a good day for Galaxy S23 users in the US today. Those who have enrolled in Samsung’s One UI 6.0 beta program are getting a new beta update, the seventh so far. Devices running One UI 5.1.1 are getting the latest security patch. The October SMR (Security Maintenance Release) is also rolling out to the Galaxy Z Flip 5G.

The October update is rolling out to the Galaxy S23 series in the US

Samsung‘s October update is currently available for the factory-unlocked units of the Galaxy S23, Galaxy S23+, and Galaxy S23 Ultra in the US. The Korean behemoth is pushing the new SMR with the firmware build number S91*U1UES1AWIF. The devices aren’t getting anything more than this month’s security fixes.

The company has already revealed that its latest security patch contains fixes for 46 vulnerabilities. 12 of those are Galaxy-specific patches coming directly from Samsung, while others concern Android OS issues. They are patched by Google or the vendor of an affected system component. At least two vulnerabilities patched this month are confirmed to be critical flaws.

Samsung has already rolled out these security patches to dozens of Galaxy devices, including the international versions of the Galaxy S23 series. The US versions are now getting them too. If you’re using a Samsung smartphone, you can check for new updates from the Settings app. Go to the Software update menu and tap on Download and install.

Note that Galaxy S23 phones running One UI 6.0 beta have already received the October security patch. The newly released beta update brings a handful of bug fixes as Samsung prepares for the stable rollout. The big update, which introduces Android 14 to Galaxy devices, is expected to arrive later this month. We will let you know when the rollout begins.

The new security patch is also available for the Galaxy Z Flip 5G

Along with the Galaxy S23, Samsung is also pushing the latest SMR to the Galaxy Z Flip 5G in the US. The update is currently available for carrier-locked units with the build number F707USQU6IWI2. The device is getting some system stability improvements as well, the company’s changelog confirms.

The 4G model of the original clamshell foldable has yet to pick up the update. It isn’t yet available for the unlocked 5G model either. Hopefully, Samsung won’t keep users of these devices waiting for much longer. Both Galaxy Z Flip models have received the October SMR in international markets.


[ad_2]
Source link

Intel launches new Raptor Lake refresh CPUs with AI-overclocking

0
[ad_1]

Intel today has announced the launch of its Raptor Lake CPU refresh. The new family of CPUs for this year consists of the 14th gen Core i5, Core i7, and Core i9 CPUs powered by AI overclocking features for enhanced performance during gaming and content creation. As well as just general day-to-day use for power users.

The new family of processors will include six different CPU versions for desktop PCs at launch. Each of the three models will come in both a K and KF version, with the KF versions coming as a graphics-less variation that will save you a few bucks. For instance, the top-end flagship CPU which is the Core i9-14900K will cost $589. But you’ll be able to pick up the Core i9-14900KF for $564 if you feel like dropping that price down a bit. Comparatively Intel will offer the Core i7-14700K for $409 and its KF model for $384, and then the Core i5-14600K for $319 and then its KF model for $294.

Basically Intel is offering its Raptor Lake refresh CPUs for the same price as 2022’s 13th Gen but upping the performance. Making these a great option if you haven’t upgraded for quite a few years.

Intel Raptor Lake refresh CPUs go on sale October 17

Intel says that its latest CPUs for the desktop category will officially go on sale on October 17 so you should start to see these hit store shelves sometime in the morning the day of. Expect them to be available from local retailers like Best Buy, Microcenter and others as well as their online counterparts, and retailers like Amazon.

Intel says these new chips provide a performance boost by up to 23% more than competing options. Which in this case is referring to the AMD Ryzen 7000X3D CPUs. Chips like the Core i9-14900K arrive out of the box with up to 24 cores and 32 threads, and up to 6GHz of frequency. Meanwhile the 14700K has 20 cores and up to 28 threads. The 14th Gen chips also support WiFi 7 and come with new AI assist tuning for overclocking, which will be accessible from Intel’s Extreme Tuning Utility. What’s more is that Intel says this provides a “one-click guided overclocking” process to really amp up the performance of each chip.

And overclocking should be easier for all users across the board to accomplish overclocking for their own systems because of this process.


[ad_2]
Source link