A threat actor has claimed that there is a vulnerability in the HackerOne Bug Bounty Platform that allows 2FA to be bypassed. This vulnerability requires only a username and password without user interaction or… pic.twitter.com/CyxwP8Hrtz
HackerOne, a leading platform that connects businesses with cybersecurity experts to identify and fix vulnerabilities, has yet to release an official statement regarding the alleged 2FA bypass vulnerability.
The platform is known for its robust security measures, including mandatory 2FA for all users, which makes this claim particularly alarming.
Experts suggest that if the vulnerability is confirmed, it could have significant implications for the platform’s users and the broader cybersecurity community.
“We are aware of the claims made on social media and are actively investigating the matter. Our priority is the security of our users and the integrity of our platform,” a HackerOne representative stated in a preliminary response.
The cybersecurity community has reacted with a mix of skepticism and concern.
While some experts are waiting for official confirmation and details from HackerOne, others are already speculating about the potential impact of such a vulnerability.
If the 2FA bypass is real, it could allow unauthorized access to sensitive information and reports submitted by ethical hackers, undermining the trust in the bug bounty process.
“This could be a significant setback for the bug bounty ecosystem if proven true. It highlights the need for continuous vigilance and improvement in security measures, even for platforms dedicated to cybersecurity,” commented Jane Doe, a cybersecurity analyst.
As the investigation unfolds, users of the HackerOne platform are advised to stay vigilant and follow any security recommendations issued by the platform.
The cybersecurity community eagerly awaits further updates on this developing story.
"Is Your System Under Attack? Try Cynet XDR: Automated Detection & Response for Endpoints, Networks, & Users!"- Free Demo
Using mapping and navigation apps like Apple Maps, Google Maps, and Waze are great reasons to buy a smartphone. Those of you old enough to remember writing down directions or using a map to get from point “A” to point “B” safely are probably still amazed at how we can type in our destination in one of the aforementioned trio of apps and quickly have a route to follow on our phone screens.
It feels like magic and even more so when a route change is forced on the driver due to roadwork, police action, a surprising change in the weather, or a traffic problem. Perhaps the most amazing thing is that Google Maps has been providing mobile phone owners with free turn-by-turn directions ever since the Motorola DROID became the first phone released with Android 2.0 in November 2009.
Google has been quietly adding a new feature to the iOS version of Google Maps only in certain regions and to a limited number of users. That feature is a speedometer which is already available to many of those using the Android version of Google Maps and both variants of Waze. The speedometer on a mapping and navigation app that uses GPS is more accurate than the one on your car’s dashboard according to autoevolution. And since some drivers glance at the directions on their navigation app while driving (more on that later), they can check out these directions while seeing how fast they are going all at the same time.
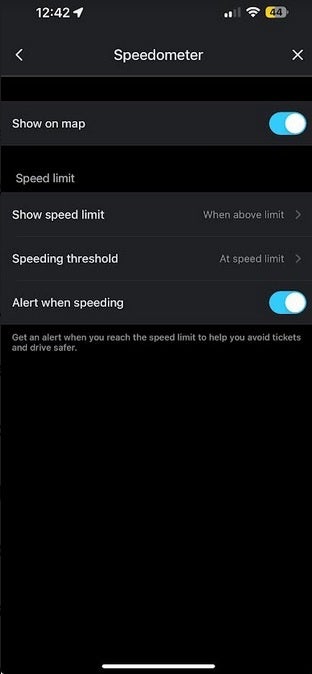
Setting the speedometer feature in Waze
It appears that Google is testing the appearance of a speedometer for the iOS version of Google Maps and for CarPlay, and this is being confirmed by the feature showing up intermittently on some iPhone handsets. As recently as two days ago, a post was left on Reddit from an iPhone user that stated, “I was going to work today and using google maps on my work phone (iPhone 14 pro) and noticed the exclusive android speedometer feature was visible. However upon testing on another phone (iPhone 14 Pro Max) the feature was nowhere to be seen.”
In some states, a driver won’t have the legal right to view his speed as it appears on Google Maps as holding a smartphone while behind the wheel in these jurisdictions is against the law. If you’re not driving in such a state, Waze will show you how fast you’re going and can even alert you when you’re speeding. Open the Waze app and tap the three-line hamburger menu in the upper left corner of the screen.
Tap on Settings > Speedometer and toggle the settings the way you want them. You can have your speed appear on the map, show the current speed limit when you’re driving faster than the limit, show it all the time, or never show it. You can also arrange to hear an alert when you’re driving at the speed limit, or driving 5 MPH, 10 MPH, 15 MPH, or 20 MPH above the limit, or if you’re 5%, 10%, 15%, or 20% above the limit.
An unauthenticated endpoint vulnerability allowed threat actors to identify phone numbers associated with Authy accounts, which was identified, and the endpoint has been secured to prevent unauthorized access.
No evidence suggests the attackers gained access to internal systems or other sensitive data, but as a precaution, it’s crucial to implement additional security measures to mitigate potential phishing attacks that could exploit the leaked phone numbers.
An unauthenticated endpoint in Twilio’s Authy app allowed malicious actors to identify user phone numbers. While no evidence suggests a broader system intrusion or sensitive data exposure,
They urge all Authy users to update their Android and iOS apps to address the vulnerability, which mitigates the risk of threat actors exploiting the exposed phone numbers for phishing and smishing attacks.
Authy users should maintain vigilance and carefully examine any text messages that appear to be suspicious.
A new software update is available for both Android and iOS devices, which addresses various bug fixes, including security vulnerabilities.
It is imperative to install this update promptly to preserve the device’s functionality and integrity.
For Android users, a link has been provided to download the update, while iOS users can acquire the update through the standard software update process on their devices.
Twilio recognizes a security incident and apologizes for the disruption, as their Security Incident Response Team (T-SIRT) is currently investigating the issue and will provide updates as the situation evolves.
This incident underscores the critical role of T-SIRT in proactively identifying security vulnerabilities, implementing preventative measures to mitigate risks, and taking corrective actions in the event of a breach.
T-SIRT’s swift response and ongoing communication are essential to minimizing the impact of security incidents and maintaining customer trust.
If users are unable to access the Authy account due to login issues or lost access to the registered phone number, contacting Authy support is the recommended course of action.
Their specialists will address the request and collaborate to restore functionality to the Authy account, which may involve troubleshooting login problems or initiating a phone number change procedure.
"Is Your System Under Attack? Try Cynet XDR: Automated Detection & Response for Endpoints, Networks, & Users!"- Free Demo
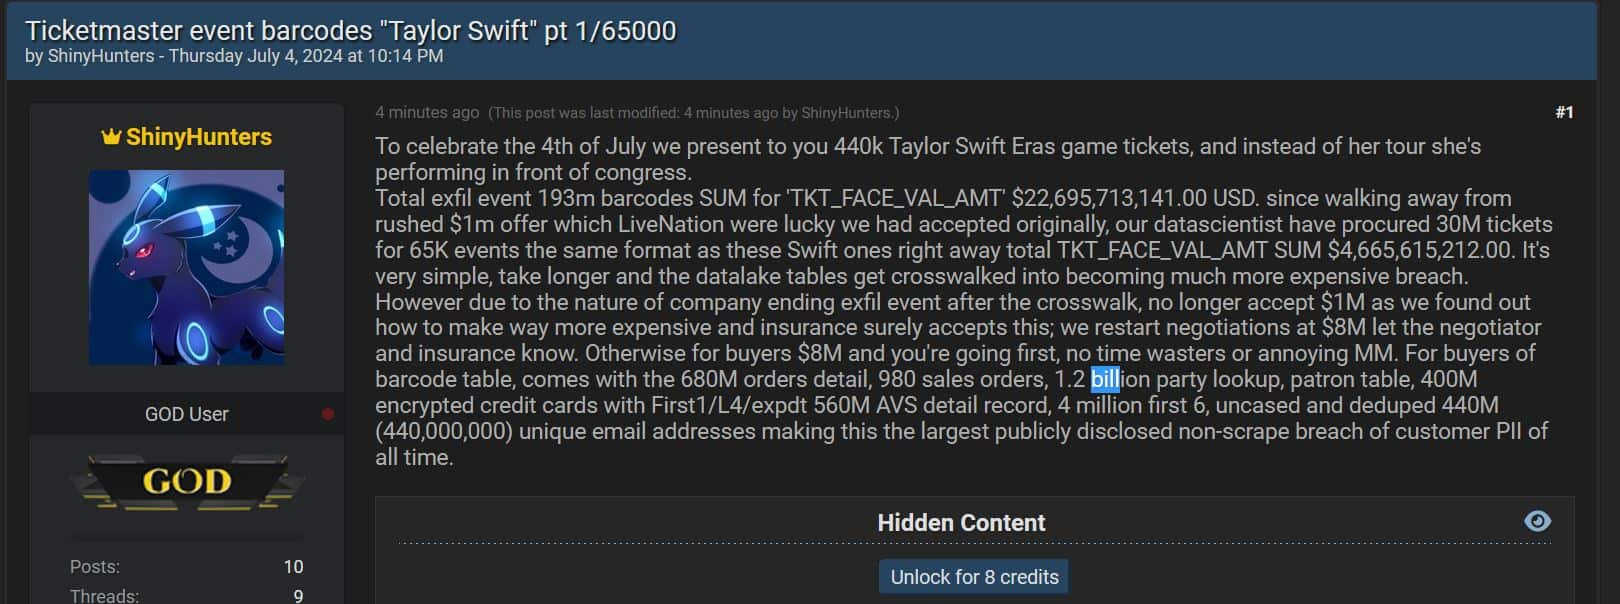
The ShinyHunters hacker group claims the Ticketmaster breach is far bigger than previously anticipated, stealing 193 million barcodes, including 440,000 Taylor Swift tickets. Valued at $22 billion, they now demand $8 million from LiveNation!
In May 2024, the notorious hacker group ShinyHunters breached Ticketmaster – LiveNation, as we know it. However, the hackers have now released new details about the extent of their breach. These details have been published on the infamous cybercrime and hacker platform Breach Forums titled “Ticketmaster event barcodes ‘Taylor Swift’ pt 1/65000.”
ShinyHunters on Breach Forums (Screenshot: Hackread.com)
The Breach Unveiled
ShinyHunters marked the Fourth of July with a disturbing announcement: they claim to have stolen 440,000 tickets for Taylor Swift’s Eras Tour. In a symbolic twist, they suggest that instead of Swift performing on her tour, she will be “performing in front of Congress,” indicating this breach’s severity and public exposure.
The Staggering Numbers
The hackers provide an extensive breakdown of their hack:
Total Exfiltrated Barcodes: 193 million
Total Value of Stolen Tickets (TKT_FACE_VAL_AMT): $22,695,713,141.00 USD
A Shift in Negotiations
According to ShinyHunters, the hackers initially accepted a rushed $1 million offer from LiveNation to keep the breach under wraps. However, realizing the true value of the data they possess, they have escalated their demand to $8 million. They justify this increase by pointing out that they have found ways to make the breach more costly and complicated for the affected company.
Expanded Scope
In addition to the Taylor Swift tickets, ShinyHunters claims to have:
30 million tickets for 65,000 events: Similar to the Swift tickets, valued at $4,665,615,212.00 USD
Data at Risk
The hackers have detailed the extensive nature of the stolen data, which includes:
980 million sales orders
680 million orders detail
1.2 billion party lookup records
440 million unique email addresses
4 million uncased and deduped records
560 million AVS (Address Verification System) detail records
400 million encrypted credit card details with partial information
They boast that this breach is the largest publicly disclosed non-scrape breach of customer Personally Identifiable Information (PII) to date.
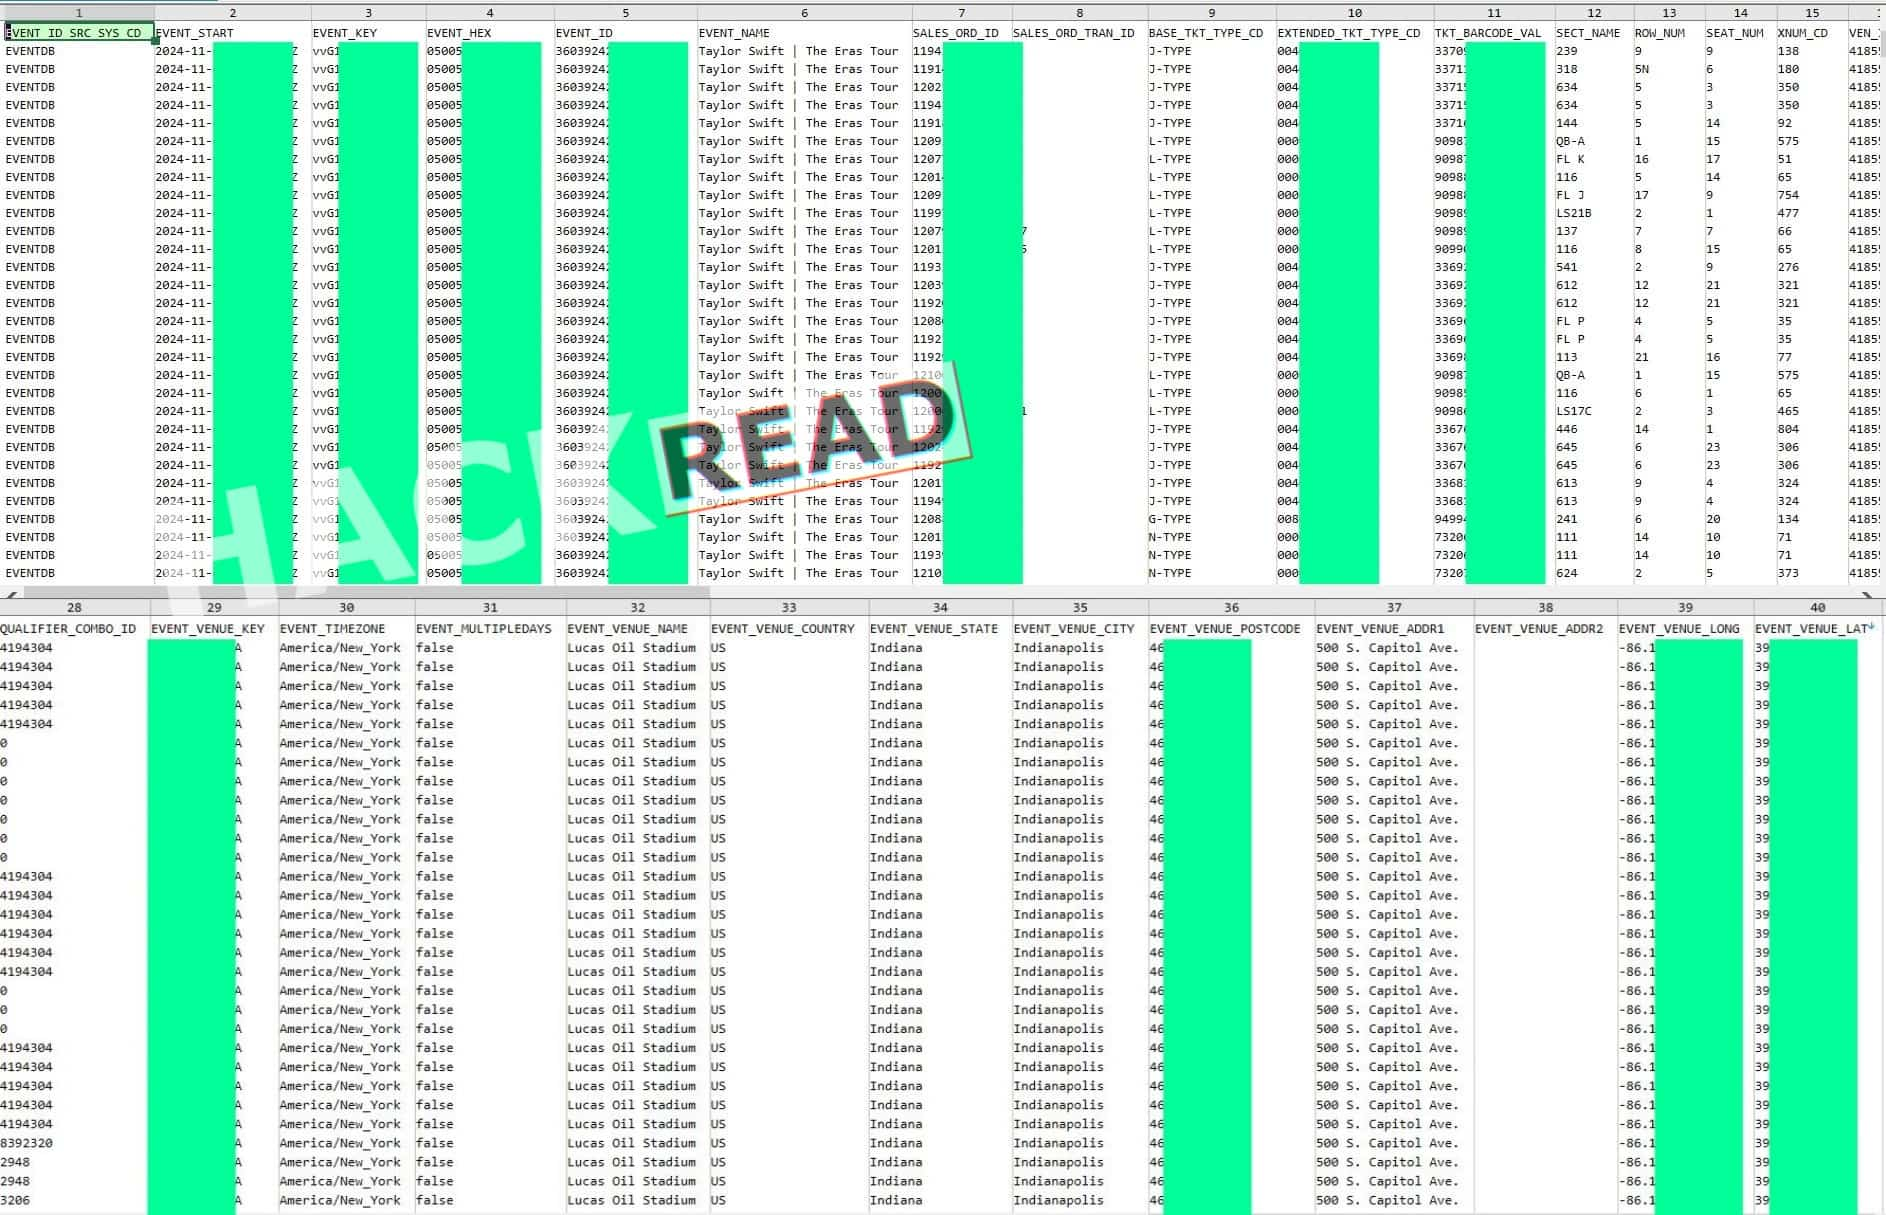
Screenshot from the leaked file (Screenshot: Hackread.com)
Disclosure:
Hackread.com believes in transparency; therefore, we are publicly revealing that we used ChatGPT-4o to analyze the leaked data due to its complexity. Here’s the breakdown and conclusion:
The leaked data contains detailed information about ticket sales for Taylor Swift's Eras Tour event, specifically for a concert at Lucas Oil Stadium in Indianapolis, Indiana. Here is a breakdown of the key data fields present in the leak:
Event Details:
EVENT_ID_SRC_SYS_CD: Source system code for the event. EVENT_START: Date and time of the event. EVENT_KEY: Unique identifier for the event. EVENT_HEX: Hexadecimal representation of the event ID. EVENT_ID: Numeric ID of the event. EVENT_NAME: Name of the event (Taylor Swift | The Eras Tour). EVENT_TIMEZONE: Timezone of the event. EVENT_MULTIPLEDAYS: Indicator if the event spans multiple days. EVENT_VENUE_NAME: Venue name. EVENT_VENUE_COUNTRY: Country where the event is located. EVENT_VENUE_STATE: State where the event is located. EVENT_VENUE_CITY: City where the event is located. EVENT_VENUE_POSTCODE: Postcode of the event venue. EVENT_VENUE_ADDR1: Address line 1 of the venue. EVENT_VENUE_ADDR2: Address line 2 of the venue (if applicable). EVENT_VENUE_LONG: Longitude of the event venue. EVENT_VENUE_LAT: Latitude of the event venue. Ticket Details:
SALES_ORD_ID: Sales order ID. SALES_ORD_TRAN_ID: Transaction ID related to the sales order. BASE_TKT_TYPE_CD: Base ticket type code. EXTENDED_TKT_TYPE_CD: Extended ticket type code. TKT_BARCODE_VAL: Barcode value for the ticket. SECT_NAME: Section name where the seat is located. ROW_NUM: Row number of the seat. SEAT_NUM: Seat number. XNUM_CD: Additional numerical code related to the seat. VEN_ID: Venue ID. HOST_SYS_CD: Host system code. HOST_VAX_ACCT_NUM: Host VAX account number. HOST_ACCT_CREATE_DT: Date when the host account was created. TKT_FACE_VAL_AMT: Face value amount of the ticket. TRAN_VOID_FLG: Indicator if the transaction was voided. TRAN_VOID_DT: Date when the transaction was voided (if applicable). CPN_CAT_ID: Coupon category ID. CPN_PWD_PRIM_VAL: Primary value of the coupon password. QUALIFIER_NAME1/2/3: Qualifier names. QUALIFIER_COMBO_ID: Qualifier combo ID. EVENT_VENUE_KEY: Venue key.
Potential Uses of the Data
The barcode values (TKT_BARCODE_VAL) and seat details (section, row, seat numbers) can be used to create counterfeit tickets or resell tickets fraudulently. Identity Theft and Financial Fraud:
The data includes host account creation dates and VAX account numbers, which could be leveraged to identify and exploit user accounts. Phishing and Social Engineering Attacks:
With detailed personal information, attackers can craft convincing phishing emails or social engineering attacks targeting ticket buyers. Market Analysis and Competitor Intelligence:
Competitors can analyze the pricing (TKT_FACE_VAL_AMT), seating arrangements, and sales data to understand Ticketmaster's market strategies. Reputation Damage:
Public disclosure of this data can significantly harm Ticketmaster's reputation, causing loss of customer trust and future business.
The exposure of personally identifiable information (PII) might result in substantial fines from regulatory bodies and legal actions from affected customers.
Conclusion
The leaked data is highly sensitive and can be exploited in numerous malicious ways, from direct financial fraud to broader market implications and significant reputational damage for Ticketmaster. Immediate steps to mitigate these risks and protect affected customers are crucial.
Implications for Ticketmaster and Customers
This breach could have severe implications for Ticketmaster and its customers:
Financial Loss: The face value of the stolen tickets alone amounts to billions of dollars. Additionally, the potential costs of managing the breach, compensating affected customers, and potential fines could be astronomical.
Reputation Damage: Such a high-profile breach can severely damage Ticketmaster’s reputation, leading to loss of customer trust and future business.
Customer Impact: The stolen data includes highly sensitive information, such as encrypted credit card details and personal email addresses, putting millions of customers at risk of identity theft and financial fraud.
Increased Security Measures: This breach underscores the need for enhanced security measures within the company to prevent future incidents.
The ShinyHunters’ breach of Ticketmaster goes on to show the cybersecurity threat posed by cybercriminals. Although Ticketmaster previously acknowledged the breach, as the situation develops, it will be necessary for Ticketmaster to address the breach transparently, enhance its security protocols, and work towards restoring customer trust. Meanwhile, customers should remain alert and monitor their accounts for any suspicious activity.
For more updates on this developing story, stay tuned!
Twilio’s Authy app for both iOS and Android, designed to make it easier for users to request two-factor authentication (2FA) when signing into an app, ironically has been hacked resulting in the theft of customer smartphone numbers. In a blog post, Authy wrote, “Twilio has detected that threat actors were able to identify data associated with Authy accounts, including phone numbers, due to an unauthenticated endpoint. We have taken action to secure this endpoint and no longer allow unauthenticated requests.”
Twilio requests that all Authy users update to the latest iOS or Android versions of the app in order to install the latest security updates. Twilio adds, “While Authy accounts are not compromised, threat actors may try to use the phone number associated with Authy accounts for phishing and smishing attacks; we encourage all Authy users to stay diligent and have heightened awareness around the texts they are receiving.
Two-factor authentication (2FA) requires the use of a second layer of protection when signing into an app. For example, after signing into an app you receive an SMS on your phone containing a code that you need to type in to open the app. This prevents an attacker from opening one of your apps and getting into your account, changing your password, and robbing you blind. Right now, Twilio says that the customer data stolen in the hack was limited to phone numbers.
You need to submit your phone number when opening an account with Authy
Twilio is blaming the use of “unauthenticated endpoints” for the successful hack and notes that it has taken action to secure this endpoint and “no longer allows unauthenticated requests.” A media report puts the number of phone numbers stolen at 33 million. On a well-known hacking forum, hackers known as ShinyHunters admitted to hacking Twilio and stealing 33 million cellphone numbers.
While the theft of phone numbers shouldn’t necessarily scare Authy users, the attackers could use these numbers to call or text the victimized Authy subscribers. The attackers could then pretend to be from Authy, and seek other user information including social security numbers, bank account numbers, and other sensitive personal data. Be careful when receiving a call or text that supposedly comes from Twilio or Authy and do not reveal any personal data no matter how insistent the caller or the text is.
And this hack has nothing to do with whether 2FA works to protect your personal data. If you like 2FA as a deterrent, don’t stop using it because Authy has been attacked.
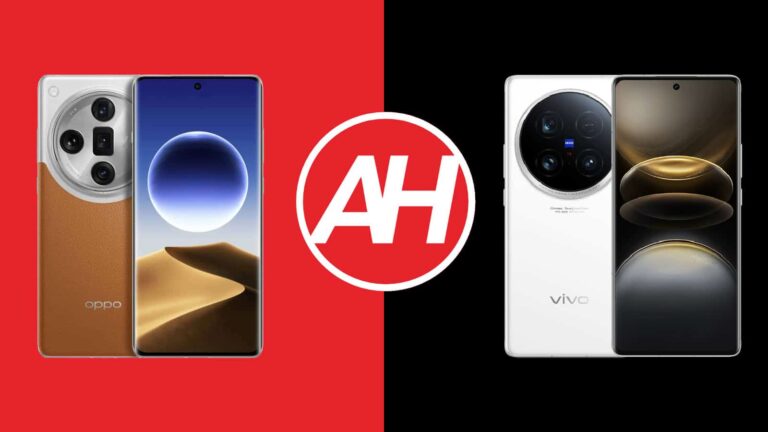
We’re here to compare two ‘Ultra’ phones yet again. This time around we’re comparing two sister smartphones, the OPPO Find X7 Ultra vs Vivo X100 Ultra. Why sister smartphones? Well, OPPO and Vivo are sister companies, both are under the BBK Electronics umbrella. Having said that, these two phones are quite different. They not only look different, but come with different software, and so on. Do note that neither phone is available in global markets, however. They are both limited to China, though they work fine once you install the Google Play Store. Carrier support does vary from region to region, though.
As we usually do, we will first list their specifications and take it from there. They do have very powerful specs, hence the ‘Ultra’ name that both companies used. We will also compare their designs, displays, performance, battery life, cameras, and audio output. With that in mind, let’s get down to it, shall we?
Specs
OPPO Find X7 Ultra vs Vivo X100 Ultra, respectively
The first thing you’ll notice when you look at them from the front is that both smartphones offer curved displays. Those displays have a centered display camera hole, each, and the bezels are also very thin. The corners on both smartphones are slightly rounded, and both devices have their physical keys on the right-hand side. The OPPO Find X7 Ultra also has the alert slider, but it’s located on the left side.
You will also notice a circular camera island on the backs of both phones. Both of those are centered and placed in the upper portion of the back. They do look different, however, and the OPPO Find X7 Ultra does have one extra camera back there. More on that later. The materials these two phones use are different. They do use aluminum for their frame, but the back sides are different. The OPPO Find X7 Ultra combines vegan leather with glass. Vegan leather actually covers two-thirds of its back. The Vivo X100 Ultra, on the flip side, has glass on the back. Because of this, the OPPO Find X7 Ultra does offer a bit more grip in comparison.
Now, in regards to the size. The OPPO Find X7 Ultra does have a slightly larger display, and it is slightly wider than the Vivo X100 Ultra. They’re basically the same in terms of height, while the Find X7 Ultra is barely thicker (0.3mm difference). OPPO’s handset is slightly lighter (8-gram difference), and the use of vegan leather is the reason for it. Both smartphones are IP68 certified for water and dust resistance. Both of them are large and feel very premium in hand.
OPPO Find X7 Ultra vs Vivo X100 Ultra: Display
The OPPO Find X7 Ultra includes a 6.82-inch QHD+ (3168 x 1440) LTPO AMOLED display. That display has a refresh of up to 120Hz, and it can project up to 1 billion colors. Dolby Vision is supported, as is HDR10+ content. The display brightness goes up to 4,500 nits in theory, though you’ll never get that high. The screen-to-body ratio is at around 90%. This panel is protected by the Gorilla Glass Victus 2.
The Vivo X100 Ultra, on the flip side, includes a 6.78-inch QHD+ (3200 x 1440) LTPO AMOLED display. It can project up to 1 billion colors, and it has a refresh rate of up to 120Hz. Dolby Vision is supported here too, and the peak brightness is at 3,000 nits. The screen-to-body ratio is at around 90% too, though slightly lower than on the Find X7 Ultra. The display aspect ratio here is 20:9. Display protection is unknown.
You will be extremely happy regardless of which of the two displays you end up getting. Both of them are outstanding. Not only are they large, sharp, and vivid, but they have great viewing angles, and those inky blacks that people love so much. They are also very fluid during use and get immensely bright when needed. Both displays also support high-frequency PWM dimming. The OPPO Find X7 Ultra possibly offers better display protection, though. Either way, you can’t go wrong with either one of these two panels.
OPPO Find X7 Ultra vs Vivo X100 Ultra: Performance
The Snapdragon 8 Gen 3 SoC from Qualcomm fuels both of these smartphones. That is one of the best processors on the market at the moment. It’s a 4nm chip. Having said that, both smartphones also offer up to 16GB of LPDDR5X RAM, and UFS 4.0 flash storage too. In other words, they are on the same playing ground when it comes to performance-related specifications. They both also ship with Android 14 out of the box, albeit with different skins installed on top of Google’s OS.
The performance is outstanding on both devices. Regular day-to-day performance is as good as it gets, basically. Bogging down either of these two phones is not easy at all. They fly through app launches, multitasking, browsing, image editing, and everything else you can think of, basically. Even video editing is a piece of cake on both. Not even truly heavy multitasking slowed down either of these two devices.
What about gaming, though? Well, that’s also something you don’t have to worry about. Both smartphones not only come with gaming-related software to help you out, but they offer great performance. Truly demanding titles, such as Genshin Impact, will make both phones sweat a bit (they’ll get quite warm after prolonged gaming sessions), but that won’t affect the performance. Neither phone got too hot to handle for us either, which is great.
OPPO Find X7 Ultra vs Vivo X100 Ultra: Battery
OPPO’s flagship has a 5,000mAh battery pack, while the Vivo X100 Ultra comes with a 5,500mAh unit. Yes, the Vivo X100 Ultra does have a bigger battery pack, but both smartphones deliver great battery life. It depends on your usage, but both smartphones can go over the 7-hour screen-on-time mark, and even reach that 8-hour mark if you’re careful enough. Technically, yes, the Vivo X100 Ultra tends to be a bit better in the battery life department, but not by much at all.
Your mileage may vary, of course. You’ll be using different apps in different ways with different signal strengths, so you’ll likely get different results. Playing games will affect the battery life quite a bit, of course. Do note that the battery numbers mentioned in the previous paragraph were achieved without gaming thrown into the mix. The bottom line is, both smartphones do deliver when it comes to battery life, very much so.
Even if you end up running low on juice, both of these devices offer truly fast charging. OPPO’s handset supports 100W wired, 50W wireless, and 10W reverse wireless charging. The Vivo X100 Ultra comes with 80W wired, 30W wireless, and reverse wired charging support. OPPO technically offers faster charging across the board. Both smartphones do ship with a charger in the box, though.
OPPO Find X7 Ultra vs Vivo X100 Ultra: Cameras
Both of these smartphones have extremely compelling camera hardware and performance. The OPPO Find X7 Ultra is equipped with four 50-megapixel cameras. It includes a 50-megapixel main camera (1-inch type sensor), a 50-megapixel ultrawide unit (123-degree FoV), a 50-megapixel periscope telephoto camera (2.8x optical zoom), and a second 50-megapixel periscope telephoto unit (6x optical zoom). These cameras are also boosted by Hasselblad, who does color tunning for OPPO and helps out in other ways.
The Vivo X100 Ultra includes three cameras on the back. It has a 50-megapixel main camera (1-inch type sensor, gimbal OIS), a 50-megapixel ultrawide camera (116-degree FoV), and a 200-megapixel periscope telephoto camera (3.7x optical zoom). This phone’s cameras are boosted by ZEISS. The company’s T* coating is used, while ZEISS also helps in other ways with the camera performance.
The end results are different, but both smartphones do a fantastic job. The OPPO Find X7 Ultra prefers more contrasty shots and does a great job with HDR. Both smartphones do preserve a ton of detail, and do a great job of balancing shots. The Vivo X100 Ultra does lean towards warmer color tones for photos, though. Both smartphones do a great job with macro photography and with portraits too, though the images do end up looking different, of course.
In low light, they both shine. The OPPO Find X7 Ultra prefers to keep images a bit closer to real life, as it is not afraid of keeping parts of an image a bit darker than the Vivo X100 Ultra. It all depends on your personal preference, but both smartphones really do a fantastic job in low light. The Vivo X100 Ultra is a bit better when it comes to light flares, but the OPPO Find X7 Ultra also does a great job with those. These are some of the best phones you can get for low light photography at the moment, no doubt about that.
Audio
You will find stereo speakers on both of these smartphones. The ones on the OPPO Find X7 Ultra are slightly louder, though. The difference is not that big, but still, it’s worth noting. The sound quality is great on both sides.
What neither of the two phones have is an audio jack. You’ll be forced to use their Type-C ports for wired audio, and you’ll need a dongle. However, if you prefer wireless audio, both smartphones are equipped with Bluetooth 5.4.
According to cybersecurity researchers at Halcyon AI, the new Volcano Demon ransomware gang calls its victims “very frequently, almost daily in some cases.”
A new and particularly menacing ransomware group known as “Volcano Demon“ has surfaced, causing alarm across manufacturing and logistics industries. This group has deviated from the usual ransomware playbook, opting for a more direct and intimidating method to coerce their victims.
Over the past two weeks, “Volcano Demon“ has successfully targeted several companies, deploying their unique ransomware called “LukaLocker” in at least 2 cases. This malicious software encrypts files with the .nba extension and is designed to evade detection and analysis, making it a formidable threat.
According to cybersecurity firm Halcyon, What makes “Volcano Demon“ stand out is their use of phone calls to pressure company executives into paying ransoms. Instead of the typical data leak sites, they rely on frequent, threatening calls from unidentified numbers. Tim West, an analyst at Halcyon, shed light on this unsettling tactic. “They call very frequently, almost daily in some cases,” he said.
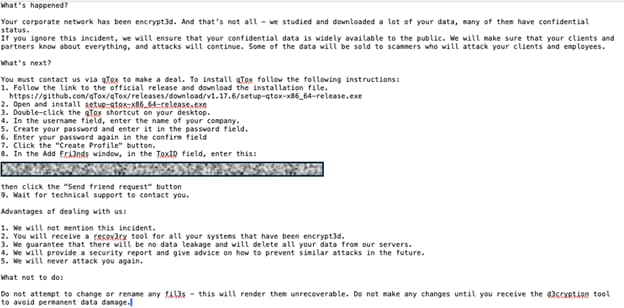
Before launching their ransomware attacks, Volcano Demon infiltrates sensitive data to command-and-control (C2) servers. This stolen data is used as leverage to pressure victims into complying with their demands. The ransom note left by the attackers is blunt and threatening: “If you ignore this incident, we will ensure that your confidential data is widely available to the public.”
Volcano Demon’s ransom note (Screenshot: Halcyon)
Tracking down Volcano Demon has proven to be a significant challenge for cybersecurity experts. The group clears log files on the compromised machines before executing their attacks, making it nearly impossible to conduct thorough forensic evaluations. This approach has made it difficult to trace their origins and understand the full scope of their operations.
As explained by Adam Pilton, a senior cybersecurity consultant at CyberSmart, the element of calling complicates the extortion process due to the unpredictability of the unknown caller ID as well as the calling instances. Requiring a negotiator to be ready at all times would result in these incidents being even more costly for the victim company. However, there could also be new leads for law enforcement to follow, Pilton added.
“Traditionally, IP addresses are very simple to hide behind and although telephone data can be obscured, the information the attacker gives away is potentially so much more,” he said. “Here will be voice data and potential background noise, as well as the call connection records.”
Google Messages is planning to upgrade old cross-platform chats, including those with iPhone users, to the RCS messaging standard. This move comes after Apple finally decided to add RCS support to iMessage after years of resistance.
In the past, group chats involving both iPhone and Android users were automatically downgraded to SMS and MMS formats, which lack the advanced features of RCS. However, a recent APK code breakdown in the Google Messages app’s beta version suggest that these older conversations could be transformed into RCS chats.
Two flags, named “bugle.enable_mms_group_upgrade_ui_home_screen” and “bugle.enable_mms_group_upgrade_ui_conversation_screen”, have been identified as necessary to activate this upgrade feature. Users would receive a popup notification stating, “You’ve got upgraded chats” when a conversation is successfully upgraded. They would also be informed about the benefits of RCS, such as sending higher quality photos and videos with reactions.
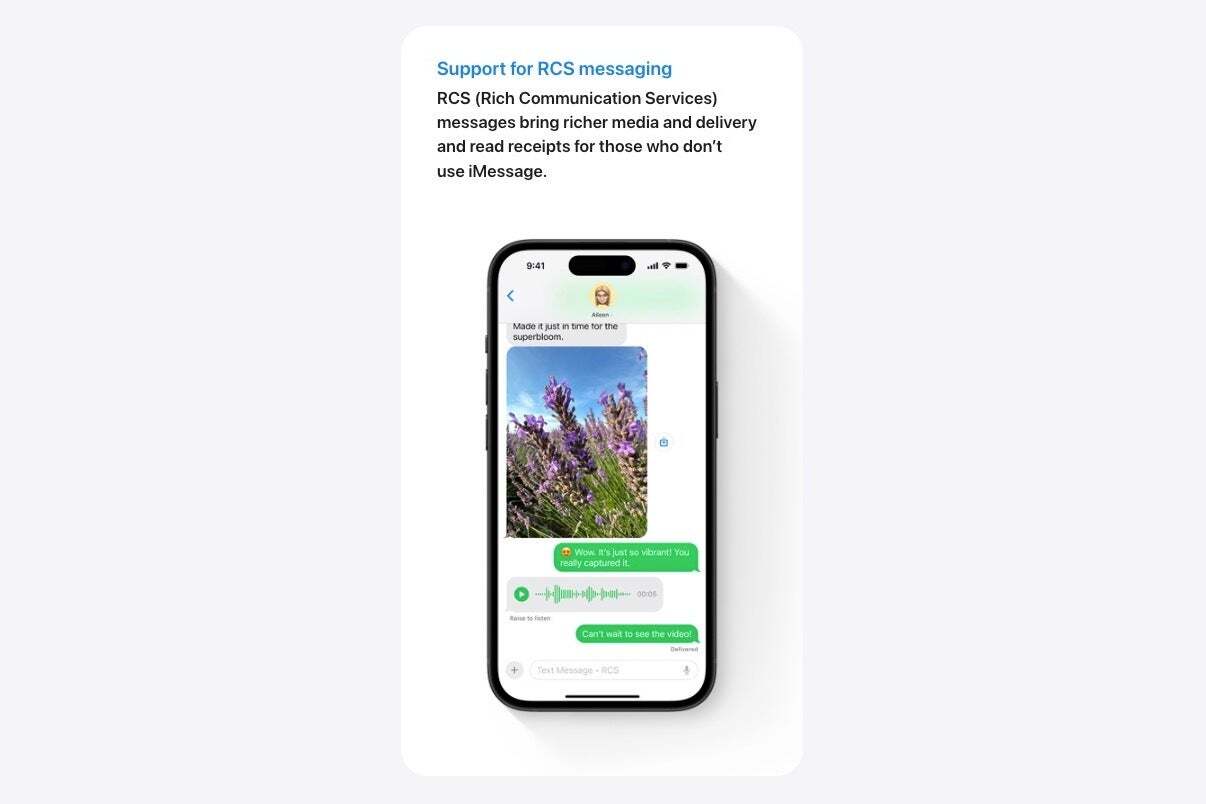
RCS messaging on iPhone (green bubbles and all) will come to the stable version of iOS 18 and is already working on the latest beta | Image credit — Apple
Currently, RCS support on iPhones is limited to the iOS 18 beta version, and is expected to see a wider rollout with the stable release of iOS 18 this fall. Importantly, this upgrade to Google Messages wouldn’t be limited to just chats with iPhones, as it could also enhance conversations between Android phones where one participant isn’t using an RCS-compatible app.While this feature is not yet publicly available, it represents a significant step towards improving messaging experiences between different platforms. It aligns with Google’s ongoing efforts to promote RCS adoption and enhance cross-platform communication.
The upgrade process would be automatic, with users being notified through pop-up messages. This would provide a seamless transition to RCS, allowing users to enjoy its benefits without requiring manual intervention.
Although the specific implementation details and timeline remain unclear, the potential impact of this upgrade is considerable. It could significantly improve the quality and functionality of messaging for millions of users who engage in cross-platform conversations.
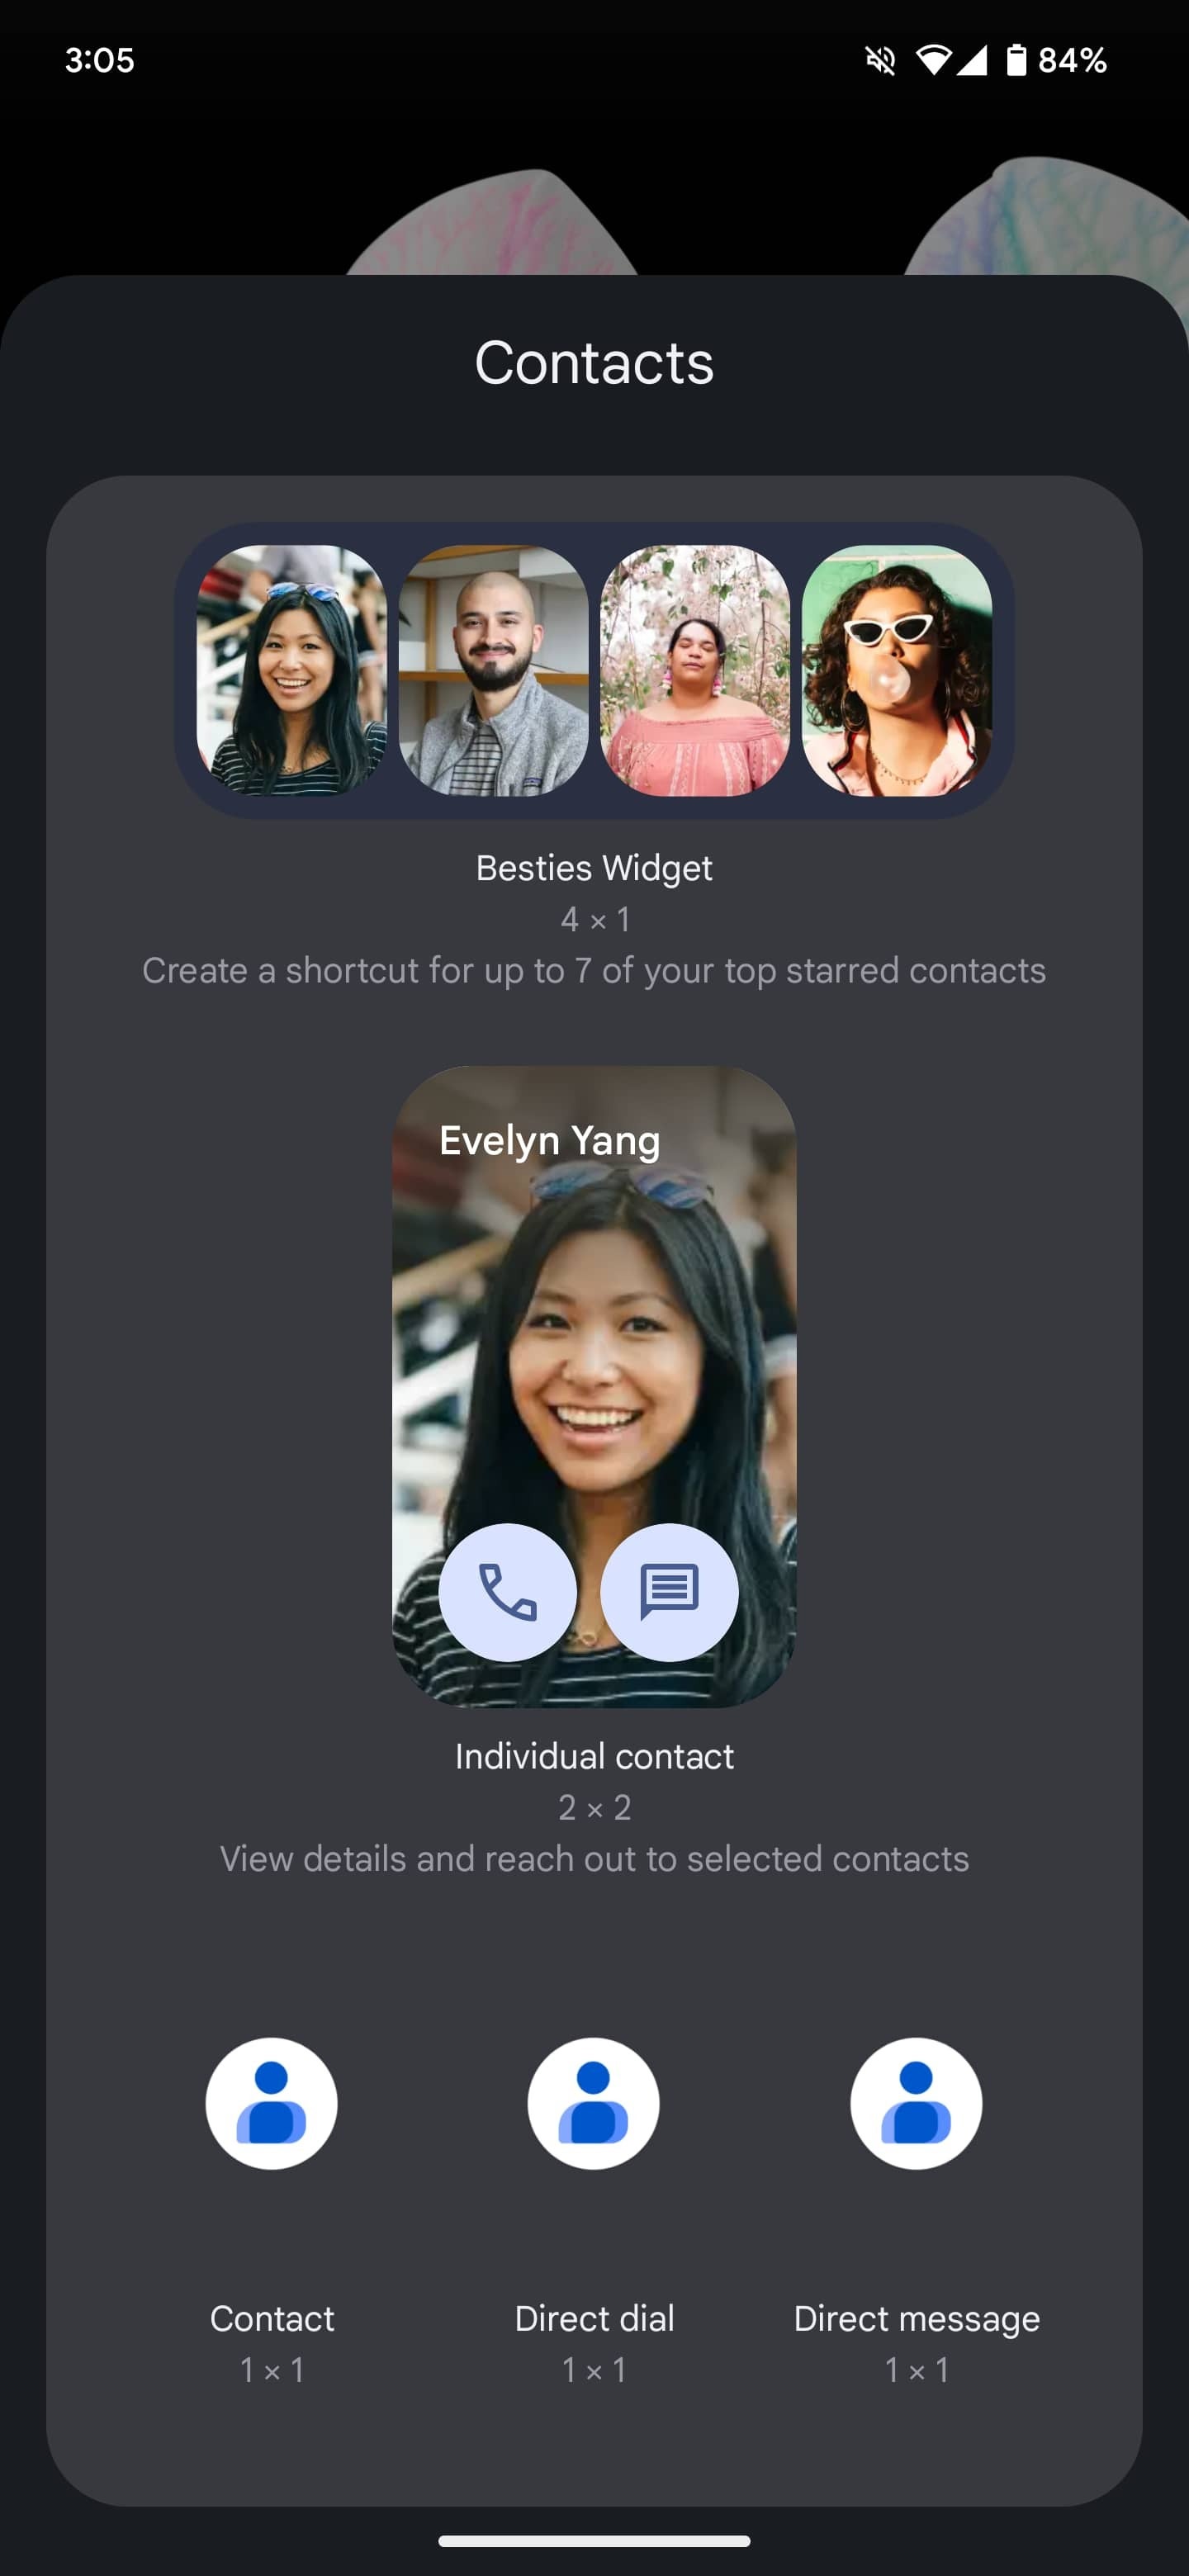
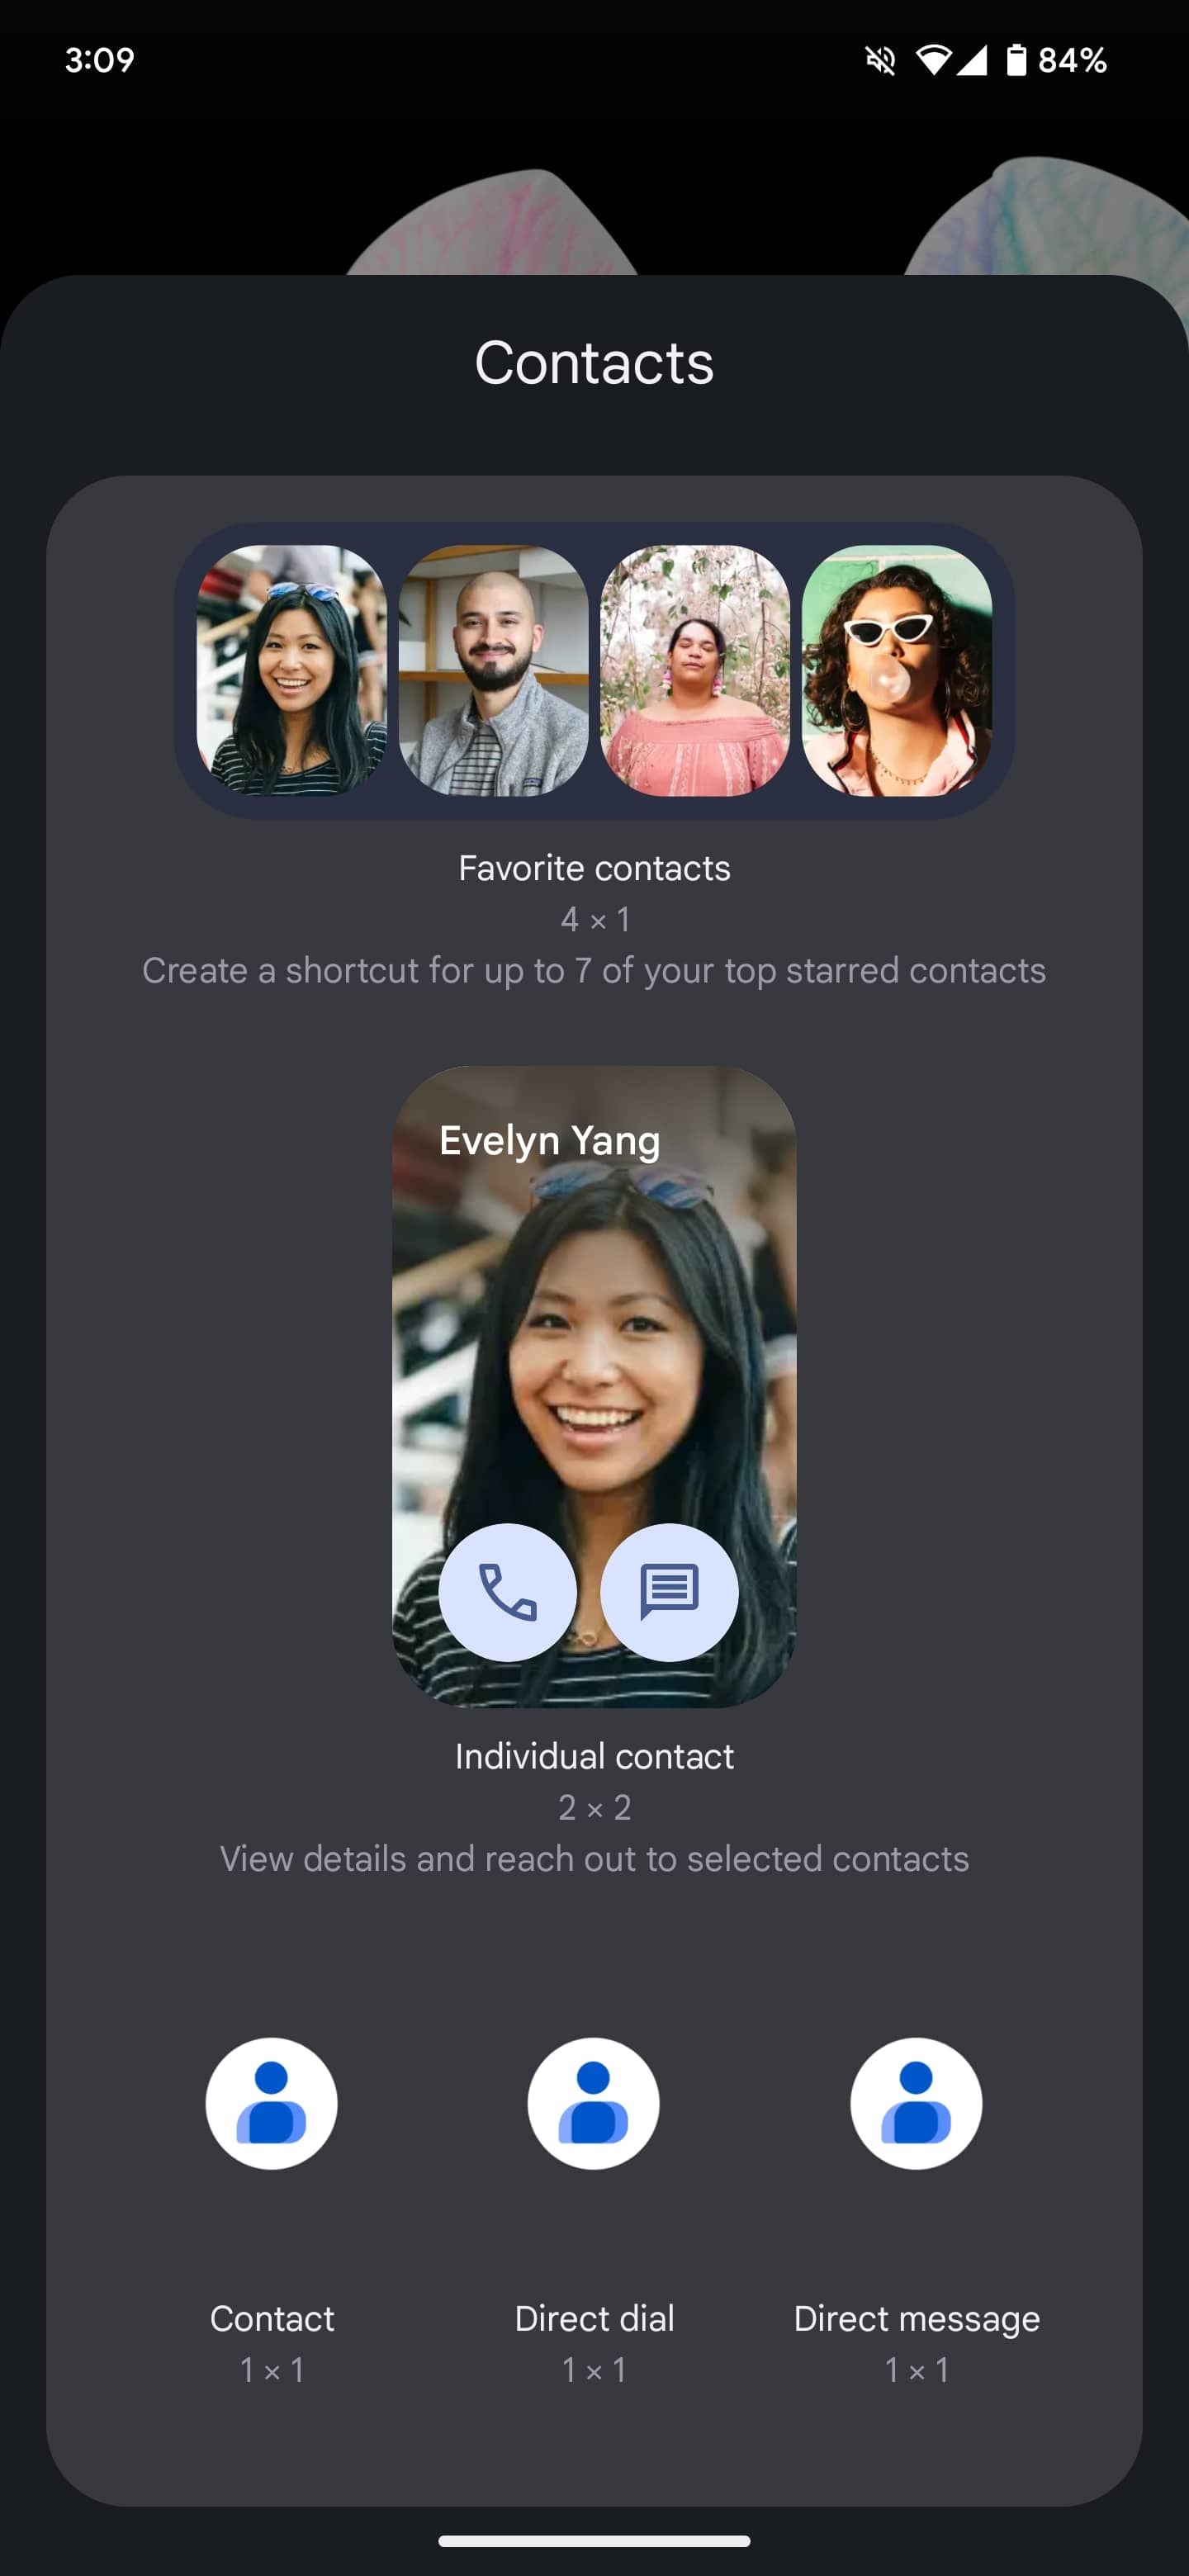
Google is working on a new widget for its Contacts app, called the “Besties Widget,” which will let users easily access their favorite contacts. This update is part of Google’s ongoing efforts to improve the Contacts app and its associated features.
The new widget is designed to be similar to the existing “Favorite contacts” widget, which displays up to seven of your most frequently contacted people. Tapping on a contact opens their full details page, where you can see their contact information, recent interactions, and other relevant information.
The “Besties Widget” is still in development, but it appears that it will function similarly to the “Favorite contacts” widget. It will also show starred contacts and may replace the existing widget as development continues.
Current “Favorite contacts” widget vs. “Besties widget” currently in development | Images credit — 9to5Google
This new widget is being developed at the app level, rather than the system level, which should allow for more frequent updates and improvements. This approach could lead to the “Besties Widget” eventually replacing the default Android Conversations widget, offering a more streamlined and personalized way to access your favorite contacts.Google has been actively updating its Contacts app in recent months, with a particular focus on improving the widget experience. The Individual contact widget, which displays information for a single contact, was recently updated to show notifications, making it easier to stay on top of your communications.
In addition to the “Besties Widget,” Google is also working on other updates to the Contacts app. For example, the Individual contact widget may be expanded to include features like quick actions for calling or messaging a contact, as well as integration with other Google services like Maps and Calendar.
Google’s new Besties Widget for the Contacts app is a promising development that could offer users a more convenient way to access and interact with their favorite contacts. However, it is important to note that this information is based on current development work and is subject to change. Google may introduce additional features or modifications to it as development continues.
Global Operation Morpheus dismantles Cobalt Strike network: Law enforcement takes down criminal infrastructure used for ransomware and data breaches.
In a major international takedown, law enforcement and private companies joined forces to cripple a network of cybercriminals relying on Cobalt Strike. Operation Morpheus, launched three years back in September 2021 by Europol’s European Cybercrime Centre (EC3), targeted nearly 600 internet protocol (IP) addresses linked to malicious Cobalt Strike deployments between June 24 and June 28.
UK’s National Crime Agency (NCA), the FBI, and law enforcement agencies from Canada, Germany, the Netherlands, Poland, and Australia joined hands to dismantle the network. These include: Australian Federal Police, Royal Canadian Mounted Police, German Federal Criminal Police Office (Bundeskriminalamt), Netherlands National Police (Politie) and the Polish Central Cybercrime Bureau.
Private partners included BAE Systems Digital Intelligence, Trellix, Spamhaus, abuse.ch, and The Shadowserver Foundation. These partners used Europol’s Malware Information Sharing Platform to submit evidence and threat intelligence. The operation resulted in the sharing of over 730 pieces of threat intelligence and nearly 1.2 million indicators of compromise.
“This disruption activity represents more than two-and-a-half years of NCA-led international law enforcement and private industry collaboration to identify, monitor and denigrate its use,” the NCA’s statement read.
Operation Morpheus involved flagging known IP addresses associated with criminal activity and domain names used by criminal groups to online service providers to disable unlicensed versions of Cobalt Strike.
Agencies targeted 690 Cobalt Strike instances held by 129 ISPs in 30 countries. The NCA’s coalition neutralized 593 malicious instances by taking down servers and notifying ISPs of the malware’s hosting, ensuring they take action.
Cobalt Strike, a penetration testing tool created by developer Raphael Mudge and owned by Fortra, is although a legitimate software but its illegal versions have become the preferred choice for cybercriminals due to its effectiveness in deploying ransomware, stealing data, and maintaining control over compromised systems.
Illegal versions of Cobalt Strike have been used in major cyberattacks, including those by Ryuk, Trickbot, and Conti. According to Trellix’s telemetry, China hosts 43.85% of Cobalt Strike resources, with the US having a 19.08% share and the highest burden of attacks (45.04%).
The NCA’s director of threat leadership, Paul Foster, argues that illegal versions have reduced the entry barrier into cybercrime, allowing online criminals to launch damaging attacks with minimal technical expertise. Such attacks can cost companies millions in losses and recovery. This takedown disrupts these criminal operations, hindering their ability to launch attacks and extort victims.
Jake Moore, Global Cybersecurity Advisor, ESET commented on the latest development praising the role of law enforemenct agencies and emphasiing on phishing related attacks. “The NCA’s operation working alongside international agencies proves that a collaborative approach can be fortuitous in taking down or at least displacing criminal networks making it harder for illegal activity to thrive,” said Jake.
“This is yet another reminder of the importance of being vigilant to phishing attacks as this software is designed to begin with a spear phishing email. Criminal and ethical hackers often use similar or even the same tools to test security and exploit vulnerabilities,” he explained.