ShinyHunters Leak 33M Twilio Authy Phone Numbers, Neiman Marcus and Truist Bank Data

0
[ad_1]

ShinyHunters hackers have taken responsibility for three high-profile data breaches involving Neiman Marcus, Truist Bank, and Twilio Authy, compromising personal details of millions of users and tens of thousands of employees.

The infamous ShinyHunters hacking group, known for their recent Ticketmaster data breach, has struck again with a series of new attacks. This time, they have targeted Neiman Marcus, a renowned American luxury department store chain based in Dallas, Texas; Truist Financial Corporation, a major bank holding company headquartered in Charlotte, North Carolina; and extracted 33 million phone numbers from Twilio’s Authy service.

Neiman Marcus Data Breach

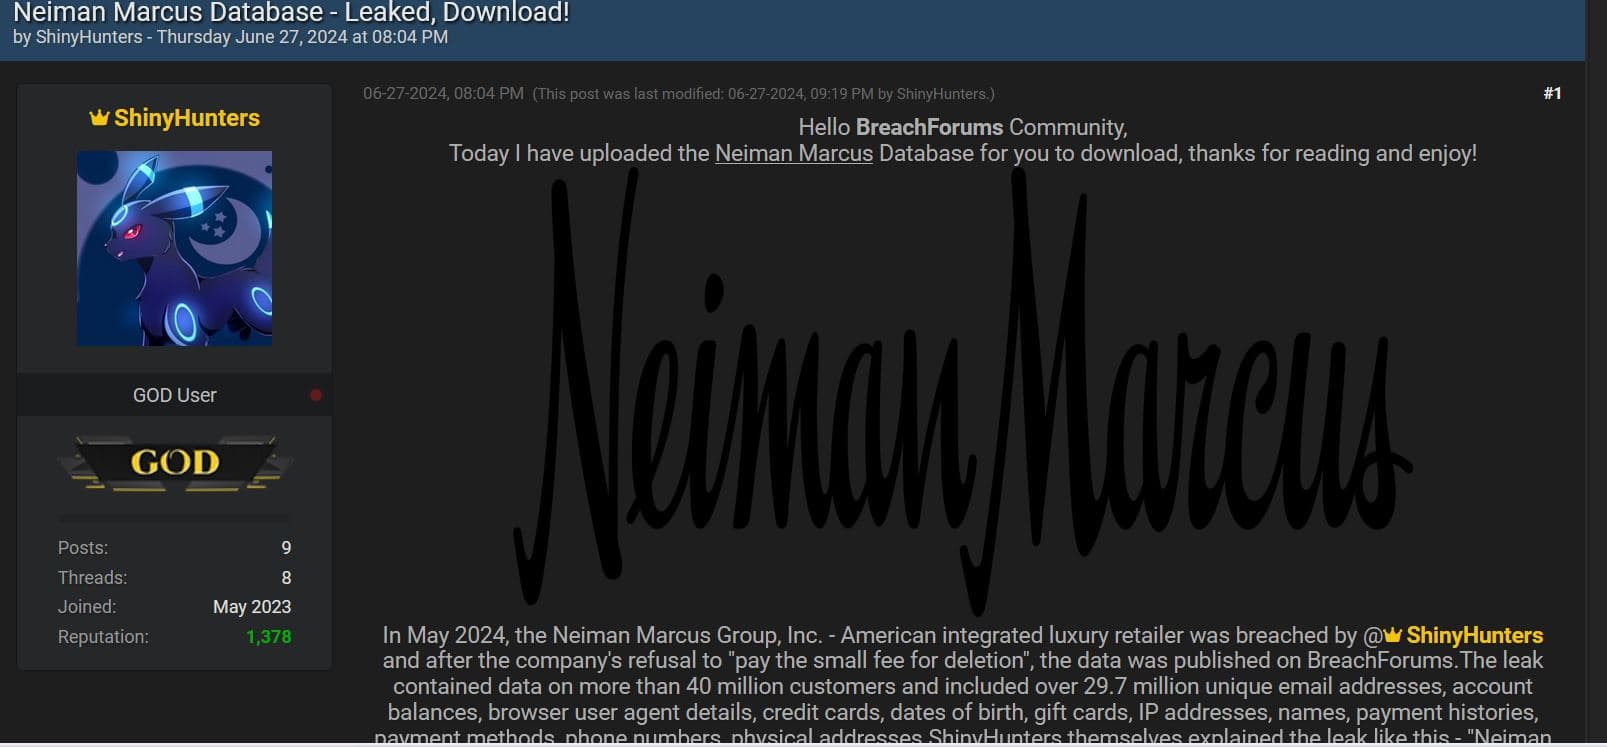
On Thursday, June 27, 2024, ShinyHunters leaked the Neiman Marcus database on the Breach Forums cybercrime platform. In their post, the hackers criticized Neiman Marcus for not paying a “small fee for deletion” of the database, referencing the common ransom tactic of “pay to have the data deleted or don’t pay and face a leak.

“Neiman Marcus didn’t pay the small fee for deletion, hiding behind legal terms they invented; so we decided Neiman Marcus can pay $200 million in fines instead, we are giving for free the hottest base (of the hour).”

ShinyHunters

As seen by Hackread.com, the leaked Neiman Marcus database contains personal data of over 40 million customers, including 29.7 million unique email addresses. The compromised data includes the following information:

  • Full names
  • IP addresses
  • Dates of birth
  • phone numbers
  • Payment histories
  • Account balances
  • Payment card data
  • payment methods
  • physical addresses
  • Browser user agent details
  • Gift cards numbers (without PINs)

and a lot more…

In a data breach notification submitted to the Office of the Attorney General of the state of Maine, Neiman Marcus acknowledged the incident and held Snowflake, a third-party cloud computing-based data company, responsible. According to the notification, the data breach occurred between April and May 2024, and the affected customers were notified on June 24, 2024.
ShinyHunters Leak 33M Twilio Authy Phone Numbers, Neiman Marcus and Truist Bank Data
ShinyHunters on Breach Forums announcing and leaking Neiman Marcus database (Screenshot: Hackread.com)

Truist Bank Employee Database

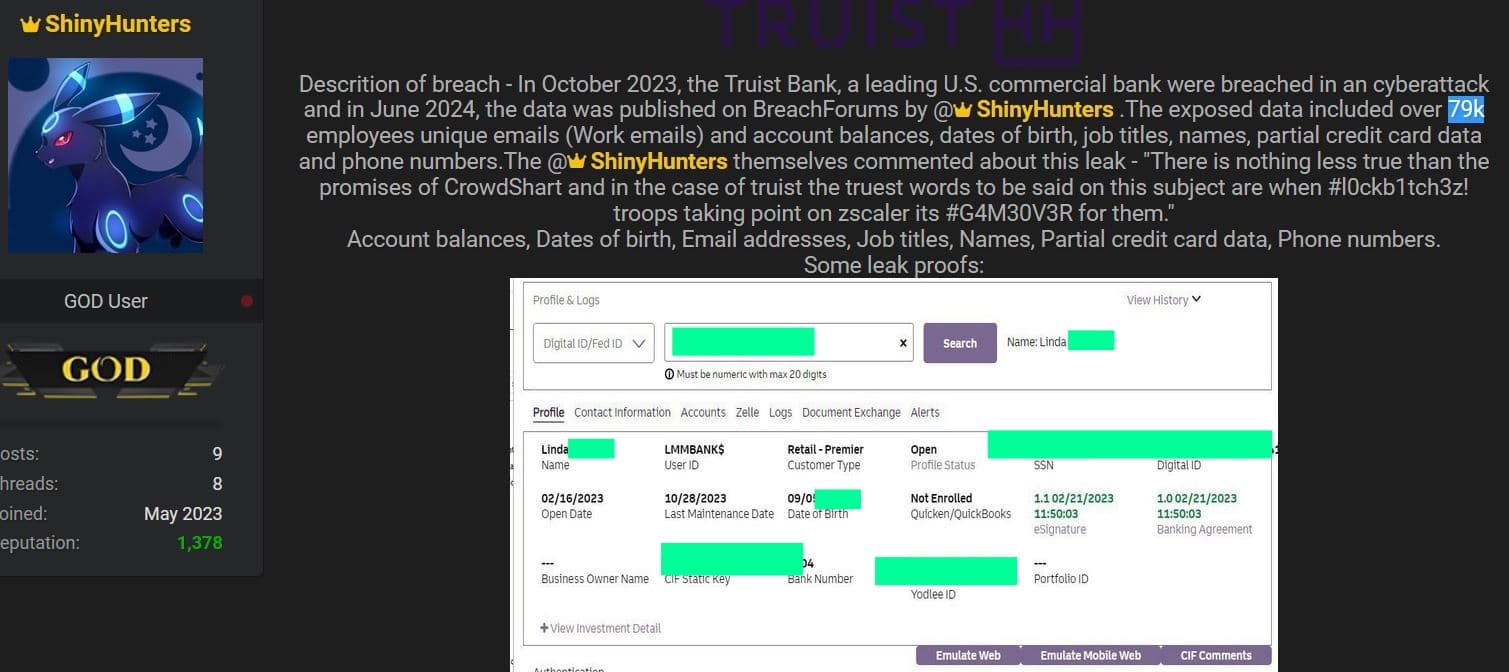
On Thursday, June 27, 2024, ShinyHunters leaked another database on Breach Forums, this time belonging to Truist Bank or Truist Financial Corporation, an American bank holding company headquartered in Charlotte, North Carolina.

It is important to note that the database contains only employee information; no customers were impacted. According to the hacker group, the data breach occurred in October 2023 and the database included 79,000 unique email addresses of the bank’s employees. Other data included in the leak consists of the following:

  • Job titles
  • Full names
  • Dates of birth
  • phone numbers
  • Account balances
  • Partial credit card data

And more…

Like Neiman Marcus, Truist Bank also acknowledged the breach. The company released the following statement:

“In October 2023, we experienced a cybersecurity incident that was quickly contained…In partnership with outside security consultants, we conducted a thorough investigation, took additional measures to secure our systems, and notified a small number of clients last Fall.”

However, this is not the first time that Truist Bank suffered a data breach. In December 2021, the company confmrimed a security incident in which hackers managed to steal customer names and other personal identifier in combination including Social Security Number (SSNs).
ShinyHunters Leak 33M Twilio Authy Phone Numbers, Neiman Marcus and Truist Bank Data
ShinyHunters on Breach Forums announcing and leaking Truist Bank database (Screenshot: Hackread.com)

Twilio Authy Phone Numbers

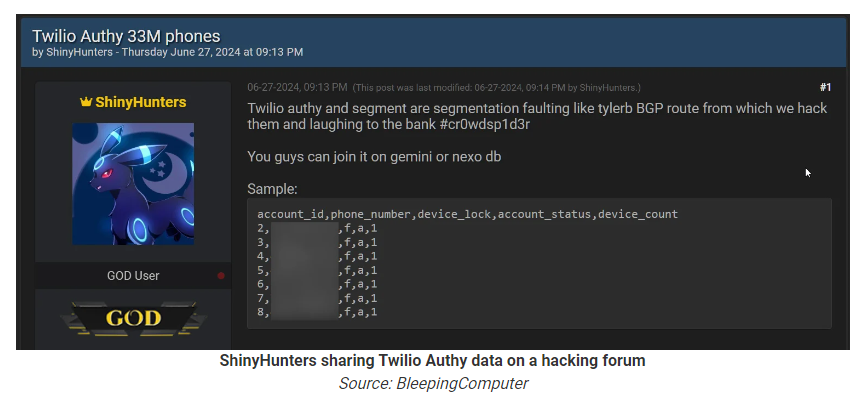
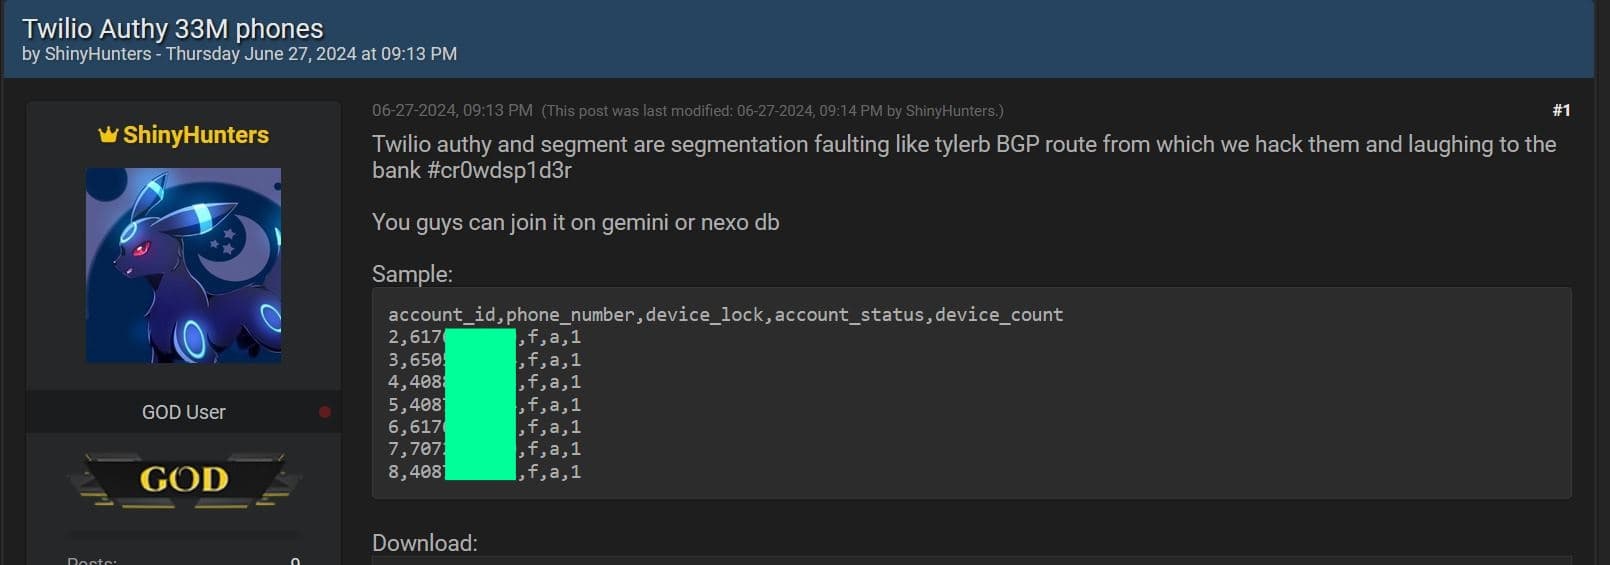
On Thursday, June 27, 2024, ShinyHunters leaked yet another set of data. This time, it involved 33 million phone numbers belonging to Twilio Authy, a two-factor authentication (2FA) service provided through a free mobile app.
ShinyHunters Leak 33M Twilio Authy Phone Numbers, Neiman Marcus and Truist Bank Data
ShinyHunters on Breach Forums announcing and leaking Twilio Authy phone numbers (Screenshot: Hackread.com)

In response to the group’s claims, on July 1, 2024, Twilio acknowledged that threat actors were able to access data associated with Authy accounts, including phone numbers, due to an unauthenticated endpoint. However, the company stated that there is no evidence the hackers obtained access to Twilio’s systems or other sensitive data.

Twilio is urging users to update their Twilio Authy app on iOS and Android to the latest version. The American cloud communications giant is also advising users to be vigilant for smishing (SMS phishing) and phishing attacks.

Nevertheless, all three data leaks put unsuspecting users and employees at risk of various cybersecurity and physical threats. Users and employees of Twilio, Neiman Marcus, and Truist Bank should change their passwords on all services, enable 2FA through another service, and remain vigilant for malicious emails and social media-related scams targeting them.

  1. BreachForums Returns Under ShinyHunters Hackers
  2. Alleged ShinyHunters Hacker Group Member Arrested
  3. ShinyHunters Hacks Santander Bank: 30M User Data for Sale
  4. ShinyHunters leak database of Indian wedding site WedMeGood
  5. AT&T breach ShinyHunters selling AT&T database with 70M SSN

[ad_2]
Source link

Authy phone numbers accessed by cybercriminals, warns Twilio

0
[ad_1]

Twilio has warned users of the Authy multi-factor authentication (MFA) app about an incident in which cybercriminals may have obtained their phone numbers.

Twilio said the cybercriminals abused an unsecured Application Programming Interface (API) endpoint to verify the phone numbers of millions of Authy multi-factor authentication users.

Authy is an app that you install on your device which then produces a MFA code for you when logging into services.

The cybercriminals were able test the validity of an enormous list of phone numbers against the unsecured API endpoint. If the number was valid, the endpoint would return information about the associated accounts registered with Authy.

Twilio says it has seen no evidence of the attackers gaining access to Twilio’s systems or other sensitive data, but as a precaution it is asking all Authy users to update to the latest Android and iOS apps.

BleepingComputer notes that a threat actor named ShinyHunters leaked a CSV text file containing what they claim are 33 million phone numbers registered with the Authy service.

“In late June, a threat actor named ShinyHunters leaked a CSV text file containing what they claim are 33 million phone numbers registered with the Authy service.”

ShinyHunters post on a breach forum

In that post, ShinyHunters suggests that buyers combine the data set with those leaked in the Gemini or Nexo data breaches. Nexo is a crypto platform where users can buy, exchange, and store Bitcoin and other cryptocurrencies. Gemini is another cryptocurrency exchange which has suffered several breaches in the past years.

With matches between the data sets, a cybercriminal could engage in SIM-swapping or phishing attacks to steal the target’s cryptocurrencies.

If you are an Authy user we advise you to update at your earliest convenience and keep an eye out for any potential phishing messages.

How to avoid being phished

Remember that phishing messages will try to rush you into making a decision by setting an ultimatum or otherwise imposing a sense of urgency. Don’t let them rush you into an expensive mistake.

There are a few tell-tale signs for phishing mails:

  1. It asks you to update/fill in personal information.
  2. The URL on the email and the URL that displays when you hover over the link are different from one another.
  3. The “From” address is not the legitimate address, although it may be a close imitation.
  4. The formatting and design are different from what you usually receive from the impersonated brand.
  5. The email contains an attachment you weren’t expecting.

However, with the advancement of AI, phishing emails are getting more sophisticated. So if you have even a tiny amount of suspicion that something is phishy, don’t hesitate to confirm the source of the email through another method. The chances of losing your money are much smaller after a quick call asking “Did you send this?”


We don’t just report on threats – we help safeguard your entire digital identity

Cybersecurity risks should never spread beyond a headline. Protect your—and your family’s—personal information by using identity protection.


[ad_2]
Source link

Google Messages bug is annoying some Pixel phone users

0
[ad_1]

A new Google Messages bug has been spotted, though it seems to be affecting only some Pixel phone users. To be more specific, I’m talking about a bug with Google Messages notifications, which seem to be disappearing.

A missing notifications bug hit Google Messages, and it’s affecting Pixel users

Needless to say, this can be quite annoying. Missing notifications is far from ideal. I know it would create a considerable problem for me, and I believe many of you would be quite irritated by this.

So, what exactly is happening? Well, those notifications seem to disappear almost instantly for some users. There is not a workaround for this as of yet, it seems, let alone a fix.

Google Messages app is no stranger to bugs. Many of you will remember the one from earlier this year that prevented people from replying to messages from notifications. Then again the one that caused GIFs sent from iPhones to appear distorted.

This is arguably the worst Google Messages bug we’ve seen this year, at least

This one with disappearing notifications is the worst we’ve seen yet, or at least in a while. The good news is that you can still see the message you’ve recieved in-app. You have no way of knowing it arrived, though, as the notification appears almost instantly.

We’ve only seen reports of this bug affecting Pixel users, so at least it has not spread to other phones. The first instance of this bug was spotted 19 days ago, on Reddit.

One of the affected users, teslamash, said the following: “when a new text arrives in Messages, the notification slides down from the top of the screen, but disappears in about a second and doesn’t appear in the status bar or pull down menu, almost as if it’s been dismissed by being seen in the app itself”.

The Pixel 7, Pixel 6a, Pixel 7 Pro, and Pixel 8 Pro users all reported the bug, from what we’ve seen. So it doesn’t really matter what Pixel phone you’re using, it seems, it could end up affecting you.


[ad_2]
Source link

Samsung’s profits estimated to explode in Q2 2024 thanks to AI

0
[ad_1]

After a staggering 85% drop in annual profit in 2023, Samsung began 2024 with a bang. Its Q1 profit soared an eye-popping 933% to reach KRW 6.61 trillion (roughly $4.8 billion). The company may top that financial performance in the second quarter. Industry analysts estimate it to take home over KRW 8.5 trillion in Q2 (~$6.1 billion), with some estimating an operating profit of KRW 8.8 trillion (~$6.4 billion). That’s a 13-fold increase in profit over Q2 2023, all thanks to AI.

The AI boom helped Samsung increase its profit in Q2 2024

Samsung is the world’s largest maker of smartphones, TVs, and memory chips. The latter product category has been its cash cow for years. A sudden drop in memory chip demand and prices in 2023 hurt the company badly. Its semiconductor division posted operating losses for the first time in 14 years, while its overall earnings hit a 14-year low. Thankfully, this slowdown didn’t last long as demand and prices recovered in 2024, benefitting Samsung big time.

A weak post-pandemic demand for electronics caused last year’s price drop. However, with the industry rapidly adopting AI, memory chip demand has surged this year. High-end DRAM chips such as high bandwidth memory (HBM) solutions and other chips used in AI data centers are in high demand. Market estimates say DRAM chip prices increased 13% to 18% in Q2 2024, while NAND Flash storage chip prices increased 15% to 20%.

Samsung is reaping the benefits of this price rise. Data solution provider FactSet recently compiled consensus estimates from 33 analysts forecasting an operating profit of KRW 8.547 trillion for the quarter ended in June. A separate LSEG SmartEstimate average from 27 analysts says Samsung’s second-quarter profit may go up to KRW 8.8 trillion. These figures are a massive jump (13x) over the Korean firm’s Q2 2023 profit of KRW 0.67 trillion.

The semiconductor division, riding on the back of memory chips, is the driving force behind Samsung’s profit increase in Q2 2024. Citigroup analysts expect the business unit to post an operating profit of KRW 5.1 trillion this past quarter That’s nearly 60% of the company’s total profit for the period. What a turnaround this is proving to be, all thanks to the AI boom. Samsung is currently seeking approval for its advanced HBM products from Nvidia.

The Korean firm may soon share its earnings estimate

Samsung usually posts its quarterly earnings estimates about a week after the quarter ends. So, its Q2 2023 earnings estimate may come soon. A more detailed report will follow at the end of the month. The Korean firm would be happy with the rise in chip prices but would be looking to increase profit from other business divisions. It launches the Galaxy Z Fold 6 and Galaxy Z Flip 6 foldables on July 10. The event will also bring new watches, earbuds, and a smart ring.


[ad_2]
Source link

Galaxy Z Fold 6 product page leaked, reveals everything before Unpacked

0
[ad_1]

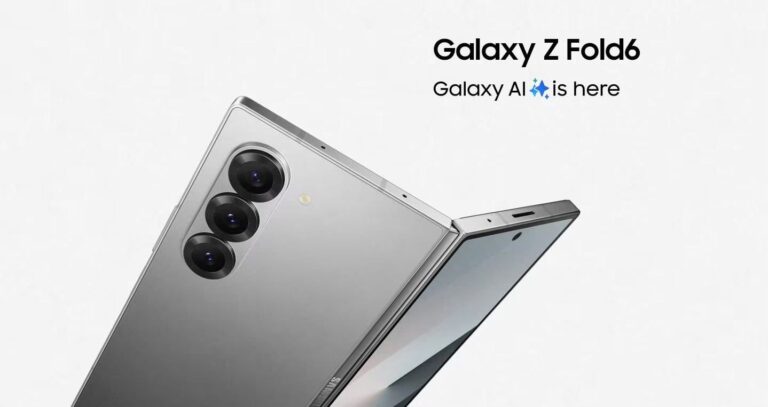
Alongside the Galaxy Z Flip 6, leakster Evan Blass shared the official product page for Samsung’s Galaxy Z Fold 6. It contains all the key features of the upcoming foldable along with detailed specifications. The Korean firm will launch both devices at its next Unpacked on July 10.

Samsung’s first dust and water-resistant foldable

Samsung was the first company to make a water-resistant foldable. It achieved this feat with its third-gen models in 2021. The Galaxy Z Flip 3 and Galaxy Z Fold 3 featured an IPX8 rating. The company didn’t improve things with the next two generations. But this year, it has made the Galaxy Z Flip 6 and Galaxy Z Fold 6 dust-resistant thanks to an IP48 rating. Not as foolproof as the IP68 rating on other Galaxy flagships, but certainly a big durability upgrade.

Unfortunately, the rumors of a titanium frame don’t seem to have materialized. This leaked product page from Evleaks says the Galaxy Z Fold 6 has an Armor Aluminum frame with Gorilla Glass Victus 2 display protection. That’s unchanged from last year. There have been strong rumors of Samsung upgrading the new foldable to a titanium frame like the Galaxy S24 Ultra. Unless the latest leak is inaccurate, we are in for an anti-climactic end in this regard.

The other big change that the Galaxy Z Fold 6 brings to the table is in its design. The new Fold has a bixier body similar to the Galaxy S24 Ultra. Samsung has slightly shortened the device (by 1.4mm) and made it wider (by 1mm) than the Fold 5. It is also significantly thinner. The upcoming foldable is just 5.6mm thick when unfolded and 12.1mm when folded. The 2023 model was 6.1mm and 13.4mm, respectively. It weighs 239 grams, down from 253 grams.

Samsung Galaxy Z Fold 6 major leak 1

Despite a slimmer and lighter build, the Galaxy Z Fold 6 keeps a 4,400mAh battery. Its charging specs aren’t mentioned but earlier leaks said the new Fold will not charge faster than Fold 5, i.e., at 25W speeds. It will support wireless and reverse wireless charging. Note that the Galaxy Z Flip 6 is getting slightly thinner and packing a bigger battery (4,000mAh instead of 3,700mAh). There is no titanium on Samsung’s new Flip model either.

The Galaxy Z Fold 6 has a bigger and wider cover display

Thanks to a wider design and slimmer bezels, the Galaxy Z Fold 6’s cover display now measures 6.3 inches diagonally, marginally larger than Fold 5’s 6.2-inch panel. It is wider than before, closer to a regular smartphone screen. The Dynamic AMOLED 2X panel on the outside should boast a 120Hz refresh rate like the main display. The inner folding screen still measures 7.6 inches, though. It supports Samsung’s S Pen and is incredibly bright at 2,600 nits.

Samsung Galaxy Z Fold 6 major leak 2

Leaks have previously hinted at new AI-powered S Pen features but we don’t see any on this leaked spec sheet. However, Samsung touts enhanced productivity with Galaxy AI features such as Note Assist and Interpreter. The Galaxy Z Fold 6’s large screen makes it a handy tool for live translation and transcription of spoken languages. The Flip model can show translated text on its cover screen. It’s unclear if the Fold has the same feature.

Samsung didn’t change the camera hardware on the new Fold

Unlike the Galaxy Z Flip 6, which is getting a new 50MP primary camera, the Galaxy Z Fold 6 comes with the same camera hardware. We have a triple camera setup on the back featuring a 50MP main shooter, a 12MP ultrawide lens, and a 10MP 3x zoom camera. On the front, there is a 10MP selfie camera, while another selfie camera sits on the inside. It’s a 4MP under-display unit that exists pretty much only for video calls. You won’t want to capture selfies with it.

Samsung says the 50MP primary camera can capture lossless photos at 2x zoom. The Galaxy Z Fold 6 can also record 8K videos, while the Flip is limited to 4K videos. Both foldables are powered by Qualcomm’s Snapdragon 8 Gen 3 (For Galaxy) chipset. This Samsung-exclusive SoC also powered the Galaxy S24 Ultra. The new Fold has 12GB RAM as standard and comes in 256GB, 512GB, and 1TB storage variants. The Flip is also getting a 12GB RAM variant this year.

The rest of the setup remains unchanged, meaning that the big foldable misses out on Wi-Fi 7. Like last year, Samsung is limiting it to Wi-Fi 6E. The Galaxy Z Fold 6 boasts stereo speakers, Samsung DeX support, NFC, UWB (Ultra Wideband) Bluetooth v5.3, and USB-C 3.2 Gen 1. It has two SIM slots and also supports eSIM, though you cannot use more than two SIMs at once. Stay tuned for the official announcement next Wednesday, July 10.


[ad_2]
Source link

Xiaomi 15 Pro to get considerable battery & charging boost

0
[ad_1]

The Xiaomi 15 Pro is getting a considerable battery capacity and charging speed boost, it would seem. Well, at least based on the information shared by Digital Chat Station, one of the industry’s most prolific tipsters.

The Xiaomi 15 Pro to feature a considerably larger battery and faster wireless charging

He went to Weibo to report that the Xiaomi 15 Pro will include a 5,400mAh battery. That’s a huge improvement over the 4,880mAh battery that was included in the Xiaomi 14 Pro.

The Xiaomi 14 Pro offers 120W wired and 50W wireless charging. That in itself is great, needless to say. However, the Xiaomi 15 Pro will improve things in that area too. It is said to offer 100W wired and 100W wireless charging.

While the wired charging will be a tiny bit slower, wireless charging will match it, and be a lot faster than on the Xiaomi 14 Pro. Many would take 100W + 100W charging for wired and wireless charging instead of a 120W + 50W combo, that’s for sure.

The tipster did note that Xiaomi is currently testing 120W + 100W prototype, but that it will likely end up settling for 100W + 100W combo due to thermal concerns.

It remains to be seen if the charger will be included in the box, though

It remains to be seen if Xiaomi will include a charger with the phone, though. In some markets, the all-new Redmi 13 handset ships without a charger. That’s not Xiaomi’s usual practice, as it always includes chargers, so… we’re wondering if things are changing.

What Digital Chat Station also said is that Xiaomi opted for a 5,400mAh battery to keep the phone slimmer and lighter. We don’t see how it will be slimmer and lighter than its predecessor, but if that’s true, it’s an incredible feat. That will be a silicon-carbon battery, in case that wasn’t clear.

We already knew that the Xiaomi 15 Pro will include three cameras on the back, three 50-megapixel cameras. Xiaomi is allegedly planning to ditch variable aperture, unfortunately.

This handset will launch later this year, alongside the regular Xiaomi 15 model. The Snapdragon 8 Gen 4 SoC is expected to fuel both of those phones.


[ad_2]
Source link

Over 380,000+ Hosts Embedding Polyfill JS to Malicious Domain

0
[ad_1]

Over 380,000 web hosts have been found embedding a compromised Polyfill.io JavaScript script, linking to a malicious domain.

This supply chain attack has sent shockwaves through the web development community, highlighting the vulnerabilities inherent in widely used open-source libraries.

Polyfill.js, a popular tool designed to provide modern functionalities for older web browsers, was the target of this sophisticated attack.

In February 2024, the domain and GitHub account for Polyfill.io were acquired by Funnull, a Chinese CDN company.

This acquisition raised immediate concerns about the service’s legitimacy.

These concerns were validated when malware injected through cdn.polyfill.io began redirecting users to malicious sites.

High-profile platforms such as JSTOR, Intuit, and the World Economic Forum were among the affected, showcasing the widespread impact of this breach.

"Is Your System Under Attack? Try Cynet XDR: Automated Detection & Response for Endpoints, Networks, & Users!"- Free Demo

The Scale of the Attack

According to Censys, a cybersecurity firm, 384,773 hosts were found to include references to “https://cdn.polyfill[.]io” or “https://cdn.polyfill[.]com” in their HTTP responses.

A significant concentration of these hosts, approximately 237,700, is located within the Hetzner network in Germany.

This is not surprising, given Hetzner’s popularity among web developers.

Further analysis revealed that major companies such as Warner Bros, Hulu, Mercedes-Benz, and Pearson had large numbers of hosts referencing the malicious Polyfill endpoint.

Interestingly, the most common hostname associated with these hosts was ns-static-assets.s3.amazonaws.com, indicating widespread usage among Amazon S3 static website hosting users.

The presence of government domains like “www.feedthefuture.gov” among the affected hosts underscores the attack’s reach across various sectors.

Censys observed 182 affected hosts displaying a “.gov” domain.

Industry Response and Mitigation Efforts

The attack has prompted swift responses from multiple companies.

Cloudflare and Fastly have offered alternative, secure endpoints for users to mitigate the threat while preventing websites from breaking.

Google has blocked ads for e-commerce sites using Polyfill.io, and the website blocker uBlock Origin has added the domain to its filter list.

Andrew Betts, the original creator of Polyfill.io, has urged website owners to immediately remove the library, emphasizing that it is no longer necessary for modern browsers.

Namecheap, the domain registrar for Polyfill.io, took down the malicious domain, mitigating the immediate threat.

However, the incident is a stark reminder of the growing threat of supply chain attacks on open-source projects.

The interconnected dependencies within the open-source ecosystem mean a single compromised package can have far-reaching security implications.

Investigating the Malicious Domain

Further investigation into the malicious Polyfill[.]io domain revealed additional concerning details.

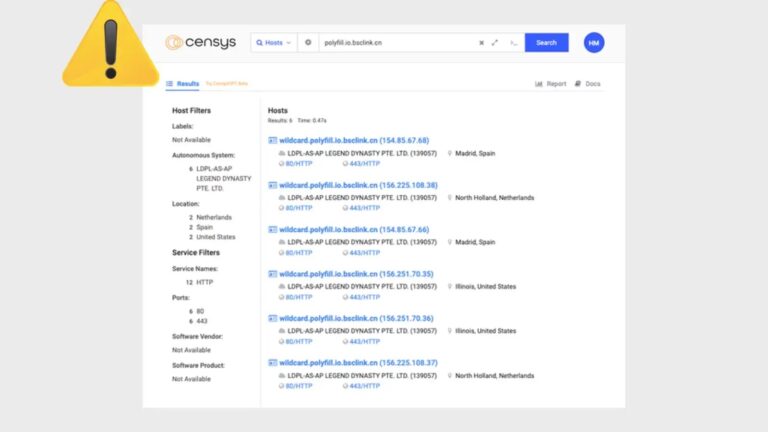
Historical DNS records linked the domain to several other suspicious domains, including 5f52353c.u.fn03.vip, cdn.polyfill.io.bsclink.cn, and wildcard.polyfill.io.bsclink.cn.

LEGEND DYNASTY PTE hosted these domains. LTD., a company based in Singapore.

Interestingly, the maintainers of the Polyfill GitHub repository had leaked their Cloudflare API secrets within the repo.

This leak revealed four additional active domains linked to the same account: bootcdn[.]net, bootcss[.]com, staticfile[.]net, and staticfile[.]org.

One of these domains, bootcss[.]com, has been observed engaging in similar malicious activities since June 2023.

Analyzing the malicious Polyfill JavaScript code revealed a function named check_tiaozhuan(), which checks if the user uses a mobile device.

If so, it sets a value based on various conditions. Then it calls another function that loads a JavaScript file from a specified URL, potentially redirecting the user’s browser to another page.

This tactic closely mirrors the methods used in the Polyfill.io attack.

The Polyfill.io supply chain attack is a stark reminder of the vulnerabilities inherent in the web development ecosystem.

As developers rely on a diverse technology stack of open-source packages, the security of these dependencies becomes crucial.

The incident underscores the need for vigilance and robust security measures to protect against such sophisticated attacks.

As the web development community grapples with the fallout from this breach, the lessons learned will clearly shape future approaches to securing open-source projects.

The industry must continue collaborating and innovating to safeguard the digital infrastructure that underpins our modern world.

Are you from SOC/DFIR Teams? - Sign up for a free ANY.RUN account! to Analyse Advanced Malware Files


[ad_2]
Source link

OnePlus Nord 4 launch date revealed, live image leaks

0
[ad_1]

OnePlus has announced the launch date of the OnePlus Nord 4, its new mid-range phone. The device will become official on July 16, and the launch event will take place in Milan, Italy. It will kick off at 3 PM CEST / 9 AM EST / 6 AM PST / 2 PM BST.

The OnePlus Nord 4 launch date has been revealed

This is what OnePlus had to say in the press invite: “Some say it’s impossible in the 5G era to make a smartphone with the strength, sophistication and enduring quality of metal. We say…Never Settle”.

As reported, the invite itself is metallic-looking, and the company also shared a teaser image to go along with it. You can check out both of those in the gallery below. That teaser image also utilizes liquid metal, it seems. Is OnePlus trying to tell us something here? Well, possibly, more on that in a moment.

It will offer a different design than the OnePlus Ace 3V after all

Now, based on various reports, the OnePlus Nord 4 could be a rebranded OnePlus Ace 3V that has already launched in China. While that may be true for its specs, its design will be completely different, it seems.

A well-known tipster, Digital Chat Station, shared a schematic of the device. On top of that, a real-life image of the phone surfaced too, and they kind of match each other. Both are different than the OnePLus Ace 3V, quite a bit.

The schematic is shown below. A flat display is on the front, with a centered display camera hole. Its physical buttons sit on the right-hand side, while the alert slider is located on the left.

OnePlus Nord 4 schematic

Two cameras are horizontally aligned on the back, in the top-left corner. Some sensors sit on the right. You will notice a line drawn very high up. The live image we’ll talk about will reveal more information about that.

The phone’s live image surfaced too

If you take a look at the image below, you’ll see the live image of the OnePlus Nord 4. Needless to say, it looks quite odd. The top quarter of the phone’s back has glass on top of it, while the rest is covered by… metal?

OnePlus Nord 4 live image leak

We’re guessing this is metal based on OnePlus’ invite, but it does look weird. At first, I thought it was some sort of case or protection, but no, this seems to be a part of the device. The fact that the glass portion is shiny and reflective, while the black portion is matte… it simply looks weird.


[ad_2]
Source link

FakeBat Malware Weaponizing AnyDesk, Zoom, Teams & Chrome

0
[ad_1]

Hackers target and weaponize AnyDesk, Zoom, Teams, and Chrome as these applications are widely used in a multitude of sectors.

Not only that, but even these widely used applications also provide access to many users and sensitive information.

Cybersecurity researchers at Sekoia identified that FakeBat malware has been actively weaponizing widely used applications, AnyDesk, Zoom, Teams, and Chrome.

FakeBat Malware Loader

In 2024, FakeBat loader malware has become a major threat that uses drive-by-download methods for propagation.

This is sold as Loader-as-a-Service on dark web platforms and masquerades itself through malvertising and social engineering tricks.

Mostly, it is used for launching various payloads such as botnets and infostealers, which have been also associated with ransomware attacks.

The malware’s operators have updated its capabilities to include MSIX format builds and digital signatures to bypass security measures.

"Is Your System Under Attack? Try Cynet XDR: Automated Detection & Response for Endpoints, Networks, & Users!"- Free Demo

The prices of FakeBat range from $1,000-$5,000 per week or month, depending on the package. Sekoia said that FakeBat deliberately restricts its customer base to maintain control over distribution and reduce the risks of detection.

FakeBat’s distribution has evolved into a sophisticated operation that involves different strategies such as malvertising, software impersonation, and social engineering on social networks.

Compromised website displaying a fake web browser update popup (Source – Sekoia)

Another way this malware is distributed is through compromised websites, fake browser updates, and targeted campaigns such as the “getmess.io” web3 chat app scam.

Fake web3 chat application (Source – Sekoia)

FakeBat’s infrastructure consists of many C2 servers with changing communication patterns and obfuscation techniques.

The operators use specific domain naming conventions and host their servers on select ASNs.

They have implemented traffic filtering based on user attributes and recently enhanced evasion by anonymizing their domain registrations.

This shows how Fakebat’s conspirators are adaptable while seeking evasion from detection during expansion.

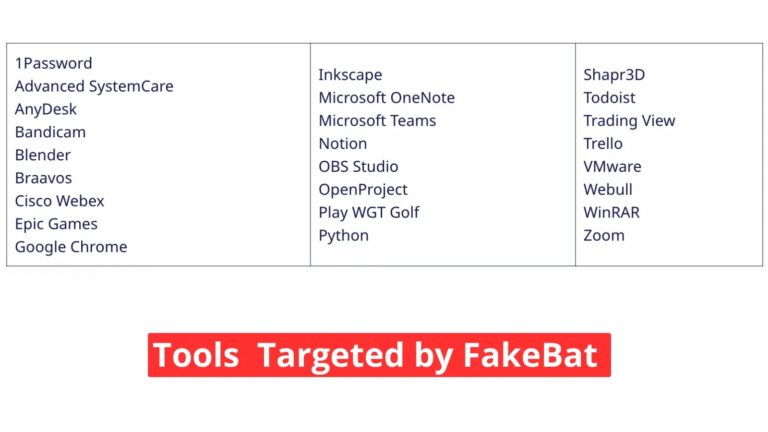
Researchers observed that the following software were targeted by the FakeBat malvertising campaigns:-

  • 1Password
  • Advanced SystemCare
  • AnyDesk
  • Bandicam
  • Blender
  • Braavos
  • Cisco Webex
  • Epic Games
  • Google Chrome
  • Inkscape
  • Microsoft OneNote
  • Microsoft Teams
  • Notion
  • OBS Studio
  • OpenProject
  • Play WGT Golf
  • Python Shapr3D
  • Todoist
  • Trading View
  • Trello
  • VMware
  • Webull
  • WinRAR
  • Zoom

Nowadays, threat actors prefer making use of fake software landing pages to share malware, and this is done through the practice of tracking campaigns.

Other observed sets contain entities like FIN7 and Nitrogen campaigns which circulate different kinds of malicious codes.

FakeBat, a widely distributed loader marketed as Malware-as-a-Service, uses multiple means of distribution and constantly modifies itself to avoid being identified.

Are you from SOC/DFIR Teams? - Sign up for a free ANY.RUN account! to Analyse Advanced Malware Files


[ad_2]
Source link

Powerful RedMagic 9S Pro gaming smartphones are now official

0
[ad_1]

RedMagic has just announced two new smartphones, the RedMagic 9S Pro and RedMagic 9S Pro+. Both of these are gaming smartphones that come with an extremely powerful set of specs and a bevy of gaming features, of course.

Before we get to that, let’s talk about the design first. The two phones look the same, and their specifications are also quite similar. The only differences relate to RAM, storage, battery size, and charging speed.

Both the RedMagic 9S Pro & Pro+ include an under-display camera

These two smartphones feature an under-display camera and very thin bezels. They have a square shape, and flat frame on the sides… all around the phone. Shoulder triggers are still placed on the right-hand side, as is that red switch that fires up the fan and pushes the phone into heavy-duty gaming mode.

The phones have three cameras on the back, which are flush with the phone’s backplate. That’s always nice to see. You’ll also notice that they have a very nice-looking backplate, appropriate for a gaming smartphone. All of this is quite similar to their predecessor, though.

ICE 13.5 advanced cooling system is implemented here

These devices also come with the ICE 13.5 advanced cooling system. It features a 10,182mm² single-layer vapor chamber (VC) plate. It also includes a new frost cooling gel to reduce thermal resistance and lower the core temperature to 19.5°C.

RedMagic also included an upgraded 22,000 rpm high-speed turbofan with shark-fin blades. That fan is not that loud at all as it operates at just 4dB. That’s a notable improvement.

Custom RGB lights are once again a part of the package, and the display also offers high-frequency PWM dimming at 2,160Hz.

Qualcomm’s most powerful processor fuels both devices

The Snapdragon 8 Gen 3 fuels these phones, the overclocked version. The RedMagic 9S Pro includes 12GB of LPDDR5X RAM, while the Pro+ model comes with up to 24GB of LPDDR5X RAM. Storage goes up to 512GB inside the regular model, and up to 1TB inside the Pro+ model. UFS 4.0 is used, by the way.

You will find a 6.8-inch fullHD+ (2480 x 1116) OLED display here, which is flat. It has a 120Hz refresh rate, and up to 960Hz touch sampling rate. 10-bit color depth is also on offer as is 100% DCI-P3 color gamut. The peak brightness of this display is 1,600 nits.

Android 14 comes pre-installed on both phones with RedMagic OS 9.5. The RedMagic 9S Pro includes a 6,500mAh battery and supports 80W charging. The Pro+ model comes with a 5,500mAh battery and supports 165W charging. Wireless charging is not supported.

Dual 1115K speakers are here, and the same goes for DTS:X Ultra support

Both phones have dual 1115K speakers and DTS:X Ultra support. Three microphones are also included, and there is also an audio jack on each of the two phones. An optical in-display fingerprint scanner is also something you’ll find inside each of the phones.

A 50-megapixel main camera (Samsung’s GN5 sensor) is backed by a 50-megapixel ultrawide camera (Samsung JN1 sensor). The third camera on the back is a 2-megapixel macro unit (GigaDevice GC02M1 sensor). There is a 16-megapixel under-display camera included on the front.

5G is supported here, as is Wi-Fi 6E. The same goes for Bluetooth 5.4. Both smartphones come with two nano SIM card slots too. AI has a role to play in the software too, as it improves some of the company’s gaming features and various other aspects of the software.

The RedMagic 9S Pro pricing starts at CNY4,799 ($660) and goes up to CNY5,399 ($742). The RedMagic 9S Pro+ model starts at CNY5,799 ($797) in China, and its price goes up to CNY6,999 ($962). Do note that the global variant(s) is coming soon, on July 16, so stay tuned for that.


[ad_2]
Source link