Microsoft analysts reported that China uses AI-generated content to trick American voters ahead of the 2024 election. The tech company also says Chinese agents are getting better at doing this.
Concerns about election safety are arising as we get closer to the US 2024 presidential election. Back in 2016, Russia was accused of meddling in the election. Now, Chinese agents are reportedly trying to influence American public opinion with AI photos. Ex-Google CEO Eric Schmidt already predicted that the upcoming US election could become a “mess” due to AI.
According to the Microsoft analysts report, China and North Korea currently employ AI-generated content to target voters. The scope of their operation is said to be greater than anything already seen.
“We have observed China-affiliated actors leveraging AI-generated visual media in a broad campaign that largely focuses on politically divisive topics, such as gun violence, and denigrating US political figures and symbols,” Clint Watts, the Microsoft Threat Analysis Center general manager, said.
China uses AI content to target US voters ahead of the 2024 election
The images spread by these agents mostly revolve around racial issues. For example, they reposted a Black Lives Matter poster showing bullet holes and a Black man surrendering.
Microsoft has warned the accounts that repost these photos. Chinese Communist Party agents mostly create these accounts and try to add fuel to the fire of racial issues in the United States. In one case, an account impersonating a conservative US voter reposted a Black Lives Matter poster complaining about racial discrimination.
Microsoft analysts warned that the AI-generated content by Chinese agents “has already drawn higher levels of engagement from authentic social media users.” Additionally, the new images are even more eye-catching, and US voters are reposting them despite knowing that AI generates them.
Analysts added that CCP-affiliated actors behind these accounts use fictitious or stolen identities to hide their affiliation with China. However, they’ve made some obvious mistakes, like posting in Mandarin and then switching to another language to conceal their main intention. The CCP-affiliated accounts also try to increase each other’s visibility by reposting content reciprocally.
As expected, a spokesperson for the Chinese Embassy in Washington rejected the allegations, saying, “Such remarks are full of prejudice and malicious speculation against China, which China firmly opposes.”
A Global Ticketing Giant company, See Tickets, recently reported a data breach that exposed the payment card information of over 300,000 customers.
See Tickets, owned by Vivendi Ticketing, revealed the latest breach in a complaint with Maine’s attorney general.
The ticketing business said that in May, it discovered unusual activity on its e-commerce website.
An anonymous cybersecurity company investigated and found that hackers “inserted multiple instances of malicious code into a number of its e-commerce checkout pages.”
Data Compromised in the Breach
Between February 28 and July 2, the hackers could access the names, addresses, and payment data of customers who made transactions on the See Tickets website. The compromised information includes:
Customer names
Addresses
Debit or credit card numbers in combination with security codes, access codes, passwords, or PINs.
According to the notification to impacted consumers, the data breach affected over 323,000 See Ticket users.
This attack reveals the prevalence of credit card skimming malware, in which criminals insert malicious code into a website’s checkout pages to steal users’ payment card information.
Card skimming is stealing credit card information or payment card data from online store consumers. Customers are unaware that their transaction data is being intercepted throughout the online purchase checkout procedure.
This issue represents the second known breach that See Tickets has experienced recently. See Tickets disclosed in October 2022 that hackers acquired consumers’ credit card credentials after hacked event checkouts for over two years.
According to the business, the skimming started on June 25, 2019; however, the code wasn’t found until April 2021.
The malware wasn’t entirely removed from the See Tickets website until over a year later, in January 2022.
Global Ticketing Giant company See Tickets adds that its investigation into the breach was finished on July 21 and that the firm “moved quickly to notify you” — even though it took more than six weeks to contact affected consumers.
Customers who are alerted receive a free year of Kroll credit monitoring service and are urged to be watchful against identity theft and fraud.
Spotify has offered audiobooks since last year, and you can enjoy them if you’re willing to pay. However, what if you want to just try out some of the books that are on the platform before taking out your wallet? Well, according to The Wall Street Journal (via The Verge), Spotify could let you listen to audiobooks for free. There’s just a bit of a catch.
At the moment, Spotify doesn’t have the selection of audiobooks that Amazon has, but it’s still making gains in the market. If you’re interested in listening to audiobooks on Spotify, you can use them even if you don’t have a premium. Just go to the app/website, and search “audiobook” in the search bar. You should also see an audiobook tab on the home screen.
Spotify could let people listen to audiobooks for free
Spotify’s audiobook service operates just like other services. You’ll pay for each audiobook you listen to. The price will depend on the book, also. When you buy the book you want to listen to, it will be held in your library.
If you use Amazon’s audiobook platform called Audible, you’ll get some free books when you sign up. There’s no such perk with Spotify, but the company might provide a way for people to get some free listening in. The Wall Street Journal states that the company is working on a pilot program for a free trial for audiobooks.
This free trial could allow people to listen to up to 20 hours of audiobook content each month for free. That should be enough for two average-length books each month, which sounds pretty nice. From the sounds of it, it seems like you’ll have a 20-hour reservoir each month, and as you listen, it’ll be eaten away.
It also sounds like it won’t be tied to specific books. So, you might be able to spend your hours on any book that you like. If that’s the case, then you will be able to test drive different books to see if you want to buy them. This gives you more options when you’re looking for a book to buy.
At this point, we don’t know too much about this pilot program, but more information about it will come up as time goes on.
It’s long been lauded as just an accessory to the computer experience; the computer mouse. Little do people know that the kind of mouse they have attached to their computer can define their work or play experience on their computer. Here’s a list of some of the best computer mice you can buy.
We’ll show you mice for general computer usage on this list. However, if you’re a gamer, then we have a list of the Best Gaming Mice, so you’ll want to take a look at that one. Also, these lists are constantly updated, so check back for new entries.
Best computer mice you can buy
This list will show you some useful, ergonomic, unique, and business-forward mice that you can use to add to your computer experience. These are targeted toward casual and professional computer users.
8Bitdo N30
This is for you nostalgic nerds out there. The Super Nintendo defined a generation, and if you’re into the aesthetic of that system’s controller, then you’re sure to love this mouse. It sports the controller’s design with the light gray chassis, red buttons, and black accents.
On the side of the controller, there’s a D-pad on the side to help with navigation. This will help make up for the lack of the scrolling wheel in the middle. If you’re used to traditional mice, this mouse will take some getting used to. The click buttons are circular rather than being curved planes across the front of the mouse.
This mouse is wireless, and it works with both Windows and Mac computers. It’s a fun mouse to use, but it might not be the most ergonomic. So, if you’re looking for a more ergonomic mouse, then you might want to pass this one up.
As stated at the beginning of this article, there will be unique mice, and this is definitely under that category. Looking at this device, it doesn’t really look like a mouse; however, it is. You’ll carry this mouse as you would a laser pointer and control your computer in that way.
To move the cursor, you’ll use the blue trackball on the top. Right under the trackball, you’ll have your left and right mouse buttons with the scrolling wheel in between them.
The reason why this mouse is like this is for ergonomic purposes. It allows you to have your hand in a more natural position rather than resting flat on a table. You’ll be able to use it just like any other mouse for a longer amount of time.
If you’re looking for a mouse with a minimalist design, then you might want to try out the Microsoft Arc mouse. This is as simple as a mouse can get with its simple unibody design. The body is relatively thin with a notable arc to it, giving it its name.
This mouse is for people who want a simple mouse that doesn’t take up much space on the desk. It’s small enough to fit pretty much any setup. Also, when you need to store it, the Arc mouse can go flat. This means that you can pack it away much easier.
This is a Microsoft mouse, so you know that it works perfectly for Windows computers. However, you can still use this mouse on Mac computers and on Chromebooks.
This definitely doesn’t look like your typical mouse. Rather, the Hippus M2WB is a mouse that prioritizes ergonomics. The mouse is like a bed that your hand rests upon. It’s wave-shaped, so your hand will lay on the mouse in a natural way. It’s to help prevent your hands from sitting flat on the table or resting in an unnatural position.
This is a wired mouse that uses a USB 1.1 connector. You’ll plug it into your computer and immediately start using it. The rest of the mouse is pretty standard. In the front, you have your left and right clicker buttons with the scrolling wheel in the middle. The buttons are angled so that your fingers will rest comfortably on them.
This mouse is compatible with all versions of Windows, Mac OS 9 and X, Linux, and Unix. So, you’ll most likely be able to use this no matter what computer that you’re using.
This is definitely the most futuristic-looking mouse on the list with its almost robotic design. It has this metallic material to it with a unique segmented design. Adding to the futuristic design, there’s a blue LED in the middle of the mouse.
The DANCESOUL Mouse can both be used wired and wirelessly, which only adds to the utility. This mouse has a rechargeable battery, so you won’t have to worry about replacing the battery when it goes out. Also, with fast charging technology, you won’t be out of the game for too long when the battery does run out.
This mouse can run on pretty much any operating system you’d be using. It’s compatible with Windows, Mac OS, and recent game consoles, but it has a special adaptor that further expands its usability. One side of it has a USB type-A head and the other has a USB type-C head. This means that you’re able to use this with your Android devices as well.
This is a mouse with a unique almost arrowhead shape. It’s shaped like this for the sake of ergonomics. When you use the mouse, your hand will rest on the mouse in a natural sideways position, eliminating strain when using it for long periods of time. It will take some getting used to if you’re used to traditional mice. However, it’s a worthy upgrade if you have wrist pains.
On the thumb side of the mouse, you have a backward and forward button to help you navigate easier. On the other side, of course, you have your typical clicking buttons with the scrolling wheel in the middle. At the top of the mouse, there’s a DPI button to help adjust the speed of the cursor.
The Lekvey Ergonomic Mouse has a rechargeable battery that can last you a long time on a single charge. Speaking of use, you can use this mouse on a wide range of Windows and Linux devices, but it’s not compatible with Mac OS products.
This is a mouse that prioritizes ergonomics, and that lends to its unique shape. It’s a vertical mouse, so your hand will pretty much stand upright. Just like other ergonomic mice, this one keeps your hand in a more natural side-ways position.
Your thumb will sit in a little slot on the side of the mouse with a button above and below it. These are the forward and backward buttons that will help you navigate easier. On the other side, you’ll see the typical clicker buttons with the scrolling wheel in the middle. On the bottom of the mouse, there’s a palm rest that will keep your palm from scraping against the mouse pad.
This is also the kind of mouse that you’d want if you want to keep quiet when you’re using it. The mouse buttons are much quieter than with other mice. So, you won’t have to worry if you’re working in a quiet location.
So, you have a smaller setup, and you need a mouse that won’t take up too much space. Well, the Logitech Pebble i345 is the mouse for you. It’s a very low-profile mouse that you’ll use when you need to save space. Say, you need to work at a crowded coffee shop or your desk is cluttered. This mouse is small and portable. You can actually fit it in your pocket.
This is a Bluetooth mouse, so you don’t need to worry about the USB attachment. You’re able to use it for your computer, and you’re also able to use it for your tablet or other mobile device.
It’s not the most ergonomic mouse, so you’ll want to keep that in mind. The main focus of the mouse is saving space, so if you’re alright with using a pebble-shaped mouse, then it’s the mouse for you.
Multiple vulnerabilities have been discovered in Aruba 9200 and 9000 Series Controllers and Gateways running ArubaOS. The vulnerabilities related to Buffer Overflow and Hardware Root of Trust bypass. Aruba has released a security advisory for addressing these vulnerabilities.
At the end of August, Aruba released patches for multiple vulnerabilities affecting Aruba Switches, which were related to Stored Cross-site Scripting (Stored XSS), Denial of Service (DoS), and Memory corruption.
CVE-2023-38484, CVE-2023-38485
These two vulnerabilities are related to Buffer Overflow that exists in the BIOS implementation of Aruba 9200 and 9000 Series Controllers and Gateways. These vulnerabilities can allow a threat actor to execute arbitrary code in the boot sequence.
In addition to this, the threat actor can also gain access to sensitive information in the affected Aruba Series controllers and change them which leads to a complete system compromise. The severity for these vulnerabilities has been given as 8.0 (High).
CVE-2023-38486 – Hardware Root of Trust Bypass
This vulnerability exists in the secure boot implementation on the affected Aruba 9200 and 9000 Series Controllers and Gateways could allow a threat actor to bypass the security control that prohibits unsigned kernel images from executing.
Furthermore, the threat actor can also use this vulnerability to execute arbitrary runtime operating systems, including unverified and unsigned OS images. The severity of this vulnerability has been given as 7.7 (High).
Prerequisites for a Threat Actor & Workaround
In order to exploit these vulnerabilities, the threat actor must exploit other vulnerabilities and gain access to the root shell of the Local ArubaOS controller since these vulnerabilities require root shell access for exploitation.
As a workaround, Aruba has recommended its users restrict the CLI and web-based management interfaces to a dedicated layer 2 segment or by firewall policies at layer 3 and above.
“HPE Aruba Networking recommends that the CLI and web-based management interfaces be restricted to a dedicated layer 2 segment/VLAN and/or controlled by firewall policies at layer 3 and above.” reads the security advisory by Aruba.
For detailed information about these vulnerabilities, it is recommended to check the security advisory released by Aruba.
Affected Products
Affected Software Versions
End-of-support products (Patches will not be released)
Fixed in versions
9200 Series Mobility Controllers and SD-WAN Gateways9000 Series Mobility Controllers and SD-WAN Gateways
ArubaOS 10.4.x.x: 10.4.0.1 and belowArubaOS 8.11.x.x: 8.11.1.0 and belowArubaOS 8.10.x.x: 8.10.0.6 and belowArubaOS 8.6.x.x: 8.6.0.21 and below
ArubaOS 10.4.x.x: 10.4.0.2 and aboveArubaOS 8.11.x.x: 8.11.1.1 and aboveArubaOS 8.10.x.x: 8.10.0.7 and aboveArubaOS 8.6.x.x: 8.6.0.22 and above
Users of these products are recommended to upgrade to the latest ArubaOS versions to fix these vulnerabilities and prevent them from getting exploited.
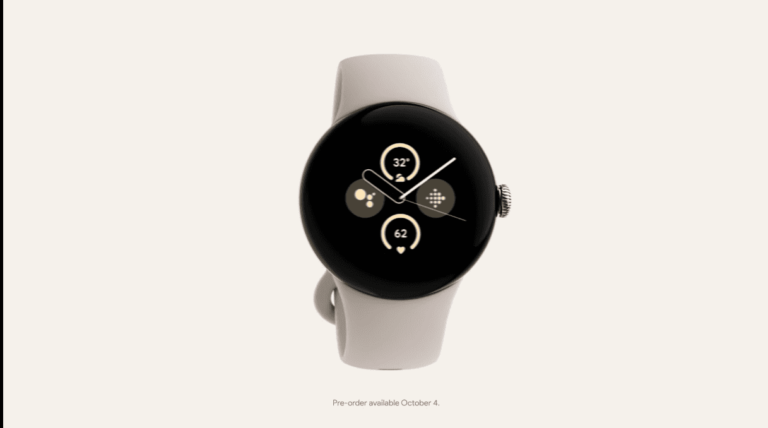
Yesterday, Google put out a few teasers, to let us know what to expect at their October 4 launch in New York City. And today, the company put out another video. This time, showing the Pixel Watch 2 from every angle. And while we know the Pixel Watch 2 is coming, and was shown off in the video, we’re starting to see a few other details.
At the very start of the video, you can see on the backside of the watch “IP68” and also what looks to be “Pixel Watch 2”. Which does definitely confirm the name, though Google did also call it that in its post on X.
This means that the Pixel Watch 2 is going to be IP68, which is a big deal. That is going to let you wear it in the shower, take it to the beach or the pool and go swimming and much more. It’s a little surprising that the first Pixel Watch wasn’t waterproof, since other Fitbits have been for quite some time.
Google pre-announced the Pixel Watch 2
After giving us a sneak peak at the Pixel 8 series yesterday, now Google’s doing the same with the Pixel Watch 2. It’s a bit of an interesting move for Google. Whereas most companies want to keep leaks down and as a secret ahead of the launch, Google is doing the opposite. Though this isn’t new for them. They kinda started doing this a few years ago with the Pixel 5 and Pixel 4a 5G.
It’s interesting, because of the timing. We’re just days away from the iPhone event, which is going to be the most watched smartphone launch of the year. And it appears that Google wants to get some of that attention off of Apple. And in doing so, basically announced all of their products ahead of the October 4 event.
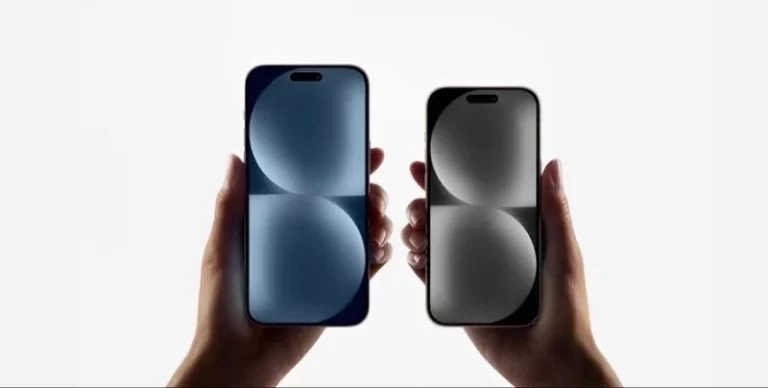
The Pro Max model of every iPhone (and before that, the Plus) has always been the most popular model out of the lineup. But this year, it looks like it’s a much more popular model. As market intelligence company, TrendForce is expecting about 40% of iPhone sales to be the iPhone 15 Pro Max.
This is particularly surprising since there is going to be an iPhone 15 Plus, and the iPhone 15 Pro Max is seeing a price bump of at least $100. However, Apple is rumored to be moving the base storage up to 256GB, which makes the price increase a bit easier to swallow, since it is actually the same price as the 256GB iPhone 14 Pro Max.
TrendForce is expecting Apple to sell 80 million iPhone 15 units this year
This year, TrendForce is expecting Apple to sell about 80 million units of the iPhone 15 series. That’s up about 6% from the iPhone 14 series. Though part of that is because the iPhone 14 series was heavily constrained due to the supply chain. The firm is also expecting that the Pro models will continue to be more popular than the non-Pro models. With a 60/40 split between Pro and non-Pro iPhones.
If the iPhone 15 Pro Max does become the most popular model, and by a large model as TrendForce is expecting, that will be great news for Apple. You see, Apple’s average price of an iPhone sale has dropped quite a bit over the past couple of quarters. And this is because customers are buying the base storage models, and not opting to upgrade their storage as often. Raising the price on the iPhone 15 Pro Max and making it the most popular model, will do wonders for Apple.
The company is expected to announce a 2TB model for the iPhone 15 Pro and Pro Max this year too. Which is just bonkers on a smartphone.
A single sign-on (SSO) implementation flaw in the Cisco BroadWorks Application Delivery Platform and Cisco BroadWorks Xtended Services Platform might make it possible for a remote, unauthenticated attacker to forge credentials to access a vulnerable system.
This “Critical” severity vulnerability has a CVSS base score of 10.0 and is tracked as CVE-2023-20238.
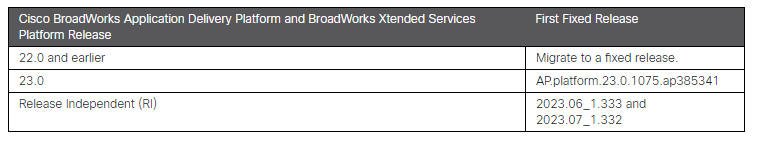
Cisco has issued software upgrades to address this vulnerability. There are no workarounds that address this vulnerability.
Details of the Vulnerability
Cisco stated that the process used to validate SSO tokens causes this vulnerability. By logging into the application using fake credentials, an attacker might take advantage of this vulnerability.
“This vulnerability is due to the method used to validate SSO tokens. An attacker could exploit this vulnerability by authenticating to the application with forged credentials”, Cisco said in its Security Advisory.
If the vulnerability is successful, the attacker may be able to use the forged account to execute commands or commit toll fraud. Further, the attacker would be able to read sensitive data, change customer settings, or change settings for other users if that account is an Administrator account.
“If that account is an Administrator account, the attacker would have the ability to view confidential information, modify customer settings, or modify settings for other users,” Cisco said.
The attacker would require a legitimate user ID linked to an affected Cisco BroadWorks system to take advantage of this flaw.
Affected Products
If you are running a vulnerable release of Cisco BroadWorks and have enabled one of the following applications, you are vulnerable to this issue.
AuthenticationService
BWCallCenter
BWReceptionist
CustomMediaFilesRetrieval
ModeratorClientApp
PublicECLQuery
PublicReporting
UCAPI
Xsi-Actions
Xsi-Events
Xsi-MMTel
Xsi-VTR
Products Unaffected
BroadWorks Ansible Playbook
BroadWorks Database Server
BroadWorks Database Troubleshooting Server
BroadWorks Execution Server
BroadWorks Media Server
BroadWorks Messaging Server
BroadWorks Network Database Server
BroadWorks Network Function Manager
BroadWorks Network Server
BroadWorks Pre-Install Check
BroadWorks Profile Server
BroadWorks Service Control Function Server
BroadWorks Service License Report Tool
BroadWorks Sharing Server
BroadWorks Software Manager
BroadWorks Video Server
BroadWorks WebRTC Server
Fixes Available
Cisco has made free software upgrades available to fix this issue.
Customers are encouraged to upgrade to an applicable fixed software release as soon as feasible.
As has been rumored since the beginning of the summer, rising chipmaker, MediaTek’s got a hot new flagship chipset in the works. Which aims to narrow the gap between its top-of-range offerings and industry standard bearer Qualcomm’s leading Snapdragon 8 series.
Unfortunately for the Taiwanese firm, word among those in the know is that the upcoming Dimensity 9300’s hotness is not limited to mere literary flourish. The unconventionally-designed model is said to literally be running too hot to operate at its advertised frequencies. This has the potential of generating some uncomfortable conversations between MediaTek and its OEM customers, the latter of whom have been promised performance that may not be achievable within acceptable thermal ranges.
Why is the Dimensity 9300 running so hot?
Apparently the problem stems from the silicon maker’s ambitious design choices with regard to ARM core distribution on the octa-core wafer: whereas most modern ARM-based chips contain a mix of fast and slow cores to throttle back the power (and thus the heat) during less intensive computing tasks, the Dimensity 9300 can most accurately be said to eschew the slow cores completely in favor of a mix that includes only fast and very fast (four each of Cortex-A720 and Cortex-X4, respectively).
While the envelope-pushing, four-nanometer design — previously reported by Weibo leaker Digital Chat Station — has been generating early buzz, it’s also allegedly causing headaches for phone manufacturers trying to unbottle that potential performance without singeing users’ hands in the process.
So now, as the chip’s rumored October launch approaches and partners scramble to finalize their plans around it, MediaTek reportedly finds itself in an unenviable bind. It can either dial back the speed somewhat significantly in order to meet stringent OEM thermal requirements — deflating much of the buzz-making and thus earnings-generating performance of D9300 — or it can try to move customers over to its more tried-and-true (but less exciting) solutions. Alternatively, it could watch them walk away altogether, a last-ditch maneuver that would be sure to cause production delays as well as leaving a sour taste in the mouths of everyone involved.
As part of Apple’s event next week, Apple is going to be giving the AirPods Pro a pretty major upgrade. That’s USB-C. Okay, that might not sound like a huge upgrade, but it really is.
Don’t expect this to be a full on generational upgrade for the AirPods Pro, as it isn’t quite time for that yet. The main upgrade here is changing Lightning to USB-C. Apple is also planning to upgrade the AirPods and AirPods Max to USB-C as early as next year. While it is time for the AirPods Max to get updated, the regular AirPods were just updated about a year ago. So those will likely be just a change to USB-C too.
Gurman says that there won’t be any other changes to the AirPods Pro at the event. But the AirPods Pro are a big seller for Apple, so updating them to USB-C first is smart.
Apple is working on new health features for AirPods
Although this update will really only be USB-C, Apple is still working on some new health features for the AirPods. This includes body-temperature sensing and a new hearing-test system. Those enhancements are likely coming later on down the road though. As it does seem to be pretty early on for these features.
Adding health features to the AirPods are going to help make them more “sticky” for users. Which, for iPhone users, they are already pretty sticky, because of how well they work with the iPhone, iPad and Macs already.
AirPods are typically updated about every two years or so. It’s one of the few products that Apple does not update yearly, which they really don’t need to. There have been a couple of one-offs, like updating the original AirPods to a wireless charging case, and now updating the AirPods Pro to USB-C. But as far as new hardware, that’s about every two to three years.