Rapid7 to Acquire Noetic Cyber to Enhance Attack Surface Visibility

0
[ad_1]

Rapid7, Inc., a leader in extended risk and threat detection, has announced a definitive agreement to acquire Noetic Cyber, a pioneering company in cyber asset surface management (CAASM).

This strategic move aims to bolster Rapid7’s existing cybersecurity solutions by integrating Noetic’s advanced CAASM capabilities, providing customers with a more comprehensive view of their digital environments.

Enhanced Visibility and Risk Management

Integrating Noetic Cyber’s CAASM solution into Rapid7’s platform will offer unparalleled visibility into internal and external assets spanning on-premise and cloud environments.

This enhanced visibility will empower customers to:

  • Gain a high-context, inside-out view and an adversary-aware, outside-in perspective to better anticipate threats and manage risks.
  • Prioritize risks with threat-aware context, identifying the most critical exposures.
  • Improve signal-to-noise ratios across security teams, enhancing asset inventory and reducing risks through pragmatic remediation guidance and automation.
  • Boost efficiency and productivity by providing highly correlated asset and resource views with searchable risk context.

"Is Your System Under Attack? Try Cynet XDR: Automated Detection & Response for Endpoints, Networks, & Users!"- Free Demo

Corey Thomas, CEO of Rapid7, emphasized the importance of this acquisition, stating, “Fragmented attack surfaces stifle security productivity, efficiency, collaboration, and credibility.

Adding Noetic’s solution to our platform positions Rapid7 to deliver the most productive security operations experience while making it more accessible to the teams who need it most.”

Addressing a Critical Industry Challenge

According to the 2024 Gartner® Innovation Insight: Attack Surface Management report, only 17% of organizations can identify and inventory a majority (95% or more) of their assets.

This statistic underscores the critical need for improved asset visibility and management in the cybersecurity landscape.

Paul Ayers, CEO and co-founder of Noetic Cyber highlighted the acquisition’s benefits, stating, “The addition of Noetic Cyber to Rapid7’s portfolio ensures even more security teams can be confident they have the right visibility of their security data.

Rapid7 customers will now be able to better prioritize exposures based on the meaningful insights from Noetic and take action to identify security gaps and reduce cyber risk.”

Noetic Cyber, founded in 2019 by Paul Ayers, Allen Hadden, and Allen Rogers, has been dedicated to empowering security teams to command their attack surface.

The company’s proactive approach to cyber asset and exposure management aims to enhance security tools and control efficacy by breaking down existing data silos.

The acquisition is expected to close during Rapid7’s fiscal third quarter and is not anticipated to have a material impact on the company’s 2024 Annualized Recurring Revenue (ARR).

Rapid7 plans to make Noetic Cyber’s capabilities available to its customers this summer after the transaction’s completion.

The company’s comprehensive security solutions help over 11,000 global customers manage cloud risk and detect threats quickly and precisely.

Are you from SOC/DFIR Teams? - Sign up for a free ANY.RUN account! to Analyse Advanced Malware Files


[ad_2]
Source link
Meta changes how it labels AI-generated content after complaints from photographers

0
[ad_1]
Meta introduced new policies regarding all AI-generated content posted on Facebook and Instagram back in April. One of the new rules rolled out a few months ago was the labeling of AI-generated content and manipulated media with a “Made with AI” watermark.

However, photographers all around the world noticed that their images were labeled with “Made with AI” watermarks even though they only suffered minor modifications.

Meta acknowledged the issue and admitted that its labels weren’t always aligned with people’s expectations. Moreover, the “Made with AI” watermark didn’t provide enough context.

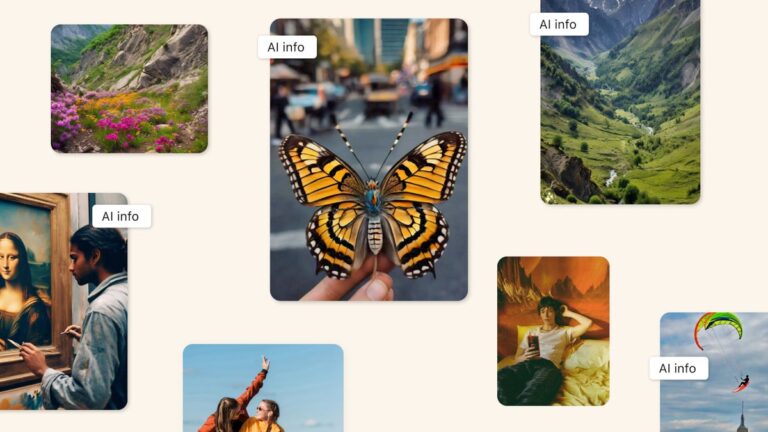
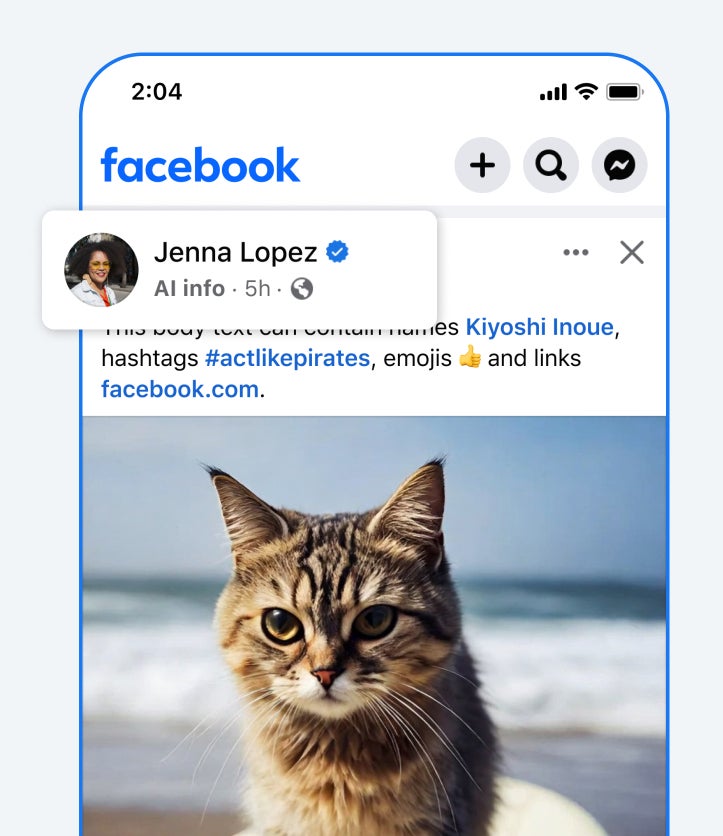
To avoid content that includes minor modifications using AI, such as retouching tools, to be labeled “Made with AI,” the social giant announced that it’s updating the label to “AI info” across its apps.

– Meta, July 2024

On top of that, people can now click on the “AI info” label to get more information about the image they’re looking at. Hopefully, Meta will provide more context on the content labeled “AI info,” so that users can figure out if they’re looking at AI-generated content or original content that’s been slightly modified using AI tools.

Meta’s new “AI info” label | Image credit: Meta

Obviously, this means that Meta will start adding “AI info” labels to a wider range of video, audio and image when it detects industry standard AI image indicators or when users disclose that they’re uploading AI-generated content.

Meta amended its policy regarding AI-generated content a few times since launch, and it’s probably going to fine-tune it further as AI tech continues to evolve and more people start using it for various purposes.


[ad_2]
Source link

regreSSHion RCE Flaw Impacts 700K Linux Systems

0
[ad_1]

The Qualys Threat Research Unit has identified a newly discovered vulnerability in OpenSSH, dubbed “regreSSHion” (CVE-2024-6387).

This critical flaw, which allows unauthenticated remote code execution (RCE) as root, affects over 700,000 Linux systems exposed to the internet.

The regreSSHion vulnerability is a signal handler race condition in OpenSSH’s server (sshd) that can be exploited to execute arbitrary code with the highest privileges.

This flaw is particularly concerning because it does not require user interaction and affects OpenSSH’s default configuration.

This vulnerability is a regression of a previously patched issue (CVE-2006-5051) reintroduced in October 2020 with the release of OpenSSH 8.5p1.

"Is Your System Under Attack? Try Cynet XDR: Automated Detection & Response for Endpoints, Networks, & Users!"- Free Demo

If exploited, regreSSHion could lead to a complete system takeover, allowing attackers to install malware, manipulate data, and create backdoors for persistent access.

This could facilitate network propagation, enabling attackers to compromise other vulnerable systems within an organization.

The vulnerability poses a significant risk as it allows attackers to bypass critical security mechanisms such as firewalls and intrusion detection systems, potentially leading to significant data breaches and leakage.

Exposed OpenSSH Instances

Qualys researchers used internet scanning services like Censys and Shodan to identify over 14 million potentially vulnerable OpenSSH server instances exposed to the internet.

Anonymized data from Qualys customer data revealed that approximately 700,000 external internet-facing instances are vulnerable, accounting for 31% of all internet-facing instances with OpenSSH in the Qualys global customer base.

The vulnerability arises from sshd’s SIGALRM handler calling various sensitive functions such as syslog() in an asynchronous way when an attempted connection fails to pass authentication within the LoginGraceTime period.

This can lead to heap corruption, which can be exploited to execute arbitrary code with root privileges. The flaw is particularly challenging to exploit due to its remote race condition nature, requiring multiple attempts for a successful attack.

Mitigation Steps

To mitigate the risk posed by regreSSHion, organizations are advised to:

While no active exploits have been seen in the wild, the potential impact of this flaw necessitates urgent action from system administrators to protect their systems.

How to Scan for regreSSHion Vulnerability

Organizations can use several tools to scan for the regreSSHion vulnerability (CVE-2024-6387) in their systems. Here are some of the most effective tools available:

1. CVE-2024-6387_Check Script

This is a lightweight and efficient tool designed specifically to identify servers running vulnerable versions of OpenSSH.

It supports rapid scanning of multiple IP addresses, domain names, and CIDR network ranges.

The script retrieves SSH banners without authentication and uses multi-threading for concurrent checks, significantly reducing scan times. The output provides a clear summary of the scanned targets, indicating which servers are vulnerable, not vulnerable, or have closed ports.

2. Qualys Vulnerability Management

Qualys offers a comprehensive vulnerability management tool that can scan for a wide range of vulnerabilities, including CVE-2024-6387. It provides extensive protection and is capable of aggregating and prioritizing cyber risks across all assets and attack vectors.

Are you from SOC/DFIR Teams? - Sign up for a free ANY.RUN account! to Analyse Advanced Malware Files


[ad_2]
Source link
This One Mistake Could Brick Your Phone!

0
[ad_1]

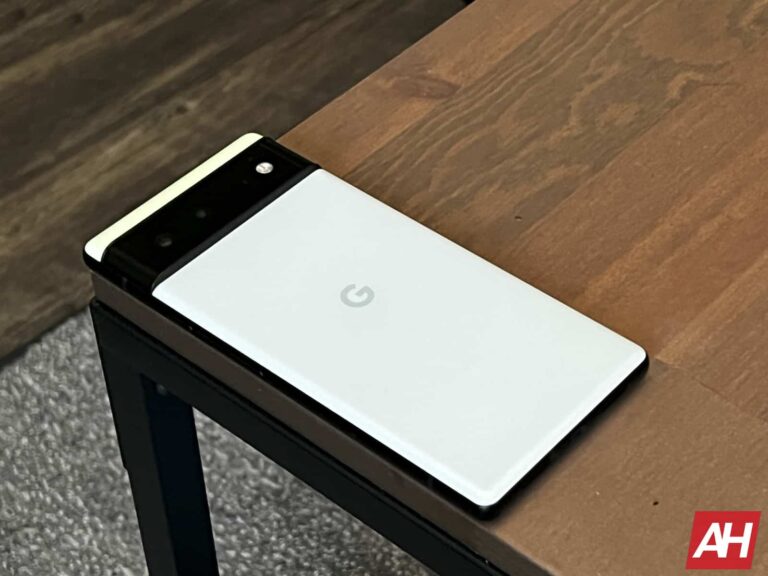
Google Pixel 6 series devices risk getting bricked if users perform a “factory reset”. Although sporadic, reports about Pixel 6, 6 Pro, and 6A turning into a dead paperweight have suddenly surged in the last few days.

A software update isn’t bricking Pixel 6 series smartphones

Google Pixel 6 series smartphone owners should avoid resetting their devices to factory settings for the next few days. This is because attempting a “factory reset” could brick their smartphones.

Reports about Google Pixel 6, Pixel 6 Pro, and Pixel 6a “bricking” after owners tried to perform a full reset have appeared on Reddit and the Google Pixel support community.

According to Tech-Issues Today, the issue isn’t limited to any specific model in the Pixel 6 series. In other words, any Android smartphone from the Pixel 6 series could fail to boot up after a factory reset.

Similarly, the Android version doesn’t matter either. Hence, some users have observed that a recent software update or an Android firmware update might not be the root cause. This means a Pixel 6 series smartphone could be bricked primarily due to a factory reset.

Most of the Pixel 6 owners who managed to brick their devices observed a similar pattern. The affected smartphone would refuse to boot normally. Instead, it would throw the following error:

“Cannot load Android system. Your data may be corrupt. If you continue to get this message, you may need to perform a factory data reset and erase all user data stored on this device.”

If users attempt to perform a “wipe”, a separate error mentions the phone is missing a file called tune2fs. According to The Verge, this file is a Unix command line tool used to set file system parameters.

Is Google aware performing a factory reset may brick Pixel 6 devices?

The Pixel 6 series launched in 2021. What this means is that the majority of Pixel 6 smartphones would be out of standard warranty.

This strongly implies Google would offer paid service or replacements, presumably citing motherboard issues. In other words, Pixel 6 owners who brick their smartphones could be looking at an expensive resolution to their troubles.

All hope, however, isn’t lost. A person who identifies as Detlef M., and claims to be a “Platinum Product Expert” on the Google Pixel support community, has implied Google is aware of the issue.

He added that Google is investigating the issue and advised affected users to watch the thread for any updates.


[ad_2]
Source link

Google Maps could soon let you co-navigate with multiple drivers

0
[ad_1]

Google Maps is without a doubt one of the most widely used services by the search engine giant. Just like with its other popular products, Google continues to enhance the user experience by providing new features for Google Maps from time to time. The company is now reportedly working on a new functionality, which will make driving for a family getaway a lot less hassle.

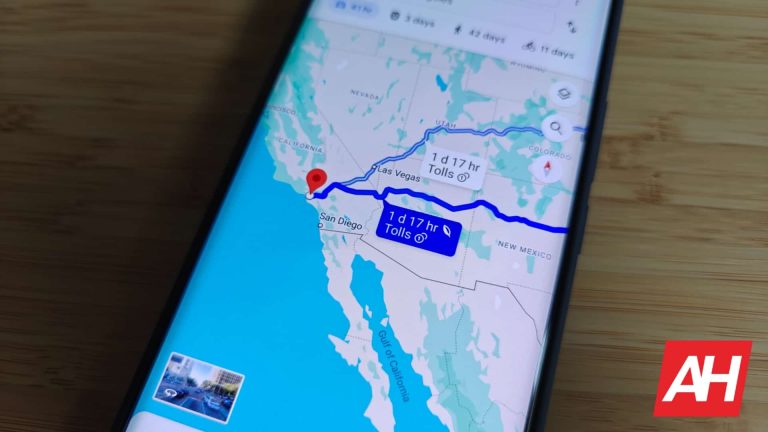
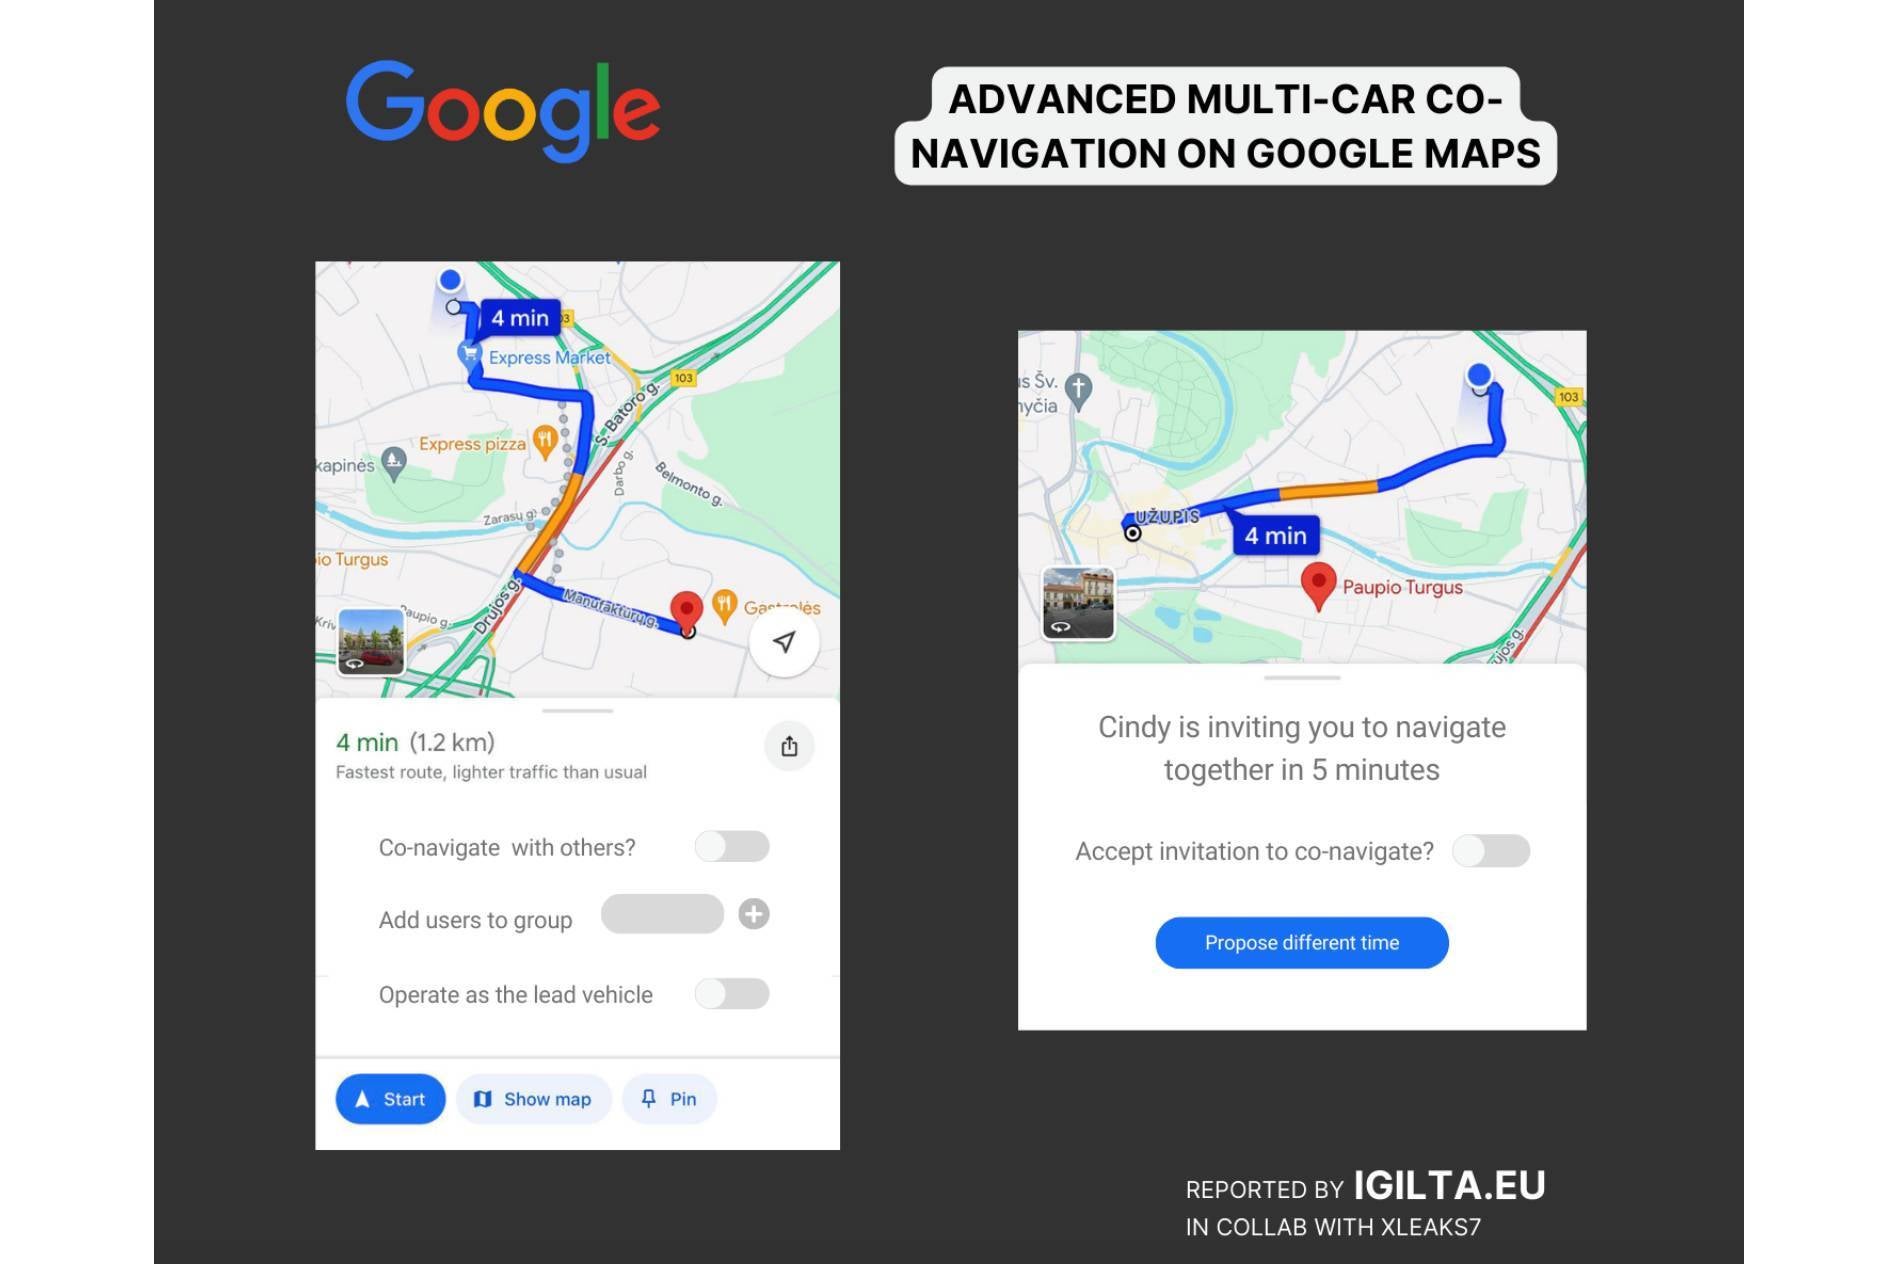
According to a newly found patent, Google Maps will soon let users co-navigate with multiple drivers in real-time. The new feature will make it immensely easier for several people to meet up at a single location while co-navigating together.

Google Maps will soon make it easier for multiple drivers to co-navigate, even coming from different locations

Some patent documents regarding a new Google Maps feature have been uncovered by Igilta and David Kowalski (xleaks7 on X). The document describes a new Google Maps functionality that will make it easier for multiple drivers to co-navigate to a single destination. This feature will certainly be helpful in situations when people are meeting at a place while coming from different locations.

Currently, navigation on Google Maps is quite easy for individuals or one vehicle. After all, this is how the service is intended to be used. But, if you are traveling in a group, with separate vehicles coming from different locations, navigation becomes a little more complex. However, the feature seen in the patent will organize hassle-free multi-car co-navigation for you and your friends.

The patent hints at a lot of new features to revolutionize group travel by road in Google Maps

The patent’s details suggest that Google Maps will soon be getting a lot of new co-navigation features. These are expected to revolutionize group travel by road. The new features will identify situations in which multiple people in your group are going to the same place. The system will co-navigate all the users in the group by sending notifications, sharing the location of other vehicles, and more.

While co-navigating, Google Maps will also suggest meeting spots where routes of multiple drivers can merge. It will also provide notifications about the latest traffic and road conditions. These will be determined by the leading vehicle. If a car makes a detour, all other people in the group will be notified. If that’s not enough, once the destination is reached, the system will also help with parking.

It’s worth mentioning that the aforementioned Google Maps feature is just a patent at the moment. So, there’s no way to tell when exactly Google is planning to launch this functionality. Given the usefulness of the feature, we hope it sees the light of the day very soon.


[ad_2]
Source link

Samsung Galaxy S24 FE may be available in these 5 colors

0
[ad_1]

The Galaxy S24 FE will not be one of the devices that Samsung will launch at the Unpacked event on July 10. In fact, it’s expected sometime in the last quarter of the year. However, leaks around the device have revealed key details, such as its cameras. Now, a new report reveals the colors in which the Samsung Galaxy S24 FE will be available.

Leak reveals 5 colors for the Samsung Galaxy S24 FE

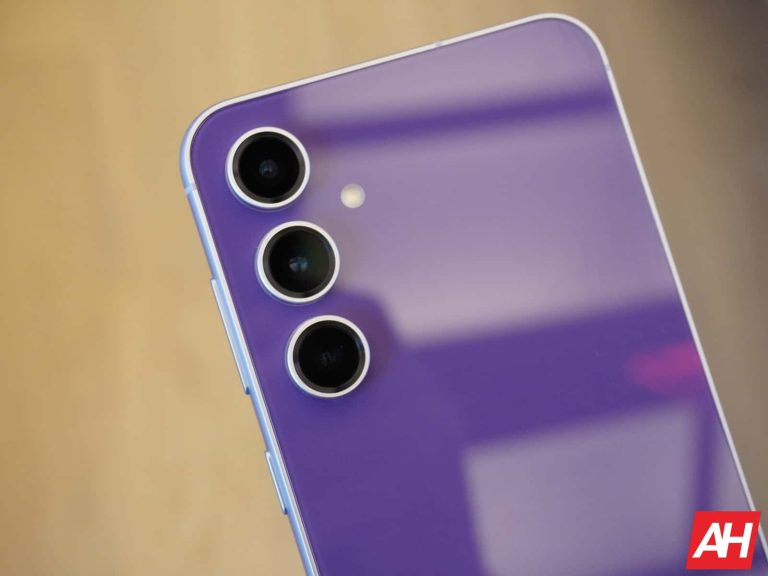
Like previous FE generations, the device will offer some of the key specs of the Galaxy flagships at a more affordable price. Plus, according to Ross Young on X/Twitter, it will be available in a wide variety of colors. This is a hallmark of Galaxy phones, so it was expected. The report claims that Samsung will launch the Galaxy S24 FE in Black, Gray, Light Blue, Light Green, and Yellow.

The source adds that the Black variant of the device will have the highest volume among all colors. Ross Young is a well-known analyst in the display industry and often offers reliable tips on future Samsung devices. So, the leak has high credibility. Previous reports about the Galaxy S24 FE revealed that it will be powered by the Exynos 2400 and Snapdragon 8 Gen 3 chipsets, depending on the region. This means that the phone will be a powerhouse with the latest mobile flagship chipsets available, which is good news.

Other leaked specs

According to leaks, the S24 FE will be built around a 6.5″ AMOLED screen with a 120 Hz refresh rate. The dimensions of the device would be 162 x 77.3 x 8 mm, so it would be easy to hold and use with one hand. Its rear area would be the home of a triple-camera system commanded by a 50 MP main sensor. This sensor would be the ISOCELL GN3, the same as the Galaxy S24 and S23 series (vanilla and Plus variants).

It doesn’t seem like Samsung wants to shake things up with the Galaxy S24 FE. However, the correct price tag could make it an instant success.


[ad_2]
Source link

Android 15 Beta 3.1 update now available; fixes lockscreen bug

0
[ad_1]

About two weeks ago, Google rolled out Android 15 Beta 3 for Pixel devices. This update brought some new features and key tweaks, being the first Android 15 beta build with the “Platform Stability” tag. Now, the company has released Android 15 Beta 3.1, a minor update focused on some bug fixes. However, users will be happy to know that it solves the annoying lock screen authentication bug.

Android 15 Beta 3.1 update rolling out for supported Pixel devices

The main bug reported in Android 15 Beta 3 prevented people from using their device normally from the lockscreen. When the phone is locked, users can still access actions, such as activating shortcuts or controlling music playback. However, a bug was causing the device to request PIN or fingerprint authentication to execute such actions. Of course, this bug was quite frustrating, since it forced you to unlock the device to perform actions that should not require it.

Fortunately, the fix to that bug is available in the latest Android 15 Beta 3.1 update. The firmware, which is identified with the build number AP31.240517.031, is now available for download from the official Google repositories. Those whose devices are running the previous update should also be receiving the OTA availability notification. You can also manually check for updates from the Settings menu on your phone.

Compatible Pixel devices; more fixed bugs

The update is available for the Pixel 6, Pixel 6 Pro, Pixel 6a, Pixel 7, Pixel 7 Pro, Pixel 7a, Pixel Tablet, Pixel Fold, Pixel 8, Pixel 8 Pro, and Pixel 8a. In addition to the lock screen authentication bug, there is a fix for facial unlocking. Before, face unlocking could sometimes fail for no apparent reason, even under ideal conditions. Lastly, the update also includes fixes for issues that “were impacting system stability, connectivity, and audio quality.”

The Android 15 Beta 3.1 OTA size is around 63.87 MB. If you have not yet received the update notification and do not want to wait, you can try a manual installation. You will find the necessary files and tools here.


[ad_2]
Source link

Microsoft AI CEO considers public web content as “freeware”

0
[ad_1]

The CEO of Microsoft AI considers that the public information available on the web is like “freeware.” Much of this data has been used to train AI models. However, not everyone agrees with this statement. Content creators continue to feel affected by the potential use of their work for this purpose, without receiving compensation.

Mustafa Suleyman, CEO of Microsoft AI, answered multiple questions related to the current role of AI and its development. One of the issues that most concern people in this regard has to do with copyright. Currently, there is still no firm “AI legislation” that considers all items, participants, and fair compensation. There are many “gray lines” that can cause questions even about the ethical use of AI.

Microsoft AI CEO says that publicly available content on the internet is “freeware”

With this in mind, CNBC’s Andrew Ross Sorkin asked Suleyman about the topic. Sorkin touched on the issue of the intellectual property of the data used to train AI models. This encompasses all content that is publicly available on the Internet. More specifically, he asked who owns the IP over that content, who should receive compensation for use of the IP, and whether AI companies have “stolen” that content.

To this, the CEO of Microsoft AI responded: “The social contract of that content since the 90’s has been…it is fair use. Anyone can copy it, recreate with it, reproduce with it. That has been freeware if you like.” This response is causing controversy among people, especially among content creators. They consider that comparing all publicly available content on the Internet with “freeware” is dangerous. They fear that, under that view, AI companies will feel free to take the content whenever they want.

“Gray area” cases should be dealt with in court, Suleyman claims

Suleyman makes a point by trying to separate the types of content publicly available on the Internet. He mentions that there is another category where creators explicitly say that their content cannot be taken or used without consent. Suleyman considers these cases a “gray area” that must be dealt with in court. He mentions that there are other people who had also used that kind of content without authorization. Creators might not even know anything about the use of the content, because it is not so easy to determine.

With no firm AI legislation currently in place, cases of this nature are being dealt with separately and with different results. However, the legal boundaries between fair use and “theft” of publicly available content are still unclear when it comes to training AI services.


[ad_2]
Source link

Galaxy Watch 7 may be able to track early signs of heart attack & more

0
[ad_1]

Samsung is all set to take covers off its next-gen foldable smartphones – the Galaxy Z Flip 6 and Z Fold 6 – at the Unpacked event on July 10. The company is also rumored to unveil a couple of smartwatches including the Galaxy Watch 7 and Watch 7 Ultra or Watch Ultra at the same event.

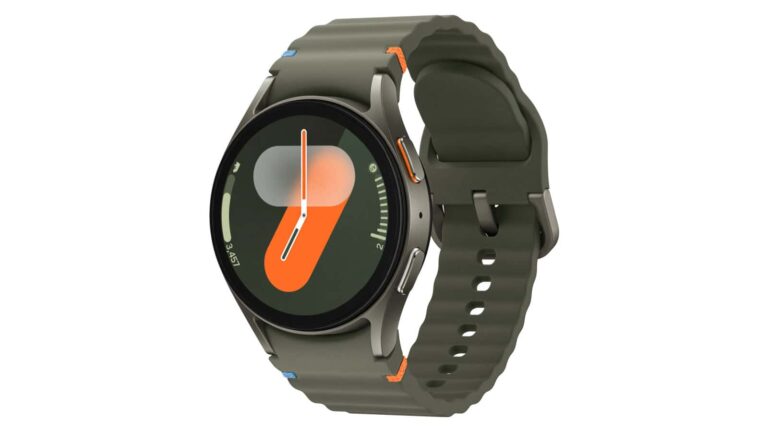
Ahead of the launch, the alleged photos and specs of the Galaxy Watch 7 series have already leaked. Now, a new leak suggests that the Galaxy Watch 7 could track early signs of heart attack, stroke, diabetes, and more.

The Watch 7 could offer an AGE index feature to track early signs of age-related diseases

Folks over at Android Authority have found a UI for a new feature called the AGEs (Advanced Glycation Endproducts) index in the Samsung Health app. This feature could enable the Watch 7 series to track early signs of age-related diseases. There are clues in the code regarding how the brand could deliver some sort of tracking for cardiovascular risk. The company will implement the AGEs index feature to provide advanced health tracking.

AGEs are thought to play an essential role in the development of chronic age-related diseases. They are linked to various health conditions like diabetes, stroke, and heart attack. With the AGEs index feature, users of Watch 7 could create an index of data gathered by their wearable. It will be available on their smartphones with the Samsung Health app.

The upcoming Galaxy smartwatches could measure AGEs optically and non-invasively

It looks like the Galaxy Watch 7 series of smartwatches may be able to measure these AGEs optically and non-invasively. The readings from the AGEs index will allow users to monitor the risk of various diseases like diabetes. The leaked UI in the Health app suggests that the company has partnered with DiagnOptics to develop this functionality.

Besides the AGE index-based advanced health tracking, the Watch 7 series could also feature blood glucose monitoring. However, there aren’t many details available about how the brand will implement it. That said, we will know more in just a matter of a few days, so watch this space for regular updates.

Watch 7 early signs AGEs


[ad_2]
Source link

A future Google Maps feature will help you co-navigate with friends and family

0
[ad_1]
Many drivers use online maps like Google Maps for navigation directions but they mostly aim to serve individual drivers. Google Maps provides no way to coordinate a group travel but according to a new patent filing, this may change in the future.

Currently, if you and a group of friends are going to the same destination in different cars, you probably either follow the lead car or every car relies on individual Google Maps directions. 

A new document hints at a Google Maps feature to facilitate a group of vehicles traveling to a common destination, whether from the same starting point or different locations. The feature will identify situations in which multiple users are going to the same place, either based on explicit requests from users or based on implicit signals such as calendar entries or text messages.

If you are thinking why anyone would want to use a multi-car navigation system instead of each driver using their own Google Maps app, it’s because there are many advantages to such a system. For instance, it will keep all the participants informed about the current location of other cars, so you won’t have to bother with regular texts to ensure you are not too far ahead or not too far behind. The system may even suggest a stop for a car that’s ahead of others so that the whole group reaches the destination at roughly the same time.

The system will also provide notifications about traffic and road conditions, which will be determined by the lead vehicle, and suggest stops along the way. If a car makes a detour, all others will be notified.

The document also states that the feature will also identify potential locations at which routes can merge and drivers can wait for each other. Once the desired location is reached, the system can also help with parking.

As is the case with all patents, we don’t know if the feature will see the light of the day.


[ad_2]
Source link