What is Static Network Address Translation?

0
[ad_1]
NAT

Static NAT is a type of NAT that maps one public IP address to one private IP address. Every time a device with a private IP address on your network tries to access the internet, its traffic will be routed through the NAT device and assigned the public IP address that is statically mapped to it.

What is Static Network Address Translation?

Static NAT is a type of NAT that maps one public IP address to one private IP address. This means that every time a device with a private IP address on your network tries to access the internet, its traffic will be routed through the NAT device and assigned the public IP address that is statically mapped to it.

Static NAT is often used in small businesses and home networks where only one public IP address is available. This allows all of the devices on the network to share the same public IP address, which can save money on internet service costs.

Static Network Address Translation (NAT) is used to save IP addresses. It allows unregistered IP addresses from private IP networks to connect to the Internet.

NAT converts private (not globally unique) addresses in the internal network into legal addresses before they are sent to another network.

Sites that already have registered IP addresses for customers on an internal network may wish to hide those addresses from the Internet in order to prevent hackers from directly attacking clients. A degree of security is achieved by concealing client addresses.

How does Static NAT Work?

Static NAT routes network traffic from a static external IP address to an internal IP address or network. It generates a static translation of actual addresses to mapped addresses. Static NAT connects networking devices to the internet through a private LAN and an unregistered private IP address.

Static NAT defines a one-to-one mapping from one IP subnet to another. The mapping contains destination IP address translation in one direction and source IP address translation in the other.

The NAT device’s original destination address is the virtual host IP address, whereas the mapped-to address is the real host IP address.

Static NAT permits connections to originate from either side of the network, but translation is limited to one-to-one or between blocks of addresses of the same size. A public address must be assigned for each private address. No address pools are required.

Static NAT additionally allows the following sorts of translation:

  • To map multiple IP addresses and specified port ranges to a single IP address and a separate port range
  • To map a given IP address and port to another IP address and port

You should grasp the following terms to comprehend static NAT:

  • The Layer 3 interface that confronts the private network is known as the NAT inside interface.
  • The Layer 3 interface that faces the public network is known as the NAT outside interface.
  • Every address that occurs on the internal (private) part of the network is referred to as a local address.
  • Every address that appears on the network’s outer (public) ring is referred to as a global address.
  • A legitimate IP address is one that the Network Information Center (NIC) or service provider has assigned.
  • The IP address given to a host on the inside network is known as the inside local address. It is not necessary for this address to be a real IP address.
  • The IP address of an external host, as it appears on the internal network, is known as the “outside local address”. Given that it is assigned from an address space that may be routed on the internal network, it is not necessary that it be a valid address.
  • Inside global address: A valid IP address that, to the outside world, corresponds to one or more inside local IP addresses.
  • Outside global address: The IP address that the host owner has assigned to an outside network host. The address is a valid one that is chosen from network space or an address that can be routed.

What are the typical Scenarios where Static NAT is used? 

Static Network Address Translation (NAT) serves several functions, including providing low-cost internet access to small businesses and improving security by shielding private IP addresses from potential threats.

  • If only one public IP address is available, as in a small business or household network. This allows any device connected to the network to use the same public IP address, potentially lowering the cost of internet access. A small company with ten employees, for example, could use static NAT to provide internet access to all of them via a single public IP address.
  • To establish a static IP address on a device’s connection to the internet. This is frequently done for equipment such as web servers and file servers that must be accessed via the Internet. For example, a company may use static NAT to connect its web server to the internet so that users from all over the world can access its website.
  • To enhance the network’s security.  Static NAT can improve network security by shielding the network’s devices’ private IP addresses from the internet. As a result, attackers may find it more difficult to target specific network devices. A home user, for example, can use static NAT to hide their computer’s private IP address from the internet, making them less likely to be the target of hackers.

A use case for static NAT is shown here:

  • A tiny company is made up of one public IP address and ten people. The company would like to provide each employee with a public IP address that they can use to connect to the internet.
  • The company configures and installs a NAT device to use static NAT on its network. The NAT device is assigned a public IP address, and each employee’s PC is assigned a private IP address.
  • Traffic from a worker’s PC attempting to connect to the internet is routed through the NAT device. The NAT device then sends the traffic to the internet using the employee’s computer’s statically assigned public IP address.
  • This allows all of the staff to access the internet without difficulty using the same public IP address. 

How does Static NAT Enable External Access to Internal Network Resources?

Static NAT is a network traffic mapping technique that maps traffic from a fixed external IP address to an internal IP address or network. It establishes a one-to-one mapping from one IP subnet to another, including destination IP address translation in one direction and source IP address translation in the other. Static NAT connects networking devices to the internet via a private LAN with an unregistered private IP address.

The following steps are required to enable external access to internal network resources via Static NAT:

  1. Configure private/public IP address mapping by using the inside static PRIVATE_IP PUBLIC_IP command.
  2. When an external host sends a packet to the public IP address, the router (acting as the NAT device) will translate the packet to the server’s private IP address.
  3. When the server responds, the router will untranslate the packet back to the original IP address of the external host.
  4. The Static NAT allows the internal host with the private IP address to be accessed by an external host.

Here is how static NAT enables external access to internal network resources:

Topology:

  • Inside network: This is the private network that is behind the NAT device. It contains the devices that need to access the internet.
  • Outside network: This is the public internet. It is the network that the inside network can access through the NAT device.
  • NAT device: This is the device that performs the static NAT translation. It has two interfaces: one for the inside network and one for the outside network.

Static NAT configuration:

The following is the static NAT configuration for this topology:

ip nat inside source static 192.168.1.100 10.0.0.1

This command maps the private IP address 192.168.1.100 to the public IP address 10.0.0.1. This means that any traffic from the inside network with a source IP address of 192.168.1.100 will be translated to the public IP address 10.0.0.1 when it goes out to the internet.

How it works:

When a device on the inside network with the IP address 192.168.1.100 tries to access the internet, the NAT device will translate the traffic to the public IP address 10.0.0.1. The traffic will then be sent out to the internet using the NAT device’s public IP address.

The important point to remember is that a Static NAT translation is bidirectional. Whether the first packet was sent by an internal or external host, it would “pass through” the Static NAT. Static NAT allows connections to be established from either side of the network, but translation is restricted to one-to-one or between blocks of addresses of the same size. For each private address, a public address must be assigned.

What are the differences between Static NAT and Dynamic NAT?

Static NAT is a type of Network Address Translation (NAT) in which one public IP address is mapped to one private IP address. This means that whenever a device on your network with a private IP address attempts to connect to the internet, its traffic will be routed through the NAT device and assigned the public IP address that is statically mapped to it.

Dynamic NAT is a type of NAT in which public IP addresses are dynamically assigned to private IP addresses. This means that the public IP address assigned to a device on your network may change based on the traffic sent and received.

The two types of Network Address Translation (NAT) techniques used to translate private IP addresses to public IP addresses are static NAT and dynamic NAT. The following are the distinctions between static and dynamic NAT:

Static NAT:

  • Allows for permanently mapping an internal address to a specific public address.
  • Is useful when a network device within a private network requires internet access.
  • Creates a one-to-one mapping from one IP subnet to another.
  • Allows connections to be established from either side of the network.
  • The translation is limited to one-to-one or between identical address blocks.
  • A public address must be assigned to every private address.

Dynamic NAT:

  • Dynamically converts private IP addresses to public IP addresses.
  • Allows for translating unregistered private IP addresses into registered public IP addresses from a pool of public IP addresses.
  • Creates a one-to-one mapping from a group of public IP addresses known as the NAT pool between a private IP address and a public IP address.
  • The router selects an address from the global address pool that is not currently assigned.
  • The dynamic entry remains in the NAT translations table as long as traffic is exchanged.
  • The entry expires after a period of inactivity, and the global IP address can be used for new translations.
  • Two sets of addresses are required on the router: the inside addresses that will be translated and a pool of global addresses.

The following table summarizes the key differences between static and dynamic NAT:

Feature

Static NAT

Dynamic NAT

  • Public IP address mapping
  • One-to-one
  • Many-to-one
  • Use cases
  • Small businesses and home networks
  • Large networks
  • Security
  • Can improve security by hiding private IP addresses
  • Does not improve security
  • Performance
  • Can reduce performance by routing all traffic through the NAT device
  • Can improve performance by reducing traffic through the NAT device

[ad_2]
Source link
How “EDR Extra Strength” simplifies traditional EDR complexity

0
[ad_1]

Learn how EDR Extra Strength can help IT teams save time, money, and stop more threats.

Traditional Endpoint Detection and Response (EDR) today has a three-fold complexity problem—with big consequences.

First, complexity in EDR deployment causes long delays, directly impacting ROI and leaving organizations vulnerable to breaches. In fact, almost 10 percent of small security teams cite such complexity as a primary reason for deployment setbacks. (Global Surveyz 2022)

Second, lack of integrated security tools within an EDR can lead security teams to overcompensate by buying and operating additional security platforms. This complexity multiplies operational overhead and creates gaps in security.

Dealing with day-to-day EDR complexity is a third challenge. A survey of 200 CISOs by Global Surveyz found that nearly half (45 percent) of small IT teams flag issues like excessive alerts and multiple dashboards as chief product concerns, culminating in alert fatigue and drops in productivity. 

To save time, money, and to stop more threats, IT teams need an EDR that resists complexity—one that’s easy to implement and straightforward to operate.

What is EDR Extra Strength?

The solution is EDR Extra Strength.

EDR Extra Strength combines the award-winning threat detection of Malwarebytes EDR, with Alert Prioritization and Guided Remediation, and Vulnerability & Patch Management. EDR Extra Strength offers a singular, cost-effective strategy for organizations looking for in-depth security.

Instead of navigating through multiple platforms, each with their own separate cost and learning curve, organizations can now harness the unified strength of all-in-one protection with EDR Extra Strength—boosting visibility and protection at a cost that makes sense.

Deployment

With the average deployment timeline for traditional EDRs stretching up to 18 months for small security teams, the need for a swifter solution is clear.

Simply put, smaller teams just can’t afford extensive learning curves, which perhaps is why, from a financial standpoint, they prioritize implementation costs (50 percent) in their endpoint security more than anything else. (Global Surveyz) 

Malwarebytes EDR, the cornerstone of EDR Extra Strength, takes the complexity out of EDR deployment as evidenced by an average time to become fully operational that is two times shorter than the industry average.

Cloud-hosted on the Nebula platform, EDR Extra Strength core technology can deploy within minutes and has won multiple G2 awards for its unique combination of rapid time to go live and time to ROI, all delivered via an agent deployed with a small footprint.

Integration

Managing too many platforms is challenging. Each additional security tool requires its own set of configurations, updates, and management protocols, ultimately translating to longer response times, inefficient workflows, and an inability to have a unified view of the threat landscape.

According to Global Surveyz, 77 percent of small security teams ranked a ‘one-stop’ product with the ‘most integrated’ features as one of their top considerations when choosing a new security technology. In addition, 80 percent of CISOs recognize vendor consolidation as an avenue for more efficient security. 

And, once you consider that over 5 percent of breaches in 2022 came from known vulnerabilities that had yet to be patched—and that the average cost of those breaches was $4.17 million—it goes without saying that Vulnerability and Patch Management needs to be part of any all-in-one security solution today.

By combining Endpoint Protection (EP), EDR, and an award-winning Vulnerability and Patch Management solution, EDR Extra Strength gives IT teams the ‘one-stop’ product they need to streamline detection and response through a single pane of glass.

Day-to-Day Operation

It’s not hard to see why Gartner ranks ease-of-use as the top buying priority in the endpoint protection platform. Daily struggles related to navigation, excessive alerts, and an inability to view the full picture of a digital environment are often symptoms of a complicated-to-use EDR.

The core technology of EDR Extra Strength has won awards for end-user focused attributes (Ease of Use, Meets Requirements, Quality of Support), and administration-specific attributes (Ease of Admin, Ease of Setup, Ease of Doing Business With). 

In addition, EDR Extra Strength provides meaningful contextualization for analyst actions with its Alert Prioritization and Guided Remediation feature, helping to reduce alert fatigue and time-to respond associated with complex EDR. Learn more about Alert Prioritization and Guided Remediation here.

Try EDR Extra Strength today

The complexity challenges in EDR deployment, integration, and day-to-day use have big consequences for organizations, ultimately leading to wasted time and money.

EDR Extra Strength addresses this three-fold EDR complexity by combining multiple effective and easy-to-use products under one hood, harnessing the power of award-winning EDR, Vulnerability and Patch Management, and Alert Prioritization and Guided Remediation to boost security without added complexity.

Learn more about EDR Extra Strength here.


[ad_2]
Source link

Level up your gaming PC with this Skytech desktop that’s $200 off

0
[ad_1]

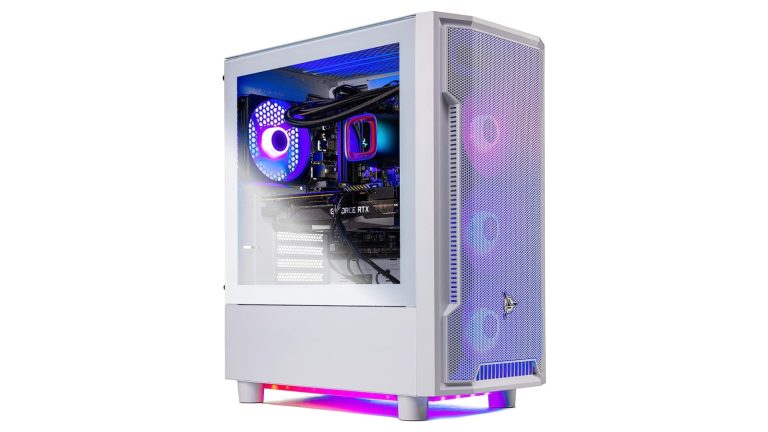
A gaming PC can be an expensive investment if you get a rig with high-end specs, but that doesn’t mean you can’t save money, like on this deal from Skytech on the Archangel desktop. Normally $1,399.99, you can currently get the Skytech Archangel PC for $1,199.99. Saving you $200 on a desktop with performance-heavy specs.

Now this is a prebuilt machine so if you’re new to PC gaming or have just never built one yourself before, this is a really great solution. It comes with some pretty good specs including the NVIDIA GeForce RTX 4060 Ti GPU. As well as an Intel Core i7-12700F CPU, a 1TB NVMe SSD, 16GB of DDR4 3200MHz RAM, and a 600W Gold power supply.

Everything is wrapped up in a fairly sizeable mid-tower case with lots of room for airflow. Speaking of airflow, there’s multiple fans. One rear fan and three front fans to really push air through the system and keep things cool. There’s an AIO in there too to help keep the CPU temps down. All-in-all it’s a nice little setup for the price. And because it’s a desktop PC, you can easily get to and swap out parts if you ever need to replace parts or want to upgrade.

Plus, the RGB lighting is a nice bonus if you like that style. RGB can be found on all the fans as well as the AIO, RAM, and underside of the case. And the tempered glass panel on the side ensures you can see everything. If you want to snag this awesome gaming desktop deal for yourself you can do so at the link below.

Skytech Archangel Gaming PC – Amazon


[ad_2]
Source link

US Air Force wants to invest billions in AI-controlled drones

0
[ad_1]

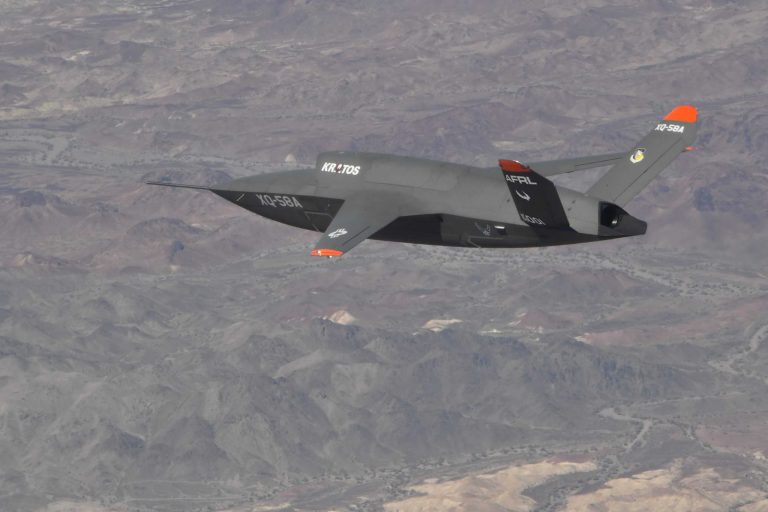
The US Air Force announced its plans to build a fleet of XQ-58A Valkyrie AI-controlled drones, Engadget reports.

When it comes to using cutting-edge technologies in warfare, the United States Army is the first name that comes to mind. As the most powerful army in the world, the US Army has a bright record of investing in new technologies. This time, the Pentagon has requested a $6 billion federal budget to build a fleet of AI-controlled drones.

The budget will be spent on building a fleet of XQ-58A Valkyrie uncrewed aircraft built by Kratos Defense & Security Solutions. The XQ-58A is 30 feet long and weighs 2,500 pounds. It can also carry up to 1,200 total pounds of weapons. While the Kratos CEO already said each XQ-58A drone costs $6.5 million, a bulk order might lower the price to $3 million.

The US Air Force invests $6 billion on a fleet of AI-controlled drones

The XQ-58 Valkyrie is still an experimental stealth aircraft, but the army hopes to have an operational fleet of them as soon as possible. The drone has already operated in a three-hour demonstration at Elgin Air Force Base. This AI-controlled drone will be used in combat missions to support F-22 and F-35 aircraft, which cost $143 million and $75 million.

The XQ-58 Valkyrie is a product of USAF’s Low Cost Attritable Strike Demonstrator (LCASD) program and can be used for surveillance and resupply actions as well. Additionally, the drone’s weapons and instructions are adjustable according to the mission.

The USAF test pilot, Major Ross Elder, called the XQ-58 Valkyrie testing a “very strange feeling.” He added, “I’m flying off the wing of something that’s making its own decisions. And it’s not a human brain.” Of course, the USAF asserted that drones remain under human control.

The $6 billion budget requested by the Pentagon is for the next five years and needs Congress’s approval. The program might require an initial budget of $3.3 billion in 2024.


[ad_2]
Source link

Crooks Using Stealers and Stolen Cookies to Hack Airbnb Accounts

0
[ad_1]

The cybersecurity researchers at SlashNext have unveiled a concerning attack trend that targets unsuspecting users who own Airbnb accounts. This trend involves a wide range of malicious techniques, though not entirely new, that pose a significant threat.

KEY FINDINGS

  • Cybercriminals are using a variety of methods to gain unauthorized access to Airbnb accounts, including stealers, stolen cookies, and account checkers.
  • Once cybercriminals have gained access to an Airbnb account, they can use it to book properties, make fraudulent purchases, or even steal the victim’s personal information.
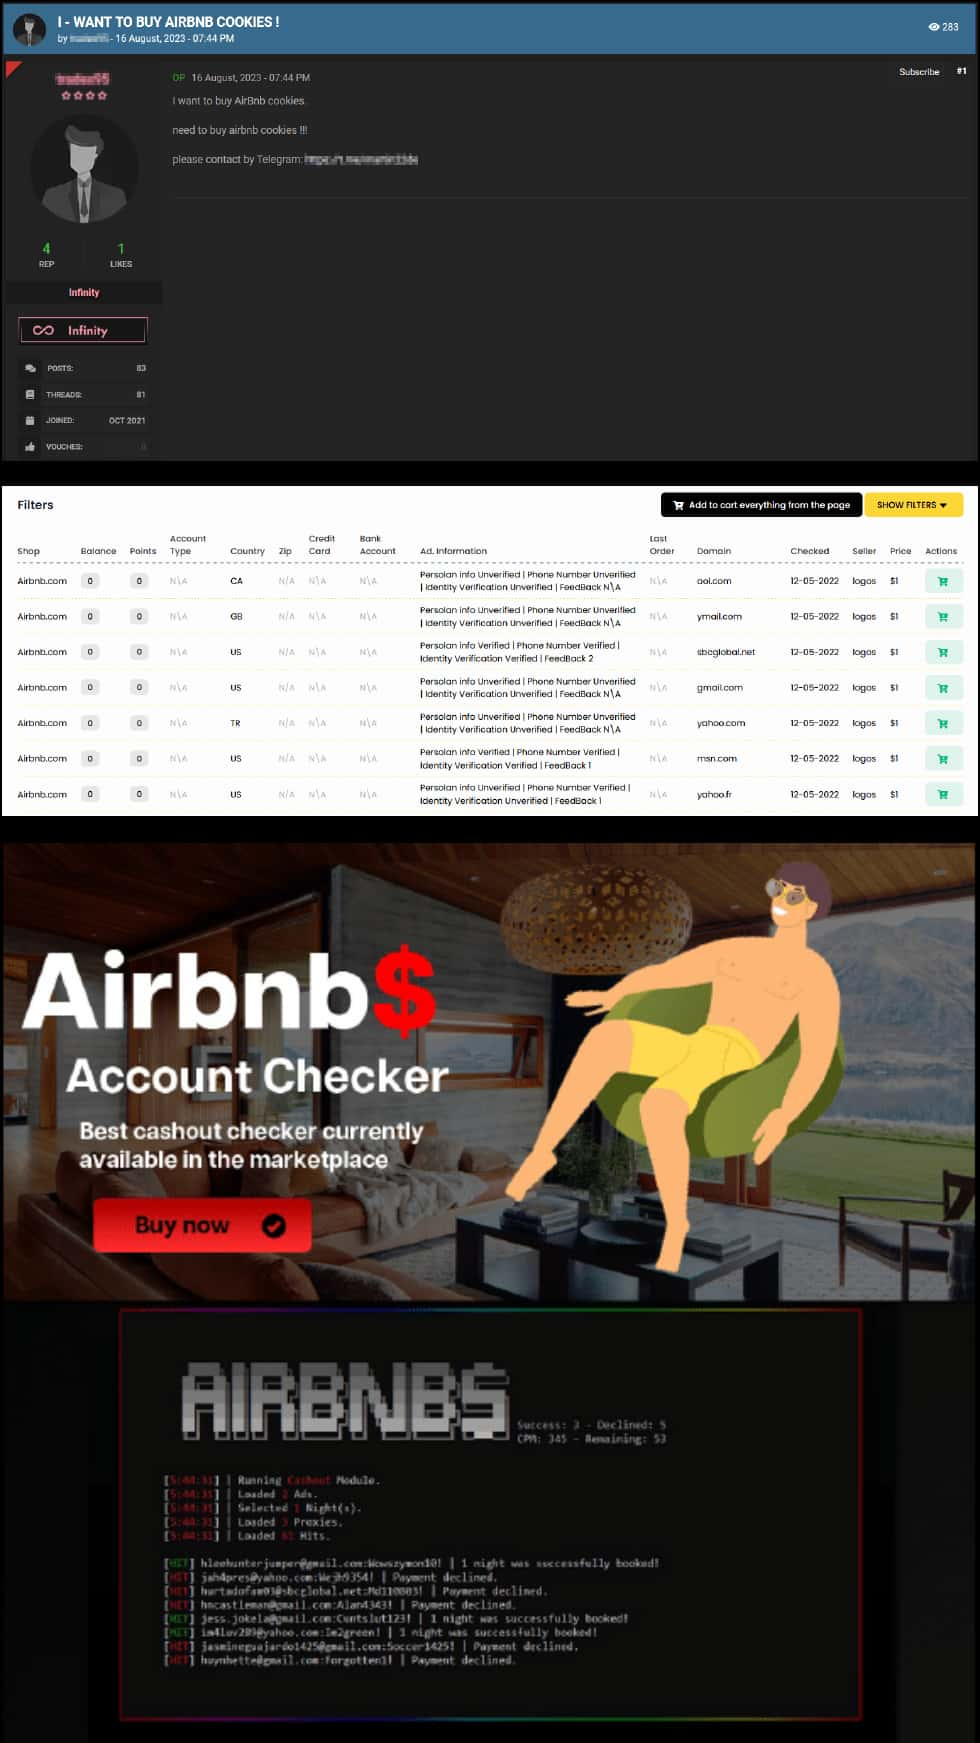
  • The scale of the problem is significant, with thousands of Airbnb accounts available for purchase on digital stores for as low as one dollar.
  • To protect yourself from this type of fraud, it is important to take steps to secure your Airbnb account, such as using a strong password and enabling two-factor authentication.
  • You can also help to protect yourself from Airbnb scams by only booking with hosts who have a good reputation and positive reviews, being wary of offers that seem too good to be true, and never giving out your personal information to anyone you don’t know and trust.

Cybercriminals are constantly finding new ways to exploit popular online platforms, and Airbnb is no exception. In a recent investigation by SlashNext cybersecurity firm, researchers found that cybercriminals are using a variety of methods to gain unauthorized access to Airbnb accounts, including stealers, stolen cookies, and account checkers.

Once cybercriminals have gained access to an Airbnb account, they can use it to book properties, make fraudulent purchases, or even steal the victim’s personal information. In some cases, cybercriminals have even used stolen Airbnb accounts to commit identity theft.

The scale of the problem is significant. In the SlashNext investigation, researchers found that thousands of Airbnb accounts were available for purchase on digital stores for as low as one dollar. This suggests that cybercriminals are regularly stealing Airbnb account information and selling it on the black market.

A recent blog post released by cybersecurity firm SlashNext sheds light on the audacious tactics employed by cybercriminals to exploit Airbnb for their nefarious activities.

Stealers

Cybercriminals harness a breed of malicious software (malware or trojan), aptly named “stealers,” to extract sensitive information like usernames, passwords and other sensitive logs. from a targeted device. Once collected, these logs are typically routed to servers controlled by crooks.

The deployment of stealers is carried out through a variety of techniques, ranging from manipulating human psychology (social engineering) to exploiting software vulnerabilities and leveraging deceptive advertising (malvertising).

Beneath the digital underbelly lies a clandestine market where cybercriminals can purchase and vend unauthorized access to devices, referred to as “bots,” “installs,” or “infections,” en masse.

For those willing to invest, cybercriminals can swiftly acquire a repository of thousands, if not tens of thousands, of devices teeming with stealers.

Targeting web application account information across most browsers, stealers neatly package their loot within a structured format. This format comprises columns and rows, encapsulating a slew of data fragments—names, credit card particulars, and more. Aside from harvesting login credentials, stealers can also hijack cookies.

Cookies: A Gateway to Illicit Access

Cookies, unobtrusive data packets housing users’ online preferences and activities, have unwittingly become pawns in the hands of cybercriminals. These crooks thrive on stealing, trading, and buying Airbnb account cookies on various illicit forums. Armed with these ill-gotten tokens, cybercriminals temporarily breach Airbnb accounts without the need for legitimate usernames or passwords.

Imagine a scenario where cybercriminals purchase a trove of stolen Airbnb cookies, load them onto their browsers, and slip into victims’ accounts undetected. Armed with this unauthorized access, they can masquerade as legitimate users, booking properties or orchestrating other unauthorized transactions without triggering any alarms. It’s imperative to note that such session cookies possess a brief lifespan, compelling cybercriminals to act swiftly.

Monetizing Stolen Data

With user accounts compromised and stolen cookies in their arsenal, cybercriminals pivot toward monetizing. A common practice involves directly peddling stolen account data and cookies to other crooks. This trade occurs on online forums, dark web markets and even through Telegram channels.

According to SlashNext, the dark web and underground platforms are filled with thousands of Airbnb accounts on sale, a shocking devaluation reducing each account’s worth to a mere dollar.

Evidently, the scale of Airbnb account heists has created the emergence of “account checkers”—automated tools that systematically scrutinize Airbnb credentials stored in a text file.

The modus operandi behind account checkers is straightforward: threat actors input a text file crammed with stolen credentials, and the checker discerns the valid from the defunct. Some advanced iterations of these tools even execute specific actions, like making fraudulent bookings.

With a “passion” for innovation, cybercriminals have even initiated a service slashing up to 50% off Airbnb bookings. The profusion of interest in these services is evident, with forum threads racking up tens of thousands of views and hundreds of replies.

The unsettling reality is that cybercriminals have masterminded an array of techniques to exploit Airbnb’s popularity, leveraging stealers and purloined cookies to breach user accounts.

The stolen information is subsequently sold to other criminals or leveraged to offer discounted services on the black market. The rampant account theft underscores the pressing need for vigilance and proactive measures to counteract these insidious cyber threats.

Cybercriminals Using Stealers and Stolen Cookies to Hack Airbnb Accounts
Cybercriminals willing to pay for stolen Airbnb accounts – A popular market selling stolen Airbnb accounts – Airbnb account checker (Screenshots: SlashNext)

Protection

Hackread.com has compiled a list of steps that can help Airbnb users (or any unsuspecting user online) protect themselves against the growing trend of attacks.

  • Enable two-factor authentication.
  • Use a strong password and change it regularly.
  • Be careful about clicking on links in emails or messages from people you don’t know.
  • If you think your account has been compromised, immediately change your password and contact Airbnb customer support.

In addition to the tips above, here are some other things you can do to protect yourself from Airbnb scams:

  • Be wary of offers that seem too good to be true.
  • Only book with hosts who have a good reputation and positive reviews.
  • Never give out your personal information, such as your credit card number or passport number, to anyone you don’t know and trust.
  • If you have any concerns about a booking, contact Airbnb customer support.

However, the best defence against cybersecurity threats is using common sense. Therefore, employ it at all times.


[ad_2]
Source link
Stealthy Android Malware Attacking Mobile Users

0
[ad_1]
Stealthy Android Malware

A recently discovered Android Trojan, dubbed “MMRat,” poses a serious threat to mobile banking security. Unlike other forms of malware, this Trojan is designed to evade detection from traditional antivirus software.

The security experts at TrendMicro have identified the Trojan as AndroidOS_MMRat.HRX, warning users to be cautious when downloading new apps or accessing their banking information from their Android devices.

This group has been committing bank fraud by targeting mobile users in Southeast Asia since late June 2023.

The sophisticated malware, operating under the package name com.mm.user, is equipped with advanced capabilities, including capturing user input, remote device control, and data exfiltration.

Infiltration and Distribution

MMRat utilizes deceptive phishing websites, posing as legitimate app stores, to distribute its payload. 

These phishing sites are tailored to specific language demographics, suggesting a targeted approach to victim selection. 

The exact mechanism of how these malicious links find their way to victims’ devices remains unclear. One notable aspect of MMRat’s infiltration is its complete evasion from detection. 

Even on VirusTotal, the malware has remained undetected, underscoring the effectiveness of its tactics.

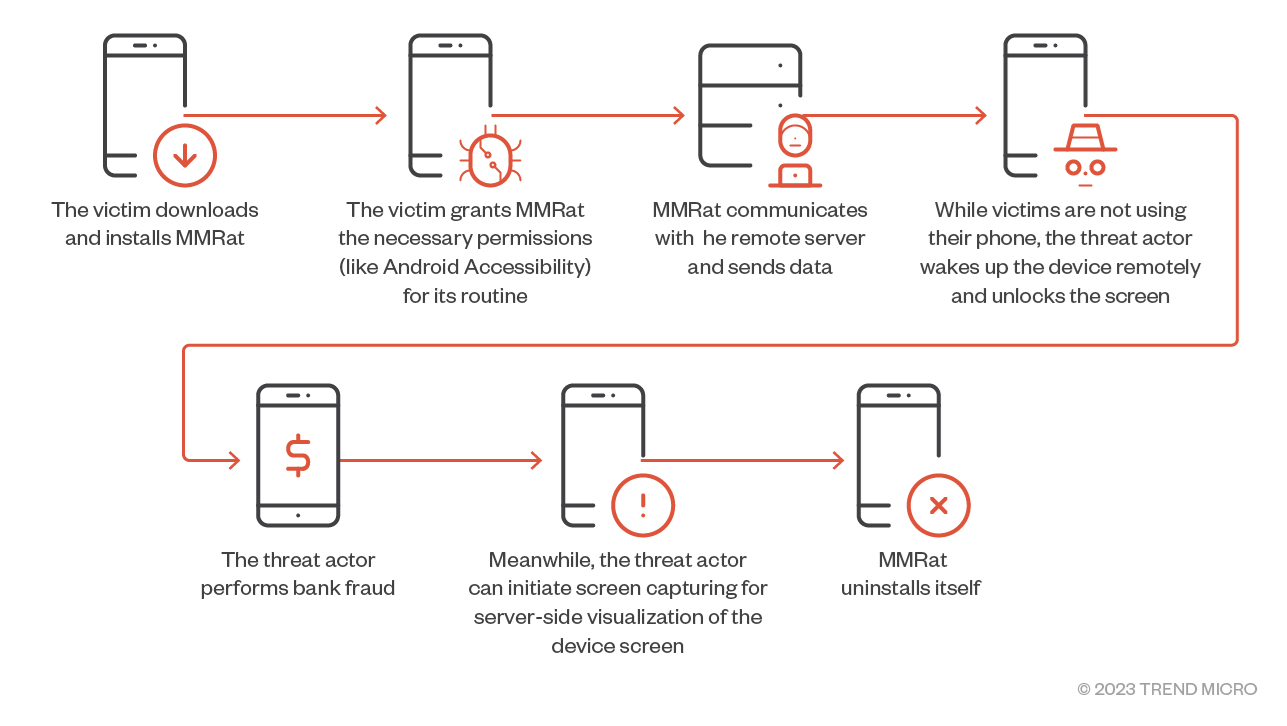
The sequence of events involving MMRat’s bank fraud operations unfolds as follows:

  1. Victim downloads and installs MMRat.
  2. Victim grants necessary permissions.
  3. MMRat establishes communication with a remote server, sending substantial amounts of data, including personal and device-related information.

The threat actor can remotely wake up the device, unlock the screen, and initiate bank fraud. Additionally, they can visualize the device screen in real-time via screen capturing.

After accomplishing its fraudulent objectives, MMRat uninstalls itself, leaving minimal traces on the system.

             The MMRat attack sequence

Key Features of MMRat

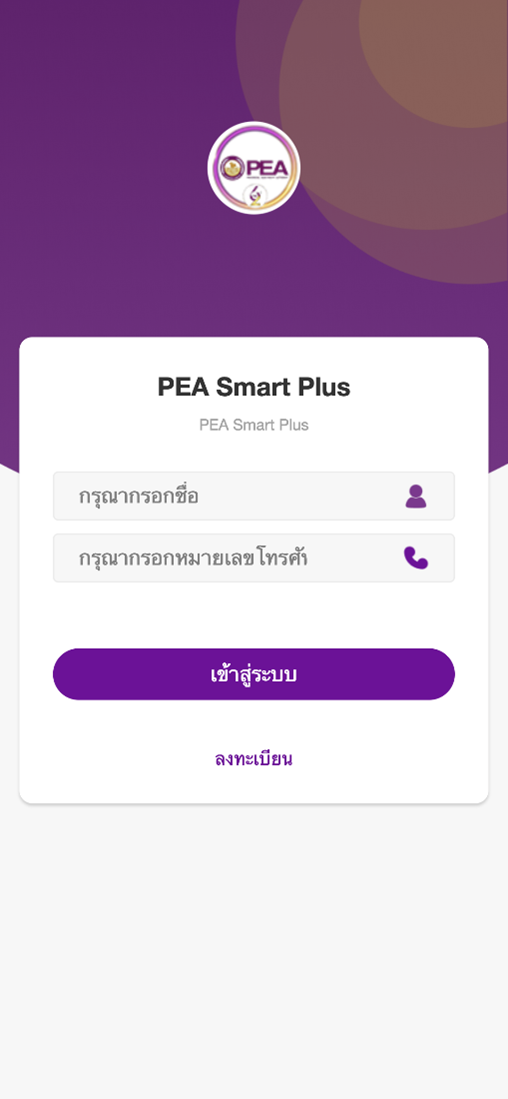
Impersonation and Persistence MMRat disguises itself as an official app, presenting victims with phishing websites upon launch. It establishes a receiver for system events, ensuring persistence by launching a 1×1-sized pixel activity.

         Fake login website displayed by WebView

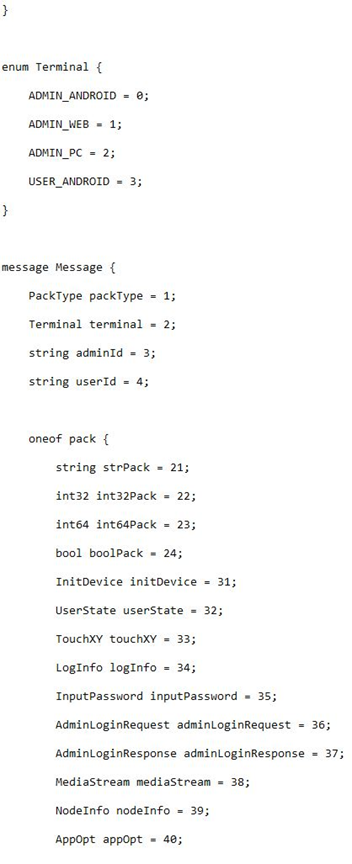
Network Communication MMRat communicates with a remote server through different ports, using a customized command-and-control (C&C) protocol based on protocol buffers (Protobuf). This unique approach enhances data transfer efficiency, which is particularly useful for transferring large data volumes.

The Protobuf schemas used for C&C communication

User Terminal State MMRat employs Android Accessibility to capture user actions and screen content. This unconventional method focuses on text data and bypasses the FLAG_SECURE protection.

Screen Capturing MMRat captures real-time screen content via the MediaProjection API and the “user terminal state” approach. It can stream screen content to a remote server in real-time, providing the threat actor with a live view of the device.

Remote Control The malware uses the Accessibility service to remotely control the victim’s device remotely, performing actions like gestures and inputting text. This aids in bank fraud execution.

Document
FREE Demo

Implementing AI-Powered Email security solutions “Trustifi” can secure your business from today’s most dangerous email threats, such as Email Tracking, Blocking, Modifying, Phishing, Account Take Over, Business Email Compromise, Malware & Ransomware

Preventive Measures

To safeguard against MMRat and similar threats, users are advised to:

  1. Download apps only from official sources, such as Google Play Store or Apple App Store.
  2. Regularly update device software to benefit from security enhancements.
  3. Exercise caution while granting accessibility permissions and scrutinize app permissions.
  4. Install reputable security solutions on their devices.
  5. Be vigilant with personal and banking information shared online.

Keep informed about the latest Cyber Security News by following us on Google News, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

One UI 5.1.1 update reaches Samsung Galaxy Z Fold 2 and more

0
[ad_1]

Samsung‘s One UI 5.1.1 update is now available for a few more foldable devices. The company has released the update for the Galaxy Z Fold 2, Galaxy Z Flip, and Galaxy Z Flip 5G, adding new features and functional improvements to the aging foldables.

Samsung introduced One UI 5.1.1 with its latest foldables and tablets last month. The Galaxy Z Fold 5, Galaxy Z Flip 5, and Galaxy Tab S9 series all run the new One UI version out of the box. The company is now pushing the new features to eligible older models.

As of this writing, the Galaxy Z Fold 2 is getting the One UI 5.1.1 update in Asia, Europe, and Australia. The new firmware build number for the phone in these regions is F916BXXU4KWH7 (F916NKSU2KWH7 in South Korea). Samsung will expand the rollout to the US and other remaining markets soon.

The Galaxy Z Flip and Galaxy Z Flip 5G are also initially picking up the One UI 5.1.1 in these markets. The updated build numbers for the two variants of the original clamshell foldable are F700FXXUDKWH7 and F707BXXUAKWH7, respectively. A wider rollout for these phones should also follow shortly.

As far as the new features are concerned, Samsung is making it easier to switch from pop-up view to split screen on foldable smartphones. The taskbar can also now show more recent apps, while the Recents screen offers better app previews. The Flex Mode panel works with more apps as well. You can see the full official One UI 5.1.1 changelog here.

A bunch of budget and mid-range Galaxy tablets will get One UI 5.1.1

With the Galaxy Z Fold 2, Galaxy Z Flip, and Galaxy Z Flip 5G getting One UI 5.1.1, Samsung is done pushing the latest One UI version to its folding phones. It has already updated the Galaxy ZF Fold 4, Galaxy Z Flip 4, Galaxy Z Fold 3, and Galaxy Z Flip 3 to One UI 5.1.1. The rollouts may be limited to select markets, but that’s a different matter. All eligible users will get the update over the next few days.

Meanwhile, Samsung still has some tablets waiting for One UI 5.1.1. So far, it has only pushed the update to its eligible flagship models — Galaxy Tab S8 series and Galaxy Tab S7 series. The company has confirmed that the update will also be available to the Galaxy Tab S6 Lite, Galaxy Tab A8, Galaxy Tab A7 Lite, Galaxy Tab Active 3, and Galaxy Tab Active 4. It will gradually cover them all with One UI 5.1.1 in the coming weeks.


[ad_2]
Source link

Take a look at the iPhone 15 Pro wallpapers in this latest mockup

0
[ad_1]

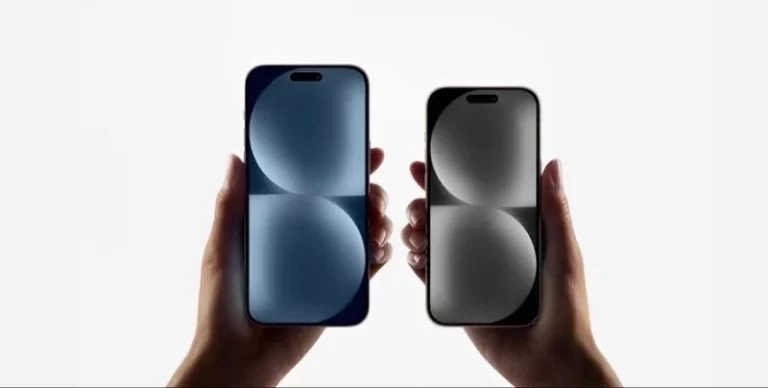
Yesterday, Apple sent out invites for the iPhone 15 event on September 12. So now we’re starting to see more leaks and mockups ahead of the event. That includes a concept render from William Faix, who was able to transpose the marketing material from the iPhone 14 Pro models.

So this wallpaper here uses the same sort of style as the iPhone 14 Pro wallpapers, but it also uses the colors from the Apple logo in the invite that was sent out yesterday. The wallpapers look pretty subtle, and actually look really good. So there’s a good chance that these could be nearly identical to what actually ships on the iPhone 15 Pro models in a few weeks.

It also has a matte particle-like texture, which is coincides with the invites from Apple. And that’s supposed to be a nod to the texture of the new titanium chassis on the iPhone 15 Pro.

iPhone 15 Pro launches with USB-C on September 12

The iPhone 15 Pro is set to be announced, alongside the iPhone 15 and Apple Watch Series 9, on September 12. The event will be taking place at Apple Park in Cupertino and will start at 10AM PT, as it always does. This is set to be a big event, but not as big as previous ones.

There’s quite a few things that we are expecting to be announced at this event. That includes the iPhone 15 series, Apple Watch Series 9, Apple Watch Ultra 2, and we could see some updates to AirPods and HomePod – mostly adding USB-C.

However, don’t expect to see a new iPad at the event. Those usually come in October alongside new Macs. Apple typically does two fall events to refresh its lineup, and this year we’re expecting to see M3 Macs in October along with a new iPad Mini and maybe a new iPad Pro, though that’s rumored more for next year with a new redesign.


[ad_2]
Source link

Amazing in just about every way!

0
[ad_1]

The latest Galaxy phones, Pixel phones, and iPhones are usually lauded as the most exciting phones of the year. That’s true; they’re exciting, but they’re not interesting. A lot of the time, it’s the underdogs who churn out the most interesting handsets; the obscure companies that produce phones that are worth much more than their price tag will indicate.

Infinix is one of those underdogs. This is a pretty obscure Chinese smartphone OEM, but that doesn’t mean that it doesn’t deserve the spotlight. We were given the opportunity to review the Infinix Note 30 Pro.

This is a more budget-friendly phone than the premium options out there, but as you’ll see, that doesn’t mean that it doesn’t deserve your attention. Sometimes, price is just a number, and the fine line between premium and mid-range can blur. Let’s dive into the review of the Infinix Note 30 Pro.

Infinix Note 30 Pro Review: Build and design

I repeat: Sometimes, price is just a number, and that became evident when I first picked up this phone. When making a budget-friendly handset, the premium feeling is usually the first thing to take a hit. The Infinix Note 30 Pro is an interesting case when it comes to the feel in the hand, and not for a bad reason.

Infinix Note 30 Pro 14

As far as first impressions go, I had a hard time believing that this phone cost less than $500 let alone $300 when I first picked it up. The Infinix Note 30 Pro has a certain heft to it that you don’t get with most budget phones. While it’s hefty, it doesn’t feel bulky. Infinix was able to reach that balance between hefty and heavy.

That’s just my first impression, however. What makes this phone an interesting case is the fact that it feels pretty premium without really using premium materials. If you take a second and appraise the phone, you’ll start to notice some things. Firstly, the frame of the phone is made from plastic. That’s not something that you’d see in a more premium phone, not even a modern Pixel A series phone.

Also, the back is made from plastic. However, it doesn’t really feel like it. It has the cool sensation that you’d get from a metal unibody phone.

The solid metal camera island only adds to the feeling. While the materials are more budget-oriented, Infinix was able to fake it and deliver a decently premium-feeling phone using modest materials.

Design

As for the design, the Infinix Note 30 Pro is having a bit of an identity crisis. It’s pretty yet industrial at the same time; flamboyant yet fortified. The phone is heavy and sturdy, and the metal camera package gives it a very no-BS look to it. The camera package is just this hunk of square metal on the back. It makes the phone look like a tank…

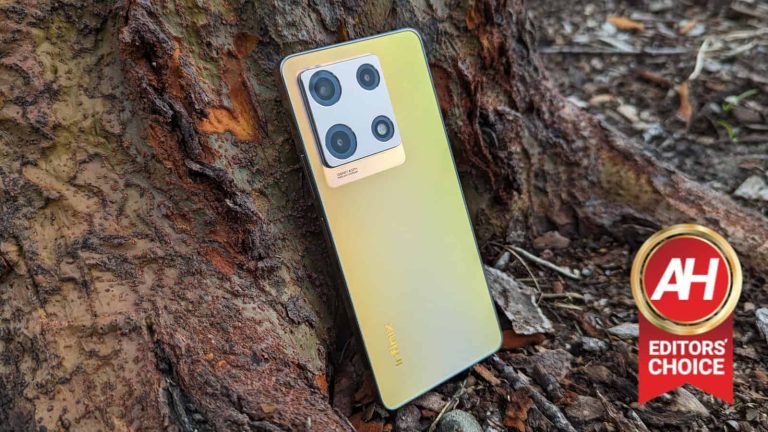
But, at the same time, it’s very pretty. There’s this pleasant soft-touch material on the back that plays with the light in such a pleasant way. Depending on the angle of the light, the phone will reflect several colors. You get hints of blue, teal, green, and rose gold. It’s really a sight for sore eyes. Also, the metal camera package is a delightful rose gold.

Infinix Note 30 Pro 13

Infinix Note 30 Pro Review: Display

It’s hard to put into words how beautiful this phone’s display is. I can say flat out that a display this amazing does not belong on a sub-$300 phone; yet, here we are. Again, price is just a number, and the delusions I had about what a $300 phone should cost were shattered the moment I laid eyes on this display.

It’s an OLED display, but it goes much deeper than that. Any company can slap an OLED display on a phone, but that doesn’t automatically make it good. The colors are punchy, the blacks are deep, the contrast is great, blah blah blah blah. We’ve heard that advertising copy before.

Colors

The beauty of this display goes beyond the hardware; Infinix did an amazing job calibrating this display. With the Bright-colored mode enabled, the colors are saturated, but that’s not what makes them beautiful. They’re punchy enough to dazzle the eye and make movies and videos pop, but they don’t go overboard. You can see where Infinix restrained itself. It struck the right balance to make the colors absolutely gorgeous.

While the colors have been tuned amazingly, some of the bolder shades of red will sizzle a bit. At full brightness, if you’re looking at photos of vibrant red roses, it might be a bit too much for the eyes. That’s the nature of the color red and digital displays, however.

Brightness

It’s summer here in Florida, so using a phone outdoors is just asking for a hard time. In the case of the Infinix Note 30 Pro, sunlight visibility is not a problem. It doesn’t get as bright as a Galaxy S23 Ultra, but it’s definitely up there at 900 nits. I have no trouble seeing the screen in the bright sun. I’d literally need to have the sun directly reflected on the phone’s screen to have a hard time.

Infinix Note 30 Pro 8

All in all, there’s no reason for this phone’s display to be this good! I can honestly say that this phone’s display trumps the display on the $1,000 Motorola Edge+. I even found it more enjoyable than the display on the Pixel 6. It goes toe-to-toe with the displays on some of Samsung’s phones, and that’s saying a lot. I can honestly say that the display is my favorite aspect of this phone.

Infinix Note 30 Pro Review: Speakers

Watching your media on this phone is great, but what about listening to it? The audio experience with this phone is pretty good, which is a bit of a letdown because the build quality and display are so great.

Sound quality

Out of the box, the speakers are nothing to write home about. They’re not great, but they’re not particularly good. The speakers are rather tinny, and they lack any sort of depth. They’re speakers to get the job done, and that’s what they do.

One thing I’ll say about the speakers’ out-of-the-box quality is that the highs cut through pleasantly. Higher tones come through nicely, and they’re great if you’re a person who’s into ASMR.

But, these speakers have a trick up their sleeves

If the speakers don’t sound like they’ll suit your interests, you can fix that. This phone has some tools that you can use to customize the audio quality. Starting off, there’s a handful of audio profiles that you can change the sound based on the listening scenario.

The Smart option will choose the profile based on the audio that’s playing. There’s a Music option that gives you a warmer, bassier, and wider sound. The Video setting will boost the high tones more so that voices cut through better. The Game setting will give you a more neutral profile.

Next, you can make adjustments to each sound profile. In the settings, you can choose the stereo settings. You’ll be able to choose whether you want a wide stereo sound, a more frontward sound, or a traditional sound.

Infinix Note 30 Pro 6

Under those settings, you can choose which aspect of the sound to boost. You can choose to boost the bass, the vocals, or the treble.

Last, but not least, there’s an EQ that you can use to further customize the sound. It’s a 5-band EQ that adjusts the 100Hz, 300Hz, 1KHz, 3KHz, and 10KHz bands. Each band can go between -5dB and +5dB. It’s pretty robust for a built-in EQ, and it can help you further fine-tune your sound.

After adjusting

After fine-tuning the sound, there was definitely a difference. The speakers definitely sounded better. However, the difference wasn’t like night and day. After making tweaks, I still felt that the speakers were lacking in depth. I’d say that the sound options do a good job, but they can’t make a pair of decent speakers sound great. That’s what the speakers are, decent. They’re not bad, but they’re definitely nothing to write home about.

Infinix Note 30 Pro Review: Battery

Back in the day, most mid-range phones were destined to have smaller batteries than flagships. However, things have changed; a ton of mid-rangers are rocking batteries as large as the latest Galaxy S phones. The Infinix Note 30 Pro is rocking a large 5,000mAh battery.

I was more than pleased with the battery life of this phone. I usually start off my day with a full battery. After that point, I’d typically have to charge it by the afternoon of the next day. It wasn’t uncommon for me to get a day and a half of moderate usage out of this phone. That consists of a ton of social media, a good amount of video-watching, and casual gaming.

On heavier days, days when I’d play games more religiously or be binge-watching content, I’d still have a hard time killing the battery before turning in for the night.

Charging

The Infinix Note 30 Pro comes with a charger in the box, and that’s a major plus for this phone. The charger is a 68W charging brick, and it can charge the phone very quickly. Charging from 0% to 100% doesn’t take much more than an hour. It also comes with 15W wireless charging.

Infinix Note 30 Pro Review: Performance

Yes, I’m going to say it again: Price is just a number. That statement is extremely true when talking about this phone’s performance. Honestly, if this was just a few years earlier, I’d be calling this phone a flagship killer (remember those things?).

The Infinix Note 30 Pro is using the MediaTek Helio G99 SoC. Now, we’ve all become accustomed to instantly associating MediaTek with poor performance. However, that’s not always the case, and the Infinix Note 30 Pro is proof of that. Infinix did a great job at optimizing the software for the chip.

Infinix Note 30 Pro 2

Navigation

Starting off with navigating the software, this phone just glides. Jumping from app to app and using said apps, I didn’t really notice any stutters or dropped frames. That’s not to say that they’re non-existent, as there is the occasional hiccup. Maybe the phone lags when rotating the screen for a fraction of a second; maybe it drops a frame when opening the app. However, those instances are few and far apart.

Usage

Also, when it comes to using the apps themselves, the story is the same. I didn’t stumble across any apps that could slow this phone down. With a processor like the Helio G99, you’d expect typical mid-range performance, but I think that this phone goes beyond that. It’s definitely in premium mid-ranger territory.

The performance is also helped by the smoothness of the 120Hz display. Gliding through the interface and using this phone with the 120Hz display just makes it feel that much more fluid. It gives you the experience of just picking up a phone and using it without any performance issues- like you’d get from a flagship phone.

Temperature

When using this phone for extended periods of time, it doesn’t really heat up too much. It gets warm, but it was never hot to the point where it felt uncomfortable. One thing to note is that the camera island is made from metal, and that could get quite warm. However, it’s more than manageable. It manages to keep cool using a VC liquid cooling system.

Infinix Note 30 Pro Review: Gaming

Gaming on this phone isn’t too bad. It’s like getting a B+ on a report. It’s not bad by any means, but it’s right on the cusp of greatness. Right off the bat, your run-of-the-mill 2D games will run like butter. Games like Sweet Sins 2, Fishing Paradiso, Dream Hopper, Dragon Ball Z Dokkan Battle, and so on will run with no problems. That’s to be expected because of this phone’s baseline performance.

Moving from 2D to simple 3D games doesn’t yield any different results. They run smoothly with no stutters or lag. These include games like Crash of Cars, Pocket World, Sonic Rush, and so on. Even the decently graphically intensive 3D game Sky: Children of The Light runs smoothly. If you’re going to be doing more casual gaming, then you won’t have any problems using this phone.

Infinix Note 30 Pro 5

Heavier gaming

Now, let’s crank up the graphics. There are games that tower above the rest in terms of graphics, and one of the best-looking games on the market is Genshin Impact. This game is pretty… and it’s pretty daunting. How does this phone perform against this title? Not bad, but not great.

When you load up Genshin Impact, which looks like it belongs on the PS3 or Xbox 360, you’ll see the phone struggle to keep up. However, this is if the graphical settings are turned to the maximum setting.

If you knock the graphical settings down to regular, then you’ll be able to get pretty smooth gameplay. Overall, if you knock the settings down to their lowest setting, you still won’t be able to get up to 60fps. So, with more graphically intensive games, you should expect the phone to chug just a bit.

The Infinix Note 30 Pro is definitely more for casual and light gaming. More graphically intensive games are definitely playable, but you should expect less-than-smooth gameplay.

Infinix Note 30 Pro Review: Camera

A big part of the smartphone experience is the camera, so let’s see if that large camera package on the back is just for show.

Details

Starting off with the details, the Infinix Note 30 Pro produced nicely detailed images. they come out reasonably sharp. They look great when they’re zoomed out. However, the phone does lean on the oversharpening a bit. It actually creates this weird spaghetti noodle effect when you zoom in closely.

Exposure/Dynamic range

Shots in the bright sun are well-exposed without being overexposed or underexposed. I’d say that the dynamic range is pleasing. I noticed a few times, however, when the exposure leaned on the bright side just a little. It’s not too bad, however. Just be prepared for a few extended highlights.

Colors

The colors produced by the Infinix Note 30 Pro are nice, but they have one minor flaw. They’re nicely saturated without going overboard. It has the classic issues with digital sensors in that properly exposing reds is difficult. However, the colors are nice overall.

The one minor drawback is that they tend to lean rather warm. The photos are noticeably warmer than the scene. They can almost change the whole feeling of the scene. I took a picture of some rocks on the ground. They’re grayish rocks in the midday sunlight. Instead of showing a bland and gray scene, it gave me this warm, almost desert-like scene. I’d prefer that the system focused more on color accuracy.

Infinix Note 30 Pro camera Sample (5)

Low light

The low-light performance with this phone isn’t amazing for the price, but it’s not too bad. I’d say that it’s as good as a flagship phone’s low-light performance from around 2016-2017. The quality degrades rather quickly when you turn down the lights. However, it still manages to keep the scene well-lit and it still retains the colors nicely.

Infinix Note 30 Pro Review: Software

The thing that differentiates this phone from most other phones in the West is the software. The Infinix Note 30 Pro is running a heavily skinned version of Android called XOS. It’s version 13.0.00, so it’s based on Android 13.

For the most part, the software is really good. It’s different, but it still remains intuitive. Infinix didn’t change too many things about the software, so if you’re used to using Android phones, you’ll feel right at home.

Infinix Note 30 Pro 3

There are a bunch of settings and features that you can dig through, so you’ll be able to tailor the software experience to your liking. This involves a bunch of gestures and home screen customizations.

There are a few complaints

The notification shade is split into two pages. You’ll swipe down from the top left of the screen to summon the notifications and the top right of the screen for the quick settings. You can swipe between them, but most Android users are used to having everything available on one screen.

Another issue has to do with compatibility. There are certain apps and services that will not work on this phone, and that might be because of the region this phone was made for. Just know that not every app from the Google Play Store will work on this phone.

The Infinix Note 30 Pro does come pre-loaded with a third-party app store called the Palm Store. you can use that, but it won’t have the same robust library of apps that the Play Store has.

Also, I could not set up Google Wallet, which was a major bummer.

Infinix Note 30 Pro Review: Additional and missing features

This phone has some features and additions that make the experience that much better. For starters, it comes with a 3.5mm headphone jack, so you won’t need to worry about charging it while listening to music. Also, there’s microSD card expansion.

On the side of the phone, there’s a fingerprint scanner on the power button. It’s super fast and accurate. Along with the fingerprint scanner, there’s also the option to use face unlock. The face-unlocking feature is very accurate and extremely fast. You can unlock your phone even if your face is at an angle. Using the lift-to-wake feature, you’ll simply have to lift your phone, and, within a second of you swiping your screen, the phone’s unlocked.

Infinix Note 30 Pro 7

Here’s a feature that you don’t see on many phones. If you need to frame a selfie in the dark, there’s actually an LED flash on the front of the phone along with the one on the back.

Another nice feature of this phone is reverse wireless charging.

What it’s missing

This phone has IP water and dust resistance, but it’s only IP53. This means that it can only survive if caught in the rain. It can not be submerged fully under the water. If that happens, then you risk damaging the phone.

Final verdict

Being a reviewer, I’ve come across the full spectrum of devices from premium masterpieces to downright trash. There’s often a recurring theme among these devices: the more expensive the device, the better.

Notice how I used the word “often” and not “always”. This is because every so often, I stumble upon a device that gives me so much more value than I initially expected. This is exactly how I feel about the Infinix Note 30 Pro. We’re conditioned to think that once a phone falls below the $300 line, it ceases to be a worthy handset; it’s just a phone to get you through the day.

Infinix Note 30 Pro 4

But, the Infinix Note 30 Pro completely smashes that notion. This phone is, in so many ways, much better than its price lets on. The display is drop-dead gorgeous, the design is pretty premium, the performance is snappy, the camera performance is strong, the software experience is great, and so on.

I can honestly say that the Infinix Note 30 Pro is one of the best phones I’ve reviewed, especially for this price. I highly recommend that you pick it up.


[ad_2]
Source link

Email Authentication Protocols: SPF, DKIM, and DMARC

0
[ad_1]
Email Authentication Protocols

Email communication is essential for personal and professional contact in the modern digital environment.

Email is widely used, making it a perfect target for cybercriminals, leading to increased phishing attempts, spam, and email spoofing.

Strong email security measures are becoming essential as these threats become more sophisticated. Email authentication techniques like SPF, DKIM, and DMARC are crucial in situations like this.

By authenticating the sender’s identity and confirming the accuracy of the received messages, these procedures act as the first line of protection against email-based threats.

This article will thoroughly review these three important email authentication methods, including their roles, how they cooperate, and why they are crucial for upholding a reliable and secure email communication infrastructure.

What are Email Authentication Protocols?

Secure email communications can be achieved through Email Authentication Protocols, standards, or technologies that validate the sender’s identity and protect the message’s integrity.

These standards aim to protect users from spam, phishing, and other malicious email-based assaults.

As a bonus, they make it less likely that a good email will be incorrectly deleted as spam or malware.

Here are the primary email authentication protocols commonly in use:

  • Sender Policy Framework (SPF)
  • DomainKeys Identified Mail (DKIM)
  • Domain-based Message Authentication, Reporting, and Conformance (DMARC)

Sender Policy Framework (SPF)

The Sender Policy Framework (SPF) is an email authentication technology developed to prevent spam.

By letting domain owners choose which mail servers can send emails on their behalf, SPF assists receiving servers in authenticating the sender of incoming messages.

For this purpose, the DNS records of the domain are consulted to ensure that the emails come from the addresses they claim to represent.

The Sender Policy Framework (SPF) aims to improve email security by limiting the possibility that an unauthorized sender may use a specific domain in the “From” address.

This helps keep the sender’s and the recipient’s inboxes free of unwanted messages and strengthens the confidence each party has in email.

You can Analyze and Detect SPF Issues using Trustifi’s SPF Record Checker Tool.

How It Works

  • Domain owners create SPF records showing trusted IP addresses and domains from which emails can be sent.
  • Email servers do a Sender Policy Framework (SPF) record check whenever they receive an email.
  • When a message is received, the server checks the IP address to see if it is one of the approved senders mentioned in the SPF record.
  • The SPF check is successful if the sending IP address is known and accepted; otherwise, the email may be flagged as suspicious and deleted.

How Do Attackers Abuse SPF:

Sender Policy Framework (SPF) is an email authentication system that checks the sender’s name to stop email spoofing and phishing. But, like any other system, SPF isn’t completely safe from possible attack vectors. Here are some possible ways to attack SPF:

Manipulating SPF Records: Attackers could try to change or create SPF records by changing the DNS records of a domain. This would let them list unauthorized IP addresses or servers as valid senders. This can make it possible for tactics like spoofing or phishing to work.

Domain Hijacking: If an attacker takes control of a legal domain, they can change the SPF records to include their own malicious servers. This can cause bad emails that look like they came from a trusted source to be sent.

Subdomain Attacks: SPF records are often set up for an organization’s primary domain, but they might forget to set up SPF records for subdomains. Attackers who send emails from subdomains without the proper SPF records can use this against you.

Inadequate SPF Policies: Organizations may have weak SPF policies that let many IP addresses send emails on their behalf. This can give attackers a bigger pool of possible IP numbers to trick people.

Document
FREE Demo

Implementing AI-Powered Email security solutions “Trustifi” can secure your business from today’s most dangerous email threats, such as Email Tracking, Blocking, Modifying, Phishing, Account Take Over, Business Email Compromise, Malware & Ransomware

DomainKeys Identified Mail (DKIM)

DomainKeys Identified Mail (DKIM) is an email authentication technology that uses encryption to confirm an email’s authenticity.

The sending server adds a distinctive DKIM signature using a private key to each email. The receiving server verifies the signature of the incoming email using a public key obtained from the sender’s DNS records.

If it matches, the email can be trusted as genuine and safe from tampering. DKIM is designed to prevent email spoofing and phishing attacks and guarantee the safe delivery of email communications by verifying the sender’s domain and the message’s encrypted signature.

You can Understand and diagnose Email Issues using Trusitifi’s Email Header Analyzer Tool.

How It Works

  • Using a private key, the email’s computer makes a digital signature.
  • The email packaging has been changed to include this signature.
  • From the DNS records, the email server that receives the email gets the sender’s public key.
  • The digital signature is then decrypted and checked using the public key.
  • The genuine email has not been changed if the signature is correct.

How Do Attackers Abuse DKIM

  1. Private Key Compromise: DKIM relies on a private key stored on the sending server to sign outgoing emails. If an attacker gains access to the private key, they can sign malicious emails that recipients might consider legitimate, as the DKIM signature would appear valid.
  2. DNS Record Manipulation: DKIM public keys are stored in DNS records as text (TXT) records. If an attacker gains control over a domain’s DNS records, they could modify or replace the DKIM public key, allowing them to sign fraudulent emails that appear authentic.
  3. Subdomain Spoofing: Organizations might configure DKIM for their main domain but overlook implementing it for subdomains. Attackers could then send emails from subdomains that lack proper DKIM signing, making it harder for recipients to verify the email’s authenticity.
  4. Key Length and Algorithms: If an organization uses weak encryption algorithms or short key lengths for DKIM signing, it becomes easier for attackers to crack the encryption and forge DKIM signatures.

Solution: Organizations should adopt efficient incident response plans, regularly monitor email traffic for anomalies, and stay updated on emerging threats to stay ahead of the evolving email threat landscape with AI-powered solutions like Trustifi.

Domain-based Message Authentication, Reporting, and Conformance (DMARC)

To improve upon SPF and DKIM, a new email authentication protocol called Domain-based Message Authentication, Reporting, and Conformance (DMARC) was developed.

Domain administrators can instruct receiving mail servers on what to do with messages that do not pass authentication.

Domain owners can direct mail servers to stop accepting spam by adding a DMARC policy record to their DNS settings. Email traffic and any security risks can be better understood using DMARC’s reporting features.

DMARC is designed to strengthen email security by adding an extra layer of verification, decreasing phishing and spoofing, and increasing the credibility and delivery of legitimate communications.

How it Works

  • The receiving server references the DMARC policy if SPF or DKIM authentication fails.
  • The DMARC policy can direct the server to take various actions, such as classifying spam, placing it in quarantine, or outright rejecting it.
  • To improve their email protection measures, domain administrators can use forensic and aggregate data on authentication activity.

DMARC Attack Vector

Aggressive Enforcement: Some organizations may choose to use DMARC with a strategy of “quarantine” or “reject” right from the start. This can work, but if the policy isn’t carefully set, it can also cause valid emails to be blocked.

Reporting Address Spoofing: Attackers could try to change the DMARC reporting address to send reports of failed DMARC checks to sites they control. This could give them a chance to learn more about how the organization’s email system works.

Targeted Spoofing: Attackers could try to pose as people or parts of an organization that haven’t fully set up DMARC. This specific method makes it more likely that their emails will be read.

As with other email-related attacks, attackers could use social engineering to get receivers to ignore DMARC warnings or think a DMARC-failed email is real.

Trustifi employs AI algorithms to detect unauthorized access, compromised accounts, or unusual email activity, alerting users to security risks.

Where are SPF, DKIM, and DMARC Records Stored?

Spf records:

SPF records are TXT (text) records in the DNS. Emails from this domain must be sent from the IP addresses or parts specified in these records.

The recipient’s email server will check the SPF record for the sender’s field in the Domain Name System (DNS) to ensure the email is legitimate.

Example SPF record:

v=spf1 ip4:192.0.2.1 ip6:2001:db8::1 include:example.com all

DKIM Records: 

DKIM records are similarly stored in DNS, although they are TXT entries. These entries store the public key to authenticate the domain’s digital signatures in outgoing emails.

The DKIM record is retrieved from the DNS by the receiving email server, which then uses the public key to verify the signature and ensure the email’s authenticity.

Example DKIM record:

v=DKIM1; k=rsa; p=MIGfMA0GCSqGSIb3DQEBAQUAA4GNADCBiQKBgQDnWLKu6qIH66AjqkMYyq3A5bkD

  sY+T4rQzSXFJWzh7DQoKmmrkRDbCIPRrkRHF/EpTExGDD2P8WOEqdGTfVbRy14

  5k3soVGMItcL1QvWskhNKLQYGJME6XE1WUCmAw29FcYKavqnGQFWFpDBIMVFOFw

  7/TZS0Lj1QIDAQAB

DMARC Records:

DNS also stores DMARC records in the TXT record format. The measures to take if an email fails SPF or DKIM checks are provided in the domain’s DMARC policy, defined by these records.

To keep the domain owner aware of authentication actions, DMARC additionally provides reporting tools.

Example DMARC record:

v=DMARC1; p=quarantine; pct=25; rua=mailto:[email protected]; ruf=mailto:[email protected]

Checking an Email for SPF, DKIM, and DMARC Compliance

It takes multiple procedures and the capacity to query DNS records to ensure an email complies with SPF, DKIM, and DMARC.

Here are the measures taken to ensure that an email adheres to these standards:

Check SPF Compliance:

  • Extract the IP address of the email server that sent the email from the email headers.
  • Retrieve the SPF record from the domain’s DNS that the email claims to be sent from. This is usually found in a TXT record in the domain’s DNS.
  • Check if the sending server’s IP address is listed in the SPF record. If it is, the email passes the SPF check; otherwise, it fails.

Check DKIM Compliance:

  • Check the email headers for a DKIM signature. This will usually be found in a header field called ‘DKIM-Signature’.
  • Extract the ‘d=’ parameter from the DKIM signature to find the signing domain and the ‘s=’ parameter to find the selector.
  • Retrieve the DKIM public key from the DNS of the signing domain. This will be found in a TXT record at selector>._domainkey.signing domain>’.
  • Use the public key to verify the DKIM signature in the email header. If the signature is valid, the email passes the DKIM check; otherwise, it fails.

Check DMARC Compliance:

  • Ensure that the email has passed both the SPF and DKIM checks. At least one of them must pass for the DMARC check to pass.
  • Retrieve the DMARC record from the domain’s DNS from which the email claims to be sent. This is usually found in a TXT record at ‘ _dmarc.domain>’.
  • Check if the ‘From’ address domain matches the SPF domain or the DKIM signing domain. If it does, then the email passes the DMARC alignment check.
  • Follow the policy specified in the DMARC record for handling emails that fail the DMARC check.

How to configure SPF, DKIM, and DMARC for a domain

Configure SPF:

  • Identify Authorized IP addresses or servers: Determine the IP addresses or servers authorized to send email on behalf of your domain.
  • Create an SPF Record: Create an SPF record by creating a TXT record in your domain’s DNS settings. The value of this TXT record will start with ‘v=spf1’ followed by the authorized IP addresses or servers.
Example SPF Record: 'v=spf1 ip4:192.168.0.1 -all'

This example authorizes the IP address ‘192.168.0.1’ to send emails on behalf of your domain and denies all others.

  • Update DNS Settings: Add the SPF record to your domain’s DNS settings.

Configure DKIM:

  • Generate a DKIM Key Pair: Generate a public-private key pair for DKIM. Your email server will use the private key to sign outgoing emails, and your domain’s DNS settings will make the public key available.
  • Configure Email Server: Configure your email server to sign outgoing emails using the private DKIM key.
  • Create a DKIM Record: Create a DKIM record by creating a TXT record in your domain’s DNS settings.
  • The name of this TXT record will be in the format selector>._domainkey.yourdomain>’, and the value will contain your DKIM public key.
Example DKIM Record: 'v=DKIM1; k=rsa; p=MIGfMA0...'

This example specifies that the key type is RSA and includes the public key.

  • Update DNS Settings: Add the DKIM record to your domain’s DNS settings.

Configure DMARC:

  • Create a DMARC Record: Create a DMARC record by creating a TXT record in your domain’s DNS settings. The name of this TXT record will be ‘_dmarc.your domain>’, and the value will contain your DMARC policy.
Example DMARC Record: 'v=DMARC1; p=reject; rua=mailto:[email protected]'

This example specifies that emails that fail the DMARC check should be rejected and that reports should be sent to ‘[email protected]’.

  • Update DNS Settings: Add the DMARC record to your domain’s DNS settings.

Conclusion

The SPF, DKIM, and DMARC standards are essential components of a reliable email security architecture in an age when email is vulnerable to a wide range of attacks.

Though each has advantages and disadvantages, they provide an enormous defense against a significant fraction of email-based attacks.

By implementing these authentication processes, your email systems’ security will improve, and your emails’ deliverability will also be enhanced, reducing the possibility that your legitimate messages will be miscategorized as spam.

Applying these standards to your digital communication infrastructure can significantly improve the safety and dependability of your communications.

Implementing AI-powered email security solutions can secure your business from today’s most dangerous email threats, such as Email Tracking, Blocking, Modifying, Phishing, Account takeover, Business Email Compromise, Malware and ransomware – Request Free Demo.


[ad_2]
Source link