Amazon & Disney explore potential ESPN streaming partnership

0
[ad_1]

Amazon.com is presently in early discussions with Walt Disney Co. about collaborating on the development of ESPN’s streaming version. Amazon is also exploring the option of acquiring a minority stake in the sports network as part of this potential partnership.Individuals familiar with the situation reported these details through The Information on Thursday.

Currently, Disney and ESPN are actively determining an appropriate price for the new service, according to the report. And the pricing is one of the things necessary for smooth negotiations

The report adds that ESPN is considering a subscription fee ranging from $20 to $35 a month for the new streaming service. This pricing structure could potentially position it as the most expensive streaming service in the United States.

Amazon.com, Walt Disney, and ESPN have not yet provided responses to requests for comment from news media

Disney CEO’s stance on the Partnership

In July, Disney CEO Robert Iger informed CNBC of his company’s intention to retain control over ESPN. He also expressed a desire to seek out strategic partners for forming a joint venture or acquiring a stake in the sports network. This strategy aims to empower ESPN to directly engage consumers, marking a significant shift in distribution strategy.

In summary, preliminary discussions are ongoing between Amazon.com and Walt Disney regarding the collaborative development of ESPN’s streaming version. Simultaneously, Amazon.com is actively looking at the prospect of owning a minority share in the sports network and negotiation between Disney and ESPN is dependent on setting the appropriate subscription fee for the Upcoming streaming service,with $20 to $35 the potential monthly charges ranging from.

While awaiting responses from the involved parties, it’s worth noting that Disney’s CEO previously underlined the company’s commitment to elevating ESPN’s significance and exploring partnerships for improved consumer accessibility. This strategic direction highlights the evolving media distribution landscape, emphasizing the growing importance of direct-to-consumer offerings within the industry.


[ad_2]
Source link
Hackers Disrupted Poland’s Railway System Signals

0
[ad_1]

Poland’s Railway infrastructure, a crucial transit route for Western weapons transported to Ukraine, has been compromised by cybercriminals.

The signals were intermingled with recordings of the Russian national anthem and a speech by President Vladimir Putin, according to the Polish Press Agency (PAP).

According to the information shared, the incident occurred on Saturday when hackers sent a signal that caused emergency train stops close to Szczecin, Poland. About 20 trains came to a complete stop, but services were soon resumed.

“We know that for some months there have been attempts to destabilize the Polish state,” Stanislaw Zaryn, a senior security official, said. 

“Such attempts have been undertaken by the Russian Federation in conjunction with Belarus.”

Criminals Instructed The Trains Via Radio Frequency 

The “cyberattack” doesn’t appear to have involved any “cyber” at all, despite how disruptive the railway sabotage has been, claims Lukasz Olejnik, a Polish-speaking independent cybersecurity researcher and consultant.

In reality, the criminals seem to have instructed the trains they targeted with straightforward radio frequency “radio-stop” commands.

Olejnik claims that since the trains use a radio system that does not have encryption or authentication for those commands, anyone with as little as $30 in common radio equipment can transmit the command to Poland’s Railway.

Further, they activate their emergency stop function by sending a series of three acoustic tones at a frequency of 150.100 megahertz.

“It is three tonal messages sent consecutively. Once the radio equipment receives it, the locomotive goes to a halt,” Olejnik says.

In Polish radio and railway forums as well as on YouTube, the capability to send the command has long been discussed.

“Everybody could do this. Even teenagers trolling. The frequencies are known. The tones are known. The equipment is cheap”, he added.

The proximity of the saboteurs to the target trains, which might range from a few hundred feet to several miles, depending on the strength of the radio equipment they would be using to cause disruption.

“It is really a cheap operation. The biggest risk is the need to be in proximity”, Olejnik said.

According to a statement from the railways, the train delays were caused by ‘unauthorized broadcasting of the radio-stop signal’ that was transmitted “using a radiotelephone by an unknown perpetrator.”

“There is no threat to rail passengers. The result of this event is only difficulties in the running of trains”, the Railway Agency wrote.

By 2025, Poland’s Railway systems will be upgraded to almost entirely employ GSM cellular radios, which feature encryption and authentication, according to the country’s national transportation agency. 

However, as long as that point, it will continue to operate on the comparatively unprotected VHF 150 MHz system, which makes it possible to spoof “radio-stop” instructions.

Keep informed about the latest Cyber Security News by following us on Google News, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

First Motorola Edge 2023 image shows us a familiar design

0
[ad_1]

The very first Motorola Edge 2023 image has just appeared. Well, truth be said, several renders are offered here, but they’re all a part of the same image, technically.

The very first Motorola Edge 2023 image indicates a Motorola Edge 40 rebrand

If you take a look at the image provided below, you’ll be able to see the Motorola Edge 2023 from the front, back, and also from both its left and right sides.

Motorola Edge 2023 image leak

You can clearly see here that the phone will feature a curved display. It will also offer thin bezels, and a centered display camera hole. Motorola will place all three of its physical keys on the right-hand side.

The back of the phone will also be curved, proportionally to the front side. Two cameras will be placed on the back, and both of them will be included in the same camera island. That camera island will sit in the top-left corner.

Those cameras do protrude on the back quite a bit, which is easily visible thanks to the provided image. Motorola’s logo is located on the back of the phone, and this seems to be a dark gray variant of the phone.

It will have either glass or vegan leather on the back

We’re not sure what the backplate will be made of, but it’s possible it’s either glass or vegan leather. The image is not sharp enough for us to be sure. This image also reveals that an under-display fingerprint scanner will be used by the company.

The Motorola Edge 2023 will be inferior to the Motorola Edge 40+, it seems. It will likely be a rebrand of the Motorola Edge 40, by the looks of it. The phone is expected to offer a 6.55-inch fullHD+ P-OLED display with a 144Hz refresh rate.

The MediaTek Dimensity 8020 SoC will fuel the phone. Motorola will include 8GB of RAM on the inside, and pack that with 256GB of storage. It’s possible more than one variant will be on offer, though.

A 4,400mAh battery was also mentioned in rumors, and the same goes for 68W wired charging. The phone is also said to offer 15W wireless charging. A 50-megapixel main camera (OIS) will sit on the back, alongside a 13-megapixel ultrawide unit. Android 13 will come pre-installed on the device.


[ad_2]
Source link

Prominent figures including OpenAI CTO fell victim to SIM swapping attacks

0
[ad_1]

In recent years, SIM swapping has emerged as a popular option for threat actors looking to gain unauthorized access to people’s phones and steal their hard-earned money. Now, according to a report from crypto detective ZachXBT, several high-profile personalities and institutions have fallen victim to SIM-swapping attacks, resulting in a collective loss of a staggering $13 million.

Prominent figures, including Mira Murati (OpenAI’s CTO), Daniel Alegre (CEO of Bored Ape), the Aptos Foundation, Stellar Development Foundation, Bryan Pellegrino (LayerZero’s CEO), Garry Tan (Y Combinator’s CEO), along with Pleasr DAO, and Peter Schiff, have fallen victim to SIM swap attacks this year. Additionally, even Bart Stephens, the founder of Blockchain Capital and an early investor in Coinbase and Kraken, suffered a significant loss of $6.3 million in a recent attack.

So, what exactly is SIM swapping?

As the name suggests, these attacks involve threat actors exploiting vulnerabilities within cellular providers’ systems, manipulating them into transferring victims’ phone numbers to new SIM cards under the attackers’ control. Once achieved, cybercriminals gain full access to the target’s calls, texts, and online activities, rendering the original SIM card obsolete.

Additionally, what makes these attacks even more concerning is the minimal requirement for hacking expertise. This is because threat actors only need personal data obtainable from social media, illicit online markets, or phishing scams to convincingly assume the identity of their targets.

Indicators of such an attack include unfamiliar calls and messages regarding changes in cellular service, as well as loss of account access on your device. Unfortunately, victims of the attack often remain oblivious until threat actors do considerable damage, which may involve password resets, deactivation of two-factor authentication, and unauthorized access to sensitive banking accounts. Therefore, if you ever see any of the mentioned signs, then the best course of action would be to contact your carrier.

Protecting from such attacks?

Although it’s not possible to completely shield themselves from such attacks, users can adopt certain measures to enhance their protection. These include utilizing built-in security features such as PINs and passwords for additional layers of defence and employing your carrier’s “Number Lock” feature, which would lock your phone number with them, thus disabling unauthorized transfers.


[ad_2]
Source link

WhatsApp explores avatar reactions for status updates

0
[ad_1]
In February of this year, WhatsApp added a new feature allowing users to react to a status with emojis. This was one of the most requested features since the debut of reactions last year. And now, it looks like WhatsApp is working on yet another option for you to express your reaction to a status.

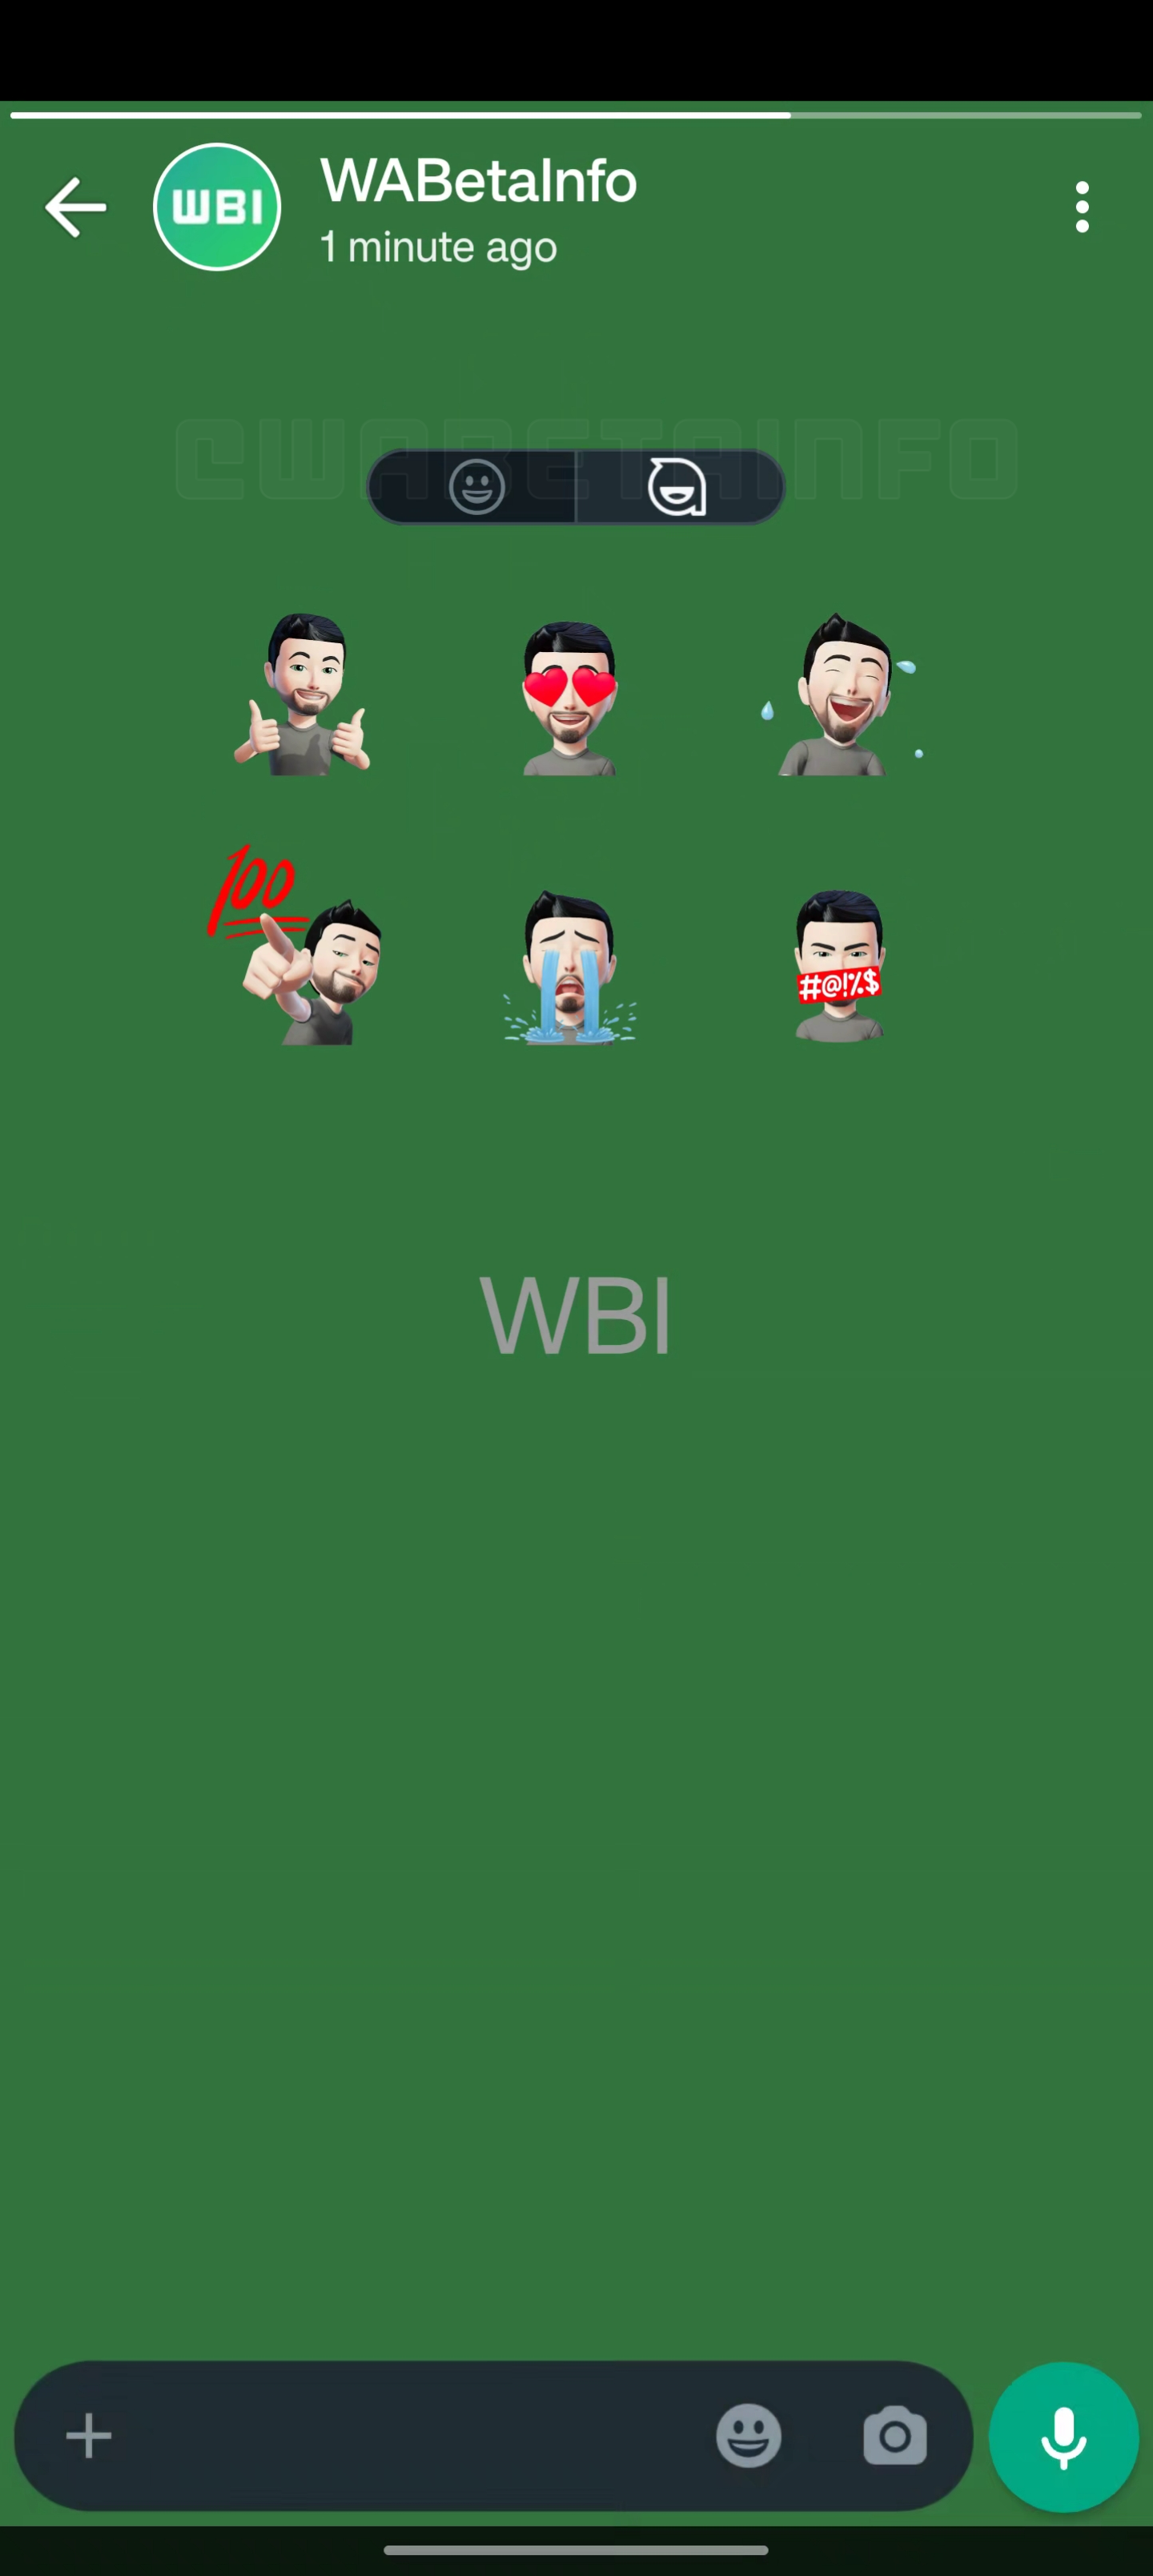
According to info from Wabetainfo, WhatsApp is working on a feature that lets you reply to status updates using avatars. The latest update, WhatsApp beta for Android 2.23.18.9, shows that WhatsApp plans to bring in this avatar reply feature in a future app update. As per the source, the feature is still being worked on, and unlike most other WhatsApp betas, this one doesn’t seem to be rolling out widely to testers just yet.

When the update eventually comes out, you’ll be able to react to status updates using not only the 8 emojis available now but also avatars, which again might have 8 different options. Avatars would let you express your feelings about someone’s status in a more personal way and could be a well-received feature.

Status is a way to drop quick updates to friends and close contacts on WhatsApp. These updates vanish in 24 hours and can include photos, videos, GIFs, and text. Similar to your one-on-one chats and calls, your WhatsApp status is locked up tight with end-to-end encryption.

It is still uncertain when exactly this new status reactions option will be available, but knowing WhatsApp’s history, it might not be that far in the future.

The Meta-owned app tries to keep its more than two billion users satisfied by introducing new features regularly. Just recently, WhatsApp started supporting HD videos, following the introduction of HD photos. And that is not all: a new feature allowing users to share their screen during video calls was also introduced.


[ad_2]
Source link

Hackers Exploited WinRAR Zero-Day To Target Traders

0
[ad_1]

Days after fixing the vulnerability, details have surfaced online about a WinRAR zero-day vulnerability that went under attack. The researchers noticed active exploitation of the vulnerability to target traders. While the patch has already arrived, many devices still need users’ attention to receive the updates.

WinRAR Zero-Day Exploited In The Wild

Researchers from Group-IB have shared a detailed post about a zero-day vulnerability in WinRAR. Given WinRAR’s huge user base, the zero-day caused a severe threat to the users as it went under attack before the patch could arrive.

Specifically, the vulnerability, CVE-2023-38831, impacted the processing of the ZIP format, allowing the adversary to spoof the malicious executable file as a .jpg or .txt file within the archive. However, successfully exploiting the flaw required an attacker to lure the victim user into interacting with the infected file.

As elaborated, the researchers found the vulnerability being exploited for spreading the DarkMe malware. Some cases also showed the dissemination of other malware, such as GuLoader (CloudEye) and Remcos RAT. However, they noticed a specific pattern for the victims, mainly traders.

The threat actors leverage the vulnerability to create malicious archives that they upload on popular trading forums. To lure victims, the threat actors accompany the files with catchy texts to grab the attention of avid traders.

Clicking on the malicious zipped file would execute the embedded payload on the target device, allowing the attackers to withdraw money from the victims’ broker accounts.

Following this discovery, the researchers reported the matter to WinRAR developers, who patched the flaw. They released the fix with the WinRAR version 6.23 earlier this month.

However, at that time, the official RARLAB advisory didn’t state any details about this specific flaw, mentioning only the fix and highlighting another critical severity remote code execution reported earlier. But in the updated advisory, they have also confirmed patching the zero-day CVE-2023-38831.

Since this zero-day is already under attack, users must rush to update their systems with the latest WinRAR release to avoid the threat.

Let us know your thoughts in the comments.


[ad_2]
Source link

OPPO Find N3 Flip images show the retail box, its contents & more

0
[ad_1]

The OPPO Find N3 Flip has surfaced in images once again, and this time around its retail box is shown, along with its contents. The same goes for the OPPO Watch 4 Pro, actually. In addition to that, renders of both devices leaked, and a real-life image of the Find N3 Flip too.

The OPPO Find N3 Flip retail box leaks, along with some additional images

Let’s kick things off with the OPPO Find N3 Flip, shall we. The phone’s launch date was confirmed last week, and the phone’s design was confirmed by the company. The device will launch tomorrow, alongside the OPPO Watch 4 Pro.

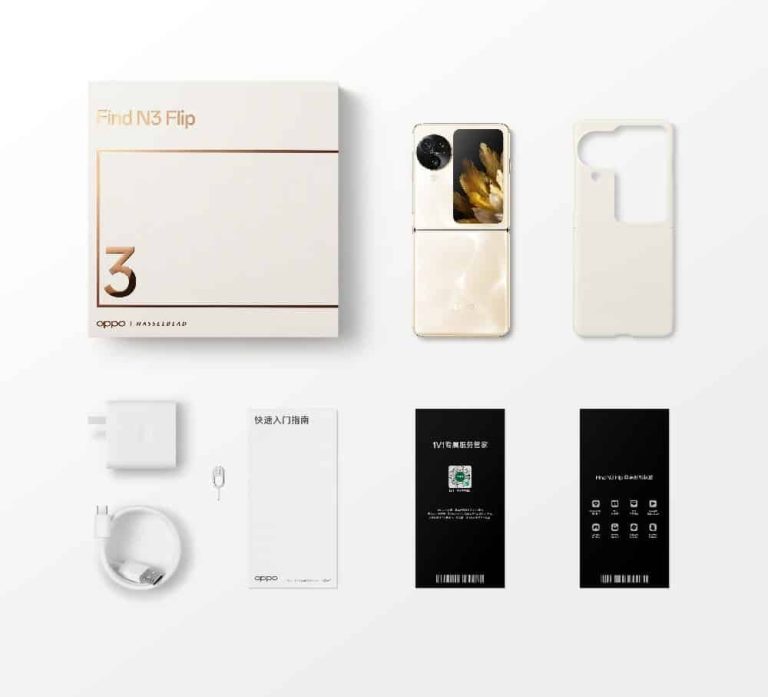
If you check out the first image in the gallery below, you’ll see the OPPO Find N3 Flip’s retail box, the phone itself, and the contents of the packaging. You’ll notice that a case is included here, a seemingly-plastic one.

In addition to that, a charger is in the box, and it’s rather compact. As a reminder, the phone is tipped to offer 67W wired charging. A cable is noticeable here, along with a SIM card ejector tool, and some paperwork.

The second and third images in the gallery show you a render of the device, and a real-life image too. You can clearly see its cover display, which is just as large as the one from the OPPO Find N2 Flip. It’s vertical again too.

The OPPO Watch 4 Pro is also coming, and here’s what you’ll get

Now, if you check out the gallery below, you’ll see the OPPO Watch 4 Pro retail box, its contents, and a render of the watch itself in a separate image.

The OPPO Watch 4 Pro will seemingly come with a leather watch band, but a silicone one will also be included in the box. Well, at least one of the variants will. A wireless charging will also be included, along with a cable, and some paperwork.

The watch will have a rectangular body, with a rotating crown on the right side. That crown will also double as a physical button, while a secondary button is located below it.


[ad_2]
Source link

Samsung to unveil its generative AI tool in September

0
[ad_1]

Samsung is reportedly planning to unveil its ChatGPT-like generative AI tool next month. According to the Korean media, the company will demo the new tool during its Real Summit 2023 event in Seoul, South Korea on September 12. The latest edition of the annual tech event will focus on generative AI and cloud technologies.

Samsung is known to be developing an in-house AI tool since at least May this year. Local media said the company has teamed up with domestic tech firm Naver on the project, which doesn’t yet have a name. Its co-CEO Kyung Kye-hyun confirmed the plans the following month. However, he didn’t reveal when the tool will arrive.

Meanwhile, reports suggested that Samsung would rush to launch the product. It appears the company is now ready to show the tool to the world. The Korean firm will demo the AI solution to its clients and the media during the tech event in a couple of weeks, Korea Daily reports. It’s unclear whether it will be the final product or if Samsung is bringing an early version of the tool to Real Summit 2023.

Samsung will keep its generative AI tool private to itself

Generative AI is all the rage lately. Almost every online tool we use today comes with some sort of AI-powered generative features. ChatGPT started the trend, but we now have hundreds of such products. Some are standalone tools capable of answering every question, while others have expertise in a certain field or come integrated with existing products.

Samsung’s AI tool, meanwhile, will be a little different. The unnamed service is designed to help the company improve and speed up business processes. It plans to use the tool in various business areas, including data analysis and information sourcing for chip production, cost management, transcription of audio files or voice notes, translation of documents, and customer service.

In other words, Samsung’s ChatGPT alternative will be private to the company. It won’t be available to the public, at least that isn’t the plan right now. The Korean firm developed the tool to use internally after some employees inadvertently leaked critical chip information through ChatGPT. This happened when Samsung allowed employees to use OpenAI’s AI tool to speed up some work earlier this year.

The company has since banned the use of all third-party generative AI tools on official devices and internal networks. But this means it’s missing out on potential business advancements with the help of AI. This is likely why Samsung is rushing to launch its in-house solution. It remains to be seen whether the Korean behemoth ever launches a public version of the tool to go head-on against ChatGPT, Google Bard, and others.


[ad_2]
Source link

Dropbox ends unlimited storage plans due to crypto miners

0
[ad_1]

After years of providing users with unlimited cloud storage, Dropbox is finally abandoning the “all the space you need” storage plan. This decision comes in response to users exploiting the service for activities such as crypto mining and reselling storage to others.

In a blog post, Dropbox also pointed out a notable instance involving the cryptocurrency Chia, which heavily relies on storage capacity as a fundamental component of its mining process. The currency’s “proof of space and time” model, which rewards users based on their ownership of “plots,” each demanding 100 GB of storage on physical hard drives, led to crypto miners combining their storage resources.

“In recent months, we’ve seen a surge of this behaviour in the wake of other services making similar policy changes. We’ve observed that customers like these frequently consume thousands of times more storage than our genuine business customers, which risks creating an unreliable experience for all of our customers,” reads Dropbox’s blog post.

New plans

As a result of the shift, the company’s Advanced plan, which includes three active licenses, will now provide 15TB of shared storage space, sufficient for storing approximately 100 million documents, 4 million photos, or 7,500 hours of HD video content. Additionally, Dropbox emphasizes that users who utilize less than 35TB of storage will retain their current storage capacity and receive an extra 5TB of pooled storage credit for five years. However, for businesses exceeding the 35TB threshold, the company will offer a similar arrangement, including a 5TB credit for one year, up to a maximum total of 1,000TB.

Moreover, starting September 18 for new customers, Dropbox will introduce new storage add-ons, which will provide an extra 1TB of storage at a monthly rate of $10 or a discounted rate of $8 per month for annual purchases.

However, it is important to note that the company will introduce the changes gradually from November 1st, giving users at least 30 days’ notice before their scheduled migration date.


[ad_2]
Source link

Cisco Nexus 3000 and 9000 Series Switches Flaw

0
[ad_1]

A Denial-of-Service vulnerability has been discovered in the Cisco Nexus 3000 and 9000 series switches, which could allow a threat actor to cause a denial-of-service condition due to a flaw in the IS-IS (Intermediate System-to-Intermediate System) protocol.

ISIS is one of the family of IP routing protocols and can also act as an Interior Gateway Protocol (IGP), which is used to distribute IP routing information throughout a very large network that has a single routing policy.

The vulnerability exists due to the unexpected restart of the IS-IS process, causing an infected device to restart. Threat actors can exploit this vulnerability by sending a crafted IS-IS packet to an infected device that can cause the device to reload.

CVE-2023-20169: Cisco Nexus 3000 and 9000 Series Switches IS-IS Protocol Denial of Service Vulnerability

Additionally, there is insufficient input validation when parsing ingress IS-IS packets, leading to this denial of service condition on the affected devices. This vulnerability has been assigned with a CVE ID of CVE-2023-20169 and has a severity of 7.4 (High), as stated by NVD. 

However, there are prerequisites for threat actors to exploit this vulnerability. The threat actor must be layer 2 adjacent to the affected device for successful exploitation. 

Cisco has released a security advisory for this vulnerability, including a list of affected devices and a list of not vulnerable devices.

Affected Products & How to Detect

As mentioned by Cisco, the affected products include Nexus 3000 Series Switches and Nexus 9000 Series Switches in standalone NX-OS mode. In addition, Cisco has also provided steps to detect if a Switch has enabled IS-IS Protocol. 

“A device that is configured for IS-IS authentication can still be affected by this vulnerability. For more information, see Cisco Nexus 9000 Series NX-OS Unicast Routing Configuration Guide, Release 10.3(x): IS-IS Authentication,” reads the security advisory released by Cisco.

The list of products that Cisco has confirmed are not vulnerable can be checked in this Cisco security advisory section.

Keep informed about the latest Cyber Security News by following us on Google News, Linkedin, Twitter, and Facebook.


[ad_2]
Source link