Motorola Edge 40 Neo nears launch with a MediaTek chipset

0
[ad_1]

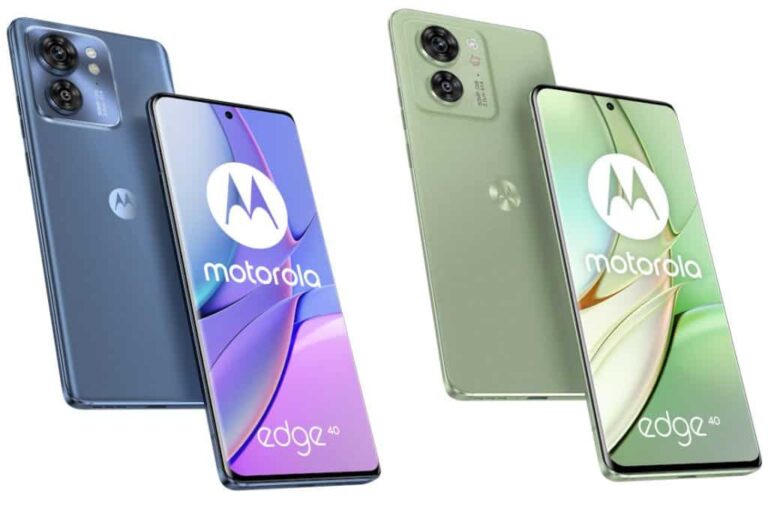
Motorola doesn’t seem to be done launching its Edge 40 series flagship smartphones. The company has already launched the vanilla Edge 40 and Edge 40 Pro. It’s now readying the Edge 40 Neo. After appearing in some certification listings, the new model has now popped up on the popular benchmarking platform Geekbench. The benchmark entry confirmed some of its rumored specs.

Spotted by 91Mobiles, the Motorola Edge 40 Neo is listed with its full name on Geekbench. We can see that the device features an ARM v8-based octa-core processor with a base CPU frequency of 2.0GHz and a maximum frequency of 2.50GHz. The CPU is supported by the Mali-G610 MC3 GPU. Based on this information, the publication speculates the SoC to be MediaTek’s Dimensity 1050, which is a 6nm chipset.

Motorola is pairing the chipset with 8GB of RAM, Geekbench confirms. However, there may be more RAM variants. The Edge 40 Pro has 12GB of RAM. Like other models in the series, the Edge 40 Neo will also run Android 13 out of the box. Previous sightings of the phone revealed that it has the model number XT2307-1, at least in some markets. The device will offer 5G cellular connectivity (the chipset supports both Sub-6GHz and mmWave 5G networks).

Other Motorola Edge 40 Neo rumors have hinted at a 6.55-inch Full HD+ pOLED display with a 144Hz refresh rate, a 50MP primary rear camera, a 13MP secondary rear camera (ultrawide lens), a 32MP front camera, up to 12GB of RAM and 256GB of onboard storage, a 5,000mAh battery, and an IP68 rating for dust and water resistance. The Edge 40 Neo could be the most affordable model in Motorola’s Edge 40 series.

Motorola Edge 40 Neo launch date

Motorola hasn’t officially confirmed the existence of the Edge 40 Neo. However, recent developments suggest the phone is nearing its debut. Rumors say it will launch in India on September 15. It’s unclear if the device will arrive in other markets on the same day if at all. There’s no telling if Motorola will launch the Edge 40 Neo globally.

If these rumors are accurate, we may soon hear more about Motorola’s upcoming flagship smartphone. The Lenovo-owned company is also working on a new mid-range model called the Moto G84 5G. It is also rumored to arrive in September. We will have to wait and see if Motorola will launch the two phones on the same day. We will let you know as soon as we have more information.


[ad_2]
Source link

5 best gaming controllers for Android smartphones

0
[ad_1]

If you want more control over your movements when you next play your favourite mobile games from your Android smartphone, you may want to consider investing in a dedicated mobile gaming controller.

The good news for gamers is that there are plenty of reliable controllers to choose from. However, instead of listing them all, here are just five of the best Android controllers money can buy in 2023.

What are the best mobile game controllers for Android devices?

When choosing a reliable mobile game controller for your Android smartphone, you need to weigh up the pros and cons of each device to see which controller would be the best fit for you.

In other words, take the time to read as many product and user reviews as possible for each of these highly recommended controllers and then cross reference the reviews to get a better idea as to which one you should go for.

Without further ado, five of the best gaming controllers for Android smartphones are the following:

1. Razer Kishi V2
2. Nacon MG-X Pro
3. Gamesir X3
4. 8Bitdo Pro 2
5. Turtle Beach Atom

Your gaming needs will determine which Android mobile gaming controller you should go for. For example, if you’re going to be playing the more graphically demanding triple-A games, where characters and vehicles require precision movements that are hard to pull off, any of these top 5 controllers will do the job.

If you’re only going to be playing retro arcade games, mini social games, iconic online board games, or today’s best online slots at licensed casino sites – for which you’ll find online casino bonuses that apply to many casino games – then you shouldn’t need to invest in one of these controllers.

In other words, think about why you need a controller and which controller will benefit you most before purchasing one.

Honorable mentions

There are several other reliable Android controllers, so if you are looking for something other than the top five mentioned above, you may want to look into getting either the 8BitDo SN30 Pro, the Xbox Series X Controller, Razer Raiju Mobile, the Sony PlayStation DualSense Controller, or the 8Bitdo Zero 2.

Others include the MSI FORCE GC30, the 8BitDo M30, and the 8Bitdo Pro 2. To give you an idea of the cost, they range in value from around $40 up to $200.

At a glance

Many of today’s most trusted review sites have the Nacon MG-X Pro ranked either as their number 1 controller or at least in their top 3. Many avid mobile gamers regard it as the best overall Android controller. It has a great ergonomic design and impressive battery life.

Others will argue that the Razer Kishi V2 is the best overall Android controller, but the truth is that you can’t go wrong with either. They are both superb pieces of kit that can make gaming from a smartphone much easier and more enjoyable.

The Razer Kishi V2 works well with more smartphones than ever and comes with programmable M2 bumpers. If you enjoyed using the V1, then you should also enjoy the V2, which is slightly bigger than V1 but doesn’t have a headphone jack.

The 8Bitdo Pro 2 is quite possibly the best Android gaming controller for versatility. It has a retro look, which some people these days love, and it’s packed with lots of modern innovative features, such as custom button mapping, a four-way toggle switch, and a rechargeable battery.

The Gamesir X3, on the other hand, is ideal for playing your favourite games for hours at a time because it has the best built-in fan cooling system. It also comes with a USB-C connector and swappable buttons.

What are the best mobile games to play using a top-of-the-range Android controller?

If you purchase a top-of-the-range Android smartphone controller and want to put it to good use, don’t forget to check out some of these popular mobile games.

Examples include Call of Duty Mobile, BombSquad, Stardew Valley, Modern Combat 5, Minecraft, PUBG Mobile, Asphalt 8: Airborne, Grand Theft Auto: San Andreas, and Genshin Impact.

Other hit titles to check out with your new controller are Diablo Immortal, Asphalt 9: Legends, Fortnite, Terraria, Brawlhalla, and GRID Autosport.

If that’s not enough to keep you going, try Castlevania: Symphony of the Night, Shadowgun Legends, Sky: Children of the Light, Grimvalor, Dead Cells, and Rocket League: Sideswipe, to name a few. Don’t forget that some of these games have a PEGI-18 age restriction.

Final note

When purchasing any new controller for your Android mobile device, always remember to shop around to try and find the best deals. Also, make sure you purchase from a trusted merchant.

Some of these controllers are much more comfortable than others, so if you would rather physically hold it before buying, you would be better off purchasing one from a land-based gaming store rather than online from a website, so you can get a good feel for the device.


[ad_2]
Source link

Deezer rolls out new Home and Explore tabs on mobile

0
[ad_1]

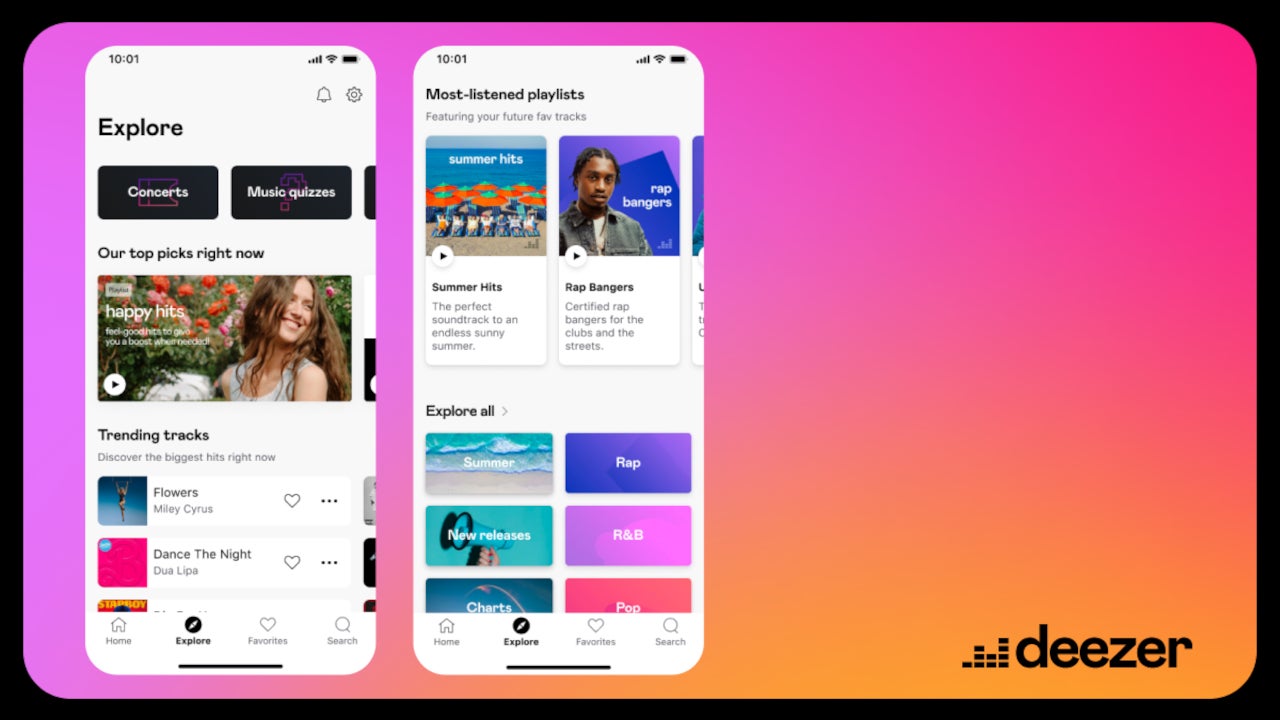
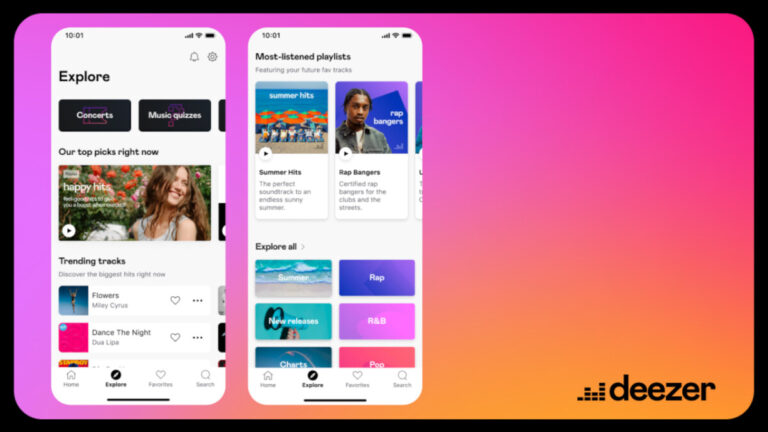
Deezer, one of the major music streaming services available worldwide, has just launched two new tabs on mobile: Home and Explore. The new tabs will be available to everyone, so they’re not gated behind a paywall.

The new Home tab aims to provide users with a personalized experience. It’s also the main hub for all recommended content based on listening habits and liked songs, including the infinite AI-generated playlist, also known as Flow.

It’s also important to add the Home tab gives Deezer users access to their top genres, new releases from their favorite artists, and the playlists they like.

On the other hand, the Explore tab is the place to go if you’re particularly looking for new music to listen to. According to Deezer, the new Explore tab will feature a curated selection of music that takes into consideration new artists, genres and trends.

Surprisingly, Deezer is not among the most popular music streaming platforms in the United States, probably the most important market for this type of services. Or at least it’s not among the top five most popular music streaming services in the US, and neither is TIDAL.

The addition of the two new tabs will further improve user experience and make Deezer a more appealing product overall. It will certainly not convince millions of people to suddenly switch to Deezer, but it’s a step in the right direction.


[ad_2]
Source link

Kali Linux 2023.3 Released: What’s New!

0
[ad_1]
Kali Linux 2023.3

Kali Linux 2023.3 is now available, and it includes a variety of new packages and tools, as well as the usual upgrades. The release of Kali Linux 2023.3 arrives three months after Kali Linux 2023.2. 

This upgrades the kernel from Debian Bookworm’s long-term supported LiLinux 6.1 LTS to Linux kernel 6.3, which reached the end of life in early July 2023. Still, the updated kernel ought to provide better hardware assistance.

The Kali Linux 2023.3 version includes nine new tools in particular.

An advanced Linux distribution called Kali Linux is utilized for network security analysis, ethical hacking, and penetration testing.

New Updates in Kali Linux 2023.3

  • Internal Infrastructure: Major improvements to the internal infrastructure have been made.
  • Kali Autopilot: A significant update to the automation attack framework
  • New Tools: Nine new tools have been included.

Improvements to the Internal Infrastructure

The Debian 12 release this summer gave the Kali team the chance to rework, re-design, and re-architecture the infrastructure.

“It is as massive as it sounds, and should not be a surprise that it’s not yet complete! This is where a good amount of our focus has been for this release cycle (and also the next one, unfortunately). We are hoping that the majority of it will be done by the end of the year (so we can get back to what we do best!)”, Kali team said

Further, the team has automated several processes, including the cleaning up of suites (aka branches – kali-experimental and kali-bleeding-edge).

Packaging Tools improved by updating the old files with new functionality and distinct quality-of-life enhancements.

Kali Autopilot 

An automated attack framework is called Kali Autopilot. It resembles an “AutoPwner, ” which employs pre-defined “attack scenarios.”

A web API interface for remote control is included with Kali Autopilot and a GUI tool for designing attacks and producing attack scripts that carry out certain attack sequences, either manually or as a service.

Kali AutoPilot
Kali Autopilot- Automatic attack generator

The developers now claim to have continued to work on the platform, adding and updating features in response to customer input.

“This tool has come along a lot in the last 6 months, and no plans to slow down. As always, it’s shaped by the community; ideas, features, and direction can be submitted and shaped by YOU”, Kali team.

“If you have developed attack scripts for vulnerable machines, we would love to include it on our Kali Purple Hub”.

New Tools in Kali

  • Calico – Cloud-native networking and network security
  • cri-tools – CLI and validation tools for Kubelet Container Runtime Interface
  • Hubble – Network, Service & Security Observability for Kubernetes using eBPF
  • ImHex – A Hex Editor for reverse engineers, programmers, and people who value their retinas when working at 3 AM
  • kustomize – Customization of Kubernetes YAML configurations
  • Rekono – Automation platform that combines different hacking tools to complete pentesting processes
  • rz-ghidra – Deep ghidra decompiler and sleigh disassembler integration for rizin
  • unblob – Extract files from any kind of container formats
  • Villain – C2 framework that can handle multiple reverse shells, enhance their functionality, and share them among instances.

Kali NetHunter Updates

  • LG V20 for Lineage 19.1
  • Nexus 6P for Android 8.0 (Oreo)
  • Nothing Phone (1) for Android 12 (Snow cone) and 13 (Tiramisu) (new)
  • Pixel 3/XL for Android 13 (Tiramisu)
  • Samsung Galaxy A7 for LineageOS 18.1 (new)
  • Xiaomi Mi A3 for Lineage 20
  • Xiaomi Redmi 4/4X for VoltageOS 2.5

Get Kali Linux 2023.3

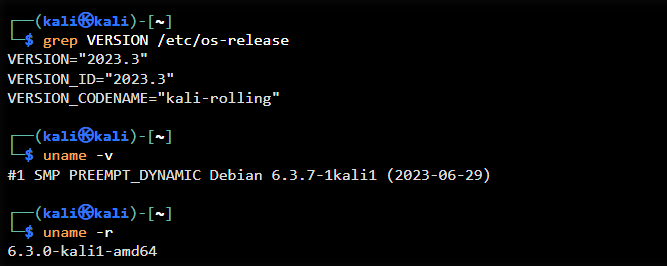
If you already have Kali Linux installed, you can always do a simple update:

You can check which version you are using:

Keep informed about the latest Cyber Security News by following us on Google News, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

Samsung pushes One UI 5.1.1 to Galaxy Z Flip 4 & Galaxy Tab S7

0
[ad_1]

Samsung‘s One UI 5.1.1 update is now available for the Galaxy Z Flip 4 and Galaxy Tab S7 series. These devices follow the Galaxy Z Fold 4 and Galaxy Tab S8 series in picking up the latest One UI version. The Korean firm will push One UI 5.1.1 to several other foldables and tablets.

As of this writing, we have confirmation about the availability of the One UI 5.1.1 update for the Galaxy Z Flip 4 in India and South Korea. The new firmware build numbers for the phone in these two markets are F721BXXUDWH5 and F721NKSU2DWH5, respectively. The OTA (over-the-air) download size of the update is about 2.5GB (via).

The Galaxy Tab S7 series, on the other hand, is initially getting One UI 5.1.1 in Europe. The updated firmware build number for Samsung’s flagship tablet trio varies depending on the model and connectivity variant (Wi-Fi, 4G, or 5G). It’s T875XXU4DWH3 for the Galaxy Tab S7 4G and T976BXXU4DWH3 for the Galaxy Tab S7+ 5G.

Regardless of the build number, the update brings the same changes to these tablets. This applies to the Galaxy Z Flip 4 as well. All of these Samsung devices will soon receive One UI 5.1.1 in more markets, including the US. If you’re using any of these, or the ones listed below, watch out for an update in the coming weeks.

Samsung will push One UI 5.1.1 to more Galaxy devices

One UI 5.1.1 is the latest version of Samsung’s custom Android software. Based on Android 13, it debuted with the Galaxy Z Fold 5, Galaxy Z Flip 5, and Galaxy Tab S9 series a few weeks back. The company later announced that One UI 5.1.1 will reach older foldables and tablets via an update.

A couple of days after that announcement, it rolled out the update to the Galaxy Z Fold 4 and Galaxy Tab S8 series. The Galaxy Z Flip 4 and Galaxy Tab S7 series have now joined too. The Galaxy Z Fold 3, Galaxy Z Flip 3, Galaxy Z Fold 2, Galaxy Z Flip, Galaxy Tab S6 Lite, Galaxy Tab A8, Galaxy Tab A7 Lite, Galaxy Tab Active 3, and Galaxy Tab Active 4 are other confirmed eligible models to receive One UI 5.1.1.

As for the changes, you can see the full official changelog here. One UI 5.1.1 brings several new features and functional improvements, mostly tailored to the big screens of foldables and tablets. Samsung has improved the taskbar, multitasking features, and more. Some of these features won’t be available on some models due to compatibility issues, but the majority will reach all of the devices listed above.


[ad_2]
Source link

The 500Hz Alienware gaming monitor launches early September

0
[ad_1]

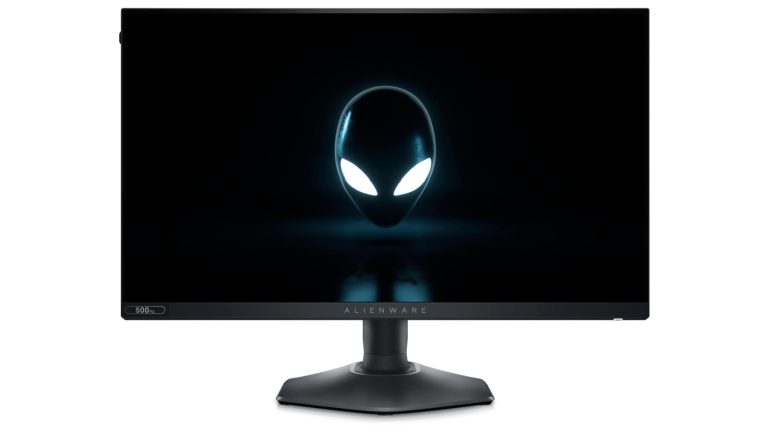
Alienware is back with its latest gaming monitor sporting a 500Hz refresh rate. A display that has the ability to set you up for frame rates so fast, clarity of motion so smooth, you just might think you’re Sasuke Uchiha having just unlocked his Sharingan as you take out opponents.

Alienware claims its newest monitor is the world’s fastest IPS gaming monitor. And that very well might be true. But it’s also important to note that this is based on Alienware’s own internal testing and analysis from June of this year. Even if by some measure it wasn’t the fastest, a 500Hz gaming monitor is still wicked fast. So much so that you’d be leagues ahead of most gamers when it comes to frame rates. Provided, of course, that the rest of your rig is set up to handle it.

One also very important detail worth reiterating, is that the 500Hz is with the display overclocked. Its native refresh rate is actually 480Hz. Which again, is still way above the numbers that most gamers are probably working with. So from a competition standpoint, that’s a decent leg up.

The Alienware 500Hz gaming monitor is available for under $700

Alienware 500Hz gaming monitor (2)

Alienware officially announced this monitor back during CES 2023 in January. But it didn’t mention a release date at the time, and there was no word of a price tag. Now the company has shared both of those details. It retails for $649.99 and launches officially on September 12.

So you have a couple of weeks left to wait. When it comes to the design, Alienware is taking both esports and desk space into account here. These two things are heavy focuses for the build. To that end, the monitor comes with a hexagonal base on the stand that takes up less surface area on your desk. So even if you have a small desk, you have more room for peripherals this way. Speaking of which, the monitor also features the hidden headphone hangar that Alienware debuted on some of its other monitors from the middle of last year.

Additionally, the monitor features support for AMD FreeSync, and offers a 24.5-inch panel with a Full HD resolution. If you value frame rates above all else, this might be the monitor for you.


[ad_2]
Source link

WhatsApp introduces nameless groups and explores a recent history-sharing feature

0
[ad_1]

WhatsApp has more than 2 billion users around the world, and it tries to keep them satisfied by introducing new features and updates regularly. Just recently, the Meta-owned app added support for high-resolution photos and introduced screen sharing during video calls. Now, users can create groups without adding any names, which is an update from before, when users were required to put in a group name when creating a new one.Mark Zuckerberg, the CEO of Meta, revealed this update on his Facebook page. According to reports from TechCrunch, the company clarified that, unlike the typical WhatsApp groups that can accommodate more than 1,000 participants, the unnamed groups will be limited to a maximum of six participants.

These groups will be dynamically named based on the added users. The name of the group will appear differently for each participant, contingent on their contact listings on their phone. The company has plans to introduce this new group feature globally within the upcoming weeks.


That is not all, as it appears that WhatsApp focus lies on groups these days because, according to Wabetainfo, it is developing a new group feature named “Recent History Sharing.” This feature is set to automatically share messages sent within the group 24 hours before a new person joins. The ability to use this option will be limited to group admins once it becomes available in a forthcoming WhatsApp update.

This feature could be warmly welcomed and certainly prove to be useful. It addresses the challenge new members face when trying to join group chats and participate in discussions without proper context. For now, the feature is under development, but it will come out eventually.


[ad_2]
Source link

What Are Brute Force Attacks, and How to Protect Your APIs?

0
[ad_1]
What Are Brute Force Attacks

Brute force attacks have been one of the most common attack types. In Q1 2022, brute force made up 51% of all attacks! These attacks often pave the way for other types of threats and have devastating consequences for the organization.

Brute force on APIs is a bigger problem since APIs programmatically expose data, functionalities, and business logic. You need to act urgently to stop these attacks and keep your digital assets secure from attackers.

Want to know how? Keep reading to find out more about brute force attacks and ways to protect your APIs, apps, and websites against them.

Table of Contents

What is a Brute Force Attack?
Brute Force in APIs
Brute Force vs. Other Cracking Techniques
Types of Brute Force Attacks
How Do Brute Force Attacks Work? 
Real-life Examples
What Factors Lead to Brute Force Attacks?
Who Are Common Targets for Brute Force Attacks?
What Makes Brute Force API Attacks Dangerous?
Protecting Against Brute Force API Attacks
Brute Force Attack Detection
Access violations
Strong Password Policies & Multifactor Authentication
Robust Access Control and Authorization Policies
Lockout Policies
Progressive Delays
Implement CAPTCHA Challenges Intelligently
Use Hashing to Secure Passwords
Bot Mitigation
Conclusion

What is a Brute Force Attack?

Brute force attacks are common, simple, and easy-to-orchestrate credential cracking/ password guessing attack types. In these attacks, the threat actor uses trial and error to decode passwords, login credentials, API keys, SSH logins, encryption keys, hidden web pages, and content. Thereon, they gain unauthorized access to apps, APIs, accounts, systems, and networks.

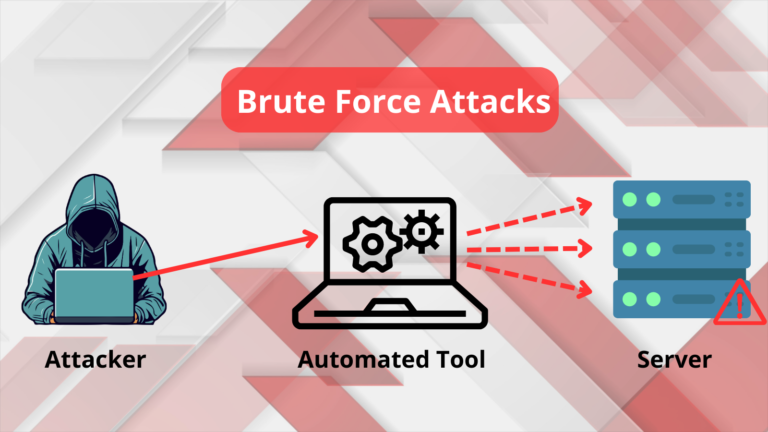
Attackers keep guessing usernames and passwords till they find valid combinations. They systematically try all possible combinations of letters, numbers, and symbols until they crack the credentials. Attackers may use manual or automated methods to inject username passwords and find the right credentials.

Brute Force in APIs

Brute force in APIs is an attack where the threat actors leverage tools to continuously send requests to APIs to guess correct combinations of credentials. The end goal may be anything from stealing an account by brute forcing API authentication forms to exfiltrate sensitive data by brute forcing logins.

Brute Force vs. Other Cracking Techniques

Brute force attacks don’t use an intellectual strategy to crack credentials; they use a simple trial-and-error method instead. They try exhaustively to break credentials by trying various combinations of characters till they find a combination that allows them to enter. This is the main difference between brute force and other stuffing & cracking methods.

In credential stuffing attacks, attackers throw bona fide login credentials to fool the API/ app into believing they are legitimate users. To this end, they use stolen credentials and keys.

In brute force attacks, attackers repeatedly attempt different character combinations until they gain access to the API or app.

Types of Brute Force Attacks

  • Simple brute force attacks where attackers use a simple, systematic approach to guess and crack credentials without relying on intellectual strategy or logic. Automated tools and scripts are typically used to automate guessing credentials.
  • Dictionary attacks are where attackers use a common database of words, strings, and phrases – a dictionary. They start with a word/ phrase from the dictionary and try combinations of letters and characters to determine the login credentials.
  • Hybrid brute force attacks are where attackers combine aspects of simple and dictionary attacks. They use external logic to determine password variations that may have a higher probability of success and then amend those to try various combinations.
  • Rainbow table attacks where attackers use a rainbow table – a precomputed table/ dictionary of plaintext passwords and hash functions corresponding to them. Using the rainbow table, they try to reverse cryptographic hash functions.
  • Reverse brute force attacks where attackers use common/known passwords or collections of passwords against possible usernames/ account numbers by trying different combinations.
  • Password spraying attacks where attackers take commonly used passwords like admin or 123456 and use them across different accounts instead of trying different password combinations. This is used in cases where account lockout policies are in place, and attackers have only limited attempts to crack credentials.
  • Botnet brute force attacks where attackers leverage powerful bots to brute force APIs, apps, and networks. One of the biggest drawbacks of brute force for attackers is that it takes days, even months, to crack credentials, especially more complex ones. With additional security measures like rate limiting and account lockout policies, the challenges are even bigger. But botnets help overcome these challenges. They provide high computing power to attackers and help them evade traditional defenses while infusing speed and efficiency into the process.

How Do Brute Force Attacks Work? 

Traditional brute force attacks typically use exhaustive manual effort to crack credentials. But given the security measures at play and the time it takes to crack a single complex password, attackers today leverage automated tools, scripts, and powerful botnets to brute force APIs, apps, and networks.

These tools and bots can send voluminous server requests and make hundreds of thousands of login attempts per hour. They can guess and find combinations that work in minutes rather than weeks or months.

There are 3 broad steps in brute force attacks that use automated tools and bots.

  1. Attackers identify the target URLs of the APIs, apps, or sites they want to attack and preconfigure parameter values in the brute force tool.
  2. They run the brute force processes using the tool/ bot, which attempts to identify all valid credentials.
  3. Upon identifying successful login credentials, attackers log in and do their bidding.

Here are some of the common tools attackers use for brute forcing:

  • THC-Hydra runs a large number of password combinations using simple or dictionary-based methods to crack network password protocols.
  • Aircrack-ng uses a dictionary of widely used passwords to breach wireless networks.
  • John the Ripper is a tool that exhaustively runs possible combinations using a dictionary.
  • Hashcat is the fastest CPU-based cracking tool that runs simple brute force, rule-based, and hybrid attacks.
  • Ncrack helps crack network authentication and supports various attack types.
  • RainbowCrack is one of the fastest cracking tools that leverage rainbow tables.

Real-life Examples

The Canadian Revenue Agency faced a brute force attack in 2020, compromising 11,000 accounts of CRA and other government-related services. Attackers used previously stolen credentials to brute force the agency.

In 2018, Magneto, an e-commerce platform, was a victim of a brute force attack that compromised its admin panels. No less than 1,000 account credentials were exposed on the dark web.

In 2018, the Northern Ireland Parliament was brute forced, exposing the accounts of some of its members. Hackers are known to have used several combinations to crack passwords and access the mailboxes of these members.

TaoBao, an Alibaba e-commerce site, was brute forced in 2016, compromising 21 million accounts (1/5th of all TaoBao accounts). Attackers used a database of 99 million usernames and passwords to orchestrate this brute-force attack.

What Factors Lead to Brute Force Attacks?

One of the top causes of brute force attacks is poor password practices.

Users, including admin accounts, use simple or generic passwords like 123456, abdce, 111111, or admin. These are easy to crack.

Even when users use stronger passwords, they reuse them across accounts and platforms. So, if their credentials were stolen from one account, all their other accounts using the same credentials are at risk of exposure.

Organizations use predictable taxonomies for the login credentials, creating patterns that are easy to detect. For instance, the employee’s initial and last names followed by the company name for login IDs are commonly used.

Many organizations continue to store credentials, API keys, encryption keys, and passwords in plaintext or poorly encrypted databases. So, attackers can exfiltrate these databases and use them for brute forcing APIs and apps.

Organizations continue to rely on passwords or keys as their only authentication mechanism. Even when organizations use MFA (multifactor authentication), they are still at risk if they don’t have proper authorization and role-based access control measures.

Furthermore, organizations often overlook the importance of implementing multi-layered security measures such as account lockout and rate limiting to prevent brute force attacks.

Who Are Common Targets for Brute Force Attacks?

If your website/ API/ app/ system requires user authentication, it will be targeted by threat actors. Brute force attacks are much easier to orchestrate than other attacks since attackers don’t have to scan for and develop ways to exploit vulnerabilities.

However, e-commerce APIs, apps, and sites are the most common targets of these attacks. This is because they process payments and have access to large volumes of sensitive customer data such as PII, banking information, credit card details, and so on. Suppose an attacker gains access to an e-commerce API or site. In that case, they can easily perform data breaches, financial theft, identity theft, sell user information on the dark web, and so on. This causes distrust among users and affects the reputation of the organization.

What Makes Brute Force API Attacks Dangerous?

Impact

The impact of brute force on APIs is severe and damaging. Because APIs expose data and functionalities by their very nature, attackers brute force them to discover login credentials and API keys to access user accounts and the app to find more vulnerabilities.

By brute forcing APIs, attackers can also cause downtimes and crashes for other users. They could lock out legitimate users by brute forcing APIs with a lockout mechanism for failed logins.

Successful login attempts enable attackers to exfiltrate user information, keys, and so on that they can sell on the dark web. They could also spread malware, engage in account takeover, and perform other attacks.

Other Reasons Why They Are Dangerous

  • They are easy and simple to orchestrate, especially with the easy availability of automation tools and bots for hire.
  • The weak password problem still exists.
  • Even if attackers don’t find or can’t use other vulnerabilities, brute force attacks work.

Protecting Against Brute Force API Attacks

Brute Force Attack Detection

Before knowing how to prevent them, you need to understand how to detect brute-force attacks.

Firstly, you need to continuously monitor incoming traffic and user behavior using an API-specific, fully managed, intuitive security solution. AppTrana API protection uses behavioral and pattern analysis to identify anomalous behaviors and patterns. Some examples :

  • Serious failed login attempts
  • Unusual patterns of failed logins
  • Unusual user behavior after successful login
  • One successful login followed numerous failed attempts
  • Successful login coming in from an unusual IP address
  • Successful login into different accounts from the same IP address
  • Unusual network activity
  • Unusually high number of login requests to APIs

Access violations

The security solution must provide real-time alerts and triggers when unusual activities happen. Only then you can take instant action to stop attacks.

Your API-specific security solution must include automated scanning tools equipped with AI-ML and threat intelligence to find authentication flaws that allow brute-force attacks proactively.

You must use manual pen-testing to find authentication flaws and other weaknesses that enable brute forcing of your APIs. To ensure a comprehensive assessment, following an API penetration testing checklist is essential, which will guide you through the systematic evaluation of your API’s security measures.

Strong Password Policies & Multifactor Authentication

This is the most important way to prevent brute force API and other attacks.

  • Create complex passwords containing a combination of alphanumeric and special characters.
  • Reject generic and weak passwords for enhanced security.
  • Avoid common patterns when crafting usernames and passwords.
  • Ensure password expiration at regular intervals and disallow the reuse of prior passwords.
  • Educate users on the significance of crafting distinct passwords for individual accounts or platforms.
  • Explore the adoption of a password manager or embrace passwordless authentication.
  • Prevent storing passwords, keys, and credentials in plaintext.
  • Implement 2FA or MFA as mandatory measures for APIs and websites, particularly for those granting access to sensitive data and features. These steps provide supplementary safeguards for your APIs and accounts.

Robust Access Control and Authorization Policies

Even when a successful login happens, the attacker shouldn’t be able to access too much sensitive information. This is why role-based access control and strong authorization policies are necessary. Also, ensure that unused accounts, especially high-permission accounts, are closed.

Lockout Policies

The account should automatically be locked if the number of failed attempts exceeds the preset limit. Only the administrator should be able to unlock the account after verification from the user.

Remember, there is a possibility that competitors brute force you to lock out your legitimate users. By doing so, they can create mistrust and a loss of reputation for your organization. This is why you need to prohibit multiple login attempts from the same IP address for different accounts.

Progressive Delays

You can also lockout accounts temporarily after failed login attempts and implement progressive delays between each failed login. This slows down brute force attacks.

Implement CAPTCHA Challenges Intelligently

Brute force tools and bots cannot perform CAPTCHA challenges. So, you can create hurdles for attackers by implementing these challenges. Your security solution must implement these challenges intelligently based on real-time insights.

Use Hashing to Secure Passwords

Randomized password hashing is a vital rest API brute force protection measure. Password hashing protects the systems even when it is compromised owing to successful attacks.

Bot Mitigation

Since modern-day brute force attacks widely leverage bots and automated tools, you must use a security solution that offers intelligent, fully managed bot mitigation capabilities.

Conclusion

With an API-specific, fully managed, comprehensive security solution like AppTrana, you can proactively hunt down brute force threats and prevent attackers from brute forcing your APIs.
[ad_2]
Source link

Samsung readying a special version Galaxy Z Fold 5, seven new products

0
[ad_1]

Samsung launched seven new Galaxy products during its Galaxy Unpacked event in late July. The company debuted two foldables, three flagship tablets, and two smartwatches at the event. However, it may not be done for the year yet. The Korean firm has eight more Galaxy devices lined up for launch in the coming months, including a special version of the Galaxy Z Fold 5.

Galaxy Z Fold 5 Thom Browne Edition is coming soon

Over the years, Samsung has launched Thom Browne Editions of several Galaxy foldables. It teamed up with the New York City-based fashion designer for customized versions of the Galaxy Z Flip, Galaxy Z Fold 2, Galaxy Z Flip 3, and Galaxy Z Fold 3. However, the company didn’t launch Thom Browne Editions of last year’s Galaxy Z Flip 4 and Galaxy Z Fold 4.

With that in mind, there has been little hope of Samsung teaming up with the designer again for its latest foldables. However, it turns out the partnership hasn’t ended. The company recently took to X to tease a new book-like foldable with the iconic Thom Browne stripes. It doesn’t require rocket science to determine that we are looking at a customized Galaxy Z Fold 5 here.

Samsung didn’t reveal when the Galaxy Z Fold 5 Thom Browne Edition will arrive. However, we may not have to wait for much longer. Note that it’s the same foldable phone that arrived in stores a couple of weeks back. However, its external appearance has been customized with unique colors. If history is any indication, Samsung will offer the device in a special package consisting of other goodies. Naturally, it will cost more than the standard version, which starts at $1,800.

Samsung has seven more new Galaxy products in the pipeline

The Galaxy Z Fold 5 Thom Browne Edition may not be a completely new product, but Samsung does have more in the pipeline. As pointed out by X tipster @TheGalox, the company is readying at least seven new Galaxy devices. These include the Galaxy S23 FE, Galaxy Tab S9 FE, Galaxy Tab S9 FE+, Galaxy Tab A9, Galaxy Tab A9+, Galaxy Buds 3, and Galaxy SmartTag 2.

Rumors about these devices have been around for a long time now. Some of them have even received regulatory approvals and picked up support pages on Samsung’s official website. It remains to be seen whether the Korean behemoth will unveil them all together. In that case, we could have a major Samsung launch event next month. The Galaxy S23 FE is rumored to arrive in September.


[ad_2]
Source link

Samsung partnered up with ‘MINI’ to unveil ‘MINI Incubator’

0
[ad_1]

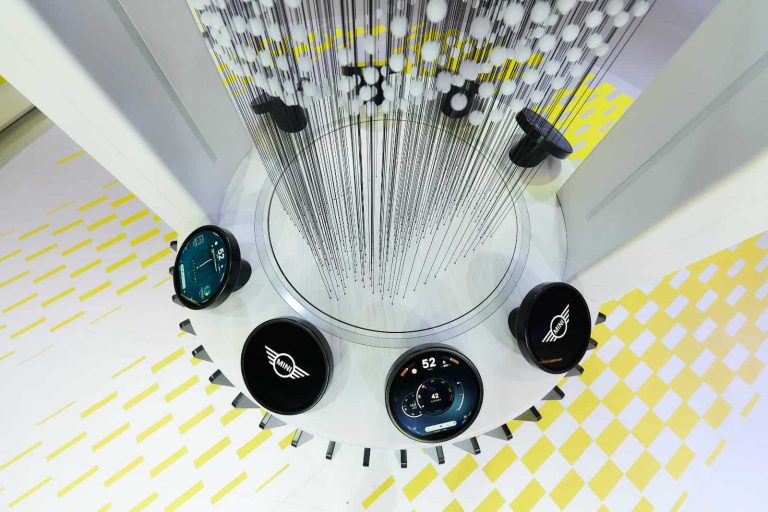
MINI and Samsung Display jointly unveiled the ‘MINI Incubator’ sculpture at Gamescom 2023 in Cologne, Germany. Samsung Display’s 9.4-inch round OLED display takes the spotlight, getting attention from gamers and tech enthusiasts.

It is prominently positioned within the MINI exhibition space. This cylindrical display tower proudly showcases ten 9.4-inch round OLEDs, drawing inspiration from iconic science fiction laboratories. The design highlights the pivotal role of cutting-edge display technology in shaping MINI’s visionary mobility solutions.

In perfect harmony with the MINI Incubator, Samsung Display seizes the opportunity to showcase its OLED mastery, emphasizing automotive displays. A standout feature is their commitment and efforts to environmental sustainability via means of reduced plastic components. The details and features is that the displays offer true black rendering, infinite contrast, and adaptable flexible designs. Moreover, advanced technology effectively reduces blue light emission. Samsung Display further enhances the experience with an engaging OLED Finder Experience Zone, captivating avid gamers and tech enthusiasts attending Gamescom.

Head of Samsung display’s views on the collaboration

Brad Jung, VP and Head of Samsung Display’s Mobile Display Marketing Team, expresses excitement about the collaboration. Leveraging Samsung Display’s unrivaled expertise in OLED technology within realms of mobility, Brad Jung eagerly anticipates empowering customers with captivating visual experiences. With most of the main experience of most customers being based on the visual appeal. The Head of Samsung Display aims to improve on the visual aspects with this solution.

Building on tradition, MINI proudly returns to Gamescom as an official sponsor and dedicated mobility partner for the second consecutive year. The ‘MINI Lab’ theme of their exhibition booth curates a mobility experience tailored to young gamers. By seamlessly blending innovation and mobility, MINI effectively underscores its commitment to shaping the future of gaming-related encounters and beyond.


[ad_2]
Source link