Dirac and Bluesound partner to boost your audio setup

0
[ad_1]

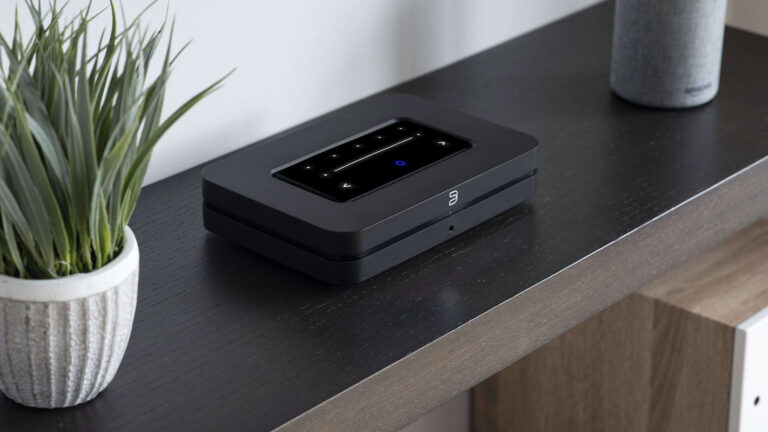
Life is better when we all work together! Dirac and Bluesound, two popular audio companies, have partnered to help boost your room’s audio setup. Through this partnership, select Bluesound devices will come with Dirac Live out of the box. This is great for people who want to get the most from their speakers.

When you listen to music in your room, there’s a chance that your room could have a negative effect on the sound you’re hearing. It could be the shape of the room, the objects in it, etc. These could cause sound waves to clump in certain areas. It could also cause some sound waves to be too quiet.

Dirac is a company that primarily focuses on room audio correction. This tunes the audio so that it compensates for whatever effect your room has on it. It will tune it so that the audio sounds crisp and clear.

Dirac partnered with Bluesound to help improve your multi-room audio

If you’re an audiophile, audio engineer, composer, etc., then you’ll want to make sure that you’re hearing the audio as clearly as possible. This is true even if you have a quality speaker. Bluesound is a company that makes some great speakers. The company specializes in upper-tier and luxury speakers. Its portfolio includes speakers for personal use and for your home theater.

If you have such high-quality speakers, then you’ll want to make sure that you’re hearing the best possible sound. This is where this partnership comes in. As noted by the two companies, future Bluesound devices will come with Dirac Live compatibility out of the box. While this is good news, neither company indicated which devices will come Dirac-ready.

If you buy one of those devices, it will be able to use the Dirac Live software once you purchase a Dirac license. This means that you’ll be able to calibrate the Bluesound speaker using the Dirac Live software right away.

Bringing the Dirac software to you

Dirac Live is a software solution, but you have the option to purchase a calibration kit. The report states that Bluesound will make calibration kits available to purchase on its site. On the Bluesound website. The company will offer the kit when the first Dirac-ready device becomes available to purchase.

What’s neat is the fact that the companies are exploring making these speakers backwards-compatible. So, your current Bluesound speakers might eventually be compatible with Dirac Live.

If you’re excited about improving your audio setup, then you’ll want to keep an ear out for new updates.


[ad_2]
Source link
ASUS reveals the VivoWatch 6, its new health-focused smartwatch

0
[ad_1]

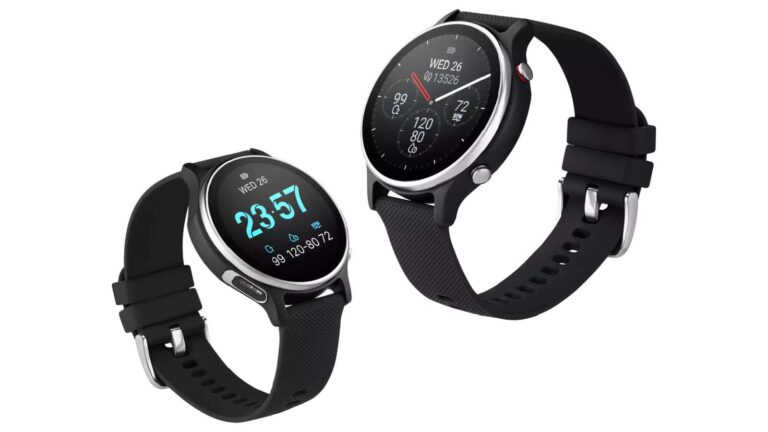
ASUS has announced the VivoWatch 6 today, and it’s the company’s new flagship smartwatch for “staying in touch with your wellness”. The VivoWatch 6 is in line with ASUS’ previous smartwatch offerings in the Vivo line, focusing less on general smartwatch features and more on health management.

While much of the watch is pretty standard for what you would expect a smartwatch to have, it does come with one unique feature that no other smartwatch on the market offers. The VivoWatch 6 isn’t running on Wear OS either. Instead, ASUS has opted to continue using its own OS and UI. The watch works with both Android and iOS too, so if you aren’t fond of the Apple Watch, you can pair this to your iPhone instead.

Again this is more of a health and fitness watch than a smartwatch. It’ll certainly show you smartphone notifications and you can use the VivoWatch 6 as an alarm clock, a stopwatch, or even a remote camera button for your phone. But the major focus is on health. “Leveraging cutting-edge innovations and years of medical expertise, ASUS VivoWatch 6 is designed to help users keep track of their long-term health goals easily, allowing them to monitor vital health stats anytime, anywhere to truly achieve preventive healthcare,” said Sharon Pan, senior director of Smart Health Product Planning at ASUS.

The VivoWatch 6 is the world’s first smartwatch announced with finger-based measurement sensors

This is what really sets the VivoWatch 6 apart from other smartwatches on the market right now. ASUS has equipped the watch with two medical-grade ECG and PPG sensors that use your fingertips. Two sensors placed on the sides of the watch face allow you to measure things like body fat and skeletal muscle percentages. In addition to water content and basal metabolic rate. At any point, you can place your index finger and thumb on the sensors (one on each side) and measure any of these metrics.

ASUS says this is a more accurate way of taking those measurements due to the higher microvascular density in your fingertips. There’s a set of sensors on the back of the watch as well. These measure things like your body’s vitals, including during sleep, and are used for things like heart rate and sleep tracking.

ASUS VivoWatch 6 (2)

Battery life for days

There’s always one main issue that most people have with their smartwatches. Battery life. Or in some cases, lack thereof. The VivoWatch 6 shouldn’t present that issue to its wearers. In its regular mode, it offers up to 9 days of battery life on a single charge, and that’s a significant amount of days more than what you’ll get with anything that runs on Wear OS. And if you put it into battery-saving mode, ASUS says it’ll last up to 14 days.

In terms of other specs, the VivoWatch 6 has a 1.39-inch AMOLED display protected by Gorilla Glass 3. The display also has a peak brightness of 350 nits. Additionally, it has a 5ATM rating for water resistance. The battery meanwhile, is 290mAh. It comes with dual-frequency GPS as well. Overall, on paper, it’s a capable smartwatch that has a lot to offer the health-conscious user.

ASUS doesn’t have pricing or availability listed on the website. However, previous VivoWatch models are available in the US both from ASUS directly and from retailers like Amazon. So this should make it to the US as well. That being said, PhoneArena does mention that ASUS has stated the VivoWatch 6 would cost £110 / €130 / $140.


[ad_2]
Source link

YouTube Premium adds new features like Jump Ahead and Picture-in-Picture for Shorts

0
[ad_1]

Image credit — PhoneArena

YouTube Premium members are getting several new features aimed at improving the user experience, including easier skipping to key video moments, offline viewing options, and early access to experimental features.

Skipping to favorite parts in videos

Premium subscribers using Android devices in the U.S. can now take advantage of a new “jump ahead” button which will appear when you double-tap to skip ahead. This feature is designed to quickly navigate to the most interesting parts of a video. The feature is powered by AI and viewership data, and will be available to iOS users in the coming weeks.

A new “jump ahead” button will appear when you double-tap to skip ahead on a video | Video credit — Google

Picture-in-Picture mode for YouTube Shorts

Multitasking while watching YouTube Shorts will now be easier with the new picture-in-picture feature available for Android devices. This allows users to browse other apps or check messages while Shorts continue playing in a small window.

YouTube Shorts now have a picture-in-picture mode for Premium subscribers | Video credit — Google

Early access to experimental features

In addition to these new features, YouTube Premium subscribers also get early access to experimental features such as:
  • Smart downloads for YouTube Shorts: Automatically download new Shorts to your phone for offline viewing.
  • Conversational AI: An assistive tool that can answer questions and suggest related content on Android devices in the US.
  • Redesigned Watch Page: A new watch page on web to enhance viewing experience and facilitate content discovery and engagement.

These new features are just the latest additions to YouTube Premium. All of these, according to the company, have contributed to a major milestone for YouTube, with over 100 million YouTube Music and Premium subscribers worldwide.

It should be noted that this plan also includes features like enhanced 1080p HD video quality and the ability to pick up where you left off on any video. YouTube Music Premium members also get ad-free music, offline listening, background play, and the Samples tab to discover new music. It’s the best option right now for an ad-free experience on YouTube without resorting to ad-blocking measures that could compromise the status of your account.


[ad_2]
Source link

YouTube may bet heavily on the AI-generated music segment

0
[ad_1]

It seems that YouTube wants to invest fully in the AI-generated music segment. The company wants to do it fairly, reaching licensing agreements with record labels. This could greatly benefit the YouTube Music service too. However, multiple artists do not agree with the use of AI in music.

AI-based tools took the tech industry by storm, offering capabilities that were unimaginable until relatively recently. They can generate music, images, and even videos. However, this sparked a debate about possible copyright infringements. After all, it is sometimes difficult to determine whether the multimedia used to train AI models is licensed. This has led to situations such as lawsuits against services like AI Udio and Suno.

YouTube allegedly seeking license deals with major labels for AI-Generated music

Due to the sudden impact of AI on the segment, there is still no complete clarity on fair agreements between artists, record labels, and developers of AI-powered tools. However, platforms like YouTube do not want to be left behind in the emerging AI-generated music segment. According to a recent report, the company would be in talks with Universal, Sony, and Warner. The goal would be agreements to use music from artists on those labels to train AI models.

The company would look for agreements based on a single payment that allow them to use the artists’ musical catalog. That said, artists may not be entirely on board if there is not fair compensation for them as well. However, being able to grant musical rights to third parties will depend on how much control the record labels have over the media content.

Multiple artists still reluctant to use AI in the music industry

In April, more than 200 artists signed an open letter against AI in the music industry. More specifically, they criticized the use of their work to train AI models without authorization. As of today, there is still no firm legislation for this type of situation. Meanwhile, artists, record labels, and third parties will have to seek favorable agreements through negotiation.

YouTube has tried to ensure that the use of generative AI on its platform does not mean that artists lose control over their work. The company requires that AI-generated content (be it music or videos) be labeled as such. Additionally, they allow artists to request the removal of media based on their works if they wish. It will be interesting to see if the negotiations result in agreements that leave all parties happy. After all, generative AI is here to stay, and the industry must adapt to it.


[ad_2]
Source link

TP-Link Omada Vulnerabilities – Attackers Execute Remote Code

0
[ad_1]

Multiple vulnerabilities have been identified in the TP-Link Omada system, a software-defined networking solution widely used by small to medium-sized businesses.

These vulnerabilities, if exploited, could allow attackers to execute remote code, leading to severe security breaches.

The affected devices include wireless access points, routers, switches, VPN devices, and hardware controllers for the Omada software.

Vulnerability Details

Identified Vulnerabilities

Twelve unique vulnerabilities were identified and reported to the vendor following our responsible disclosure policy.

Cisco Talos researchers have identified twelve unique vulnerabilities in the TP-Link Omada system.

These vulnerabilities were reported to the vendor following a responsible disclosure policy. The affected devices include:

  • EAP 115 and EAP 225 wireless access points
  • ER7206 gigabit VPN router
  • Omada software controller

Scan Your Business Email Inbox to Find Advanced Email Threats - Try AI-Powered Free Threat Scan

The vulnerabilities are categorized as follows:

  1. TALOS-2023-1888: A stack-based buffer overflow in the web interface Radio Scheduling functionality of the TP-Link AC1350 Wireless MU-MIMO Gigabit Access Point (EAP225 V3) v5.1.0, build 20220926. This can lead to remote code execution.
  2. TALOS-2023-1864: A memory corruption vulnerability in the web interface functionality of the same device, leading to denial of service.
  3. TALOS-2023-1862: A command execution vulnerability in the tddpd enable_test_mode functionality of the TP-Link AC1350 Wireless MU-MIMO Gigabit Access Point (EAP225 V3) and TP-Link N300 Wireless Access Point (EAP115 V4). This can lead to arbitrary command execution.
  4. TALOS-2023-1861: A denial-of-service vulnerability in the TDDP functionality of the TP-Link AC1350 Wireless MU-MIMO Gigabit Access Point (EAP225 V3), allowing an adversary to reset the device to factory settings.
  5. TALOS-2023-1859: A post-authentication command execution vulnerability in the web filtering functionality of the TP-Link ER7206 Omada Gigabit VPN Router.
  6. TALOS-2023-1858: A post-authentication command injection vulnerability when configuring the web group member of the TP-Link ER7206 Omada Gigabit VPN Router.
  7. TALOS-2023-1857: A post-authentication command injection vulnerability when configuring the WireGuard VPN functionality of the TP-Link ER7206 Omada Gigabit VPN Router.
  8. TALOS-2023-1856: A post-authentication command injection vulnerability when setting up the PPTP global configuration of the TP-Link ER7206 Omada Gigabit VPN Router.
  9. TALOS-2023-1855: A post-authentication command injection vulnerability in the GRE policy functionality of the TP-Link ER7206 Omada Gigabit VPN Router.
  10. TALOS-2023-1854: A post-authentication command injection vulnerability in the IPsec policy functionality of the TP-Link ER7206 Omada Gigabit VPN Router.
  11. TALOS-2023-1853: A post-authentication command injection vulnerability in the PPTP client functionality of the TP-Link ER7206 Omada Gigabit VPN Router.
  12. TALOS-2023-1850: A command execution vulnerability in the guest resource functionality of the TP-Link ER7206 Omada Gigabit VPN Router.

Technical Details

TDDP on Wireless Access Points

The TP-Link Device Debug Protocol (TDDP) is available on many devices and is exposed for 15 minutes of a device’s runtime. This service allows remote servicing without manual activation.

During this time, various functions on the device are exposed, which can be exploited by attackers.

Example Code Snippet:

struct tddp_header {

    uint8_t version;

    uint8_t type;

    uint8_t code;

    uint8_t direction;

    uint32_t pay_len;

    uint16_t pkt_id;

    uint8_t sub_type;

    uint8_t reserved;

    uint8_t digest[0x10];

};

Payload Construction:

Python

digest_req = b''

digest_req += struct.pack('B', self.version)

digest_req += struct.pack('B', self.type)

digest_req += struct.pack('B', self.code)

digest_req += struct.pack('B', self.direction)

digest_req += struct.pack('>L', self.pkt_len)

digest_req += struct.pack('>H', self.pkt_id)

digest_req += struct.pack('B', self.sub_type)

digest_req += struct.pack('B', self.reserved)

digest_req += b'\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00'

digest_req += self.payload

digest = hashlib.md5(digest_req).digest()

Vulnerability Impact

Factory Reset Device (TALOS-2023-1861)

The TDDP service can factory reset the device through a single ENC_CMD_OPT request, passing a subtype code of 0x49 via the payload field.

This causes the device to reset its configuration to the factory default and act abnormally until the next power cycle.

Gain Root Access (TALOS-2023-1862)

The TDDP service can also indirectly obtain root access on specific devices through the enableTestMode command.

This command causes the device to execute a shell script from a predefined address, allowing an attacker to execute any command as the root user.

The discovery of these vulnerabilities highlights the importance of regular security assessments and timely patching of network devices.

TP-Link has been notified and has released patches to address these issues.

Users are strongly advised to update their devices to the latest firmware to mitigate potential risks.

Free Webinar! 3 Security Trends to Maximize MSP Growth -> Register For Free


[ad_2]
Source link

Google already had defense against Snowblind Android malware

0
[ad_1]

Yesterday, a security firm published a report about a never-before-seen Android malware named Snowblind. It allegedly abuses a built-in Android safety feature to avoid detection. Its novel technique made all modern Android devices and apps vulnerable to it. However, Google refutes the claim. In a statement to Android Headlines, the Android maker said it was already aware of the malware and has implemented safety measures against it.

Google Play Protect can detect and block Snowblind Android malware

Discovered by mobile app security provider Promon, Snowblind is a new Android banking malware that manipulates the Android system to compromise apps without detection. It attacks Android’s safety tool called “seccomp” (secure computing) to bypass security checks and stealthily execute malicious activities. The attackers can steal login credentials and other information to make unauthorized financial transactions on infected devices.

Promon said it had never seen “seccomp being used as an attack vector before,” making Snowblind a first-of-its-kind Android malware. The firm added that it does not expect many apps to have protections against it. The security provider encouraged its customers and other app developers to upgrade to its Promon SHIELD version 6.5.2 or newer to keep their products safe from Snowblind and other potential seccomp-based security attacks in the future.

Shortly after we reported on Promon’s discovery, Google reached out saying it was aware of Snowblind and its techniques. “We can confirm we were already aware of this malware before this report,” the company said in an emailed statement to us. It didn’t mention the malware’s name for obvious reasons—Promon gave the name Snowblind because it was the first to publicly disclose this Android banking malware abusing a system feature.

“Based on our current detection, no apps containing this malware are found on Google Play,” the official statement added. “Android users are automatically protected against known versions of this malware by Google Play Protect, which is on by default on Android devices with Google Play Services. Google Play Protect can warn users or block apps known to exhibit malicious behavior, even when those apps come from sources outside of Play.”

Snowblind may not be as dangerous as it originally sounded

Promon’s report suggested that Snowblind is a dangerous malware and that most Android apps lack protection against it. However, Google’s statement clarifies the threat. While the malware exists, Google Play Protect automatically blocks its activities, protecting Android users from all known versions of Snowblind. Google Play Protect can also detect malicious behavior in apps installed from outside of the Play Store. However, it is always safer to only download apps from official stores.


[ad_2]
Source link
Here are Samsung’s new Galaxy Buds 3 and Buds 3 Pro!

0
[ad_1]

Well, the rumors seem to be true; Samsung is giving up its identity in the earbuds market and opting for an AirPod aesthetic. We’ve been seeing a ton of leaked images and renders about these new buds. Now, thanks to Evan Blass, we have some high-res images of the Galaxy Buds 3 and Galaxy Buds 3 Pro.

Oh, we miss the olden days when Samsung was the antithesis of Apple. Sure, people mocked the Galaxy S5’s “Band-Aid” back, but it was unique, for goodness’ sake! It contrasted what Apple was doing with the iPhone, and people appreciated it. Now…. we’re seeing the Korean giant copy Apple’s homework more than we’d like to see.

Recent leaks of the Galaxy Buds and the Galaxy Watch 7 show that Samsung is leaning more towards Apple’s aesthetic. The Galaxy Watch might bring a square design when its previous watches sported beautiful circular designs.

Here are high-res images of the Galaxy Buds 3 and Buds 3 Pro

Looking at the renders of these upcoming earbuds, it’s not hard to see the AirPod inspiration. The most notable thing is the addition of the stem design. Several brands opted for this design, but Samsung famously brought wild and interesting designs for its earbuds. We all remember the Galaxy “Beans.”

However, these images show us two types of earbuds. We expect one pair to be the Galaxy Buds 3 and the other to be the Galaxy Buds 3 Pro. Starting off with the base model, these look like your typical stemmed earbuds. We see that there’s a black line that runs down the stem. That’s one defining feature.

One thing that reports point to is a squeeze gesture. If so, then that will be another defining feature of these earbuds. We’re not sure if squeezing the stem will make interacting with them any easier.

On the outside of the bud, we see two microphones. We don’t know if there’s going to be a microphone on the stem.

Galaxy Buds 3 Pro

Now, let’s move on to the Pro variant. According to the images, these will look even closer to AirPods. It looks like they’ll forgo the removable ear tips and slide directly into the ears. We see the actual speaker grill with what looks like the in-ear sensor in the image. Above the alleged sensor, we see what looks like a microphone.

The Pro will also have the black line down the stem. This could be the main visual cue making these stick out. On the back of the Galaxy Buds 3 Pro, we see two additional microphones.

Case

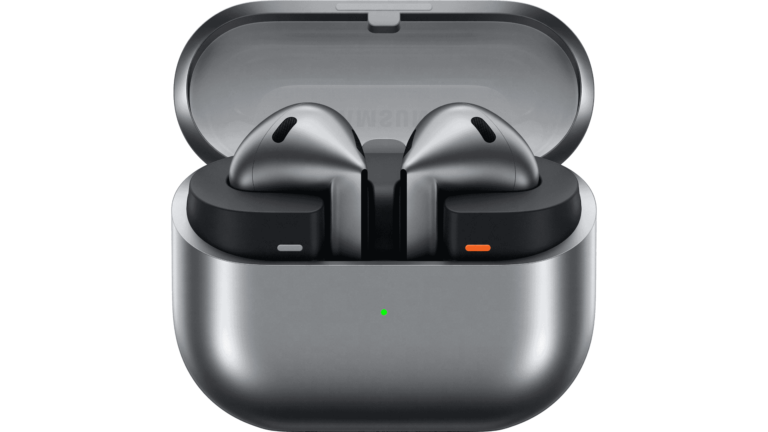
Along with the images of the buds, we also see the case that they’ll come in. As you could guess, the case will look closer to the AirPods’ case. What makes this case different from the AirPods case is the transparent lid.

The transparent lid will allow you to see the colored lights on either side of the case. There’s a blue light for the left bud and an orange light for the right bud. This matches the colored strips on the bottom of the actual earbuds. We’re not sure if these are just colored strips or if they’re lights. We’ll have to see them to be sure.

Right now, we’re still waiting for more information about these earbuds to come out. Right now, we only have leaked specs. They could have up to 24 hours of battery life, IP57 water and dust resistance, and be compatible with Google’s Find My Device network.


[ad_2]
Source link

Google could soon expand access to Imagen 3 AI model to its Gemini Advanced subscribers

0
[ad_1]

Image credit — Google

Google appears to be expanding access to its most advanced text-to-image AI model, Imagen 3. Originally announced last month with limited access, Google is believed to be planning early access to it for Gemini Advanced subscribers through a popup within the beta version of the Google app for Android.Spotted through an APK teardown, the app’s code reveals that Imagen 3 could become more widely available after its initial limited release. While there’s no definitive way to confirm if the updated model uses Imagen 3, it’s highly likely based on the app’s popup message.

The popup header announces the “First look: Imagen 3” and invites Gemini Advanced subscribers to experience early access to the latest version of the AI tool. Additionally, a drop-down list outlines the updated features of this advanced AI model.

Imagen 3 as spotted in the latest beta of the Google app for Android and unofficially activated via code flags

| Images credit — AssembleDebug and Android Authority

The popup also provides information about the new and enhanced features available in the latest version of the AI tool, although the specifics of those features remain undisclosed. Initially, only select creators were granted access to Imagen 3 through a private preview, with others able to join a waitlist. Now, with this expanded access, Gemini Advanced subscribers will be given the opportunity to explore and test the capabilities of Imagen 3.

The expanded access suggests that Google is progressively rolling out the model to a wider user base, starting with its Gemini Advanced subscribers. While the company hasn’t made an official announcement about this wider access, the discovery within the Google app for Android strongly indicates a broader release.

Although there’s no confirmation yet that the model is using Imagen 3, it seems highly probable given the available information. With this expanded access, users will be able to explore the latest advancements in AI-generated images and contribute to refining the model’s capabilities through their feedback and experiences.


[ad_2]
Source link

Thousands of UEFA Customer Credentials Sold on Dark Web

0
[ad_1]

The thrilling UEFA League, aka Euro 2024, is attracting over 20 million football fans in Germany and millions more worldwide. However, this excitement has also attracted the attention of threat actors who are exploiting the event’s anticipation to fulfil their nefarious objectives.

A new report from Cyberint highlights a surge in cyber threats targeting the event. Its Dark Web monitoring reveals threat actor discussions related to UEFA, sales account searches, ticket offers, free/cheap streaming services, and the sale of compromised customer credentials. 

Reportedly, threat actors are using compromised UEFA customer credentials to perform fraudulent activities, such as account takeovers and ticket purchases. They can also steal sensitive personal information, impersonate account owners, and gain access to funds or payment cards. 

Cyberint has detected over 15,000 exposed UEFA customer credentials since 2024, and over 2,000 UEFA customer credentials were found for sale on dark web marketplaces. These credentials are often exposed through credential harvesting malware, which infects the victim’s machine and sends user input logs to the C&C server operator.  

Since UEFA has sold streaming rights for its tournaments to media networks, it provides cybercriminals with an opportunity to create illegal content sites to lure fans without cable or streaming subscriptions through promises of free livestreaming and real-time scores. Clicking on links on these malicious websites can lead to data breaches or virus infections. These sites may demand ransom for the victim’s computer and network, or gain control of a system for fraud or spying. Drive-by downloads, a type of malware attack, can also occur by visiting the site.

Researchers noted that mobile apps impersonating UEFA’s official app are widely available on third-party app stores, often containing malicious elements. These stores are less regulated, allowing anyone to upload unauthorized apps without supervision.

Threat actors upload unauthorized apps, often containing malicious elements, exposing users to malware and data breaches. The apps target UEFA’s fans, customers, and volunteers, using the brand’s name and logo.

Moreover, Euro 2024 fans are increasingly relying on third-party ticket-selling websites, which also presents opportunities for scammers. Some sellers exploit fans’ enthusiasm by peddling fake or non-existent tickets, reaching out through social media or creating elaborate phishing websites to mimic legitimate ticket sellers.

Another fraud vector is the ticket lottery, offering fans a chance to earn free tickets. Threat actors can use the provided details to target victims for scams or sell the information to the highest bidder. 

Euro 2024 Fans Beware: Thousands of UEFA Customer Credentials Sold on Dark Web
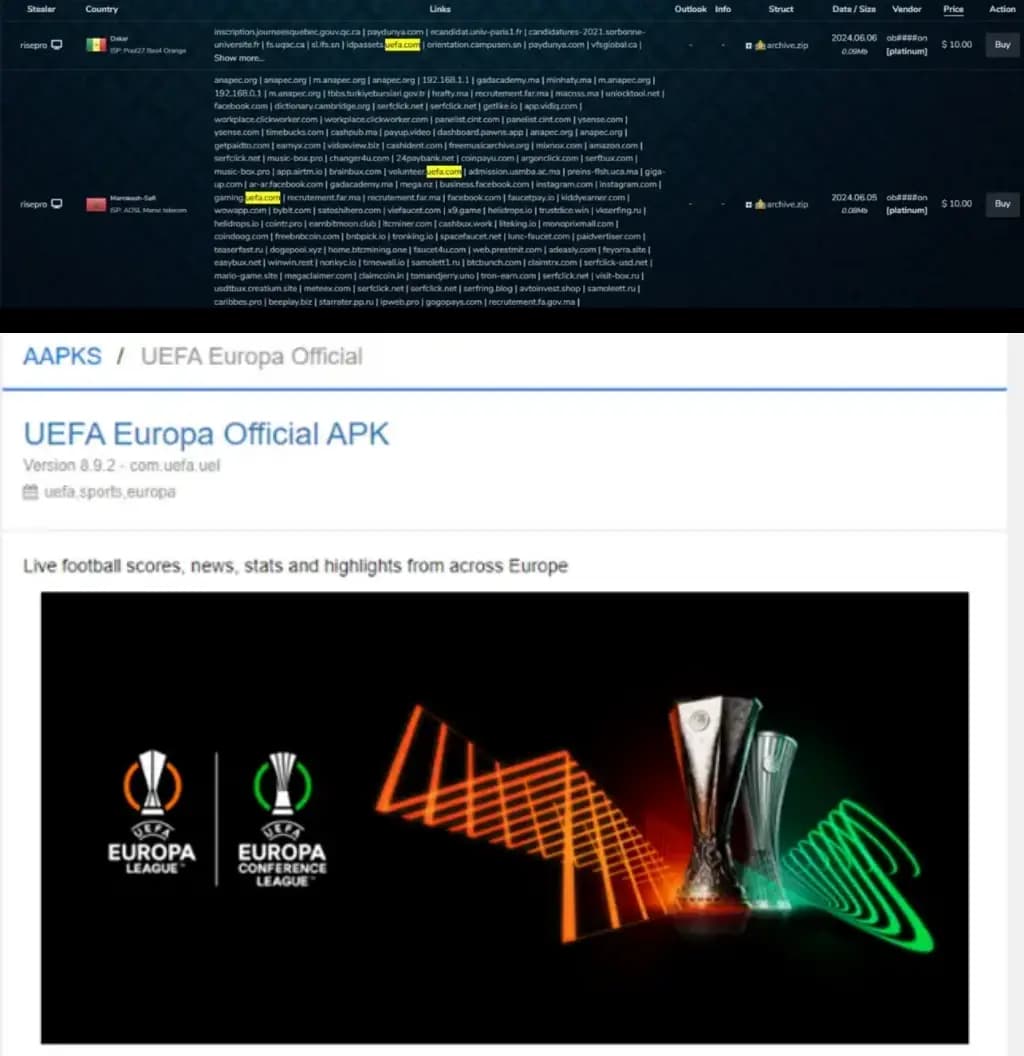
Screenshot shows cybercriminals selling UEFA customer accounts and a malicious app impersonating the original UEFA app (Screenshot: Cyberint)

Researchers identified that UEFA’s website might be the weak link in this scenario.

“One notable aspect is the misconfiguration of UEFA’s official website – uefa.com. Such vulnerabilities present a tangible risk, potentially serving as gateways for threat actors to launch attacks,” researchers explained in the report shared with Hackread.com.

Cyberint recommends being cautious of unsolicited communications, verifying website authenticity, and using secure payment methods. To avoid ticket fraud, buy tickets only from authorized sources, use secure payment platforms like PayPal, prefer credit card payments, and avoid direct bank or money transfers, to prevent Euro 2024 from being marred by “opportunist threat actors.”

  1. Stolen Singaporean Identities Sold on Dark Web Starting at $8
  2. Crooks Exploited Satellite Live Feed Delay for Betting Advantage
  3. Russia hacked Winter Olympics & framed N.Korea in false-flag attack
  4. Cybersecurity Loopholes Found in Paris 2024 Olympics Infrastructure
  5. Hackers Disrupts Winter Olympics Website During Opening Ceremony

[ad_2]
Source link

Medusa RAT Attacking Android to Steal SMS & Screen Control

0
[ad_1]

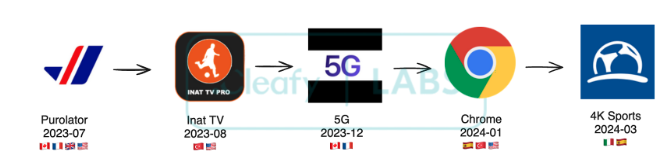
A new variant of the Medusa malware family was discovered disguised as a “4K Sports” app, which exhibits changes in command structure and capabilities compared to previous versions. 

Researchers believe these changes are aimed at improving efficiency and strengthening the botnet.

The MaaS model used by Medusa allows for adaptations based on various factors, such as new affiliates seeking less detectable variants to target unexplored regions. 

Sports 4K Activities

The Medusa banking Trojan, first discovered in 2020, grants attackers remote access to devices through VNC and accessibility services, allowing them to perform real-time screen sharing, steal keystrokes, and launch overlay attacks for on-device fraud (ODF) such as account takeover (ATO). 

Medusa communicates with the attacker’s C2 server through a web socket connection, fetching the URL dynamically from social media platforms like Telegram for obfuscation and resilience against takedowns.

The malware also utilizes backup channels on social media for additional communication redundancy. 

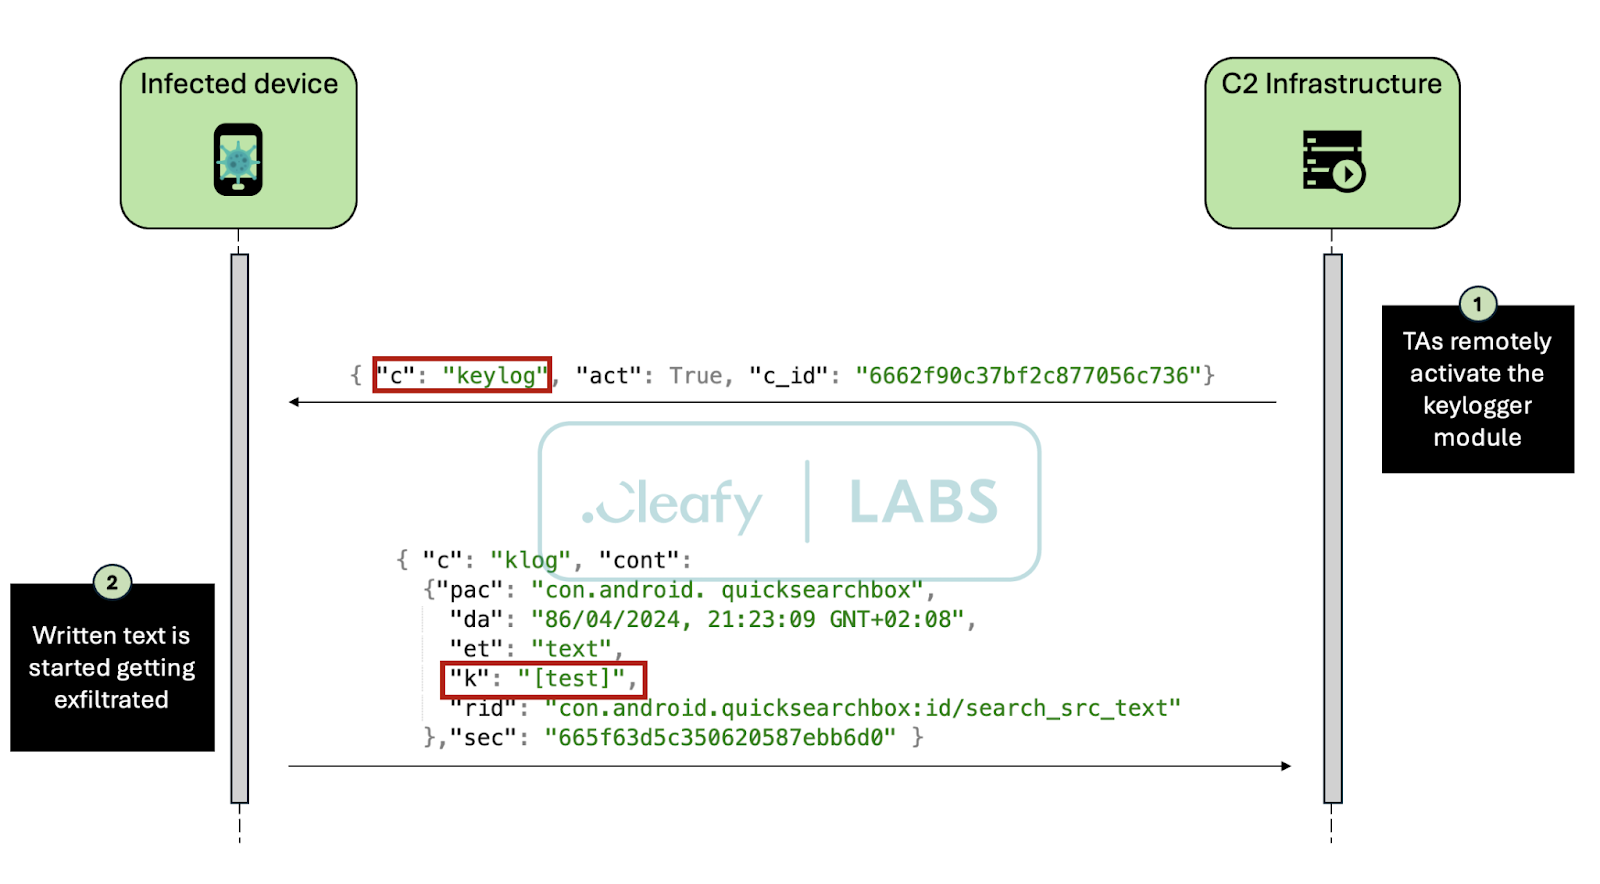
Key-logging in Action

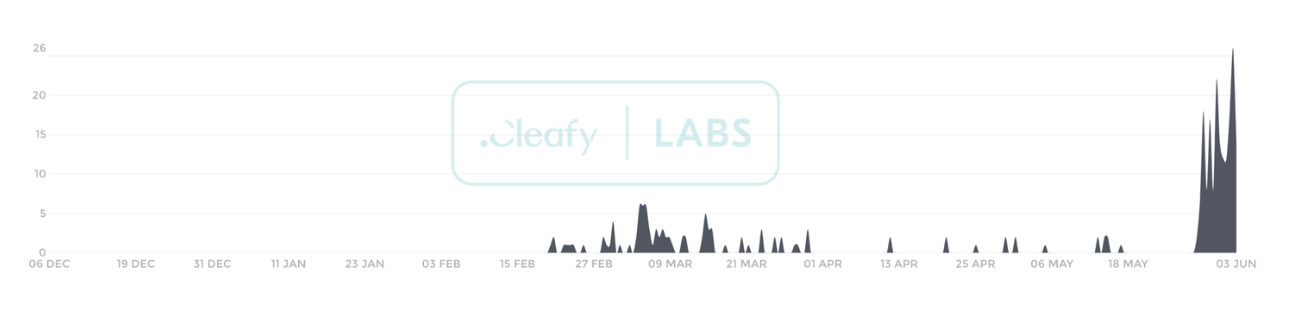
A recent resurgence of Medusa malware campaigns, since July 2023, utilizes social engineering (smishing) to deliver droppers that side-load the malware onto Android devices in targeted countries (CA, ES, FR, IT, UK, US, TK). 

Scan Your Business Email Inbox to Find Advanced Email Threats - Try AI-Powered Free Threat Scan

This new variant leverages on-device fraud (ODF) but specific cash-out methods and transfer amounts remain unknown, while Medusa exhibits adaptability through its backend infrastructure, which can support multiple botnets with distinct functionalities. 

Cleafy discovered five active botnets that were distinguished from one another based on the types of decoys, distribution strategies, and locations that were targeted. 

 Most-used icons and names in recent Medusa campaigns
 Most-used icons and names in recent Medusa campaigns

Two Medusa botnet clusters were identified; where Cluster 1 targets Turkey, the US, and Canada and uses traditional phishing tactics, while Cluster 2 targets Europe and uses droppers besides phishing, as both clusters are reducing requested permissions to evade detection. 

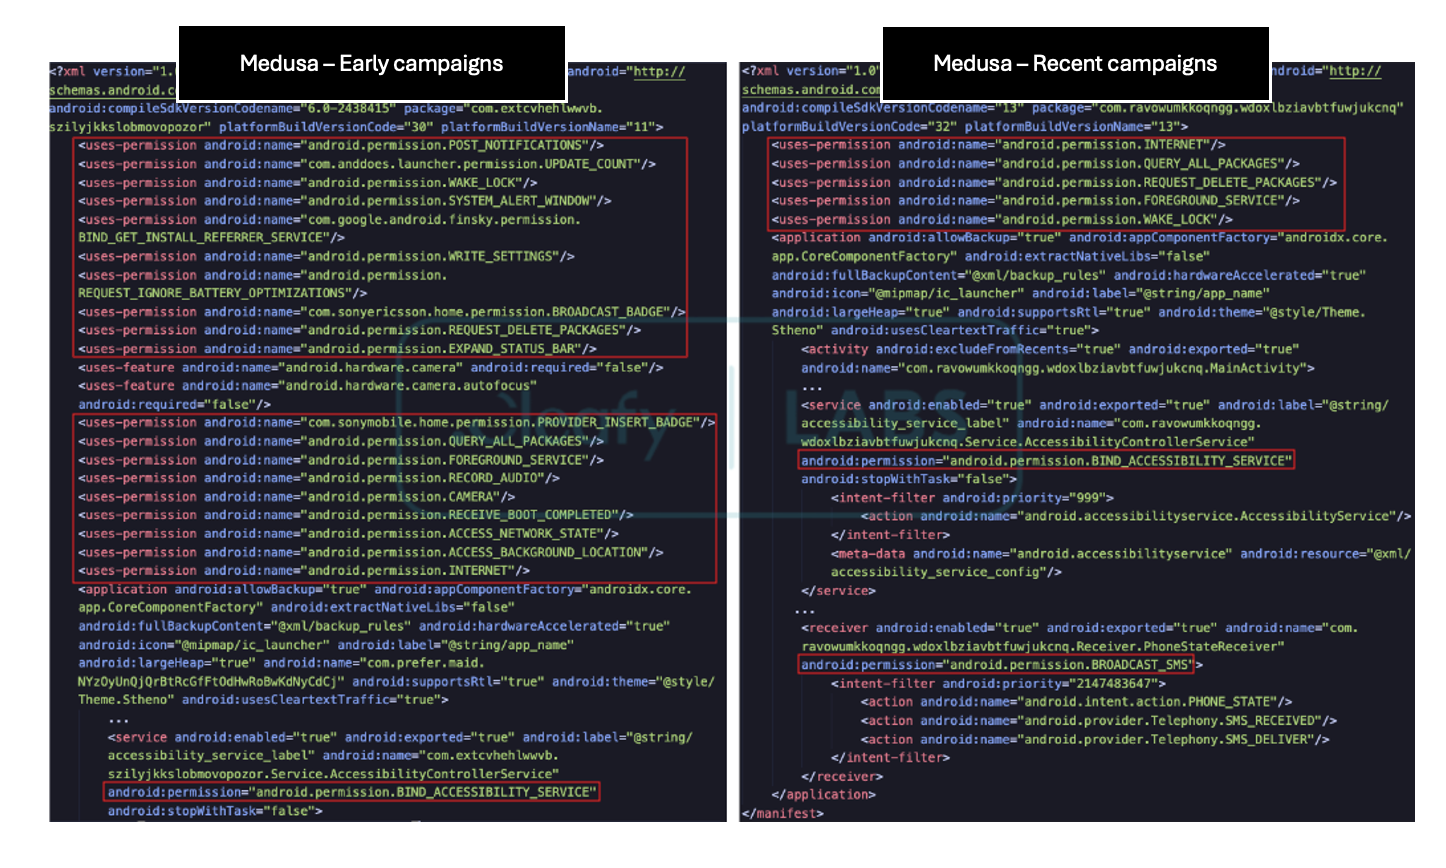
Early campaigns requested permissions for cameras, microphones, locations, etc., but recent campaigns only request permissions for core functionalities like accessibility, SMS, internet, foreground service, and package management, which makes them stealthier and harder to detect.  

Comparison of permissions required in early and recent campaigns

Researchers identified a new variant of Medusa malware with a streamlined command set, and 17 commands from the previous version were removed to reduce its footprint and improve stealth. 

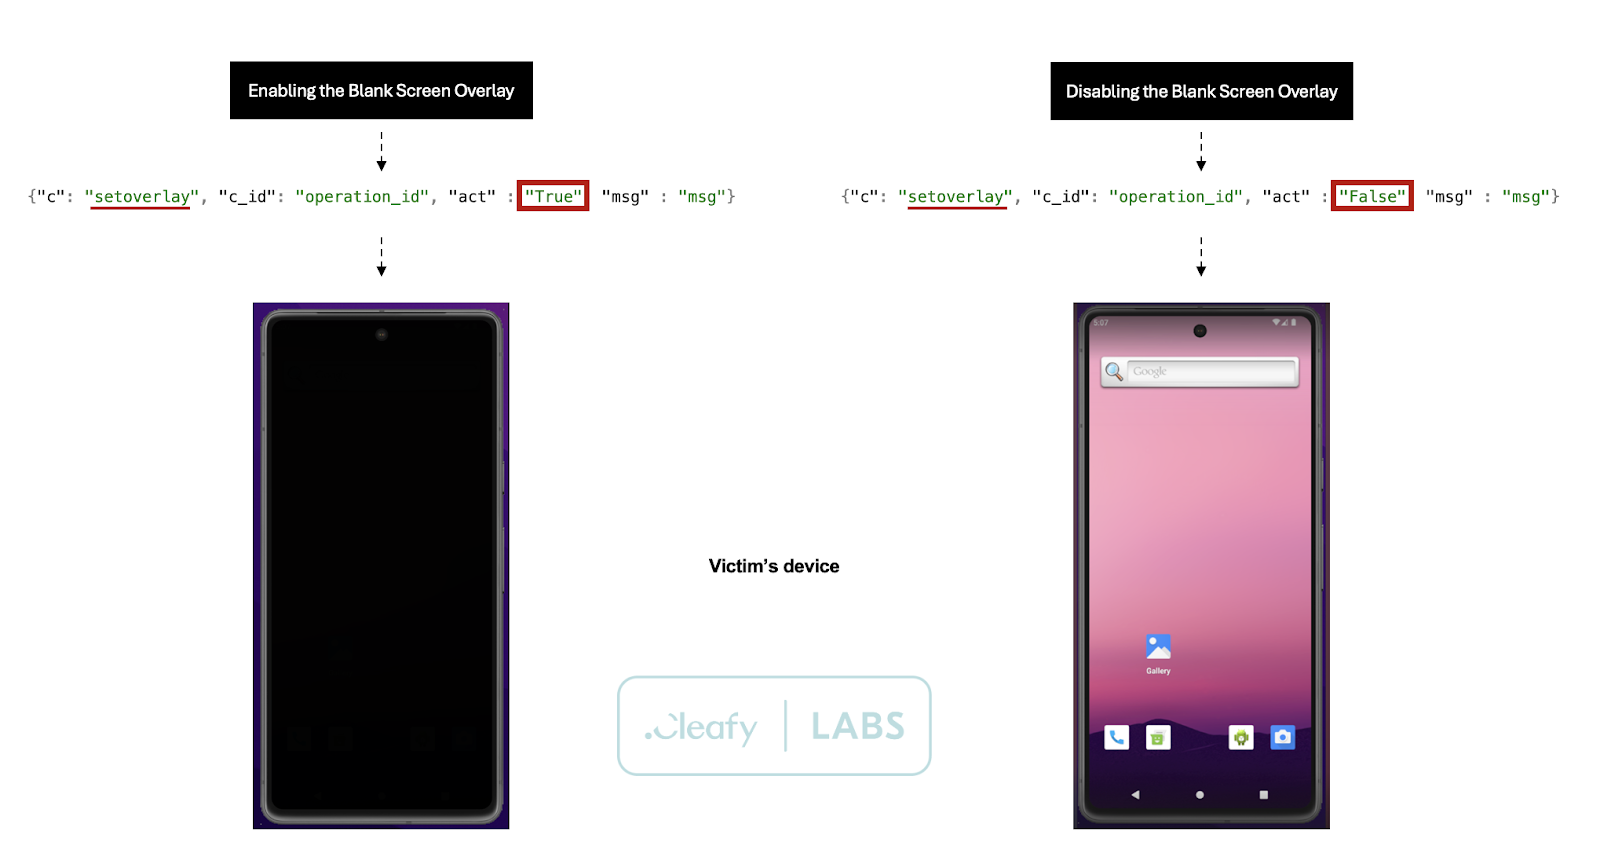
Command “setoverlay” in action

Five new commands were introduced, including taking screenshots, uninstalling apps, and controlling the device screen with a black overlay, which allows attackers to mask malicious activities and potentially steal sensitive information. 

Some functionalities requiring permissions (e.g., sending SMS, getting contacts) are still present in the code but blocked by the system without permission grants, which suggests that the malware is adaptable and can be easily modified for future campaigns. 

Free Webinar! 3 Security Trends to Maximize MSP Growth -> Register For Free


[ad_2]
Source link