Elite North Korean Hackers Breach Russian Missile Developer

0
[ad_1]
  • North Korean hackers breached a major Russian missile developer, NPO Mashinostroyeniya, for at least five months.
  • Cyber-espionage teams ScarCruft and Lazarus installed stealthy digital backdoors into NPO Mash’s systems.
  • It remains unclear if data was stolen or linked to North Korea’s ballistic missile program developments.
  • Experts warn that North Korea targets even its allies to acquire critical technologies.
  • The breach exposes vulnerabilities in cybersecurity and raises concerns about sensitive technology transfers.

It has been uncovered that an elite group of North Korean hackers successfully breached the computer networks of a major Russian missile developer for an extended period last year.

The evidence, reviewed by Reuters and analyzed by security researchers, points to cyber-espionage teams associated with the North Korean government, namely ScarCruft (aka APT37, InkySquid, Reaper, and Ricochet Chollima). The same group was also reported to have used the Dolphin Backdoor against South Korea in December 2022.

The researchers also noted tracks of the infamous North Korean state-backed group, Lazarus, in these attacks. This was identified after researchers noted the presence of OpenCarrot Windows OS backdoor. The backdoor is known to be used by the Lazarus group.

These hackers discreetly installed stealthy backdoors into systems at NPO Mashinostroyeniya, commonly referred to as NPO Mash, a prominent rocket design bureau located in Reutov, on the outskirts of Moscow.

Reuters’ investigation did not ascertain whether any data was taken during the intrusion or what information might have been accessed. Nonetheless, it is noteworthy that in the months following the breaches, North Korea declared significant advancements in its banned ballistic missile program, raising suspicions about a possible connection to the breach.

Technical data reveals that the intrusion began approximately in late 2021 and persisted until May 2022 when the company’s IT engineers, as per internal communications reviewed by Reuters, detected the hackers’ activities.

Tom Hegel, a security researcher with US cybersecurity firm SentinelOne, who first uncovered the compromise, highlighted the importance of these findings, providing rare insight into clandestine cyber operations that often elude public scrutiny. Hegel’s team stumbled upon the hack when an NPO Mash IT staffer inadvertently leaked the company’s internal communications while attempting to investigate the North Korean attack by uploading evidence to a private cybersecurity research portal.

With a high level of confidence, we attribute this intrusion to threat actors independently associated with North Korea. Based on our assessment, this incident stands as a compelling illustration of North Korea’s proactive measures to covertly advance their missile development objectives, as evidenced by their direct compromise of a Russian Defense-Industrial Base (DIB) organization.

Tom Hegel – SentinelOne

Two independent computer security experts, Nicholas Weaver and Matt Tait, verified the exposed email content’s authenticity by cross-referencing cryptographic signatures with a set of keys controlled by NPO Mash. SentinelOne expressed confidence that North Korea was responsible for the hack, as the cyberspies reused previously known malware and malicious infrastructure utilized in other intrusions.

The information potentially accessed by North Korean hackers includes details about NPO Mash’s hypersonic missile, “Zircon,” which Russian President Vladimir Putin had praised as a promising product capable of reaching speeds around nine times that of sound.

However, missile expert Markus Schiller, who has researched foreign aid to North Korea’s missile program, downplayed the immediate impact of obtaining plans for the Zircon. Schiller asserted that merely possessing drawings wouldn’t be sufficient to replicate the missile’s capabilities, as the process involves more complexities than what appears on paper.

Nevertheless, NPO Mash’s role as a leading Russian missile designer and producer makes it a highly valuable target. As the company’s advancements could have strategic implications, the breach raises concerns about the potential transfer of sensitive missile-related technology to North Korea.

The incident underscores the isolated nation’s willingness to target even its allies, as evidenced by the breach of Russia’s defence technologies. NPO Mashinostroyeniya has played a crucial role in developing hypersonic missiles, satellite technologies, and newer generation ballistic armaments—areas of immense interest to North Korea in its pursuit of an Intercontinental Ballistic Missile (ICBM) capable of striking the mainland United States.

  1. CIA Wants Russians to Share Secret via its Darknet Site
  2. Russian hacking forums warming up to Chinese hackers
  3. Hackers steal personal data of 1,000 North Korean Defectors

[ad_2]
Source link

HarmonyOS 4 is official with new customization options & refreshed UI

0
[ad_1]

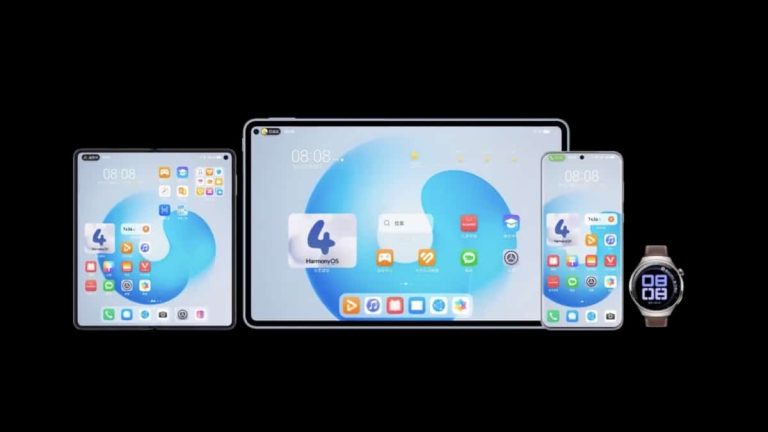
Huawei announced HarmonyOS 4 during the Huawei Developer Conference 2023. Do note that it got announced in China, so this info is based on that launch, as are the images you’ll see below.

That being said, HarmonyOS 4 will likely look the same globally, but without some China-focused functionality. Therefore, covering this makes all the sense in the world.

HarmonyOS 4 has been announced with a UI overhaul, new customization options & more

HarmonyOS 4 does bring a UI refresh, along with some new customization options. By ‘UI’ refresh, we mean a major redesign, basically, as it’s quite different than HarmonyOS 3, visually.

Huawei now offers you the chance to change system fonts, colors, clock, and widget styles. You can create your own combinations, and customize them as you please, basically. The company also allows users to set emoji wallpapers.

The company also introduced something called ‘Panorama Weather’, so that you can get great-looking weather updates right on your home screen. The conditions will update in real-time.

The notification center has been changed up

Huawei also changed up the notification center, as it needed a refresh. You do have an option to divide upcoming alerts, if you want. You can now also pin your preferred app notifications to the notification center.

Those rumors regarding Huawei’s very own Dynamic Island also came to fruition, kind of. Huawei now offers something called ‘Live Window’ in HarmonyOS 4. Apps that are supported will show you real-time alerts and notifications in a pill-shaped icon in the top-left corner of the device. You can expand that window with a single tap.

The company has also added more widgets with HarmonyOS 4. HarmonyOS 4 actually comes with Ark Engine below everything, and Huawei claims it offers 20% better performance. The system should launch apps quicker, and the animations should also be nicer without an impact on the battery.

HarmonyOS is running on over 700 million devices worldwide

We’re only scratching the surface here, though. Huawei did mention that the HarmonyOS ecosystem now powers over 700 million devices. That includes smartphones, tablets, smartwatches, TVs, and more.

The HarmonyOS 4 public beta is available for a ton of smartphones as we speak, though only their Chinese variants. We’re not sure when will Huawei announce a global version of HarmonyOS 4. Perhaps with the Mate 60 launch? We’ll see.


[ad_2]
Source link

Apple might bring a motion detection feature to Siri

0
[ad_1]

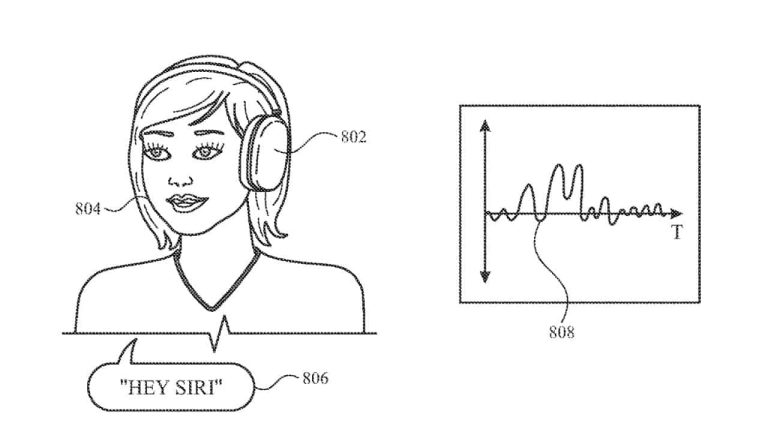
Apple is reportedly working on a motion detection feature for its voice assistant Siri. The company’s recent patent filing reveals that Siri might soon be able to read a user’s lips and get triggered without voice commands.

Voice assistants are becoming an integral part of our life, and you can now find them on smartphones, cars, and smart home gadgets. These tools are even getting more intelligent, thanks to AI. Apple’s Siri is one of the most popular voice assistants that can be found on the company’s devices. Traditionally, you need the famous “Hey Siri” commands to trigger the app. However, this pattern might soon change.

According to Apple Insider, Apple has filed a patent for Siri dubbed “Keyword Detection Using Motion Sensing.” The patent promises a lip and head detection feature that could be used for activating the app as well as enhancing its accuracy.

You might soon be able to trigger Siri through your lips and head movements

The patent application further explains that Siri gets a motion sensor to track and record a user’s movements as they speak. If Siri concludes that the movements are matched to a specific command, then it will perform the command.

Apple added that voice control systems can sometimes produce false responses due to the background noise or picking up ambient noise or speech from an unintended user. To prevent this, Siri motion sensors such as accelerometers and gyroscopes will track face, head, and neck movements.

Introducing a new way to trigger Siri doesn’t mean Apple wants to remove the microphone from its devices- like what it did with iPhone’s headphone jack. Instead, a motion detection feature would allow users to switch off the microphone, which is currently used for listening to “Siri” or “Hey, Siri” commands. The tech giant argues that switching off the microphone could save power and processing capacity.

Yet, it remains to be seen which Apple products will get Siri with a motion detection sensor. However, iPhones, AirPods, and Apple Vision Pro are the most likely candidates to get the feature.


[ad_2]
Source link

IBM SDK, Java Technology Flaw

0
[ad_1]

IBM has discovered a vulnerability in the IBM SDK, Java Technology Edition, that allows threat actors to execute arbitrary code on the system due to unsafe deserialization.

This vulnerability exists in the Object Request Broker (ORB) and is given a CVE ID: CVE-2022-40609.

ORB is a middleware application component that is used to make program calls between computers on the network using remote procedure calls (RPC). It also provided transparency about the location.

CVE-2022-40609: Unsafe Deserialization Flaw

A remote attacker can exploit this vulnerability by sending specially crafted data, which will result in arbitrary code execution on the system. The CVSS Score for this vulnerability is given as 8.1 (High).

Affected Products & Fixed in Versions

Affected Product(s)Version(s)Fixed in Version
IBM SDK, Java Technology Edition8.0.8.0 and earlier7.1.5.19
IBM SDK, Java Technology Edition7.1.5.18 and earlier8.0.8.5

This vulnerability is classified on the CWE (Common Weakness Enumeration) with CWE-502: Deserialization of Untrusted Data. 

In response to this vulnerability, Red Hat has also released patches for their products Red Hat Enterprise Linux 7 Supplementary, and Red Hat Enterprise Linux 8 in order to fix this vulnerability.

Red Hat Enterprise Linux 7 with Java 1.7.1-ibm was found to be Out of support scope, as mentioned by Red Hat in their policies and advisory.

Furthermore, Tenable has also released plugins for this vulnerability for scanning this vulnerability through Nessus.

Nessus Plugins:

Users of these products are recommended to upgrade to the latest versions for preventing exploitation from threat actors.

Keep informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

CEO confirms all Amazon divisions are working on generative AI

0
[ad_1]

Ever since its introduction late last year, generative AI has become the buzzword, with almost every tech giant currently working to integrate the technology into its services. Now, during a recent earnings call, Amazon CEO Andy Jassy announced that “every single one” of Amazon’s businesses is actively pursuing multiple generative AI initiatives.

Although Jassy did not confirm the specific areas the company is focusing on, he mentioned that their efforts to integrate AI would range from bolstering cost-effectiveness and operational efficiency to revolutionizing customer experiences. Additionally, he hinted towards AI improvements coming to Alexa, which the company might showcase at their upcoming event on September 20th.

“It’s true in our Stores business, it’s true in our AWS business, it’s true in our advertising business, it’s true in all our devices — and you can just imagine what we’re working on with respect to Alexa there — it’s true in our entertainment businesses… every single one. It is going to be at the heart of what we do. It’s a significant investment and focus for us,” said Jassy.

Not the only company focusing on AI

As mentioned before, Amazon is not the only company pushing its boundaries in the generative AI industry. This is because, Microsoft has already integrated its Bing AI chatbot into most of its services and is now looking to integrate generative AI into its Windows operating system.

Similarly, Google, after fearing competition from Microsoft, has also started testing a slew of generative AI services, including the new Google Search Generative Experience, which could revolutionize how we search for things on the internet. While Apple’s efforts in the AI industry have been cautious, the company is also reportedly working on an AI chatbot that will run on the company’s newly developed “Ajax” framework, a collaboration between Apple and Google’s JAX machine learning framework and Google Cloud.


[ad_2]
Source link

HONOR confirms global Magic V2 launch, September 1 is the date

0
[ad_1]

HONOR has just confirmed that the Magic V2 foldable will launch on September 1. This device will become official as part of IFA 2023 in Berlin. As a reminder, the Magic V2 did already launch, but in China only.

The global variant of the HONOR Magic V2 is coming, as the launch date has just been revealed

That phone managed to get a lot of attention, despite not launching globally just yet. Why? Well, HONOR managed to achieve something great here. The Magic V2 became the thinnest foldable smartphone on the market.

The Magic V2 is only 4.7-4.8mm thick when unfolded, and 9.9-10.1mm thick when folded, depending on the model. On top of that, the phone weighs only 231 or 237 grams, once again, depending on the model, as both glass and eco leather variants got announced. The eco-leather one is lighter.

The global variant of the phone will offer the same exact design, but we still don’t know what variants will be available globally. The company’s press event will kick off at 10 AM CET/ 9 AM BST / 4 AM EST / 1 AM PST in Berlin, in case you’re interested.

Two HONOR foldables are coming, actually

That is not all, though. HONOR says that two foldable smartphones will become official at IFA. The first is the Magic V2, while the other is a mystery. If we had to guess, we’d say that HONOR’s first-ever clamshell foldable is coming.

We didn’t really hear much about that phone, so it really is a mystery. If that is, in fact, what we’re getting. We’ll just have to wait and see what HONOR is preparing for us, and who knows, perhaps that other phone leaks ahead of launch too.

All in all, HONOR will have a rather considerable presence at IFA 2023, and add two more foldable devices to the global market, which is surely appreciated. The more competition is present out there, the better for the end consumer.


[ad_2]
Source link

Malicious PyPI Package Mimicking Common Python Tools

0
[ad_1]
  1. ReversingLabs discovered a malicious PyPI package named VMConnect.
  2. The package imitated common Python tools & showed suspicious behavior.
  3. The attack started on 28th July with daily appearances of notorious packages.
  4. PyPI team swiftly removed the packages, but attackers kept replacing them.
  5. Objectives of the attack remain unclear to researchers.

Threat researchers at ReversingLabs, a software supply chain security and malware analysis platform, have discovered a malicious new PyPI package dubbed VMConnect on the Python Package Index (PyPI) repository.

ReversingLabs’ reverse engineer, Karlo Zanki, wrote in a technical blog post that around 24 malicious Python packages were identified on the PyPI open-source repository. These packages imitated three very common, open-source Python tools, including pyVmomi VMware vSphere bindings’ wrapper module vConnector, databases that allow asyncio support for different databases, and a set of tools used to test Ethereum-based applications called eth-tester.

According to the company, its static analysis engine Titanium Platform identified the suspicious PyPI packages while performing routine scanning. Further probing revealed suspicious behaviour, such as the packages established communication with a C2 server for downloading additional malicious software. However, researchers didn’t observe any commands when this C2 server was live.

Per their analysis, this campaign went active on 28 July 2023 as that is when the first malicious package was published, and packages kept appearing on a daily basis, each being more notorious than the previous ones.

“Additionally, these malicious packages were promptly removed from PyPI, likely due to internal system detections or external reports. However, the attackers quickly replaced the packages, indicating a well-organized and ongoing campaign.”

Karlo Zanki

Researchers have observed that campaign operators go to great lengths to make their malicious activities appear genuine. They achieve this by creating GitHub repositories with authentic-looking descriptions and even using legitimate source code. However, they deliberately remove any traces of their malicious behaviour from these repositories to build trust with potential victims.

Interestingly, this campaign managed to evade detection in the source code. Its presence was only discovered when researchers scanned the build process artifacts. This sets it apart from other recently discovered supply chain campaigns like “Brainleeches.”

VMCONNECT: Malicious PyPI Package Mimicking Common Python Tools
VMConnect package’s behaviour and description

Suspicious PyPI packages have been found to exhibit deceptive behaviour by fully emulating the functionalities of the modules they imitate. To add to the deceit, these packages link to GitHub projects where their malicious behaviour has been cleverly removed, creating a false sense of trust in the PyPI release package.

The swift action taken by PyPI administrators is commendable, as all the malicious packages, including VMConnect, were swiftly removed from the platform within just three days of their appearance. However, this incident raises serious concerns, as researchers are noticing a growing trend of exploiting open-source modules to distribute malicious code and carry out various types of supply chain attacks.

In the past, the majority of supply chain attacks were targeted at the NPM open-source repository. Surprisingly, the PyPI repository has now become the prime target for such malicious activities. For instance, in January 2023, researchers detected 41 suspicious PyPI packages posing as popular HTTP libraries, and in March, a PyPI package named “termcolour” (after a now-defunct package) with multiple versions of a three-stage downloader was discovered by ReversingLabs.

Despite intensive investigation, researchers have been unable to determine the objectives of this campaign or what happens in its later stages. The purpose behind these attacks, whether it involves stealing sensitive data, conducting surveillance, launching ransomware, or a combination of these, remains unclear.

  1. Malicious Packages are Swapping Out Your Crypto Addresses
  2. GitHub Abused to Distribute Malicious Packages on PyPI in Image Files
  3. Typosquatting: Legit Abquery Package Duped with Malicious Aabquerys

[ad_2]
Source link

Instagram’s new feature puts an end to DM requests spamming

0
[ad_1]

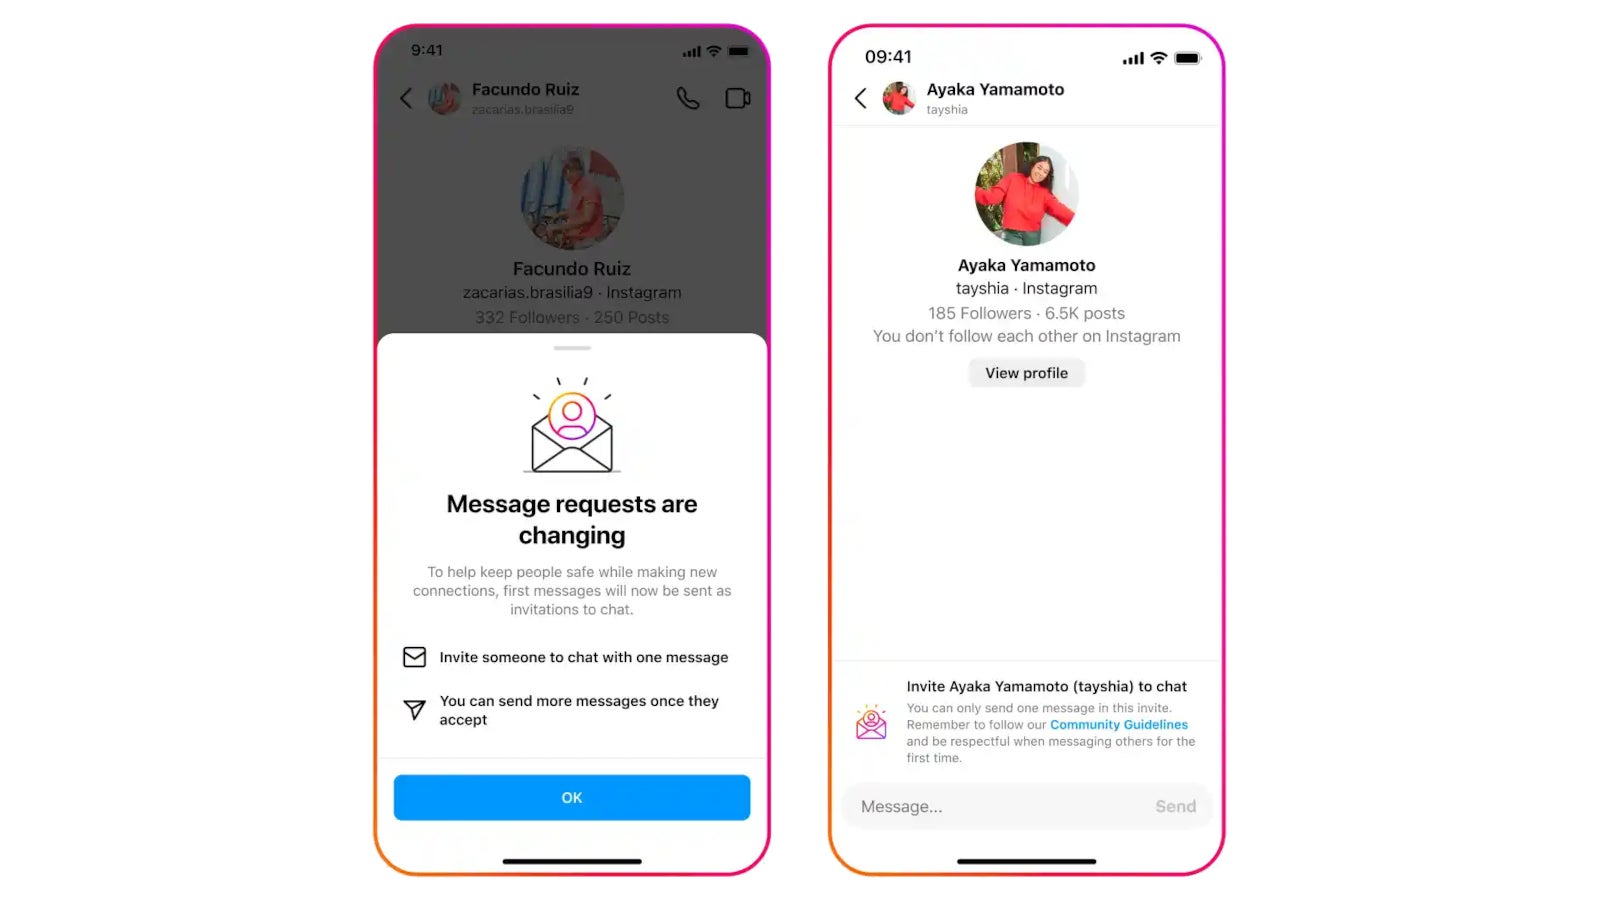
Instagram is finally adding one of the most requested features since it introduced the ability to send direct messages. A new update makes it possible for Instagram users to restrict who can send them DM requests.

The new feature was tested last month and now it’s rolling out to all Instagram users, TechCrunch reports. The first limitation introduced with the new feature prevents you from sending more than on DM request to a person who doesn’t follow you on Instagram. If they accept your request, then you will be able to continue to send them new DM requests.

The second limitation is that DM invites can’t contain images, videos or voice notes, so you can send text-only DM requests to those who don’t follow you on Instagram.

“We want people to feel confident and in control when they open their inbox. That’s why we’re testing new features that mean people can’t receive images, videos or multiple messages from someone they don’t follow, until they’ve accepted the request to chat. We’re grateful for the feedback we hear from our community — and we’ll keep listening to find ways to help everyone feel safer on Instagram,” told TechCrunch Cindy Southworth, head of Women’s Safety at Meta.

Apart from introducing these new limitations that basically remove DM requests spamming, Instagram also added a Restrict setting that makes it possible to monitor an account that you don’t want to block, but still want to restrict their presence on your Instagram page.

Once you restrict an account, their comments on your posts will only be visible to them. More importantly, they won’t know that their posts can’t be seen by anyone, and their DMs will be automatically sent to your DM requests folder. It’s a middle-ground solution in case you don’t want to outright block an account, but still want some protection against bullying.


[ad_2]
Source link

FBI warns users of NFT theft by malicious developers

0
[ad_1]

IN SUMMARY:

  1. FBI warns of new phishing scam in NFT community by crooks posing as devs.
  2. The scam includes fake NFT releases with false urgency & limited supply claims.
  3. Phishing websites resembling legit NFT projects stealing victims’ crypto data.
  4. Drainer smart contracts transfer cryptocurrency and NFTs to criminals’ wallets.
  5. Stolen NFTs laundered through crypto mixers & exchanges to conceal the trail.

The Federal Bureau of Investigation (FBI) has issued a warning about a concerning rise in financial fraud targeting the active users within the Non-Fungible Token (NFT) community. Cybercriminals are posing as legitimate NFT developers and employing sophisticated tactics to deceive unsuspecting victims.

In these fraudulent schemes, criminals either gain unauthorized access to NFT developer social media accounts or create nearly identical accounts to promote new NFT releases. To lure victims, they deploy tactics creating a false sense of urgency, using phrases like “limited supply” and promoting the NFT release as a “surprise” or previously unannounced mint.

Once victims are drawn in, the fraudsters provide links in these announcements, leading to phishing websites that convincingly mimic the appearance of legitimate NFT projects. Unsuspecting victims are then invited to connect their cryptocurrency wallets and purchase the NFTs.

Unbeknownst to them, the linked wallets are connected to a drainer smart contract, resulting in the transfer of their cryptocurrency and NFTs into wallets operated by cybercriminals.

According to the FBI’s public service announcement To further complicate the investigation and conceal their ill-gotten gains, the stolen NFT contents are typically laundered through a series of cryptocurrency mixers and exchanges. These practices aim to obfuscate the path and final destination of the stolen NFTs, making it challenging to trace and recover the stolen assets.

The FBI is urging victims to promptly report any fraudulent or suspicious activities related to these NFT scams to the FBI Internet Crime Complaint Center at www.ic3.gov. In doing so, it is crucial for victims to provide all relevant information, including links, social media accounts, crypto accounts, or domains utilized by scammers. The keyword “NFTHack” should be included in the reports to help law enforcement efficiently handle and investigate the cases.

As the popularity of NFTs continues to grow, criminals are seizing opportunities to exploit unsuspecting community members. The FBI’s warning serves as a reminder for NFT enthusiasts to remain vigilant, exercise caution when interacting with unfamiliar accounts, and verify the authenticity of NFT projects before making any transactions.

To combat the rising tide of NFT-related financial fraud, the collaborative effort of the NFT community, platforms, and law enforcement is crucial. By reporting suspicious activities promptly, victims can play an essential role in helping authorities identify and apprehend these criminal actors, thereby safeguarding the integrity of the NFT community and protecting fellow enthusiasts from falling prey to such scams.

  1. 6 of the Best Crypto Bug Bounty Programs
  2. Official website of Banksy hacked for fake NFT scam
  3. Google Ads Malware Wipes NFT Influencer’s Crypto Wallet
  4. Vulnerability Revealed OpenSea NFT Market Users’ Identities
  5. Phishing scam: NFTs Worth $1.7M Stolen from OpenSea Users
  6. Hackers Hijacked Official Ferrari Subdomain to Host NFT Scam

[ad_2]
Source link

Xiaomi phone with pop-up camera & uniform bezels appears

0
[ad_1]

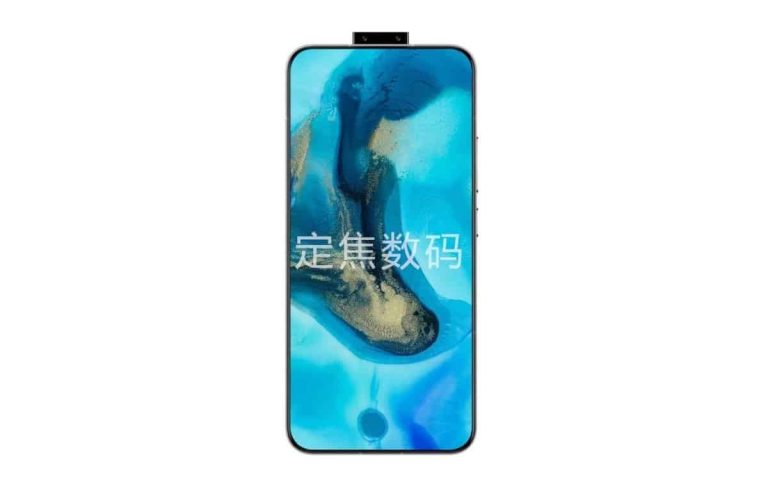
Xiaomi could release a phone with a pop-up camera and uniform bezels at some point in the future. One of the company’s design patents surfaced, and it’s described as a ‘Hidden Electronic Device and Hidden Camera’ patent.

Xiaomi could release a new phone with a pop-up camera & uniform bezels

In that patent filing, Xiaomi details the pop-up camera, and it also shares a placeholder image of a device it could be used on. This pop-up camera is looking to improve upon past models, by reducing weight and improving the mechanism altogether.

We’ve seen quite a few smartphones with pop-up cameras in the past. The OnePlus 7 Pro is likely one of the best-known ones. It’s praised for its design to this day, though pop-up cameras didn’t really stick around.

Smartphone manufacturers shifted to hole punch displays, to eliminate moving parts that pop-up cameras require. Well, Xiaomi could bring them back, better than ever, though this patent doesn’t guarantee anything, of course.

The render you can see below is based on that patent filing, it seems

A render of a phone also surfaced, and it seems to be based on this patent. You can check it out above the article. You’ll notice that the device has uniform bezels, and no hole punch or anything of the sort.

Some smartphone OEMs shifted to under-display cameras in their phones, like RedMagic, for example. Under-display cameras don’t really deliver the image quality that can be praised, though many people don’t really care that much about them. They’d gladly take the hit in selfie image quality to get a clear display canvas.

Xiaomi is looking to offer the best of both worlds, in a way. A good selfie camera when you need it, and a clear canvas when you don’t. It remains to be seen if this device will see the light of day at all. Xiaomi could shift towards under-display cameras too, we’ll see.


[ad_2]
Source link