CISA Guide to Harden Cisco Firewalls

0
[ad_1]

The National Security Agency (NSA) has released best practices for configuring and hardening Cisco Firepower Threat Defense (FTD) which can help network and system administrators in configuring these Next Generation Firewalls (NGFW).

These Cisco FTD systems provide a combination of application and network security features like application visibility and controls (AVC), URL filtering, user identity and authentication, malware protection, and intrusion prevention.

Configuring them in the best possible way will enhance the overall security of the organization.

Practices mentioned by NSA

According to the report, some of the most important practices include implementing 

  • Access control
  • Intrusion prevention policies
  • SSL policies
  • Malware and file policies 
  • Enabling Secure VPN settings and 
  • hardening FXOS (Firewall Xtensible Operating System). 

Implementation of Access Control

This implementation creates refined and controlled desired traffic flow along with minimised unauthorized access and prevention of undesirable traffic.

These access control policies also restrict threat actors from accessing specially configured external or internal network resources.

Intrusion Prevention Policies Implementation

These policies control traffic on the IDS and IPS systems which are inherited from Cisco Talos base policy templates: Balanced Security and Connectivity, Connectivity over Security, Maximum Detection, and Security over Connectivity.

Implementing SSL Policies

These policies control the inspection and decryption of encrypted traffic within the device and mostly target TLS (Transport Layer Security). Three major components of SSL decryption are a TLS proxy, the session setup, and the application data.

Implementation of Malware and File Policies

These policies control the type of files that are allowed, blocked, or inspected from all the traffic that passes through the device.

Multiple actions are available for incoming files, such as detect, block, malware cloud lookup, and block malware. In addition, these policies include static, dynamic, and local analysis.

Enabling Secure VPN settings

The use of secure protocol and strong encryption algorithms when creating a VPN with the device is extremely important.

Protocols like Internet Key Exchange (IKE) version 2 (IKEv2) key management protocol due to the IPsec and Security Association (SA) standards are recommended by the NSA.

Hardening FXOS

FXOS is the operating system used on these Firepower devices, and the FTD image is installed on top of the container.

For preventing exploitation, it is recommended that users upgrade the FXOS to the latest version periodically.

NSA has released a complete report on the best practices that can be followed during the configuration and implementation of these network devices.

Organizations are recommended to follow the guide and implement the measures accordingly to prevent threat actors.

Keep yourself informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link
Researchers Leverage ChatGPT to Expose Notorious macOS Malware

0
[ad_1]

IN SUMMARY

  1. The HVNC macOS malware tool is designed to target SMEs.
  2. The malware tool is effective on a wide range of macOS versions.
  3. This is a reminder that Macs are not immune to cyberattacks
  4. The creators of the malware tool have placed a large escrow deposit, which shows their confidence in the tool’s effectiveness.

Russian hackers and cybercrime forums are notorious for exploiting critical infrastructure. Last month, Hackread.com exclusively reported that a Russian-speaking threat actor was selling access to a US military satellite. Now, researchers have identified macOS malware being sold for $60,000.

Guardz Cyber Intelligence Research (CIR) team has uncovered a sophisticated and perilous macOS malware tool being sold on the notorious Russian cybercrime forum “Exploit.” Leveraging a lead from ChatGPT, the team has unearthed a Hidden Virtual Network Computer (HVNC) tool, designed to seize control of Macs within small to medium-sized enterprises (SMEs).

HVNC: New macOS Malware Lets Hackers Infiltrate Devices Covertly
ChatGPT assisting researchers (screenshot: Guardz)

HVNC is a malicious tool that enables cybercriminals to infiltrate Mac devices without the victim’s knowledge. Unlike conventional remote control technologies, HVNC operates covertly, creating a hidden desktop session that escapes the user’s awareness. 

According to Guardz CIR’s report, the tool was available for the staggering price of $60,000. For this sum, cybercriminals gain access to a malicious tool capable of persistently running on a Mac, evading user authorization, and executing a range of invasive functions. The tool is effective on a spectrum of macOS versions, from 10 up to macOS Ventura 13.2.

The creators of this tool, presumed to be Russian hackers, have taken their malevolent endeavours to new heights. To substantiate the tool’s credibility, an astonishing $100,000 deposit has been placed in an escrow account, earmarked as insurance should the tool fail to deliver as promised. This unprecedented measure shows the hackers’ confidence in their creation and its grave implications.

HVNC: New macOS Malware Lets Hackers Infiltrate Devices Covertly
Post by malware author on a Russian cybercrime and hacker forum (screenshot: Guardz)

Historically, Macs have enjoyed relative immunity compared to their Windows counterparts, but this equilibrium is being disrupted. Cybercriminals are increasingly targeting Macs, a trend that demands heightened awareness from both individual users and businesses alike.

Updating to the latest macOS version and refraining from downloading applications from untrusted sources is paramount. Employing reliable antivirus software, complemented by regular security audits, will further bolster defence mechanisms. 

  1. MacStealer Malware Targeting macOS Catalina Devices
  2. macOS Users Targeted by Chinese Iron Tiger APT Group
  3. SysJoker backdoor targeting Windows, macOS & Linux Devices
  4. DazzleSpy malware infects macOS devices through hacked sites
  5. UpdateAgent malware variant mimics legitimate macOS software

[ad_2]
Source link

The Motorola G54 shows up in a new leak

0
[ad_1]

We’re all still reeling after Motorola introduced us to the Razr+, but the company is still primarily a budget phone brand. The latest in its long line of G-branded phones, the Motorola G54, was just detailed in a new leak, and it shows off some of the phone’s colors.

If you’re interested in knowing more about the Razr+, you can read our full review. This phone was able to impress us more than the iterations before it. One of the main features has to be the larger cover display that lets you use any app. If you want to read the review, click on the link below.

Motorola Razr+ Review

A new leak shows off the upcoming Motorola G54

While not as exciting as the Razr+, the Moto G series of phones is popular in the budget device space. It’s the de facto phone to get if you’re looking for a solid smartphone experience. Now, we’re anticipating the next iteration in the series.

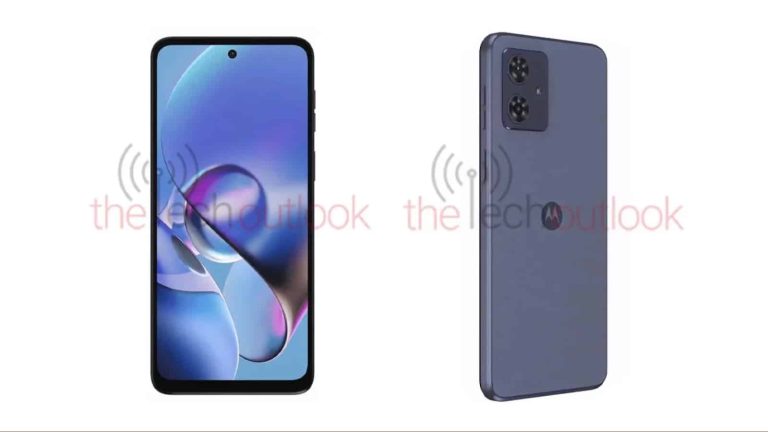
Thanks to The Tech Outlook (via 9To5Google), we have some leaked images of this phone, and it shows a very typical budget phone design. The first image shows the phone in a blue-ish gray color. We see the dual-camera package at the top left corner of the phone. It’s housed in a rounded rectangular box. The back looks like it’ll be made from a matte plastic material.

Motorola moto g54 leak 1
Image from The Tech Outlook

The front of the phone also shows a pretty standard budget phone experience. We see a center-mounted punch-hole. The bezels are decently large with the bottom chin being the thickest. It’s not bad, but you instantly get the sense that this is a more affordable phone.

The next picture shows the phone in four different colors. It only shows them from the back. Including the aforementioned blue-ish gray color, there’s also a dark gray, light blue, and green color. From the back angle, it becomes apparent that the camera package is housed in a metal island. We can see the reflections on the bottom side of the rectangle.

What are the rumored specs?

Since these specs haven’t been confirmed, you’ll want to take them with a grain of salt. If these specs are real, then this phone could be an upgrade over last year’s model. The Motorola G54 is expected to have 8GB of RAM (last year’s model boasted 4GB) and up to 256GB of onboard storage. There could also be microSD card expansion up to 1TB.

As for the display, it could have a decently large 6.5-inch FHD+ display with a 120Hz refresh rate. That’s about average for most mid-range phones nowadays.

We’re not sure on the processor for this phone. Last year’s phone used the Snapdragon 480 SoC. If the Motorola G54 is getting more RAM, hopefully, it will get a more powerful processor as well.

Motorola moto g54 leak 2
Image from The Tech Outlook

Other specs include a 50MP main camera accompanied by a 16MP selfie camera and a 5,000mAh battery. We’re still waiting to know when this phone will launch.


[ad_2]
Source link

China could limit children smartphone usage to just 2 hours per day

0
[ad_1]

The Chinese government has always maintained a tough stance on limiting children’s smartphone usage. Now, in line with these efforts, the Cyberspace Administration of China (CAC) has proposed a new draft which aims to tackle addictive behavior and the potential adverse effects of smartphones on children’s growth by imposing a limit on their smartphone usage.

If enacted into law, the proposed regulation would limit smartphone usage based on age groups. For example, children under the age of eight would have a maximum of 40 minutes of smartphone usage per day. Those between eight and 16 years old can use their phones for up to one hour daily, while teenagers aged 16 to 17 can use their phones for up to two hours.

Furthermore, the CAC has also proposed a new “minor mode” in smartphones, which mode would not only be accessible upon device activation but also enable parents to manage their children’s content access, thus ensuring they only see age-appropriate and safe material. Moreover, children under 3 years of age can only listen to songs and audio content.

Although regulated educational content and emergency services would be exempt from the restrictions, smartphones would not be allowed to offer any services to children from 10 p.m. to 6 a.m. to promote healthy sleep habits. Additionally, for children to disable the “minor mode,” they would need their parent’s verification.

Impact on the companies

Although the smartphone usage limit and the content restrictions could help kids in China overcome the growing smartphone addiction, there is some confusion about the implementation. This is because it remains uncertain whether the responsibility for creating the minor mode software would fall on operating system providers or device manufacturers.

Moreover, the content limitations for kids could also present a significant challenge for companies like Tencent and TikTok, which might need to make substantial changes to their app designs and content to align with the proposed time limits and ensure compliance with the government’s vision.


[ad_2]
Source link

Get in slo-mo, or any other camera mode, quickly with Shortcuts in iOS 17

0
[ad_1]

A more intuitive, faster iOS 17 user experience is on the way – Apple is beta testing an updated version of Shortcuts, where a newly added camera section is found (via 9to5Mac).

According to Matthew Cassineli (he worked on the iOS app Workflows before it was acquired by Apple and made free under the current name Shortcuts), “Apple has added an ‘Open Camera’ action for the Camera app that allows users to pick between camera modes and immediately open to any preset using Shortcuts”.

Shortcuts (former Workflow) lets you operate your iOS device (iPhone, iPad, Mac, Apple Watch) faster with the help of an automated series of processes. One step in a task is called an ‘action’, that’s the building block of a shortcut. Each shortcut is made up of one or more actions. You can set your own Shortcut, or use predefined ones, made by developers and fellow iOS users. For example, there’s a shortcut called Start My Day that will get you a brief overview of the weather, traffic conditions for your area with a brief summary of some world news. You can activate it via Siri command.So, the newly added Open Camera section lets users set a specific camera mode in the Camera app, without the need to hustle and bustle by opening the app and then switching to the desired mode.

Depending on the device used, there are up to nine different modes available:

  • Photo
  • Selfie
  • Video
  • Portrait
  • Portrait Selfie
  • Cinematic
  • Slo-Mo
  • Time-Lapse
  • Pano

If you’re surrounded by models in your everyday life, you can set a Portrait mode Shortcut and act on the decisive moment without worrying that you’re too slow. Or, if you’re heavy into creating beautiful time-lapse videos, Shortcuts has got you covered. Should you want to give it a try, iOS 17 beta is currently available through the Apple Developer and Apple Beta Software programs.

iOS 17 says “Hi” to entrenched Android users


An Open Camera section is far from the only thing that iOS 17 is expected to bring to the table this fall when it will debut alongside the iPhone 15 line. There are some Android-like features that Apple is bringing to iOS 17, like an improved iMessage, Contact posters, Interactive widgets, Offline Apple Maps, plus a revised Siri command-giving experience.

Presenting features that are already Android-available won’t make sworn users jump on the 2023 iPhone/iOS train right away. That’s why Apple is trying to lure Android aficionados with a bunch of tempting features, like NameDrop (an upgraded AirDrop-like feature), StandBy (it turns your iPhone into a smart display), Personal Voice (this one lets you train your iPhone to speak in your own voice by saying a bunch of random words out loud to the mic), and others.


[ad_2]
Source link

HackerOne Lays off 12% of Its Employees as a One-Time Event 

0
[ad_1]

HackerOne is a renowned cybersecurity company that offers bounty and penetration testing platforms to ethical hackers for the following activities:-

  • Asset discovery
  • Continuous assessment
  • Process enhancement for attack resistance management

HackerOne is a San Francisco-based startup, and at the moment, it boasts more than 450 employees globally.

However, HackerOne CEO Marten Mickos recently announced that the company decided to lay off 12% of its employees worldwide.

The company CEO has officially made this announcement through email and a blog post on their official site.

Announcement from HackerOne

Here’s what the CEO of HackerOne stated:-

“I have made the painful and necessary decision to undertake a restructuring and we will reduce the size of our team by up to approximately 12%. This comes as disappointing news, as we’ve all built strong connections with our fellow Hackeronies. These actions are necessary to be successful long-term. However, I understand how difficult this news is and the impact this will have on all team members, and I take responsibility for the changes we are sharing today.”

HackerOne’s global workforce of over 450 employees faces layoffs impacting more than 50 people. While besides this layoff, Mickos assured dismissal packages with:-

  • Cash compensation 
  • Non-cash benefits

Moreover, HackerOne affirmed that they continued hiring and investing in new products to expand capabilities, but unexpected anticipations and cost burdens occurred.

HackerOne is a cybersecurity category leader that remains a significant global contributor. But, as of now, they are actively preparing for growth and strength in future business conditions.

The unexpected economic impact leads HackerOne to team restructuring due to underperforming new products and challenges in the market.

The company considers this reduction in force a one-time event for future success.

HackerOne raised nearly $160 million since 2012, with key investors like:-

  • GP Bullhound
  • New Enterprise Associates
  • Valor Equity Partners
  • EQT Ventures
  • Dragoneer Investment Group

Not only that even it also serves as a bug bounty platform for U.S. DoD, Google, and Microsoft, connecting with global security researchers to fix vulnerabilities.

While this painful decision to let employees go is essential for HackerOne’s long-term success, despite their dedication to the company’s mission and open culture.

Keep yourself informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

YouTuber live streams Galaxy Z Flip 5 & Razr Plus folding test

0
[ad_1]

YouTube channel Mrkeybrd is back with Volume II of “The Great Folding Test” which tests the durability of the hinge and the folding screen of the latest foldable smartphones by manually folding and unfolding them repeatedly until they break. This time around, they are testing the Samsung Galaxy Z Flip 5 and the Motorola Razr Plus.

Like last year, the test is being live-streamed on YouTube. As of this writing, it’s already been about 19 hours since the marathon run began. Both foldables have crossed 40,000 folds without any damage. If last year’s result is the benchmark we are looking at, then it could take not hours but several days before either of the phones gives in.

Galaxy Z Flip 5 and Motorola Razr Plus face off in a manual folding test

For the uninitiated, the same YouTube channel carried out a similar test on the Galaxy Z Flip 3 last year. Samsung officially rates the phone to withstand 200,000 folds in its lifetime, but it survived much longer. The foldable reached over 418,500 folds, which is more than double the official rating. The hinge eventually gave up and the device refused to stay fully folded or unfolded.

The whole test took six days to complete. Since the Galaxy Z Flip 5 has the same official rating, it could stretch the YouTuber and their team for a similar duration this year as well. If you want to check on them, we have embedded the live stream at the end of this article.

“In the hands of consumers, these phones will go on boat rides, spend sunny days at the beach, fall in the snow, be tossed into the water, and generally get mishandled and misshapen by the chaotic nature of people,” the YouTuber wrote in a dedicated “The Great Folding Test” website. “Despite this, humans survive and sometimes even thrive, and we hope that these phones will too!”

The same website reveals that the Galaxy Z Flip 5 and Motorola Razr Plus will be subjected to various other durability tests once they pass the official fold rating stated by their respective manufacturers. Among other things, they will go through temperature, water, and drop tests. “This is where the human element of the test will shine,” the YouTuber says.

Note that folding screens can break more easily when exposed to extreme cold or extreme heat. Samsung officially rates its latest foldables to last only 30,000 folds at –4 (minus 4) degrees Fahrenheit/–20 (minus 20) degrees Celcius. So those temperature tests might kill the Galaxy Z FLip 5 and Motorola Razr Plus faster. You can watch the live stream below.


[ad_2]
Source link

Elon Musk to ask Apple to lower App Store fees on X subscriptions

0
[ad_1]

Elon Musk plans to ask Apple CEO Tim Cook to lower the App Store fees X pays on subscriptions purchased via iPhones. The X owner wants Apple to take a 30 percent cut of the subscription revenue it keeps after paying creators, rather than a 30 percent cut of the overall revenue. This would “maximize what creators receive,” he said in a lengthy post/tweet on Wednesday evening.

Apple charges a 30 percent fee on every in-app payment made on apps distributed through the App Store. This includes X subscriptions as well. If you subscribe to a creator on X using the iPhone app, only about 70 percent of the money you pay reaches the creator. Musk says this is a big loss for some creators who “live in tough circumstances.” He added that “even a few hundred dollars a month change their life.”

To ensure that, X will not keep a penny of subscription revenue creators generate for the first twelve months or even longer until the total payout exceeds $100,000. After that, it plans to take a ten percent commission. However, despite its efforts, creators lose money due to Apple’s hefty fees. Musk wants the iPhone maker to relax its policy for X subscriptions and help its efforts of supporting new and emerging creators on the platform.

Apple is unlikely to lower its App Store fees

There’s little chance Cook would entertain Musk’s request, though. The Apple CEO has fielded many such requests and public criticisms over the App Store fees over the years but never budged. Even Musk has previously called out the company publicly over its App Store policies. Matters got so worse at a point that the X owner accused Apple of threatening to withhold the app (called Twitter back then) from the App Store.

The duo eventually resolved the issue after a private meeting, with Musk later clarifying that the whole fiasco was a “misunderstanding.” However, he’s now back targeting Apple’s in-app payment policies. This time around, the world’s richest person is trying to persuade Cook by highlighting the need to support emerging content creators. Time will tell how the Apple CEO responds.

Both X and the creators would benefit if Cook accepted Musk’s proposal, though. While X won’t keep any subscription revenue for a year, a lower App Store fee means creators would reach a total payout of $100,000 sooner. X would then be able to keep ten percent of the revenue itself. The company’s ad revenue has reportedly dropped 50 percent in recent months, so any money would help.


[ad_2]
Source link

Elon Musk’s X faces copyright lawsuit in France over news content

0
[ad_1]

Elon Musk’s company, formerly known as Twitter, is facing a lawsuit in France for alleged copyright infringement. The Agence France-Presse (AFP) news agency shared that it has taken legal action against the social media platform. AFP claims that X has outright refused to discuss compensation for using AFP’s news content on its platform.


AFP is seeking an urgent court order in Paris to force X to provide the necessary information on how it reuses AFP’s content. This information is needed to calculate the amount of money AFP is owed under France’s neighboring rights legislation.


In 2019, the European Union made a decision to extend copyright law to include excerpts of news content that are shared on digital platforms. This means that using parts of news articles or content when sharing them online now falls under the scope of copyright protection in the EU.


After news of the lawsuit emerged, Musk responded in his typical manner by replying to the news tweet. It appears that he disagrees with AFP’s position.


Not only in the European Union but also in other regions, digital platforms are required by law to negotiate with publishers for remunerating news reuse. Canada recently passed the Online News Act, which also obliges tech platforms to negotiate with publishers for fair revenue sharing of their content.


In response to the Canadian law, tech giants Meta and Google have strongly opposed the measure and have hinted at the possibility of cutting off news availability in Canada instead of complying with the law. They previously used similar aggressive tactics in Australia, where they lobbied against the news bargaining code and pushed for amendments before it was eventually confirmed by lawmakers.

[ad_2]
Source link

Hackers Abuse AWS SSM Agent to Perform Malicious Activities

0
[ad_1]

Legitimate SSM agents can turn malicious when attackers with high-privilege access use it to carry out ongoing malicious activities on an endpoint.

Once compromised, the threat actors retain access to the compromised system, allowing ongoing illicit activities on AWS or other hosts.

Cybersecurity researchers at Mitiga recently discovered a new AWS post-exploitation technique. 

With the help of this new technique, threat actors run SSM agents as RAT on systems that are based on Windows and Linux. While this enables them to control the endpoints through a separate AWS account.

Abusing AWS SSM Agent

Amazon-signed SSM is a complete management system for admins that gives them the ability to manage the following things:-

AWS Systems Manager Agent (SSM) is widely used and comes pre-installed on many AMIs, which makes it a potential attack surface for hackers on a large pool of AWS instances.

Mitiga finds SSM agent can run in “hybrid” mode within EC2 limits, and this enables access to two key elements via attacker-controlled AWS accounts:-

SSM hybrid mode configures an AWS account to manage diverse machines like:-

  • Non-EC2
  • On-premise servers
  • AWS IoT devices
  • VMs across other cloud environments

Bash commands enable SSM agents to execute in non-associated AWS accounts, and SSM’s proxy feature allows traffic to pass outside AWS infrastructure.

Moreover, the complete exploitation chain depends on two scenarios, and here below we have mentioned them:-

  • Scenario 1: Hijacking the SSM agent
  • Scenario 2: Running Another SSM Agent Process

Abilities unlocked using the SSM Agent as a RAT

Here below, we have mentioned all the abilities:-

  • The SSM agent is signed by Amazon, so it’s initially trusted by Antivirus and Endpoint Detection & Response solutions.
  • Attackers don’t need to upload new RAT binaries since the SSM agent is already installed on the endpoint, avoiding AV and EDR products’ detection.
  • Threat actors can use their malicious AWS account as a C&C server which enables them to control the compromised SSM agent that makes their communication appear legitimate.
  • Attackers don’t need additional code for the attack infrastructure, as they rely solely on the SSM service and agent.
  • The SSM agent supports features like “RunCommand” and “StartSession,” giving attackers effortless control over the compromised endpoint from their AWS account, allowing them to manipulate it in various ways.
  • The SSM agent’s widespread installation in default AMIs within AWS increases the potential attack surface, providing more targets for threat actors.

Recommendations

Here Below we have mentioned all the recommendations:-

  • Reconsider adding SSM agent to AV or EDR allow list for security reasons.
  • To detect and respond to this malicious action effectively, make sure to integrate the detection techniques into your SIEM and SOAR platforms.
  • AWS security team suggests using the VPC endpoint for the Systems Manager to restrict command receipt from the original AWS account/organization.
  • Make sure to configure the System Manager service through a VPC endpoint.

Keep yourself informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link