As per reports, cybercrime will reach $10.5 trillion by 2025, including all kinds of cybercrime activities like RaaS, Phishing, malware, and much more. It will be mandatory for organizations to protect themselves from these threats.
According to Google, “ChromeOS, this is the cornerstone of our security strategy: ChromeOS devices are secure out of the box.” ChromeOS has been implemented in organizations worldwide for security and protection against data leakage.
Key Principles of ChromeOS
ChromeOS has the following things already implemented.
Booting is verified by default
Automatically blocks untrusted executables
Copy and paste, screen capture, printing, or USB downloading is prevented by default.
Chrome Browser can be used by IT and Security teams to see the Chrome extensions installed on the users’ browsers. They can also set policies for the extensions and have an approval workflow if a user requests an extension.
Security teams can see the “Extensions score” for all the extensions the user uses in the browser environment.
Note: Excavator and Spin.AI are the tools used to check the Chrome extensions’ risk assessment.
Risk Assessment Source: Google
“Secure by Design, Secure by Default” was the title of the new cybersecurity guidelines released by the CISA, NSA, FBI, and other International government agencies, including the US government.
The guidelines stated that developers and vendors must be aware of securing the core product design instead of depending on the end user.
Google stated that ChromeOS has all the core security designed and implemented by default. Adding to the security part of ChromeOS, Google has released some more features in ChromeOS. IT admins can do the following:
As part of data protection, IT administrators can protect the data in specific confidential locations like the HR or accounting apps.
Prevent Screenshotting, copy and paste, and social media leakage.
Specific user groups can be prevented from printing and screen sharing. This can be done based on the business requirements.
Nick Peterson, Security Engineer at Google Security, said, “ChromeOS data controls allow us to better understand how sensitive data moves through our company. This allows us to better focus resources, improving security while also helping teams become more productive and effective.”
Additionally, Chromebook Users can manage their camera and microphone access from the settings page of the OS itself, providing one-click access to turn on/off the camera/microphone.
Privacy Controls
As for monitoring purposes, IT admins can use Crowdstrike Falcon Insight XDR to monitor threats inside the users’ devices. Login/Logout will also be monitored, which can be integrated with any preferred SIEM Tools.
Google stated that “ChromeOS devices, built to be secure by default, have had zero reported ransomware attacks. With these capabilities announced today, ChromeOS continues to innovate and make the modern workplace safe and trusted.”
Google has released a complete list of features for users to check and strategize their organizations’ security infrastructure.
VMWare has released fixes and mitigations for three “Important” and one “Critical” vulnerability in its Fusion and Workstation software.
Four vulnerabilities in virtualisation software have been fixed by VMware, including two which were exploited at the 20223 Pwn2Own contest. Three have been given the severity rating “Important”, with the last (CVE-2023-20869) is classed as “Critical”.
CVE-2023-20869 is “Critical” flaw that affects Fusion and Workstation. It is a stack-based buffer overflow issue in the functionality for sharing host Bluetooth devices with the virtual machine. As per the advisory, “A malicious actor with local administrative privileges on a virtual machine may exploit this issue to execute code as the virtual machine’s VMX process running on the host.” Needless to say, guest VMs are not supposed to be able to make the host machines they’re running on do things.
CVE-2023-20870 is an “Important” flaw that affects Fusion and Workstation. It’s another issue in the functionality for sharing host Bluetooth devices, but with this one an attacker can potentially read privileged information stored in the virtual machine’s hypervisor memory.
CVE-2023-20871 is an “Important” flaw that only affects Fusion. It allows an attacker who has read / write access to the host operating system to elevate their privileges to gain root access to the host operating system.
CVE-2023-20872 is an “Important” flaw that affects Fusion and Workstation. It allows virtual machines with a physical CD/DVD drive attached to execute code on the hypervisor, if the drive is configured to use a virtual SCSI controller.
Workarounds and updates
All four issues can be addressed by updating to the latest version of the affected software. At the time of writing these are VMware Fusion 13.0.2 and VMware Workstation 17.0.2. Workarounds are available for CVE-2023-20869, CVE-2023-20870, and CVE-2023-20872.
CVE-2023-20869 and CVE-2023-20870 can be mitigated by turning off Bluetooth support by unchecking the “Share Bluetooth devices with the virtual machine” option. The relevant support documents for each product are VMware Workstation Pro, VMware Workstation Player, and VMware Fusion.
CVE-2023-20872 can be mitigated by removing the CD/DVD device from the virtual machine. Alternatively, you can configure the virtual machine so that it does not use a virtual SCSI controller. After shutting down the virtual machine, the steps are:
To remove the CD/DVD device in VMWare Workstation:
Select VM > Settings
Click the Hardware tab
Select the CD/DVD and click Remove
To remove the CD/DVD device in VMWare Fusion:
Select a virtual machine in the Virtual Machine Library window
Click on Virtual Machine menu
Click Settings
Under Removable Devices in the Settings window, select CD/DVD > Advanced Options > Remove CD/DVD Drive.
To configure VMWare Workstation not to use a virtual SCSI controller:
To configure VMWare Fusion not to use a virtual SCSI controller:
Select a virtual machine in the Virtual Machine Library window
Click on Virtual Machine menu
Click on Settings
Under Removable Devices in the Settings window, Select CD/DVD > Advanced options > Bus type
You can configure the Bus type.
Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.
Podcasts on YouTube Music are finally here. The new feature is gradually rolling out to users in the US, the company announced on Thursday via a YouTube Community post. All Android and iOS users should receive this update within the next few days.
YouTube Music has been working on adding support for podcasts for a few months now. The company confirmed the plans in February this year. Subsequently, it was spotted making necessary tweaks to the app behind the scenes to make room for the new feature. Yesterday, it officially rolled out podcasts to YouTube Music users in the US.
According to the official announcement, YouTube Music will host audio versions of all podcasts that are already available on the main YouTube app. You can seamlessly switch between the two apps for audio and video versions of a podcast, similar to how you can transition between music and music videos. The Music app will offer podcasts on-demand, offline, in the background, and while casting.
To listen to a podcast, all you have to do is search with a keyword. You can also tap on the “Podcasts” at the top of the Home tab for unfinished episodes and recommended podcasts. The app lets you filter the shows according to categories such as comedy, business gaming, music, health & fitness, and more. The Explore tab also lets you find new podcasts. The more you listen, the better your personalized recommendations get.
YouTube says the podcast experience on YouTube Music is different from its music experience. The latter requires a Premium or Music Premium subscription to enjoy some features, such as background playback. You do need a Premium subscription for ad-free listening, though. Note that you may still experience host-read endorsements or sponsorship messages in podcasts.
Podcasts in YouTube Music are currently limited to the US
Podcasts are growing in popularity, with all major music streaming services trying to carve out a market for themselves. Google doesn’t want to be left behind in this race. After hosting podcasts in the main YouTube app, it is now bringing this new form of entertainment to its music app as well.
At first, Google is keeping this feature limited to the US. But it plans to expand availability in other markets as well. “For those of you outside the United States, rest assured that we plan to bring podcasts in YouTube Music to other regions in the future!” the company said in its official announcement. We will let you know when the feature rolls out in other markets.
Discover the top 5 security breaches in recent history and learn how they happened, who was affected, and what lessons we can learn from them. From the Equifax data breach to the Yahoo hack, stay informed about the biggest cyber attacks that have impacted individuals and businesses worldwide.
These security breaches serve as a stark reminder of the importance of taking cybersecurity seriously. Whether you’re an individual or an organization, it’s crucial to take steps to protect yourself from potential threats.
By staying informed about past attacks and understanding how they happened, you can better prepare yourself for the future. From implementing strong passwords to regularly updating your software, there are many practical steps you can take to safeguard your digital assets. So don’t wait until it’s too late – start taking cybersecurity seriously today.
Five Of The Most Notable Security Breaches In Recent History
Here are the most significant security Breaches in history.
Equifax (2017)
In 2017, credit reporting agency Equifax suffered a massive data breach that exposed the personal information of over 147 million people. The breach occurred due to a vulnerability in Equifax’s website software, which allowed hackers to access names, Social Security numbers, birth dates, addresses, and other sensitive information.
Yahoo (2013-2014)
In 2013 and 2014, Yahoo suffered two massive data breaches that exposed the personal information of all 3 billion Yahoo user accounts. The breaches included names, email addresses, dates of birth, and encrypted passwords, as well as security questions and answers that could be used to access other accounts.
Target (2013)
In 2013, retail giant Target suffered a data breach that exposed the credit and debit card information of over 40 million customers. The breach occurred due to a vulnerability in Target’s payment system, which allowed hackers to steal card data at the point of sale.
Marriott International (2018)
In 2018, Marriott International suffered a data breach that exposed the personal information of up to 500 million guests. The breach occurred due to a vulnerability in the hotel chain’s Starwood guest reservation database, which included names, addresses, phone numbers, email addresses, passport numbers, and other sensitive information.
Sony Pictures (2014)
In 2014, Sony Pictures suffered a cyber attack that exposed the personal information of thousands of employees and leaked sensitive emails and other confidential information. The attack was believed to be carried out by a group of hackers backed by the North Korean government in retaliation for the studio’s production of the film “The Interview.”
What Kind Of Information Is Typically Stolen During A Security Breach?
During Security Breaches, different types of information can be stolen depending on the target and the attacker’s goals. Some common types of information that can be stolen during a security breach include personally identifiable information (PII) such as names, addresses, phone numbers, social security numbers, and email addresses. Other sensitive information that can be targeted includes financial data, credit card numbers, and bank account details.
In some cases, hackers may also target login credentials such as usernames and passwords, which can be used to access online accounts or even entire networks. Intellectual property such as trade secrets, product designs, and customer data can also be targeted during a security breach, especially in industries such as technology, healthcare, and finance. In some cases, attackers may seek to install malware or other types of malicious software that can provide them with ongoing access to a compromised system or network.
How Can Businesses Protect Themselves From Security Breaches?
Implement strong passwords: Use complex passwords that are difficult to guess and change them regularly.
Conduct regular security assessments: Regularly assess the security of your network and systems to identify vulnerabilities and address them proactively.
Install anti-malware software: Install anti-malware software to detect and prevent malware infections.
Use firewalls: Install firewalls to protect your network from unauthorized access.
Educate employees: Train your employees on how to identify and avoid phishing scams and other social engineering attacks.
Implement access controls: Implement access controls to restrict access to sensitive data and systems to only authorized personnel.
Keep software up-to-date: Ensure that all software is up-to-date with the latest security patches.
Backup data: Regularly back up data to ensure that it can be recovered in the event of a security breach.
Use encryption: Use encryption to protect sensitive data both in transit and at rest.
By implementing these measures, businesses can significantly reduce the risk of a security breach and protect their sensitive information.
What Are The Legal Consequences Of A Security Breach?
The legal consequences of a Security Breaches depend on various factors such as the nature and extent of the breach, the type of data that was compromised, and the jurisdiction in which the breach occurred. In some cases, a security breach may violate data protection laws and regulations, leading to fines, penalties, and legal action.
For example, the General Data Protection Regulation (GDPR) in the European Union imposes significant fines for data breaches. Additionally, some countries have data breach notification laws that require companies to notify affected individuals and regulatory authorities in case of a breach.
Apart from legal consequences, a security breach can also have a significant impact on a company’s reputation and brand image. Consumers may lose trust in the company, leading to a decline in sales and revenue. Therefore, it is essential for businesses to implement robust security measures to prevent breaches and mitigate the consequences in case of an incident.
How Can Companies Regain The Trust Of Their Customers After A Security Breach?
When a company experiences a security breach, it not only affects its finances and reputation but also erodes the trust of its customers. To regain that trust, companies need to take responsibility for the breach, provide transparency, and take proactive steps to prevent future breaches.
One way to regain trust is to offer credit monitoring and identity theft protection services to customers affected by the breach. Companies should also be transparent about the steps they’re taking to prevent future breaches, such as investing in better security protocols, conducting regular security audits, and hiring external security experts.
Another important step is to communicate with customers in a timely and clear manner. Companies should provide regular updates about the breach, the steps being taken to address it, and any compensation or remediation being offered to affected customers.
In addition, if you are searching for a safe and secure VPN so you can try this ExpressVPN Warzone deal it is the best offer and is budget friendly and this deal is especially for Call of Duty: Warzone.
What Are The Financial Costs Of A Security Breach?
Security breaches can result in significant financial costs for businesses. These costs can include direct expenses, such as the cost of repairing systems and networks, paying for forensic investigations, and providing identity theft protection services to affected customers.
In addition, there may be indirect costs such as lost revenue due to decreased customer trust, damage to brand reputation, and legal fees. The cost of a security breach can vary depending on the severity of the breach, the amount and type of data compromised, and the size of the affected organization.
According to a report by IBM, the average cost of a data breach in 2021 was $4.24 million. This represents a significant increase from previous years and underscores the importance of investing in cybersecurity measures to prevent breaches from occurring. Small businesses may also be at risk, as they may not have the same level of resources to invest in cybersecurity as larger organizations.
How Can Companies Prepare For A Potential Security Breach?
Companies can take several steps to prepare for a potential security breach, including:
Conducting regular security audits and risk assessments to identify vulnerabilities in their systems.
Establishing a comprehensive incident response plan that outlines the steps to take in case of a breach, including who to notify and how to communicate with customers.
Implementing strong access controls, including multi-factor authentication and role-based permissions, to limit the number of people who can access sensitive data.
Providing regular cybersecurity training to employees, including how to identify phishing emails and other common tactics used by hackers.
Regularly updating software and security systems to address any known vulnerabilities.
Backing up important data to an offsite location to ensure that it can be recovered in case of a breach.
By taking these steps, companies can better protect themselves from Security Breaches and minimize the damage if it does occur.
What Is The Role Of Cybersecurity Professionals In Preventing Security Breaches?
Cybersecurity professionals play a critical role in preventing Security Breaches. They are responsible for implementing security measures, monitoring networks for potential threats, and responding quickly to any security incidents.
Their role includes conducting regular security assessments, identifying vulnerabilities, and implementing security protocols to mitigate risks. They also develop incident response plans, conduct security awareness training for employees, and stay up-to-date with the latest security trends and threats.
In addition, cybersecurity professionals work closely with other departments within a company, such as IT and legal, to ensure that security policies and procedures are aligned with business goals and regulatory requirements. They may also work with external partners, such as third-party vendors, to ensure that security measures are in place and that data is protected throughout the supply chain.
How Can Companies Ensure That They Are In Compliance With Relevant Data Protection Laws?
Data protection laws are becoming increasingly strict and complex. Companies must ensure that they are in compliance with all relevant laws and regulations to avoid potential legal and financial consequences.
To ensure compliance, companies should develop comprehensive data protection policies and protocols that address all aspects of data handling, from collection to storage and destruction.
One way companies can enhance their compliance with data protection laws is by engaging legal and cybersecurity experts who can offer guidance on best practices. Additionally, regular training and education programs can be implemented for employees to ensure that everyone within the organization understands their responsibilities and knows how to handle data securely. For instance, obtaining a 1-year ExpressVPN deal could be a practical step to improve the organization’s online security and protect confidential data.
It is also important for companies to regularly review and update their data protection policies and protocols as laws and regulations evolve. This will help ensure that they are always in compliance and prepared for any changes that may come.
How Can Customers Be Notified In The Event Of A Security Breach?
In the event of a Security Breaches, companies have a responsibility to notify their customers and users as soon as possible. The notification should include details about the breach, what information was affected, and what actions the company is taking to address the issue. Companies should also provide guidance to customers on how they can protect themselves, such as changing their passwords or monitoring their financial accounts.
In some cases, companies may also offer credit monitoring or identity theft protection services to affected customers. It’s important for companies to have a clear and comprehensive communication plan in place to ensure that customers are informed and have the necessary information to protect themselves.
The Cosmos cooperative bank in Pune, among the city’s oldest urban cooperative banks, has fallen prey to cyber fraudsters. Hackers gained access to the bank’s system and stole Rs 94 crore.
A court in Maharashtra’s Pune had found 11 persons guilty. Fahim Shaikh and Mohammad Saeed Iqbal Hussain Jafari of Bhiwandi, Fahim Khan and Shaikh Mohammed Abdul Jabbar of Chhatrapati Sambhajinagar, Mahesh Rathod of Nanded, Naresh Maharana of Palghar, U A Waz alias Anthony, Bashir Ahmed and Feroz Shaikh of Mumbai, and Abdulla Shaikh and Salman Baig of Thane were convicted.
The Largest Cyber Assaults on An Indian Bank
On August 11, 2018, numerous cloned debit cards of Cosmos Bank were used for thousands of ATM transactions from India and 28 other countries over seven hours.
Reports say a further set of 2,800 transactions totaling Rs 2.5 crore were done in various locations nationwide, while more than 12,000 ATM withdrawals totaling almost Rs 78 crore were made outside of India.
The Society for Worldwide Interbank Financial Telecommunication (SWIFT) service was also used to transfer an additional Rs 13.92 crore to a Hong Kong-based organization on August 13, 2018.
According to the police investigation, Visa cards were used for transactions outside India, while RuPay cards were used for transactions within India.
Notably, in this case, which was reported to the Chaturshringi police station under the provisions of sections 120B, 420, 467, 468, 469, 471, and 34 of the Indian Penal Code (IPC) and the corresponding sections of the Information Technology Act, a total of Rs 94 crore was siphoned.
A bank official claims that early investigation indicates that the hacking activity originated in Canada.
According to the Indian bank, cybercriminals targeted its ATM infrastructure in the first intrusion. It did not disclose how the attack occurred.
Still, it did say that malware was used to disconnect the ATM infrastructure from the central switching system, preventing it from receiving real-time information about cash withdrawals from ATMs.
“We have filed a complaint and are also taking help from the National Payments Corporation of India (NPCI) and the RBI to see what can be done,” said Krishnakumar Goyal, a director of the cooperative bank.
He continued by saying that no clients were impacted and that the bank had suffered a loss due to the money being taken out of a pool account.
Pune Court Declares the Accused Guilty
The police arrested 18 people throughout their investigation for their claimed involvement in the cyberattack, who came from various areas. According to the authorities, one accused had passed away, and 17 were being held behind bars.
The majority of people arrested, according to the police, were primarily involved in following handlers’ instructions to withdraw cash from various ATMs using Cosmos Bank cloned cards. The police believe that some of the money they withdrew was given to them as a commission by the racketeers.
Fahim Shaikh, Fahim Khan, Shaikh Mohammed Abdul Jabbar, Mahesh Rathod, Naresh Maharana, Mohammad Saeed Iqbal Hussain Jafari, and Anthony were among the 11 found guilty and given simple imprisonment of four years and seven months, according to the press statement.
According to the release, Feroz Shaikh and Salman Baig received three years of simple jail, while Abdulla Shaikh and Bashir Ahmed received four years each.
Four additional people are still wanted in connection with the investigation, three of whom — Kunal Shukla, Abdul Bhai, and Sumer Shaikh — are believed to be in Dubai, according to the police.
Finally, the Pune City Police and Cosmos Bank successfully recovered Rs 5.72 crore that the scammers had fraudulently placed into a bank in Hong Kong after the malware assault.
Vulnerabilities in PaperCut printing management are being used in ransomware attacks.
A few days ago we wrote about two vulnerabilities found in PaperCut application servers. As we noted, exploitation was fairly simple so there was some urgency to install the patches. My esteemed colleague Chris Boyd literally wrote:
“Arbitrary code can be deployed, or even ransomware if that’s part of the attacker’s toolkit.”
As it turns out, there are already two flavors of ransomware preying on those that haven’t updated yet.
In a surprising turn of events for the ransomware landscape, Cl0p emerged as the most used ransomware in March 2023, coming out of nowhere to dethrone the usual frontrunner, LockBit.
Known ransomware attacks in March 2023, listed by gang
But don’t rule the habitual frontrunner LockBit out just yet. Microsoft Threat Intelligence said in a tweet that it’s “monitoring other attacks also exploiting these vulnerabilities, including intrusions leading to Lockbit deployment.”
PaperCut is printing management software that works by intercepting print jobs as they pass into a print queue. It’s used by large companies, state organizations, and education institutes because it is compatible with all major printer brands and platforms. This makes a vulnerability, especially one that is as easy to exploit, a virtual goldmine for ransomware peddlers, and puts a bullseye on anyone that is running an unpatched server.
Both the underlying vulnerabilities have been addressed with patches. If you update your PaperCut application servers, you are no longer at risk. From the Updating FAQ:
Please follow your usual upgrade procedure. Additional links on the ‘Check for updates’ page (accessed through the Admin interface > About > Version info > Check for updates) will allow customers to download fixes for previous major versions which are still supported (e.g. 20.1.7 and 21.2.11) as well as the current version available.
If you are using PaperCut MF, we highly recommend following your regular upgrade process. Your PaperCut partner or reseller information can also be found on the ‘About’ tab in the PaperCut admin interface.
If you’re unable to upgrade, PaperCut advises the following:
Block all inbound traffic from external IPs to the web management port (port 9191 and 9192 by default)
Block all traffic inbound to the web management portal on the firewall to the server. Note: this will prevent lateral movement from internal hosts but management of the PaperCut service can only be performed on that asset.
Apply “Allow list” restrictions under Options > Advanced > Security > Allowed site server IP addresses. Set this to only allow the IP addresses of verified Site Servers on your network. Note this only addresses ZDI-CAN-19226 / PO-1219.
Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.
Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.
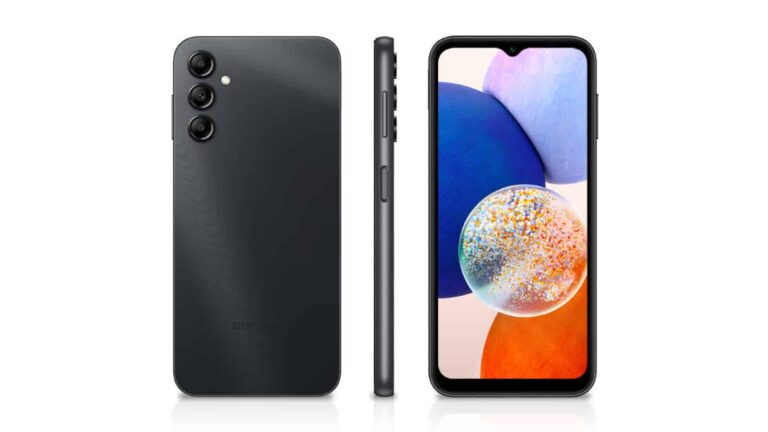
Samsung is pushing the One UI 5.1 update to the Galaxy A14 5G in the US. The rollout began recently for users on Verizon’s network. The company should cover eligible units on all carriers across the nation over the next few days. The update also brings the April 2023 Android security patch.
Samsung launched the Galaxy A14 5G in January this year. It was the first Galaxy device to arrive in the US in 2023. The budget smartphone came running Android 13-based One UI 5.0 out of the box. One UI 5.1 wasn’t ready back then as it debuted with the Galaxy S23 series in February.
Over the past couple of months, Samsung has pushed One UI 5.1 to several dozen Galaxy smartphones and tablets around the world. The Galaxy A14 5G started picking up the new One UI version in March. Following the initial release in a handful of Asian countries, the company expanded the rollout to Europe and other regions earlier this month. It has now reached the US as well.
The One UI 5.1 update for the Galaxy A14 5G on Verizon’s network comes with the firmware build number A146USQU2BWD4, SammyFans reports. Users on other networks should also get this release with a similar build number. More importantly, your phone will pick up a host of goodies with this update. Among those are a new Shared Family Album in Gallery, new gestures for minimizing or maximizing windows, enhanced modes and routines, activity-based wallpapers, dynamic widgets, and smart suggestions.
On top of these goodies, the Galaxy A14 5G is also gaining this month’s security patches. Samsung says the April SMR (Security Maintenance Release) contains fixes for more than 70 vulnerabilities. At least five of those are critical flaws. The company has already released the May security patch but the Galaxy A14 5G may not get it. This budget phone is only eligible for quarterly security updates. The company will skip a few releases and update it once every three months or so. Security updates will come at least until January 2027, though.
Galaxy A14 5G will also get Android 14 and Android 15
Along with four years of security updates, Samsung also promises two major Android OS updates for the Galaxy A14 5G. That means it will receive Android 14 and Android 15, along with the company’s latest One UI skin. Android 14 will bring One UI 6.0 and may start rolling at the fag end of this year or early next year. We will keep you posted.
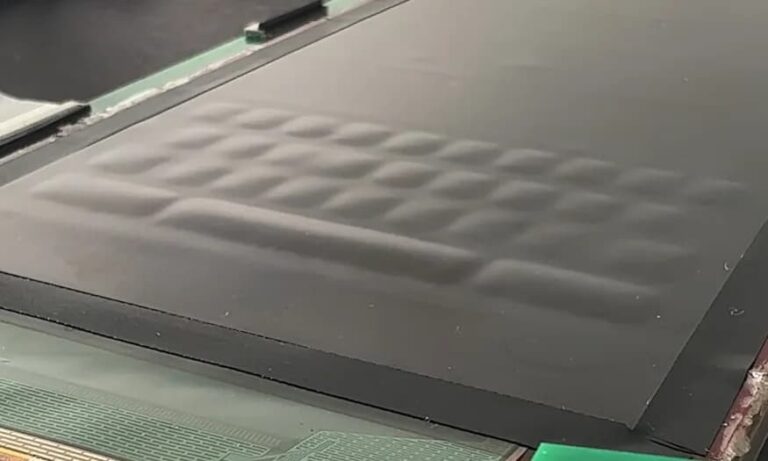
It’s no secret that ever since the first full touchscreen smartphones hit the market, keypads and keyboards have slowly disappeared. And while touchscreens have allowed for more screen real estate and greater app functionality, there is still a big fraction of people who prefer a tactile feel when interacting or typing on their smartphones. Now, to address this issue, researchers from the Future Interfaces Group (FIG) at Carnegie Mellon University have developed a new technology called “Flat Panel Haptics.”
The Flat Panel Haptics technology uses Embedded Electroosmotic Pumps (EEOPs) stacked under an OLED panel to create protrusions based on different scenarios. Therefore, when an on-screen element requires a pop-up button, fluid fills a section of the EEOP layer and bends the OLED panel on top, creating a button that protrudes from the flat surface by as much as 1.5 mm and providing tactile feedback for users. And when the user or the software dismisses it, the liquid recedes.
“In this work, we present a new approach and vision for miniaturizing haptic shape-changing displays. Flat panel haptics takes inspiration from LCD flat panel visual displays, which embed their actuator element directly in a thin, compact form factor, and allow control of a display element through an applied voltage,” says FIG.
Advantages of the Technology and the Future
While other researchers and companies have attempted to create similar technologies in the past, the required hardware was always too bulky and inconvenient. However, the pumps developed by the Carnegie Mellon team make the entire system compact and thin, with a thickness of just 5mm. Moreover, the technology is self-contained and self-powered and only adds 40 grams of weight to the device.
The FIG believes that this technology has the potential to revolutionize the way we interact with electronics. This is because touch screens, while on one hand, offer ample real estate for apps to display content and other information, they are challenging to navigate for people with visual impairment. Therefore, with the use of tactile touch displays, visually impaired users can use their smartphones without relying on auditory feedback.
If you have ever had to configure a firewall, set up a router, or choose the best VPN for your computer, chances are you heard of the TCP and UDP protocols. However, if you’re reading this article, you’re probably confused about what they are, their purpose, and their main characteristics.
Today, we’ll look at the differences between TCP and UDP and the reasons why there are two transport layer protocols.
What is Transport Protocol?
Before we can dive deeper into the differences between TCP and UDP, you should know what a transport protocol is in the first place.
Both the User Datagram Protocol (UDP) and the Transport Control Protocol (TCP) are mechanisms used by applications and software to transfer packets of data on the Internet.
In a nutshell, whenever you send data on the internet (such as sending a file over Skype or Facebook, or just a mail), the transfer protocol is like a postman that sends that information to the destination by splitting it into several small packages (packets).
They are both built on the IP protocol, meaning that each packet sent by either protocol is forwarded to an IP address through a series of intermediary routers.
In fact, neither one of them interacts directly with the IP layer. You probably heard of them as TCP/IP and UDP/IP – it’s the same thing. People call them TCP and UDP for the sake of simplicity.
However, they are, by far, the most used; the TCP and UDP are not the only two protocols working on top of IP. For example, many different VPN protocols are used to hide and encrypt data.
What is the TCP?
TCP is a connection-oriented protocol that sends packets back and forth from the sender to the destination and vice-versa. It ensures that every packet is delivered to the server in the exact order it was sent initially by establishing a two-sided connection between the sender and receiver.
It also uses a flow control mechanism that stores data in buffers. This way, the application will send data only when it’s ready to be received, preventing the sender from being overwhelmed and avoiding bottlenecks. However, all this overhead work means that TCP is usually slower.
When is it More Convenient To Use TCP?
TCP is a reliable transmission protocol that ensures that data is sent in a specific order and error-checked at all times. Since packets are tracked and checked for corruption, no data is ever lost even if network issues occur in between.
TCP is the best choice if you are hosting a website or need to ensure that data is sent correctly and without risk of corruption. However, you need both sides to be online or communication cannot be set up.
Pros of TCP
Very reliable
Data lost will be resent
Delivery is guaranteed
Packets are checked for errors and corruption
Cons of TCP
Requires both sides to be online during the transfer
Slower than UDP
Doesn’t work offline
What is UDP?
As specified in the RFC768 document, UDP is the most straightforward protocol, quickest, and most efficient. Packets are lightweight since they’re sent with minimal headers, and no connection is established before datagrams are sent (connectionless). UDP is used to send emails – you send them even if the receiver it’s offline.
To keep things more straightforward (and faster), no recovery is set – all corrupted or missing packets are discarded and not requested again. The sender will keep sending the packets, regardless of whether the recipient receives them.
Packets are sent in a continuous stream with no flow control, meaning that data is transferred much quicker than TCP, but if a network issue occurs, all packets are dropped.
When is it More Convenient to Use UDP?
To keep things simple, UDP is better than TCP whenever you need speed over reliability. For example, it is the ideal choice in online gaming, where you only care about what’s happening in real time.
If you lost a packet while shooting someone, there’s no point in receiving it later. Other examples are applications that require speed and efficiency such as broadcasting platforms or streaming networks. UDP is usually preferred in log management activities to avoid TCP-related timeouts or connection issues.
Pros of UDP
Extremely quick and efficient
Reduced network traffic
Doesn’t require both parties to be connected
Cons of UDP
Delivery is never guaranteed
Packets may get lost or corrupted
Data cannot be sequenced
Conclusion
Both the TCP and UDP protocols have their benefits and drawbacks. Depending on your needs, you may prefer one or the other. Even today, many technologies, such as emails or online gaming, require the use of either a connectionless rather than a connection-oriented protocol, regardless of overhead, reliability, or speed.
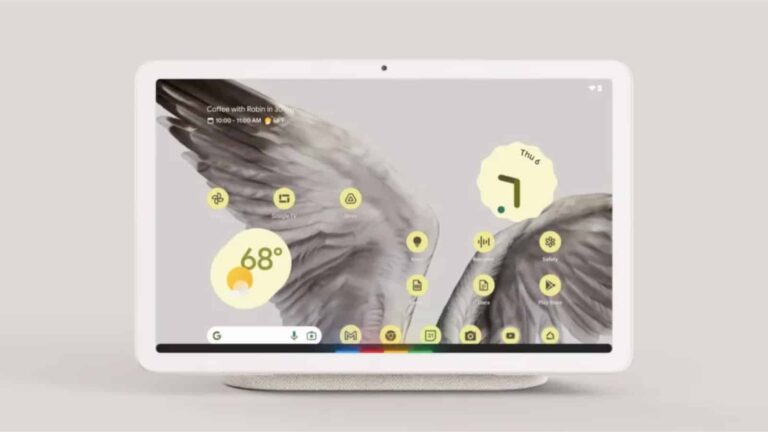
All eyes are on Google this year as the company is going to bring the first tablet into its Pixel family. At the time of writing this article, the price for it hasn’t been revealed. However, we know how much the charging dock is going to cost, and it’s pretty pricey at $129. So, it seems that Google is gearing up to offer an interesting tablet. The question is, could the Pixel Tablet be a bit too niche to pick up?
The mentality behind the Pixel Tablet is the same mentality behind notebook foldable phones: having one device that can switch modes and basically transform into another. In the case of the Pixel Tablet, it will act as a tablet when undocked and a smart display when docked.
It’s a neat idea! While this has been done before, it hasn’t been done with much success. Enter Google to turn this gimmick from trashed to trendy. The only thing is that we’re in the middle of a global economic struggle. People are watching every penny they spend that much closer, so it’s much more important to sell a tablet that will appeal to more people.
The Pixel Tablet might be a bit too niche
The Pixel Tablet is shaping up to be a pretty capable device. We’re looking at a large screen with a nice resolution, 8GB of RAM, up to 256GB of storage, and the powerful Google Tensor G2 SoC. The fact that this tablet’s going to be built from the ground up for this chip only sweetens the deal.
However, as powerful as this device is, it’s still a tablet. The tablet market has been on a consistent decline over the years, and it’s still falling despite the boost it got during the pandemic. So, getting people to buy the Pixel Tablet in the first place is already a struggle.
Also, while we’re still in the dark on the price, let’s not mince words; this is going to be a flagship tablet, so we should expect a flagship price.
Now, let’s factor in the next part of the equation, the dock. This is what’s going to turn this tablet into a smart display. More specifically, it’s going to turn it into a Nest Hub. At $129, the charging dock is a bit pricey. It’s not horrendous, but the fact that the Nest Hub (2nd Gen) costs $99 shines a pretty harsh light on it.
What makes it the Pixel Tablet niche?
Now, the reason why the Pixel Tablet could be too niche is that it’s trying to appeal to two niche markets at the same time. It’s looking to appeal to the tablet user and the smart display user. One might say that this is a good thing. Appealing to more markets might make it more likely that people will buy it.
However, it may not be as direct as that. Google is looking to appeal to the market of people who simultaneously want to use a tablet and a smart display. Those are two niche markets in and of themselves. The Pixel Tablet is meant to appeal to the Venn diagram intersection of those two markets, and that might be a small section of the graph.
Are there enough people out there who want both to justify a second-generation Pixel Tablet? While companies have blended tablets and smart displays before, there’s never really been a huge need for it. So, expecting someone to tack on an additional $129 for the full Pixel Tablet experience might be too much.
Without the stand, there’s not much to set it apart
The fact that the stand is a separate accessory that you’ll need to purchase might pose an issue because without it, what else is there to differentiate it from the other tablets?
The thing with Galaxy Tabs and iPads is that they have an immediate audience. It doesn’t matter what those devices have or lack, fans will flock to those devices en masse. Surface tablets have a full desktop operating system loaded onto them.
Those are the tablets that the Pixel Tablet is going to trade blows with when it launches; the upper-tier tablets. So, what will the Pixel Tablet have to combat them? Well, there’s the ability for it to seamlessly convert into a smart display. That’s significant, and there’s no doubt that this will attract some users.
But this tablet is going to need to appeal to the masses in order to maximize profits, and the common consumer won’t want to pay an additional $129. So, without the addition of the charging stand, the Pixel Tablet doesn’t have much to set it apart.
Sure, you get the optimized Android tablet experience, but there are other tablets like the OnePlus Pad, newer Galaxy Tabs, and the Lenovo tablets that have this. Yes, you’ll have the integration between it and other Pixel devices, but that requires you to have other Pixel devices.
As far as the specs go, there’s nothing that will make this tablet turn heads. We can expect the tablet to perfectly leverage the Tensor G2 SoC, but it has 8GB of RAM, up to 256GB of storage, a 2K display, four speakers, and a decent battery. These are really good, but nothing sticks out. The defining trait of the Pixel Tablet is its dock- an attachment.
The price could be the make-or-break aspect
One of the missing pieces to the puzzle is the price. We’re still in the dark about how much this tablet is going to cost. As stated, the specs are really good. They’re not extreme, but they could facilitate a hefty price tag.
However, there’s a chance that Google could wow us with the price. The trick is to sway people away from the Galaxy Tabs and the iPads of the world. So, if Google prices this tablet at or around the price for those tablets, then that’ll be a hard task chipping at their fanbases.
If Google can price this tablet low enough to (while making a profit, of course) undercut some of the mid-tier and upper-tier tablets from competitors, that could be a solid win for it. That would also convince customers to invest in the charging stand.
The Pixel Tablet seems like an interesting device, but there are some factors going against it at the moment. Maybe Google will surprise us; you never know. All we know is that we’re all excited to see this tablet take on the titans of the tablet world. We expect it to launch around Google I/O.