Palo Alto ZeroDay Exploited in The Wild Following PoC Release

0
[ad_1]

Palo Alto Networks has disclosed a critical vulnerability within its PAN-OS operating system, identified as CVE-2024-3400.

This zero-day flaw, found in the GlobalProtect Gateway, is currently under active exploitation by attackers.

CVE-2024-3400 allows attackers to execute arbitrary OS commands on the affected systems without proper authentication.

The threat actors are now actively exploiting this Palo Alto ZeroDay in the wild following the PoC release.

Palo Alto ZeroDay Exploited

Researchers identified vulnerabilities and developed an exploit for GlobalProtect in three days that targeted Palo Alto VPN-SSL solutions. 

WatchTowr explained a path traversal bug with a command injection resulting in a PoC via POST request to “…/ssl-vpn/hipreport.esp”. 

It permits command injection through the SESSID cookie, which can potentially drop webshells as cron jobs. 

Rapid7’s and WatchTowr’s PoCs spread quickly, followed by TrustedSec and ShadowServer reporting on some real attacks, while some of the earlier PoCs were fake or malicious. 

Expect widespread attacks soon since Palo Alto solutions are not audited enough.

Palo Alto increased the risk level to 5 out of 5 (CVE-2024-3400), requiring either patches be applied or specific Threat Prevention signatures configured in counteraction. 

This modification will help prevent devices from becoming overloaded due to command execution attempts. They shared additional IOC and CLI commands, which mainly focused on recent vulnerabilities and not the original threat actor. 

Onyphe developed a query tool that can help identify GlobalProtect versions, which can aid patch confirmation activity. However, this will expose vulnerable servers to threat actors. 

EmergingThreats unveiled a Suricata rule designed explicitly to detect WatchTowr PoC usage. Rapid7 observed constant exploit attempts and documented them via multiple logs.

Palo Alto released patches for the critical 0day CVE-2024-3400 on April 14, with three fixes available for affected branches. On April 19, patches for the older versions will be released.

Another mass compromise has not been directed by adversaries, indicating a targeted campaign called MidnightEclipse. 

Volexity established that the adversary had moved laterally into internal systems using a Python backdoor named “update.py” and additional payloads designed to exfiltrate valuable data. 

Although some infrastructure is still online, no definite public PoC exists, and expert researchers might use the patched 0day for advanced research.

Looking to Safeguard Your Company from Advanced Cyber Threats? Deploy TrustNet to Your Radar ASAP.


[ad_2]
Source link
Sony Xperia 1 VI launch event date tipped for next month

0
[ad_1]

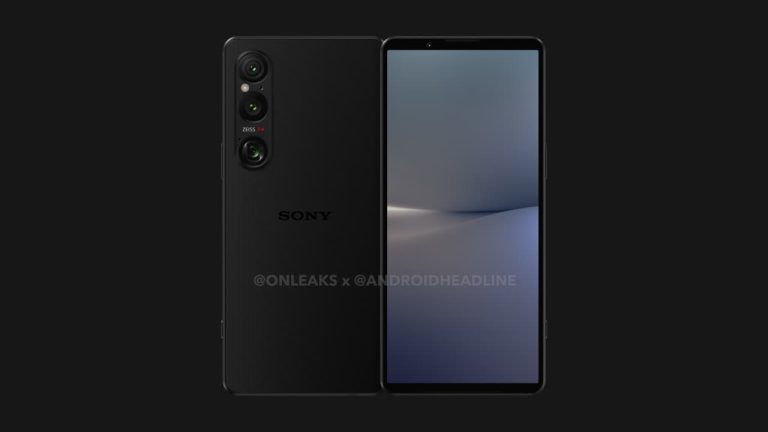
The Sony Xperia 1 VI launch event will seemingly take place next month, as the date has just been tipped. A poster leaked on Weibo (shown below the article), suggesting that the phone will become official on May 17. That’s a Friday, in case you were wondering.

The Xperia 1 VI launch date seemingly revealed, as the phone is expected to arrive next month

Do note that the poster itself does not specifically mention the Xperia 1 VI. However, it’s that time of year, and when it comes to Xperia devices, there are not many phones Sony is willing to host events for.

That being said, we’ve exclusively shared the design of the Xperia 1 VI quite recently. The phone will look similar to last year’s model, but it will be a bit shorter and a bit wider. Sony is changing the display aspect ratio from 21:9 to around 19.5:9.

In other words, the overall size will be more similar to regular smartphones. Sony’s phones have been very tall and narrow for quite some time now. The phone will measure roughly 161.9 x 74.5 x 8.4mm. It will include a 6.5-inch panel, and retain bezels above and below the display. Sony simply refuses to include a display camera hole.

It will include three cameras on the back, and retain a headphone jack

The Xperia 1 VI will have a flat display, with flat sides, and three cameras on the back. Those cameras will be vertically aligned in the top-left corner of the phone’s back. Sony’s logo will also be present on the back.

What’s also interesting is that the phone will retain a headphone jack. It will be located at the top. The Xperia 1 VI will be made out of metal and glass, as expected.

Based on rumors, the Xperia 1 VI may give up the 4K display for a QHD+ panel. It will surely be an AMOLED panel with an adaptive refresh rate that will go up to 120Hz, though.

The Snapdragon 8 Gen 3 will almost certainly fuel the Xperia 1 VI. We’re also expecting to see at least 12GB of LPDDR5X RAM inside the phone.

Xperia 1 VI launch date poster leak


[ad_2]
Source link

Google Pixel 7, Fold, and 8 series receive the April update

0
[ad_1]

Google has begun rolling out new April updates for its Pixel 7, 7 Pro, 7a, Fold, 8, and 8 Pro phones. These updates, currently available as new Android 14 QPR2 builds, offer the April 2024 security patch and features from the Developer Preview.

While these updates are not yet available over the air (OTA) for everyday users, developers can download the factory images and flash them onto their devices. Google Pixel 7, Pixel 7 Pro, Pixel 7a, Pixel 8, and Pixel 8 Pro (Review) are receiving the build number AP1A.240405.002.B1 while the Pixel Fold was listed as AP1A.240405.002.A2.

What is in the new April update and why you might want to wait

Google hasn’t announced the official OTA update date for the Android 14 QPR2 with the April patch. But factory images suggest it’s close. Google rolls out updates in stages, so some users might get it within days, while others wait a few weeks. You can check for the update manually in Settings > System > System update.

The update is expected to include the April security patch, potential bug fixes, and performance improvements. Pixel users might also see minor UI tweaks and optimizations. However, these are developer builds, meaning features and functionalities might be unstable or even missing compared to the final version.

No major update until June

The next major update, Android 14 QPR3, isn’t expected until June. So, Pixel users can expect a more minor update next month, likely focused on security and stability improvements.

For those eager to jump straight to Android 15, the Beta 1 is available. However, it currently lacks Near Field Communication (NFC) for contactless payments like Google Pay. This makes the Android 15 Beta less ideal for daily use until Google fixes this.

Google’s rollout of the Android 14 QPR2 update builds lets developers tinker with upcoming features and security patches. But for most Pixel users, waiting for the official OTA update with stable Android 14 builds remains the safest and most practical option.


[ad_2]
Source link

The New Android Banker’s Unique Techniques

0
[ad_1]

A new banker, SoumniBot, has recently been identified. It targets Korean users and is incredible by using an unusual method to evade investigation and detection, notably obfuscating the Android manifest.

In addition to its unique obfuscation, SoumniBot stands out for its ability to steal Korean online banking keys—something Android bankers hardly do. 

This capability enables malicious actors to bypass bank authentication procedures and empty the wallets of unintentional victims. 

Researchers say SoumniBot’s creators sadly succeeded because the Android manifest parser code’s validations were not strictly enough.

Techniques Used By SoumniBot

The Kaspersky researchers explain that the standard unarchiving function in the libziparchive library only allows the following two values for the Compression method in the record header: 0x0000 (STORED, which is uncompressed) and 0x0008 (DEFLATED, which is compressed using the zlib library’s deflate), else it returns an error.

However, the Android developers choose to provide a different scenario in which the value of the Compression method field is checked wrongly rather than utilizing this function.

“If the APK parser comes across any Compression method value but 0x0008 (DEFLATED) in the APK for the AndroidManifest.

xml entry, it considers the data uncompressed. This allows app developers to put any value except 8 into Compression method and write uncompressed data”, researchers said.

Invalid Compression method value followed by uncompressed data

The Android APK parser successfully identifies the manifest and permits application installation, even though any unpacker that correctly implements compression method validation would consider a manifest like that invalid.

Secondly, the size of the manifest file is indicated in the header of the AndroidManifest.xml entry within the ZIP archive.

Even though the entry’s size is indicated inaccurately, it will be copied from the archive unaltered if stored uncompressed. 

The manifest parser ignores any overlay or information after the payload that isn’t connected to the manifest.

This is exploited by the malware, which adds some of the archive content to the unpacked manifest due to the archived manifest’s reported size exceeding its real size. 

Finally, the names of the XML namespaces are represented by very long strings included in the manifest.

These kinds of strings make manifests unreadable for both people and programs, which might not have enough memory allocated to handle them. 

“When run for the first time, the Trojan hides the app icon to complicate removal, and then starts to upload data in the background from the victim’s device to mainsite every 15 seconds”, researchers said.

The information contains the victim’s ID, which was created using the trust device-android library, contact and account lists, the country inferred from the IP address, SMS and MMS messages, and other data.

The Trojan subscribes to messages from the MQTT server to receive commands.

If you want to avoid becoming a victim of malware of that kind, it is advised to use a reputable security app on your smartphone to identify the Trojan and stop it from installing despite all of its tactics.

Indicators of compromise

MD5
0318b7b906e9a34427bf6bbcf64b6fc8
00aa9900205771b8c9e7927153b77cf2
b456430b4ed0879271e6164a7c0e4f6e
fa8b1592c9cda268d8affb6bceb7a120

C&C
https[://]google.kt9[.]site
https[://]dbdb.addea.workers[.]dev


[ad_2]
Source link

Twitch is getting a new TikTok-inspired feed

0
[ad_1]

It hasn’t been too long since Twitch hinted at the development of a new feed called the Discovery feed. Now, Twitch is introducing this feed to their mobile app later this month.

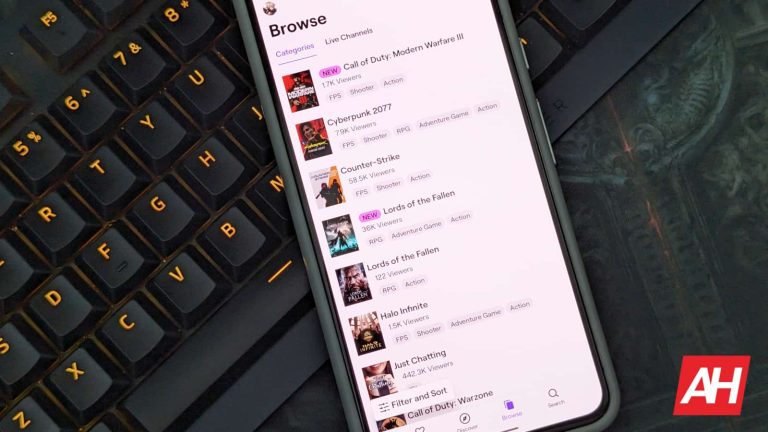
During a Patch Notes Livestream, Jessica Sung (Product Manager at Twitch) introduced the new feed that’s coming to the Twitch mobile app. It will be a scrollable feed where you can switch between livestreams and clips. This will help you find more content on Twitch, and as a streamer, it will help you get discovered by more people.

The new feed will show both livestreams and clips

In the ‘Live’ feed, you will see streams of different streamers that are currently live. This feed will not only show livestreams of streamers you already follow but also of streamers that you might like to watch based on your watch history. This will be helpful, as you won’t have to sit through a pre-roll ad before even knowing if the content is to your liking or not.

New feed of Twitch.

Although you will see some ads in the feed but they will be scrollable. This means you won’t have to pause your viewing because of ads. Additionally, the frequency of these ads will be very low, which will ensure that you have the best viewing experience.

While scrolling through the feed, if you find a stream that you would like to join, you can simply tap on the streamer’s avatar to enter the theater mode, where you can chat and follow the streamer.

You can access the Clips feed when you have a few minutes to spare on the app and want to check out interesting clips from livestreams. This feed will contain clips from both streamers you follow and clips that Twitch thinks you will enjoy watching.

The Clips feed will also indicate if the streamer is currently live, along with few other options, including the ability to like or dislike the clip. You also have the option to share the clip with your friends on different platforms. Additionally, there is a ‘Follow’ button that you can tap to return to that streamer when they are live next time.

Clips feed of Twitch.

The Twitch discovery feed is already accessible to some users as an experimental feature. It will start rolling out to all users later this month, so make sure you have the latest version of the app installed.


[ad_2]
Source link

LeSlipFrancais Data Breach: Customers Information Exposed

0
[ad_1]

LeSlipFrancais, the renowned French underwear brand, has confirmed a data breach impacting its customer base.

The breach, first reported by the online security platform Have I Been Pwned, has compromised the sensitive personal information of thousands of customers.

The breach has reportedly affected over 100,000 customers, making it one of the most significant data breaches in the retail sector this year.

The exact number is still being determined as the company works with cybersecurity experts to assess the full extent of the exposure.

Free Live Webinar for DIFR/SOC Teams: Securing the Top 3 SME Cyber Attack Vectors - Register Here.

Types of Personal Information Exposed

The information accessed by unauthorized parties includes a range of personal data, which is particularly concerning for customers.

The exposed data encompasses:

  • Full names
  • Email addresses
  • Postal addresses
  • Phone numbers
  • Purchase histories

Most alarmingly, it has been reported that encrypted passwords and, in some cases, partial credit card information may also have been compromised.

However, the company assures that the encryption methods used for passwords are robust, reducing the risk of decryption.

Company’s Response

LeSlipFrancais has been swift in its response to the breach.

In a statement released to the public, the company expressed its deep regret over the incident and assured customers that immediate steps were being taken to secure their data and prevent future breaches.

The response plan includes:

  • Immediate activation of a comprehensive security overhaul to identify and rectify the breach’s source.
  • Collaboration with leading cybersecurity experts to enhance existing security measures.
  • Direct communication with affected customers, guiding them to protect their personal information and offer credit monitoring services to those impacted.

Furthermore, LeSlipFrancais has pledged transparency throughout the process and is working closely with law enforcement agencies to investigate the breach.

The company has also established a dedicated hotline and support page for customers seeking assistance or information regarding the breach.

As the investigation continues, LeSlipFrancais faces restoring trust with its customers.

The breach serves as a stark reminder of the ever-present threats in the digital landscape and the importance of robust cybersecurity measures.

Customers are advised to remain vigilant, change their passwords, and monitor their accounts for any unusual activity.

LeSlipFrancais has reiterated its commitment to customer privacy and security, promising to take all necessary steps to protect personal information and prevent future breaches.

In the wake of this incident, the digital community is once again reminded of the critical importance of data security and the need for continuous vigilance in protecting personal information.

Looking to Safeguard Your Company from Advanced Cyber Threats? Deploy TrustNet to Your Radar ASAP


[ad_2]
Source link

Cannabis investment scam JuicyFields ends in 9 arrests

0
[ad_1]

Europol and its associates have arrested 9 people in conjunction with a cannabis investment scam known as “JuicyFields”.

The suspects used social media to lure investors to their website. There they found information about a “golden opportunity” to invest in the cultivation, harvesting and distribution of cannabis plants to be used for medicinal purposes.

JuicyFields website: Grow cannabis. It's profitable! Become a potpreneur and benefit from the booming cannabis industry. Be among the first to join the movement.

Taken from the JuicyFields website:

Grow cannabis. It’s profitable! Become a potpreneur and benefit from the booming cannabis industry. Be among the first to join the movement.

The scheme looked like a crowdsourcing scheme with a minimal investment of € 50, and played on recent discussions in Europe to liberalize cannabis laws following the example of the United States and Canada. Many European countries such as the Netherlands, Austria, Germany, and Portugal have decriminalized possession of cannabis.

As we often see with these kinds of changes in regulatory frameworks, cybercriminals are the first to spot a window of opportunity and advertise with investment opportunities, promising a high return on low-risk investments.

JuicyFields whitepaper: 21 states in the US have already legalised the adult use of marijuana for recreational purposes and this number continues to grow. Indeed, the U.S., Canada, and the soon-to-be regulated markets of the European Union are spearheading this revolution with unprecedented swiftness. However, the pent-up-demand for such regulationdoesn't necessarily translate into effective deployment. As such, there are still many teething problems.

From a JuicyFields whitepaper:

“21 states in the US have already legalised the adult use of marijuana for recreational purposes and this number continues to grow. Indeed, the U.S., Canada, and the soon-to-be regulated markets of the European Union are spearheading this revolution with unprecedented swiftness. However, the pent-up-demand for such regulationdoesn’t necessarily translate into effective deployment.”

To be one of the first investors in this growth market might have seemed just the thing to invest in for some. The scammers promised to connect investors with producers of medical cannabis. Europol stated:

“Upon the purchase of a cannabis plant, the platform assured investors – also referred to as e-growers – they could soon collect high profits from the sale of marijuana to authorized buyers. While the company pledged annual returns of 100 percent or more, they did not reveal exactly how they would accomplish this, let alone be able to guarantee it.”

The scheme was set up as a Ponzi scheme, which means the scammers paid early investors their return with the money they received from later adaptors.

So, for example, the first-time investor would deposit € 50 and receive a pay-out doubling their money soon after. Motivated by such quick financial gains, many investors would raise the stakes and invest hundreds, thousands, or in many cases even tens of thousands of euros. But that doesn’t mean the scammers forget to pocket the largest part themselves.

During the investigation and on action day, law enforcement seized or froze € 4,700,000 in bank accounts, € 1,515,000 in cryptocurrencies, € 106,000 in cash and € 2,600,000 in real estate assets, which amounts to roughly $ 9.5 Million in total. This came from 186,000 people who transferred funds into the scheme between early 2020 to July 2022.

One of the primary targets in this investigation was a Russian national residing in the Dominican Republic, suspected to be one of the main organizers of the fraudulent scheme.

Don’t fall for scams

Stick with safe investments, it’s easier said than done. But there are a few things you might want to avoid:

  • Rushing into an investment. Scammers want you to act urgently, so you spend less time thinking.
  • Skipping the fine print. Not knowing what it says in the fine print can turn out to be catastrophic.
  • Acting on cold calls. Treat calls, texts, mails, and other advice out the blue with extreme caution.
  • Judging a book by its cover. Investment scams are profitable and they can afford to look good.

Still not convinced? I have this piece of land on Venus, that I would be willing to part with for the right price. But you will need to act fast.


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.


[ad_2]
Source link

Several Galaxy S21 users are experiencing the Green Line Issue

0
[ad_1]

At this point, Samsung phones are pretty infamous for a particular display issue, which is rather ironic. Part of what makes Samsung’s phones some of the best you can get on the market is the superior display quality of its devices. However, several people using older Samsung devices, including Galaxy S21 handsets, are experiencing the infamous Green Line issue.

For those who don’t know, this is an issue that affects several Samsung devices. A lot of the time, it’s the company’s higher-end devices like the latest Galaxy S phones, which is quite a bummer. Users would unlock their phone to see a green line stretching from the top to the bottom of the screen. No matter what screen they’re on or what app they use, the line will always be there.

Most folks assume that it’s a software issue, and reply by factory resetting the device. However, it appears that that is not the case and that the screen line issue could be a hardware problem. That makes it substantially harder to fix.

Galaxy S21 users and others are affected by the green line issue

We’ve just gotten two new reports from affected Galaxy S21 users detailing this issue. Both of the users affected were using Galaxy S21 devices. The first person was using a Galaxy S21 FE, and the second was using a Galaxy S21 Ultra. While this has not been confirmed, it’s possible that this issue could be related to software updates.

Both of the reports indicate that the green lines came right after installing an update. If that’s so, this can hopefully be fixed with a future patch.

This is an issue that Samsung has been dealing with for a while, and we’re all wondering when the company will be able to fix it. It’s always a bummer spending hundreds of dollars (sometimes, over $1,000) on a phone just to run into a persistent screen issue on it.


[ad_2]
Source link

Google fires 28 employees after protests against Project Nimbus

0
[ad_1]

Google has fired 28 employees for participating in sit-in protests against the company’s contract with the Israeli government. This came shortly after the police arrested nine workers staging the protests. The arrests were made on trespassing charges as some workers protested in Google Cloud CEO Thomas Kurian’s office.

Google employees arrested for protesting against it

The protests in Google offices began on Tuesday morning. Employees in the company’s New York and Sunnyvale, California offices staged a sit-in protesting its involvement in Project Nimbus, a $1.2 billion cloud contract with the Israeli government. Signed in 2021, the project also involves Amazon and provides cloud computing services to government agencies in Israel.

The protestors wanted Google to pull out of Project Nimbus because of Israel’s war on Gaza. They wore shirts that read “Googler against genocide.” Google initially suspended the protestors, revoked their access to the building, and asked them to leave. After they refused, the company called the police. Five workers from Sunnyvale and four from New York were arrested after about eight hours of protest.

The police also first asked the protestors to exit the building, saying that it would be a non-issue if they obliged. But the Googlers didn’t oblige, leading to the arrests. Videos of the arrests were live-streamed on social media. “Listen, we’ll let you walk out the door right now — it’s a non-issue if you’re willing to go. If not, you’re going to be arrested for trespassing,” a New York City police officer can be heard saying in a video.

Cheyne Anderson, a Google Cloud software engineer arrested by the police, said Google shouldn’t sign deals with governments. “On a personal level, I am opposed to Google taking any military contracts — no matter which government they’re with or what exactly the contract is about,” Anderson told CNBC. “… Google is an international company and no matter which military it’s with, there are always going to be people on the receiving end… represented in Google’s employee base and also our user base.”

Google says Project Nimbus is not related to the Israeli military

Opposition to Project Nimbus isn’t new. There have been several internal protests against this deal since 2021. Workers from Google and Amazon formed a coalition to launch a campaign called No Tech for Apartheid against the project. However, Google says Project Nimbus is not related to the Israeli military. Instead, it offers commercial cloud services to Israeli government ministries. The deal does not involve sensitive or military workloads.

“We have been very clear that the Nimbus contract is for workloads running on our commercial cloud by Israeli government ministries, who agree to comply with our Terms of Service and Acceptable Use Policy,” said Anna Kowalczyk, the external communications manager for Google Cloud. “This work is not directed at highly sensitive, classified, or military workloads relevant to weapons or intelligence services.”

The protestors, meanwhile alleged that Google ignored their demands. “Google has ignored our demands, stifled internal discussion, openly lied, and committed flagrant acts of retaliation against workers merely for speaking up against the company’s military contract with the genocidal and apartheid regime of Israel,” said Mohammad Khatami, a Google software engineer. “Project Nimbus is a major workplace health and safety concern for Googlers.“

Google later fired those employees

While the police released the arrested Google employees after a few hours, the company continued its retaliation. It fired 28 employees who participated in the protests. However, according to Googlers with the No Tech for Apartheid campaign, some of the employees fired by the tech giant weren’t directly involved in the protests. They alleged the firm valued a genocidal government more than its workers.

“This evening, Google indiscriminately fired 28 workers, including those among us who did not directly participate in yesterday’s historic, bicoastal 10-hour sit-in protests. This flagrant act of retaliation is a clear indication that Google values its $1.2 billion contract with the genocidal Israeli government and military more than its own workers—the ones who create real value for executives and shareholders,” they said in a statement to Android Headlines.

Googlers also alleged that the company avoided confronting them and addressing their concerns directly. They accused Google of illegal, retaliatory firings and trying to justify its actions with a lie. The group cited a report from TIME saying that Google has built custom tools for Israel’s military. The company has also allegedly doubled down on contracting with the Israeli Occupational Forces since the onset of the war on Gaza.

“Google is terrified of us. They are terrified of workers coming together and calling for accountability and transparency from our bosses. They are choosing to reveal the falsity of Google’s ‘open culture’ in order to get rid of a threat. The corporation is trying to downplay and discredit our power,” the group said. “These mass, illegal firings will not stop us. On the contrary, they only serve as further fuel for the growth of this movement.”


[ad_2]
Source link

iPhone users in the EU get AltStore PAL, the first third-party app store

0
[ad_1]
Earlier this year, Apple found itself compelled to open up its ecosystem in the European Union, all thanks to the Digital Markets Act (DMA). DMA singled out 6 major tech companies, including Apple, Meta, Microsoft, Amazon, Google, and TikTok’s owner ByteDance, as gatekeepers, mandating changes to how they operate within the EU. For instance, this pushed Apple to permit third-party app stores on its iPhone, and now the first one has become a reality.

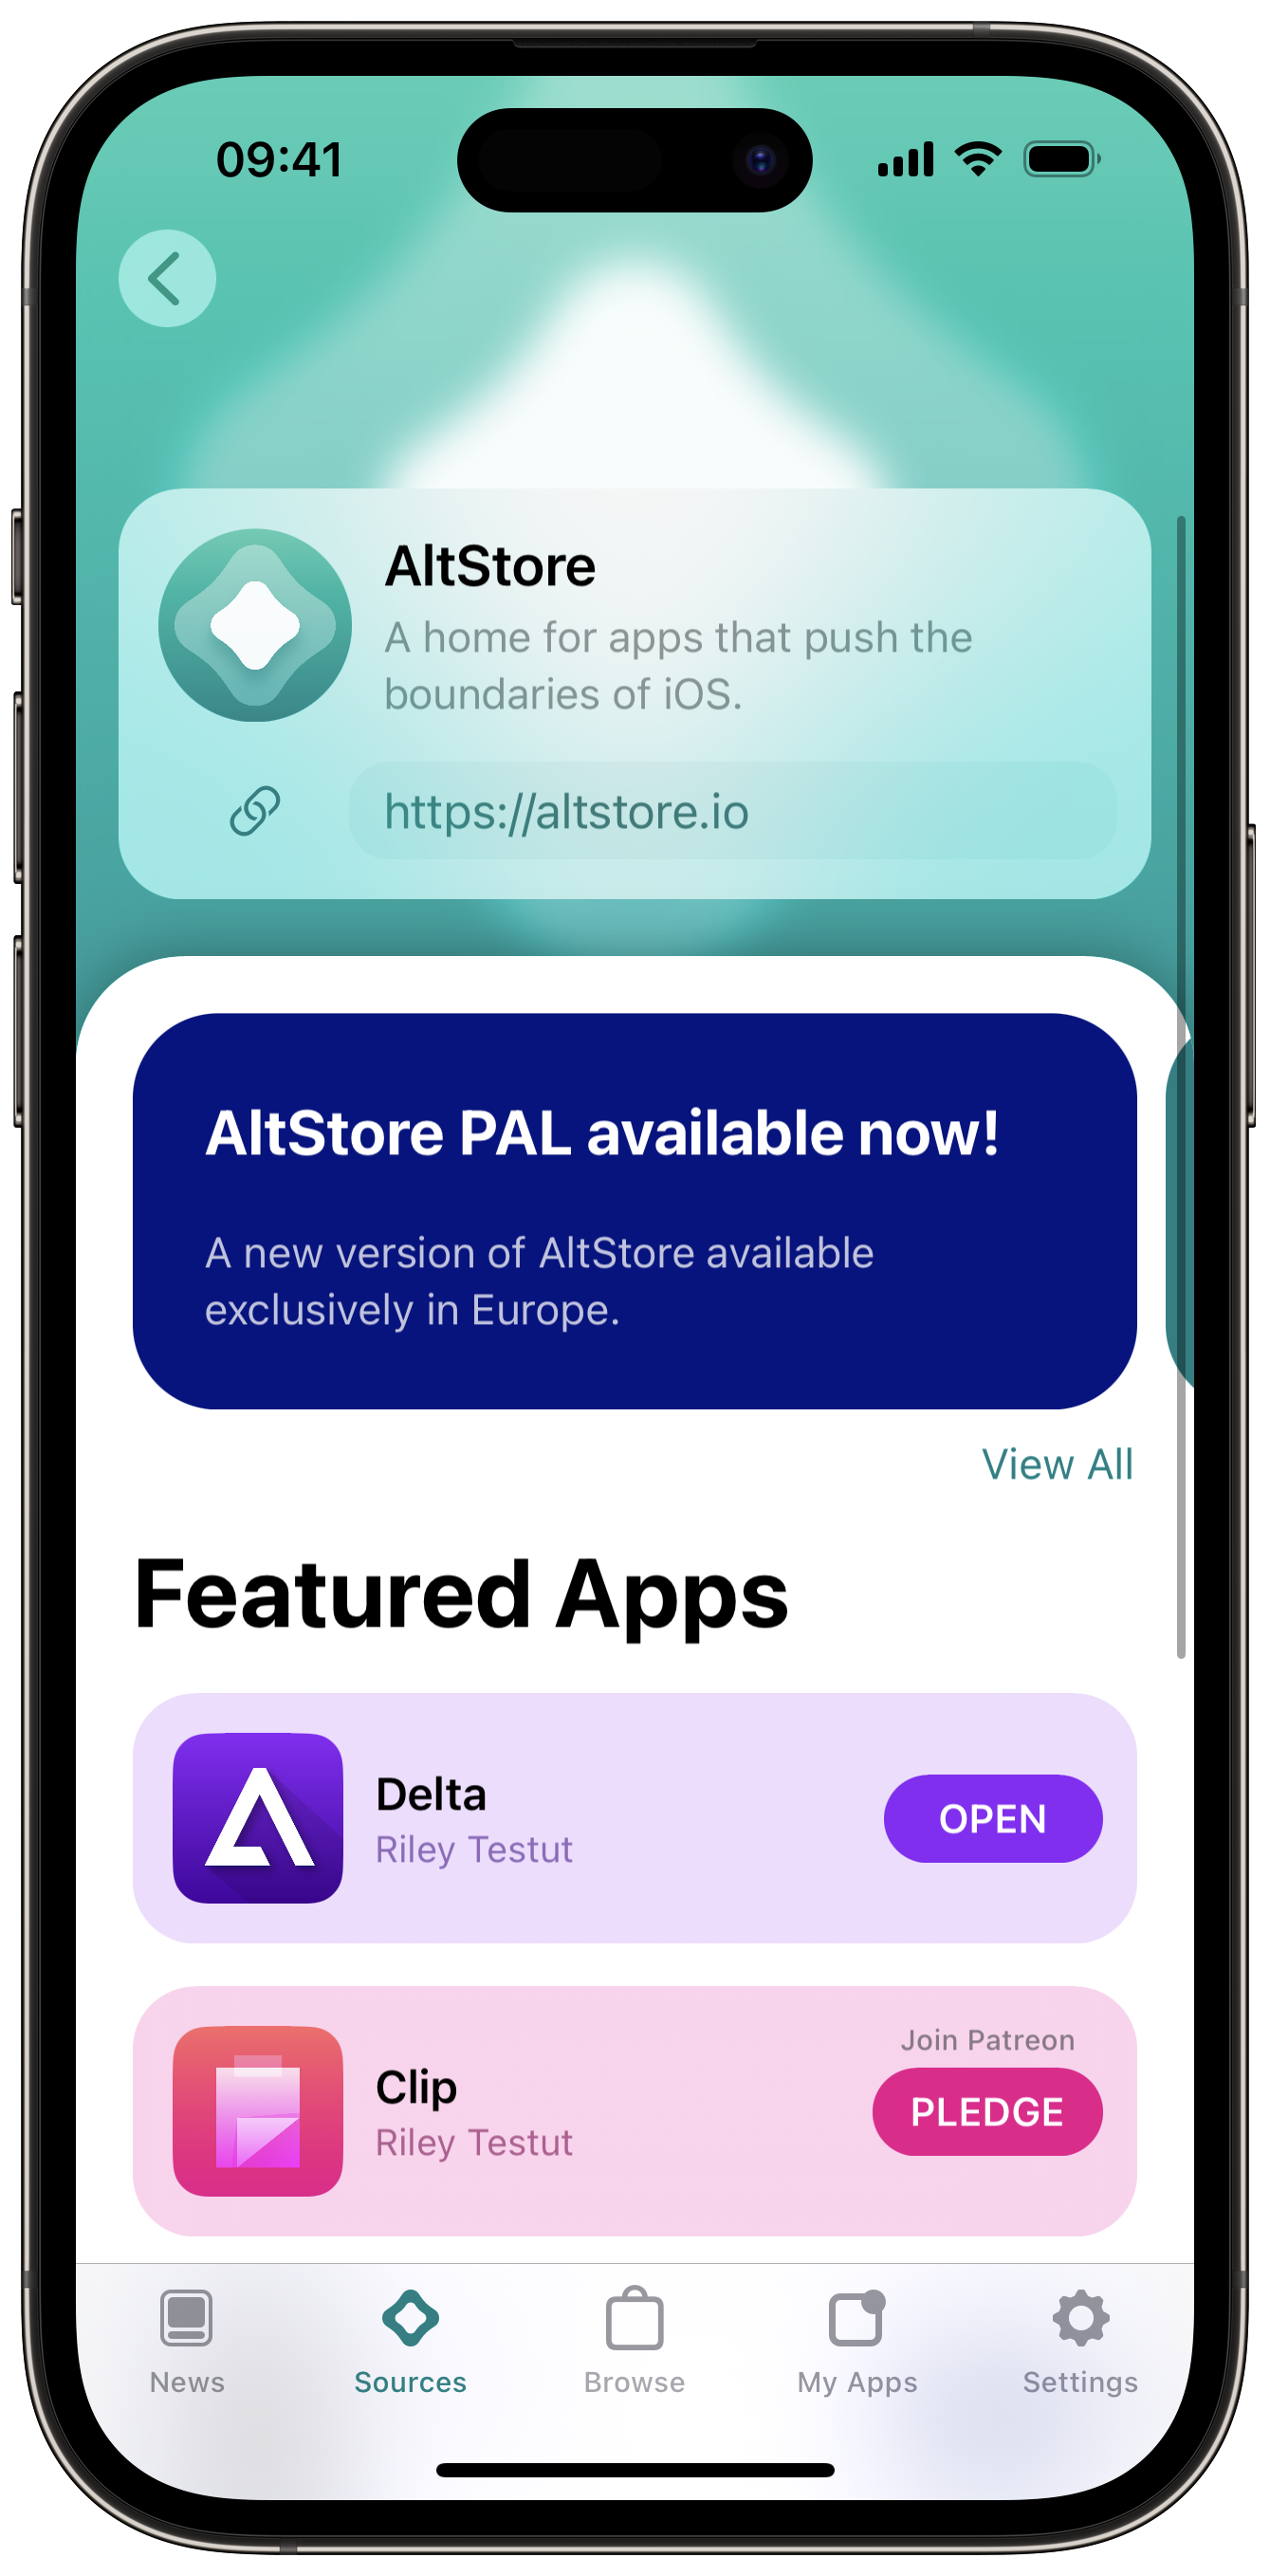
EU iPhone users can now download apps from a new store called AltStore PAL


The third-party iOS app store AltStore PAL is now up and running in the European Union (via The Verge). Users with iOS 17.4 or a later version in the EU can access this alternative app store by paying €1.50 (plus tax) per year. This annual subscription includes coverage for Apple’s Core Technology Fee (CTF), which is required for installing the app marketplace itself.

Installing AltStore PAL involves clicking through multiple warning messages from Apple, making sure you are really, really sure you want to install apps from outside the App Store. But if you keep at it and click enough times, you will eventually get it installed.

Riley Testut, the brains behind AltStore PAL, mentions that the app store is also welcoming submissions from third-party developers. Unlike Apple’s centralized App Store, the idea for AltStore PAL is to have apps self-hosted by developers on their own servers. Users will need to add extra “sources” to the app marketplace to download software created by other developers.


For now, the new app marketplace comes with two apps developed by Testut. The first is Delta, an emulator capable of playing SNES, NES, Game Boy, Game Boy Advance, Nintendo 64, and Nintendo DS games. Interestingly, Delta is also debuting in Apple’s App Store today for users outside of Europe. The other app is Clip, a clipboard manager that Apple has forbidden. Testut shares:


Additionally, AltStore PAL is teaming up with Patreon for monetization, and it is backing developers who want to share beta apps as a thank-you for crowdfunding support, something the App Store doesn’t allow.

AltStore has been a well-known app that has been around since 2019 for iOS, but up until now, getting it installed involved a workaround. Basically, you had to trick the iPhone into thinking you were the app’s developer using a companion piece of software called AltServer, which runs on a Mac or PC.

The original AltStore, which needs a desktop computer and a bit of a hacky setup, is still accessible globally at no cost.


[ad_2]
Source link