Cisco Hypershield: AI-Powered Hyper-Distributed Security

0
[ad_1]

Cisco has unveiled its latest innovation, Cisco Hypershield, marking a milestone in cybersecurity.

This groundbreaking product, described as Cisco’s most consequential security solution, introduces a cloud-native, AI-powered approach to securing highly distributed, AI-scale data centers.

Integrated directly into the network’s fabric, the Cisco Hypershield represents a radical departure from traditional security models, leveraging the power of hyperscaler security and connectivity for the enterprise.

The advent of artificial intelligence (AI) is propelling us into a future of digital abundance, where every individual and organization operates at a machine scale, effectively multiplying our global capacity.

Free Live Webinar for DIFR/SOC Teams: Securing the Top 3 SME Cyber Attack Vectors - Register Here.

This transformation necessitates reimagining our data centers, not just in terms of connectivity and operation but crucially also in terms of security.

Cisco is at the forefront of this evolution, addressing the dual shifts in infrastructure and applications.

With CPUs being complemented by GPUs and DPUs for specialized functions and applications fragmenting into thousands of microservices across various containers and clouds, the complexity of securing these environments has skyrocketed.

Despite billions invested in cybersecurity, the industry continues to grapple with significant challenges.

The sheer scale of modern applications, AI workloads, and devices introduces new vulnerabilities, making tasks like segmentation, patching, and upgrades increasingly tricky.

The introduction of Cisco Hypershield aims to address these challenges head-on, offering a solution that can autonomously adapt to the evolving landscape of digital threats.

Innovations Behind Cisco Hypershield

AI-Powered Security

At its core, Cisco Hypershield is built to leverage AI’s full potential, making it significantly more autonomous than existing security solutions.

This AI-first approach is exemplified in Cisco’s partnership with NVIDIA, focusing on co-creating security-specific AI models and optimizing Cisco Security products for NVIDIA’s technology.

eBPF and Hardware Acceleration

Cisco Hypershield utilizes modern technologies like eBPF and hardware acceleration to provide unparalleled security coverage.

eBPF allows deep visibility into every software process and I/O operation across distributed applications without compromising system integrity.

Meanwhile, hardware acceleration ensures that high-performance security control points can be deployed close to the workloads they protect, enhancing overall security efficacy.

Bringing Security to the Workloads

Cisco Hypershield introduces a novel architecture that distributes thousands of security enforcement points across public and private clouds, bringing security directly to the workloads.

This approach enables a range of innovative use cases, including:

  • Autonomous Segmentation: Leveraging ongoing visibility into network flows and application changes to dynamically define and update granular segmentation rules, protecting against lateral movement.
  • Distributed Exploit Protection: involves identifying high-risk vulnerabilities and deploying compensating controls to block attackers before patches can be applied or vulnerabilities are known.
  • Self-Qualifying Upgrades: Utilizing a shadow data path to test upgrades and policy changes against live traffic, ensuring seamless transitions to the latest versions without downtime.

Cisco Hypershield represents a paradigm shift in how we approach security in the age of AI.

By embedding security into the network’s fabric and harnessing the power of AI, Cisco is not only addressing the current challenges faced by data centers but also paving the way for a more secure, efficient, and resilient digital future.

As organizations continue to navigate the complexities of digital transformation, Cisco Hypershield stands as a beacon of innovation, offering a glimpse into the future of cybersecurity.

Looking to Safeguard Your Company from Advanced Cyber Threats? Deploy TrustNet to Your Radar ASAP


[ad_2]
Source link
Google Arts & Culture gets on board the dark theme train

0
[ad_1]

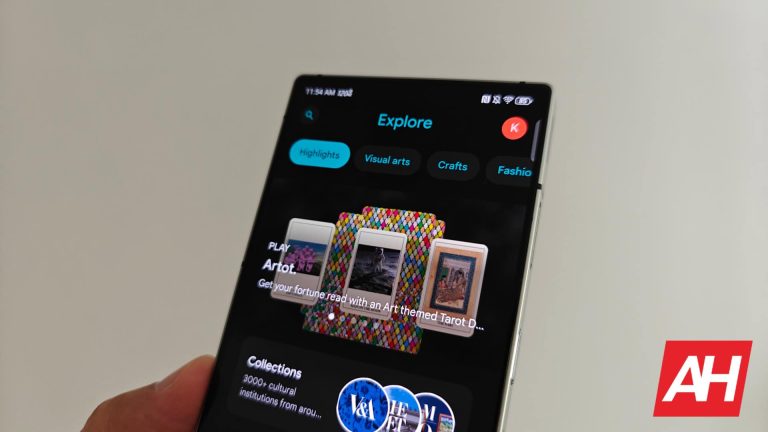
If you’ve ever found yourself squinting at your phone while browsing the world’s art treasures late at night, Google Arts & Culture has just the thing for you with the latest addition of a dark theme. The feature is rolling out to the app with the newest update to v10.9.x on Android and iOS.

It’s not just about the colors, though. Google has put some serious thought into making this dark mode feel polished. Every detail, from the headings and chips to the buttons, has been carefully adjusted to blend seamlessly with the dark theme. It’s the kind of attention to detail that makes all the difference and is a welcome change, especially for those who appreciate consistency. The new look aligns perfectly with the updated ‘&’ logo Google unveiled last year where the four-color icon was replaced by white and placed on a dark background.

Embracing the trend with flexibility

Adding a dark theme to the Google Arts & Culture app isn’t an isolated event. It’s part of a larger trend across the tech giant’s ecosystem. In recent years, more and more Google apps have offered this visual option, recognizing that it not only reduces eye strain but can also conserve battery life. This latest update brings Arts & Culture up to speed, potentially signaling that the stubbornly bright outliers, like Google Opinion Rewards, may soon receive the same treatment.

One of the most exciting aspects of the new dark theme is its flexibility. If you prefer your device settings to dictate the app’s appearance, the “System default” option seamlessly adapts to your preference. However, those who want full control can easily switch between light and dark modes directly within the app’s settings. To get to this setting, open the app, tap on your avatar in the top right corner, Arts & Culture Settings, and tap on “Theme” under Accessibility.

Beyond the surface

The introduction of a dark theme accompanies a larger trend of updates and refinements within the Google Arts & Culture app. Last year, Google initiated a substantial Material Design makeover, streamlining the interface and introducing sleek new elements like a turquoise/blue accented app bar. These changes, paired with the dark theme option, reflect Google’s ongoing commitment to making Arts & Culture a more accessible and delightful way to engage with our human artistic heritage.

Whether you’re a lifelong art lover or just starting to dip your toes into the wider world of artistic expression, the Google Arts & Culture app is a fantastic tool for you. And now with its new dark theme, it’s even easier on the eyes.


[ad_2]
Source link
Strange Android Auto bug prevents WhatsApp messages from being sent (update – fixed)

0
[ad_1]

UPDATE: In a statement to PhoneArena, Google says that the team has identified the cause of the issue. By downloading the latest version of WhatsApp (2.24.8.79) the problem should be fixed. Original story continues below.

##

You’re driving, it’s busy traffic. You receive a text on WhatsApp and Android Auto reads it for you. Your grandma is asking you where her phone is (in our scenario, she doesn’t have a PC, alright). The Assistant says your reply informing her she’s texting you from her phone has been sent. But then, minutes later, she calls you – she never received any text (at least she found her phone…)


Jokes aside, not being able to send a text via Assistant and Android Auto because of a bug is quite an annoying issue, especially when you’re driving and your focus should be on the road. Unfortunately, it seems that’s just what’s happening. An Android Auto update seems to have broken WhatsApp, at least for some people, reports 9to5Google.

Bug affecting WhatsApp and Android Auto


People have shared the issue on Google’s forums and or Reddit. In recent days, it seems like WhatsApp on Android Auto is experiencing issues. Google Assistant still reads the message you receive, but it can’t send a reply or a new message.

What happens is that the Assistant tells you it sends the message, but it’s not sent. To put it bluntly – Google Assistant is lying (well, as close to lying that tech can get). And that’s actually worse than just straight-up not responding, because if you don’t check, you’ll be under the impression you sent a reply. So far, the issue is not happening to all users, but it’s reasonably widespread.

It doesn’t appear to be a particular app version for Andriod Auto that’s bugged, so it’s more likely a server-side change that’s causing it. Google has yet to acknowledge the problem. You can still send the message from your phone, but you shouldn’t be doing that while driving, as it could be unsafe.

[ad_2]
Source link
Kirin 9010 has arrived, and it fuels Huawei’s new flagships

0
[ad_1]

As some of you may already know, Huawei announced the Pura 70 series today. Those are the company’s new flagship smartphones that have launched instead of the P series, which got rebranded. Having said that, Huawei also announced the Kirin 9010 SoC, which fuels two out of four of those phones.

The Kirin 9010 is now official, and it fuels Huawei’s new Pura 70 flagships

The Kirin 9010 fuels the Huawei Pura 70 Pro+ and Pura 70 Ultra. The Huawei Pura 70 and Pura 70 Pro are likely fueled by the Kirin 9000S. Now, the Kirin 9010 is an upgraded version of the Kirin 9000S, but it may not be what you think.

This processor comes with a 12-core CPU cluster, unlike the 8-core setup of the Kirin 9000S. Huawei went for the 2+6+4 configuration here. This chip also supports LPDDR5X RAM.

Now, what we don’t know at the moment is what process Huawei and SMIC used for this chip. If we had to guess, however, we’d say it’s the same 7nm process as for the Kirin 9000S. Huawei is kind of stuck in that regard, at the moment.

The Maleoon 910 GPU is included here, but it’s possible it has more cores than the one in the Kirin 9000S

The same Maleoon 910 GPU is included here, but it’s easily possible it comes with more GPU cores than the one in the Kirin 9000S. The Kirin 9010’s CPU cores are limited to 2,30GHz, while the Kirin 9000S was limited to 2.62GHz. The thing is, this one has more cores, as already mentioned, and it should be faster overall.

That is basically everything we know at the moment. If you were hoping for a 5nm chip, we’ll likely have to wait for the Huawei Mate 70 series. Huawei is strongly rumored to release a 5nm chip later this year, in collaboration with SMIC.

It remains to be seen if the same chip will fuel the Huawei Pura 70 series outside of China. We’re guessing that a global launch is coming, even though we still don’t know when exactly.


[ad_2]
Source link

TikTok trying hard to appeal to US lawmakers with stricter rules for its “For You” page

0
[ad_1]

TikTok is in troubled waters while it’s fighting for its future with US legislators. Now, Engadget reports that the app will be implementing stricter guidelines and penalties for creators who post potentially ‘problematic’ content.

TikTok will make sure it doesn’t recommend “problematic” content and penalize creators


Right now, TikTok is trying to convince US lawmakers and regulators that its app is safe for teens. And just in the midst of that, the company has announced new updates that will take effect in May. TikTok has provided a long list of content that’s not eligible to get recommended on people’s “For You” pages. The list includes some obvious choices but also some content seen as “controversial” like for example weight loss or dieting content, which will fall under the “dangerous activity and challenges” category. Also, clips from users under 16 will also not appear on the “For You” page.

Additionally, a wide range of content that could be misinformation or conspiratorial is also on the list. Examples include unproven recommendations to treat a minor illness, showing a crowd at a music concert and claiming it’s a protest, or misrepresenting authoritative sources such as selectively referencing scientific data to come to a conclusion not made in the study.

On top of that, TikTok will also penalize creators who disregard the new guidelines and will make their entire account ineligible for recommendations. Also, those accounts may become “harder to find” in search.

TikTok is also introducing a feature dubbed “account status” which will help creators check if they’re following the rules. The feature will also show strikes to the account or posts that violate the guidelines. You will also be able to perform an “account check” to see if you’re blocked from recommendations because of breaking the rules.


[ad_2]
Source link

What is Encryption in Malware?

0
[ad_1]

Malware commonly encrypts its traffic (stolen data sent to a command-and-control server) and internal strings (like URLs and configurations) to prevent security systems from recognizing malicious content. 

Cryptography fundamentals, classical ciphers, bitwise operations, XOR functions, and XOR cipher detection and decryption techniques, and showcase a practical example of how to decrypt malware C2 communication encrypted with XOR. 

Common encryption methods:

  • XOR
  • Rc4
  • AES
  • DES
  • 3DES (Tripple DES)

Main concepts in encryption are:

  • Plaintext is the raw data that hasn’t been encrypted and can be read and understood without processing.
  • Ciphertext is the encrypted data that looks like a bunch of random letters or bytes and can’t be read. It’s what the coding process turns into.
  • An encryption algorithm is a set of rules that turns plaintext into ciphertext. Several substitutions and permutations are usually used in plain text.
  • A key is a piece of data, usually a string of letters or numbers, used with an encryption algorithm to secure and decrypt data.

Analyze Encrypted Traffic in ANY.RUN with HTTPS MTIM Proxy - Register for Free

Fundamentals of Encryption:

The encryption algorithm dictates how the data is manipulated, typically through substitutions and permutations, allowing decryption with the correct key. 

There are two encryption methods: symmetric and asymmetric, whereas symmetric encryption utilizes a single key for both encryption and decryption, making it faster and simpler, which necessitates a secure channel for key exchange. 

Asymmetric encryption, also known as public-key cryptography, addresses this by using two mathematically linked keys: a public key for encryption, freely distributable, and a private key for decryption, kept confidential, which allows for more secure key exchange but comes at the cost of increased complexity and slower processing times. 

The breakdown will explore encryption concepts through a Lego-like approach, building towards understanding XOR with simple substitution, where a cleartext message is transformed based on a key. 

Mutating the message at the bit level, introducing bitwise operations, and synthesizing concepts result in a comprehensive understanding of XOR, a fundamental operation in cryptography. 

Simple substitution ciphers replace plaintext characters with alternative symbols according to a key, like swapping letters for emojis, as the concept underlies all encryption. 

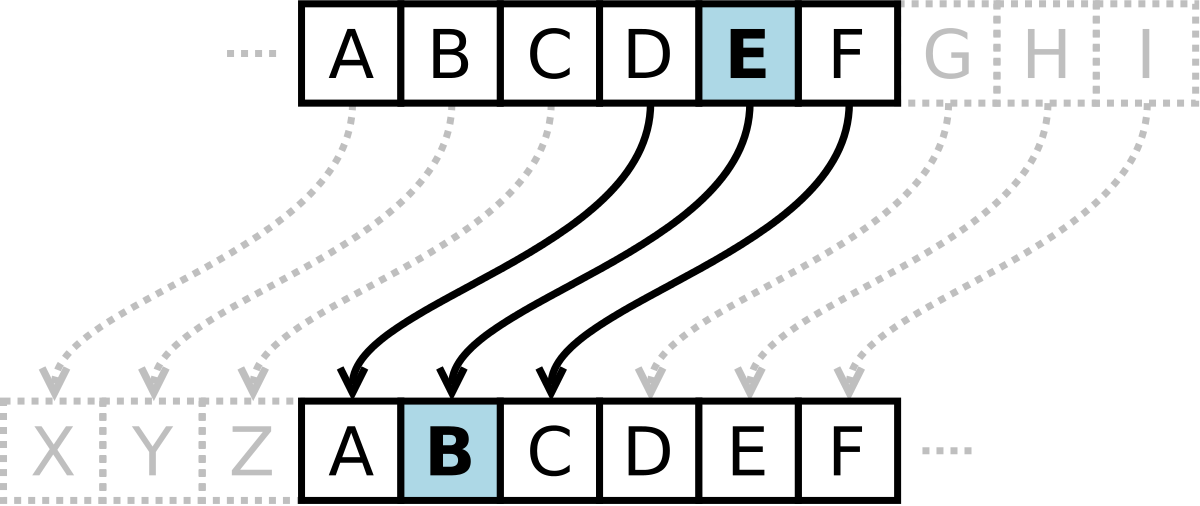
Caesar ciphers, a type of simple substitution, shift plaintext letters by a fixed amount. 

Example of Caesar Cipher

Caesar ciphers are vulnerable due to predictable patterns and unchanged symbol frequencies, where encryption relies on substituting symbols based on a defined rule. 

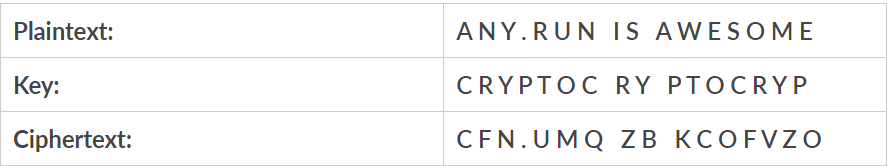
The Vigenère cipher demonstrates the concept of using a key to mutate plaintext for encryption. A keyword generates multiple Caesar ciphers, applying a shift based on the corresponding key letter’s position (A = 0).

Conversion of Plain text into Key, and Ciphertext

Repetition arises when the key is shorter than the message, making the cipher vulnerable. This vulnerability, due to key brevity, is also applicable to modern symmetric encryption methods like XOR. 

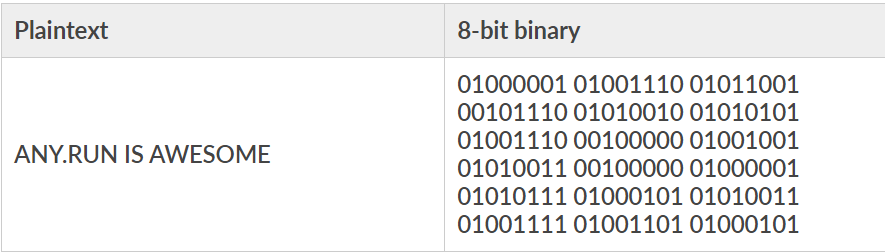
ANY.RUN explored bitwise operations, specifically XOR, for their role in encryption, where XOR operates on individual bits, returning 1 if only one input bit is 1, allowing to combine a message (plaintext) with a key using XOR, resulting in an encrypted ciphertext. 

Conversion of plain text to 8-bit binary

Decryption without the key is computationally impossible because the key controls the bit-wise changes and is thrown away after a single use (one-time pad). This shows how bitwise operations can be used to encrypt data securely.

The XOR cipher encrypts data by performing a bitwise XOR operation between the plaintext and a secret key, where each bit in the plaintext is flipped (0 to 1 or 1 to 0) if the corresponding bit in the key is 1. 

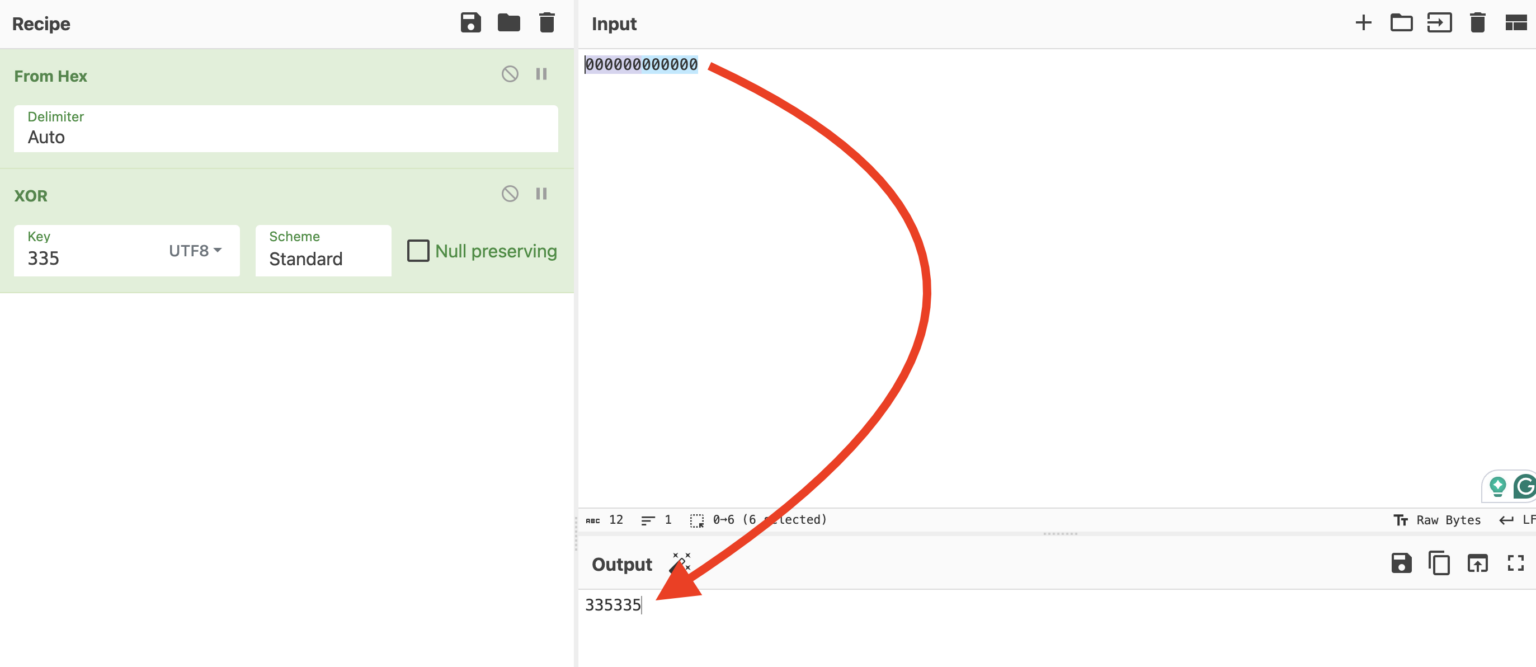
Cyberchef Screenshot

By XORing the ciphertext with the same key once more, decryption is possible. This exposes the cipher’s flaw when using short, repetitive keys. In the hexadecimal representation of the encrypted data, it appears as repeating patterns of zeros, indicating a potential XOR encryption. 

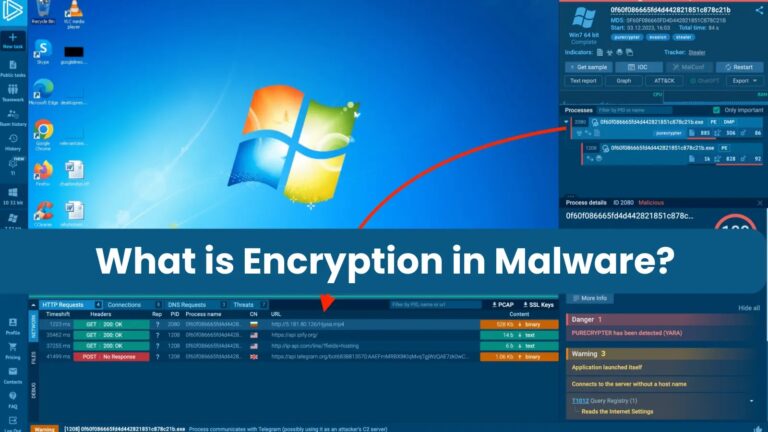
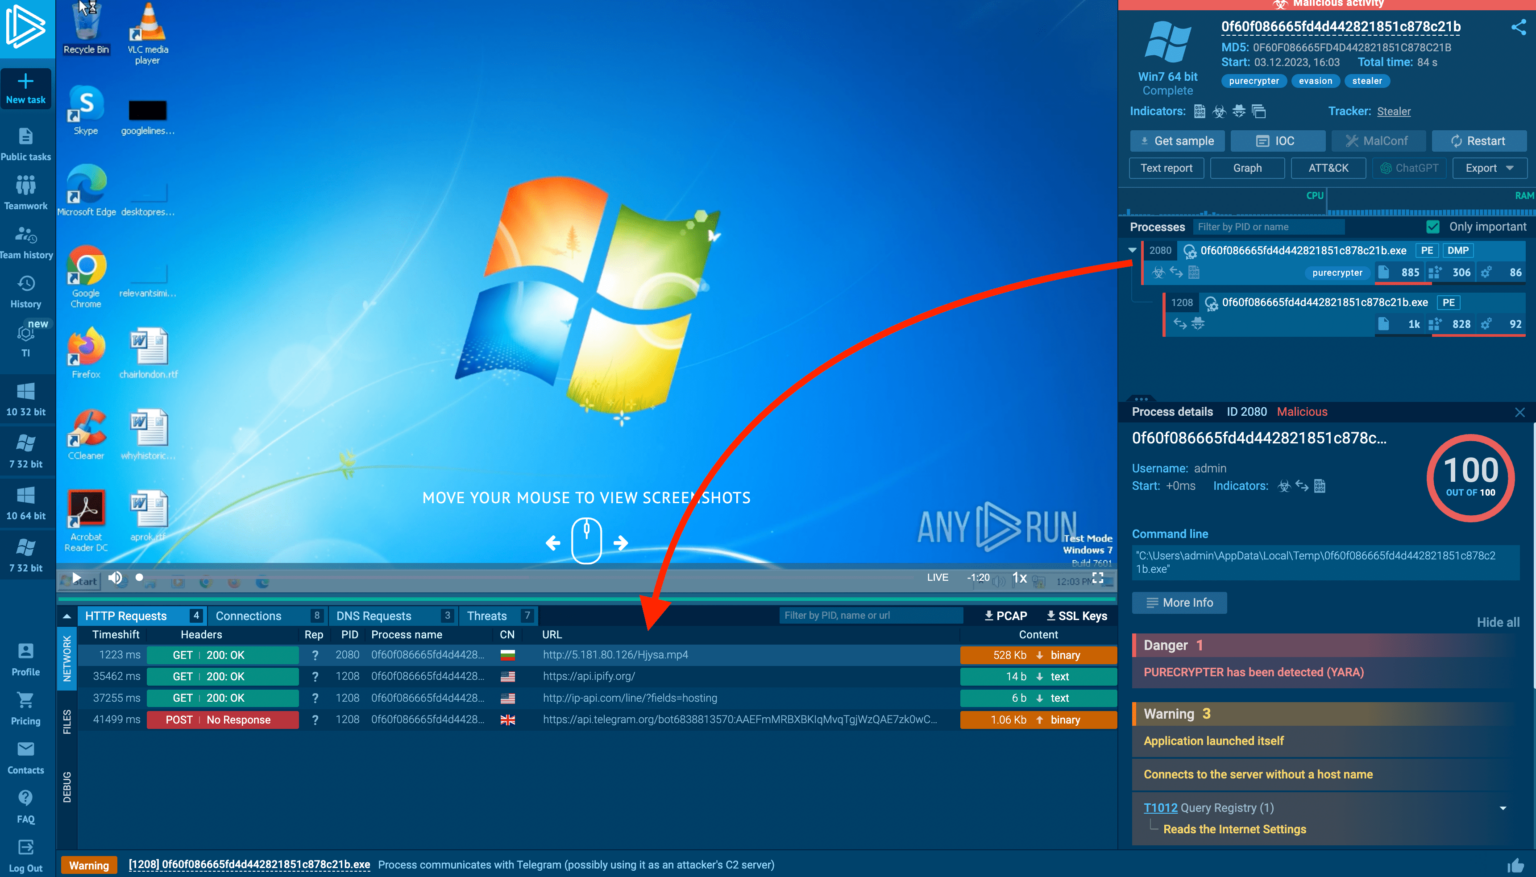
Any.Run Interface

ANY.RUN analysis revealed a process sending a suspicious GET request for a .mp4 file, where the requested content, exhibiting repetitive patterns of 5s and 3s, suggested XOR encryption. While the key likely involved a sequence of 5s and 3s, its exact length remained unknown. 

Downloading the executable from it and examining it in dnSpy could reveal the encryption function and the key itself. Once obtained, the key could decrypt the downloaded file (potentially malware) using tools like CyberChef. 

Quickly analyze malware dynamically and statically in ANY.RUN sandbox  - Register for free

What is ANY.RUN?

ANY.RUN is a cloud-based malware lab that does most of the work for security teams. 400,000 professionals use ANY.RUN platform every day to look into events and speed up threat research on Linux and Windows cloud VMs.

Advantages of ANY.RUN 

  • Real-time Detection: ANY.RUN can find malware and instantly identify many malware families using YARA and Suricata rules within about 40 seconds of posting a file.
  • Interactive Malware Analysis: ANY.RUN differs from many automated options because it lets you connect with the virtual machine from your browser. This live feature helps stop zero-day vulnerabilities and advanced malware that can get past signature-based protection.
  • Value for money: ANY.RUN’s cloud-based nature makes it a cost-effective option for businesses since your DevOps team doesn’t have to do any setup or support work.
  • Best for onboarding new security team members: ANY. RUN’s easy-to-use interface allows even new SOC researchers to quickly learn to examine malware and identify signs of compromise (IOCs).

[ad_2]
Source link

Huawei Pura 70 flagship smartphones are now official

0
[ad_1]

Huawei has finally announced its new flagship smartphones, the Pura 70 series. As some of you may recall, the company announced a rebrand of the ‘Huawei P series’ to the ‘Huawei Pura series’. This happened a couple of days ago.

The Huawei Pura 70 flagship lineup is now official

Well, the four Huawei P70 smartphones that were rumored have now been announced under the ‘Pura’ brand. That happened in China, and the devices are the Huawei Pura 70, Pura 70 Pro, Pura 70 Pro+, and Pura 70 Ultra.

The Huawei Pura 70 Ultra is the most powerful model. It is also the most interesting from a photography standpoint. However, all four devices are quite powerful, and they look very similar.

All four smartphones have flat displays, with a centered display camera hole. The Huawei Pura 70 has the thickest bezels, but even those bezels are very thin. The ones on the higher-end models are uniform, by the way.

The four devices are actually quite similar design-wise

If we flip the phones around, you’ll see that they’re quite similar on the back too. All four smartphones have a rounded edge triangle camera island on the back, in lack of a better word.

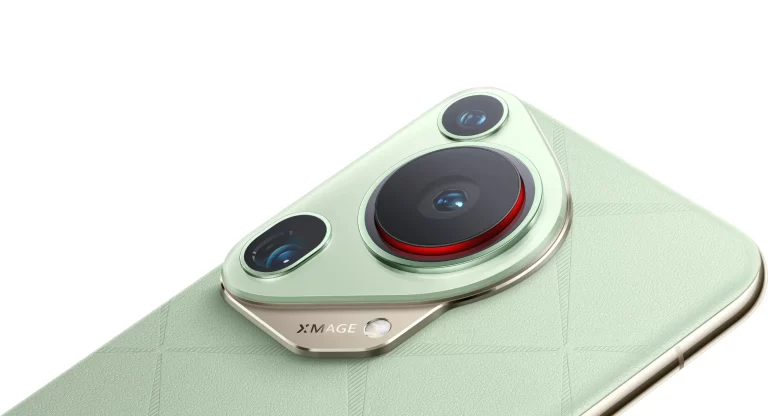
The one on the Huawei Pura 70 Ultra does look a bit different, due to different cameras that are included. On top of that, the XMAGE branding and an LED flash sits outside of the camera island. On all three other phones that branding and LED flash are included in the camera island itself.

The all-new Huawei Kirin 9010 fuels the Huawei Pura 70 Pro+ and Pura 70 Ultra. The other two models are fueled by the Kirin 9000S, it seems. The Kirin 9010 is an upgraded model of the Kirin 9000s.

The Huawei Pura 70 has the smallest display, and even that panel is far from being small

The Huawei Pura 70 has a 6.6-inch display, while all other models include 6.8-inch displays. The entry-level model has a resolution of 2760 x 1256, while all other models offer 2844 x 1260 displays. All those models support LTPO panels with adaptive refresh rates (1-120Hz). High-frequency PWM dimming (1440Hz) is also included. The displays are protected by second-gen Kunlun glass, by the way.

The Huawei Pura 70 and Pura 70 Pro offer 12GB of RAM, while the other two models ship with 16GB of RAM. Different storage options are available depending on the model, but all of them go up to 1TB.

The Huawei Pura 70 has a 4,900mAh battery. The Huawei Pura 70 Pro and Pura 70 Pro+ include a 5,050mAh unit. The ‘Ultra’ model has a 5,200mAh battery on the inside.

All four smartphones support really fast charging, both wired & wireless

When it comes to charging, the Huawei Pura 70 Pro, Pura 70 Pro+, and Pura 70 Ultra support up to 100W wired, 80W wireless, and 20W reverse wireless charging. The Huawei Pura 70, however, supports 66W wired, 50W wireless, and 7.5W reverse wireless charging.

Now, in terms of cameras, things are quite interesting. The Huawei Pura 70 is the least powerful phone in that regard, but all four devices offer variable aperture on the main camera. So, even though it’s the least powerful, its camera setup still looks great.

In any case, the Huawei Pura 70 Pro and Pura 70 Pro+ have the same camera setups. The Huawei Pura 70 Ultra sits at the very top of the food chain, no matter the way you slice it. Let’s start with the Huawei Pura 70.

That phone includes a 50-megapixel main camera with an f/1.4-f/4.0 aperture and OIS. A 13-megapixel ultrawide unit (f/2.2 aperture) is also included, as is a 12-megapixel periscope telephoto camera (f/3.4 aperture, OIS, 5x optical zoom, 50x digital zoom).

The Huawei Pura 70 Pro and Pura 70 Pro+ include a 50-megapixel main camera (f/1.4-f/4.0 aperture, OIS), along with a 12.5-megapixel ultrawide camera (f/2.2 aperture), and a 48-megapixel macro telephoto camera (f/2.1 aperture, OIS, 3.5x optical zoom, 100x digital zoom).

The Huawei Pura 70 Ultra camera setup looks truly powerful on paper

The top-end Huawei Pura 70 Ultra is the absolute camera king here. It has a 50-megapixel main camera (1-inch sensor, f/1.6-f/4.0 aperture, sensor-shift anti-shake). A 40-megapixel ultrawide camera (f/2.2 aperture) is also included, as is a 50-megapixel macro telephoto camera (f/2.1 aperture, OIS, 3.5x optical zoom, 100x digital zoom. Focal lengths: 22.5mm, 13mm, 90mm).

The Huawei Pura 70 Ultra comes in Green, Brown, White, and Black colors. Machine translation says that the colors are called Chanson Green, Mocha Brown, Starburst White, and Starburst Black, respectively. You can check them out below. Do note that vegan leather seems to be included on all these models.

Huawei Pura 70 Ultra colors

The Huawei Pura 70 comes in dark pink, light blue, white, and black colors. The Huawei Pura 70 Pro got announced in purple, white, and black colors. And finally, the Huawei Pura 70 Pro+ comes in silver, white, and black colors. You can check out all those colors across the three images below. There seems to be glass included on the back of all these variants.

All four phones are IP68 certified and ship with HarmonyOS 4.2

All four phones are IP68 certified, and all four include in-display fingerprint scanners. It’s also worth saying that HarmonyOS 4.2 comes pre-installed on all of these smartphones.

We don’t have price tags for all models, but we do know that the Huawei Pura 70 Pro+ starts at CNY7,999 ($1,105), while the ‘Ultra’ model starts at CNY9,999 ($1,380).


[ad_2]
Source link

Google working on integrating Google Keep reminders with Tasks

0
[ad_1]

The world is busy, we’re all busy, and for many people in today’s day and age, it seems time flies before you’re able to accomplish everything. Partially that’s because some people forget all the tasks they have for the day. Tech can, of course, help with that, and thus we have Google Tasks for reminders and Google Keep for note-taking.However, it can be annoying to have all your info scattered across different apps. That’s what Google seems to be working to remedy now, according to Android Headlines. It seems Google is working on making Google Tasks able to create reminders for you in Google Keep, and reminders in Google Keep to be accessible in Tasks.

Google Tasks and Google Keep reminders could be available in one place


Currently, Tasks saves and syncs your reminders from other company services and lets you set reminders. On the other hand, Google Keep is a note-taking app, but it also allows you to set reminders. However, reminders created in Google Keep don’t sync to Tasks. And hopefully, that’s to change soon.
The folks over at 9to5Google have dug into the APK code with the latest Google Tasks update and discovered something very useful. It seems that Google is working on integrating Keep reminders with Tasks. Yep, this means reminders created in Keep will be synced to Tasks, and you’ll be able to access all your reminders in one place. A quality of life update, honestly.
Apparently, you’d also be able to open the note with a reminder directly from Tasks.

However, for now, these are just hidden strings in the code that suggest that feature, and it’s not clear when it will be officially released. You may have to wait for a few months as the feature appears to be in early development.


[ad_2]
Source link

Phishing-as-a-Service Platform LabHost Seized by Authorities

0
[ad_1]

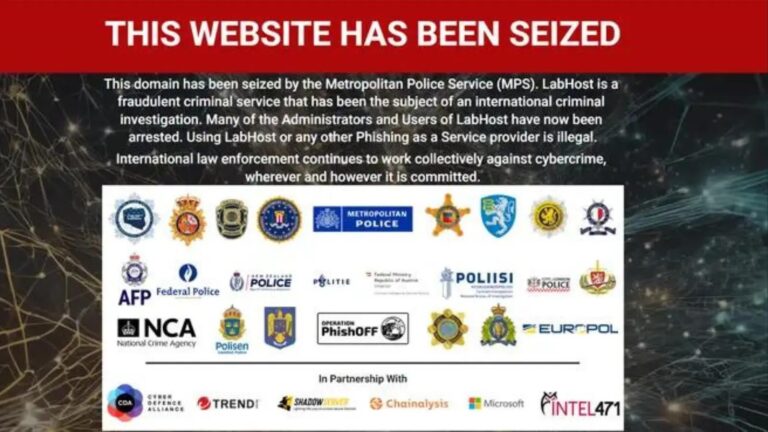
Authorities have dismantled LabHost, a notorious cybercrime platform that facilitated widespread phishing attacks across the globe.

The crackdown on LabHost, which was founded in the UK in 2021, marks a significant victory against cybercriminal networks that have long exploited digital platforms to conduct their illicit activities.

LabHost, known for its Phishing-as-a-Service (PhaaS) offerings, allowed criminals, even those with limited IT skills, to create and manage phishing websites designed to mimic legitimate organizations such as banks, healthcare agencies, and postal services.

For a monthly fee of up to £300, subscribers were provided with phishing kits, tutorials, and tools necessary to deceive victims into handing over sensitive information, including bank card details, PIN numbers, and passwords.

Free Live Webinarfor DIFR/SOC Teams: Securing the Top 3 SME Cyber Attack Vectors - Register Here.

Take Down Operation

The operation led to the arrest of dozens of individuals, and LabHost’s fraudulent sites were seized.

Authorities have revealed that the platform was instrumental in tricking nearly half a million people into divulging their bank card details and PIN numbers.

Additionally, LabHost’s activities resulted in the theft of 1.2 million unique usernames and passwords, highlighting the extensive reach and impact of its operations[1][7].

LabHost’s subscription model included various tiers, targeting financial institutions primarily in North America, with a notable increase in phishing attacks against Canadian banks.

Following a disruptive outage in October 2023, the platform’s resurgence in activity underscored the persistent threat posed by such cybercrime services[2].

The international investigation into LabHost’s activities involved collaboration between law enforcement agencies and private sector partners, demonstrating a unified approach to combating online fraud.

The Metropolitan Police Service, the National Economic Crime Centre, and other international partners played a crucial role in infiltrating and disrupting the platform.

The seizure of LabHost has sent a strong message to online fraudsters, challenging the notion that they can operate with impunity behind digital identities.

Authorities have emphasized their commitment to dismantling international fraud networks, leveraging global collaboration to target cybercriminals at their source.

As the investigation continues, up to 25,000 UK-based victims have been contacted to inform them of the data breach, with efforts underway to identify and support additional victims worldwide.

The operation against LabHost underscores the ongoing challenges in the fight against cybercrime and highlights the effectiveness of international cooperation in protecting digital spaces from exploitation.

Looking to Safeguard Your Company from Advanced Cyber Threats? Deploy TrustNet to Your Radar ASAP.


[ad_2]
Source link

Google Maps will provide detailed directions to EV charging stations and more info for drivers

0
[ad_1]
Google Maps is the navigation app that the majority of people prefer. And it’s frequently getting new features and updates to be even more enticing. Now, Google has published a new blog post about a new feature coming: detailed directions for EV drivers about charging stations.

Google Maps will show directions to EV charging stations

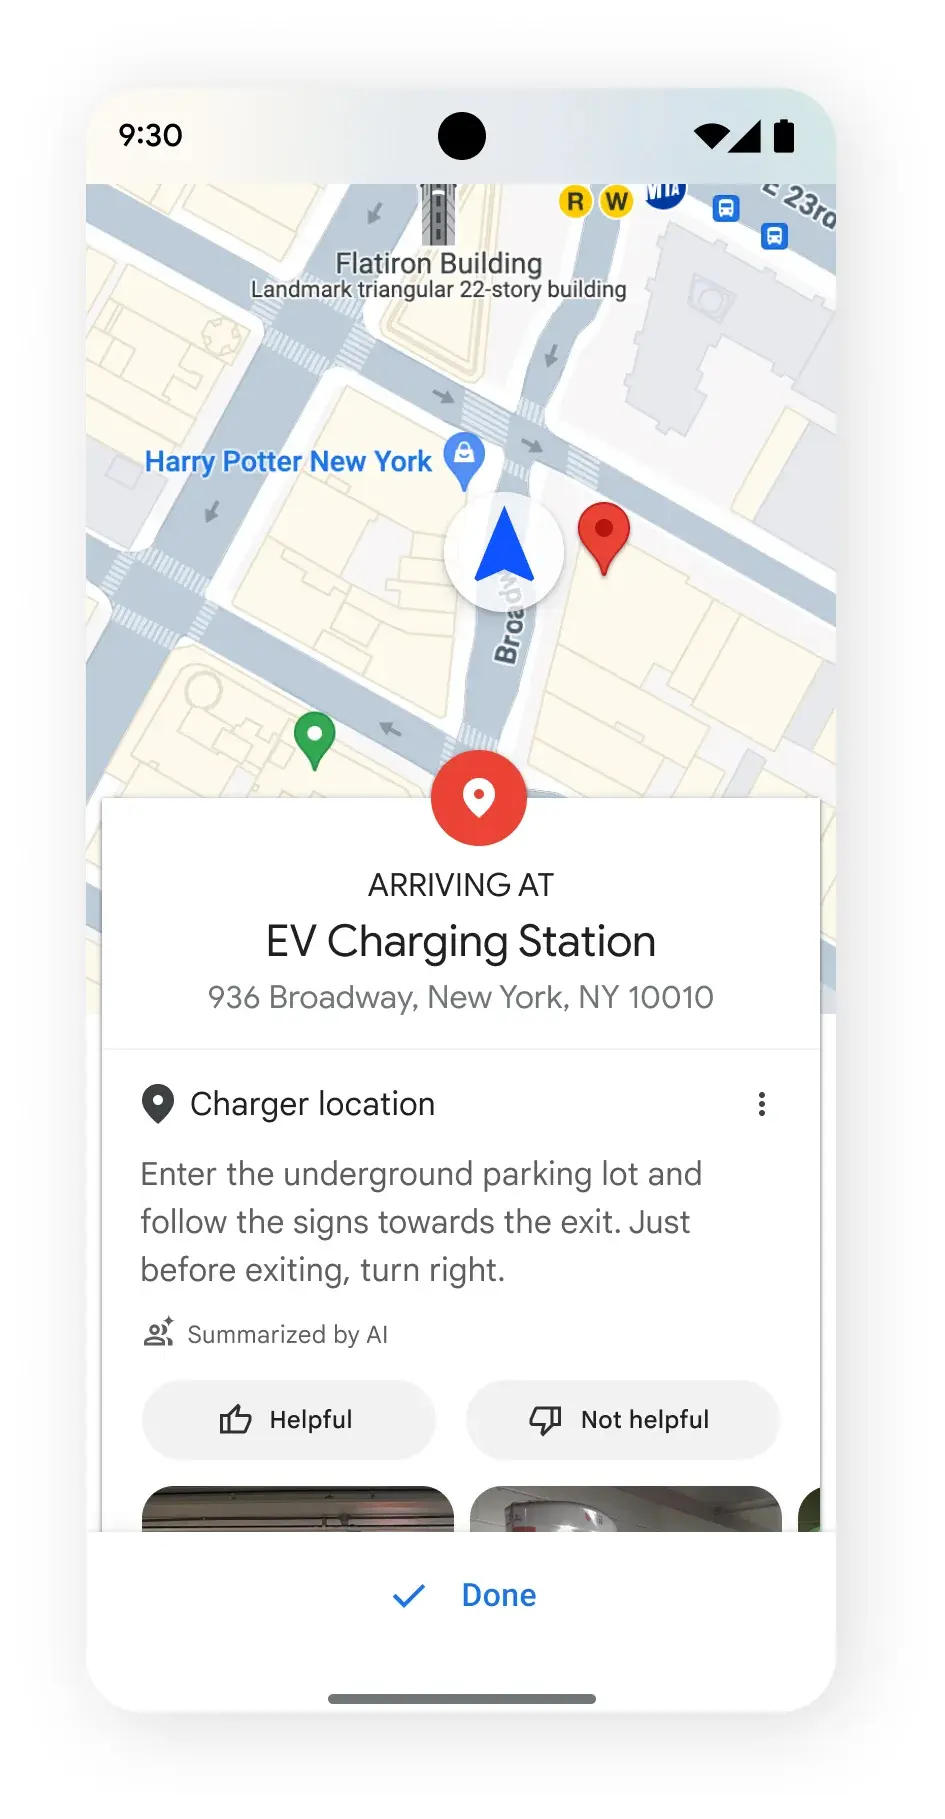
Google is looking into ways to make Maps more enhanced for EV (Electric Vehicle) support. Several new and exciting features should be available in the coming months. You will be getting more details about EV charging stations, including AI-generated descriptions of where to find a charger at a particular building.

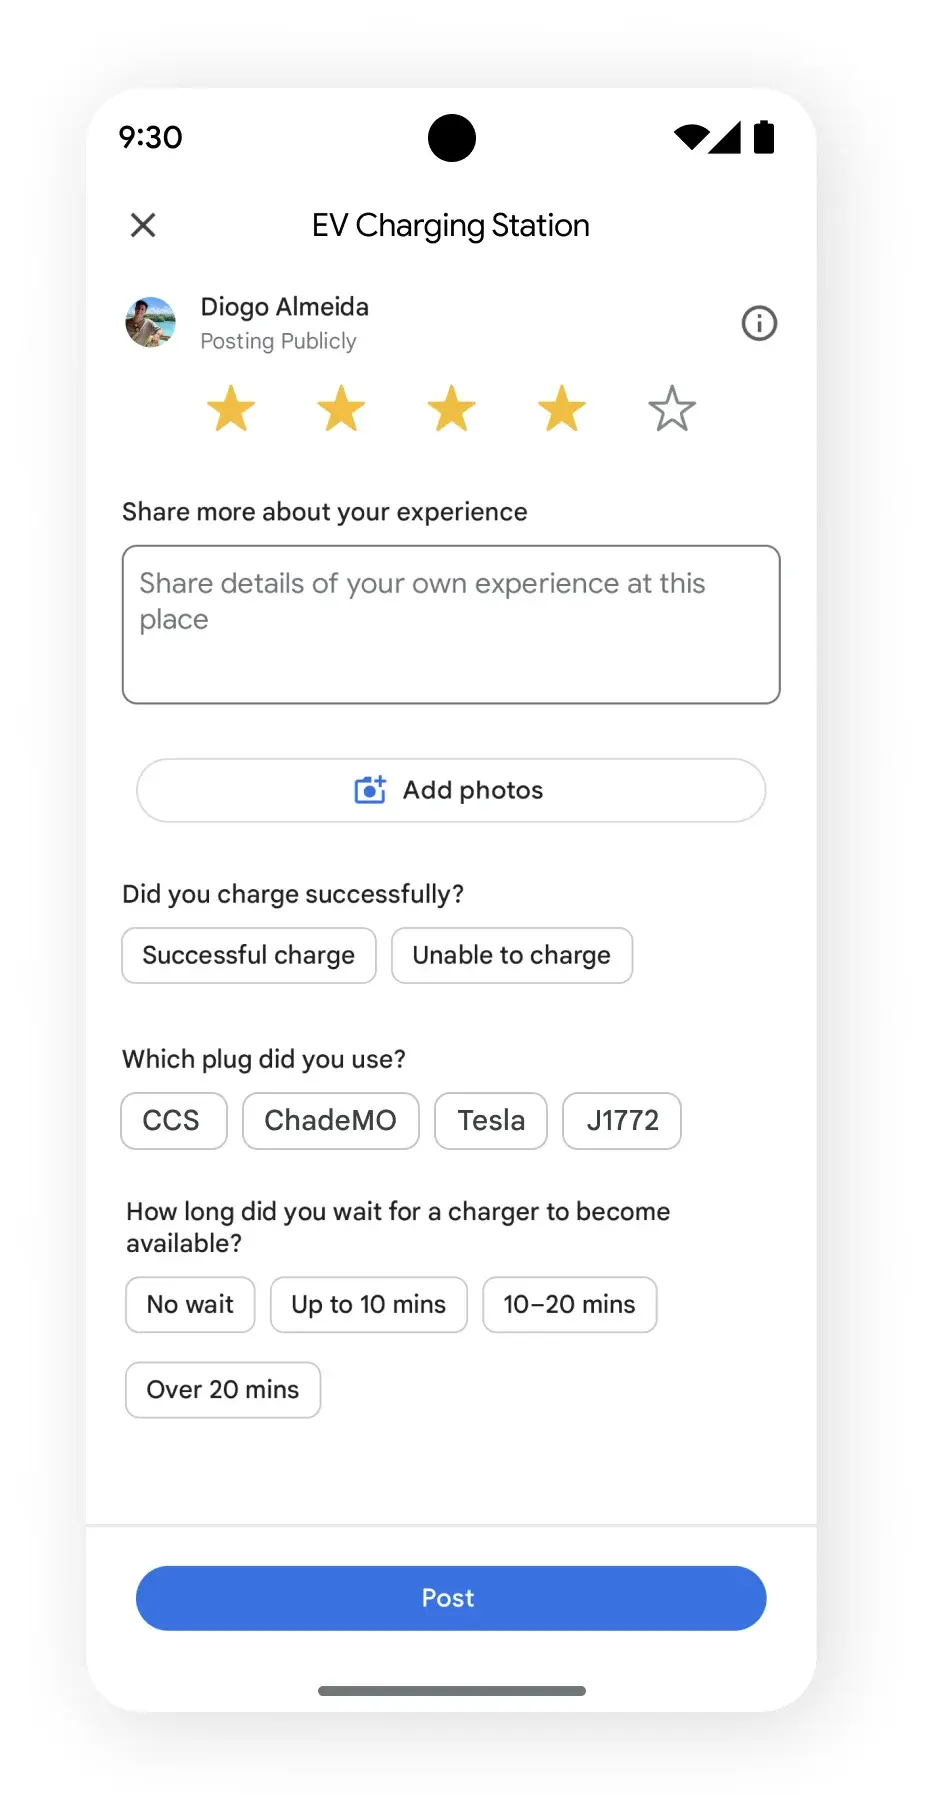
Also, Google is now prompting users to add more details to their reviews such as wait times and the sort of connector used in an EV charging station. And yep, connector types are important as not all stations support all types of EV charging connectors. Users will also be able to add photos, star ratings, and text comments, just like with any business listed in Maps.


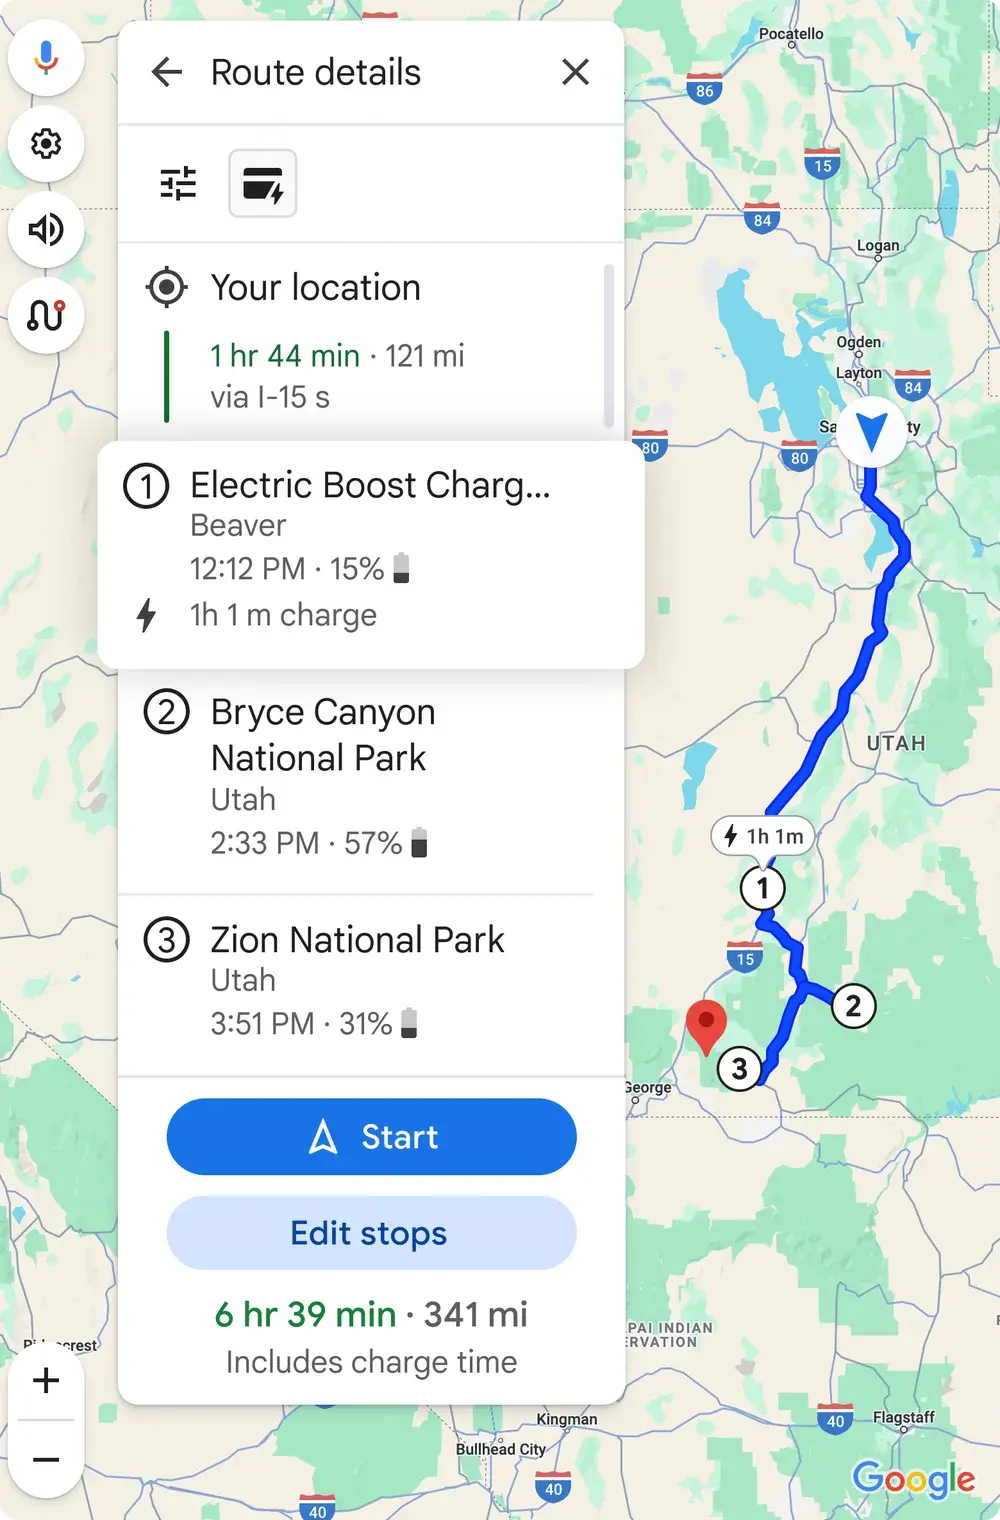
So basically, when you’re using Maps for navigation, you should be able to see nearby chargers on the map in the car. The info showcased should also include charging speeds and whether or not ports are available.

For now, though, the feature is limited to vehicles with Google software built-in. It is unclear when the feature will make it to Android Auto or the standalone Maps app. Also, so far, speed is rated with basic terms like “fast” or “very fast”, instead of by connector type.

A feature that will remain exclusive to Google-based vehicles is enhanced trip planning. This will allow Maps to recommend EV stations along the way based on the current battery level of your car. Also, it will provide a re-calculated ETA based on the time it should take to charge your car.


These changes are expected to roll out globally, and most likely they will first make their way to the U.S. However, there’s no concrete timeline just yet for when these features will become available.

[ad_2]
Source link