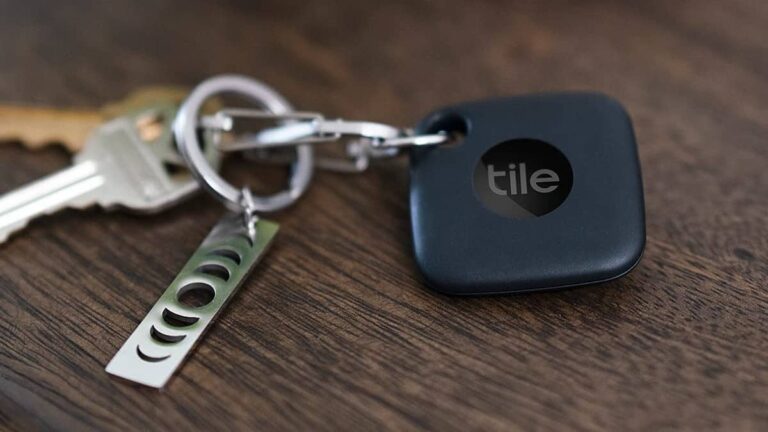
Tile may not launch Find My Device network-supported trackers

0
[ad_1]

A couple of days ago, Google finally launched the much-awaited Find My Device feature. The feature was first showcased at last year’s Google I/O event but has started rolling out just now. Soon after the launch, a variety of brands announced that they would launch their compatible trackers to support the new service. However, one notable company was missing from the list – Tile.

At the I/O event, Google announced that Tile will be one of the brands to release a compatible tracker. However, a new report suggests that Tile will not be releasing Find My Device network-supported compatible tracers, at least for now.

Tile is currently not working on a Google Find My Device network-compatible tracker

According to the source, a Tile spokesperson has revealed that the brand is not working on a compatible tracker. The company is focusing on building a “cross-platform solution that enables location-based finding of people, pets, and things”. One of the typical examples of this is the integration of Tile’s technology into Life360 map, which has over 66 million members.

So, if you are a Tile user, then don’t expect it to announce a Find My Device network-supported tracker any time soon. However, the company did mention that “we have a great working relationship with Google and look forward to future partnerships”. We will keep you updated if there’s any announcement, so stay in touch for more details.

Here are all the trackers that will work with Google’s Find My Device network

While announcing the rollout of the Find My Device network, Google posted a complete list of all devices that will support it. Chipolo’s One Point and One Card will be amongst the first to support the network. The Pebblebee Clip, Pebblebee Card, and Pebblebee Tag are also on the list. In addition, the Eufy Smart Track Link, Smart Tag Card for Android, and JioTag Go will have support in the future.

Some of the existing audio products will also support the Find My Device network. These include the JBL Tour Pro 2, Tour One M2, and the Sony WH-1000XM5. Google will also soon add support for the Pixel Buds Pro. We expect more tiny trackers and audio products to join the list in the near future.

Google’s Find My Device app is currently available for Android users in the US and Canada. However, a global launch isn’t too far. Users in these regions can install the app on their devices to locate compatible Android phones, tablets, and more. The technology relies on a crowdsourced network of over a billion devices to help users locate lost gadgets more reliably.

Tile Statement on Google Find My Device


[ad_2]
Source link

Ransomware Actors Stolen User’s Information

0
[ad_1]

Group Health Cooperative of South Central Wisconsin (GHC-SCW) has announced a significant breach in their cybersecurity, leading to unauthorized access and theft of personal information by ransomware actors.

This incident has raised alarms about the security measures to protect sensitive health information and the increasing arrogance of cybercriminals targeting healthcare institutions.

In the early hours of January 25, 2024, GHC-SCW’s vigilant IT Department detected unauthorized access within their network.

Swift action was taken to isolate and secure the network, which temporarily made several systems unavailable.

Although the attackers attempted to encrypt GHC-SCW’s system, they were frustrated.

The healthcare provider promptly reported the incident to the Federal Bureau of Investigation (FBI) and engaged external cyber incident response experts to assist in restoring and securing their network and systems.

Document
Stop Advanced Phishing Attack With AI

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Stopping 99% of phishing attacks missed by other email security solutions. .

Discovery of Data Theft

The investigation into the breach took a grim turn on February 9, 2024, when evidence emerged that the attackers had managed to exfiltrate data, including protected health information (PHI).

The stolen PHI encompassed a range of sensitive details such as names, addresses, telephone numbers, email addresses, dates of birth and death, social security numbers, member numbers, and Medicare and Medicaid numbers.

The breach was confirmed when a foreign ransomware gang contacted GHC-SCW, claiming responsibility for the attack and data theft.

GHC-SCW has taken the breach seriously, working closely with the FBI and the U.S. Cybersecurity and Infrastructure Security Agency (CISA) to mitigate potential harm.

Affected individuals and all necessary state and federal agencies and certain consumer reporting agencies have been informed of the breach.

GHC-SCW has strengthened its security measures across all systems and networks to prevent future incidents.

These enhancements include strengthening existing controls, improving data backup procedures, and intensifying user training and awareness programs.

Assurance to Affected Individuals

Despite the alarming nature of the breach, GHC-SCW has assured that there is no indication that the stolen information has been used or further disclosed.

The healthcare provider is taking comprehensive steps to mitigate any potential harm resulting from this incident and is committed to maintaining the privacy and security of the information in its possession.

The GHC-SCW hack serves as a stark reminder of the vulnerabilities within the healthcare sector and the importance of robust cybersecurity measures.

As cybercriminals become increasingly sophisticated, healthcare providers must remain vigilant and proactive in protecting sensitive health information.

GHC-SCW’s response to the incident demonstrates a commitment to security and the well-being of its members.

Still, it underscores the ongoing challenges in safeguarding personal information in the digital age.

Secure your emails in a heartbeat! To find your ideal email security vendor, Take a Free 30-Second Assessment.


[ad_2]
Source link

Google expands trade-in program to Pixel Tablet purchases

0
[ad_1]

You can now trade in your old tablet when purchasing the Pixel Tablet through the Google Store in the US. The company recently started accepting trade-ins against its tablet. The program was previously limited to Pixel phones and watches.

Google now accepts trade-ins for the Pixel Tablet

The Pixel Tablet debuted in May 2023, with sales beginning the next month. The first-gen Google tablet arrived with a starting price of $499. The company didn’t accept trade-ins against the device, making you pay the full amount or avail of other offers. However, that is no longer the case. As spotted by 9to5Google, trade-ins are now available when purchasing the tablet.

According to an email blast seen by the publication, this offer launched on April 4. The official product page for the Pixel Tablet on the Google Store now has a “Trade-in your device” section where you can get an estimated value for your old tablet depending on its condition. You will also find details about the trade-in policy, including the terms and conditions, on the same page.

Google currently only accepts Apple and Samsung tablets. Apple products fetch a maximum of $450, while Samsung Galaxy tablets will go for up to $350. The maximum value is available for the latest flagship offerings. The base amount is $250 for both groups of tablets. Google will evaluate the final amount depending on the device’s make, model, and condition.

Once you select your old device, the company asks you whether it is in good condition. You can select yes if it “turns on, is free of cracks, and the screen works properly.” Google will physically inspect the device before deciding the final value. If it is less than what you see on the website, you can either accept the new value or reject the trade-in to get back your tablet.

The top values are only available for a limited time

The Pixel Tablet has yet to see any permanent drop in price since its launch. Almost a year later, it still starts at $499. If you plan to trade in your old tablet and grab the Google device for less, you might want to hurry up. The top values are reportedly valid only till this Saturday, April 13. Google will refund the final trade-in value for your device directly into the credit card used when purchasing the Pixel Tablet on the Google Store. If you return the Google tablet, you will get an equivalent amount of Store Credit.


[ad_2]
Source link

New Walmart Pro Google TV streaming device could launch soon

0
[ad_1]

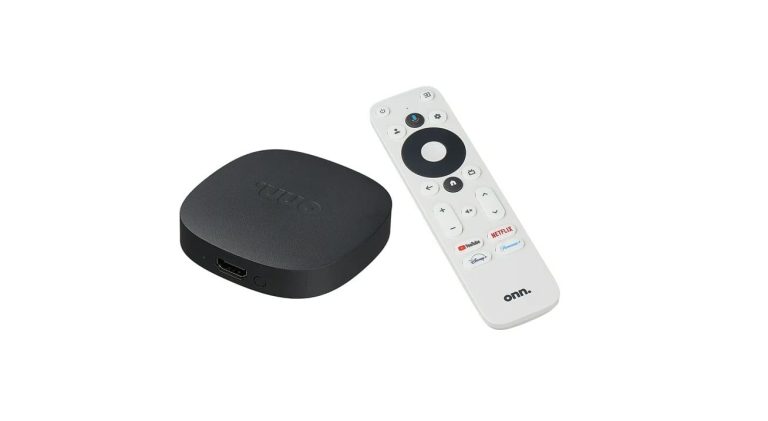
Walmart has been offering a couple of cheaper alternatives to the Google Chromecast for a while now. The company offers two Google TV streaming devices under its “onn.” brand. These include the onn. Google TV 4K Streaming box and onn. Google TV Full HD Streaming Device. Now, onn. appears to be planning to release a 4K Pro model of these streaming products.

Walmart Pro Google TV streaming box will offer Bluetooth 5.2 connectivity

The upcoming Walmart Pro Google TV streaming device has been certified by the regulatory body Bluetooth SIG. The product name of the device is mentioned as “onn. 4K Pro Streaming Device | Google TV” in the certification data. The listing has also revealed that it will be offering a faster Bluetooth 5.2 connectivity feature.

The current onn. Google TV 4K Streaming box offers the previous-gen Bluetooth 5.0 connectivity. The certification doesn’t reveal anything about the design details or features of the upcoming streaming box. However, the Pro moniker in the product name clearing indicates it will be more capable compared to existing devices. The Bluetooth certification details of this product were published on April 9.

Walmart Pro Google TV could offer more RAM, storage, and ports

Unfortunately, not many details about the features of the upcoming Pro Google TV model are available at the moment. However, the users can expect more RAM, higher storage, and additional connection ports. It will also provide features like the Google Chromecast. It should have built-in Google Assistant, content recommendations, and popular streaming apps.

The Walmart Pro Google TV variant should also come bundled with a dedicated remote control, just like the previous models. The company currently offers a white remote control, which provides dedicated keys to YouTube, Netflix, and Disney+ OTT platforms. The new Pro variant could have dedicated buttons for other OTT services as well. Only time will tell if the new offering is worth the money.

As for the pricing, the onn. Google TV 4K Streaming Box (2023) model is currently retailing for around $20. So it is safe to assume that the upcoming Pro variant will also be priced affordably.

Walmart Pro Google TV device


[ad_2]
Source link

149 Security Vulnerabilities & Zero-days

0
[ad_1]

On April Patch Tuesday, Microsoft fixed 149 bugs—one of the biggest security update releases in the company’s history. 

Many of its software products, such as Microsoft Office and its SQL Server database package, have fixed vulnerabilities.

The majority of vulnerabilities are in the Windows operating system, and nine CVEs were found in the Azure cloud platform.

Three of the 149 issues are classified as Critical, 142 as Important, three as Moderate, and one as Low in severity.

The update also addresses a vulnerability tracked as CVE-2024-26234, which is currently being exploited.

Details Of The Flaw Exploited In The Wild

CVE-2024-26234 – Proxy Driver Spoofing Vulnerability

Proxy driver spoofing vulnerability is tracked as CVE-2024-26234 and has a CVSS rating 6.7.

An attacker would require high privileges to take over the system, exploit the vulnerability, and spoof the proxy driver.

Document
Stop Advanced Phishing Attack With AI

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Stopping 99% of phishing attacks missed by other email security solutions. .

Microsoft fixed this zero-day vulnerability that impacted Windows desktop and server operating systems and was made public.

Administrators should promptly install the Windows cumulative update on their systems to prevent a security compromise, as this vulnerability is actively exploited in the wild.

Critical Flaws Addressed

CVE-2024-21322 – Microsoft Defender For IoT Remote Code Execution Vulnerability

This vulnerability, which has a CVSS base score of 7.2, is classified as critical for Improper Neutralization of Special Elements used in a Command (‘Command Injection’)

“Successful exploitation of this vulnerability requires the attacker to be an administrator of the web application. As is best practice, regular validation and audits of administrative groups should be conducted”, Microsoft said.

CVE-2024-21323 – Microsoft Defender For IoT Remote Code Execution Vulnerability

Microsoft Defender for IoT Remote Code Execution Vulnerability has a base CVSS score of 8.8.

For the IoT sensor to successfully exploit this issue, the attacker must be able to deliver a malicious update package over the network to the Defender.

The attacker first needs to establish their identity and obtain the required authorization to start the update procedure. 

“Successfully exploiting this path traversal vulnerability would require an attacker to send a tar file to the Defender for IoT sensor.”

Microsoft said that after the extraction process, the attacker could send unsigned update packages and overwrite any file they chose.

CVE-2024-29053 – Microsoft Defender For IoT Remote Code Execution Vulnerability

This is also a critical Microsoft Defender for IoT,  Remote Code Execution Vulnerability, with a CVSS base score of 8.8. 

Any authorized attacker can exploit this vulnerability. Admin or other advanced rights are not needed.

“An authenticated attacker with access to the file upload feature could exploit this path traversal vulnerability by uploading malicious files to sensitive locations on the server,” Microsoft.

Azure Vulnerabilities Addressed

  • CVE-2024-29993 – Azure
  • CVE-2024-29063 – Azure AI Search
  • CVE-2024-28917- Azure Arc
  • CVE-2024-21424 – Azure Compute Gallery
  • CVE-2024-26193 – Azure Migrate
  • CVE-2024-29989 – Azure Monitor
  • CVE-2024-20685- Azure Private 5G Core
  • CVE-2024-29990 – Microsoft Azure Kubernetes Service

Additionally, 41 SQL Server fixes have been released, all of which address issues related to remote code execution.

In addition to the vulnerabilities addressed in this month’s Patch Tuesday release, Microsoft has republished six CVEs.

It is recommended that users upgrade the impacted products to prevent threat actors from exploiting these vulnerabilities.

Secure your emails in a heartbeat! To find your ideal email security vendor, Take a Free 30-Second Assessment.


[ad_2]
Source link

New ransomware group demands Change Healthcare ransom

0
[ad_1]

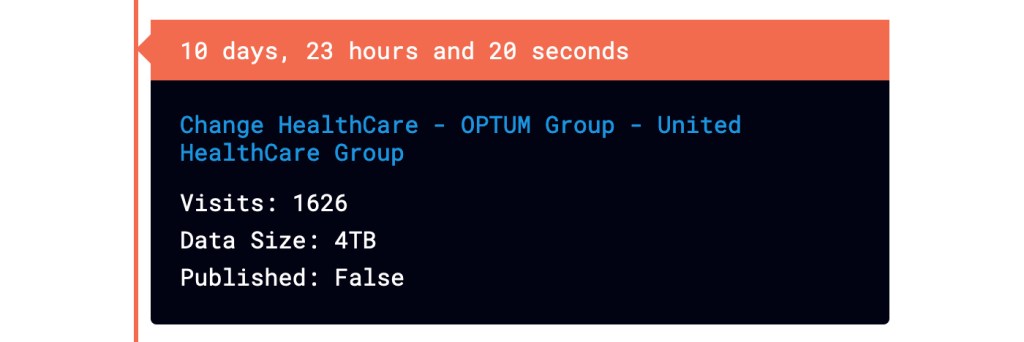
The Change Healthcare ransomware attack has taken a third cruel twist. A new ransomware group, RansomHub, has listed the organisation as a victim on its dark web leak site, saying it has 4 TB of “highly selective data,” which relates to “all Change Health clients that have sensitive data being processed by the company.”

The announcement follows a series of events that require some unpacking.

Change Healthcare is one of the largest healthcare technology companies in the USA, responsible for the flow of payments between payers, providers, and patients. It was attacked on Wednesday February 21, 2024, by a criminal “affiliate” working with the ALPHV ransomware group, which led to huge disruptions in healthcare payments. Patients were left facing enormous pharmacy bills, small medical providers teetered on the edge of insolvency, and the government scrambled to keep the money flowing and the lights on.

American Hospital Association (AHA) President and CEO Rick Pollack described the attack as “the most significant and consequential incident of its kind against the US health care system in history.”

The notorious ALPHV ransomware group claimed responsibility, chalking up Change Healthcare as one of a raft of healthcare victims in what looked like a deliberate campaign against the sector at the start of 2024.

ALPHV used the ransomware-as-a-service (RaaS) business model, selling the software and infrastructure used to carry out ransomware attacks to criminal gangs known as affiliates, in return for a share of the ransoms they extorted.

On March 3, a user on the RAMP dark web forum claimed they were the affiliate behind the attack, and that ALPHV had stolen the entirety of a $22 million ransom paid by Change Healthcare. Shortly after, the ALPHV group disappeared in an unconvincing exit scam designed to make it look as if the group’s website had been seized by the FBI.

ALPHV’s exit left Change Healthcare with nothing to show for its $22 million payment, a disgruntled affiliate looking for a ransom, and very possibly two different criminal gangs—ALPHV and its affiliate—in possession of a huge trove of stolen data.

Now, a month later, a newcomer ransomware group, RansomHub has listed Change Healthcare as a victim on its website.

Change Healthcare is listed as a victim on the RansomHub dark web leak site

While some have speculated that Change Healthcare has suffered a second attack, the RansomHub site itself makes the connection to the events surrounding February 21 quite clear:

As an introduction we will give everyone a fast update on what happened previously and on the current situation.

ALPHV stole the ransom payment (22 Million USD) that Change Healthcare and United Health payed in order to restore their systems and prevent the data leak.

HOWEVER we have the data and not ALPHV.

RansomHub first appeared in late February and its arrival dovetails neatly with ALPHV’s disappearance in very early March, leading some to think they are the same group under two different names.

The statement also pours water on the idea that RansomHub is a rebrand of the ALPHV group with its suggestion that “we have the data and not ALPHV.” However, any public statement like this has to be tempered by the fact that ransomware groups are prolific liars.

It’s not uncommon for affiliates to work with multiple RaaS providers, so the most likely explanation is that having lost its money to ALPHV, the affiliate that ransacked Change Healthcare has paired up with a different ransomware group.

Whatever the reason, there is no comfort in it for Change Healthcare. Having apparently already paid a ransom thirty times greater than the average demand, it now has to decide whether it’s going to pay out again.

For everyone else, it’s a lesson in how devastating ransomware can be, and how badly things can go even when you pay a ransom.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; and disable or harden remote access like RDP and VPNs.
  • Prevent intrusions. Stop threats early before they can even infiltrate or infect your endpoints. Use endpoint security software that can prevent exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like ThreatDown EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Our business solutions remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.


[ad_2]
Source link

RUBYCARP the SSH Brute Botnet Resurfaces With New Tools

0
[ad_1]

The cybersecurity community is again on high alert as the notorious botnet group RUBYCARP, known for its SSH brute force attacks, has resurfaced with new tools and tactics.

The Sysdig Threat Research Team (Sysdig TRT) has been closely monitoring the activities of this Romanian threat actor group, which has been active for over a decade and has recently uncovered significant developments in its operations.

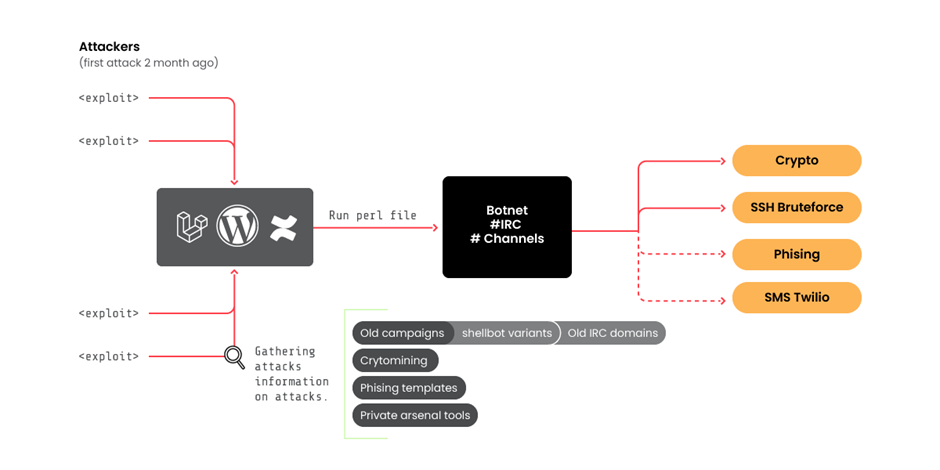
At the heart of RUBYCARP’s resurgence is exploiting a critical vulnerability in Laravel applications, CVE-2021-3129.

This vulnerability has been a focal point for the group’s targeting and exploitation efforts, allowing them to gain unauthorized access to systems and expand their botnet.

In addition to exploiting CVE-2021-3129, RUBYCARP has been using SSH brute force attacks to enter target networks.

Document
Stop Advanced Phishing Attack With AI

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Stopping 99% of phishing attacks missed by other email security solutions. .

The group’s persistence and evolution of tactics underscore the importance of patching known vulnerabilities and strengthening SSH security measures to thwart such attacks.

The latest findings from Sysdig TRT indicate that RUBYCARP has not only continued its traditional brute force and exploitation activities but also added new techniques to its repertoire.

The group now utilizes a backdoor based on the popular Perl Shellbot, connecting victim servers to an IRC server that acts as command and control, thereby joining the more giant botnet.

RUBYCARP continues to add new exploitation techniques to its arsenal to build its botnets

RUBYCARP’s toolset has expanded, with the discovery of 39 Perl file (shellbot) variants, although only eight were previously detected by VirusTotal.

The group’s communication strategies have also evolved. They use public and private IRC networks to manage their botnets and coordinate crypto-mining campaigns.

The group has been actively involved in crypto mining operations, using its pools hosted on the exact domains as their IRC servers.

This strategy allows them to evade detection from IP-based blocklists and utilize standard and random ports for further stealth.

Diversified Cryptocurrency Mining

The group has not limited itself to a single cryptocurrency; instead, it engages in mining operations for Monero, Ethereum, and Ravencoin.

The Ravencoin wallet associated with RUBYCARP has been particularly active, with over $22,800 received in transactions.

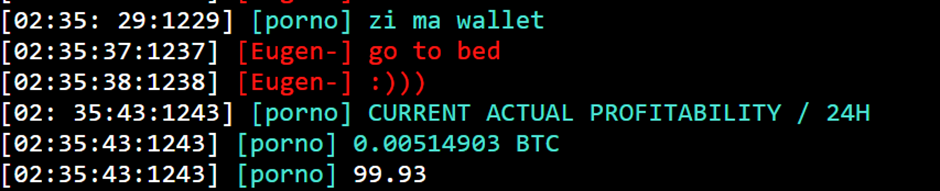
user “porno” claimed to have gained 0.00514903 BTC, around USD 360, within 24 hours

Beyond crypto mining, RUBYCARP has been executing sophisticated phishing operations to steal financially valuable assets, such as credit card numbers.

Evidence suggests that the group uses these stolen assets to fund its infrastructure and possibly for resale.

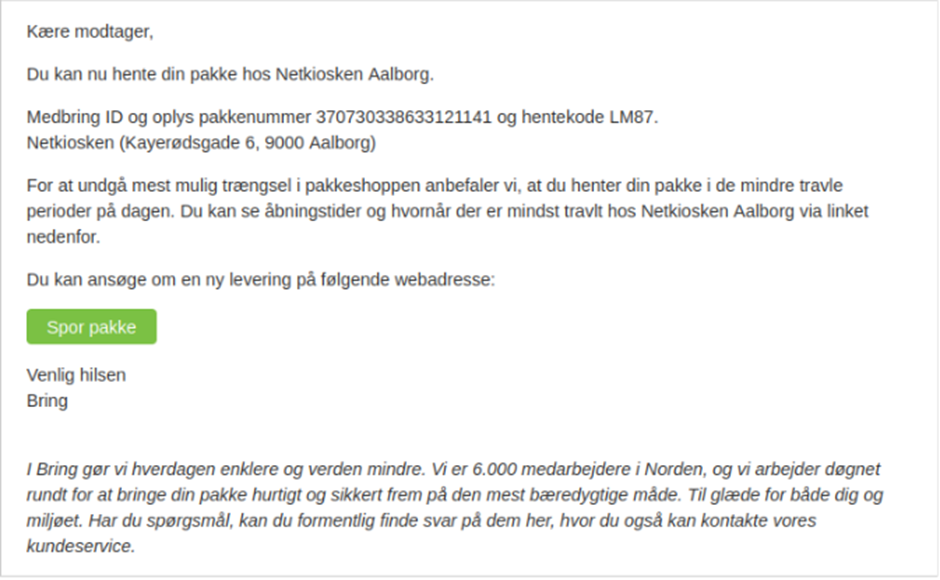
Phishing templates impersonating legitimate European companies, such as the Danish logistics company “Bring,” have been identified in RUBYCARP’s attacks.

Identified a phishing template (letter.html) targeting Danish users and impersonating the Danish logistics company “Bring.”

The group targets European entities, including banks and logistics companies, to collect payment information.

The resurgence of RUBYCARP with new tools and techniques is a stark reminder of the persistent threat posed by sophisticated cybercriminal groups.

Defending against such actors requires a proactive approach to vulnerability management, robust security postures, and advanced runtime threat detection capabilities.

As the cybersecurity community continues to grapple with the challenges posed by groups like RUBYCARP, organizations must remain vigilant and prepared to respond to the evolving threat landscape.

For more information on RUBYCARP and to stay updated on the latest cybersecurity threats, follow our dedicated news coverage and expert analysis. Stay safe and informed in the digital age.

Secure your emails in a heartbeat! To find your ideal email security vendor, Take a Free 30-Second Assessment.


[ad_2]
Source link

Moto g04s is Motorola’s new extremely affordable smartphone

0
[ad_1]

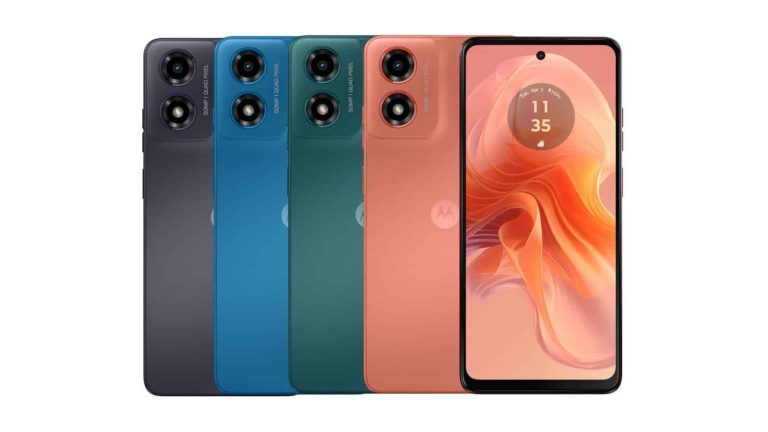
Motorola has announced a new smartphone, the Moto g04s. This is the company’s new budget smartphone. As you can see in the provided images, the device has a flat display and a centered display camera hole.

You’ll also notice that its bottom bezel is considerably thicker than the rest of them. All the physical buttons sit on the right-hand side, while the phone has a single camera on the back. There are two cutouts, but the bottom one is reserved for an LED flash. Motorola’s logo also sits on the back.

The Motorola Moto g04s is the company’s new budget offering

The device is fueled by the Unisoc T606 processor. It offers 4GB or 6GB of LPDDR4X RAM, and 64GB of UFS 2.2 flash storage. Do note that the storage is expandable up to 1TB via a microSD card.

A 5,000mAh battery sits inside the phone, while 15W wired charging is supported. The phone has a 6.6-inch HD+ (1612 x 720) IPS display with a 90Hz refresh rate. The maximum brightness it can reach is 537 nits. The Panda glass protects this panel.

Android 14 comes pre-installed on the phone, with My UX skin on top of it. There is an audio jack included on the phone, while Dolby Atmos is supported. A side-facing fingerprint scanner is also included in the package.

The device is water-repellent, and it offers storage expansion

The Motorola Moto g04s is IP52 certified, in other words, it has a water-repellent design. There are also two SIM card slots included here, and the microSD card slot is separate.

A 50-megapixel main camera (f/1.8 aperture) sits on the back, while a 5-megapixel unit (f/2.2 aperture) can be found on the front side of the phone. Bluetooth 5.0 is also supported, and there’s a Type-C port at the bottom.

The Motorola Moto g04s measures 163.49 x 74.53 x 7.99mm, while it weighs 178.8 grams. The phone comes in Concord Black, Satin Blue, Sea Green, and Sunrise Orange color variants.

Motorola’s new budget offering is priced at €119 ($129), and it is now available in Europe. It is coming to Latin America, the Middle East, Africa, and Asia soon, though.


[ad_2]
Source link

Critical Rust Flaw Let Attackers Inject Commands on Windows

0
[ad_1]

A new critical vulnerability has been discovered in two of the Rust standard libraries, which could allow a threat actor to execute shell commands on vulnerable versions.

This vulnerability has been assigned CVE-2024-24576, and its severity has been given as 10.0 (Critical).

In this report, Rust Security Response stated that they have not identified a solution yet but have created a workaround to mitigate this vulnerability.

This vulnerability was credited to RyotaK and Simon Sawicki (Grub4K) for helping them fix it.

Critical Rust Vulnerability

According to the reports shared with Cyber Security News, this vulnerability exists due to insufficient validation of arguments passed to Command::arg and Command::args APIs. 

The documentation of these two APIs states that the arguments passed to the APIs directly to the spawned process, and it will not be evaluated by a shell.

In addition, the implementation of these two APIs is complicated due to the fact that the Windows API passes all of the provided arguments as a single string, leaving the splitting process with the spawned process.

Document
Stop Advanced Phishing Attack With AI

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Stopping 99% of phishing attacks missed by other email security solutions. .

However, the cmd.exe process has a different splitting logic in Windows as it forces the standard library to perform the escaping for the arguments.

Nevertheless, this escaping sequence was not sufficiently validated, making it easier for threat actors to pass malicious arguments to the spawned process to execute arbitrary shell code. 

As a means of mitigating this vulnerability, Rust Security response team improved the escaping code with strong implementations and has made the Command API to return an InvalidInput error if it cannot safely escape any argument. 

Moreover, this error will be thrown during the process of spawning. For Windows users, the CommandExt::raw_arg method can be used to bypass the standard library’s escaping logic used by the cmd.exe process. 

Affected Versions And Fix

This vulnerability affects all the Rust versions earlier than 1.77.2 on Windows if any code or dependencies execute batch files with untrusted arguments.

Other platforms are not affected by this vulnerability.

To fix this, the Rust Security response team has recommended upgrading Rust to the latest version, 1.77.2, to prevent any unauthorized malicious threat actors from exploiting this vulnerability.

Secure your emails in a heartbeat! To find your ideal email security vendor, Take a Free 30-Second Assessment.


[ad_2]
Source link

New SharePoint Technique Lets Hackers Bypass Security

0
[ad_1]

Two new techniques uncovered in SharePoint enable malicious actors to bypass traditional security measures and exfiltrate sensitive data without triggering standard detection mechanisms.

Illicit file downloads can be disguised as harmless activities, making it difficult for cybersecurity defenses to detect them. To accomplish this, the system’s features are manipulated in various ways.

Security researchers from Varonis Threat Labs discovered two SharePoint techniques.

Open-in-App Method

The first technique dubbed the “Open in App Method,” takes advantage of the SharePoint feature, which allows users to open documents directly in their associated applications.

While this feature is designed for user convenience, it has inadvertently created a loophole for data breaches.

Attackers can use this feature’s underlying code to access and download files, leaving behind only an access event in the file’s audit log.

Document
Stop Advanced Phishing Attack With AI

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Stopping 99% of phishing attacks missed by other email security solutions. .

This subtle footprint can easily be overlooked, as it does not resemble a typical download event.

The exploitation of this method can be carried out manually or automated through a PowerShell script.

When automated, the script can rapidly exfiltrate many files, significantly amplifying the potential damage.

The script leverages the SharePoint client object model (CSOM) to fetch files from the cloud and save them to a local computer, avoiding creating a download log entry.

SkyDriveSync User-Agent

The second technique involves the manipulation of the User-Agent string for Microsoft SkyDriveSync, now known as OneDrive, Varonis said.

By masquerading as the sync client, attackers can download files or even entire SharePoint sites.

These downloads are mislabeled as file synchronization events rather than actual downloads, thus slipping past security measures that are designed to detect and log file downloads.

This method is particularly insidious because it can be used to exfiltrate data on a massive scale, and the sync disguise makes it even harder for security tools to distinguish between legitimate and malicious activities.

The use of this technique suggests a sophisticated understanding of SharePoint and OneDrive’s synchronization mechanisms, which could be exploited to systematically drain data from an organization without raising alarms.

Microsoft’s Response and Security Patch Backlog

Upon discovery, Varonis researchers promptly reported these vulnerabilities to Microsoft in November 2023. Microsoft has acknowledged the issue and categorized these vulnerabilities as “moderate” security risks.

They have been added to Microsoft’s patch backlog program, indicating that a fix is in the pipeline but may not be immediately available.

The discovery of these techniques underscores the risks associated with SharePoint and OneDrive, especially when permissions are misconfigured or overly permissive.

Organizations relying on these services for file sharing and collaboration must be vigilant and proactive in managing access rights to minimize the risk of unauthorized data access.

To combat these vulnerabilities, organizations are advised to implement additional detection strategies.

Monitoring for unusual patterns of access events, especially those that could indicate the use of the “Open in App Method,” is crucial.

Similarly, keeping an eye on sync activities and verifying that they match expected user behavior can help identify misuse of the SkyDriveSync User-Agent technique.

Furthermore, organizations should prioritize the review and tightening of permissions across their SharePoint and OneDrive environments.

Regular audits and updates to security policies can help prevent threat actors from exploiting such vulnerabilities in the first place.

Secure your emails in a heartbeat! To find your ideal email security vendor, Take a Free 30-Second Assessment.


[ad_2]
Source link