Apple Wallet pass support in Google Wallet arrives for more users

0
[ad_1]

For a while now, Google has been working on Apple Wallet pass support for its Wallet service. Now, the company is rolling out the feature more widely. However, it will probably take a while for its adoption across all relevant apps and services.

Some Google Wallet users had already received support for “.pkpass” files in March as a test. These types of files are what Apple Wallet uses to read, store, and manage pass data. Now, as spotted by the 9to5Google team, the Google Wallet “.pkpass” file support is going live for more users around the world.

That said, there is an initial problem: the adoption of the new option. Google’s public tests lasted just a few weeks, so it seems likely that not all services had enough time to adapt. However, integrating this feature into Google Wallet en masse will likely help speed up the process.

Google Wallet now supports Apple Wallet passes, but it’s not working everywhere yet

The 9to5Google report indicates that its test results were hit-or-miss. For example, clicking on the “Add to Apple Wallet” button of a parking pass from the Charlotte NC airport allowed the ability to download the “.pkpass” file and import it immediately to Google Wallet. On the other hand, there were cases where the download of the “.pkpass” file was blocked due to a message indicating that it was necessary to use the Safari browser.

This last error will probably be the most common among Android users until the adaptation of apps and services is massive. As a temporary solution, Max Weinbach suggested a workaround that consists of sharing a pass from the Apple Wallet app. After pressing the “share” option, you can choose a messaging app. Once you send the pass, the recipient (which can be yourself) will receive the “.pkpass” file. This way, you can import all your Apple Wallet passes.

From now on, it is up to the relevant services to adapt to Apple Wallet pass support in the “rival” service. The Mountain View company has already taken the most important step, and all that remains is to wait for widespread adoption.

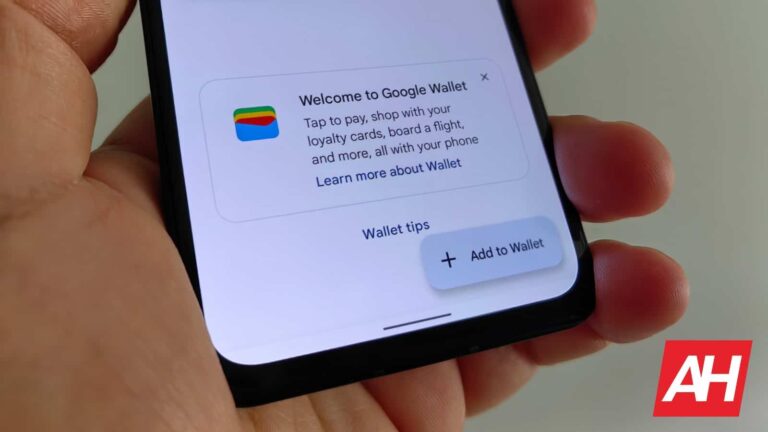
importing Apple Wallet pass to Google Wallet AH
importing Apple Wallet pass to Google Wallet. Source: 9to5Google

[ad_2]
Source link

The Disney+ password crackdown will come in June

0
[ad_1]

Oh, Netflix, look what you’ve done! For several months, we’ve known that Disney+ was looking to implement a password-sharing crackdown. We’ve seen Hulu bring its own password crackdown, and Disney owns Hulu. Well, according to a new report, Disney+ will bring its password crackdown in June.

To catch you up, companies like Disney, Hulu, and Netflix have been looking for a way to stave off password sharing. This is when an account holder gives another person they’re login credentials to watch content on a streaming service without paying. This is something that all streaming services hate.

Last year, Netflix cracked down on password sharing. Netflix accounts are geo-locked, so, if any person tries to watch Netflix while outside of the designated household, it will be blocked and the potential watcher would be prompted to buy their own subscription. Obviously, many people were infuriated with this. However, it actually worked. After the crackdown, Netflix’s subscriber count rose- we’re sure that many people chose the Netflix with ads tier. So, naturally, we expect all major streaming services to bring policies such as these.

The Disney+ password crackdown is coming in June

If you like sharing your Disney+ account with your friend from across town, it looks like your days are numbered. In an interview with CNBC, Disney’s CEO Bob Iger stated that the company will be cracking down on password sharing “in just a few countries in a few markets,” starting in June. This will be just like Netflix’s password crackdown where the company tested it extensively in a few markets. However, Disney plans on expanding this to all users starting in September.

So, if you enjoy sharing your password, you have, at the very most, about five months to keep doing so. After that, you may be prompted to buy your own service. This is a massive bummer for people who really enjoy sharing passwords. However, this is something that should not come as a surprise. With a struggling global economy, several companies around the world are making tough decisions that users are not a fan of. The question remains whether this will hold the same results for Disney+ as it did for Netflix. Only time will tell.


[ad_2]
Source link
Bing ad for NordVPN leads to SecTopRAT

0
[ad_1]

Most of the malicious search ads we have seen have originated from Google, but threat actors are also abusing other search engines. Microsoft Bing is probably the second best target due to its close ties to the Windows ecosystem and Edge browser.

In this blog post, we look at a very recent malvertising campaign impersonating the popular VPN software NordVPN. A malicious advertiser is capturing traffic from Bing searches and redirecting users to a decoy site that looks almost identical to the real one.

The threat actors went ever further by trying to digitally sign a malicious installer and hosting it on Dropbox. Victims will have the impression they are getting NordVPN as it is part of the package, but will also inadvertently install a Remote Access Trojan known as SecTopRAT on their computer.

We have reported the malicious Bing ad to Microsoft, and other parts of the distribution infrastructure to their respective provider. We want to reiterate that NordVPN is a legitimate VPN provider and they are being impersonated by threat actors.

Fraudulent Bing ad

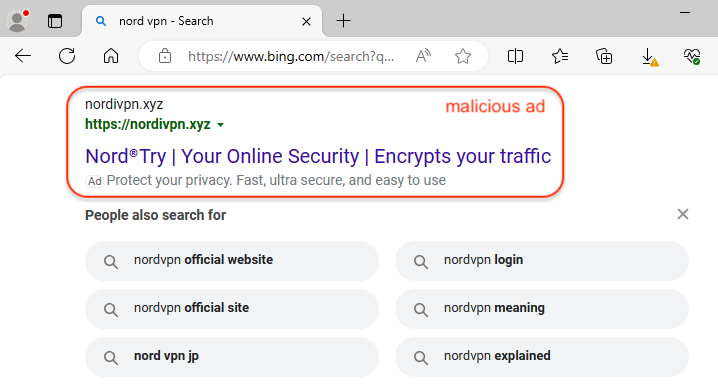
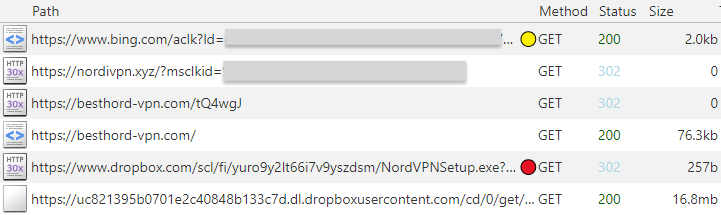
When searching for “nord vpn” via the Bing search engine, we identified a malicious ad that impersonates NordVPN. The ad itself looks suspicious because of the URL in the ad snippet. The domain name nordivpn[.]xyz was created one day ago (April 3, 2024). It was probably chosen as it looks quite similar to the official name and can deceive users who aren’t looking too closely.

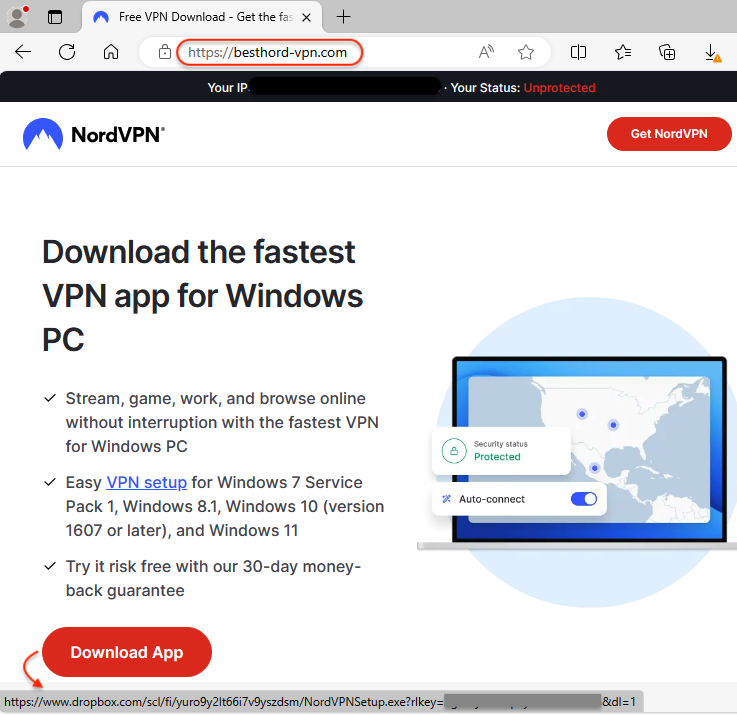
As we often see, the ad URL is simply used as a redirection mechanism to a fake website that is meant to look identical to the one being impersonated. This is true here as well, where we have a redirect to besthord-vpn[.]com (note again the spelling chosen with the ‘h‘ looking like an ‘n‘) which was created today, only a few hours ago.

The website looks incredibly convincing, and victims will be tricked into downloading the app from there. Unlike the legitimate NordVPN that goes through a sign up process, here you can directly download the installer from Dropbox.

Here’s a summary of the traffic flow from the malicious ad to the download link:

Malware payload

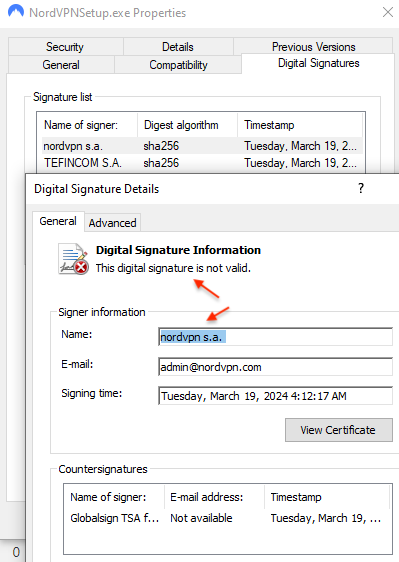
The downloaded file is called NordVPNSetup.exe and is digitally signed, as if it was from its official vendor; however, the signature is not valid.

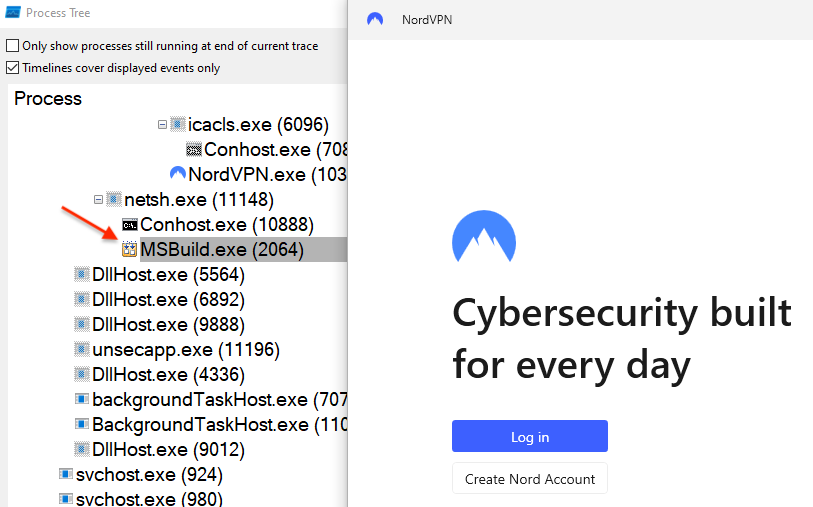
The file contains both an installer for NordVPN and a malware payload. The installer for NordVPN is meant to give victims the illusion that they are actually installing a real file.

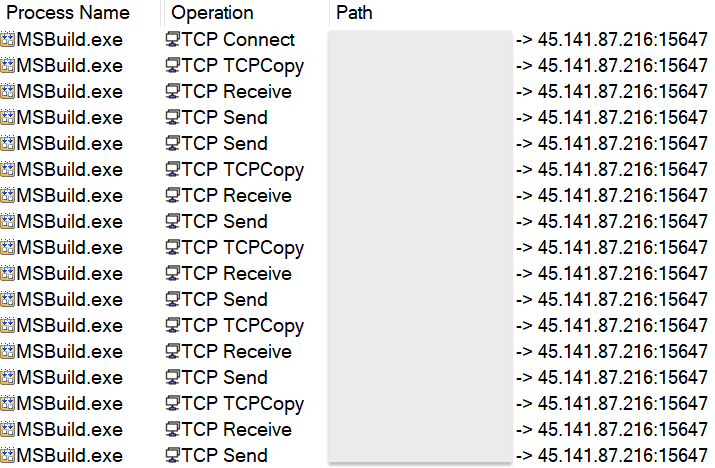
The payload is injected into MSBuild.exe and will connect to the malware author’s command and control server at 45.141.87[.]216 on port 15647.

That network traffic is detected by Emerging Threats as Arechclient2 Backdoor, an alias for SecTopRAT.

Conclusion

Malvertising continues to show how easy it is to surreptitiously install malware under the guise of popular software downloads. Threat actors are able to roll out infrastructure quickly and easily to bypass many content filters.

ThreatDown customers who have DNS Filtering can proactively block online ads by enabling the rule for advertisements. This is a simple, and yet powerful way to prevent malvertising across an entire organization or in specific areas.

The malicious ad and related indictors have been reported as we work with industry partners to take down this campaign.

Indicators of Compromise

Malicious domains

nordivpn[.]xyz
besthord-vpn[.]com

Fake NordVPN installer

e9131d9413f1596b47e86e88dc5b4e4cc70a0a4ec2d39aa8f5a1a5698055adfc

SecTopRAT C2

45.141.87[.]216

[ad_2]
Source link

Motorola Edge 50 Fusion [Updated]

0
[ad_1]

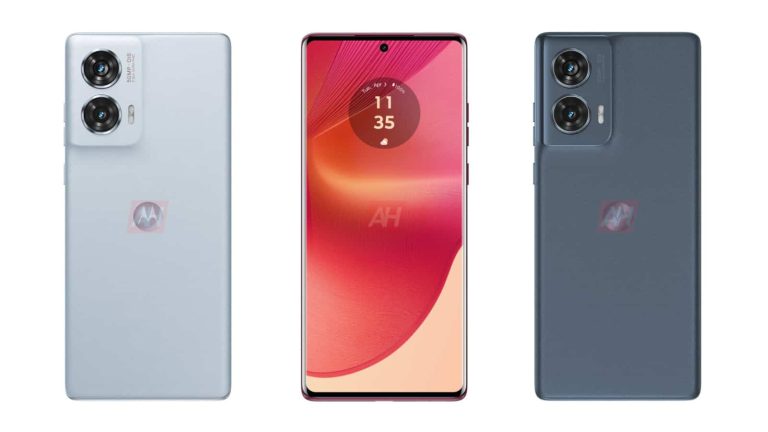
Just a couple of weeks after bringing you an exclusive look at the Motorola Edge 50 Pro (also known as the X50 Ultra and Edge Plus 2024), we’re back with another look at a new Motorola smartphone that is also launching on April 3.

This is the Motorola Edge 50 Fusion.

Motorola’s Edge 50 Fusion is a good-looking mid-range phone

On the front of the phone, it has the April 3 date, when the device will be announced. In fact, Motorola has already begun sending out invites for an event in India on April 3. We’d expect it to launch first in India and China, then make its way to Europe and North America shortly after that.

Motorola’s Edge 50 Fusion will sport a curved 6.7-inch pOLED display powered by the Snapdragon 6 Gen 1. The Edge 30 Fusion recently appeared on Geekbench with the Snapdragon 6 Gen 1, scoring a 913 in the single-core test and a 2,629 in the multi-core. Motorola also includes 8GB of RAM and 256GB of storage, which is pretty standard for Motorola with its mid-range phones, actually.

The company includes a 50-megapixel primary camera with OIS on the back and a 13-megapixel ultrawide camera. At the same time, the front has a 32-megapixel camera in the hole punch display.

The Edge 50 Fusion is also expected to sport a 5,000mAh battery with 68W wired charging. However, the 68W charger is not expected to be included in the box. Motorola has also ensured that the Edge 50 Fusion is waterproof with an IP68 rating and also has Gorilla Glass 5, so it should be pretty resistant to shattering.

In the gallery below, you can see all three colors in which the Motorola Edge 50 Fusion will be available. This includes Ballad Blue, Peacock Pink, and Tidal Teal. All three have a textured back; however, the Ballad Blue has a vegan leather back. We expect the Motorola Edge 50 Fusion to be priced around $300 USD or around Rs 25,000 in India.

Update: Evleaks has recently posted a video showing off the Motorola Edge 50 Fusion. This video shows all three colors that we have shown above. Essentially confirming our leak.


[ad_2]
Source link

Disney Plus’ password-sharing crackdown begins in June

0
[ad_1]

If you have a Disney Plus account, and you happen to share your login with friends and family outside your home, get ready to spend more. As originally shared back in February, Disney+ will begin to crack down on password sharing. However, now Disney CEO Bob Iger has laid out a definite timeline, and the end of an era is coming this summer.
Disney, taking cues from Netflix’s anti-password-sharing playbook, is now determined to do the same and boost profits. This is a strategy that is becoming popular among streamers, along with incorporating ads and asking subscribers to pay more in order to get rid of them. Even Hulu and Amazon Prime Video have jumped on these trends.
As per Iger (via 9to5Mac), Disney will begin its password crackdown experiment in a few countries starting in June. By September, expect it to be rolled out everywhere. Though Iger didn’t get super technical about how this’ll work, Disney has said they’ll be keeping an eye on your account activity to make sure you’re all watching from a single household.

The writing’s been on the wall since last summer when Disney announced they were joining Netflix in the fight against shared accounts. In February, they even gave US subscribers a heads-up, so this latest announcement isn’t exactly a surprise. Still, at least now there’s a clearer idea of when you’ll need to start budgeting for that extra Disney+ subscription and break the news to the friends and/or family members that may have access to it.

Netflix’s anti-password-sharing move caused a bit of a stir initially, but it ultimately led to a boost in paying subscribers. Disney is probably hoping for the same results and banking on the popularity of their current and upcoming shows. Considering all the recent price hikes, streaming is becoming more expensive than ever. Now that password-sharing looks like it’ll be a thing of the past, we’re really in for some more strict budgeting.


[ad_2]
Source link

New Latrodectus Downloader Malware Linked to IcedID and Qbot Creators

0
[ad_1]
New Latrodectus Downloader Malware Linked to IcedID and Qbot Creators
Image credit: Hackread.com

A new malware threat named Latrodectus has emerged, bypassing detection methods and linked to the developers behind IcedID. This downloader malware empowers cybercriminals (including infamous actors like TA577 and TA588) to breach systems and deploy various malicious payloads.

Cybersecurity researchers at Proofpoint have identified a new malware threat dubbed “Latrodectus.” First observed in November 2023, Latrodectus is a downloader malware used by cybercriminals to gain initial access to victim systems and deploy further malicious payloads.

This malware poses a major threat due to its ability to evade detection techniques commonly employed in sandboxes, which are security environments used to analyze suspicious code.

Latrodectus: A New Player with Familiar Traits

Initial analysis suggested Latrodectus might be a variant of the notorious IcedID malware. However, further investigation revealed it to be an entirely new strain, likely created by the same developers behind IcedID. This connection is supported by shared infrastructure and code characteristics.

Initial Access Brokers Leverage Latrodectus

Proofpoint report shared with Hackread.com on Thursday 04, 2024 ahead of publication on Tuesday attributes Latrodectus to two specific threat actors: TA577 and TA578. It is worth mentioning that TA578 is known for delivering malware threats like BazaLoader, Cobalt Strike, Ursnif, and KPOT Stealer.

On the other hand, TA577 is infamous for having served as a key affiliate of the Qbot network until its recent disruption. TA577 has been linked by Proofpoint to various campaigns, with subsequent ransomware infections such as Black Basta being notably attributed to them.

These actors are classified as Initial Access Brokers (IABs), specializing in gaining initial footholds within victim networks. Latrodectus serves as their tool to establish a foothold and potentially deploy ransomware or other malicious tools.

Commenting on this, Ken Dunham, Cyber Threat Director at Qualys Threat Research Unit told Hackread.com, “Battling eCrime is similar to moving a couch where roaches live, they simply run to another piece of furniture or room nearby to seek harbour and continue business as normal, despite any actions taken by the homeowner.“

“Latrodectus has powerful components upon its emergence, capable of defeating sandboxes, use of RC4 encrypted command and control communications, and more,“ Ken warned. “It appears likely that actors behind QBot felt the heat from takedowns last year, migrating to this new code base and infrastructure in the fall of 2023.“

While Latrodectus activity dropped in December 2023 and January 2024, Proofpoint reports a surge in campaigns throughout February and March 2024. This suggests a growing adoption of Latrodectus by cybercriminals.

The specific payloads delivered by Latrodectus remain unknown, but its downloader functionality allows attackers to deploy a wide range of tools through malicious emails depending on their objectives.

New Latrodectus Downloader Malware Linked to IcedID and Qbot Creators
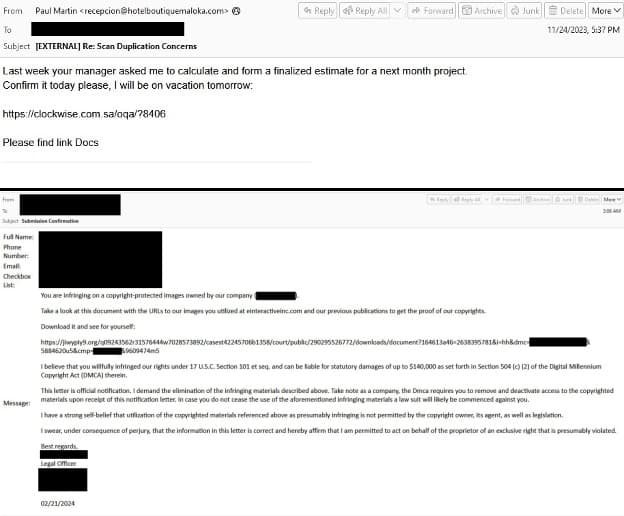
Two of the malicious emails used in the campaign to spread Latrodectus (Screenshot: Proofpoint)

While technical details of Latrodectus’s modus operandi are available in Proofpoint’s blog post, here are some to mitigate the risk of Latrodectus:

  • Maintain strong cybersecurity hygiene: Regularly update software and firmware on all devices. Utilize robust security solutions with advanced malware detection capabilities.
  • Be cautious of suspicious emails: Phishing emails are a common method for distributing malware. Be wary of unsolicited attachments and links.
  • Educate employees: Train employees on cybersecurity best practices, including email security awareness and the importance of reporting suspicious activity.
  1. New Malware “BunnyLoader 3.0” Steals Credentials
  2. WordPress Websites Hacked with New Sign1 Malware
  3. TheMoon Malware Hacks 6,000 Asus Routers in 72 Hours
  4. AcidRain Linux Malware Variant “AcidPour” Targeting Ukraine
  5. New Vcurms Malware Targets Popular Browsers for Data Theft

[ad_2]
Source link

Android 15 could bring a Bluetooth auto-on feature

0
[ad_1]

When you switch your Bluetooth off on an Android phone, you expect it to stay off until you enable it again. This is how it’s been. However, Android 15 may change that with a Bluetooth auto-on feature.

Right now, people are digging into the latest Android 15 developer preview and Android 14 Beta release to figure out what sort of features to expect from Android 15. So far, we’ve gotten hints at features such as the app archiving feature, the Auracast multi-device streaming feature, the revamped volume panel, Etc. As time goes on, we’re going to discover more features and additions to the software that will help characterize Android 15.

Android 15 may bring a Bluetooth auto-on feature

As stated before, when you turn off Bluetooth, you’re going to want to keep it off until you turn it back on. However, since the company is about to launch its Find My Device network, it seems like Google doesn’t want you to be able to keep your Bluetooth off for long.

The Find My Device network seems like it will be similar to Apple’s Find My network. Different Android devices will be able to contact and ping other devices via Bluetooth. This will help people pinpoint their devices if they ever lose it.

So, this new feature may be a result of that. Digging into the Android 14 QPR 2 update, Android engineer Mishaal Rahman was able to find some strings of code alluding to this feature. This was discovered via an APK Deep dive, so this news should be taken with a grain of salt.

For starters, when you turn off your Bluetooth radio within the Quick Settings panel, you will see a dialog pop up saying, “Features like Quick Share, Find My Device, and device location use Bluetooth”. So, this is a dialogue that will pop up to dissuade you from turning off your Bluetooth radio.

Also, when enabled, you will see a toggle appear that will automatically turn the Bluetooth back on the next day. You will also be able to find a similar dialogue when you go to your Bluetooth settings page in the system settings.

A few things to note about this

Firstly, you don’t have to worry about Shady apps using this Bluetooth Auto-on feature. Only system-level apps will be able to use it. So, you should only expect native Android apps to be able to use this feature.

Also, looking at the code, it appears that this will not be exclusive to Android 15. It’s possible that Google could distribute this to older versions of Android. While that is the case, it appears that it won’t be available for all devices. However, we’ll have to wait and see.


[ad_2]
Source link

Samsung pushes the March update to the Galaxy A32

0
[ad_1]

The Galaxy A32 5G was the first mid-range smartphone to receive Samsung’s March 2024 security update. The rollout began early last month in Latin America and gradually expanded to other regions, including the US. However, the update never trickled down to the 4G version of the phone. That is finally changing as the company begins the rollout in Asia.

Galaxy A32 gets Samsung’s March 2024 update

Over the past few years, Samsung has launched 4G and 5G versions of several mid-range smartphones. Some markets get both variants while the company only brings one to others. For example, the US only got the Galaxy A32 5G while both variants were released in Latin America. Updates are also often rolled out separately, meaning that one gets the latest security patch ahead of the other.

In the Galaxy A32’s case, the 5G version picked up the March 2024 update early. Several weeks later, last month’s security patch is rolling out to the 4G model. According to SamMobile, which first reported this update, the phone is getting the new SMR (Security Maintenance Release) in India and neighboring countries, including Bangladesh, Nepal, and Sri Lanka.

The update comes with the firmware build number A325FXXS8DXC1. Unsurprisingly, it doesn’t bring anything more than the 40+ vulnerability fixes part of Samsung’s March 2024 security patch. The Galaxy A32 is no longer eligible for feature updates, so don’t expect any new features or improvements. Launched in early 2021 with Android 11, the devices received OS updates up to Android 13.

Samsung will continue to deliver security patches to the phone for at least one more year—it is eligible for four years of security updates. The Galaxy A32 and Galaxy A32 5G are currently getting these updates quarterly, i.e., once every three months. The frequency may go down in the coming months. The Korean firm will pull official software support for the duo sometime in early 2025.

Samsung has already released the April SMR for Galaxy devices

The Galaxy A32 joins more than 40 other models in Samsung’s March 2024 update party. It is probably one of the last entrants as the company starts to push the April SMR to eligible models. The Galaxy S24 series has already picked up the latest security patch. It will soon be available for the Galaxy S23 and other devices, including foldables. The Galaxy A32 and Galaxy A32 5G may not get it though, as they are on a quarterly update schedule.


[ad_2]
Source link

OWASP Disclosed Data Breach Affecting Old Members

0
[ad_1]

Heads up, OWASP members! A data breach might have exposed your information online, particularly if you joined the OWASP community in its early phase. OWASP recently disclosed a data breach affecting its old members while assuring it didn’t impact the new members.

OWASP Admitted Data Breach

The OWASP Foundation recently disclosed a data breach due to a misconfigured Wiki web server.

As elaborated in its advisory, the data breach affected some of its old members who joined the Foundation from 2006 to 2014. At that time, OWASP had asked the members to provide their resumes to show a connection to the OWASP Community. While it was merely a step in the early membership process, no longer continued by OWASP, this information has now suffered a breach. Consequently, this security breach has affected those old OWASP members, leaving the newly registered ones unaffected.

Regarding the information breached in this incident, OWASP stated that it includes the data mentioned in the resumes. That means the details exposed include personally identifiable information (PII), such as users’ names, contact numbers, email addresses, and physical addresses.

Members After 2014 Protected – Confirms OWASP

OWASP explained that since the breach affected old members, many of whom are no longer with OWASP. Besides, the incident happened roughly 10 years ago, making it possible that the breached data, including the email addresses, must have been changed. Yet, OWASP would still contact the available email addresses to inform the impacted users.

In addition, OWASP removed the breached information from the internet. Nonetheless, it still advised members with no changes in their resumes to practice caution when interacting with unsolicited phone calls, emails, and messages.

Today, OWASP applies contemporary cloud-based security measures to protect users. This includes implementing two-factor authentication, limited access, minimal data collection, and strict membership data protection. Hence, users joining OWASP after 2014 and those who have updated their details may rest assured about their data security.

Let us know your thoughts in the comments.


[ad_2]
Source link

Jackson County hit by ransomware, declares state of emergency

0
[ad_1]

On April 2, 2024, Jackson County tweeted that it had identified significant disruptions within its IT systems, “potentially attributable to a ransomware attack”. Jackson County is one of 114 counties in Missouri, with a population of approximately 718,000 people, mostly in Kansas City.

The tweet explains that the attack has affected systems dealing with “tax payments and online property, marriage license and inmate searches,” and says that “the Assessment, Collection and Recorder of Deeds offices at all County locations will be closed until further notice.”

The Kansas City Board of Elections and Jackson County Board of Elections are not affected. County officials also confirmed that the compromised systems did not store residents’ financial data.

“In its commitment to protect residents, Jackson County prioritizes the security of sensitive financial information and does not keep any such data on its systems. Instead, these crucial details are securely handled and stored by our trusted partner, Payit.”

On the same date an executive order declared a state of emergency. The state of emergency exists to help officials investigate and take necessary measures without the need for the usual requirements of competitive bidding. And it allows them to make appropriations from the County’s emergency fund, and additional financial adjustments, to address the requirements imposed by the emergency.  

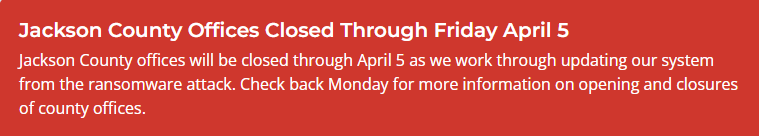
Today, the official Jackson County site says that the Jackson County offices will remain closed through Friday April 5.

Jackson County offices will be closed through April 5 as we work through updating our system from the ransomware attack. Check back Monday for more information on opening and closures of county offices.

Even though it looks like the county had its emergency plans ready and the county associates, especially those within the IT department, played a critical role in mitigating the impact of the attack, the impact of such a ransomware attack is not to be underestimated.

The County is investigating the security breach with the help of law enforcement agencies and cybersecurity experts. So far, there is no information available about the ransomware group that is behind this attack, but we’ll keep you posted.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; and disable or harden remote access like RDP and VPNs.
  • Prevent intrusions. Stop threats early before they can even infiltrate or infect your endpoints. Use endpoint security software that can prevent exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like ThreatDown EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Our business solutions remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.


[ad_2]
Source link