IntelBroker Leaks Alleged National Security Data Tied to US Contractor Acuity Inc.

0
[ad_1]
IntelBroker Leaks Alleged National Security Data Tied to US Contractor Acuity Inc.

IntelBroker hacker leaks data linked to US contractor Acuity Inc., exposing potentially sensitive intelligence agencies-related data – US government previously denied Acuity Inc. breach, but experts warn of national security risks.

The notorious IntelBroker hacker and their affiliates have leaked a trove of sensitive records, which they claim jeopardize the United States national security. The data, leaked on Breach Forums, is linked to US Federal contractor Acuity Inc., in a data breach allegedly carried out in March 2024. The data was previously being sold for just $3,000 in Monero (XMR) cryptocurrency.

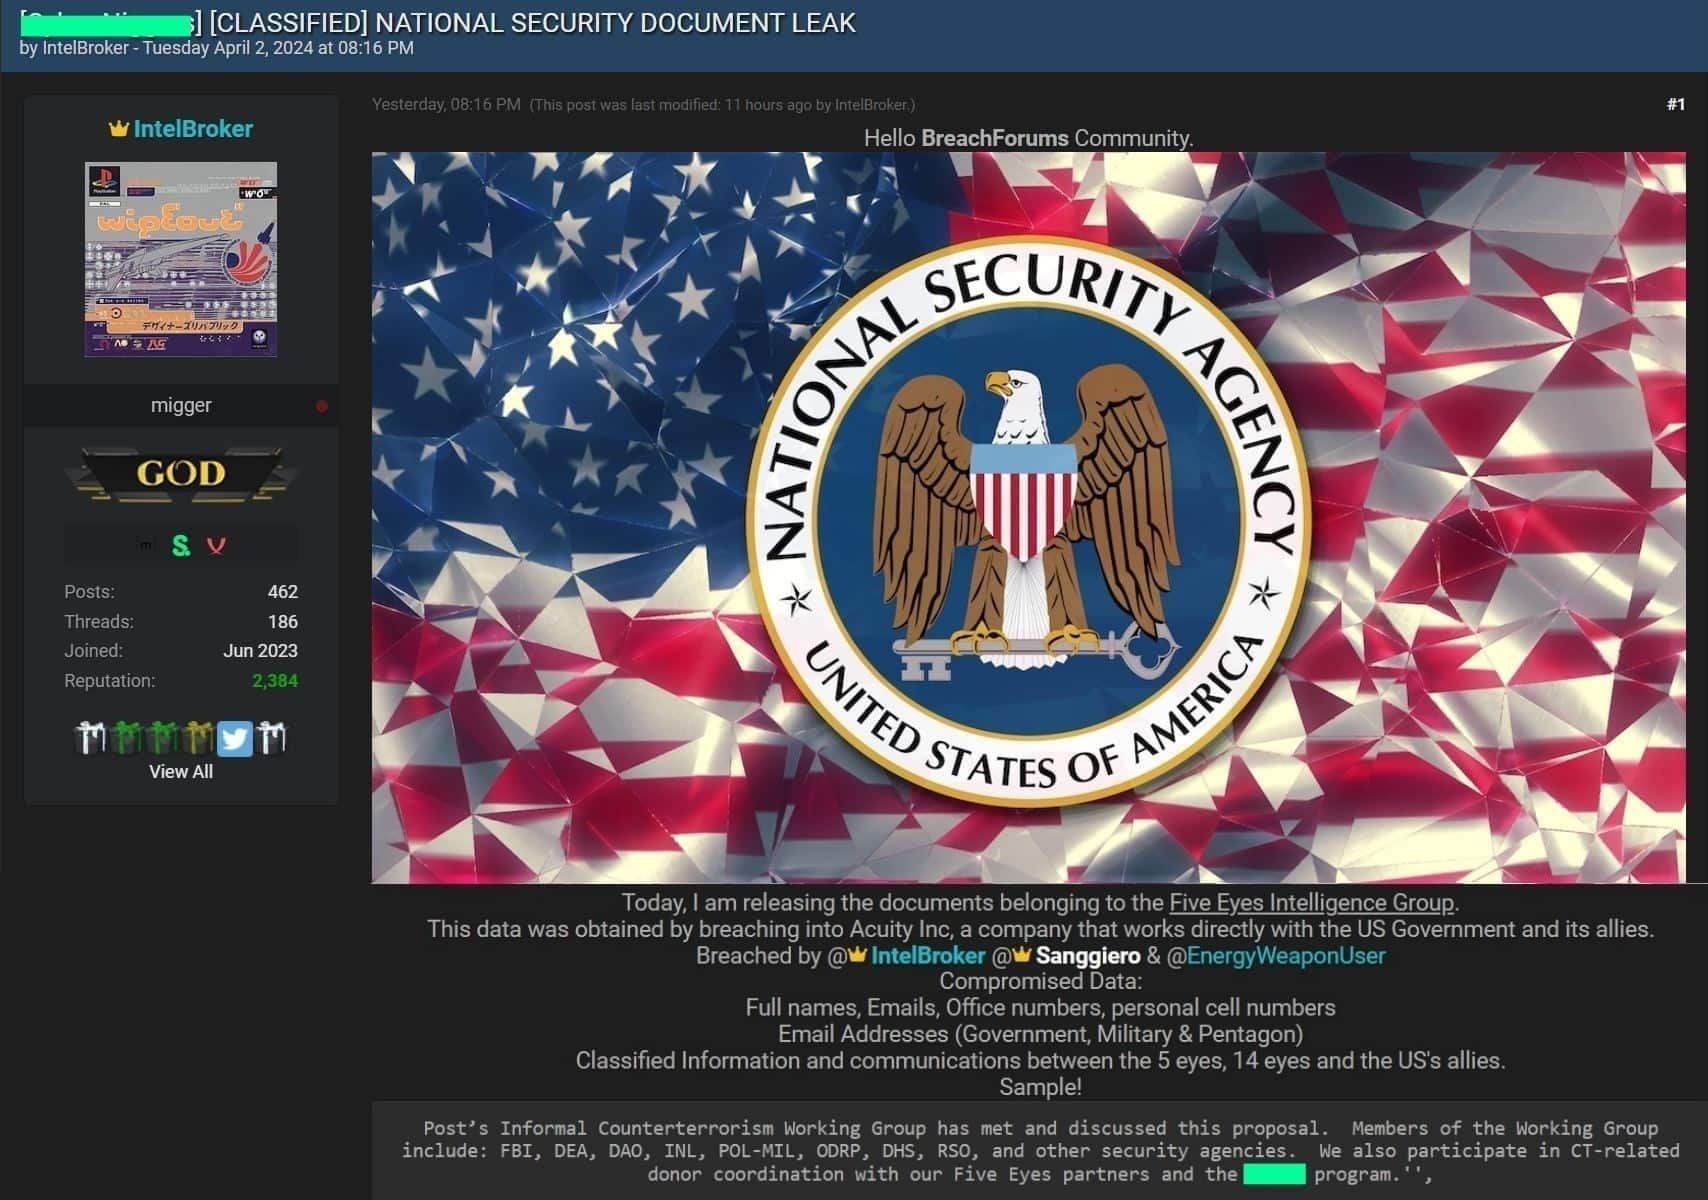
As seen by Hackread.com, IntelBroker has classified the breach as a “National Security Documents Leak,” involving documents from the “Five Eyes Intelligence Group.” The leaked records now accessible to the public include highly sensitive information such as full names, email addresses, office numbers, personal cell numbers, email addresses (government, military, and Pentagon), classified information, and communications between the Five Eyes, 14 Eyes, and the US’s allies.
IntelBroker Leaks Alleged National Security Data Tied to US Contractor Acuity Inc.
Screenshot from Breach Forums (Credit: Hackread.com)

For your information, The Five Eyes Intelligence Group is an intelligence alliance including five English-speaking countries: the United States, the United Kingdom, Canada, Australia, and New Zealand. The alliance aims to share intelligence and collaborate on signals intelligence (SIGINT) gathering, surveillance, and cybersecurity activities.

Background of the alleged Acuity Inc. data breach

On March 4, 2024, Hackread.com published an exclusive report on a data breach allegedly involving Acuity Inc., a federal contractor based in Reston, Virginia. The breach was claimed by IntelBroker.

The hacker claimed the use of a zero-day security vulnerability in GitHub to access Acuity Inc.’s tokens and facilitate their malicious activities, including the theft of data belonging to U.S. Citizenship and Immigration Services (USCIS) and U.S. Immigration and Customs Enforcement (ICE).

Hackread.com reported the breach to GitHub, Acuity Inc., ICE, and USCIS. However, none of the organizations responded to the report. In contrast, Homeland Security, responding to a third-party media site that had not reported on the incident or analyzed the data, denied IntelBroker’s claims and labelled the breach as false, categorizing the leaked information as “test demos for vendors” with fake names and contact information used solely to provide examples of received data.

Now What?

Despite the US Government’s version that the data leak is fake, Hackread.com’s analysis suggests that the publicly leaked information remains highly consequential. Even if the data is fabricated, it exposes the modus operandi of US intelligence agencies and their allies, potentially risking their operational security and strategies.

IntelBroker

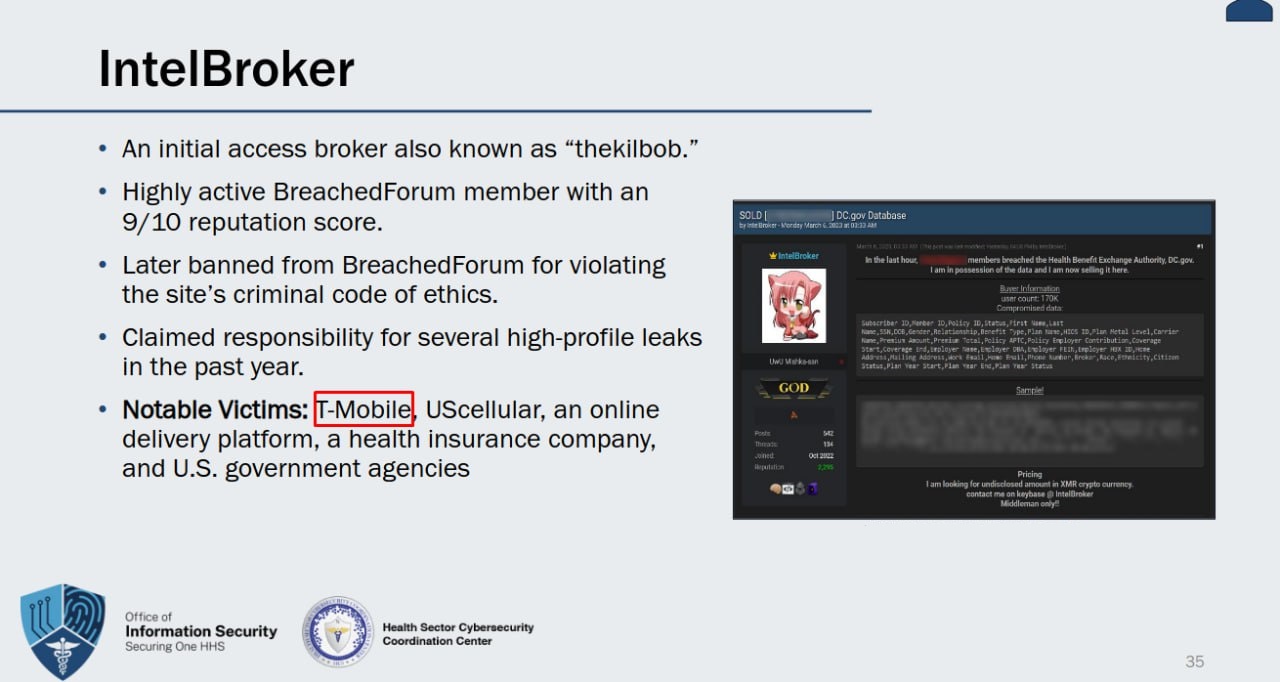
The hacker’s origins and affiliates are unknown; however, according to the United States government, IntelBroker is alleged to be the perpetrator behind one of the T-Mobile data breaches.
IntelBroker Hackers Leak Sensitive Records, Raising National Security Concerns

Additionally, IntelBroker is known for targeting high-profile targets in the United States. Some of their previous data breaches include Las Angeles Intl. Airport, US DoD Documents, Staffing Giant Robert Half, Facebook Marketplace Database, DARPA-related accesses in General Electric breach, Weee! Grocery and several others.

  1. US Govt’s secret terrorist watchlist with 2M records exposed online
  2. Chinese Group Storm-0558 Hacked European Govt Emails, Microsoft
  3. Adobe ColdFusion Flaw Used by Hackers to Access US Govt Servers
  4. Traffic sign near ICE headquarters hacked with “Abolish ICE” message
  5. Norweigian researcher exposes how a US firm collected his location data

[ad_2]
Source link
Android 15 could revamp the status bar

0
[ad_1]

Android 15 is getting closer, and we are still discovering new information about this next iteration of Android. As discovered by noted Android engineer Mishaal Rahmen, a part of Android that has been the same for years. Android 15 could revamp the status bar.

The status bar is part of the UI that sits at the top of the screen. It displays your battery level notifications, Wi-Fi/data connection status, Etc. While Android has changed over the years, the icons in the status bar have remained the same. It changed a little over the years, but not much. So, Android 15 could breathe new life into the status bar.

Android 15 could revamp the status bar

Right now, we are dealing with very early information. There is no guarantee that the changes made in the developer preview will be reflected in the final release. So, you will want to take this news with a grain of salt. Anything could change between now and the official release.

What’s probably the biggest change is the battery icon. We are all used to seeing the battery icon standing vertically with the percentage right next to it in stock Android. It has not changed over the years. However, the battery icon will be bigger in Android 15. Also, we see that it’s lying down rather than standing up.

The most notable thing about this is the fact that the battery percentage could sit inside of the battery. Also, when your phone is plugged in, we’ll see a little lightning icon appear next to the battery percentage. The picture below shows how this will look in both light mode and dark mode.

Android 15 new status bar (2)Android 15 new status bar (1)

Another thing we noticed is the Wi-Fi icon. We’re used to seeing the downward-facing wedge showing the Wi-Fi signal strength. Historically, it’s been one singular shape. However, with Android 15, it appears that Google is going to go for a segmented icon. So, you will see each signal bar at its own element. We see the same thing for the data signal icon.

It’s unlikely that we will see these new icons in the developer preview. However, it’s possible that we will see it in one of the beta versions of the software. Stay tuned for more news on it.


[ad_2]
Source link

New XZ Utils Backdoor Free Scanner to Detect Malicious

0
[ad_1]

A critical vulnerability has been discovered in XZ Utils, a widely used data compression tool across Unix-like operating systems, including Linux.

This vulnerability, identified as CVE-2024-3094, involves a backdoor that could potentially allow unauthorized remote access, posing a significant threat to software supply chain security.

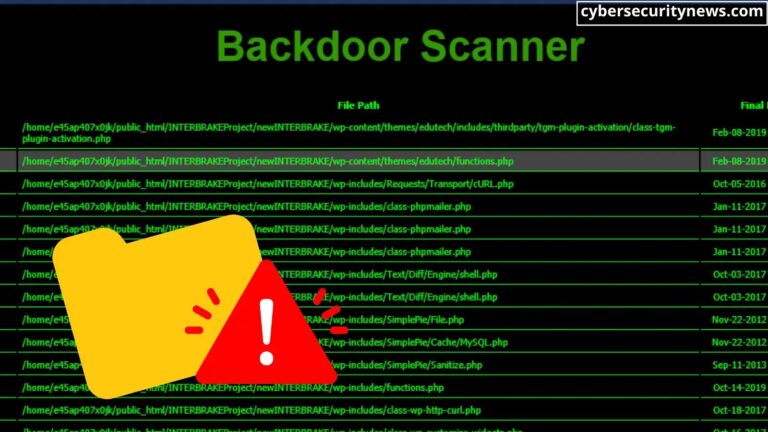
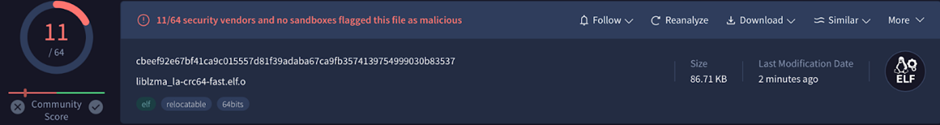
zero detection from VirusTotal
Zero detection from VirusTotal

The initial alarm was raised by Andres Freund, who noticed unusual activity in the XZ Utils project. Versions 5.6.0 and 5.6.1 of XZ Utils were found to be compromised.

Shortly after Freund’s warning, the United States government’s Cybersecurity and Infrastructure Security Agency (CISA) and the Open Source Security Foundation (OpenSSF) issued alerts about the critical nature of this backdoor, emphasizing the urgency of addressing this vulnerability due to its potential impact on OpenSSH security.

Document
Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

The revelation of this backdoor is particularly alarming because it represents a nightmare scenario for software supply chain security.

XZ Utils is integral to embedded systems and firmware development across various ecosystems, with the Linux ecosystem being a primary target due to its role in powering modern cloud infrastructure.

The Response and Mitigation Efforts

In response to the discovery of CVE-2024-3094, the community acted swiftly.

Many Linux distributions impacted by the vulnerability have rolled back to a known safe version of XZ Utils, demonstrating the effectiveness of industry-wide, community-driven coordination.

However, the challenge remains in quickly detecting and deactivating deployed backdoored versions in the field.

Traditional detection tools, which often rely on simple version checks, hash-based detection, or YARA rules, have proven inadequate.

These methods can lead to alert fatigue and false positives, overwhelming security teams.

Recognizing the limitations of existing detection methods, the Binary Research Team embarked on a mission to develop a more practical approach to identify the backdoored binaries.

exported by the payload object file

Their investigation revealed the complexity of the XZ Utils backdoor, believed to be part of a sophisticated, state-sponsored operation with multi-year planning.

An essential technique employed by the backdoor involves the GNU Indirect Function (ifunc) attribute, which allows for runtime resolution of indirect function calls.

The backdoor intercepts execution and modifies ifunc calls to insert malicious code.

Binary Intelligence technology in action
Binary Intelligence technology in action.

This static analysis method can generically detect tampering of control flow graph transitions, significantly reducing the false positive rate.

The discovery of the XZ Utils backdoor underscores the critical importance of software supply chain security.

Through the collaborative efforts of the security community and the innovative solutions provided by teams like Binary, the industry is better equipped to defend against these sophisticated threats.

As the landscape of cyber threats continues to evolve, such proactive measures and tools will be indispensable in safeguarding our digital infrastructure.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

New OnePlus Open update brings photo collages, camera improvements & more

0
[ad_1]

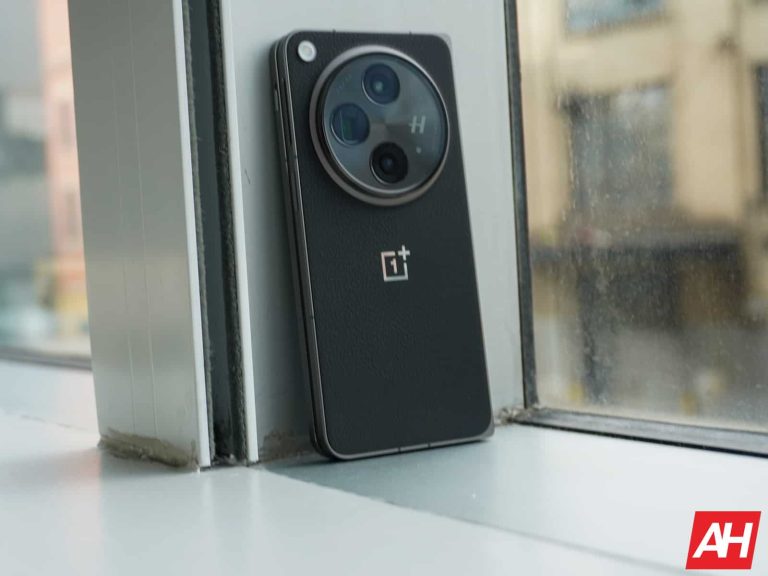
A new update has started rolling out to the OnePlus Open, and it brings photo collages, camera improvements, and more. If that sounds familiar, that’s because a very similar update landed on the OnePlus 12 and OnePlus 11 not long ago.

A new update brings photo collages to the OnePlus Open, along with camera improvements

This update is marked as OxygenOS v14.0.0.600, and it’s coming to Indian variants of the OnePlus Open at the moment. The update will soon spread to other markets, and it will have the same changelog. The update itself weighs around 770MB, so it is recommended that you be connected to WiFi when you update.

This update brings the March 2024 Android security patch along with it. On top of that, it includes some new features, and also some improvements to the camera and more.

Let’s kick things off with some new features, though. This update brings photo collages to the OnePlus Open. You can now make collages from the phone’s default Photos app. It’s a pretty basic tool now, but it’s here.

‘Partial screenshot’ feature has been added too, and several others

The company also added a ‘Partial screenshot’ option to the Smart Sidebar, if you use it. You can now also hold down the volume down button in order to turn on the flashlight when the screen is off.

Settings app-specific volumes is now possible as well. This is great to have if you prefer the volume to be higher when you want the videos, listen to podcasts, or whatever else.

The volume bar’s design has been altered too, and the system stability in general has been improved. We also got some camera improvements with this update.

OnePlus now enables you to switch between more focal lengths by tapping the zoom buttons. You can now also use the ultrawide and telephoto cameras in XPAN mode. The update also increases shutter response and improves the snapshot experience. You can now also use the zoom wheel to switch between different zoom options when taking videos.


[ad_2]
Source link

Galaxy S23 users report fingerprint issues after One UI 6.1 update

0
[ad_1]

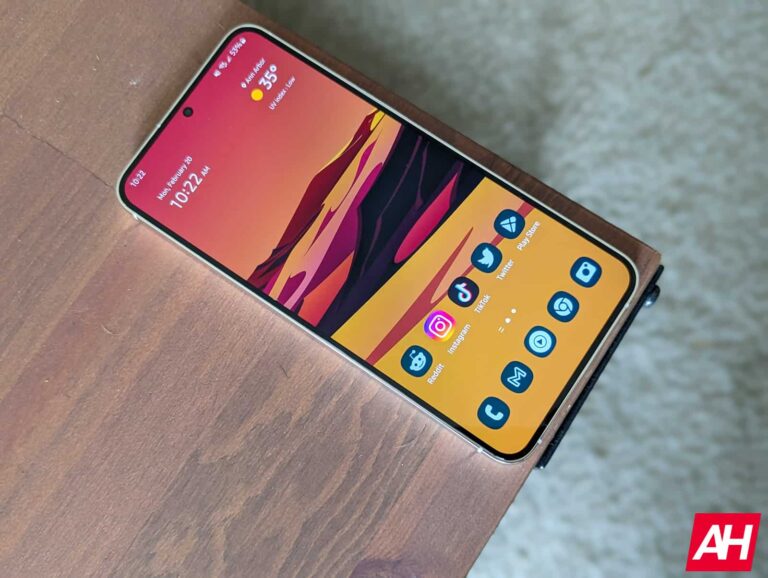
Samsung appears to have rushed the One UI 6.1 update for Galaxy devices. Users who have installed the update are encountering various issues. Over the past few days, we have seen reports about slow charging speeds and devices running warmer. Now, some Galaxy S23 users say the fingerprint scanner on their device is not working properly following the update.

One UI 6.1 may have introduced a fingerprint issue to the Galaxy S23

According to user reports on Reddit, the fingerprint icon occasionally does not appear on the Galaxy S23’s screen after the One UI 6.1 update. It doesn’t show up when they wake up the phone by pressing the power button or double-tapping the screen. The bigger problem is that fingerprint recognition does not work when this happens. Placing a registered finger above the scanner does nothing.

To make it work, users have to lift their fingers and wait for the icon to show up. The fingerprint scanner then worked properly. It appears to be a fairly widespread issue. We have seen reports from dozens of Galaxy S23 users on Reddit, including a Galaxy S23 FE user (the FE model has an optical scanner while the flagships have an ultrasonic scanner). SamMobile could replicate the issue on a Galaxy S23.

While this happens occasionally, it can be frustrating to users. Hopefully, Samsung has noted the issue and is working on a fix. The company has also updated the Galaxy Z Fold 5, Galaxy Z Flip 5, and Galaxy Tab S9 series to One UI 6.1 but there aren’t any reports about fingerprint issues from users of these devices. The foldables feature side-mounted capacitive scanners while the tablets have optical under-display scanners.

Reports about slow charging speeds may be misleading

Several Galaxy S23 and Galaxy Z Fold 5 users have claimed that their phones are charging slower than usual after the One UI 6.1 update. They shared screenshots from the Electron app, showing a charging speed of 15W or lower. While it isn’t unusual for major updates to contain a few bugs, it is unclear whether One UI 6.1 is the culprit here. Phones rely on various factors to dynamically adjust the charging speed.

The charging speed is usually fast when the battery level is low and gradually slows down as we reach higher levels. The readings reported by Electron may not be accurate either. SamMobile used a pluggable voltage and amperage meter to check the charging speed and found that their Galaxy S23 charges at 20W when the battery level is 47%. This suggests One UI 6.1 hasn’t slowed down the charging of Galaxy devices. We will let you know when we have more information.


[ad_2]
Source link

Google Messages could get satellite messaging, not just for emergencies

0
[ad_1]

Have you ever been in a tough situation where you urgently need to contact someone while away from home, only to discover that your phone has suddenly lost its connection? It’s a common issue that many of us have faced, and it always seems to occur at the worst possible moments.

There is light at the end of the tunnel, as manufacturers are joining forces with mobile service providers to confront this problem directly. They are leading the way in developing a new type of connectivity that relies solely on clear skies. That’s right – we’re talking about satellite connectivity.

Recent reports from 9to5Google suggest that the long-awaited satellite connectivity feature could be arriving at Google Messages soon. Contrary to initial beliefs, this feature may not limit itself to emergency situations only. If the rumors about the beta version are accurate, users might soon enjoy sending messages to their loved ones via a non-terrestrial network (NTN) connection.

Google Messages conducting satellite messaging feature
Image credit: 9to5Google

How satellite messaging feature works?

Coding in the newest edition of Google Messages provides insight into how satellite connectivity operates. To begin, you must have an unobstructed view of the sky to access the signal. However, a restriction exists—currently, users can only send text messages, meaning photos or videos are off the table. Additionally, be prepared for potentially slower transmission speeds.

On the bright side, it appears that this satellite-based messaging solution may have more capabilities beyond just casual chats. If the system reaches potential, users may access emergency services, offering vital help during emergencies.

As we look ahead, it’s clear that satellite connectivity has huge potential to enhance our mobile communication network. The technology can transmit messages in isolated or difficult terrains, revolutionizing staying connected on the move.

Satellite messaging could arrive with Android 15

The highly anticipated launch of this cutting-edge connectivity is slated to align with the debut of Android 15, pending final approval. Developers with early access to Android 15 have already seen a sneak peek of the future, including rumors of an exciting “Auto-connected to satellite” notification.

Once users connect, they can easily send and receive messages, eliminating the need for traditional mobile service.

Furthermore, there’s potential for partnerships between Google and satellite industry players like T-Mobile or Starlink. There’s still no word about that, though.


[ad_2]
Source link

Jackson County Missouri Ransomware Attack Impacts IT Systems

0
[ad_1]

Jackson County, Missouri, has become the latest victim of a ransomware attack, which has caused substantial disruptions within its Information Technology (IT) systems.

This attack has highlighted the vulnerabilities in digital infrastructures and the cascading effects such disruptions can have on public services and operations.

The first signs of the cyberattack emerged as operational inconsistencies across Jackson County’s digital infrastructure.

Specific systems were found to be inoperative, while others continued to function normally.

The affected systems are critical to the county’s daily operations, including tax payments and online services for property searches, marriage licenses, and inmate searches.

Consequently, the Assessment, Collection, and Recorder of Deeds offices at all counties have been forced to close until further notice, significantly impacting residents and county operations.

Services Unaffected

It is noteworthy that the Kansas City Board of Elections and Jackson County Board of Elections have not been impacted by this system outage.

Document
Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

This detail is crucial, especially during electoral activities, ensuring the democratic process remains uninterrupted.

Response and Actions Taken

Upon detecting the disruptions, Jackson County promptly notified law enforcement and engaged IT security contractors to assist in the investigation and remediation efforts.

The county has emphasized that the integrity of its digital network and the confidentiality of resident data remain top priorities.

To date, no evidence suggests that any data has been compromised.

The investigation is in its early stages, with cybersecurity partners working closely with the county to diagnose the issue.

While ransomware is considered a potential cause, comprehensive analyses are underway to confirm the exact nature of the disruption.

Immediate measures have been taken to secure the systems against further compromise.

The county’s IT teams are working tirelessly to restore total operational capacity to the impacted services.

Community Impact and Ongoing Efforts

The closure of critical county offices has undeniably affected residents, who rely on these services for various legal and administrative needs.

Jackson County has acknowledged the inconvenience caused by these closures and expressed appreciation for the community’s patience and understanding.

As the situation unfolds, Jackson County is committed to providing timely updates and ensuring transparency with its residents.

The focus remains on swiftly resolving the issue and implementing measures to prevent future attacks.

This incident is a stark reminder of the ever-present threat of cyberattacks and the importance of robust cybersecurity measures.

As Jackson County navigates this challenging time, the lessons learned will undoubtedly strengthen its defenses and preparedness for similar incidents in the future.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Motorola Edge 50 Pro is here with 144Hz display, 125W charging

0
[ad_1]

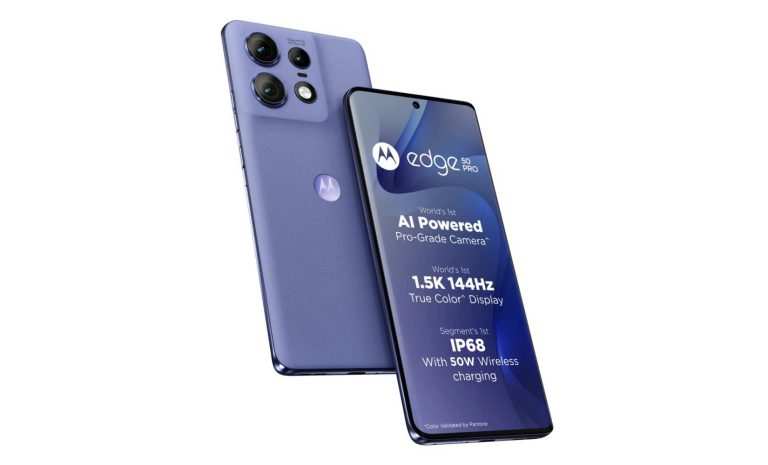
Motorola has announced a new mid-range smartphone, the Motorola Edge 50 Pro. The device was shown off during a press event in India, as expected. This handset may be a mid-ranger, but it does look very nice, and its specs are nothing to scoff at.

The Motorola Edge 50 Pro is now official, and the leaks were spot on

We’ve exclusively leaked the design of this phone a while back, and it turns out it was spot on. The Motorola Edge 50 Pro features a curved display on the front, with a centered display camera hole. The bezels around that panel are really thin.

On the back, you’ll find three cameras, which sit inside a camera island in the top-left corner of the phone. That camera island does protrude a bit, but the overall design is really nice, it blends in with the backplate.

Motorola’s logo is also visible on the back of the device, while all the physical buttons sit on the right-hand side. The phone comes with a frame made out of aluminum. Two different backplate styles are available, glass and vegan leather, it all depends on the model.

The phone includes a 144Hz display, and the Snapdragon 7 Gen 3 SoC

The device features a 6.7-inch 2712 x 1220 pOLED display with a 144Hz refresh rate. As already mentioned, this display is curved, and it has a 360Hz touch sampling rate. Its brightness goes up to 2,000 nits, and the display is protected by the Gorilla Glass 5.

The Snapdragon 7 Gen 3 fuels the Motorola Edge 50 Pro. That is Qualcomm’s mid-range chip, a 4nm processor. The phone comes in 8GB and 12GB LPDDR4X RAM variants, both of which offer 256GB of UFS 2.2 flash storage.

Motorola Edge 50 Pro image 2

125W wired charging is also supported, along with 50W wireless charging

A 4,500mAh battery sits inside of this phone, and it supports 125W wired charging. 50W wireless charging is also supported, as is 10W reverse wireless charging. It’s always nice to see wireless charging on mid-rangers, especially charging that is this fast.

A 50-megapixel main camera (f/1.4 aperture, OIS, Quad Pixel Technology) is backed by a 13-megapixel ultrawide unit (f/2.2 aperture, 120-degree FoV, macro option). The third camera on the back is a 10-megapixel telephoto unit (3x optical zoom, 50x hybrid zoom). There is also a 50-megapixel front-facing camera with Quad Pixel Technology.

Android 14 comes pre-installed on this smartphone

Android 14 comes pre-installed on the phone. The device is also IP68 certified for water and dust resistance. It supports 5G connectivity, and Bluetooth 5.4. The Motorola Edge 50 Pro measures 161.23 x 72.4 x 8.19mm, while it weighs 186 grams.

The Luxe Lavender and Black Beauty color variants have a vegan leather backplate. The Moon Light Pearl model has a smooth finish on the back, we presume it’s glass. The phone’s pricing starts at INR31,999 ($384) in India. There’s no word on its global availability.

Motorola Edge 50 Pro image 1


[ad_2]
Source link

Meta to cut off app updates for original Quest this month

0
[ad_1]

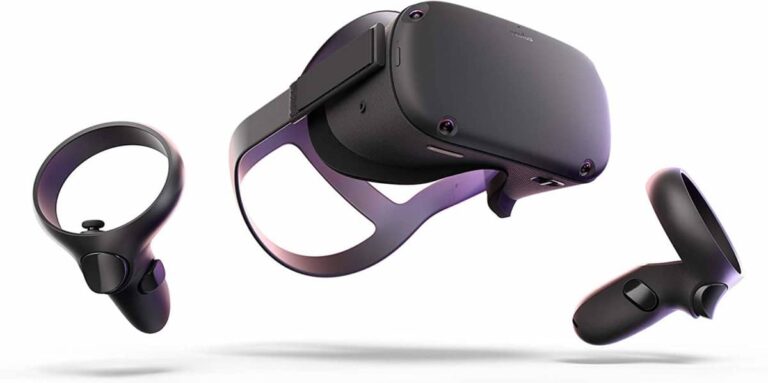
In January 2023, Meta announced its plans to wind down the original Quest. The company said the first-gen VR (virtual reality) headset will gradually lose features and stop receiving security updates in 2024. While the device remains functional, it will soon become less usable. Starting April 30, the Quest 1 will no longer support new apps and app updates.

Meta will block new apps and app updates for the original Quest

Meta (formerly Facebook) launched the first-gen Quest VR headset in early 2019 under the Oculus brand. It followed up with the Quest 2 in late 2020 and the Quest 3 late last year. Ahead of the latter’s unveiling, the company announced that it is depreciating the original model. The Quest 1 stopped receiving feature updates and lost access to Parties and Meta Horizon Home social features.

In a recent email to developers, Meta has detailed the next steps for this ongoing winding down of the original Quest. The company said it won’t accept new apps and app updates for the device from April 30, 2024. Apps submitted beyond the deadline will not appear in the Meta Store for the headset. Updates for existing apps will also be blocked, even though Quest 2 and Quest 3 users will receive those updates.

The Quest 1 will receive critical bug fixes and security patches at least until August 2024. However, users will not be able to update existing apps and download or purchase new apps. Coupled with the removal of some features last year, the original Quest is substantially less useful than it was earlier. Meta doesn’t block the sideloading of apps on the device, so there is a backdoor. However, it comes with security risks.

Meta wants you to stop using the Quest 1

Meta’s latest move suggests it does not want people to continue using the original Quest. The idea might be to drive them toward the Quest 3 or the Quest 2. The latter arrived about 18 months after the first-gen model but should get longer support. It significantly outsold the Quest 1. By early 2023, Meta had sold 20 million VR headsets, 18 million of which were the second-gen models.

The Quest 2 also sold better than the Quest 3 during the 2023 holiday season. Despite being about three years older, people likely preferred it because of the price difference. The 2020 model currently costs $200 for the base variant, while the 2023 model starts at $500. Meta might keep supporting both models for a few years until it is ready with a newer one. As for the original Quest, its time is almost up.


[ad_2]
Source link

Google Messages leak hints at satellite messaging allowing you to text anyone, anywhere

0
[ad_1]

A closer look at the latest Android 14 QPR3 Beta 2 release has got the tech world buzzing about the possibility of Android 15 bringing satellite messaging to the table. But guess what? Google Messages seems to be dropping some hints, too, suggesting that this satellite connection could be not only for messaging from anywhere but with anyone.According to 9to5Google, a trio of explanatory strings in the beta version 20240329_01_RC00 sheds some light on how satellite messaging functions in Google Messages. Reportedly, these strings read:
  • To send and receive, stay outside with a clear view of the sky
  • Satellite messaging may take longer and can’t include photos & videos
  • You can message with anyone, including emergency services

The third string hints that you won’t be restricted to just emergency services; you will be able to message “anyone” in your contacts via SMS. This could take the satellite connectivity capabilities of Android smartphones a step beyond Apple’s Emergency SOS via satellite feature, which, as the name implies, only allows you to send distress signals when you are off the grid.The smartphones with satellite connection support landscape is getting hotter as tech titans like Google, Apple, Samsung, and Huawei enter the cosmic connection race. With satellite connectivity anticipated to debut on Android phones through the release of Android 15, theoretically, all devices running on it could potentially support this feature.

Meanwhile, Huawei has already dived into the realm with its Mate 50 series, enabling you to make calls and send satellite messages even when you are not linked to cellular or Wi-Fi networks. However, there is a catch – it’s currently limited to China.

Unlike traditional smartphones, those equipped with satellite connection support break free from reliance on cell towers. Instead, they directly connect with satellites orbiting the Earth. When you make a call or send a message, the signal travels from your phone to the nearest satellite and then bounces to a ground station on the network before reaching its final destination. This setup guarantees connectivity even in remote areas without cellular coverage.

As we get closer to the rumored reveal of Android 15, possibly happening at Google’s annual I/O conference on May 14, you can bet more leaks will start popping up. Keep your eyes peeled for updates!

[ad_2]
Source link