After a months-long unexplained delay, a new Google Play System Update (GPSU) is finally rolling out to Samsung Galaxy smartphones. The devices, including the Galaxy S24 series, are picking up the January 2024 GPSU. They have been stuck on the July 2023 release for so long.
The Galaxy S24 and other Samsung devices get a new Play System Update
Google pushes monthly Play System Updates to Android smartphones and tablets. These are updates for underlying system services that make the core of Android. New releases are installed automatically behind the scenes, though users can manually check for them. Unlike major Android updates and security patches, Google has complete control over Play System Updates.
However, for the past several months, most Samsung phones haven’t received a new GPSU. They last picked up one in July 2023. The issue affected flagships, foldables, and mid-range devices alike. It was unclear whether there was a problem with Galaxy products that blocked their access to new releases or Google held back the updates for some undisclosed reason.
Even the Galaxy S24 series, which debuted last month, arrived with the July 2023 GPSU. Neither Google nor Samsung came forward to tell what was going on. Thankfully, whoever was at fault has addressed the problem. A new Google Play System Update is now rolling out to the likes of the Galaxy S24 and other models. It isn’t the latest release—the February GPSU is already available for Pixels—but a fairly recent one.
As reported by Android expert Mishaal Rahman, the January and February 2024 GPSUs don’t bring any “interesting changes.” However, he says the March 2024 release will have “a pretty significant” changelog. The source didn’t go into details but it shouldn’t be long before we get to know more. There is only one day remaining in February, so a new GPSU is on the horizon.
Check for updates on your Samsung devices
If your Samsung Galaxy is also stuck on the July 2023 Play System Update, the January 2024 release should reach you soon. You can check for it manually from the Settings app. Scroll down to the About phone section, tap on Software information, and then on Google Play system update. Your phone will now check for a new GPSU.
If available, you will be prompted to download it. But if you still don’t see an update, fret not. It should be available in a few days. You can repeat these steps to check for Google Play System Updates anytime. These updates usually aren’t big, though you might still need to restart the phone to complete the installation.
Right now, many people fear the march of generative AI technology becoming more powerful. It proves to be a major threat to the journalism industry, and Google’s new tool only strengthens our fear of it. Google was testing a tool called Genesis via a new program, and this tool allows people to generate news articles using AI.
Speaking of AI technology, Google’s CEO has finally spoken out about the recent drama with Gemini’s image generator. Gemini has been generating pictures inaccurately depicting people’s race and gender. He said that this is “completely unacceptable.” He also stated that the company is making progress to fix it.
Google is testing Genesis via a new program
According to reports, Google is in the process of training Genesis for a public release. As such, the company is contacting news outlets to potentially use the tool. At this point, we’re not certain which outlets the company contacted. However, we know that it’s focusing on smaller publications.
In order to use the tool, publications have to agree to a minimum number of articles being posted. Google wants the publications to post at least three news articles a day using the AI tool. Also, they need to post at least one newsletter and one marketing campaign every month using the AI tool. That’s definitely a doable task.
Google isn’t just asking favors here, as the company is offering money to these companies to use the tool. We don’t know the specific amounts. However, reports say that Google is offering five-figure sums. So, the company is paying publications between $10,000 and $99,999. We’re pretty sure that the publications will receive this money over the course of the agreed-upon 12-month period.
At this point, there’s still a lot of information that we don’t know. Since this is a platform dedicated to making news articles, we can expect it to be optimized for news. It will do a better job than if a person simply went to ChatGPT or Gemini and asked it to write an article. Also, Google says that the articles will still need human intervention. So, it will still need to be a human Editor to make sure that everything is in check.
Regardless, there are still some issues with this
Firstly, Google says that the Genesis program does not want to replace human journalists. However, it’s blatantly obvious that this tool gives publications more reason to forgo human workers. Articles can be produced quickly with very little effort. So, why hire human writers when articles can be produced at lightning speed?
Also, the company is targeting smaller news publications, which will present a major barrier to entry for potential journalists. Smaller news publications are where many journalists get their start. Well, if you are a smaller news company, and you’re not quite pulling in the big bucks like The Verge or CNET, the last thing you’re focusing on is hiring full-time journalists.
Providing smaller news organizations with AI tools that eliminate the need for human writers could make it less likely that potential journalists will be able to get their start there. However, that’s only speculation at this point.
Right now, we don’t know the potential risks of this tool. So, we are just going to have to wait and see what happens.
To raise awareness of the ALPHV Blackcat ransomware as a service (RaaS) that targets the US healthcare industry, the FBI, CISA, and the Department of Health and Human Services (HHS) have collaborated to release a joint Cybersecurity Advisory (CSA).
To get initial access to the victim’s device, the BlackCat/ALPHV ransomware uses previously compromised credentials.
The malware compromises Active Directory administrator and user accounts as soon as it has access.
“Since mid-December 2023, of the nearly 70 leaked victims, the healthcare sector has been the most commonly victimized”, reads the joint advisory.
You can analyze a malware file, network, module, and registry activity with the ANY.RUN malware sandbox, and the Threat Intelligence Lookup that will let you interact with the OS directly from the browser.
“This is likely in response to the ALPHV Blackcat administrator’s post encouraging its affiliates to target hospitals after operational action against the group and its infrastructure in early December 2023”.
ALPHV Blackcat Attack Techniques
ALPHV Blackcat affiliates obtain initial access to a company through sophisticated social engineering methods and open-source investigation.
Actors utilize phone calls or SMS messages to gain credentials from staff members to enter the target network, posing as business IT and helpdesk employees.
ALPHV Blackcat affiliates use uniform resource locators (URLs) to communicate with victims via live chat, making demands and restoring the encrypted files.
ALPHV Blackcat affiliates use remote access tools like AnyDesk, Mega sync, and Splashtop to prepare for data exfiltration after they get access to a victim network.
Affiliates of ALPHV Blackcat establish a user account called “aadmin” and utilize Kerberos token generation to get access to domains.
Once inside networks, they employ tools like Plink and Ngrok, authorized remote access and tunneling tools.
ALPHV Blackcat affiliates get multi-factor authentication (MFA) credentials, login credentials, and session cookies using the open-source Evilginx2 adversary-in-the-middle attack framework.
The ransomware is then deployed, with the ransom note embedded as a file.txt.
Ransom Note
The finding comes after CISA warned last week that there had been active exploitation in the wild of a critical-severity authentication bypass vulnerability in ConnectWise ScreenConnect (CVE-2024-1709).
The co-founder of RedSense, Yelisey Bohuslavskiy, has connected the compromised state of Change Healthcare to the ScreenConnect vulnerability.
This advisory contains updates to the FBI’s FLASH BlackCat/ALPHV ransomware indicators of compromise for April 2022 and December 2023.
A ScreenConnect remote access domain is one of the additional indications of the compromise included.
ScreenConnect remote access domain
The FBI, CISA, and HHS advise software manufacturers to increase their clients’ security postures by limiting the impact of ransomware techniques by using secure-by-design concepts and strategies in software development practices.
It is imperative that “critical infrastructure organizations” implement the guidelines into practice to lessen the probability and consequences of data extortion incidents and the ALPHV Blackcat ransomware.
You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.
Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.
It was just a little over a year ago that the Rhadamanthys stealer was first publicly seen distributed via malicious ads. Throughout 2023, we observed a continuation in malvertising chains related to software downloads.
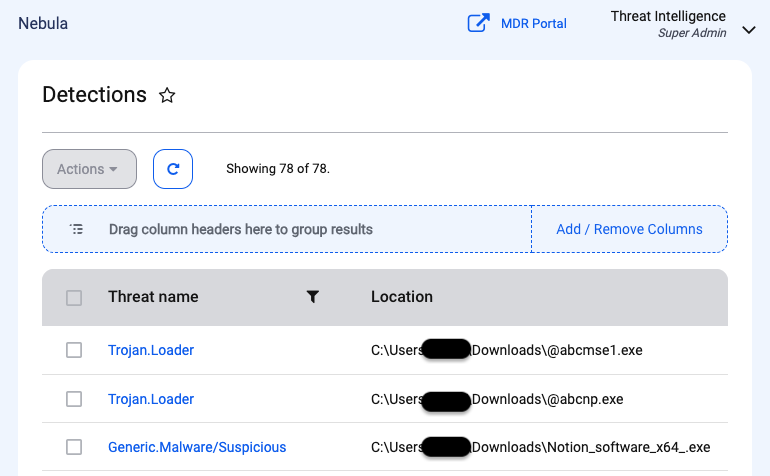
Fast forward to 2024 and the same malvertising campaigns are still going on. After a lull last summer, we noticed an increase since the fall which so far has been sustained. The most recent targeted searches are for Parsec and FreeCad, followed by WinSCP, Advanced IP Scanner, Slack and Notion.
Threat actors are targeting business users with payloads such as FakeBat, Nitrogen or Hijackloader. One other malware family we have seen here and there is Rhadamanthys. In this blog post, we detail the latest distribution chain related to this malware.
Key points
Rhadamanthys is an infostealer distributed via malspam and malvertising.
Google searches for popular software such as Notion return malicious ads.
Threat actors are using decoy websites to trick users into downloading malware.
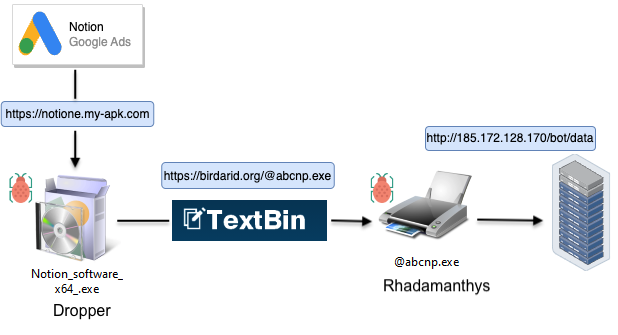
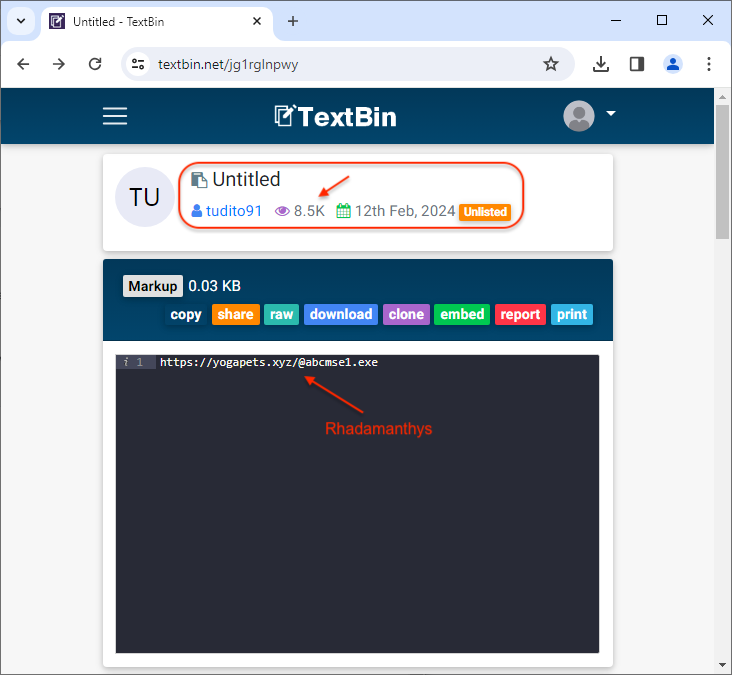
The initial payload is a dropper that retrieves Rhadamanthys via a URL pasted online.
The TexBin paste site shows the URL was seen/accessed 8.5K times.
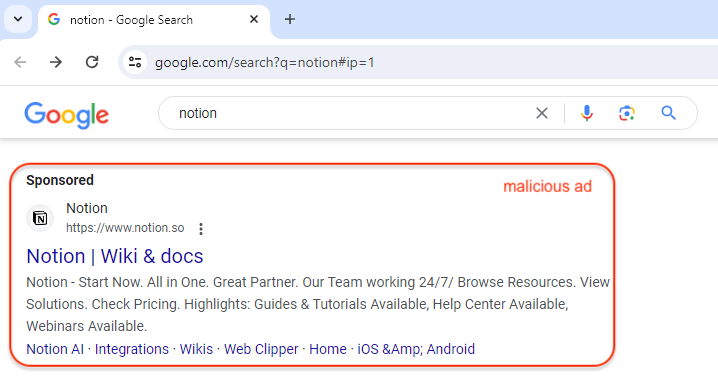
Malicious ad
Threat actors continue to impersonate well-known brands via sponsored search results. As can be seen below in a search for Notion (productivity software), an extremely deceiving ad is shown. Because it includes the official logo and website for Notion, most users will not think twice and click on the link.
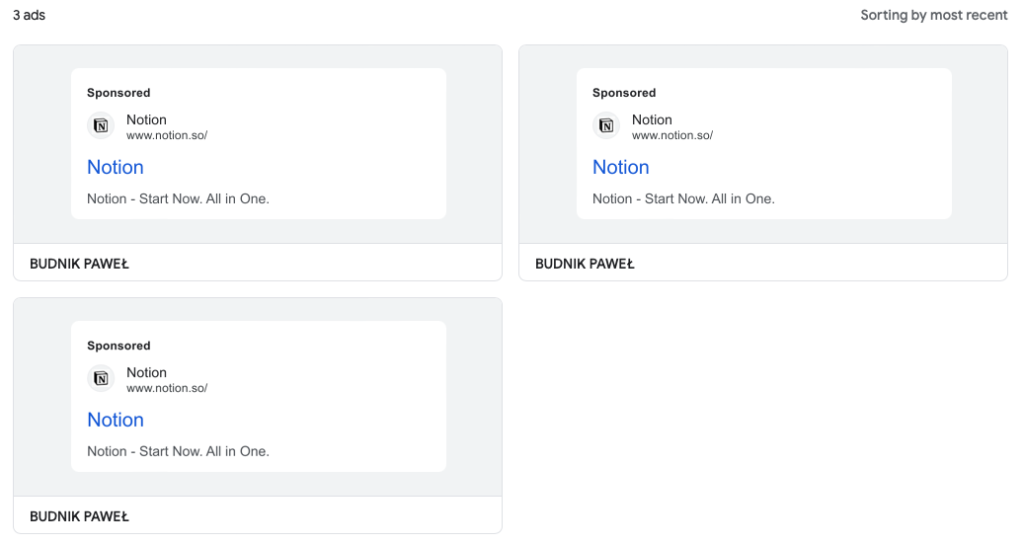
While the ad looks real on the surface, the Google Ads Transparency Center page (which can be accessed by clicking on the menu right next to the ad’s URL) shows this ad was created by a certain ‘BUDNIK PAWEŁ’ from Poland. According to the same report, the first ad first appeared on January 23, 2024.
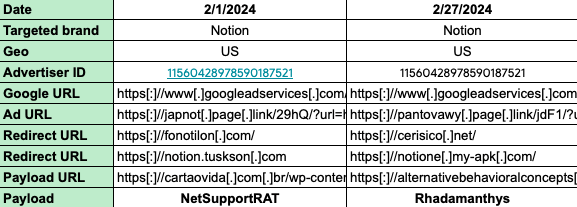
As a matter of fact, we have been tracking this fraudulent advertiser for a few weeks and had reported it to Google in early February, when we first ran into it. At the time, victims who clicked the ad and visited the site were tricked with a download for NetSupport RAT.
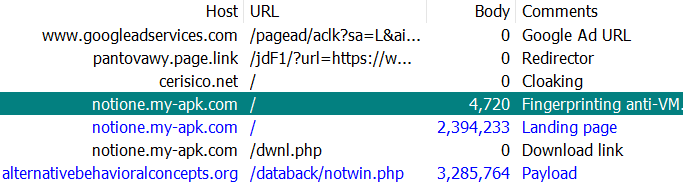
In this more recent campaign, the threat actor is pushing Rhadamanthys as the final payload, after an initial dropper. In the web traffic seen below, we can see that the threat actor uses a number of redirects to evade detection. URL shorteners and redirectors are quite common for the initial ad click, often followed by an attacker-controlled domain responsible for cloaking traffic.
There is one more check within the browser via JavaScript to detect virtual machines before the actual landing page is displayed to the victim.
Landing page and payload
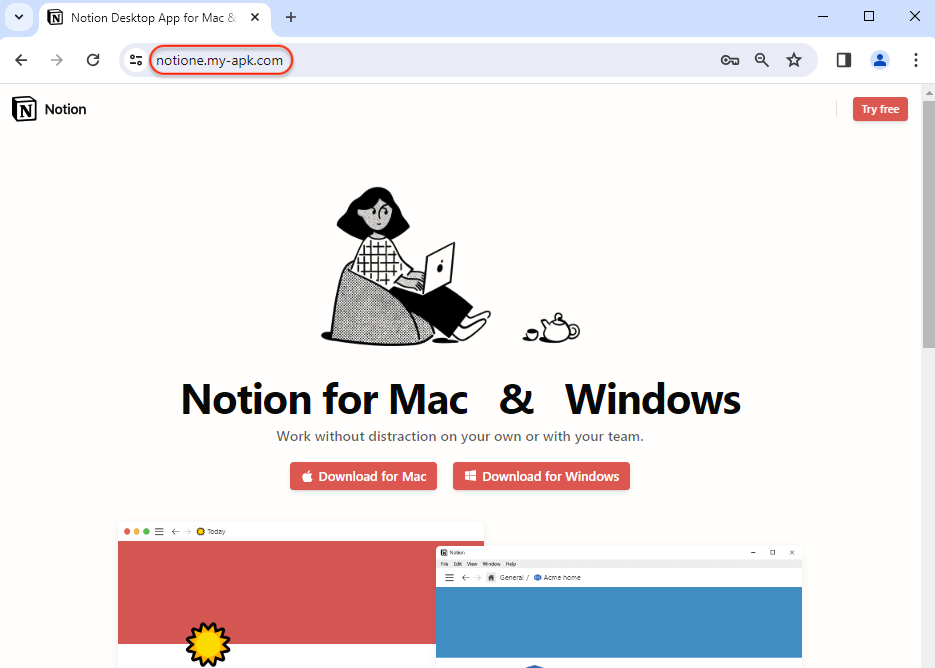
The landing page is the decoy site that victims will see after they click on the ad. Apart from the URL in the address bar, it looks very similar to the official web site for Notion, although somewhat simplified. There are two download buttons, one for Mac and the other for Windows.
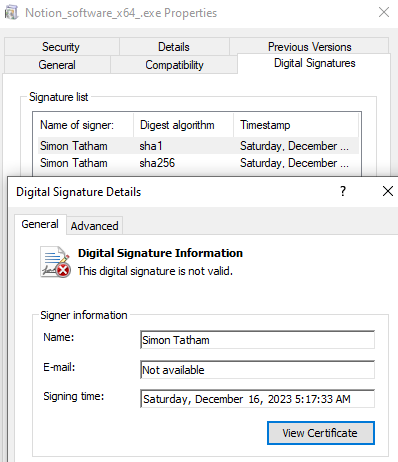
The Windows binary is a signed file but its digital signature is not valid. The name of the signer that shows here is from the inventor of PuTTY, a popular admin tool. This digital certificate is likely fake or was revoked, but it may evade detection in some cases.
This dropper contacts the paste site TextBin where it retrieves a URL for the followup payload, Rhadamanthys. If the numbers are correct this unlisted paste was viewed 8.5k times already.
Rhadamanthys attempts to steal credentials stored in applications such as PuTTY, WinSCP and mail programs (screenshot from Joe Sandbox):
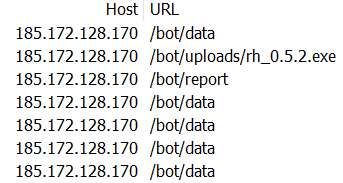
Upon execution, Rhadamanthys reports to its command and control server, sends and receives data.
Conclusion
Not a lot has changed with malvertising campaigns focused on software downloads as we enter the second year of actively tracking them. Sponsored search results continue to be highly misleading due to the fact that any verified individual is able to impersonate popular brands by using their logo and official site within the ad itself.
We are aware of reports shared within private circles, that businesses were compromised after an employee clicked on a malicious ad. Follow-up activities post infection include the usual ‘pentesting tools’ that precede a company-wide breach or ransomware deployment.
The infrastructure used in this particular attack was reported to the relevant parties. Malwarebytes and ThreatDown customers are protected against the payloads and distribution sites.
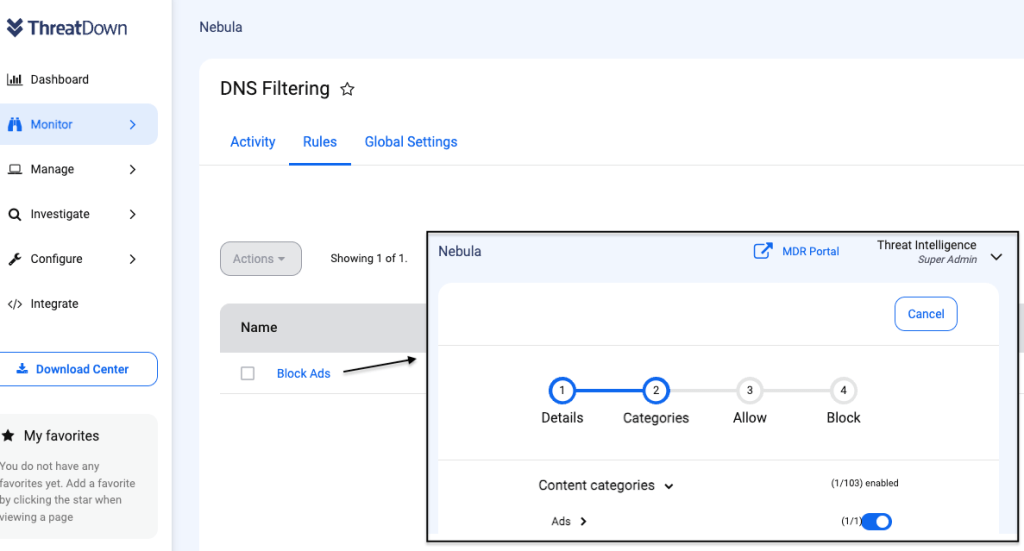
Additionally, EDR customers who have DNS Filtering can proactively block online ads by enabling the rule for advertisements. This is a simple, and yet powerful way to prevent malvertising across an entire organization or in specific areas.
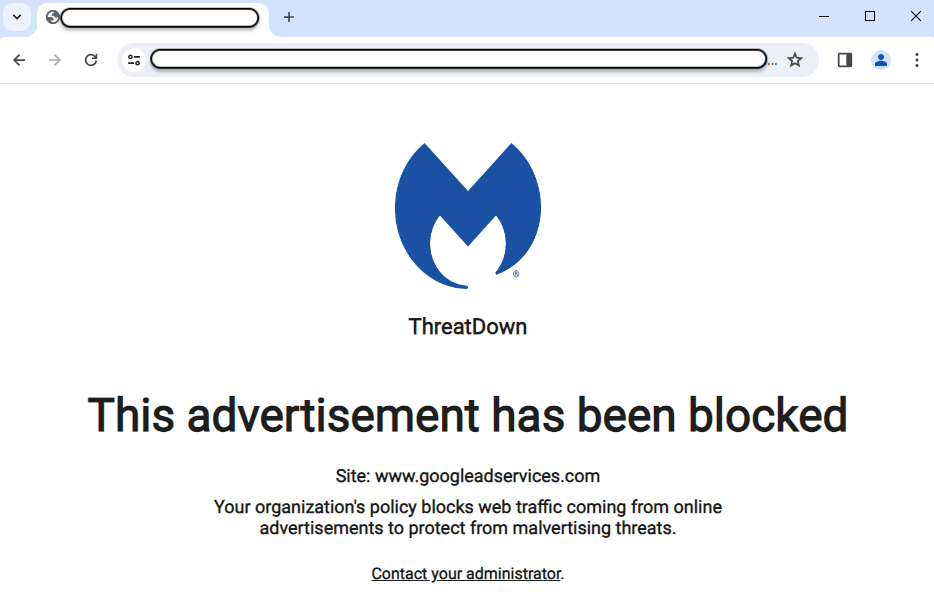
Endpoint users will see a customizable message when they click on an ad such as those that appear on a search engine results page:
Back in January, we shared the Samsung Galaxy A35 renders with you, exclusively. Now we’re partnering with @OnLeaks to do the same with the Galaxy A35 specifications. This is one of Samsung’s upcoming Galaxy A series devices, and it’s expected to launch alongside the Galaxy A55.
Here are the Samsung Galaxy A35 specifications, in detail
The Galaxy A35 will be inferior to the Galaxy A55, it will be fueled by the Samsung Exynos 1380 processor. In addition to that, you’ll be able to choose between 6GB and 8GB of RAM. Those two RAM models will come with 128GB and 256GB of internal storage, respectively. The good news is, you’ll be able to expand the phone’s storage. The Galaxy A35 will accept a microSD card with up to 1TB of storage.
On the front of the phone, you’ll find a 6.6-inch fullHD+ (2380 x 1080) Super AMOLED display. Its refresh rate will be 120Hz, so double what the iPhone 15 offers, despite the fact this phone will be a fraction of the price. It’s always nice to see 120Hz panels on budget phones. That display will be flat, by the way.
Moving onto the battery. The Galaxy A35 will include a 5,000mAh battery and supports 25W wired charging. That seems to be a solid battery life considering the display and SoC on the phone.
The phone will include three cameras on the back
The Galaxy A35 will feature three cameras on the back and a single one on the front. A 50-megapixel main camera (f/1.8 aperture) will be backed by an 8-megapixel ultrawide unit (f/2.2 aperture). The third camera on the back will be a 5-megapixel macro (f/2.4 aperture) unit.
The phone will have a centered display camera hole on the front, and a 13-megapixel unit (f/2.2 aperture) in there. This handset will be IP67 certified for water and dust resistance as well.
We still don’t have the information about the Android version that’ll come pre-installed, but it’ll almost certainly be Android 14 with One UI 6.1 on top of it. It’s hard to imagine Samsung launching the Galaxy A35 with Android 13 at this point in time.
it’s coming in four colors, and the pricing will start at €379
If you’re wondering about its measurements, we have that info too. The Samsung Galaxy A35 will measure 161.7 x 78 x 8.2mm, while it will weigh 209 grams.
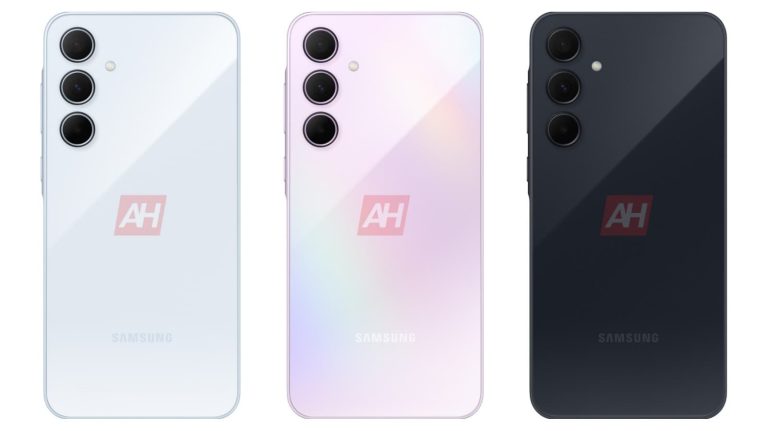
The device comes in four ‘Awesome’ color variants. Those colors are Awesome Ice Blue, Awesome Lemon, Awesome Lilac, and Awesome Navy. The 6GB RAM model will cost €379 in Europe, while the 8GB RAM variant will set you back €449.
What about its design?
The Samsung Galaxy A35 will feature be flat all around. It will feature a flat display and a flat backplate. On top of that, its frame will be flat all around. The corners of the phone will be rounded, though.
The only thing that will break the flatness of its backplate are the phone’s cameras. It will include three of them, as already mentioned, and they will be located in the top-left corner of the phone’s back. Those cameras will be vertically aligned. Each one of them will protrude from the backplate on their own, there won’t be a dedicated camera island or anything like that.
An LED flash will sit between the first and second cameras, but a bit to the side, closer to the center, as you can see in the image above. Samsung’s logo will be placed in its usual place, centered towards the bottom of the back side. We’re still not sure if Samsung will use plastic or glass on the back of the phone, but we’re hoping for glass.
The frame around the phone will be flat, as already mentioned, but it will also curve a bit towards the edges. Why? Well, for comfort. The power/lock button and volume up and down keys will also sit on the right-hand side. The power/lock button will be located below the volume rocker buttons.
When will the Samsung Galaxy A35 launch?
What we know now is that the Galaxy A35 will launch alongside the Galaxy A55. These will be the company’s new budget/mid-range Galaxy A phones for 2024. What we do not know is when exactly will they arrive. Considering how much detail already surfaced, we cannot imagine the launch being far off at this point.
Let’s try and guess, shall we? The Samsung Galaxy A34 and Galaxy A54 arrived back in mid-March last year. If we had to guess, we’d say that the same will happen with the Galaxy A35 and Galaxy A55, but this year. A mid-March launch timeframe is quite probable, though Samsung could move it a week or two. Let’s wait and see.
YouTube’s picture-in-picture mode was released in 2017 when Google introduced the Android Oreo version. At the time, the PIP feature was available for just those with a subscription to the YouTube Red premium service. However, in 2022, the company started allowing free users to access the PIP feature, but only in the US.
But this could be changing soon as multiple Redditors across Europe without YouTube premium subscriptions can access the PIP mode for free.
YouTube’s picture-in-picture mode is reportedly available for some users for free in Europe
Multiple Reddit users have reported that they can access YouTube’s picture-in-picture mode for free without a premium subscription to the service. Multiple Reddit threads are talking about the availability of the PIP mode for free on non-premium accounts. YouTube may be currently testing the free feature only in European countries like Germany and Romania.
It’s worth noting that Redditors who have access to YouTube’s picture-in-picture feature for free can’t play every video in this mode. One user wrote that some of the restricted videos open in the PIP mode, but the app closes and stops the video.
Another user claims that in addition to music videos, free users can’t play some videos that have copyrighted content. There’s a possibility that most of the videos will be accessible in the PIP mode after the testing period is over.
Support pages continue to mention that PIP mode still requires a premium subscription outside the US
Notably, the YouTube support pages continue to mention that picture-in-picture mode still requires a premium subscription outside the USA. In addition, YouTube’s account on X also said that premium subscriptions are required to access PIP outside the US.
So, it’s advisable to take this news with some skepticism. It could be an error from YouTube’s side to offer free PIP mode to the non-premium users in Europe. We hope it’s not an error and the feature will be available for free across the globe in the future.
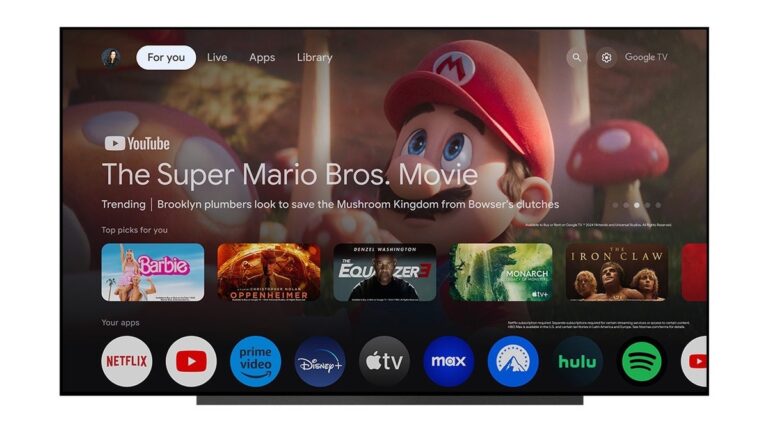
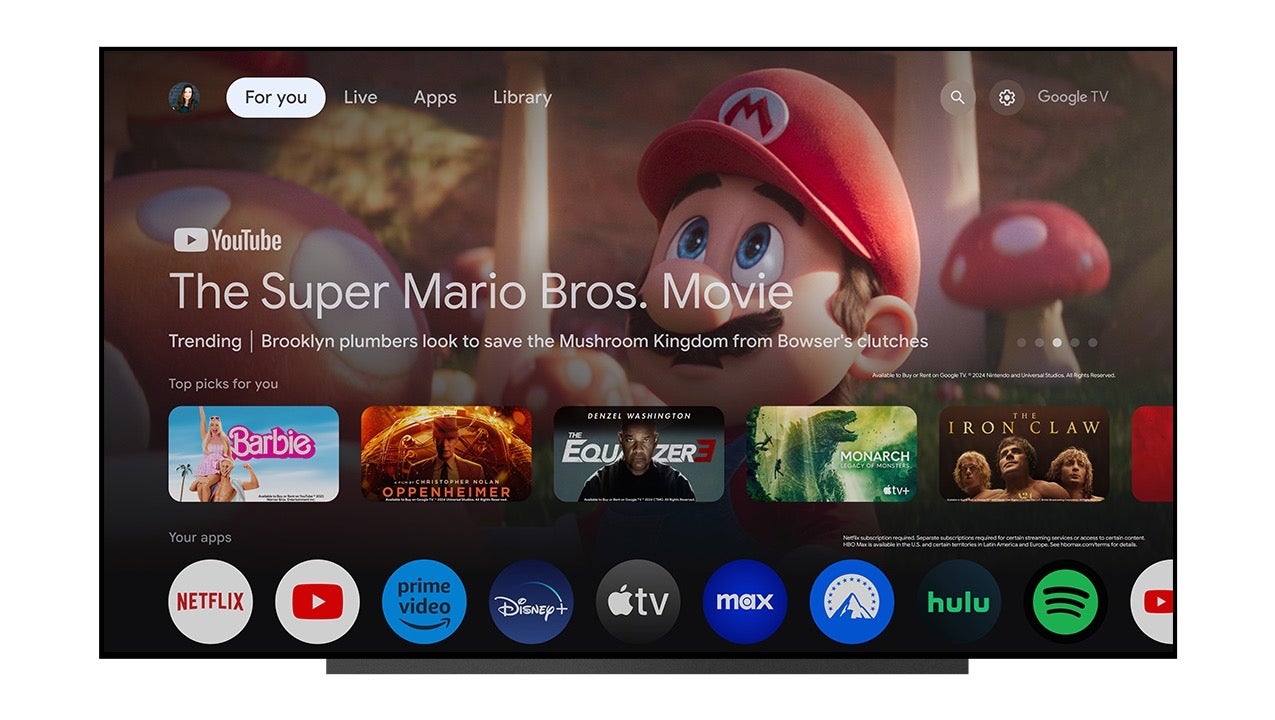
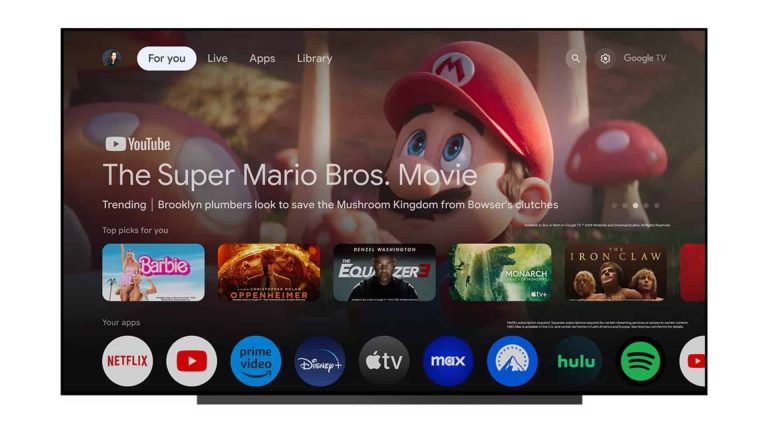
Google TV is once again getting a design tweak. Following the addition of new landing pages last year aimed at simplifying navigation, the “For you” screen is now tackling the “Your apps” row, introducing several updates to make navigation easier and your overall viewing experience more enjoyable.
Circular and modern app icons
The app icons on your Google TV are sporting a brand new look, with the old squares and rectangles gone and circular app icons replacing them. This change aims to give your home screen a more modern feel while also making it easier to locate your favorite applications.
Faster access to free TV channels
The update also adds a new shortcut that gives you direct access to free TV channels on Google TV. The platform added over 800 new fully-integrated free channels last year that included hit TV shows, game shows, music channels, various entertainment shows, and more — all without needing to download additional apps or pay for a subscription.
Now, you’ll have yet another way to access these channels, without having to click away from the “For you” section. A new shortcut to free channels will now be added to the “Your apps” row for your convenience.
Fit more apps at a glance
Now that the app icons will be circular, they will take up less space. This opened the door for Google TV to expand the number of app icons visible in the “Your apps” row. You can now quickly jump into more of your most-used apps without unnecessary scrolling.
Customize your app experience
You have always been able to rearrange the order of your apps, however, the process wasn’t exactly very user-friendly. Now, Google TV will feature “reorder” and “add app” buttons at the end of the “Your apps” row. This will allow you to take control of your app layout by moving your favorites to the front and seamlessly discovering and installing new apps to enhance your entertainment setup.These updates are rolling out over the next few months, so keep an eye on your Google TV screen for the transformation. With a sleeker design, easier access to content, and more user control, Google TV is continuously getting better at putting your entertainment experience first.
Over the years, several reports associated with cybercriminals have been based in Russia and Western countries.
This is due to the fact that many sophisticated cyber attacks and data leaks originate from these regions.
Though this is the case, there has been major blindness towards the growing threat actor community from China.
The Chinese underground hackers have made it to the media several times, but they have built a major place in Telegram and Twitter for illegally advertising large amounts of PII data that were obtained through several Tactics, techniques, and procedures involving data exfiltration.
However, there were also other methods, such as malicious software development kits (SDKs), deep packet inspection (DPI), penetration services, insider access underpinned by formal contracts, and counterfeit mobile applications.
According to the reports shared with Cyber Security News, the value of black market data in Chinese media outlets is estimated to be between 100 and 150 billion yuan.
Although this is not officially confirmed, it is still important to understand the difference between the data leak publishing of Western Cybercriminals and Chinese-speaking cybercriminals.
Telegram social media has paved the way for Chinese hackers to bypass surveillance from their country.
They were also found to be using proxy or VPN services to connect to the Telegram messaging app.
Moreover, they also have a separate way of offering and advertising their services using Chinese colloquialisms.
Leaked data on Telegram with Chinese Colloquialism words (Source: Spy Clouds)
Data: Leaks And Exfiltration
The Data leak advertisements from these Chinese Telegram channels have been observed to follow a specific structure that obfuscates victim names to maintain access to the entity without intervention from Law enforcement.
As a workaround, they specify the sector that the victim is associated with. When these threat actors receive customer requests, they attempt to exfiltrate the real-time with the most accurate data for offering “High Value.”
Twitter Advertisement (Source: Spy Cloud)
In case data exfiltration is impossible, they attempt it via SMS or DPI methods.
The threat actors have also claimed to have login access to the applications or websites that they are exfiltrating, which makes them the controllers of the data exfiltration and selling.
These Chinese cybercriminals employed several methods for gathering personally identifiable data from victims, which include SMS hijacking, Smishing, Software Development Kits, and Penetration Testing tools.
Furthermore, these Chinese cybercriminals have also been found to be selling CVV/POS financial data as part of their data leaks.
In addition, they also created their own repositories of leaked PII named “Social Work Libraries.”
Once a particular data has been sold, these Chinese actors wait for some time and upload the same to this repository.
However, these threat actors were not linked with Chinese APT actors.
You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.
Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.
Google TV is rolling out a new homescreen redesign, featuring circular icon shapes for apps and a host of other enhancements. Announced via Google’s support forum, this update brings significant changes to the user interface. The circular icons are smaller than their rectangular predecessors and allow more apps to be displayed simultaneously. Not to mention, it enhances user accessibility and navigation.
The “Your apps” row now features “reorder” and “add apps” buttons
One of the standout improvements is the revamped “Your apps” row. With a dedicated button for app reordering, users can easily customize the arrangement of their apps without navigating through multiple menus. Additionally, the introduction of an “add apps” button simplifies the process of installing new applications, streamlining the user experience further. These enhancements aim to streamline app management and improve overall usability.
Furthermore, Google is introducing a new shortcut to free live TV channels within the “Your apps” row. This feature provides easy access to a variety of content, including local news, movies, and sports, without requiring additional downloads or subscriptions. By integrating free TV channels directly into the homescreen, Google TV enhances content discovery and accessibility for users.
Google TV expands the “Your apps” row to accommodate more apps
In response to user feedback and evolving preferences, Google has expanded the “Your apps” row to accommodate more app icons. It ensures that users have quick access to their most-used apps, optimizing efficiency and productivity. With an emphasis on user-centric design, Google aims to provide a seamless and intuitive experience for its users.
By prioritizing user feedback and addressing user needs, Google TV strives to enhance the overall viewing experience and elevate its platform’s usability. As the redesign begins its rollout starting today, users can expect to see these updates gradually implemented across all devices “over the next few months”.
In short, Google’s homescreen redesign for Google TV represents a significant step forward in enhancing user experience and accessibility. With circular app icons, improved app management features, and easier access to free live TV channels, the redesign aims to streamline navigation and provide users with a more personalized viewing experience.
Apple has decided to cancel its electric car plans, the project is dead
Many people expected Apple to join the electric car fold, and thus compete with Tesla, primarily in the US. That won’t be happening. Apple is shifting some of the employees who were working on that project to Generative AI teams, as it’s shifting focus.
Bloomberg reports that the program employed thousands of employees. The thing is, it never fit with Apple’s core business of electronics and online services. That could be one of the reasons why Apple gave up on it.
The news regarding Apple’s electric car first surfaced way back in 2014. Since then we haven’t heard much about it, but Apple was working on it. The company probably came far since then, so it’s a bit odd it’s ditching its efforts now, but there you go. Mark Gurman is almost never wrong when it comes to Apple news.
CarPlay could be one of the reasons for Apple’s decision
Another reason for the demise of this project could be CarPlay. Many car companies use Apple’s CarPlay software in their cars. Apple actually says that it’s used in 80% of new vehicles. That gives Apple a piece of the pie without the need to actually manufacture a vehicle.
Xiaomi announced its very first electric car not long ago. The company even brought it over to MWC 2024 in Barcelona. The name of that car is the Xiaomi SU7, and it seems to be a compelling vehicle.
We were all expecting Apple to enter the game at some point, but that won’t be happening, it seems. Just to be clear, the company still hasn’t confirmed anything, so… keep that in mind.