Google Photos adding option to tailor your memories based on your activity

0

[ad_1]

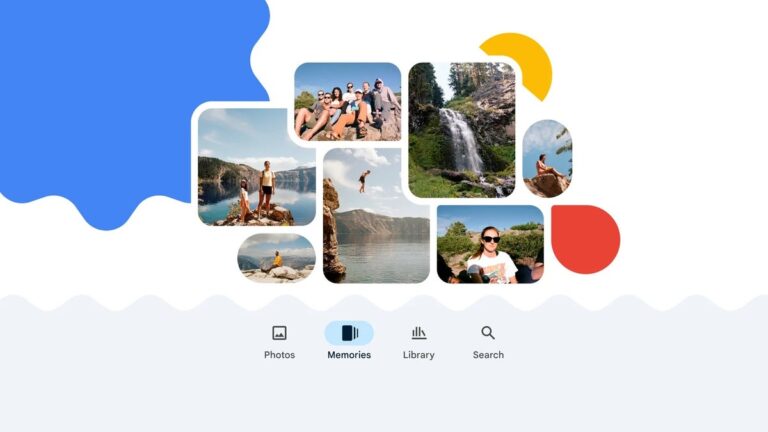
Google Photos is adding another feature intended to make your cherished memories more easily accessible and enjoyable. In addition to the recently expanded rollout of automatic Stacks (which organize similar photos together), Google has unveiled a new setting called “Activity-based personalization.” This powerful feature enhances the app’s “Memories” section.

What is activity-based personalization?

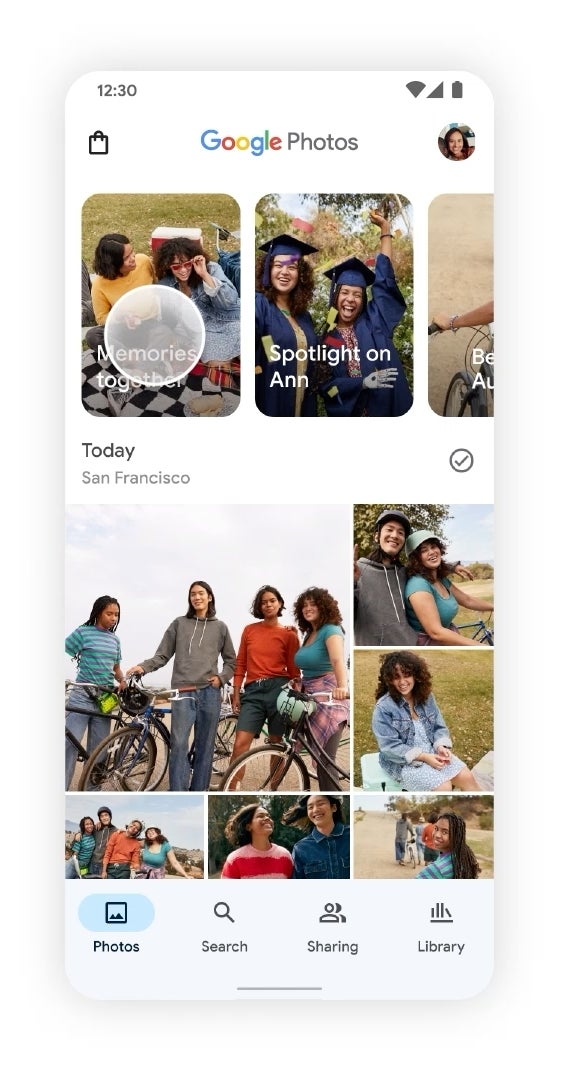
The “Memories” section, which you might recognize as that carousel of photos and videos at the top of the Google Photos app, can now be set to learn from your actions within it. Activity-based personalization learns about the way you engage with Memories — those you linger on and those you may skip — and uses that information to make them more relevant.According to 9to5Google, activity-based personalization is by default enabled, ensuring that you get the most out of Memories right away. However, you can easily disable this setting at any time. If you do, data about your Memories interactions from the last 18 months will be deleted. Don’t worry, though; this won’t affect your photo library, other Memories, or the Creations that Google Photos generates.

Memories carousel inside of the Google Photos app | Image credit: Google

How to activate or deactivate activity-based personalization

For now, it appears that setting can only be accessed from the web version of Google Photos, although it isn’t appearing for everyone yet. That said, the Memories carousel is present on both the web and mobile (Android and iOS) versions of the app, so whatever setting you choose for it will affect your experience throughout.

To check if the feature has rolled out to you and to tweak it, you’ll need to head to photos.google.com on your computer, then click on “Settings” at the top right of the page. From there, you’ll need to scroll down to the “Memories” sub-section to find the “Activity-based personalization” toggle, which should be grouped with the “Time-based memories” and “Themed memories” toggles for featured memories.

Google Photos is a great app for backing up and enjoying photos and videos, and this new feature joins a range of options already available to personalize your experience. It’s great to see that the app continues to get better and offer more options to those who choose it as the keeper of their previous memories.

[ad_2]

Source link

Hackers Using Weaponized PDF Files To Kickstart Infection Chain

0

[ad_1]

Threat actors use weaponized PDF files for initial infection. This is because they can be embedded with malicious code, PDF readers’ vulnerabilities are exploited, and users are tricked into activating the payload.

Since they are common trusted file types, PDFs have also become an effective vehicle for delivering malware that initiates the infection chain.

Cybersecurity researchers at Zscaler’s ThreatLabz discovered that hackers actively use weaponized PDF files to kickstart the infection chain.

Weaponized PDF Files

Experts detailed a new backdoor called ‘WINELOADER’ in this report. It is likely a nation-state actor that was found to be targeting Indian-European diplomatic ties.

Threat actors executed this low-volume attack with advanced tactics. Although unnamed, analysts dubbed them SPIKEDWINE due to wine-themed elements in the attack chain.

Multi-stage attack chain of WINELOADER (Source – Zscaler)

The PDF is a fake invite to a wine event at the Indian ambassador’s place on Feb 2, 2024, mimicking the official language. 

It links to a fake survey, starting the infection process and leading to the following compromised site:-

  • hxxps://seeceafcleaners[.]co[.]uk/wine.php

The PDF’s metadata shows it was made using LibreOffice 6.4 on Jan 29, 2024, at 10:38 AM UTC.

Fake PDF invitation (Source – Zscaler)

The HTA file runs obscured JavaScript for the next malicious stage using obfuscation, similar to obfuscator.io. 

Besides this, it disguises with decoy content mirroring the fake wine-tasting details from the original PDF file.

Here below, we have mentioned the key functions of the HTA file:-

  • Download Base64 encoded text file from URL: seeceafcleaners[.]co[.]uk/cert.php
  • Save to: C:\Windows\Tasks\text.txt
  • Use certutil.exe to decode the text file:
  • Command: certutil -decode C:\Windows\Tasks\text.txt C:\Windows\Tasks\text.zip
  • Extract ZIP archive contents:
  • Command: tar -xf C:\Windows\Tasks\text.zip -C C:\Windows\Tasks\
  • Execute sqlwriter.exe:
  • Path: C:\Windows\Tasks\

Executing SQLwriter.exe loads a rogue vcruntime140.dll via DLL side-loading that decrypts the WINELOADER using a hardcoded 256-byte RC4 key. 

WINELOADER uses encryption for core modules, strings, and C2 data to decrypt and re-encrypt certain strings dynamically. 

The DLL hollowing injects WINELOADER into a randomly chosen Windows DLL by employing SECFORCE’s method with added randomization for diverse DLL selection.

WINELOADER is not injected into the following DLLs:-

  • advapi32.dll
  • api-ms-win-crt-math-l1-1-0.dll
  • api-ms-win-crt-stdio-l1-1-0.dll
  • bcryptprimitives.dll
  • iphlpapi.dll
  • kernel32.dll
  • kernelbase.dll
  • mscoree.dll
  • ntdll.dll
  • ole32.dll
  • rpcrt4.dll
  • shlwapi.dll
  • user32.dll
  • wininet.dll

WINELOADER re-injects into another DLL via DLL hollowing before its first beacon to the C2 server. The beacon, a unique HTTP GET request, uses a fixed User-Agent. 

The body is encrypted with a 256-byte RC4 key, and the core commands include module execution, DLL injection, and beacon interval update. 

The persistence module installs tasks and registry keys that notify the C2 upon completion. The compromised infrastructure was used throughout the attack. 

Meanwhile, the C2 server selectively responds by preventing the automated analysis.

However, the complete tactics indicate interest in exploiting Indo-European relations, evading memory forensics and URL scanning.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link

HONOR has a 3-year plan to increase global market share considerably

0

[ad_1]

HONOR has been doing great for years now. The is doing great in both China and Europe, and it’s planning to continue growing. HONOR actually has a 3-year plan to increase its global market share quite considerably.

HONOR has a plan to increase its presence/sales in global markets, a 3-year plan

According to the company’s CEO, George Zhao, HONOR plans to increase its global smartphone sales to over 50% of its total sales in the next 3 years. That figure currently sits at 20%, reports GizmoChina.

The CEO added that the key lies in HONOR’s presence in key markets like Latin America (LATAM) and the Middle East and Africa (MEA). The company’s affordable X series and mid-range series phones (the ones with numbers added, such as the HONOR 50, 70, 90, and so on). As already mentioned, HONOR is doing great in Europe, but it’s planning to expand in that area too.

HONOR’s smartphone sales grew more than 200% in the EU in 2023 (YoY). HONOR also predicts a 100% growth for 2024, which would be yet another great feat by the company.

HONOR announced some very compelling hardware & software at MWC 2024

During the Mobile World Congress (MWC) in Barcelona, HONOR had plenty to say. It announced its HONOR Magic6 Pro flagship for global markets, and the company did the same with the Porsche Design HONOR Magic V2 RSR.

In addition to that, the HONOR Pad 9 was also presented to global consumers, and the same goes for the HONOR MagicBook Pro 16. HONOR’s MagicOS 8.0 which runs on the company’s newest hardware also got some love.

HONOR is not slowing down, however. Next month, the Porsche Design HONOR Magic6 RSR is coming. That’s something HONOR already confirmed recently, basically right after its press event in Barcelona.

There’s plenty to look forward to when it comes to HONOR. The company’s products are getting more and more interesting, that’s for sure.

[ad_2]

Source link

Microsoft Paint reportedly getting Midjourney-like art generation capabilities

0

[ad_1]

Microsoft introduced the Paint program nearly 40 years ago, and it’s been the first choice of rookies who want to paint their first pixel. Throughout Paint’s existence, Microsoft has been updating the features and looks of the program to meet the demands of modern times. Lately, the Redmond-based tech giant has been paying a lot of attention to the Paint app.

Now, the credible Windows leaker PhantomOfEarth on X suggests that Paint could soon be getting a major upgrade. It could bring AI-powered art-generation capabilities to the popular Paint program. These functionalities could be similar to the popular art-generation program Midjourney.

Microsoft Paint could get a Midjourney-like ability to create AI art in real-time

Microsoft could be working towards adding the ability to create AI art in real-time in Paint, which could be similar to Midjourney. For the unversed, Midjourney is one of the immensely popular image generator programs. It allows you to generate an image by just typing the description of the photo.

Notably, you can create the image in a style of your choosing including pixel art, paintwork, or photorealism. For example, you can just type “a tiny adorable ginger kitten in studio light”, and Midjourney will create an image for you. Similar functionalities could be coming to Microsoft Paint soon.

Microsoft Paint’s new feature may be something known as Live Canvas

According to the leaker, “The upcoming AI feature for Paint may be something known as Live Canvas”. However, the tipster isn’t entirely clear what exactly this feature will be capable of. However, the name of the AI feature is quite similar to Leonardo.Ai’s Real-Time Canvas functionality. Leonardo.Ai’s feature lets users draw a rough image in one window. And the generative AI brings it to life in the art form in the other window.

Paint new AI feature rumour

The tipster revealed this information by reposting Mayank Palmar’s post, which suggests the upcoming AI feature will be powered by NPU.

If this feature is coming to Paint, then it will become a much more interactive image editing tool for Windows. Notably, Microsoft already offers an AI-powered tool called Paint Cocreator for the Paint app. This is based on OpenAI’s DALL-E text-to-image. Now, it would be good to see more AI-powered real-time art-generation features coming to the Paint app soon.


[ad_2]

Source link

NIST Releases Cybersecurity Framework 2.0: Guide for All Organizations

0

[ad_1]

NIST’s Applied Cybersecurity Division has updated its framework to better suit the needs of a wider range of users, reflecting recent cybersecurity challenges and management practices.

The National Institute for Standards and Technology (NIST) has released its Cybersecurity Framework 2.0, which expands on its recommendations to include organizations beyond critical infrastructure. The first Cybersecurity Framework (CSF) was released in 2014 as a crucial tool for reducing cybersecurity risk to help organizations mitigate cybersecurity risk. 

NIST has updated CSF to be more accessible to all audiences and organizations, including small-to-large organizations across all industries, schools, and nonprofits, regardless of their cybersecurity sophistication level. The updated version is designed to provide “tailored pathways” into the framework, making it easier to implement. 

The CSF 2.0 is not just a single document but a suite of resources that can be customized over time, explained Laurie E. Lozascio, Under Secretary of Commerce for Standards and Technology and NIST Director.

In CSF 2.0, a sixth function, Govern, has been added to the five core functions of Identify, Protect, Detect, Respond, and Recover. It also addresses supply chain risks and includes a reference tool and a searchable catalogue for cybersecurity teams.

The Cybersecurity and Privacy Reference Tool (CPRT) has been launched to simplify the implementation of the Cybersecurity Standard (CSF) by allowing users to search, search, and export data/details from “the CSF’s core guidance in human-consumable and machine-readable formats.”

The searchable catalogue of informative references will allow organizations to cross-reference the CSF’s guidance to over 50 other cybersecurity documents, including NIST’s SP 800-53 Rev. 5. 

The CPRT also provides a set of NIST guidance documents that can be accessed and communicated to technical experts and the C-suite, ensuring coordination across all levels of an organization. 

NIST is expanding its CSF resources, with versions 1.1 and 1.0 translated into 13 languages. CSF 2.0 will be translated by volunteers worldwide. NIST’s collaboration with ISO and IEC has aligned cybersecurity documents, enabling organizations to build frameworks and organize controls with CSF functions.

CSF 2.0 emphasizes governance in cybersecurity strategy, emphasizing that cybersecurity is a significant enterprise risk.

“This update aims to make the framework even more relevant to a wider swath of users in the United States and abroad,” noted Kevin Stine, chief of NIST’s Applied Cybersecurity Division.

According to NIST’s press release, it plans to continue enhancing its resources and amplify user experiences to better understand and manage cybersecurity risks.

Experts Opinions:

For insights into the NIST’s Cybersecurity Framework 2.0; we reached out to Jason Soroko, Senior Vice President of Products at Sectigo. “NIST includes identity management as a first-class citizen within NIST Cybersecurity Framework 2.0. This very comprehensive guidance on cybersecurity, meant to be valuable to many different profiles, includes many of the pillars of certificate lifecycle management,” Jason explained. “It is worth studying the rich resources available by NIST to help navigate to the most useful and relevant parts of the guidance.”

Claude Mandy, Chief Evangelist, Data Security at Symmetry Systems appreciated NIST’s latest release. “It is great to see the update to the NIST Cybersecurity Framework formally released. It is important that standards and framework that are so widely adopted are continually and frequently updated to address the security needs of modern organizations,” said Claude.

“The inclusion of the Govern function is a recognition that mature and defensible security is only possible with clear governance to make decisions on what is required. Although this was implicit in the broader NIST Cybersecurity Framework, the explicit inclusion as a function elevates its importance of it,” he emphasised.

  1. NSA, CISA Release Guidelines to Secure VPNs
  2. CVSS v4.0 – New Supplemental Metrics, OT/ICS/IoT Support
  3. U.S Govt launches new website to fight ransomware, help victims
  4. Poisoned Data, Malicious Manipulation: NIST Study Reveals AI Flaws
  5. White House Cyber Strategy: Software Firms Face Liability for Breaches


[ad_2]

Source link

Russian Hackers Target Ubiquiti Routers for Data, Botnet Creation

0

[ad_1]

Russian hackers, part of Russia’s Main Intelligence Directorate of the General Staff, are using compromised Ubiquiti EdgeRouters to build extensive botnets, steal credentials, collect NTLMv2 digests, and proxy malicious traffic.

The FBI, NSA, US Cyber Command, and international partners have released a joint Cybersecurity Advisory to caution against Russian state-sponsored cyber actors using compromised Ubiquiti EdgeRouters for malicious cyber operations. They have also used compromised routers for spoofed landing pages and post-exploitation tools.

As per the advisory (PDF), Russia-backed APT28 actors (aka Fancy Bear) have been using compromised Ubiquiti EdgeRouters since 2022 to carry out covert cyber operations against various industries, including Aerospace & Defense, Education, and Energy & Utilities. The Czech Republic, Italy, Lithuania, Jordan, Montenegro, Poland, Slovakia, Turkey, Ukraine, and the US are some of its key targets. 

In 2023, APT28 actors used Python scripts to collect webmail user credentials and uploaded them to compromised Ubiquiti routers via cross-site scripting and browser-in-the-browser spear-phishing campaigns. They also exploited the CVE-2023-23397 zero-day, despite being patched, to install tools like Impacket ntlmrelayx.py and Responder on compromised routers, allowing NTLM relay attacks and host rogue authentication servers.

For your information, Microsoft’s Threat Protection Intelligence team discovered this vulnerability in Outlook that allowed attackers to steal Net-NTLMv2 hashes and access user accounts. The vulnerability was previously exploited by the group Forest Blizzard, suspected to have affiliations with the Russian military intelligence agency.  

The FBI has identified IOCs for the Mirai-baed Moobot OpenSSH trojan and APT28 activity on EdgeRouters. APT28 actors exploit vulnerabilities in OpenSSH server processes, hosting Python scripts to collect and validate stolen webmail account credentials. The actors have used iptables rules on EdgeRouters to establish reverse proxy connections and upload adversary-controlled SSH RSA keys to compromised routers. They have also used masEPIE, a Python backdoor capable of executing arbitrary commands on victim machines.

Further probing revealed that APT28 used compromised Ubiquiti EdgeRouters as C2 infrastructure for MASEPIE backdoors deployed against targets. Data sent to and from the EdgeRouters was encrypted using a randomly generated 16-character AES key.

The FBI recommends remediating compromised EdgeRouters by performing a hardware factory reset, upgrading to the latest firmware, changing default usernames and passwords, and implementing strategic firewall rules on WAN-side interfaces.

Network owners should keep their operating systems, software, and firmware up-to-date, and update Microsoft Outlook to mitigate CVE-2023-23397. To mitigate other forms of NTLM relay, network owners should consider disabling NTLM or enabling server signing and Extended Protection for Authentication configurations.

Experts Opinions:

For insights into the latest advisory, we reached out to John Bambenek, President at Bambenek Consulting who emphasised on the importance of patching flaws and keeping the system up-to-date.

“The single biggest advance in cybersecurity across the technical stack in 25 years was when Microsoft made auto-updating the default setting in Windows. Across the IoT, embedded devices, and network stack, this is not the norm,” John argued.

“We know devices aren’t patched by consumers or most organizations so why wouldn’t nation-state actors get in on the target-rich environment? These devices have all the weaknesses of normal computers, just without the ability of the user to harden them, put EDR on them, or do anything we would to a server to make it safer. Until manufacturers treat this problem seriously, whether it’s Mirai or a spy, these devices will continue to be compromised in bulk.”

  1. Hackers Steal $47 Million From American Tech Firm Ubiquiti
  2. US Military Satellite Access Sold on Russian Forum for $15K
  3. Russian Hackers Employ Telekopye Toolkit in Phishing Attacks
  4. Russian APT29 Hacked US Biomedical Giant in TeamCity Breach
  5. Russian Midnight Blizzard Hackers Hit MS Teams in Precision Attack
  6. Russian Hackers Hit European Mail Servers for Political, Military Intel


[ad_2]

Source link

Vivo V30 Pro official with four 50MP cameras, sleek design

0

[ad_1]

Vivo has unveiled its latest V-series premium mid-range Android smartphone, the Vivo V30 Pro. It arrives almost a month after the vanilla V30. The Pro model is focused on performance and photography, with the company partnering with Zeiss for its imaging system. The device will go on sale in early March.

Vivo V30 Pro arrives with four 50MP cameras

The Vivo V30 Pro features four 50MP cameras. There’s a Professional Portrait Camera with a 50mm focal length for “more realistic and vivid portraits.” The main camera comes with a Vivo-exclusive Camera-Bionic Spectrum (VCS) touted to capture accurate colors and clarity in low-light conditions. The ultrawide lens has a 119° field-of-view and boasts autofocus, a first for the V-series ultrawide camera.

There is also a 50MP selfie camera with autofocus on this phone. Vivo doesn’t talk much about the front camera in its official press release. Instead, the company goes into depth on the camera features co-engineered with Zeiss. We have the Vivo V30 Pro in our office for review, so we will soon find out whether the phone lines up to the hype in terms of camera performance.

Vivo V30 Pro 3

Besides cameras, the new Vivo phone features MediaTek’s 4nm Dimensity 8200 chipset paired with up to 12GB of RAM and 12GB of Extended RAM. Vivo has included a large vapor chamber of 3002 sq mm. and its Ultra Large Cooling System for sustained performance during heavy usage. There are 11 built-in temperature sensors on the phone to help keep thermals in check.

As far as the display is concerned, you get a 3D curved AMOLED panel with a 120Hz refresh rate and a peak brightness of 2,800 nits. Vivo has slapped a protective layer of “Schott α” glass on top of the screen. The device is powered by a 5,000mAh battery rated to last up to 20 days on standby. It supports 80W fast charging, reaching from 0 to 100% in just 46 minutes.

Despite a big battery, the Vivo V30 Pro is incredibly slim. The company made it possible with the help of an industry-leading One-Piece Encapsulation Technique to make the battery casing thinner. It claims a battery health of over 80% even after 1600 charge-discharge cycles. The phone also boasts an IP54 rating for dust and water resistance. It runs Android 14 out of the box.

Price and availability

The Vivo V30 Pro will go on sale in several Asia countries, including India, Indonesia, Thailand, Malaysia, Philippines, and Taiwan, in early March. Vivo has already confirmed that the phone will debut in India on March 7. It will reveal the pricing for each market separately. There is no word on the phone’s availability in other regions such as Europe and the US.

Vivo V30 Pro 2

[ad_2]

Source link

A new era for Bitcoin

0

[ad_1]

The cryptocurrency landscape is constantly evolving, and with it, the technology that underpins these digital assets. One of the most exciting developments in recent years is Fantom’s Directed Acyclic Graph (DAG) technology, which has the potential to usher in a new era for Bitcoin and other cryptocurrencies. To stay informed and make well-versed decisions in this rapidly changing environment, engaging with quantum-gforce.com, an Investment Education Firm, can be beneficial. In this article, we will delve deep into the world of Fantom’s DAG, exploring its innovative features, comparing it to Bitcoin’s traditional blockchain, examining real-world use cases, and discussing the challenges and future prospects of this groundbreaking technology.

Understanding DAG Technology

Explanation of Directed Acyclic Graph (DAG)

Directed Acyclic Graph, or DAG, is a data structure that differs significantly from the conventional blockchain. Unlike a blockchain, which consists of a linear chain of blocks, a DAG is a more complex, non-linear structure. In a DAG, transactions are interconnected in a network, forming a directed acyclic graph without a single chain of blocks. This architecture allows for multiple transactions to be confirmed simultaneously, improving scalability and transaction throughput.

How DAG differs from traditional blockchain

One of the key distinctions between DAG and traditional blockchain is the elimination of miners and the associated proof-of-work consensus mechanism. Instead, DAG utilizes a consensus model known as Directed Acyclic Graph Tangle (DAG-Tangle). In this model, each transaction confirms two previous transactions, making it inherently more efficient and scalable.

Advantages and disadvantages of DAG

DAG technology offers several advantages over traditional blockchain:

– Scalability: DAG can process a higher number of transactions per second, making it a potential solution to Bitcoin’s scalability issues.
– Reduced transaction fees: With no miners to pay, transaction fees can be significantly lower.
– Faster confirmations: DAG’s consensus mechanism leads to faster transaction confirmations.

However, there are also challenges and criticisms, including concerns about security and network stability. These issues are actively being addressed by projects like Fantom.

The Evolution of Bitcoin

Overview of Bitcoin’s blockchain technology

Bitcoin, the first cryptocurrency, introduced the concept of blockchain technology in 2009. It relies on a decentralized ledger to record and verify transactions, with miners securing the network and adding new blocks to the chain through proof-of-work.

Limitations and challenges faced by Bitcoin

While revolutionary, Bitcoin’s blockchain has faced several challenges, including scalability issues that result in slower transaction processing times and higher fees during network congestion. Additionally, Bitcoin’s energy consumption has been a topic of concern due to its reliance on proof-of-work mining.

The need for scalability and efficiency improvements

The limitations of Bitcoin’s blockchain have led to the exploration of alternative technologies, such as DAG, to address these issues and enable broader adoption and utility.

Fantom’s Innovative Approach

Introduction to Fantom as a smart contract platform

Fantom is a blockchain platform that incorporates DAG technology to offer a more efficient and scalable solution for decentralized applications (DApps). Fantom aims to combine the security of a blockchain with the scalability of a DAG, making it an attractive option for developers.

How Fantom’s DAG technology works

Fantom’s DAG-Tangle consensus model allows for the confirmation of multiple transactions simultaneously, without the need for miners. This not only increases transaction throughput but also reduces the environmental impact associated with energy-intensive mining.

Unique features and benefits of Fantom’s DAG

Fantom’s DAG technology brings several unique advantages to the table, including:

– High throughput: Fantom can process thousands of transactions per second, far exceeding Bitcoin’s capacity.
– Low transaction fees: The elimination of miners reduces transaction costs.
– Energy efficiency: Fantom’s consensus model consumes significantly less energy than proof-of-work.

Comparing Fantom’s DAG to Bitcoin

Scalability and transaction speed

Fantom’s DAG technology outpaces Bitcoin in terms of scalability and transaction speed. While Bitcoin can handle only a limited number of transactions per second, Fantom’s DAG enables much higher throughput, making it suitable for applications that require quick, low-cost transactions.

Security and consensus mechanisms

Bitcoin’s proof-of-work is known for its robust security, while Fantom’s DAG-Tangle has faced some skepticism in this regard. However, Fantom’s team is continuously working to enhance security and address potential vulnerabilities, making it a viable alternative to Bitcoin.

Environmental impact and sustainability

One of the significant criticisms of Bitcoin is its environmental impact due to energy-intensive mining. Fantom’s energy-efficient DAG technology offers a more sustainable solution, aligning with the growing demand for eco-friendly blockchain solutions.

Challenges and Future Prospects

Potential obstacles and criticisms of Fantom’s DAG

Despite its promise, Fantom’s DAG technology faces challenges related to security, network stability, and adoption. It’s important to acknowledge these obstacles and actively address them to ensure the technology’s success.

How Fantom aims to address these challenges

The Fantom team is actively working on research and development to enhance the security and stability of their DAG technology. Their commitment to addressing challenges is crucial for its long-term viability.

The role of Fantom in shaping the future of blockchain technology

Fantom’s DAG represents a significant step forward in the evolution of blockchain technology. Its success could pave the way for the adoption of DAG in other blockchain platforms, driving innovation and efficiency across the entire crypto space.

Conclusion

In conclusion, Fantom’s DAG technology holds immense promise in addressing the limitations of Bitcoin’s traditional blockchain. With its efficient consensus model, high throughput, and eco-friendly approach, Fantom has the potential to shape the future of blockchain technology, offering a compelling alternative to Bitcoin and other cryptocurrencies. As the crypto landscape continues to evolve, Fantom’s DAG is undoubtedly a technology worth watching.
[ad_2]

Source link

LoanDepot January Hack: 16.9M Individuals Data Exposed

0

[ad_1]

In a significant cybersecurity incident, loanDepot, a prominent player in the loan and mortgage industry, announced a data breach that potentially compromised the sensitive personal information of approximately 16.9 million individuals.

This breach, identified in early January 2024, has raised concerns over the security measures to protect consumer data in the financial sector.

You can analyze a malware file, network, module, and registry activity with the ANY.RUN malware sandbox, and the Threat Intelligence Lookup that will let you interact with the OS directly from the browser.

The Breach Unfolded

The incident occurred on January 4, 2024, when loanDepot detected unusual activity within its systems.

Immediate steps were taken to contain the breach, including contacting law enforcement and initiating a thorough investigation with the help of external cybersecurity experts.

The investigation revealed that between January 3rd and January 5th, 2024, an unauthorized party accessed systems containing a wealth of personal information.

The data accessed during the breach includes names, addresses, email addresses, financial account numbers, social security numbers, phone numbers, and dates of birth.

This extensive range of personal details poses a significant risk of identity theft and fraud for those affected.

LoanDepot has taken several measures to address the situation and mitigate potential damages in response to the breach.

These steps include enhancing security protocols and offering affected individuals 24 months of complimentary identity protection services and credit monitoring through Experian.

This service aims to detect and resolve any misuse of personal information and support victims of identity theft.

loanDepot urges affected individuals to take advantage of the Experian IdentityWorksSM membership, including credit monitoring, $1M identity theft insurance, and full-service identity restoration.

Enrollment instructions have been provided to ensure timely access to these protective services.

Additionally, consumers are advised to remain vigilant by regularly reviewing their account statements and credit reports.

Immediately reporting suspicious activity can significantly reduce the risk of financial loss and identity theft.

This breach underscores financial institutions’ ongoing challenges in safeguarding consumer data against increasingly sophisticated cyber threats.

It also highlights the importance of robust regulatory frameworks to ensure companies implement adequate security measures and respond appropriately to incidents.

The loanDepot data breach serves as a stark reminder of the vulnerabilities in the digital infrastructure of financial services.

As the investigation continues, the incident prompts a broader discussion on the need for enhanced cybersecurity measures and consumer awareness to combat the rising tide of digital fraud and identity theft.

Affected individuals are encouraged to take proactive steps to protect their personal information and seek assistance if they suspect any fraudulent activity.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link

Change Healthcare outages reportedly caused by ransomware

0

[ad_1]

On Wednesday February 21, 2024, Change Healthcare—a subsidiary of UnitedHealth Group—experienced serious system outages due to a cyberattack.

In a Form 8-K filing the company said it:

“identified a suspected nation-state associated cyber security threat actor had gained access to some of the Change Healthcare information technology systems.”

Change Healthcare is one of the largest healthcare technology companies in the United States. Its subsidiary, Optum Solutions, operates the Change Healthcare platform. This platform is the largest payment exchange platform between doctors, pharmacies, healthcare providers, and patients in the US healthcare system.

The incident led to widespread billing outages, as well as disruptions at pharmacies across the United States.

According to Reuters, the group behind the attack is the ALPHV/BlackCat ransomware group. ALPHV is currently one of the most active groups, and generally associated with Russia. They are certainly no strangers to attacking healthcare providers. In our monthly ransomware reviews you will typically find them in the top five of ransomware groups. Even after a disruption in December 2023 they returned and maintained a high level of activity.

BleepingComputer confirmed Reuters assertion, saying it had received information from forensic experts involved in the incident response that linked the attack to the ALPHV ransomware gang.

It would certainly make more sense to us that the attacker was a ransomware group than a nation-state associated group, but both ALPHV and UnitedHealth have not commented on this. That’s no surprise since the investigation is probably still ongoing and solving the security issue is a higher priority.

What the ramifications of any stolen data are, remains to be seen, but they could be very serious given the size of the company and the nationwide application of their electronic health record (EHR) systems, payment processing, care coordination, and data analytics.

In a February 26 update the company says it took immediate action to disconnect Change Healthcare’s systems in order to prevent further impact. You can follow updates about the issue on the dedicated incident report site.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; and disable or harden remote access like RDP and VPNs.
  • Prevent intrusions. Stop threats early before they can even infiltrate or infect your endpoints. Use endpoint security software that can prevent exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like ThreatDown EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Our business solutions remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

[ad_2]

Source link