New Android threat sends your photos, texts, contacts, hardware data and more to a foreign server

0

[ad_1]

According to Bleeping Computer, a new version of the XLoader malware (aka MoqHao) is making the rounds. Previously, this malware was spotted in the U.S., U.K., Germany, France, Japan, South Korea, and Taiwan. The malware is disseminated through SMS text messages that feature a shortened URL link and XLoader can launch immediately after installation. This allows the malware to run undetected in the background while personal data is stolen away.

McAfee says, “While the app is installed, their malicious activity starts automatically. We have already reported this technique to Google and they are already working on the implementation of mitigations to prevent this type of auto-execution in a future Android version.”

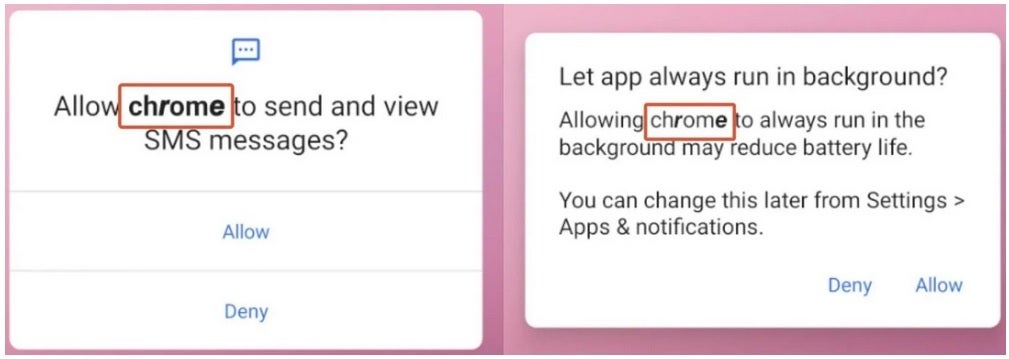
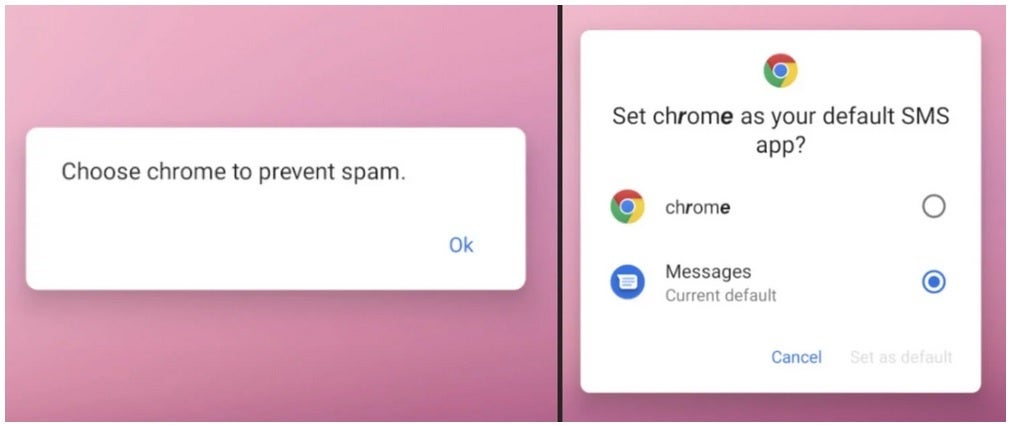
The malicious apps send out permission requests pretending to come from Google Chrome requesting permission to send and view SMS (text) messages and asking permission to keep “Chrome” running in the background. And the coup de grace is permission to make “Chrome” your default SMS app. The malware, once it gets all of these permissions, is used to send photos, text messages, contact lists, and info on the hardware you are using (including your phone’s unique IMEI number) to the control server. Yes, it is very scary.

McAfee says that since minimal interaction is required by the victim, the new XLoader malware is even more dangerous than its predecessor. There is some good news. An update from McAfee dated a couple of weeks ago says that Android devices with Google Play Services are protected from attacks from this kind of malware by Google Play Protect which is enabled by default.

Still, there are some takeaways to consider here. Never click on a shortened URL found in a message. And never sideload an app.

[ad_2]

Source link

X (formerly Twitter) expands audio and video calls to all users

0

[ad_1]

X, the social media network formerly known as Twitter, is expanding its audio and video calling capabilities. Previously a perk for Premium (what used to be called “Twitter Blue”)  subscribers, this feature will now be available to everyone on the platform.

As reported by Engadget, Enrique Barragan, an engineer at X, announced the expansion via a post on the platform. This was done while quoting Elon Musk’s promise back in January where he said this would arrive to all users when the feature was robust enough.
The move brings X closer to Elon Musk’s goal of making the platform an “everything app,” as he has so often expressed. Calls were added for iOS users last year, followed by Android, but only paying subscribers could use them. 

How does it work?

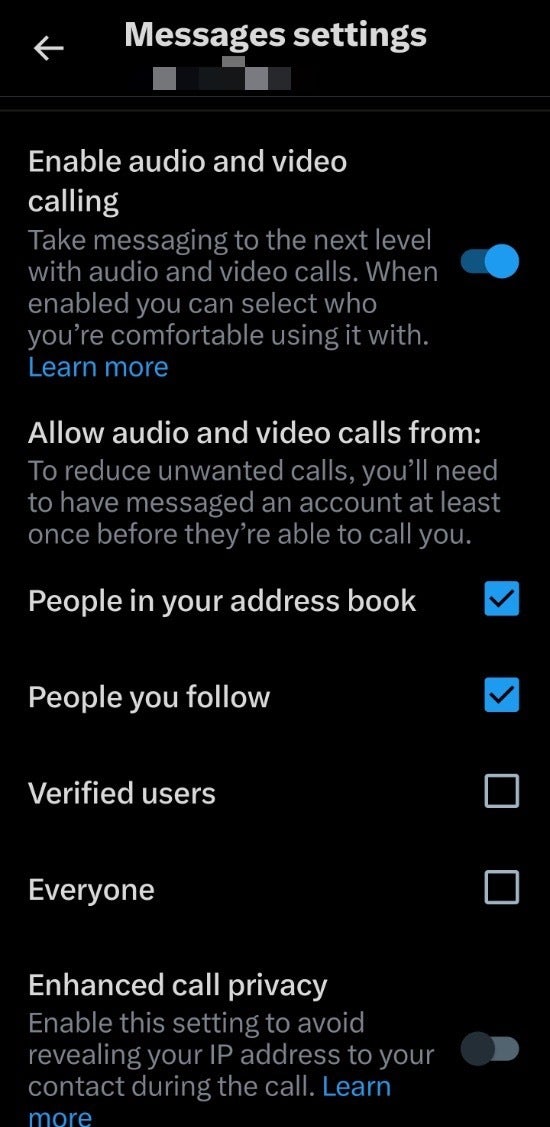
The official support page says that you are able to control your audio and video calling options from the Direct Messages settings. From there, you will notice that by default, you are able to receive calls from accounts you follow or have in your address book — provided that you give X access to your address book. However, in order to call another user, both the caller and the recipient must have been in contact at least once via X’s Direct Messages (DMs).

X’s Audio and Video call settings in Direct Messages

This doesn’t mean that you cannot allow calls from everyone on the platform, though. If you are feeling adventurous, you can go ahead and do just that by turning on that option. However, if you plan on doing so, our advice would be to also turn on the new “Enhanced call privacy” setting, which hides your IP from people you call and receive calls from. As a matter of fact, you should probably turn on this option anyway if you plan on calling people from X.

The updated calling features aren’t instantly available for everyone. X is slowly rolling them out, likely in batches, and it appears that they are automatically turned on without prompting. If you do not wish to make and receive calls on X/Twitter, you may need to log in to the app and navigate to your Direct Message settings to turn the feature off.


[ad_2]

Source link

New features eyed for the Google Search widget on the Android home screen

0

[ad_1]

Android users of all shapes and sizes are used to the Google Search widget that appears on their home screen. Back in the day when Android was starting to make a name for itself and this writer carried a Motorola DROID, I  thought the Google Search widget was cool. Perhaps some of you guys and gals feel (and still feel) the same. Nonetheless, it appears that Google is considering making some changes to the capabilities of the Search widget and the tech company needs your help.

The Google Search home screen widget is part of the “Mobile Application Distribution Agreement” that Android phone manufacturers sign when installing the Google Mobile Services version of Android on a new model. In some markets, Android users are able to change the search engine used by the widget.
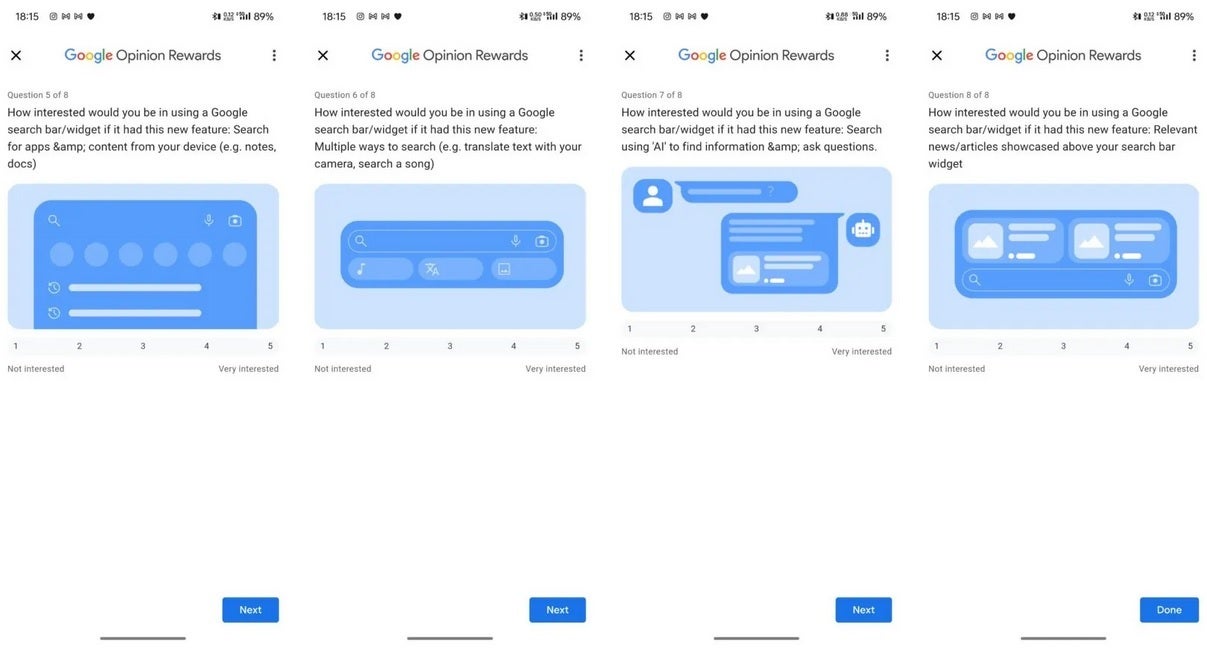
According to Android Authority’s Aamir Siddiqui, while setting up a new Android phone, he removed the Google Search widget from the home screen, Aamir received a Google Opinion Rewards survey that wanted to know why Siddiqui removed the Google Search widget from the home screen. The survey also asked, on a scale of 1-5 with the latter indicating the most interest, what Siddiqui thought about adding a few new search features to the widget such as translating text with the camera or using the widget to search for a song.

Other survey questions wanted to know whether Aamir wanted a new feature on the widget that would allow him to search through app content on his phone (similar to universal search), and use AI to help him search from the widget. Another survey question asked Aamir how interested he was in viewing relevant news articles above the search bar widget on the home screen.

Whether the results of the survey lead to changes to the Google Search widget is impossible to tell since we don’t know how each Android user will respond to the questions. But if changes are made (and we get the feeling that it wouldn’t be imminent) the survey might have had a hand in how Google “improves” the Search widget.

[ad_2]

Source link

Recent Joomla Update Brings Multiple Security Fixes – Latest Hacking News

0

[ad_1]

Joomla users must ensure that they receive the latest update as the platform fixes numerous security vulnerabilities. One of these includes a severe code execution vulnerability.

Joomla Fixes Numerous Security Vulnerabilities

According to a recent advisory, Joomla developers addressed five vulnerabilities with the latest CMS update, calling it a “security and bug fix” release. These include the following.

  • CVE-2024-21722: A low-severity vulnerability due to improperly terminating existing user sessions during MFA changes.
  • CVE-2024-21723: A low-severity open redirect vulnerability that existed due to inadequate parsing of URLs.
  • CVE-2024-21724: A  moderate severity cross-site scripting (XSS) vulnerability that could affect extensions due to improper input validation for media selection fields.
  • CVE-2024-21725: Another cross-site scripting vulnerability that existed due to inadequate escaping of mail addresses. Given the nature of the exploit which could lead to remote code execution, this vulnerability achieved a high severity rating.
  • CVE-2024-21726: A moderate severity cross-site scripting vulnerability that could affect various components due to inadequate content filtering.

These vulnerabilities affected different Joomla versions, which the developers patched with Joomla 4.4.3 and 5.0.3 releases. Besides, for Joomla version 3.x users, the update 3.10.14-elts arrived as a security update, carrying all bug fixes.

While the platform addressed the security vulnerabilities for all Joomla releases, users are still advised to upgrade to Joomla 5.0.3 as it also includes new features.

Joomla is an open-source content management system (CMS) that facilitates organizations, small companies, web agencies, and e-stores in setting up their websites and online apps without hassle.

Given its free availability, user-friendly interface, and seamless compatibility with Microsoft Windows and Unix-like systems alike, Joomla attracts a huge user base from around the world. Consequently, any security vulnerabilities in the platform directly risk a large number of users worldwide. Hence, Joomla users must ensure updating their sites with the latest security releases to receive all bug fixes in time and avoid potential threats.

Let us know your thoughts in the comments.

[ad_2]

Source link

X gets with the program and lets free users make voice and video calls

0

[ad_1]

When Elon Musk’s X gained the ability to make voice and video calls, we were all pretty bummed by the fact that it was only available for X Premium users. This is a feature that’s freely available on platforms like WhatsApp, Instagram, Facebook Messenger, Snapchat, and so on. However, it appears that X got with the program and now allows free users to make video and voice calls.

Late last year, X introduced the ability to make voice and video calls, and it finally made it to the public. However, one thing about this feature that people appreciated was the fact that a person can only call you if they’ve been in contact with you at some point before. So, if you’ve sent a person the message in the past, only then will they be able to call you. There are other settings you could set to control who can call you, as well.

X now lets free users make video and voice calls

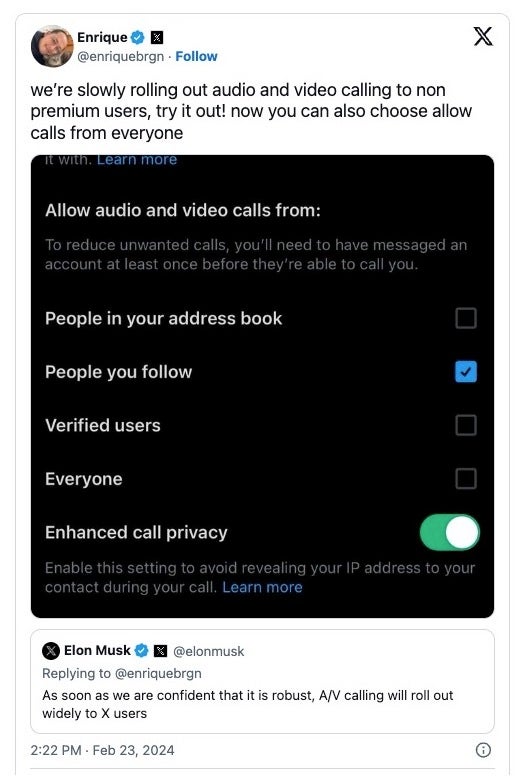
X Employee @enriquebrgn made a post stating “we’re slowly rolling out audio and video calling to non premium users, try it out!” In the post, we see a screenshot of the voice and video call settings. These settings allow you to choose who is able to call you.

You can choose to have only people in your address book call you, only people you follow, only verified users, and everyone. The ability to allow everyone to call you is a new addition. So, if you’re feeling brave, you can enable that feature. However, notable figures and accounts with a lot of enemies may want to steer clear of it. Enabling voice and video calls from everyone basically gives any sort of person free rein to call you out of the blue.

Since this is still rolling out, there’s a chance that you won’t be able to make calls just yet. You’re going to have to wait for the functionality to reach you via the latest update. To check for an update, go to the Google Play Store or Apple App Store and search for X. If you’re on Android, you can simply hold your finger down on the X app icon on your home screen and tap the App info button. This will take you straight to the X Google Play Store page.

If you see the option to update the app, update it. If you don’t see it, then you’ll just want to wait a few days.


[ad_2]

Source link

US goes even further to prevent a 5nm successor to Huawei’s Kirin 9000s

0

[ad_1]

Reuters reported that the Biden administration has intensified restrictions on China’s top sanctioned chipmaker, SMIC, following revelations that its most advanced factory, SMIC South, produced a sophisticated chip for Huawei’s Mate 60 series devices.

China manages to fabricate chips despite several trade restrictions intended to prevent the same

The trade sanctions aim to curb the flow of U.S. technology to SMIC and undermine its ability to manufacture advanced chips for Huawei or any other Chinese manufacturer. The Huawei Mate 60 series, powered by the 7nm Kirin 9000 series chip, symbolized China’s technological resurgence despite ongoing efforts by the U.S. to impede its semiconductor capabilities.

There are also reports that Huawei is working on a 5nm chip amidst all the sanctions. As PhoneArena noted, this new Kirin chip could result in a significant leap for Huawei phones in 2024. It reportedly gets closer to Apple’s 3nm A17 Pro. Although, there’s no concrete evidence of the development at this point. Nonetheless, US officials are definitely feeling the need to impose even stricter restrictions on the US suppliers of chip-building equipment in order to prevent a successor to China’s Kirin 9000 chips.

A response to Huawei’s development of Kirin chips

Late last year, the US Department of Commerce sent letters to US suppliers to SMIC, preventing them from supplying chip manufacturing equipment to SMIC’s most advanced plant, SMIC South. Notably, it was reported that SMIC South is the only chip manufacturing plant in China capable of fabricating cutting-edge chips that can meet the requirements of Huawei’s flagship devices. The said letters to US suppliers effectively cut off millions of dollars worth of shipments of chipmaking materials to the said plant, reported Reuters.

The trajectory of restrictions on SMIC and Huawei has been gradual but consequential. Both companies were added to trade restrictions lists in 2019 and 2020, respectively, over alleged violations and ties to China’s military complex. However, the Trump administration allowed shipments to them under certain conditions. In October 2022, the Biden administration implemented new rules banning U.S. suppliers from sending semiconductor tools and materials to advanced Chinese-run chipmaking factories, including SMIC South.

While Entegris, a Massachusetts-based company maintains it complied with valid export licenses, it ceased shipments after receiving letters from the Commerce Department. The Biden administration’s actions signify a concerted effort to restrict SMIC’s access to advanced U.S. technology, a move criticized by the Chinese embassy in Washington as “economic bullying.”

The impact of these restrictions extends beyond SMIC’s operations, affecting its supply chain and potentially disrupting production for several months. As Lita Shon-Roy, CEO of market research firm Techcet said, “It would take time to find and conduct rigorous testing of new suppliers unless SMIC South had done so in advance.”

[ad_2]

Source link

A Red Team Tool For Generative AI Systems

0

[ad_1]

In a significant move to bolster the security of generative AI systems, Microsoft has announced the release of an open automation framework named PyRIT (Python Risk Identification Toolkit).

This innovative toolkit enables security professionals and machine learning engineers to proactively identify and mitigate risks in generative AI systems.

Collaborative Effort in AI Security

Microsoft emphasizes the importance of collaborative efforts in security practices and the responsibilities associated with generative AI. The company is dedicated to providing tools and resources that support organizations worldwide in responsibly innovating with the latest AI technologies.

PyRIT, along with Microsoft’s ongoing investments in AI red teaming since 2019, underscores the company’s commitment to democratizing AI security for customers, partners, and the broader community.

The Evolution of AI Red Teaming

AI red teaming is a complex, multistep process that requires an interdisciplinary approach. Microsoft’s AI Red Team consists of experts in security, adversarial machine learning, and responsible AI, drawing on resources from across the Microsoft ecosystem.

This includes contributions from the Fairness Center in Microsoft Research, AETHER (AI Ethics and Effects in Engineering and Research), and the Office of Responsible AI.

Over the past year, Microsoft has proactively red-teamed several high-value generative AI systems and models before their release to customers.

This experience has revealed that red teaming generative AI systems distinctly differ from traditional software or classical AI systems. It involves probing security and responsible AI risks simultaneously, dealing with the probabilistic nature of generative AI, and navigating the varied architectures of these systems.

Document

Analyse Shopisticated Malware with ANY.RUN

More than 300,000 analysts use ANY.RUN is a malware analysis sandbox worldwide. Join the community to conduct in-depth investigations into the top threats and collect detailed reports on their behavior..

Introducing PyRIT

PyRIT was initially developed as a set of scripts used by the Microsoft AI Red Team as they began red teaming generative AI systems in 2022. The toolkit has evolved to include features that address various risks identified during these exercises.

PyRIT is now a reliable tool that increases the efficiency of red teaming operations, allowing for the rapid generation and evaluation of malicious prompts and responses.

The toolkit is designed with abstraction and extensibility in mind, supporting a variety of generative AI target formulations and modalities. PyRIT integrates with models from Microsoft Azure OpenAI Service, Hugging Face, and Azure Machine Learning Managed Online Endpoint.

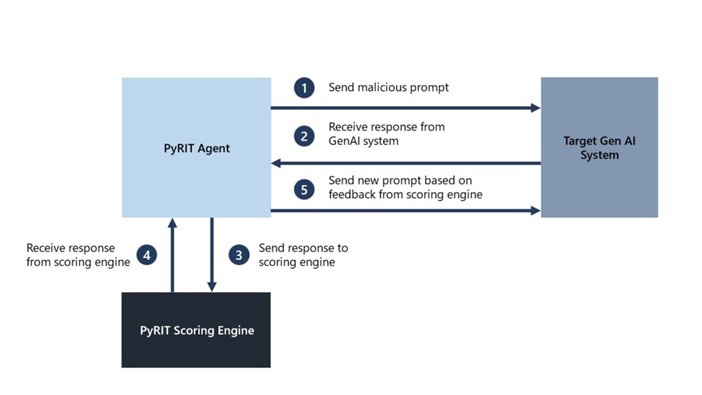
It also includes a scoring engine that can use classical machine learning classifiers or leverage an LLM endpoint for self-evaluation. It also supports single and multi-turn attack strategies.

Moving Forward with PyRIT Components

Microsoft encourages industry peers to explore PyRIT and consider how it can be adapted for red teaming their own generative AI applications. To facilitate this, Microsoft has provided demos and is hosting a webinar in partnership with the Cloud Security Alliance to demonstrate PyRIT’s capabilities.

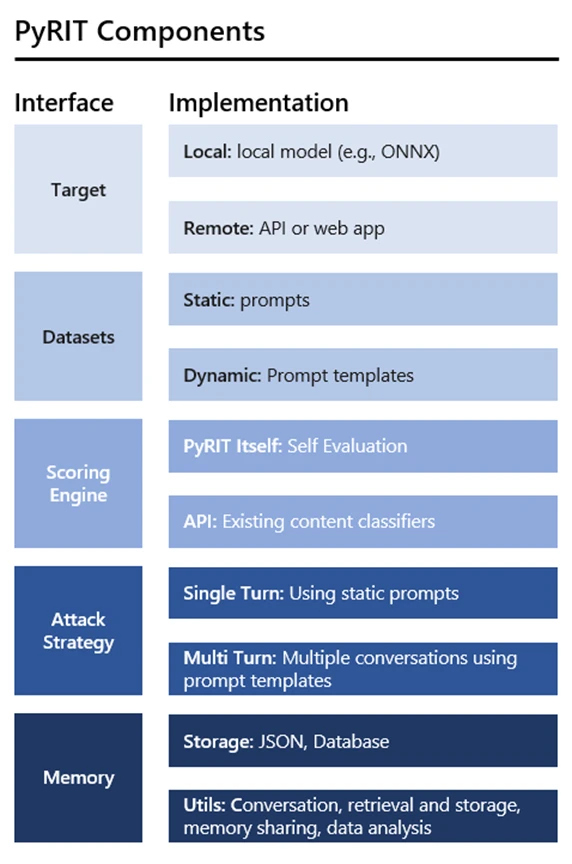
PyRIT components
PyRIT may be used as a web service or incorporated in apps to formulate generative AI targets. Text inputs are originally supported, but more modalities can be added. Microsoft Azure OpenAI Service, Hugging Face, and Azure Machine Learning Managed Online Endpoint models work smoothly with the toolkit. This integration makes PyRIT a versatile AI red team bot that can interact in single and multi-turn scenarios.
The datasets component of PyRIT lets security experts choose a static collection of malicious questions or a dynamic prompt template to test the system. These templates enable encoding many damage categories, including security and responsible AI failures, and automated harm investigation across all categories. PyRIT’s initial version contains prompts with popular jailbreaks to assist people get started.
PyRIT’s scoring engine evaluates target AI system outputs using a standard machine learning classifier or an LLM endpoint for self-evaluation. Additionally, Azure AI Content filters may be used via API.
Two attack techniques are supported by the toolkit. Sending jailbreak and harmful suggestions to the AI system and rating its reaction is the single-turn strategy. The multi-turn approach responds to the AI system depending on the starting score, creating more intricate and realistic adversarial behavior.
To analyze intermediate input and output interactions later, PyRIT stores them in memory. This feature allows for more multi-turn talks and the sharing of explored topics.
Microsoft invites industry colleagues to use PyRIT to red team generative AI solutions. Microsoft and Cloud Security Alliance are holding a webinar to highlight PyRIT’s capabilities. Microsoft’s plan to map, measure, and manage AI risks promotes a safer, more responsible AI environment.

This release represents a significant step in Microsoft’s strategy to map, measure, and mitigate AI risks, contributing to a safer and more responsible AI ecosystem.

For more information on Microsoft’s AI Red Team and resources for securing AI, interested parties can watch Microsoft Secure online and learn about product innovations that enable the safe, responsible, and secure use of AI.

[ad_2]

Source link

Russian Ministry Software Backdoored with North Korean KONNI Malware

0

[ad_1]

Discover the latest cybersecurity revelation: KONNI malware, linked to North Korean cyber operations, targets the Russian Ministry of Foreign Affairs. Learn about the sophisticated tactics and geopolitical implications

German cybersecurity firm DCSO has discovered a malware sample uploaded to VirusTotal in January 2024, believed to be part of North Korea-linked activity targeting the Russian Ministry of Foreign Affairs (MID). The malware is believed to be KONNI, a North Korean nexus tool used since 2014.

KONNI, first discovered in 2014, is associated with the Democratic People’s Republic of Korea (DPRK)-nexus actors like Konni Group and TA406. The malware has unique stealer functionality and remote administration capability. It’s installed in an MSI file, with C2 servers encrypted with AES-CTR, and a CustomAction for detection and payload selection.

In the latest discovery, researchers noted that KONNI’s command set remains unchanged, allowing operators to execute commands, upload/download files, specify sleep intervals, communicate via HTTP, and compress file extensions into .CAB archives.

Interestingly, the sample DCSO analyzed was delivered via a backdoored Russian language software installer, similar to a previously observed KONNI delivery technique. The sample was for a tool called “Statistika KZU”, which is believed to be intended for internal use within the Russian MID. The software is used for relaying annual report files from overseas consular posts to the MID’s Consular Department via a secure channel.

Additionally, two user manuals were found in the backdoored installer, detailing the installation and usage of the “Statistika KZU” program. The first manual explains installing the program on an administrative account, providing minimum software requirements and screenshots.

The second 22-pager manual, “StatRKZU_Pyкoвoдcтвo,” outlines how to use the software for generating annual report files on KZU consular activities, including templates for calculating registered and detained citizens.

The MID’s software, identified as “GosNIIAS” (a Russian federal research institute primarily involved in aerospace research), was tested offline and found legitimate. Despite no direct correlations between GosNIIAS and Statistika KZU, references to contracts were found, including a procurement order for automated system maintenance and data protection software.

This discovery comes amid increasing geopolitical proximity between Russia and the DPRK, following Russia’s renewed invasion of Ukraine in 2022.

Russia and North Korea’s Cyber Standoff

This is not the first time Russia and North Korea have made collective headlines over cybersecurity threats. In August 2023, the world witnessed another significant incident when “elite North Korean hackers” affiliated with OpenCarrot and the Lazarus group breached NPO Mashinostroyeniya, a key Russian missile developer. This breach, lasting for at least five months, revealed the alarming capabilities and determination of the attackers.

Previous Use of KONNI Backdoor

KONNI has been used in many cyberespionage campaigns targeting Russian agencies. FortiGuard Labs discovered a KONNI malware campaign in November 2023, targeting Windows systems through Word documents with malicious macros. Malwarebytes researchers discovered a campaign in mid-2021 using Russian language lures concerning Russian-Korean trade and economic issues and a meeting of a Russian-Mongolian intergovernmental commission.

An unknown hacking group targeted North Korean organizations using KONNI Malware in 2017. Three campaigns were identified back then- two by Talos Intelligence, a Cisco-owned cybersecurity firm, and the third reported by Cylance security firm.

For insights into this, we reached out to John Bambenek, President at Bambenek Consulting, who emphasised that “It is not uncommon for intelligence agencies to spy even on their putative allies, if for nothing else, for insights to either strengthen the relationship or to identify and mitigate threats.”

Mr. Bambenek highlighted that “The use of a backdoor in software used almost exclusively by the Russian Foreign Ministry stands out and shows that the DPRK did their research here for a particular hook into their victims and is, ironically, a more targeted and precise adaptation of the approach Russian intelligence used with NotPetya.”

“Espionage has a couple of nuances where sometimes you want more sophisticated tools and for some attacks, you want narrow and simpler tools. For espionage, you want long-term persistent infection and sophisticated and interactive tools provide defenders more opportunities for detection. It’s not uncommon to see tools used for espionage that lack some of the obfuscation commonly observed in cybercrime tools,” he added.

  1. Gone: Russian Central Bank hacked; $31 million stolen
  2. 2 Russian Industrial Firms Hacked, 112GB of Data Leaked
  3. Anonymous Leaks 128 GB of Data from Russian ISP Convex
  4. Elite North Korean Hackers Breach Russian Missile Developer
  5. Anonymous Hacks Central Bank of Russia; Leaks 28GB of Data


[ad_2]

Source link

Intel aims to surpass TSMC in advanced chip-manufacturing

0

[ad_1]

Intel has revealed its strategy to surpass its biggest rival TSMC in advanced chip manufacturing, aiming to regain its position as the maker of the world’s fastest and most sophisticated chips. At the IFS Direct Connect 2024 event in San Jose, California, the company disclosed its roadmap, including the use of Intel 18A and Intel 14A manufacturing technologies, with Microsoft set to utilize its 18A technology for a custom computing chip.

Intel’s ambitious plans mark a significant effort to reclaim its dominance in chip manufacturing. The company aims to outpace TSMC later this year with its Intel 18A technology, followed by extending this lead into 2026 with the introduction of Intel 14A. With Microsoft on board as a customer for its 18A technology, Intel expects to see an increase in foundry orders, now projecting $15 billion compared to the previously estimated $10 billion.

TSMC remains tight-lipped about the competitiveness of its advanced technologies

Meanwhile, TSMC is keeping quiet about the competitiveness of its advanced technologies, despite Intel’s push to regain market leadership. TSMC’s stock performance reflects its current dominance in producing advanced chips for AI applications, with its Taipei-listed stock surging nearly 17% this year.

The unveiling of Intel’s 14A technology marks the company’s first detailed roadmap beyond 2025, a deadline set by Intel CEO Pat Gelsinger to regain chipmaking supremacy. Intel’s focus on attracting outside customers and securing government subsidies underscores its commitment to revitalizing its chip manufacturing operations. The company hopes to leverage its geographic diversity and partnerships with institutions like ARM and universities to strengthen its position in the market.

Intel’s effort to entice outside customers, including potential collaborations with industry leaders like Nvidia, is seen as crucial for its turnaround strategy. While Nvidia has not announced a deal with Intel yet, analysts believe Intel’s special technology for AI chips could be appealing to companies in the AI chip market.

Overall, Intel’s roadmap signals a determined effort to regain its competitive edge in chip manufacturing, with the success of its strategy dependent on attracting key customers and executing its plans effectively over the coming years.

Intel Core Ultra Specs Benchmarks Features (1)

[ad_2]

Source link